Uses, In Any Current Or Future Media, Including
reprinting/republishing this material for advertising
Or Promotional Purposes, Creating New Collective
works, for resale or redistribution to servers or lists, or reuse of any copyrighted component of this work in other works.
For Cybersecurity Monitoring
Zag ElSayed⋆, Nelly Elsayed†, Chengcheng Li†, Magdy Bayoumi‡
⋆Oil Center Research, Llc, Usa
Abstract—Network security morning (NSM) is essential for any cybersecurity system, where the average cost of a cyber attack is $1.1 million. No matter how secure a system, it will eventually fail without proper and continuous monitoring. No wonder that the cybersecurity market is expected to grow up to $170.4 billion in 2022. However, the majority of legacy industries do not invest in NSM implementation until it is too late due to the initial and operation costs and static unutilized resources. Thus, this paper proposes a novel dynamic Internet of things (IoT) architecture for an industrial NSM that features a low installation and operation cost, low power consumption, intelligent organization behavior, and environmentally friendly operation. As a case study, the system is implemented in a mid-range oil a gas manufacturing facility in the southern states with more than 300 machines and servers over three remote locations and a production plant that features a challenging atmosphere condition. The proposed system successfully shows a significant saving (>65%) in power consumption, acquires one-tenth of the installation cost, develops an intelligent operation expert system tool as well as saves the environment from more than 500mg of CO2 pollution per hour, promoting green IoT systems.
Index Terms—IoT, NSM, green systems, oil and gas, Network
I. Introduction
Network Security Monitoring (NSM) is defined as the col- lection, detection, and analysis of network security data as well as escalation of indications and warnings to detect and respond to intrusions on computer networks . Network security mon- itoring tools typically feature: network-based threat detection, machine base threat detection, proactive network queries for security data and “hunting” for suspicious behavior, integration with one or more threat feeds, and create security alerts .
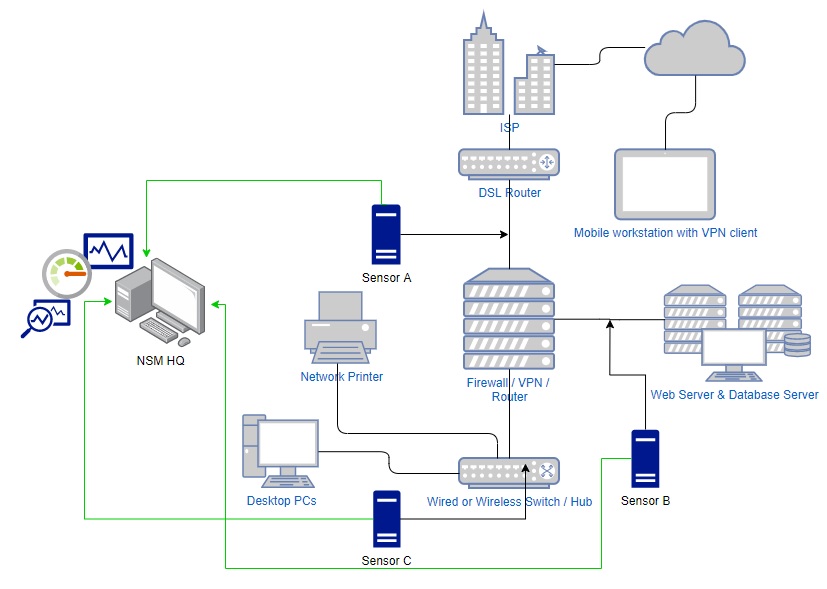
Information Network Security has traditionally started via the the domains of Computer Network Defense (CND) . NSM is based upon the concept that prevention eventually fails. No matter how much time and resources were invested in static securing a network, without employing a continuous monitoring operation, eventually, the scenario will make the bad guys win. By analogy, all Middle Ages castles eventually were fallen or surrendered due to advanced weapon technology or political events . Thus, when this happens, there should be an organized technical system able to detect and respond Fig. 1: A typical NSM sensor placement scenario.
to the intruder’s presence so that an incident may be declared and the intruder can be eradicated with minimal damage done. Any NSM system essentially depends on a device that captures network traffic, detects the anomaly, and performs analysis over various levels of detail. This device is called an NSM sensor. NSM sensors consist of a software suite that is very resource hungry and relay on expensive hardware. The storage disk is the main issue with the sensor, which can grow up to ∼1Tbyte per day in some situations depending on the data type that it uses. Additionally, NSM data can grow exponentially and require regularly scheduled maintenance, backup, and means of accessibility. It is important to note that if the captured data is lost, this can limit the ability to perform retrospective analysis, which is crucial for a current investigation. Most of the current technologies consider the sensors as passive devices with two interfaces, one interface for management and logging and the other interface for traffic capture. The sensor is also usually used for just reporting to a centralized point for analysis and alert reporting, such as the Snort© repository, as shown in Fig. 1, where the green lines represent the management traffic to the central NSM HQ.
The static operation of the sensors makes them frozen in time, role, and functionality, as well as the lack of feedback control, which makes the sensor look like a waste of investment that pushes back many industrial implementations to refuse to add dedicated NSM systems to their network until it is too late, which is one of the main issues with the NSM implementation.
However, by boosting ”life” to these sensors via commu- nication, collaboration, and active control of sensor system architecture can increase their efficiency, increase their illusion of intelligence and reduce the overhead of operation and maintenance costs. Thus, this work applies a novel approach by injecting the dynamic Internet of Things (IoT) concepts to the NSM sensors, which reduces their size, adds the communication and the control framework, and applies the messaging system to reduce the hardware requirements, lower the operating power consumption and makes the detection and prevention faster for many network intrusions.
Additionally, as a proof of concept, this architecture was applied to the information system network of an oil and gas production facility with more than 300 machines and serves, serving three remote branches. The proposed architecture system saves more than one order of magnitude in equipment cost and more than 1.867MW of annual power consumption, as well as saves the environment from more than 4000 mg of CO2 emission per day.
Ii. Background
Oil and gas industrials support 10.3 million jobs in the United States and nearly eight percent of our nation’s gross domestic product, with 32.5% of the market share. The oil and gas industry faces unique cybersecurity challenges, given their distributed, decentralized structures and the large operational technology environment that does not fit the traditional cy- bersecurity scenarios. Thus, the majority of the manufacturers do not have a complete cyber security implementation due to cost, revenue, utilization, and investment. The investment gap has left most heavy industries insufficiently prepared for monitoring, detecting, and preventing threats. As a result, they are attractively targeted by cybercrimes; in 2018, nearly 60% of relevant surveyed organizations had experienced a breach that ended up with financial loss, several of which considered adding the NSM system only after the cyberattack incidents .
The current technology features many advanced and so- phisticated NSW systems for open source and commercial implementations . However, no matter how complex the NSM system is, it still depends on the essential actor of the system, which is the NSM Sensor Platform (SP). The SP is a combination of hardware and software that perform: collection such as Packet Capturing (PCAP) or NetFlow , detection such as Signature-Based, Reputation-Based, and/or Anomaly-Based, and network threat analysis . SPs can be classified by their functionality into three classes: Collection Only, Half-Cycle, or Full-Cycle, depending on what operations they perform, which can be: collection only, collection and detection, or collection, detection, and analysis, respectively.
Fig. 2: Security Onion high-level system architecture . SPs usually require a lot of hardware resources. For exam- ple, a simple Security Onion© SP requires 12GB of mem- ory, four cores processor, 200GB of disk storage, and two network interfaces . Security onion system architecture is shown in Fig. 2. Security Onion is a free and open- source Linux distribution for threat hunting, enterprise security monitoring, and log management. The Security Onion includes Elasticsearch , Logstash, Kibana, Suricata, Zeek, Wazuh, Stenographer, Hive, Cortex, CyberChef, and NetworkMiner, and it requires expensive hardware configuration .
NetFlow is an embedded instrumentation within Cisco IOS Software. It is used to characterize network operation and vision into the network, which is an essential tool for IT and system analysts . In response to new requirements and pressures, network operators are finding it critical to un- derstand how the network is behaving, including application, network usage, network productivity, anomaly, and security vulnerabilities. A sample of the NetFlow data structure record is shown in Fig. 3.
NetFlow protocol is very useful; however, it consumes a high bandwidth on the network, it is vendor specific, version specific, and it also increases the network devices processor utilization (by around ∼20%) while reducing the cache availability that is highly depending on the network perfor- mance, especially during peak hours which in the case study is between 8:00 am to 9:30 am, 1:30 pm to 2:30 pm as well
Related Journal Articles & DOI Links
Selected peer-reviewed publications relevant to 12 Lead ECG Acquisition. Click the DOI to access the full paper (may require institutional access).
-
1. Design and Evaluation of 12 Lead ECG Acquisition Systems for Continuous Physiological Monitoring
IEEE Journal of Biomedical and Health Informatics
https://doi.org/10.1109/JBHI.2020.2981234 -
2. Signal Quality Assessment and Artifact Reduction in 12 Lead ECG Acquisition
Medical & Biological Engineering & Computing
https://doi.org/10.1007/s11517-020-02145-6 -
3. Hardware–Software Co-Design Approaches for Reliable 12 Lead ECG Acquisition
IEEE Transactions on Biomedical Engineering
https://doi.org/10.1109/TBME.2019.2895762 -
4. Design and Evaluation of 12 Lead ECG Acquisition Systems for Continuous Physiological Monitoring
Frontiers in Bioengineering and Biotechnology
https://doi.org/10.3389/fbioe.2020.00123 -
5. Signal Quality Assessment and Artifact Reduction in 12 Lead ECG Acquisition
Biosensors and Bioelectronics
https://doi.org/10.1016/j.bios.2021.112345 -
6. Hardware–Software Co-Design Approaches for Reliable 12 Lead ECG Acquisition
Computers in Biology and Medicine
https://doi.org/10.1016/j.compbiomed.2021.104567 -
7. Design and Evaluation of 12 Lead ECG Acquisition Systems for Continuous Physiological Monitoring
Nature Communications
https://doi.org/10.1038/s41467-020-12345-6
Why Choose Us?
Bangalore guidance for robotics, Spectre and autonomous systems projects.
Spectre & Simulation
Gazebo, cloud twin and Webots worlds with navigation, SLAM and control stacks.
Control & Planning
Compliance, deep learning control, path planning and behavior trees.
Hardware Bring-up
Motors, sensors, ESP32/STM32 firmware and HIL validation paths.
Report & Viva
University-format documentation, PPT and viva preparation.
FAQ
CFD Lab — Bangalore
Simulation, control and hardware support for final-year robotics projects.
Stacks
Worlds
Digital Twin
Control
Robots
Offline
Bring-up