Complete Technical Paper Content — Active Directory Security Auditing Tool Using Powershell
Overview & System Context
Active Directory Security Auditing Tool Using Powershell: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8608 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Windows Server 2012, codenamed "Windows Server 8", is the ninth major version of the Windows NT operating system produced by Microsoft to be released under the Windows Server brand name. It is the server version of Windows based on Windows 8 and succeeds the Windows 7-based Windows Server 2008 R2, released nearly three years earlier. Three pre-release versions, a developer preview, a beta version and a release candidate, were released during development. The software was officially launched on September 4, 2012, which was the month before the release of Windows 8. It was succeeded by Windows Server 2012 R2. Mainstream support ended on October 9, 2018, and extended support ended on October 10, 2023. It is eligible for the paid Extended Security Updates (ESU) program, which offers continued security updates until October 13, 2026. It removed support for Itanium and processors without PAE, SSE2 and NX. Four editions were released. Various features were added or improved over Windows Server 2008 R2 (with many placing an emphasis on cloud computing), such as an updated version of Hyper-V, an IP address management role, a new version of Windows Task Manager, and ReFS, a new file system. Windows Server 2012 received generally good reviews in spite of having included the same controversial Metro-based user interface seen in Windows 8, which includes the Charms Bar for quick access to settings in the desktop environment. It is the final version of Windows Server that supports processors without CMPXCHG16B (Compare and Exchange 16 Bytes), PrefetchW, LAHF and SAHF. As of April 2017, 35% of servers were running Windows Server 2012, surpassing usage share of Windows Server 2008.
Windows Server 2012 includes a new version of Windows Task Manager together with the old version. In the new version the tabs are hidden by default, showing applications only. In the new Processes tab, the processes are displayed in varying shades of yellow, with darker shades representing heavier resource use. Information found in the older versions are now moved to the new Details tab. The Performance tab shows "CPU", "Memory", "Disk", "Wi-Fi" and "Ethernet" graphs. Unlike the Windows 8 version of Task Manager (which looks similar), the "Disk" activity graph is not enabled by default. The CPU tab no longer displays individual graphs for every logical processor on the system by default, although that remains an option.
Additionally, it can display data for each non-uniform memory access (NUMA) node. When displaying data for each logical processor for machines with more than 64 logical processors, the CPU tab now displays simple utilization percentages on heat-mapping tiles. The color used for these heat maps is blue, with darker shades again indicating heavier utilization. Hovering the cursor over any logical processor's data now shows the NUMA node of that processor and its ID, if applicable.
Additionally, a new Startup tab has been added that lists startup applications, however this tab does not exist in Windows Server 2012. The new task manager recognizes when a Windows Store app has the "Suspended" status. Resilient File System (ReFS), codenamed "Protogon", is a new file system in Windows Server 2012 initially intended for file servers that improves on NTFS in some respects. Major new features of ReFS include: Improved reliability for on-disk structures ReFS uses B+ trees for all on-disk structures including metadata and file data.
Metadata and file data are organized into tables similar to a relational database. The file size, number of files in a folder, total volume size and number of folders in a volume are limited by 64-bit numbers; as a result ReFS supports a maximum file size of 16 exabytes, a maximum of 18.4 × 10¹⁸ folders and a maximum volume size of 1 yottabyte (with 64 KB clusters) which allows large scalability with no practical limits on file and folder size (hardware restrictions still apply). Free space is counted by a hierarchical allocator which includes three separate tables for large, medium, and small chunks. File names and file paths are each limited to a 32 KB Unicode text string. Built-in resilience ReFS employs an allocation-on-write update strategy for metadata, which allocates new chunks for every update transaction and uses large IO batches. All ReFS metadata has built-in 64-bit checksums which are stored independently. The file data can have an optional checksum in a separate "integrity stream", in which case the file update strategy also implements allocation-on-write; this is controlled by a new "integrity" attribute applicable to both files and directories. If nevertheless file data or metadata becomes corrupt, the file can be deleted without taking the whole volume offline. As a result of built-in resiliency, administrators do not need to periodically run error-checking tools such as CHKDSK when using ReFS. Compatibility with existing APIs and technologies ReFS does not require new system APIs and most file system filters continue to work with ReFS volumes. ReFS supports many existing Windows and NTFS features such as BitLocker encryption, Access Control Lists, USN Journal, change notifications, symbolic links, junction points, mount points, reparse points, volume snapshots, file IDs, and oplock. ReFS seamlessly integrates with Storage Spaces, a storage virtualization layer that allows data mirroring and striping, as well as sharing storage pools between machines. ReFS resiliency features enhance the mirroring feature provided by Storage Spaces and can detect whether any mirrored copies of files become corrupt using background data scrubbing process, which periodically reads all mirror copies and verifies their checksums then replaces bad copies with good ones. Some NTFS features are not supported in ReFS, including object IDs, short names, file compression, file level encryption (EFS), user data transactions, hard links, extended attributes, and disk quotas. Sparse files are supported. Support for named streams is not implemented in Windows 8 and Windows Server 2012, though it was later added in Windows 8.1 and Windows Server 2012 R2. ReFS does not itself offer data deduplication. Dynamic disks with mirrored or striped volumes are replaced with mirrored or striped storage pools provided by Storage Spaces. In Windows Server 2012, automated error-correction with integrity streams is only supported on mirrored spaces; automatic recovery on parity spaces was added in Windows 8.1 and Windows Server 2012 R2. Booting from ReFS is not supported either.
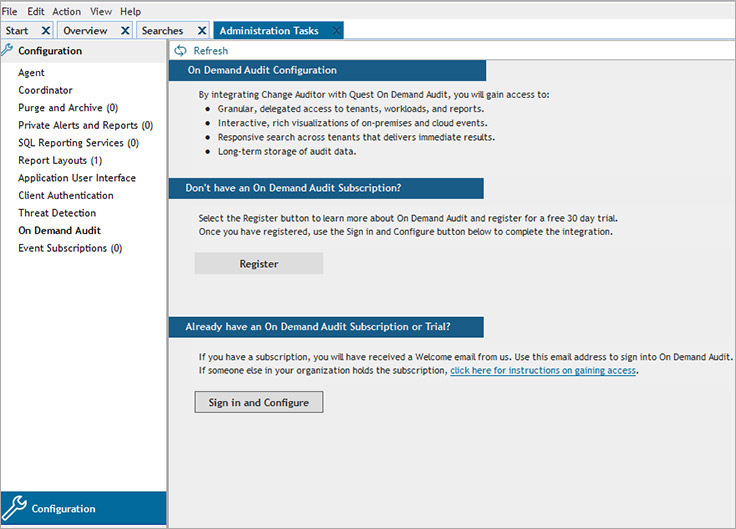
Figure 1: Active Directory Auditing Tools – CEMK Windows Server 2012 runs only on x86-64 processors. Unlike older versions, Windows Server 2012 does not support Itanium. Upgrades from Windows Server 2008 and Windows Server 2008 R2 are supported, although upgrades from prior releases are not.
A second release, Windows Server 2012 R2, which is derived from the Windows 8.1 codebase, was released to manufacturing on August 27, 2013 and became generally available on October 18, 2013, by Microsoft. An updated version, formally designated Windows Server 2012 R2 Update, was released in April 2014. Official website Windows Server 2012 R2 and Windows Server 2012 on TechNet Windows Server 2012 R2 on MSDN Windows Server 2012 on MSDN Tutorials and Lab Manual Articles of Windows Server 2012 R2 NT File System (NTFS) is a proprietary journaling file system developed by Microsoft in the 1990s. It was developed to overcome scalability, security and other limitations with FAT. NTFS adds several features that FAT and HPFS lack, including: access control lists (ACLs); filesystem encryption; transparent compression; sparse files; file system journaling and volume shadow copy, a feature that allows backups of a system while in use. Starting with Windows NT 3.1, it is the default file system of the Windows NT family superseding the File Allocation Table (FAT) file system. NTFS read/write support is available on Linux and BSD using NTFS3 in Linux and NTFS-3G in both Linux and BSD. NTFS uses several files hidden from the user to store metadata about other files stored on the drive which can help improve speed and performance when reading data.
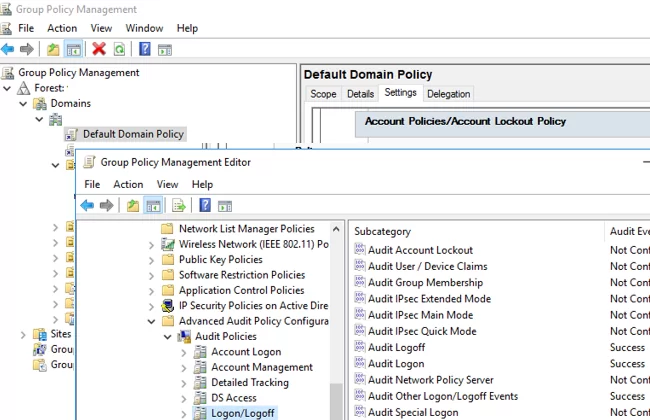
Figure 2: Checking User Logon History in Active Directory Domain with PowerShell ... The NTFS.sys version number (e.g. v5.0 in Windows 2000) is based on the operating system version; it should not be confused with the NTFS version number (v3.1 since Windows XP). Although subsequent versions of Windows added new file system-related features, they did not change NTFS itself. For example, Windows Vista implemented NTFS symbolic links, Transactional NTFS, partition shrinking, and self-healing. NTFS symbolic links are a new feature in the file system; all the others are new operating system features that make use of NTFS features already in place.
In NTFS, each file or folder is assigned a security descriptor that defines its owner and contains two access control lists (ACLs). The first ACL, called discretionary access control list (DACL), defines exactly what type of interactions (e.g. reading, writing, executing or deleting) are allowed or forbidden by which user or groups of users. For example, files in the C:\Program Files folder may be read and executed by all users but modified only by a user holding administrative privileges. Windows Vista adds mandatory access control info to DACLs. DACLs are the primary focus of User Account Control in Windows Vista and later. The second ACL, called system access control list (SACL), defines which interactions with the file or folder are to be audited and whether they should be logged when the activity is successful, failed or both. For example, auditing can be enabled on sensitive files of a company, so that its managers get to know when someone tries to delete them or make a copy of them, and whether they succeed.
Encrypting File System (EFS) provides user-transparent encryption of any file or folder on an NTFS volume. EFS works in conjunction with the EFS service, Microsoft's CryptoAPI and the EFS File System Run-Time Library (FSRTL). EFS works by encrypting a file with a bulk symmetric key (also known as the File Encryption Key, or FEK), which is used because it takes a relatively small amount of time to encrypt and decrypt large amounts of data than if an asymmetric key cipher is used. The symmetric key that is used to encrypt the file is then encrypted with a public key that is associated with the user who encrypted the file, and this encrypted data is stored in an alternate data stream of the encrypted file. To decrypt the file, the file system uses the private key of the user to decrypt the symmetric key that is stored in the data stream. It then uses the symmetric key to decrypt the file. Because this is done at the file system level, it is transparent to the user. Also, in case of a user losing access to their key, support for additional decryption keys has been built into the EFS system, so that a recovery agent can still access the files if needed. NTFS-provided encryption and NTFS-provided compression are mutually exclusive, meaning they can not be used for the same files at the same time; however, NTFS can be used for one and a third-party tool for the other. The support of EFS is not available in Basic, Home, and MediaCenter versions of Windows, and must be activated after installation of Professional, Ultimate, and Server versions of Windows or by using enterprise deployment tools within Windows domains.
The incompatibility of the $LogFile versions implemented by Windows 8, Windows 10, Windows 11 prevents Windows 7 (and earlier versions of Windows) from recognizing version 2.0 of the $LogFile. Backward compatibility is provided by downgrading the $LogFile to version 1.1 when an NTFS volume is cleanly dismounted. It is again upgraded to version 2.0 when mounting on a compatible version of Windows. However, when hibernating to disk in the logoff state (a.k.a. Hybrid Boot or Fast Boot, which is enabled by default), mounted file systems are not dismounted, and thus the $LogFiles of any active file systems are not downgraded to version 1.1. The inability to process version 2.0 of the $LogFile by versions of Windows older than 8.0 results in an unnecessary invocation of the CHKDSK disk repair utility. This is particularly a concern in a multi-boot scenario involving pre- and post-8.0 versions of Windows, or when frequently moving a storage device between older and newer versions. A Windows Registry setting exists to prevent the automatic upgrade of the $LogFile to the newer version. The problem can also be dealt with by disabling Hybrid Boot. The USN Journal (Update Sequence Number Journal) is a system management feature that records (in $Extend\$UsnJrnl) changes to files, streams and directories on the volume, as well as their various attributes and security settings. The journal is made available for applications to track changes to the volume.
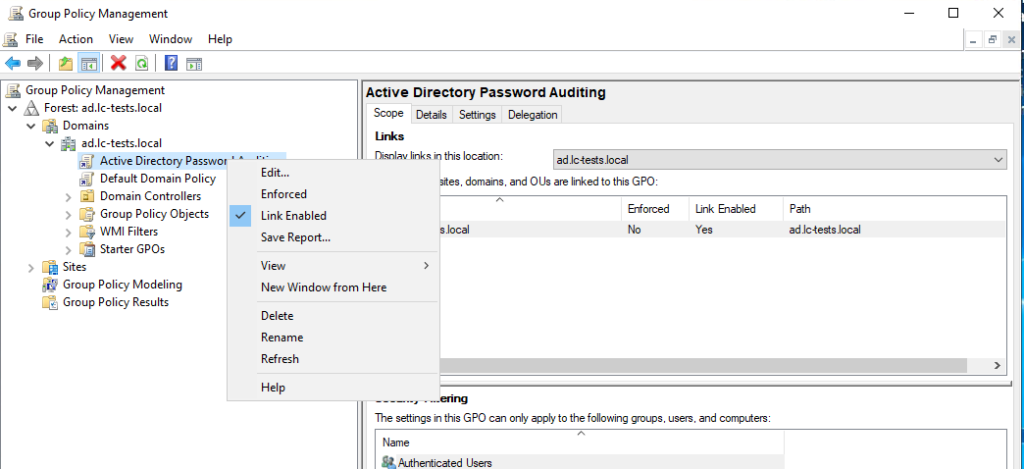
This journal can be enabled or disabled on non-system volumes. Figure 3: Automate Active Directory Auditing with PowerShell Alternate data streams allow more than one data stream to be associated with a filename (a fork), using the format "filename:streamname" (e.g., "text.txt:extrastream"). These streams are not shown to or made editable by users through any typical GUI application built into Windows by default, disguising their existence from most users. Although intended for helpful metadata, their arcane nature makes them a potential hiding place for malware, spyware, unseen browser history, and other potentially unwanted information. Alternate streams are not listed in Windows Explorer, and their size is not included in the file's size. When the file is copied or moved to another file system without ADS support the user is warned that alternate data streams cannot be preserved. No such warning is typically provided if the file is attached to an e-mail, or uploaded to a website. Thus, using alternate streams for critical data may cause problems. Microsoft provides a downloadable tool called Streams to view streams on a selected volume. Starting with Windows PowerShell 3.0, it is possible to manage ADS natively with six cmdlets: Add-Content, Clear-Content, Get-Content, Get-Item, Remove-Item, Set-Content. A small ADS named Zone.Identifier is added by Internet Explorer and by most browsers to mark files downloaded from external sites as possibly unsafe to run; the local shell would then require user confirmation before opening them. When the user indicates that they no longer want this confirmation dialog, this ADS is deleted. This functionality is also known as "Mark of the Web". All Chromium (e.g. Google Chrome) and Firefox-based web browsers also write the Zone.Identifier stream to downloaded files. Malware has used alternate data streams to hide code. Since the late 2000s, some malware scanners and other special tools check for alternate data streams. Due to the risks associated with ADS, particularly involving privacy and the Zone.Identifier stream, there exists software specifically designed to strip streams from files (certain streams with perceived risk or all of them) in a user-friendly way. NTFS Streams were introduced in Windows NT 3.1, to enable Services for Macintosh (SFM) to store resource forks. Although current versions of Windows Server no longer include SFM, third-party Apple Filing Protocol (AFP) products (such as GroupLogic's ExtremeZ-IP) still use this feature of the file system.
Since Windows 10, Microsoft has introduced new file compression scheme based on the XPRESS algorithm with 4K/8K/16K block size and the LZX algorithm; both are variants of LZ77 updated with Huffman entropy coding and range coding, which LZNT1 lacked. These compression algorithms were taken from Windows Imaging Format (WIM file). The new compression scheme is used by CompactOS feature, which reduces disk usage by compressing Windows system files. CompactOS is not an extension of NTFS file compression and does not use the 'compressed' attribute; instead, it sets a reparse point on each compressed file with a WOF (Windows Overlay Filter) tag, but the actual data is stored in an alternate data stream named "WofCompressedData", which is decompressed on-the-fly by a WOF filesystem filter driver, and the main file is an empty sparse file. This design is meant purely for read-only access, so any writes to compressed files result in an automatic decompression. CompactOS compression is intended for OEMs who prepare OS images with the /compact flag of the DISM tool in Windows ADK, but it can also be manually turned on per file with the /exe flag of the compact command. CompactOS algorithm avoids file fragmentation by writing compressed data in contiguously allocated chunks, unlike core NTFS compression. CompactOS file compression is an improved version of WIMBoot feature introduced in Windows 8.1. WIMBoot reduces Windows disk usage by keeping system files in a compressed WIM image on a separate hidden disk partition.
Similarly to CompactOS, Windows system directories only contain sparse files marked by a reparse point with a WOF tag, and Windows Overlay Filter driver decompresses file contents on-the-fly from the WIM image. WIMBoot is less effective than CompactOS though, as new updated versions of system files need to be written to the system partition, consuming disk space.
Sparse files are files interspersed with empty segments for which no actual storage space is used. To the applications, the file looks like an ordinary file with empty regions seen as regions filled with zeros; the file system maintains an internal list of such regions for each sparse file. A sparse file does not necessarily include sparse zeros areas; the "sparse file" attribute just means that the file is allowed to have them. Database applications, for instance, may use sparse files. As with compressed files, the actual sizes of sparse files are not taken into account when determining quota limits.
Introduced in NTFS v3, NTFS reparse points are used by associating a reparse tag in the user space attribute of a file or directory. Microsoft includes several default tags including symbolic links, directory junction points and volume mount points. When the Object Manager parses a file system name lookup and encounters a reparse attribute, it will reparse the name lookup, passing the user controlled reparse data to every file system filter driver that is loaded into Windows. Each filter driver examines the reparse data to see whether it is associated with that reparse point, and if that filter driver determines a match, then it intercepts the file system request and performs its special functionality.
This boot partition format is roughly based upon the earlier FAT filesystem, but the fields are in different locations. Some of these fields, especially the "sectors per track", "number of heads" and "hidden sectors" fields may contain dummy values on drives where they either do not make sense or are not determinable. The OS first looks at the 8 bytes at 0x30 to find the cluster number of the $MFT, then multiplies that number by the number of sectors per cluster (1 byte found at 0x0D). This value is the sector offset (LBA) to the $MFT, which is described below.
These metafiles are treated specially by Windows, handled directly by the NTFS.SYS driver and are difficult to directly view: special purpose-built tools are needed. As of Windows 7, the NTFS driver completely prohibits user access, resulting in a BSoD whenever an attempt to execute a metadata file is made. One such tool is the nfi.exe ("NTFS File Sector Information Utility") that is freely distributed as part of the Microsoft "OEM Support Tools". For example, to obtain information on the "$MFT"-Master File Table Segment the following command is used: nfi.exe c:\$MFT Another way to bypass the restriction is to use 7-Zip's file manager and go to the low-level NTFS path \\.\X:\ (where X:\ resembles any drive/partition). Here, 3 new folders will appear: $EXTEND, [DELETED] (a pseudo-folder that 7-Zip uses to attach files deleted from the file system to view), and [SYSTEM] (another pseudo-folder that contains all the NTFS metadata files). This trick can be used from removable devices (USB flash drives, external hard drives, SD cards, etc.) inside Windows, but doing this on the active partition requires offline access (namely WinRE).
For each file in the MFT, the attributes identified by attribute type, attribute name must be unique. Additionally, NTFS has some ordering constraints for these attributes. There is a predefined null attribute type, used to indicate the end of the list of attributes in one MFT record. It must be present as the last attribute in the record (all other storage space available after it will be ignored and just consists of padding bytes to match the record size in the MFT). Some attribute types are required and must be present in each MFT record, except unused records that are just indicated by null attribute types. This is the case for the $STANDARD_INFORMATION attribute that is stored as a fixed-size record and contains the timestamps and other basic single-bit attributes (compatible with those managed by FAT in DOS or Windows 9x). Some attribute types cannot have a name and must remain anonymous. This is the case for the standard attributes, or for the preferred NTFS "filename" attribute type, or the "short filename" attribute type, when it is also present (for compatibility with DOS-like applications, see below). It is also possible for a file to contain only a short filename, in which case it will be the preferred one, as listed in the Windows Explorer. The filename attributes stored in the attribute list do not make the file immediately accessible through the hierarchical file system. In fact, all the filenames must be indexed separately in at least one other directory on the same volume. There it must have its own MFT record and its own security descriptors and attributes that reference the MFT record number for this file. This allows the same file or directory to be "hardlinked" several times from several containers on the same volume, possibly with distinct filenames. The default data stream of a regular file is a stream of type $DATA but with an anonymous name, and the ADSs are similar but must be named. On the other hand, the default data stream of directories has a distinct type, but are not anonymous: they have an attribute name ("$I30" in NTFS 3+) that reflects its indexing format. All attributes of a given file may be displayed by using the nfi.exe ("NTFS File Sector Information Utility") that is freely distributed as part of the Microsoft "OEM Support Tools". Windows system calls may handle alternate data streams. Depending on the operating system, utility and remote file system, a file transfer might silently strip data streams. A safe way of copying or moving files is to use the BackupRead and BackupWrite system calls, which allow programs to enumerate streams, to verify whether each stream should be written to the destination volume and to knowingly skip unwanted streams.
Some attributes (such as the preferred filename, the basic file attributes) cannot be made non-resident. For non-resident attributes, their allocation map must fit within MFT records. Encrypted-by-NTFS, sparse data streams, or compressed data streams cannot be made resident. The format of the allocation map for non-resident attributes depends on its capability of supporting sparse data storage. In the current implementation of NTFS, once a non-resident data stream has been marked and converted as sparse, it cannot be changed back to non-sparse data, so it cannot become resident again, unless this data is fully truncated, discarding the sparse allocation map completely. When a non-resident attribute is so fragmented that its effective allocation map cannot fit entirely within one MFT record, NTFS stores the attribute in multiple records. The first one among them is called the base record, while the others are called extension records. NTFS creates a special attribute $ATTRIBUTE_LIST to store information mapping different parts of the long attribute to the MFT records, which means the allocation map may be split into multiple records. The $ATTRIBUTE_LIST itself can also be non-resident, but its own allocation map must fit within one MFT record. When there are too many attributes for a file (including ADS's, extended attributes, or security descriptors), so that they cannot fit all within the MFT record, extension records may also be used to store the other attributes, using the same format as the one used in the base MFT record, but without the space constraints of one MFT record. The allocation map is stored in a form of data runs with compressed encoding. Each data run represents a contiguous group of clusters that store the attribute value. For files on a multi-GB volume, each entry can be encoded as 5 to 7 bytes, which means a 1 KB MFT record can store about 100 such data runs. However, as the $ATTRIBUTE_LIST also has a size limit, it is dangerous to have more than 1 million fragments of a single file on an NTFS volume, which also implies that it is in general not a good idea to use NTFS compression on a file larger than 10 GB. The NTFS file system driver will sometimes attempt to relocate the data of some of the attributes that can be made non-resident into the clusters, and will also attempt to relocate the data stored in clusters back to the attribute inside the MFT record, based on priority and preferred ordering rules, and size constraints. Since resident files do not directly occupy clusters ("allocation units"), it is possible for an NTFS volume to contain more files on a volume than there are clusters. For example, a 74.5 GB partition NTFS formats with 19,543,064 clusters of 4 KB. Subtracting system files (a 64 MB log file, a 2,442,888-byte Bitmap file, and about 25 clusters of fixed overhead) leaves 19,526,158 clusters free for files and indices. Since there are four MFT records per cluster, this volume theoretically could hold almost 4 × 19,526,158 = 78,104,632 resident files.
Level 2 (or shared) oplock: multiple readers, no writers (i.e. read caching). Level 1 (or exclusive) oplock: exclusive access with arbitrary buffering (i.e. read and write caching). Batch oplock (also exclusive): a stream is opened on the server, but closed on the client machine (i.e. read, write and handle caching). Filter oplock (also exclusive): applications and file system filters can "back out" when others try to access the same stream (i.e. read and write caching) (since Windows 2000) Opportunistic locks have been enhanced in Windows 7 and Windows Server 2008 R2 with per-client oplock keys.
This is a list of TCP and UDP port numbers used by protocols for operation of network applications. The Transmission Control Protocol (TCP) and the User Datagram Protocol (UDP) only need one port for bidirectional traffic. TCP usually uses port numbers that match the services of the corresponding UDP implementations, if they exist, and vice versa. The Internet Assigned Numbers Authority (IANA) is responsible for maintaining the official assignments of port numbers for specific uses.
However, many unofficial uses of both well-known and registered port numbers occur in practice. Similarly, many of the official assignments refer to protocols that were never or are no longer in common use. This article lists port numbers and their associated protocols that have experienced significant uptake. The port numbers in the range from 0 to 1023 (0 to 210 − 1) are the well-known ports or system ports. They are used by system processes that provide widely used types of network services. On Unix-like operating systems, a process must execute with superuser privileges to be able to bind a network socket to an IP address using one of the well-known ports.
The range of port numbers from 1024 to 49151 (210 to 215 + 214 − 1) are the registered ports. They are assigned by IANA for specific service upon application by a requesting entity. On most systems, registered ports can be used without superuser privileges. The range 49152–65535 (215 + 214 to 216 − 1), 16 384 ports, contains dynamic or private ports that cannot be registered with IANA. This range is used for private or customized services, for temporary purposes, and for automatic allocation of ephemeral ports.
A practical field guide for designing, securing, automating, monitoring, and recovering Active Directory Domain Services in enterprise environments. It combines architecture guidance, operational runbooks, PowerShell automation, DNS and DHCP administration, hybrid identity, and validation tests. Review SECURITY.md before using any script. Test every command in an isolated lab, inspect its scope, and use -WhatIf or other dry-run controls where available before touching production.
Corrections, tested examples, and additional operational scenarios are welcome. Read CONTRIBUTING.md before opening a pull request. For security-sensitive reports, follow SECURITY.md . Enterprise Active Directory field guide: architecture, security hardening, PowerShell automation, DNS/DHCP, monitoring, hybrid identity, and disaster recovery.
A comprehensive PowerShell module for Active Directory security auditing, remediation, and monitoring based on Microsoft's official security best practices and performance tuning guidelines . 2. System Architecture & Core Working Principles Enterprise PowerShell module for comprehensive Active Directory security auditing. Features 9 security modules, Microsoft compliance coverage, CI/CD integration, SQLite database, and comprehensive reporting. Perfect for security teams and M&A due diligence.
Quarterly security reviews require the same AD data every time: who is in privileged groups, which accounts have passwords that never expire, which users have not logged in for 90 days, and which passwords are about to expire. With a PowerShell active directory audit script, this entire data gathering takes two minutes instead of two hours, and the results are consistent and reproducible. This post builds each section of the audit report and combines them into an Excel-ready CSV export.
Privileged group membership is the most critical section of any AD audit. Check both direct and nested membership: Service accounts often have PasswordNeverExpires set legitimately, but regular user accounts with this flag are a security risk that auditors frequently flag: Stale enabled accounts (no logon in 90 days) and disabled accounts that have not been removed are both security risks: Warn users and admins about passwords expiring soon. This requires the domain’s Maximum Password Age policy: Empty security groups accumulate over time after projects and teams dissolve. They are noise in permission audits and waste administrative attention: Combine all findings into a single CSV with a Section column so auditors can filter by finding type in Excel: An automated AD audit script consistently finds the same categories of risk: over-privileged accounts, passwords that never expire, stale accounts, and empty groups. Run it monthly rather than quarterly to catch issues before they reach an auditor’s report, and combine the CSV output with your ticketing system to track remediation progress.
Voice Reminders Alarm Clock plays your own recorded message as a full-screen alarm, with daily, weekday or custom schedules. Built for medication, hydration and kids' routines, and for reminding a parent who ignores every other notification. Record a short message in your own voice and Voice Reminders plays it back on a full-screen alarm, on the schedule you set. A PowerShell auditor that checks your domain for the misconfigurations behind lateral movement and privilege escalation, scores each finding by how far it deviates from baseline, and writes a single HTML report with an overall security score.
adaudit runs a wide sweep across the domain âII credential and password security, lateral-movement paths, privileged access, protocol and host hardening, DNS, trusts and platform health. Every finding is risk-scored and rolled into several HTML reports, each backed by raw evidence and data-extract files. The areas below are only a handful of examples âII the script runs far more checks than can be listed here.
Unconstrained delegation, Kerberoastable service accounts, AS-REP-roastable users, dangerous ACLs and overlapping privileged-group paths âII the weaknesses chained to move sideways and escalate across a domain. A full password-quality pass: KRBTGT rotation, duplicate or reused passwords, accounts matching breach and dictionary lists, reversible encryption, LM hashes and accounts that don't require a password.
Domain, Enterprise and Schema Admins weighed against a size-adjusted baseline, built-in RID-500 Administrator hygiene, and any service account, computer or nested group hiding inside a tier-0 group. Replication and dcdiag, SYSVOL/DFSR backlog, the NTDS database, time sync, core AD services, sites and subnets, the Recycle Bin âII and DCs that exist in AD but can't be reached on the network.
LDAP and SMB signing, NTLM, LAPS coverage, the Print Spooler on domain controllers, MachineAccountQuota, tombstone lifetime and weak RC4/DES Kerberos ciphers âII including CVE-2026-20833 exposure. Parses certificate templates and CA configuration to flag the misconfigurations behind ESC1âII4 and ESC8 âII the certificate-based abuse and escalation paths in AD Certificate Services.
DNS zones that allow insecure dynamic updates or zone transfers, domain trust direction and type, plus dormant users and computers and passwords set never to expire. Findings roll up into several HTML reports âII audit results, risk report, AD health and group overlap âII each backed by raw evidence and data-extract files you can archive or hand to auditors.
Static checklists treat every finding the same. adaudit scores each finding by how far it sits from its baseline, so larger deviations carry more weight and sort toward the top of the report. Every run writes a set of self-contained HTML reports âII an audit summary, a risk report with an overall score, and an AD health report âII each backed by raw evidence files. Here is a sample built entirely on fictional data.
adaudit ships in two flavours âII a legacy PowerShell 5 build and the current, actively developed PowerShell 7 build. Both can install their dependencies online or fully offline for locked-down domains. Run from a Domain Controller or a server with RSAT, using an account with Domain Admin rights for full coverage. Add DSInternals and NuGet online with -installdeps or from the GUI, or drop the offline .nupkg files beside the script for air-gapped domains.
Run with -all for every check, or pick a subset in the GUI. adaudit scores each finding and writes risk-scored HTML reports backed by raw evidence files. The repository also ships two focused PowerShell scripts dedicated to password quality. Both read replicated directory data with DSInternals and export their findings to CSV âII run them on their own for a deeper pass than the headline report.
adaudit is an assessment aid, not a verdict. Evaluate every finding against your organisation's policies, regulatory requirements and risk appetite âII the presence of a finding does not automatically mean there is a security issue. Always run it with appropriate authorisation. Clone the repository, install NuGet and DSInternals, and run the script to generate a risk-scored HTML report.
3. Software Implementation, Frameworks & Protocols During the Trimarc Webcast on June 17, 2020 , Sean Metcalf covered a number of Active Directory (AD) components and areas that should be reviewed for potential security issues. The presentation included PowerShell code in the presentation and that code is incorporated in the PowerShell script Trimarc released for free that can be used to perform an AD security scan. This script is called Invoke-TrimarcADChecks.ps1 and only needs AD user rights to be run.
Download the Invoke-TrimarcADChecks,ps1 by visiting the Trimarc Github Page. Last updated: 02-13-2024 The Invoke-TrimarcADChecks.ps1 PowerShell script is designed to gather data from a single domain AD forest based on our similar checks performed during Trimarc’s Active Directory Security Assessment (ADSA) engagement . It can be run against each domain in a multi-domain environment, but there is no guarantee that it captures the type of cross-domain (or cross-forest) data elements that may be involved. This script is meant to enable smaller organizations to more quickly identify potential issues. For larger, more complex AD environments, please contact Trimarc to talk about your concerns .
This script is designed for a single AD forest and is not designed to capture all data for a multiple domain forest. If this script is used for a single domain in a multi-domain AD forest, not all elements may be captured. This script is licensed under BSD 3-Clause License and is provided as-is, without support. The PowerShell script gathers domain data using the Active Directory PowerShell & Group Policy modules and displays some results on the screen. The data shown on the screen is also saved to a transcript log file and all captured data is also saved to csv/text files in c:\temp\Trimarc-ADReports (report folder is created upon script execution and this folder location can be changed).
This article covers the key AD security areas in which the Invoke-TrimarcADChecks.ps1 PowerShell script gathers data. The Invoke-TrimarcADChecks PowerShell script gathers data for key AD security items in a domain: There are several potential issues that Active Directory domain user accounts may have. Trimarc scans for these (and others) during our Active Directory Security Assessment (ADSA) engagement .
Inactive accounts – these are accounts that have not changed their password or logged on in a while (we typically focus on accounts with a combination of Password Age & User Logon Age over 90 to 180 days old) Reversible Encryption – accounts configured with reversible encryption are stored in the AD database in a reversible format (which effectively means a clear-text version of the password is available).
Password Not Required – accounts created programmatically may have this set which means that technically a password is not required for the account to authenticate. Password Never Expires – accounts with a password that is not subject to password expiration requirements. These accounts typically have very old passwords.
Do not require Kerberos Pre-Authentication – accounts that don’t require Kerberos pre-authentication. There are known attacks against accounts with this configuration. Review accounts configured with SID History and clean up SIDs in SID History for accounts from domains that no longer have trusts configured with them.
The Domain Password policy determines how passwords are created and how often they need to be changed, etc. The AD default password minimum is 7 characters. Most AD environments we see have this set to between 8 and 10. Some are set to 0 or 3 or 5. Password Spray attacks are effective against Active Directory due to bad passwords (often with short minimum requirements).Increasing password length can limit Password Spray effectiveness. Fine-Grained Password Policies (FGPP) provide additional flexibility, especially for admin and service accounts.
Trimarc Recommendation: Trimarc recommends that the Domain Password Policy be set to 12 characters (preferably 14 to 16 characters). The Active Directory module cmdlet “Get-ADPasswordPolicy” can easily capture the domain password policy. The AD Tombstone Lifetime determines how long deleted items exist in AD before they are purged. The default value was originally 60 days, but this was increased to 180 days starting with new AD forests created with Windows 2003 SP1. While the tombstone lifetime directly affects deleted items, it also has an impact on Domain Controllers. If a DC hasn’t replicated within the tombstone lifetime with another DC, it is effectively orphaned from the domain . Additionally, DC backups are only useful for restoring AD data within this tombstone lifetime – a backup that is 181 days old is no longer useful when the tombstone lifetime is 180 days.
Trimarc Recommendation: Trimarc recommends configuring the Tombstone Lifetime to 180 days (or more if needed). Microsoft supported backups update a partition attribute to identify the last backup date for that partition. Not all systems that backup Active Directory set this attribute since they are likely not using a Microsoft supported method. In most scenarios, System State Backups on a Domain Controller are required to properly backup AD. We can easily check last Microsoft supported AD backup date/time by querying an attribute on each partition. Trimarc also identified that events like “Install From Media” creation on a DC can update AD backup date/time attribute.
Ensure you run a System State Backup on at least the FSMO role holders in the AD forest at least once a month and keep for at least 6 months. An Active Directory forest is the security boundary for AD. When a trust is configured, that extends the security boundary in include the system included in the trust since the trust extends the authentication boundary.
Review trust configuration & ensure that trusts are appropriate. Trusts should be reviewed at least annually to ensure they are still required Bidirectional trusts should be scrutinized to ensure they need to be two-way trusts and still required. If a trust is required, look to shift to Selective Authentication which changes from Allow All to only those explicitly allowed to connect across the trust.
Selective Authentication changes the default behavior from allow any user across the trust to see everything to users require explicit approval to access resources otherwise they can’t view or access anything across the trust The Kerberos Service Principal Name (SPN) is effectively a signpost that connects a service on a server supporting Kerberos authentication with the service account. When there are duplicate SPNs, Kerberos authentication breaks since a Domain Controller can’t identify a single account associated with the SPN. Authentication will need to fallback to NTLM authentication.
Duplication of the Krbtgt config is normal in a multiple domains in an AD forest. Using SetSPN.exe we can discover any duplicate SPNs in the forest using the following command: 4. Practical Deployment, Analysis & Case Studies Any identified duplicate SPNs should be resolved since duplicate SPNs break Kerberos authentication which forces NTLM for authentication.
Group Policy Preferences was released in the 2008 time-frame and included capability to provide and update credentials. These credentials were encrypted using AES256 which sounds good until you realize that a static key is used to encrypt them. The cpassword value in the GPP xml files is the encrypted password. Using a PowerShell function from PowerSploit, we can reverse this encryption and get the plain-text value. Since authenticated users have read access to Group Policies in the SYSVOL share on all DCs, anyone can view this information and get the passwords stored in GPP xml files, even across trusts. This is less of an issue now that Microsoft released a patch preventing the use of Group Policy Preference passwords.
Old GPOs with these credentials remain though and Trimarc has identified a few in the past year during AD security assessments that would lead to either full AD compromise or compromising sensitive server data. The fast way to identify passwords in Group Policy Preferences is by using the findstr.exe command: During Trimarc’s standard Active Directory Security Assessment, we focus on identifying “AD Admins” which includes members of the domain Administrators group, Domain Admins, Enterprise Admins, etc. These accounts have full AD rights and require careful protection.
The fastest way to identify AD admins is to run the following command which leverages the AD PowerShell module: First, we get the recursive membership of the domain Administrators group (which includes all the members of member groups). Protected Users is a new group created when the domain PDC Emulator is running Windows Server 2012 R2. Full Domain protection is only available when the domain functional level is 2012 R2.
AD Admin accounts with old passwords, especially those older than 5 years, are vulnerable to password spraying (and password guessing). Password Spraying & Kerberoasting are popular attack methods for compromising accounts lacking strong passwords. PowerShell Sample Code & Results: Note that this check leverages the AD Admin array data collected earlier.
This is an adjusted version similar to what we find in customer environments during AD security assessments Kerberos Service Principal Name or SPN is effectively the signpost that points to the service account for a service on a server that supports Kerberos authentication. When the client needs to connect to a service, it must request a Kerberos service ticket from a DC and in order to do this it needs to provide a SPN for that service. The DC looks up the account in the AD forest that has that SPN, identifies the account, and uses the account’s password data to encrypt the ticket. Once the service ticket is delivered to the service, it attempts to open the service ticket and if it can, it can assume the DC provided it, so it validates access for the user.
Kerberoasting, developed by Tim Medin in 2014, requests service tickets (usually RC4 encrypted) for target service accounts and saves them to attempt offline brute password forcing – once the attacker can open a service ticket, they have successfully guessed the account password. This is a big deal and I have been talking about the importance of ensuring AD admin accounts don’t have SPNs and service accounts needing long passwords since Tim released his Kerberoast tool at DerbyCon 2014.
Attackers can “Kerberoast” accounts with Kerberos Service Principal Names (SPNs). This shifted attacking service accounts with old passwords from hypothetical to practical and many attackers use this method now. Trimarc published Kerberoast detection with 100% accuracy , no false positives as while back on the Trimarc website. Request Kerberos service ticket for SPN (RC4 encrypted which uses the NT password hash for the ticket encryption key).
Move the service ticket to a password cracking system and perform hybrid password guessing Limit service account membership in privileged Active Directory groups and ensure these service account passwords are longer than 25 characters (to mitigate Kerberoasting). Here we simply filter the AD Admins list by only displaying the accounts with SPNs. Note that this check leverages the AD Admin array data collected earlier.
The default domain administrator account should only be used when the other AD admin accounts are inaccessible. It should not be logged on to so set loud alerting for when it does. This account should never have a SPN since that means it is being used as a service account for a service on a server on the network. This means that compromise of that server would compromise Active Directory. Or Kerberoast the domain Administrator account and get that password to compromise AD.
The account password should change at least annually (and when an AD Admin leaves the organization). Reviewing the default privileged groups in Active Directory is important to identify accounts with high-level privileges. We can create an array of the default/builtin common groups that have privileged in AD and loop through these to get the group membership Here’s the looping code which gets the group membership and counts members. Note this membership enumeration is NOT recursive, so any groups listed in these groups need to be enumerated separately (add to the Array above to include them).
The following screenshots show output. The PowerShell script will show an error if it can’t enumerate the group which is usually because it doesn’t exist (or is inaccessible). https://docs.microsoft.com/en-us/windows/security/identity-protection/access-control/active-directory-security-groups#bkmk-a dmins https://docs.microsoft.com/en-us/windows/security/identity-protection/access-control/active-directory-security-groups#bkmk-d omainadmins This group should remain empty in a single domain forest and membership very limited in a multi-domain forest.
https://docs.microsoft.com/en-us/windows/security/identity-protection/access-control/active-directory-security-groups#bkmk-e ntadmins This group is effectively “Domain Controller Admins” and members of this group should be scrutinized at a similar level to Domain Admins. This group has no default members. Default Rights: https://docs.microsoft.com/en-us/windows/security/identity-protection/access-control/active-directory-security-groups#bkmk-s erveroperators 5. Performance Evaluation & Extended Technical Observations Reference https://docs.microsoft.com/en-us/windows/security/identity-protection/access-control/active-directory-security-grou ps#bkmk-accountoperators Trimarc sees “VMWare Admins” in most environments. The VMWare Admins AD group is granted full VMWare Admin rights.
This means that if an attacker can compromise an account that is a member of the VMWare Admins group, they can compromise VMWare. In an environment with virtual Domain Controllers hosting in VMWare, this would result in AD compromise. The krbtgt account is the domain service account. This account is disabled but used for Kerberos Tickets. The password set when created & practically never changes. DC/AD backups contains the KRBTGT account password. If an attacker gains knowledge of this password, they can create Golden Tickets! The double hop issue occurs when you have a user connecting to a web server which then connects to a back-end database server. The web server updates records on the back-end database on behalf of the user. The problem is that the TGS Service ticket the user provides to the web server is only good for the web server. The web server can’t authenticate to the database server as the user to make the updates *as* the user. Enter delegation. Kerberos Delegation enables the web server to impersonate the user to the database server in order to perform the updates the user requested.
Constrained: Impersonate authenticated users connecting to service to SPECIFIC Kerberos services on servers. Constrained with Protocol Transition: Impersonate any user to SPECIFIC Kerberos services on servers. (aka “Kerberos Magic”) Resource-based Constrained Delegation: Enables delegation configured on the resource instead of the account.
Ensure service accounts with Kerberos delegation have long, complex passwords (preferably group Managed Service Accounts). Group Policy Objects (GPO) have owners which are able to change permisisons. Typically when an account creates a GPO, the account that created it is delegate modify rights and I confiugred as the owner.
Ensure all GPO owners are set to Domain Admins or Enterprise Admins, especially GPOs linked to the domain root and Domain Controllers OU. Domain permissions should be reviewed to ensure that configuration is appropriate. Security of the domain often depends on proper domain permissions.
Review domain root permissions with special attention paid to the following:Any non-default admin groups (Domain Admins, domain Administrators, Enterprise Admins, etc) with GenericAll (Full Control), WriteDACL (change permissions), write property (modify), and ExtendedRights. Ensure that the domain root owner is configured to Domain Admins or Enterprise Admins.
The PowerShell script outputs to a CSV file which Excel can open. Use the Data, Filter feature to filter known grouprs from the IdentityReference column (Administrators, Domain Admins, Enterprise Admins, etc). This screenshot shows a sample environment with some IdentityReference filtering. The following screenshot identify some potentially concerning permissions, including the DS-Replication-Get-Changes & DS-Replication-Get-Changes ExtendedRights.
The following screenshot identifies that the Domain Computers group has GenericAll (Full Control) rights on All objects. Domain Controllers must be running Microsoft supported Windows versions. You can run all Windows Server 2012 R2 DCs even with older Windows Server versions in the domain (note that some testing to ensure Windows 2003/XP works with the new DCs, especially for SMB shares).
All DCs should be running a minimum of Windows Server 2012 R2, preferably 2016/2019. If all DCs are not running 2012 R2 with 2012R2 DFL, Protected Users group doesn’t have full domain protection. AD Forest Functional Level / Domain Functional Level Older than Domain Controller Operating System The Domain Functional Level (DFL) provides additional AD security features up to Windows Server 2016. Forest & Domain Functional Levels have less emphasis in recent versions. All AD Forests should match the DC version (after all DCs in the AD forest are running the same version). This can be configured after the DCs are updated to a recent OS and have had time to “bake in” over time.
Ensure all Domain Controllers are updated to Windwos Server 2012 R2 (or newer) and set DFL/FFL to 2012 R2 (or newer). Tools for Reviewing AD Note that Trimarc provides these as references and does not necessarily endorse any tool listed ADCollector https://hakin9.org/adcollector-a-lightweight-tool-to-quickly-extract-valuable-information-from-the-active-directory- environment-for-both-attacking-and-defending/ Trimarc provides leading expertise in security solutions including security reviews, strategy, architecture, and implementation .
Our methodology leverages our internal research and custom tooling which better discovers multiple security issues attackers could exploit to compromise the environment. Trimarc security services fit between traditional compliance/audit reviews and standard penetration testing/red teaming engagements, providing deep understanding of Microsoft and Virtualization technologies, typical security issues and misconfigurations, and provide recommendations based on our own best practices custom-tailored to balance operational and security challenges.
This PowerShell script is designed to conduct a comprehensive audit of Microsoft Active Directory, focusing on identifying common security vulnerabilities and weaknesses. Its execution facilitates the pinpointing of critical areas that require reinforcement, thereby fortifying your infrastructure against prevalent tactics used in lateral movement or privilege escalation attacks targeting Active Directory.
If you have any decent powershell one liners that could be used in the script please let me know. I'm trying to keep this script as a single file with no requirements on external tools (other than ntdsutil and cmd.exe) Run directly on a DC using a DA. If you don't trust the code I suggest reading it first and you'll see it's all harmless! (But shouldn't you be doing that anyway with code you download off the net and then run as DA??) In Active Directory, every event has an ID. Using the PowerShell Get-WinEvent cmdlet we can find auditing records.
Alternatively, you can use a comprehensive AD auditing solution like ADAudit Plus that will make things simpler for you. This article compares the method of getting AD audit reports using PowerShell and ADAudit Plus. Security logs comprise multiple events like, file or AD object modifications, account logon or logoff failures, permission changes.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Windows%20Server%202012 • https://en.wikipedia.org/wiki/NTFS • https://en.wikipedia.org/wiki/List%20of%20TCP%20and%20UDP%20port%20numbers • https://github.com/mohamedmahersaid/Microsoft-Active-Directory-Complete-Guide • https://github.com/adrian207/AD-Audit • https://www.powershelltips.com/powershell-ad-audit-report/ • https://keberneth.dev/adaudit.html • https://www.trimarcsecurity.com/hub-post/securing-active-directory-performing-an-active-directory-security-review • https://github.com/phillips321/adaudit • https://www.manageengine.com/products/active-directory-audit/powershell/audit-active-directory-using-powershell.html
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Active Directory Security Auditing Tool Using Powershell.
[*] Metasploit Scan Running on Target Subnet for Active Directory Security Auditing Tool Using Powershell... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |