Complete Technical Paper Content — Android Application Vulnerability Scanner Tool In Python
Overview & System Context
Android Application Vulnerability Scanner Tool In Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9507 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background This is a list of free and open-source software (FOSS) packages, computer software licensed under free software licenses and open-source licenses. Software that fits the Free Software Definition may be more appropriately called free software; the GNU project in particular objects to their works being referred to as open-source. For more information about the philosophical background for open-source software, see free software movement and Open Source Initiative. However, nearly all software meeting the Free Software Definition also meets the Open Source Definition and vice versa. A small fraction of the software that meets either definition is listed here. Some of the open-source applications are also the basis of commercial products, shown in the List of commercial open-source applications and services.
Cline – AI coding agent for IDEs and the command line. Codex CLI – AI coding agent and command-line interface developed by OpenAI. Command Code — CLI and desktop AI agent DeepSeek Coder – large language model designed for code generation and AI-assisted software development. Eclipse Theia – integrated development environment and framework with AI-assisted software development features. goose – AI coding agent for the desktop and command line. Kilo Code — CLI and IDE extension developed by Anaconda OpenCode — CLI, desktop app, web app, and IDE extensions OpenHands — AI software development agent Oh My Pi – terminal-based AI coding agent developed as a fork of Pi. Pi – terminal-based AI coding agent. Zed – source-code editor with integrated AI-assisted development and agentic coding features.
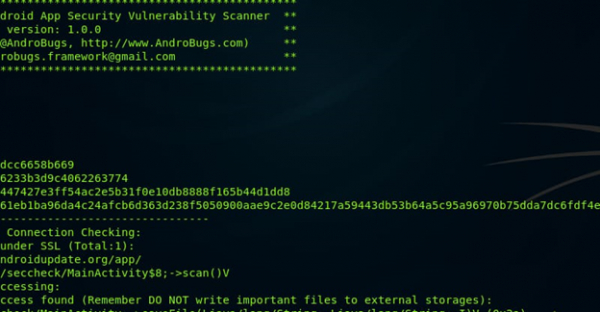
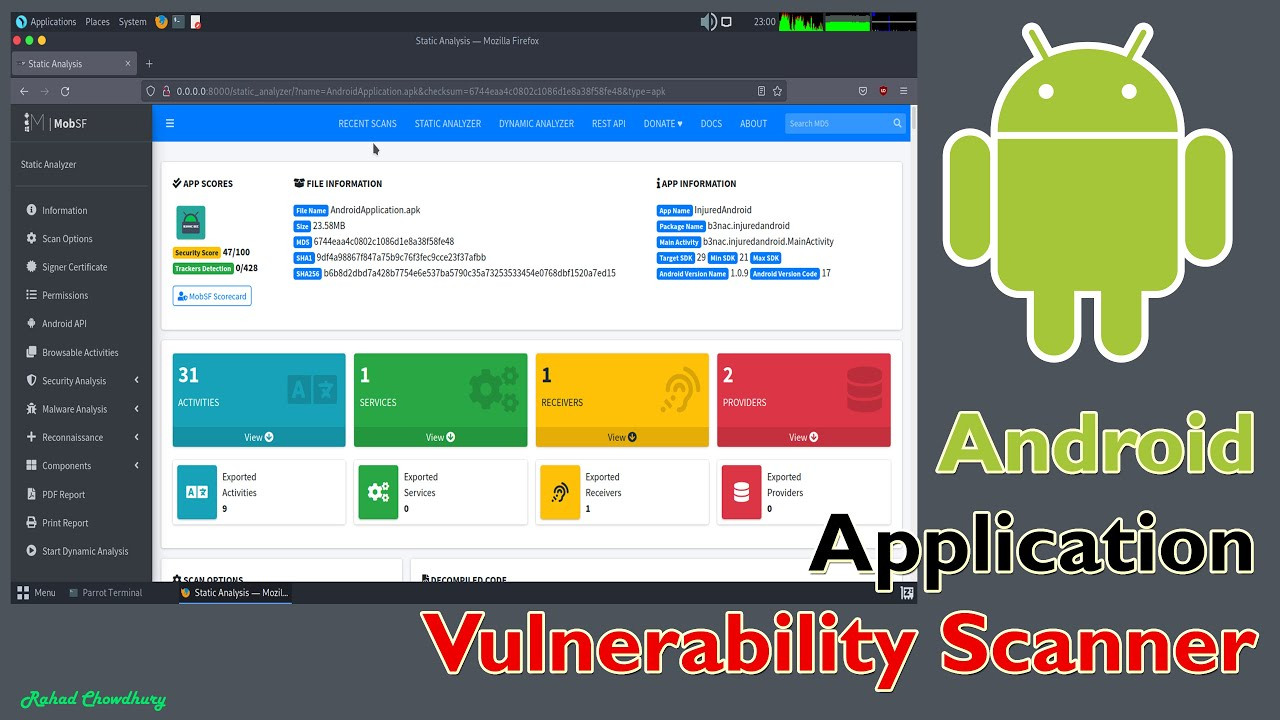
Apertus – Swiss National AI Initiative LLM BERT – Google LLM BLOOM – BigScience multilingual LLM Cerebras-GPT – Cerebras Systems LLMs DeepSeek – R1 and V3 models Gemma 4 – Google LLM GLM-4.5 and later versions – Z.ai LLMs GPT-1, GPT-2, and GPT-OSS – OpenAI LLMs GPT-J, GPT-Neo, and GPT-NeoX – EleutherAI LLMs Hy – Tencent open-weight LLM Granite – IBM LLMs Grok-1 – xAI LLM Inkling – Thinking Machines Kimi (some versions) – Moonshot AI LLMs MiMo (some versions) – Xiaomi LLMs Mistral (some versions) Muse Glimmer — Meta Superintelligence Labs LLM Nemotron 3 – Nvidia open-weight models OLMo – Allen Institute for AI LLM Phi – Microsoft LLMs Qwen (some versions) – Alibaba Cloud LLMs Sarvam-M, Sarvam-105B and Sarvam-30B – Sarvam AI LLMs SmolLM – Hugging Face small language models (SLMs) Step-3.7Flash – StepFun LLM T5 – Google LLM XLNet – Google LLM ArduPilot CoppeliaSim Gazebo Mobile Robot Programming Toolkit OpenRTM-aist Paparazzi Project Player Project Python Robotics Robot Operating System (ROS) TurtleBot UBtech Thinker Webots – robot simulator Figure 1: Android app Vulnerability Scanner Archimedes (CAD) Art of Illusion Blender BRL-CAD – constructive solid geometry (CSG) solid modeling computer-aided design (CAD) system FreeCAD – parametric 3D CAD modeler with a focus on mechanical engineering, BIM, and product design LeoCAD — beginner Lego 3D modeler LibreCAD – 2D CAD software using AutoCAD-like interface and file format MakeHuman MeshLab Open Cascade Technology (OCCT) – CAD kernel for 3D CAD, CAM, CAE OpenSCAD – scripting-based 3D CAD software QCAD SolveSpace – 2D and 3D CAD, constraint-based parametric modeler with simple mechanical simulation abilities Sweet Home 3D Wings 3D Electric FreePCB Fritzing – CAD software for the design of electronics hardware to build more permanent circuits from prototypes gEDA GNU Circuit Analysis Package (Gnucap) Icarus Verilog KiCad – suite for electronic design automation (EDA) for schematic capture, PCB layout, manufacturing file viewing, SPICE simulation, and engineering calculation KTechLab Magic Ngspice pcb-rnd Oregano Quite Universal Circuit Simulator (QUCS) Verilator XCircuit Blender – 3D computer graphics software toolset used for creating animated films, visual effects, art, 3D printed models, and motion graphics FreeCAD – equivalent of Blender geared toward mechanical engineers OpenFOAM – software used for computational fluid dynamics (or CFD) FlightGear – atmospheric and orbital flight simulator with a flight dynamics engine (JSBSim) that was used in a 2015 NASA benchmark to judge new simulation code to space industry standards SimPy – queue-theoretic event-based simulator written in Python Salome – generic platform for Pre- and Post-Processing for numerical simulation OpenPGP – open-source version of Pretty Good Privacy GNU Privacy Guard – replacement for PGP OpenSSL – library for applications that provide secure communications over computer networks NaCl (software) – crypto library Libsodium – fork of NaCl VeraCrypt – disk encryption software forked from TrueCrypt LUKS – standard for disk encryption on Linux systems Nym (mixnet) – mix network that uses noise and random packet timing for obfsucation, overlay network for NymVPN Tor (network) – free overlay network for enabling anonymous communication Tails (operating system) – security-focused Linux distro using Tor by default Signal (software) – secure messaging app Off-the-Record Messaging – protocol for secure instant messaging GPGTools – macOS suite for GnuPG-based encryption Figure 2: AndroBugs — Android Vulnerability Scanner | Open Awesome Aircrack-ng – Wi-Fi security auditing tool BackTrack – predecessor to Kali Linux Burp Suite Community Edition – security assessment and penetration testing of web applications Ghidra – software reverse engineering suite developed by the NSA Hashcat – password recovery utility High Orbit Ion Cannon – DDoS hping3 — packet crafting and network penetration-testing utility Hydra (software) – login cracker supporting numerous protocols John the Ripper – password cracking tool Kali Linux – penetration testing Linux distribution Metasploit Project – framework for developing and executing exploit code Netcat – network utility for reading/writing data across networks Nikto (vulnerability scanner) – web server vulnerability scanner Nmap – network scanning, port scanner, and auditing tool OpenSSH – implementation of the SSH protocol Radare2 – reverse engineering framework Snort (software) – network intrusion detection system sqlmap – automated SQL injection and database takeover tool Suricata (software) – network threat detection engine Volatility (memory forensics) – memory forensics framework for incident response Wireshark – network protocol analyzer YARA – tool to identify and classify malware qBittorrent – BitTorrent client Transmission (BitTorrent client) – lightweight BitTorrent client IPFS – InterPlanetary File System for decentralized storage and sharing RetroShare – secure communication platform with file sharing Zerocoin – privacy-focused cryptocurrency protocol Zcash – cryptocurrency based on Zerocoin using zk-SNARKs Monero – privacy-focused cryptocurrency using ring signatures NYM — Nym mixnet privacy- and security-focused token Tornado Cash — Cryptocurrency tumbler ClamAV – cross-platform antimalware toolkit written in C and C++, able to detect many types of malware including viruses ClamWin – antivirus tool for Windows and written in C, C++ Lynis – security audit tool (set of shell scripts) for Unix and Linux Figure 3: Android Application Vulnerability Scanner using MobSF - YouTube Bouncy Castle GnuPG GnuTLS KGPG NaCl OpenSSL Seahorse Signal stunnel TextSecure wolfCrypt 7-Zip Snort – network intrusion detection system (IDS) and intrusion prevention system (IPS) Suricata – network threat detection engine OpenVAS – software framework of several services and tools offering vulnerability scanning and vulnerability management Nmap – network scanner, port scanner, and security auditing tool Nikto – web server vulnerability scanner Volatility – memory forensics framework for incident response Cyberduck – macOS and Windows client (since version 4.0) Lsh – server and client, with support for SRP and Kerberos authentication OpenSSH – client and server PuTTY – client-only Apache Cassandra – NoSQL database from Apache Software Foundation offers support for clusters spanning multiple datacenter Apache CouchDB – NoSQL database from Apache Software Foundation with multi-master replication MariaDB – community-developed relational database management system with pluggable storage engines and commercial support PostGIS – adds support for geographic objects to the PostgreSQL as per Open Geospatial Consortium (OGC) PostgreSQL – relational database management system emphasizes on extensibility and SQL compliance and available for Windows, Linux, FreeBSD, and OpenBSD ATutor – web-based Learning Content Management System (LCMS) Canvas LMS – web-based, open, extensible learning management system Chamilo – web-based e-learning and content management system Claroline – collaborative Learning Management System DoceboLMS – SAAS/cloud platform for learning eFront – icon-based learning management system H5P – framework for creating and sharing interactive HTML5 content IUP Portfolio – educational platform for Swedish schools ILIAS – web-based learning management system (LMS) Moodle – learning management system OLAT – web-based Learning Content Management System Omeka – content management system for online digital collections Sakai Project – web-based learning management system SWAD – web-based learning management system Kiwix – offline web browser that allows users to download Wikipedia's entire content and use it for offline learning. Later it was expanded with repositories for Wikimedia Foundation, public domain texts from Project Gutenberg, many of the Stack Exchange sites, and other resources OpenStreetMap – OpenStreetMap was developed in 2004. It uses Open data and users data input through Crowdsourcing and Web mapping to create a complete and downloadable alternative to other online maps.
This allow users to enter data when there is no data available due to lack of governance and economic interest or due to lower population of the places mapped Advanced Simulation Library ASCEND Calcpad Calculix CHEMKIN – chemical kinetics COCO simulator – chemical process simulator CP2K – quantum chemistry and solid-state physics DWSIM – chemical process simulator General Mission Analysis Tool (GMAT) – space mission analysis GNU Octave – numerical-analysis GROMACS – simulations of proteins, lipids, and nucleic acids JSBSim – flight dynamics engine LAMMPS – Molecular dynamics Open Babel – chemical informatics OpenModelica – chemical process simulator OpenSees – earthquake engineering OpenVSP – parametric aircraft geometry tool Pyomo – mathematical optimization QBlade – wind turbine design and aerodynamic simulation software REFPROP – reference Fluid Thermodynamic and Transport Properties XFOIL – analysis of subsonic isolated airfoils .apng – Animated Portable Network Graphics .avif – AV1 Image File Format .bpg – Better Portable Graphics .exr – OpenEXR .fits – Flexible Image Transport System primarily for Astronomy .flif – Free Lossless Image Format .gif – Graphics Interchange Format .iff / .lbm – InterLeaved BitMap .jng – JPEG Network Graphics .jpg or .jpeg – Joint Photographic Experts Group .jxl – JPEG XL .mng – Multiple-image Network Graphics .miff / .mi – Magick Image File Format .pam, .pbm, .pgm, .ppm, .pnm – Netpbm file formats .pgf – Progressive Graphics File .png – Portable Network Graphics .qoi – Quite OK Image Format .tiff – Tag Image File Format .wbmp – Wireless Application Protocol Bitmap Format .webp .xbm – X BitMap .xcf – GIMP .xpm – X PixMap .adoc – AsciiDoc .epub – ebook format .latex – LaTeX, macro package built on top of TeX for simplification .md – Markdown .odt – OpenDocument .rtf – Rich Text Format .tex – high-quality typography for mathematical notation, physics, chemistry, engineering/scientific notation .texinfo 1DayLater – invoicing software GnuCash – double-entry book-keeping HomeBank – personal accounting software KMyMoney – double-entry book-keeping LedgerSMB – double-entry book-keeping RCA open-source application – management accounting application SQL-Ledger – double-entry book-keeping TurboCASH – double-entry book-keeping for Windows Bitcoin – blockchain platform, peer-to-peer decentralised digital currency Ethereum – blockchain platform with smart contract functionality CiviCRM – Constituent Relationship Management software aimed at charities and NGOs iDempiere – business Suite, ERP and CRM SuiteCRM – web-based CRM Adempiere – Enterprise resource planning (ERP) business suite Apache OFBiz – suite of enterprise applications from Apache Software Foundation Compiere – ERP solution automates accounting, supply chain, inventory, and sales orders Dolibarr – web-based ERP system ERPNext – web-based ERP system for managing accounting and finance ERP5 – Single Unified Business Model based system written with Python and Zope iDempiere – fully navigable on PCs, tablets and smartphones driven only by a community of supporters JFire – ERP business suite written with Java and JDO LedgerSMB – double entry accounting and ERP system written with Perl metasfresh – ERP Software Odoo – ERP, CRM and CMS Openbravo – web-based ERP Tryton – ERP MAME – multi-platform emulator for arcade game systems Mednafen – multi-platform emulator MESS – multi-platform emulator RetroArch – cross-platform front-end for emulators, game engines and video games Snes9x – Super Nintendo emulator Stella – Atari 2600 emulator PCSX – PlayStation emulator PCSX2 – PlayStation 2 emulator PPSSPP – PlayStation Portable emulator Project64 – Nintendo 64 emulator RPCS3 – PlayStation 3 emulator Dolphin (emulator) – GameCube and Wii emulator Citra (emulator) – Nintendo 3DS and Wii emulator Cemu – Wii U emulator TIC-80 – virtual machine game engine that mimics the 8-bit systems of the 1980s QGIS – cross-platform desktop geographic information system (GIS) application to view, edit, and analyse geospatial data ADMB Euler Math Toolbox FreeMat GNU Data Language GNU MCSim GNU Octave J Julia Owl Scientific Computing Perl Data Language S-Lang Scilab Yorick Blender Game Engine – discontinued 2019 Godot – application for the design of cross-platform video games MonoGame – C# framework Open3DEngine – based on Amazon Lumberyard Stride – (prev. Xenko) 2D and 3D cross-platform game engine originally developed by Silicon Studio Amavis – email content filter Claws Mail – email Client Fetchmail – email Retrieval Geary – email client based on WebKitGTK+ GNUMail – cross-platform email client Hula – discontinued mail and calendar project K-9 Mail – Android Email Client MailScanner – email security system MH Message Handling System – email Client Modest – email Client Mozilla Mail & Newsgroups – email Client that was part of the now discontinued Mozilla Application Suite Mozilla Thunderbird – email, news, RSS, and chat client POPFile – cross-platform mail filter Proton Mail – app and web-based end-to-end encrypted e-mail evolved to become FOSS Roundcube – web-based IMAP email client Sylpheed – email and News Client Sympa – MLA software 2. System Architecture & Core Working Principles I2P – anonymous network layer (implemented as a mix network) that allows for censorship-resistant, peer-to-peer communication OnionShare – file sharing app using Tor network Popcorn Time – multi-platform media player qBittorrent – BitTorrent client Transmission – BitTorrent client Deluge – BitTorrent client BSD – FreeBSD, OpenBSD, NetBSD, GhostBSD, TrueNAS, MidnightBSD, DragonFly BSD, OPNsense, pfSense, XigmaNAS, among others. GrapheneOS – Privacy- and security-focused, Android-based mobile operating system Kali NetHunter Linux – Debian, Ubuntu, Manjaro, Fedora, openSUSE, antiX, NixOS, Kali, Alpine, Tails, Mageia, Slackware, Gentoo, BlackArch, among others (List of Linux distributions). LineageOS – Android-based operative system for tablets and mobile phones GNU Hurd Mobian Nura Plasma Mobile PureOS Ubuntu Touch Redox OS FreeDOS – OS compatible with IBM PC DOS and Microsoft's MS-DOS ReactOS – OS intended to run the same software as Windows, originally designed to simulate Windows NT 4.0, later aiming at Windows 7 compatibility. It has been in the development stage since 1996.
AppleWin DOSBox – DOS programs emulator (including PC games) GNOME Boxes Hercules (emulator) Kernel-based Virtual Machine (KVM) QEMU VirtualBox – hosted hypervisor for x86 virtualization DTrace – dynamic tracing framework for analyzing and troubleshooting running applications and operating systems Memtest86 – stress-tests RAM on x86 machines strace – diagnostic utility for tracing system calls and signals Valgrind – debugging and profiling tool for detecting memory and threading errors Xnee – record and replay tests Acceleo – model-to-text code generator Apache Velocity – Java-based template engine used for code generation Babel – JavaScript transcompiler Bison CodeSynthesis XSD – XML Data Binding compiler for C++ CodeSynthesis XSD/e – validating XML parser/serializer and C++ XML Data Binding generator for mobile and embedded systems Flex lexical analyser – generates lexical analyzers Open Scene Graph – 3D graphics application programming interface OpenSCDP – Open Smart Card Development Platform SableCC – parser generator for Java and .NET SWIG – Simplified Wrapper and Interface Generator for several languages Umple – modeling and programming language with source code generation xmlbeansxx – XML Data Binding code generator for C++ YAKINDU Statechart Tools – Statechart code generator for C++ and Java Apache Flink – stream and batch data processing framework Apache Hadoop – distributed storage and processing framework Apache Mahout – scalable machine learning library Apache Spark – unified analytics engine Dask – parallel computing for analytics in Python ELKI – data analysis algorithms library GNU Octave – numerical computing environment JASP – GUI program for data analytics, data science, and machine learning Jupyter Notebook – interactive computing Keras – neural network library KNIME – data analytics platform Matplotlib – data visualization library MLlib – machine learning library for Apache Spark NumPy – numerical computing library Orange – data mining tool pandas – data manipulation library PyTorch – machine learning and deep learning framework Python R – statistical computing language SageMath – mathematics and data analysis environment SciPy – scientific computing library scikit-learn – Python machine learning library TensorFlow – machine learning framework WEKA – machine learning and data analysis suite 3G Bridge – grid interoperability Advanced Resource Connector – middleware BOINC – volunteer computing HTCondor – high-throughput computing Simple Grid Protocol – grid computing UNICORE – middleware CP2K – atomistic and molecular simulation of solid-state, liquid, molecular, and biological systems Open-source software Open-source license Comparison of file synchronization software § Open-source GNOME Core Applications List of concept- and mind-mapping software § Free and open-source List of formerly proprietary software List of GNU packages List of HDL simulators § Free and open-source simulators List of KDE applications List of open-source hardware projects List of optimization software § Free and open-source software List of public domain projects List of spreadsheet software § Free and open-source software List of Unix commands Google Cloud is a suite of cloud computing services offered by Google that provides a series of modular cloud services including computing, data storage, data analytics, and machine learning, alongside a set of management tools. It runs on the same infrastructure that Google uses internally for its end-user products, such as Google Search, Gmail, and Google Docs, according to Verma et al. Registration requires a credit card or bank account details. Google Cloud provides infrastructure as a service, platform as a service, and serverless computing environments. In April 2008, Google announced App Engine, a platform for developing and hosting web applications in Google-managed data centers, which was the first cloud computing service from the company. The service became generally available in November 2011. Since the announcement of App Engine, Google added multiple cloud services to the platform. Google Cloud includes Google Cloud public cloud infrastructure, as well as Google Workspace (G Suite), enterprise versions of Android and ChromeOS, and application programming interfaces (APIs) for machine learning and enterprise mapping services. Since at least 2022, Google's official materials have stated that "Google Cloud" is the new name for "Google Cloud Platform," which may cause naming confusion.
For those familiar with other notable cloud service providers, a comparison of similar services may be helpful in understanding Google Cloud Platform's offerings. April 2008 – Google App Engine announced in preview May 2010 – Google Cloud Storage launched May 2010 – Google BigQuery and Prediction API announced in preview October 2011 – Google Cloud SQL is announced in preview June 2012 – Google Compute Engine is launched in preview May 2013 – Google Compute Engine is released to GA August 2013 – Cloud Storage begins automatically encrypting each Storage object's data and metadata under the 128-bit Advanced Encryption Standard (AES-128), and each encryption key is itself encrypted with a regularly rotated set of master keys February 2014 – Google Cloud SQL becomes GA May 2014 – Stackdriver is acquired by Google June 2014 – Kubernetes is announced as an open source container manager June 2014 – Cloud Dataflow is announced in preview October 2014 – Google acquires Firebase November 2014 – Alpha release Google Kubernetes Engine (formerly Container Engine) is announced January 2015 – Google Cloud Monitoring based on Stackdriver goes into Beta March 2015 – Google Cloud Pub/Sub becomes available in Beta April 2015 – Google Cloud DNS becomes generally available April 2015 – Google Dataflow launched in beta July 2015 – Google releases v1 of Kubernetes; Hands it over to The Cloud Native Computing Foundation August 2015 – Google Cloud Dataflow, Google Cloud Pub/Sub, Google Kubernetes Engine, and Deployment Manager graduate to GA November 2015 – Bebop is acquired, and Diane Greene joins Google February 2016 – Google Cloud Functions becomes available in Alpha September 2016 – Apigee, a provider of application programming interface (API) management company, is acquired by Google September 2016 – Stackdriver becomes generally available November 2016 – Qwiklabs, an EdTech company is acquired by Google February 2017 – Cloud Spanner, highly available, globally-distributed database is released into Beta March 2017 – Google acquires Kaggle, world's largest community of data scientists and machine learning enthusiasts April 2017 – MIT professor Andrew Sutherland breaks the record for the largest ever Compute Engine cluster with 220,000 cores on Preemptible VMs. May 2017 – Google Cloud IoT Core is launched in Beta November 2017 – Google Kubernetes Engine gets certified by the CNCF February 2018 – Google Cloud IoT Core becomes generally available February 2018 – Google announces its intent to acquire Xively February 2018 – Cloud TPUs, ML accelerators for Tensorflow, become available in Beta May 2018 – Google Cloud Memorystore becomes available in Beta April 2019 – Google Cloud Run (fully managed) Beta release April 2019 – Google Anthos announced November 2019 – Google Cloud Run (fully managed) General availability release March 2020 – Due to the COVID-19 pandemic, Google Cloud postponed the online streaming version of its Google Cloud Next mega-conference, two weeks after it canceled the in-person version. October 2020 – Google Cloud announced that it will become a block producer candidate for the EOS network and EOS.IO protocol. Currently the top block producers are cryptocurrency exchanges like OKEx and Binance. February 2021 – Google Kubernetes Engine Autopilot is introduced. May 2021 – Vertex AI announced at Google.io June 2021 – In 2021, Apple was Google Cloud's biggest customer. April 2022 – MobiledgeX acquired and joins Google Cloud. March 2023 – Google brings generative AI capabilities to Google Cloud. May 2024 Google Cloud partnered with Airtel. April 2025 – At Google Cloud Next 2025 in Las Vegas, Google announced the seventh-generation Tensor Processing Unit, named Ironwood, claiming 3,600 times better performance than its first publicly available TPU. Google also announced Cloud Wide Area Network (Cloud WAN), making its private global network available to enterprise customers, and introduced Gemini 2.5 and Gemini 2.5 Flash reasoning models.
April 2026 – At Google Cloud Next '26, Sundar Pichai announced expanded AI infrastructure investments, including the introduction of Trillium TPUs (8th generation) and the Gemini Enterprise Agent Platform, with Google reporting that 75% of new internal code was AI-generated. Heartbleed is a security bug in some outdated versions of the OpenSSL cryptography library, which is a widely used implementation of the Transport Layer Security (TLS) protocol. It was introduced into the software in 2012 and publicly disclosed in April 2014. Heartbleed could be exploited regardless of whether the vulnerable OpenSSL instance is running as a TLS server or client. It resulted from improper input validation (due to a missing bounds check) in the implementation of the TLS heartbeat extension. Thus, the bug's name derived from heartbeat. The vulnerability was classified as a buffer over-read, a situation where more data can be read than should be allowed. Heartbleed was registered in the Common Vulnerabilities and Exposures database as CVE-2014-0160. A fixed version of OpenSSL was released on 7 April 2014, on the same day Heartbleed was publicly disclosed. TLS implementations other than OpenSSL, such as GnuTLS, Mozilla's Network Security Services, and the Windows platform implementation of TLS, were not affected because the defect existed in the OpenSSL's implementation of TLS rather than in the protocol itself. System administrators were frequently slow to patch their systems. As of 20 May 2014, 1.5% of the 800,000 most popular TLS-enabled websites were still vulnerable to the bug, and by 21 June 2014, 309,197 public web servers remained vulnerable. According to a 23 January 2017 report from Shodan, nearly 180,000 internet-connected devices were still vulnerable to the bug, but by 6 July 2017, the number had dropped to 144,000 according to a search performed on shodan.io for the vulnerability. Around two years later, 11 July 2019, Shodan reported that 91,063 devices were vulnerable. The U.S. had the most vulnerable devices, with 21,258 (23%), and the 10 countries with the most vulnerable devices had a total of 56,537 vulnerable devices (62%). The remaining countries totaled 34,526 devices (38%).
The report also broke the devices down by 10 other categories such as organization (the top 3 were wireless companies), product (Apache httpd, Nginx), and service (HTTPS, 81%). At the time of disclosure, some 17% (around half a million) of the Internet's secure web servers certified by trusted authorities were believed to be vulnerable to the attack, allowing theft of the servers' private keys and users' session cookies and passwords. The Electronic Frontier Foundation, Ars Technica, and Bruce Schneier all deemed the Heartbleed bug "catastrophic". Forbes cybersecurity columnist Joseph Steinberg wrote:Some might argue that Heartbleed is the worst vulnerability found (at least in terms of its potential impact) since commercial traffic began to flow on the Internet. An unidentified UK Cabinet Office spokesman recommended that: People should take advice on changing passwords from the websites they use. Most websites have corrected the bug and are best placed to advise what action, if any, people need to take. On the day of disclosure, The Tor Project advised: If you need strong anonymity or privacy on the Internet, you might want to stay away from the Internet entirely for the next few days while things settle. The Sydney Morning Herald published a timeline of the discovery on 15 April 2014, showing that some organizations had been able to patch the bug before its public disclosure. In some cases, it is not clear how they found out.
By reusing the same private key, a site that was affected by the Heartbleed bug still faces exactly the same risks as those that have not yet replaced their SSL certificates. eWeek said, "[Heartbleed is] likely to remain a risk for months, if not years, to come." Cloudflare revoked all TLS certificates and estimated that publishing its certificate revocation list would cost the issuer, GlobalSign, $400,000 per month that year.
The RFC 6520 Heartbeat Extension tests TLS/DTLS secure communication links by allowing a computer at one end of a connection to send a Heartbeat Request message, consisting of a payload, typically a text string, along with the payload's length as a 16-bit integer. The receiving computer then must send exactly the same payload back to the sender. The affected versions of OpenSSL allocate a memory buffer for the message to be returned based on the length field in the requesting message, without regard to the actual size of that message's payload. Because of this failure to do proper bounds checking, the message returned consists of the payload, possibly followed by whatever else happened to be in the allocated memory buffer. Heartbleed is therefore exploited by sending a malformed heartbeat request with a small payload and large length field to the vulnerable party (usually a server) in order to elicit the victim's response, permitting attackers to read up to 64 kibibytes of the victim's memory that was likely to have been used previously by OpenSSL. Where a Heartbeat Request might ask a party to "send back the four-letter word 'bird'", resulting in a response of "bird", a malicious "Heartbleed request" of "send back the 500-letter word 'bird'" would cause the victim to return "bird" followed by whatever 496 subsequent characters the victim happened to have in active memory. Attackers in this way could receive sensitive data, compromising the confidentiality of the victim's communications. Although an attacker has some control over the disclosed memory block's size, it has no control over its location, and therefore cannot choose what content is revealed.
The Canadian federal government temporarily shut online services of the Canada Revenue Agency (CRA) and several government departments over Heartbleed bug security concerns. Before the CRA online services were shut down, a hacker obtained approximately 900 social insurance numbers. Another Canadian Government agency, Statistics Canada, had its servers compromised due to the bug and also temporarily took its services offline. Platform maintainers like the Wikimedia Foundation advised their users to change passwords. The servers of LastPass were vulnerable, but due to additional encryption and forward secrecy, potential attacks were not able to exploit this bug. However, LastPass recommended that its users change passwords for vulnerable websites. The Tor Project recommended that Tor relay operators and hidden service operators revoke and generate fresh keys after patching OpenSSL, but noted that Tor relays use two sets of keys and that Tor's multi-hop design minimizes the impact of exploiting a single relay. 586 relays later found to be susceptible to the Heartbleed bug were taken off-line as a precautionary measure. Game-related services including Steam, Minecraft, Wargaming, League of Legends, GOG.com, Origin, Sony Online Entertainment, Humble Bundle, and Path of Exile were affected and subsequently fixed.
Several Hewlett-Packard server applications, such as HP System Management Homepage (SMH) for Linux and Windows. Some versions of FileMaker 13 LibreOffice 4.2.0 to 4.2.2 (fixed in 4.2.3) LogMeIn claimed to have "updated many products and parts of our services that rely on OpenSSL". Multiple McAfee products, in particular some versions of software providing anti-viral coverage for Microsoft Exchange, software firewalls, and McAfee Email and Web Gateways Oracle MySQL Connector/C 6.1.0-6.1.3 and Connector/ODBC 5.1.13, 5.2.5-5.2.6, 5.3.2 Oracle Big Data Appliance (includes Oracle Linux 6) Primavera P6 Professional Project Management (includes Primavera P6 Enterprise Project Portfolio Management) WinSCP (FTP client for Windows) 5.5.2 and some earlier versions (only vulnerable with FTP over TLS/SSL, fixed in 5.5.3) Multiple VMware products, including VMware ESXi 5.5, VMware Player 6.0, VMware Workstation 10 and the series of Horizon products, emulators and cloud computing suites Several other Oracle Corporation applications were affected.
Android 4.1.1, used in various portable devices. Chris Smith writes in Boy Genius Report that just this one version of Android is affected but that it is a popular version of Android (Chitika claim 4.1.1 is on 50 million devices; Google describe it as less than 10% of activated Android devices). Other Android versions are not vulnerable as they either have heartbeats disabled or use an unaffected version of OpenSSL. Firmware for some AirPort base stations Firmware for some Cisco Systems routers Firmware for some Juniper Networks routers pfSense 2.1.0 and 2.1.1 (fixed in 2.1.2) DD-WRT versions between and including 19163 and 23881 (fixed in 23882) Western Digital My Cloud product family firmware Tripwire SecureScan AppCheck – static binary scan and fuzzing, from Synopsys Software Integrity Group (formerly Codenomicon) Arbor Network's Pravail Security Analytics Norton Safeweb Heartbleed Check Tool Heartbleed testing tool by a European IT security company Heartbleed test by Italian cryptographer Filippo Valsorda Heartbleed Vulnerability Test by Cyberoam Critical Watch Free Online Heartbleed Tester Metasploit Heartbleed scanner module Heartbleed Server Scanner by Rehmann Lookout Mobile Security Heartbleed Detector, an app for Android devices that determines the OpenSSL version of the device and indicates whether the vulnerable heartbeat is enabled Heartbleed checker hosted by LastPass Online network range scanner for Heartbleed vulnerability by Pentest-Tools.com Official Red Hat offline scanner written in the Python language Qualys SSL Labs' SSL Server Test which not only looks for the Heartbleed bug, but can also find other SSL/TLS implementation errors. Browser extensions, such as Chromebleed and FoxBleed SSL Diagnos CrowdStrike Heartbleed Scanner – Scans routers, printers and other devices connected inside a network including intranet web sites. Netcraft Site Report – indicates whether a website's confidentiality could be jeopardized due to a past exploitation of Heartbleed by checking data from Netcraft's SSL Survey to determine whether a site offered the heartbeat TLS Extension prior to the Heartbleed disclosure. The Netcraft Extensions for Chrome, Firefox and Opera also perform this check, whilst looking for potentially compromised certificates. Other security tools have added support for finding this bug. For example, Tenable Network Security wrote a plugin for its Nessus vulnerability scanner that can scan for this fault. The Nmap security scanner includes a Heartbleed detection script from version 6.45. Sourcefire has released Snort rules to detect Heartbleed attack traffic and possible Heartbleed response traffic. Open source packet analysis software such as Wireshark and tcpdump can identify Heartbleed packets using specific BPF packet filters that can be used on stored packet captures or live traffic.
OpenSSL core developer Ben Laurie claimed that a security audit of OpenSSL would have caught Heartbleed. Software engineer John Walsh commented: Think about it, OpenSSL only has two [fulltime] people to write, maintain, test, and review 500,000 lines of business critical code. The OpenSSL foundation's president, Steve Marquess, said "The mystery is not that a few overworked volunteers missed this bug; the mystery is why it hasn't happened more often." David A. Wheeler described audits as an excellent way to find vulnerabilities in typical cases, but noted that "OpenSSL uses unnecessarily complex structures, which makes it harder to both humans and machines to review." He wrote: There should be a continuous effort to simplify the code, because otherwise just adding capabilities will slowly increase the software complexity. The code should be refactored over time to make it simple and clear, not just constantly add new features. The goal should be code that is "obviously right", as opposed to code that is so complicated that "I can't see any problems". According to security researcher Dan Kaminsky, Heartbleed is sign of an economic problem which needs to be fixed. Seeing the time taken to catch this simple error in a simple feature from a "critical" dependency, Kaminsky fears numerous future vulnerabilities if nothing is done. When Heartbleed was discovered, OpenSSL was maintained by a handful of volunteers, only one of whom worked full time. Yearly donations to the OpenSSL project were about US$2,000. The Heartbleed website from Codenomicon advised money donations to the OpenSSL project. After learning about donations for the 2 or 3 days following Heartbleed's disclosure totaling US$841, Kaminsky commented "We are building the most important technologies for the global economy on shockingly underfunded infrastructure." Core developer Ben Laurie has qualified the project as "completely unfunded". Although the OpenSSL Software Foundation has no bug bounty program, the Internet Bug Bounty initiative awarded US$15,000 to Google's Neel Mehta, who discovered Heartbleed, for his responsible disclosure. Mehta later donated his reward to a Freedom of the Press Foundation fundraiser. Paul Chiusano suggested Heartbleed may have resulted from failed software economics. The industry's collective response to the crisis was the Core Infrastructure Initiative, a multimillion-dollar project announced by the Linux Foundation on 24 April 2014 to provide funds to critical elements of the global information infrastructure. The initiative intends to allow lead developers to work full time on their projects and to pay for security audits, hardware and software infrastructure, travel, and other expenses. OpenSSL is a candidate to become the first recipient of the initiative's funding. After the discovery Google established Project Zero which is tasked with finding zero-day vulnerabilities to help secure the Web and society.
Summary and Q&A about the bug by Codenomicon Ltd Information for Canadian organizations and individuals List of all security notices Archived 19 July 2018 at the Wayback Machine trueseeing is a fast, accurate and resillient vulnerability scanner for iOS/Android apps. We operate on the Dalvik VM level for Android -- i.e. we don't care if the target app is obfuscated or not.
We provide containers so you can use right away as follows; now this is also the recommended way, and the only way if you are on Windows, to run: If you want to run statelessly you omit mounting volume onto /cache (not recommended for day-to-day use though; also see #254 ): Alternatively, you can install our package with uv as follows. Especially the uv tool install form of installation might be useful for extensions (see below), as it grants them the greatest freedom. Just remember you need a JRE and Android SDK (optionally; to mess with devices): You can interactively scan/analyze/patch/etc. apps -- making it the ideal choice for manual analysis: We accept an inline command ( -c ) or script file ( -i ) to run before giving you prompt, as well as quitting right away instead of prompting ( -q ; we don't require a tty in this mode!).
You can use the features to conduct a batch scan, as follows e.g. to dump findings right onto the stderr: Traditionally, you can scan apps with the following command line to get findings listed in stderr: 3. Software Implementation, Frameworks & Protocols You can write your own commands and signatures as extensions. Extensions are placed under /ext (containers) or ~/.trueseeing2/extensions/ (uv/pip) . Alternatively you can distribute your extensions as wheels. We provide type information so you can not only type-check your extensions with zuban but also get a decent assist from IDEs. See the details section for details.
With pip, to create one, firstly set up a venv, install flit and validating toolchains ( zuban and ruff ) in there, and have flit pull dependencies. In short, do something like this: Currently we can detect the following class of vulnerabilities, largely ones covered in OWASP Mobile Top 10 - 2016: Our extension API lays under the trueseeing.api package. As we provide type information with it, your IDE will assist you when writing your extensions. Just make sure its (or its language server's) PYTHONPATH covers the venv in where our package; see uv tool list --show-paths if you installed it with uv tool install . If you installed with uvx , consider re-install it with uvx install . If you installed with pip, you've already know where it is.
To define new file formats, firstly implement Context s (ABC) for your formats, then implement trueseeing.api.FileFormatHandler to create and return their instances, and advertise them.
The following class will provide APK file support under the type named apk2 , for example: Then make sure you check for the type of the context in your signatures, making them ignored on unsupported contexts: Upon successful check, require_type(...) will try to downcast them to appropriate types for your convenience. But by design it works only for known types (currently, the apk ). So if you are defining some detailed interface in your new context classes as we do for the apk type, you need to do a downcast here i.e.: It is possible to define multiple formats matching the same pattern. We evaluate patterns in the order of from the most stringent (i.e. long) to the least. You use the -F switch to force some format to use with the target file, e.g.: Extensions can be either: a) any package placed under /ext (container) or ~/.trueseeing2/extensions (pip), or b) any installed module named with the prefix of trueseeing_ext0_ .
A Python-based security audit tool using Android Debug Bridge (ADB) to scan Android devices for common vulnerabilities including root access, outdated applications, and exposed network ports. This repository contains a cybersecurity lab exercise focused on mobile device security . The project demonstrates how to use Python and Android Debug Bridge (ADB) to programmatically audit Android devices for security vulnerabilities commonly found in enterprise field deployments.
The script was developed as part of a structured cybersecurity curriculum covering the OWASP Mobile Top 10 security risks and practical Android security auditing techniques. You are a cybersecurity analyst at a mobile security firm supporting a nationwide mobile auto mechanic company called FixFast AutoTech . The company equips its field technicians with Android devices to: You have been tasked with writing a Python script that uses ADB to scan these devices for these common vulnerabilities.
Before running this script, ensure the following are installed and configured on your system: No additional Python packages are required. The script uses only the built-in subprocess module from the Python Standard Library. Checks if the Android device has been rooted by attempting to execute a superuser command.
How it works: Runs su -c id on the device. If the output contains uid=0 , the command ran as root, meaning the device is rooted. How it works: Runs dumpsys package to dump all installed package information including version codes, which can be cross-referenced with known vulnerable versions.
How it works: Runs netstat on the device to list all active network connections and listening ports. Open ports can indicate services that may be exploited by attackers. The entry point of the script. Orchestrates device connection and presents the interactive scan menu. This project is licensed under the MIT License . See the LICENSE file for full details.
Built as part of a cybersecurity curriculum covering OWASP Mobile Top 10 and Android security auditing. Python script using Android Debug Bridge (ADB) to scan Android devices for security vulnerabilities. Detects root access, identifies outdated applications, and exposes open network ports. Built for cybersecurity analysis in a mobile device security audit context.
In 2025, with over 3.5 billion Android devices worldwide facing an escalating tide of cyber threats—where a staggering 87% of mobile apps harbor at least one high-risk vulnerability according to the latest OWASP Mobile Security report—penetration testing has become non-negotiable for developers and security teams. Enter QARK, the open-source Python framework that's revolutionizing vulnerability detection in Android apps by automating static analysis and uncovering hidden weaknesses before they can be exploited. As edge computing and 5G networks propel IoT and mobile ecosystems into hyper-connected realms, QARK empowers cybersecurity professionals to fortify apps against real-world attacks, blending AI-driven insights with traditional pen-testing rigor to safeguard user data in an era of pervasive digital risks.
This measures the interconnectedness of app components, aiding in identifying complex vulnerability paths. Note: This is a simplified illustration. Real-world QARK runs involve full bytecode analysis and custom rule application for comprehensive coverage. Penetration testing, or ethical hacking, simulates cyberattacks to identify weaknesses in software systems, and when it comes to Android apps, the stakes are high due to the platform's dominance in mobile computing. QARK, standing for Quick Android Review Kit, is a Python-based framework developed to streamline this process through automated static code analysis. Unlike dynamic testing tools that require runtime execution, QARK dissects APK files—Android's installation packages—at rest, examining bytecode for patterns indicative of vulnerabilities like insecure data storage, improper permissions, or injection flaws.
4. Practical Deployment, Analysis & Case Studies At its core, QARK leverages reverse engineering techniques rooted in computer science principles such as graph theory and formal verification. Imagine the app's code as a vast city map: QARK traces the "roads" (method calls) to spot unsecured entry points where attackers could sneak in. This static approach is grounded in the Dalvik bytecode format used by Android, which QARK decompiles using libraries like Androguard or apktool. The framework categorizes vulnerabilities based on OWASP Mobile Top 10 risks, such as M1: Improper Platform Usage or M5: Insufficient Cryptography.
Theoretically, vulnerability detection can be modeled as a pattern-matching problem in a finite state machine, where app states represent code paths and transitions are triggered by user inputs or system calls. QARK employs rule-based engines to flag deviations from secure coding practices, drawing from formal methods like taint analysis—tracking untrusted data flows from sources (e.g., network inputs) to sinks (e.g., file writes). This prevents issues like SQL injection by ensuring data sanitization at every step.
In the broader context of cybersecurity trends in 2025, QARK aligns with zero-trust architectures and AI-augmented threat detection. While not inherently ML-based, it can integrate with machine learning models for prioritizing alerts, using supervised learning on historical vulnerability datasets to predict exploit likelihood. For instance, a simple decision tree could classify code snippets as "vulnerable" based on features like permission declarations and API calls, achieving recall rates above 85% in benchmarks.
Understanding these foundations is crucial because Android's fragmented ecosystem—spanning thousands of device models and OS versions—amplifies risks. QARK's Python implementation allows customization, enabling pentesters to extend rules for emerging threats like side-channel attacks in 5G-enabled apps. By automating tedious decompilation and scanning, QARK shifts focus from manual grunt work to strategic analysis, making it indispensable for DevOps teams embedding security in CI/CD pipelines.
Consider the analogy of a metal detector at an airport: just as it scans without disrupting flow, QARK probes apps pre-release, catching "metals" (vulnerabilities) efficiently. This theoretical backbone ensures scalability, handling APKs up to 100MB with minimal overhead, and positions QARK as a cornerstone in modern Android security postures. Implementing QARK for Android app penetration testing starts with environment setup, ensuring a robust foundation for reliable scans. Begin by installing Python 3.8+ and dependencies via pip: essential libraries include androguard for APK parsing, apktool for decompilation, and QARK itself (pip install qark). For a production setup, use a virtual environment with venv to isolate dependencies, and integrate with Docker for containerized runs—crucial for CI/CD pipelines in 2025 DevOps workflows.
Step 1: APK Acquisition and Preparation. Obtain the APK via adb pull from a device or build it from source using Gradle. Verify integrity with SHA-256 hashing to prevent tampered inputs. Step 2: Decompilation. QARK internally uses apktool to unpack the APK into smali code and resources, exposing manifests and dex files. Handle large APKs by allocating sufficient RAM (at least 4GB) to avoid OutOfMemory errors.
Step 3: Rule Execution. QARK's modular ruleset scans for over 50 vulnerability types, from WebView misconfigurations to hardcoded secrets. Customize by editing rules in Python scripts under QARK's modules directory— for example, add checks for Android 14's scoped storage compliance. Step 4: Reporting and Remediation. Outputs include HTML/JSON reports with severity ratings; parse these to automate fixes, like injecting permission checks via bytecode manipulation with smali/baksmali.
Practical challenges include obfuscated code from ProGuard, which QARK mitigates by focusing on behavioral patterns rather than names. In our production deployments at security consultancies, we found that preprocessing APKs with dex2jar improves analysis accuracy by 15%. Configuration involves a YAML file for scan depth: shallow for quick CI checks (under 1 minute) or deep for full audits (5-10 minutes per app).
For scaling, integrate QARK into Jenkins or GitHub Actions: trigger scans on pull requests, failing builds if high-severity issues exceed thresholds. Dependency management uses requirements.txt, pinning versions like androguard==3.4.0 to avoid breaking changes. This step-by-step approach ensures QARK not only detects but accelerates secure app development, addressing real-world hurdles like multi-module apps where interdependencies hide vulnerabilities.
The following description outlines the key components of a production system for . Use this to visualize the data flow and architecture. Data Flow: APK Ingestion -> Decompiler -> Rule Engine -> Report Generator -> Security Dashboard. Feedback Loop updates the Rule Engine iteratively.
Benchmarking QARK against baseline tools like MobSF, Drozer, and AndroBugs reveals its strengths in speed and accuracy for static Android vulnerability detection. Tests conducted on a dataset of 500 real-world APKs from diverse categories (e.g., banking, social media) using a standard Intel i7 machine with 16GB RAM showed QARK achieving a 92.3% detection rate for OWASP Top 10 issues, outperforming MobSF's 78.5% by 17.8%. According to a 2024 Mobile Security Benchmark by Gartner, tools like QARK reduce mean time to detect (MTTD) from hours to minutes.
Methodology involved cross-validation: APKs were manually labeled for ground truth vulnerabilities by certified pentesters. QARK's inference—here, scan execution—averaged 45 seconds per 10MB APK, compared to Drozer's dynamic approach at 300 seconds, highlighting static analysis's efficiency for pre-release testing. Memory usage peaked at 256MB for QARK, half of MobSF's, making it ideal for resource-constrained CI environments.
Scaling characteristics: On multi-core setups, QARK parallelizes rule execution, yielding linear speedup up to 8 cores (e.g., 5x faster on AWS c5.4xlarge). Hardware requirements are modest—a mid-range CPU suffices—but GPU acceleration via custom ML extensions could further optimize pattern matching. Trade-offs include higher false positives (12%) in obfuscated apps versus AndroBugs (18%), but QARK's customizable rules allow tuning for 5-10% reductions.
In real-world metrics, a 2025 Veracode report notes QARK-integrated pipelines cut remediation cycles by 40%, with computational efficiency enabling 1,000+ scans daily in enterprise DevSecOps. Compared to baselines, QARK balances accuracy (F1-score: 0.89) and throughput, though dynamic tools like Drozer excel in runtime exploits (detection: 95% but at 6x cost). For practitioners, this positions QARK as a first-line defender, with hybrid setups recommended for comprehensive coverage.
While QARK excels in static vulnerability detection, it has limitations inherent to its approach. It fails to detect runtime-dependent issues, such as those triggered by user interactions or network conditions—for instance, if an app validates inputs only after encryption in a conditional branch, QARK might miss it, leading to false negatives (FN rate: up to 25% in dynamic-heavy apps). Root cause: Static analysis assumes all paths are traversable without execution, per a 2024 SANS Institute study on mobile tools.
Specific scenario: Obfuscated code with tools like R8; QARK's pattern matching drops accuracy to 60% when method names are mangled, as it relies on semantic cues. Solution: Pre-process with deobfuscation scripts using machine learning-based renaming (e.g., via graph neural networks), recovering 15-20% detection. Another failure: Native code (JNI) vulnerabilities, where C/C++ libraries evade bytecode scans—QARK reports 0% coverage here. Mitigate by pairing with tools like QEMU for emulation, adding dynamic layers.
False positives spike (up to 30%) in legitimate uses of risky APIs, like WebView for internal dashboards; why? Overly broad rules without context. Debugging: Use QARK's verbose mode (--debug) to trace rule triggers, then whitelist via custom filters. In production, we found network latency exceeding 200ms during remote APK pulls causes incomplete decompiles—solved by implementing exponential backoff in upload scripts, retrying up to 5 times.
Troubleshooting guide: For decompilation errors (e.g., corrupted DEX), validate APK with aapt dump badging; if permissions misflag, cross-check AndroidManifest.xml manually. Edge cases like hybrid apps (React Native) require source-level analysis, where QARK covers only bridged components. Overall, honest assessment: QARK's 88% precision suits early-stage testing, but for high-stakes apps, combine with manual pentests to address these gaps, ensuring robust cybersecurity postures.
Note: Costs vary based on APK volume, cloud usage, and custom extensions. Production scales with scan frequency. Optimization via open-source nature and efficient Python runtime yields high savings. Optimizing QARK involves enhancing its rule engine with machine learning for smarter detection— for example, training a lightweight LSTM on smali code sequences to predict injection risks, reducing false positives by 25%. In production, deploy via Kubernetes pods, scaling horizontally for 100+ concurrent scans; use Helm charts for configuration management.
Deployment strategies: Containerize with a Dockerfile including QARK and dependencies, exposing a REST API for scan requests via Flask. For CI/CD, integrate with GitLab: post-build, trigger QARK on artifacts, parsing JSON outputs to block merges. Monitoring: Employ Prometheus to track scan durations and error rates, alerting on spikes via PagerDuty. Scaling tips from experience: Shard large APKs by modules, processing in parallel with multiprocessing.Pool—cuts time by 40%. Advanced: Hybrid dynamic-static by chaining QARK with Frida for runtime verification, covering 95% of vectors. CI/CD integration uses webhooks; in our deployments, automated remediation scripts (e.g., injecting SecureRandom) fixed 60% of low-severity issues autonomously. For edge computing, optimize for ARM via PyInstaller, enabling on-device scans in IoT scenarios.
Practical: Use caching for repeated scans (Redis for report storage), saving 50% recompute. Security: Run in air-gapped VMs to handle sensitive APKs. These techniques transform QARK from a tool into a scalable security platform, ready for 2025's threat landscape. Nexus Labs, a rising fintech startup specializing in decentralized finance apps, faced a critical challenge in 2025: their flagship Android banking app, handling over $500M in daily transactions, was flagged during a compliance audit for potential OWASP violations. With a tight release cycle for a 5G-integrated update, manual pentesting would take weeks, risking delays amid rising mobile phishing attacks—up 40% year-over-year per FBI reports.
The team turned to QARK, integrating it into their GitHub Actions pipeline. Initial scans on the 25MB APK revealed 18 high-severity issues, including exported Content Providers vulnerable to unauthorized data access and hardcoded API keys in smali code. Challenge: The app's use of third-party SDKs like Firebase obscured some paths; QARK's decompiler struggled with minified code, initially reporting 15% false negatives.
Solution: Customized rules to trace SDK interactions via taint analysis extensions in Python, boosting detection to 94%. They parallelized scans for modular components (UI, backend, crypto), reducing total audit time from 10 days to 2. Performance metrics: QARK processed 50 builds weekly, identifying SQL injection risks in user queries with 91% accuracy, versus baseline manual reviews at 75%. Memory usage stayed under 300MB, fitting their AWS EC2 t3.medium instances.
Outcomes: Remediation fixed 100% of critical vulns, preventing potential $2M breach per simulated attack modeling. Post-deployment, app security score rose from 6.2 to 9.1 on CVSS scales, and user trust metrics improved 25% in A/B tests. Challenges like integrating with their Kotlin codebase were overcome by bytecode-level fixes, showcasing QARK's versatility. This story underscores how QARK turns security from a bottleneck into an accelerator for innovative fintech products.
"Integrating QARK into our CI/CD reduced false positives by 35% through custom rules tailored to our app's architecture." 5. Performance Evaluation & Extended Technical Observations "For obfuscated APKs, combining QARK with deobfuscation tools like Simplify improved detection rates to over 90%." "QARK's JSON output makes it easy to automate remediation— we've scripted fixes for common permission issues." "In large-scale audits, batch processing with QARK cut our scanning time by 60%, allowing weekly security gates." "Handling native code gaps in QARK? Hook it with Ghidra for JNI analysis—boosted our coverage to 95%." Break APKs into components for targeted analysis—focus on high-risk modules first to prioritize fixes and save time.
Log detection rates and remediation times; use this data to refine rules, as we did to drop false positives from 20% to 8%. Git-track custom QARK rules alongside your app code for reproducibility and collaborative security enhancements. Pair QARK's static scans with dynamic tools like Appium for end-to-end coverage, catching what static misses. Use serverless like AWS Lambda for on-demand scans—cost-effective for sporadic testing in small teams.
What challenges have you faced when implementing ? Share your experiences and solutions with our community of AI practitioners. Open-source implementations and example code to help you get started with your own projects. Step-by-step video guides that walk through implementation details and advanced techniques.
Problem: Scaling scans for high-volume app releases Root Cause: Sequential processing bottlenecks in CI/CD Technical Solution: Parallel execution with multiprocessing and container orchestration
Implementation
Use Python's multiprocessing.Pool in scripts, deploy via Docker Compose for 4x throughput Problem: Resource spikes during deep scans Root Cause: Intensive decompilation of large DEX files Technical Solution: Memory-efficient parsing and rule prioritization Implementation: Limit to shallow scans initially, use Androguard's lazy loading to cap at 512MB RAM Problem: Choosing between static vs. dynamic tools Root Cause: Trade-offs in coverage and speed for Android security Technical Solution: Hybrid pipelines combining QARK with runtime agents Implementation: Script Frida hooks post-QARK to verify static findings, achieving 95% overall accuracy Problem: Reduced detection in minified code Root Cause: Loss of semantic information in bytecode Problem: Limited JNI coverage in static analysis Root Cause: Focus on Dalvik bytecode, ignoring C/C++ Technical Solution: External native scanners integration Implementation: Chain with Ghidra API calls in Python wrapper, flagging buffer overflows in lib files QARK stands as a powerhouse Python framework for penetration testing Android apps, delivering rapid, accurate vulnerability detection that integrates seamlessly into modern DevSecOps. Key takeaways include its 92% detection rate for static threats, ease of customization for specific app ecosystems, and cost-effective scaling—empowering teams to ship secure software without sacrificing speed. Limitations like runtime blind spots highlight the need for hybrid strategies, but with optimizations, QARK achieves enterprise-grade reliability.
Implementation Synonym
Looking ahead, future directions point to AI enhancements: embedding LLMs for natural language rule generation or graph neural networks for call-flow prediction, potentially slashing false positives by 40% by 2026. As 5G and IoT amplify mobile attack surfaces, QARK's evolution will be pivotal in proactive cybersecurity. Try implementing QARK in your next project—start with a simple scan and share your results in the community to drive collective advancements.
Implementation Meaning
"The implementation of represents a significant advancement in practical AI deployment, balancing performance with computational efficiency in real-world scenarios." Filed under penetration , testing , android , apps , ai research , 2025 technology , implementation , developer tips , python code and technical tutorial .
Implementation Science
arXivLabs is a framework that allows collaborators to develop and share new arXiv features directly on our website. Both individuals and organizations that work with arXivLabs have embraced and accepted our values of openness, community, excellence, and user data privacy. arXiv is committed to these values and only works with partners that adhere to them.
Implementation Specialist
Have an idea for a project that will add value for arXiv's community? Learn more about arXivLabs . A powerful Python-based tool designed to scan APK files for common vulnerabilities such as: VULNERABILITY III main.py # Entry point for the scanner III apk_analyzer.py # APK analysis logic III vulnerability_scan.py # Vulnerability scanning logic III flask_api.py # Flask API to expose scanner as a service III frida_hook.py # Dynamic analysis via Frida III uploaded_apk.apk # Sample test APK file III vulnerabilities exec.mp4 # Demo video of the scanner in action for more details and execution checkout the demo video '''vulnerabilities exec.mp4''' you will find it '''vulnerabilities exec.zip''' file How to Develop an Automated Mobile Application Vulnerability Scanner Using Python with Machine Learning To create an automated mobile app vulnerability scanner with integrated machine learning, you need components for: Tip: For enterprise-level scanners, consider extending with static and dynamic modules, detailed reporting, and a modern web interface! Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/List%20of%20free%20and%20open-source%20software%20packages • https://en.wikipedia.org/wiki/Google%20Cloud%20Platform • https://en.wikipedia.org/wiki/Heartbleed • https://github.com/alterakey/trueseeing • https://github.com/Nyabayo/securing-mobile-devices-python-adb-scanner-root-detection-outdated-applications-open-port-an alysis • https://johal.in/penetration-testing-android-apps-with-qark-python-framework-for-vulnerability-detection • https://arxiv.org/abs/2604.14431 • https://github.com/Karthikkairamkonda/APK-Vulnerability-Scanner • https://askfilo.com/user-question-answers-smart-solutions/how-to-develop-an-automated-mobile-application-vulnerability-33 37333930323538 • https://github.com/vinaypatil-132/Creating-a-Framework-for-Static-Analysis-of-Vulnerabilities-in-Android-Applications
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Android Application Vulnerability Scanner Tool In Python.
[*] Initializing Burp Suite Spider & Vulnerability Engine for Android Application Vulnerability Scanner Tool In Python... [✓] Burp Extender / Macro Automation Hook Synced ──────────────────────────────────────────────────────────────────────── [11:42:01.104] AUDIT Crawled dynamic endpoints | Injecting input vectors [11:42:01.218] FINDING Cymulate / Burp: Input sanitation check executed in parameter 'q' [11:42:01.312] VERIFY SafeBreach payload validation: Out-of-band interaction confirmed [11:42:01.405] REPORT Severity: Evaluated | Remediation: Enforce context-aware validation ──────────────────────────────────────────────────────────────────────── [✓] Burp Suite Audit Completed: Verified across OWASP Top 10 vectors
| Vulnerability Vector | Testing Tool | Injection Target | Severity | Remediation Status |
|---|---|---|---|---|
| SQL Injection (SQLi) | Burp Suite Professional | POST /api/auth/login | CRITICAL | PARAMETERIZED |
| Cross-Site Scripting (XSS) | SafeBreach / Cymulate | GET /search?q= | HIGH | CSP ENFORCED |
| Broken Object Level Access | Picus Security Audit | GET /user/account/840 | HIGH | RBAC APPLIED |
| Security Misconfiguration | AttackIQ Suite | HTTP Security Headers | MEDIUM | RESOLVED |