Complete Technical Paper Content — Android Runtime Permission Analyzer For Privacy Leakage
Overview & System Context
Android Runtime Permission Analyzer For Privacy Leakage: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8519 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Guidelines for auditing permission vulnerabilities, enforcing least privilege, securing IPC boundaries, and handling runtime permissions across the Android ecosystem.
When auditing an Android project for permission and IPC security vulnerabilities, systematically inspect each area: When declaring custom permissions or partner certificates in the manifest, you must follow the instructions in the
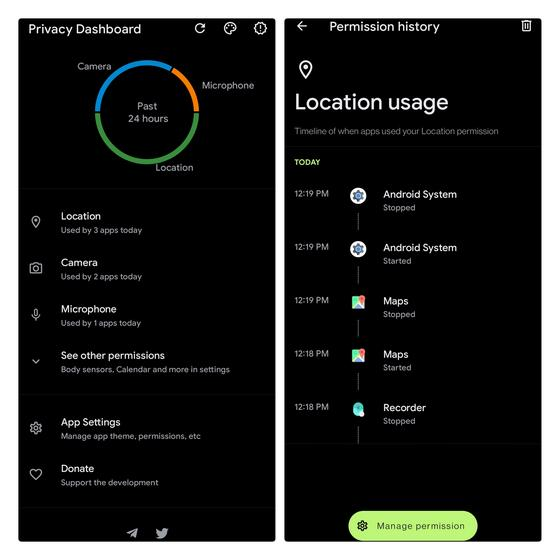
Figure 1: How to Get Android 12's Privacy Dashboard on Any Phone | Beebom
*/ fun getActivePersistedPermissions ( context : Context ): List
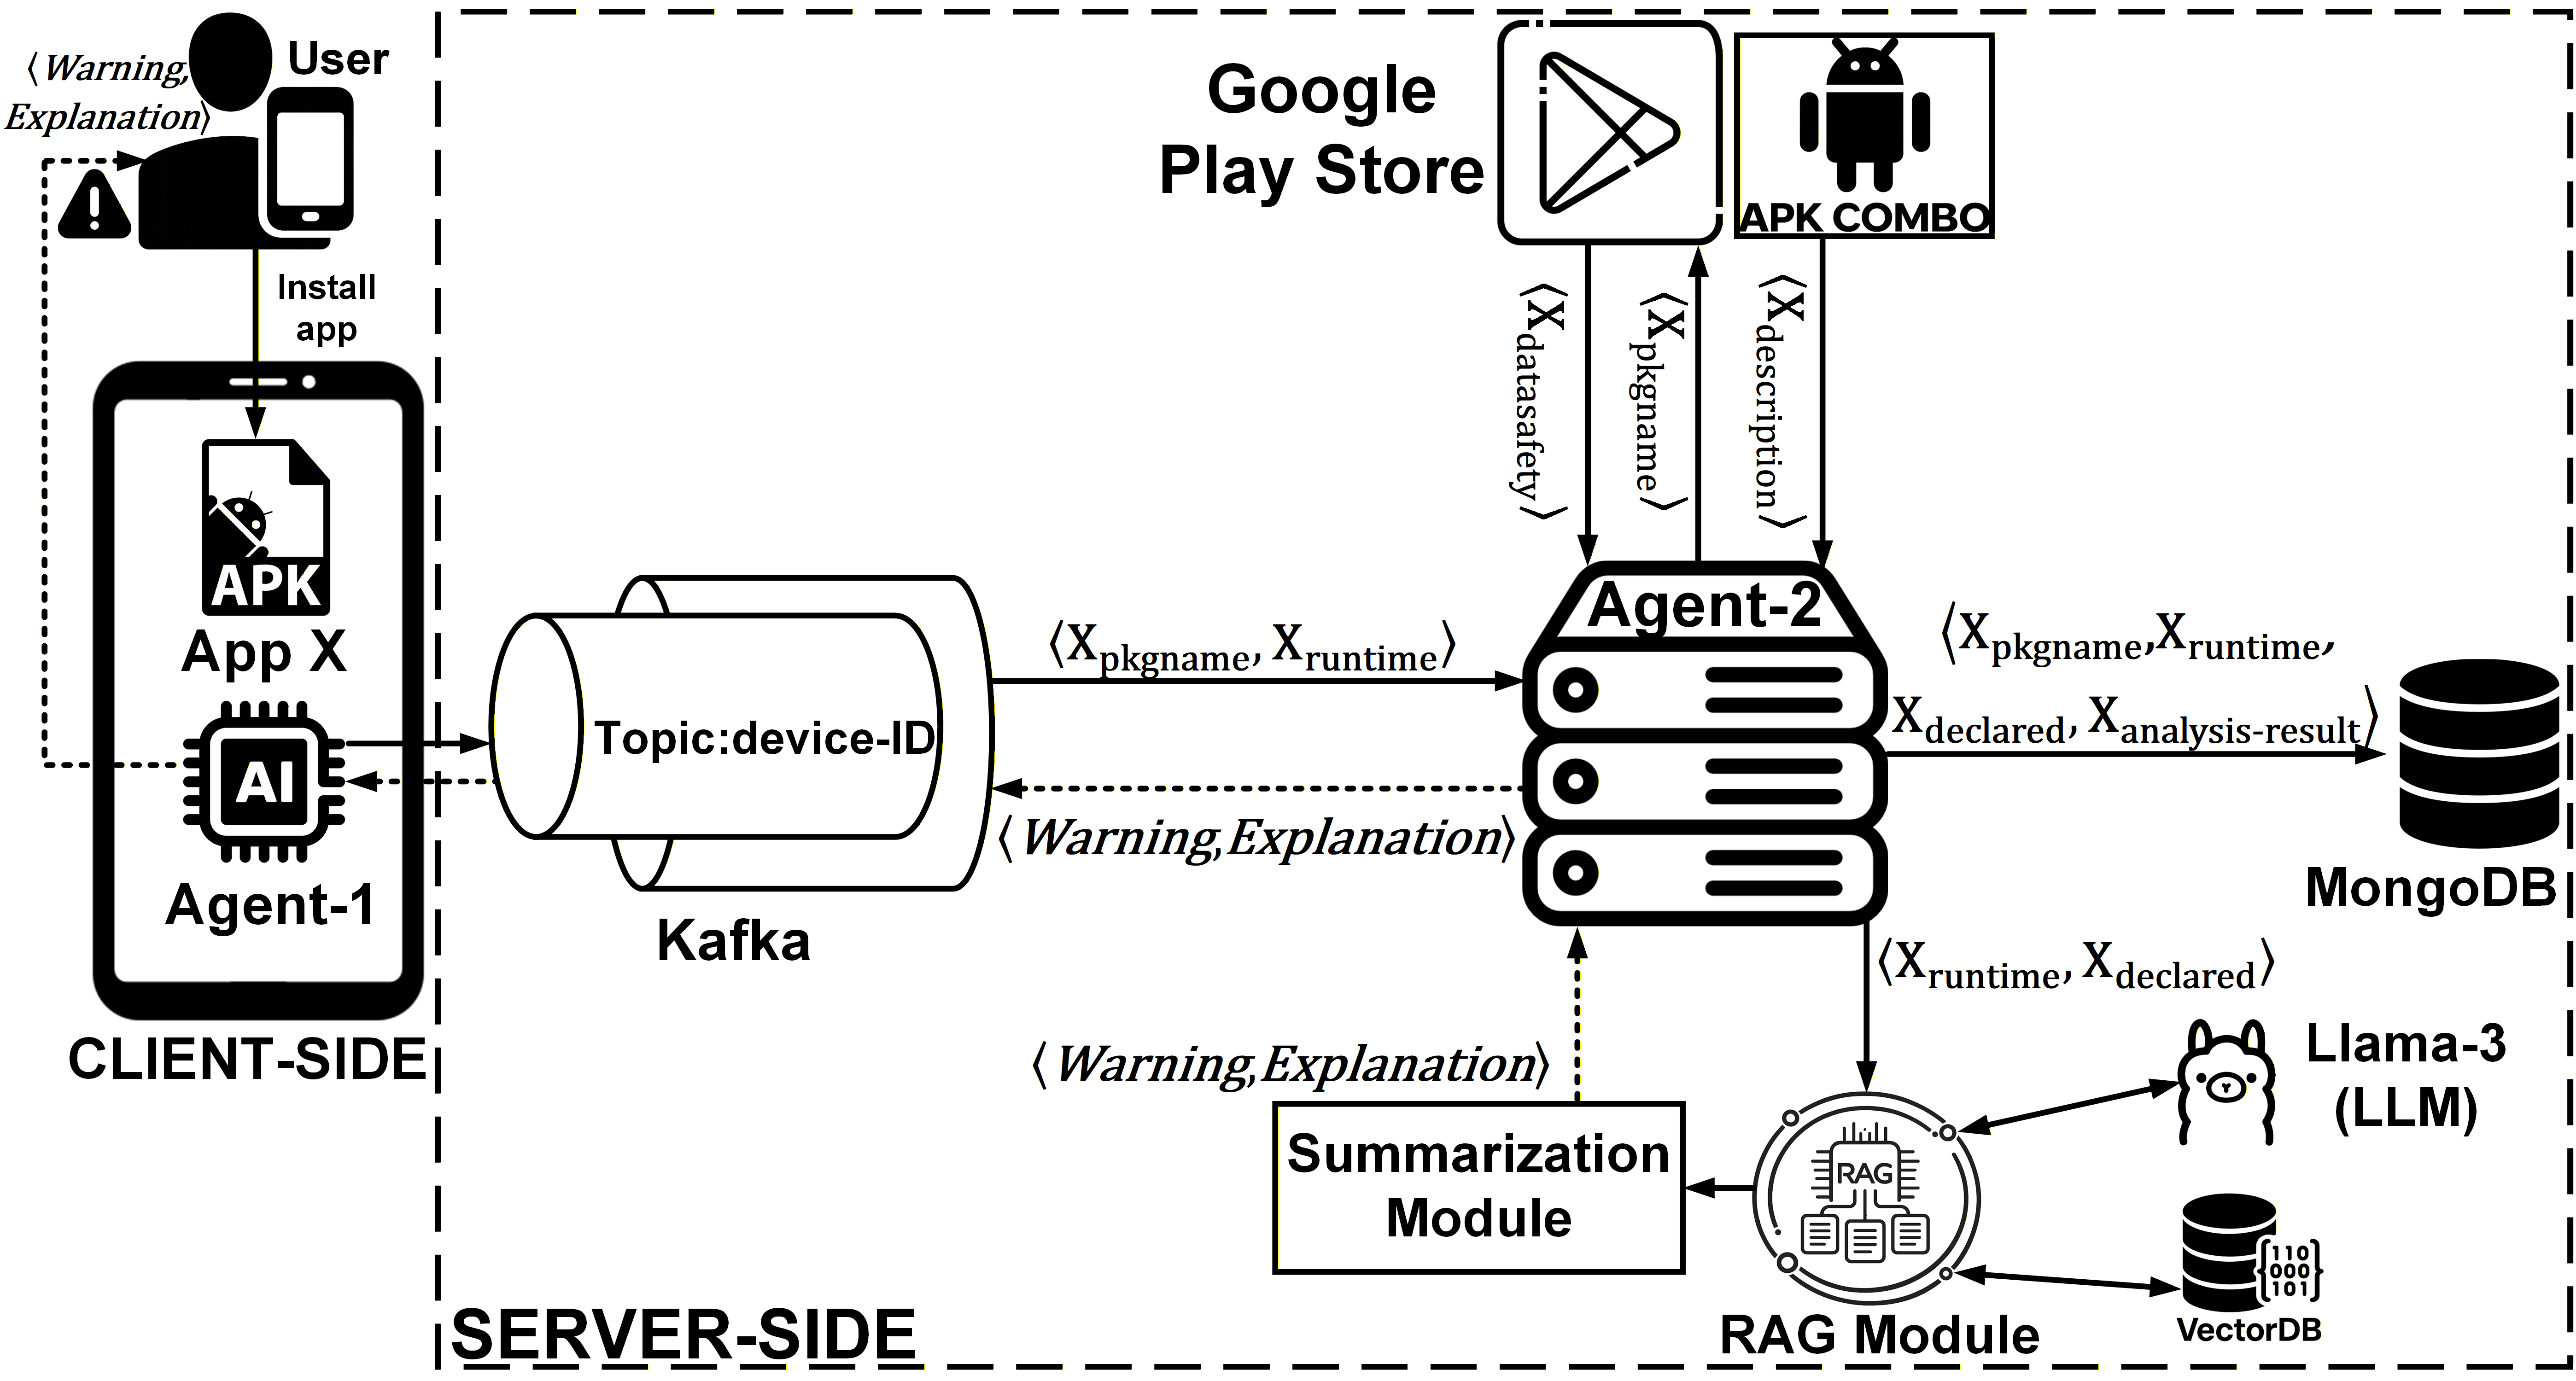
Figure 3: PrivacyAssist: A User-Centric Agent Framework for Detecting Privacy ... // VULNERABLE PATTERN: DO NOT DO THIS val callingPackage = intent ?. getStringExtra ( "calling_package" ) if ( callingPackage != null && SignatureUtils . verifyPartnerPackage ( this , callingPackage )) { // A malicious app passes "com.example.partner" in the extra. // The signature check verifies the installed partner on disk, but the CALLER was malicious! } CallerVerifier . kt object CallerVerifier { private const val TRUSTED_PARTNER_SHA256 = "A1B2C3D4E5F60708090A0B0C0D0E0F1011121314151617181920212223242526" fun isCallerAuthorized ( context : Context ): Boolean { val callingUid = Binder . getCallingUid () if ( callingUid == android . os . Process . myUid ()) return true val pm = context . packageManager // Modern API 28+ check by UID: if ( Build . VERSION . SDK_INT > = Build .
VERSION_CODES . P ) { val certBytes = hexStringToByteArray ( TRUSTED_PARTNER_SHA256 ) if ( pm . hasSigningCertificate ( callingUid , certBytes , PackageManager . CERT_INPUT_SHA256 )) { return true } } // Fallback for legacy APIs: val callingPackages = pm . getPackagesForUid ( callingUid ) ?: return false for ( pkg in callingPackages ) { if ( verifyPackageSignature ( pm , pkg )) { return true } } return false } @Suppress ( "DEPRECATION" ) private fun verifyPackageSignature ( pm : PackageManager , packageName : String ): Boolean { return try { val packageInfo = pm .
getPackageInfo ( packageName , PackageManager . GET_SIGNATURES ) val signatures = packageInfo . signatures ?: return false for ( sig in signatures ) { val digest = java . security . MessageDigest . getInstance ( "SHA-256" ). digest ( sig . toByteArray ()) val hex = digest . joinToString ( "" ) { "%02X" . format ( it ) } if ( hex . equals ( TRUSTED_PARTNER_SHA256 , ignoreCase = true )) return true } false } catch ( e : PackageManager . NameNotFoundException ) { false } } private fun hexStringToByteArray ( s : String ): ByteArray { val len = s . length val data = ByteArray ( len / 2 ) for ( i in 0 until len step 2 ) { data [ i / 2 ] = (( Character . digit ( s [ i ] , 16 ) shl 4 ) + Character . digit ( s [ i + 1 ] , 16 )). toByte () } return data } } CallerVerifier . kt In bound services exposing AIDL Binder stubs, protect state-modifying methods using enforceCallingPermission() .
class SecureBoundService : Service () { private val binder = object : IMyService . Stub () { override fun getData (): String { // Read-only operation guarded by manifest-level permission return "Confidential Data" } override fun modifyData ( newData : String ) { // MUST use enforceCallingPermission or checkCallingPermission. // NEVER use checkCallingOrSelfPermission or enforceCallingOrSelfPermission.
this @SecureBoundService.enforceCallingPermission ( "com.example.snippets.permission.WRITE_DATA" , "Caller lacks WRITE_DATA permission" ) updateInternalState ( newData ) Log . d ( "SecureBoundService" , "Data modified to: $ newData with proper WRITE_DATA permission check" ) } } override fun onBind ( intent : Intent?) : IBinder = binder private fun updateInternalState ( data : String ) { // Internal state update logic } } SecureBoundService . kt When implementing runtime permission requests or handling permission denial states, you must follow the instructions in the Request runtime permissions guide and Permissions overview . Implement a 3-state flow without caching states or creating infinite retry loops: class RuntimePermissionsActivity : ComponentActivity () { private val cameraLauncher = registerForActivityResult ( ActivityResultContracts . RequestPermission ()) { isGranted - > if ( isGranted ) { startCameraPreview () } else { if ( ! shouldShowRequestPermissionRationale ( Manifest . permission . CAMERA )) { // User selected 'Don't ask again' or permanently denied.
// Direct user to Application Details Settings.
val intent = Intent ( Settings .
ACTION_APPLICATION_DETAILS_SETTINGS ). apply { data = Uri . fromParts ( "package" , packageName , null ) } startActivity ( intent ) } else { showSnackbar ( "Camera permission is required to preview camera feed." ) } } } fun requestCameraPermissionSafely () { val permission = Manifest . permission . CAMERA when { ContextCompat . checkSelfPermission ( this , permission ) == PackageManager . PERMISSION_GRANTED - > { startCameraPreview () } shouldShowRequestPermissionRationale ( permission ) - > { showSnackbar ( "Camera permission is needed to preview camera feed." ) cameraLauncher . launch ( permission ) } else - > { cameraLauncher . launch ( permission ) } } } private fun startCameraPreview () { Log . d ( "RuntimePermissionsActivity" , "Camera preview started" ) } private fun showSnackbar ( msg : String ) { Log . i ( "RuntimePermissionsActivity" , msg ) } } RuntimePermissionsActivity . kt When implementing photo or media selection, you must follow the instructions in the Photo Picker API guide to avoid requesting broad storage permissions.
private val photoPickerLauncher = registerForActivityResult ( ActivityResultContracts . PickVisualMedia ()) { uri - > if ( uri != null ) { handleImageUri ( uri ) } } fun selectPhoto () { photoPickerLauncher . launch ( PickVisualMediaRequest ( ActivityResultContracts . PickVisualMedia . ImageOnly ) ) } MediaPickerSnippets . kt private val foregroundLocationLauncher = registerForActivityResult ( ActivityResultContracts . RequestMultiplePermissions ()) { permissions - > val fineGranted = permissions [ Manifest . permission . ACCESS_FINE_LOCATION ] ?: false val coarseGranted = permissions [ Manifest . permission . ACCESS_COARSE_LOCATION ] ?: false if ( fineGranted || coarseGranted ) { startForegroundLocationUpdates () } } fun requestForegroundLocation () { foregroundLocationLauncher .
launch ( arrayOf ( Manifest .
permission . ACCESS_FINE_LOCATION , Manifest .
permission . ACCESS_COARSE_LOCATION ) ) } // Background location requested only AFTER foreground is granted and user explicitly opts in: private val backgroundLocationLauncher = registerForActivityResult ( ActivityResultContracts . RequestPermission ()) { isGranted - > if ( isGranted ) { startBackgroundTracking () } } LocationPermissionSnippets . kt fun performLocationAccess () { val fine = ContextCompat . checkSelfPermission ( this , Manifest . permission .
ACCESS_FINE_LOCATION ) val coarse = ContextCompat . checkSelfPermission ( this , Manifest . permission . ACCESS_COARSE_LOCATION ) if ( fine != PackageManager . PERMISSION_GRANTED && coarse != PackageManager . PERMISSION_GRANTED ) { requestForegroundLocation () return } val provider = if ( fine == PackageManager . PERMISSION_GRANTED ) { LocationManager . GPS_PROVIDER } else { LocationManager . NETWORK_PROVIDER } try { val location = locationManager . getLastKnownLocation ( provider ) processLocation ( location ) } catch ( e : SecurityException ) { Log . e ( "LocationAccess" , "Permission revoked at runtime" , e ) } } PermissionErrorHandling . kt Use explicit intents, required receiver permissions, or Android 14+ broadcast options: // Sender: Enforce permission and share identity val intent = Intent ( "com.example.snippets.permission.ACTION_SECRET_UPDATE" ). apply { setPackage ( "com.example.partner" ) // Explicit target } val isUdc = Build . VERSION . SDK_INT > = Build . VERSION_CODES . UPSIDE_DOWN_CAKE val options = if ( isUdc ) { BroadcastOptions . makeBasic (). apply { setShareIdentityEnabled ( true ) }. toBundle () } else null sendBroadcast ( intent , "com.example.snippets.permission.RECEIVE_SECRET_UPDATE" , options ) ProtectedReceiver . kt // Receiver: Validate sender on Android 14+ class ProtectedReceiver : BroadcastReceiver () { override fun onReceive ( context : Context , intent : Intent ) { if ( intent . action == "com.example.snippets.permission.ACTION_SECRET_UPDATE" ) { if ( Build . VERSION . SDK_INT > = Build . VERSION_CODES . UPSIDE_DOWN_CAKE ) { val sender = sentFromPackage if ( sender != "com.example.trusted_sender" ) { return // Reject unauthorized sender } } processUpdate ( intent ) } } private fun processUpdate ( intent : Intent ) {} } ProtectedReceiver . kt Legacy compatibility (Pre-API 34) : For apps targeting API 33 or lower, attach an immutable PendingIntent extra ( FLAG_IMMUTABLE ) to the broadcast and authenticate the sender using pendingIntent.creatorPackage .
code samples are licensed under the Apache 2.0 License . For details, see the Google Developers Site Policies . Java is a registered trademark of Oracle and/or its affiliates. Effective in 2026, to align with our trunk stable development model and ensure platform stability for the ecosystem, we will publish source code to AOSP in Q2 and Q4. For building and contributing to AOSP, use android-latest-release . The android-latest-release manifest branch will always reference the most recent release pushed to AOSP. For more information, see Changes to AOSP .
In Android 6.0 and higher, the Android app permissions model is designed to make permissions more understandable, useful, and secure for users. The model moved Android apps that require dangerous permissions (see Affected permissions ) from an install-time permission model to a runtime permission model: ( Android 5.1 and lower ) Users grant dangerous permissions to an app when they install or update the app. Device manufacturers and carriers can preinstall apps with pregranted permissions without notifying the user.
( Android 6.0 to 9 ) Users grant dangerous permissions to an app when the app is running. When permissions are requested (such as when the app launches or when the user accesses a specific feature) depends on the app, but the user grants/denies app access to specific permission groups. OEMs/carriers can preinstall apps, but can't pregrant permissions unless they go through the exception process. (See Creating exceptions .) ( Android 10 ) Users see increased transparency and have control over which apps have activity recognition (AR) runtime permissions. Users are prompted by the runtime permissions dialog to either always allow, allow while in use, or deny permissions. On an OS upgrade to Android 10, permissions given to apps are retained, but users can go into Settings and change them.
Runtime permissions prevent apps from gaining access to private data without a user's consent, and provide them with additional context and visibility into the types of permissions that apps are either seeking, or have been granted. The runtime model encourages developers to help users understand why apps require the requested permissions, and provides greater transparency so users can make better decisions about granting or denying them.
Android 6.0 and higher requires dangerous permissions to use a runtime permissions model. Dangerous permissions are higher-risk permissions (such as READ_CALENDAR ) that grant requesting apps access to private user data, or control over a device, which can negatively impact the user. To view a list of dangerous permissions, run the command: Android 6.0 and higher doesn't change the behavior of normal permissions . These are all non-dangerous permissions including normal, system, and signature permissions. Normal permissions are lower-risk permissions (such as SET_WALLPAPER ) that grant requesting apps access to isolated app-level features with minimal risk to other apps, the system, or the user. As in Android 5.1 and lower releases, the system automatically grants normal permissions to a requesting app at installation and doesn't prompt the user for approval. For details on permissions, see the
In addition to being dangerous, a permission can be either hard-restricted or soft-restricted. In either case, the restricted permission must also be allowlisted. Non-allowlisted hard restrictions behave differently than non-allowlisted soft restrictions: When installing an app, the installer (such as Google Play Store) may select to not allowlist the restricted permissions for the app. Permissions are restricted by the platform and are grantable only if an app meets special criteria per platform policy.
Examples of hard-restricted permission types include SMS and Call Log permissions. The runtime permission model applies to all apps, including pre-installed apps and apps delivered to the device as part of the setup process. App software requirements include: Permissions granted to apps on Android 5.x remain granted after updating to Android 6.0 or higher, but users can revoke those permissions at any time.
In an Android 9-to-10 update, all hard-restricted permissions get allowlisted. For details on implementing the foreground/background split permissions, see Android 10 privacy change , beginning with Request background location . When integrating the app runtime permissions model for Android 6.0 and higher, you must update preinstalled apps to work with the new model. You can also define exceptions for apps that are the default handlers/providers for core functionality, define custom permissions, and customize the theme used in the PermissionController app.
Apps on the system image and preinstalled apps aren't automatically pregranted permissions. We encourage you to work with preinstalled app developers (OEM, carrier, and third party) to make the required app modifications using developer guidelines . Specifically, you must ensure that preinstalled apps are modified to avoid crashes and other issues when users revoke permissions.
2. System Architecture & Core Working Principles In Android 9 and lower, preloaded apps that use dangerous permissions must target API level 23 or higher, and maintain the Android 6.0 and higher AOSP permission model. For example, the UI flow during an app installation mustn't deviate from the AOSP implementation of PermissionController . Users can even revoke the dangerous permissions of preinstalled apps.
In Android 6.0 through 9, some permissions are granted during the install flow. However, starting in 10, the install flow (performed by the Package Installer app) is a separate function from permissions granting (in the Permission Controller app). The goal is to avoid confusing users with permission requests that appear out of context. If desired, you can customize the Permissions UI theme by updating the default device themes ( Theme.DeviceDefault.Settings and Theme.DeviceDefault.Light.Dialog.NoActionBar ) used by PackageInstaller. However, because consistency is critical for app developers, you can't customize the placement, position, and rules of when the Permissions UI appears.
You can pre-grant permissions to apps that are default handlers or providers for core OS functionality using the DefaultPermissionGrantPolicy.java class in PackageManager. Examples: You can define custom permissions and groups as normal or dangerous and add OEM/Carrier-specific permissions to existing permissions groups, just as you could in Android 5.x and earlier releases.
In Android 6.0 and later, if you add a new dangerous permission, it must be handled in the same way as other dangerous permissions (requested during app runtime and revocable by users). Specifically: Android includes Compatibility Test Suite (CTS) tests that verify individual permissions are mapped to the correct groups. Passing these tests is a requirement for Android 6.0 and later CTS compatibility.
In Android 13 and later, you are able to revoke your own granted runtime permissions using Context.revokeSelfPermissionsOnKill() . The revocation happens asynchronously and is triggered when it is safe to do so without disrupting the user. When the revocation is triggered, all processes running in the calling UID is killed.
It's important to understand that revoking a single permission may not be reflected in the settings UI, which treats permissions by group. Typically, a permission group is displayed as granted as long as at least one of the permissions in that group is granted. If ensuring that users are able to confirm the revocation in the settings is important to you, make sure to revoke every permission in the permission group. To learn which permissions belong to a certain group, you may use PackageManager.getGroupOfPlatformPermission and PackageManager.getPlatformPermissionsForGroup .
When the system revokes the permissions requested, it also revokes corresponding background permissions if none of their corresponding foreground permissions are still granted. The revocation isn't triggered as long as the process remains in the foreground but can also be triggered right away by manually killing all processes running in the current uid, for instance using System.exit() . However it is recommended to let the system decide when to trigger it.
After a permission revocation is effective, you are able to request it again, and the user is prompted to grant or deny the request. It isn't possible to request a permission that had previously been denied by the user. While you are encouraged to revoke permissions that you currently hold but are no longer needed, you should be careful not to inform the user about the revocation until after it's in effect.
Content and code samples on this page are subject to the licenses described in the Content License . Java and OpenJDK are trademarks or registered trademarks of Oracle and/or its affiliates. This page provides an overview to how Android permissions work, including a high-level workflow for using permissions, descriptions of different types of permissions, and some best practices for using permissions in your app. Other pages explain how to minimize your app's requests for permissions , declare permissions , request runtime permissions , and restrict how other apps can interact with your app's components.
To view a complete list of Android app permissions, visit the permissions API reference page . To view some sample apps that demonstrate the permissions workflow, visit the Android permissions samples repository on GitHub. If your app offers functionality that might require access to restricted data or restricted actions, determine whether you can get the information or perform the actions without needing to declare permissions . You can fulfill many use cases in your app, such as taking photos, pausing media playback, and displaying relevant ads, without needing to declare any permissions.
If you decide that your app must access restricted data or perform restricted actions to fulfill a use case, declare the appropriate permissions. Some permissions, known as install-time permissions , are automatically granted when your app is installed. Other permissions, known as runtime permissions , require your app to go a step further and request the permission at runtime.
Android categorizes permissions into different types, including install-time permissions, runtime permissions, and special permissions. Each permission's type indicates the scope of restricted data that your app can access, and the scope of restricted actions that your app can perform, when the system grants your app that permission. The protection level for each permission is based on its type and is shown on the permissions API reference page.
Install-time permissions give your app limited access to restricted data or let your app perform restricted actions that minimally affect the system or other apps. When you declare install-time permissions in your app, an app store presents an install-time permission notice to the user when they view an app's details page, as shown in figure 2. The system automatically grants your app the permissions when the user installs your app.
Android includes several sub-types of install-time permissions, including normal permissions and signature permissions. These permissions allow access to data and actions that extend beyond your app's sandbox but present very little risk to the user's privacy and the operation of other apps. The system grants a signature permission to an app only when the app is signed by the same certificate as the app or the OS that defines the permission.
Applications that implement privileged services, such as autofill or VPN services, also make use of signature permissions. These apps require service-binding signature permissions so that only the system can bind to the services. Runtime permissions, also known as dangerous permissions, give your app additional access to restricted data or let your app perform restricted actions that more substantially affect the system and other apps. Therefore, you need to request runtime permissions in your app before you can access the restricted data or perform restricted actions. Don't assume that these permissions have been previously granted—check them and, if needed, request them before each access.
When your app requests a runtime permission, the system presents a runtime permission prompt, as shown in figure 3. Many runtime permissions access private user data , a special type of restricted data that includes potentially sensitive information. Examples of private user data include location and contact information. The microphone and camera provide access to particularly sensitive information. Therefore, the system helps you explain why your app accesses this information .
Special permissions correspond to particular app operations. Only the platform and OEMs can define special permissions. Additionally, the platform and OEMs usually define special permissions when they want to protect access to particularly powerful actions, such as drawing over other apps. The Special app access page in system settings contains a set of user-toggleable operations. Many of these operations are implemented as special permissions.
Permissions can belong to permission groups . Permission groups consist of a set of logically related permissions. For example, permissions to send and receive SMS messages might belong to the same group, as they both relate to the application's interaction with SMS. Permission groups help the system minimize the number of system dialogs that are presented to the user when an app requests closely related permissions. When a user is presented with a prompt to grant permissions for an application, permissions belonging to the same group are presented in the same interface. However, permissions can change groups without notice, so don't assume that a particular permission is grouped with any other permission.
App permissions build on system security features and help Android support the following goals related to user privacy: This section presents a set of core best practices for using permissions effectively in your app. For more details on how you can work with permissions on Android, visit the app permissions best practices page. When the user requests a particular action in your app, your app should request only the permissions that it needs to complete that action. Depending on how you are using the permissions, there might be an alternative way to fulfill your app's use case without relying on access to sensitive information.
Request permissions as late into the flow of your app's use cases as possible. For example, if your app lets users send audio messages to others, wait until the user has navigated to the messaging screen and has pressed the Send audio message button. After the user presses the button, your app can then request access to the microphone. When you include a library, you also inherit its permission requirements. Be aware of the permissions that each dependency requires and what those permissions are used for.
When you make a permissions request, be clear about what you're accessing, why, and what functionalities are affected if permissions are denied, so users can make informed decisions. When you access sensitive data or hardware, such as the camera or microphone, provide a continuous indication in your app if the system doesn't already provide these indicators . This reminder helps users understand exactly when your app accesses restricted data or performs restricted actions.
Permissions aren't only for requesting system functionality. Your app's system components can restrict which other apps can interact with your app, as described on the page about how to restrict interactions with other apps . Content and code samples on this page are subject to the licenses described in the Content License . Java and OpenJDK are trademarks or registered trademarks of Oracle and/or its affiliates.
3. Software Implementation, Frameworks & Protocols Privacy Intelligence Platform is an automated system designed to analyze Android applications and privacy policies to detect potential privacy and security risks. This system helps users understand how mobile applications access sensitive data and evaluate their privacy implications before installation.
Mobile applications often request sensitive permissions such as location, contacts, camera, and storage. Many users install applications without understanding the potential privacy implications. Privacy Intelligence Platform was developed to provide automated analysis of Android applications and privacy policies, enabling users to better understand the risks associated with mobile applications.
The system combines security analysis, policy intelligence, and risk scoring to present clear insights about application behavior. User ↓ React Frontend (Dashboard Interface) ↓ Node.js Backend API ↓ Python Analysis Engine frontend React web interface server Node.js backend API analyzer Python APK and policy analysis engine docs UML diagrams and documentation uploads Temporary uploaded files reports Generated analysis reports Dangerous Permissions Permissions requiring user approval such as location, contacts, storage, camera, and microphone.
Special Permissions High risk permissions requiring additional authorization such as system overlay and usage access. This screen shows the APK permission analysis interface where users upload APK files and view detected permissions and risk scores. Displays metadata extracted from the Android application including package details and other information.
Allows users to analyze privacy policies by providing the policy URL. The system extracts and evaluates privacy statements. Displays privacy compliance analysis results and highlights red flags and green flags in the policy. Automated security and privacy risk analysis platform for Android applications using APK permission analysis, NLP policy evaluation, and app store intelligence.
A static analysis tool that scans Android APK files to detect risky permissions and identify privacy-violating apps. Authors: Azhan Shoaib (22P-9054) · Muhammad Subhan Tariq (22P-9067) Course: Cybersecurity / Android Security A static analysis tool to detect risky Android APK permissions and identify privacy-violating apps. Every Android app runs in a limited-access sandbox. If your app needs to use resources or information outside of its own sandbox, you can declare a runtime permission and set up a permission request that provides this access. These steps are part of the workflow for using permissions .
If you declare any dangerous permissions , and if your app is installed on a device that runs Android 6.0 (API level 23) or higher, you must request the dangerous permissions at runtime by following the steps in this guide. If you don't declare any dangerous permissions, or if your app is installed on a device that runs Android 5.1 (API level 22) or lower, the permissions are automatically granted, and you don't need to complete any of the remaining steps on this page.
Before you declare and request runtime permissions in your app, evaluate whether your app needs to do so . You can fulfill many use cases in your app, such as taking photos, pausing media playback, and displaying relevant ads, without needing to declare any permissions. If you conclude that your app needs to declare and request runtime permissions, complete these steps: runtime permission your app requires. If so, your app can access the private user data. If not, continue to the next step.
You must check whether you have a permission every time you perform an operation that requires that permission. Check whether your app should show a rationale to the user, explaining why your app needs the user to grant a particular runtime permission. If the system determines that your app shouldn't show a rationale, continue to the next step directly, without showing a UI element.
If the system determines that your app should show a rationale, however, present the rationale to the user in a UI element. In this rationale, clearly explain what data your app is trying to access and what benefits the app can provide to the user if they grant the runtime permission. After the user acknowledges the rationale, continue to the next step. Request the runtime permission your app requires to access the private user data. The system displays a runtime permission prompt, such as the one shown on the permissions overview page .
If the user granted the permission to your app, you can access the private user data. If the user denied the permission instead, gracefully degrade your app experience so that it provides functionality to the user without the information that's protected by that permission. To check whether the user already granted your app a particular permission, pass that permission into the ContextCompat.checkSelfPermission() method.
This method returns either PERMISSION_GRANTED or PERMISSION_DENIED , depending on whether your app has the permission.
The permissions dialog shown by the system when you call requestPermissions() says what permission your app wants, but doesn't say why. In some cases, the user might find that puzzling. It is a good idea to explain to the user why your app wants the permissions before you call requestPermissions() . Research shows that users are much more comfortable with permissions requests if they know why the app needs them, such as whether the permission is needed to support a core feature of the app or for advertising. As a result, if you are only using a fraction of the API calls that fall under a permission group, explicitly list which of those permissions you are using and why. For example, if you are only using coarse location, let the user know this in your app description or in help articles about your app.
Under certain conditions, it is also helpful to let users know about sensitive data access in real time. For example, if you are accessing the camera or microphone, consider letting the user know by using a notification icon somewhere in your app, or in the notification tray (if the application is running in the background), so it doesn't seem like you are collecting data surreptitiously.
If you need to request a permission for a feature to work, but the reason is not clear to the user, find a way to explain why you need sensitive permissions. If the ContextCompat.checkSelfPermission() method returns PERMISSION_DENIED , call shouldShowRequestPermissionRationale() . If this method returns true , show an educational UI to the user. In this UI, describe why the feature that the user wants to enable needs a particular permission.
Additionally, if your app requests a permission related to location, microphone, or camera, consider explaining why your app needs access to this information. After the user views an educational UI, or the return value of shouldShowRequestPermissionRationale() indicates that you don't need to show an educational UI, request the permission. Users see a system permission dialog, where they can choose whether to grant a particular permission to your app.
To do this, use the RequestPermission contract, included in an AndroidX library, where you allow the system to manage the permission request code for you. Because using the RequestPermission contract simplifies your logic, it is the recommended solution when possible. However, if needed you can also manage a request code yourself as part of the permission request and include this request code in your permission callback logic.
To allow the system to manage the request code that is associated with a permissions request, add dependencies on the following libraries in your module's build.gradle file: The following steps show how to use the RequestPermission contract. The process is nearly the same for the RequestMultiplePermissions contract.
In your activity or fragment's initialization logic, pass in an implementation of ActivityResultCallback into a call to registerForActivityResult() . The ActivityResultCallback defines how your app handles the user's response to the permission request. Keep a reference to the return value of registerForActivityResult() , which is of type ActivityResultLauncher .
To display the system permissions dialog when necessary, call the launch() method on the instance of ActivityResultLauncher that you saved in the previous step. 4. Practical Deployment, Analysis & Case Studies After launch() is called, the system permissions dialog appears. When the user makes a choice, the system asynchronously invokes your implementation of ActivityResultCallback , which you defined in the previous step.
Note: Your app cannot customize the dialog that appears when you call launch() . To provide more information or context to the user, change your app's UI so that it's easier for users to understand why a feature in your app needs a particular permission. For example, you might change the text in the button that enables the feature. Also, the text in the system permission dialog references the permission group associated with the permission that you requested. This permission grouping is designed for system ease-of-use, and your app shouldn't rely on permissions being within or outside of a specific permission group.
And this code snippet demonstrates the recommended process to check for a permission and to request a permission from the user when necessary: As an alternative to allowing the system to manage the permission request code , you can manage the permission request code yourself. To do so, include the request code in a call to requestPermissions() .
The following code snippet demonstrates how to request a permission using a request code: After the user responds to the system permissions dialog, the system then invokes your app's implementation of onRequestPermissionsResult() . The system passes in the user response to the permission dialog, as well as the request code that you defined, as shown in the following code snippet: When you request location permissions, follow the same best practices as for any other runtime permission . One important difference when it comes to location permissions is that the system includes multiple permissions related to location. Which permissions you request, and how you request them, depend on the location requirements for your app's use case.
If your app contains a feature that shares or receives location information only once, or for a defined amount of time, then that feature requires foreground location access. Some examples include the following: The system considers your app to be using foreground location if a feature of your app accesses the device's current location in one of the following situations: Your app is running a foreground service. When a foreground service is running, the system raises user awareness by showing a persistent notification. Your app retains access when it is placed in the background, such as when the user presses the Home button on their device or turns their device's display off.
On Android 10 (API level 29) and higher, you must declare a foreground service type of location , as shown in the following code snippet. On earlier versions of Android, we recommend that you declare this foreground service type. You declare a need for foreground location when your app requests either the ACCESS_COARSE_LOCATION permission or the ACCESS_FINE_LOCATION permission, as shown in the following snippet: An app requires background location access if a feature within the app constantly shares location with other users or uses the Geofencing API . Several examples include the following: The system considers your app to be using background location if it accesses the device's current location in any situation other than the ones described in the foreground location section. The background location accuracy is the same as the foreground location accuracy , which depends on the location permissions that your app declares.
On Android 10 (API level 29) and higher, you must declare the ACCESS_BACKGROUND_LOCATION permission in your app's manifest to request background location access at runtime. On earlier versions of Android, when your app receives foreground location access, it automatically receives background location access as well. If the user denies a permission request, your app must help them understand the implications of denying the permission. In particular, your app must make users aware of the features that don't work because of the missing permission. When you do so, keep the following best practices in mind: Guide the user's attention. Highlight a specific part of your app's UI where there is limited functionality because your app doesn't have the necessary permission. Examples of what you can do include the following: Be specific. Don't display a generic message. Instead, make clear which features are unavailable because your app doesn't have the necessary permission.
Don't block the user interface. In other words, don't display a full-screen warning message that prevents users from continuing to use your app at all. Accept the user’s preference: While it is okay to communicate to users how their functionality is being impacted by lack of access to the requested permissions, they should not feel pressured to change their mind. Letting a user know that they aren’t getting full feature access when it is appropriate (such as when attempting to use a part of the app blocked without the permission) is important, but persistent nagging to reconsider is not respectful of their choice.
Following these guidelines can help ensure that users feel empowered to manage access to their private data in a way that aligns with their values. Failing to gracefully accept highly visible user privacy decisions damages the trust and reputation not only of your app, but of the ecosystem as a whole. Additionally, if the user taps Deny for a specific permission more than once during your app's lifetime of installation on a device, the user will no longer see the system permissions dialog if your app requests that permission again. The user's action implies "don't ask again,” and is considered a permanent denial. It is very important to only prompt users for permissions when they need access to a specific feature; otherwise, you might inadvertently lose the ability to re-request permissions. In certain situations, the permission might be denied automatically, without the user taking any action. (A permission might be granted automatically as well.) It is important to not assume anything about automatic behavior. Each time your app needs to access functionality that requires a permission, check that your app is still granted that permission. To provide the best user experience when asking for app permissions, also see App permissions best practices .
To identify whether an app has been permanently denied permissions (for debugging and testing purposes), use the following command: Permissions that have been denied once by the user are flagged by USER_SET . Permissions that have been denied permanently by selecting Deny twice are flagged by USER_FIXED .
To make sure that testers see the request dialog during testing, reset these flags when you're done debugging your app. To do this, use the command: To view a complete list of Android app permissions, visit the permissions API reference page . Starting in Android 11 (API level 30), whenever your app requests a permission related to location, microphone, or camera, the user-facing permissions dialog contains an option called Only this time , as shown in figure 2. If the user selects this option in the dialog, your app is granted a temporary one-time permission .
Your app can then access the related data for a period of time that depends on your app's behavior and the user's actions: If the user revokes the one-time permission, such as in system settings, your app cannot access the data, regardless of whether you launched a foreground service. As with any permission, if the user revokes your app's one-time permission, your app's process terminates.
When the user next opens your app and a feature in your app requests access to location, microphone, or camera, the user is prompted for the permission again. Android provides several ways to reset unused runtime permissions to their default, denied state: On Android 13 (API level 33) and higher, you can remove your app's access to runtime permissions that your app no longer requires. When you update your app, perform this step so that users are more likely to understand why your app continues to request specific permissions. This knowledge helps build user trust in your app.
To remove access to a runtime permission, pass the name of that permission into revokeSelfPermissionOnKill() . To remove access to a group of runtime permissions at the same time, pass a collection of permission names into revokeSelfPermissionsOnKill() . The permission removal process happens asynchronously and kills all processes associated with your app's UID.
For the system to remove your app's access to the permissions, all processes tied to your app must be killed. When you call the API, the system determines when it is safe to kill these processes. Usually, the system waits until your app spends an extended period of time running in the background instead of the foreground. To inform the user that your app no longer requires access to specific runtime permissions, show a dialog the next time the user launches your app. This dialog can include the list of permissions.
If your app targets Android 11 (API level 30) or higher and is not used for a few months, the system protects user data by automatically resetting the sensitive runtime permissions that the user had granted your app. Learn more in the guide about app hibernation . Some apps depend on access to sensitive user information related to call logs and SMS messages. If you want to request the permissions specific to call logs and SMS messages and publish your app to the Play Store, you must prompt the user to set your app as the default handler for a core system function before requesting these runtime permissions.
For more information on default handlers, including guidance on showing a default handler prompt to users, see the guide about permissions used only in default handlers . To grant all runtime permissions automatically when you install an app on an emulator or test device, use the -g option for the adb shell install command, as demonstrated in the following code snippet: Content and code samples on this page are subject to the licenses described in the Content License . Java and OpenJDK are trademarks or registered trademarks of Oracle and/or its affiliates.
Welcome to the Skill Permission Analyzer, In today's digital era, mobile applications have become an integral part of our daily lives. However, concerns regarding user privacy have surged with the widespread use of these apps. Many applications collect vast amounts of user data without explicit consent, potentially compromising user privacy. 5. Performance Evaluation & Extended Technical Observations Our Android application serves as a solution to address these privacy concerns. It enables users to input the names of apps they use, fetches and analyzes the trackers and permissions requested by these apps, and provides insights into potential privacy risks associated with each app.
Note: Please be advised that this project constitutes a component of an academic endeavor for CSC 533: Privacy in a Digital Age, completed during the Fall semester of 2023. Skill Permission Analyzer: An Android application designed to fetch, analyze, and report on trackers and permissions requested by user-inputted app names. Safeguarding user privacy in the digital realm by offering insights into potential privacy risks associated with various mobile applications.
A web-based tool that analyzes Android application permissions and estimates the potential privacy and security risk associated with an app. Android applications often request permissions that allow access to sensitive device resources such as contacts, location, camera, microphone, storage, and SMS. This project analyzes an app's requested permissions and generates a risk assessment to help users better understand the potential privacy implications.
The project is powered by a large Android permissions dataset containing information from approximately 2.2 million Android applications collected from the Google Play Store. This repository does not include the dataset because it exceeds GitHub's file size limits. Dataset source: Android Permissions Dataset by Gautham Prakash. The dataset contains permission information for approximately 2.2 million Android applications collected from the Google Play Store.
This tool provides a permission-based risk estimate and should not be considered a complete security audit. Actual application behavior may differ from what permissions alone suggest. Android’s inter-process communication (IPC) mechanisms are fundamental to its architecture, enabling diverse applications and system services to interact seamlessly. From sharing data between apps to invoking system functionalities, IPC is ubiquitous. However, this interoperability comes with significant security implications. Misconfigured or insecure IPC endpoints are prime targets for malicious applications to trigger privilege escalation, perform unauthorized data access, or facilitate data leakage. This article delves into the intricacies of securing Android IPC, focusing on practical debugging techniques for permission denials and strategies to identify and prevent data leaks.
Understanding and securing IPC is not just a best practice; it’s a necessity for building robust and trustworthy Android applications. Binder services, often defined using Android Interface Definition Language (AIDL), are secured primarily through the android:permission attribute in the AndroidManifest.xml . When a client attempts to bind to or call a method on such a service, the system checks if the client possesses the declared permission.
Within the service implementation, developers can also use checkCallingPermission() or enforceCallingOrSelfPermission() for fine-grained, runtime checks based on specific method calls. Content Providers are secured using android:permission , android:readPermission , and android:writePermission attributes on the
A common pitfall is using android:grantUriPermissions="true" without careful management, as it allows temporary, fine-grained access to specific URIs, potentially bypassing broader permissions if not revoked properly. Broadcast Receivers can be protected by specifying android:permission on the
For intra-app communication, LocalBroadcastManager is preferred as it avoids global broadcasts and the need for manifest permissions. Permission denials typically manifest as SecurityException crashes or unexpected behavior where an IPC call fails silently. The primary tool for debugging is logcat .
When an IPC permission check fails, Android usually logs a SecurityException detailing the missing permission, the component attempting access, and the calling UID/PID. Connect your device and run: This output clearly indicates that the application (pid=1234, uid=5678) tried to read from MyContentProvider and lacked the com.example.READ_DATA permission.
Once you identify the component and the required permission from logcat , verify the component’s manifest configuration. The pm dump command provides detailed information about an installed package, including its declared permissions and exported components. This confirms the provider requires com.example.READ_DATA for reading. You’d then check the client app’s manifest (using pm dump on the client package) to ensure it declares
If manifest analysis doesn’t yield immediate answers, review the source code of both the provider and consumer applications. Data leaks via IPC typically occur when sensitive data is exposed to unauthorized applications due to lenient permissions or incorrect component export settings. A Content Provider declared with android:exported="true" but lacking any android:readPermission or android:writePermission will allow any application to access its data. This is a common source of sensitive data exposure.
Remedy: Always specify appropriate readPermission and writePermission . If the provider is only for internal use, set android:exported="false" . While useful for temporary access, misuse of grantUriPermissions="true" can allow an app to bypass explicit permissions. If an app receives a URI with granted permissions and then passes that URI to another untrusted app, a leak can occur.
Remedy: Use grantUriPermissions judiciously.
Always revoke permissions when no longer needed using revokeUriPermission() . Prefer explicit permission declarations.
Sending sensitive data via an implicit broadcast (i.e., not targeting a specific component) to a receiver that is exported="true" and lacks a strong android:permission allows any app listening for that action to receive the data. Binder services can also leak data if they return sensitive information without proper authorization checks, or if they lack input validation, potentially leading to denial-of-service or information disclosure through error messages.
Remedy: Implement robust input validation for all AIDL methods.
Perform authorization checks (e.g., checkCallingPermission() ) before returning sensitive data. Treat all IPC input as untrusted.
Securing Android IPC is a multifaceted challenge that demands careful attention to manifest declarations, permission enforcement, and robust coding practices. By systematically debugging permission denials using tools like logcat and pm dump , and by proactively identifying potential data leakage vectors, developers can significantly harden their applications against common IPC-related vulnerabilities. Adhering to the principle of least privilege and implementing strict validation and authorization checks are paramount to building secure and trustworthy Android ecosystems.
Are you researching mobile hardware properties, processor SoCs, GPU chipsets, or RAM configurations? Access our complete specs catalog to compare up to 5 devices side-by-side! Effective in 2026, to align with our trunk stable development model and ensure platform stability for the ecosystem, we will publish source code to AOSP in Q2 and Q4. For building and contributing to AOSP, use android-latest-release . The android-latest-release manifest branch will always reference the most recent release pushed to AOSP. For more information, see Changes to AOSP .
This section contains recommendations to ensure the security of apps on Android devices. Source code review can detect a broad range of security issues, including those identified in this document. Android strongly encourages both manual and automated source code review. Automated testing can help detect a broad range of security issues and should be performed regularly.
Vulnerability scanning can help ensure that pre-installed apps are free of known security vulnerabilities. Advanced detection can reduce the time and cost required with addressing these vulnerabilities and preventing risk to users and devices. It is important to ensure that the pre-installed apps on your device aren't Potentially Harmful Applications (PHAs). You are responsible for the behavior of all apps that are included on your devices. Prior to device launch, scan all pre-loaded apps for vulnerabilities.
For more information about PHAs and how Google is combating them in the Play store see the Google Play Protect developer documentation . Excessive permissions for pre-installed apps can create a security risk. Restrict pre-installed apps to the minimum necessary permissions and ensure they don't have access to unnecessary permissions or privileges. App permissions are described in the AndroidManifest.xml .
App signatures play an important role in device security and are used for permissions checks and software updates. When selecting a key to use for signing apps, it is important to consider whether an app is available only on a single device or common across multiple devices. Harvested Online Documentation & Reference Sources • https://developer.android.com/agents/skills/security/android-permissions-security/skill • https://source.android.com/docs/core/permissions/runtime_perms • https://developer.android.com/guide/topics/permissions/overview • https://github.com/chaitu135/privacy-intelligence-platform • https://github.com/azhanshoaib15/privacy-leakage-detector • https://developer.android.com/training/permissions/requesting • https://github.com/Akruti25/Skill-Permission-Analyzer • https://github.com/greeshg6/Andriod-Permission-Risk-Analyzer • https://androidmobiles.org/troubleshooting-android-ipc-security-debugging-permission-denials-and-data-leaks/ • https://source.android.com/docs/security/best-practices/app
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Android Runtime Permission Analyzer For Privacy Leakage.
[*] Metasploit Scan Running on Target Subnet for Android Runtime Permission Analyzer For Privacy Leakage... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |