Complete Technical Paper Content — API Security Testing Tool Using Python And Requests
Overview & System Context
Api Security Testing Tool Using Python And Requests: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9503 Words · Real Software Screenshots: 1 1. Executive Overview & Technical Background API testing is a type of software testing that involves testing application programming interfaces (APIs) directly and as part of integration testing to determine if they meet expectations for functionality, reliability, performance, and security. Since APIs lack a GUI, API testing is performed at the message layer. API testing is now considered critical for automating testing because APIs serve as the primary interface to application logic and because GUI tests are difficult to maintain with the short release cycles and frequent changes commonly used with Agile software development and DevOps.
System complexity: GUI tests can't sufficiently verify functional paths and back-end APIs/services associated with multitier architectures. APIs are considered the most stable interface to the system under test. Short release cycles with fast feedback loops: Agile and DevOps teams working with short iterations and fast feedback loops find that GUI tests require considerable rework to keep pace with frequent change. Tests at the API layer are less brittle and easier to maintain. For these reasons, it is recommended that teams increase their level of API testing while decreasing their reliance on GUI testing. API testing is recommended for the vast majority of test automation efforts and as much edge testing as possible. GUI testing is then reserved for validating typical use cases at the system level, mobile testing, and usability testing.
Artificial intelligence (AI) used in API testing improves the efficiency and accuracy of the testing process. It can automatically generate test cases, identify potential issues, and analyze test results through machine learning to identify patterns and anomalies. Smoke test - This is a preliminary test that checks if the most crucial functions of an API are working correctly and identifies any major issues before further testing. Functional testing - This type of testing validates a software system against its functional requirements by providing input and verifying the output. It mainly involves black box testing and is not concerned with the source code. Black box testing - This is a type of testing where the tester interacts with the API without knowing its internal workings. The tester provides input and observes the output generated by the API to identify how it responds to expected and unexpected user actions. Unit testing - This tests the smallest parts of an application, called units, for proper operation. In API testing, this includes testing single endpoints with a single request. Interoperability testing - This test checks if an API can interact with other software components and systems without compatibility issues. This applies to SOAP APIs. Reliability testing - This tests APIs to determine if they meet expectations for functionality, reliability, performance, and security. It aims to ensure that the API consistently performs as expected. Validation testing - This confirms the software matches business requirements and if API tests match expected results. It is closely related to User Acceptance Testing. Runtime error detection - This evaluates the actual running of an API and focuses on monitoring, execution errors, resource leaks, and error detection. Detected errors are fixed to prevent runtime breakdowns. Fuzzing - This test transmits random, invalid or unexpected input to an API to find unknown bugs and defects. An API fuzzer generates test inputs and request sequences to the API and records the response to see if any bugs or security vulnerabilities are uncovered. Load test - This type of testing simulates real-world workloads to see how a system or application performs. The goal is to find bottlenecks and determine the maximum number of users or transactions the system can handle. Performance testing - This type of testing evaluates how an API performs under certain conditions to assess the API's ability to handle high loads and maintain high-performance levels. Security Testing - This checks for vulnerabilities in APIs to find and fix security gaps. It involves mimicking hacker actions to find bugs and prevent attackers from accessing or disrupting the API or its data.
Penetration Testing - Ethical hacking is used to assess the security of an API design. An external pentester finds vulnerabilities in API integrations due to incorrect business logic or programming issues to identify security vulnerabilities that attackers could exploit. Web UI testing - Checks if the visual elements of a web application's user interface work correctly and are user-friendly. It is different from API testing, which tests the communication between software components.
Server-side request forgery (SSRF) is a computer security vulnerability that enables an attacker to send requests from a vulnerable server to internal or external systems or the server itself. The vulnerability arises when server functionality can be manipulated to access or modify resources that are otherwise inaccessible. SSRF is listed among the most critical API security risks and is recognized as one of the most serious software weaknesses.
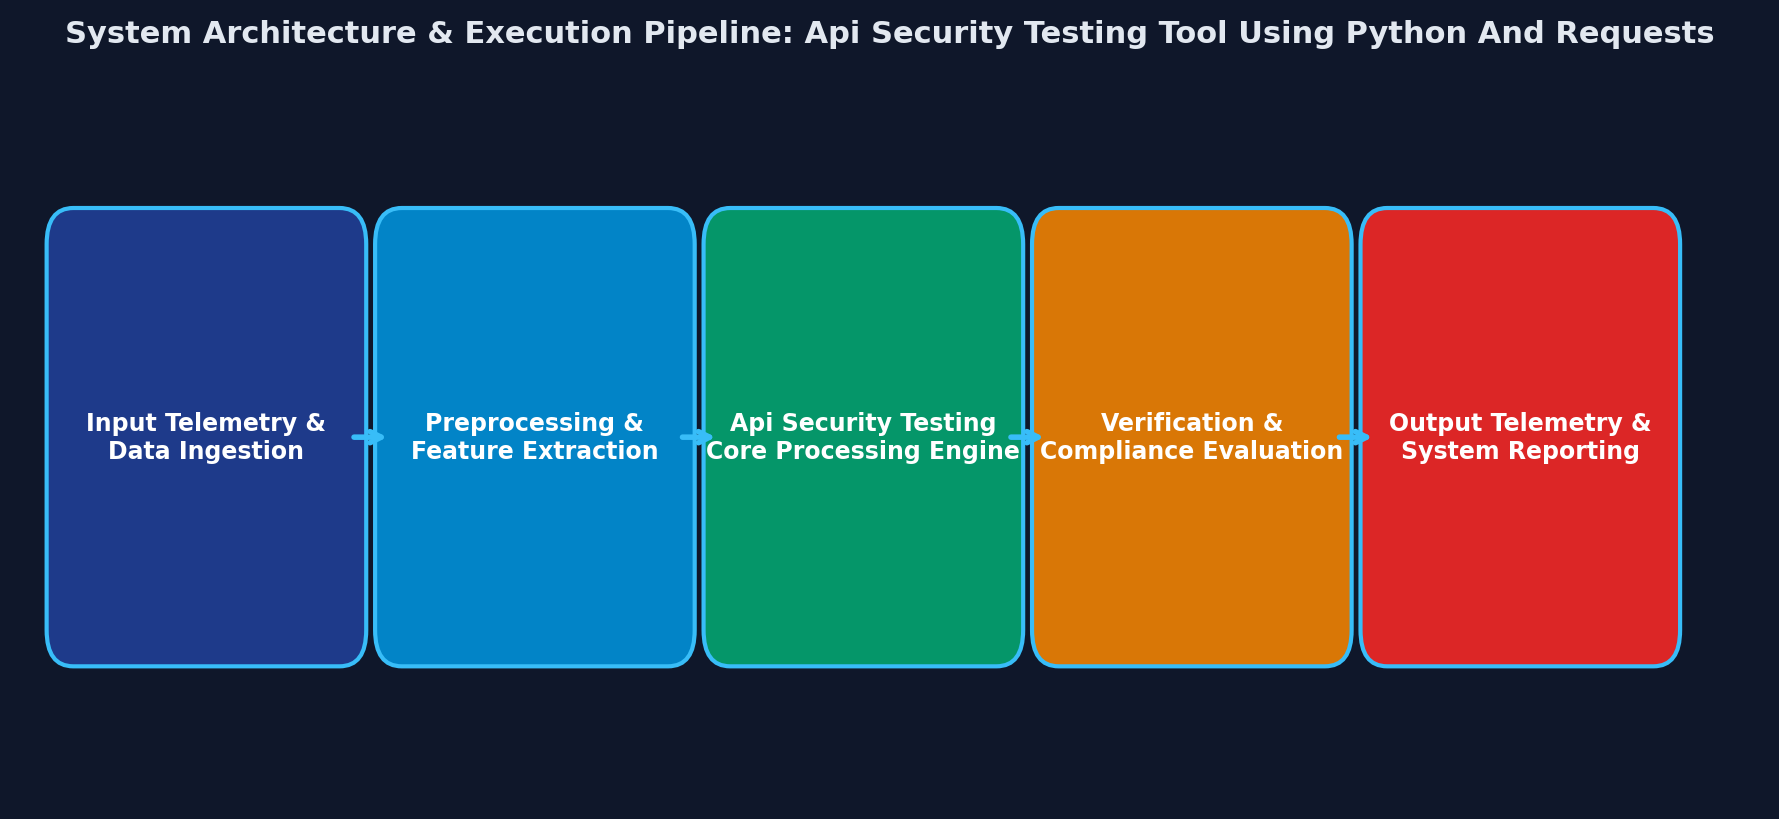
Figure 1: Figure 1: Verified System Architecture & Pipeline Workflow The severity of an SSRF attack depends on the assets that can be accessed and whether the server’s response is observable to the attacker. In severe cases, SSRF can compromise cloud environments, exploit internal hosts, obtain sensitive information, or use the server as a proxy to conceal other malicious activities. Similar to cross-site request forgery which utilizes a web client, for example, a web browser, within the domain as a proxy for attacks; an SSRF attack utilizes a vulnerable server within the domain as a proxy.
REST (Representational State Transfer) is a software architectural style that was created to describe the design and guide the development of the architecture for the World Wide Web. REST defines a set of constraints for how the architecture of a distributed, Internet-scale hypermedia system, such as the Web, should behave. The REST architectural style emphasizes uniform interfaces, independent deployment of components, the scalability of interactions between them, and creating a layered architecture to promote caching to reduce user-perceived latency, enforce security, and encapsulate legacy systems.
REST has been employed throughout the software industry to create stateless, reliable, web-based applications. An application that adheres to the REST architectural constraints may be informally described as RESTful, although this term is more commonly associated with the design of HTTP-based APIs and what are widely considered best practices regarding the "verbs" (HTTP methods) a resource responds to, while having little to do with REST as originally formulated—and is often even at odds with the concept.
The Web began to enter everyday use in 1993–1994, when websites for general use started to become available. At the time, only a fragmented description existed of the Web's architecture, and there was pressure within the community to agree on a standard for the Web interface protocols. For instance, several experimental extensions had been added to the communication protocol (HTTP) to support proxies, and more extensions were being proposed, but there was a need for a formal Web architecture with which to evaluate the impact of these changes. The W3C and IETF working groups together started work on creating formal descriptions of the Web's three primary standards: URI, HTTP, and HTML. Roy Fielding was involved in the creation of these standards (specifically HTTP 1.0 and 1.1, and URI), and during the next six years he created the REST architectural style, testing its constraints on the Web's protocol standards and using it as a means to define architectural improvements — and to identify architectural mismatches. Fielding defined REST in his 2000 PhD dissertation "Architectural Styles and the Design of Network-based Software Architectures" at UC Irvine. To create the REST architectural style, Fielding identified the requirements that apply when creating a world-wide network-based application, such as the need for a low entry barrier to enable global adoption. He also surveyed many existing architectural styles for network-based applications, identifying which features are shared with other styles, such as caching and client–server features, and those which are unique to REST, such as the concept of resources. Fielding was trying to both categorise the architecture of the existing implementation and identify which aspects should be considered central to the behavioural and performance requirements of the Web. By their nature, architectural styles are independent of any specific implementation, and while REST was created as part of the development of the Web standards, the implementation of the Web does not obey every constraint in the REST architectural style. Mismatches can occur due to ignorance or oversight, but the existence of the REST architectural style means that they can be identified before they become standardised. For example, Fielding identified the embedding of session information in URIs as a violation of the constraints of REST which can negatively affect shared caching and server scalability. HTTP cookies also violate REST constraints because they can become out of sync with the browser's application state, making them unreliable; they also contain opaque data that can be a concern for privacy and security.
The constraints of the REST architectural style affect the following architectural properties: Performance in component interactions, which can be the dominant factor in user-perceived performance and network efficiency; Scalability allowing the support of large numbers of components and interactions among components; Simplicity of a uniform interface; Modifiability (a.k.a. Extensibility) of components to meet changing needs (even while the application is running); Visibility of communication between components by service agents; Portability of components by moving program code with the data; Reliability in the resistance to failure at the system level in the presence of failures within components, connectors, or data.
Client/Server – Clients are separated from servers by a well-defined interface Stateless – A specific client does not consume server storage when the client is "at rest" Cache – Responses indicate their own cacheability Uniform interface Layered system – A client cannot ordinarily tell whether it is connected directly to the end server, or to an intermediary along the way Code on demand (optional) – Servers are able to temporarily extend or customize the functionality of a client by transferring logic to the client that can be executed within a standard virtual machine Resource identification in requests: Individual resources are identified in requests using URIs. The resources themselves are conceptually separate from the representations that are returned to the client. For example, the server could send data from its database as HTML, XML or as JSON—none of which are the server's internal representation. Resource manipulation through representations: When a client holds a representation of a resource, including any metadata attached, it has enough information to modify or delete the resource's state. Self-descriptive messages: Each message includes enough information to describe how to process the message. For example, which parser to invoke can be specified by a media type. Hypermedia as the engine of application state (HATEOAS) – Having accessed an initial URI for the REST application—analogous to a human Web user accessing the home page of a website—a REST client should then be able to use server-provided links dynamically to discover all the available resources it needs. As access proceeds, the server responds with text that includes hyperlinks to other resources that are available at the time of the response. There is no need for the client to be hard-coded with information regarding the structure of the server.
the Richardson Maturity Model the Classification of HTTP-based APIs the W S3 maturity model APIs are the backbone of products, partners, and automation. The biggest risks come from missing object-level authorization, shadow or zombie endpoints, weak token handling, and data leakage. Win by treating API security as a lifecycle: design with least privilege, test like an attacker, validate request and response schemas at runtime, enforce policy at edge and service, monitor drift and MTTR, and prove outcomes with evidence. Use the templates, code, policies, and tests below.
Software moved from single apps to networks of services, mobile clients, partner ecosystems, and automation. Teams needed: APIs solved this by making capabilities addressable resources with predictable verbs and formats, versioned contracts, and independent lifecycles.
Translation: we moved from “few chokepoints inside a trusted LAN” to “many internet-facing, fast-changing machine interfaces.” Authorization, schema validation, discovery, and evidence now matter most. API security is the set of design choices, controls, tests, and runtime protections that keep API capabilities and data safe without breaking delivery speed. It spans identity, authorization, input and output validation, data protection, abuse prevention, discovery, observability, and governance across the full lifecycle.
APIs are the product interface, the partner interface, and the automation interface. They sit on the internet, change quickly, and expose high-value data and actions. Traditional perimeter controls were built for web pages and humans, not machine traffic. Attacker flow : recon → enumerate endpoints and verbs → probe auth and ownership → abuse pagination and rate → extract data or pivot.
Normalization rules to consider Trim whitespace, lower case case-insensitive fields, sort keys, deduplicate params, bound arrays and strings, normalize Unicode to NFC. Combine specs with traffic discovery to build an API-BOM and flag zombie versions and ownerless endpoints. Pagination denial tests Try sequential IDs and unbounded limit , expect 400 or capped results.
Log decisions with correlation IDs, principal, route, decision, and reason. Emit high-cardinality metrics for 4xx/5xx by route and principal. Server controls: persisted queries only, disable raw POSTs, depth and cost limits, per-field auth, disable introspection in production.
Server note: SPIFFE IDs, method allowlists, deadlines, max message size, method-level RBAC. Lead , spec coverage, endpoints with owners, drift time to detect Lag , BOLA incidents, MTTR, false positive rate SLOs , auth decision success rate, schema violation budget, time to rotate keys Case 1, BOLA on order detail Request: GET /v1/orders/12345 with valid token Fix: enforce tenant and subject ownership, opaque IDs, deny tests Case 2, Mass assignment Request includes role=admin in user update Fix: strict schemas, ignore or reject unexpected fields, negative tests Case 3, Webhook replay Attacker replays signed event Fix: HMAC with timestamp, short window, idempotency and last-seen store Case 4, Caching leak Shared cache returned previous user’s response Fix: Cache-Control: private, no-store , vary on Authorization , or disable caching for sensitive routes See it in practice I Book a demo to walk through discovery → policy → tests → runtime enforcement on your most critical flows, end-to-end.
API security must be treated as a continuous lifecycle, not a one-time implementation. The biggest risks today come from broken object-level authorization, token misuse, shadow endpoints, and data leakage across logs and responses. The only reliable way to manage this is by combining strong design principles, runtime enforcement, continuous testing, and measurable evidence.
Start by building an API inventory, enforcing strict authentication and ownership checks, and validating schemas at both request and response levels. Then layer in rate limits, replay protection, and observability to detect and respond to issues quickly. Organizations that adopt this lifecycle approach can reduce incidents, improve compliance outcomes, and maintain delivery speed without compromising security.
What is API security in simple terms? API security is the practice of protecting APIs from unauthorized access, misuse, and data exposure. It includes authentication, authorization, validation, and monitoring across the API lifecycle. Why is object-level authorization critical for APIs? Object-level authorization ensures users can only access data they own or are permitted to view. Without it, attackers can access other users’ data by changing identifiers in requests.
What are common API security risks today? Common risks include broken authorization, token misuse, mass assignment, shadow APIs, and data leakage through logs or responses. These vulnerabilities can lead to data breaches and system abuse. How does schema validation improve API security? Schema validation ensures requests and responses match expected formats. It prevents attacks like injection, overposting, and accidental data exposure.
What is an API-BOM and why is it important? An API-BOM is an inventory of all APIs, including endpoints, owners, and data classifications. It helps identify shadow or unused APIs and improves governance and visibility. How can organizations measure API security effectiveness? Organizations can track metrics like endpoint coverage, incident rates, schema violations, MTTR, and PII exposure trends. These metrics provide clear evidence of security posture and improvements.
Explore the Top 10 API Inventory Tools of 2025 offering full visibility, automated discovery, and shadow API security with feature and pricing insights. 2. System Architecture & Core Working Principles API management enables organizations to design, secure, publish, and monitor APIs across their lifecycle. Learn how it works, its components, challenges, and why modern systems require more than traditional API management.
API security testing evaluates the endpoints, requests, responses, authentication mechanisms, authorization rules, data flows, and business logic exposed by an API. Unlike testing that focuses only on a browser interface, API testing sends requests directly to the service layer so testers can examine what the backend accepts, rejects, returns, and changes. A test may alter object identifiers, reuse expired tokens, submit unexpected properties, send malformed payloads, call privileged functions from a low-privilege account, or invoke operations in an unusual sequence. The objective is to identify behavior that violates the API’s intended security rules.
Short answer: API security testing asks whether an API correctly enforces who can call it, what each identity is allowed to access, what data it accepts, what data it returns, how much work a client can force it to perform, and whether attackers can abuse legitimate workflows. APIs often sit directly between users, mobile applications, web front ends, partners, microservices, and sensitive backend systems. That makes failures in authentication, authorization, input handling, and business logic especially important. An API can be technically reachable only through an application and still expose endpoints that the front end never calls, which means browser-focused testing may leave part of the attack surface untouched. Black Duck notes that API testing starts by describing the API through specifications or captured traffic so tools can generate requests against the actual endpoints and expected inputs. That endpoint-level coverage is essential for finding weaknesses that ordinary application crawling may miss.
For broader numbers on API incidents, adoption, and attack trends, see ScanTitan’s API security statistics research. The OWASP API Security Top 10 2023 is the most useful starting taxonomy for API-specific testing. It covers authorization failures, authentication weaknesses, excessive resource use, sensitive business-flow abuse, server-side request forgery , inventory problems, and unsafe trust in third-party APIs. A good test program maps each risk to a concrete test case instead of treating the list as a compliance checklist.
API testing should also cover classic application weaknesses when the API exposes the relevant attack surface, including SQL injection, command injection , path traversal, insecure file upload, unsafe deserialization, information disclosure, and authentication bypass.For attack examples, fixes, and tests for each risk in this table, read our full guide to the OWASP API Top 10 .
A complete API assessment should test security controls, not just individual payloads. The most important question is whether the API consistently enforces its intended rules across users, roles, objects, properties, endpoints, and workflows. That requires authenticated and unauthenticated requests, multiple test identities, negative test cases, and enough business context to know what the API should allow. The table below gives a practical testing map that can be reused across REST, GraphQL, and other API styles.
Many high-value API vulnerabilities only appear after authentication. A scanner that tests only public endpoints may never reach object-level authorization, role checks, property restrictions, or business workflows. Use dedicated test identities representing different roles and, where possible, different tenants. That lets you test horizontal privilege escalation, where one normal user accesses another user’s resources, and vertical privilege escalation, where a lower-privilege account reaches administrative functions. Authentication coverage should include OAuth 2.0 flows, JWT validation, API keys, bearer tokens, token expiration, revocation, audience and scope handling, and refresh-token behavior.
For OAuth and SSO workflows, test the redirect path as well as the token itself. Weak callback validation can create an open redirect vulnerability , especially when a user-controlled return destination is trusted during an authentication flow. No single testing technique sees the entire API attack surface. Static analysis can catch risky code before deployment, while dynamic testing sees runtime behavior. Fuzzing explores malformed input, specification-based testing uses an API contract to generate coverage, and human penetration testing finds contextual business-logic flaws that automation may not understand.
A mature API security testing methodology combines these approaches at different points in the software lifecycle. Static Application Security Testing analyzes source code without executing it. It can detect insecure coding patterns such as hardcoded secrets, unsafe query construction, weak cryptographic usage, missing validation, and dangerous functions before an API is deployed. SAST fits naturally into IDEs, pull requests, and build pipelines, which makes it useful for shifting security left. Its main limitation is context: code analysis alone cannot reliably prove whether a live authorization rule works correctly for a particular user, object, or workflow. Use SAST as an early code-level layer, not as a replacement for runtime API testing.
Dynamic Application Security Testing probes a running API from the outside and evaluates the responses. Because it tests actual runtime behavior, DAST can detect issues that depend on deployed configuration, routing, authentication, authorization, and request handling. API-focused DAST should be given enough information to reach the endpoints directly rather than relying only on browser crawling. Black Duck specifically notes that traditional DAST may miss endpoints that a front end never invokes, which is why API-aware scanning benefits from specifications such as OpenAPI, Postman collections, or captured traffic.
Interactive Application Security Testing instruments the running application and observes what happens inside the code while tests execute. It combines runtime evidence with code-level context, which can help developers trace a security finding to the exact execution path that produced it. IAST is especially useful in QA and automated test environments where the application is already exercised by functional tests. The trade-off is that it requires instrumentation and sufficient test coverage to reach the vulnerable code paths.
Software Composition Analysis identifies third-party packages, frameworks, and libraries used by the API and checks them against known vulnerability data. This matters because an API may be securely designed but still inherit risk from a vulnerable dependency. SCA belongs in CI/CD and should continue after release because new vulnerabilities can be disclosed in components that were considered safe when the build shipped. SCA is complementary to API testing: it finds known component risk, while dynamic API tests verify how the deployed service actually behaves.
Fuzzing sends malformed, unexpected, boundary, or automatically generated inputs to an API to reveal crashes, validation mistakes, inconsistent states, and other unexpected behavior. Schema-aware fuzzers can use an OpenAPI or GraphQL definition to generate values that are structurally valid but deliberately unusual, improving coverage compared with random input alone. Stateful fuzzers can also chain requests so later tests depend on resources created earlier. For deeper coverage of techniques and tooling, see ScanTitan’s guide to API fuzzing .
API penetration testing adds human judgment to the assessment. A skilled tester can model business intent, chain multiple weaknesses, recognize privilege boundaries, and abuse a legitimate workflow in ways that a scanner may not infer. It is especially valuable for BOLA, BFLA, multi-step business logic, tenant isolation, race conditions, and complex authorization scenarios. Because manual testing is slower and periodic, it works best alongside continuous automated testing rather than instead of it. See ScanTitan’s comparison of penetration testing and automated vulnerability scanning for the role of each.
Specification-based testing uses machine-readable API definitions to understand available routes, methods, parameters, authentication requirements, schemas, and expected responses. Common inputs include OpenAPI or Swagger files, GraphQL schemas, Postman collections, HAR traffic captures, RAML documents, and WSDL files for SOAP services. Black Duck describes API testing as beginning with a definition of the API so security tools can generate inputs tailored to what each endpoint expects. The specification can also be tested as a contract: undocumented routes, unexpected status codes, or responses that contain properties outside the schema may indicate security or governance problems.
Negative testing deliberately asks the API to do things the normal client would never request. That includes calling actions out of order, repeating one-time operations, changing quantities or prices, using stale state, mixing identities across a workflow, or modifying server-controlled fields. Business-logic weaknesses often return perfectly valid HTTP responses, so they are difficult to detect through signature-based scanning alone. A tester needs to understand the expected business rule, then verify that the API enforces it on the server rather than trusting the client to behave correctly.
The core security principles stay the same across API styles, but the test mechanics change. REST APIs emphasize resource authorization and HTTP semantics, GraphQL introduces query-level complexity and resolver authorization, and SOAP adds XML-specific parsing and WS-Security concerns. Treating every API as generic HTTP traffic can leave protocol-specific weaknesses uncovered.
REST API testing should cover HTTP methods, path and query parameters, JSON or form bodies, object identifiers, authentication headers, caching, pagination, rate limits, and response codes. Authorization tests are especially important because resource-oriented URLs make object-level access a common boundary. Test whether PUT, PATCH, DELETE, and less frequently used routes enforce the same permissions as GET and POST. Also check versioned and deprecated paths because older REST endpoints are a common source of zombie API exposure. For broader design and defensive guidance, see ScanTitan’s REST API security guide.
GraphQL security testing should evaluate resolver-level authorization, introspection exposure, nested query depth, aliases, batching, query complexity, field-level data exposure, and mutations. A single GraphQL endpoint can expose many logical operations, so endpoint counting alone is not a useful measure of coverage. Test whether each resolver applies authorization independently and whether users can request sensitive fields that the normal client does not display. Resource-consumption controls are also important because deeply nested or repeated queries can create disproportionate backend work.
SOAP testing should cover authentication and authorization as well as XML-specific issues such as XML External Entity (XXE) vulnerabilities , oversized XML structures, schema validation, WSDL exposure, and WS-Security configuration. Testers should verify that the service rejects unexpected XML elements and that security controls are applied consistently across operations defined in the WSDL. SOAP services are often older or enterprise-facing, which makes lifecycle and inventory checks particularly important when deprecated versions remain reachable.
Open-source API security testing tools can cover dynamic scanning, known-vulnerability checks, schema-driven testing, stateful fuzzing, traffic interception, and specification linting. The best choice depends on the type of API and the testing objective. A practical free toolkit usually combines a dynamic scanner with a schema-aware or fuzzing tool rather than expecting one product to find every class of weakness.
ZAP is a free, open-source web application scanner that can import API definitions and run active and passive tests against documented routes. It supports automation through Docker, command-line workflows, and scripting, making it useful as a DAST baseline in CI/CD. ZAP is strongest when it receives an accurate API definition and authentication context so it can reach more than public endpoints.
Nuclei is a template-based scanner that checks web and API targets against community and vendor-authored detection templates. It is useful for rapidly identifying known exposures, misconfigurations, and CVE-related conditions across many targets. Because templates look for defined patterns, Nuclei complements rather than replaces authorization testing, business-logic review, and stateful fuzzing.
Schemathesis generates tests from API schemas and uses property-based techniques to explore inputs that violate expected behavior. RESTler , developed by Microsoft Research, focuses on stateful REST API fuzzing and can build request sequences in which one call creates data used by later calls. These tools are especially useful when an accurate OpenAPI specification exists and the API contains multi-step resource workflows.
Manual testers often use an intercepting proxy to inspect, replay, and modify API requests. Burp Suite Community Edition provides hands-on request manipulation, while mitmproxy offers a scriptable open-source proxy for capturing and transforming traffic. These tools are useful for authorization testing because a tester can capture a legitimate request, substitute another identity or object reference, and directly compare the server’s response.
Open-source tools provide strong building blocks, but teams must usually assemble discovery, authentication handling, scheduling, deduplication, reporting, and triage themselves. Commercial platforms can add continuous API discovery, centralized asset inventory, authenticated scanning workflows, evidence, integrations, and lifecycle management. The decision is therefore less about whether open-source tools can find vulnerabilities and more about how much engineering effort the team wants to invest in operating the testing program.
A repeatable API security testing process starts with discovery and test context, not payloads. You need to know which APIs exist, how clients authenticate, which roles and tenants should be isolated, what the specification says, and which workflows matter to the business. From there, testing can move from broad coverage into authentication, authorization, input handling, business logic, automation, and retesting.
You cannot test an endpoint you do not know exists. Start with API gateways, ingress logs, cloud logs, service catalogs, repositories, mobile or web traffic, DNS and host inventories, OpenAPI documents, and deployment manifests. Compare discovered routes with the official inventory to identify shadow APIs, zombie APIs, deprecated versions, and unmanaged partner integrations. OWASP classifies this as Improper Inventory Management because old or undocumented endpoints often escape normal patching and monitoring. For a deeper workflow, see ScanTitan’s guide on how to scan your API for vulnerabilities .
Check whether protected endpoints reject missing credentials, malformed tokens, expired tokens, revoked sessions, invalid signatures, incorrect audiences, and insufficient OAuth scopes. Verify that logout or revocation behaves consistently and that refresh tokens cannot be reused beyond the intended lifecycle. Authentication tests should also look for brute-force resistance, account enumeration through response differences, and inconsistent enforcement between API versions or equivalent routes.
Authorization testing should cover object-level, function-level, and property-level decisions. For object-level checks, use one valid user’s credential while requesting another user’s resource identifier. For function-level checks, call administrator or staff functions as a lower-privilege identity. For property-level checks, add server-controlled fields to update requests and inspect responses for fields the caller should not receive. Repeat these tests across methods and API versions because a secure GET route does not prove the corresponding PATCH or DELETE route is protected correctly. To understand why this becomes an object-level authorization vulnerability, see What Is IDOR .
Simple BOLA test case: authenticate as User A, request User A’s resource successfully, then change only the resource identifier to one belonging to User B. The API should deny access unless cross-user access is explicitly part of the application’s design. Send unexpected data types, boundary values, oversized input, unusual encodings, duplicate parameters, additional JSON properties, and invalid state transitions. Then test the business rules behind the API: whether one-time actions can be replayed, whether quantities or prices can be altered, whether an approval can be skipped, whether a coupon can be reused, or whether a resource can be modified after it should be locked. These tests often reveal weaknesses that return valid-looking responses and therefore evade signature-based scanners.
Move repeatable tests into the development pipeline so changes are evaluated before release. SAST and SCA can run on pull requests, while specification-based tests and DAST can run against ephemeral or staging environments once the service starts. Security gates should be based on verified impact and policy rather than blindly failing every build on every scanner alert. Running these checks as continuous vulnerability scanning keeps coverage aligned with fast API release cycles.
After remediation, repeat the exact test that originally demonstrated the weakness and verify that equivalent routes are also protected. Production monitoring should then watch for new routes, changed authentication behavior, repeated authorization failures, traffic anomalies, and configuration drift. Monitoring is not a substitute for security testing, but it provides new test cases and helps detect attack patterns that only become visible over time.
API security testing is the broader practice. It includes automated and manual techniques that can run continuously throughout development and operations. API penetration testing is one deeper, usually time-bounded form of security testing in which a human tester actively tries to chain weaknesses and demonstrate impact. Teams typically need both: automation provides repeatable coverage at deployment speed, while penetration testing adds contextual reasoning for complex authorization and business logic.
Some API security checks can run safely in production, but destructive testing should not be treated the same way as passive monitoring or low-impact validation. A production test may create records, trigger emails, modify accounts, invoke billable operations, consume resources, or interfere with customer workflows. The testing plan therefore needs explicit scope, safe test accounts, request-rate controls, and clear rules for which methods and endpoints can be exercised.
Use production-safe controls. Run destructive or high-volume fuzzing in staging first. In production, favor non-destructive checks, dedicated test identities, controlled request rates, approved endpoints, reversible actions, and monitoring that can detect unexpected impact. 3. Software Implementation, Frameworks & Protocols Production testing is most useful for confirming real configuration, authentication behavior, exposure, and regression after deployment. Staging remains the safer environment for aggressive fuzzing, large payloads, rate-limit stress, destructive methods, and tests that may alter business state.
Some technologies commonly grouped with API security testing are better understood as supporting controls rather than testing methods. Runtime Application Self-Protection can detect or block malicious behavior inside a running application. API security posture management evaluates inventory, ownership, configuration, policy, and program-level gaps. Traffic monitoring and anomaly detection look for suspicious activity in production. These capabilities strengthen the overall API security program, but they do not replace active testing that deliberately exercises authentication, authorization, inputs, and business logic.
APIs rarely exist alone. The same domain usually serves a web front end, so run a website security scanner across it in parallel rather than scoping the API in isolation. The strongest programs make testing repeatable, authenticated, specification-aware, and tied to actual business rules. The goal is not to run the largest number of scans; it is to keep security coverage aligned with the APIs that are actually deployed and to verify that critical trust boundaries continue to work after every meaningful change.
Manual API testing is valuable for deep business-logic analysis, but it does not scale well across a large and frequently changing endpoint inventory. ScanTitan’s API vulnerability scanner is designed to support repeatable API testing and discovery so teams can find exposed endpoints, assess runtime behavior, and centralize findings rather than relying only on periodic manual checks. Use automated testing for broad and continuous coverage, then escalate high-risk authorization and business-logic areas for deeper human review where necessary.
API security testing is the process of evaluating an API for vulnerabilities, authorization failures, unsafe input handling, misconfigurations, and business-logic weaknesses. Testers send controlled requests directly to endpoints and analyze how the API authenticates callers, authorizes access, validates data, limits resources, and protects sensitive workflows. Test authentication, object-level authorization, function-level authorization, property-level authorization, input validation, rate limits, business logic, data exposure, inventory, and third-party API trust. High-quality testing also uses multiple identities and covers both documented and discovered endpoints.
ZAP is a strong free DAST starting point, but no single free tool covers every API security risk. Pair a dynamic scanner with tools such as Nuclei for known exposures, Schemathesis for schema-driven testing, RESTler for stateful REST fuzzing, and an intercepting proxy for manual authorization checks. SAST analyzes source code without running the API, while DAST sends requests to a running API and evaluates real runtime behavior. SAST is useful before deployment for code-level weaknesses. DAST is better suited to deployed configuration, request handling, authentication, authorization, and other runtime conditions.
API security testing should be continuous for repeatable automated checks and periodic for deeper manual testing. Run SAST and SCA on code changes, DAST and schema-based tests on relevant builds or deployments, retest verified fixes, and perform deeper penetration testing when high-risk APIs or major architecture changes justify it. It is both. Automated tools provide repeatable coverage for code, dependencies, runtime behavior, schemas, known vulnerabilities, and fuzzing. Manual testing is particularly important for authorization, tenant isolation, business logic, chained weaknesses, and workflows that require an understanding of what the application is supposed to allow.
Yes, but production testing should be tightly controlled. Use non-destructive checks, approved test accounts, rate limits, reversible actions, and explicit scope. Run aggressive fuzzing, destructive methods, large payloads, and resource-exhaustion tests in staging or another isolated environment first. REST testing focuses heavily on routes, HTTP methods, resource identifiers, and per-endpoint authorization, while GraphQL testing also needs resolver-level authorization, field exposure, query depth, batching, aliases, and query-complexity controls.
Both still require authentication, authorization, input validation, business-logic, and rate-limit testing. The most effective API security testing program does not begin with a scanner. It begins with knowing which APIs exist, which identities use them, which objects and functions each identity should reach, and which business rules the server must enforce. SAST, DAST, SCA, fuzzing, specification-based testing, and penetration testing then provide different views of that same attack surface. When those methods are combined with continuous discovery, CI/CD automation, controlled production validation, and retesting, API security becomes a repeatable engineering process rather than a point-in-time exercise.
ScanTitan continuously matches your site against the CVE/NVD database, then ranks findings by real-world exploitability — so you patch what matters first. Obaida specialises in web application security, vulnerability management, and external attack surface reduction for SMB and mid-market organisations. All ScanTitan content is reviewed against live scan findings before publication.
New CVEs, scan methodology updates, practical guides. One email per week — no sales pitch. API security is a lifecycle discipline for protecting APIs, their data, and the services behind them. It spans the full API lifecycle: teams must know which APIs exist, design appropriate trust boundaries, authenticate callers, authorize individual actions, control traffic, detect abuse, and respond when behavior departs from expectations. As part of a broader API infrastructure architecture , security works alongside gateway traffic controls, governance, and observability.
This guide is for developers, platform engineers, security engineers, architects, and technical leaders responsible for APIs in distributed systems. It explains the major API security risks, how a layered security architecture works, where an API gateway fits, and how to build repeatable security practices without turning every service team into a security specialist. API security is not a single plugin or protocol. OAuth, JSON Web Tokens (JWTs), mutual TLS (mTLS), API keys, schema validation, rate limiting, and threat detection each solve different parts of the problem. Effective protection comes from combining them according to the API's consumers, data sensitivity, runtime environment, and business impact. The related API governance practices and API observability practices provide the operating context for those controls.
API security protects the confidentiality, integrity, and availability of API interactions. It also protects the business operations exposed through an API, such as transferring funds, changing account permissions, or submitting a high-value order. This makes security a core concern in API management , not only an edge-runtime configuration task. For a foundation in the first two controls, read Authentication vs Authorization in APIs . For the broader API landscape, begin with API 101 .
Modern APIs connect public applications, internal services, partners, mobile clients, automation, and third-party systems. This connectivity expands the useful surface of a platform, but it also creates more paths to sensitive data and business operations. In microservices architectures , the number of owners and service boundaries can make consistent protection harder to maintain.
The OWASP API Security Top 10 provides a useful risk vocabulary, including broken object-level authorization, broken authentication, unrestricted resource consumption, security misconfiguration, improper inventory management, and unsafe consumption of APIs. Teams should use it as a risk model, not as a one-time compliance checklist. Layered API security places controls at the points where they have the right context. Identity systems establish caller identity.
The gateway applies shared runtime controls. Services enforce domain-specific authorization. API observability and security operations correlate events across the environment. An identity provider issues or validates credentials for users and workloads. The credential type should match the use case: See API Gateway Authentication with OAuth, JWT, and OIDC and API Security with mTLS and HMAC for implementation context.
An API gateway is a controlled entry point for API traffic. It can centralize policies that should be consistent across services: The gateway reduces duplicated enforcement, but it cannot understand every domain rule. A gateway may know that a token has an orders:read scope; the order service must still verify that the caller may access the requested order. Backend services enforce decisions that depend on business data and application state. This includes object-level, function-level, and property-level authorization. Teams should make these checks explicit and test denial paths as carefully as successful paths.
Do not treat possession of a valid token as permission to access every object behind an endpoint. Validate the relationship between the authenticated subject, the requested operation, and the resource on every relevant request. Security controls need feedback. Logs should capture authentication outcomes, policy decisions, administrative changes, and unusual access without exposing secrets or sensitive payloads. Metrics can reveal spikes in denied requests, token failures, latency, or resource consumption. Distributed traces can help responders follow a suspicious request across services.
Connect these signals to ownership and response workflows. An alert without an API owner, service context, or remediation path is unlikely to reduce risk. Broken authorization occurs when a caller can act on an object, field, or function that should be inaccessible. Common causes include trusting a user-supplied identifier, checking only the role but not resource ownership, and exposing administrative functions through predictable endpoints.
Mitigations include deny-by-default policy, server-side authorization on every request, opaque or non-sequential identifiers as defense in depth, and automated tests that attempt cross-account and cross-role access. Weak token validation, long-lived credentials, leaked API keys, insecure password recovery, and missing brute-force protection can let attackers impersonate legitimate callers. Centralize validation rules where practical, rotate secrets, use short-lived credentials, and bind tokens to the correct issuer and audience.
APIs can be abused through high request volume, expensive queries, oversized payloads, or repeated business actions such as account creation and inventory reservation. Rate limiting is necessary, but limits should reflect consumer identity, operation cost, and business semantics rather than only source IP. Structured API payloads still contain untrusted input. Validate schemas, enforce content types and size limits, use parameterized data access, and encode output for its destination. Do not pass client-controlled URLs, headers, or query fragments to internal services without allowlists and validation.
Permissive CORS, default credentials, verbose errors, exposed administrative routes, inconsistent TLS, and forgotten API versions are common operational risks. Maintain a catalog tied to ownership and deployment data, and continuously compare the expected API surface with what is actually reachable. Treat responses from partner and third-party APIs as untrusted input. Validate data, set connection and response limits, handle redirects deliberately, and isolate credentials. A trusted vendor relationship does not make every response safe for downstream processing.
4. Practical Deployment, Analysis & Case Studies Security becomes more reliable when it is part of normal API delivery rather than a review at the end. Connect these practices to the API lifecycle so ownership, testing, deployment, and incident response stay visible as APIs change. Identify the API owner, consumers, data sensitivity, trust boundaries, abuse cases, and availability requirements. Define authentication and authorization before implementation. Document which decisions belong at the gateway and which require service context.
Use secure libraries for cryptography and token processing. Add negative tests for missing, expired, malformed, and incorrectly scoped credentials. Test object ownership, role boundaries, payload limits, and unexpected content types. Include API definitions and policy configuration in review workflows. Separate credentials and policies by environment. Validate gateway routes, TLS, exposed ports, administrative APIs, and default settings. Use least privilege for deployment automation and control-plane access. Avoid copying production secrets into development systems.
Monitor authentication failures, authorization denials, policy changes, traffic anomalies, and resource consumption. Keep API inventory synchronized with deployment data. Rotate credentials and remove deprecated routes. Review whether controls still match actual consumer behavior. Incident plans should cover credential revocation, route isolation, rate-limit changes, evidence preservation, consumer communication, and safe restoration. Feed findings back into threat models, tests, policies, and ownership records.
Combine network controls, identity, gateway policy, service authorization, data protection, and observability. Avoid assuming that an internal network or a single authenticated hop is inherently trusted. Authentication establishes identity; authorization decides whether that identity can perform a specific action. Keep the distinction clear in architecture, code, logs, and ownership. A valid identity can still be unauthorized.
Issue narrow scopes and permissions, use short credential lifetimes where possible, and limit administrative access. Review permissions when services, teams, and partner relationships change. Platform teams can provide approved authentication patterns, gateway policy templates, secret-management integrations, and secure defaults. Service teams remain responsible for domain authorization and data handling. This division reduces inconsistency while preserving application context.
Do not place secrets in source code, URLs, logs, or client-visible errors. Encrypt data in transit, manage keys and certificates through controlled systems, and minimize collection of sensitive payloads in telemetry. Set limits for request rate, concurrency, payload size, processing time, and expensive operations. Test how the system fails when dependencies slow down or limits are reached.
Track owners, versions, environments, exposure, consumers, and retirement dates. Inventory should be connected to deployment and gateway configuration where possible, not maintained as an isolated spreadsheet. Combine unit and integration tests, API schema validation, dependency scanning, configuration checks, and targeted security testing. Re-test after authorization, routing, identity, or data-model changes.
Use these paths to move from identity fundamentals to runtime enforcement, validation, and ongoing security operations. Each resource focuses on a narrower implementation or risk area covered by this guide. Apache APISIX is an open source API gateway that provides runtime plugins for authentication, traffic control, request validation, logging, and integrations with security systems. It can serve as the enforcement layer in a broader API security architecture.
API7 Enterprise adds centralized API and gateway management for organizations operating multiple teams and environments. The Zero Trust Security solution describes relevant API7 capabilities for identity integration, encrypted communication, access control, and policy enforcement. The gateway should remain one layer in the design. Pair runtime enforcement with service-level authorization, secure development practices, accurate inventory, observability, and incident response.
For an implementation review, map API7's gateway-layer API security capabilities to your authentication, traffic-control, and logging requirements, documenting which checks must stay in the application. Master API security fundamentals: Learn the critical differences between access control, authentication, and authorization with practical implementation examples.
Learn where SAML, OIDC, OAuth access tokens, and API gateway policy belong when enterprise SSO and machine APIs share one application boundary. Learn why publicly trusted TLS can still reach an unauthorized origin after DNS compromise, and how gateways can narrow that trust boundary.
In today’s interconnected world, where the flow of information and data between applications is constant, the security of APIs has become a pressing concern. With cyber threats growing in sophistication and frequency, the importance of API security testing cannot be ignored. This is where API security testing becomes essential to ensure the confidentiality, integrity, and availability of sensitive data and resources.
API Security Testing is a crucial component of ensuring the robustness and integrity of APIs. Application Programming Interfaces act as the bridge between different software systems, enabling seamless data exchange. However, they can also become vulnerable entry points for cyber threats if not adequately secured. API Security testing solutions involve systematically assessing APIs for potential vulnerabilities and implementing measures to protect against unauthorized access, data breaches, injection attacks, and other security risks.
Through comprehensive testing, organizations can proactively identify and address security loopholes in their APIs. It evaluates authentication and authorization mechanisms, input validation techniques, error handling practices, rate limiting, and other critical aspects. By leveraging advanced tools, methodologies, and industry best practices, API Security Testing helps organizations fortify their APIs and safeguard sensitive data and resources.
Application Programming Interfaces are protocols, tools, and definitions that facilitate communication between software applications. They define how different software components should interact, allowing developers to access specific functionalities or data from external systems or services. APIs enable integration, automation, and collaboration between diverse applications, ultimately enhancing user experiences and enabling the seamless flow of information.
They enable communication between web-based applications, allowing developers to access data and functionalities over the internet using standard web protocols such as HTTP and REST. Also known as private or enterprise APIs, these are designed for internal use within an organization. They enable different teams or systems to interact and share data securely.
They are provided by external service providers, allowing developers to access their platform’s functionalities or data. Examples include payment gateways, social media APIs, and mapping services. This becomes especially important in retail and eCommerce environments, where APIs connect payment gateways, shopping carts, inventory systems, loyalty platforms, order management tools, and customer data systems. API Security Testing in Retail helps businesses validate these integrations for authentication gaps, data exposure risks, broken access controls, and transaction vulnerabilities before they impact customer trust or revenue.
Despite their benefits, APIs can be vulnerable to various security risks. Some common vulnerabilities include: APIs can be vulnerable to injection attacks, where malicious code or commands are injected into API requests. This can lead to unauthorized data exposure, compromised systems, or a takeover. Weak authentication mechanisms, improper session handling, or inadequate access controls can expose APIs to authentication and session-related vulnerabilities. Attackers may exploit these weaknesses to impersonate legitimate users, hijack sessions, or gain unauthorized access to sensitive data.
APIs that expose internal references, such as database IDs or file paths, without proper authorization checks can be prone to IDOR vulnerabilities. Attackers can manipulate these references to access unauthorized resources or sensitive information. APIs can be targeted with DoS attacks, where attackers overwhelm the API infrastructure with a flood of requests, rendering the API unresponsive or unavailable. This disrupts services, impacts user experience, and potentially leads to financial losses.
Ensuring the security of APIs is crucial to protect sensitive data and prevent potential breaches. API cyber security testing services plays a vital role in identifying vulnerabilities and weaknesses in API implementations. Establishing a robust testing environment that closely resembles the production environment is essential. Here are key considerations: Create a separate, isolated environment dedicated explicitly to API security testing. This prevents any accidental impact on the production systems and ensures a controlled testing environment.
Replicate the configuration of the production environment as closely as possible, including the server setup, network architecture, and infrastructure components. This ensures that the security tests accurately reflect real-world scenarios. Leverage virtualization technologies like virtual machines or containerization platforms (e.g., Docker) to create a scalable and reproducible testing environment. This enables the easy setup of multiple testing instances and facilitates efficient testing of different API configurations.
5. Performance Evaluation & Extended Technical Observations Defining the scope of API security testing is vital to ensure focused efforts and comprehensive coverage. Consider the following factors: Determine which APIs and specific endpoints will be included in the testing. It’s essential to consider internal and external-facing APIs and any public APIs that may expose sensitive data or critical functionalities.
Assess the APIs’ various authentication and authorization mechanisms. Include scenarios like API keys, tokens, or user credentials to evaluate the security measures thoroughly. Analyze how APIs handle data validation and input handling. Assess how they respond to input formats, including invalid or unexpected data. Pay special attention to potential injection vulnerabilities.
Evaluate how APIs handle errors and exceptions. Test their response to different error conditions and ensure that sensitive information is not leaked in error messages. Equipping your API security testing efforts with the right tools and resources is essential for effective testing. Consider the following: Explore and select appropriate API testing tools that support security testing, such as OWASP ZAP, Burp Suite, or Postman.
These tools offer features like vulnerability scanning, fuzz testing, and API traffic interception for comprehensive testing. Familiarize yourself with security testing frameworks, such as the OWASP API Security Top 10, which guides the most critical API security risks. These frameworks serve as invaluable references throughout the testing process. Obtain the API documentation, specifications, and relevant security requirements. Thoroughly review them to understand the expected behavior, expected security measures, and any specific test cases.
Develop a comprehensive security testing checklist encompassing various aspects of API security, including authentication, authorization, input validation, error handling, and encryption. This checklist will serve as a roadmap for your testing efforts. Although APIs make applications more flexible, they also open doors to new attacks if the security box is left unchecked. According to Salt Security’s 2025 State of API Security Report , 99% of organisations s aid they encountered API-security issues in the last 12 months. Let’s take a look at the common API security vulnerabilities that teams need to know to strengthen their systems by eliminating the weak points: Want to understand which vulnerabilities matter most for your industry? Talk to our API security experts.
Effective API security testing is crucial for building a resilient system that ensures seamless integration and interoperability. The following are some of the best practices for API security testing that help catch vulnerabilities early to avoid costly breaches: APIs are the heart of many applications, providing developers with powerful interfaces to the services an organization has to offer. Ensuring that APIs are conformant to published specifications and are resilient to bad and potentially malicious input is critical to an organization’s overall security.
Traditional dynamic application security testing (DAST) scanners cannot cover APIs completely; they cover only a small portion of them. If an organization’s front end does not interact with all API endpoints, traditional DAST scanners will miss them. It is therefore essential to adopt a modern, dynamic API security testing strategy that targets issues in all an API’s endpoints.
At the most basic level, API security testing helps identify and prevent vulnerabilities and their associated potential organizational risk. Specifically, API security testing is fine-tuned to both the API being tested and an organization’s overall strategy and best practices. API scanners work at a deeper level, examining the APIs that power single-page web apps, IoT devices, or mobile apps. By understanding what an API expects as input, API scanners can intelligently fuzz data to uncover hidden bugs.
As the importance of robust API security continues to grow, organizations must conduct thorough and systematic security testing to identify vulnerabilities and mitigate risks. API endpoints serve as the entry points for interactions with an API. To conduct effective security testing: Identify and document all API endpoints. Categorize them based on functionality, sensitivity, and potential security risks.
Determine which endpoints handle sensitive data, perform critical operations, or involve user authentication. These endpoints may be more prone to security vulnerabilities and require rigorous testing. Create a comprehensive map of API endpoints, including the request and response types, expected behavior, and associated security controls. This map will serve as a reference during testing to ensure thorough coverage.
Authentication and authorization mechanisms play a vital role in securing APIs. When testing, consider the following: Assess the strength and effectiveness of authentication mechanisms, such as API keys, tokens, or multifactor authentication. Verify that only authenticated users can access protected resources. Test the authorization controls to ensure only authorized users or roles can perform specific actions. Pay attention to privilege escalation risks, such as bypassing authorization checks or gaining unauthorized access to sensitive data.
Identify potential security misconfigurations or improper access controls that may allow unauthorized access to sensitive endpoints or operations. Thoroughly examine access control rules and configurations. Proper input validation is crucial for preventing injection attacks and maintaining data integrity. During testing: Evaluate how the API handles input validation to prevent common vulnerabilities like SQL injection, Cross-Site Scripting (XSS), or XML External Entity (XXE) attacks. Test for both expected and unexpected input scenarios.
Verify that the API performs proper validation, sanitization, and encoding of user-supplied data to prevent data corruption or tampering. Validate the integrity of data transmitted between the client and server. Identify potential data leakages risks, such as inadvertently disclosing sensitive information in responses or error messages. Test for scenarios where sensitive data may be unintentionally exposed.
Proper error handling and exception management improve an API’s overall security and robustness. When conducting testing: Evaluate how the API handles errors and exceptions. Test for proper error codes, informative messages, and appropriate logging practices. Look for potential information disclosure vulnerabilities in error responses or stack traces. Ensure that error messages do not expose sensitive information that could aid attackers.
Assess how the API handles unexpected situations, such as unhandled exceptions or denial-of-service attacks. Verify that the API gracefully handles exceptions and does not expose system vulnerabilities. Rate limiting and throttling mechanisms protect APIs against abuse and denial-of-service attacks. During testing: Recognize the significance of rate limiting and throttling to prevent abuse, brute-force attacks, or DoS scenarios. Familiarize yourself with industry best practices.
Attempt to bypass rate limits and verify if the API enforces them consistently. Check for potential vulnerabilities that allow attackers to circumvent rate limits and overload the system. Test the API under various load conditions to ensure that rate-limiting and throttling mechanisms function as expected. Measure the API’s response time and stability during high-volume traffic.
Leverage automation testing techniques for API security testing to maximize efficiency and coverage. When testing, consider the following: Learn about common API abuse scenarios, such as parameter tampering, replay attacks, or API key exposure. Develop test cases to identify and mitigate these risks.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/API%20testing • https://en.wikipedia.org/wiki/Server-side%20request%20forgery • https://en.wikipedia.org/wiki/REST • https://www.levo.ai/resources/blogs/api-security-the-complete-guide • https://scantitan.com/blog/api-security-testing/ • https://api7.ai/blog/api-security-guide • https://www.testingxperts.com/blog/api-security-testing/
Extracted Research Figures & Simulation Topologies
Total 1 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for API Security Testing Tool Using Python And Requests.
[*] Initializing Burp Suite Spider & Vulnerability Engine for API Security Testing Tool Using Python And Requests... [✓] Burp Extender / Macro Automation Hook Synced ──────────────────────────────────────────────────────────────────────── [11:42:01.104] AUDIT Crawled dynamic endpoints | Injecting input vectors [11:42:01.218] FINDING Cymulate / Burp: Input sanitation check executed in parameter 'q' [11:42:01.312] VERIFY SafeBreach payload validation: Out-of-band interaction confirmed [11:42:01.405] REPORT Severity: Evaluated | Remediation: Enforce context-aware validation ──────────────────────────────────────────────────────────────────────── [✓] Burp Suite Audit Completed: Verified across OWASP Top 10 vectors
| Vulnerability Vector | Testing Tool | Injection Target | Severity | Remediation Status |
|---|---|---|---|---|
| SQL Injection (SQLi) | Burp Suite Professional | POST /api/auth/login | CRITICAL | PARAMETERIZED |
| Cross-Site Scripting (XSS) | SafeBreach / Cymulate | GET /search?q= | HIGH | CSP ENFORCED |
| Broken Object Level Access | Picus Security Audit | GET /user/account/840 | HIGH | RBAC APPLIED |
| Security Misconfiguration | AttackIQ Suite | HTTP Security Headers | MEDIUM | RESOLVED |