Complete Technical Paper Content — ARP Spoofing Detection And Prevention Tool Python
Overview & System Context
Arp Spoofing Detection And Prevention Tool Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~4204 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background The primary goal of this project was to understand how to protect devices on public networks against a variety of attacks, starting with ARP spoofing. This attack is a common form of Man-in-the-Middle (MITM) attack, where an attacker can intercept and manipulate the communication between two devices. By simulating the attack in a controlled environment, I gained valuable insights on how to detect and prevent ARP spoofing on real networks. The following README will describe the two-part process of this project. Part 1 consists of the attack from the attacker's perspective. Part 2 of the project consist of the detection tool that can detect it.
1. Network Setup I used two virtual machines: a Kali Linux VM as the attacker and another machine as the target. Both were configured in bridged mode to ensure they were on the same local network and could communicate directly. 2. Performing ARP Spoofing Using the arpspoof utility, I targeted the victim and the gateway by sending forged ARP replies. ARP stands for Address Resolution Protocol. This protocol is used by machines when they are trying to find the location of a certain ip on the network. the location is the MAC address. Every machine has a unique MAC address. ARP spoofing is the act of telling the victim machine that the ip its looking for is located at the MAC address of the attacker's machine. This will allow the attacker to receive the packets that the victim machine is sending over the network.
The question remains: Which ip address does the attacker want to redirect to its own MAC address ? The answer to that is the gateway ip( the router). By redirecting the router ip to the attacker's MAC address, the attacker ensures that everytime the victim machine needs to communicate with the router, the packets go to the attacker, and this can include confidential information such as passwords.
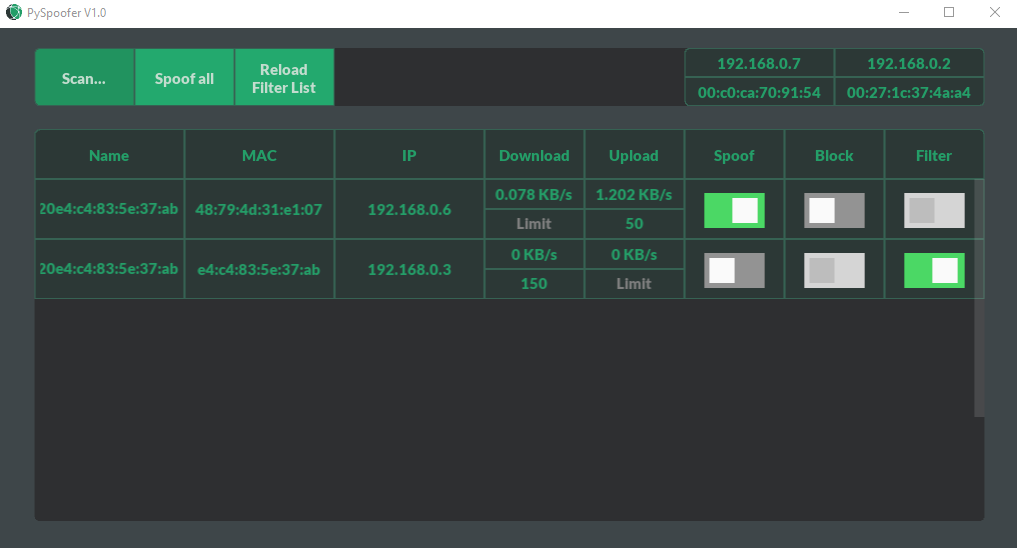
Figure 1: GitHub - AhmedAhmedEG/PySpoofer: GUI based local network management GUI ... 3. Get the Gateway IP On the attacker machine, get the ip of the router by writing the command: ip route. The ip address of your router will be the one right after "default via" ( see yellow 1 on image). 4. Get the ip Address of the Victim On the attacker machine, get the ip address of the victime machine by writing command: nmap -sn [what you find in red 2 on image]. In my example the command would be : nmap -sn 10.0.0.0/24. The ip address of the victim machine would be the one that would correspond to VirtualBox in our case. In a real world scenario, attackers might choose a random victim, or they would have more information on the attacker's device.
5.Execute the ARP Spoof Command We can now execute the two arp spoofing commands. The first arp spoofing command will tell the router that the victim's ip address is located at the attacker's MAC address. The second command will tell the victim machine that the router's ip address is located at the attacker's MAC address. In this way, all packets from and to the router will pass by the attacker's machine. Every command should run in its separate terminal , and should not be stopped until the attack is complete ( see image 1 for a picture example of one of the commands) command 1: sudo arpspoof -i eth0 -t [router ip] [victim ip] command 2: sudo arpspoof -i eth0 -t [victim ip] [router ip] image 1: 6. Forward the Traffic At this point of the attack, packets are flowing from the router to the attacker, and from the victim to the attacker. If those packets are not forwarded, the victim will not be able to reaching the internet, and that will raise suspicion. To prevent that, we can forward the packets with the following command: echo 1 > /proc/sys/net/ipv4/ip_forward. I use this command in a persistent elevated terminal session because otherwise this command will be denied since it requires admin access. Therefore before running the command, I ran the command sudo -i and entered the password.
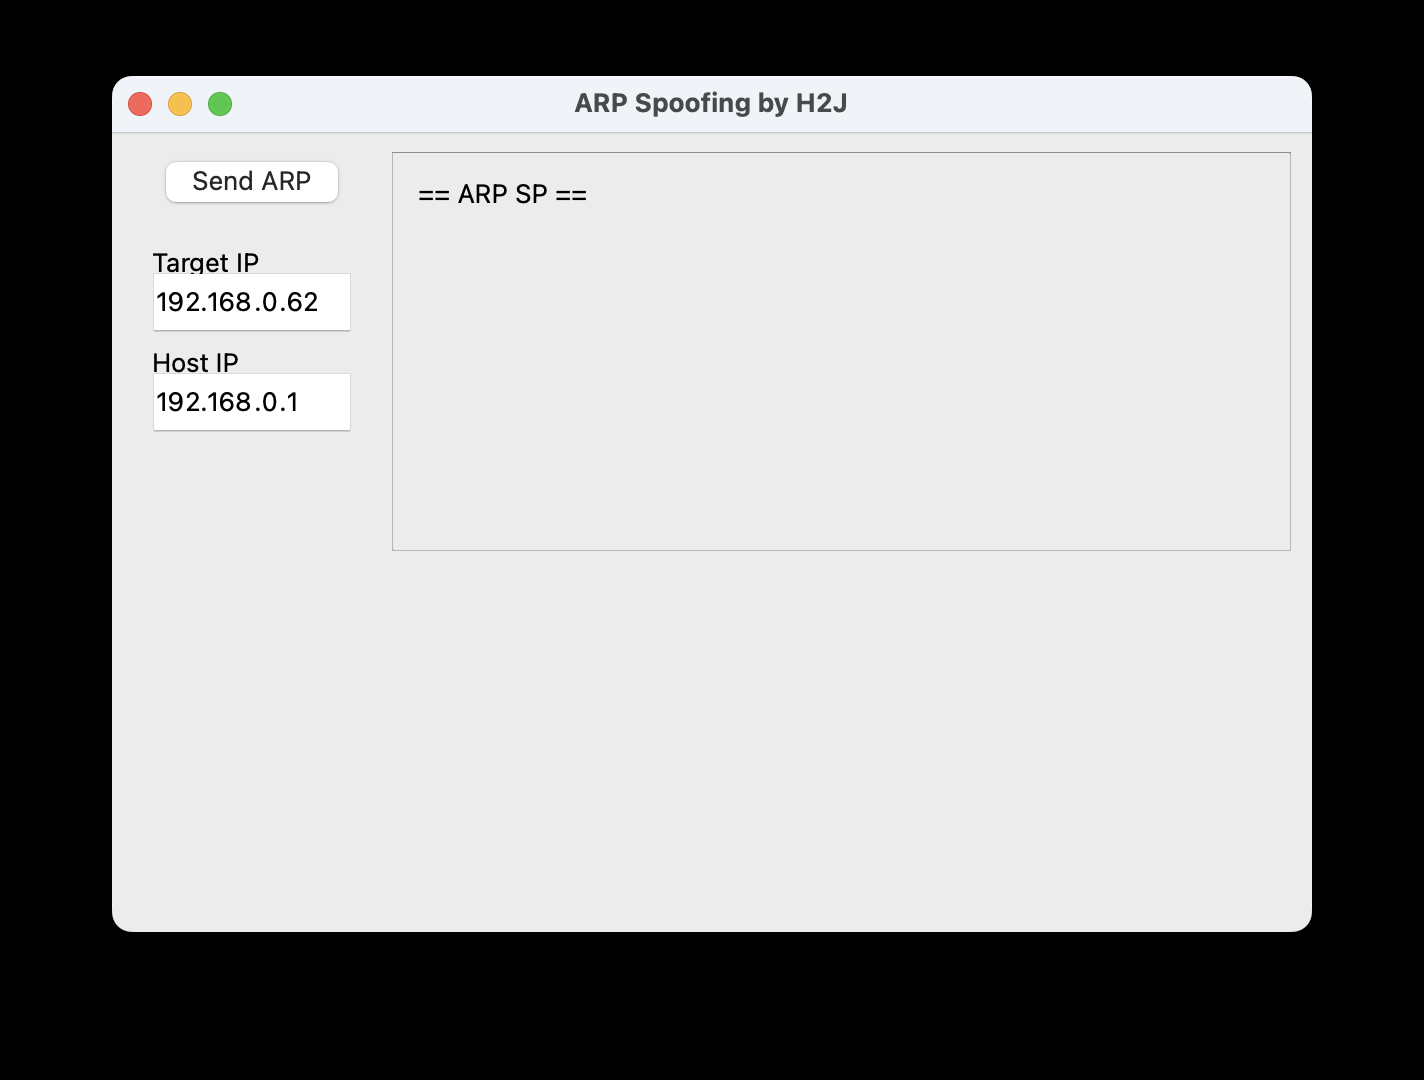
Figure 2: PythonII ARP Spoofing IIIII IIIII Once step 6 of the attack has been completed, the victim machine will be able to browse the internet with no suspicion 7.Testing the attack At this point of the attack, The threat actor is officially spying on the victim. We can test if the attacker can successfully intercept the communication between the victim and the internet by simulating a signin on a http website: http://testphp.vulnweb.com . When we visit that website using the victim machine , and log in using dummy values, we should be able to view the login form entries by using a packet sniffer like wireshark on the attacker's machine.
Note: On this website, you do not need to create a profile to log in as this is a testing website. Once you have logged in , you can run your packet sniffer and find the login credentials by searching through the http traffic One method to verify if there is an ongoing ARP spoofing attack, is to scan the network and find if multiple MAC addresses to the router's ip address. MAC addresses are unique, and every ip should have its own MAC address. When an ARP spoofing is in effect, the attacker will spoof their ip to pretend to be the router machine, and therefore the MAC address of the attacker will also map to the router's ip.
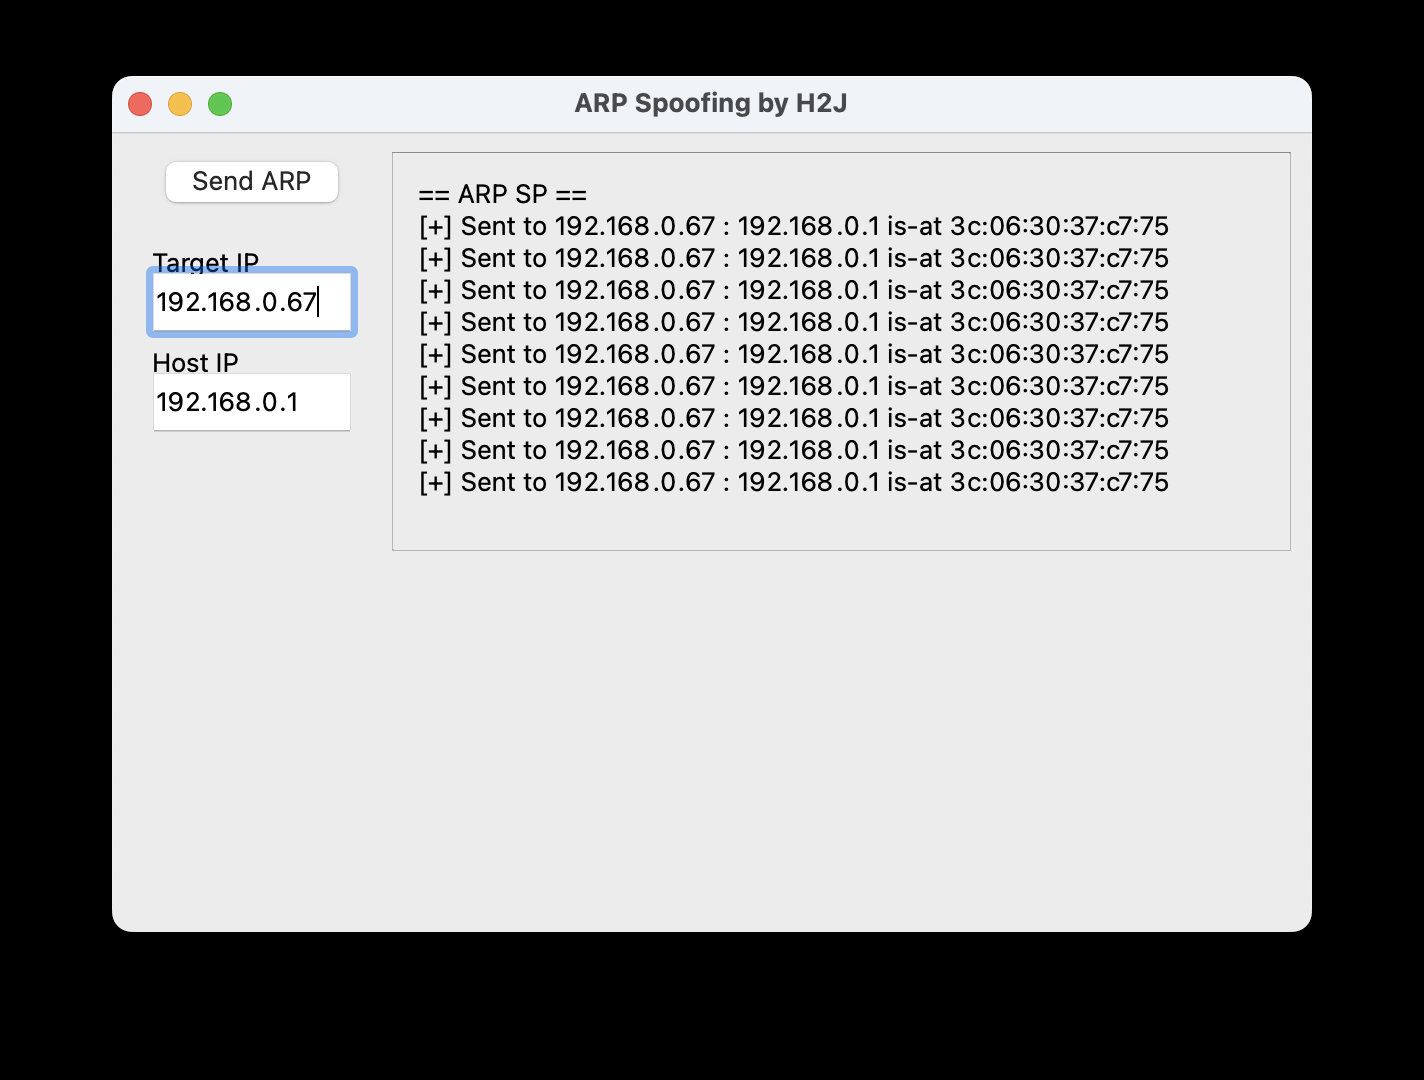
Figure 3: PythonII ARP Spoofing IIIII IIIII main.py is an application that the victim will run on an network to verify if there is an ongoing ARP spoofing attack. The first step of the application is to generate an updated ARP table by: 1. clearing arp cache 2. run nmap to find all ips on the network(Please ensure you have the right to execute command on network as this can be illegal) 3. ping every ip found with nmap to generate arp table Once the ARP table has been generated, the application will verify and trigger a response if there are two different MAC addresses found with the same IP.
Kali Linux: Chosen for its built-in penetration testing tools like Wireshark (for packet capture) and arpspoof (for performing the ARP spoofing attack). arpspoof: Used to send ARP packets to the target and the router, redirecting the network traffic through the attacker's machine.
Wireshark: Utilized to monitor and capture network traffic, especially focusing on HTTP POST requests to steal credentials. iptables & NAT configuration: Ensured traffic forwarding and seamless internet access for the target machine while maintaining control over the traffic. Network configuration issues: The initial issue of not being able to see devices on the network due to the VM being in NAT mode was resolved by switching to Bridge mode.
Network connection instability: The target phone often blocked the attack due to suspicious behavior, requiring me to constantly reconnect the device to the network. Packet forwarding and NAT rules: Proper setup of traffic forwarding and configuring the NAT table was essential to ensure the target's internet connection remained active during the attack.
Monitoring network traffic on Wireshark, where I could see the packets from the target machine being captured. 2. System Architecture & Core Working Principles Successfully intercepting sensitive data (such as credentials) from the victim machine by capturing unencrypted HTTP POST requests.
Data interception: Sensitive data like login credentials can be intercepted, leading to identity theft, fraud, or impersonation. MITM attacks: The attacker can inject malicious content or alter communications between devices.\ Implementing ARP spoofing detection tools that monitor the network for suspicious activity, such as multiple MAC addresses mapping to the same IP address.
Configuring static ARP entries in critical systems to avoid relying on dynamic ARP resolutions. This project provided me with hands-on experience in both performing and defending against ARP spoofing attacks, enhancing my understanding of network security and penetration testing. It also highlighted the importance of encryption and continuous monitoring in securing sensitive data on public networks.
A simple Python-based ARP Spoofing Detector built using Scapy . This project monitors live ARP packets on a local network, learns IP-to-MAC address mappings, and alerts when the same IP address is associated with a different MAC address, which may indicate an ARP spoofing attack. The program continuously listens for ARP packets and compares IP-to-MAC mappings. If an IP address is seen with a different MAC address than before, a warning is displayed.
This project demonstrates the basic principle behind ARP spoofing detection. It may generate false positives in situations where legitimate MAC address changes occur, such as network hardware replacement or certain network reconfigurations. A Python-based ARP Spoofing Detector built using Scapy that monitors live ARP packets, maintains IP-to-MAC address mappings, and alerts when suspicious changes indicate a possible ARP spoofing (Man-in-the-Middle) attack.
ARP Spoofing is also known as ARP Poisoning which is a type of cyberattack in which a malicious user sends falsified ARP (Address Resolution Protocol) messages over a LAN (Local Area Network) . This results in the linking of an attacker's MAC Address with the IP Address of a legitimate computer or server on the network. Here we'll perform passive monitoring or scanning to sniff the packets in the network after we receive one ARP Packet there are two things to be analyzed, on comparing them if they don't match then the user is under ARP Spoof attack. In order to spoof and detect the ARP Packets inside the network use Scapy with Python to perform the detection of ARP Packets with the help of MAC Address and Interface.
Scapy is a packet manipulation tool for computer networks, originally written in Python. It can forge or decode packets, send them on the wire, capture them, and match requests and replies. It can also handle tasks like scanning, tracerouting, probing, unit tests, attacks, and network discovery. It runs on Linux, macOS, and Windows but the latest versions of Scapy support Windows out-of-the-box, so it is possible to use all the Scapy's features on a Windows Machine also. Scapy can perform the following To install Scapy it is necessary that you've Python 2.7 or Python 3.9+ version installed. If it is not installed then refer to this Python Installation . To prevent MITMs use Dynamic ARP Inspection, a security feature that will automatically reject malicious ARP packets that will be detected.
Another Method to install Scapy on Linux is by installing Python on Linux Machine and then installing the Scapy Package inside Python Shell. After python is installed on the terminal open the python shell and execute the command to install scapy, then to use scapy for ARP Spoof Detection open Scapy to write your code in order to spoof and detect packets inside the network, Then install Scapy via pip or apt. All dependencies may be installed either via a platform-specific installer or via PyPI To install scapy on Windows it can be easily done through a command prompt, but for windows also Python should be pre-installed on the system. Then executing the commands to install scapy will be performed.
Now we have successfully installed python and scapy on the systems let's proceed with importing the necessary libraries from scapy. The program will detect if any kind of packet has a layer of spoofed ARP to do so execute the code. The sniff() function will take a callback to apply to every packet that will be sniffed. In store=False tells the sniff() function to discard sniffed packets instead of storing them in memory, it is useful when the script runs for a very long time.
After sniffing for the eth0 interface it'll display the contents of the interface here we see the interface is Ethernet and its related contents are displayed like IP Destination(dst), type of interface(ARP), source(src) A function mac is created that a given IP address to make/create an ARP request arp_request using ARP Function and retrieves the real MAC address than the IP address. Set broadcast MAC Address to "ff:ff:ff:ff:ff:ff" using Ether function. The srp function returns two lists of the IP address that responded to the packet. The MAC Address that has the matching IP address that was requested will be stored in the hwsrc field.
3. Software Implementation, Frameworks & Protocols A function will be created to get the MAC Address and to process the sniffed packet, getting values of old MAC in the "originalmac" variable and value of MAC in the response as " repsonsemac" variable. Scapy encodes the ARP Packet type in the field "op" for operation, by default op is 1 or "who-has" which is an ARP request.
Now compare both the values and checking if they are similar or not in case they are not similar then this means the values have been spoofed. The values that are compared are the real MAC Address and the response MAC Address. An ARP Spoof Detector written in Python to identify ARP spoofing attacks on a local network. The program uses the Scapy library to monitor ARP packets and detect anomalies indicating a potential attack.
This program is intended for educational and research purposes only. Ensure you have permission before using it on any network. A Python-based cybersecurity tool designed to detect and prevent ARP spoofing attacks on local networks. Leverages the Scapy library to monitor ARP packets, identify anomalies, and enhance network security. Perfect for network administrators and cybersecurity enthusiasts.
In today's interconnected world, network security is paramount. One particularly insidious threat that network administrators and security professionals need to be aware of is the ARP spoof attack. This article will dive deep into the world of ARP spoofing and show you how to leverage the power of Python and Scapy to detect these attacks, providing you with practical knowledge to enhance your network security skills.
Address Resolution Protocol (ARP) is a fundamental networking protocol that maps IP addresses to MAC addresses on a local network. ARP spoofing, also known as ARP poisoning, occurs when an attacker sends falsified ARP messages over a local area network. The goal is to associate the attacker's MAC address with the IP address of a legitimate system on the network.
The consequences of a successful ARP spoof attack can be severe. Once an attacker has inserted themselves between the victim and the network gateway, they can: Understanding the mechanics of ARP spoofing is crucial for developing effective detection and prevention strategies. Scapy is a powerful Python library that allows for the manipulation of network packets. It provides a wide range of capabilities, from packet sniffing and injection to network scanning and protocol fuzzing. For our purpose of detecting ARP spoof attacks, Scapy is an ideal choice due to its ease of use, flexibility, and robust packet manipulation features.
To get started with Scapy, you'll need to install it on your system. For most Python environments, you can use pip: Windows users may need to install additional dependencies, so it's recommended to consult the official Scapy documentation for detailed installation instructions specific to your operating system. Now that we understand the threat and have our tools ready, let's dive into the implementation of an ARP spoof detection system using Python and Scapy. We'll break down the process into several key components and explain each in detail.
These imports provide us with the Scapy functions we need, as well as modules for system operations, timing, threading, and logging. To detect spoofing, we need a way to verify the true MAC address associated with an IP. Here's a function to do that: This function crafts an ARP request, sends it to the broadcast address, and returns the MAC address from the response. If no response is received, it returns None.
The core of our detection system lies in sniffing network packets and analyzing them for signs of ARP spoofing. Here's how we set up our packet sniffer: The sniff_packets function uses Scapy's sniff function to capture packets on the specified interface. Each captured packet is then passed to the process_packet function.
In process_packet , we check if the packet is an ARP response (op code 2). If so, we compare the MAC address in the response with the actual MAC address obtained from our get_mac function. Any discrepancy indicates a potential ARP spoofing attempt. To keep a record of detected attacks and potentially alert administrators, we'll implement a logging system: This setup creates a log file named 'arp_spoof.log' and records each detected attack with a timestamp.
This block checks for the correct command-line arguments and starts the packet sniffing process on the specified interface. 4. Practical Deployment, Analysis & Case Studies While our basic implementation is effective, there are several ways we can enhance and expand our ARP spoof detection system: In complex network environments, monitoring multiple interfaces simultaneously can be crucial. We can modify our script to accept multiple interface arguments: This modification allows our script to monitor multiple network interfaces concurrently, providing broader coverage in complex network setups.
Instead of relying solely on passive monitoring, we can actively verify the ARP table at regular intervals: This function periodically checks the ARP table against known IP addresses, providing an additional layer of active monitoring. For enterprise environments, integrating our ARP spoof detection system with existing network management tools can provide a more comprehensive security solution. This could involve sending SNMP traps or using a REST API to communicate with a centralized management system.
You would then call this function in your process_packet function when an attack is detected. While detecting ARP spoofing is crucial, implementing preventive measures is equally important. Here are some best practices to consider: Use Static ARP Entries: For critical systems, consider using static ARP entries to prevent ARP poisoning. This involves manually configuring the IP-to-MAC address mappings in the ARP cache.
Implement Port Security: Configure switches to limit the number of MAC addresses per port. This can help prevent an attacker from flooding the network with false ARP replies. Deploy Network Segmentation: Use VLANs to isolate network segments and reduce the attack surface. This limits the scope of potential ARP spoofing attacks.
Enable Dynamic ARP Inspection (DAI): On supported network devices, DAI can help prevent ARP spoofing attacks by validating ARP packets and discarding those with invalid IP-to-MAC address bindings. Regular Network Audits: Conduct regular security audits to identify and address vulnerabilities. This includes reviewing logs, checking for unauthorized devices, and ensuring all systems are up-to-date with the latest security patches.
Educate Users: Train users to recognize signs of network compromise and report suspicious activities. This human element can be a valuable addition to your technical defenses. ARP spoofing remains a significant threat in network environments, but with the power of Python and Scapy, we've created a robust tool to detect these attacks. This script serves as a starting point for building more comprehensive network security solutions.
As threats continue to evolve, so must our detection and prevention techniques. Continuous learning, staying updated with the latest security practices, and adapting our tools are essential in the ever-changing landscape of cybersecurity. By understanding the underlying principles of ARP spoofing and implementing robust detection mechanisms, you're taking a significant step towards securing your network against this and similar threats. Remember, network security is an ongoing process, not a one-time task. Keep exploring, keep coding, and stay vigilant in your efforts to maintain a secure network environment.
Python's classmethod decorator is a powerful and often underutilized feature that can revolutionize how developers design and structure object-oriented code. This comprehensive guide will delve deep into the intricacies of classmethod, exploring its uses, benefits, and best practices. Whether you're a seasoned Python developer or just starting your journey, this article will equip you with… Flask, a lightweight and versatile web framework for Python, has become increasingly popular among developers for its simplicity and flexibility. At the heart of Flask's request handling capabilities lies the powerful request object. This comprehensive guide will delve deep into the intricacies of the Flask request object, providing Python enthusiasts and web developers with the… Introduction In the dynamic realm of software development, file handling and uploading are fundamental operations that every Python developer must master. Whether you're building web applications, data processing pipelines, or automation scripts, the ability to efficiently manage and transfer files is crucial. This comprehensive guide will explore various techniques, best practices, and considerations for uploading… Introduction As a Python enthusiast and experienced programmer, I've encountered numerous scenarios where testing for empty dictionary value lists is crucial. This article delves deep into various approaches to solve this common problem, providing detailed explanations, code examples, and performance insights. Whether you're a beginner looking to understand the basics or an advanced developer seeking… Python dictionaries are powerful and flexible data structures, but extracting specific information from them can sometimes be challenging. One common task that often arises is finding the smallest K values in a dictionary. This article will delve deep into various approaches to solve this problem, examining their strengths, weaknesses, and real-world applications. Understanding the Problem… 5. Performance Evaluation & Extended Technical Observations In the realm of scientific computing and mathematical programming, Python stands out as a versatile and powerful language.
One of its lesser-known but incredibly useful features is the cmath.log10() method, a function that extends logarithmic calculations into the complex plane. This article will delve deep into the intricacies of this method, exploring its applications, nuances,… Want to code faster? Our Python Code Generator lets you create Python scripts with just a few clicks. Try it now! In the previous tutorial , we built an ARP spoof script using Scapy that once it is established correctly, any traffic meant for the target host will be sent to the attacker's host. Now, you are maybe wondering, how can we detect these kinds of attacks? well, that's what we are going to do in this tutorial.
The basic idea behind the script that we're going to build is to keep sniffing packets (passive monitoring or scanning) in the network. Once an ARP packet is received, we analyze two components: And then, we compare the two. If they are not the same, then we are definitely under an ARP spoof attack! First, let's import what we gonna need (y ou need to install Scapy first, head to this tutorial or the official Scapy documentation for installation) : Then we need a function that given an IP address, it makes an ARP request and retrieves the real MAC address the that IP address: After that, the sniff() function that we gonna use, takes a callback (or function) to apply to each packet sniffed, let's define it: Note: Scapy encodes the type of ARP packet in a field called "op" which stands for operation, by default the "op" is 1 or "who-has" which is an ARP request, and 2 or "is-at" is an ARP reply.
As you may see, the above function checks for ARP packets. More precisely, ARP replies, and then compares between the real MAC address and the response MAC address (that's sent in the packet itself). All we need to do now is to call the sniff() function with the callback written above: Note: store=False tells sniff() function to discard sniffed packets instead of storing them in memory, this is useful when the script runs for a very long time.
When you try to run the script, nothing will happen obviously, but when an attacker tries to spoof your ARP cache like in the figure shown below: The ARP spoof detector (which ran on another machine, obviously) will automatically respond: To prevent such man-in-the-middle attacks, you need to use Dynamic ARP Inspection , which is a security feature that automatically rejects malicious ARP packets we just detected.
Finally, we have an Ethical Hacking with Python Ebook , where we build 24 hacking tools and scripts! Make sure to check it out if you're interested. Why juggle between languages when you can convert? Check out our Code Converter . Try it out today! Building and creating an ARP Spoof script in Python using Scapy to be able to be a man in the middle to monitor, intercept and modify packets in the network.
Building a simple network scanner using ARP requests and monitor the network using Scapy library in Python. Writing a DNS spoofer script in Python using Scapy library to successfully change DNS cache of a target machine in the same network. Got a coding query or need some guidance before you comment? Check out this Python Code Assistant for expert advice and handy tips. It's like having a coding tutor right in your fingertips! Paper Publication Format: Publication of any paper or manuscript in IJERT requires strict conformance to the paper template.
Once the paper is selected, the manuscript will be published in the IJERT Digital Library. The paper template can be downloaded from this link. Harvested Online Documentation & Reference Sources • https://github.com/yasserhous/Arp-Spoofind-Detection-Tool • https://github.com/heerkakkar/arp_spoof_detector • https://www.geeksforgeeks.org/python/how-to-detect-arp-spoof-attack-using-scapy-in-python/ • https://github.com/king04aman/ARP-Spoof-Detector • https://www.bomberbot.com/python/detecting-arp-spoof-attacks-with-scapy-in-python-a-comprehensive-guide/ • https://thepythoncode.com/article/detecting-arp-spoof-attacks-using-scapy • https://www.ijert.org/research/ARP+Spoof+Detection+and+Mitigation-IJERTV12IS110058.pdf • https://iopscience.iop.org/article/10.1088/1742-6596/1911/1/012022/pdf
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for ARP Spoofing Detection And Prevention Tool Python.
[*] Metasploit Scan Running on Target Subnet for ARP Spoofing Detection And Prevention Tool Python... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |