Complete Technical Paper Content — Attack Tree Generation Using Python
Overview & System Context
Attack Tree Generation Using Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8255 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background In cryptography and computer science, a hash tree or Merkle tree is a tree in which every "leaf" node is labelled with the cryptographic hash of a data block, and every node that is not a leaf (called a branch, inner node, or inode) is labelled with the cryptographic hash of the labels of its child nodes. A hash tree allows efficient and secure verification of the contents of a large data structure. A hash tree is a generalization of a hash list and a hash chain. Demonstrating that a leaf node is a part of a given binary hash tree requires computing a number of hashes proportional to the logarithm of the number of leaf nodes in the tree. Conversely, in a hash list, the number is proportional to the number of leaf nodes itself. A Merkle tree is therefore an efficient example of a cryptographic commitment scheme, in which the root of the tree is seen as a commitment and leaf nodes may be revealed and proven to be part of the original commitment. The concept of a hash tree is named after Ralph Merkle, who patented it in 1979.
hash-based cryptography. InterPlanetary File System (IPFS), BitTorrent hashtree ZFS file system (to counter data degradation); Dat protocol; Apache Wave protocol; Git and Mercurial distributed revision control systems (although, strictly speaking, they use directed acyclic graphs, not trees); the Tahoe-LAFS backup system; Zeronet; OpenZFS the Bitcoin and Ethereum peer-to-peer networks; the Certificate Transparency framework; Merkle Tree Certificates; the Nix package manager and descendants like GNU Guix; a number of NoSQL systems such as Apache Cassandra, Riak, and Dynamo. Suggestions have been made to use hash trees in trusted computing systems.
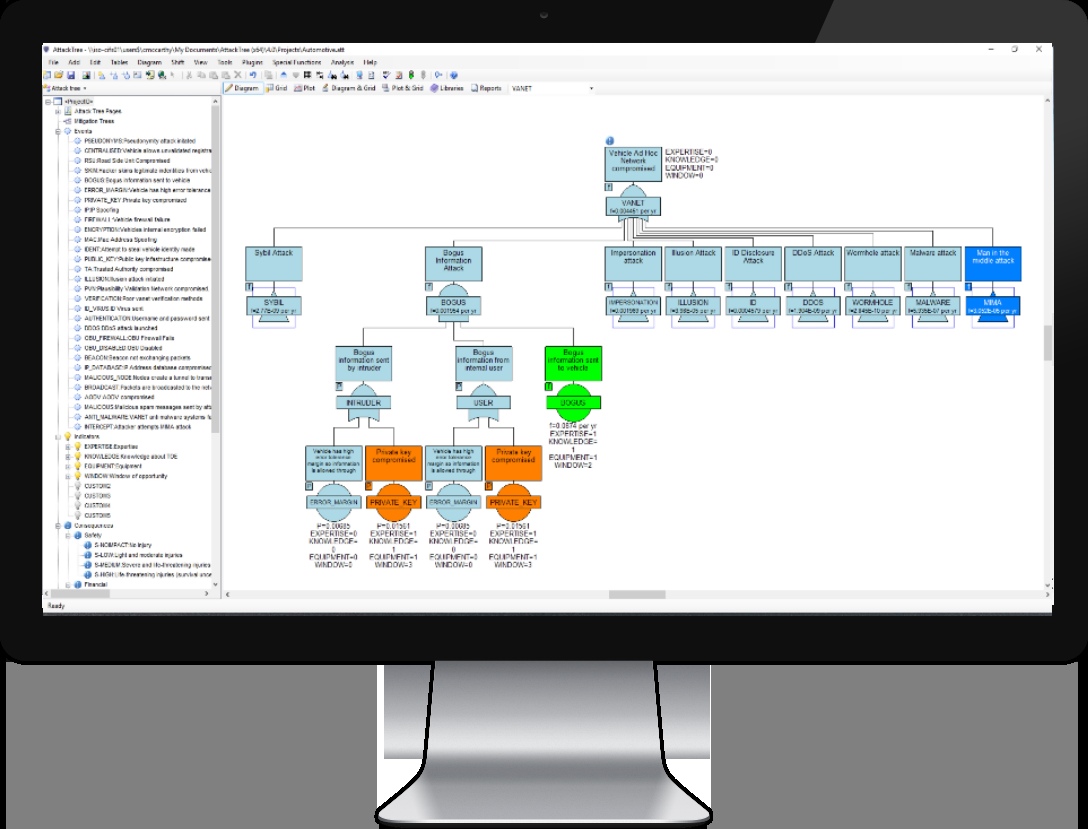
Binary tree Blockchain Distributed hash table Hash table Hash trie Linked timestamping Radix tree A C implementation of a dynamically re-sizeable binary SHA-256 hash tree (Merkle tree) Merkle tree implementation in Java Tiger Tree Hash (TTH) source code in C#, by Gil Schmidt Tiger Tree Hash (TTH) implementations in C and Java RHash, an open source command-line tool, which can calculate TTH and magnet links with TTH Figure 1: Isograph AttackTree Software The first generation (generation I) of the Pokémon franchise features the original 151 fictional species of monsters introduced to the core video game series in the 1996 Game Boy games Pocket Monsters Red, Green and Blue (known as Pokémon Red, Green and Blue outside of Japan). Later, Pokémon Yellow and Blue were released in Japan. The following list details the 151 Pokémon of generation I in order of their National Pokédex number. The first Pokémon, Bulbasaur, is number 0001 and the last, Mew, is number 0151. Alternate forms that result in type changes are included for convenience. Mega evolutions and regional forms are included on the pages for the generation in which they were introduced. MissingNo., a glitch, is also on this list.
The Bhatt PeshwI family earlier known as Bhatt family is a prominent Indian Marathi Chitpavan Brahmin royal family. Most of the members in this family were the Peshwas (prime ministers) in the Maratha Empire, and Peshwa later became their family name. In the eighteenth century, most of the Indian subcontinent came under their control. Balaji Vishwanath was the first of a series of hereditary Peshwas (Marathi for Prime Minister) hailing from the Chitpavan Brahmin family who gained effective control of the Maratha Empire during the 18th century. Balaji Vishwanath assisted a young Maratha Emperor Shahu I, grandson of Shivaji, to consolidate his grip on a kingdom that had been racked by civil war and persistent attack by the Mughals under Aurangzeb. He was called "the second founder of the Maratha State." Baji Rao I (18 August 1700 – 28 April 1740), also known as Bajirao I, was a noted general who was appointed as the Peshwa by Shahu I of the Maratha Empire in 1720., He is also known as Thorale Bajirao (Bajirao the elder) in Marathi to distinguish him from his grandson and namesake, Bajirao II, the last Peshwa. Bajirao, after Shivaji, is considered to be the most charismatic and dynamic leader in Maratha history, and one of the greatest Military generals of his time. He was just twenty years old when he was appointed Peshwa, and already had a reputation for rapid decisions and a passion for military adventure. Chimaji Appa (1707–1741) was a son of Balaji Vishwanath Bhat and the younger brother of Peshwa Bajirao I. He was an able military commander who liberated Portuguese controlled territory north of Mumbai including Vasai fort in a hard-fought battle in 1739. Bhiubai – She married Abaji Joshi of Baramati, brother of the banker Balaji Naik famed as Bajirao I's "most tormenting creditor". Anubai – she married Venkatrao Ghorpade of Ichalkaranji. Their heirs ruled the state of Ichalkaranji until 1947.
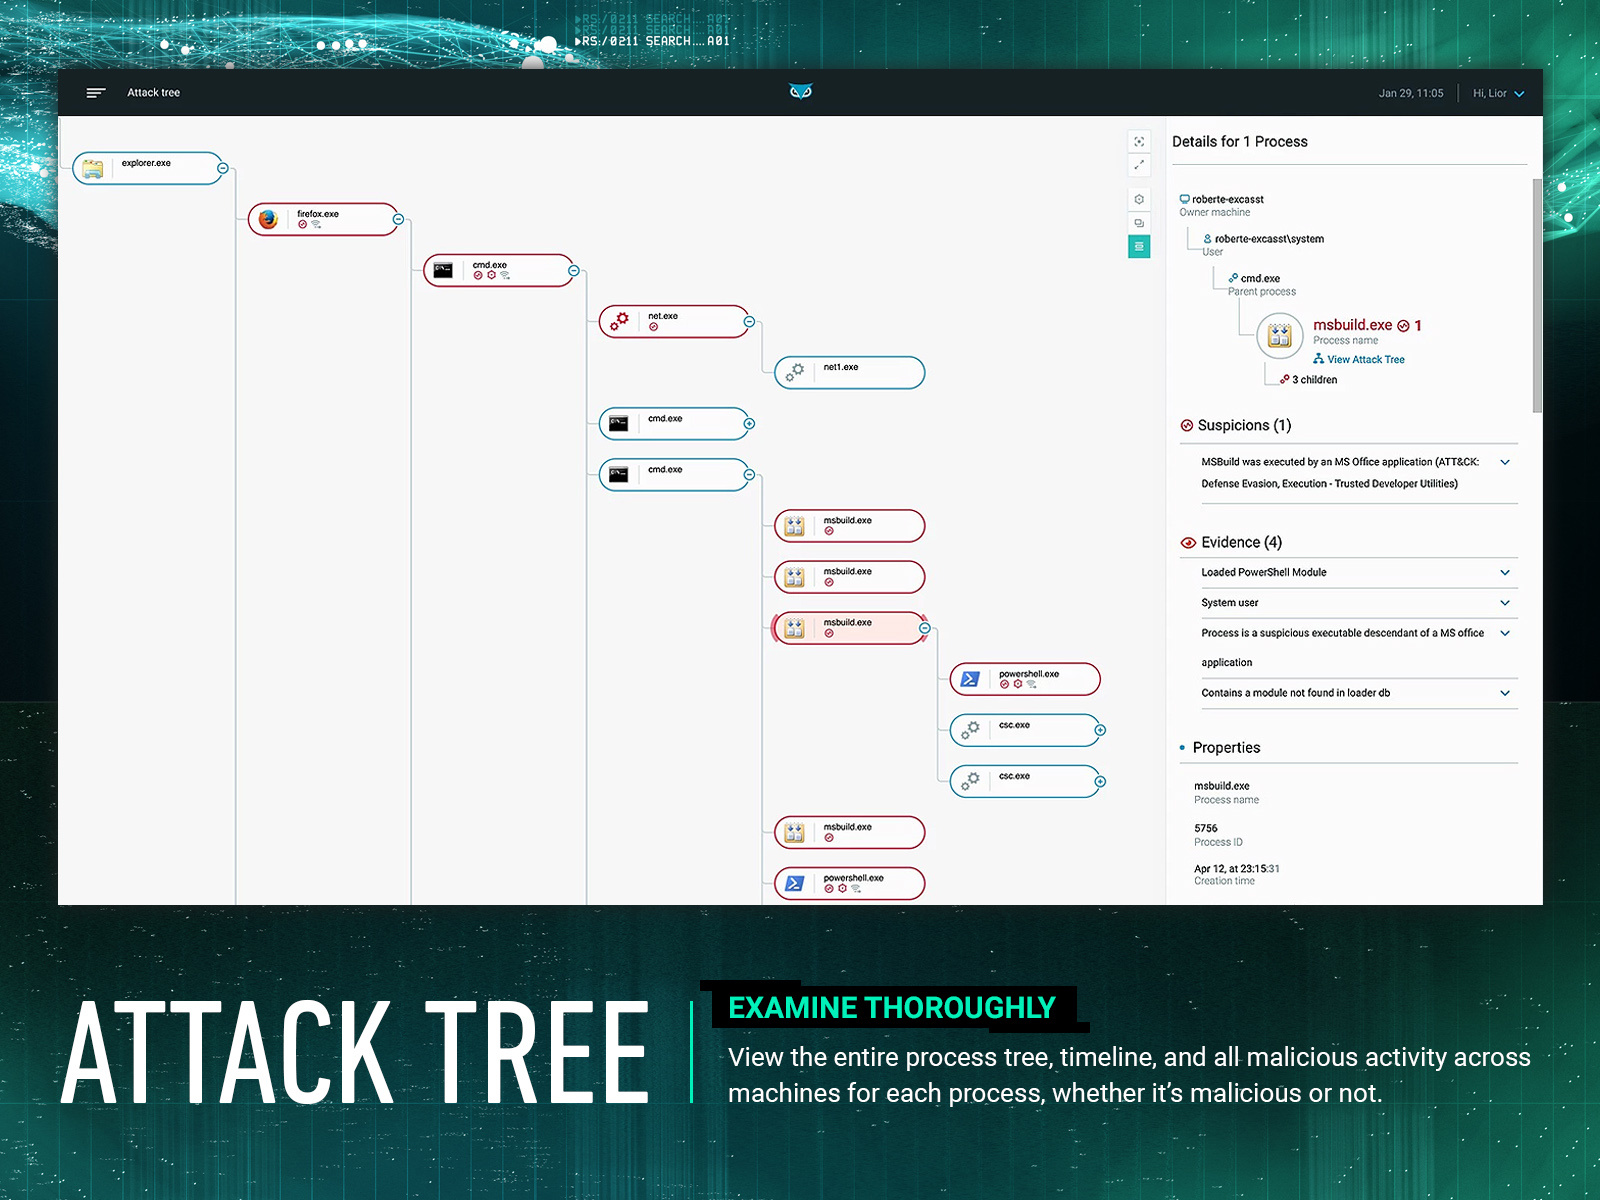
Figure 2: CYBEREASON ATTACK TREE by CYBEREASON on Dribbble |Bajirao was married to Kashibai Chaskar Joshi, and had two sons together: Balaji Bajirao Peshwa (Nanasaheb) who was later appointed Peshwa by Shahu in 1740. Their second son was named Raghunathrao. Bajirao also took Mastani as the second wife who was the daughter of Maharaja Chhatrasal of Panna by a Persian Muslim wife. Chimajiappa was married to Rakhmabai (Pethe family). He had only son, Sadashivrao known popularly as Sadashivrao Bhau who led the Maratha forces in the Third Battle of Panipat against Ahmad Shah Abdali. Rakhmabai died shortly after Sadashivrao's birth, which led to Chimajiappa's second marriage to Annapuurnabai. Bajirao and Mastani had a son named Shamsher Bahadur.
Balaji Baji Rao (Nanasaheb) (8 December 1720 – 23 June 1761), also known as Nana Saheb Peshwa, was son of Bajirao and Kashibai. Chattrapati Shahu, at time of his death, appointed Balaji Baji Rao Peshwa of Maratha Empire. He contributed to development of Pune, India. Under his reign, borders of Maratha Empire crossed Peshawar (presently in Pakistan) by 1760 AD . However, he is also held responsible for defeat of Marathas at the Battle of Panipat (1761). Raghunathrao (b. 18 Aug.1734 – d. 11 Dec.1783) was Peshwa of the Maratha Empire from 1773 to 1774. Earlier in his career as a commander of Maratha forces, he is credited with expanding the Maratha Kingdom to include far-flung areas such as Attock in present-day Pakistan. However, he is also blamed sowing the seeds for the downfall of the Peshwa Dynasty. He is nicknamed as Ragho Bharari since he is instrumental in planting the triumphant Hindu Maratha flag till Attock in present-day Pakistan. Shamsher Bahadur I (Krishna Rao) (1734–1761) also spelled as Samsher Bahadur, a.k.a. Krishnasinh, was a Maratha ruler of the dominion of Banda in northern India. He was the son of Bajirao I and Mastani. Sadashivrao Bhau (4 August 1730 – 14 January 1761) was the son of Chimaji Appa and Rakhmabai and the nephew of Peshwa Baji Rao I. He served as the Sarsenapati (commander-in-chief) of the Maratha army at the third battle of Panipat. He died fighting at the third battle of Panipat. Janardan Rao who died young Vishwasrao (7 March 1741 – 14 January 1761) was the eldest son of Balaji Baji Rao, Peshwa of Pune (Poona) (the prime minister and de facto ruler/administrator) of the Maratha Empire and also was the heir to the title of Peshwa of Maratha Empire. He was killed during the period of the most intense fighting (Approx. between 01pm and 02:30pm) at Third Battle of Panipat, fighting on the front lines. It is generally accepted that the third battle of Panipat, which hung in balance till his death, moved decisively in favour of the Afghans and ended up in victory of Durrani Empire. Madhavrao I (or Pradhanpant Shrimant Madhavrao (Ballal) Peshwa I a.k.a. Thorle Madhav Rao Peshwa ) (14 February 1745 – 18 November 1772) was the fourth Peshwa of the Maratha Empire. During his tenure, Maratha power recovered from the losses suffered during the Panipat Campaign, a phenomenon known as "Maratha Resurrection". He is considered one of the greatest personalities of the Maratha history. Narayan Rao (10 August 1755 – 30 August 1773) was the fifth Peshwa or ruler of the Maratha Empire from November 1772 until his murder by his palace guards in August 1773 Baji Rao II (10 January 1775 – 28 January 1851), also Rao Pandit Pandham, was the son of Peshwa Raghunathrao and Anandibai was Peshwa of the Maratha Empire, and governed from 1796 to 1818.He was installed as the Peshwa after his nephew, Sawai Madhavrao died without leaving an heir.
Ali Bahadur (Krishna Sinh) (1758-1802), was a Nawab of the dominion of Banda (present day Uttar Pradesh) in northern India, a vassal of Mahratta polity. He was the son of Shamsher Bahadur I (Krishna Rao) and the grandson of Bajirao I Under the auspices of the powerful Maratha nobles, Ali Bahadur established his authority over large parts of Bundelkhand and became the Nawab of Banda .Ali Bahadur supported Pune polity and fought the English in the Anglo-Maratha War of 1803 Welcome to the ThreatForest User Guide. This section provides comprehensive guidance on using ThreatForest for threat modeling and attack tree generation.
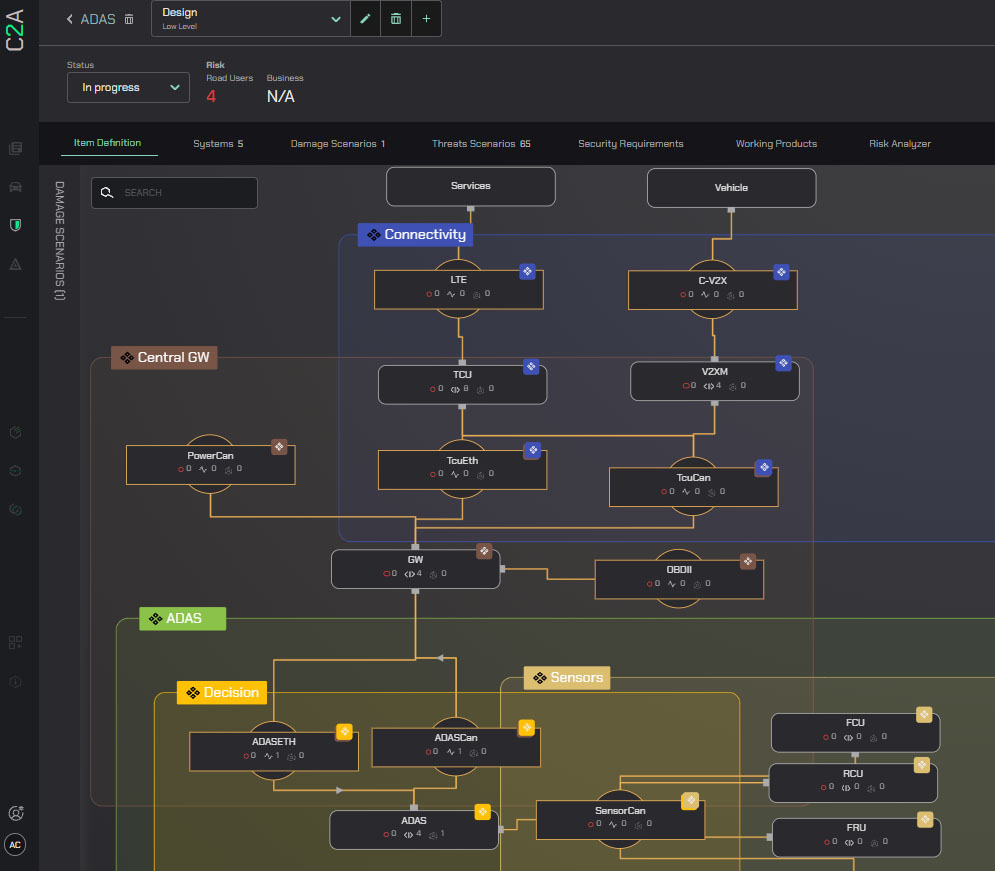
Figure 3: Attack trees aren’t one-size-fits-all: designing adaptable attack tree ... This user guide covers everything you need to know to effectively use ThreatForest in your security workflow: ThreatForest is built on a modular architecture that combines autonomous AI agents with industry-standard security frameworks. The system orchestrates multiple specialized components to deliver comprehensive threat modeling and attack tree generation.
The v2 pipeline, defined in agents/graph.py . Each node is a Strands agent or function wrapped as a GraphNode . Verifier nodes run after each stage — if verification fails, the graph retries that stage automatically. Agents operate independently using Strands tools, reducing manual intervention and enabling: I Read the paper: ThreatForest: Multi-Agent Attack Tree Generation with Pluggable TTP Framework Mapping (arXiv:2607.27528) ThreatForest is an agentic threat modeling platform built on the Strands agent framework. Point it at a repository and it autonomously generates attack trees, maps attack steps to MITRE ATT&CK techniques, and produces actionable mitigation recommendations.
Built for security teams, architects, and DevSecOps engineers who want to bring threat modeling into the development loop without turning it into a second full-time job. Privacy: ThreatForest sends project context to your configured LLM provider. AWS Bedrock is recommended for production workloads.
The Python ML service is required — the engine pre-flights it and refuses to start a run when it is unreachable, rather than producing a threat model with silently missing attack paths. From a repository path to a fully mapped attack tree in a single run. For a deeper tour — including the dashboard, filtering, and mitigation details — see the full walkthrough in the docs .
ThreatForest is described in ThreatForest: Multi-Agent Attack Tree Generation with Pluggable TTP Framework Mapping . If you use it in your research, please cite: At first glance, applying attack trees to cyber and physical security may appear challenging. But, in its essence, it is really quite simple. Like most analytic processes, it is possible to go well beyond the basics. However, a lot can be achieved using the fundamentals.
The overall goal of attack tree analysis is to understand how an adversary will behave against a target. Knowing how an adversary will attack allows the defender to create an effective defense. An attack tree is similar to mathematical trees you are probably already familiar with (such as decision trees). As is customary, the root of the tree is at the top and the tree grows downward toward the bottom-most leaf nodes.
A basic attack tree has three types of nodes: OR , AND and leaf . OR and AND nodes represent logical states an adversary will achieve as they attempt to compromise a system's security. OR nodes represent states that can be realized in a variety of different ways. Each way is represented by one of the OR node's children. A simple example shows two ways of entering a building via a window (other methods may exist - these are shown for simplicity). OR nodes are represented using the traditional Boolean algebra symbol - a pointy topped, curved bottom shape (depicted in green).
AND nodes represent states that require the attacker to perform multiple steps (represented by the AND node's children). In a classic attack tree all of the node's children must be performed. (Sophisticated tools such as Amenaza's SecurITree can capture more complex relationships, such as m of n ). This snippet of a larger attack tree shows the steps an attack needs to perform to extract information from a data source (such as a backup tape or disk drive). The attacker must obtain the data source and then perform whatever technical operation is necessary to Read Data . AND nodes are represented by the Boolean shape with a round top and flat bottom (depicted in cyan). Also note how one of the AND 's children is an OR node with its own children beneath.
Leaf nodes are the actual point of interaction between and adversary and their target. These nodes represent the exploit tasks the adversary has to perform. Each of these tasks requires resources from the adversary. The resources may include money, time, skill, physical access and special equipment. An adversary can only perform the leaf level exploits if they possess those resources. The leaf nodes in the examples above are shown as grey rectangles. The activities represented by the leaf nodes differ greatly in the amount and type of resources required. For instance, Steal Tape requires the attacker to have physical access to the data tape, but very little technical ability. Stealing the tape may also expose the attacker to discovery. Once the tape has been stolen, the Read Data step could be done elsewhere. However, reading a backup tape does require access to a potentially expensive tape drive.
Using the AND , OR and Leaf building blocks outlined above, a complete tree is constructed that terminates in a topmost root node. The root node represents the state the attacker wishes to achieve (and that which the defender wants to prevent). Combinations of leaf node events satisfy the AND/OR logic of the tree and form paths to root (which are called attack scenarios ).
Of course, not all paths through the tree are equal. The leaf node events associated with the various attack scenarios represent different complexities that the attacker must address. Recognizing this, the analyst defines a variety of indicators that represent the types and amounts of resources the adversary must provide for the leaf level operations, the impacts these activities will have on the defender as higher level AND/OR states are realized, and to assess the benefits that will accrue to the adversary. The latter provide an indication of the attacker's degree of motivation.
Based on intelligence information, and reasonable assumptions, the analyst then defines profiles for each type of adversary that may plausibly be interested in the target. Although it may be possible to precisely identify the characteristics of any particular attacker, it is possible to come up with reasonable generalizations for the class of attackers. For instance, Script Kiddies (typically adolescents with minimal formal training) will generally have a low technical ability and little money, but significant time on their hands to perform attacks. They may also be quite bold and brazen because they fail to recognize the potentially serious consequences of their actions. By contrast, a commercial criminal may have significant technical skills and tens of thousands of dollars to fund an attack. However, their attacks will be carefully chosen to avoid detection, and especially, attribution. They understand the risks they face. The two groups also differ in objectives. The script kiddie may simply be looking to deface a website for purposes of recognition and infamy. The commercial criminal may be after valuable intellectual property.
Evaluate all of the attack scenarios through the tree to understand each path's characteristics in terms of resource requirements, benefits to the attacker and detriments to the victim. Compare each path's characteristics to each of the attack profiles generated previously. Identify the attack scenarios that are feasible and (for each adversary) desirable. Scenarios that are both feasible and desirable are probable. The scenarios that are probably and that will create a significant impact to the victim present risk. At this point, the system operator must determine whether they will accept the level of risk, transfer the risk (perhaps via insurance) or mitigate the risk.
If the decision is made to prevent high risk attack scenarios from occurring, the defender needs to identify defensive strategies. In physical situations, this may require physical controls (guns, guards, gates). In cyber situations, it may require techniques such as network segmentation, encryption, authentication and authorization mechanisms. Each of these controls can be incorporated into the original attack tree model and analysis repeated to determine whether the countermeasure is effective. This avoids implementing costly controls which may turn out to be ineffective.
In principle, all of the steps above can be performed manually. However, this is usually not practical. A typical attack tree may incorporate over a hundred thousand attack scenarios and face a handful of distinct adversaries. This would require an analyst to manually evaluate and compare a half million or more situations. Fortunately, Amenaza's SecurITree makes the attack tree analysis process simple and easy. Additionally, it incorporates many advanced analytic functions not described above. These identify the critical paths through the tree and help analysts construct effective and cost effective solutions.
Although the basics of attack tree analysis are straightforward, the maximum benefit of the process (and SecurITree) can be obtained most quickly by taking Amenaza's three-day course on advanced attack tree analysis (usually taught at the customer's site). Also consider the reference white paper on attack tree analysis. Covers DevSecOps basics, emphasizing secure SDLC and CI/CD with SCA, SAST, DAST, and Security as Code.
Covers OS hardening, infrastructure/code compliance, vulnerability management, and automation. This certification teaches students to build secure container images and analyze their vulnerabilities. 2. System Architecture & Core Working Principles Learn cloud-native security concepts and measures: hacking and defending Kubernetes clusters, authentication and etc.
Hands-on AI/LLM Security Course covering OWASP Top 10 vulnerabilities, model attacks, supply chain risks, AI Threat Modeling and MITRE ATLAS defenses. Attack, assess, & harden MCP servers: tool poisoning, prompt injection, supply chain security, & agentic AI defenses. Attack, poison, & harden AI agents: reasoning loops, memory stores, tool-calling, & multi-agent identity.
The Threat Modeling course covers STRIDE, PASTA, DREAD, MITRE, Agile, and Privacy methods. This API Security certification teaches how to secure and audit APIs against vulnerabilities. Learn how organizations protect against attacks and plan to assess/reduce software supply chain risks. Certified DevSecOps Professional and Certified DevSecOps Expert (CDP + CDE) Best Value DevSecOps Professional and AI Security Professional (CDP + CAISP) Best Seller Best Value AI Security Professional and MCP Security Expert (CAISP + CMCPSE) Best Seller Best Value Certified DevSecOps Professional and Software Supply Chain Security Expert (CDP + CSSE) AI Security Professional and MCP Security Expert and Agentic AI Security Expert (CAISP + CMCPSE + CAASE) Best Value Container Security Expert and Cloud Native Security Expert and API Security Pro (CCSE + CCNSE + CASP) Best Value An attack tree is a graphical representation of the various steps an attacker might take to exploit vulnerabilities and achieve specific malicious goals. It provides a visual and organized way to model the attack paths, potential vulnerabilities, and their dependencies. Attack trees are built using a hierarchical structure and can be subdivided into smaller attack trees to represent different attack vectors.
Start by identifying the specific goal an attacker could have. For example, the goal could be to gain unauthorized access to a system, tamper with data, or cause a denial-of-service (DoS) attack. Create the root node of the attack tree, representing the identified goal. Use a descriptive keyword or phrase as the label for the root node.
Identify different attack paths an attacker could follow to reach the goal. These paths represent a series of steps an attacker might take to exploit vulnerabilities. For each attack path, create child nodes connected to the root node. For each attack path, further subdivide it into smaller attack trees or sub-attack trees. These sub-attack trees represent individual elements, actions, or vulnerabilities that an attacker may exploit. Repeat this step recursively until you reach a level of detail that provides enough granularity for analysis.
For each node in the attack tree, add specific attack techniques, strategies, or vulnerabilities that an attacker could utilize or exploit. This helps identify potential weaknesses in the system and highlight areas requiring additional protection. Analyze the attack tree to assess the likelihood and impact of each attack path. This analysis allows you to prioritize risks, identify critical vulnerabilities, and plan appropriate countermeasures.
Attack Path 3: Exploit Server Misconfigurations Sub-Attack Tree 3.1: Default Credentials By analyzing this attack tree, we can identify the critical attack paths and vulnerabilities that need attention. For instance, we may prioritize strengthening authentication mechanisms, implementing proper input validation, and securing server configurations.
Attack trees provide a structured and visual representation of potential attack paths, vulnerabilities, and goals an attacker may exploit. By using attack trees for threat modeling, organizations can proactively identify and assess potential risks, prioritize security efforts, and plan robust defensive measures. Remember, threat modeling is an ongoing process that should be revisited regularly to account for emerging threats and evolving technologies.
The Certified Threat Modeling Professional (CTMP) is a vendor-neutral course and certification program. In fact, the course curriculum will also focus on Security requirements in agile environments, Agile Threat modeling, Threat Modeling as Code, and Secure Design Principles to help you ensure security in the design phase. The course provides hands-on training through browser-based labs, 24/7 instructor support, and the best learning resources to upskill in Threat Modeling.
Muhammed Yuga Nugraha is the creator of awesome lists which is focused on security for modern technologies, such as Docker and CI/CD. He is a thriving DevSecOps engineer who is focused on the research division exploring multiple topics including DevSecOps, Cloud Security, Cloud Native Security ,Container Orchestration, IaC, CI/CD and Supply Chain Security. The Certified AI Security Professional course offers an in-depth exploration of the risks associated with the AI sup… Given the growth and adoption of Kubernetes, a number of projects have been published in the OWASP… Gain advanced security skills through our certification courses. Upskill today and get certified to become the top 1% of cybersecurity engineers in the industry.
Imagine trying to secure your digital castle. You know there are threats, but what are the specific ways an intruder might get in? Without a clear picture, your defenses are likely to be scattered and ineffective. This is where the power of an attack tree comes into play. An attack tree is a visual representation of the various ways a security goal can be achieved. It breaks down a high-level objective, like ‘steal sensitive data,’ into smaller, manageable sub-goals and their corresponding methods. Think of it as a roadmap for an attacker, but for you, it’s a powerful tool to anticipate and mitigate those very pathways.
At its core, an attack tree is a hierarchical model that breaks down a security objective into a series of sub-goals. These sub-goals are then further decomposed until they reach basic, actionable steps that an attacker might take. The structure resembles an upside-down tree, with the root representing the ultimate attack goal and the leaves representing the fundamental actions.
The primary purpose of an attack tree is to systematically identify and analyze potential threats against a system, asset, or process. By visualizing these threats, security professionals can better understand their attack surface, prioritize vulnerabilities, and design more effective security controls. It shifts the perspective from ‘what could go wrong?’ to ‘how could someone specifically achieve this negative outcome?’ The benefits of employing attack trees in your security strategy are manifold. They provide a structured and comprehensive approach to threat modeling that goes beyond simple checklists or generic risk assessments. Here are some key advantages: Understanding the components of an attack tree is crucial for building an effective one. Each node in the tree represents a specific goal or sub-goal, and the relationships between these nodes define how an attacker can achieve them.
The root node is always the primary attack objective. Leaf nodes, at the bottom of the tree, represent the most basic, atomic actions that an attacker can perform. These are typically low-level technical operations or physical actions. The edges connect the parent node to its child nodes, indicating the relationship (And or Or) between them. The arrows point from the parent goal to the sub-goals that contribute to its achievement.
Creating an effective attack tree requires a systematic and thorough approach. It’s not just about drawing boxes and lines; it’s about thinking like an attacker and understanding your system’s weaknesses. (See Also: How Much Does A Redwood Tree Weigh ) Begin by clearly defining the specific security objective you want to model. This should be a high-level, undesirable outcome that you want to prevent. Examples include: Be as specific as possible. Instead of ‘compromise system,’ aim for ‘gain root access to the production database server.’ Once you have your root goal, brainstorm the main ways an attacker could achieve it. These will become the first level of child nodes. Consider the different categories of attacks that could lead to your goal. For the goal ‘Steal sensitive customer data,’ primary methods might include: At this stage, you’ll likely use ‘Or-nodes’ to connect the root goal to these primary methods, as any one of them could lead to data theft.
3. Software Implementation, Frameworks & Protocols This is the core of building the attack tree. For each sub-goal identified in Step 2, repeat the process: ask ‘How can this sub-goal be achieved?’ and break it down into smaller, more specific steps. Continue this decomposition until you reach atomic actions that are either: Notice how we’re using Or-nodes to represent choices an attacker has. If a goal requires multiple specific actions to occur in sequence or in parallel, you would use an And-node.
As you decompose, carefully consider whether a sub-goal requires all of its children to be met (And-node) or if any one of them is sufficient (Or-node). This is a critical decision that shapes the accuracy of your tree. This step requires a deep understanding of the attack vectors and the system’s architecture. (See Also: How Heavy Is A Redwood Tree ) The leaf nodes are the fundamental building blocks of your attack tree. These should be specific, actionable steps that don’t require further decomposition. Examples include: Once you have a draft of your attack tree, it’s essential to review and refine it. This is an iterative process.
This refinement process might involve restructuring parts of the tree, adding new branches, or removing redundant paths. While you can draw attack trees using simple diagramming tools, specialized software can enhance the process, especially for complex systems. These tools often provide features for: Choosing the right tool depends on the complexity of your needs and your team’s preferences.
Once your attack tree is built, its value lies in how you use it. Here are practical applications: Map your identified vulnerabilities to the leaf nodes of your attack tree. This helps you understand which vulnerabilities are critical because they enable significant attack paths. You can then prioritize patching or mitigation efforts based on their impact on the overall attack goal. (See Also: How To Start A Tree From A Cutting ) Attack trees help you identify the most effective places to implement security controls. By blocking a key And-node or an important Or-node, you can render entire branches of the attack tree ineffective. For example, implementing strong multi-factor authentication can block the ‘Obtain Valid Credentials’ branch, making a subsequent privilege escalation attack much harder.
Understanding common attack paths allows you to develop more targeted incident response plans. If an incident occurs, you can quickly assess which parts of the attack tree might have been exploited and prepare appropriate countermeasures. Attack trees can be simplified and used to educate employees about common threats. Showing how simple actions like clicking a malicious link can lead to a major security breach can significantly improve user awareness and adherence to security policies.
Penetration testers can use attack trees to guide their testing efforts. Instead of randomly probing for weaknesses, they can systematically explore the attack paths identified in the tree, ensuring comprehensive coverage. Despite these challenges, the structured thinking process that attack tree creation demands is invaluable for any security professional.
By following these practices, you can build attack trees that are not only accurate but also actionable and valuable for improving your organization’s security posture. Creating an attack tree is a methodical process that transforms abstract security concerns into concrete, actionable insights. By systematically breaking down potential attack goals into their constituent parts, you gain unparalleled visibility into your attack surface. This structured approach empowers you to identify critical vulnerabilities, prioritize defensive measures, and design more resilient systems. Ultimately, an attack tree is not just a diagram; it’s a powerful strategic tool for proactive security management.
Attack trees provide a way to map out the various paths an attacker might take to achieve a specific goal. The structure is simple: Think of an attack tree as a roadmap of potential attacks - it visualises possible routes to a successful breach. LetâIIs walk through how to build an attack tree using a common scenario: an attacker attempting to gain system access.
ItâIIs important to note that this simplified tree focuses specifically on obtaining credentials to gain access and doesnâIIt cover other methods like exploiting vulnerabilities directly. We keep it simple here to build intuition. Define the ultimate goal: Start with the attackerâIIs objective at the top (root) of the tree - in this case, âIIGain System AccessâII.
Identify key prerequisites: Determine what the attacker needs to achieve their goal - in this case, obtaining valid credentials is a critical first step. Identify attack methods: Branch out into different approaches to achieve the credentials goal: While shown as separate paths, itâIIs worth remembering that data leaks often provide the raw material for credential stuffing and can inform password spraying targets. The tree structure doesnâIIt explicitly show this dependency but represents them as distinct actions an attacker might take.
Applying those steps, hereâIIs the structure of our example attack tree focusing on obtaining credentials: This example shows multiple ways to achieve the intermediate goal of obtaining credentials. Once youâIIve built your attack trees they can be used as part of the wider threat modeling process. Areas for discussion include: While attack trees excel at visualising how specific attacks might unfold, this analysis in practice often integrates with broader methodologies like STRIDE (for threat categorisation), DREAD (for risk rating), or others, which inform the overall assessment.
For our credentials scenario, countermeasures resulting from this analysis could include examples like: The diagram below visualises the attack tree example weâIIve been building. It lays out the discussed paths for obtaining credentials and incorporates the corresponding MITRE ATT&CK technique IDs for each method shown. Attack trees can potentially become more useful when mapped to standardised frameworks like MITRE ATT&CK. By associating each attack vector with specific ATT&CK technique IDs: This mapping provides security teams with a wealth of additional info about each attack technique, typical adversary groups that use them, and recommended mitigations - all through the standard MITRE ATT&CK knowledge base. These mappings are just initial examples. Others exist and can likewise be mapped.
Our simplified tree mapped routes to obtain credentials, but a real-world attack often proceeds to more complex stages. We should now iterate and look at what happens next, particularly when Multi-Factor Authentication (MFA) stands in the way (e.g., service lacks MFA, unenforced MFA, or user not enrolled, among others). The specific additional areas covered would depend on the scope of the engagement.
Attack trees help bring clarity and structure to threat modeling by breaking down complex attacks into their component parts. TheyâIIre not meant to be the only tool you use, but rather a practical way to visualise and communicate specific attack scenarios. Start simple with your most critical assets, build trees for the most likely attack goals, and use what you learn to strengthen your overall security posture. The power of attack trees lies in their simplicity - they take complex security concepts and make them accessible to everyone involved in protecting your systems.
For organisations looking to implement a comprehensive threat modeling program, our professional threat modeling services can help establish systematic approaches to security risk identification and mitigation. For more information on threat modeling fundamentals, explore our comprehensive FAQ covering methodologies, implementation strategies, and common challenges.
Attack Trees are a structured, methodical way to describe the security of a system based on varying attacks. They represent attacks against a system in a tree structure, with the attacker’s goal as the root and the different ways to achieve that goal as branches and leaves. While a Threat Model casts a wide net from the top — asking “what can go wrong across the system?” — an Attack Tree starts from one specific adversarial goal and decomposes it downward into the concrete steps required to achieve it. Both perspectives are essential: top-down breadth meets bottom-up depth .
Traditional threat modeling (STRIDE, data flow diagrams, trust boundaries) excels at providing a broad, top-down overview of a system’s security posture. But it can remain abstract. Attack Trees complement this by: 4. Practical Deployment, Analysis & Case Studies Root Node — The attacker’s ultimate goal (e.g., “Exfiltrate customer PII”, “Gain admin access”, “Disrupt payment processing”) Leaf Nodes — The actual, atomic attack vectors an attacker would execute (e.g., “Exploit SQL injection in /api/search”, “Phish employee for VPN credentials”) Attack trees are uniquely powerful because they serve both sides of the security equation. They are a natural collaboration artifact for purple teaming — where offensive and defensive perspectives merge.
An attack tree is a living document. Every penetration test result, every incident, every new feature should potentially update it. The tree grows as your understanding of the threat landscape deepens. attacktree.online by Christian Schneider is a free SaaS platform for building and analyzing attack trees. It provides a structured workflow that covers the full lifecycle: A particularly powerful concept enabled by attack trees: rather than running full-blown red team engagements, use the tree to run targeted micro simulations — testing specific leaf nodes or paths to validate whether controls actually work as expected.
This is: Define the goal — What does the attacker want? Be specific. “Exfiltrate customer payment data” is better than “hack the system.” Brainstorm attack paths — What are the fundamentally different approaches? (Network attack, social engineering, insider threat, supply chain, physical access…) Decompose into steps — For each path, what intermediate steps are needed? Keep going until you reach atomic, testable attack vectors.
Assign gate logic — Is this an OR (any path works) or AND (all steps required)? AND gates are your friend as a defender. Annotate leaf nodes — Add complexity, required capabilities, and cost. This helps prioritize. Map existing controls — For each leaf node, what controls exist? What is their status and effectiveness? Analyze and prioritize — Where are the cheapest, easiest, least-detected paths? Those need attention first.
Validate — Use the tree to derive targeted tests (micro attack simulations) that confirm controls work. Iterate — Update the tree after incidents, pen tests, architecture changes, or new threat intelligence. This is just a bit of an experiment, I've been building these trees with a number of friends to map out how attackers might try to win against their services or companies. The result of this exercise is that a tool and a methodoloy are being developed at the same time.
There is value in having a detailed datastructure, containing more information than just the node-name, it's going to be useful for future simulation and analysis work, however, there's equal value in presenting a nice, fast mechanism for generating graphs that make engineering conversations about security go faster. For that reason a lot of defaults and shortcuts have been added to make basic graph generation easier. This should be followed by detail later.
Assemble a team (Security, Red Team, Service owners). Agree on a starting position and a goal. Use the best judgement of the team to constrain the start and the goal to a conversation that can be had in an hour. Avoid building "monster" graphs, these graphs are most useful when contrained to something that will fit on a screen or in a document without scrolling. Don't worry if your graph is getting to big as you build it, it's pretty easy to break a graph into sub-graphs after the fact.
Once you're agreed on the goal and objectives start working through a process of postulating "What will the attacker do next" with a strong bias towards low-cost, low-effort attacks, saving the complicated stuff for when you've exhausted the simple stuff. In real-life the easiest way to do this is on a whiteboard, with a stack of colored post-it's to represent types of node. That's not the reality for many of us who work remote who need a way to capture the graph as we talk through the problem. To make quick graphing possible each node has the ability to create a child and connect to it in one step.
Imagine this simple graph: The start point is "bad guy" and the goal is "break window". Our badguy is going to look for a rock, discover one and throw it at the window! There's value in being able to graph this quickly, and it's certainly easy to read. However, this graphing style only works when each node has only one child. A more flexible way to do this is to keep track of each object. The code below will generate exactly the same graph but maintain a handle to each node that we can use.
There's two types of mitigations described in models.py so far; "Block" and "Detect". Blocking indiciates we have a control in place that will stop a certain action. Detect won't stop the bad thing from happening but will detect it, and presumably send that detection somewhere useful like a SEIM. Each type of mitigation has a state of implemented which can be either True or False . When we are adding mitigations, a lot of the time we want to postulate that "oh, we could add X here" - there'll be a cost to that (CapEx, OpEx, Complexity, Maintentance etc) as well as other factors that we'll consider later in step 3, however for this step, we only want to add these mitigations in the right places and see how they effect our attacker.
It's up to those on building their attack graph to decide if a mitigation will completely stop an attack or only partially. Block nodes can have forward actions and discoveries just like any other node in the graph. So lets update the example and add a potential mitigation, one that's unimplemented; a rock melting laser (pew pew!): The code for this graph looks similar to previous but with the new laser parameter added.
Just as we are writing our model, one of the building architects points out that recently the building received unbreakable-glass upgrades; a blocking control. So we add that to our graph, this time as a control that is implemented. Because we belive this is 100% unbreakable, we no longer see a path to the goal The result is the following graph, which shows that the risk has been effectively mitigated by the new glass, and we probably don't need the lasers after-all...
This project seeks to be more than a quick way to generate graphs. The choice to separate the model from the view was a deliberate one. In the third stage of this methodology the team is encouraged to add metadata to the nodes, that includes: cost , probability of success , sensitivity , mitre attack stage etc. The idea is to model out complex sets of capabilities, attacks and mitigations, both potential and real. Eventually we'll be able to join models together into "big-ugly-models" where the graphs will be largely unintelligble without a wall-plotter but we'll be able to ask questions like "If I have $1m to spend, where should I spend it to improve security" or "How likely am I to suffer a breach of goal x in the next 6 months" ...
Get comprehensive threat models for your application, with autonomous AI agents that analyze, generate, and visualize attack trees mapped to MITRE ATT&CK A pipeline of specialized AI agents developed by threat modeling and data science experts, built on the Strands framework — scanner, threat identifier, attack tree generator, TTP mapper, and mitigation advisor — run automatically in sequence with parallel per-threat processing Automatically maps attack steps to TTPs (Tactics, Techniques, and Procedures) using semantic similarity and vector embeddings Explore threats visually with interactive dashboards, complete with filtering and real-time search Officially supports AWS Bedrock (Claude models). Other providers (Anthropic, OpenAI, Gemini, Ollama) are experimental and not fully tested Before starting, ensure you have Python 3.11+ and an LLM provider configured . AWS Bedrock is fully supported and recommended.
Understand security implications, identify vulnerabilities early, learn attack patterns ThreatForest sends application context to your configured LLM provider for analysis. AWS Bedrock provides enterprise-grade data handling. For other providers, review their data policies. Attack Trees are a structured, hierarchical model of how an adversary can achieve a goal by combining steps and choices.
Analogy: like a fault tree for threats where branches are attack paths. Formal line: a directed acyclic graph mapping attacker goals to subgoals and leaf actions with logical AND/OR relationships. 5. Performance Evaluation & Extended Technical Observations Attack Trees are a modeling technique used to enumerate, analyze, and prioritize potential attack paths against systems, services, or assets. They are not a checklist, a single mitigation plan, or a static compliance artifact. Instead, Attack Trees are a living analytical model used to surface risk, design controls, and guide testing and detection.
A structured model that breaks down attacker goals into combinations of subgoals and actions to analyze and prioritize attack surfaces. (Glossary of 40+ terms. Each entry: term — short definition — why it matters — common pitfall) 1) Prerequisites – Asset inventory and architecture diagrams. – Basic observability: centralized logs, traces, metrics. – Owner assigned for each service. – Agreement on scoring attributes and units.
2) Instrumentation plan – Identify required telemetry for leaves: network flows, auth logs, process events. – Ensure unique identifiers propagate (request ids, deployment ids, session ids). – Add structured logging fields to map events to tree IDs. 3) Data collection – Centralize logs with retention aligned to threat needs. – Configure audit logging for cloud control plane and K8s. – Implement sampling and high-fidelity capture for security-sensitive flows.
4) SLO design – Define SLIs: detection coverage, TTD, TTC. – Set pragmatic SLOs per maturity and criticality. – Define error budgets and escalation paths. 5) Dashboards – Build executive, on-call, and debug dashboards. – Include mapping from tree nodes to telemetry signals. – Expose remediation backlog and progress.
6) Alerts & routing – Create alert rules mapped to leaf detections. – Route critical pages to security on-call and service owner. – Define automated containment playbooks. 7) Runbooks & automation – Create runbooks per top risk path with clear actions and rollback steps. – Automate safe containment steps (isolating host, revoking keys). – Test automation in staging.
8) Validation (load/chaos/game days) – Run red-team exercises driven by trees. – Execute chaos experiments to verify containment actions. – Run CI-integrated canary tests for detection rules. 9) Continuous improvement – Update trees from postmortems and telemetry. – Recalibrate scoring with measured incident data. – Regularly prune low-value branches.
1) Public API Protection – Context: High-volume public API serving sensitive data. – Problem: Parameter tampering and enumeration. – Why Attack Trees helps: Enumerates injection and auth bypass paths. – What to measure: Detection coverage for auth failures and abnormal usage. – Typical tools: WAF, APM, SIEM. 2) Cloud Storage Data Leakage – Context: Multi-tenant object storage. – Problem: Misconfigured ACLs and leaked signed URLs. – Why Attack Trees helps: Maps exfiltration steps and detection points. – What to measure: Time-to-detect public reads and anomalous downloads. – Typical tools: DLP, cloud audit logs.
3) CI/CD Supply Chain Risk – Context: Container images and third-party libraries. – Problem: Malicious dependency or artifact tamper. – Why Attack Trees helps: Models injection into build pipeline. – What to measure: Pipeline integrity checks and artifact verification failures. – Typical tools: SBOM tooling, CI plugins. 4) Kubernetes Cluster Escalation – Context: Multi-tenant K8s cluster. – Problem: Pod compromise leading to cluster control. – Why Attack Trees helps: Breaks down lateral movement and API abuse. – What to measure: K8s audit events mapped to privilege escalation leaves. – Typical tools: K8s audit, EDR, network policies.
5) Serverless Abuse – Context: Event-driven functions with IAM roles. – Problem: Over-permissive roles enabling data access. – Why Attack Trees helps: Identifies function-level privilege chains. – What to measure: Invocation rate anomalies and IAM policy deviations. – Typical tools: Cloud logs, function tracing. 6) Insider Threat – Context: Privileged engineer accounts. – Problem: Credential misuse and data exfiltration. – Why Attack Trees helps: Models possible misuse paths and controls. – What to measure: Unusual access patterns and large data transfers. – Typical tools: DLP, EDR, IAM logs.
7) Ransomware Prevention – Context: Shared file systems and backup pipelines. – Problem: Encryption and data destruction. – Why Attack Trees helps: Models initial access to backup compromise to encryption. – What to measure: Modify activity on backup targets and unusual encryption events. – Typical tools: Backup integrity checks, EDR. 8) Financial Transaction Fraud – Context: Payment systems. – Problem: Unauthorized transactions via API abuse. – Why Attack Trees helps: Enumerates paths to authorizing payments. – What to measure: Transaction pattern anomalies and authentication failures. – Typical tools: Fraud detection, APM.
9) Credential Exhaustion/Brute Force – Context: Authentication endpoints. – Problem: Account takeover. – Why Attack Trees helps: Maps rate-limited brute-force and credential stuffing paths. – What to measure: Failed login rates and account lockout events. – Typical tools: WAF, auth logs. 10) Third-party Integration Risks – Context: SaaS connectors and webhooks. – Problem: Compromise via compromised vendor. – Why Attack Trees helps: Models vendor pivot and trust boundary errors. – What to measure: Anomalous data flows and permission changes. – Typical tools: API gateways, audit logs.
Context: Multi-tenant Kubernetes cluster hosting payment microservices. Goal: Prevent worst-case scenario where attacker gains cluster admin from compromised pod. Why Attack Trees matters here: Cluster compromise requires chained exploits and privileges; tree enumerates those chains to prioritize controls. Architecture / workflow: K8s control plane, node pool, image registry, CI/CD, RBAC, network policies. Step-by-step implementation: Context: Serverless functions handling PII in a managed cloud PaaS. Goal: Prevent function from exfiltrating data using overly broad IAM role. Why Attack Trees matters here: Maps role misuse and discovery to exfiltration steps enabling targeted detection and least-privilege enforcement. Architecture / workflow: Functions, IAM roles, storage buckets, event triggers.
Step-by-step implementation: Context: Production incident where unexplained lateral movement occurred. Goal: Reconstruct attacker path and close detection gaps. Why Attack Trees matters here: Provides a canonical map to annotate discovered steps and identify missing observability. Architecture / workflow: Multiple services, host logs, network flows, identity logs. Step-by-step implementation: Context: High-cardinality telemetry for a large microservice fleet with cost constraints. Goal: Maintain sufficient detection coverage without excessive logging cost. Why Attack Trees matters here: Helps prioritize high-value leaves for high-fidelity logging and cheaper coverage for low-risk leaves. Architecture / workflow: Logging pipeline, retention policies, sampling strategies. **Step-by-step implementation: Attack Trees are hierarchical decompositions of goals into subgoals using AND/OR logic. Attack Graphs model state transitions and reachability across system states. Trees are simpler; graphs capture dynamic interactions.
At minimum after any significant architecture change, major incident, or quarterly as part of governance. Frequency depends on change rate. Service or product team with security co-ownership. Security architects should govern standards and review. Yes. Automation can link telemetry to tree leaves, surface coverage metrics, and integrate CI tests and SOAR runbooks.
Use SLIs like detection coverage, TTD, TTC, and incident-to-tree mapping. Regular red-team validation also measures effectiveness. They are useful when calibrated with incident history and telemetry. Alone, they are estimates and must be validated. Use templates, inheritance, and centralized catalogs. Focus on high-impact services and reuse subtrees.
Yes. Insider scenarios are often high-impact and should be modeled with detection and controls. A pragmatic starting point is 60–80% coverage for critical leaves and higher for top 10 paths. Tie tree leaves to SLIs, SLOs, runbooks, and incident postmortems to ensure operational relevance. Atomic action that can be detected or tested; avoid micro-steps that cannot be observed.
Prioritize critical leaves, apply dedupe and suppression, improve rule precision, and automate containment. A combination of SIEM, observability, CI/CD, and SOAR along with repositories for tree storage. Run scheduled red-team exercises and automated simulated attacks against tree branches. By prioritizing where to log at high fidelity, reducing unnecessary telemetry spend while retaining security coverage.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Merkle%20tree • https://en.wikipedia.org/wiki/List%20of%20generation%20I%20Pok%C3%A9mon • https://en.wikipedia.org/wiki/Bhat%20family • https://aws-samples.github.io/sample-agentic-attack-tree-generator/user-guide/ • https://aws-samples.github.io/sample-agentic-attack-tree-generator/architecture/overview/ • https://github.com/aws-samples/sample-agentic-attack-tree-generator/ • https://www.amenaza.com/step-by-step-guide.php • https://www.practical-devsecops.com/threat-modeling-using-attack-trees/ • https://guidedreview.com/how-to-create-an-attack-tree/ • https://threatmodel.co/blog/threat-modeling-with-attack-trees
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Attack Tree Generation Using Python.
[*] Metasploit Scan Running on Target Subnet for Attack Tree Generation Using Python... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |