Complete Technical Paper Content — Automated Certificate Lifecycle Tool
Overview & System Context
Automated Certificate Lifecycle Tool: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9530 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Sectigo is an American cybersecurity company specializing in digital certificates and automated certificate lifecycle management. It is one of the ten largest certificate authorities. It provides public root certificates distributed with operating systems, and it issues public key certificates for websites. Formerly known as Comodo Certification Authority (Comodo CA), the company was founded under Comodo Group and was later acquired by Francisco Partners in 2017 and by GI Partners in 2020. Comodo CA was rebranded to Sectigo in 2018. The company has been headquartered in Scottsdale, Arizona since 2023.
Cryptographic bill of materials (CBOM—also cryptography bill of materials) is a structured inventory of all cryptographic assets present in a software, firmware, device, or system. It enumerates algorithms (and parameters such as key sizes and modes), cryptographic libraries or modules, digital certificates, keys and related material, and protocols in use, and maps their relationships to the components that implement or invoke them. CBOMs are used to improve security analysis, compliance, and cryptographic agility, and are increasingly referenced in guidance for postIquantum cryptography (PQC) migration.
DigiCert, Inc. is a digital security company that operates as a certificate authority and provides SaaS solutions for public key infrastructure (PKI) and certificate lifecycle management. Its offerings support authentication, encryption, and identity verification for systems, software, devices, and networks. DigiCert was founded by Ken Bretschneider in 2003. In 2005, DigiCert became a founding member of the CA/Browser Forum.
In 2007, DigiCert and Microsoft developed the first multi-domain (SAN) certificate. In 2012, Nicholas Hales was named the CEO of DigiCert. In 2015, DigiCert acquired the CyberTrust Enterprise SSL business from Verizon Enterprise Solutions. Following the acquisition, DigiCert expanded its extended validation (EV) business. In August 2015, private equity firm Thoma Bravo acquired a majority stake in DigiCert, with TA Associates holding a minority share. In 2016, John Merrill was named CEO of DigiCert. In 2017, DigiCert acquired the TLS/SSL and PKI businesses from Symantec, including brands GeoTrust, Rapid SSL (part of GeoTrust), Thawte and Verisign The acquisition resulted from questions first raised in 2015 by web browsers Google and Mozilla about the authenticity of certificates issued by Symantec, which represented one-third of all TLS/SSL certificates on the web. In September 2017, Google and Mozilla announced they would "reduce, and ultimately remove, trust in Symantec's Root Keys in order to uphold user's security and privacy when browsing the web". The final distrust deadline for certificates chaining to Symantec roots was set for October 2018. Symantec agreed to transfer its certificate business to its top TLS/SSL competitor, DigiCert, whose roots were trusted by browsers. In December 2017, DigiCert began issuing free replacements for all distrusted certificates from Symantec, GeoTrust, RapidSSL, Thawte, and VeriSign. By Oct. 2018, the company had revalidated more than 550,000 organizational identities and issued more than 5 million replacement certificates for affected customers. In 2018, DigiCert acquired QuoVadis, a trust service provider headquartered in Switzerland offering qualified digital certificates, PKI services, and PrimoSign electronic signature software.
Qualified digital certificates from QuoVadis (now backed by DigiCert) comply with eIDAS, a set of EU standards for electronic transactions requiring legal proof of authentication. The company operates as a Qualified Trust Service Provider in Belgium, the Netherlands, and Switzerland. According to DigiCert, "the QuoVadis acquisition aligns with the company's vision of providing globally dispersed and robust PKI-based solutions with local support." In 2019, the company announced a new R&D division called DigiCert Labs. DigiCert Labs will collaborate with other enterprise labs – including Microsoft Research, Utimaco, ISARA, and Gemalto – and make grants to universities for the study of topics related to authentication, data integrity, encryption and identity. Initial research projects will focus on post-quantum cryptography and machine learning. In 2019, DigiCert also launched a post-quantum computing tool kit. In 2019, Clearlake Capital Group, L.P., a leading private investment firm, and TA Associates, an existing investor, reached an agreement to make a strategic growth investment in DigiCert. As part of the transaction, Clearlake, and TA Associates become equal partners in the company. In January 2022, DigiCert acquired IoT security company Mocana. In June 2022, the company acquired DNS Made Easy, a DNS services provider. In October 2022, DigiCert named Dr. Amit Sinha as CEO and board member. Amit had previously led technology and innovation at the cloud-security company Zscaler the previous 12 years. In September 2024 DigiCert acquired Vercara, which previously was Neustar Security Services. In July 2024, DigiCert revoked over 83,000 certificates due to failures in domain control validation (DCV), affecting approximately 0.4% of its active certificates. The scale and impact of the incident led to criticism from industry observers, who argued that it reflected broader concerns about DigiCert’s operational reliability and compliance practices. In September 2025, DigiCert acquired Valimail, a provider of zero trust email authentication delivered as a service. DigiCert was also selected to operate the ASC X9 PKI providing PKI solutions for the financial industry.
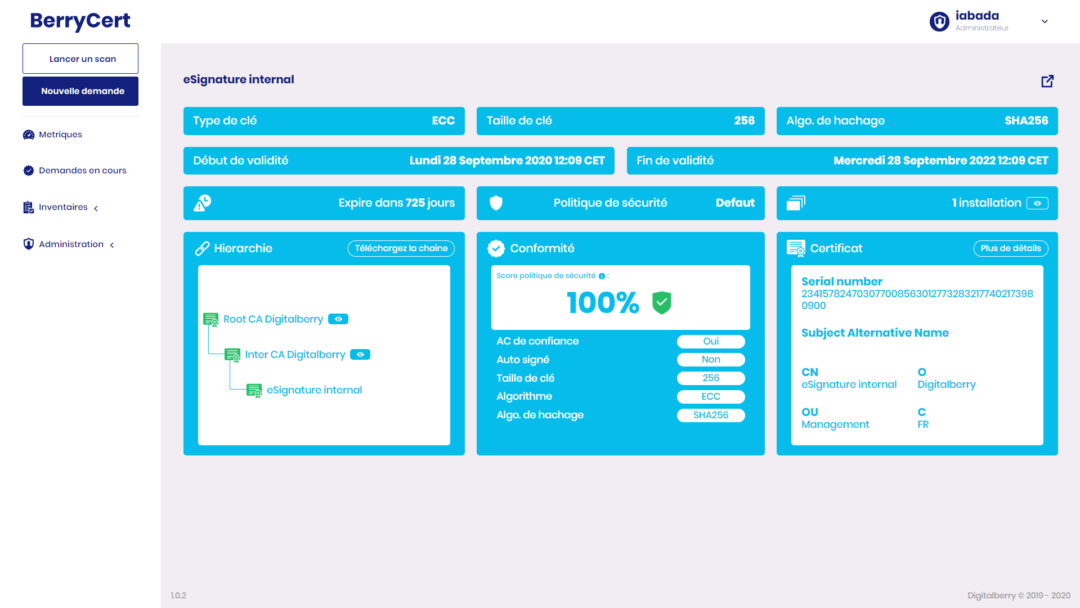
Figure 1: Certificate Lifecycle Management Software (CLM) - BerryCert Certificate lifecycle automation reduces the time and resources you need for repetitive, human-dependent TLS/SSL management tasks. Automation assigns common certificate work, such as generating a certificate signing request (CSR) and installing the TLS/SSL certificate, to an agent on your web server. Automation reduces TLS/SSL administrative overhead, reinforces security, and mitigates the risk of business disruptions.
In addition to saving time and resources (hours or days per request), automation is essential due to shorter certificate lifespans for public-facing certificates . In 2026, the maximum validity for a public-facing certificate will be 200 days, almost half of the current 398 days. By 2029, the maximum validity will be 47 days—less than 2 months. That means you'll need to renew and reinstall your TLS/SSL certificate at least 7 times each year.
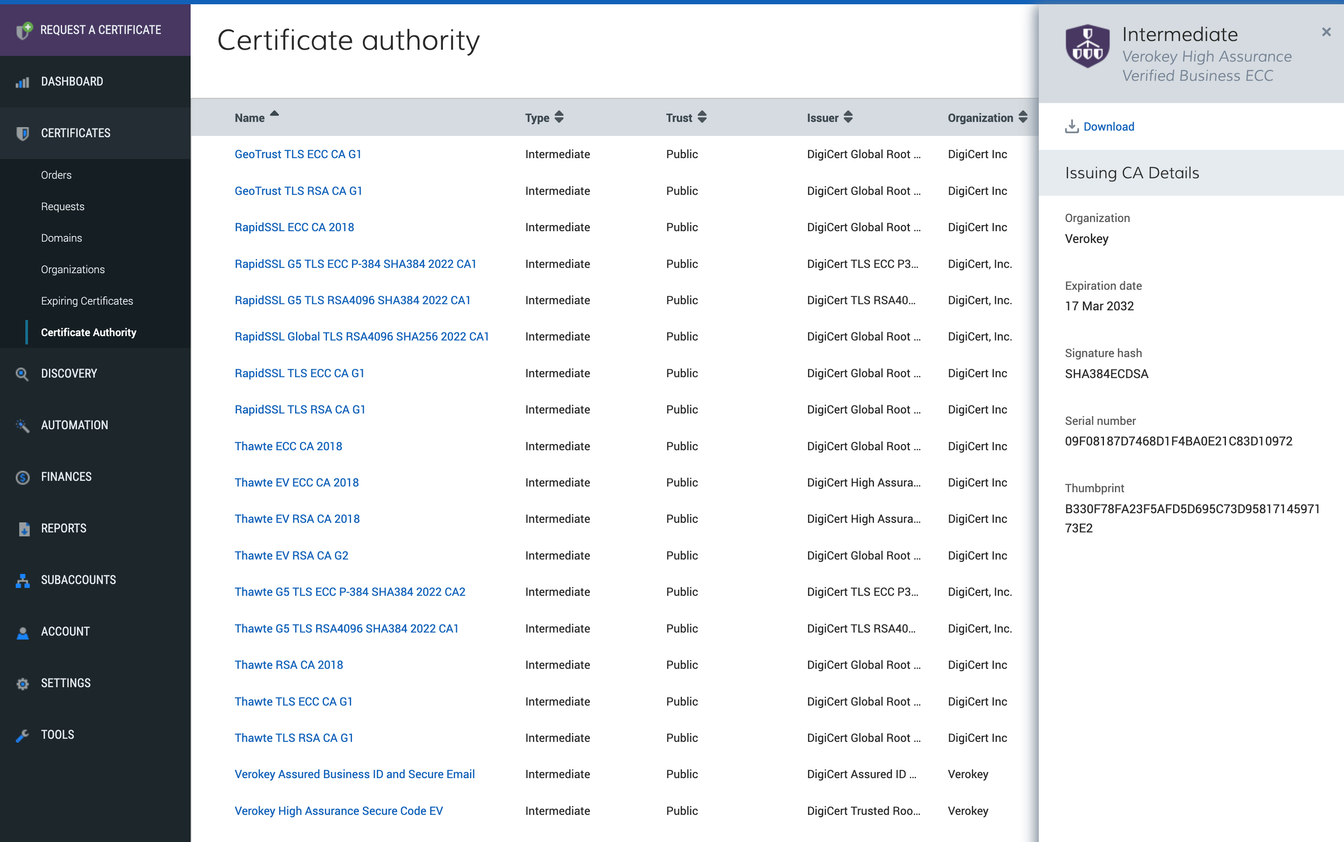
If your server admin team has the skill to install a TLS/SSL certificate, you already have the resources to install the automation client on your server that does the work for you. Also, automation client management is a one-time setup with minimal maintenance later. Before you get started, check the system and knowledge requirements for automation. Figure 2: PKI Certificate Lifecycle Management If you're new to certificate automation, CertCentral guides you through the setup process. Even if you're more experienced, our guided automation setup helps configure your credentials and client commands. If you're do-it-yourself or need a more scalable automation solution, see our advanced certificate lifecycle automation help .
DigiCert TLS/SSL automation is based on the ACME protocol (Automated Certificate Management Environment). ACME is one of the most common and robust forms of certificate lifecycle automation. No regular manual maintenance is required following initial setup. By default, we recommend the CertCentral automation agent. When you generate the automation command for this agent, the command installs the agent and configures automation.
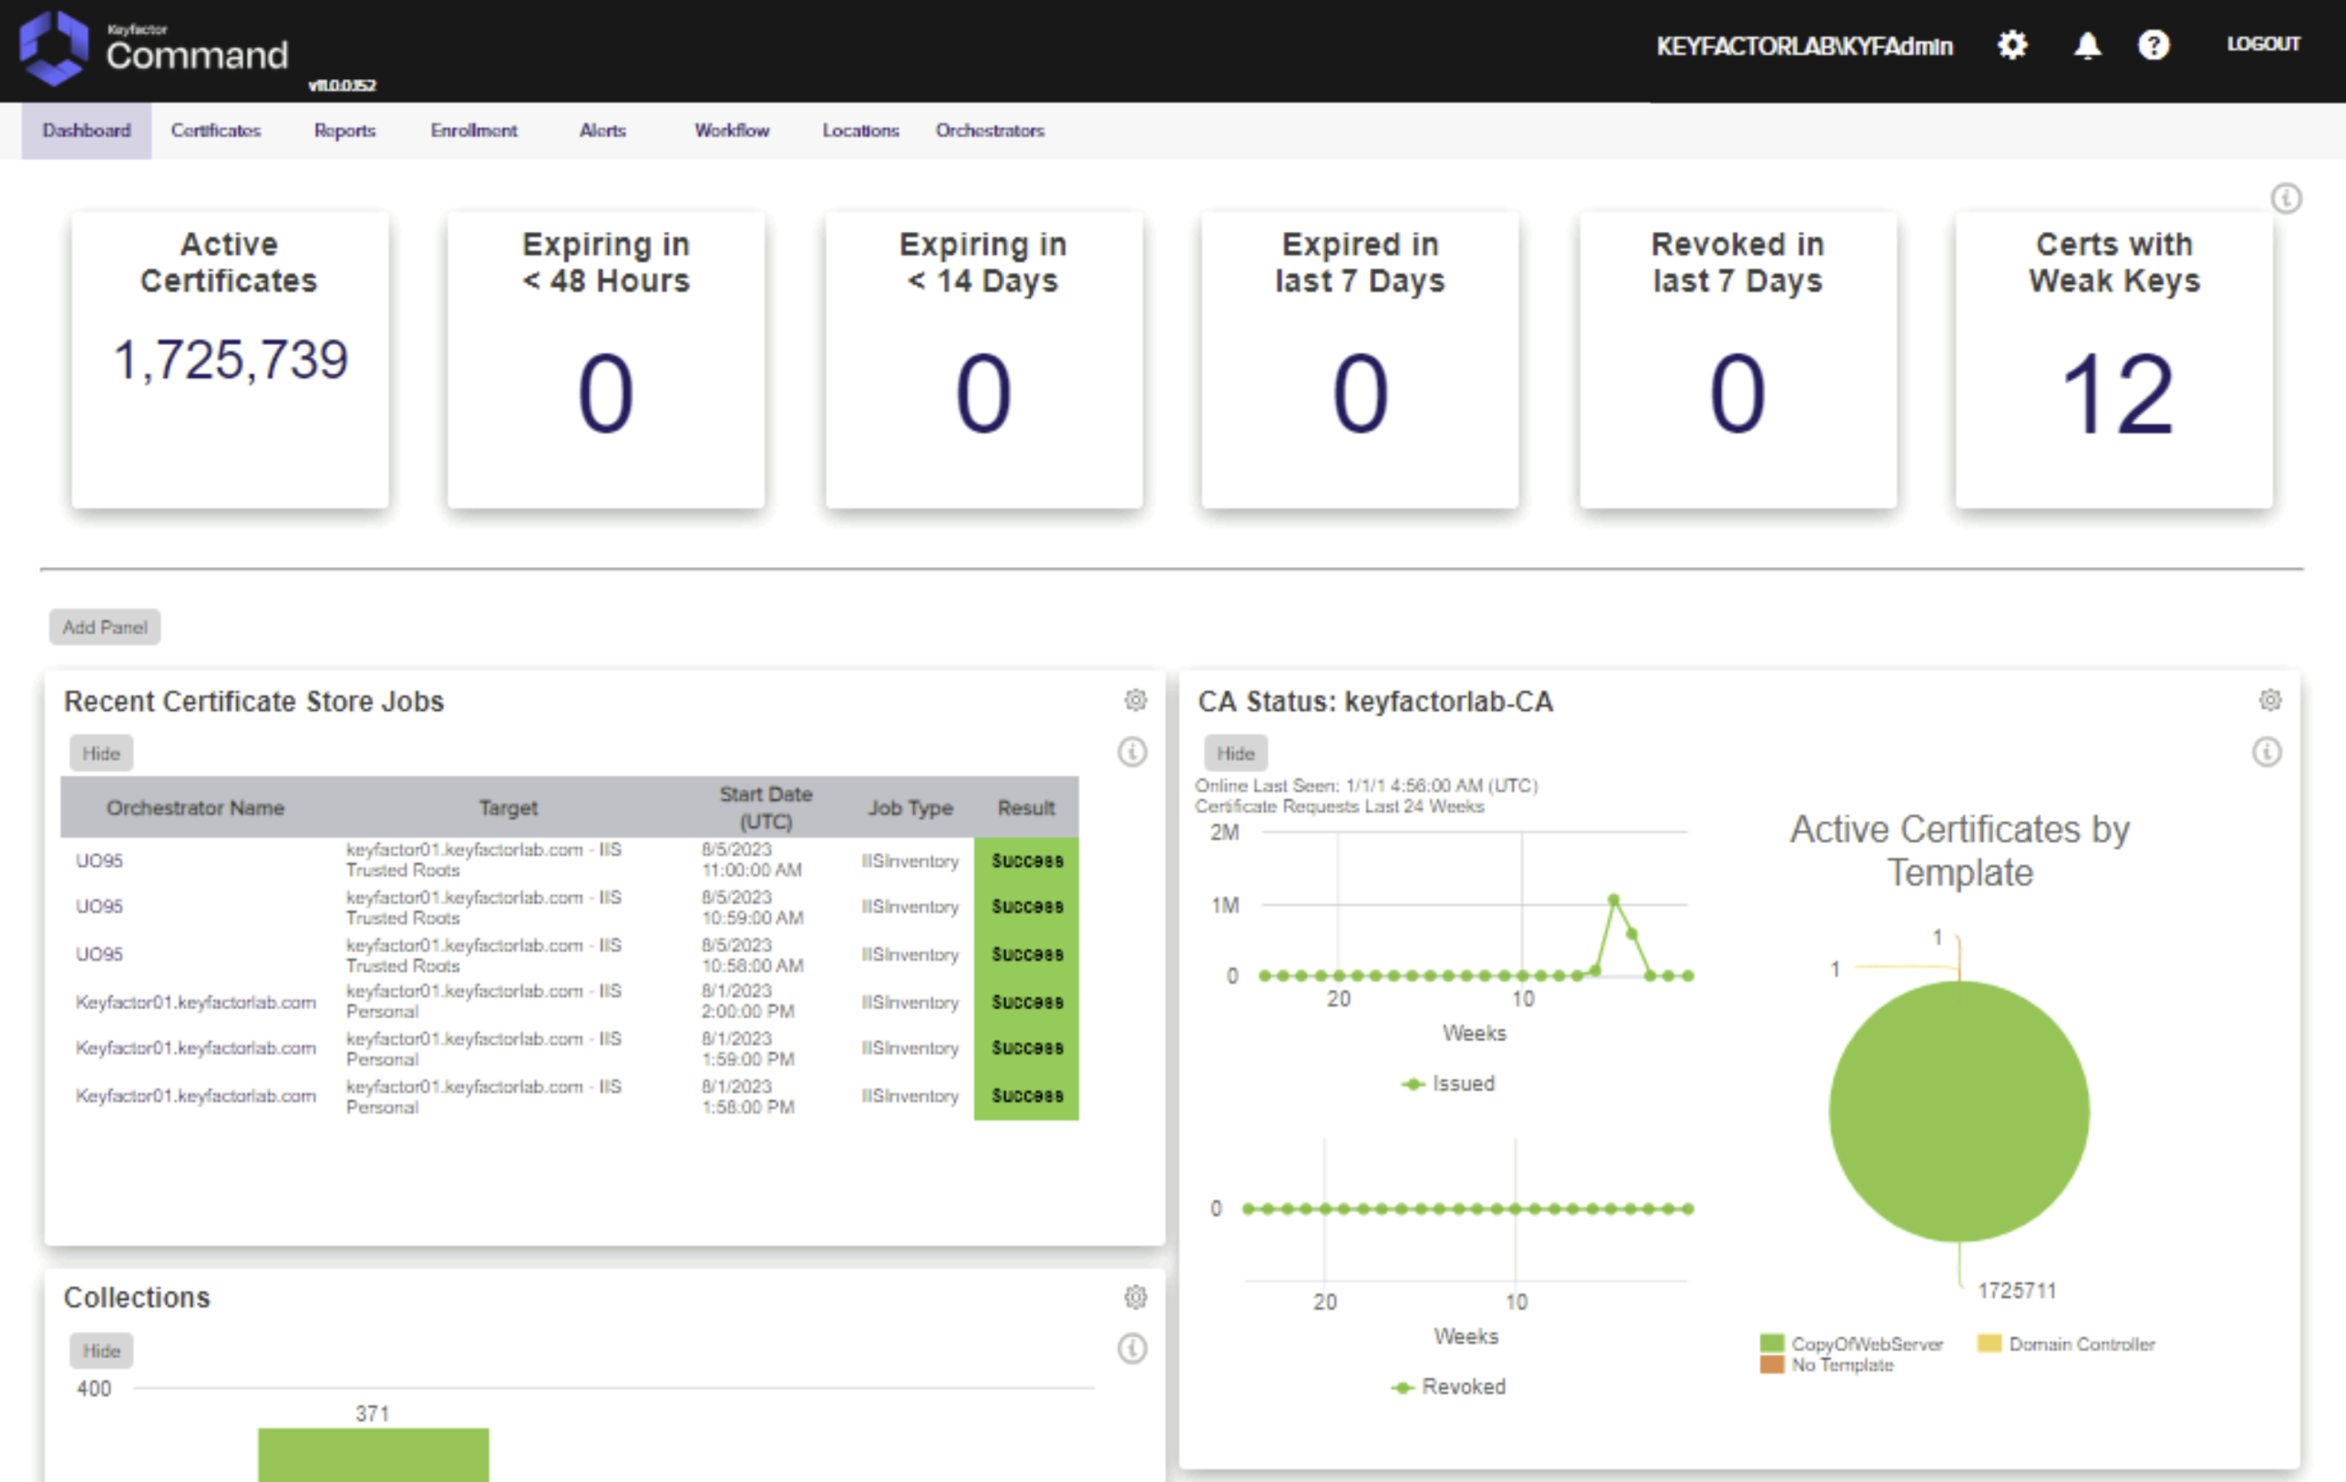
If you prefer a third-party ACME client (such as Certbot), you'll need to install the client on your web server. You can then run the ACME instructions we generate for you on your preferred client. Figure 3: Keyfactor Certificate Management - prntbl.concejomunicipaldechinu.gov.co Access to this page requires authorization. You can try signing in or changing directories .
Organizations that use an internal or nonintegrated certificate authority (CA) often rely on manual processes to renew Transport Layer Security (TLS) and Secure Sockets Layer (SSL) certificates. Manual renewal can lead to expired certificates that cause service outages, like when a web server certificate expires unnoticed and disrupts customer-facing applications. Azure Key Vault supports automatic certificate renewal for integrated CAs like DigiCert or GlobalSign , but nonintegrated CAs require a manual approach . This article presents an architecture that automates certificate renewal for nonintegrated CAs by using Key Vault, Azure Event Grid, Azure Automation, and the Key Vault extension. The solution reduces human error, minimizes service interruptions, and enforces principle of least privilege across all identities in the renewal process.
This section provides an overview of the underlying architecture that supports this solution. The diagram has two main sections. One section is labeled Azure landing zone subscription, and the other section is labeled on-premises. In the landing zone subscription section, a large box labeled CERTLC contains smaller boxes for Azure Virtual Network and an Automation account. In the Virtual Network box, two computer icons are labeled DC and ENT-CA. A dotted line that represents the Hybrid Runbook Worker connects the ENT-CA icon to the runbook worker and the CERTLC runbook in the Automation account box. The Virtual Network box also contains computer icons that represent two servers, one with the Key Vault extension and one with a custom script. A solid line connects the Virtual Network box to the on-premises section of the diagram. The Automation account box also contains the dashboard ingestion runbook. A dotted line connects this runbook to the Log Analytics workspace in the CERTLC box. The CERTLC box also contains icons that represent a storage account, Event Grid, Key Vault, and a workbook. The Azure landing zone subscription section includes icons that represent a recovery services vault, role assignments, policy assignments, Azure Network Watcher, and Microsoft Defender for Cloud. In the on-premises section, a box labeled Active Directory contains two smaller boxes for Azure Arc-enabled servers. One server uses the Key Vault extension, and the other server uses a custom script.
To monitor the process and status of expired and expiring certificates, Log Analytics stores the data, and the workspace presents it in the form of tabular and graphical dashboards. This scenario assumes that an existing public key infrastructure (PKI) is already in place and consists of a Microsoft Enterprise CA joined to an Active Directory domain. The PKI, the Active Directory domain, and the servers that require certificate renewal can reside on Azure or onâIIpremises environments. The architecture automates the renewal and deployment of certificates that the CA already issued. It doesn't distribute trust anchors or manage PKI life cycle governance.
You don't need to join the virtual machines (VMs) that host certificates to monitor for renewal to Active Directory or to Microsoft Entra ID. You only need to join the CA and the hybrid worker, if it's located on a different VM than the CA, to Active Directory. The following diagram shows the automatic workflow for certificate renewal within the Azure ecosystem.
The diagram uses arrows and numbers to show the automatic workflow for certificate renewal within the Azure ecosystem. Icons for Key Vault, a user, a server with a Key Vault extension, a CA with a Key Vault extension, an Event Grid system topic, a storage account, and an Automation account are at the top of the diagram. Arrows are labeled 1 through 9. Arrow 1 points from a certificate in the CA to Key Vault. Arrow 2 points from a certificate in Key Vault to the server. Arrow 3 points from a certificate in Key Vault to Event Grid. Arrow 4 points from Event Grid to both the storage account and the webhook in the Automation account. Arrow 5 is a bidirectional arrow that points to and from the certificate in the storage account and the Automation account. Arrow 6 is a bidirectional arrow that points to and from the certificate in the CA and the Automation account. Arrow 7 points from the certificate in the Automation account to Key Vault. Arrow 8 points from a message icon in the Automation account to a user icon at the server. Arrow 9 points from the certificate in Key Vault to the server.
Key Vault configuration: The initial phase of the renewal process entails storing the certificate object in the designated certificates section of the key vault. We recommend that you use certificate tags to configure custom email notifications by tagging each certificate with the recipient's email address. This approach lets you notify specific admins for each certificate rather than applying the same recipient to all certificates. Use the Recipient tag and set its value to one or more email addresses separated by a comma or semicolon. Tag-based notifications ensure timely alerts when the certificate renewal completes on the internal CA and when the renewed certificate becomes available in Key Vault.
You can use built-in Key Vault certificate notifications in combination with this approach, but they serve a different purpose. Built-in notifications apply globally to all certificates in the key vault and are limited to upcoming certificate expiration alerts. They use the same recipient for all certificates. Key Vault extension configuration: You must equip the servers that need to use the certificates with the Key Vault extension.
The extension is compatible with Windows and Linux systems. It supports Azure infrastructure as a service (IaaS) servers and on-premises or other cloud servers that integrate through Azure Arc . Configure the Key Vault extension to periodically poll Key Vault for any updated certificates. The polling interval is customizable and flexible, so it can align with specific operational requirements.
On some Linux distributions or hardened enterprise images, the Key Vault extension might not be available or supported. In these cases, schedule the script_for_not_supported_ARC_on_Linux_distro script as a recommended fallback. The script periodically checks Key Vault for certificate updates and applies them to the server. It can run on Azure native VMs (IaaS) and on-premises servers integrated with Azure Arc.
Event Grid integration: As a certificate nears expiration, two Event Grid subscriptions intercept this important lifetime event from the key vault. Event Grid triggers: One Event Grid subscription sends certificate renewal information to a storage account queue. The other subscription triggers the launch of a runbook through the configured webhook in the Automation account. If the runbook fails to renew the certificate, or if the CA is unavailable, a scheduled process retries renewing the runbook from that point until the queue clears. This process makes the solution robust.
To enhance the solution's resiliency, set up a dead-letter location mechanism. It manages potential errors that might occur during message transit from Event Grid to the subscription targets, the storage queue, and the webhook. Storage account queue: The runbook launches within the CA server configured as an Automation Hybrid Runbook Worker. It receives all messages in the storage account queue that contain the name of the expiring certificate and the key vault that hosts the runbook. The following steps occur for each message in the queue.
Certificate renewal: The script in the runbook connects to Azure to retrieve the certificate's template name that you set up during generation. The template is the configuration component of the CA that defines the attributes and purpose of the certificates that it generates. After the script interfaces with Key Vault, it initiates a certificate renewal request. This request triggers Key Vault to generate a certificate signing request (CSR) and applies the same template that generated the original certificate. This process ensures that the renewed certificate aligns with the predefined security policies. For more information about security in the authentication and authorization process, see Security .
The CA generates a new x509 certificate based on the correct template and sends it back to the script. This step ensures that the renewed certificate aligns with the predefined security policies. Certificate merging and Key Vault update: The script merges the renewed certificate back into the key vault. This step finalizes the update process and removes the message from the queue. Throughout the entire process, the private key of the certificate is never extracted from the key vault.
Monitoring and email notification: All logs related to operations that run across various Azure components, including the Automation account, Key Vault, the storage account queue, and Event Grid, should be sent to the Azure Monitor Logs workspace. After the certificate merges into the key vault, the script sends an email message to administrators to notify them of the outcome.
Certificate retrieval: The Key Vault extension on the server plays an important role during this phase. It automatically downloads the latest version of the certificate from the key vault into the local store of the server that uses the certificate. You can configure multiple servers with the Key Vault extension to retrieve the same certificate from the key vault, including wildcard or with multiple Subject Alternative Name (SAN) certificates.
For Linux distributions in which you can't install the Key Vault extension, schedule the script_for_not_supported_ARC_on_Linux_distro script to achieve the same functionality as the extension.
This solution uses various components to handle automatic certificate renewal on Azure. The following sections describe each component and its specific purpose. The Key Vault extension is a tool installed on servers that provides automatic refresh of certificates stored in an Azure key vault. In this architecture, you must install the Key Vault extension on servers that require automatic certificate renewal. For more information about installation procedures for various servers, see the following articles: The following scripts are samples that you can run from Azure Cloud Shell to configure the Key Vault extension: Certificate Store, Name, and Location: The certificate store where the certificate is stored. On Windows servers, the default value for Name is My and Location is LocalMachine , which is the personal certificate store of the computer. On Linux servers, you can specify a file system path, assuming that the default value is AzureKeyVault , which is the certificate store for Key Vault.
linkOnRenewal: A flag that indicates whether the certificate should be linked to the server on renewal. If the flag is set to true on Windows machines, it copies the new certificate in the store and links it to the old certificate, which effectively rebinds the certificate. The default value is false , which means that an explicit binding is required. pollingIntervalInS: The polling interval for the Key Vault extension to check for certificate updates. The default value is 3600 seconds (1 hour).
authenticationSetting: The authentication setting for the Key Vault extension. For Azure servers, you can omit this setting so that the extension uses the VM's system-assigned managed identity to authenticate to the key vault. For on-premises servers, if you specify the setting msiEndpoint = "http://localhost:40342/metadata/identity" , the extension uses the service principal associated with the computer object created during Azure Arc onboarding.
Specify the Key Vault extension parameters only during the initial setup. This approach ensures that the parameters remain unchanged throughout the renewal process. An Automation account is a cloud-based service that automates tasks via runbooks. In this architecture, it handles the certificate renewal process. You need to configure the account with a runbook by using the PowerShell script .
2. System Architecture & Core Working Principles You also need to create a Hybrid Worker Group. Associate the Hybrid Worker Group with a Windows Server member of the same Active Directory domain of the CA, ideally the CA itself, for launching runbooks. The runbook must have an associated webhook initiated from the Hybrid Runbook Worker. Configure the webhook URL in the event subscription of the Event Grid system topic.
The storage account queue is a message queue within Azure Storage. In this architecture, it stores the messages that contain the name of the certificate being renewed and the key vault that contains the certificate. Configure the storage account queue in the event subscription of the Event Grid system topic. The queue handles decoupling the script from the certificate expiration notification event. It supports persisting the event within a queue message. This approach helps ensure that the renewal process for certificates is repeated through scheduled jobs even if problems occur during the script's run.
The Hybrid Runbook Worker is a feature of Automation that you use to run runbooks on machines located in a datacenter. In this architecture, it runs the certificate renewal runbook. Install the Hybrid Runbook Worker by using the Azure Hybrid Worker extension method, which is the supported mode for a new installation. You create the worker and associate it with a Windows Server member in the same Active Directory domain of the CA, ideally the CA itself.
Key Vault is the secure repository for certificates. In this architecture, it stores certificates issued only by the same nonintegrated CA. Under the event section of the key vault, associate the Event Grid system topic with the webhook of the Automation account and a subscription. Event Grid is an event-routing service. In this architecture, it handles event-driven communication within Azure. Configure Event Grid by setting up the system topic and event subscription to monitor relevant events. Relevant events include certificate expiration alerts, actions triggered within the automation workflow, and messages posted in the storage account queue. Configure the Event Grid system topic by using the following parameters: Source Type: The type of the source. For example, the source type for this solution is Azure Key Vault .
Event Type: The event type to monitor.
For example, the event type for this solution is Microsoft.KeyVault.CertificateNearExpiry . This event triggers when a certificate is near expiration.
Endpoint Type: The type of endpoint to use. For example, the endpoint type for this solution is Webhook . Endpoint: The URL of the webhook associated with the Automation account runbook. For more information, see Automation account . Endpoint Type: The type of endpoint to use. For example, the endpoint type for this solution is StorageQueue .
Log Analytics workspaces and Azure workbooks are Azure resources that collect, aggregate, and analyze data. In this architecture, they enhance monitoring and visualization of certificate statuses stored in Key Vault. These components are crucial for maintaining visibility into certificate health: Log Analytics workspace: Collects and stores data about certificate states. It identifies expired certificates, certificates that expire soon, and valid certificates.
Azure workbook: Retrieves data from the Log Analytics workspace and presents it in a dashboard with visual representations, such as pie charts and detailed tables. It categorizes certificates into Not Expired (green), Expiring Soon (yellow), and Expired (red). The following components retrieve and present certificate information in the workbook: Data ingestion runbook execution: A runbook runs directly from Azure, without requiring the context of a Hybrid Worker. The runbook retrieves certificate data from the key vault and sends it to a custom table defined in the Log Analytics workspace.
The runbook runs on a scheduled cadence. Workbook visualization: A workbook queries the data from the custom table and displays it in both a pie chart and a detailed table. It highlights certificates based on their expiration status. By integrating these extra components, your solution builds a more comprehensive approach to certificate life cycle management.
This solution uses an Automation account to orchestrate the certificate renewal process. It also uses Hybrid Runbook Worker to provide the flexibility to integrate with a CA on-premises or in other clouds. An alternative approach is to use Azure Logic Apps. The main difference between the two approaches is that the Automation account is a PaaS solution, and Logic Apps is a software as a service (SaaS) solution.
Logic Apps is a fully managed service, so you don't need to manage the underlying infrastructure. It can also integrate with external connectors. This capability expands the range of notification options, such as engagement with Microsoft Teams or Microsoft 365. Logic Apps doesn't have a feature similar to Hybrid Runbook Worker, which results in less flexible integration with the CA, so an Automation account is the preferred approach.
Every organization requires secure and efficient management of their certificate life cycle. Failing to update a certificate before expiration can lead to service interruptions and incur significant costs for the business. Enterprises typically operate complex IT infrastructures that involve multiple teams who are responsible for the certificate life cycle. The manual nature of the certificate renewal process often introduces errors and consumes valuable time.
This solution addresses these challenges by automating certificate renewal issued by Microsoft Certificate Service. The service is widely used for various server applications, such as web servers and SQL servers, and for encryption, nonrepudiation, signing purposes, and ensuring timely updates and secure certificate storage within Key Vault. The service's compatibility with Azure servers and on-premises servers supports flexible deployment.
This article focuses on the automated renewal, retrieval, and deployment of certificates that an enterprise CA already issued. The architecture assumes that a trusted PKI is already in place and that root and intermediate CA certificates are distributed to consuming systems through organization-approved trust management processes. PKI design, CA hierarchy definition, trust-anchor distribution, and CA rollover procedures are outside the scope of this article.
Address these activities through your organization's PKI governance framework. For more information, see Trust distribution considerations . Require automation in the certificate renewal process to accelerate operations and minimize errors, which helps avoid business loss and service-level agreement (SLA) violations.
This architecture serves as a foundational deployment approach across workload landing zone subscriptions. You can extend the same life cycle pattern to Azure App Service, Azure Application Gateway, and Kubernetes workloads that integrate with Key Vault. These considerations implement the pillars of the Azure Well-Architected Framework, which is a set of guiding tenets that you can use to improve the quality of a workload. For more information, see Well-Architected Framework .
Security provides assurances against deliberate attacks and the misuse of your valuable data and systems. For more information, see Design review checklist for Security . Key Vault securely stores certificates as encrypted secrets protected by Azure role-based access control (Azure RBAC). In environments that have strict compliance requirements, such as NIS2 or public-sector regulations, consider evaluating Azure Key Vault Managed HSM for key protection if you need to keep the certificate renewal workflow that this article describes.
The system account of the Hybrid Runbook Worker, which operates under the VM's account Least privilege is rigorously enforced across all identities engaged in the certificate renewal procedure. The system account of the Hybrid Runbook Worker server must have the right to enroll certificates on one or more certificate templates that generate new certificates.
On the key vault that contains the certificates, the Automation account identity must have the Key Vault Certificate Officer role. Additionally, servers that require certificate access must have Get and List permissions within the Key Vault certificate store. On the storage account queue, the Automation account identity must have the Storage Queue Data Contributor , Reader and Data Access , and Reader roles.
In scenarios in which the Key Vault extension deploys on an Azure VM, authentication occurs via the VM's managed identity. However, when the extension deploys on an Azure Arc-enabled server, a service principal handles authentication. You must assign the Key Vault secret user role within the key vault that stores the certificate to both the managed identity and the service principal. You must use a secret role because the certificate is stored in the key vault as a secret.
Certificate renewal automation is only one aspect of certificate life cycle management. A renewed certificate is trusted only if the systems that consume it already trust the issuing CA chain. Define processes that: Distribute root and intermediate CA public certificates to all consuming systems. Protection of the CA private keys remains a responsibility of the PKI and isn't part of this renewal workflow.
Plan root and intermediate CA rollover independently from end-entity certificate renewal. Distribute the new trust anchor alongside the existing one before any dependent certificate changes, and retire the previous anchor only after you validate the new chain. Verify trust store requirements for the operating systems, platforms, and application runtimes that consume the certificates.
Delivery mechanisms differ across these environments, so follow the product documentation for each one. Trust store mechanisms and constraints differ significantly across platforms, and some Azure services don't support custom trust anchors. Consult the product documentation for each environment that consumes the certificates, such as: Manage these activities as part of your organization's PKI governance framework and your encryption and key management strategy rather than through the renewal workflow that this article describes.
Cost Optimization focuses on ways to reduce unnecessary expenses and improve operational efficiencies. For more information, see Design review checklist for Cost Optimization . 3. Software Implementation, Frameworks & Protocols This solution uses Azure PaaS solutions that operate under a pay-as-you-go framework to optimize cost. Expenses depend on the number of certificates that need renewal and the number of servers equipped with the Key Vault extension, which results in low overhead.
Expenses that result from the Key Vault extension and the Hybrid Runbook Worker depend on your installation choices and polling intervals. The cost of Event Grid corresponds to the volume of events that Key Vault generates. The cost of the Automation account correlates with the number of runbooks that you use. The cost of Key Vault depends on various factors, including Standard or Premium SKUs, the quantity of stored certificates, and the frequency of operations conducted on the certificates.
Similar considerations for Key Vault configuration apply to the storage account. In this scenario, a Standard SKU with locally redundant storage replication is sufficient for the storage account. Generally, the cost of the storage account queue is minimal. To estimate the cost of implementing this solution, use this preconfigured estimate in the Azure pricing calculator . Adjust the values to match your certificate volume and operational requirements.
Operational Excellence covers the operations processes that deploy an application and keep it running in production. For more information, see Design review checklist for Operational Excellence . The automatic certificate renewal procedure securely stores certificates by applying standardized processes across all certificates within the key vault.
Integration with Event Grid triggers supplementary actions, such as notifying Microsoft Teams or Microsoft 365 and streamlining the renewal process. This integration significantly reduces certificate renewal time and mitigates the potential for errors that might lead to business disruptions and SLA violations. Integration with Azure Monitor, Microsoft Sentinel, Microsoft Security Copilot, and Microsoft Defender for Cloud facilitates continuous monitoring of the certificate renewal process. It supports anomaly detection and ensures that robust security measures are maintained. Defender for Cloud contributes primarily through posture management and alert correlation rather than direct certificate renewal event handling.
Select the following button to deploy the environment described in this article. The deployment takes about two minutes to complete and creates a key vault, an Event Grid system topic configured with the two subscriptions, a storage account that contains the CERTLC queue, and an Automation account that contains the runbook and the webhook linked to Event Grid. For more information about the parameters that you need for the deployment, see the code sample portal.
You can deploy a full lab environment to demonstrate the entire automatic certificate renewal workflow. Use the code sample to deploy the following resources: Active Directory Certificate Services (AD CS) within a CA VM, joined to the domain, configured with a template, WebServerShort , for enrolling the certificates to renew.
A Windows Simple Mail Transfer Protocol (SMTP) server installed on the same VM as the CA for sending email notifications. MailViewer also installs to verify the email notifications sent. The Key Vault extension installed on the domain controller VM for retrieving the renewed certificates from the Key Vault extension.
A vendor-neutral reference architecture for designing secure, scalable, and automated TLS/PKI infrastructure in enterprise environments. This repository contains a practical reference architecture for implementing Enterprise Public Key Infrastructure (PKI) and Certificate Lifecycle Management (CLM).
The document is based on real implementation experience, industry best practices, and practical lessons learned while assisting customers with SSL/TLS deployment, certificate automation, and PKI architecture. This document is intended for educational purposes and aims to help organizations build secure, scalable, and future-ready PKI environments.
I enjoy designing secure, scalable, and vendor-neutral PKI architectures while helping organizations bridge business requirements with technical implementation. Centralized PKI Architecture & Enterprise SSL Automation system design for multicloud environments, built using Zero Trust and Defense in Depth principles.
Certificates are the backbone of trust on the internet and within enterprise networks. They authenticate servers, encrypt communications, sign code, verify device identities, and enable mutual TLS between services. Yet certificate management remains one of the most operationally challenging aspects of identity and security. The consequences of poor certificate management are severe and immediate. An expired certificate causes an outage, your website goes down, your API stops working, your VPN becomes inaccessible. A compromised certificate enables man-in-the-middle attacks. An over-issued certificate expands your attack surface. These are not theoretical risks: certificate-related outages make headlines regularly, affecting organizations from airlines to cloud providers.
This guide provides a complete approach to certificate lifecycle management, from PKI design through automated renewal and revocation. The root CA is kept offline (not connected to any network) and is only used to sign intermediate CA certificates. The intermediate CAs are online and handle day-to-day issuance. If an intermediate CA is compromised, it can be revoked without replacing the root.
Manual certificate renewal does not scale and is the primary cause of certificate-related outages. Automate everything. When a private key is compromised or a certificate is no longer needed, revocation must happen immediately. CRLs are lists of revoked serial numbers that clients download periodically. They are simple but have drawbacks: the CRL can grow large, and there is a delay between revocation and the next CRL publish.
OCSP provides real-time revocation checking. The client sends the certificate's serial number to the OCSP responder and gets back a signed "good," "revoked," or "unknown" response. The most elegant revocation strategy is to not need revocation at all. If certificates are valid for only 24 hours (or less), a compromised certificate expires before an attacker can make meaningful use of it. This approach requires strong renewal automation but eliminates the complexity of CRL/OCSP infrastructure.
Certificate pinning adds a layer of defense by ensuring your application only trusts specific certificates or CAs, rather than any CA in the system trust store. Use pinning sparingly and always include a backup pin (for the next certificate you will rotate to). Pinning the wrong thing or failing to update pins before certificate rotation causes outages.
Certificate lifecycle management is an operational discipline, not a one-time project. Certificates are constantly being issued, renewed, and revoked. The organizations that avoid certificate-related outages are those that invest in automation, monitoring, and short certificate lifetimes. Start by gaining visibility: discover every certificate in your environment and monitor their expiry dates. Then automate renewal: use ACME for public certificates and Vault PKI or cert-manager for internal certificates. Finally, shorten lifetimes: move toward 90-day public certificates and 24-hour internal certificates. Each step reduces risk and operational burden.
Q: How short should certificate lifetimes be? A: As short as your automation can support. For public-facing TLS, 90 days (Let's Encrypt default) is standard. For internal services with strong automation, 30 days or less. For service mesh (SPIFFE/SPIRE), 1-24 hours. Q: Do I need a private CA? A: If you have internal services that communicate over mTLS, client certificate authentication, or code signing, yes. Public CAs issue certificates for public DNS names only. Internal services need a private CA.
Q: What about wildcard certificates? A: Wildcard certificates (*.example.com) are convenient but risky. A single compromised key exposes all subdomains. Use them at the edge (CDN, load balancer) where they reduce certificate count, but use specific certificates for individual services behind the load balancer. Q: How do I handle certificate rotation with zero downtime? A: Most web servers and load balancers support certificate reload without restart (NGINX: nginx -s reload , HAProxy: set ssl cert ). For applications, implement hot-reloading of TLS certificates from the filesystem or vault.
Q: What is ACME and should I use it? A: ACME (Automated Certificate Management Environment) is the protocol that Let's Encrypt uses for automated certificate issuance and renewal. You should use ACME for all public certificates and consider using it for private certificates too (step-ca supports ACME). Q: How do I prepare for post-quantum cryptography? A: Start by inventorying all certificates and their algorithms. Monitor NIST PQC standards. Test hybrid certificates (classical + PQC) when your CA supports them. Plan for a migration window of 3-5 years once PQC standards are finalized.
Certificate lifecycle management (CLM), often called certificate management, is the practice of discovering, issuing, renewing, and revoking X.509 certificates, Certificate management explained: discovery, issuance, renewal, and revocation across public and private PKI, why the CA/Browser Forum schedule to 47-day certif A complete guide to managing machine identities including certificates, service accounts, API keys, secrets rotation, PKI setup, and machine-to-machine authenti The best open-source PKI tools in 2026, from EJBCA and step-ca to Dogtag, cert-manager, OpenXPKI, and Boulder, compared on protocol support, automation, and who Complete guide to automating the user lifecycle from onboarding through role changes to offboarding, including orphan account detection and provisioning workflo A practical guide to automating API key rotation with zero downtime, covering rotation strategies, secrets management integration, dual-key patterns, monitoring 4. Practical Deployment, Analysis & Case Studies Access to this page requires authorization. You can try signing in or changing directories .
In this tutorial, you will learn how to deploy the components for the Certificate Lifecycle on Azure scenario. The goal of the LAB is to showcase a comprehensive solution for the automated renewal of certificates issued by non-integrated Certificate Authorities. To initiate the deployment of the LAB environment, verify to have the Owner role on the subscription then click on the Deploy to Azure button provided above. This action will trigger the deployment process within the Azure Portal. You will be prompted to provide input parameters.
For resources such as key vaults, automation accounts and event-grid, which necessitate globally unique names, kindly replace the UNIQUESTRING placeholder with a unique string of your choice, following the resource's constraints (e.g., maximum character count, lowercase only, etc.). Additional parameters needed for the deployment can be left to their default values for the purpose of this LAB. Those parameters are listed in the table below: The LAB environment is designed to represent an in-depth technical overview of an automated renewal process for certificates from non-integrated CAs, which embodies the entire workflow shown below.
The LAB environment is structured to showcase the seamless workflow, allowing for a complete demonstration of the automated certificate management process. Let's delve into the key components, shown in the diagram below, constituting this environment: The CA virtual machine is configured also as an SMTP server to allow for email communication in this demo environment.
RunBook Execution Steps on the CA as a Hybrid RunBook Worker: The RunBook performs the following steps: The RunBook performs the actions described above on Azure, using the System Managed Identity of the automation account, and inside the Certification Authority, using the system account (domain computer account) of the CA server. To access the Azure Key Vault, the System Managed Identity of the automation account has been granted the " Key Vault Certificate Officer " role on the Key Vault.
Certificate Retrieval: The DC01, configured as the server expecting the renewed certificate via the Key Vault extension, receives the certificate in its machine's personal certificate store after the polling period elapses. To access the Azure Key Vault, the System Managed Identity of the DC01 virtual machine has been granted the " Key Vault Secret User " role on the Key Vault.
Real-World Implementation: In a real-world scenario, an additional step is required to bind the certificate to the respective service (e.g., binding the certificate to IIS for a web certificate). The LAB environment also includes the deployment of a Dashboard to monitor the expiration status of certificates stored in the Key Vault. While these resources are optional in the production environment, they are deployed and automatically configured in the LAB environment to showcase the dashboard's output. The workflow includes the following additional steps: Data Ingestion Runbook Execution: A Runbook, executed directly from Azure (without requiring the context of a Hybrid Worker), retrieves certificate data from the Key Vault and sends this information to a custom table defined in the Log Analytics workspace. The Runbook runs on a scheduled cadence.
Workbook Visualization: A Workbook queries the data from the custom table and displays it in both a pie chart and a detailed table, highlighting certificates in the following statuses: "Not Expired" (green), "Expiring Soon" (yellow), and "Expired" (red). The LAB is fully automated and requires no manual intervention. The following steps are provided to verify the whole process and to showcase the seamless workflow.
LAB environment deployment: The LAB environment is deployed using the ARM template provided in this repository. Connect to the Domain Controller VM via RDP using the credentials provided during the deployment process. Use this VM as a jumpbox to connect to the CA VM with the same credentials (member of Domain Admins group) used to connect to the DC. Certificate Creation: The certificate is created and stored in the Key Vault. The certificate is configured with a 5-day validity, and the Key Vault is configured to trigger the Event Grid when the certificate is nearing expiration. Open the KeyVault an select the Certificate Section. You should see the certificate created by the deployment named " democert ".
To access the certificate section you need at least the "Key Vault Certificate Officer" role on the Key Vault. Certificate Near Expiration The certificate is nearing expiration, and the Key Vault triggers the Event Grid, which in turn triggers the Webhook, initiating the execution of the RunBook. Open the Event Grid System Topic and select the Subscriptions Section. You should see the " CertLC " subscription, select it to see the URL of the Webhook created by the deployment. The graph should show the events generated by the Key Vault that correspond to the triggering of the Webhook.
RunBook Execution The RunBook is executed on the CA as a Hybrid RunBook Worker. At the end of the execution, the certificate is renewed and stored in the Key Vault and an email is sent to the recipient. Connect to the CA VM and open the Certificate Server Console. Select " Issued Certificate " and you should see the renewed certificate. Open the MailViewer tool provided on the desktop of the CA server (which also serves as an SMTP server in this LAB) and select the most recent ".eml" file. You should see the email sent by the RunBook to the recipient defined in the certificate's "Recipient" tag.
Certificate Retrieval At this stage, the certificate is renewed and stored in the Key Vault. The tag " Recipient " is maintained in the new certificate object inside the Key Vault. The DC01, configured as the server expecting the renewed certificate via the Key Vault extension, receives the certificate in its machine's personal certificate store after the polling period elapses. Connect to the DC VM and open the Certificate Manager Console. Select "Personal" and you should see the renewed certificate.
Dashboard A scheduled job runs every hour to retrieve information about the expiration of the certificates stored in the Key Vault. To ensure that data is collected immediately after deployment, you can manually run the CertLCDashboardDataIngestion Runbook. To view the dashboard displaying the expiration status of certificates stored in your Key Vault, navigate to the Monitor section and select the created Workbook.
Note: In the LAB deployment, the Runbook adds some "fake" data to demonstrate all possible expiration statuses: 'Not Expired' (green), 'Expiring Soon' (yellow), and 'Expired' (red). The Production base deployment creates a Key Vault, an Event Grid System Topic configured with two subscriptions, a Storage Account containing the 'certlc' queue and an Automation Account containing the RunBook and the webhook linked to the Event Grid.
To initiate the deployment of the Production environment, verify to have the Owner role on the subscription then click on the Deploy to Azure button provided above . This action will trigger the deployment process within the Azure Portal. You will be prompted to provide input parameters. Additional parameters needed for the deployment can be left to their default values. Those parameters are listed in the table below: To integrate the solution with your existing environment, you need to perform the following manual steps: Configure an Hybrid Worker VM installing the Azure Hybrid Worker Extension on the Certification Authority server (or on a server joined to the same AD domain) and adding it to the Hybrid Worker Group defined in the Automation Account.
Add the 'System' account of the Hybrid RunBook Worker VM the "Read" and "Enroll" permissions to the Certificate Template(s) used to generate the certificates. Install the Key Vault extension on the servers that need to retrieve the renewed certificates from the Key Vault. Add the 'Key Vault Secret User' role to the the servers with the Key Vault extension on the Key Vault containing the certificates.
Import the certificates into the Key Vault and TAG them with the administrator e-mail address for notification purposes. If multiple recipients are required, the e-mail addresses should be separated by comma or semicolon. The expected tag name is 'Recipient' and the value is the e-mail address(es) of the administrator(s). The optional Production dashboard deployment sets up a Log Analytics workspace with a custom table to track the expiration dates of each certificate stored in the Key Vault. It also includes a Runbook, configured within the existing Automation Account, to ingest data into this custom table, and a Workbook to visualize the certificates' expiration status.
To initiate the deployment of the optinal dashboard in the Production environment, verify to have the Owner role on the subscription then click on the Deploy to Azure button provided above . This action will trigger the deployment process within the Azure Portal. You will be prompted to provide input parameters. Additional parameters needed for the deployment can be left to their default values. Those parameters are listed in the table below: | Schedule Dashboard Data Start Time | The start time of the scheduled runbook job. | Initial start time with a recurrence of 1 hours | To integrate the dashboard with your existing environment, you need to perform the following manual steps: Certificate management explained: discovery, issuance, renewal, and revocation across public and private PKI, why the CA/Browser Forum schedule to 47-day certificates makes automation mandatory, and how to run device certificates at scale.
Certificate lifecycle management is the practice of discovering, issuing, deploying, renewing, and revoking certificates across an organization. Most teams have a certificate authority and no lifecycle management, which is why expired certificates remain one of the most common causes of self-inflicted downtime. That is about to get harder. The CA/Browser Forum approved Ballot SC-081v3 in April 2025, phasing maximum public TLS certificate validity from 398 days down to 47 days between 2026 and 2029 . A yearly renewal is a calendar entry. A six-weekly renewal across a few hundred certificates is a full-time job, or an automation problem.
This is what the lifecycle actually involves, where it breaks, and what to automate first. For the concepts see PKI , X.509 , and certificate lifecycle . 5. Performance Evaluation & Extended Technical Observations You cannot renew what you do not know about, and every organization has certificates nobody remembers: on a forgotten load balancer, inside a container image, on a vendor appliance, issued from an internal CA that was decommissioned.
Discovery scans network ranges, certificate transparency logs for your domains, and cloud provider certificate stores. The output that matters is not a list, it is a list with an owner against each entry. An inventory of 4,000 certificates with no owners is an inventory you cannot act on. How a certificate request is authenticated and approved. For public TLS this means domain control validation, usually over ACME. For private PKI it means an enrolment protocol appropriate to what is enrolling: The security question at this stage is what proves the requester is entitled to the identity in the certificate. For workloads, platform attestation answers it better than a shared enrolment secret. See workload identity .
The stage that quietly defeats automation. A certificate is issued and then has to reach the load balancer, the Kubernetes secret, the Java keystore, the appliance's web console, and every replica. Where deployment is manual, renewal cadence is limited by human availability regardless of how automated issuance is. Expiry monitoring should be independent of the issuing system, because the failure mode you are guarding against includes the issuing system not renewing. Alert on time-to-expiry with enough lead time to act, and alert on renewal failures rather than only on expiry, which is too late.
Revocation through CRL and OCSP has never worked well at internet scale, which is a large part of why the industry chose shorter lifetimes instead. Treat revocation as necessary for private PKI, where you control the clients, and as unreliable for public certificates, where expiry is the real control. Key rotation matters more than most teams treat it. Renewing with the same key indefinitely means a key compromised years ago is still valid today. Generate a new key pair on renewal.
The stage nobody assigns. A certificate is a machine credential, so it needs the same things every other non-human identity needs: a named owner, a known expiry, a rotation path, and a record of where the private key lives. Without ownership, the other five stages produce reports rather than outcomes. Manual renewal stops being viable. A process that works for 50 certificates once a year fails at eight times the frequency.
Anything still renewed by a human needs an automation path or a plan to move it behind something that has one. Deployment automation becomes the bottleneck, not issuance. ACME solves getting the certificate. Getting it onto the appliance that only accepts a manual upload through a web console is the remaining work, and it is usually the argument for putting such systems behind a reverse proxy that can automate.
Certificate inventory accuracy becomes operationally critical. At annual renewal, an unknown certificate fails once a year. At 47 days it fails eight times a year, which at least surfaces the problem faster. Note the scope: the CA/Browser Forum requirements bind public CAs. Private CAs can still issue long-lived certificates, and many organizations will. That is a legitimate choice for internal service-to-service traffic, and a bad habit if it means internal certificates are never rotated.
Open-source PKI is capable enough to run in production: EJBCA for full enterprise hierarchies with SCEP and CMP, step-ca for lightweight ACME-native internal CAs, Dogtag inside FreeIPA estates. Our open-source PKI comparison covers the trade-offs. Commercial certificate lifecycle platforms earn their cost on discovery breadth across heterogeneous estates, integration with the appliances and platforms you cannot automate yourself, and the reporting a regulated environment needs. See the PKI and certificate lifecycle vendor category .
The decision usually comes down to how heterogeneous your estate is. A cloud-native environment with everything behind load balancers and Kubernetes can automate with open-source tooling. An estate with network equipment, industrial systems, and appliances across multiple vendors is where a commercial platform pays for itself. A complete guide to managing the certificate lifecycle, covering PKI fundamentals, certificate issuance, automated renewal, revocation strategies, monitoring fo A complete comparison of the top 10 PAM solutions in 2026, covering CyberArk, BeyondTrust, Delinea, and more to help you secure privileged accounts across your Compare the top 5 CIEM platforms, Ermetic (Tenable), Zscaler CIEM, CrowdStrike Falcon Cloud Security, Wiz, and Orca Security, to manage cloud permissions, reduc Complete guide to automating the user lifecycle from onboarding through role changes to offboarding, including orphan account detection and provisioning workflo Firmware security firm Lava found that 67 percent of 36,872 internet-exposed Baseboard Management Controllers hand over IPMI authentication hashes before a logi Public Key Infrastructure (PKI) automation has become essential for modern organisations managing thousands of digital certificates across complex environments. Manual certificate management is no longer sustainable, leading to security vulnerabilities, operational inefficiencies, and compliance risks. This comprehensive guide explores PKI automation strategies that streamline certificate lifecycle management whilst maintaining robust security postures.
Traditional certificate management processes are fraught with challenges that can compromise security and operational efficiency: PKI automation encompasses the entire certificate lifecycle, from issuance to revocation, with minimal human intervention. Modern automation solutions address key areas: Streamlined certificate provisioning reduces manual errors and accelerates deployment: Complete automation of the certificate lifecycle ensures consistent security practices: PKI automation is no longer optional for organisations managing complex digital certificate environments. By implementing comprehensive automation strategies, organisations can significantly reduce security risks, improve operational efficiency, and ensure compliance with regulatory requirements.
The key to successful PKI automation lies in careful planning, proper tool selection, and ongoing optimisation. Partnering with experienced PKI automation specialists can help ensure your implementation is robust, secure, and aligned with your organisation's specific needs. Our PKI automation experts can help you design and implement comprehensive certificate lifecycle management solutions tailored to your organisation's requirements.
Learn how to implement Zero Trust architecture in your organisation with practical steps and best practices. Comprehensive guide to DNS security covering DoH, DoT, DNSSEC, and advanced threat protection strategies. In a controlled study by Horizon3 researchers, models that explicitly identified a trap in their reasoning still attacked it 73.4% of the time. Read the findings and see what they mean for canaries, decoys, and early detection.
TLS certificate expiration has caused outages at Microsoft, Azure, LinkedIn, Spotify, and dozens of enterprise IT environments that did not make the news. The pattern is consistent: a certificate was issued, added to a spreadsheet or forgotten entirely, and when it expired, the service it protected stopped working. In 2025, this problem is getting harder, certificate validity periods are shortening (Apple has proposed 47-day maximum), the number of certificates per enterprise is growing (DevOps, microservices, and cloud-native architectures have multiplied certificate counts), and post-quantum migration will require replacing virtually every certificate in the enterprise. Certificate lifecycle management (CLM) has moved from a nice-to-have to a core infrastructure security capability.
Understanding how certificate sprawl develops helps design governance that prevents it. Manual certificate issuance without central tracking: The traditional PKI workflow: a team needs a certificate, they submit a CSR to an internal CA or external CA, receive the certificate, install it, and... nothing. No system was updated with the expiration date. No monitoring is configured. In 12 months (or 13 months, or 2 years), the certificate expires and the first notification is a user error.
DevOps and microservices multiplication: A monolithic application needed one certificate. The same application decomposed into 50 microservices may need 50 certificates, for TLS between services, for service identity in a service mesh, for mutual TLS (mTLS) authentication between components. Teams self-provisioning certificates without central visibility creates rapid sprawl.
Cloud and CDN certificates outside PKI visibility: AWS Certificate Manager, Azure App Service certificates, Cloudflare-managed certificates, and GCP-managed SSL certificates may be managed by individual application teams with no visibility from the central security or infrastructure team. These represent a growing fraction of total enterprise certificates. Shadow certificates: Certificates issued directly to developers, operations staff, or external vendors without going through any central process. These often have long validity periods, weak key parameters, or are issued by CAs not on the organization's approved CA list.
Validity period reduction forcing faster rotation: Historically, TLS certificates were valid for 2-3 years. Today, Let's Encrypt certificates are 90 days. Apple's ballot in the CA/Browser Forum to reduce maximum validity to 47 days by 2027 would require all enterprise TLS certificates to be renewed every 45 days. Manual renewal at that cadence is impossible, automation is required.
CLM starts with discovery, you cannot manage certificates you do not know exist. Discovery has two components: network scanning and CA/vault integration. Network scanning for TLS certificates: Scan all IP ranges and hostnames in your environment on ports 443, 8443, and any other HTTPS ports used. For each TLS connection, extract the certificate and record: common name, SANs, issuer CA, validity dates, key type and length, and whether the certificate chain is trusted.
Reconcile discovery sources: Network scan results and CA records rarely match perfectly. Certificates found in network scanning but not in CA records are shadow certificates (issued by an unapproved CA or issued by an approved CA outside the tracked workflow). Certificates in CA records but not found in network scanning may be installed in non-standard locations, on systems not in your IP inventory, or already revoked but not removed from CA records.
Manual certificate renewal does not scale below 90-day validity periods. The ACME (Automatic Certificate Management Environment) protocol, standardized in RFC 8555, provides the automation foundation for certificate lifecycle management. This entire process runs automatically on a schedule, no human involvement required after initial setup. ACME for internal CAs: ACME is not just for public CAs. Microsoft ADCS supports ACME via a third-party module. HashiCorp Vault PKI includes a native ACME endpoint. Smallstep step-ca provides a full ACME-compliant internal CA. Running ACME against your internal CA gives you the same automation for internal certificates that Let's Encrypt provides for public TLS.
For large enterprises with thousands of certificates across multiple CAs and platforms, a dedicated CLM platform is required. Spreadsheets and manual tracking do not scale. Venafi Trust Protection Platform: The market leader for enterprise CLM. Discovers certificates across the full environment (network scanning, CA integration, cloud integration), provides a centralized inventory, enforces policy (approved CAs, minimum key lengths, maximum validity periods), automates renewal via ACME and proprietary connectors, and integrates with DevOps toolchains (Kubernetes, HashiCorp Vault, Terraform). Strong for large, heterogeneous environments with multiple CAs and complex certificate policies.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Sectigo • https://en.wikipedia.org/wiki/Cryptographic%20bill%20of%20materials • https://en.wikipedia.org/wiki/DigiCert • https://docs.digicert.com/en/certcentral/automate-certificate-lifecycle/guided-tls-ssl-certificate-lifecycle-automation.html • https://learn.microsoft.com/en-us/azure/architecture/example-scenario/certificate-lifecycle/ • https://github.com/Muhammad-Jaffar-Documentation/PKI-ENTERPRISE-ARCHITECTURE • https://startwithidentity.com/guides/machine-identity/certificate-lifecycle-management-guide/ • https://learn.microsoft.com/en-us/samples/azure/certlc/certlc/ • https://startwithidentity.com/articles/certificate-lifecycle-management-guide/ • https://packetblock.com/blog/pki-automation-complete-guide
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Automated Certificate Lifecycle Tool.
[*] Metasploit Scan Running on Target Subnet for Automated Certificate Lifecycle Tool... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |