Complete Technical Paper Content — Automated Cloud Penetration Testing
Overview & System Context
Automated Cloud Penetration Testing: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9508 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background A penetration test, colloquially known as a pentest, is an authorized simulated cyberattack on a computer system, performed live to evaluate the security of the system. The test is performed to identify weaknesses (or vulnerabilities), including the potential for unauthorized parties to gain access to the system's features and data, as well as strengths, enabling a full risk assessment to be completed. The process typically identifies the target systems and a particular goal, then reviews available information and undertakes various means to attain that goal. A penetration test target may be a white box (about which background and system information are provided in advance to the tester) or a black box (about which only basic information other than the company name is provided). A gray box penetration test is a combination of the two (where limited knowledge of the target is shared with the auditor). There are different types of penetration testing, depending on the goal of the organization which include: Network (external and internal), Wireless, Web Application, Social Engineering, and Remediation Verification. A penetration test can help identify a system's vulnerabilities to attack and estimate how vulnerable it is. The UK National Cyber Security Center describes penetration testing as: "A method for gaining assurance in the security of an IT system by attempting to breach some or all of that system's security, using the same tools and techniques as an adversary might." Penetration tests are a component of a full security audit. For example, the Payment Card Industry Data Security Standard requires penetration testing on a regular schedule, and after system changes. Penetration testing also can support risk assessments as outlined in the NIST Risk Management Framework SP 800-53. Several standard frameworks and methodologies exist for conducting penetration tests. These include the Open Source Security Testing Methodology Manual (OSSTMM), the Penetration Testing Execution Standard (PTES), the NIST Special Publication 800-115, the Information System Security Assessment Framework (ISSAF) and the OWASP Testing Guide. CREST, a not for profit professional body for the technical cyber security industry, provides its CREST Defensible Penetration Test standard that provides the industry with guidance for commercially reasonable assurance activity when carrying out penetration tests. Since 2017 the terms Penetration Testing as a Service (PTaaS) has become popular. This involves using a platform to invoke a test as an alternative to using consultants.
Find an exploitable vulnerability. Design an attack around it. Test the attack. Seize a line in use. Enter the attack. Exploit the entry for information recovery. Over time, Anderson's description of general computer penetration steps helped guide many other security experts, who relied on this technique to assess time-sharing computer system security. In the following years, computer penetration as a tool for security assessment became more refined and sophisticated. In the early 1980s, the journalist William Broad briefly summarized the ongoing efforts of tiger teams to assess system security. As Broad reported, the DoD-sponsored report by Willis Ware "...showed how spies could actively penetrate computers, steal or copy electronic files and subvert the devices that normally guard top-secret information. The study touched off more than a decade of quiet activity by elite groups of computer scientists working for the Government who tried to break into sensitive computers. They succeeded in every attempt." While these various studies may have suggested that computer security in the U.S. remained a major problem, the scholar Edward Hunt has more recently made a broader point about the extensive study of computer penetration as a security tool. Hunt suggests in a recent paper on the history of penetration testing that the defense establishment ultimately "...created many of the tools used in modern day cyberwarfare," as it carefully defined and researched the many ways that computer penetrators could hack into targeted systems.
BlackArch based on Arch Linux BackBox based on Ubuntu Kali Linux (replaced BackTrack December 2012) based on Debian Parrot Security OS based on Debian Pentoo based on Gentoo WHAX based on Slackware Many other specialized operating systems facilitate penetration testing—each more or less dedicated to a specific field of penetration testing. A number of Linux distributions include known OS and application vulnerabilities, and can be deployed as targets to practice against. Such systems help new security professionals try the latest security tools in a lab environment. Examples include Damn Vulnerable Linux (DVL), the OWASP Web Testing Environment (WTW), and Metasploitable.
Proxmark3 — multi-purpose hardware tool for radio-frequency identification (RFID) security analysis. BadUSB — toolset for exploiting vulnerabilities in USB devices to inject malicious keystrokes or payloads. Flipper Zero — portable, open-source multi-functional device pentesting wireless protocols such as Sub-GHz, RFID, NFC, Infrared and Bluetooth. Raspberry Pi — a compact, versatile single-board computer commonly used in penetration testing for tasks like network reconnaissance and exploitation. SDR (Software-defined Radio)— versatile tool for analyzing and attacking radio communications and protocols, including intercepting, emulating, decoding, and transmitting signals. ChipWhisperer — specialized hardware tool for side-channel attacks, allowing analysis of cryptographic implementations and vulnerabilities through power consumption or electromagnetic emissions.
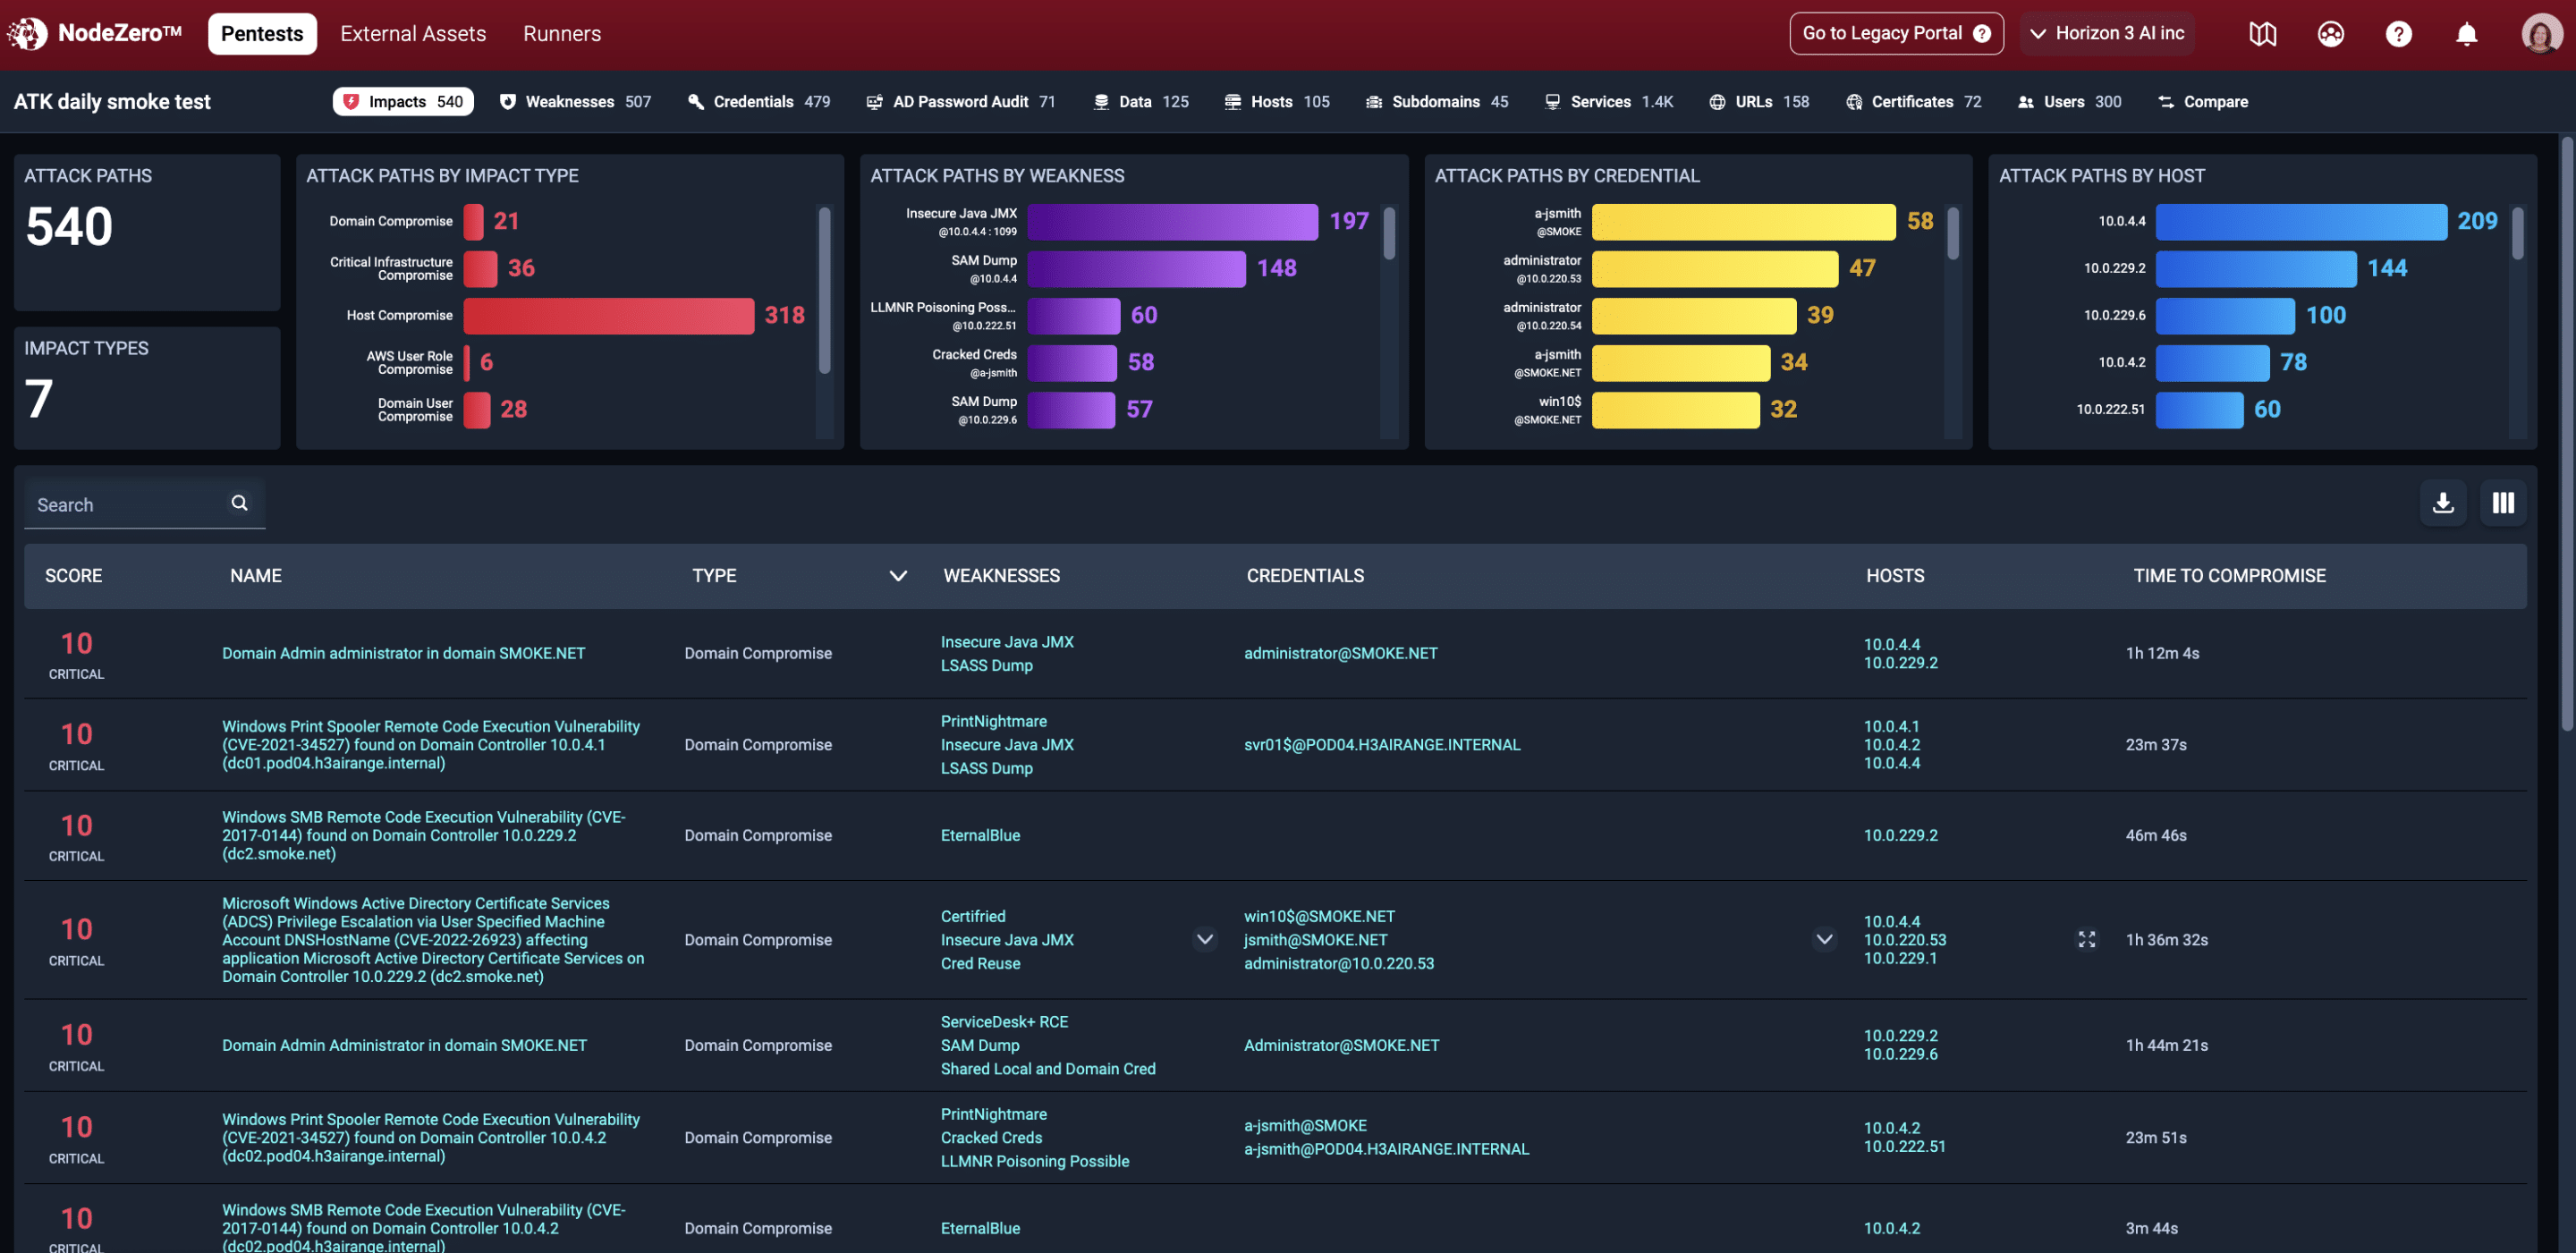
Figure 1: What is Automated Penetration Testing? - Updated in 2026 Reconnaissance: The act of gathering important information on a target system. This information can be used to better attack the target. For example, open source search engines can be used to find data that can be used in a social engineering attack. Scanning: Uses technical tools to further the attacker's knowledge of the system. For example, Nmap can be used to scan for open ports. Gaining access: Using the data gathered in the reconnaissance and scanning phases, the attacker can use a payload to exploit the targeted system. For example, Metasploit can be used to automate attacks on known vulnerabilities.
Once an attacker has exploited one vulnerability they may gain access to other machines so the process repeats i.e. they look for new vulnerabilities and attempt to exploit them. This process is referred to as pivoting. Maintaining access: Maintaining access requires taking the steps involved in being able to be persistently within the target environment in order to gather as much data as possible. Covering tracks: The attacker must clear any trace of compromising the victim system, any type of data gathered, log events, in order to remain anonymous. Reporting: Vulnerabilities are classified via risk matrix and documented in a report which contains executive summary, vulnerability description, and recommendations for remediation.
Remediation & Re-testing: Once the target organization assesses the penetration test report and remediates items based on their internal risk appetite, a re-test of those vulnerabilities is performed in order to confirm remediation was successful, and a cut down re-test report is provided showing the results. Red team exercises are an extension of penetration testing in which a dedicated adversarial team (the red team) simulates a sophisticated, sustained attack against an organisation's people, processes, and technology — without the defending team (the blue team) being fully aware of the timing or scope. This differs from a standard penetration test in that it focuses on testing the organisation's detection and response capabilities, not just its technical vulnerabilities. Purple team exercises involve the red and blue teams working collaboratively, such as by sharing information in real time.
Aikido Security BV is a Belgian cybersecurity company headquartered in Ghent. Founded in 2022, it develops a software security platform that analyzes source code, open-source dependencies, cloud infrastructure, applications and devices for vulnerabilities, malware and misconfigurations. Its products include code and dependency analysis, cloud-security assessment, automated penetration testing, vulnerability remediation and runtime protection.
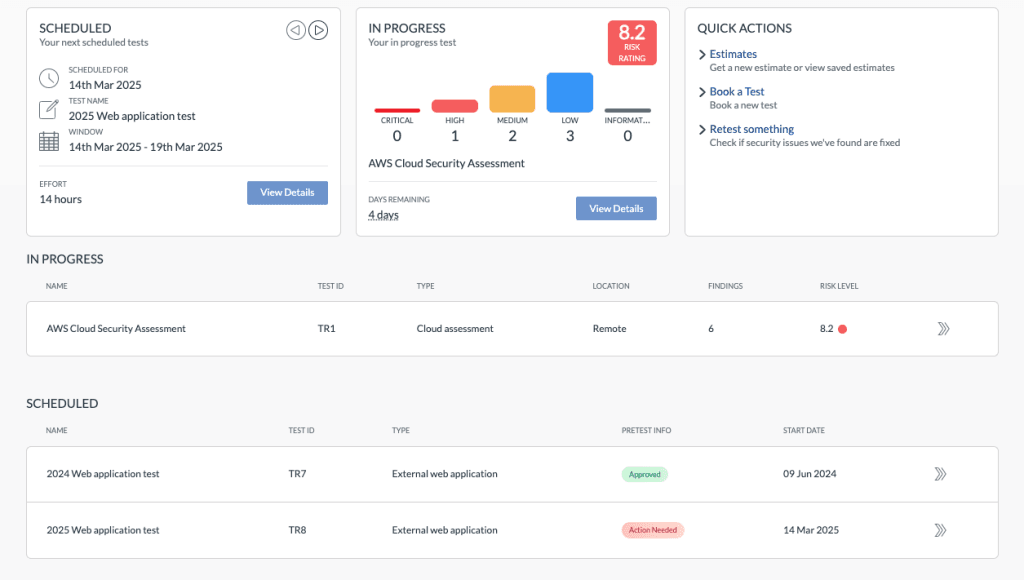
Fluid Attacks is an application security (AppSec) company founded in 2001 in Colombia. It specializes in security testing for software development companies through automated tools (SaaS) and penetration testing (PTaaS). Figure 2: Best tools for SOC 2 compliance penetration testing [2025] Master cloud penetration testing across AWS, Azure & GCP. Learn industry-approved methodologies, vulnerability discovery techniques, and security validation frameworks for multi-cloud environments.
Cloud infrastructure demands a fundamentally different approach to penetration testing than traditional on-premises environments. At Pentagon Infosec , our penetration testing methodology encompasses AWS, Azure, and GCP security validation frameworks, delivering comprehensive vulnerability discovery within 15-20 business days. With 500+ cloud security assessments completed, our CISA-certified architects understand the nuances of multi-cloud attack surfaces, API security , identity management, and data exposure risks that organizations face.
This comprehensive guide walks you through cloud penetration testing methodology, actionable steps, and how to validate your cloud security posture across major cloud service providers. Cloud environments introduce unique security challenges: shared responsibility models, API-driven architectures, identity federation, and rapid infrastructure changes. Traditional penetration testing methodologies fail to address cloud-specific attack vectors like misconfigured IAM policies , exposed S3 buckets, insecure Kubernetes deployments, and cloud service enumeration.
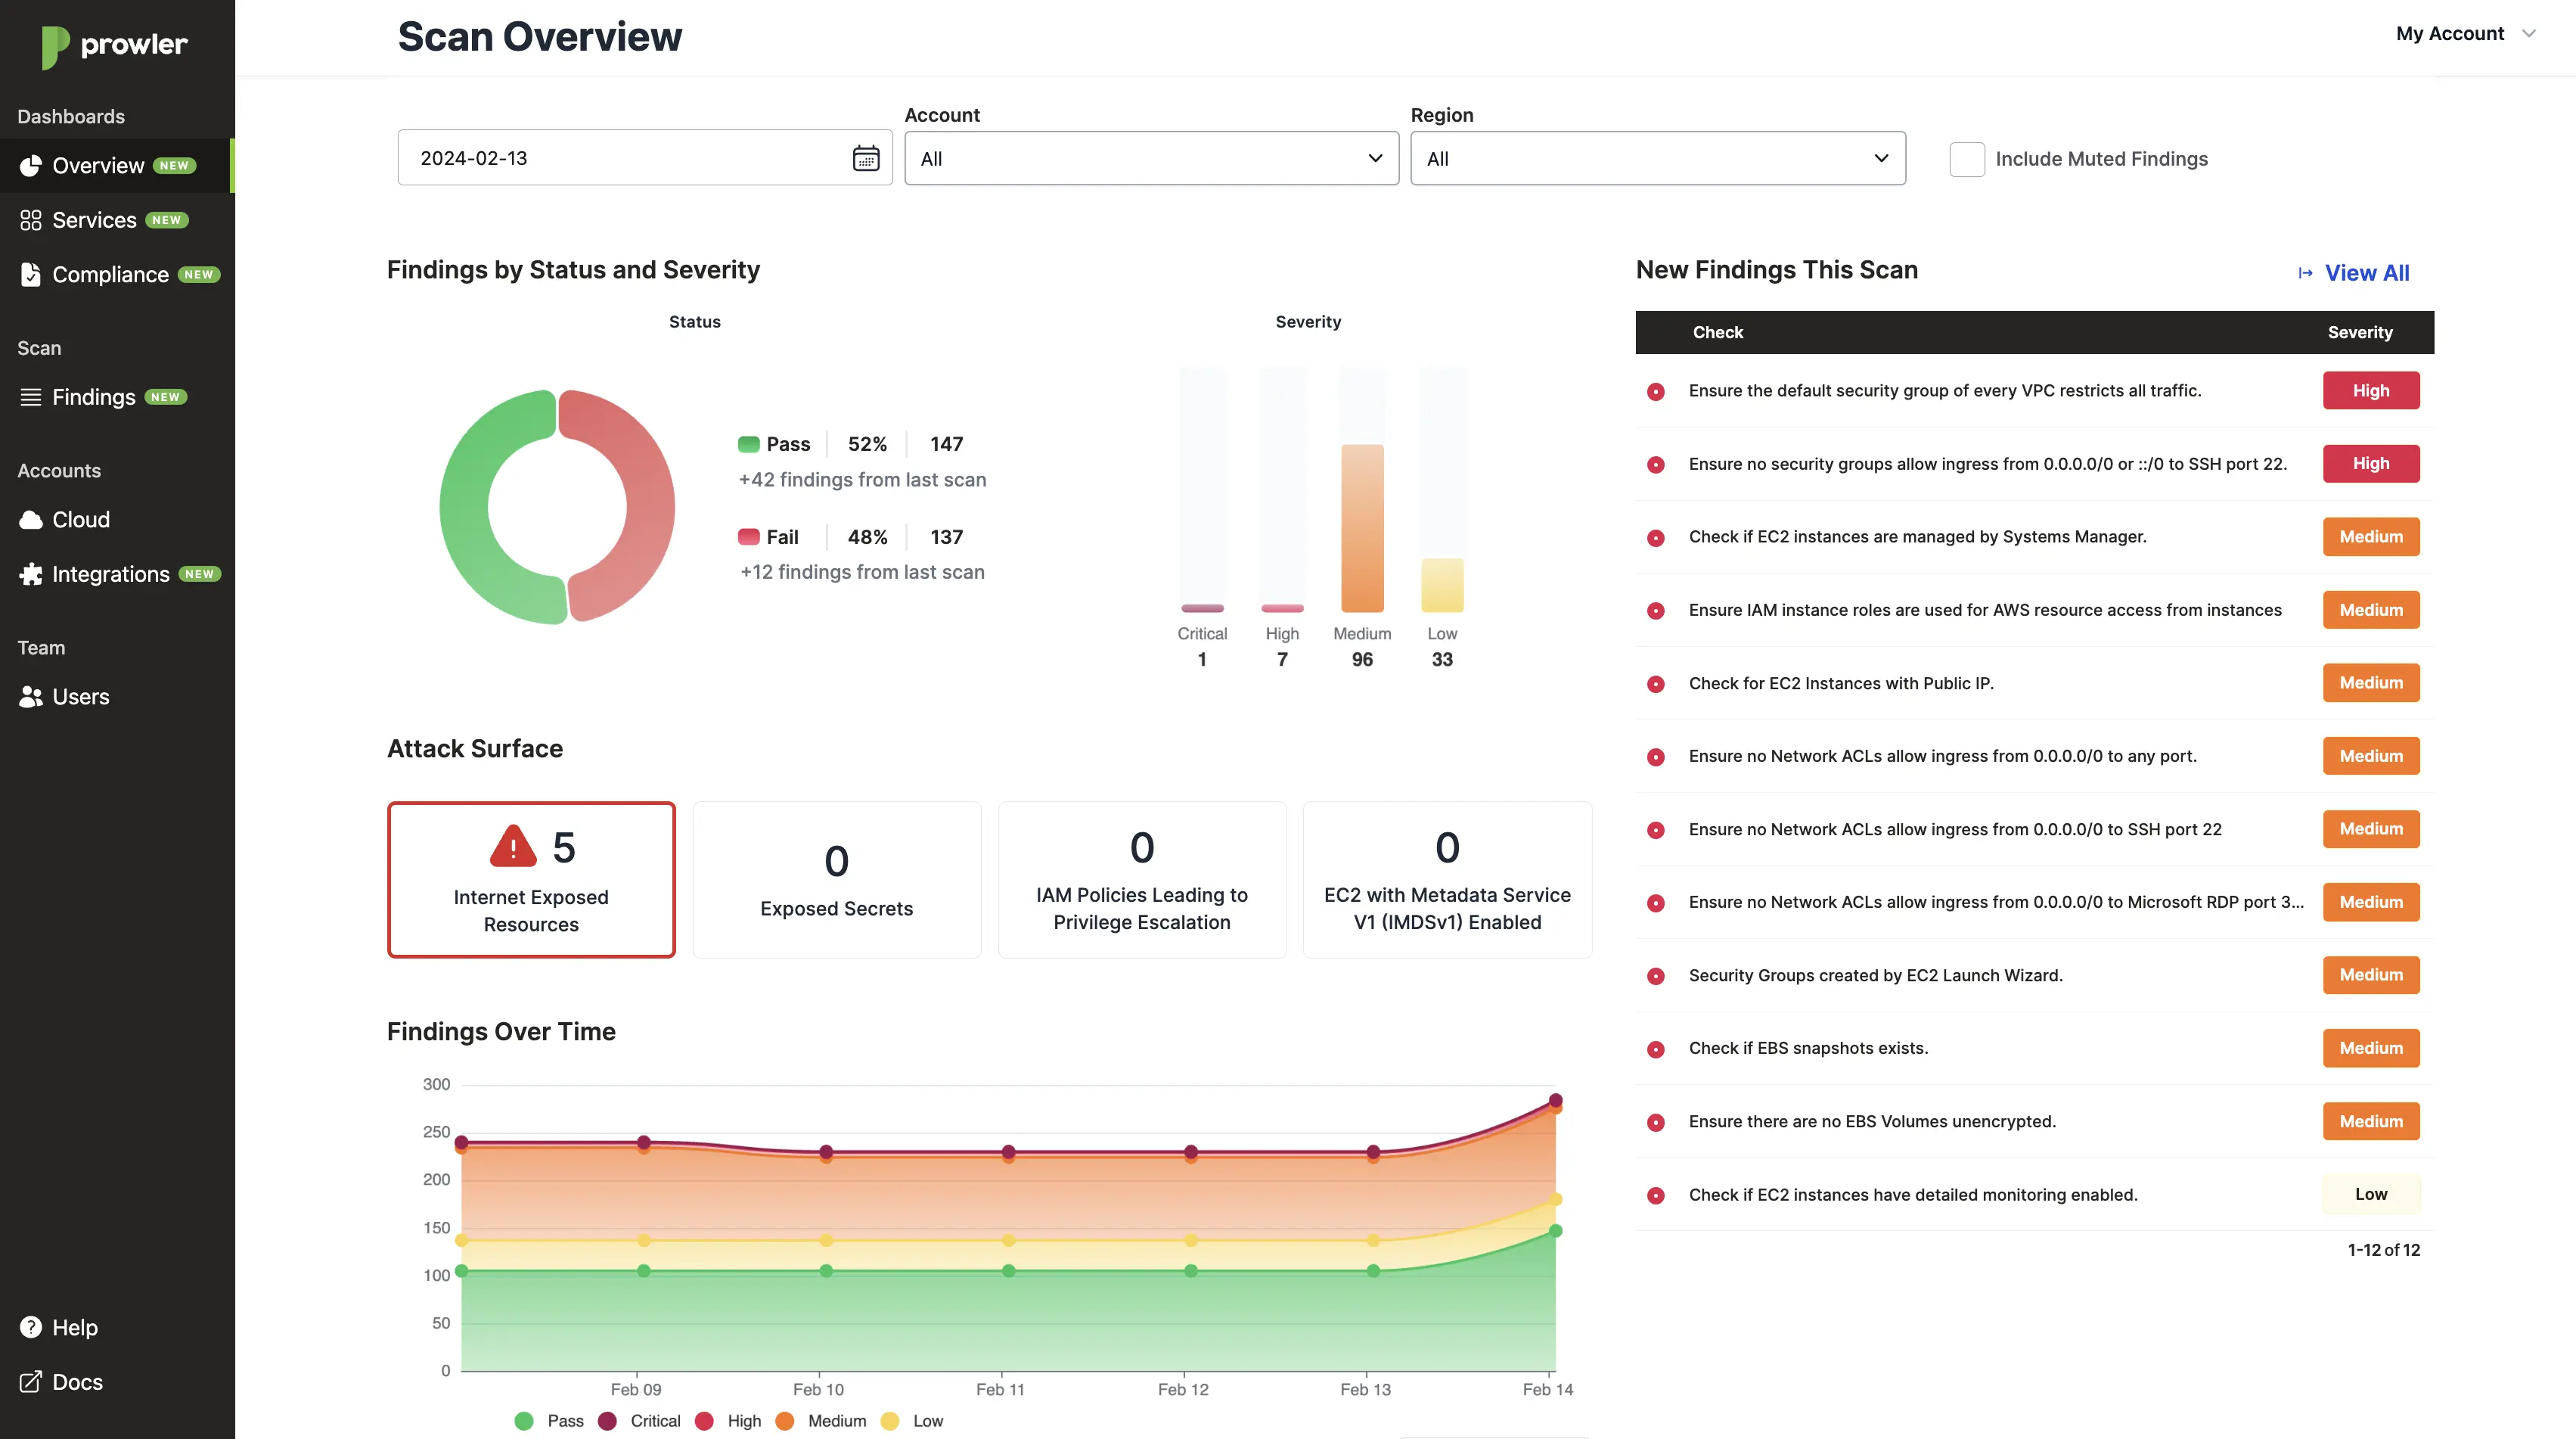
Figure 3: Cloud Penetration Testing Services - OnSecurity Pentagon Infosec's cloud penetration testing methodology integrates OWASP Cloud Top 10, NIST Cloud Security guidelines, and cloud-native vulnerability frameworks. Our approach ensures: We begin by identifying AWS resources using legitimate tools (AWS CLI, CloudMapper, Prowler). This phase maps out EC2 instances, RDS databases, S3 buckets, Lambda functions, and API Gateways. We document IAM users, roles, policies, and network architecture without triggering security alarms.
Automated scanning identifies security group misconfigurations, public snapshots, unencrypted EBS volumes, and insecure IAM policies. Manual review reveals business logic flaws and authorization bypasses specific to your application architecture. We exploit identified vulnerabilities to demonstrate real-world impact: accessing RDS credentials from EC2 metadata, escalating IAM privileges, moving laterally between subnets, and extracting sensitive data from S3 buckets.
Our penetration testing reports include CVSS scores, AWS-specific remediation steps, and hardened Terraform/CloudFormation templates. We provide 15-20 day fast-track delivery with executive summaries and technical deep-dives.
We test Azure App Service, Azure Functions, and API Management endpoints for authentication flaws, injection vulnerabilities, and insecure direct object references (IDOR). We also validate Azure Key Vault access controls and secret management practices. Azure Storage accounts, SQL Databases, and Cosmos DB are assessed for encryption gaps, firewall misconfigurations, and anonymous access. We verify encryption-in-transit and encryption-at-rest implementations.
Google Cloud Storage buckets and BigQuery datasets are assessed for public access, weak authentication, and data exfiltration paths. We verify encryption policies, versioning controls, and access logging. Compute Engine instances, GKE clusters, and App Engine deployments are tested for privilege escalation, container escape vulnerabilities, and network segmentation failures.
1. Define Scope & Authorization Document all cloud environments, workloads, and applications in scope. Exclude non-production resources or define specific attack scenarios. Obtain executive written authorization before testing begins. 2. Enable Comprehensive Logging Activate CloudTrail (AWS), Activity Logs (Azure), or Cloud Audit Logs (GCP) to capture all API calls and security events. This aids post-exploitation analysis and forensic investigation.
3. Establish Communication Channels Designate a security contact and escalation procedures. Agree on testing windows to minimize production impact. Define incident response protocols if critical vulnerabilities are discovered during testing. 4. Document Current Security Controls Provide details on existing WAFs, DDoS protection, EDR solutions, and SIEM integrations. This helps us tune testing to avoid false positives and focus on blind spots.
5. Schedule Post-Testing Review Plan a comprehensive debrief to discuss findings, remediation priorities, and security roadmap improvements. Pentagon Infosec provides actionable remediation guidance aligned with your compliance requirements (PCI DSS, HIPAA, ISO 27001, NIST). Pentagon Infosec delivers comprehensive cloud penetration testing reports within 15-20 business days. Timeline depends on scope (single-cloud vs. multi-cloud), environment complexity, and vulnerability density. Small-scope testing may complete in 10 days; large enterprise deployments spanning AWS, Azure, and GCP may extend to 20 days with detailed remediation guidance.
Our methodology prioritizes non-destructive testing. We coordinate with your infrastructure teams, use staging environments where possible, and apply conservative exploitation techniques. Destructive tests (data deletion, resource termination) are only performed with explicit authorization and on isolated resources. Cloud penetration testing validates security controls required by PCI DSS, ISO 27001, SOC 2, HIPAA, NIST CSF, and RBI SAR standards. Pentagon Infosec tailors testing scope to your regulatory obligations, ensuring audit-ready documentation and compliance evidence.
Our penetration testing reports include CVSS severity ratings, risk impact analysis, and AWS/Azure/GCP-specific remediation steps. We provide hardened Infrastructure-as-Code templates, policy recommendations, and architectural guidance. For enterprises requiring implementation support, Pentagon Infosec offers post-testing remediation services within agreed SLAs. Industry best practices recommend annual penetration testing as a baseline, with quarterly testing for high-risk environments (payment systems, healthcare, financial services). Continuous vulnerability scanning between penetration tests identifies emerging risks. Pentagon Infosec supports both scheduled assessments and ad-hoc testing following infrastructure changes or security incidents.
Cloud penetration testing methodology goes beyond automated scanning—it simulates real-world attacks, identifies business-logic vulnerabilities, and validates your security architecture. AWS, Azure, and GCP each require distinct testing approaches that account for their unique threat models, shared responsibility frameworks, and native security controls. Pentagon Infosec's 15-20 day fast-track delivery model, combined with our CISA-certified architects and 500+ cloud security assessments, ensures your organization receives actionable insights and compliance-aligned remediation guidance. Whether you operate single-cloud or multi-cloud environments, our penetration testing methodology identifies critical gaps before malicious actors exploit them.
Ready to validate your cloud security? Explore our comprehensive Penetration Testing Methodology services and schedule a cloud security assessment with Pentagon Infosec today. CISA, ISO 27001 LA, AWS Certified. 11+ years in information security, cloud services, and compliance. Founder of Pentagon Infosec.
AI agents have traditionally faced three core limitations: they can’t retain learned information or operate autonomously beyond short periods, and they require constant supervision. AWS addresses these limitations with frontier agents—a new category of AI that performs complex reasoning, multi-step planning, and autonomous execution for hours or days. Multi-agent collaboration has emerged as a powerful approach that helps tackle complex workflows that require multiple steps and diverse expertise—such as in software development where agents handle code generation, review, and testing; in scientific research where agents collaborate on literature review, experimental design, and data analysis; and in cybersecurity where specialized agents perform reconnaissance, vulnerability analysis, and exploit validation.
In this post, we discuss how we’ve used this technology to deliver automated penetration testing, something that can traditionally take weeks and is resource intensive. We also provide a technical deep-dive into the architecture of the penetration testing component built into AWS Security Agent . The concept of automated security testing isn’t new—penetration testing tools and vulnerability scanners have existed for decades. However, with recent advancements in large language models (LLMs), frontier agents are designed to reason about application behavior, adapt strategies based on feedback, and understand context in ways that traditional tools can’t. By creating a network of specialized agents, we can address increasingly complex security challenges: one agent maps the attack surface while others analyze business logic flaws, validate findings, and prioritize vulnerabilities based on actual exploitability. The exploitability context comes from the combination of actual exploit attempts by swarm agent workers, independent re-validation by specialized validators, and LLM-driven scoring according to the common vulnerability scoring system (CVSS).
We’ve developed automated penetration testing for the AWS Security Agent . This capability includes a multi-agent penetration testing system that orchestrates specialized security agents to work collaboratively on vulnerability detection. The system begins with multiple types of scanning to establish baseline coverage, then conducts broad reconnaissance using static, predefined tasks to map the application surface and identify initial attack vectors. Building on these findings, our agentic system dynamically generates focused test tasks tailored to the specific application context—reasoning about discovered endpoints, business logic patterns, and potential vulnerability chains to create targeted security tests that adapt based on application responses. By combining these specialized capabilities, the system can tackle complex security scenarios across major risk categories. Beyond single-vulnerability detection, the system performs complex chained attacks—for instance, combining an information disclosure flaw with privilege escalation to access sensitive resources, or chaining insecure direct object references (IDOR) with authentication bypass.
This section describes the major components of the system. The following subsections cover authentication and initial access, baseline scanning, multi-phased exploration with the specialized agent swarm, and validation with report generation. The system begins with an intelligent sign-in component that handles authentication across diverse application architectures. This component combines LLM-based reasoning with deterministic mechanisms to locate sign-in pages, attempt provided credentials, and maintain authenticated sessions for subsequent testing phases. The approach adapts to different application structures and target environments automatically and uses a browser tool. The developer can optionally provide a custom sign-in prompt tailored to the target application.
Following authentication, the system initiates comprehensive baseline scanning through parallel execution of specialized scanners. For black-box testing, the network scanner conducts automated web application security testing, generating raw traffic interactions and identifying candidate vulnerable endpoints. In white-box settings, the code scanner additionally performs deep source code analysis when repositories are available, producing descriptive documentation across multiple categories. Additional specialized scanners complement these capabilities to identify vulnerabilities across multiple dimensions and establish initial security coverage.
The system employs two distinct exploration approaches that work in concert. Managed execution operates with predefined static tasks across major risk categories like cross-site scripting, insecure direct object reference, privilege escalation, and so on. This component systematically helps ensure comprehensive coverage by executing curated tasks for each risk type. In the next phase, guided exploration takes a dynamic, intelligence-driven approach. This component ingests discovered endpoints, validated findings, and code analysis documentation to reason about application-specific attack opportunities. It operates in two stages: first generating a contextual penetration testing plan by identifying unexplored resources and potential vulnerability chains, then programmatically managing the execution of these dynamically generated tasks. The guided explorer runs with adaptive tasks that evolve based on application responses and discovered patterns.
Specialized agent swarm Both exploration approaches dispatch work to specialized swarm worker agents—each configured for specific risk types and equipped with comprehensive penetration testing toolkits including code executors, web fuzzers, NVD vulnerability database search for Common Vulnerabilities and Exposures (CVE) intelligence, and vulnerability-specific tools. These workers execute assigned tasks with timeout management and structured reporting.
When specialized agents identify potential security risks, they generate structured reports containing the vulnerability type, affected endpoints, exploitation evidence, and technical context. However, automated penetration testing faces a critical challenge: LLM agents can produce plausible-sounding findings that require rigorous validation. Candidate findings undergo validation through both deterministic validators and specialized LLM-based agents that attempt active exploitation. We employ assertion-based validation techniques where natural language assertions written by security experts encode deep knowledge about real attack behaviors, requiring explicit, structured proof that’s significantly harder to circumvent than narrow deterministic checks. Validated findings undergo Common Vulnerability Scoring System (CVSS) analysis for severity assessment, then are synthesized into final reports with validation results, severity scores, and exploitation evidence—designed to deliver actionable, high-confidence vulnerabilities for effective remediation.
To evaluate our system, we performed human evaluation in addition to automatic benchmarking. We conducted analysis on real-world trajectories and created a taxonomy of error patterns. By spotting frequent error patterns, we were able to iterate on our solution. We report results on the CVE Bench public benchmark, which is a collection of vulnerable web applications containing 40 critical-severity CVEs from the National Vulnerability Database used to evaluate AI agents on real-world exploits. Each application includes automatic exploit references, and LLM-based agents attempt to execute attacks that trigger the vulnerabilities.
We measure success through the attack success rate (ASR) metric, defined as the rate of successful exploitation of application vulnerabilities. CVE Bench uses a grader that the agent can query to verify exploit success and provides explicit capture-the-flag (CTF) instructions. We evaluate in three configurations: 2. System Architecture & Core Working Principles The following code example shows an LLM agent demonstrating parametric knowledge of CVE-2023-37999 from its training data, then issuing a bash command to check exploitation prerequisites.
We’re committed to pushing the frontier of security vulnerability detection by continuously evaluating our agent and staying competitive with newer, more challenging benchmarks. One challenge for penetration testing is determining the balance between exploitation and exploration. Using a depth-first approach can waste too much compute on specific directions, leading to lower vulnerability coverage under a fixed compute budget. Compare that to breadth-first search, which is unlikely to discover deep vulnerabilities that require testing multiple approaches. Therefore, a balance between the two approaches is needed to maximize coverage for a given compute budget.
Our proposed system design aims to include a hybrid approach. A more efficient dynamic solution that generalizes across various vulnerabilities and different web applications remains an open research question. Another challenge with penetration testing is non-determinism. Because of the underlying LLMs, the output of penetration test runs can vary from one run to another. Having different findings across multiple runs can lead to confusion. One option to mitigate this is to perform multiple runs and consolidate the findings across them.
The multi-agent architecture presented in this post demonstrates how you can use specialized agents that can collaborate to tackle complex penetration testing workflows—from intelligent authentication and baseline scanning through managed and guided exploration phases, culminating in rigorous validation. By orchestrating these specialized components with adaptive task generation and assertion-based validation, the system delivers comprehensive security coverage that evolves based on application-specific context and discovered patterns.
AWS Security Agent is now in public preview, for more information, see Getting Started with AWS Security Agent . If you run an MSSP or security consultancy, you've probably seen this already. A client asks for a cloud pentest, your team uses the same habits that work well on external networks, and the report comes back heavy on exposed services, missing patches, and web issues. Then an identity problem in AWS, Azure, or GCP turns out to be the actual path to compromise.
That gap is where a lot of cloud penetration testing programs fail. The issue isn't effort. It's model mismatch. Cloud estates don't behave like static perimeter environments, and service providers that keep selling them as if they do will under-deliver, burn senior tester time, and leave obvious value on the table. For MSSPs, cloud penetration testing is no longer a specialist side offering. It's becoming a core service line that has to be repeatable, scoped cleanly, executed safely, and packaged into a deliverable clients can act on. The firms that do this well usually treat automation as an operating requirement, not a nice-to-have.
A client passes an annual pentest, then gets breached through a forgotten access key in CI, an over-permissive role, and a snapshot the attacker can read without touching the public edge. That sequence is common in cloud incidents. The failure is not patching. The failure is testing the wrong system. Cloud penetration testing examines how identities, permissions, APIs, workloads, and managed services combine into an attack path. It is closer to validating compromise routes across the control plane than checking a list of internet-facing hosts. If a team only tests exposed applications and network paths, it will miss the issues that cause the most expensive cloud incidents.
The old approach starts with ports, services, and reachable applications. In cloud, those checks still matter, but they are no longer enough to answer the client's real question: can an attacker turn one weak point into data access, privilege escalation, or account takeover? Cloud environments break static testing assumptions. Assets are short-lived. Permissions change weekly. New services appear through Terraform, pipelines, and delegated admin models. A clean host-level result can sit beside a dangerous IAM path that gives broad read access to storage, snapshots, secrets, or build systems. Teams that want a clear example of how cloud APIs expand exposure can review this analysis of attack surface expansion through cloud API pentesting .
A simple standard works well: if the team cannot show how an identity reaches a resource through a permission chain, the engagement is an infrastructure review, not a cloud pentest. For MSSPs and consultancies, this is a service design problem as much as a technical one. Buyers are no longer satisfied with a network test relabeled for AWS, Azure, or GCP. They want validation of cloud-native attack paths, and they want it delivered in a way that can be repeated as environments change.
That creates a strong business case. Cloud estates do not stay still, so testing demand shifts from one-off projects toward recurring validation around new accounts, major architecture changes, mergers, product launches, and quarterly assurance cycles. The firms that do well here define the service tightly, automate the repeatable parts, and reserve senior consultant time for attack-path analysis, controlled exploitation, and remediation guidance.
The offer should be specific. Sell a scoped exercise that tests identities, exposed assets, privilege paths, and high-value data access across the client's cloud estate, then produces evidence a security lead can act on and a buyer will pay to repeat. The fastest way to explain the difference to a client or delivery team is this. Traditional pentesting often feels like testing a fortress. Cloud penetration testing feels more like testing an airport.
A fortress has a clearer perimeter. An airport has thousands of moving parts, temporary access, service corridors, trusted personnel, and systems that depend on each other. The cloud is closer to the airport model. In a perimeter-heavy environment, the tester asks questions like: what is reachable, what is exposed, what software is vulnerable, and can I gain execution on a host? GuidePoint's cloud guidance makes this distinction explicit. Cloud penetration testing has to validate attack paths across control planes and identities at the same time, and a single over-permissive IAM role can create an end-to-end compromise path even when workloads are fully patched, as described in GuidePoint Security's cloud pentesting overview .
That changes the tester's success criteria. “I got shell on a box” isn't the only outcome that matters anymore. In many cloud assessments, the more important proof is “this role can assume that role, access that storage, and reach that dataset.” Cloud attackers rarely care whether your report found ten medium findings on patched compute nodes. They care whether one identity path gets them to the data they want.
For MSSPs, this difference creates a staffing problem. Strong network pentesters aren't automatically strong cloud testers. They need to reason about IAM, trust policies, service relationships, and cloud-native post-exploitation. There's also a commercial implication. Scoping cloud work by “number of external assets” almost always underprices the engagement. Scope it by cloud reality instead: accounts, subscriptions, projects, critical services, identity complexity, and whether hybrid paths are in play.
If you want a good way to frame this for prospects, this article on attack surface expansion in cloud API pentesting is useful because it aligns with how cloud exposure spreads: through APIs, identities, and service-to-service trust. Even solid service providers can create unnecessary risk. You can't treat a client's cloud estate like an unbounded test range. Cloud platforms operate under provider terms, shared responsibility limits, and explicit restrictions around what can be tested and how.
The operational rule is simple. Never start a cloud pentest until scope, ownership, allowed methods, and provider-specific constraints are documented in writing. AWS usually allows testing of customer-owned resources, but that doesn't mean every technique is safe or appropriate. A mature AWS test plan also lists the exact accounts, regions, and sensitive services in scope. “AWS environment” is not scope. It's shorthand for future confusion.
Azure introduces the same basic issue with different operational details. The cloud provider secures the platform. Your client owns what they configure, expose, and authorize. The cleanest cloud pentests start with paperwork that feels excessive. The messy ones usually begin with “we'll figure out the details once testing starts.” GCP assessments often expose a different kind of problem. Teams underestimate how much trust is embedded in projects, service accounts, inherited permissions, and attached services.
Across AWS, Azure, and GCP, the discipline is the same. Test what the customer owns. Don't test what the provider owns. Don't assume allowed technical access equals allowed legal access. A cloud pentest usually goes off course in the first hour, not the fifth day. The client gives access to one AWS account, the actual admin path sits in a different account, the CI/CD role is out of scope, and nobody agreed on whether temporary credentials can be used for privilege escalation validation. By the time the team sorts that out, delivery time is gone and the report is thinner than the client expected.
That is why the methodology matters. MSSPs that deliver cloud pentests well do not treat them as a standard network assessment with cloud services added on top. They run a structured process built for identities, control planes, and fast-changing estates. Many teams still use the familiar seven-phase penetration testing model as a baseline. The difference is how each phase is executed in cloud, and how much of the evidence collection and triage can be standardized for repeatable delivery.
Cloud scoping needs more precision than many consultancies expect. The team needs the exact accounts, subscriptions, or projects in scope, approved identities, known high-value services, region boundaries, testing windows, and a list of assets that cannot be touched. Starting conditions matter just as much. A black-box test, a gray-box test, and an identity-seeded assessment produce very different findings in cloud. If the client wants an answer to "what happens when one developer identity is compromised," the test plan should reflect that from day one.
This phase builds the complete target map. That includes resource discovery, IAM enumeration, exposed service review, trust relationships, storage visibility, secret exposure checks, and control plane reconnaissance across the approved scope. This is also where delivery economics start to show. In a multi-account estate, manual discovery burns senior tester time on repetitive work. MSSPs that want to make cloud pentesting profitable need a standard way to collect, normalize, and label cloud assets before a consultant starts validating attack paths.
Cloud threat modeling should start with identities and permission chains. Analysts regularly attribute a large share of cloud incidents to identity compromise and credential misuse, as summarized in StationX's cloud security statistics roundup . For MSSPs, this phase determines whether the engagement becomes a scanner output review or a real attack-path exercise. It also informs how to package the service. Clients buying cloud pentesting want proof of impact tied to their architecture, not a list of misconfigurations they already saw in CSPM.
Teams that want to shift some of this thinking left should also review pentesting in the DevOps pipeline for DevSecOps teams . It is a useful reference for bringing cloud attack-path validation closer to engineering changes, where fixes are cheaper and easier to verify. To ground the workflow, this video is worth sharing with technical teams before they start building a cloud testing service.
Automation should handle broad coverage here. The tester's job is to judge exploitability and chain potential. Review IAM policies, federation paths, public exposure, storage access, service configurations, workload posture, and secret handling with one question in mind. Can these weaknesses be combined into business-relevant access? That distinction matters commercially. Clients do not renew because a team found 300 low-context issues. They renew because the team showed how three small flaws could expose production data or give control of deployment systems.
Cloud exploitation should be controlled and evidence-driven. Validate the role assumption, exposed credential, policy weakness, or resource access path with the least disruptive technique that still proves risk. 3. Software Implementation, Frameworks & Protocols Good testers avoid theatrics. A screenshot of successful cross-account role assumption, access to a sensitive bucket prefix, or the ability to read deployment secrets is usually stronger than noisy exploitation that creates cleanup work for the client.
In cloud, post-exploitation is usually about lateral movement across identities, services, and management layers. The important questions are whether the tester can pivot into another role, reach additional storage, access CI/CD, interact with key management, or gain durable control through the customer's own configuration choices. The engagement's true value becomes apparent as blast radius changes budget priority. An isolated finding gets deferred. A validated path from one workload credential to production data or infrastructure administration gets fixed.
A cloud pentest earns its value when it shows blast radius, not when it piles up isolated findings. The report should read like an attack sequence, not a pile of screenshots. Show the starting condition, the discovery steps, the permission chain, the proof of impact, the affected business function, and the remediation action in the order the client needs to fix it.
For MSSPs and consultancies, this is also the delivery model that scales. A repeatable methodology, supported by standardized evidence capture and attack-path logic, lets senior testers spend time on validation and judgment instead of rebuilding the same workflow on every engagement. Cloud pentesting is hard to scale manually for one reason above all others. The work expands faster than senior tester capacity.
A single client may have multiple accounts, several regions, dozens of services, inherited IAM sprawl, and a mix of production and forgotten environments. If every engagement depends on a senior consultant manually enumerating, correlating, validating, documenting, and packaging all of that, margins get thin quickly. Manual cloud testing still matters, but the delivery model breaks when the team has to repeat the same discovery and triage patterns on every job.
Open-source tools help, and good teams should know them. Prowler is useful for broad cloud posture review. Pacu is valuable for AWS attack simulation. Cloudsplaining helps analyze IAM risk. The problem isn't the tools. The problem is that they don't create an operating model on their own. The practical answer is selective automation around the repeatable parts of the engagement.
The firms that scale this service well usually standardize their runbooks, approved tooling, evidence format, and report language. They don't let every tester reinvent the workflow. That consistency is what turns cloud penetration testing into a repeatable service line instead of a heroic craft exercise. For service providers, the report is the product. The test matters, but the deliverable is what the client buys, shares internally, and uses to justify remediation.
A cloud pentest report should prove a path, not just state a possibility. Strong evidence usually includes: Weak reporting dumps scanner findings into a PDF and adds severity labels. Strong reporting tells a short, defensible story of how the compromise path worked and how to close it. The best MSSP reports do one more thing. They translate technical findings into business and compliance terms without watering down the technical detail.
That means mapping a privilege escalation path to the client's real risk, such as exposure of regulated data, excessive administrative reach, or weakness in access control governance. It also means producing outputs that both engineering and audit stakeholders can use. If you want a benchmark for what actionable reporting should look like, this guide to pentest report quality and actionable findings is a useful reference.
Clients rarely argue with evidence-backed reporting. They argue with vague reporting, missing validation, and findings that don't connect to operational risk. A scalable cloud pentesting practice wins when its reports are consistent, technically credible, and easy for clients to act on across security, cloud engineering, and compliance teams.
ThreatExploit AI helps MSSPs and security consultancies turn cloud penetration testing into a repeatable service instead of a manual bottleneck. The platform automates reconnaissance, exploitation, verification, and reporting across AWS, Azure, and GCP, using an agentic workflow aligned to PTES phases. If you need to increase testing capacity, produce evidence-backed reports faster, and deliver cloud assessments without adding headcount, take a look at ThreatExploit AI .
This guide explains how cloud penetration testing is actually performed — the phases, the techniques used at each stage, and what a rigorous assessment looks like across AWS, Azure and GCP. It is written for security engineers, cloud architects, and technical leaders who want to understand the process, prepare their environment for testing, or evaluate whether a provider’s methodology is deep enough to trust.
Looking to engage a provider rather than understand the process? See our cloud penetration testing services . Traditional network penetration testing assumes a defined perimeter, IP ranges you can scan, and infrastructure you fully control. Cloud environments break all three assumptions. Identity is the new perimeter. In cloud environments, most successful attacks are not exploits against software — they are the abuse of over-permissioned identities. An IAM role with an unintended permission is more dangerous than an unpatched server.
The infrastructure is API-driven. Every resource is created, modified and destroyed through APIs. That means the control plane itself is attack surface, and misconfigurations propagate at machine speed. Responsibility is shared. The provider secures the underlying platform; you secure everything you configure within it. Testing must target the customer side of that boundary — and only that side.
The environment is ephemeral. Assets scale up and disappear. A point-in-time asset list is stale almost immediately, so discovery must be continuous throughout the engagement. Everything begins with defining exactly what will be tested and confirming you are permitted to test it. Why it matters: an unscoped cloud test can breach your provider agreement or disrupt production. Grey-box access almost always produces better results per unit of effort, because it mirrors the realistic scenario of an attacker who has already phished one set of credentials.
The objective is to build an accurate picture of the cloud estate — including the assets the organisation has forgotten about. Why it matters: most cloud breaches involve an asset nobody knew was exposed — a forgotten development account, a public bucket from a migration, or an orphaned test environment with production credentials. This is the heart of cloud penetration testing and where the highest-severity findings almost always emerge.
Why it matters: a single over-permissioned role can convert a low-privilege foothold into full environment compromise without exploiting a single software vulnerability. This phase is what separates genuine cloud penetration testing from configuration scanning. Findings are validated by demonstrating real, controlled exploitation — proving what an attacker could actually achieve.
Boundaries observed throughout: no destructive actions, no customer data exfiltration, no impact on availability, and no techniques prohibited by the provider. Proof of concept, not proof of damage. Retesting should follow remediation to confirm fixes are effective and have not introduced new issues. Use this to assess coverage — whether you are testing internally or evaluating a provider’s scope.
What not to do: do not harden the environment specifically for the test. Testing a temporarily hardened environment produces a report describing a system you do not actually operate. Discovery and enumeration — cloud provider CLIs, ScoutSuite, Prowler, CloudMapper, and custom API-driven enumeration Identity and privilege analysis — PMapper, Cloudsplaining, IAM policy simulators, and graph-based permission analysis Exploitation frameworks — Pacu (AWS), MicroBurst and ROADtools (Azure), and purpose-built exploitation scripts The critical caveat: automated tools reliably surface misconfigurations, but they do not chain findings together. Recognising that three individually low-severity issues combine into a full compromise path is manual analysis — and it is where the real value of a penetration test lies.
Understanding the methodology is the first step. If you are ready to assess your own environment, our team performs cloud penetration testing across AWS, Azure and GCP — scoped to your architecture and aligned to provider testing policies. From AWS to Azure to GCP, businesses now run critical workloads on platforms that change by the minute. With that speed comes risk. Studies show that misconfigurations, identity flaws, and exposed APIs account for the majority of cloud breaches.
This is why penetration testing in the cloud is no longer optional. Unlike traditional IT, cloud environments shift constantly; every new bucket, role, or pipeline can open the door to attackers. A well-executed pen test gives both executives and security teams clarity: where risks actually exist, how they can be exploited, and what must be fixed before a real attacker makes the move.
4. Practical Deployment, Analysis & Case Studies In this guide, we’ll break down why cloud penetration testing is different, how to run it step by step in AWS, Azure, and GCP, and what lessons recent real-world breaches teach us for 2025 and beyond. Cloud penetration testing is not just on-prem testing in a new setting. In AWS, Azure, and GCP, the provider secures the platform, but the customer must secure workloads, data, and settings. Most failures happen here, misconfigurations cause almost a quarter of cloud incidents, and Gartner predicts that by 2025, 99% of cloud breaches will be the customer’s fault.
The Capital One breach, which exposed 100 million records, was not due to a sophisticated exploit but a misconfigured web application firewall (WAF) in an AWS cloud environment, not a complex exploit. This shows why cloud testing must focus on identity, access, and configuration, while also accounting for AI-driven monitoring. Cloud penetration testing, in short, is a discipline of its own, faster, sharper, and focused on risks unique to the cloud.
Decide what success looks like: Which assets are in scope (e.g., EC2, S3, Azure Blob, Kubernetes clusters)? Are you uncovering IAM weaknesses, testing data storage, or evaluating resilience under attack? A well-defined scope reduces noise and ensures findings align with business risk. Each cloud provider handles penetration testing differently, and overlooking this step can halt your assessment before it starts.
Securing provider approvals, along with internal executive sign-off, ensures your testing is compliant, safe, and credible. Misconfigurations are the leading cause of cloud incidents. Here’s what to test across AWS, Azure, and GCP: Do not attempt DDoS, stress tests, or infrastructure-wide scanning; they are often prohibited. To identify critical vulnerabilities in your cloud environment before attackers do: Download our exclusive Checklist The timing of a cloud penetration test is just as important as the test itself. In fast-moving environments like AWS, Azure, and GCP, risks do not only appear once a year; they emerge whenever systems change, scale, or connect with new services.
The right time to test is after major changes, before audits, following incidents, and at regular intervals that keep pace with the cloud’s speed. Testing at the wrong time can leave blind spots that attackers exploit long before the next scheduled assessment. Not every team has the bandwidth or expertise to perform cloud pen tests. We help organizations conduct safe, compliant penetration testing across AWS, Azure, and GCP. Contact our experts to get started.
Penetration testing in the cloud is no longer optional; it is essential. But testing alone is not enough. With identity-based threats and API exposure on the rise, adopting a Zero Trust approach is key. Zero Trust assumes no implicit trust; every user, device, and system must be continuously verified. Start by integrating penetration testing into your CI/CD pipeline and enforcing least privilege across all accounts.
Shantanoo Govilkar brings over 30 years of experience in cybersecurity strategy, IT leadership, and business transformation. At DivIHN, he leads the Risk and Cybersecurity Solutions practice, working with enterprise clients across healthcare, financial services, manufacturing, and technology sectors. He is a Certified Global CISO, a member of FBI InfraGard, and a contributor to the GlobalCISO Leadership Foundation.
A practical guide to cloud penetration testing across AWS, Azure, and GCP. Learn methods, tools, and best practices to identify vulnerabilities and improve security. In the digital age, businesses must adopt an adaptive Enterprise Architecture to succeed. Many businesses have decided to use Salesforce's customer relationship management solution.
Cloud environments have redefined the attack surface and, with them, the role of penetration testing. 80% of organizations have experienced at least one cloud security breach in the past year, with an average of 43 misconfigurations per account. What used to be a matter of scanning ports and identifying known exploits is now about understanding complex trust relationships, misconfigured identities, and services that rarely behave consistently.
This guide breaks down how to approach cloud penetration testing with the depth and precision modern infrastructure demands. Building on these challenges, cloud penetration testing takes a fundamentally different approach. Unlike traditional pentests that assume a fixed, on-premises infrastructure, cloud pentesting adapts to the cloud’s dynamic, API-driven nature and shared-responsibility model. It focuses specifically on testing what you control within your IaaS, PaaS, or SaaS stacks.
The distinctions between cloud and traditional penetration testing come down to several key factors: Here is the methodology to assess cloud security, from mapping assets and reviewing configurations to exploiting vulnerabilities, reporting risks, and verifying fixes. This stepwise process ensures cloud environments are tested against real-world attack scenarios across AWS, GCP, and Azure.
The initial crucial step for a cloud penetration test is Inventory Mapping. It means identifying and inventorying all the cloud-based assets in a target environment. You identify the complete attack surface, ensuring no crucial component is missed during testing. Begin by using reconnaissance tools to discover exposed services and assets. For AWS, leverage the AWS CLI combined with commands like aws ec2 describe-instances to enumerate EC2 instances, or aws s3 ls to list S3 buckets.
Tools like Nmap can scan for open ports (e.g., nmap -sS -p- ), while Shodan helps find internet-facing cloud assets. CloudMapper generates visual network diagrams of your AWS infrastructure, making it easier to map relationships between services. As part of this step, catalog all segregated compute resources (EC2 instances, Lambda functions), storage resources (S3 buckets, EBS volumes), databases (RDS, DynamoDB), network components (VPCs, security groups), and IAM entities (users, roles, policies).
Document API endpoints and integrate findings into a centralized asset inventory for continuous visibility. One of the most important parts of a cloud pentest methodology is identifying misconfigurations that can be exploited. This phase is called cloud configuration review. In this phase, you need to have excellent knowledge of all services used in the cloud infrastructure and best practices from each cloud provider . Now, let us dissect this for the three largest cloud providers: AWS, GCP, and Azure.
Penetration testing in the AWS Penetration Testing Service means extensive scanning of each service and its configurations. Start by setting up AWS CLI with read-only credentials for reconnaissance. Use aws iam get-account-authorization-details to extract all IAM policies and roles, then analyze them for overly permissive access. S3Scanner : A tool for finding and testing S3 buckets. Execute python3 s3scanner.py --threads 5 buckets.txt to check for public read/write access. In 2024, 1.48% of S3 buckets remained publicly accessible according to industry data, making this crucial.
AWS CLI : Official AWS command-line tool. Install via pip install awscli , configure credentials, then enumerate resources across all regions using commands like aws ec2 describe-security-groups to find open ports (0.0.0.0/0) in security groups. Scout Suite – Open-source multi-cloud security auditing tool. Run python scout.py aws to generate HTML reports highlighting IAM misconfigurations, S3 bucket permissions, and CloudTrail settings. It checks against 400+ rules and outputs findings by severity.
Pacu : An open-source AWS exploitation framework. After installing, run run iam__enum_permissions to enumerate IAM permissions, then run s3__download_bucket to test data exfiltration. Pacu simulates real attacks like privilege escalation and EC2 impersonation. For example, Capital One’s 2019 breach could have been detected using Pacu to identify the misconfigured Web Application Firewall.
CloudMapper – A tool to generate network diagrams of AWS environments. Use python cloudmapper.py prepare --account myaccount to collect data, then python cloudmapper.py webserver to visualize VPC connections and identify network segmentation issues. GCP penetration testing requires a thorough understanding of Google Cloud Services and their security models. Start by authenticating with service account credentials and use gcloud compute instances list to enumerate resources. The process incorporates GCP-native tools and third-party solutions to find threats in the GCP cloud.
Forseti Security : Open-source tool for GCP security monitoring. Deploy it to continuously scan for policy violations, unusual IAM changes, and firewall misconfigurations. GCP CLI (gcloud): Official command-line tool. Run gcloud projects get-iam-policy [PROJECT_ID] to audit IAM bindings and identify excessive permissions like “Editor” or “Owner” roles assigned broadly.
G-Scout : GCP security scanner that automatically audits configurations. Execute python gscout.py -p [PROJECT_ID] to scan for exposed Cloud Storage buckets and overprivileged service accounts. GCPBucketBrute : Google Storage bucket enumeration tool. Use it to brute-force common bucket naming patterns and identify publicly accessible storage with python3 gcpbucketbrute.py -k keywords.txt .
5. Performance Evaluation & Extended Technical Observations Azure penetration testing is a security assessment targeting Microsoft Azure cloud services, including VMs, storage accounts, Virtual Networks, and Azure AD. Begin by authenticating with az login and run az account list to enumerate subscriptions and resources.
Stormspotter – Creates attack graphs within Azure environments. After data collection via stormspotter.py , analyze privilege escalation paths from Azure AD users to subscription-level permissions. Azure CLI – Command-line tool to manage Azure resources. Use az vm list to list all VMs and az network nsg rule list to check network security group rules for overly permissive access (like allowing SSH from any source).
Azucar – Azure auditing tool that generates configuration reports. Run Get-AzucarReport in PowerShell to analyze Azure AD roles, storage account encryption, and VM configurations. MicroBurst – PowerShell-based scripts for Azure security assessment. Use Invoke-EnumerateAzureBlobs to discover publicly accessible storage containers and Invoke-AzureRmVMBulkCMD to execute commands across VMs.
In this stage of the cloud pentesting methodology, you need to find different types of vulnerabilities and attempt to exploit them to help the organization understand real risks. It combines automated scanning (as discussed in the previous step) with manual testing techniques to comprehensively assess the cloud environment’s security posture . Begin with cloud-native and third-party tools that can perform automated vulnerability scanning. For instance, AWS Inspector automatically discovers EC2 instances and Lambda functions, continuously scanning them for CVE findings and network exposure risks.
With these tools, you can easily find misconfigurations and common vulnerabilities specific to each cloud platform. For a more in-depth analysis, you can also utilize market-tested vulnerability scanners such as Astra Security , Nessus , Qualys , or Tenable . These VAPT tools are often configured to scan cloud environments with specific modules for cloud services.
For example, Nessus Cloud Edition can orchestrate scans of your cloud VPC or managed instances, producing detailed HTML/JSON reports for compliance teams. Real-world case: the 2024 Football Australia breach occurred when developers misconfigured AWS S3 buckets, exposing 127 digital storage containers with player data—a vulnerability that automated scanning could have detected.
The reporting part of a cloud penetration test is essential. It involves taking technical discoveries and putting them in simple language for the client. A good report should graphically display the findings, highlight areas that could be exploited, and outline the necessary fixes. Structure your findings, detailing every vulnerability (describing the issue and potential impact) with proof of how to reproduce it. Utilize a widely recognized vulnerability scoring system such as CVSS (Common Vulnerability Scoring System) to aid in prioritizing findings.
For example, an S3 bucket with public read access might score 7.5 (High), while an overly permissive IAM role allowing privilege escalation could score 9.1 (Critical). Don’t miss out on an executive summary and a technical section. The guidance should outline a clear path for developers to remediate each vulnerability.
Include specific commands (e.g., aws s3api put-public-access-block ) and infrastructure-as-code examples. Screenshots from tools like Pacu or ScoutSuite showing the misconfiguration add credibility. This is where you analyze your penetration test results to enhance the overall security of your environment. This stage should be conducted in close cooperation between the penetration testing team and the client’s development team.
Prioritize fixes based on CVSS scores and business impact; remediate critical IAM misconfigurations before addressing low-severity logging gaps. The last phase of penetration testing of cloud infrastructures is verifying that the provided solutions have fixed the identified vulnerabilities. For complex vulnerabilities or significant modifications of the cloud infrastructure, these targeted retests may range from focused to more comprehensive assessments.
Of course, pay special attention to critical vulnerabilities. A more rigorous test than usual will likely be required to confirm that they have been completely mitigated. Re-run the same tools (Scout Suite, Pacu) with identical credentials to verify that the issues no longer appear. For example, if significantly misconfigured IAM permissions are detected, verify that the new structure adheres to the principle of least privilege and doesn’t allow unauthorized access.
Test this by attempting the same privilege escalation path (e.g., using Pacu’s iam__privesc_scan module) and confirming it now fails. According to 2024-2025 data, 82% of cloud misconfigurations stem from human error, making verification essential to prevent recurrence. Knowledge of various cloud computing models is mandatory when performing cloud penetration tests, as each model has security implications.
Different testing approaches give you different views of risk. Pick the model that matches your threat profile and the questions you need answers to. Testers receive no internal information or credentials. They act like an external hacker using OSINT, DNS enumeration, and public API probing to find visible weaknesses. This shows how exposed your perimeter and public services really are.
In this method, testers get limited access or partial documentation, like a user account or topology notes. This simulates a compromised employee or contractor and helps reveal privilege escalation and lateral movement paths. It balances realism with the ability to dig deeper. In white-box pentesting, testers have full access to code, configurations, IaC templates, and credentials. This is a comprehensive audit that uncovers subtle misconfigurations in IAM, Terraform, CloudFormation, and CI/CD pipelines. It finds issues that surface scans often miss.
Red teaming or adversary emulation, cloud native threat simulation, and continuous pentesting are often used as complementary approaches. Red teams validate detection and response. Adversary emulation follows frameworks such as MITRE ATT&CK for Cloud. Automated emulators and continuous checks validate controls across deployments and catch drift. While the term’ cloud penetration testing’ itself is broad and encompasses various disciplines, several core aspects require a definite focus due to their adverse impact on the overall security posture. It can be broken down into the following broad categories: Identity has become the primary security perimeter in cloud environments, making IAM testing critical: The dynamic and complex nature of cloud environments makes penetration testing more challenging. Some of the challenges during this phase require pentesters to modify their approach to pentesting and focus on key points. Let’s take a look at some of them.
The shared responsibility model approach requires carefully scoped tests that target areas under client control and clearly define boundaries with the cloud provider’s offerings. This requires clear communication and a deep understanding of cloud architectures. Distributed cloud environments also present complicated issues surrounding legality and ethics. In some instances, cloud penetration testers must also navigate jurisdictional claims and data protection laws (for example, the Service Agreement), particularly in multi-tenant scenarios.
The characteristics of cloud resources are dynamic, including fast provisioning and auto-scalability, which necessitate agile testing. Static, point-in-time assessments can rapidly become outdated, and a process is needed to monitor and adjust them. Eliminate misconfigurations and hidden risks in your cloud setup with Astra’s pentest platform. Astra Security’s cloud penetration testing services blend automated scanning and expert-driven manual testing to uncover deep, actionable vulnerabilities in AWS, Azure, and GCP environments. From misconfigurations and exposed services to logic flaws and privilege escalations, our Offensive Security Engine runs 400+ cloud-specific test cases while our security team layers on custom tests tailored to your infrastructure.
Covering critical vectors across cloud storage, networking, and IAM, we evaluate configurations against CIS benchmarks, analyze access controls in line with the PoLP, and flag gaps using industry frameworks like the CSA Cloud Controls Matrix (CCM). The built-in business logic testing helps expose hidden issues like privilege escalation, insecure workflows, and data access bypasses often missed by automated tools.
Inside Astra’s platform, all vulnerabilities (manual or automated) are delivered with clear impact, reproduction steps, and remediation guidance. With configuration reviews, gap analysis, real-time fix validation, and audit-ready reporting, you can review authentication setups, security groups, firewall rules, and encryption policies through a dedicated dashboard. Modern cybersecurity plans require multi-cloud pentesting (a must-have), a solution that enables organizations to identify and remediate security vulnerabilities, typically in a tightly integrated cloud environment. This keeps the infrastructure and applications safe from threats and enables compliance across the multi-cloud area.
The process requires a deep theoretical understanding of cloud architectures, as well as a comprehension of specific challenges, such as the shared responsibility model and dynamic environments. Routine penetration testing keeps organizations informed of rapidly changing threats and maintains compliance with industry regulations. By embracing cloud penetration testing as a continuous process, businesses can utilize the latest technology while efficiently managing security risks.
This zero-trust approach secures assets and builds a reputation with stakeholders, further aiding business objectives in increasing cloud reliance. No, AWS doesn’t pentest your environment directly, but allows you to host pentesting tools on it. It also allows you to perform penetration testing, including activities like vulnerability scanning, exploitation attempts, and code injection, but it excludes DoS attacks without prior approval.
Cloud pen testing blends IT security and hacking skills. Start with general IT or cybersecurity roles to build a foundation. Then focus on cloud platforms like AWS or Azure through courses and certifications (Security+ or CCSP). Practice with CTFs and labs to hone your hands-on skills in finding and exploiting cloud vulnerabilities. Cloud security testing safeguards your confidential information in the cloud and checks your cloud provider’s security measures and your cloud-based applications for weaknesses that hackers could exploit.
Cloud penetration testing is essential for organizations that use cloud services such as AWS, Azure, or GCP. It benefits C-level executives, security managers, and IT professionals responsible for infrastructure and data security. Essentially, any business that needs to validate its cloud security controls should consider it. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Penetration%20test • https://en.wikipedia.org/wiki/Aikido%20Security • https://en.wikipedia.org/wiki/Fluid%20Attacks • https://pentagoninfosec.com/blog/cloud-infrastructure-penetration-testing • https://aws.amazon.com/blogs/security/inside-aws-security-agent-a-multi-agent-architecture-for-automated-penetration-testi ng/ • https://threatexploit.ai/en/resources/cloud-penetration-testing • https://bluefire-redteam.com/cloud-penetration-testing-guide/ • https://divihn.com/perspectives/blog/how-to-perform-penetration-testing-cloud-environments • https://www.getastra.com/blog/cloud/cloud-penetration-testing/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Automated Cloud Penetration Testing.
[*] Metasploit Scan Running on Target Subnet for Automated Cloud Penetration Testing... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |