Complete Technical Paper Content — Automated Directory Traversal Vulnerability Scanner Github
Overview & System Context
Automated Directory Traversal Vulnerability Scanner Github: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9514 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background The Hewlett-Packard Company, commonly shortened to Hewlett-Packard ( HEW-lit PAK-Ird) or HP, was an American multinational information technology company. It was founded by Bill Hewlett and David Packard in 1939 in a one-car garage in Palo Alto, California. Growing to become an influential high-tech powerhouse at the heart of Silicon Valley, the company was known for its progressive business philosophy, deemed the HP Way. HP developed and provided a wide variety of hardware components, as well as software and related services, to consumers, small and medium-sized businesses (SMBs), and fairly large companies, including customers in government sectors. At its peak in 2011, HP employed 350,000 people around the globe. The company officially split into Hewlett Packard Enterprise and HP Inc. in 2015. HP initially produced a line of electronic test and measurement equipment. It won its first big contract in 1938 to provide the HP 200B, a variation of its first product, the HP 200A low-distortion frequency oscillator, for Walt Disney's production of the 1940 animated film Fantasia, which allowed Hewlett and Packard to formally establish the Hewlett-Packard Company on July 2, 1939. The company grew into a multinational corporation widely respected for its products. HP was the world's leading PC manufacturer from 2007 until the second quarter of 2013 when Lenovo moved ahead of HP. HP specialized in developing and manufacturing computing, data storage, and networking hardware, designing software, and delivering services. Major product lines included personal computing devices, enterprise and industry standard servers, related storage devices, networking products, software, and a range of printers and other imaging products. The company directly marketed its products to households, small- to medium-sized businesses, and enterprises, as well as via online distribution, consumer-electronics, and office-supply retailers, software partners, and major technology vendors. It also offered services and a consulting business for its products and partner products. In 1999, HP spun off its electronic and bio-analytical test and measurement instruments business into Agilent Technologies; HP retained focus on its later products, including computers and printers. It merged with Compaq in 2002 in what was then a major deal within the industry. They made numerous other acquisitions including Electronic Data Systems in 2008, which led to combined revenues of $118.4 billion that year and a Fortune 500 ranking of 9 in 2009, and later 3Com, Palm, Inc., and 3PAR, all in 2010, followed by Autonomy Corp. However, as a result of the turmoil created by several of these acquisitions, the company's fortunes swiftly declined in the 2010s. This led to Hewlett-Packard Company's split into two separate companies on November 1, 2015: its enterprise products and services business were spun-off to form Hewlett Packard Enterprise, while its personal computer and printer businesses became HP Inc. The split was structured so that the former Hewlett-Packard Company would change its name to HP Inc. and spin off Hewlett Packard Enterprise as a newly created company. HP Inc. retained the old Hewlett-Packard's stock-price history and original NYSE ticker symbol; Hewlett Packard Enterprise trades under its own ticker symbol: HPE.
Bill Hewlett and David Packard graduated with degrees in electrical engineering from Stanford University in 1935. The company started in a garage in Palo Alto during a fellowship they had with past professor Frederick Terman at Stanford during the Great Depression, whom they considered a mentor. In 1938, Packard and Hewlett began part-time work in a rented garage with an initial capital investment of US$538 (equivalent to $12,305 in 2025). In 1939, Hewlett and Packard decided to formalize their partnership. They tossed a coin to decide whether the company they founded would be called Hewlett-Packard (HP) or Packard-Hewlett. Hewlett and Packard's first financially successful product was a precision audio oscillator known as the HP 200A, which used a small incandescent light bulb as a temperature dependent resistor in a critical portion of the circuit, and a negative feedback loop to stabilize the amplitude of the output sinusoidal waveform. This allowed the HP 200A to be sold for $89.40 when competitors were selling less stable oscillators for over $200. The 200 series of generators continued production until at least 1972 as the 200AB, still tube-based but improved in design through the years. One of the company's earliest customers was Bud Hawkins, chief sound engineer for Walt Disney Studios, who bought eight HP 200B audio oscillators (at $71.50 each) to be used in the animated film Fantasia. HP's profit at the end of 1939, its first full year of business, was $1,563 (equivalent to $36,177 in 2025) on revenues of $5,369. In 1942, they built their first building at 395 Page Mill Road and were awarded the Army-Navy "E" Award in 1943. HP employed 200 people and produced the audio oscillator, a wave analyzer, distortion analyzers, an audio-signal generator, and the Model 400A vacuum-tube voltmeter during the war. Hewlett and Packard worked on counter-radar technology and artillery shell proximity fuzes during World War II; the work exempted Packard from the draft, but Hewlett had to serve as an officer in the Army Signal Corps after being called to active duty. HP was incorporated on August 18, 1947, with Packard as president. Sales reached $5.5 million in 1951 with 215 employees. The company went public on November 6, 1957. In 1959, a manufacturing plant was established in Böblingen and a marketing organization in Geneva. Packard handed the presidency over to Hewlett when he became chairman in 1964, but remained CEO of the company.
HP is recognized as the symbolic founder of Silicon Valley, though it did not actively investigate semiconductor devices until a few years after the "traitorous eight" abandoned William Shockley to create Fairchild Semiconductor in 1957. The company's HP Associates division was established around 1960 under the leadership of Jack Melchor to develop semiconductor devices primarily for internal use. Instruments and calculators were some of the original HP products that used semiconductor devices. During the 1960s, HP partnered with Sony and Yokogawa Electric in Japan to develop several high-quality products.
The products were not a huge success, as there were high costs involved in building HP-looking products in Japan. In 1963, HP and Yokogawa formed the joint venture Yokogawa-Hewlett-Packard to market HP products in Japan. HP bought Yokogawa Electric's share of Hewlett-Packard Japan in 1999. HP spun off the small company Dynac to specialize in digital equipment. The name was picked so that the HP logo could be turned upside down to be a reflected image of the logo of the new company (DY). Dynac was eventually renamed Dymec and folded back into HP in 1959. HP experimented with using Digital Equipment Corporation (DEC) minicomputers with its instruments, but entered the computer market in 1966 with the HP 2100 / HP 1000 series of minicomputers after it decided that it would be easier to build another small design team than deal with DEC. The minicomputers had a simple accumulator-based design with two accumulator registers and, in the HP 1000 models, two index registers. The series was produced for 20 years in spite of several attempts to replace it, and was a forerunner of the HP 9800 and HP 250 series of desktop and business computers. Beginning in 1961, Hewlett-Packard was listed on the New York Stock Exchange (as well as the now-closed Pacific Exchange) under its own ticker symbol, "HWP". At the end of 1968, Packard handed over the duties of CEO to Hewlett to become United States Deputy Secretary of Defense in the incoming Nixon administration. He resumed the chairmanship in 1972 and served until 1993, but Hewlett remained the CEO.
The HP 3000 was an advanced stack-based design for a business computing server, later redesigned with RISC technology. The HP 2640 series of smart and intelligent terminals introduced forms-based interfaces to ASCII terminals, and also introduced screen labeled function keys. The HP 2640 series included one of the first bit mapped graphics displays that, when combined with the HP 2100 21MX F-Series microcoded Scientific Instruction Set, enabled the first commercial WYSIWYG presentation program, BRUNO, that later became the program HP-Draw on the HP 3000. Although scoffed at in the formative days of computing, HP surpassed IBM as the world's largest technology vendor in terms of sales. HP was identified by Wired magazine as the producer of the world's first device to be called a personal computer: the Hewlett-Packard 9100A, introduced in 1968. HP called it a desktop calculator because, as Hewlett said: "If we had called it a computer, it would have been rejected by our customers' computer gurus because it didn't look like an IBM. We therefore decided to call it a calculator, and all such nonsense disappeared." An engineering triumph at the time, the logic circuit was produced without any integrated circuits, and the CPU assembly was entirely executed in discrete components. With CRT display, magnetic-card storage, and printer, the price was around $5,000. The machine's keyboard was a cross between the keyboard of a scientific calculator and the keyboard of an adding machine. There was no alphabetic keyboard. Apple co-founder Steve Wozniak originally designed the Apple I computer while working at HP and offered it to HP under its right of first refusal to his work. It did not take it up as the company wanted to stay in scientific, business, and industrial markets. Wozniak said that HP "turned him down five times", but that his loyalty to HP made him hesitant to start Apple with Steve Jobs. The company earned global respect for a variety of products. They introduced the world's first handheld scientific electronic calculator in 1972 (the HP-35), the first handheld programmable in 1974 (the HP-65), the first alphanumeric, programmable, expandable in 1979 (the HP-41C), and the first symbolic and graphing calculator, the HP-28C. Like its scientific and business calculators, HP oscilloscopes, logic analyzers, and other measurement instruments had a reputation for sturdiness and usability. HP introduced the Hewlett-Packard Interface Bus (HPIB) computer peripheral interface (later cloned by National Instruments as GPIB and standardized by the IEEE as IEEE-488) on its relay actuator products in 1973. HPIB was later integrated into most high end test & measurement equipment it produced from 1980 onward. As early as 1977, HP began production of the HP856x spectrum analyzers to complement its RF power meters and sensors capable of measuring signals in excess of 20 GHz. HP also produced configurable chassis based sweep generators capable of generating signals to 20 GHz. Other T&M products of the time included lab grade multimeters, microwave frequency counters, RF amplifiers, high accuracy microwave detectors, lab grade power supplies and more. These products were succeeded by modernized versions as well as the introduction of the scalar and vector network analyzer product lines prior to the business being spun off into Agilent Technologies. The HP 9800 series of technical desktop computers started in 1971 with the 9810A. The HP Series 80 started in 1979 with the 85. Some of these machines used a version of the BASIC programming language, which was available immediately after they were switched on, and used a proprietary magnetic tape for storage. HP computers were similar in capabilities to the much later IBM Personal Computer, though the limitations of available technology forced prices to be high. In 1978, Hewlett stepped down as CEO and was succeeded by John A. Young.
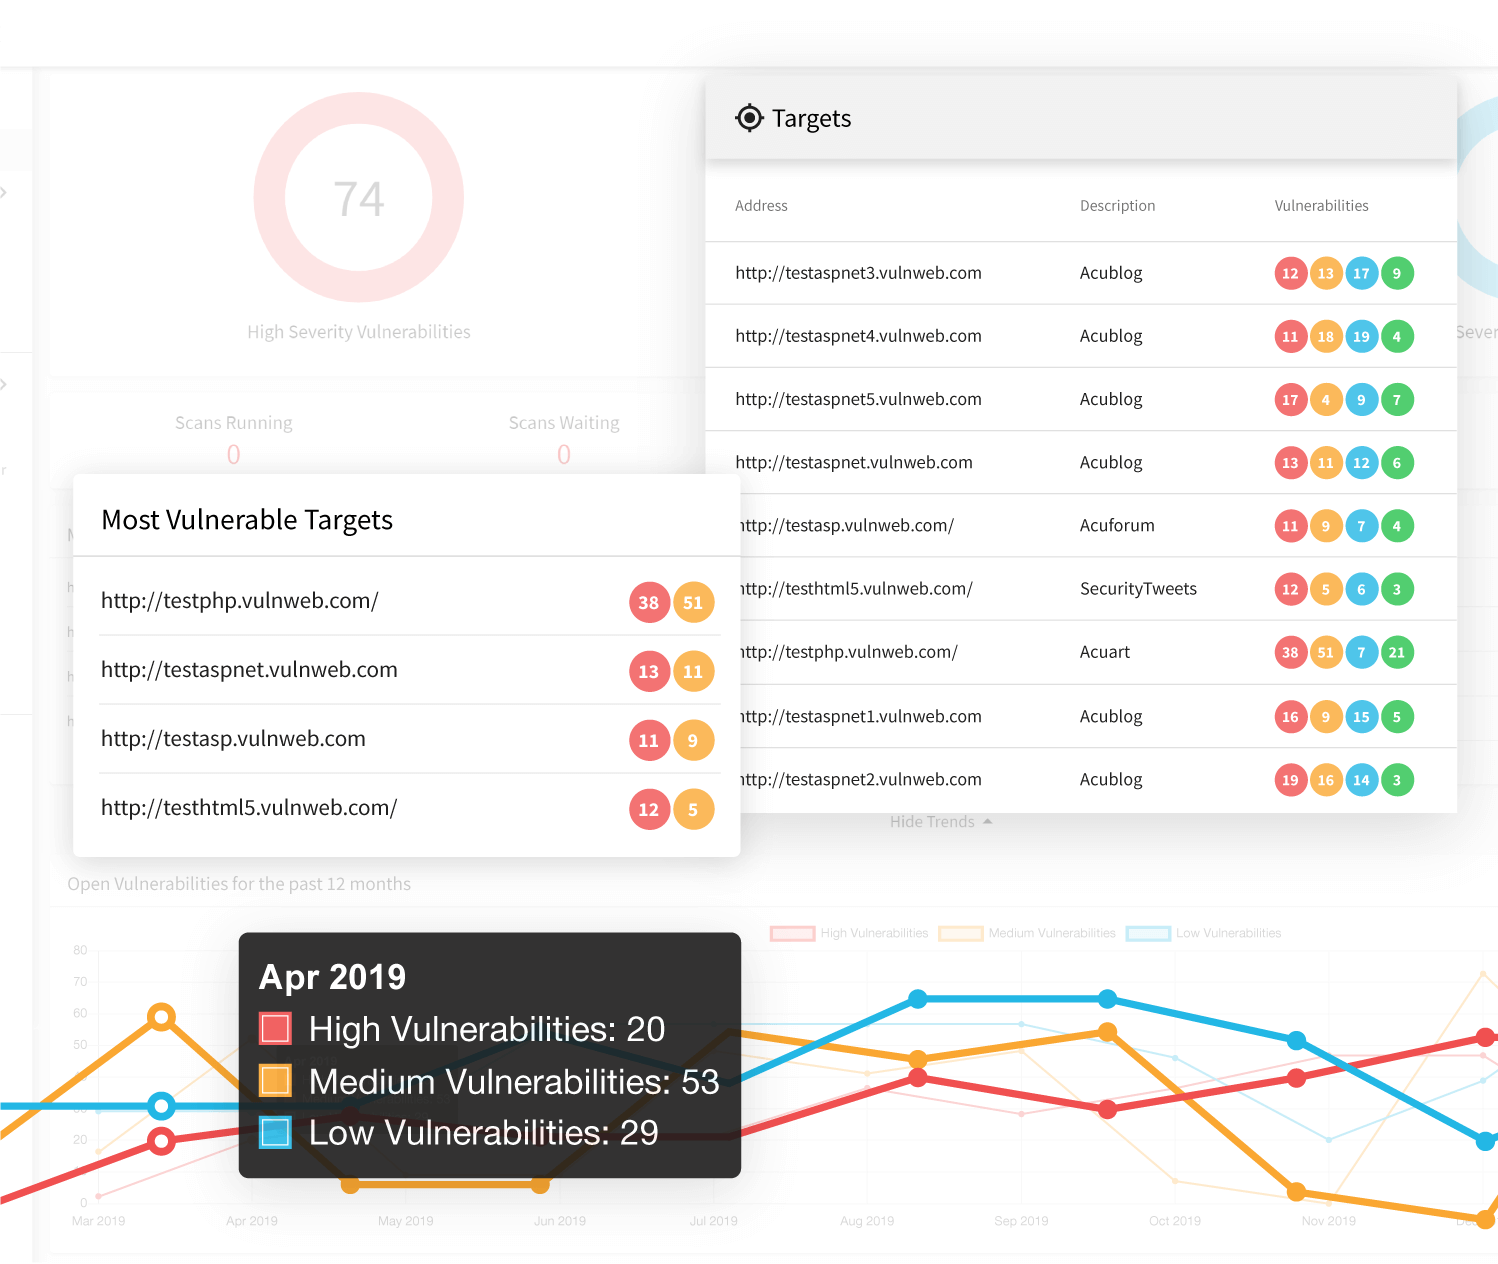
Figure 1: Vulnerability Scanner – Automated Web App Security Testing In the 1990s, HP expanded its computer product line, which initially had been targeted at university, research, and business users, to reach consumers. In 1995, HP entered into the home and home office market for the first time with the introduction of the HP Pavilion brand of personal computers, which initially featured desktop models but later added laptop and notebook models to the lineup in 1999. HP also grew through acquisitions: it bought Apollo Computer in 1989 and Convex Computer in 1995. In 1992, Young was succeeded by Lewis E. Platt, and in 1993 Packard stepped down from the board, with Platt succeeding Packard as chairman. In 1993, HP acquired Advanced Design System from Pathwave. The ADS suite of RF simulation tools was spun off into Agilent in 1999 along with related T&M business units, all of which were carried forward into the spinoff of Agilent into Keysight. Later in the decade, HP opened hpshopping.com as an independent subsidiary to sell online, direct to consumers; in 2005, the store was renamed "HP Home & Home Office Store". From 1995 to 1999, Hewlett-Packard were sponsors of the English football team Tottenham Hotspur. In 1999, all of the businesses not related to computers, storage, and imaging were spun off from HP to form Agilent Technologies. Agilent's spin-off was the largest initial public offering in the history of Silicon Valley, and it created an $8 billion company with about 30,000 employees, manufacturing scientific instruments, semiconductors, optical networking devices, and electronic test equipment for telecom and wireless, research and development, and production. In July 1999, HP appointed Carly Fiorina as the first female CEO of a Fortune-20 company in the Dow Jones Industrial Average. Fiorina received a larger signing offer than any of her predecessors. The same year, Fiorina articulated a set of "rules of the garage" in an attempt to reinterpret the spirit of the company's founders.
On September 3, 2001, HP announced that an agreement had been reached with Compaq to merge the two companies. On May 3, 2002, after passing a shareholder vote, HP officially announced the merger with Compaq; the newly-merged company would officially launch a few days later on May 7, 2002. Prior to this, plans had been put in place to consolidate the companies' product teams and product lines. As Compaq acquired Tandem Computers in 1997 and Digital Equipment Corporation (DEC) in 1998, HP gained control of both acquired companies' product lines, and offered support for the Tandem NonStop family (now owned by Hewlett Packard Enterprise) and DEC products PDP-11, VAX and Alpha for quite some time until the later years where support was gradually dwindled. Both the DEC PDP-11 and VAX were discontinued years prior to the merger, and HP supported Alpha until April 2007. The merger was preceded by a proxy fight in 2001 with numerous large HP shareholders, in particular Bill Hewlett's son Walter and other descendants of the business founders, objecting to the merger, only approving it reluctantly. Prior to the merger, HP's ticker symbol was "HWP", which became "HPQ" shortly after acquiring Compaq, and was subsequently announced on May 6, 2002. The new ticker symbol is a combination of the two previous symbols, "HWP" and "CPQ" respectively, showing the significance of the alliance. HP then became a major producer in desktop computers, laptops, and servers for many different markets in the coming years. In 2002, Mscape was established as a mobile media gaming platform that could be used to create location-based games. HP would release new models of laptops under the Pavilion name during the early-to-mid 2000s, including the dv1000 series (which includes the dv1040 and the later dv1658 models) in August 2004 and the dv4000 and dv8000 series in 2005. In January 2005, following years of underperformance, which included HP's Compaq merger that fell short and disappointing earning reports, the board asked Fiorina to resign as chair and chief executive officer of the company, which she did on February 9, 2005. After her departure, HP's stock jumped 6.9 percent. Robert Wayman, chief financial officer of HP, served as interim CEO while the board undertook a formal search for a replacement. Mark Hurd of NCR Corporation was hired to take over as CEO and president, effective April 1, 2005. Hurd was the board's top choice given the revival of NCR that took place under his leadership.
In 2006, HP unveiled several new products including desktops, enhanced notebooks, a workstation, and software to manage them—OpenView Client Configuration Manager 2.0. That same year, HP's share price skyrocketed due to consistent results in the last couple quarters of the year with Hurd's plan to cut back HP's workforce and lower costs. HP was delisted from the Pacific Exchange (now closed with trades going through the NYSE Arca platform) on May 1, 2006, but continues to trade on the New York Stock Exchange as well as Nasdaq. HP introduced a global marketing campaign for its line of personal computers in May 2006 under the tagline "The Computer is Personal Again", coinciding with the launch of its new line of consumer and business products that same month. The campaign aimed at bringing back the computer as a powerful personal tool, utilizing viral marketing and sophisticated visuals, and had its own website. The ads featured Pharrell, Petra Nemcova, Mark Burnett, Mark Cuban, Alicia Keys, Jay-Z, Gwen Stefani, and Shaun White. This campaign applied to HP's product offerings which included desktops, laptops, and other hardware and software. HP introduced new laptop models for the HP Pavilion lineup in 2006, starting with the dv5000 series in January, the dv2000 series in May and later the dv6000 and dv9000 series in July. In July 2007, HP signed a definitive agreement to acquire Opsware in a cash tender deal that values the company at $14.25 per share, which combined Opsware software with the Oracle enterprise IT management software. In the first few years of Hurd's tenure as CEO, HP's stock price more than doubled. By the end of the 2007 fiscal year, HP reached the $100 billion mark for the first time. The company's annual revenue reached $104 billion, allowing HP to overtake competitor IBM. On May 13, 2008, HP and Electronic Data Systems (EDS) announced that they had signed a definitive agreement under which HP would purchase EDS. On June 30, HP announced that the waiting period under the Hart-Scott-Rodino Antitrust Improvements Act of 1976 had expired. "The transaction still requires EDS stockholder approval and regulatory clearance from the European Commission and other non-U.S. jurisdictions and is subject to the satisfaction or waiver of the other closing conditions specified in the merger agreement." The agreement was finalized on August 26, 2008, at $13 billion, and it was publicly announced that EDS would be re-branded. The first targeted layoff of 24,600 former EDS workers was announced on September 15, 2008. (The company's 2008 annual report gave the number as 24,700, to be completed by end of 2009.) This round was factored into the purchase price as a $19.5 billion liability against goodwill. As of September 23, 2009, EDS was known as HP Enterprise Services (now known as DXC Technology). On November 11, 2009, 3Com and Hewlett-Packard announced that the latter would be acquiring 3Com for $2.7 billion in cash. The acquisition was one of the biggest in size among a series of takeovers and acquisitions by technology giants to push their way to become one-stop shops. Since the beginning of the financial crisis in 2007, tech giants have constantly felt the pressure to expand beyond their current market niches. Dell purchased Perot Systems to move into the technology consulting business area previously dominated by IBM. Hewlett-Packard's latest move marked its diversification into enterprise networking gear market dominated by Cisco.
On April 28, 2010, HP announced that it would buy Palm, Inc. for $1.2 billion in cash and debt. The acquisition of Palm, Inc. was finalized on July 1, 2010. Adding Palm handsets to the HP product line created some overlap with the iPAQ series of mobile devices, but was thought to significantly improve HP's mobile presence as iPAQ devices had not been selling well. Buying Palm, Inc. gave HP a library of valuable patents and the mobile operating platform, webOS. Purchasing its webOS was a big gamble to build HP's own ecosystem. On July 1, 2011, HP launched its first tablet, HP TouchPad, which brought webOS to tablet devices. On September 2, 2010, HP won the bidding war for 3PAR with a $33 a share offer ($2.07 billion) that Dell declined to match. After HP acquired Palm Inc., it phased out the Compaq brand. On August 6, 2010, Hurd resigned amid controversy and CFO Cathie Lesjak assumed the role of interim CEO. Hurd had turned HP around and was widely regarded as one of Silicon Valley's star CEOs, and under his leadership, HP became the largest computer company in the world when measured by total revenue. He was accused of sexual harassment against a colleague, though the allegations were deemed baseless. The investigation led to questions concerning some of his expenses and the lack of disclosure related to the friendship. Some observers have argued that Hurd was innocent, but the board asked for his resignation to avoid negative public relations. Public analysis was divided between those who saw it as a commendable tough action by HP and those who saw it as an ill-advised, hasty, and expensive reaction, that ousted a capable leader who had turned the business around. At HP, Hurd oversaw a series of acquisitions worth over $20 billion, which allowed the company to expand into services of networking equipment and smartphones. HP shares dropped 8.4% in after-hours trading, hitting a 52-week low with a $9 billion reduction in market capitalization. Larry Ellison publicly attacked HP's board for Hurd's ousting, stating that the HP board had "made the worst personnel decision since the idiots on the Apple board fired Steve Jobs many years ago". On September 30, 2010, Léo Apotheker was named HP's new CEO and president. His appointment sparked a strong reaction from Ellison, who complained that Apotheker had been in charge of SAP when one of its subsidiaries was systematically stealing software from Oracle. SAP accepted that its subsidiary, which has now closed, illegally accessed Oracle intellectual property. Following Hurd's departure, HP was seen to be problematic by the market, with margins falling and them failing to establish themselves in major new markets such as cloud and mobile services. Apotheker's strategy was to broadly aim at disposing hardware, whilst moving into the more profitable software services sector. On August 18, 2011, HP announced that it would strategically exit the smartphone and tablet computer business, and focus on higher-margin "strategic priorities of Cloud, solutions and software with an emphasis on enterprise, commercial and government markets". It also contemplated selling off its personal computer division or spinning it off into a separate company, and quitting PC development while continuing to sell servers and other equipment to business customers, which was a strategy undertaken by IBM in 2005. On November 1, 2010, the classic 1979 Hewlett-Packard logo was discontinued and replaced with a new circle HP logo, with a larger and thinner wormark, for corporate branding. The 2008 circle variant was continued to be used as the secondary logo.
This also made the 1999 symbol-only variant was also discontinued on the same day. The last product to use this logo was the HP ProLiant DL380 G7. HP's stock dropped by about a further 40% after the company abruptly announced a number of decisions: to discontinue its webOS device business (mobile phones and tablet computers), the intent to sell its personal computer division (at the time HP was the largest personal computer manufacturer in the world), and to acquire British big data software firm Autonomy for a 79% premium, seen externally as an "absurdly high" price for a business with known concerns over its accounts. Media analysts described HP's actions as a "botched strategy shift" and a "chaotic" attempt to rapidly reposition HP and enhance earnings. HP's CFO objected to the Autonomy acquisition. HP lost more than $30 billion in market capitalization during Apotheker's tenure, and on September 22, 2011, the HP Board of Directors fired him as chief executive and replaced him with fellow board member and former eBay chief Meg Whitman, with Raymond J. Lane as executive chairman. Although Apotheker served barely ten months, he received over $13 million in compensation. Weeks later, HP announced that a review had concluded its PC division was too integrated and critical to business operations, and the company reaffirmed its commitment to the Personal Systems Group. On March 21, 2012, HP said its printing and PC divisions would become one unit headed by Todd Bradley from the PC division, and printing chief Vyomesh Joshi left the company. On May 23, 2012, HP announced plans to lay off approximately 27,000 employees, after posting a profit decline of 31% in the second quarter of 2012. Profits declined because of the growing popularity of smart phones, tablets, and other mobile devices, which slowed down personal computer sales. On May 30, 2012, HP unveiled its first net zero energy data center, which used solar energy and other renewable sources instead of traditional power grids. On July 10, 2012, HP's Server Monitoring Software was discovered to have a previously unknown security vulnerability. A security warning was given to customers about two vulnerabilities, and a patch addressing the issues was released. One month later, HP's official training center was hacked and defaced by a Pakistani hacker known as Hitcher to demonstrate a Web vulnerability. On September 10, 2012, HP revised its restructuring figures and started cutting 29,000 jobs. In November 2012, HP wrote off almost $9 billion related to the Autonomy acquisition, which became the subject of intense litigation, as HP accused Autonomy's previous management of fraudulently exaggerating Autonomy's financial position and called in law enforcement and regulators in both countries. Autonomy's previous management accused HP of "textbook" obfuscation and finger pointing to protect HP's executives from criticism and conceal HP culpability, their prior knowledge of Autonomy's financial position, and gross mismanagement of Autonomy after acquisition.
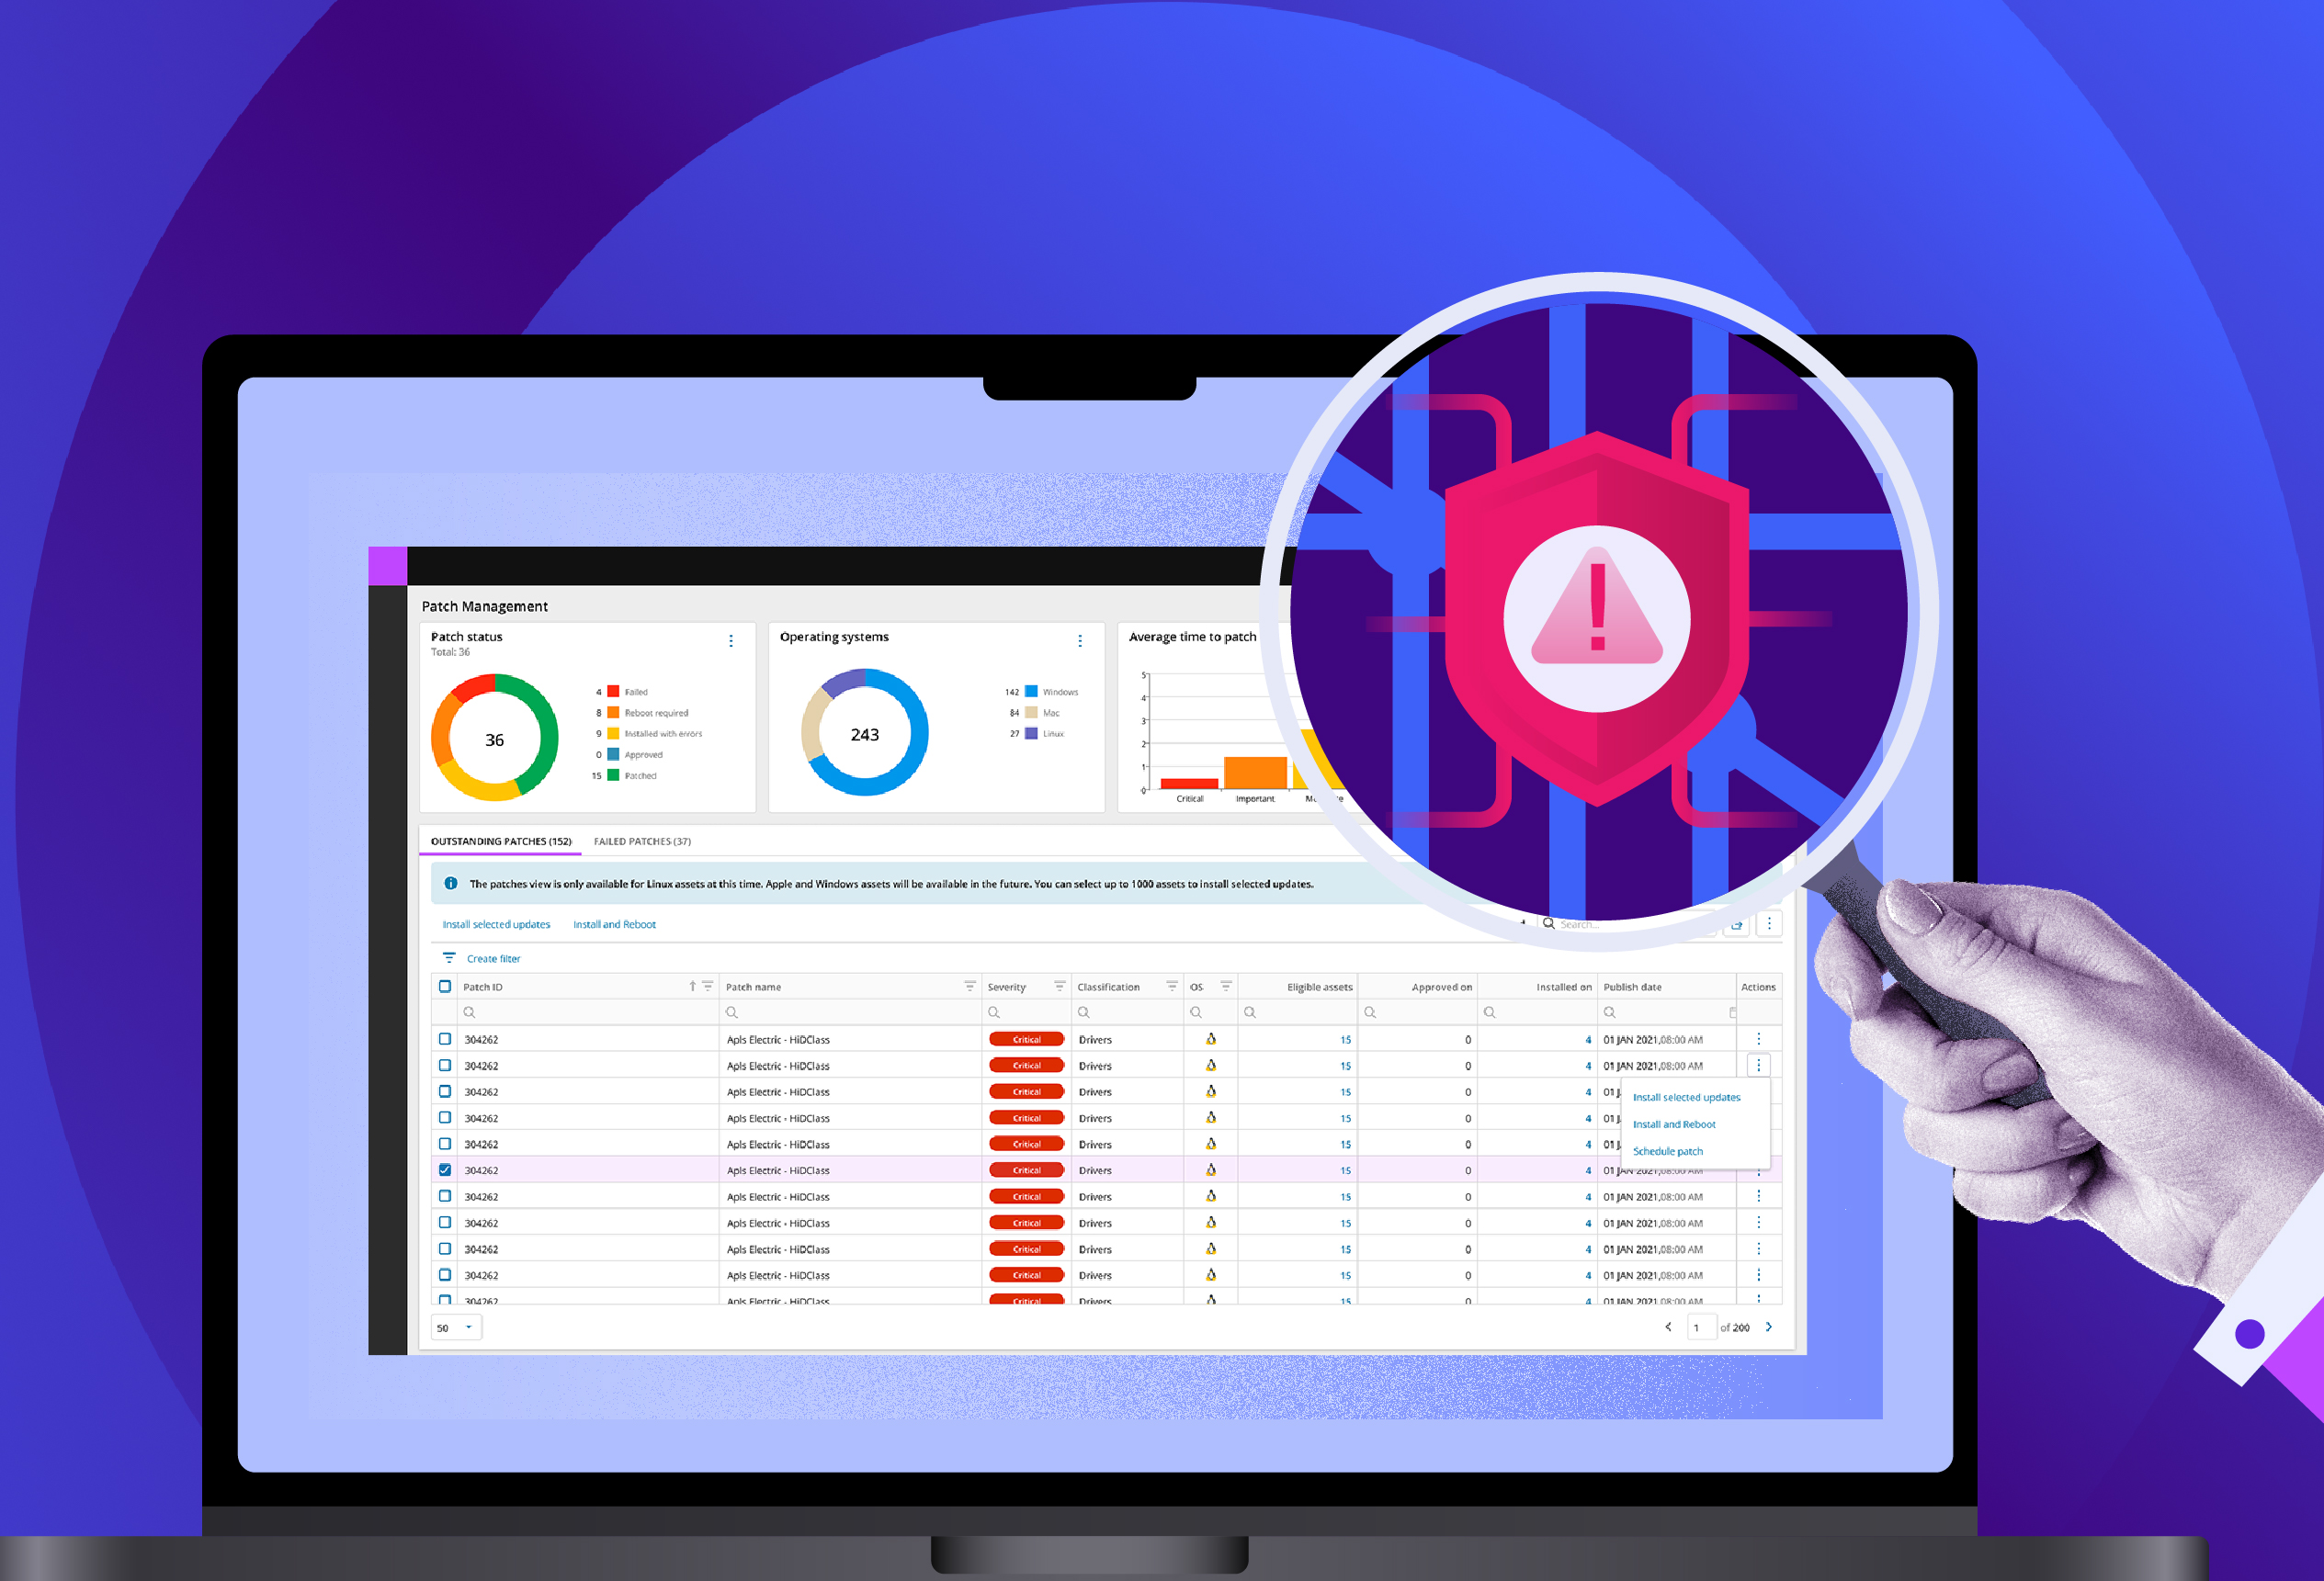
Figure 2: Continuous Vulnerability Scanning Tools - N-able HP's global operations were directed from its headquarters in Palo Alto, California. Its US operations were directed from its facility in an unincorporated area of Harris County, Texas, near Houston. Its Latin America offices were in unincorporated Miami-Dade County, Florida. Its European offices were in Meyrin, close to Geneva, Switzerland, but it also had a research center in the Paris-Saclay cluster 20 km south of Paris, France. Its Asia-Pacific offices were in Singapore. HP had large operations in Leixlip, Ireland; Austin, Texas; Boise, Idaho; Corvallis, Oregon; Fort Collins, Colorado; Roseville, California; Saint Petersburg, Florida; San Diego, California; Tulsa, Oklahoma; Vancouver, Washington; Conway, Arkansas; and Plano, Texas. In the UK, HP was based at a large site in Bracknell, Berkshire, with offices in various UK locations, including a landmark office tower in London, 88 Wood Street. Its acquisition of 3Com expanded its employee base to Marlborough, Massachusetts, where HP Inc. has been manufacturing its convertible laptop series since late 2019. HP had a large workforce and numerous offices in Bucharest, Romania, and at Bangalore, India, to address their back end and IT operations. Mphasis, which is headquartered at Bangalore, also enabled HP to increase their footprint in the city, as it was a subsidiary of EDS which the company acquired.
HP produced lines of printers, scanners, digital cameras, calculators, personal digital assistants, servers, workstation computers, and computers for home and small-business use; many of the computers came from the 2002 merger with Compaq. HP as of 2001 promoted itself as supplying not just hardware and software, but also a full range of services to design, implement, and support IT infrastructure. HP's Imaging and Printing Group (IPG) was described by the company in 2005 as "the leading imaging and printing systems provider in the world for printer hardware, printing supplies and scanning devices, providing solutions across customer segments from individual consumers to small and medium businesses to large enterprises".
Products and technology associated with IPG included the Inkjet and LaserJet printers, the Officejet all-in-one multifunction printer/scanner/faxes, Indigo Digital Press, the HP Photosmart digital cameras and photo printers, and the photo sharing service Snapfish. On December 23, 2008, HP released iPrint Photo for the iPhone. HP's Personal Systems Group (PSG) was claimed by HP in 2005 to be "one of the leading vendors of personal computers ("PCs") in the world based on unit volume shipped and annual revenue". PSG dealt with business and consumer PCs and accessories (such as e.g., HP Pavilion, Compaq Presario, and VoodooPC), handheld computing (e.g., iPAQ Pocket PC), digital "connected" entertainment (e.g., HP MediaSmart TVs, HP MediaSmart Servers, HP MediaVaults, DVD+RW drives) and Apple's iPod (until November 2005). HP Enterprise Business (EB) incorporated HP Technology Services and Enterprise Services (an amalgamation of the former EDS, and what was known as HP Services). HP Enterprise Security Services oversaw professional services such as network security, information security and information assurance/compliancy, HP Software Division, and Enterprise Servers, Storage and Networking Group (ESSN). The Enterprise Servers, Storage and Networking Group (ESSN) oversaw "back end" products like storage and servers. HP Networking (former ProCurve) was responsible for the NW family of products.
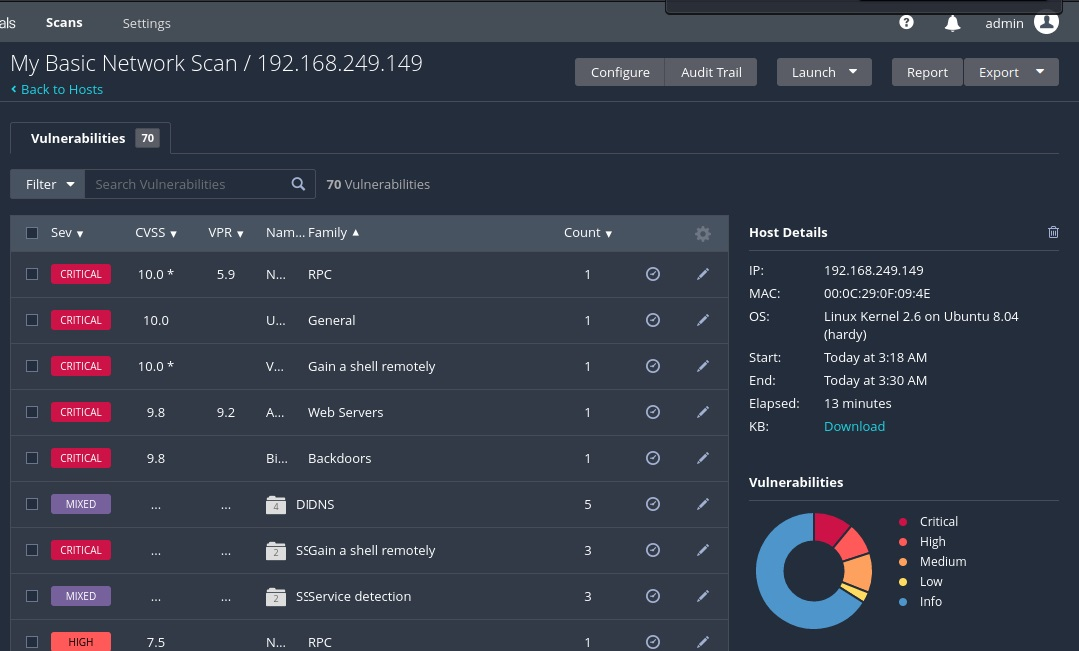
Figure 3: Nessus Vulnerability Scanner Software – PHDBKI HP Software Division was the company's enterprise software unit, which produced and marketed its brand of enterprise-management software, HP OpenView. From September 2005 HP purchased several software companies as part of a publicized, deliberate strategy to augment its software offerings for large business customers. HP Software sold several categories of software, which included business service management software, application lifecycle management software, mobile apps, and enterprise security software (the latter of which included, ArcSight, Fortify Software, Atalla and TippingPoint). HP Software also provided software as a service (SaaS), cloud computing solutions, and software services, including consulting, education, professional services, and support. HP's Office of Strategy and Technology had four main functions: To steer the company's $3.6 billion research and development investment; foster the development of the company's global technical community; lead the company's strategy and corporate development efforts, and perform worldwide corporate marketing activities. HP Labs served as the research arm of HP. HP also offered managed services by which it provides complete IT-support solutions for other companies and organizations. One example of this was offering "Professional Support" and desktop "Premier Support" for Microsoft in the EMEA marketplace. This was done from the Leixlip campus near Dublin, Sofia and Israel. Support was offered for Microsoft Windows, Exchange, SharePoint, and some office applications.
HP had many sponsorships, such as Mission: SPACE in Epcot at the Walt Disney World Resort. From 1995 to 1999, and again from 2013 to 2014, HP had been the shirt sponsor of Premier League club Tottenham Hotspur F.C. From 1997 to 1999 it sponsored Australian Football League club North Melbourne Football Club. It also sponsored the Jordan Grand Prix from 1999 to 2001, Stewart Grand Prix in 1999, Jaguar Racing from 2000 to 2002, BMW Williams Formula 1 team from 2002 to 2005 (which was formerly sponsored by Compaq prior to the merger from 2000 to 2001), and Renault F1 from 2010 to 2011.
In 2024, HP became the title sponsor of Scuderia Ferrari. HP also had the naming rights arrangement for the HP Pavilion at San Jose, which was previously held by Compaq prior to the merger as the Compaq Center at San Jose, those naming rights were acquired by SAP AG and consequently renamed SAP Center at San Jose. HP also maintained a number of corporate sponsorships in the business sector, including sponsorships of trade organisations including Fespa (print trade exhibitions), and O'Reilly Media's Velocity (web development) conference.
On September 5, 2006, Shawn Cabalfin and David O'Neil of Newsweek wrote that HP's general counsel, at the behest of chairwoman Patricia Dunn, contracted a team of independent security experts to investigate board members and several journalists to identify the source of an information leak. In turn, those security experts recruited private investigators who used pretexting, which involved investigators impersonating HP board members and nine journalists (including reporters for CNET, The New York Times and The Wall Street Journal) in order to obtain their phone records. The information leaked related to HP's long-term strategy and was published as part of a CNET article in January 2006. Most HP employees accused of criminal acts have since been acquitted.
In November 2012, HP recorded a write-down of around $8.8 billion related to its acquisition a year earlier of the UK-based Autonomy Corporation PLC. At that time, HP had fired its previous CEO for expenses irregularities a year before, and appointed Apotheker. HP was seen as problematic by the market. Autonomy was acquired by HP in October 2011. HP paid $10.3 billion for 87.3% of the shares, valuing Autonomy at around $11.7 billion (£7.4 billion) overall, a premium of 79% over market price. The deal was widely criticized as "absurdly high", a "botched strategy shift" and a "chaotic" attempt to reposition HP and enhance earnings, and was objected to by HP's own CFO. Within a year, Apotheker was fired, major culture clashes became apparent, and HP wrote off $8.8 billion of Autonomy's value. The Serious Fraud Office (SFO) and the SEC joined the FBI in investigating the potential anomalies. HP incurred damage with its stock falling to its lowest in decades. Three lawsuits were brought by shareholders against HP for the fall in value of HP shares. In August 2014, a United States district court judge threw out a proposed settlement, which Autonomy's previous management had argued would be collusive and intended to divert scrutiny of HP's own responsibility and knowledge. It essentially engaged the plaintiff's attorneys from the existing cases and redirected them against the previous Autonomy vendors and management for a fee of up to $48 million, with plaintiffs agreeing to end any claims against HP's management and similarly redirect those claims against the previous Autonomy vendors and management. In January 2015 the SFO closed its investigation as the likelihood of a successful prosecution was low. The dispute continued in the US, and is being investigated by the UK and Ireland Financial Reporting Council. On June 9, 2015, HP agreed to pay $100 million to investors who bought HP shares between August 19, 2011 and November 20, 2012, to settle the lawsuits over the Autonomy purchase. Another term of the shareholder settlement was to sue Autonomy management, which occurred in London in 2019. HP "failed to produce a smoking gun for the fraud it alleges", and its accountants admitted that they "never formally prepared anything to attribute the irregularities to the amount of the fraud". In June 2024, a jury acquitted Autonomy founder Mike Lynch and co-defendant Steve Chamberlain. Steve Chamberlain was hit by a car while jogging on August 17, 2024. Mike Lynch, along with his 18 year old daughter, drowned after their yacht sank on August 20, 2024 (the accident killed a total of seven people). In July 2025, a judge at London's High Court ruled that HP is owed more than 700 million pounds ($944 million), in respect of the acquisition of Autonomy.
ArcSight Fortify HP calculators HP Linux Imaging and Printing HP Software & Solutions List of acquisitions by Hewlett-Packard List of computer system manufacturers List of Hewlett-Packard products TippingPoint Hewlett-Packard Credit Union Hewlett-Packard The Museum of HP Calculators HP History Links Protect 724 Community Business data for Hewlett-Packard Company: Web Application Vulnerability Scanners are automated tools that scan web applications, normally from the outside, to look for security vulnerabilities such as Cross-site scripting, SQL Injection, Command Injection, Path Traversal and insecure server configuration. This category of tools is frequently referred to as Dynamic Application Security Testing (DAST) Tools. A large number of both commercial and open source tools of this type are available and all of these tools have their own strengths and weaknesses. If you are interested in the effectiveness of DAST tools, check out the OWASP Benchmark project, which is scientifically measuring the effectiveness of all types of vulnerability detection tools, including DAST.
Here we provide a list of vulnerability scanning tools currently available in the market. 2. System Architecture & Core Working Principles Note: Some tools listed below may support multiple testing types (SAST, DAST, and/or SCA). Tools are shown here if they include DAST capabilities.
Disclaimer : The tools listing in the table below are presented in alphabetical order. OWASP does not endorse any of the Vendors or Scanning Tools by listing them in the table below. OWASP is aware of the Web Application Vulnerability Scanner Evaluation Project (WAVSEP) . WAVSEP is completely unrelated to OWASP and we do not endorse its results, nor any of the DAST tools it evaluates. However, the results provided by WAVSEP may be helpful to someone interested in researching or selecting free and/or commercial DAST tools for their projects. This project has far more detail on DAST tools and their features than this OWASP DAST page.
You're midway through an MSSP web application engagement. The client says downloads are restricted, uploads are renamed, and the report generator only serves approved documents. Burp Suite's automated checks are quiet, so the endpoint is close to being marked clean. Then a legacy export route catches your attention. Its filename parameter behaves differently from the newer download function. A controlled traversal request confirms arbitrary file read, and a second test shows that the same path-handling logic can reach a writable location. The finding isn't just “an attacker can read /etc/passwd .” It's a potential route to configuration overwrite, persistence, credential exposure, or code execution, depending on the server-side sink.
That pattern appears repeatedly in penetration testing. Teams protect the obvious file browser while overlooking report generation, archive extraction, template loading, and upload workflows. This guide approaches the path traversal vulnerability as a filesystem-boundary failure, with special attention to write primitives, manual verification, MSSP evidence, and remediation that survives a client's QA review.
The application under test has a document-download feature. The development team has already added extension validation, blocked obvious ../ strings, and placed the service in a container. A scanner reports no confirmed path traversal, and the client's security contact points to the result as evidence that the file surface is covered. During feature mapping, you find a separate report endpoint. It accepts a document name, builds a temporary output path, and returns a generated file. The route isn't linked from the main interface, but it appears in older JavaScript and API traffic. A single request with a controlled relative path produces an error that reveals the application's base directory. That error is more useful than a large automated payload set because it tells you which resolver and sink you're dealing with.
The next probe should stay inside the engagement's rules of engagement. Use a harmless, approved file for read confirmation, and never write to a production path unless the client has explicitly authorized a safe marker-file test. The objective is to prove the boundary failure, not to create persistence or damage data. Practical rule: A read primitive establishes exposure. A verified write primitive changes the risk conversation.
This is why path traversal remains a meaningful penetration-testing target rather than a legacy checklist item. One independent analysis reported that path traversal represented roughly 5% of new CVEs each year since 2014 and about 5% of CISA's Known Exploited Vulnerabilities catalog , while a May 2024 Secure by Design alert from CISA and the FBI called out the issue directly. The OWASP directory traversal testing guidance reflects why testers still encounter this class at scale.
The scenario also explains why MSSP workflows need stronger verification. Automated tools can identify a suspicious parameter, but a client-ready finding needs a reproducible request, a safe impact demonstration, and a clear distinction between arbitrary read, arbitrary write, and code execution potential. A path traversal vulnerability occurs when external input helps construct a filesystem path, and the application fails to keep the resolved path inside the directory it intended to expose. CWE-22 describes this as improper limitation of a pathname to a restricted directory. Special path elements such as .. allow the operating system or runtime to resolve a path above the application's intended root.
The important word is resolved . The string the application receives may look harmless before normalization, yet resolve somewhere dangerous after URL decoding, separator handling, dot removal, or symbolic-link resolution. A secure test therefore follows the value through the entire processing chain, from HTTP parameter to filesystem API. Consider an endpoint served from a Linux container with an intended base directory of /var/www/uploads . A request such as: The filesystem resolves each .. component by moving to the parent directory. The resulting path can escape /var/www/uploads and reach /etc/passwd , assuming the process has permission to read it. The bug isn't that /etc/passwd is special. The bug is that an attacker controls a path component that should have remained confined.
CWE-22 is the right primary classification for this behavior. Related cases can overlap with file inclusion when the application executes or includes the resolved file, but a read-only download endpoint should not be overstated as remote code execution without evidence. OWASP places the access-control aspect of this problem within the broader A01:2021 Broken Access Control family.
The same boundary mistake can affect writes. An upload handler that stores user-controlled-name beneath an upload directory may overwrite a configuration file, place content where a template loader will process it, or create a link that redirects future operations. That's why a penetration tester should trace both read and write sinks before closing the finding. The scale is measurable. A 2024 to 2025 academic study analyzed 40,546 open-source projects , 41,870 unique files , and 33,436 samples judged safe by static analysis , yet identified 8,397 vulnerable samples and 1,756 exploitable path traversal instances . The researchers generated 1,600 valid local patches , submitted 433 pull requests , and recorded 63 fixed repositories , as documented by the OWASP Path Traversal community page .
A blacklist is not a path-security model. It's a guess about how an attacker will spell a path, and the guess often fails because different layers decode and normalize input at different times. Test encoding only when you have permission and a clear reason. A value may arrive URL-decoded at the web server, decoded again by a framework, and normalized later by a library. If validation occurs before the final decoding step, the validator may inspect a harmless representation while the filesystem receives traversal syntax.
3. Software Implementation, Frameworks & Protocols Absolute paths deserve a separate probe. A filter that rejects ../ but accepts /etc/passwd , a Windows drive path, or a file URI hasn't established confinement. Likewise, a startsWith() check can approve /var/www/uploads/../../etc/passwd if it tests the raw string rather than the canonical result.
Older null-byte techniques are mainly relevant to legacy stacks, but they still matter during assessments of unmaintained applications. More important in current engagements is the write path. Archive extraction, report generation, template storage, and upload renaming can all create files. If the application follows symlinks during extraction or writes through a link already present in the destination, a safe-looking directory can become a route to an unintended target.
Don't stop after a read response. Ask what the application does with the same input when it creates, extracts, copies, or overwrites a file. A useful modern case study is CVE-2022-23457 in OWASP ESAPI .
In versions before 2.3.0.0 , Validator.getValidDirectoryPath(String, String, File, boolean) could mishandle directory validation and incorrectly treat attacker-controlled input as a child of the specified parent directory. The issue was patched in ESAPI 2.3.0.0, as described in this CVE-2022-23457 vulnerability record .
The lesson isn't to memorize one Java method. It's to identify the gap between a validation decision and the final filesystem operation. A function can believe that a path belongs beneath a parent directory while the operating system resolves the path somewhere else. In a live engagement, that means you should record the supplied value, the application's interpreted path where available, and the final read or write effect.
Recent advisories show why write behavior deserves equal attention. The referenced vulnerability coverage includes node-tar linkpath sanitization issues, OliveTin arbitrary file writes, Tenable Agent arbitrary file writes, and .NET Core write-to-arbitrary-files behavior. The Aqua vulnerability advisory coverage frames the practical concern: a write primitive can become credential overwrite, persistence, or remote code execution when it reaches a consequential sink.
Use non-destructive markers for write tests. Don't upload a webshell, overwrite a live configuration file, or attempt command execution merely to make a report look more severe. If the sink can reach executable content, document that as an impact path and obtain explicit approval before any further validation. Reporting and document-processing components deserve special scrutiny. Vulnerabilities reported in Allure Report, Bold Reports, Cacti reporting functionality, and related components show that traversal can surface in report workflows, with impacts ranging from arbitrary file read to command execution, according to this CVE-2026-33166 vulnerability entry . A team that tests only download routes can miss the component with the most authority over the filesystem.
Start with feature mapping , not payload spraying. During reconnaissance, inventory every function that accepts or derives a filename, path, template, archive member, document identifier, or export destination. Downloads and image loaders are obvious, but report generators, static asset routes, upload handlers, backup restoration, API imports, and template previews often reveal the more valuable sinks.
Capture normal requests first. Note the parameter name, content type, authentication context, error behavior, and whether the response contains file content, a generated document, or only a job identifier. Trace asynchronous workflows as well, because the initial request may queue a file operation that executes later under a different service account. Look for values such as file , filename , path , template , document , resource , export , and custom names that behave like them. JavaScript bundles, API schemas, OpenAPI documents, and server error messages can expose routes that the user interface doesn't show.
For a read endpoint, begin with a harmless known file and then use a controlled traversal value. For a write endpoint, use a marker that has no operational meaning and target an approved test directory. Test the transformations that the observed stack suggests, including URL encoding, double decoding, separator changes, absolute-path handling, and canonicalization. The testing workflow is easier to standardize when it follows the application's behavior rather than a generic payload list. A documented penetration testing methodology for MSSP delivery can help teams keep reconnaissance, exploitation, verification, and reporting aligned.
Send a single confirmation request through Burp Repeater or an equivalent client. Compare status, response length, content type, error text, timing, and downstream job behavior against the baseline. Manual probing keeps the signal interpretable and reduces the chance that a scanner's concurrent requests alter the application state. Automation belongs at the handoff point. If the parameter produces an anomalous response but no confirmation, use targeted Intruder payloads or a purpose-built script to vary encoding and depth. Don't launch broad fuzzing before you know whether the sink reads, writes, extracts, or renders content.
For write testing, include filesystem evidence from the server or a controlled application response when the client can provide it. A successful HTTP status alone doesn't prove a write occurred. A short practical demonstration can reinforce the sequence, but keep it separate from the evidence record. Manual testing and automated scanning answer different questions. A scanner is good at breadth across common request patterns and textbook traversal strings. A senior tester is better at deciding whether an unusual response represents a real filesystem effect, especially when the application queues work, transforms filenames, or writes through an archive library.
Burp Suite Active Scan and similar tools can reliably identify straightforward file-read cases when the parameter is visible, the response contains a recognizable change, and the application uses conventional request and response flows. They're less dependable when traversal appears in an archive entry, a generated report name, a template-loader argument, or a symlink chain. Those cases often require understanding the server-side sink, not just comparing response bodies.
The most common operational mistake is treating a scanner's “not vulnerable” result as proof that no write primitive exists. Many tools focus on read disclosures because they can confirm them from the response. An archive extraction bug may return a normal success page while writing outside the intended directory, and a template loader may fail until a later request uses the created file.
False-positive control needs the same discipline. A useful false-positive reduction workflow should require evidence from the sink, not just a changed response. For MSSPs, the practical division is clear. Keep manual judgment for destructive-risk decisions, write confirmation, chained impact, and client-facing severity. Hand repetitive discovery and regression checks to automation once the endpoint and expected signal are understood.
4. Practical Deployment, Analysis & Case Studies ThreatExploit AI is one platform option for security providers that need automated reconnaissance, exploitation, verification, and reporting across web applications, APIs, networks, and cloud environments. Its role fits the candidate-generation and evidence-collection side of this workflow, while authorized human review remains important for confirming write effects and deciding how far exploitation should proceed.
The strongest fix removes direct path control from the user. Give the client an opaque document ID, resolve that ID to a server-side record, and keep the actual filesystem name outside the request. This approach avoids a large class of normalization and encoding mistakes because the caller never supplies a path component. The upload-then-serve anti-pattern needs special attention. Storing an uploaded file under a user-influenced name and later serving it from a predictable route creates two opportunities for abuse. The upload operation may write outside its root, and the serving operation may interpret attacker-controlled content in a sensitive context.
Refuse three tempting shortcuts. Extension blacklists don't control directories. A naive startsWith() check doesn't prove canonical containment. Container boundaries alone don't make an unsafe path construction routine safe, especially when the process can reach mounted secrets or shared volumes. A path traversal finding becomes useful to an audit team when the technical proof, business impact, and control mapping agree. Map the primary defect to CWE-22 , then use the surrounding implementation to identify related categories such as CWE-23, CWE-36, CWE-41, or CWE-59 for symlink behavior. OWASP mapping commonly points to A01:2021 Broken Access Control, while an inclusion or execution path may justify a separate classification rather than inflating the traversal finding.
Use the compliance documentation workflow to keep the technical finding connected to the client's audit artifacts. Severity should reflect the actual sink and environment, using CVSS 4.0 with environment modifiers where appropriate. A read-only disclosure of a public file is not equivalent to an authenticated write primitive that reaches a configuration directory. Triage the affected endpoint and determine whether the flaw is exposed externally, limited to authenticated users, or reachable through an internal service. Rotate credentials if the vulnerable path could expose secrets, review relevant access and application logs for suspicious filenames and traversal representations, preserve evidence, and schedule a retest with the development owner.
The remediation deliverable should name the vulnerable parameter, the filesystem sink, the containment failure, and the exact fix required. After the patch, test the original payload, encoded forms, absolute paths, symlink behavior, archive entries, and the write workflow. Close the finding only when the application rejects the normalized path and the evidence shows that the intended operation still works safely.
ThreatExploit AI offers MSSPs automated penetration testing workflows covering reconnaissance, exploitation, verification, and evidence-backed reporting across web applications and APIs. Visit ThreatExploit AI to evaluate how automated coverage can support path traversal discovery while your testers retain control of write-path verification and compliance-ready delivery. PwnTraverse is an advanced Path Traversal & Endpoint Vulnerability Scanner designed for security researchers, bug bounty hunters, and penetration testers . This tool automates the discovery of Path Traversal vulnerabilities and related CVEs, helping security professionals quickly assess and report security issues.
Automated Path Traversal Detection Scans and detects path traversal vulnerabilities using a variety of payloads ( ../ , double-encoding, bypass tricks). Deep Directory Enumeration Performs intelligent directory brute-forcing to uncover hidden files and endpoints. CVE & Endpoint Mapping Correlates discovered endpoints with known CVEs and potential LFI/RCE attack surfaces.
Clean & Actionable Reports Generates structured vulnerability reports for easy documentation and bug bounty submission. PwnTraverse, An advanced path traversal & endpoint vulnerability scanner for security researchers, bug bounty hunters, and penetration testers. Detects path traversal flaws, performs deep directory enumeration, and identifies CVE-related issues automatically.
PwnTraverse is an advanced Path Traversal & Endpoint Vulnerability Scanner designed for security researchers, bug bounty hunters, and penetration testers . This tool automates the discovery of Path Traversal vulnerabilities and related CVEs, helping security professionals quickly assess and report security issues. Automated Path Traversal Detection Scans and detects path traversal vulnerabilities using a variety of payloads ( ../ , double-encoding, bypass tricks).
Deep Directory Enumeration Performs intelligent directory brute-forcing to uncover hidden files and endpoints. CVE & Endpoint Mapping Correlates discovered endpoints with known CVEs and potential LFI/RCE attack surfaces. Clean & Actionable Reports Generates structured vulnerability reports for easy documentation and bug bounty submission. PwnTraverse, An advanced path traversal & endpoint vulnerability scanner for security researchers, bug bounty hunters, and penetration testers. Detects path traversal flaws, performs deep directory enumeration, and identifies CVE-related issues automatically.
5. Performance Evaluation & Extended Technical Observations Use the HTTP scan module ( -m http ) against a host ( -h 192.168.1.1 ) , using the GET method ( -M GET ): Directory Traversal Fuzzer. DotDotPwn is a very flexible intelligent fuzzer to discover traversal directory vulnerabilities in software such as HTTP/FTP/TFTP servers, Web platforms such as CMSs, ERPs, Blogs, etc.
Directory traversal vulnerabilities (also known as file path vulnerabilities) allow an attacker to read arbitrary files on the server that is running an application. This might include application code and data, credentials for back-end systems, and sensitive operating system files. You can follow this process using the File path traversal, traversal sequences stripped with superfluous URL-decode lab from our Web Security Academy.
If you're using Burp Suite Professional, you can use Burp Scanner to test for directory traversal vulnerabilities: You can alternatively use Burp Intruder to test for directory traversal vulnerabilities. This process also enables you to closely investigate any issues that Burp Scanner has identified: In the Payloads side panel, under Payload configuration , add a list of directory traversal fuzz strings: A web application at a financial services firm is serving a document preview feature. The URL looks like this: https://app.example.com/preview?file=reports/2026-q1.pdf .
A security engineer changes the parameter to file=../../../../etc/passwd and receives the contents of the server's password file in the HTTP response. Two thousand lines of user accounts, immediately readable.
Path traversal is one of the oldest vulnerability classes in web security, documented for over two decades — and still found in production applications today. This guide covers how to test for it systematically, the encoding and bypass techniques that evade naive defenses, and what good remediation actually looks like. Path traversal (also called directory traversal or Local File Inclusion — LFI ) occurs when an application uses user-controlled input to construct a file system path and fails to adequately restrict which files can be accessed. The ../ sequence moves up one directory level on Unix systems; ..\ does the same on Windows. Chaining multiple traversal sequences lets an attacker walk from the application's web root up to the filesystem root and then back down to any readable file.
The classic target is /etc/passwd on Linux — not because the file itself causes damage, but because reading it proves the vulnerability is exploitable and provides a list of usernames for further attacks. More impactful targets include: Remote File Inclusion (RFI) occurs when the file inclusion mechanism can be pointed at an external URL. In PHP applications, if allow_url_include is enabled and the application passes user input directly to include() or require() , an attacker can point the parameter to a remote server they control and have the application execute arbitrary PHP code.
RFI has largely disappeared from modern applications because PHP now disables allow_url_include by default and modern frameworks don't use raw include statements driven by user input. But legacy PHP applications, CMSes running on old PHP versions, and shared hosting environments still have it. Always test for RFI when you find a path traversal, because the remediation effort is the same and the exploitability difference is significant.
Path traversal vulnerabilities are most likely in parameters that reference files or resources by name: Start with the simplest payloads and work toward more complex ones only when the basics don't work. The initial test is just four traversal sequences followed by a known file: If any of these produces the /etc/passwd file content in the response, the vulnerability is confirmed. On Windows targets, try: The number of traversal sequences needed depends on how deep in the directory tree the application's base path is. Start with four; if that doesn't work, try eight. If the application is clearly rejecting the sequences, move to bypass techniques.
Many applications implement partial defenses — blocking ../ but not encoding variants, or stripping traversal sequences but not doing so recursively. Here are the bypass techniques to test systematically: Useful when the server decodes once on input validation and again during processing. The first decode produces a %2e sequence that passes the filter; the second decode produces the . character.
In languages where file paths are passed to underlying C libraries, a null byte terminates the string. The validation code sees .jpg and passes; the filesystem sees the path up to the null byte. This affects old PHP versions and some Python/Ruby implementations. Modern languages handle null bytes correctly, but it's worth testing on legacy systems. If the application strips ../ but doesn't do so recursively, ....// becomes ../ after one pass of stripping.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Hewlett-Packard • https://community.owasp.org/Vulnerability_Scanning_Tools • https://threatexploit.ai/en/resources/path-traversal-vulnerability • https://github.com/odaysec/PwnTraverse • https://github.com/marcostolosa/pwntraverse • https://www.kali.org/tools/dotdotpwn/ • https://portswigger.net/burp/documentation/desktop/testing-workflow/vulnerabilities/input-validation/directory-traversal • https://ironimo.online/blog/path-traversal-lfi-testing-guide
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Automated Directory Traversal Vulnerability Scanner Github.
[*] Initializing Burp Suite Spider & Vulnerability Engine for Automated Directory Traversal Vulnerability Scanner Github... [✓] Burp Extender / Macro Automation Hook Synced ──────────────────────────────────────────────────────────────────────── [11:42:01.104] AUDIT Crawled dynamic endpoints | Injecting input vectors [11:42:01.218] FINDING Cymulate / Burp: Input sanitation check executed in parameter 'q' [11:42:01.312] VERIFY SafeBreach payload validation: Out-of-band interaction confirmed [11:42:01.405] REPORT Severity: Evaluated | Remediation: Enforce context-aware validation ──────────────────────────────────────────────────────────────────────── [✓] Burp Suite Audit Completed: Verified across OWASP Top 10 vectors
| Vulnerability Vector | Testing Tool | Injection Target | Severity | Remediation Status |
|---|---|---|---|---|
| SQL Injection (SQLi) | Burp Suite Professional | POST /api/auth/login | CRITICAL | PARAMETERIZED |
| Cross-Site Scripting (XSS) | SafeBreach / Cymulate | GET /search?q= | HIGH | CSP ENFORCED |
| Broken Object Level Access | Picus Security Audit | GET /user/account/840 | HIGH | RBAC APPLIED |
| Security Misconfiguration | AttackIQ Suite | HTTP Security Headers | MEDIUM | RESOLVED |