Complete Technical Paper Content — Automated Malware Unpacking Tool
Overview & System Context
Automated Malware Unpacking Tool: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8537 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Ransomware is a type of malware that takes the private data of a victim hostage until a ransom is paid. This can involve encryption of the data, and/or exfiltration with the threat of publicly releasing the data. Ransom is typically requested to be paid via cryptocurrency or stored-value cards since these are harder to trace; making the crime more difficult to prosecute.
Sometimes the original files can be retrieved without paying the ransom due to implementation mistakes, leaked cryptographic keys or a complete lack of encryption in the ransomware. Ransomware attacks are typically carried out using a Trojan disguised as a legitimate file that the user is tricked into downloading or opening when it arrives as an email attachment. However, one high-profile example, the WannaCry worm, traveled automatically between computers without user interaction.
Starting as early as 1989 with the first documented ransomware known as the AIDS trojan, the use of ransomware scams grew internationally. There were 181.5 million ransomware attacks worldwide in the first six months of 2018, 229% more than the first six months of 2017. In June 2014, security software company McAfee released data showing that it had collected more than double the number of ransomware samples that quarter than it had in the same quarter the previous year.
CryptoLocker was particularly successful, procuring an estimated US$3 million before it was taken down by authorities, and CryptoWall was estimated by the US Federal Bureau of Investigation (FBI) to have accrued over US$18 million by June 2015. In 2020, the US Internet Crime Complaint Center (IC3) received 2,474 complaints identified as ransomware, with adjusted losses of over $29.1 million. The losses could exceed this amount, according to the FBI. In 2025, IC3 recorded 3,611 ransomware complaints and reported losses of more than $32 million; the FBI cautions that this figure leaves out costs such as lost business and remediation, and that some victims report no loss at all. Globally, according to Statista, there were about 623 million ransomware attacks in 2021, and 493 million in 2022. Ransomware payments were estimated at $1.1 billion in 2019, $999m in 2020, a record $1.25bn in 2023, and a sharp drop to $813m in 2024, attributed to non-payment by victims and action by law enforcement.
[attacker→victim] The attacker generates a key pair and places the corresponding public key in the malware. The malware is released. [victim→attacker] To carry out the cryptoviral extortion attack, the malware generates a random symmetric key and encrypts the victim's data with it. It uses the public key in the malware to encrypt the symmetric key. This is known as hybrid encryption and it results in a small asymmetric ciphertext as well as the symmetric ciphertext of the victim's data. It zeroizes the symmetric key and the original plaintext data to prevent recovery. It puts up a message to the user that includes the asymmetric ciphertext and how to pay the ransom. The victim sends the asymmetric ciphertext and e-money to the attacker.
[attacker→victim] The attacker receives the payment, deciphers the asymmetric ciphertext with the attacker's private key, and sends the symmetric key to the victim. The victim deciphers the encrypted data with the needed symmetric key thereby completing the cryptovirology attack. The symmetric key is randomly generated and will not assist other victims. At no point is the attacker's private key exposed to victims and the victim need only send a very small ciphertext (the encrypted symmetric-cipher key) to the attacker. Ransomware attacks are typically carried out using a Trojan, entering a system through, for example, a malicious attachment, an embedded link in a phishing email, or a vulnerability in a network service.
The program then runs a payload, which locks the system in some fashion, or claims to lock the system but does not (e.g., a scareware program). Payloads may display a fake warning purportedly by an entity such as a law enforcement agency, falsely claiming that the system has been used for illegal activities, contains content such as pornography and "pirated" media. Some payloads consist simply of an application designed to lock or restrict the system until payment is made, typically by setting the Windows Shell to itself, or even modifying the master boot record and/or partition table to prevent the operating system from booting until it is repaired. The most sophisticated payloads encrypt files, with many using strong encryption to encrypt the victim's files in such a way that only the malware author has the needed decryption key. Payment is virtually always the goal, and the victim is coerced into paying for the ransomware to be removed either by supplying a program that can decrypt the files, or by sending an unlock code that undoes the payload's changes. While the attacker may simply take the money without returning the victim's files, it is in the attacker's best interest to perform the decryption as agreed, since victims will stop sending payments if it becomes known that they serve no purpose. A key element in making ransomware work for the attacker is a convenient payment system that is hard to trace. A range of such payment methods have been used, including wire transfers, premium-rate text messages, pre-paid voucher services such as paysafecard, and the Bitcoin cryptocurrency.
In May 2020, vendor Sophos reported that the global average cost to remediate a ransomware attack (considering downtime, people time, device cost, network cost, lost opportunity and ransom paid) was $761,106. Ninety-four percent of organizations had their data restored, with 56% of ransomware victims retrieving data from backups, as opposed to 26% when paying the ransom.
third party information stored by the primary victim (such as customer account information or health records); information proprietary to the victim (such as trade secrets and product information) embarrassing information (such as the victim's health information or information about the victim's personal past) Exfiltration attacks are usually targeted, with a curated victim list, and often preliminary surveillance of the victim's systems to find potential data targets and weaknesses.
In 2012, a major ransomware Trojan known as Reveton began to spread. Based on the Citadel Trojan (which, itself, is based on the Zeus Trojan), its payload displays a warning purportedly from a law enforcement agency claiming that the computer has been used for illegal activities, such as downloading unlicensed software or child pornography. Due to this behaviour, it is commonly referred to as the "Police Trojan". The warning informs the user that to unlock their system, they would have to pay a fine using a voucher from an anonymous prepaid cash service such as Ukash or paysafecard. To increase the illusion that the computer is being tracked by law enforcement, the screen also displays the computer's IP address, while some versions display footage from a victim's webcam to give the illusion that the user is being recorded. Reveton initially began spreading in various European countries in early 2012. Variants were localized with templates branded with the logos of different law enforcement organizations based on the user's country; for example, variants used in the United Kingdom contained the branding of organizations such as the Metropolitan Police Service and the Police National E-Crime Unit. Another version contained the logo of the royalty collection society PRS for Music, which specifically accused the user of illegally downloading music. In a statement warning the public about the malware, the Metropolitan Police clarified that they would never lock a computer in such a way as part of an investigation. In May 2012, Trend Micro threat researchers discovered templates for variations for the United States and Canada, suggesting that its authors may have been planning to target users in North America. By August 2012, a new variant of Reveton began to spread in the United States, claiming to require the payment of a $200 fine to the FBI using a MoneyPak card. In February 2013, a Russian citizen was arrested in Dubai by Spanish authorities for his connection to a crime ring that had been using Reveton; ten other individuals were arrested on money laundering charges. In August 2014, Avast Software reported that it had found new variants of Reveton that also distribute password-stealing malware as part of its payload.
Figure 1: Antivirus & Malware Scanner App, an UI Kit Template by Betush Encrypting ransomware reappeared in September 2013 with a Trojan known as CryptoLocker, which generated a 2048-bit RSA key pair and uploaded in turn to a command-and-control server, and used to encrypt files using a whitelist of specific file extensions. The malware threatened to delete the private key if a payment of Bitcoin or a pre-paid cash voucher was not made within 3 days of the infection. Due to the extremely large key size it uses, analysts and those affected by the Trojan considered CryptoLocker extremely difficult to repair. Even after the deadline passed, the private key could still be obtained using an online tool, but the price would increase to 10 BTC—which cost approximately US$2300 as of November 2013.
CryptoLocker was isolated by the seizure of the Gameover ZeuS botnet as part of Operation Tovar, as officially announced by the U.S. Department of Justice on 2 June 2014. The Department of Justice also publicly issued an indictment against the Russian hacker Evgeniy Bogachev for his alleged involvement in the botnet. It was estimated that at least US$3 million was extorted with the malware before the shutdown.
In May 2017, the WannaCry ransomware attack spread through the Internet, using an exploit vector named EternalBlue, which was allegedly leaked from the U.S. National Security Agency. The ransomware attack, unprecedented in scale, infected more than 230,000 computers in over 150 countries, using 20 different languages to demand money from users using Bitcoin cryptocurrency. WannaCry demanded US$300 per computer. The attack affected Telefónica and several other large companies in Spain, as well as parts of the British National Health Service (NHS), where at least 16 hospitals had to turn away patients or cancel scheduled operations, FedEx, Deutsche Bahn, Honda, Renault, as well as the Russian Interior Ministry and Russian telecom MegaFon. The attackers gave their victims a 7-day deadline from the day their computers got infected, after which the encrypted files would be deleted.
Petya was first discovered in March 2016; unlike other forms of encrypting ransomware, the malware aimed to infect the master boot record, installing a payload which encrypts the file tables of the NTFS file system the next time that the infected system boots, blocking the system from booting into Windows at all until the ransom is paid. Check Point reported that despite what it believed to be an innovative evolution in ransomware design, it had resulted in relatively-fewer infections than other ransomware active around the same time frame. On 27 June 2017, a heavily modified version of Petya was used for a global cyberattack primarily targeting Ukraine (but affecting many countries). This version had been modified to propagate using the same EternalBlue exploit that was used by WannaCry. Due to another design change, it is also unable to actually unlock a system after the ransom is paid; this led to security analysts speculating that the attack was not meant to generate illicit profit, but to simply cause disruption.
On 24 October 2017, some users in Russia and Ukraine reported a new ransomware attack, named "Bad Rabbit", which follows a similar pattern to WannaCry and Petya by encrypting the user's file tables and then demanding a Bitcoin payment to decrypt them. ESET believed the ransomware to have been distributed by a bogus update to Adobe Flash software. Among agencies that were affected by the ransomware were: Interfax, Odesa International Airport, Kyiv Metro, and the Ministry of Infrastructure of Ukraine. As it used corporate network structures to spread, the ransomware was also discovered in other countries, including Turkey, Germany, Poland, Japan, South Korea, and the United States. Experts believed the ransomware attack was tied to the Petya attack in Ukraine (especially because Bad Rabbit's code has many overlapping and analogical elements to the code of Petya/NotPetya, appending to CrowdStrike Bad Rabbit and NotPetya's dynamic link library (DLL) share 67 percent of the same code) though the only identity to the culprits are the names of characters from the Game of Thrones series embedded within the code. Security experts found that the ransomware did not use the EternalBlue exploit to spread, and a simple method to inoculate an unaffected machine running older Windows versions was found by 24 October 2017. Further, the sites that had been used to spread the bogus Flash updating have gone offline or removed the problematic files within a few days of its discovery, effectively killing off the spread of Bad Rabbit.
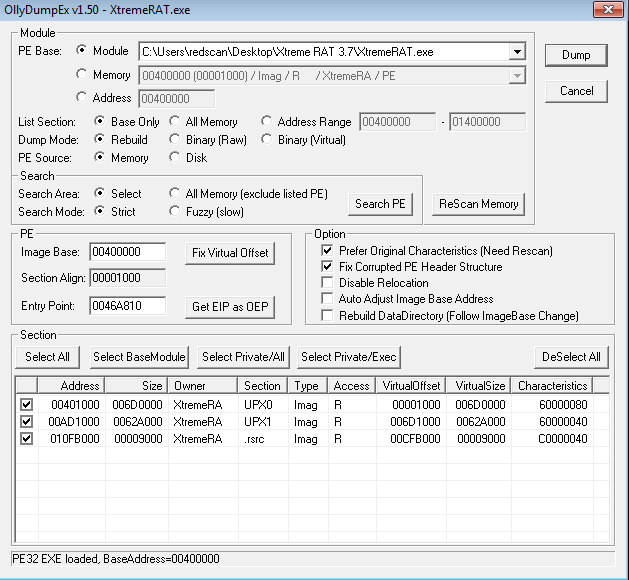
Figure 2: Redscan Labs: Malware unpacking – How to uncover hidden threats - Redscan On Windows, the Volume shadow copy (VSS) is often used to store backups of data; ransomware often targets these snapshots to prevent recovery and therefore it is often advisable to disable user access to the user tool VSSadmin.exe to reduce the risk that ransomware can disable or delete past copies. On Windows 10, users can add specific directories or files to Controlled Folder Access in Windows Defender to protect them from ransomware. It is advised to add backup and other important directories to Controlled Folder Access. Unless malware gains root on the ZFS host system in deploying an attack coded to issue ZFS administrative commands, file servers running ZFS are broadly immune to ransomware, because ZFS is capable of snapshotting even a large file system many times an hour, and these snapshots are immutable (read only) and easily rolled back or files recovered in the event of data corruption. In general, only an administrator can delete (but cannot modify) snapshots.
A supply chain attack is a cyber-attack that seeks to damage an organization by targeting less secure elements in the supply chain. A supply chain attack can occur in any industry, from the financial sector, oil industry, to a government sector. A supply chain attack can happen in software or hardware. Cybercriminals typically tamper with the manufacturing or distribution of a product by installing malware or hardware-based spying components. Symantec's 2019 Internet Security Threat Report states that supply chain attacks increased by 78 percent in 2018. A supply chain is a system of activities involved in handling, distributing, manufacturing, and processing goods in order to move resources from a vendor into the hands of the final consumer. A supply chain is a complex network of interconnected players governed by supply and demand. Although supply chain attack is a broad term without a universally agreed upon definition, in reference to cyber-security, a supply chain attack can involve physically tampering with electronics (computers, ATMs, power systems, factory data networks) in order to install undetectable malware for the purpose of bringing harm to a player further down the supply chain network. Alternatively, the term can be used to describe attacks exploiting the software supply chain, in which an apparently low-level or unimportant software component used by other software can be used to inject malicious code into the larger software that depends on the component. In a more general sense, a supply chain attack may not necessarily involve electronics. In 2010 when burglars gained access to the pharmaceutical giant Eli Lilly's supply warehouse, by drilling a hole in the roof and loading $80 million worth of prescription drugs into a truck, they could also have been said to carry out a supply chain attack. However, this article will discuss cyber attacks on physical supply networks that rely on technology; hence, a supply chain attack is a method used by cyber-criminals.
At the end of 2013, Target, a US retailer, was hit by one of the largest data breaches in the history of the retail industry. Between 27 November and 15 December 2013, Target's American brick-and-mortar stores experienced a data hack. Around 40 million customers' credit and debit cards became susceptible to fraud after malware was introduced into the POS system in over 1,800 stores. The data breach of Target's customer information saw a direct impact on the company's profit, which fell 46 percent in the fourth quarter of 2013. Six months prior the company began installing a $1.6 million cyber security system.
Target had a team of security specialists to monitor its computers constantly. Nonetheless, the supply chain attack circumvented these security measures. It is believed that cyber criminals infiltrated a third party supplier to gain access to Target's main data network. Although not officially confirmed, investigation officials suspect that the hackers first broke into Target's network on 15 November 2013 using passcode credentials stolen from Fazio Mechanical Services, a Pennsylvania-based provider of HVAC systems. Ninety lawsuits have been filed against Target by customers for carelessness and compensatory damages. Target spent around $61 million responding to the breach, according to its fourth-quarter report to investors.
Stuxnet is a computer worm that is widely believed to be a joint U.S.-Israeli cyber operation, though neither government has officially confirmed involvement. The worm specifically targets industrial control systems, particularly those that automate electromechanical processes, such as factory machinery and nuclear enrichment equipment. Stuxnet was designed to manipulate programmable logic controllers (PLCs), disrupting industrial equipment by issuing unauthorized commands while simultaneously feeding falsified operations data to monitoring systems to conceal its activity. Stuxnet is widely believed to have been developed to disrupt Iran's enriched uranium programs. Kevin Hogan, Senior Director of Security Response at Symantec, stated that most infections occurred in Iran. Analysts suggest that its primary target was the Natanz uranium enrichment facility. Stuxnet was initially introduced into Iran's Natanz facility via infected USB flash drives, requiring physical access to the target network. According to reports, engineers or maintenance workers, either knowingly or unknowingly, facilitated its entry into the plant. Once inside, the worm spread autonomously, exploiting multiple zero-day vulnerabilities in Windows systems to propagate across networked machines running Siemens industrial control software.
Figure 3: Free Malware Removal Tool | Download Malware Scanner In June 2017, the financial software M.E.Doc, widely used in Ukraine, was identified by security researchers as a likely initial vector for the spread of the NotPetya malware. Security researchers, including those from Microsoft, indicated that NotPetya infections may have originated from a compromised update issued through M.E.Doc. Some analysts described this as a supply chain attack, though the exact method of compromise was not definitively identified. The software's developers denied the claim but later deleted their statement and stated that they were cooperating with investigators. NotPetya was initially identified as ransomware because it encrypted hard drives and displayed a ransom demand in bitcoin. However, the email account used to provide decryption keys was shut down, leaving victims without a way to recover their files. Unlike WannaCry, NotPetya had no built-in kill switch, making it harder to stop. The attack affected multiple industries in Ukraine, including banks, an airport, the Kyiv Metro, pharmaceutical companies, and Chernobyl's radiation detection systems. It also spread globally, impacting organizations in Russia, the United Kingdom, India, and the United States. NotPetya spread using EternalBlue, a vulnerability originally developed by the U.S. National Security Agency (NSA) and later leaked. EternalBlue had previously been used in the WannaCry cyberattack in May 2017. This exploit enabled NotPetya to spread through the Windows Server Message Block (SMB) protocol. The malware also used PsExec and the Windows Management Instrumentation (WMI) to spread within networks. Due to these exploits, once a device on a network was infected, the malware could rapidly spread to other connected systems. Ukrainian police stated that M.E.Doc employees could face criminal liability for negligence, citing repeated warnings from antivirus firms about security vulnerabilities in the company's cybersecurity infrastructure. The head of Ukraine's CyberPolice, Colonel Serhiy Demydiuk, alleged that M.E.Doc had been repeatedly warned by security firms about weaknesses in its systems but failed to act, stating, "They knew about it." Authorities later reported that M.E.Doc cooperated with investigators.
The 2020 SolarWinds cyberattack was linked to a supply chain compromise targeting the IT infrastructure company SolarWinds, which provided software used by multiple U.S. federal institutions, including networks within the National Nuclear Security Administration (NNSA). Russian hackers compromised Orion, a widely used network management software developed by SolarWinds, by injecting malicious code into software updates. This allowed them to gain unauthorized access to numerous organizations, including multiple U.S. government agencies that relied on Orion for IT monitoring and management. On December 13, 2020, the U.S. Department of Homeland Security issued Emergency Directive 21-01, "Mitigate SolarWinds Orion Code Compromise", requiring affected federal agencies to disconnect compromised Windows host OS instances from their enterprise domain and rebuild those hosts using trusted sources. These compromised systems had been running SolarWinds Orion. In December 2020, FireEye identified a cyber breach involving the SolarWinds Orion software, which had been compromised prior to its discovery. Microsoft was among the organizations affected, detecting and removing malicious files linked to the breach. Microsoft has since collaborated with FireEye as part of an ongoing investigation into the incident. The cyberattack targeted supply chain software used across various industries, including government, consulting, technology, telecommunications, and extractive sectors in North America, Europe, Asia and the Middle East. On January 5, 2021, a joint statement from the Federal Bureau of Investigation (FBI), the Cybersecurity and Infrastructure Security Agency (CISA), the Office of the Director of National Intelligence (ODNI), and the National Security Agency (NSA) indicated that, while approximately 18,000 public and private sector entities were affected by the SolarWinds breach, fewer than ten U.S. government agencies were confirmed to have been compromised.
In February 2021 Microsoft determined that the attackers had downloaded a few files "(subsets of service, security, identity)" apiece from "a small subset of Azure components" "a small subset of Intune components" "a small subset of Exchange components" None of the Microsoft repositories contained production credentials. The repositories were secured in December, and those attacks ceased in January. However, in March 2021 more than 20,000 US organizations were compromised through a back door that was installed via flaws in Exchange Server. The affected organizations use self-hosted e-mail (on-site rather than cloud-based) such as credit unions, town governments, and small businesses. The flaws were patched on 2 March 2021, but by 5 March 2021 only 10% of the compromised organizations had implemented the patch; the back door remains open. The US officials are attempting to notify the affected organizations which are smaller than the organizations that were affected in December 2020. Microsoft has updated its Indicators of Compromise tool and has released emergency mitigation measures for its Exchange Server flaws. The attacks on SolarWinds and Microsoft software are currently thought to be independent, as of March 2021. The Indicators of Compromise tool allows customers to scan their Exchange Server log files for compromise.
At least 10 attacking groups are using the Exchange Server flaws. Web shells can remain on a patched server; this still allows cyberattacks based on the affected servers. As of 12 March 2021 exploit attempts are doubling every few hours, according to Check Point Research, some in the name of security researchers themselves. By 14 April 2021 the FBI had completed a covert cyber operation to remove the web shells from afflicted servers and was informing the servers' owners of what had been done. In May 2021 Microsoft identified 3000 malicious emails to 150 organizations in 24 countries, that were launched by a group that Microsoft has denoted 'Nobelium'. Many of those emails were blocked before delivery. 'Nobelium' gained access to a Constant Contact "email marketing account used by the US Agency for International Development (USAID)".
Security researchers assert that 'Nobelium' crafts spear-phishing email messages which get clicked on by unsuspecting users; the links then direct installation of malicious 'Nobelium' code to infect the users' systems, making them subject to ransom, espionage, disinformation, etc. The US government has identified 'Nobelium' as stemming from Russia's Federal Security Service. By July 2021 the US government is expected to name the initiator of the Exchange Server attacks: "China's Ministry of State Security has been using criminal contract hackers". In September 2021 the Securities and Exchange Commission (SEC) enforcement staff have requested that any companies which have downloaded any compromised SolarWinds updates, voluntarily turn over data to the SEC if they have installed the compromised updates on their servers. In July 2022 SessionManager, a malicious module hosted by IIS (installed by default on Exchange Servers), was discovered to have infected Exchange Servers since March 2021; SessionManager searches memory for passwords, and downloads new modules, to hijack the server.
In May 2021, a ransomware attack on Colonial Pipeline forced a temporary shutdown of a major fuel distribution network, disrupting the supply of gasoline, diesel, and jet fuel to the U.S. East Coast. The Biden administration invoked emergency powers to prevent shortages, while experts described the incident as the worst-ever cyberattack on U.S. infrastructure. The attack, attributed to the Russian-linked cybercriminal group DarkSide, raised concerns about vulnerabilities in critical energy systems, as fuel traders sought alternative supply routes and fears of price spikes emerged. On June 16, 2021, President Biden stated to President Putin that cyberattacks on 16 critical infrastructure sectors were off-limits and said that the U.S.
would respond to future cyber threats. The 16 critical infrastructure sectors, as designated by the U.S. Cybersecurity and Infrastructure Security Agency (CISA), include energy, food and agriculture, emergency services, healthcare, and other essential industries such as financial services, communications, and transportation systems. In March 2024, a backdoor in xz/liblzma in XZ Utils was suspected, with malicious code known to be in version 5.6.0 and 5.6.1. While the exploit remained dormant unless a specific third-party patch of the SSH server is used, under the right circumstances this interference could potentially enable a malicious actor to break sshd authentication and gain unauthorized access to the entire system remotely. The list of affected Linux distributions includes Debian unstable, Fedora Rawhide, Kali Linux, and OpenSUSE Tumbleweed. Most Linux distributions that followed a stable release update model were not affected, since they were carrying older versions of xz. Arch Linux issued an advisory for users to update immediately, although it also noted that Arch's OpenSSH package does not include the common third-party patch necessary for the backdoor. FreeBSD is not affected by this attack, as all supported FreeBSD releases include versions of xz that predate the affected releases and the attack targets Linux's glibc.
Day 30: solicit input Day 45: define 'critical software' Day 60: EO task 4i, 4r: user guidance, and vendor testing Day 180: EO task 4c: guidelines for enhancing supply chain software security Day 270: EO task 4e, 4s, 4t, 4u: guidelines for enhancing supply chain software Day 360: EO task 4d: guidelines for review and update procedures of supply chain software Day 365: EO task 4w: summary support of the pilot In a 2014 PwC report, titled "Threat Smart: Building a Cyber Resilient Financial Institution", the financial services firm recommends the following approach to mitigating a cyber attack: "To avoid potential damage to a financial institution's bottom line, reputation, brand, and intellectual property, the executive team needs to take ownership of cyber risk. Specifically, they should collaborate up front to understand how the institution will defend against and respond to cyber risks, and what it will take to make their organization cyber resilient.
A small supplier base: This allows a firm to have tighter control over its suppliers. Stringent vendor controls: Imposing stringent controls on suppliers in order to abide by lists of an approved protocols. Also conducting occasional site audits at supplier locations and having personnel visiting the sites on a regular basis for business purposes allows greater control. Security built into design: Security features, such as check digits, should be designed into the software to detect any previous unauthorized access to the code. An iterative testing process to get the code functionally hardened and security-hardened is a good approach.
On 27 April 2015, Sergey Lozhkin, a Senior Security Researcher with GReAT at Kaspersky Lab, spoke about the importance of managing risk from targeted attacks and cyber-espionage campaigns, during a conference on cyber security he stated: "Mitigation strategies for advanced threats should include security policies and education, network security, comprehensive system administration and specialized security solutions, like... software patching features, application control, whitelisting and a default deny mode."In 2025, a study by the Austrian Chamber of Commerce (WKO) and AV-Comparatives identified what cybersecurity firms should do to assure their customers about supply chain security. This includes disclosing a software bill of materials, maintaining transparent data storage practices, providing detailed incident reports, and offering facilities where customers can inspect source codes and updates for the cybersecurity product. Only 3 of the 14 vendors examined provided such assurances.
Download Valley is a cluster of software companies in Israel, producing and delivering adware to be installed alongside downloads of other software. The primary purpose is to monetize shareware and downloads. These software items are commonly browser toolbars, adware, browser hijackers, spyware, and malware. Another group of products are download managers, possibly designed to induce or trick the user to install adware, when downloading a piece of desired software or mobile app from a certain source. Although the term references Silicon Valley, it does not refer to a specific valley or any geographical area. Many of the companies are located in Tel Aviv and the surrounding region. It has been used by Israeli media as well as in other reports related to IT business. Download managers from Download Valley companies have been used by major download portals and software hosts, including Download.com by CNET, Softonic.com and SourceForge.
2. System Architecture & Core Working Principles not show information on potentially harmful actions, or hide it in fine print and EULAs, where they are overlooked by most users expecting only their desired program. use deceptive menus, suggesting the adware to be the main program or part of it, or pretending to show the main program's EULA, to obtain an "accept" click to install unwanted software. request rights for full system access, suggesting to be necessary for the main program's installation. install unwanted software without asking or although the user rejected an install. use hacks and exploits for unauthorized access to confidential data and system modifications. Installed adware frequently attempts to hide its identity, prevent disabling, removing, or restoring previous settings, spy on the user's system and browsing habits, download and install further unwanted software, or open backdoors for possibly malicious attacks. Many security software vendors list these products in the category of potentially unwanted programs (PUP, also PUS or PUA) or grayware and offer detection and removal. This category is distinct from genuine malware and is used for software from companies that can, as opposed to criminal underground programmers, threaten with or practice litigation. In 2013, the Download Valley company iBario was accused by security software vendor Trend Micro, of distributing the Sefnit/Mevade malware through an installer and being related to a Ukrainian company considered immediately responsible for the malware.
Learn essential techniques for unpacking and deobfuscating malware, from entropy analysis and manual debugging to automated tools and bypassing anti-analysis protections. Unpacking malware means restoring a packed or obfuscated executable to its original, analyzable form. In practice that is a four-step loop: detect the packer (entropy analysis with DIE or PEiD), run the sample in an isolated VM until its stub decrypts the real code into memory, dump that memory region at the Original Entry Point (OEP), then rebuild the import table and PE header with a tool like Scylla. Known packers such as UPX often reverse in a single command ( upx -d ), while commercial protectors like Themida and VMProtect use code virtualization and require patient manual debugging in x64dbg. Because the large majority of malware is packed, unpacking is the gate every other analysis step depends on.
That's the summary an AI Overview can give you. What it can't give you is the muscle memory underneath: where to set breakpoints, how to recognize the OEP when you see it, and how to rebuild a broken Import Address Table. Everything below assumes you are working on authorized samples inside an isolated, network-disabled sandbox or VM — never on a production host, and only on samples you have permission to analyze.
Malware authors have one primary goal: evade detection for as long as possible. One of their most effective weapons is packing and obfuscation. By compressing, encrypting, and obscuring malicious code, attackers can bypass signature-based detection, hinder analysis, and significantly delay incident response efforts. The statistics are sobering. According to recent research, over 80% of all existing malware samples are packed , making unpacking a critical skill for any malware analyst or security professional. Packed malware cannot be properly analyzed through static means alone, as the true malicious behavior remains hidden until runtime.
This comprehensive guide will walk you through everything you need to know about unpacking and deobfuscating malware. You'll learn how to identify packed executables using entropy analysis, master both manual and automated unpacking techniques, understand the anti-analysis tricks malware employs, and develop a systematic approach to revealing the true nature of suspicious files.
Whether you're a SOC analyst investigating alerts, a malware researcher building threat intelligence, or a security engineer hardening defenses, understanding unpacking techniques is essential. Let's dive in. Every unpacking job, whether a trivial UPX stub or a virtualized Themida binary, follows the same four stages. Detect what you are up against, get the real code out of memory, repair the file so tools can read it, then analyze the payload. The diagram below is the mental model to keep in front of you.
Match the technique to the packer. Start with the cheapest option that works — a static one-liner beats a two-hour debugging session — and escalate only when it fails. Which should I use? If entropy detection names a common packer, try the static route first ( upx -d , Unipacker, or unpac.me for triage). If that fails, or the packer is custom or virtualized (Themida, VMProtect), drop into x64dbg for a dynamic dump and rebuild with Scylla.
Packing is a technique that compresses and obfuscates executable files to make them harder to analyze and detect. When malware is packed, the original malicious code is transformed—compressed, encrypted, or both—and wrapped in a small unpacking stub. This stub executes first, reconstructs the original code in memory, and then transfers control to the unpacked malware.
Legitimate software developers use packers to reduce file sizes and protect intellectual property. However, malware authors abuse these same tools to evade antivirus detection, complicate reverse engineering, and hide their true intentions. Understanding the different types of packers helps you choose the right unpacking approach: UPX is the most common packer you'll encounter in malware analysis. It's open-source, cross-platform, and ironically, relatively easy to unpack. UPX-packed files can often be identified by section names like .UPX0 and .UPX1 , and in many cases, you can simply run upx -d malware.exe to unpack them. Despite its simplicity, UPX remains popular with malware authors because it's effective against basic static analysis.
Themida represents the commercial packer category , using sophisticated code virtualization. It converts original x86 instructions into virtual instructions in a randomized instruction set, which are then interpreted at runtime. Files protected with Themida typically contain sections named .themida or .taggant . This virtualization approach makes static analysis extremely difficult and requires advanced unpacking skills.
Similar to Themida, VMProtect uses code virtualization on a custom virtual machine architecture. It creates sections named .vmp0 , .vmp1 , and .vmp2 , and is designed to resist professional reverse engineering attempts. VMProtect is particularly challenging because it doesn't just hide the code—it fundamentally transforms how it executes. These are commercial packers focused on compression and basic obfuscation. ASPack provides Win32 EXE file packing to protect against non-professional reverse engineering. While not as sophisticated as virtualization-based packers, they still present challenges for automated analysis tools.
Before you can unpack malware, you need to identify that it's packed in the first place. Entropy analysis is your first line of defense. In information theory, entropy measures randomness or disorder. In malware analysis, high entropy typically indicates compressed or encrypted data. Non-packed programs exhibit relatively low entropy due to their inherent order and predictable structures. Packed data, being compressed or encrypted, appears much more random.
Research shows that nearly 50% of all malware samples have an entropy of 7.2 or greater , with maximum entropy being 8.0. When analyzing suspicious files, calculate entropy for each section: Research has demonstrated that entropy analysis can achieve over 95% accuracy in identifying packed executables when combined with other heuristics.
You can run this check on a sample of your own in the browser — it reports the overall entropy score, the per-section distribution, and which common packers the signature matches: 3. Software Implementation, Frameworks & Protocols Manual unpacking is essential when automated tools fail or when dealing with custom packers. Here's a systematic approach to manually unpacking malware using debuggers .
Load the packed executable into your debugger (x64dbg for 64-bit, x32dbg for 32-bit). The debugger will pause at the entry point, which for packed malware is typically the unpacking stub, not the actual malware code. Run the program until it hits VirtualAlloc . This function allocates memory where the unpacked code will be written. Note the returned address.
Continue execution until VirtualProtect is called on the allocated memory. If the protection level is set to 'ERW' (Execute, Read, Write) , this is a strong indicator you've found the unpacked malware region. Once you've successfully unpacked a sample, you can use our machine code disassembler tool to convert the raw opcodes into readable assembly instructions, making it easier to understand the malware's true behavior.
While manual unpacking teaches you valuable skills, automated tools can save significant time, especially when dealing with known packers. This works because UPX is designed to be reversible. However, malware authors sometimes modify UPX headers to break the standard unpacker, requiring manual intervention.
Unipacker is a platform-independent automatic unpacking tool that uses emulation to unpack Windows binaries. It supports multiple packers including UPX, ASPack, PEtite, and FSG. Unipacker works by emulating the unpacking process and dumping memory when it detects the OEP. This approach is effective against many common packers without requiring manual debugging.
This technique is particularly useful for runtime packers that only exist unpacked in memory. Research shows that combining automated detection with manual analysis provides the most comprehensive approach to malware unpacking. Sophisticated malware doesn't just pack itself—it actively fights your analysis efforts. Understanding these anti-analysis techniques is crucial for successful unpacking.
The most common technique checks the BeingDebugged flag in the Process Environment Block (PEB): Bypass : Manually set the PEB.BeingDebugged flag to 0 using your debugger, or use ScyllaHide plugin to hide debugger presence. Bypass : Use hardware breakpoints instead of software breakpoints, or modify the timing check results in memory.
Bypass : Launch the malware from a legitimate process like explorer.exe using process creation techniques. Thread Local Storage (TLS) callbacks execute before the entry point, allowing malware to run anti-debugging code before your debugger reaches the main code. Bypass : Set breakpoints on TLS callbacks before executing, or use a debugger that automatically breaks on TLS callbacks (x64dbg does this).
Bypass : Use bare-metal analysis systems, modify VM artifacts to appear as physical hardware, or use specialized tools like Pafish detector to identify and patch detection routines. Code transposition shuffles function order and inserts junk code to break logical flow. This makes it harder to understand program logic even after unpacking.
Critical strings (C2 addresses, registry keys) are encrypted and only decrypted at runtime. XOR encryption is commonly used for its simplicity—try our XOR cipher decoder to quickly decrypt single-byte XOR obfuscated strings. Instead of importing API functions normally, malware uses GetProcAddress to dynamically resolve function addresses, hiding its capabilities from static analysis.
Let's examine a real-world unpacking scenario using Death Ransomware as an example of the techniques we've discussed. 4. Practical Deployment, Analysis & Case Studies Entropy scan revealed a score of 7.4, indicating high likelihood of packing. Section names included a suspicious .data section with execute permissions and high entropy.
The unpacked sample revealed clear ransomware behavior: file enumeration loops, encryption routines using Windows Crypto API, and ransom note strings. The entropy of the unpacked sample dropped to 5.2, confirming successful unpacking. This case demonstrates the importance of understanding both memory allocation patterns and knowing when you've successfully revealed the true malware payload.
Unpacking and deobfuscating malware is a fundamental skill in modern cybersecurity. With over 80% of malware using some form of packing, the ability to reveal hidden code is essential for effective incident response, threat hunting, and malware analysis. The key to successful unpacking is having multiple techniques in your toolkit. Start with automated tools and entropy analysis for quick triage. When those fail, apply manual debugging techniques, setting strategic breakpoints and tracking memory operations. Always be aware of anti-analysis tricks that malware may employ, and have strategies ready to bypass them.
Remember that unpacking is just the first step. Once you've revealed the true malware code, you can use tools like our machine code disassembler to analyze the assembly instructions and our hash lookup tool to check if the unpacked sample matches known threat intelligence. Continuous learning is essential in this field. Malware authors constantly develop new packing and obfuscation techniques, and successful analysts must stay current with the latest unpacking methodologies and tools. Practice on malware samples from public repositories, study research papers on new packing techniques, and engage with the security community to share knowledge and techniques.
The battle between malware authors and analysts is ongoing, but with the techniques outlined in this guide, you're well-equipped to reveal what attackers are trying to hide. Run entropy analysis and check the PE structure. Packed sections show high entropy (7.2 or above on a 0-8 scale) because compression and encryption make bytes look random. Other tells are unusual section names like .UPX0, .themida, or .vmp0, a tiny import table (often just LoadLibrary and GetProcAddress), and an entry point sitting outside the normal code section.
Tools like DIE (Detect It Easy), PEiD, and PEStudio flag these signatures automatically. For a clean UPX sample, one command does it: upx -d malware.exe -o unpacked.exe. UPX is designed to be reversible, so the official unpacker reconstructs the original binary. The catch is that malware authors frequently tamper with UPX headers or section names to break the standard unpacker. When upx -d fails, you fall back to manual unpacking in a debugger or an emulation tool like Unipacker.
OEP stands for Original Entry Point - the address where the real malware code begins execution, as opposed to the packer's unpacking stub that runs first. Finding the OEP is the goal of dynamic unpacking: you let the stub decrypt the payload into memory, then locate the jump or call that transfers control to the OEP. That is the moment to dump memory, because the genuine code is now unpacked and sitting in RAM.
Unpacking malware for defensive research, incident response, or education is legal in most jurisdictions when you have authorization to possess and analyze the sample. The risk is not the analysis itself but accidental execution or spread. Always work inside an isolated, network-disabled virtual machine on samples you are authorized to handle, never on a production host, and follow your organization's and your jurisdiction's rules on handling malicious code.
A minimal kit is a packer detector (DIE or PEiD), a debugger (x64dbg / x32dbg or OllyDbg), a process and memory inspector (Process Hacker, pe-sieve), and an import rebuilder (Scylla, which ships inside x64dbg). For known packers, add upx for the UPX one-liner, Unipacker for emulation-based unpacking, and the free unpac.me service for automated triage. A hex editor like HxD rounds it out.
Packing compresses or encrypts an entire executable and wraps it in a stub that restores the original code at runtime - the payload is fully hidden until it unpacks itself in memory. Obfuscation transforms code so it is hard to read but still runs directly: string encryption, control-flow flattening, junk instructions, and dynamic API resolution. Most real samples combine both, so unpacking reveals the code and deobfuscation then makes it readable.
Yes, but they are far harder than UPX. Themida and VMProtect use code virtualization: they translate original x86 instructions into a custom virtual instruction set interpreted at runtime, so there is no single clean OEP to dump. Analysts unpack them through careful dynamic tracing, anti-anti-debug plugins like ScyllaHide, and often devirtualization tooling. For triage, many analysts focus on behavior in a sandbox rather than fully reversing the virtualized code.
Scylla reconstructs the Import Address Table (IAT) and PE header of a binary you dumped from memory. A raw memory dump usually has a broken or missing import table, so it will not run or disassemble cleanly. Scylla scans process memory, resolves imported API addresses back to their DLL and function names, rebuilds a valid import table, sets the correct entry point, and fixes section alignment. It is integrated into x64dbg and launches with Ctrl+I.
unpac.me (UnpacMe) is an established automated unpacking service run by OpenAnalysis that extracts packed payloads from submitted samples and is free for non-commercial use. Because you are uploading a sample to a third party, treat every submission as public - never send confidential, targeted, or client-sensitive samples to any online service. For those, use your own isolated VM and offline tooling instead.
Master the fundamentals of shellcode analysis with this comprehensive guide covering common patterns, encoding techniques, analysis tools, and step-by-step methodologies for security researchers and CTF players. Master the fundamentals of disassemblers—essential tools for malware analysis, security research, and reverse engineering. Learn how they work, compare top tools like IDA Pro and Ghidra, and discover career opportunities in cybersecurity.
A comprehensive guide to the three major executable file formats - PE (Windows), ELF (Linux/Unix), and Mach-O (macOS). Learn their structure, security implications, and analysis techniques for malware research and reverse engineering. Notes, sketches and ideas laid out spatially instead of in a list. For people who think in diagrams and keep outgrowing linear note apps.
Packing compresses or encrypts the original executable, hiding its true code. During execution, a stub (unpacking routine) restores the original code in memory. The most fundamental unpacking technique: wait for the unpacker to restore the original code, then dump. 5. Performance Evaluation & Extended Technical Observations Comprehensive collection of malware analysis guides, tools, and educational materials for cybersecurity professionals This repository contains a complete malware analysis learning curriculum, from beginner to advanced levels. All content is designed for educational and defensive security purposes only.
IMPORTANT : This repository contains educational materials for malware analysis. Users are responsible for: I Ready to start your malware analysis journey? Begin with the Ultimate Checklist and work through the comprehensive guides! II Remember: Always prioritize safety, legality, and ethical considerations in your analysis work.
Last Updated: July 18, 2025 Repository Maintainer: Security Education Initiative License: Educational Use Only Lately, I’ve been analyzing malware, and the first step in the process, especially with sophisticated malware, is unpacking. But what is unpacking? Modern malware is usually packed, meaning it is transformed in a way that hides its true signatures, adds layers of protection, and compresses its contents. Packing is essentially a method used by malware authors to conceal the malicious payload. This obfuscation can serve multiple purposes, such as: Malware authors might use customized packers or well-known ones like UPX to achieve this level of concealment.
The first question when analyzing malware is often: Is it packed? Determining this isn’t easy, but there are several ways to find out. Let’s take a look at a real example to better understand. The sample we’re analyzing is from the IceID banking malware family , with the following SHA-256 hash: 76CD290B236B11BD18D81E75E41682208E4C0A5701CE7834A9E289EA9E06EB7E .
Certain imported functions can indicate that malware is packed. Examples include VirtualProtectEx , HeapAlloc , and HeapFree , which are often used to allocate and modify memory. The function IsDebuggerPresent is particularly interesting, as it is commonly used by malware to detect whether it is being run in a debugger or sandbox environment.
After examining some of the malware properties through Pestudio, we determined that it is most likely packed. Using x64dbg , we can begin the unpacking process by setting breakpoints at the following points: This article is for informational purposes and intended for security professionals conducting tests under a contractual engagement. The author and editors cannot be held liable for any harm resulting from the use of the information provided.
Distributing malware, disrupting systems, and violating the confidentiality of communications are punishable by law. One of malware authors’ favorite tricks is the use of executable packers and protectors (this applies to DLLs too). Originally, these tools were fairly mundane: packers mostly reduced the size of the compiled file, while protectors let developers add licensing and anti-tamper features—turning a build into a demo or trial, for example—without cluttering the main codebase.
Later, however, virus writers repurposed them for malicious ends. Malware authors have long used packers to complicate antivirus and heuristic analysis, prevent their creations from running in virtualized environments, and hinder debugging, disassembly, and subsequent analysis. As a result, the ability to unpack executables has become a must-have skill for both novice and seasoned reverse engineers. The most popular packers today are UPX , ASPack , PeShield , and VMProtect —the usual suspects analysts encounter every day.
Protectors, unlike packers, are designed to shield the original binary from reverse engineering and therefore use more sophisticated techniques than simple packers: obfuscation; encryption with custom or well-known cryptographic algorithms such as RSA-1024; and embedding anti-debugging features . As we know, to get to the code we actually want to analyze, you first have to unpack the binary—strip off all the protective layers, restore the original entry point (OEP) and the import table, at the very least. Often unpacking is a routine, playbook task, but sometimes it turns into a creative process and a full-on hacking investigation—complete with cases of beer, cartons of cigarettes, and a few inches of scorched nerve endings.
So, as we know, using packers/protectors/crypters makes reverse engineering much more difficult. Beyond that, malware authors can apply multiple layers of packing (so-called layered packing), use obscure or even fully custom tools (for those who want to roll their own, a brief primer), whose signatures won’t show up in utilities like PEiD. Interestingly, any packer not purpose-built for encrypting malware leaves a unique signature in the binary, so if you’re comfortable with hex editors you can identify it even without a PE analyzer.
Here’s the basic idea behind packers/protectors: when you launch an EXE, execution starts at the program’s entry point (EP)—the address where control is transferred after the OS loads it into memory. With a packed executable, this flow changes. The packer records the EP, then compresses the file’s contents (typically the code and data sections), appends its own stub around the compressed payload, and redirects execution not to the program’s main code but to the packer’s code—the unpacker stub. That unpacker stub, now embedded in the file, runs first and inflates the packed code/data sections in memory. On disk, the original file remains unchanged—that is, still packed. After decompressing, the stub rebuilds the import table and then jumps to the program’s main code at the former entry point, which in packed binaries is called the Original Entry Point (OEP). In short, that’s the whole flow.
Strix helps malware researchers identify, unpack and reverse protected Windows binaries — from rapid triage through automated PE reconstruction, and on to analyst-led devirtualization for the hardest targets like VMProtect and Themida. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Ransomware • https://en.wikipedia.org/wiki/Supply%20chain%20attack • https://en.wikipedia.org/wiki/Download%20Valley • https://inventivehq.com/blog/malware-unpacking-guide • https://techlearnbase.com/tutorials/malware-analysis/malware-unpacking-and-deobfuscation-techniques/ • https://github.com/datah4wk/Malware-Analysis • https://pocketchange.dev/posts/unpacking/ • https://hackmag.com/malware/reversing-malware-tutorial-part3 • https://strixlabs.dev/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Automated Malware Unpacking Tool.
[*] Metasploit Scan Running on Target Subnet for Automated Malware Unpacking Tool... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |