Complete Technical Paper Content — Automated Memory Dump Forensics Tool Using Volatility
Overview & System Context
Automated Memory Dump Forensics Tool Using Volatility: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9167 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Flash memory is an electronic non-volatile computer memory storage medium that can be electrically erased and reprogrammed. The two main types of flash memory, NOR flash and NAND flash, are named for the NOR and NAND logic gates. Both of these use the same cell design, consisting of floating-gate MOSFETs. They differ at the circuit level, depending on whether the state of the bit line or word lines is pulled high or low; in NAND flash, the relationship between the bit line and the word lines resembles a NAND gate; in NOR flash, it resembles a NOR gate. Flash memory, a type of floating-gate memory, was invented by Fujio Masuoka at Toshiba in 1980 and is based on EEPROM technology. Toshiba began marketing flash memory in 1987. EPROMs had to be erased completely before they could be rewritten. NAND flash memory, however, may be erased, written, and read in blocks (or pages), which generally are much smaller than the entire device. NOR flash memory allows a single machine word to be written – to an erased location – or read independently. A flash memory device typically consists of one or more flash memory chips (each holding many flash memory cells), along with a separate flash memory controller chip. The NAND type is found mainly in memory cards, USB flash drives, solid-state drives (those produced since 2009), feature phones, smartphones, and similar products, for general storage and transfer of data. NAND or NOR flash memory is also often used to store configuration data in digital products, a task previously made possible by EEPROM or battery-powered static RAM. A key disadvantage of flash memory is that it can endure only a relatively small number of write cycles in a specific block. NOR flash is known for its direct random-access capabilities, making it apt for executing code directly. Its architecture allows for individual byte access, facilitating faster read speeds compared to NAND flash. NAND flash memory operates with a different architecture, relying on a serial access approach. This makes NAND suitable for high-density data storage, but less efficient for random-access tasks. NAND flash is often employed in scenarios where cost-effective, high-capacity storage is crucial, such as in USB drives, memory cards, and solid-state drives (SSDs). The primary differentiator lies in their use cases and internal structures. NOR flash is optimal for applications requiring quick access to individual bytes, as in embedded systems for program execution. NAND flash, on the other hand, shines in scenarios demanding cost-effective, high-capacity storage with sequential data access. Flash memory is used in computers, PDAs, digital audio players, digital cameras, mobile phones, synthesizers, video games, scientific instrumentation, industrial robotics, and medical electronics. Flash memory has a fast read access time but is not as fast as static RAM or ROM. In portable devices, it is preferred to use flash memory because of its mechanical shock resistance, since mechanical drives are more prone to mechanical damage. Because erase cycles are slow, the large block sizes used in flash memory erasing give it a significant speed advantage over non-flash EEPROM when writing large amounts of data. As of 2019, flash memory costs much less than byte-programmable EEPROM and has become the dominant memory type wherever a system required a significant amount of non-volatile solid-state storage. EEPROMs, however, are still used in applications that require only small amounts of storage, e.g. in SPD implementations on computer-memory modules. Flash memory packages can use die stacking with through-silicon vias and several dozen layers of 3D TLC NAND cells (per die) simultaneously to achieve capacities of up to 1 tebibyte per package using 16 stacked dies and an integrated flash controller as a separate die inside the package.
Charge trap flash (CTF) technology replaces the polysilicon floating gate, which is sandwiched between a blocking gate oxide above and a tunneling oxide below it, with an electrically insulating silicon nitride layer; the silicon nitride layer traps electrons. In theory, CTF is less prone to electron leakage, providing improved data retention. Because CTF replaces the polysilicon with an electrically insulating nitride, it allows for smaller cells and higher endurance (lower degradation or wear). However, electrons can become trapped and accumulate in the nitride, leading to degradation. Leakage is exacerbated at high temperatures since electrons become more excited with increasing temperatures. CTF technology, however, still uses a tunneling oxide and blocking layer, which are the weak points of the technology, since they can still be damaged in the usual ways (the tunnel oxide can be degraded due to extremely high electric fields and the blocking layer due to Anode Hot Hole Injection (AHHI). Degradation or wear of the oxides is the reason why flash memory has limited endurance. Data retention goes down (the potential for data loss increases) with increasing degradation, since the oxides lose their electrically-insulating characteristics as they degrade. The oxides must insulate against electrons to prevent them from leaking, which would cause data loss. In 1991, NEC researchers, including N. Kodama, K. Oyama and Hiroki Shirai, described a type of flash memory with a charge-trap method. In 1998, Boaz Eitan of Saifun Semiconductors (later acquired by Spansion) patented a flash memory technology named NROM that took advantage of a charge trapping layer to replace the conventional floating gate used in conventional flash memory designs. In 2000, an Advanced Micro Devices (AMD) research team led by Richard M.
Fastow, Egyptian engineer Khaled Z. Ahmed and Jordanian engineer Sameer Haddad (who later joined Spansion) demonstrated a charge-trapping mechanism for NOR flash memory cells. CTF was later commercialized by AMD and Fujitsu in 2002. 3D V-NAND (vertical NAND) technology stacks NAND flash memory cells vertically within a chip using 3D charge trap flash (CTP) technology. 3D V-NAND technology was first announced by Toshiba in 2007, and the first device, with 24 layers, was commercialized by Samsung Electronics in 2013.
Flash memory stores information in an array of memory cells made from floating-gate transistors. In single-level cell (SLC) devices, each cell stores only one bit of information. Multi-level cell (MLC) devices, including triple-level cell (TLC) devices, can store more than one bit per cell. The floating gate may be conductive (typically polysilicon in most kinds of flash memory) or non-conductive (as in SONOS flash memory).
In flash memory, each memory cell resembles a standard metal–oxide–semiconductor field-effect transistor (MOSFET) except that the transistor has two gates instead of one. The cells can be seen as an electrical switch in which current flows between two terminals (source and drain) and is controlled by a floating gate (FG) and a control gate (CG). The CG is similar to the gate in other MOS transistors, but below this is the FG, which is insulated all around by an oxide layer. The FG is interposed between the CG and the MOSFET channel. Because the FG is electrically isolated by its insulating layer, electrons placed on it are trapped. When the FG is charged with electrons, this charge screens the electric field from the CG, thus increasing the threshold voltage (VT) of the cell. This means that the VT of the cell can be changed between the uncharged FG threshold voltage (VT1) and the higher charged FG threshold voltage (VT2) by changing the FG charge. In order to read a value from the cell, an intermediate voltage (VI) between VT1 and VT2 is applied to the CG. If the channel conducts at VI, the FG must be uncharged (if it were charged, there would not be conduction because VI is less than VT2). If the channel does not conduct at the VI, it indicates that the FG is charged. The binary value of the cell is sensed by determining whether there is current flowing through the transistor when VI is asserted on the CG. In a multi-level cell device, which stores more than one bit per cell, the amount of current flow is sensed (rather than simply its presence or absence), in order to determine more precisely the level of charge on the FG. Floating gate MOSFETs are so named because there is an electrically insulating tunnel oxide layer between the floating gate and the silicon, so the gate "floats" above the silicon. The oxide keeps the electrons confined to the floating gate. Degradation or wear (and the limited endurance of floating gate Flash memory) occurs due to the extremely high electric field (10 million volts per centimeter) experienced by the oxide. Such high voltage densities can break atomic bonds over time in the relatively thin oxide, gradually degrading its electrically insulating properties and allowing electrons to be trapped in and pass through freely (leak) from the floating gate into the oxide, increasing the likelihood of data loss since the electrons (the quantity of which is used to represent different charge levels, each assigned to a different combination of bits in MLC Flash) are normally in the floating gate. This is why data retention goes down and the risk of data loss increases with increasing degradation. The silicon oxide in a cell degrades with every erase operation. The degradation increases the amount of negative charge in the cell over time due to trapped electrons in the oxide and negates some of the control gate voltage. Over time, this also makes erasing the cell slower; to maintain the performance and reliability of the NAND chip, the cell must be retired from use. Endurance also decreases with the number of bits in a cell. With more bits in a cell, the number of possible states (each represented by a different voltage level) in a cell increases and is more sensitive to the voltages used for programming. Voltages may be adjusted to compensate for degradation of the silicon oxide, and as the number of bits increases, the number of possible states also increases and thus the cell is less tolerant of adjustments to programming voltages, because there is less space between the voltage levels that define each state in a cell.
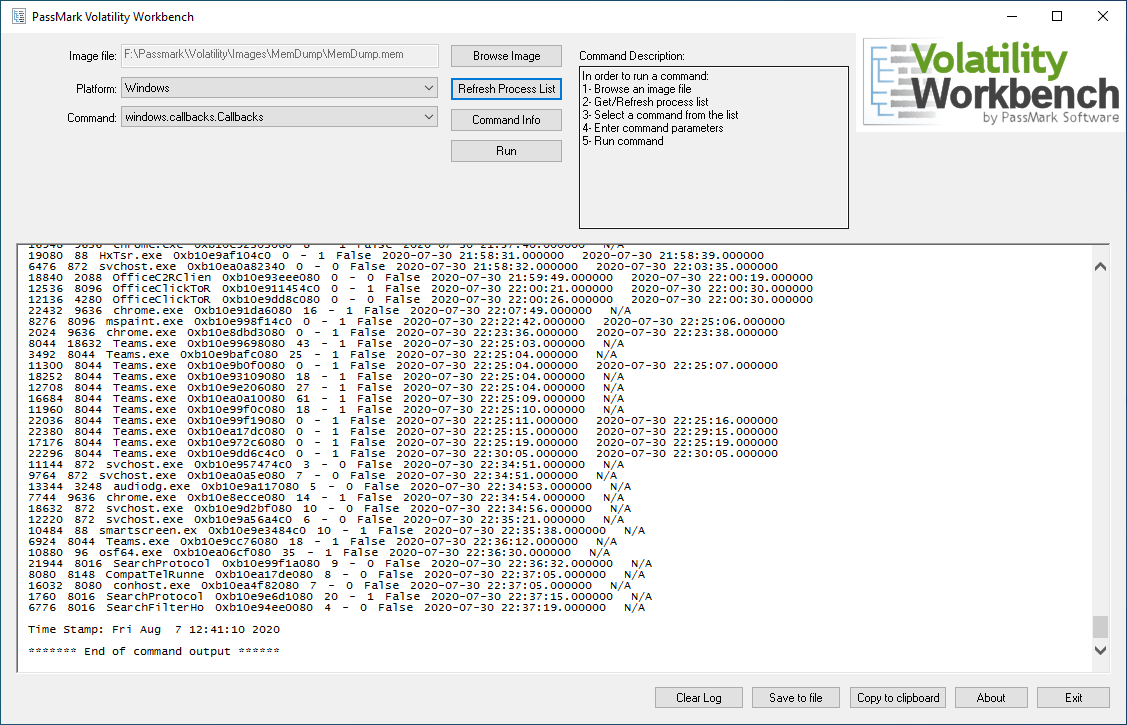
Figure 1: Volatility Workbench - A GUI for Volatility memory forensics The process of moving electrons from the control gate and into the floating gate is called Fowler–Nordheim tunneling, and it fundamentally changes the characteristics of the cell by increasing the MOSFET's threshold voltage. This, in turn, changes the drain-source current that flows through the transistor for a given gate voltage, which is ultimately used to encode a binary value. The Fowler-Nordheim tunneling effect is reversible, so electrons can be added to or removed from the floating gate, processes traditionally known as writing and erasing.
In both NOR and NAND flash memories, the cells are arranged in a grid. We can think of the memory as consisting of "words" of a certain number of bits (or cells), with each word being confined to a particular column of the grid, and the bits being in different rows. All the bits of a particular word are linked by a wordline, a conductor connecting to the control gates of all the bits of that word. All the first bits of a certain number of adjacent words (columns) are linked by a bitline, as are all the second bits and so on. The bitlines connect to one of the terminals (source or drain) of the cells. By manipulating the voltages on the wordlines one can read a certain bit by measuring the voltage on the corresponding bitline. The way to do this depends on whether the memory chip is a NOR or a NAND flash. In NOR flash, each cell has one end connected directly to ground, and the other end connected directly to a bit line. This arrangement is called "NOR flash" because it acts like a NOR gate – if any of the word lines (connected to the CG of the cells) is brought high, the corresponding storage transistor may act to pull the output bit line low, but this depends on the charge in the floating gate. Since several words are connected by the bit line, the output does not depend on only two (the bitline staying high if neither the first NOR the second wordline is high) but on all (the bitline remaining high if NONE of the wordlines is high). So to read a bit of a certain word, all the wordlines except that of the desired word are put low. NOR flash continues to be the technology of choice for embedded applications requiring a discrete non-volatile memory device. The low read latencies characteristic of NOR devices allow for both direct code execution and data storage in a single memory product.
A single-level NOR flash cell in its default state is logically equivalent to a binary "1" value, because current will flow through the channel under application of an appropriate voltage to the control gate, so that the bitline voltage is pulled down. A NOR flash cell can be programmed, or set to a binary "0" value, by the following procedure: an elevated on-voltage (typically >5 V) is applied to the CG the channel is now turned on, so electrons can flow from the source to the drain (assuming an NMOS transistor) the source-drain current is sufficiently high to cause some high energy electrons to jump through the insulating layer onto the FG, via a process called hot-electron injection.
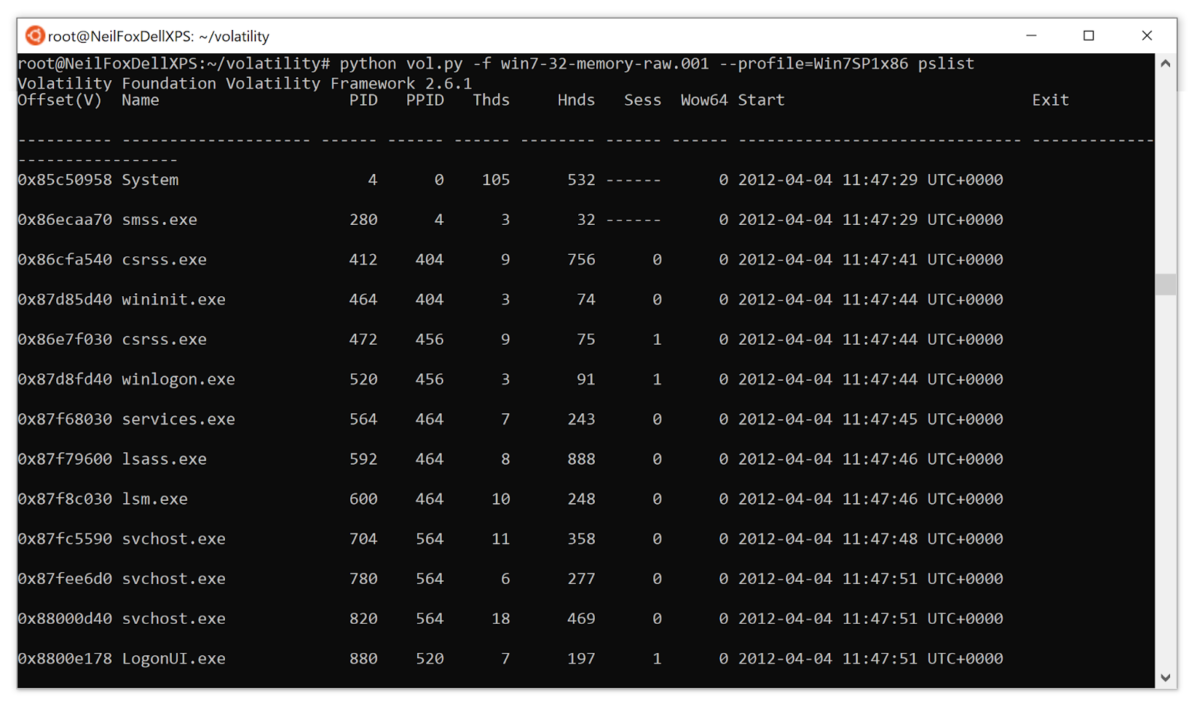
Figure 2: Memory Forensics for Incident Response Vertical NAND (V-NAND) or 3D NAND memory stacks memory cells vertically and uses a charge trap flash architecture. The vertical layers allow larger areal bit densities without requiring smaller individual cells. It is also sold under the trademark BiCS Flash, which is a trademark of Kioxia Corporation (formerly Toshiba Memory Corporation). 3D NAND was first announced by Toshiba in 2007. V-NAND was first commercially manufactured by Samsung Electronics in 2013.
The wafer cost of a 3D NAND is comparable with scaled down (32 nm or less) planar NAND flash. However, with planar NAND scaling stopping at 16 nm, the cost per bit reduction can continue by 3D NAND starting with 16 layers. However, due to the non-vertical sidewall of the hole etched through the layers; even a slight deviation leads to a minimum bit cost, i.e., minimum equivalent design rule (or maximum density), for a given number of layers; this minimum bit cost layer number decreases for smaller hole diameter.
2. System Architecture & Core Working Principles Data stored on flash cells is steadily lost due to electron detrapping. The rate of loss increases exponentially as the absolute temperature increases. For example: For a 45 nm NOR flash, at 1000 hours, the threshold voltage (Vt) loss at 25°C is about half that at 90°C.
Reading from NOR flash is similar to reading from random-access memory, provided the address and data bus are mapped correctly. Because of this, most microprocessors can use NOR flash memory as execute in place (XIP) memory, meaning that programs stored in NOR flash can be executed directly from the NOR flash without needing to be copied into RAM first. NOR flash may be programmed in a random-access manner similar to reading. Programming changes bits from a logical one to a zero. Bits that are already zero are left unchanged. Erasure must happen a block at a time, and resets all the bits in the erased block back to one. Typical block sizes are 64, 128, or 256 KiB. Bad block management is a relatively new feature in NOR chips. In older NOR devices not supporting bad block management, the software or device driver controlling the memory chip must correct for blocks that wear out, or the device will cease to work reliably. The specific commands used to lock, unlock, program, or erase NOR memories differ for each manufacturer. To avoid needing unique driver software for every device made, special Common Flash Memory Interface (CFI) commands allow the device to identify itself and its critical operating parameters. Besides its use as random-access ROM, NOR flash can also be used as a storage device, by taking advantage of random-access programming. Some devices offer read-while-write functionality so that code continues to execute even while a program or erase operation is occurring in the background. For sequential data writes, NOR flash chips typically have slow write speeds, compared with NAND flash. Typical NOR flash does not need an error correcting code.
32 pages of 512+16 bytes each for a block size (effective) of 16 KiB 64 pages of 2,048+64 bytes each for a block size of 128 KiB 64 pages of 4,096+128 bytes each for a block size of 256 KiB 128 pages of 4,096+128 bytes each for a block size of 512 KiB 2048 pages of 16,386+128 bytes each for a block size of 32768 KiB Modern NAND flash may have erase block size between 1 MiB to 128 MiB. While reading and programming is performed on a page basis, erasure can only be performed on a block basis. Since changing a cell from 0 to 1 requires erasing an entire block instead of just modifying some pages, making changes to the data of a block may in reality be a read-erase-write (REW) or read-modify-erase-write (RMEW) process, where the new data is actually moved to another block. NAND devices also require bad block management by the device driver software or by the flash memory controller chip. Some SD cards, for example, include controller circuitry to perform bad block management and wear leveling. When a logical block is accessed by high-level software, it is mapped to a physical block by the device driver or controller. A number of blocks on the flash chip may be set aside for storing mapping tables to deal with bad blocks, or the system may simply check each block at power-up to create a bad block map in RAM. The overall memory capacity gradually shrinks as more blocks are marked as bad. NAND relies on ECC to compensate for bits that may spontaneously fail during normal device operation. A typical ECC will correct a one-bit error in each 2048 bits (256 bytes) using 22 bits of ECC, or a one-bit error in each 4096 bits (512 bytes) using 24 bits of ECC. If the ECC cannot correct the error during read, it may still detect the error. When doing erase or program operations, the device can detect blocks that fail to program or erase and mark them bad. The data is then written to a different, good block, and the bad block map is updated.
Hamming codes are the most commonly used ECC for SLC NAND flash. Reed–Solomon codes and BCH codes (Bose–Chaudhuri–Hocquenghem codes) are commonly used ECC for MLC NAND flash. Some MLC NAND flash chips internally generate the appropriate BCH error correction codes. Most NAND devices are shipped from the factory with some bad blocks. These are typically marked according to a specified bad block marking strategy. By allowing some bad blocks, manufacturers achieve far higher yields than would be possible if all blocks had to be verified to be good. This significantly reduces NAND flash costs and only slightly decreases the storage capacity of the parts. When executing software from NAND memories, virtual memory strategies are often used: memory contents must first be paged or copied into memory-mapped RAM and executed there (leading to the common combination of NAND + RAM). A memory management unit (MMU) in the system is helpful, but this can also be accomplished with overlays. For this reason, some systems will use a combination of NOR and NAND memories, where a smaller NOR memory is used as software ROM and a larger NAND memory is partitioned with a file system for use as a non-volatile data storage area. NAND sacrifices the random-access and execute-in-place advantages of NOR. NAND is best suited to systems requiring high capacity data storage. It offers higher densities, larger capacities, and lower cost. It has faster erases, sequential writes, and sequential reads.
A standard physical interface (pinout) for NAND flash in TSOP-48, WSOP-48, LGA-52, and BGA-63 packages A standard command set for reading, writing, and erasing NAND flash chips A mechanism for self-identification (comparable to the serial presence detection feature of SDRAM memory modules) The ONFI group is supported by major NAND flash manufacturers, including Hynix, Intel, Micron Technology, and Numonyx, as well as by major manufacturers of devices incorporating NAND flash chips. Two major flash device manufacturers, Toshiba and Samsung, have chosen to use an NAND flash interface of their own design known as Toggle Mode (and now Toggle). This interface isn't pin-to-pin compatible with the ONFI specification. The result is that a product designed for one vendor's devices may not be able to use another vendor's devices.
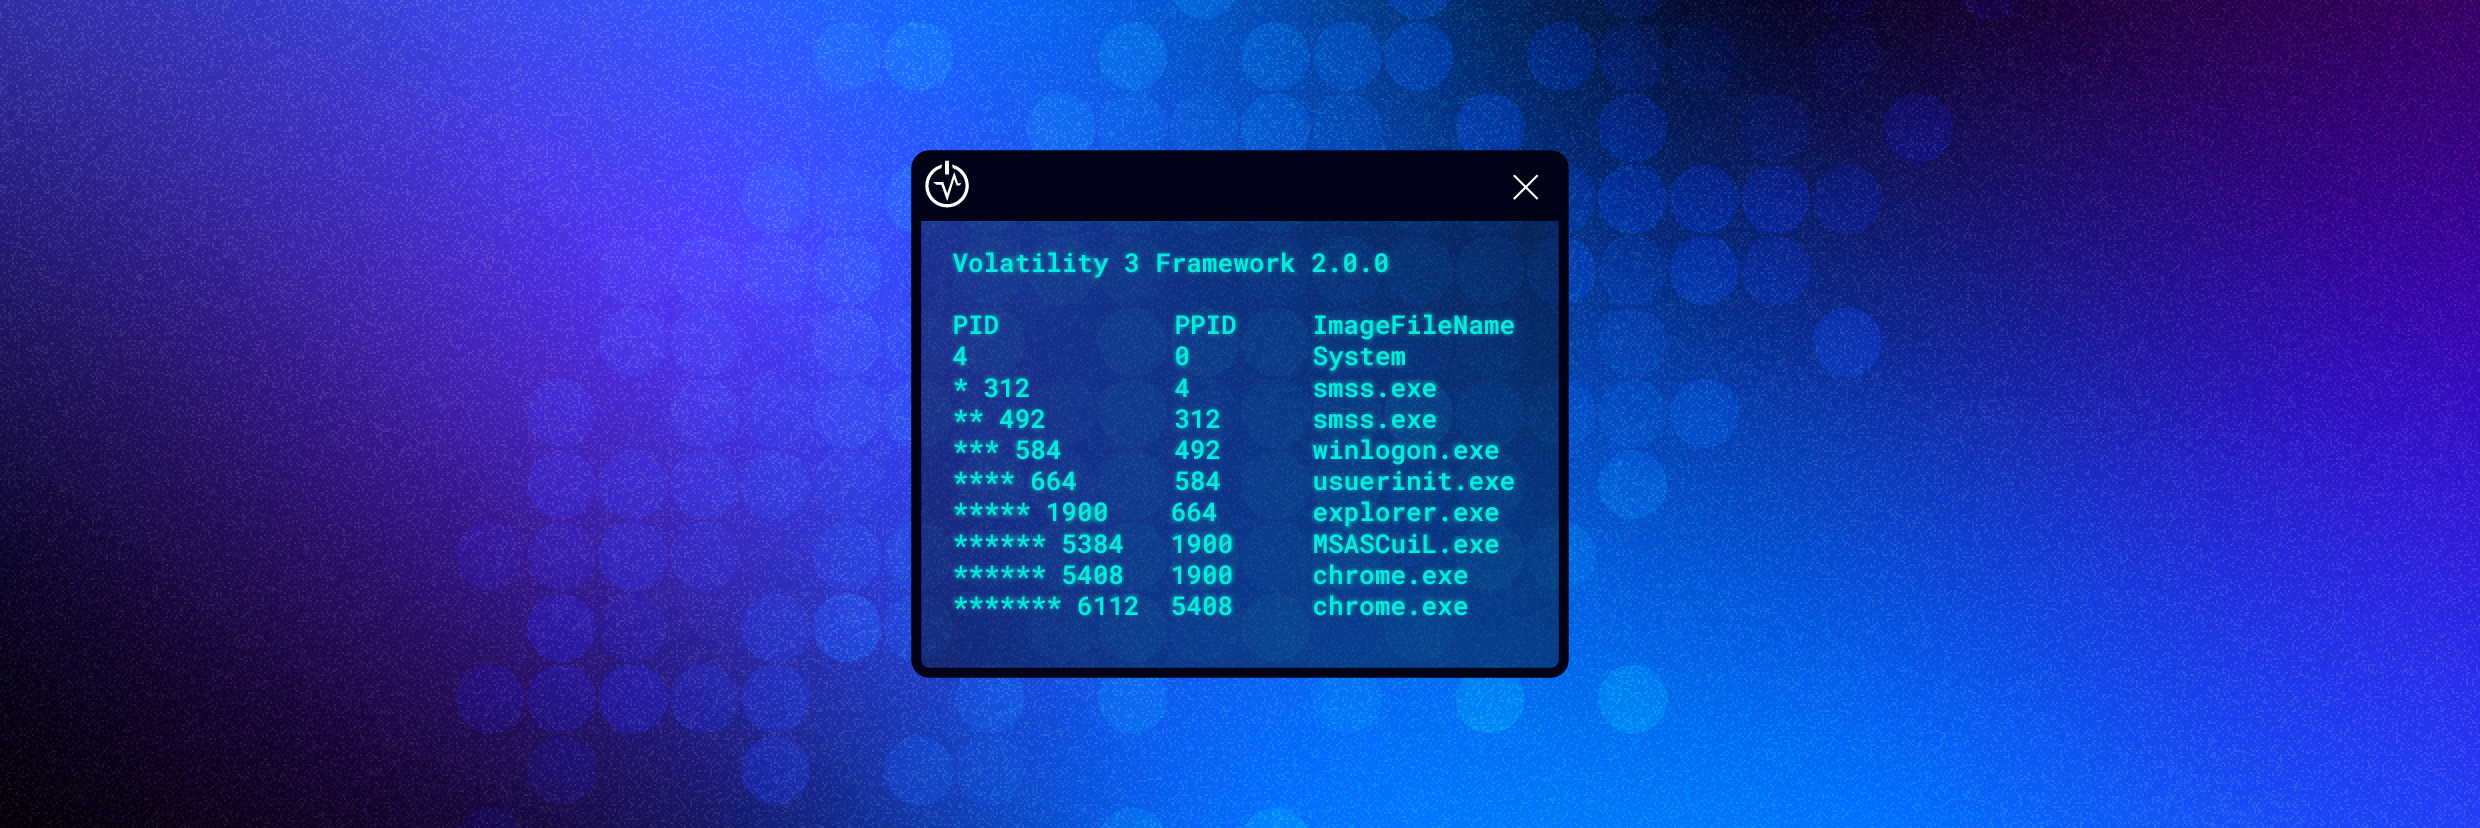
A group of vendors, including Intel, Dell, and Microsoft, formed a Non-Volatile Memory Host Controller Interface (NVMHCI) Working Group. The goal of the group is to provide standard software and hardware programming interfaces for nonvolatile memory subsystems, including the "flash cache" device connected to the PCI Express bus. Figure 3: How to Use Volatility for Memory Forensics and Analysis | Varonis The connections of the individual memory cells are different. The interface provided for reading and writing the memory is different; NOR allows random access as it can be either byte-addressable or word-addressable, with words being for example 32 bits long, while NAND allows only page access. NOR and NAND flash get their names from the structure of the interconnections between memory cells. In NOR flash, cells are connected in parallel to the bit lines, allowing cells to be read and programmed individually. The parallel connection of cells resembles the parallel connection of transistors in a CMOS NOR gate. In NAND flash, cells are connected in series, resembling a CMOS NAND gate. The series connections consume less space than parallel ones, reducing the cost of NAND flash. It does not, by itself, prevent NAND cells from being read and programmed individually. Each NOR flash cell is larger than a NAND flash cell – 10 F2 vs 4 F2 – even when using exactly the same semiconductor device fabrication and so each transistor, contact, etc. is exactly the same size – because NOR flash cells require a separate metal contact for each cell. Because of the series connection and removal of wordline contacts, a large grid of NAND flash memory cells will occupy perhaps only 60% of the area of equivalent NOR cells (assuming the same CMOS process resolution, for example, 130 nm, 90 nm, or 65 nm). NAND flash's designers realized that the area of a NAND chip, and thus the cost, could be further reduced by removing the external address and data bus circuitry. Instead, external devices could communicate with NAND flash via sequentially accessed command and data registers, which would internally retrieve and output the necessary data. This design choice made random access to NAND flash memory impossible, but the goal of NAND flash was to replace mechanical hard disks, not ROMs. The first GSM phones and many feature phones had NOR flash memory, on which processor instructions could be executed directly in an execute-in-place architecture, allowing for short boot times. With smartphones, NAND flash memory was adopted for its larger storage capacity and lower cost, but it causes longer boot times because instructions cannot be executed directly from it and must be copied to RAM before execution.
However, by applying certain algorithms and design paradigms, such as wear leveling, flash over-provisioning and high-quality flash memory (such as pSLC and eTLC), the endurance of a storage system can be tuned to serve specific requirements. To compute the longevity of the NAND flash, one must account for the size of the memory chip, the type of memory (e.g., SLC/MLC/TLC), and the usage pattern. Industrial NAND and server NAND are in demand due to their capacity, longer endurance and reliability in sensitive environments. As the number of bits per cell increases, the performance and life of NAND flash may degrade, increasing random read times to 100µs for TLC NAND, which is 4 times the time required in SLC NAND and twice the time required in MLC NAND for random reads.
Because of the particular characteristics of flash memory, it is best used with either a controller to perform wear leveling and error correction or specifically designed flash file systems, which spread writes over the media and deal with the long erase times of NOR flash blocks. The basic concept behind flash file systems is the following: when the flash store is to be updated, the file system will write a new copy of the changed data to a fresh block, remap the file pointers, then erase the old block later when it has time. In practice, flash file systems are used only for memory technology devices (MTDs), which are embedded flash memories that do not have a controller. Removable flash memory cards, SSDs, eMMC/eUFS chips and USB flash drives have built-in controllers to perform wear leveling and error correction so use of a specific flash file system may not add benefit.
Serial flash is a small, low-power flash memory that provides only serial access to the data - rather than addressing individual bytes, the user reads or writes large contiguous groups of bytes in the address space serially. Serial Peripheral Interface Bus (SPI) is a typical protocol for accessing the device. When incorporated into an embedded system, serial flash requires fewer wires on the PCB than parallel flash memories, since it transmits and receives data one bit at a time. This may permit a reduction in board space, power consumption, and total system cost. There are several reasons why a serial device, with fewer external pins than a parallel device, can significantly reduce overall cost: Many ASICs are pad-limited, meaning that the size of the die is constrained by the number of wire bond pads, rather than the complexity and number of gates used for the device logic. Eliminating bond pads thus permits a more compact integrated circuit, on a smaller die; this increases the number of dies that may be fabricated on a wafer, and thus reduces the cost per die. Reducing the number of external pins also reduces assembly and packaging costs. A serial device may be packaged in a smaller and simpler package than a parallel device. Smaller and lower pin-count packages occupy less PCB area. Lower pin-count devices simplify PCB routing. There are two major SPI flash types. The first type is characterized by small blocks and one internal SRAM block buffer allowing a complete block to be read to the buffer, partially modified, and then written back (for example, the Atmel AT45 DataFlash or the Micron Technology Page Erase NOR Flash). The second type has larger sectors where the smallest sectors typically found in this type of SPI flash are 4 KB, but they can be as large as 64 KB. Since this type of SPI flash lacks an internal SRAM buffer, the complete block must be read out and modified before being written back, making it slow to manage. However, the second type is cheaper than the first and is therefore a good choice when the application is code shadowing. The two types are not easily exchangeable, since they do not have the same pinout, and the command sets are incompatible. Most FPGAs are based on SRAM configuration cells and require an external configuration device, often a serial flash chip, to reload the configuration bitstream every power cycle.
One more recent application for flash memory is as a replacement for hard disks. Flash memory does not have the mechanical limitations and latencies of hard drives, so a solid-state drive (SSD) is attractive in terms of speed, noise, power consumption, and reliability. Flash drives are gaining traction as mobile device secondary storage devices; they are also used as substitutes for hard drives in high-performance desktop computers and some servers with RAID and SAN architectures.
There remain some aspects of flash-based SSDs that make them unattractive. The cost per gigabyte of flash memory remains significantly higher than that of hard disks. Also, flash memory has a finite number of P/E (program/erase) cycles, but this seems to be currently under control since warranties on flash-based SSDs are approaching those of current hard drives. In addition, deleted files on SSDs can remain for an indefinite period of time before being overwritten by fresh data; erasure or shred techniques or software that work well on magnetic hard disk drives have no effect on SSDs, compromising security and forensic examination. However, due to the so-called TRIM command employed by most solid state drives, which marks the logical block addresses occupied by the deleted file as unused to enable garbage collection, data recovery software is not able to restore files deleted from such. For relational databases or other systems that require ACID transactions, even a modest amount of flash storage can offer vast speedups over arrays of disk drives. In May 2006, Samsung Electronics announced two flash-memory based PCs, the Q1-SSD and Q30-SSD were expected to become available in June 2006, both of which used 32 GB SSDs, and were at least initially available only in South Korea. The Q1-SSD and Q30-SSD launch was delayed and finally was shipped in late August 2006. The first flash-memory based PC to become available was the Sony Vaio UX90, announced for pre-order on 27 June 2006 and began to be shipped in Japan on 3 July 2006 with a 16 GB flash memory hard drive. In late September 2006 Sony upgraded the flash-memory in the Vaio UX90 to 32 GB. A solid-state drive was offered as an option with the first MacBook Air introduced in 2008, and from 2010 onwards, all models were shipped with an SSD. Starting in late 2011, as part of Intel's Ultrabook initiative, an increasing number of ultra-thin laptops are being shipped with SSDs standard. There are also hybrid techniques such as hybrid drive and ReadyBoost that attempt to combine the advantages of both technologies, using flash as a high-speed non-volatile cache for files on the disk that are often referenced, but rarely modified, such as application and operating system executable files. On smartphones, the NAND flash products are used as file storage device, for example, eMMC and eUFS.
3. Software Implementation, Frameworks & Protocols One source states that, in 2008, the flash memory industry includes about US$9.1 billion in production and sales. Other sources put the flash memory market at a size of more than US$20 billion in 2006, accounting for more than eight percent of the overall semiconductor market and more than 34 percent of the total semiconductor memory market. In 2012, the market was estimated at $26.8 billion. It can take up to 10 weeks to produce a flash memory chip.
The following were the largest NAND flash memory manufacturers, as of the third quarter of 2025. Samsung Electronics – 30% SK Hynix – 20% Kioxia – 14% Micron Technology – 13% YMTC – 13% Western Digital Corporation – 11% Notes: Samsung remains the largest NAND flash memory manufacturer as of Q3 2025. Kioxia spun out and got renamed of Toshiba in 2018/2019. SK Hynix acquired Intel's NAND business at the end of 2021.
In addition to individual flash memory chips, flash memory is also embedded in microcontroller (MCU) chips and system-on-chip (SoC) devices. Flash memory is embedded in ARM chips, which have sold 150 billion units worldwide as of 2019, and in programmable system-on-chip (PSoC) devices, which have sold 1.1 billion units as of 2012. This adds up to at least 151.1 billion MCU and SoC chips with embedded flash memory, in addition to the 45.4 billion known individual flash chip sales as of 2015, totalling at least 196.5 billion chips containing flash memory.
Due to its relatively simple structure and high demand for higher capacity, NAND flash memory is the most aggressively scaled technology among electronic devices. The heavy competition among the top few manufacturers only adds to the aggressiveness in shrinking the floating-gate MOSFET design rule or process technology node. While the expected shrink timeline is a factor of two every three years per the original version of Moore's law, this has recently been accelerated in the case of NAND flash to a factor of two every two years.
As the MOSFET feature size of flash memory cells reaches the 15–16 nm minimum limit, further flash density increases will be driven by TLC (3 bits/cell) combined with vertical stacking of NAND memory planes. The decrease in endurance and increase in uncorrectable bit error rates that accompany feature size shrinking can be compensated by improved error correction mechanisms. Even with these advances, it may be impossible to economically scale flash to smaller and smaller dimensions as the number of electron holding capacity reduces. Many promising new technologies (such as FeRAM, MRAM, PMC, PCM, ReRAM, and others) are under investigation and development as possible more scalable replacements for flash.
Semiconductor Characterization System has diverse functions Archived 22 October 2018 at the Wayback Machine Understanding and selecting higher performance NAND architectures Archived 31 October 2012 at the Wayback Machine How flash storage works, presentation by David Woodhouse from Intel Flash endurance testing NAND Flash Data Recovery Cookbook Type of Flash Memory by OpenWrt File carving is the process of reassembling computer files from fragments in the absence of filesystem metadata.
It is used in IT forensics and data recovery. Carving is typically used on storage media with a corrupted file system or for storage areas that are listed as free in the existing file system. File carving is the process of trying to recover files without this metadata. This is done by analyzing the raw data and identifying what it is (text, executable, png, mp3, etc.). This can be done in different ways, but the simplest is to look for the file signature or "magic numbers" that mark the beginning and/or end of a particular file type. For instance, every Java class file has as its first four bytes the hexadecimal value CA FE BA BE. Some files contain footers as well, making it just as simple to identify the ending of the file.
4. Practical Deployment, Analysis & Case Studies Most file systems, such as the FAT family and UNIX's Fast File System, work with the concept of clusters of an equal and fixed size. For example, a FAT32 file system might be broken into clusters of 4 KiB each. Any file smaller than 4 KiB fits into a single cluster, and there is never more than one file in each cluster. Files that take up more than 4 KiB are allocated across many clusters. Sometimes these clusters are all contiguous, while other times they are scattered across two or potentially many more so called fragments, with each fragment containing a number of contiguous clusters storing one part of the file's data. Obviously, large files are more likely to be fragmented.
Simson Garfinkel reported fragmentation statistics collected from over 350 disks containing FAT, NTFS and UFS file systems. He showed that while fragmentation in a typical disk is low, the fragmentation rate of forensically important files such as email, JPEG and Word documents is relatively high. The fragmentation rate of JPEG files was found to be 16%, Word documents had 17% fragmentation, AVI had a 22% fragmentation rate and PST files (Microsoft Outlook) had a 58% fragmentation rate (the fraction of files being fragmented into two or more fragments). Pal, Shanmugasundaram, and Memon presented an efficient algorithm based on a greedy heuristic and alpha-beta pruning for reassembling fragmented images. Pal, Sencar, and Memon introduced sequential hypothesis testing as an effective mechanism for detecting fragmentation points. Richard and Roussev presented Scalpel, an open-source file-carving tool existing since 2005 and initially based on Foremost.
File carving is a highly complex task, with a potentially huge number of permutations to try. To make this task tractable, carving software typically makes extensive use of models and heuristics. This is necessary not only from a standpoint of execution time, but also for the accuracy of the results. State-of-the-art file carving algorithms use statistical techniques like sequential hypothesis testing for determining fragmentation points.
File carving can be performed using free or commercial software and is often performed in conjunction with computer forensics examinations or alongside other recovery efforts (e.g. hardware repair) by data recovery companies. Whereas the primary goal of data recovery is to recover the file content, computer forensics examiners are often just as interested in the metadata such as who owned a file, where it was stored, and when it was last modified. Thus, while a forensic examiner could use file carving to prove that a file was once stored on a hard drive, they might need to seek out other evidence to prove who put it there.
Mobile device forensics is a branch of digital forensics relating to recovery of digital evidence or data from a mobile device under forensically sound conditions. The phrase mobile device usually refers to mobile phones; however, it can also relate to any digital device that has both internal memory and communication ability, including PDA devices, GPS devices and tablet computers. Mobile devices can be used to save several types of personal information such as contacts, photos, calendars and notes, SMS and MMS messages. Smartphones may additionally contain video, email, web browsing information, location information, and social networking messages and contacts. There is growing demand for mobile forensics due to several reasons and some of the prominent reasons are: Use of mobile phones to store and transmit personal and corporate information Use of mobile phones in online transactions Use of mobile phone devices by criminals Mobile device forensics can be particularly challenging on a number of levels: Evidential and technical challenges exist. For example, cell site analysis following from the use of a mobile phone usage coverage is not an exact science. Consequently, whilst it is possible to determine roughly the cell site zone from which a call was made or received, it is not yet possible to say with any degree of certainty that a mobile phone call emanated from a specific location e.g. a residential address.
To remain competitive, original equipment manufacturers frequently change mobile phone form factors, operating system file structures, data storage, services, peripherals, and even pin connectors and cables. As a result, forensic examiners must use a different forensic process compared to computer forensics. Storage capacity continues to grow thanks to demand for more powerful "mini computer" type devices. Not only the types of data but also the way mobile devices are used constantly evolve.
Hibernation behavior in which processes are suspended when the device is powered off or idle, but at the same time remaining active. As a result of these challenges, a wide variety of tools exists to extract evidence from mobile devices; no one tool or method can acquire all the evidence from all devices. It is therefore recommended that forensic examiners, especially those wishing to qualify as expert witnesses in court, undergo extensive training in order to understand how each tool and method acquires evidence; how it maintains standards for forensic soundness; and how it meets legal requirements such as the Daubert standard or Frye standard.
The forensics process for mobile devices broadly matches other branches of digital forensics; however, some particular concerns apply. Generally, the process can be broken down into three main categories: seizure, acquisition, and examination/analysis. Other aspects of the computer forensic process, such as intake, validation, documentation/reporting, and archiving still apply.
The second step in the forensic process is acquisition, in this case usually referring to retrieval of material from a device (as compared to the bit-copy imaging used in computer forensics). Due to the proprietary nature of mobiles it is often not possible to acquire data with it powered down; most mobile device acquisition is performed live. With more advanced smartphones using advanced memory management, connecting it to a recharger and putting it into a faraday cage may not be good practice. The mobile device would recognize the network disconnection and therefore it would change its status information that can trigger the memory manager to write data. Most acquisition tools for mobile devices are commercial in nature and consist of a hardware and software component, often automated.
Early investigations consisted of live manual analysis of mobile devices; with examiners photographing or writing down useful material for use as evidence. Without forensic photography equipment such as Fernico ZRT, EDEC Eclipse, or Project-a-Phone, this had the disadvantage of risking the modification of the device content, as well as leaving many parts of the proprietary operating system inaccessible. In recent years a number of hardware/software tools have emerged to recover logical and physical evidence from mobile devices. Most tools consist of both hardware and software portions. The hardware includes a number of cables to connect the mobile device to the acquisition machine; the software exists to extract the evidence and, occasionally, even to analyze it. Most recently, mobile device forensic tools have been developed for the field.
This is in response both to military units' demand for fast and accurate anti-terrorism intelligence, and to law enforcement demand for forensic previewing capabilities at a crime scene, search warrant execution, or exigent circumstances. Such mobile forensic tools are often ruggedized for harsh environments (e.g. the battlefield) and rough treatment (e.g. being dropped or submerged in water). Generally, because it is impossible for any one tool to capture all evidence from all mobile devices, mobile forensic professionals recommend that examiners establish entire toolkits consisting of a mix of commercial, open-source, broad support, and narrow support forensic tools, together with accessories such as battery chargers, Faraday bags or other signal disruption equipment, and so forth.
5. Performance Evaluation & Extended Technical Observations Desoldering the chips is done carefully and slowly, so that the heat does not destroy the chip or data. Before the chip is desoldered the PCB is baked in an oven to eliminate remaining water. This prevents the so-called popcorn effect, at which the remaining water would blow the chip package at desoldering. There are mainly three methods to melt the solder: hot air, infrared light, and steam-phasing. The infrared light technology works with a focused infrared light beam onto a specific integrated circuit and is used for small chips. The hot air and steam methods cannot focus as much as the infrared technique.
The first is to use a stencil. The stencil is chip-dependent and must fit exactly. Then the tin-solder is put on the stencil. After cooling the tin the stencil is removed and if necessary a second cleaning step is done. The second method is laser re-balling. Here the stencil is programmed into the re-balling unit. A bondhead (looks like a tube/needle) is automatically loaded with one tin ball from a solder ball singulation tank. The ball is then heated by a laser, such that the tin-solder ball becomes fluid and flows onto the cleaned chip. Instantly after melting the ball the laser turns off and a new ball falls into the bondhead. While reloading, the bondhead of the re-balling unit changes the position to the next pin. A third method makes the entire re-balling process unnecessary. The chip is connected to an adapter with Y-shaped springs or spring-loaded pogo pins. The Y-shaped springs need to have a ball onto the pin to establish an electric connection, but the pogo pins can be used directly on the pads on the chip without the balls. The advantage of forensic desoldering is that the device does not need to be functional and that a copy without any changes to the original data can be made. The disadvantage is that the re-balling devices are expensive, so this process is very costly and there are some risks of total data loss. Hence, forensic desoldering should only be done by experienced laboratories.
This is the documentation for Volatility 3, the most advanced memory forensics framework in the world. Like previous versions of the Volatility framework, Volatility 3 is Open Source. A comprehensive open-source toolkit for memory forensics using Volatility. This repository provides detailed documentation, forensic workflows, and best practices for detecting fileless malware and performing advanced memory analysis. All related documents are available in the docs folder.
The Volatility Forensics Toolkit is designed to assist cybersecurity professionals, digital forensic analysts, and incident responders in: For a detailed description of all versions and updates, please refer to our Google Docs version history . Detailed usage instructions, including commands and forensic workflows, are provided in the documentation located in the docs folder. Key commands include: All supporting documents, including detailed explanations of the forensic methods, attack techniques, and mitigation strategies, can be found in the docs directory.
This project is licensed under the GNU General Public License (GPL). See the LICENSE file for more details. A comprehensive open-source toolkit for memory forensics using Volatility. This repository provides detailed documentation, forensic workflows, and best practices for detecting fileless malware and performing advanced memory analysis. All related documents are available in the `docs` folder.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Flash%20memory • https://en.wikipedia.org/wiki/File%20carving • https://en.wikipedia.org/wiki/Mobile%20device%20forensics • https://volatility3.readthedocs.io/en/latest/ • https://github.com/sravs-01/Volatility_Forensics_Toolkit • https://www.cyberforensicacademy.com/blog/volatility-framework-complete-memory-forensics-guide
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Automated Memory Dump Forensics Tool Using Volatility.
[*] Metasploit Scan Running on Target Subnet for Automated Memory Dump Forensics Tool Using Volatility... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |