Complete Technical Paper Content — Automated Network Penetration Testing Framework In Python
Overview & System Context
Automated Network Penetration Testing Framework In Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~3851 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background The Metasploit Project is a computer security project that provides information about security vulnerabilities and aids in penetration testing and IDS signature development. It is owned by Rapid7, a Boston-based security company. Its best-known sub-project is the open-source Metasploit Framework, a tool for developing and executing exploit code against a remote target machine. Other important sub-projects include the Opcode Database, shellcode archive and related research. The Metasploit Project includes anti-forensic and evasion tools, some of which are built into the Metasploit Framework. In various operating systems it comes pre installed.
Optionally checking whether the intended target system is vulnerable to an exploit. Choosing and configuring an exploit (code that enters a target system by taking advantage of one of its bugs; about 900 different exploits for Windows, Unix/Linux and macOS systems are included). Choosing and configuring a payload (code that will be executed on the target system upon successful entry; for instance, a remote shell or a VNC server). Metasploit often recommends a payload that should work.
Choosing the encoding technique so that hexadecimal opcodes known as "bad characters" are removed from the payload, these characters will cause the exploit to fail. Executing the exploit. This modular approach – allowing the combination of any exploit with any payload – is the major advantage of the Framework. It facilitates the tasks of attackers, exploit writers and payload writers. Metasploit runs on Unix (including Linux and macOS) and on Windows. The Metasploit Framework can be extended to use add-ons in multiple languages. To choose an exploit and payload, some information about the target system is needed, such as operating system version and installed network services. This information can be gleaned with port scanning and TCP/IP stack fingerprinting tools such as Nmap. Vulnerability scanners such as Nessus, and OpenVAS can detect target system vulnerabilities. Metasploit can import vulnerability scanner data and compare the identified vulnerabilities to existing exploit modules for accurate exploitation.
A command-line interface for controlling exploit modules. Database for managing scan data and exploit results. Import of network scan results from external scanning utilities such as Nmap. Scanning support using the integrated `db_nmap` feature for automated execution and data integration. Over 1,500 built-in exploits, with the ability of adding custom exploit modules or automated resource scripts. The Metasploit Framework is implemented in Ruby and uses a modular software architecture.
Command shell enables users to run collection scripts or run arbitrary commands against the host. Meterpreter (the Metasploit Interpreter) enables users to control the screen of a device using VNC and to browse, upload and download files. Dynamic payloads enable users to evade anti-virus defense by generating unique payloads. Static payloads enable static IP address/port forwarding for communication between the host and the client system.
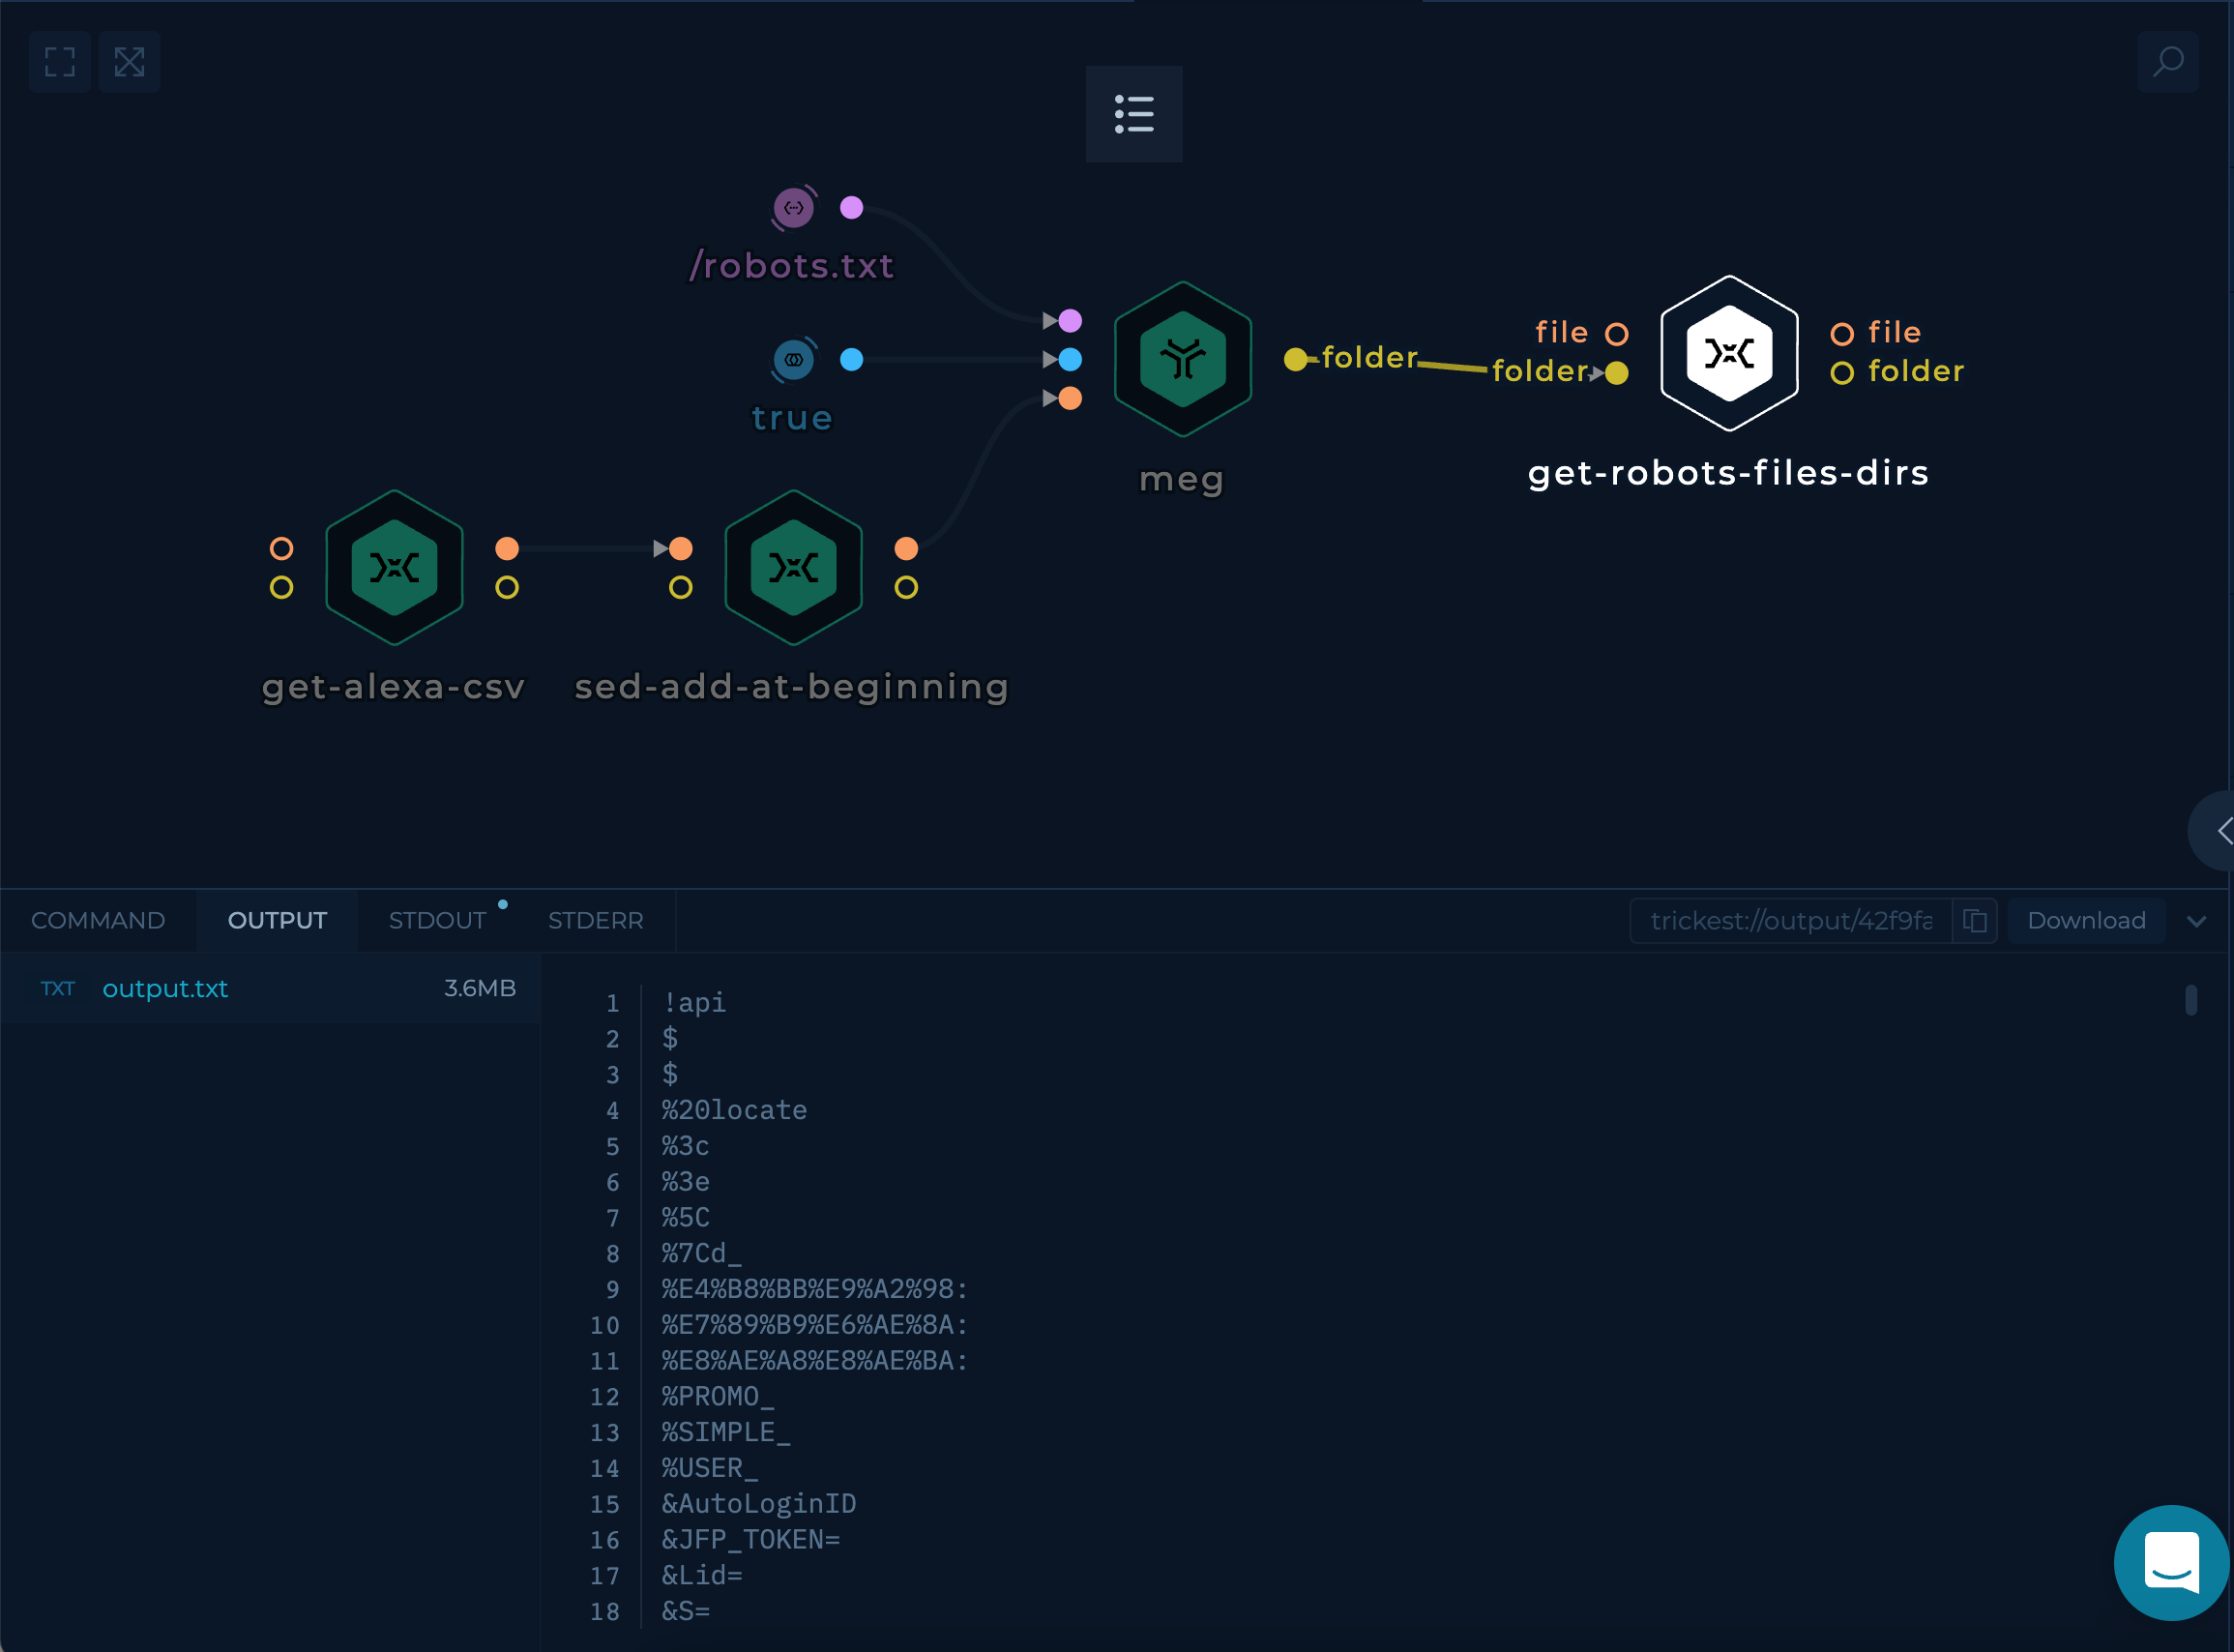
Figure 1: Penetration Testing Tools Github H. D. Moore (founder and chief architect) Matt Miller (core developer from 2004–2008) Dean McNamee (Spoonm) (core developer from 2003–2008) Kali Linux is a Linux distribution designed for digital forensics and penetration testing. It is maintained and funded by Offensive Security. The software is based on the testing branch of the Debian Linux Distribution: most packages Kali uses are imported from the Debian repositories. Kali Linux has gained popularity in the cybersecurity community due to its comprehensive set of tools designed for penetration testing, vulnerability analysis, and reverse engineering. It was developed by Mati Aharoni and Devon Kearns of Offensive Security through the rewrite of BackTrack, their previous information security testing Linux distribution based on Knoppix. Kali Linux was featured in multiple episodes of the TV series Mr. Robot.
A minimum of 20GB hard disk space for installation, depending on the version. Version 2020.2 requires at least 20GB. A minimum of 128 MB of RAM, 2 GB if opting to use the Xfce4 interface A CD-DVD drive, USB stick or other bootable media. Kali NetHunter, an Android-based penetration testing platform, expands Kali’s capabilities, allowing penetration testing from Android devices, providing features like wireless frame injection and MITM attacks. It was the first open source Android penetration testing platform for Nexus devices, created as a joint effort between the Kali community member "BinkyBear" and Offensive Security. It supports Wireless 802.11 frame injection, one-click MANA Evil Access Point setups, HID keyboard (Teensy like attacks), as well as Bad USB MITM attacks.
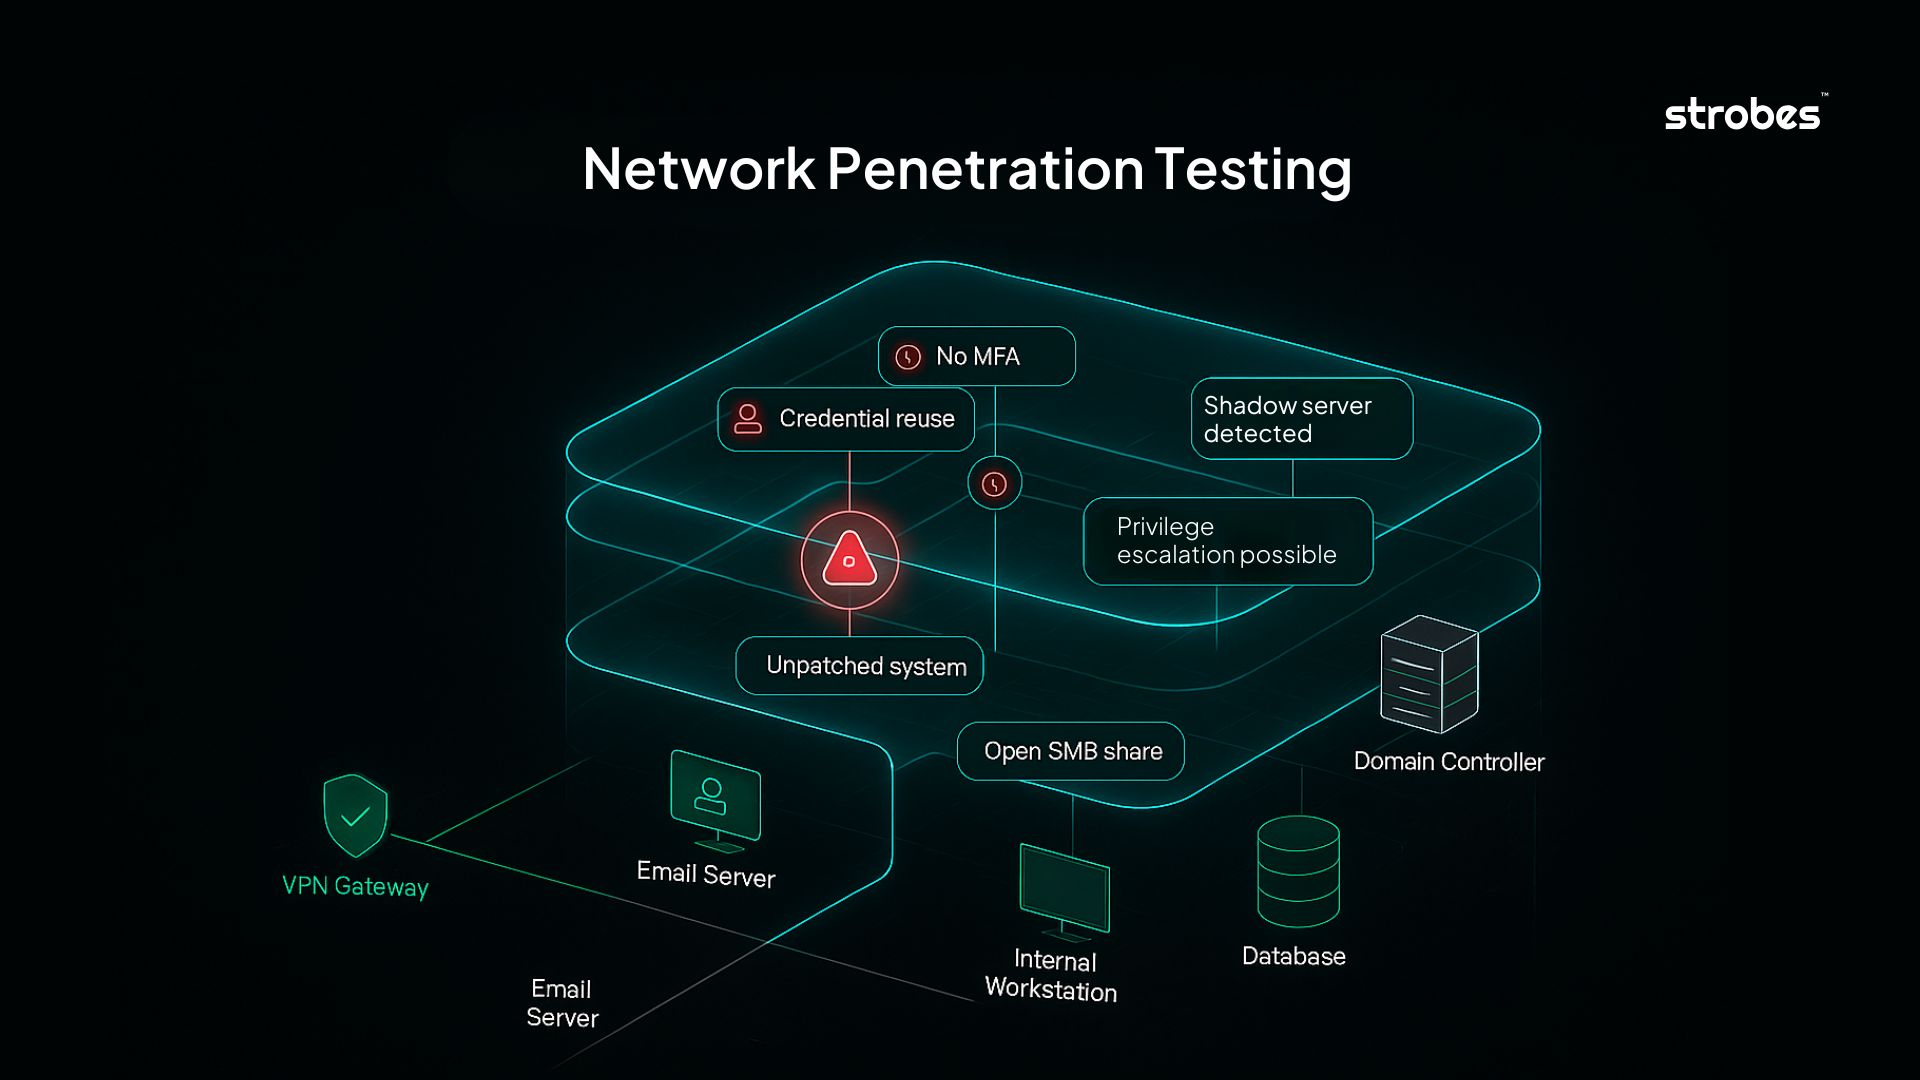
Figure 2: What is Network Penetration Testing? | Strobes Kali NetHunter List of digital forensic tools Offensive Security Offensive Security Certified Professional Security-focused operating system In programming and software development, fuzzing or fuzz testing is an automated software testing technique that involves providing invalid, unexpected, or random data as inputs to a computer program. The program is then monitored for exceptions such as crashes, failing built-in code assertions, or potential memory leaks. Typically, fuzzers are used to test programs that take structured inputs. This structure is specified, such as in a file format or protocol and distinguishes valid from invalid input.
An effective fuzzer generates semi-valid inputs that are "valid enough" in that they are not directly rejected by the parser, but do create unexpected behaviors deeper in the program and are "invalid enough" to expose corner cases that have not been properly dealt with. For the purpose of security, input that crosses a trust boundary is often the most useful. For example, it is more important to fuzz code that handles a file uploaded by any user than it is to fuzz the code that parses a configuration file that is accessible only to a privileged user.
A fuzzer can be generation-based or mutation-based depending on whether inputs are generated from scratch or by modifying existing inputs. A fuzzer can be dumb (unstructured) or smart (structured) depending on whether it is aware of input structure. A fuzzer can be white-, grey-, or black-box, depending on whether it is aware of program structure. to detect memory related errors, such as buffer overflows and use-after-free (using memory debuggers such as AddressSanitizer), to detect race conditions and deadlocks (ThreadSanitizer), to detect undefined behavior (UndefinedBehaviorSanitizer), to detect memory leaks (LeakSanitizer), or to check control-flow integrity (CFISanitizer).
Fuzzing can also be used to detect "differential" bugs if a reference implementation is available. For automated regression testing, the generated inputs are executed on two versions of the same program. For automated differential testing, the generated inputs are executed on two implementations of the same program (e.g., lighttpd and httpd are both implementations of a web server). If the two variants produce different output for the same input, then one may be buggy and should be examined more closely.
Figure 3: Best Open Source Penetration Testing Tools – KDFT Preparation of inputs Choose a fuzzer. Choose software or a library as the fuzz target. Prepare a seed corpus from existing test inputs or hand-craft inputs for the fuzzer to mutate. Seeds give the fuzzer starting inputs that can be modified into new test cases. Optionally prepare a dictionary, a file that specifies interesting tokens or keywords for a fuzz target. Input generation and mutation The fuzzer will create new test cases from the seeds. Execution The fuzz target will be run with each generated input. Sanitizers such as AddressSanitizer and UndefinedBehaviorSanitizer are also often used when building or configuring the target to detect certain classes of programming errors during execution. Feedback and coverage Feedback-guided fuzzers use feedback, such as code coverage, to guide the generation of future inputs. However, this is depending on the fuzzer, not all fuzzers use coverage feedback. Interesting inputs, such as those that reach previously unexplored behavior, can be retained for further mutation. Iteration The process is repeated to explore more program behavior and potentially find bugs.
Automated bug triage is used to group a large number of failure-inducing inputs by root cause and to prioritize each individual bug by severity. A fuzzer produces a large number of inputs, and many of the failure-inducing ones may effectively expose the same software bug. Only some of these bugs are security-critical and should be patched with higher priority. For instance the CERT Coordination Center provides the Linux triage tools which group crashing inputs by the produced stack trace and lists each group according to their probability to be exploitable. The Microsoft Security Research Centre (MSEC) developed the "!exploitable" tool which first creates a hash for a crashing input to determine its uniqueness and then assigns an exploitability rating: Exploitable Probably Exploitable Probably Not Exploitable, or Unknown. Previously unreported, triaged bugs might be automatically reported to a bug tracking system. For instance, OSS-Fuzz runs large-scale, long-running fuzzing campaigns for several security-critical software projects where each previously unreported, distinct bug is reported directly to a bug tracker.
The OSS-Fuzz bug tracker automatically informs the maintainer of the vulnerable software and checks in regular intervals whether the bug has been fixed in the most recent revision using the uploaded minimized failure-inducing input. 2. System Architecture & Core Working Principles The following is a list of fuzzers described as "popular", "widely used", or similar in the academic literature.
OWASP Nettacker is an open-source, Python-based automated penetration testing and information-gathering framework designed to help cyber security professionals and ethical hackers perform reconnaissance, vulnerability assessments, and network security audits efficiently. Nettacker automates tasks like port scanning, service detection, subdomain enumeration, network mapping, vulnerability scanning, credential brute-force testing making it a powerful tool for identifying weaknesses in networks, web applications, IoT devices and APIs.
Penetration Testing Automate reconnaissance, misconfiguration checks, service discovery, and vulnerability scanning to support efficient and repeatable penetration testing workflows. Recon & Vulnerability Assessment Map live hosts, open ports, services, default credentials, and directories, then perform credential brute-forcing or fuzzing using built-in or custom wordlists.
Attack Surface Mapping Discover exposed hosts, ports, subdomains, and services quickly using built-in enumeration modules—ideal for both internal and external assets. Bug Bounty Recon Automate and scale common reconnaissance tasks like subdomain enumeration, directory brute-forcing, and default credential checks to speed up finding targets.
Network Vulnerability Scanning Efficiently scan IPs, IP ranges, or entire CIDR blocks or all subdomains of the organisation in parallel using a modular, multithreaded approach for large-scale network assessments. Shadow IT & Asset Discovery Use historical scan data and drift detection to uncover unmanaged or forgotten hosts, open ports/services, and subdomains appearing over time.
CI/CD & Compliance Monitoring Integrate Nettacker into pipelines to track infrastructure changes and detect new vulnerabilities via stored scan history and comparison features. OWASP Nettacker is an open-source project, built on the principles of collaboration and shared knowledge. The vibrant OWASP community contributes to its development, ensuring that the tool remains up-to-date, adaptable, and aligned with the latest security practices. Thanks to all our awesome contributors! I We’re grateful to the organizations, community projects, and individuals who adopt and rely on OWASP Nettacker for their security workflows.
If you’re using OWASP Nettacker in your organization or project, we’d love to hear from you! Feel free to add your details to the ADOPTERS.md file by submitting a pull request or reach out to us via GitHub issues. Let’s showcase how Nettacker is making a difference in the security community! OWASP Nettacker is supported by Sorena AI , a compliance and GRC platform that helps security teams streamline assessments, evidence collection, risk management, and regulatory workflows.
Automated Penetration Testing Framework - Open-Source Vulnerability Scanner - Vulnerability Management Vulnerability Scanning is the process of detection of security flaws in the Web-based Application. We can perform automated Scanning using various tools. OWaASP has a project named Nettacker which is built to automate the various phases like Information Gathering, Enumeration, Scanning, Vulnerability Scanning, etc. Along with this Nettacker tool eventually generates a report for networks, including services, bugs, vulnerabilities, misconfigurations, and other information. Nettacker tool is developed in the Python Language and available on the GitHub platform. Nettacker tool is open-source and free to use the tool. Nettacker tool supports bypassing of Firewall/IDS/IPS devices on the target server.
3. Software Implementation, Frameworks & Protocols Note: Make Sure You have Python Installed on your System, as this is a python-based tool. Click to check the Installation process - Python Installation Steps on Linux python3 nettacker.py -l targets.txt -m all -x port_scan -g 20-100 -t 5 -u root -p 123456,654321,123123 python3 nettacker.py -i geeksforgeeks.org -s -m port_scan -t 10 -M 35 -g 20-100 --graph d3_tree_v2_graph Example 4: Scan the IP range automatically by getting the range from the RIPE database online python3 nettacker.py -i owasp.org -s -r -m port_scan -t 10 -M 35 -g 20-100 --graph d3_tree_v2_graph python3 nettacker.py -i geeksforgeeks.org -m clickjacking_vuln -T 5 --socks-proxy socks://127.0.0.1:80 AutoPentest is a comprehensive, automated penetration testing framework designed to streamline security assessments through a modular, configurable approach. It orchestrates reconnaissance, vulnerability scanning, exploitation, and post-exploitation phases while maintaining safety controls and generating detailed reports.
Kali Linux is the recommended platform for AutoPentest as it comes with most security tools pre-installed and configured. This tool is for authorized security testing only. Users are responsible for ensuring they have proper authorization before using this tool against any target. The authors are not responsible for any misuse of this software. A comprehensive Python-based framework designed to automate vulnerability assessment and penetration testing (VAPT) tasks for enterprise environments.
This framework streamlines the security testing process by providing automated tools for target discovery, vulnerability scanning, exploitation, and reporting. Built with scalability and extensibility in mind, it can handle everything from single application assessments to large-scale enterprise infrastructure testing. This framework is designed for authorized security testing only. Users are responsible for ensuring they have proper permission before testing any systems.
1,500+ tech insiders, business leaders, and Pluralsight Authors share their predictions on what’s shifting fastest and how to stay ahead. 1,500+ tech insiders, business leaders, and Pluralsight Authors share their predictions on what’s shifting fastest and how to stay ahead.
Learn how to build your own automated penetration testing application using Python and Kali Linux. Also, learn how to understand software tools and how they work. 4. Practical Deployment, Analysis & Case Studies Learn how to build your own automated penetration testing application using Python and Kali Linux. Also, learn how to understand software tools and how they work.
Get a good understanding on how to use Python to automate your web penetration testing scenarios. In this course, Penetration Testing Automation Using Python and Kali Linux, you'll learn how to start automating your penetration testing tasks using Python and Kali Linux. First, you'll learn about information gathering automation. Next, you'll learn about network scanning automation. Finally, you'll learn about vulnerabilities assessment automation. By the end of this course, you'll be able to develop your own automated scanner for gathering information, scanning the network, and conducting an automated vulnerability assessment.
Get a good understanding on how to use Python to automate your web penetration testing scenarios. In this course, Penetration Testing Automation Using Python and Kali Linux, you'll learn how to start automating your penetration testing tasks using Python and Kali Linux. First, you'll learn about information gathering automation. Next, you'll learn about network scanning automation. Finally, you'll learn about vulnerabilities assessment automation. By the end of this course, you'll be able to develop your own automated scanner for gathering information, scanning the network, and conducting an automated vulnerability assessment.
Gus is an IT expert specialized in programming and security. He's a passionate blogger, geek, and loves what he's doing. OWASP Nettacker is an automated penetration testing framework designed to help cyber security professionals and ethical hackers perform reconnaissance, vulnerability assessments, and network security audits efficiently. Nettacker automates information gathering, vulnerability scanning, and credential brute forcing tasks, making it a powerful tool for identifying weaknesses in networks, web applications, IoT devices and APIs.
OWASP Nettacker is an open-source software written in Python language. OWASP Nettacker uses YAML files to define modules in a structured and human-readable format. OWASP Nettacker project was created to automate information gathering, vulnerability scanning and in general to aid penetration testing engagements. Nettacker is able to run various scans using a variety of methods and generate scan reports(in HTML/TXT/JSON/CSV format) for applications and networks, including discovering open ports, services, bugs, vulnerabilities, misconfigurations, default credentials, subdomains, etc. Nettacker can be run as a command-line utility (including running as a Docker container), API, Web GUI mode OWASP Nettacker's modular architecture is one of its core strengths, allowing users to perform specific tasks by leveraging a range of pre-built and customizable modules.
By leveraging a modular framework, Nettacker supports multiple protocols and scanning methods, making it highly adaptable to various security testing scenarios. OWASP Nettacker is written in 100% Python and does not rely on launching any external tools. OWASP Nettacker can also help you find instances of critically vulnerable MOVEit Transfer, Citrix Netscaler, Ivanti ICS/EPMM/vTM/CSA services and other CISA KEV vulnerabilities in your network as well as help build your asset inventory.
A modular, Python-based network penetration testing automation framework that chains recon → port scanning → service enumeration → CVSS-scored vulnerability assessment → report generation into a single command — with a real-time web dashboard, parallel multi-target scanning, and Slack/email alerting. See lab_setup/lab_setup.md for full guide on setting up Metasploitable 2 as a target using UTM on macOS (M1/M2/M3).
This tool is for authorized penetration testing and educational use only . Only run against systems you own or have explicit written permission to test. Unauthorized use is illegal under the CFAA and equivalent laws worldwide. Anveeksh M Rao (Ish) MS Cybersecurity — Northeastern University (Khoury College of Computer Sciences) Co-Founder, Cyber Tech Associates Advanced automated network penetration testing framework — recon, port scanning, CVSS scoring, web dashboard, and PDF report generation. Built in Python.
5. Performance Evaluation & Extended Technical Observations > your AI agent picks dependencies from memory; give it dated facts — try starlog.dev I vet your agent's deps I vibe-coding is fine. vibe-importing isnâIIt. — try starlog.dev I vibe-importing isnâIIt fine I your agent has never seen your private packages — try starlog.dev I facts for private packages I a linter for the dependencies your AI agent picks — try starlog.dev I a linter for agent deps I whois is redacted, cdns mask the rest âII get the real operator — try whoisgeni.us I who really runs that domain I domain attribution that shows its work âII full evidence chain — try whoisgeni.us I domain intel w/ evidence I Metrics below are heuristic approximations computed from repository structure, not authoritative measurements.
While most developers know Metasploit, the Python security ecosystem contains over 200 specialized tools that security professionals actually use dailyâIIand most remain invisible to mainstream engineering teams. Before centralized repositories like this emerged, penetration testers faced a discovery problem. Security tools were scattered across personal blogs, conference presentations, and obscure GitHub repositories. Finding a Python library to craft custom packets, analyze memory dumps, or intercept HTTPS traffic meant hours of forum searches and word-of-mouth recommendations. The dloss/python-pentest-tools repository, created and maintained by Dirk Loss, addresses this fragmentation by cataloging Python-based security tools across the entire penetration testing lifecycle.
The focus on Python isn't arbitrary. While C and C++ dominate low-level exploit development, Python's expressiveness makes it ideal for rapid prototyping, automation, and scriptingâIIcore activities in modern pentesting. Python bindings to powerful C libraries like libpcap (via Scapy) or Frida's instrumentation engine let security professionals combine performance with productivity. This repository captures that intersection, organizing tools by function: network analysis, debugging, fuzzing, web exploitation, forensics, and malware analysis. It's essentially a map of how Python conquered security testing.
The repository's value lies in its categorization, which reveals architectural patterns across the security tool ecosystem. Take network tools: Scapy stands out not just for packet manipulation but for its approach to protocol abstraction. Unlike raw socket programming, Scapy treats packets as composable objects. This design patternâIIdomain-specific languages embedded in PythonâIIappears repeatedly. Frida, listed under debugging tools, extends this concept to runtime instrumentation. Rather than writing C code to hook functions, you write JavaScript (executed in Frida's engine) controlled by Python: The forensics category showcases a different architectural choice: Python as a plugin host. Volatility, the memory forensics framework, uses a plugin architecture where community members extend core functionality. Each plugin analyzes specific memory structuresâIIprocess lists, network connections, registry hivesâIIby implementing a common interface. This modularity explains why Volatility remains dominant despite being a mature project: the architecture accommodates new operating system versions and attack techniques without rewriting the core.
Web security tools like mitmproxy demonstrate yet another pattern: Python as a control plane. The actual proxy logic handles performance-critical TLS interception in compiled code, but Python scripts modify traffic flows. You can write a few lines to intercept API calls, modify JSON payloads, or inject headers: The fuzzing tools section reveals Python's role in orchestrating complex workflows. American fuzzy lop (AFL) and its variants do the heavy lifting in compiled code, but Python wrappers manage test case generation, corpus minimization, and crash triage. Tools like Sulley define protocol state machines in Python, making it easier to fuzz stateful protocols than writing C code to manage connection sequences.
What unifies these tools is Python's position as glue code for security workflows. You might use Scapy to discover services, Impacket to interact with Windows protocols, Frida to analyze a proprietary client, and Volatility to examine memory after exploitationâIIall scriptable from Python, all composable into custom toolchains. The repository doesn't just list tools; it maps an ecosystem designed for programmatic security testing.
The repository's fundamental limitation is that it's a snapshot, not a living ecosystem. Many linked tools haven't been updated in years, and the repository itself doesn't track tool health or compatibility. Clicking through reveals broken links, archived projects, and tools that predate Python 3. There's no CI/CD testing each tool, no version matrix showing what works with Python 3.11, no automated checking of GitHub stars or commit activity. You're essentially browsing a 2010s-era security bookmarks folder that happened to get GitHub stars.
More critically, the legal disclaimer about excluding "aggressive tools" creates gaps in specific categories. Tools for wireless cracking, certain exploit frameworks, and sophisticated evasion techniques are absentâIIexactly what some pentesting scenarios require. The whitehats-focused curation is ethically defensible but functionally limiting. Additionally, newer tool categories are missing: cloud security tools, container escape techniques, and Kubernetes pentesting utilities barely existed when many entries were added. The repository captures a pre-cloud, pre-container security worldview. For modern infrastructure pentesting, you'll need supplementary resources covering cloud-native attack patterns and tools built for ephemeral, API-driven environments.
Use if you're building foundational knowledge of Python security tools, researching historical context for penetration testing methodologies, or need a broad survey before specializing in a particular area like memory forensics or protocol fuzzing. It's valuable for understanding tool categories and discovering lesser-known projects that might suit niche requirements. Also use it if you're teaching security concepts and want to show students the breadth of Python's security ecosystem. Skip if you need current, production-ready tooling for professional engagementsâIIthe lack of maintenance status and version compatibility makes it unreliable for real-world work. Skip if you're focused on cloud-native security, mobile application testing, or modern web frameworks where newer, specialized repositories provide better coverage. Instead, cross-reference tools here with actively maintained alternatives, check each project's GitHub activity before investing time, and supplement with domain-specific lists for your actual target environment.
Inside the Uncensored AI Arsenal: A Critical Look at Offensive Security Model Repositories Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Metasploit • https://en.wikipedia.org/wiki/Kali%20Linux • https://en.wikipedia.org/wiki/Fuzzing • https://github.com/OWASP/Nettacker • https://www.geeksforgeeks.org/linux-unix/nettacker-automated-penetration-testing-framework/ • https://github.com/Pavan-sk/AutoPentest • https://gauravsingh-cybersecurity.github.io/projects/vapt-framework/ • https://www.pluralsight.com/courses/penetration-testing-automation-using-python-kali-linux • https://owasp.org/projects/nettacker • https://github.com/anveeksh/netpwn
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Automated Network Penetration Testing Framework In Python.
! Define Extended Access List to Block Malicious Traffic ip access-list extended SECURE_PERIMETER_ACL remark Block Inbound Telnet and Unencrypted Services deny tcp any any eq 23 log remark Permit Verified Web SSL Traffic permit tcp any any eq 443 permit tcp any any eq 80 remark Mitigate ICMP Flood and Ping Sweeps permit icmp any any echo-reply deny icmp any any echo log deny ip any any log
! Apply ACL to Ingress Interface GigabitEthernet0/0 interface GigabitEthernet0/0 ip access-group SECURE_PERIMETER_ACL in no shutdown end write memory
Extended IP access list SECURE_PERIMETER_ACL (Cisco Packet Tracer) ──────────────────────────────────────────────────────────────────────── 10 deny tcp any any eq telnet log (142 matches) [Probes Dropped] 20 permit tcp any any eq 443 (18402 matches) [TLS 1.3 Traffic Permitted] 30 permit tcp any any eq 80 (4812 matches) 40 deny icmp any any echo log (524 matches) [Flood Mitigated] 50 deny ip any any log (38 matches) [Default Implicit Deny Rule] ──────────────────────────────────────────────────────────────────────── [✓] Packet Tracer Verification: 0 Unsanitized Ingress Leaks on Gi0/0
| Interface Port | Network Zone | Filter Applied | Traffic Processed | Firewall Decision |
|---|---|---|---|---|
| Gig0/0 (WAN) | Untrusted External | Extended ACL 101 | 24,810 Packets | INSPECTED & FILTERED |
| Gig0/1 (DMZ) | Public Web Services | Port 443 Only | 18,402 Packets | PERMITTED |
| Gig0/2 (LAN) | Corporate Users | 802.1X Port Security | 142 Probes | DENIED & QUARANTINED |