Complete Technical Paper Content — Automated Owasp Top 10 Web Scanner Project
Overview & System Context
Automated Owasp Top 10 Web Scanner Project: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9563 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background A Web application firewall (WAF) is a specific form of application firewall that filters, monitors, and blocks HTTP traffic to and from a web service. By inspecting HTTP traffic, it can prevent attacks exploiting a Web application's known vulnerabilities, such as SQL injection, cross-site scripting (XSS), file inclusion, and improper system configuration. Financial institutions often utilize WAFs to help in the mitigation of Web application zero-day vulnerabilities, as well as hard-to-patch bugs or weaknesses through custom attack signature strings.
Dedicated Web application firewalls entered the market in the late 1990s during a time when web server attacks were becoming more prevalent. Early WAF products, from Kavado and Gilian technologies, tried to solve the increasing amount of attacks on Web applications in the late 1990s. In 2002, the open-source project ModSecurity was formed in order to make WAF technology more accessible. They finalized a core rule set for protecting Web applications, based on OASIS Web Application Security Technical Committee’s (WAS TC) vulnerability work. In 2003, they expanded and standardized rules through the Open Web Application Security Project’s (OWASP) Top 10 List, an annual ranking for Web security vulnerabilities. This list would become the industry standard for Web application security compliance. Since then, the market has continued to grow and evolve, especially focusing on credit card fraud prevention. With the development of the Payment Card Industry Data Security Standard (PCI DSS), a standardization of control over cardholder data, security has become more regulated in this sector.
Application security (AppSec) includes all tasks that introduce a secure software development life cycle to development teams. Its final goal is to improve security practices and, through that, to find, fix and preferably prevent security issues within applications. It encompasses the whole application life cycle from requirements analysis, design, implementation, verification as well as maintenance. Web application security is a branch of information security that deals specifically with the security of websites, web applications, and web services. At a high level, web application security draws on the principles of application security but applies them specifically to the internet and web systems. The application security also concentrates on mobile apps and their security which includes iOS and Android Applications. Web Application Security Tools are specialized tools for working with HTTP traffic, e.g., Web application firewalls.
Design review. Before code is written the application's architecture and design can be reviewed for security problems. A common technique in this phase is the creation of a threat model. White-box testing, or code review. Critical examination of internal structure, architecture, design, etc. Black-box testing. Tests functionality rather than internal structure. Automated Tooling. Many security tools can be automated through inclusion into the development or testing environment. Examples of those are automated DAST/SAST tools that are integrated into code editor or CI/CD platforms. Coordinated vulnerability platforms. These are hacker-powered application security solutions offered by many websites and software developers by which individuals can receive recognition and compensation for reporting bugs.
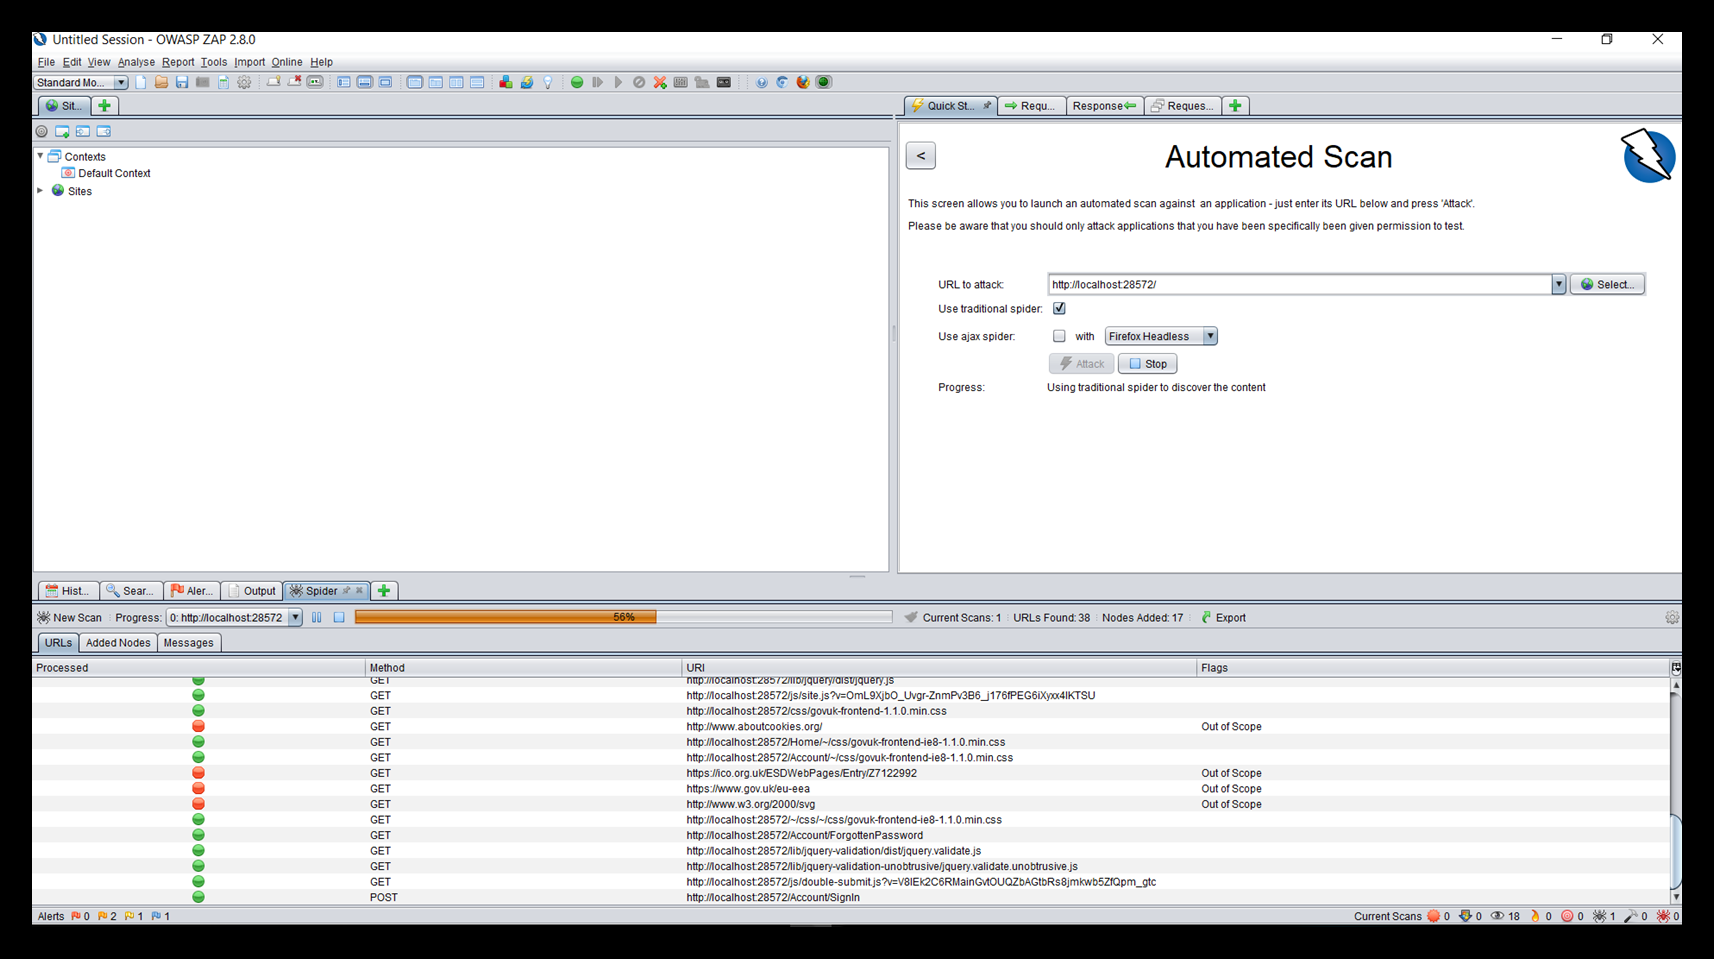
Figure 1: Using OWASP ZAP to find web app security vulnerabilities - Triad article Broken access control Cryptographic failures Injection Insecure design Security misconfiguration Vulnerable and outdated components Identification and authentification failures Software and data integrity failures Security logging and monitoring failures* Server-side request forgery (SSRF)* Implement access control Use cryptography the proper way Validate all input & handle exceptions Address security from the start Secure by default configurations Keep your components secure Implement digital identity Use browser security features Implement security logging and monitoring Stop server-side request forgery Static application security testing (SAST) analyzes source code for security vulnerabilities during an application's development. Compared to DAST, SAST can be utilized even before the application is in an executable state. As SAST has access to the full source code it is a white-box approach. This can yield more detailed results but can result in many false positives that need to be manually verified. Dynamic application security testing (DAST, often called vulnerability scanners) automatically detects vulnerabilities by crawling and analyzing websites. This method is highly scalable, easily integrated and quick. DAST tools are well suited for dealing with low-level attacks such as injection flaws but are not well suited to detect high-level flaws, e.g., logic or business logic flaws. Fuzzing tools are commonly used for input testing. Industry application security research highlights increasing risks related to insecure APIs, client-side code tampering, and runtime exploitation, reinforcing the importance of comprehensive dynamic and runtime security testing. Interactive application security testing (IAST) assesses applications from within using software instrumentation. This combines the strengths of both SAST and DAST methods as well as providing access to code, HTTP traffic, library information, backend connections and configuration information. Some IAST products require the application to be attacked, while others can be used during normal quality assurance testing. Runtime application self-protection augments existing applications to provide intrusion detection and prevention from within an application runtime. Dependency scanners (also called software composition analysis) try to detect the usage of software components with known vulnerabilities. These tools can either work on-demand, e.g., during the source code build process, or periodically.
In computing, SQL injection is a code injection technique used to attack data-driven applications, in which malicious SQL statements are inserted into an entry field for execution (e.g. to dump the database contents to the attacker). SQL injection must exploit a security vulnerability in an application's software, for example, when user input is either incorrectly filtered for string literal escape characters embedded in SQL statements or user input is not strongly typed and unexpectedly executed.
SQL injection is mostly known as an attack vector for websites but can be used to attack any type of SQL database. SQL injection attacks allow attackers to spoof identity, tamper with existing data, cause repudiation issues such as voiding transactions or changing balances, allow the complete disclosure of all data on the system, destroy the data or make it otherwise unavailable, and become administrators of the database server. Document-oriented NoSQL databases can also be affected by this security vulnerability. SQL injection remains a widely recognized security risk due to its potential to compromise sensitive data. The Open Web Application Security Project (OWASP) describes it as a vulnerability that occurs when applications construct database queries using unvalidated user input. Exploiting this flaw, attackers can execute unintended database commands, potentially accessing, modifying, or deleting data. OWASP outlines several mitigation strategies, including prepared statements, stored procedures, and input validation, to prevent user input from being misinterpreted as executable SQL code.
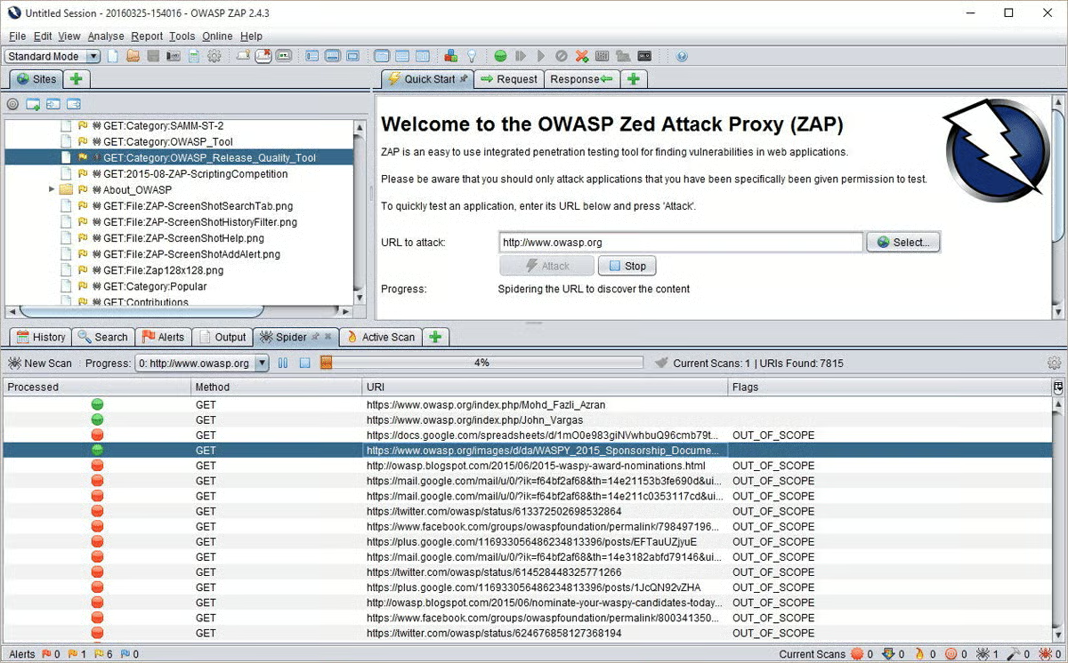
Figure 2: Top 7 Website & Application Vulnerability Scanners SQL injection is a common security vulnerability that arises from letting attacker-supplied data become SQL code. This happens when programmers assemble SQL queries either by string interpolation or by concatenating SQL commands with user supplied data. Therefore, injection relies on the fact that SQL statements consist of both data used by the SQL statement and commands that control how the SQL statement is executed. For example, in the SQL statement select * from person where name = 'susan' and age = 2 the string 'susan' is data and the fragment and age = 2 is an example of a command (the value 2 is also data in this example). SQL injection occurs when specially crafted user input is processed by the receiving program in a way that allows the input to exit a data context and enter a command context. This allows the attacker to alter the structure of the SQL statement which is executed. As a simple example, imagine that the data 'susan' in the above statement was provided by user input. The user entered the string 'susan' (without the apostrophes) in a web form text entry field, and the program used string concatenation statements to form the above SQL statement from the three fragments select * from person where name=', the user input of 'susan', and ' and age = 2. Now imagine that instead of entering 'susan' the attacker entered ' or 1=1; --. The program will use the same string concatenation approach with the 3 fragments of select * from person where name=', the user input of ' or 1=1; --, and ' and age = 2 and construct the statement select * from person where name='' or 1=1; --' and age = 2. Many databases will ignore the text after the '--' string as this denotes a comment. The structure of the SQL command is now select * from person where name='' or 1=1; and this will select all person rows rather than just those named 'susan' whose age is 2. The attacker has managed to craft a data string which exits the data context and entered a command context.
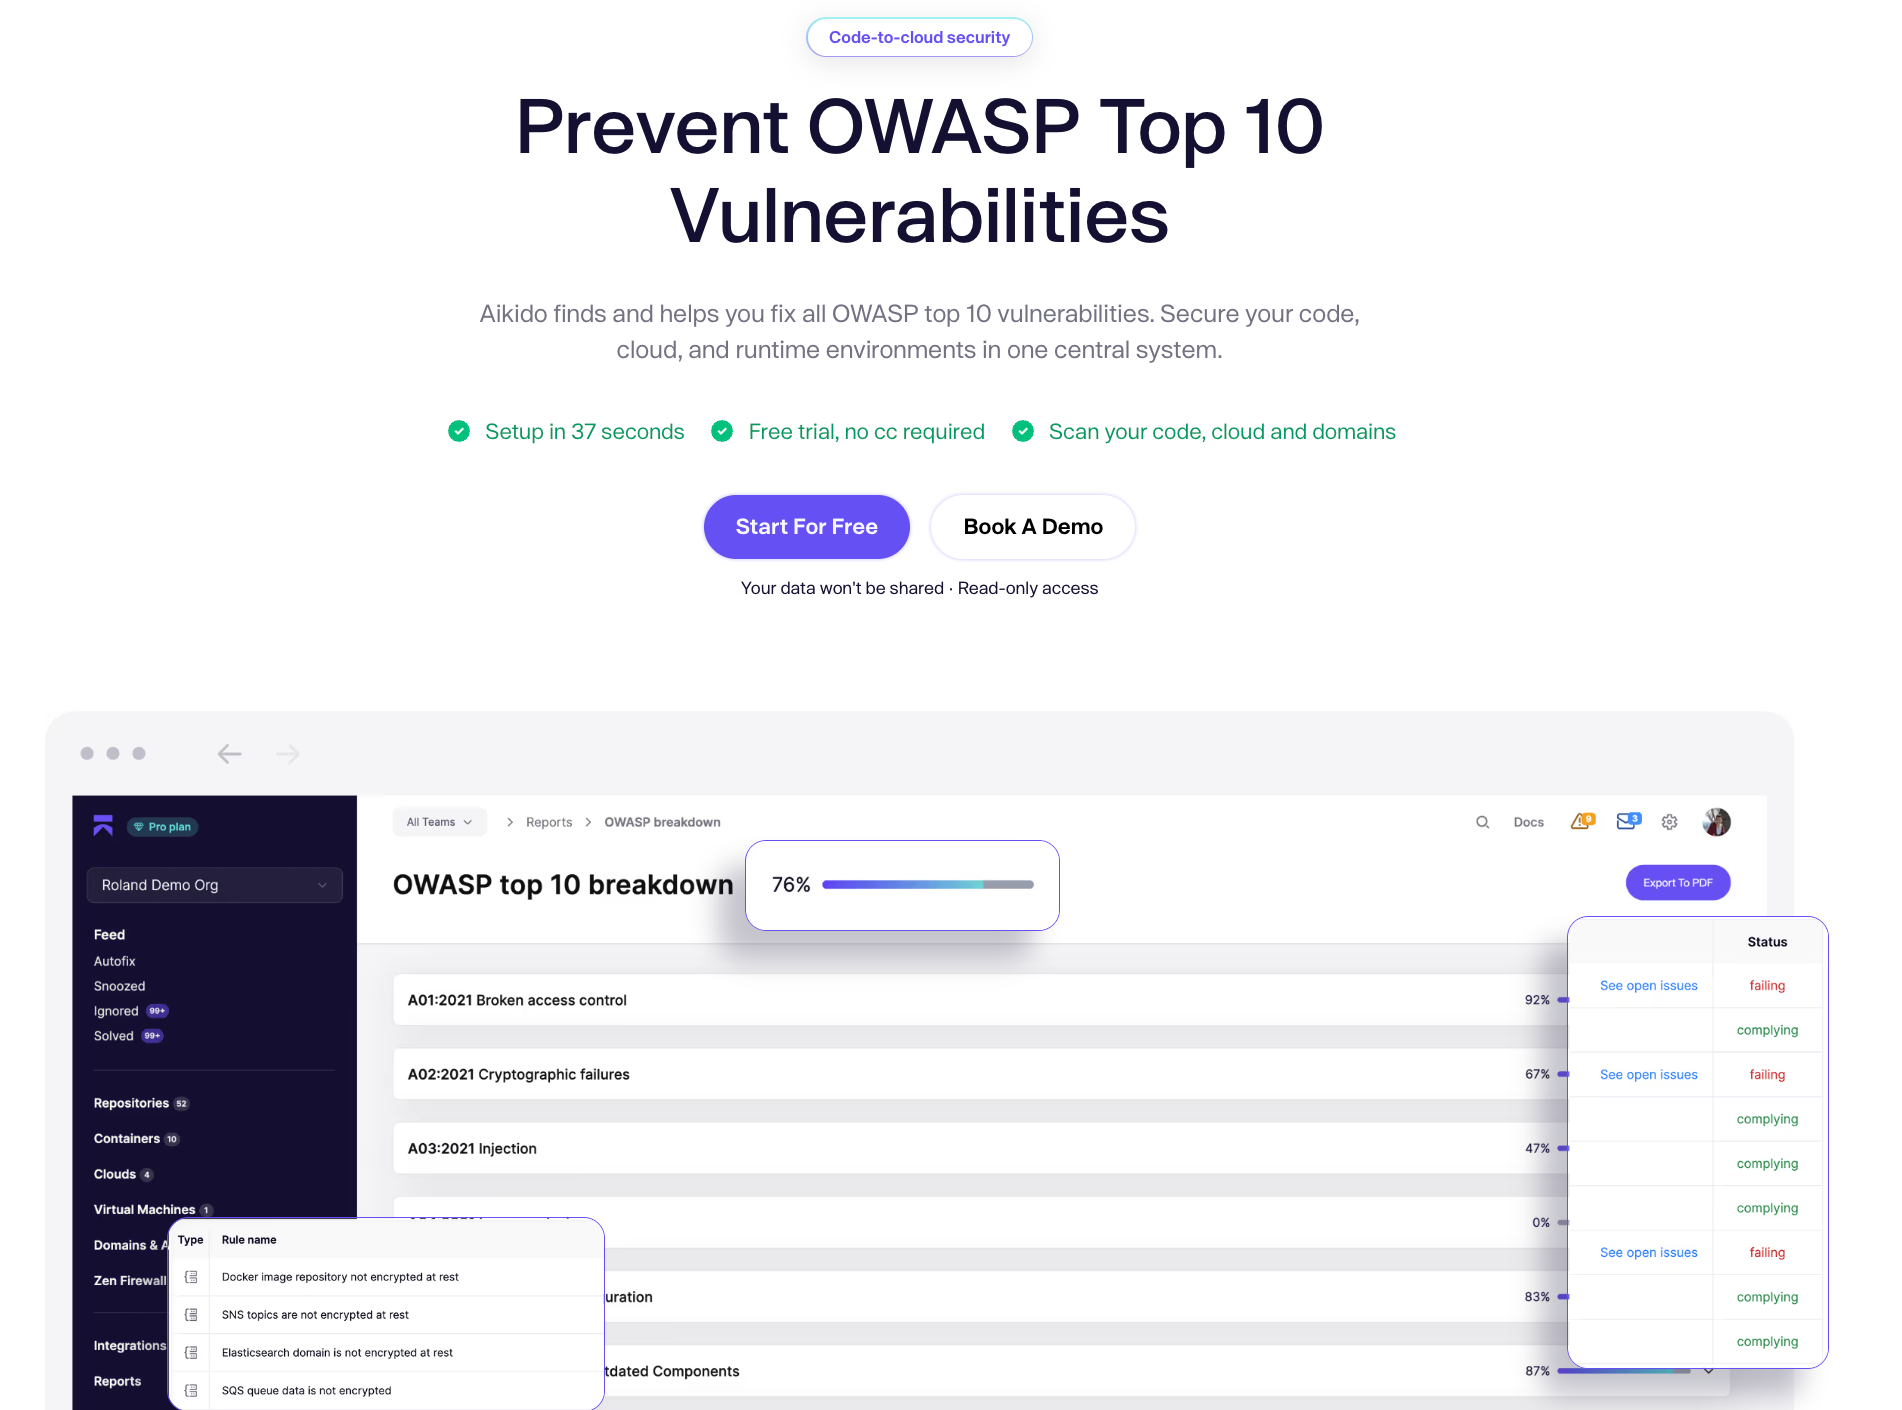
' OR '1'='1 or using comments to even block the rest of the query (there are three types of SQL comments). All three lines have a space at the end: ' OR '1'='1' -- ' OR '1'='1' { ' OR '1'='1' /* renders one of the following SQL statements by the parent language: If this code were to be used in authentication procedure then this example could be used to force the selection of every data field (*) from all users rather than from one specific user name as the coder intended, because the evaluation of '1'='1' is always true. The following value of "userName" in the statement below would cause the deletion of the "users" table as well as the selection of all data from the "userinfo" table (in essence revealing the information of every user), using an API that allows multiple statements: a';DROP TABLE users; SELECT * FROM userinfo WHERE 't' = 't This input renders the final SQL statement as follows and specified: Figure 3: Best OWASP Scanners in 2026 for Web App Security While most SQL server implementations allow multiple statements to be executed with one call in this way, some SQL APIs such as PHP's mysql_query() function do not allow this for security reasons. This prevents attackers from injecting entirely separate queries, but doesn't stop them from modifying queries.
from which it would populate the review page with data from the review with ID 5, stored in the table bookreviews. The query happens completely on the server; the user does not know the names of the database, table, or fields, nor does the user know the query string. The user only sees that the above URL returns a book review. A hacker can load the URLs https://books.example.com/review?id=5' OR '1'='1 and https://books.example.com/review?id=5' AND '1'='2, which may result in queries respectively. If the original review loads with the "1=1" URL and a blank or error page is returned from the "1=2" URL, and the returned page has not been created to alert the user the input is invalid, or in other words, has been caught by an input test script, the site is likely vulnerable to an SQL injection attack as the query will likely have passed through successfully in both cases. The hacker may proceed with this query string designed to reveal the version number of MySQL running on the server: https://books.example.com/review?id=5 AND substring(@@version, 1, INSTR(@@version, '.') - 1)=4, which would show the book review on a server running MySQL 4 and a blank or error page otherwise. The hacker can continue to use code within query strings to achieve their goal directly, or to glean more information from the server in hopes of discovering another avenue of attack.
Most development platforms support parameterized statements, also known as placeholders or bind variables, to securely handle user input instead of embedding it in SQL queries. These placeholders store only values of a defined type, preventing input from altering the query structure. As a result, SQL injection attempts are processed as unexpected input rather than executable code. With parametrized queries, SQL code remains separate from user input, and each parameter is passed as a distinct value, preventing it from being interpreted as part of the SQL statement.
Besides, not every piece of data can be added to SQL as a string literal (MySQL's LIMIT clause arguments or table/column names for example) and in this case escaping string-related special characters will do no good whatsoever, leaving resulting SQL open to injections. ZAPping the OWASP Top 10 (2021) - a guide mapping Top 10 items to ZAP functionality that can assist IT security personnel Authentication Decision Tree - the best place to start if you need ZAP to authenticate to your app Some links in this article may be affiliate links. We may earn a commission if you purchase through them, at no extra cost to you.
Most teams know they should be scanning for security vulnerabilities. Few have a pipeline that actually covers the OWASP Top 10 end-to-end. This guide walks through building an automated security scanning pipeline from scratch âII tool selection, scan orchestration, finding triage, and CI/CD integration. No theory. Just the architecture that works. An effective security scanning pipeline has four layers, each running at a different point in the development lifecycle: Each layer catches different vulnerability classes. No single layer covers everything. The pipeline's strength comes from layering âII what static analysis misses, dynamic scanning catches. What dynamic scanning misses, configuration auditing catches.
Static analysis runs on every pull request before code is merged. It catches issues that are visible in source code without running the application.
Implementation
Add as a required check on pull requests. The scan should block merge if it finds high-severity issues (hardcoded secrets, SQL injection patterns). Medium-severity issues (missing input validation) should warn but not block. OWASP coverage: A02 (hardcoded keys), A03 (injection patterns in code), A05 (insecure defaults). Key principle: Static analysis has the highest false positive rate of any layer. Tune your rules aggressively âII a noisy scanner that developers ignore is worse than no scanner at all. Start with 5-10 high-confidence rules and expand gradually.
Implementation Synonym
Dependency scanning checks your third-party libraries against known vulnerability databases. It runs on every PR (to catch new vulnerable dependencies) and daily (to catch newly disclosed CVEs in existing dependencies).
Implementation Meaning
Trivy is the most versatile option âII it scans npm, pip, Go modules, container images, and OS packages with a single tool. Run it in CI on every PR and as a daily cron job against your deployed images. OWASP coverage: A06 (Vulnerable and Outdated Components) âII this is the primary layer for A06. Key principle: Not every CVE is exploitable in your context. A vulnerability in a function you never call is low risk. Prioritize CVEs that affect code paths your application actually uses. Trivy's --ignore-unfixed flag filters out CVEs with no available patch âII useful for reducing noise.
Implementation Science
Dynamic scanning tests the running application by sending requests and analyzing responses. This is where you catch runtime vulnerabilities that static analysis can't see âII XSS, SQL injection, SSRF, authentication flaws, and access control issues.
Implementation Specialist
Run dynamic scans against your staging environment after every deployment. Use ZAP for broad coverage (spider + active scan), Nuclei for known vulnerability templates, and SecurityClaw for targeted OWASP skill checks. Don't run active injection scans (XSS, SQLi, SSRF) against production without explicit approval. OWASP coverage: A01 (access control), A03 (injection), A04 (insecure design), A07 (auth failures), A10 (SSRF).
Implementation Definition
Key principle: Dynamic scanning is slow. A full ZAP active scan can take hours. Run a fast baseline scan (passive + spider) on every deploy, and a full active scan on a weekly schedule. This balances coverage with pipeline speed. 2. System Architecture & Core Working Principles Configuration auditing checks the deployed infrastructure for security misconfigurations âII TLS settings, HTTP headers, exposed services, and cloud resource policies. It runs continuously because configurations can change independently of code deployments.
Implementation Manager
Run SecurityClaw's tls-crypto-auditor, security-header-checker, and apigw-cors-tester on a daily cron. Use Mozilla Observatory for a quick external check. For cloud configuration, use AWS Config rules, Azure Policy, or GCP Organization Policy. Key principle: Configuration drift is real. A TLS configuration that was correct last month may be insecure today if a certificate expired or a load balancer was reconfigured. Continuous auditing catches drift that point-in-time scans miss.
Implementation Consultant
Running 4 layers of scanning generates a lot of data. Orchestration is how you manage it without drowning in findings. Result aggregation: All scan results should flow into a single dashboard or issue tracker. Don't make developers check 4 different tools for findings. Options: DefectDojo (open source), GitHub Security tab (if using GitHub Advanced Security), or a custom aggregation script that creates issues from scan output.
Implementation Intentions
Deduplication: Multiple tools will find the same issue. A missing CSP header will be flagged by ZAP, SecurityClaw, and Mozilla Observatory. Deduplicate by (URL + finding type + severity) before creating issues. The hardest part of security scanning isn't running the scans âII it's triaging the results. A typical first scan of a web application produces hundreds of findings. Most are low severity, many are false positives, and a few are critical.
Implementation Engineers
False positive management: Every scanner produces false positives. The key is to have a documented process for marking findings as false positives so they don't reappear in future scans. Most tools support suppression files or baseline configurations. Maintain these as code alongside your application. Pattern 1: Gate (blocking) âII The scan runs as a required check. If it finds issues above a severity threshold, the pipeline fails and the deployment is blocked. Best for: Layer 1 (secrets) and Layer 2 (critical CVEs).
Pattern 2: Report (non-blocking) âII The scan runs and posts results as a comment or dashboard update, but doesn't block the pipeline. Best for: Layer 3 (dynamic scanning) and Layer 4 (config auditing), where false positives are common and blocking would slow development. Pattern 3: Async (scheduled) âII The scan runs on a schedule (daily, weekly) independent of deployments. Results are aggregated and triaged separately. Best for: Full active scans (Layer 3) and continuous monitoring (Layer 4).
Most teams use a combination: Gate for secrets and critical CVEs, Report for dynamic baseline scans, and Async for full active scans. Every OWASP category is covered by at least one layer. Most are covered by two or three. This redundancy is intentional âII different layers catch different manifestations of the same vulnerability class.
1. Scanning production with active injection tests. XSS probes, SQL injection payloads, and SSRF attempts can break production applications. Always run active scans against staging or a dedicated security testing environment. 2. Blocking CI/CD on every finding. If your pipeline fails on every medium-severity finding, developers will either disable the scanner or stop caring about the results. Block only on critical and high severity. Report everything else.
3. Running scans without triaging results. A scan that produces 500 findings and no one looks at them is worse than no scan âII it creates a false sense of security. Assign ownership for triage. If no one is triaging, reduce scan scope until someone is. 4. Scanning only at deploy time. New CVEs are disclosed daily. A dependency that was safe yesterday may have a critical CVE today. Run dependency scans on a daily schedule, not just at deploy time.
5. Not maintaining false positive suppressions. Every scanner produces false positives. If you don't maintain a suppression file, the same false positives will appear in every scan, burying real findings in noise. Treat suppression files as code âII review them, version them, and audit them periodically. A security scanning pipeline isn't a single tool âII it's four layers working together. Static analysis catches code-level issues before merge. Dependency scanning catches known CVEs in libraries. Dynamic scanning catches runtime vulnerabilities in the running application. Configuration auditing catches infrastructure misconfigurations continuously.
Start with Layer 1 (secrets scanning) and Layer 2 (dependency scanning) âII they're the easiest to implement and have the lowest false positive rate. Add Layer 3 (dynamic scanning) once you have a staging environment. Add Layer 4 (config auditing) once you're deploying to production. The goal isn't zero findings âII it's a process that catches critical issues before they reach production and gives your team a clear path to fix everything else. Build the pipeline, triage the results, and iterate.
This project is an automated DevSecOps security lab that simulates a secure development lifecylce. It integrates: CI/CD pipeline enforcement (GitHub Actions) to identify and respond to security risks automatically. Enforces policy thresholds and automatically triggers build failures, GitHub issues, and alerting when risks are detected - bringing real-world security maturity to automated development pipelines [+] Bandit scans Python code for Security vulnerabilities like hardcoded passwords, unsafe functions, etc. [+] ZAP performs Active scanning for OWASP Top 10 issues (XSS, Injection, etc...) [+] CI/CD Workflow (GitHub Actions) Automated web application security lab performing OWASP Top 10 vulnerability scanning, secure coding remediation, and CI/CD pipeline integration for DevSecOps workflows Previous versions are available at OWASP Top 10 2021 and OWASP Top 10 2017 (PDF) . Older versions are available in the GitHub repo .
The OWASP Top 10 is a standard awareness document for developers and web application security. It represents a broad consensus about the most critical security risks to web applications. Companies should adopt this document and start the process of ensuring that their web applications minimize these risks. Using the OWASP Top 10 is perhaps the most effective first step towards changing the software development culture within your organization into one that produces more secure code.
TL;DR: Automated scanners are strong on the OWASP Top 10 categories that leave observable evidence: security misconfiguration, cryptographic failures, vulnerable components, and most injection classes. They are weaker where the flaw lives in business logic, such as broken access control and insecure design, which still require manual testing. Knowing which is which tells you exactly what a scan report covers and where a human tester needs to pick up.
The OWASP Top 10 is the most widely used shorthand for web application risk, and most write-ups explain what each category means and why it made the list. If you want that grounding, Byte Optimizer publishes a general OWASP Top 10 explainer that walks through the categories and how the list has evolved. This post takes a different angle. For each category, it asks one question: how well can an automated scanner detect it from the outside? The answer matters because it defines what a clean scan report actually proves. A scanner that reports "no findings" is not saying "no vulnerabilities." It is saying "no vulnerabilities of the kinds a scanner can see." Those are different statements, and confusing them is one of the most common mistakes in application security programs.
An external scanner works with the same raw material an attacker starts with: HTTP responses, headers, TLS handshakes, DNS records, and the way endpoints behave when probed. OnScanner, for example, runs live, never-cached scans against the real target, either unauthenticated (the anonymous attacker's view) or authenticated (the logged-in surface), and verifies selected findings with safe, non-destructive, in-band active checks. The full detection approach is documented on the methodology page .
What a scanner cannot observe is intent. It does not know which user should see which record, what a business workflow is supposed to allow, or what your internal logs capture. Each category's detectability follows directly from that boundary. The table is the summary; the sections below explain the reasoning behind the ratings. 3. Software Implementation, Frameworks & Protocols A02, cryptographic failures, and A05, security misconfiguration, are the scanner's home turf. Whether TLS 1.0 is still enabled, whether HSTS is present, whether a certificate has expired, whether a Content-Security-Policy exists, whether a server banner leaks a version: these are objective facts, observable in every response or handshake, with essentially no ambiguity. A scanner can check them on every run, at any frequency, without any risk to the target.
A06, vulnerable and outdated components, is almost purpose-built for automation. A scanner fingerprints products and versions, matches them against CVE databases, and attaches exploitation context such as EPSS scores and CISA KEV listings, which are covered in depth in EPSS and KEV explained . Automation also does something here that no human team can: re-checking the entire surface on a schedule as new CVEs are published against software you already run.
A03, injection, is more nuanced but still favorable. Error-based SQL injection, reflected cross-site scripting, and template injection produce discriminating markers that a scanner can safely elicit and read back. Blind and time-based variants are detectable through response timing. What automation tends to miss are second-order cases, where a stored payload only surfaces later in a different context, such as an internal admin panel the scanner never sees.
A01, broken access control, is the honest disappointment. It sits at the top of the OWASP list, and a scanner can only see part of it. The observable subset is real and worth catching: admin consoles reachable without login, directory listing, unsafe HTTP methods, exposed configuration files, open redirects. But the core of the category is authorization logic: can user A read user B's invoice by changing an ID in the URL? Answering that requires knowing what the application is supposed to allow, which is intent, not evidence. Authorization testing needs a human with two accounts and a hypothesis.
A04, insecure design, is by definition about controls that were never built. Automation can flag design smells that show up externally, like a login endpoint that accepts unlimited attempts or a password reset flow that confirms whether an account exists. It cannot evaluate whether a checkout flow can be abused, whether a trust boundary sits in the wrong place, or whether a threat model was ever written. Design review is a whiteboard activity, not a network activity.
A09, security logging and monitoring failures, is mostly invisible from outside. A scanner can check the disclosure hygiene that correlates with it: verbose stack traces, a missing security.txt file, a robots.txt that maps out sensitive paths. Whether you actually log authentication failures, and whether anyone reads those logs before an incident, cannot be observed from the network.
A07 and A10 sit in between. Authentication failures have detectable symptoms (login forms served over HTTP, weak token handling) while credential-lifecycle logic needs manual review. SSRF can be confirmed automatically when a URL-fetching parameter responds to an in-band probe, but chained SSRF paths deep inside application logic usually take a human to find. Automated scanning provides breadth, frequency, and consistency. Every header, TLS setting, exposed path, and known CVE gets checked identically on every run, and scheduled monitoring catches drift the day it happens rather than at the next annual test. If you are setting up this layer for the first time, start with how to scan a website for vulnerabilities .
Manual testing provides depth on exactly the rows marked Partial and Limited: authorization matrices, workflow abuse, chained attacks that combine several low-severity findings into one real breach path. That work is a different discipline, and it is what a manual penetration test is for. The mistake to avoid is treating either one as a substitute for the other. A yearly pentest with nothing in between leaves eleven months of unmonitored drift. Continuous scanning with no manual testing leaves the top category on the list only partially covered. The strongest programs run both and let each do what it is structurally good at.
It can produce findings in every category, but depth varies sharply. Misconfiguration, cryptographic failures, vulnerable components, and injection are covered well because they leave observable evidence in responses and handshakes. Broken access control, insecure design, and logging failures are only partially observable from outside, so a scanner covers their externally visible symptoms while the underlying logic flaws require manual testing.
Broken access control and insecure design benefit most. Both depend on understanding what the application is supposed to allow, which cannot be inferred from responses alone. A tester with multiple accounts can systematically probe authorization boundaries, abuse business workflows, and chain low-severity findings into realistic attack paths. Logging and monitoring gaps also need internal review, since external scanning only sees their surface symptoms.
No. A clean report means the scanner found no issues in the classes it can observe: configuration, transport security, known-vulnerable components, and injectable inputs. It says little about authorization logic, workflow abuse, or design gaps. Treat a clean scan as a strong baseline that rules out the most common attack paths, and schedule manual testing for the categories that remain.
OnScanner runs live, never-cached security and privacy scans in minutes: OWASP Top 10, CVE intelligence with EPSS and KEV context, 40+ privacy checks, and monitoring, with a REST API and MCP server. The Automation Framework is the best way to automate ZAP for most people. It allows you to control ZAP via one YAML file and provides more flexibility while not being tied to any specific container technology.
The Automation Framework is included with the latest version of ZAP as well as the stable docker image. The framework is plugable and many of the existing add-ons have been enhanced to support it. For details of how to get started with the framework see the main framework help page . The addOns job has been found to cause problems when updating add-ons which are defined in the current plan. This job has been depreciated and no longer does anything.
The framework will exit with 2 if there are warnings even if the environment failOnWarning parameter is set to false . An OWASP scanner — specifically an OWASP Top 10 scanner — is a security tool that probes a running web application for the classes of weakness named in the OWASP Top 10 (broken access control, injection, security misconfiguration, and so on) and reports findings mapped back to those categories. The "OWASP Top 10" part is the differentiator. A generic vulnerability scanner spits out a flat list of issues; an OWASP-aware scanner organizes the same results into the categories your auditors, your PCI assessor, and your own backlog already speak in.
No single OWASP scanner covers all ten categories well, and a couple can't really be scanned at all. The practical goal isn't to find one magic tool; it's to assemble automated coverage where automation works and know exactly where you still have to test by hand. That's what the rest of this guide lays out: how to test OWASP Top 10 coverage on your own app, category by category.
If you're not yet clear on what each category actually means , read our companion guide OWASP Top 10 web vulnerabilities explained first — this article assumes you know what A01 through A10 are and focuses on how to test for them. Because it's the most widely used baseline for web application security, and almost everyone downstream of you already uses it as the common vocabulary.
The Top 10 is referenced as a benchmark by major compliance and governance frameworks. PCI DSS expects web applications to be protected against the kinds of flaws it enumerates; ISO 27001 programs routinely point to it when defining secure-development and vulnerability-management controls. When an assessor asks "how do you ensure your app isn't vulnerable to injection or broken access control," answering in OWASP categories is the answer they're expecting.
There's a practical reason too. The Top 10 is a prioritization , not an exhaustive checklist — these are the failure modes that show up most often and hurt most when they do. Testing against it means spending your first hours on the issues most likely to be present, rather than chasing exotic bugs while an unauthenticated IDOR sits in your API. So OWASP vulnerability scanning means two things: get coverage across all ten categories, and report findings in those categories so results plug straight into compliance evidence and your remediation workflow.
For each category below: what to test, how far automation gets you, what stays manual, and which tool fits. Treat it as a coverage map — most categories are scanner-friendly, two (A04, A08) are weak spots for any scanner. What to test. Whether a user can reach data or actions they shouldn't: change /invoice/1001 to /invoice/1002 and see someone else's invoice (IDOR), hit an admin endpoint as a regular user (privilege escalation), or reach /admin directly without a link (forced browsing). Open redirect flaws also live near this category and overlap with A10. (If those terms aren't familiar, the OWASP Top 10 web vulnerabilities guide defines them.) Automated test. A scanner can spider the app, hammer object IDs, and flag missing authorization — but only if it's authenticated with valid sessions for at least two roles, so it can detect that role A reaches role B's data.
Manual test. Authorization logic is business-specific, so the highest-value testing is manual: capture a request as a privileged account, replay it as an unprivileged one, confirm it's rejected. Repeat across sensitive actions. Tool. ZAP (authenticated, multiple user contexts) for discovery; Burp/ZAP for manual replay; Exploita verifies each finding with a working proof-of-concept before reporting, cutting the "is this real?" noise that plagues access-control scanning.
What to test. The testable surface is mostly transport: outdated TLS versions, deprecated TLS 1.0 , weak cipher suites , missing HSTS, and sensitive data sent over plain HTTP. Automated test. TLS configuration is highly automatable — a scanner enumerates supported protocols and ciphers and flags anything obsolete. A quick manual check: If that handshake succeeds, TLS 1.0 is still enabled and should be turned off. Note that recent OpenSSL builds often disable TLS 1.0/1.1 in the client, so a failed handshake here doesn't by itself prove the server has it off — confirm with nmap --script ssl-enum-ciphers -p 443 example.com , which reports the server's actual supported protocols and ciphers.
Manual test. At-rest encryption, key management, and whether sensitive fields are encrypted in the database aren't visible from outside — they need code and architecture review. 4. Practical Deployment, Analysis & Case Studies Tool. openssl / nmap ssl-enum-ciphers or a generic SSL/TLS testing tool for transport; the linked glossary entries explain exactly what to remediate.
What to test. Untrusted input reaching an interpreter — SQL injection, command injection, LDAP injection, and cross-site scripting (XSS, injection into the browser; merged into A03 in the 2021 revision). This is the category DAST tools were built for. Automated test. Strong. A scanner fuzzes every parameter, header, and form field with injection payloads and watches for error signatures, time delays (blind SQLi), or reflected scripts.
Manual test. Stored/second-order injection (payload saved now, executed later) and injection behind complex multi-step flows often slip past automated crawlers — worth a manual pass on anything that persists user input. Tool. SQLMap for SQLi depth, ZAP active scan for breadth, Nuclei for known patterns; Exploita exercises these injection points dynamically.
What to test. Flaws in the design itself — missing rate limiting on a password reset, a logic loop that lets you buy an item for a negative quantity, trust boundaries that were never drawn. Be honest: scanners are weak here. Insecure design is the absence of a control that should have existed. A scanner has no model of what your app is supposed to do, so it can't tell a missing control is missing. This category needs threat modeling and manual design review ; the most a scanner contributes is catching downstream symptoms (e.g., missing rate limiting showing up as brute-forceability). Don't let a clean scan create false confidence.
What to test. Defaults and deployment mistakes: missing security headers, directory listing left enabled, verbose error pages leaking stack traces, clickjacking from absent X-Frame-Options /CSP, mixed content , default credentials, and exposed admin panels. Automated test. Very automatable and a great quick win. Start with our free security headers checker — it flags missing or weak headers (CSP, HSTS, X-Frame-Options ) in seconds.
Manual test. Confirm default accounts are removed, error verbosity is dialed down in production, and admin interfaces are network-restricted. Tool. The headers checker for headers; ZAP and Nuclei for directory listing, default files, and exposed panels. Ready to see where your app stands? Run a free OWASP Top 10 scan with Exploita — it maps every finding to its OWASP category and ships a verified proof-of-concept so you're not triaging guesses.
What to test. Known-vulnerable libraries, frameworks, plugins, and server software — an old jQuery, an unpatched CMS, a web server with a public CVE. Automated test. Strong, and this is where CVE-aware scanning earns its keep. The scanner fingerprints observable components (response headers, JS libraries, framework signatures, CMS markers) and cross-references CVE databases. For dependencies you control, a Software Composition Analysis (SCA) tool reading your lockfiles catches more, since not every component is detectable from outside.
Manual test. Maintain an inventory of what you ship and reconcile it with what the scanner sees — external fingerprinting misses internal and transitive dependencies. Tool. Nuclei (large CVE template library), SCA for dependencies; Exploita runs CVE checks on every scan and maps confirmed component vulnerabilities to A06.
What to test. Weak login defenses: no protection against credential stuffing or brute force, weak password policy, predictable or non-rotating session tokens, session fixation, broken password-reset flows. Manual test. Multi-factor logic, account-recovery edge cases, and the full session lifecycle need a human walking the flows with a proxy.
What to test. Trusting code or data that hasn't been verified — unsigned updates, an insecure CI/CD pipeline, deserialization of untrusted data, third-party scripts loaded without Subresource Integrity (SRI). Be honest: mostly out of scope for scanners. A DAST scanner can sometimes spot missing SRI or a deserialization endpoint, but the heart of this category — your build pipeline, signing, and update mechanisms — lives in infrastructure and process, not the app's HTTP surface. Cover it with pipeline hardening, dependency-integrity controls, and review; treat any scanner signal as a bonus, not coverage.
What to test. Whether attacks are detected and recorded — are failed logins logged, do alerts fire, is there an audit trail for sensitive actions? Automated test. Essentially none from the outside. By definition this is about what happens inside your systems, which an external scanner can't observe.
Manual test. Run a controlled attack (a burst of failed logins, an injection attempt), then check your logs and alerting. If nothing showed up, that's the finding — and skipping this check is itself the most common A09 failure. What to test. Whether the server can be tricked into making requests on the attacker's behalf — any feature that fetches a URL (webhooks, image-from-URL, PDF generators, link previews) pointed at internal addresses like 169.254.169.254 (cloud metadata) or localhost .
Automated test. Good and improving. Scanners inject internal/callback URLs into fetch-style parameters and watch for out-of-band callbacks or response differences. ZAP and Nuclei both have SSRF detection. Manual test. SSRF often hides in non-obvious parameters and parsers; manually testing every URL-accepting input with internal targets and a callback server catches what crawlers miss.
Tool. ZAP/Nuclei with an interaction server; Exploita confirms SSRF with a proof-of-concept rather than reporting a maybe. The scanner question is which engine carries the automatable load — open-source OWASP testing tools you run yourself versus a hosted scanner. OWASP ZAP is the default open-source DAST tool: free, actively maintained, with authentication and scripting support and reports you can map to OWASP categories. The cost is operational — you configure contexts and policies and triage results yourself, and ZAP can be noisy, so budget time for false-positive validation.
Nuclei is template-driven and excellent for known patterns (CVEs, misconfigurations, exposed files). Fast and low-noise because each template encodes a deterministic check; the flip side is it finds what its templates describe, not novel injection or access-control logic. It pairs well with ZAP rather than replacing it. Wapiti is a lighter open-source scanner — straightforward black-box crawling and injection testing, easy to run in CI, but with a smaller feature set than ZAP. Useful as a quick gate, not a complete program.
SaaS / hosted scanners trade control for convenience: no infrastructure or policies to manage, usually stronger reporting and triage, and good ones de-duplicate and prioritize. The questions to ask: what's the OWASP category coverage, does the report map findings to OWASP out of the box, what's the false-positive rate, and does it verify findings or just flag potential ones? That last point is where unverified findings cost the most engineering time. Exploita runs DAST plus CVE checks, maps every result to its OWASP Top 10 category, and verifies each finding with a working proof-of-concept before it reaches your report — so a reported SQL injection or SSRF comes with evidence that it actually fires, not a "potential" you have to reproduce yourself. Full scans typically complete in around 12 minutes, and it's free to start.
No automated OWASP scanner — open source or hosted — covers A04, A08, or A09 meaningfully. Choose an engine for the eight categories where automation works and schedule manual review for the rest. For how dynamic scanning differs from static analysis, see DAST vs SAST . You can stand up meaningful OWASP Top 10 testing today with free tools — here are the four that give the most coverage per minute.
5. Performance Evaluation & Extended Technical Observations That alone gives you injection, misconfiguration, and SSRF coverage. Configure authentication contexts to extend it toward access-control testing. 2. Zero-setup online scan. If you don't want to install anything, run a free OWASP Top 10 scan with Exploita — point it at a URL and get OWASP-categorized, proof-verified findings. Good as a fast baseline alongside ZAP, or as your main scan if you'd rather not operate tooling.
3. Security headers (A05) in seconds. Run the free security headers checker to catch missing CSP, HSTS, and X-Frame-Options . It's the fastest single check here and clears a real chunk of A05. 4. SSL/TLS (A02). Test transport security with openssl s_client , nmap --script ssl-enum-ciphers , or a generic SSL/TLS testing tool. The glossary entries on weak cipher suites and deprecated TLS 1.0 explain the remediation.
For a structured walkthrough of turning raw findings into a prioritized remediation plan, see website vulnerability assessment . For the broader program this fits into, our pillar guide on web application security testing covers how scanning, manual testing, and process come together — and how to scan a website for vulnerabilities is a good starting point if you're new to running scans.
When you're ready, lean on a capable OWASP scanner to do the automatable work: run a free OWASP Top 10 scan with Exploita — DAST plus CVE checks, every finding mapped to its OWASP category and verified with a proof-of-concept, in about 12 minutes. Pair it with the free security headers checker for an instant A05 read. What are the best free OWASP Top 10 scanners? OWASP ZAP is the leading free DAST tool and the natural starting point — it covers injection, misconfiguration, and SSRF well and supports authenticated scanning. Pair it with Nuclei for CVE and known-pattern coverage (A06), the free security headers checker for A05, and openssl or nmap ssl-enum-ciphers for TLS (A02). Exploita offers a free zero-setup online scan that maps findings to OWASP categories and verifies each with a proof-of-concept. No single free tool covers all ten categories, so combine a few and reserve A04, A08, and A09 for manual review.
Is OWASP ZAP enough for a production app? ZAP is a strong, free DAST engine, but on its own it isn't a complete OWASP program for production. It needs careful authentication setup to test access control (A01) and auth failures (A07), it can be noisy with false positives that require validation, and it can't meaningfully cover insecure design (A04), integrity failures (A08), or logging and monitoring (A09). For production, supplement ZAP with CVE-aware scanning, manual review of the design and auth flows, and a tool that verifies findings so you're not triaging false positives by hand.
How long does a full OWASP Top 10 scan take? It depends on the size of the app and the tool. A thorough OWASP ZAP active scan on a non-trivial application can run from tens of minutes to several hours, especially with authenticated crawling. Hosted scanners are usually faster because they parallelize and tune the scan — an Exploita scan typically completes in around 12 minutes. Manual testing for A01, A04, A08, and A09 takes additional, separate time and isn't captured in the automated scan duration.
Should I run an OWASP scan in production or staging? Scan staging when you can — active scanning sends real attack payloads, which can create junk data, trigger side effects, or stress the system. Use a staging environment that mirrors production configuration so the results are representative. Some checks (like TLS and security headers, or read-only checks) are safe to run against production. If you must active-scan production, do it in a maintenance window, exclude destructive endpoints, and notify your team so the traffic isn't mistaken for a real attack.
OWASP ZAP just became a harder tool to ignore. The project shipped version 2.17.0 in December 2025, bumped its Java floor to version 17, added first-pass JWT support, and spent the first half of 2026 wiring its scan rules directly into the new OWASP Top 10:2025 categories. For a tool that costs nothing and runs the same in a laptop terminal as it does in a GitHub Actions pipeline, that is a meaningful upgrade cycle. This tutorial walks through installing OWASP ZAP 2.17.0, running your first scans, automating them with YAML, wiring them into CI/CD, and avoiding the mistakes that get teams flooded with false positives or, worse, banned from a target’s network for scanning without permission.
By the end you will have a working OWASP ZAP setup that runs locally, in Docker, and inside a GitHub Actions workflow, plus a repeatable automation framework plan you can drop into any web project. Most application security programs lean on three overlapping tool categories: static analysis (SAST) that reads source code without running it, software composition analysis (SCA) that checks dependencies for known vulnerabilities, and dynamic analysis (DAST) that actually attacks a running application the way a real attacker would. OWASP ZAP sits squarely in that third category, and it is the only one of the three that catches issues only visible at runtime, things like misconfigured security headers, session handling bugs, and access control failures that only show up once a request actually hits a live server. That makes an OWASP ZAP setup a natural complement to whatever static scanning already runs in your pipeline, not a replacement for it.
Add Tech Insider once in the Google app and our stories appear in your news suggestions. OWASP ZAP, short for Zed Attack Proxy, is a free dynamic application security testing (DAST) tool that sits between your browser and a target web application, intercepting and analyzing traffic for vulnerabilities. It started as a fork of the Paros proxy, moved under OWASP for years, and formally left the OWASP umbrella in 2023. Since September 2024, development has continued under Checkmarx sponsorship as “ZAP by Checkmarx,” but the project remains independently governed by the ZAP core team and stays free under the Apache License 2.0, with no paid tier, feature gate, or scan cap. That governance held through the 2.16.x line too: OWASP shipped ZAP 2.16.0 in January 2025 with a new spider and refreshed policy definitions, then followed it with ZAP 2.16.1 in March 2025 as a bug-fix and enhancement release, the kind of unglamorous maintenance update that signals a project still being actively run rather than coasting on a sponsor’s goodwill.
That governance detail matters for anyone deciding whether to commit engineering time to an OWASP ZAP setup: a project that changed sponsors without changing its license or its release cadence is a very different risk profile than a tool that could disappear behind a paywall next quarter. ZAP’s GitHub organization remains one of the more active security projects on GitHub, with the core repository and its dozens of add-on repositories seeing regular commits and monthly add-on releases throughout 2026 — 18 separate add-ons received updates in a single push in June 2026 alone, including the Client Side Integration add-on, which reached version 0.29 that same month — which is the cadence that produced the OWASP Top 10:2025 rule tagging, the JWT support, and the cloud metadata checks covered later in this guide.
The reason OWASP ZAP setup is worth revisiting right now is the pace of the 2.17.x release line. The core 2.17.0 build landed December 15, 2025, bringing core performance improvements and a meaningful cut to duplicate alert noise, and as of July 2026 it formally became the mandatory minimum baseline that every updated add-on must build against. Passive scanner rules v73 and active scanner rules v81, both released April 14, 2026, added tags mapping alerts directly to OWASP Top 10:2025 and the API Top 10 2023. Active scanner rules v80 added checks for cloud metadata exposure on IBM and OpenStack in March 2026. And in August 2026 the project shipped an LLM Support add-on, its first real answer to AI-assisted application testing.
None of that matters if you cannot get a scan running cleanly and reading its output correctly, so the rest of this guide is a straight path from zero to a working, automated OWASP ZAP pipeline. Before installing anything, it helps to know what each ZAP component actually does, since the terminology trips up a lot of first-time users. The classic Spider crawls a site the way a search engine bot would: it follows hyperlinks in HTML, builds a map of every URL it finds, and adds each one to the Sites tree. It works well against traditional server-rendered pages but misses content that only appears after JavaScript runs, which is most modern single-page applications.
ZAP 2.16.0 and later, including the current 2.17.0 release, requires a minimum of Java 17. The Windows and Linux installers expect Java 17 or higher already on the system; the macOS package bundles a Zulu JRE so most Mac users skip a separate Java install entirely. Below is the full checklist before you start. You will also need written authorization to scan your target. Active scanning sends real attack payloads, including SQL injection and cross-site scripting strings, at every parameter it finds. Running it against infrastructure you do not own or have explicit permission to test is a legal risk, not just a technical one. Stick to a staging environment, a deliberately vulnerable practice app, or a target where you have documented sign-off.
Start by confirming your Java version, since a mismatch here is the single most common install failure people report. On Windows, download the ZAP 2.17.0 installer from the official ZAP downloads page and run it like any other installer; it will prompt you to point at an existing Java 17 install or use the bundled option if offered. On macOS, the .dmg package includes Java, so a double-click install is enough. If you would rather skip local installation entirely, jump ahead to the Docker section, since that path needs nothing but a working container runtime.
On first launch, ZAP asks whether to persist the session to disk or run in memory only. For a one-off exploratory scan, memory-only is fine. For anything you want to revisit or hand off to a teammate, choose “Yes, I want to persist this session” and give it a name. The main window is split into three panels: the Sites tree on the left tracks every URL ZAP has seen, the top-right panel switches between the Quick Start tab, request/response viewers, and the Automation Framework tab, and the bottom panel streams the Alerts, History, and Spider progress in real time.
The fastest way to get oriented is the Quick Start tab. It exposes three buttons: Automated Scan, which chains a spider and an active scan against a URL you paste in; Manual Explore, which opens a ZAP-controlled browser — Microsoft Edge reached tier-1 support in July 2025, putting it on equal footing with Chrome and Firefox for exploring, crawling, and attacking — so you can click through the app yourself while ZAP records everything passively; and the newer HUD (Heads-Up Display) launch option, which overlays scan controls directly onto the page you are browsing. The HUD has not been deprecated or folded into another add-on as of the 2026 release notes, and it remains the easiest way to watch alerts fire in real time while you manually test a login flow or a multi-step checkout.
Before running any scan wider than a quick exploratory pass, define a Context. Right-click your target in the Sites tree and choose “Include in Context,” then create a new context named after the application. This does two things: it stops ZAP from wandering off into third-party domains linked from your app (analytics scripts, CDNs, social widgets), and it gives you a place to attach authentication settings later in Step 11.
Inside the Context menu, set the Include and Exclude regex rules. A typical exclude list removes logout links, password-reset endpoints that send real emails, and any payment or checkout flow you do not want ZAP hammering with active scan payloads. Skipping this step is one of the most common reasons teams end up with a scan report full of noise from scanning marketing pages, CDN assets, and third-party trackers that were never the actual target.
A baseline scan spiders the target to discover URLs, then runs ZAP’s passive scan rules against everything it captures, without sending any attack payloads. It is safe to run against production, since it never actively tries to break anything, and it is the standard first check for a CI/CD gate because it finishes in minutes rather than hours. From the GUI, use Quick Start, paste the target URL, and select “Automated Scan” but leave the active scan toggle off. From the command line or a script, ZAP ships a baseline scan script you can call directly against the desktop install, or you can use the Docker image covered in Step 9, which is the more common path for this exact scan type.
Three settings matter here. First, thread count under Options > Active Scan controls concurrency; lower it if the target starts throwing errors or timing out. Second, the Policy tab lets you disable rule categories you do not care about, which both speeds up the scan and cuts irrelevant noise. Third, and most important for anything beyond a personal test app, confirm the scan is running against a context you scoped correctly in Step 3, because an unscoped active scan against a large site can run for hours and generate thousands of requests against endpoints nobody asked you to test.
Every finding lands in the Alerts panel, grouped by risk: High, Medium, Low, and Informational. As of the 2.17.0 rule updates shipped through April 2026, ZAP tags each alert against the current OWASP Top 10:2025 categories, which reshuffled the 2021 list in a few important ways. Security Misconfiguration jumped from fifth place to second. Software Supply Chain Failures is an entirely new category debuting at third. And a new tenth category, Mishandling of Exceptional Conditions, replaced Server-Side Request Forgery as a standalone entry, folding SSRF-style issues into other categories instead.
Work High findings first, confirm each one manually before filing it (ZAP’s academic benchmark results put its false-positive rate noticeably above commercial tools in side-by-side testing, more on that later), and use the alert’s linked CWE reference to hand developers something more actionable than a raw scanner output. Clicking through the GUI does not scale past a single manual test. The Automation Framework, ZAP’s YAML-driven orchestration layer now at version 0.60.0 following a May 2026 release that improved automated setup workflows, is how every serious OWASP ZAP setup runs in practice. A plan file defines a context, a target URL, and an ordered list of jobs.
This same YAML plan is the file you will hand to both the Docker image and the GitHub Actions workflow in the next two steps, so it is worth getting this file right once rather than maintaining three separate scan configurations. Docker is now the more common way teams run OWASP ZAP, and ZAP’s own statistics page notes that direct downloads have been declining as container usage grows. The modern image lives under the zaproxy namespace; the older owasp/zap2docker-stable naming is still referenced in plenty of tutorials but points at legacy tags, so pin an explicit version rather than copying an old command verbatim.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Web%20application%20firewall • https://en.wikipedia.org/wiki/Application%20security • https://en.wikipedia.org/wiki/SQL%20injection • https://www.zaproxy.org/docs/ • https://bughuntertools.com/articles/building-automated-security-scanning-pipeline-owasp-cicd-2026/ • https://github.com/Tom-Doyle-CyberSecurity/Project-2-OWASP-Top-10 • https://owasp.org/projects/top-ten • https://onscanner.com/blog/owasp-top-10-for-automated-scanning • https://www.zaproxy.org/docs/automate/automation-framework/ • https://exploita.ai/blog/owasp-top-10-scanner
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Automated Owasp Top 10 Web Scanner Project.
[*] Initializing Burp Suite Spider & Vulnerability Engine for Automated Owasp Top 10 Web Scanner Project... [✓] Burp Extender / Macro Automation Hook Synced ──────────────────────────────────────────────────────────────────────── [11:42:01.104] AUDIT Crawled dynamic endpoints | Injecting input vectors [11:42:01.218] FINDING Cymulate / Burp: Input sanitation check executed in parameter 'q' [11:42:01.312] VERIFY SafeBreach payload validation: Out-of-band interaction confirmed [11:42:01.405] REPORT Severity: Evaluated | Remediation: Enforce context-aware validation ──────────────────────────────────────────────────────────────────────── [✓] Burp Suite Audit Completed: Verified across OWASP Top 10 vectors
| Vulnerability Vector | Testing Tool | Injection Target | Severity | Remediation Status |
|---|---|---|---|---|
| SQL Injection (SQLi) | Burp Suite Professional | POST /api/auth/login | CRITICAL | PARAMETERIZED |
| Cross-Site Scripting (XSS) | SafeBreach / Cymulate | GET /search?q= | HIGH | CSP ENFORCED |
| Broken Object Level Access | Picus Security Audit | GET /user/account/840 | HIGH | RBAC APPLIED |
| Security Misconfiguration | AttackIQ Suite | HTTP Security Headers | MEDIUM | RESOLVED |