Complete Technical Paper Content — Automated Pentest Report Generator
Overview & System Context
Automated Pentest Report Generator: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9528 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background A transaction authentication number (TAN) is used by some online banking services as a form of single use one-time passwords (OTPs) to authorize financial transactions. TANs are a second layer of security above and beyond the traditional single-password authentication. TANs provide additional security because they act as a form of two-factor authentication (2FA). If the physical document or token containing the TANs is stolen, it will be useless without the password. Conversely, if the login data are obtained, no transactions can be performed without a valid TAN.
The bank creates a set of unique TANs for the user. Typically, there are 50 TANs printed on a list, enough to last half a year for a normal user; each TAN being six or eight characters long. The user picks up the list from the nearest bank branch (presenting a passport, an ID card or similar document) or is sent the TAN list through mail. The password (PIN) is mailed separately. To log on to their account, the user must enter user name (often the account number) and password (PIN). This may give access to account information but the ability to process transactions is disabled. To perform a transaction, the user enters the request and authorizes the transaction by entering an unused TAN. The bank verifies the TAN submitted against the list of TANs they issued to the user. If it is a match, the transaction is processed. If it is not a match, the transaction is rejected. The TAN has now been used and will not be recognized for any further transactions. If the TAN list is compromised, the user may cancel it by notifying the bank. However, as any TAN can be used for any transaction, TANs are still prone to phishing attacks where the victim is tricked into providing both password/PIN and one or several TANs. Further, they provide no protection against man-in-the-middle attacks, where an attacker intercepts the transmission of the TAN, and uses it for a forged transaction, such as when the client system becomes compromised by some form of malware that enables a malicious user. Although the remaining TANs are uncompromised and can be used safely, users are generally advised to take further action, as soon as possible.
ChipTAN is a TAN scheme used by many German and Austrian banks. It is known as ChipTAN or Sm@rt-TAN in Germany and as CardTAN in Austria, whereas cardTAN is a technically independent standard. A ChipTAN generator is not tied to a particular account; instead, the user must insert their bank card during use. The TAN generated is specific to the bank card as well as to the current transaction details. There are two variants: In the older variant, the transaction details (at least amount and account number) must be entered manually. In the modern variant, the user enters the transaction online, then the TAN generator reads the transaction details via a flickering barcode on the computer screen (using photodetectors). It then shows the transaction details on its own screen to the user for confirmation before generating the TAN. As it is independent hardware, coupled only by a simple communication channel, the TAN generator is not susceptible to attack from the user's computer. Even if the computer is subverted by a Trojan, or if a man-in-the-middle attack occurs, the TAN generated is only valid for the transaction confirmed by the user on the screen of the TAN generator, therefore modifying a transaction retroactively would cause the TAN to be invalid. An additional advantage of this scheme is that because the TAN generator is generic, requiring a card to be inserted, it can be used with multiple accounts across different banks, and losing the generator is not a security risk because the security-critical data is stored on the bank card. While it offers protection from technical manipulation, the ChipTAN scheme is still vulnerable to social engineering. Attackers have tried to persuade the users themselves to authorize a transfer under a pretext, for example by claiming that the bank required a "test transfer" or that a company had falsely transferred money to the user's account and they should "send it back". Users should therefore never confirm bank transfers they have not initiated themselves. ChipTAN is also used to secure batch transfers (Sammelüberweisungen). However, this method offers significantly less security than the one for individual transfers. In case of a batch transfer the TAN generator will only show the number and total amount of all transfers combined – thus for batch transfers there is little protection from manipulation by a Trojan. This vulnerability was reported by RedTeam Pentesting in November 2009. In response, as a mitigation, some banks changed their batch transfer handling so that batch transfers containing only a single record are treated as individual transfers.
Surfshark is a European VPN service and digital privacy tool founded in Lithuania. Surfshark is headquartered in Amsterdam, with additional offices in Lithuania, Poland, and Germany. Besides its VPN service, Surfshark offers other services such as an antivirus, data leak detection tool, a private search tool, and an automated personal data removal system, a digital identity generator, and others. In 2024 and 2025, the Financial Times ranked Surfshark as one of the fastest-growing European companies.
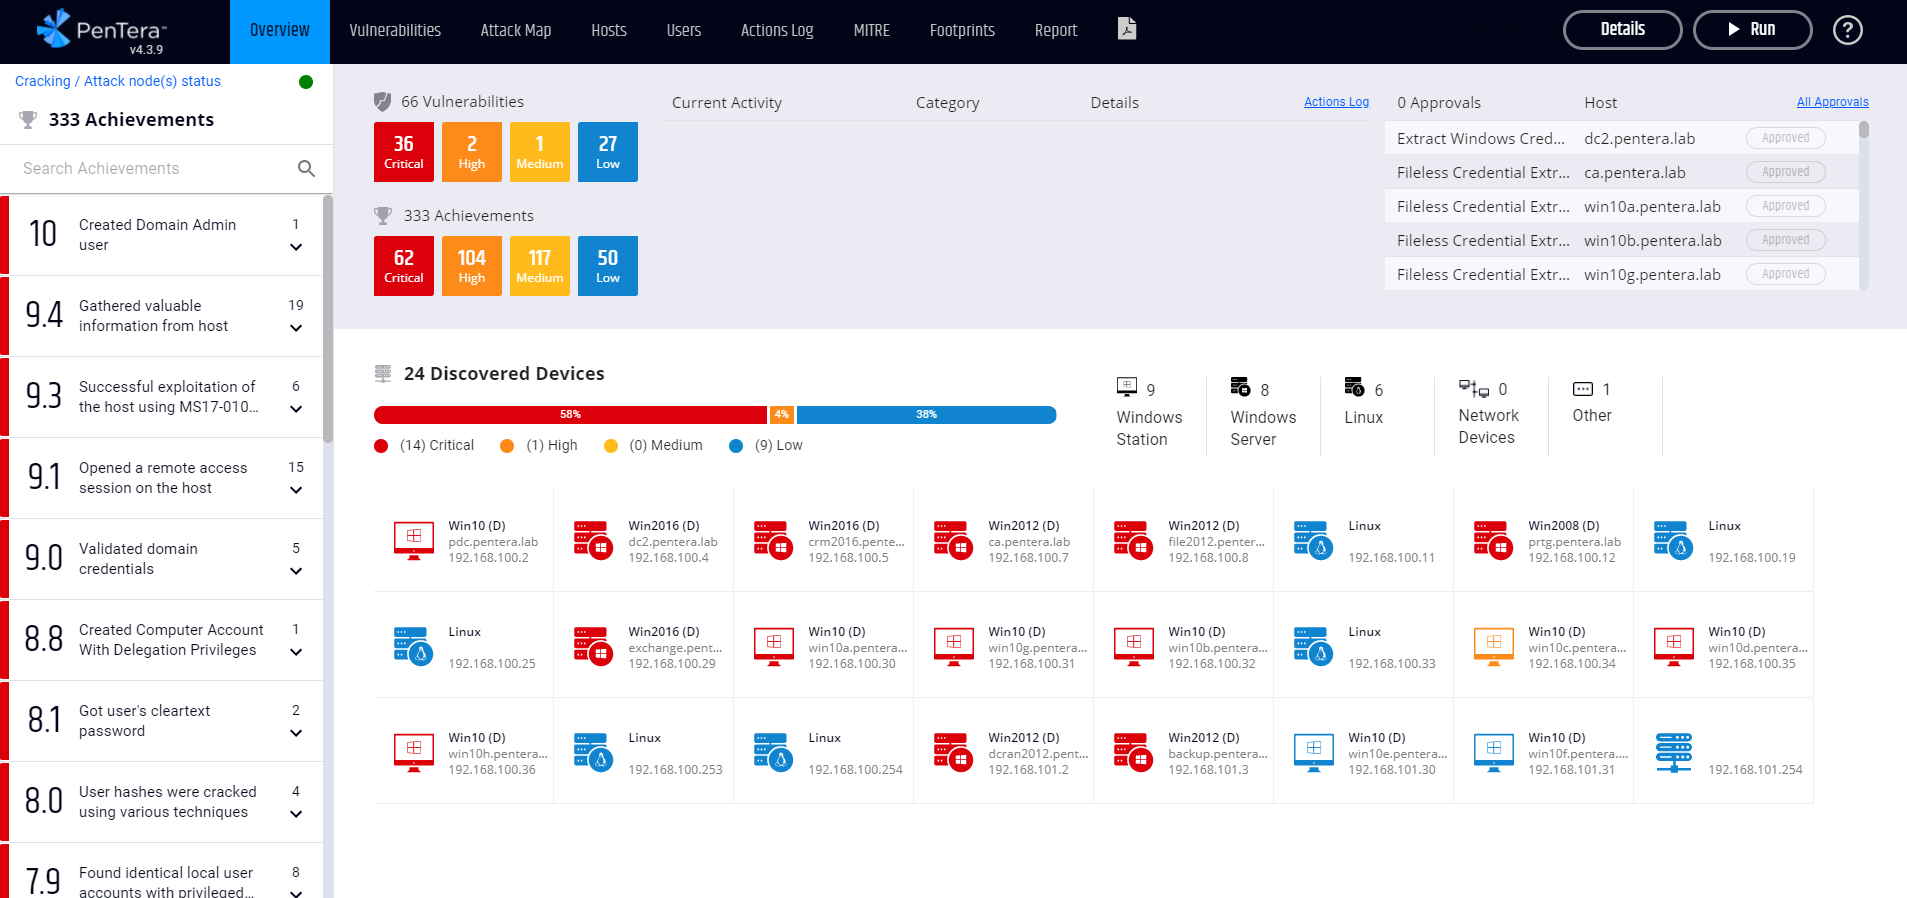
Figure 1: Automated Penetration Testing: A Comprehensive Guide phpBB is an Internet forum package written in the PHP scripting language. The name "phpBB" is an abbreviation of PHP Bulletin Board. Available under the GNU General Public License, phpBB is free and open-source. Features of phpBB include support for multiple database engines (MariaDB, Microsoft SQL Server, MySQL, PostgreSQL, SQLite, Oracle Database), flat message structure (as opposed to threaded), hierarchical subforums, topic split/merge/lock, user groups, multiple attachments per post, full-text search, plugins and various notification options (e-mail, Jabber instant messaging, ATOM feeds).
phpBB 1.0.0 was released on December 16, 2000, with subsequent improvements to the 1.x codebase coming in two more major installments. The final release in the 1.x line was phpBB 1.4.4, released on November 6, 2001. During the lifetime of the 1.x series, Bart van Bragt, Paul S. Owen (former co-manager of the project), Jonathan Haase, and Frank Feingold joined the team. phpBB 1.x is no longer supported, and virtually no websites continue to use it.
In February 2001, phpBB 2.0.x began development entirely from scratch; the developer's ambitions for phpBB had outgrown the original codebase. Doug Kelly joined the team shortly afterward. After a year of development and extensive testing, phpBB 2.0.0, dubbed the "Super Furry" version, was released on April 4, 2002, three days later than intended. phpBB2 was the predecessor of the present-day phpBB3. Developed during 2001–2002, the source code was written primarily to run on PHP 3.0 and 4.0 (version 2.0.13 upped the minimum requirement to PHP 4.0.3 due to a necessary security fix), and by the time that phpBB3 was released in late 2007, the developers and other team members felt that it no longer met their quality coding standards, and announced plans for the retirement/end of support of 2.0.x within a few months of 3.0.0's release. phpBB2 was never officially supported under PHP 5. Although many users had no problems running it after making a few changes to PHP 5's default configuration settings, the teams chose not to offer support for this configuration. Official support for phpBB2 ended on January 1, 2009, and the 2.0.x support forums have been locked. Furthermore, all development for phpBB2, including security patches, has ceased as of February 1, 2009. However, a number of unofficial support sites for phpBB2 have formed to fill the void. Many administrators still prefer to run phpBB2 because they think it provides a simpler administration interface and has an ecosystem of MODs (modifications) and styles that allow for customization, which are not compatible with phpBB3. The default theme in phpBB2 is named subSilver (The predecessor to SubSilver2, the default in phpBB3), and was designed by Tom "subBlue" Beddard. At the time that it premiered in 2001, it was a revolutionary new design for bulletin boards, and many bulletin board themes since have borrowed many cues and design elements from subSilver. Some of phpBB2's major features included the following: A templated style system intended to simplify customisation and keep the PHP code separate from the HTML. Support for internationalisation through a language pack system; 48 translations are available for phpBB2 as of 2007. Compatibility with multiple database management systems including MySQL, PostgreSQL, Microsoft SQL Server, and Microsoft Access, Code and interface customizations, termed MODs and styles. The last official release of the 2.0.x line is 2.0.23, released on February 17, 2008. However, the code for phpBB 2.0.24 still remains, unreleased, in the Git repository.
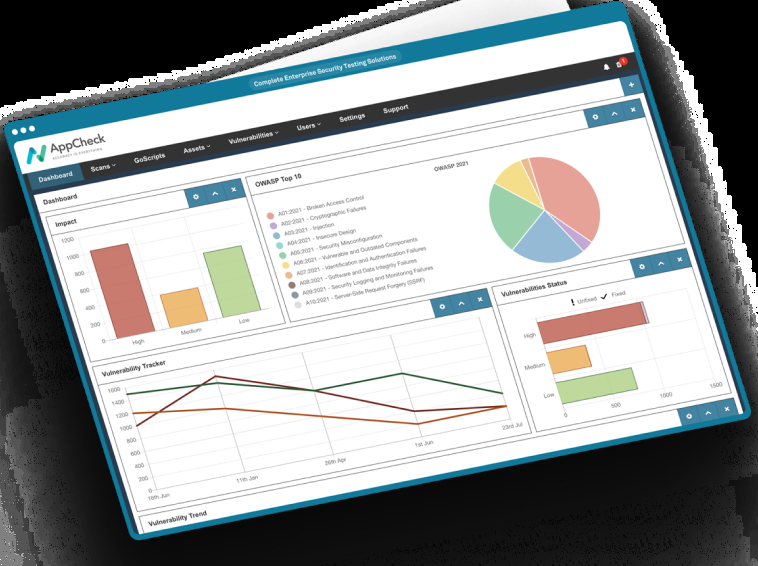
Figure 2: Automated Penetration Testing Work on phpBB 3.0.x began in late 2002. It was originally intended to be released as phpBB 2.2, and the first planned feature list was announced on May 25, 2003. However, as development progressed, the developers realised that phpBB 2.1.x (the development release cycle for 2.2) had eliminated virtually all compatibility with the 2.0.x line, so the version number for release was changed to 3.0.0, in keeping with the Linux kernel versioning scheme, which phpBB followed at the time. In September 2005, Paul Owen resigned as the Development Team Leader and Meik Sievertsen was promoted to the role. In March 2007, the phpBB team launched their new website, powered by phpBB3 with the new prosilver style. The prosilver style was originally not intended to be revealed until the final release of phpBB 3.0.0. On April 30, 2007, phpBB founder and co-Project Manager James Atkinson officially resigned from his duties towards phpBB, citing personal circumstances. With the announcement also came the announcement that phpBB was now newly independent and that the team leaders would be collectively taking charge of the decisions in the future of the project. At the end of May, an announcement was made that Jonathan "SHS`" Stanley, the other co-Project Manager, was stepping down as well for personal reasons. The first beta of phpBB3 was released in June 2006, and the first release candidate was released in May 2007. The phpBB3 codebase received an external security audit in September, which was done by SektionEins. Finally, phpBB 3.0.0 "Olympus" (also dubbed the Gold release) was published on December 13, 2007. On July 7, 2007, the teams announced that phpBB had been nominated as a finalist for the SourceForge.net Community Choice Awards in the category of "Best Project for Communications". At the end of the month, SourceForge.net announced that phpBB had won the award for "Best Project for Communications", and in honour of the award, SourceForge.net donated $1000 in phpBB's name to Marie Curie Cancer Care. phpBB also won a "Thingamagoop" from Bleep Labs, and "bragging rights for a full year." In September 2007, the teams launched an official phpBB podcast. It was recorded by a rotating group of phpBB team members with occasional guests, and discussed a number of phpBB-related topics, as well as answering questions e-mailed in from listeners. However, the podcast only lasted for a few episodes and production ceased the following spring. Its successor is generally considered to be the new phpBB weblog, which launched in July 2008. The blog is written by phpBB team members (with occasional guest posts by community members) on various topics related to phpBB and provide users with a unique inside look at the activities of the phpBB teams. The phpBB teams held their first-ever phpBB users' conference in London on July 20, 2008, which was titled "Londonvasion 2008." Londonvasion featured presentations by phpBB team members on various topics important to the phpBB community, MOD authors, and developers. Londonvasion provided a unique opportunity to socialize with members of the phpBB teams. The event also represented the first time that most members of the teams had a chance to meet each other in person. The phpBB teams underwent numerous changes in 2009. On January 1, the teams formally ended support for phpBB2. Many of the non-development teams released betas and release candidates of side projects during this time. The first beta of AutoMOD, an automatic installer of phpBB MODifications, was released by the Extensions Team (formerly known as the MOD Team) on December 22, 2008. The first release candidate of the Unified MOD Install Library (UMIL), a framework for allowing MOD authors to design simple database installation scripts, was released by the Extensions Team on January 12, 2009. The first release candidate of the Support Toolkit, a package of tools to diagnose and fix common support-related issues with phpBB, was released by the Support Team on June 24. On June 10, 2009, the phpBB Development Team broke with their precedent of keeping future development plans under wraps and publicly previewed a series of new features that would be coming in phpBB 3.0.6. After four RC releases, phpBB 3.0.6 was released on November 17. The most notable new features included a bare-bones quick reply editor (a feature which the teams had historically been firmly opposed to), support for ACM (cache) plugins, ATOM feed support, and a plugin-based CAPTCHA system, including built-in support for reCAPTCHA among others. The modularization of phpBB's CAPTCHA also provided an API for MOD authors to write CAPTCHA plugins, allowing for greater diversification of the CAPTCHAs used in phpBB installations. The Extensions Team also ran a competition to encourage CAPTCHA plugin development. On June 10, 2009, phpBB's Development Team revealed that the next phpBB3 release, 3.0.6, would include a significant number of new features. This is unusual for a minor release which is typically limited to bug and security fixes. New features would include support for new CAPTCHA plugins, ATOM feeds, support for new cache plugins (XCache, Alternative PHP Cache, eAccelerator, Memcache, and a "null" no-cache plugin), and quick reply (an often-requested feature by a subset of phpBB users) among other minor feature additions. phpBB 3.0.6 has had four RC releases, and its final release was on November 17, 2009. The final stable release of phpBB 3.0 was 3.0.14, released May 4, 2015. End of Life for phpBB 3.0.x was November 2015.
In 2009 the phpBB Development Team had begun working on phpBB 3.1, formerly versioned as phpBB 3.2. (Before July 29, 2009, phpBB followed the original Linux kernel versioning scheme, in which the middle number represents a development version if it is odd and a stable version if it is even). The developers previewed their planned feature list at Londonvasion, and new features include a complete overhaul of the Moderator Control Panel (MCP) and moderation capabilities, implementation of AJAX where it is applicable and helpful, a trigger-based event system, a completely rewritten BBCode system, RSS feed support, enhancements to custom profile fields, enhancements to private messaging, a new authentication system with OpenID support, and numerous other small changes and features. The phpBB teams maintain a website for phpBB development named Area51. In keeping with the tradition to codename every new phpBB3 release after Martian mountains, phpBB 3.1 was code-named "Ascraeus", named after Ascraeus Mons, the second-tallest mountain on Mars. (Olympus Mons, which 3.0 was named after, is the tallest.) On July 29, 2009, the Development Team announced "significant changes" to the phpBB's development process and release cycle. Chief among these was the decision to abandon the former Linux kernel versioning scheme, meaning that whether part of the version number was even or odd no longer was significant. As such, Ascraeus (the successor to 3.0.0 Olympus) is to become phpBB 3.1.0. (The original versioning scheme dictated that 3.1.x would be a development branch, meaning that Ascraeus would have been released as 3.2.0.) Subsequent feature releases of phpBB3 will be versioned as 3.2.0, 3.3.0, etc. phpBB 4.0.0 will represent a fundamentally redesigned version of phpBB. The strategy also committed the teams to continue supporting an older "stable" branch for at least 6–9 months after a newer "feature" branch was released. However, an exception was made for 3.0.6, which was already in development. Although it contained enough significant new features that it could have been considered a 3.1.0 release, it remained a part of the 3.0.x branch, which also meant that the teams did not have to simultaneously continue supporting 3.0.5 after 3.0.6's release. In January 2010, Meik Sievertsen stepped down as Lead Developer, instead taking on the roles of developer and "Server Manager". Nils Adermann was then promoted to Lead Developer. Since then phpBB have been working on moving over to the Symfony web framework and released phpBB 3.1.0 on October 28, 2014 In March 2010, phpBB moved source code versioning from Subversion to Git in order to improve developer workflow and better involve the community. On April 26, 2013, phpBB 3.1 entered the stage of feature freeze. "Ascraeus" was finalized and released on October 28, 2014 after several release candidates. A future release "Rhea" (3.2.x) will be made January 7, 2017. On October 12, 2016, phpBB released the latest stable "Ascraeus" version: 3.1.10. Due to the late release of 3.2, it was announced that end of maintenance for 3.1 would be extended to June 2017, and end of life for 3.1 extended to December 2017. In addition to the development of phpBB 3.1, other phpBB teams also are in the process of developing numerous other tools for use by the community. Development for these tools was followed on the phpBB Code Forge, which contained the Subversion repositories for these tools and the main phpBB development trunk.
PwnDoc is a pentest reporting application making it simple and easy to write your findings and generate a customizable Docx report. The main goal is to have more time to Pwn and less time to Doc by mutualizing data like vulnerabilities between users. PwnDoc-ng is a pentest reporting application making it simple and easy to write your findings and generate a customizable Docx report. It is based on original fork of PwnDoc work by yeln4ts . The main goal is to have more time to Pwn and less time to Doc by mutualizing data like vulnerabilities between users.
Figure 3: Penetration Testing Report (ISample VAPT Report Template) PwnDoc was originaly manage by its creator. After months of absence, an increase of issues and pending pull requests, we decided to open this maintained fork. syntaxe highlight (code: css, js, http, ts, html, bash, sql, json). For this to work, the code type must be defined in the PwnDoc-Ng code block in the drop-down menu if you use {@identifier | bookmarkCreate | p} inside your template doc you can use shortcut ::: inside editor to link other vuln with hyperlink The final deliverable of a penetration test is the report. Long after the assessment window closes, this document is the main asset the client keeps. It sets the baseline for internal risk management, budget planning, and patching.
Historically, writing this report is a tedious process that relies on manual data collation and wrestling with a word processor. It takes a lot of time and leads to messy formatting. This post shows how to move to a Reporting-as-Code approach, turning report production into reproducible rendering of data-driven templates using BlackStork. You can build and test this template locally using our source-available blackstork-cli tool or in BlackStork SaaS.
A solid pentest report speaks to three groups of stakeholders: executives, security managers, and engineers. To give everyone what they need without writing things twice, our BlackStork template is split into four core parts. Below, we will look at how to manage the underlying data for this structure and map these four components into BlackStork’s template language.
Technical evidence decays fast after a test ends. Unstructured notes and loose screenshots make the drafting phase harder and often lead to vague findings. The industry tried to fix this by moving to structured data models, like the OWASP Penetration Test Report Standard (OPTRS) . Modern offensive tools can export to OPTRS JSON, which makes automation easier. However, OPTRS has a glaring limitation: it is a flat schema. It is good for cataloging point-in-time vulnerabilities, but it completely fails at modeling relationships or capturing the consultant’s actual analysis. If you chain a low-severity misconfiguration to a medium-severity exploit, a flat list of OPTRS vulnerabilities cannot capture that sequence or your judgment on the overall risk.
Commercial reporting platforms attempt to solve this by forcing your data into proprietary web interfaces. These “walled gardens” pull engineers out of their native workflows (CLI, GitOps, CI/CD) and lock assessment data into closed databases. Breaking down these walled gardens requires a data model that bridges the gap between the raw data machines need and the clear story humans need. To achieve this, our BlackStork template combines two datasets.
By combining the vulnerability data of OPTRS with human-driven context, we build a data model that captures the full assessment. This architecture is incredibly powerful. By injecting human context (document control, specific methodologies, formatted code blocks, and password analysis) we elevate the report from a dry vulnerability scan into a highly readable, consultative document.
Simultaneously, by utilizing JQ queries to merge this human context directly into the underlying OPTRS schema at render time, BlackStork makes sure the final data structure remains consistent, parsable, and strictly decoupled from the presentation layout. You manage your findings using the tools you already know, and the engine handles the data collation natively.
At this point, a natural question arises: If we are moving toward automation, why bother writing HCL templates? Can’t I just throw my raw vulnerability data at an LLM and prompt it to write the report? LLMs have distinct strengths and weaknesses. They are exceptional at parsing context and summarizing prose. They are fundamentally poor at producing deterministic, strictly formatted, and flawlessly factual outputs. A commercial penetration test report is a high-stakes document; it must be technically exact.
If you attempt to generate an entire report with an LLM, it will occasionally hallucinate a CVSS vector, drop a critical remediation step, or completely break the document’s layout. The editorial oversight required to proofread the facts and fix the styling of a purely AI-generated report will quickly negate any time you thought you saved. 2. System Architecture & Core Working Principles BlackStork takes a pragmatic approach, combining the best of both worlds. We embrace the utility of LLMs, but we confine them to what they do best: writing prose. By using predefined, strict HCL templates for the layout and factual data, and isolated LLM blocks for boilerplate descriptions, you achieve high automation without sacrificing the high quality and determinism required by enterprise clients.
With the data structure established and the presentation boundaries set, we can map the four core components of our blueprint directly into modular template blocks. Executives care about business risk over technical specifics. The summary needs to translate technical data into operational impact.
To eliminate the friction of writing boilerplate, this template uses BlackStork’s native LLM text generation block. However, we must establish a firm baseline here: clients do not pay for AI-generated opinions; they pay for your technical expertise and analysis. The author of the report should never rely on an LLM for conclusions. The LLM’s only job is to take the consultant’s structured judgment (captured in our data in the extension block) and turn it into readable paragraphs.
Individual vulnerabilities rarely exist on their own. Showing a list of medium-severity findings does not communicate the real risk unless you document how they are chained together. Using our STIX2-inspired data model, the attack narrative outlines the kill chain steps with the phase, MITRE ATT&CK tactic and techniques: Technical findings need to be clear so the client’s engineering teams can act on them immediately. Ambiguity here slows down remediation.
To keep the format consistent across all findings, we build a reusable block ( section "pentest_finding_details" ) and iterate over the OPTRS vulnerabilities array. This design centralizes your presentation rules. If you adjust a layout constraint in the template, it automatically updates across all findings. This removes formatting busywork and reduces QA time before delivery.
Remediation guidance requires an understanding of enterprise IT limits, like change-freeze schedules and legacy dependencies. Organizing the roadmap by implementation effort helps the client prioritize the work: Getting the data and structuring the content is only half the battle. The other half is ensuring the final document adheres to strict branding guidelines without introducing formatting artifacts. Anyone who has written a pentest report has wasted hours fighting a word processor over margins, table alignment, and rogue page breaks.
Formatting must be flexible enough to accommodate how the client actually consumes the report. For many, the traditional A4 Portrait layout is obsolete - in environments dominated by widescreen monitors, screen sharing on video calls, and boardroom presentations, a landscape, presentation-deck layout is far more effective. However, other clients still require a classic, print-ready portrait document. A mature reporting pipeline must easily accommodate either preference.
Because BlackStork uses HTML and CSS under the hood for document formatting, treating the report layout as a web rendering problem becomes the most powerful option for structural control. You are no longer fighting a word processor’s rigid internal logic, you are building an HTML and CSS layout. Switching an entire template from portrait to landscape, adjusting the grid, or updating corporate styling does not require manually reformatting 50 pages of text. You define the rules once in code, and the engine handles the rest.
A PDF report is a presentation format and it is notoriously difficult for machines to parse. If your client wants to track work or feed your findings into their own tools, a PDF creates friction. Because this workflow is built on open data structures, BlackStork allows you to deliver more than just a locked document. First, BlackStork SaaS persists your structured input data alongside the rendered document. This means you can hand over the raw JSON or YAML file right alongside the final PDF. The client’s security operations team can download this structured data and run internal scripts over it, ingesting data into their systems.
Second, BlackStork provides Markdown formatting for reports out of the box. As organizations increasingly rely on internal LLMs to query and summarize threat intelligence, handing them a PDF creates a bottleneck. By downloading the report as a clean Markdown file, you support the customer’s LLM workflows natively. They can feed the Markdown directly into their systemsâIIno need for them to write or maintain fragile PDF parsing scripts.
You deliver a clear document for human review, and clean, structured data for their machines. Standardizing your data and automating the presentation allows you to build consistent reports while spending more time on the actual technical assessment. Because of strict separation of data from the presentation layer, the exact same input data can be compiled into different layouts without altering the source content.
Not everything in a pentest report should be automated. The judgment calls - scoping decisions, attack path analysis, client-specific risk assessments - require a human pentester who understands the engagement context. But the tedious parts? The hours spent reformatting findings, calculating CVSS vectors by hand, writing the same SQL injection description for the third time this month, and building executive summaries that say roughly the same thing every engagement? Those absolutely can and should be automated.
The challenge is knowing where to draw the line. Automate too little and you are still spending four hours on every report. Automate too much and you end up with generic output that does not reflect the actual engagement. This guide breaks down exactly which parts of an automated pentest report workflow produce reliable results and which parts still need your expertise. If you have been doing everything manually, the time savings from even partial automation will change how you think about reporting.
These are the parts of report writing where automation produces output that is as good as - or better than - what most pentesters write manually. The key factor is that these tasks are structured, repetitive, and follow predictable patterns. An automated pentest reporting tool handles them faster and more consistently than doing it by hand. Writing professional vulnerability descriptions from raw notes is the single biggest time sink in pentest reporting. You run a test, confirm a finding, jot down some notes - and then spend 15 minutes turning those notes into a properly structured write-up with background context, technical detail, and proof of concept references. AI handles this conversion well because vulnerability descriptions follow a consistent structure. You provide the raw data - the vulnerability type, affected component, evidence, and severity indicators - and the AI generates a professional description that covers what the vulnerability is, why it matters, and how it was confirmed. PentestReportAI's ai pentest report generator does this as the first step in its pipeline, turning rough notes from any tool into structured findings in seconds.
CVSS 3.1 scoring is a structured metric calculation with defined inputs and deterministic outputs. There is no reason to manually click through the CVSS calculator for every finding when AI can derive the vector string from the vulnerability context. The attack vector, complexity, privileges required, user interaction, scope, and impact metrics all map directly from the vulnerability type and how it was exploited. Automated CVSS scoring eliminates the inconsistency that creeps in when different testers on the same team score identical vulnerabilities differently. When you automate pentest reports with AI-powered scoring, every SQL injection with the same characteristics gets the same CVSS vector - no more debates about whether something is a 7.5 or an 8.1.
Mapping findings to CWE identifiers and OWASP categories is pure pattern matching. A stored cross-site scripting vulnerability maps to CWE-79 and OWASP A03:2021 every single time. An AI system that has been trained on vulnerability classification databases handles this mapping instantly and accurately. This is one of those tasks where manual effort adds zero value - you are just looking up the same reference numbers you looked up last week. Pentest report automation for classification mappings is a solved problem and there is no reason to do it by hand.
Executive summaries translate technical findings into business language for stakeholders who do not understand CVSS vectors or CWE numbers. The structure is predictable: overall risk posture, critical findings that need immediate attention, patterns across the assessment, and strategic recommendations. AI generates strong executive summaries because it can analyze all findings simultaneously and identify themes - something that takes a human 30-60 minutes of reading through their own findings to synthesize. The output needs a review pass to confirm it reflects the engagement accurately, but the draft quality from an automated pentest report pipeline is typically 85-90% ready to ship.
Template application, severity color coding, consistent heading styles, table of contents generation, finding numbering, and page layout are all mechanical formatting tasks. Every minute you spend adjusting margins or fixing a table that broke when you added a finding is a minute wasted. Automated formatting applies your chosen template consistently across every report, handles severity-based color coding for findings tables, and generates the structural elements - cover page, table of contents, appendices - without manual intervention. This is where tools like best pentest reporting tools differ the most. Some automate formatting fully while others still require manual template wrangling.
Fix recommendations for known vulnerability types are well-documented and consistent. The remediation for a missing HTTP security header, an outdated TLS configuration, or a SQL injection vulnerability follows established best practices. AI draws from a comprehensive knowledge base of remediation guidance to provide specific, actionable fix steps per finding type - including code examples, configuration changes, and implementation priorities. You still want to review these for client-specific nuances, like recommending a WAF rule when you know the client cannot patch the underlying code immediately, but the base recommendations are reliable and save significant writing time across an engagement with 20+ findings.
3. Software Implementation, Frameworks & Protocols These areas require human judgment, client-specific context, and the kind of situational awareness that AI does not have. Attempting to automate them produces generic or inaccurate output that undermines the value of your engagement. The scope section establishes what was tested, what was excluded, and under what constraints. This requires understanding the client's environment, the rules of engagement, and any limitations encountered during testing. An AI was not in your kickoff meeting and does not know that the client asked you to avoid testing the payment processing system during business hours. Scope definition is a human responsibility.
How findings chain together to create real attack scenarios is the most valuable part of a pentest report. The fact that you used a low-severity information disclosure to identify an internal service, then leveraged a misconfiguration on that service to escalate privileges, tells a story that no automated system can construct from individual findings alone. Attack path narratives require the pentester's memory of what happened during the engagement and their understanding of how each step enabled the next. This contextual thread is what separates a pentest report from a vulnerability scan export.
Business impact is specific to each client. A SQL injection on a marketing site and a SQL injection on a banking application have the same CVSS score but vastly different business consequences. Only a pentester who understands the client's business can assess actual impact. Similarly, final quality assurance - verifying that every finding is accurate, every screenshot is relevant, and the report reads coherently - cannot be outsourced to automation. And report delivery itself involves reading the room, answering questions, and explaining technical concepts to non-technical stakeholders. These are fundamentally human interactions.
The workflow for an automated pentest report follows a predictable pipeline. Understanding the steps helps you know where automation fits and where you take over. Step 1: Input your raw findings. You paste notes, tool outputs, or structured data from any source - Burp Suite exports, Nmap results, manual testing notes, or even screenshots with annotations. The system accepts unstructured input because the whole point is to eliminate the formatting step from your workflow.
Step 2: AI processes through the pipeline. PentestReportAI runs a 5-step pipeline on your input. It parses findings into structured vulnerabilities, assigns CVSS 3.1 scores with full vector strings, maps each finding to CWE and OWASP categories, generates professional descriptions with remediation steps, and creates an executive summary that synthesizes all findings into business language. Each step builds on the previous one, so the output is internally consistent.
Step 3: Review and edit. This is where you apply your expertise. Read through the generated findings, verify CVSS scores match your assessment, adjust remediation steps for client-specific constraints, and add attack path narratives that connect individual findings. The AI draft gives you a 90% starting point - your review turns it into a 100% finished product. Step 4: Export. Choose your template and output format - PDF or DOCX - and the system applies formatting, generates the table of contents, and produces the final deliverable. The entire process from raw notes to export takes minutes instead of hours. Read how I cut report writing to 15 minutes for a real-world walkthrough of this pipeline in action. The pentest report automation guide covers the fundamentals of setting up this kind of workflow.
Not every reporting tool offers the same level of automation. The market breaks down into three tiers, and understanding which tier you need prevents you from overpaying for features you will not use or under-buying and still spending hours on manual work. Tools: Microsoft Word, Google Docs with templates. You write every word, calculate every CVSS score, format every table.
Templates save some layout time but the content creation is entirely on you. This is where most pentesters start and where many stay longer than they should. The time cost per report is typically 3-6 hours depending on finding count and report complexity. Tools: Pwndoc, Dradis, GhostWriter. These tools provide structure - finding templates, reusable libraries, automated formatting - but the actual vulnerability descriptions, scoring, and summaries are still manually written. They reduce formatting time and improve consistency across engagements but do not touch the content creation bottleneck. Typical time savings: 30-40% compared to fully manual approaches.
Tools: PentestReportAI, PenReport. AI-powered end to end, these tools handle content generation, scoring, classification, formatting, and summary creation. You provide raw input and review the output. The automated pentest report generation covers everything from parsing through final formatting. Time savings: 70-85% compared to fully manual workflows, reducing a 4-hour report to 30-45 minutes of review and customization.
The jump from semi-automated to mostly automated is where the biggest time savings happen. Moving from Word to Pwndoc saves you formatting headaches. Moving from Pwndoc to an automated pentest report generator saves you the actual writing - which is where most of your reporting time goes. If you are still manually writing finding descriptions, calculating CVSS vectors, and formatting reports in Word, you are spending hours on work that an automated pentest report pipeline handles in minutes. The parts that need your brain - scope, attack paths, business impact, final review - deserve your full attention. The mechanical parts do not deserve any of your time.
PentestReportAI automates the tedious 80% so you can focus on the expert 20%. Start with a $3 report credit or choose a monthly plan to use the complete AI pipeline - CVSS scoring, CWE mapping, finding descriptions, remediation steps, executive summary, and formatted output. Test it with your real findings and see how the output compares to what you write manually.
The gap between raw technical scan data and actionable business intelligence has long been a bottleneck in penetration testing engagements. Security professionals spend countless hours translating Nmap XML outputs, Nessus findings, and vulnerability scanner results into polished executive summaries that non-technical stakeholders can understand and act upon. With the emergence of Generative AI and LLM-powered automation frameworks, this traditionally manual and labor-intensive process is being revolutionized. Tools leveraging Claude AI, RAG architectures, and MCP (Model Context Protocol) now enable security teams to transform raw diagnostics into structured, prioritized remediation advice and financial risk assessments in minutes rather than days.
The modern approach to penetration testing reporting follows a structured pipeline: raw scan output → data normalization → AI analysis → structured report generation. Raw scan outputs from tools like Nmap, Nessus, Nuclei, and Burp Suite contain valuable data but are incomprehensible to non-technical stakeholders. The pipeline begins with uploading network scan diagnostics to an LLM such as Claude AI, which then extracts business loss impact, generates financial risk scenarios, and produces structured remediation advice.
Several open-source frameworks now automate this entire workflow. VulnReport, for instance, accepts CVE IDs or raw Nmap/Nessus scan output and instantly generates professional reports with severity ratings, technical analysis, attack scenarios, and remediation steps. The VAPT Report Generator ingests outputs from multiple scanners (Nmap, Nessus, Nuclei, Burp, ZAP, Acunetix), normalizes findings into a unified model, applies CVSS v3.1 scoring, and renders polished reports in PDF, Word, HTML, or Excel. For full automation, frameworks like AutoPentester—an LLM agent-based system—complete the entire pentest lifecycle from information gathering to report generation with minimal human intervention.
To build a robust AI-powered reporting pipeline, you need to configure the right environment and tools. Most frameworks run on Kali Linux (preferred) or Ubuntu 20.04+ with Python 3.8+, minimum 8GB RAM, and administrative privileges. One of the critical functions of AI-powered reporting is translating technical findings into business impact assessments. Tools like the Security Automation Tools script automatically classify open ports by risk level—Critical, High, Medium, or Low—and provide specific remediation recommendations.
| CRITICAL | FTP, Telnet, rexec, shell, login | Direct exploitation vector; data breach within hours | | HIGH | MySQL, PostgreSQL, SMTP, SMB, VNC | Significant exposure; credential theft possible | | MEDIUM | SSH, HTTP, DNS, SNMP, Tomcat | Manageable but needs proper configuration | | LOW | HTTPS | Generally fine with standard security practices | The core of modern pentest reporting is structured, consistent output that can be automatically generated and customized for different audiences. Tools like OWASP VISTO generate comprehensive security reports summarizing findings, categorizing vulnerabilities, and providing prioritized remediation steps. The RAG-based Pentest Report Generator uses ChromaDB for vector storage and LLM integration to produce detailed reports with executive summaries, methodology, findings, risk analysis, technical details, and remediation roadmaps.
For organizations with mature DevSecOps practices, AI-powered pentest reporting can be integrated directly into CI/CD pipelines. The Penetration Testing Claude Skill provides GitHub Actions workflows that automatically run security assessments on pull requests and generate reports. This enables continuous security validation and immediate feedback to developers.
Key Takeaway 2: Open-source frameworks like VulnReport, VAPT Report Generator, and AutoPentester provide accessible, production-ready solutions for automating the entire pentest lifecycle—from reconnaissance to report generation—with minimal human intervention. Security teams no longer need to build these capabilities from scratch. Analysis: The convergence of LLM technology with traditional penetration testing tools is creating a new paradigm for security assessments. Claude AI’s semantic understanding capabilities enable context-aware vulnerability detection and false positive filtering that goes far beyond simple pattern matching. The emergence of agentic frameworks like PentestGPT and AutoPentester demonstrates that autonomous security testing—where AI agents drive the entire engagement from reconnaissance to reporting—is becoming a reality. However, this automation comes with important considerations: data sovereignty concerns when using public LLM services, the need for human oversight of dangerous actions, and the importance of validating AI-generated findings. The most effective approach combines AI automation for efficiency with human expertise for validation and complex decision-making.
+1 The integration of RAG architectures with local LLMs will address data sovereignty concerns, making AI-powered pentesting viable for government and highly regulated industries. -1 Over-reliance on AI-generated reports without human validation may lead to missed vulnerabilities or false positives being accepted as truth, necessitating robust quality assurance processes.
+1 Agentic frameworks that autonomously drive the full pentest kill chain will democratize security testing, enabling organizations with limited security resources to conduct regular, comprehensive assessments. -1 The attack surface of AI-powered pentesting tools themselves—including API key exposure, prompt injection, and model manipulation—will become a new vector for adversaries to exploit.
4. Practical Deployment, Analysis & Case Studies +1 Continuous security reporting integrated into CI/CD pipelines will shift security left, enabling developers to receive immediate, contextualized vulnerability feedback during the development process. Secure, high-velocity infrastructure and disruptive technological engineering. Contact our engineering team for high-tier development and proprietary systems: [email protected] I Smart Architecture | II Secure by Design | I Trusted by Thousands Reported By: https://lnkd.in/p/egzfPb4z – Hackers Feeds Extra Hub: Undercode MoN Basic Verification: Pass I We do not sell your personal data. If you wish to exercise your rights under applicable privacy laws, please visit our Do Not Sell My Personal Information page.
PeTeReport ( Pe n Te st Report ) is an open-source application vulnerability reporting tool designed to assist pentesting/redteaming efforts, by simplifying the task of writting and generation of reports. Focused in product security, the tool help security researchers and pentesters to provide detailed findings, appendix, attack paths and manage a finding template database to avoid wasting time spent in the reporting phase.
PeTeReport ( Pe n Te st Report ) is written in Django and Python 3 with the aim to help pentesters and security researchers to manage a finding repository, write reports (in Markdown) and generate reports in different formats (HTML, CSV, PDF, Jupyter and Markdown). From vulnerability discovery to client-ready PDF in minutes. AI fills findings, CVSS, CWE references, and remediation.
Description, impact assessment, CVSS 3.1 vector with score, CWE and OWASP references, and concrete remediation steps, filled from just a vulnerability title. Review, tweak, ship. The login endpoint concatenates the email parameter directly into a SQL query without parameterization. An unauthenticated attacker can inject a UNION-based payload to enumerate the entire users table...
Every finding follows CVSS 3.1. Severity colors are consistent across the editor, the PDF, the share link, and the CSV, so your clients never have to translate. Yes, two ways. The free plan gives you 2 PDF reports per month, unlimited Markdown exports, 5 AI calls per month, and the built-in CVSS 3.1 calculator with no credit card. Or start the 7-day Pro free trial to test every Pro feature end-to-end.
Yes. Monthly Pro signups get a 7-day free trial with full access to every Pro feature — bulk AI enhance, DOCX / HTML / CSV / JSON export, white-label branding, 200 AI calls, and the rest. A card is required at signup, but you won't be charged until day 7. Cancel any time before then and you pay nothing. Claude by Anthropic. It generates descriptions, impact assessments, CVSS 3.1 vectors with scores, CWE and OWASP references, and concrete remediation steps from a finding title. Free users get 5 AI calls per month; Pro users get 200.
Yes. Generate a read-only shareable link, your client sees a clean report view with no install or account required. Revoke the link anytime. Data is stored in encrypted Postgres. Passwords use Argon2id. Sessions are database-backed, never JWT. We never store your data in plain text.
Free users export PDF and Markdown. Pro unlocks DOCX, HTML, CSV, and JSON. Every format includes a cover page, executive summary, severity breakdown, and color-coded findings. Yes. Cancel from your billing settings. If you're inside the 7-day trial window, you won't be charged at all. After the trial, you keep Pro access until the end of your current billing period.
Yes. Pay annually and save 30%, $100 per year instead of $143.88. Toggle the period on the pricing page to see the annual price. The 7-day free trial is available on monthly billing. Your next report should take 30 minutes, not three days. Generate your first one free; it’ll take you about five. Forget investing in a separate pentest report generator. Penti has you covered as an automated penetration testing reporting tool that pulls data from multiple tools and integrated security scans, lets you bring your own data sources, and produces professional pentest reports ready for clients, auditors, and decision makers.
Penti's platform automates pentest reports end-to-end, eliminating days of manual work in pentest reporting time and delivering high quality reports ready for both technical teams and stakeholders same day testing concludes – every report and every engagement. Here's what you get when pentest report generation is built into the same platform as the testing itself – comprehensive reports, AI-driven prioritization with human validation, and a unified view of every engagement.
Penti runs many different pentest engagements: Web App, API, Network, Mobile, Cloud, IoT, Agentic AI, plus compliance-specific tests (SOC 2, ISO 27001, PCI DSS, HIPAA, GDPR, NIST) and industry-specific ones (FinTech, Healthcare, SaaS, LLM, Critical Infrastructure, and more). Your final report changes with the engagement. Below are four sample reports from common engagement types. Pick the one closest to your scope to see what your report will look like.
This report shows the deliverable from a Penti Agentic AI Penetration Testing engagement on a Web Application + API. Penti's Agentic AI autonomously executes multi-step attack chains and continuously re-tests the surface; certified pentesters review and contextualize every finding through a Human-in-the-Loop process. Supplementary scanners (Burp Suite Pro, OWASP ZAP, Nuclei, OpenVAS, Securily Headers Scanner) run in parallel on a quarterly cadence, all consolidated into one unified report. Methodology follows OWASP Top 10 2021, OWASP ASVS, NIST Cybersecurity Framework, and SOC 2 Trust Services Criteria. Inside you'll find the full scope, the tool stack, a side-by-side findings table per scanner source (unique to Agentic engagements), the manually validated findings, the OWASP Risk Rating methodology (Likelihood × Impact) and Scanner Factors (Severity, Confidence), Tier 1/2/3 prioritized remediation, the re-testing schedule, the disclosure, and the team's certifications.
This report shows the deliverable from a manual Web Application & API Penetration Test by certified pentesters. Methodology follows OWASP Top 10 2021, OWASP ASVS, OWASP API Security Top 10, PCI DSS, and NIST SP 800-95. Testing covers external-facing apps, authenticated portals, admin interfaces, and RESTful / GraphQL / SOAP APIs, across the full stack, from injection attacks to business logic to client-side security. Inside you'll find the full scope, the manual tool stack (Burp Suite Pro, OWASP ZAP, Caido, mitmproxy, SQLMap, Nuclei, Postman, GraphQL Voyager, and more), per-finding documentation with code snippets for remediation (BAD vs GOOD examples), reproduction steps with payloads, testing process, Compliance Impact mapping per finding (OWASP, CWE, PCI DSS, NIST, plus HIPAA and GDPR where applicable), Tier 1/2 prioritized remediation, the re-testing schedule, the disclosure, and the team's certifications.
This report shows the deliverable from a manual Network Penetration Test covering external perimeter, internal network, VPN, cloud infrastructure (Azure), and Active Directory. Methodology follows OWASP Top 10 & ASVS, MITRE ATT&CK Enterprise, and the NIST Cybersecurity Framework, with expertise in network pentesting, Active Directory and domain security, credential-based attacks, lateral movement, privilege escalation, and post-exploitation techniques. Inside you'll find the full scope (IP ranges, VPN endpoints, cloud, AD infrastructure), the tool stack (Nmap, BloodHound, Impacket, Mimikatz, Responder, Rubeus, CrackMapExec, Hashcat, Metasploit, PowerShell Empire, and more), the Finding Factors (Severity + Confidence), per-finding documentation with reproduction steps, Compliance Impact mapping per finding (SOC 2, ISO 27001, PCI DSS, HIPAA, GDPR, NIST), Tier 1/2/3 prioritized remediation, the re-testing schedule, the disclosure, and the team's certifications.
This report shows the deliverable from a Reconnaissance & Attack Surface Mapping engagement, a Penetration Test Evidence Log format that's deliberately distinct from the three full pentest reports above. It captures the external attack surface of a target, IP intelligence, open services, technologies, TLS posture, WAF presence, and ends with recommendations tied to the discovered exposures (the sample's recommendations include conducting a focused follow-up web application assessment on the exposed admin interface). Inside you'll find the target intelligence (IP, cloud provider, ASN, WHOIS organization, geolocation, reverse DNS), open ports and service banners, raw tool commands and outputs (whois, httpx, wafw00f, nmap -sV, nmap --script ssl-cert, ffuf), the attack surface inventory with discovered endpoints and technologies, the reconnaissance narrative with risk assessment, an evidence summary, recommendations tied to discovered exposures, and a final status line summarizing the mapped surface.
Our penetration testing report tool has shown remarkable performance across security projects and pentest reports, automating what used to take days of manual work in report creation. Run your next penetration testing engagement with Penti and see immediate value. Traditional pentests take 3–4 months from request to results, and you wait days more for the report to be written, reviewed, and polished, then pay $15k–$40k for a static PDF that “sits on a shelf until next year.” Penti replaces manual pentest reporting with an automated penetration testing report tool that runs the same OWASP and PTES methodology manual penetration testers use, delivering an audit-ready report as soon as testing concludes.
5. Performance Evaluation & Extended Technical Observations Don't invest in a separate pentest report writing tool – Penti's pentest reporting software delivers both comprehensive pentesting and AI-driven reporting at a fraction of the cost and time spent by traditional vendors. No more waiting days for pentest reports to be written, reviewed, and polished. Penti's pentest reporting tool delivers clean, actionable full reports with AI-driven prioritization as soon as testing ends – your team can save time, manage fixes, and start remediation immediately.
Our reports speak both languages – security teams and engineers get individual findings with code-level evidence and clear remediation steps, while executives, auditors, and decision makers get an executive summary aligned with business context and impact. Penti reports map findings to SOC 2, ISO 27001, PCI DSS, HIPAA, GDPR, and NIST (per-finding Compliance Impact blocks, mapping varies by engagement type), providing ready-to-use documentation for your next audit, customer request, or security reporting review.
Penti doesn't just generate static reports – the dashboard consolidates findings from multiple tools and integrates with your workflow to manage and track remediation end-to-end. Penti is the pentest reporting software that consolidates multiple tools and vulnerability scanning outputs into one single report. Every Penti engagement uses an industry-standard toolkit of pentest tools, with results captured and presented in a unified deliverable that documents the exact tools used, payloads, and reproduction steps for each finding.
Every Penti pentest report maps findings to the frameworks your auditors and customers ask about – automatically. No more cross-referencing multiple tools or external documentation at audit time. For security leaders turning to AI to stay ahead of threats and minimize costs, Penti provides the ideal solution. Penti's service is a game changer for our compliance needs. The insights we gained were invaluable for our team. Doing this well is crucial for our compliance targets and key in advancing our strategic initiatives.
The integration between Penti, our system, and third parties like Vanta is exceptional. I would also like to mention that their response times are extremely fast! Penti has been like having an experienced and nimble Security Engineer on staff. They have outlined issues in our platform and guided us towards implementations and fixes that allow for us to ensure we are treating our users data with the utmost care.
Browse more of Penti's essential features making your pentesting journey easy and effective. Ready to replace manual pentest reporting with a faster, cleaner platform built for real action? Try Penti's all-in-one pentest report tool and generate audit-ready, branded reports in just a click – ready for your clients, auditors, and decision makers. No. You don't need a separate pentest report writing tool – reporting is built directly into the Penti platform. As soon as testing concludes, full reports are export-ready in your dashboard for download or sharing.
Yes. Penti supports branded headers, logos, and template customization, so branded reports match your internal or client-facing standards. Absolutely. Reports include automatic mappings to SOC 2, ISO 27001, PCI DSS, HIPAA, GDPR, NIST, simplifying audit prep and demonstrating ongoing security posture.
Yes. Reports combine results from AI-driven vulnerability scanning and human-led testing by certified penetration testers, presenting individual findings with verified evidence for a complete view. Almost instantly. Once a pentest is complete, your full reports are generated and ready for download or sharing – cutting reporting time from days to near-instant delivery and letting your team save time that would otherwise go into manual report writing. New vulnerabilities discovered in subsequent tests flow into the same report automatically.
A traditional pentest report takes days of writing, review, and polish – and you pay for the pentester's time on top of the engagement. Penti's penetration testing report generation tool automates report creation end-to-end, with reports available almost instantly once testing concludes – and the manual work of consolidating findings from multiple tools is replaced by auto-ingestion from Penti's integrated scanners.
Can red teams and external penetration testers use Penti reports for client deliverables? Yes. Penti runs a Channel Partner program. Red teams and external penetration testers can use Penti as their primary pentest report generator, with branded reports carrying their own headers and logos, the same proven structure (Scoping → Methodology → Risk Rating → Manual Assessment → Prioritized Remediation → Re-testing) used in every professional pentest report Penti delivers, and templates for each engagement type (Web App & API, Network, Agentic, Reconnaissance).
The executive summary gives decision makers report composition, key findings counts (Critical / High / Medium), most significant findings, impact assessment, positive security controls observed, and prioritized recommendations (Immediate / Short-term / Medium-term) – written in business context language without exposing them to raw technical detail. Yes. Every finding carries a live status (Active or Remediated). Your team can track remediation on the dashboard with real-time updates, then trigger re-tests when fixes are deployed – the verified PASS/FAIL status updates inside the same report. Re-test credits are included in the original engagement scope.
Automate your penetration testing reporting with PentestPad's comprehensive pentest reporting tool. Generate professional pentest reports automatically, collaborate with your team, and deliver results through a secure client portal. Save 80% of your report writing time while maintaining the highest quality standards. Schedule a live demo of our pentest reporting tool and see how automated report generation, collaboration features, and the client portal can transform your penetration testing workflow.
Transform your penetration testing findings into professional reports instantly. Our pentest report automation generates comprehensive documentation including executive summaries, technical findings, CVSS scores, and remediation steps - all automatically formatted and ready to deliver. Choose from industry-standard pentest report templates that follow OWASP, NIST, and PTES methodologies. Each template includes pre-structured sections for vulnerability documentation, risk assessment, and compliance requirements including SOC 2, ISO 27001, and PCI DSS.
Enable seamless pentest collaboration with real-time editing, comments, and review workflows. Multiple team members can work on the same penetration testing report simultaneously, track changes, and maintain version control throughout the assessment lifecycle. Share findings securely through our dedicated pentest client portal. Clients can review vulnerability details, track remediation progress, request retests, and download final reports - all within a secure, branded environment that maintains professional communication.
See how our pentest reporting tool saves time, improves collaboration, and delivers professional results every time. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Transaction%20authentication%20number • https://en.wikipedia.org/wiki/Surfshark%20VPN • https://en.wikipedia.org/wiki/PhpBB • https://github.com/pwndoc/pwndoc • https://github.com/pwndoc-ng/pwndoc-ng • https://blackstork.io/blog/pentest-report-template/ • https://www.pentestreportai.com/blog/automated-pentest-reporting • https://undercodetesting.com/from-raw-nmap-scans-to-executive-reports-automating-penetration-test-reporting-with-ai-video/ • https://1modm.github.io/petereport/ • https://penreport.app/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Automated Pentest Report Generator.
[*] Metasploit Scan Running on Target Subnet for Automated Pentest Report Generator... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |