Complete Technical Paper Content — Automated Reentrancy Attack Detection In Smart Contracts
Overview & System Context
Automated Reentrancy Attack Detection In Smart Contracts: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9554 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background A specialized, automated security scanner designed to identify all variants of reentrancy vulnerabilities in your smart contracts with high accuracy and minimal false positives.
Build secure, auditable smart contracts for tokens, DeFi, and NFTs on EVM-compatible chains. We architect and deploy production-grade smart contracts that are secure by design. Our development process integrates formal verification and industry-standard audits to mitigate risks before deployment. Deliver a secure, gas-optimized, and fully documented contract suite in 2-4 weeks , ready for mainnet launch.
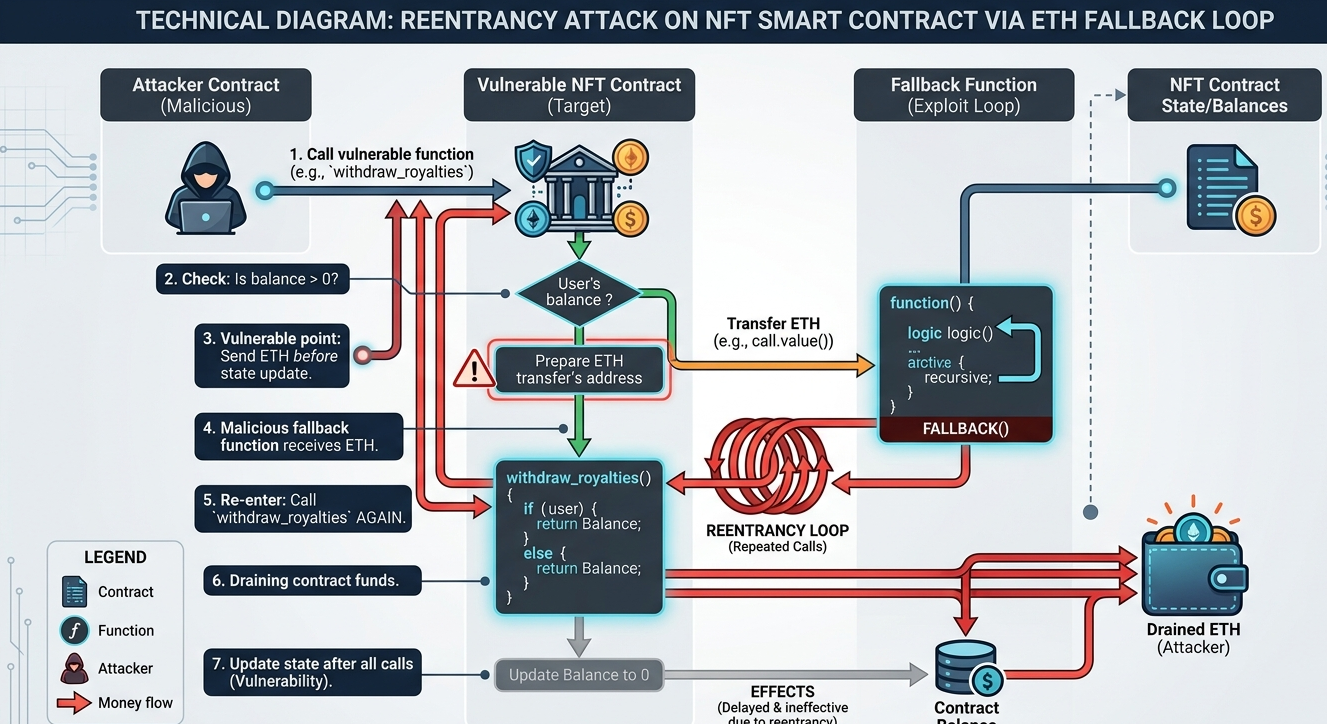
Figure 1: Smart Contract Security for NFT Projects: What You Must Know ... Our automated detection system combines symbolic execution, static analysis, and transaction simulation to identify reentrancy vulnerabilities with enterprise-grade accuracy and speed. We perform deep bytecode and source code analysis to map all potential reentrancy entry points and state variable interactions, identifying high-risk patterns before runtime.
Our engine explores all possible execution paths to find hidden state inconsistencies and complex call chain vulnerabilities that simple scanners miss. We simulate malicious transactions in a forked mainnet environment, testing contracts against known and novel attack vectors with real-world conditions.
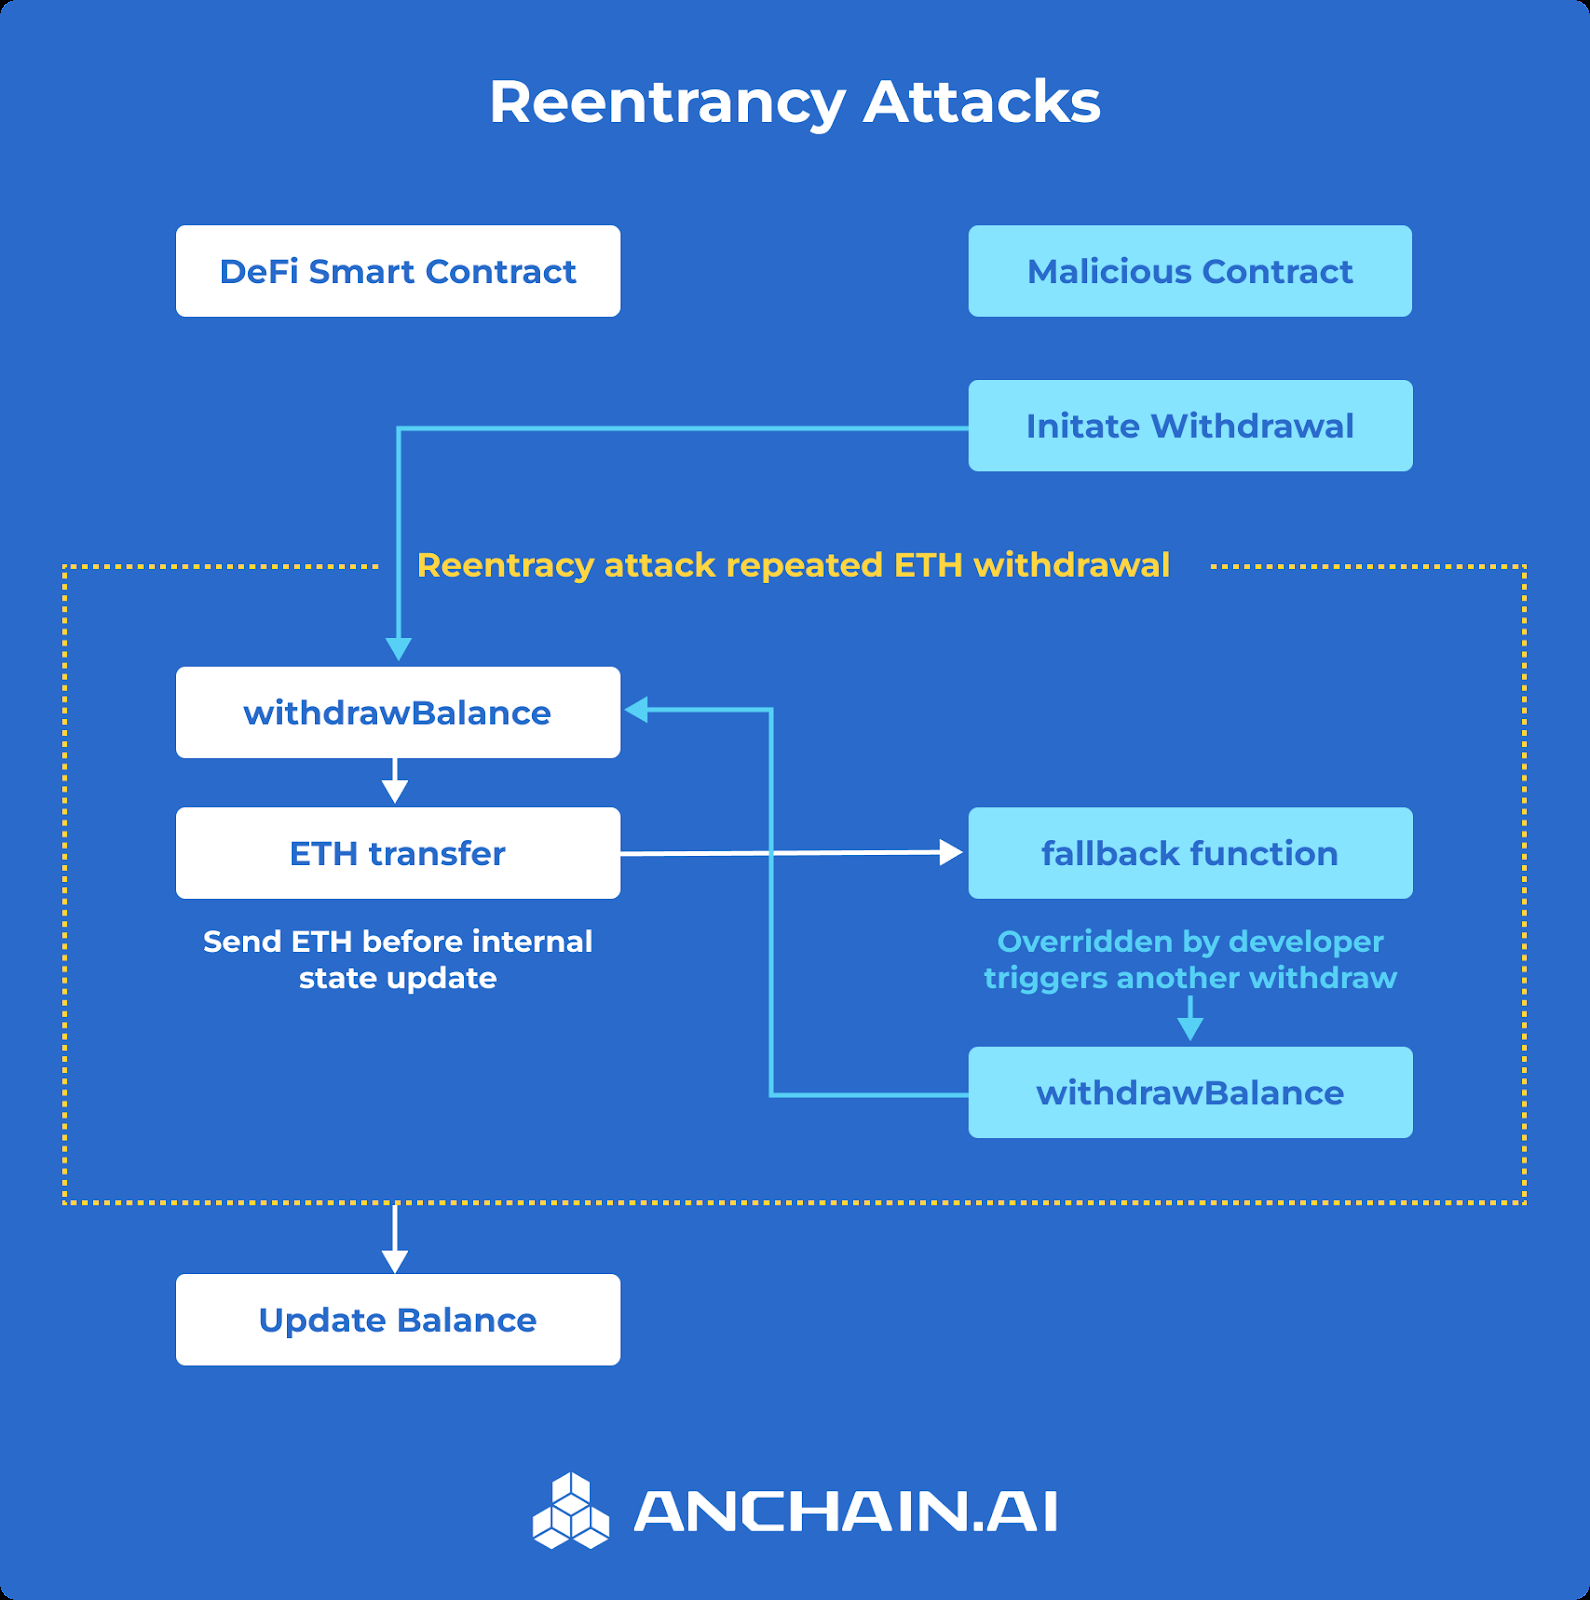
Figure 2: The Smart Contract Threats You Need To Know Receive a detailed vulnerability report with CVSS scores, exploit proof-of-concept code, and step-by-step remediation guidance for your engineering team. Generic vulnerability scanners miss the nuanced, protocol-specific attack vectors that lead to catastrophic exploits. Our service delivers targeted, high-fidelity detection engineered for production-grade DeFi and NFT applications.
We map detection logic to your specific architecture—whether it's a custom AMM, lending protocol, or NFT marketplace. This context eliminates false positives and catches logic flaws generic tools miss. Our engines simulate thousands of contract state permutations and complex transaction sequences to uncover deep, multi-step reentrancy paths that static analysis cannot see.
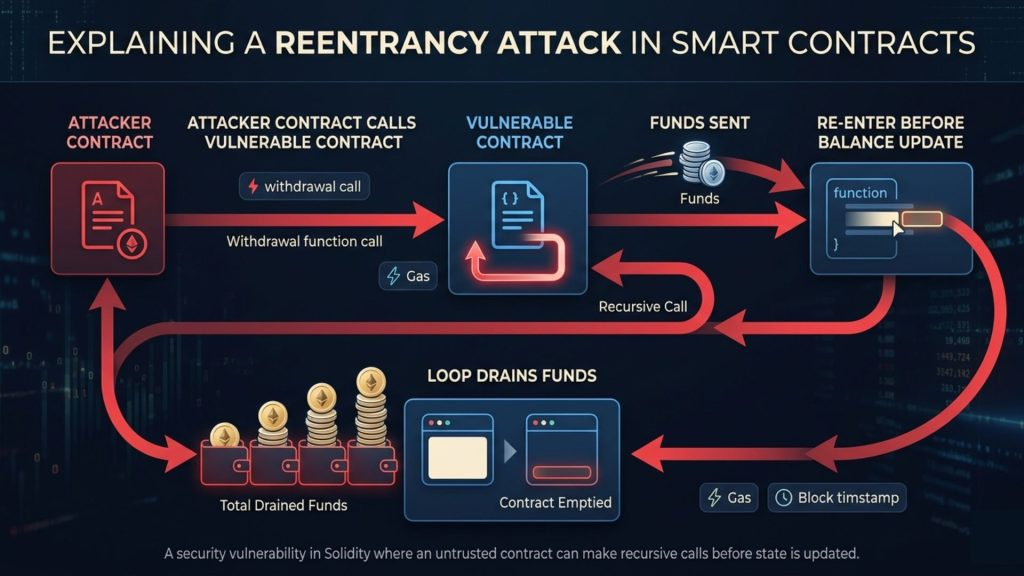
Figure 3: Smart Contract Security: Common Vulnerabilities & Solutions ... We complement dynamic testing with formal methods to mathematically prove the absence of reentrancy vulnerabilities in core financial logic, providing the highest assurance level. Every finding includes a reproducible exploit script and a detailed, audited remediation patch. We don't just report issues; we deliver the fix.
Generic security scanners often miss the nuanced patterns of reentrancy attacks. Our automated detection service is purpose-built for identifying these critical vulnerabilities with precision. Our automated detection system combines static analysis, dynamic fuzzing, and formal verification to identify reentrancy vulnerabilities with high precision and minimal false positives.
We perform deep static analysis on your contract's compiled bytecode to identify potential reentrancy patterns, including non-standard function signatures and complex call graphs that source-level tools often miss. Our system executes your contracts in a forked mainnet environment, simulating millions of adversarial transaction sequences to trigger and confirm reentrancy conditions that static analysis alone cannot catch.
For critical state variables and functions, we apply formal methods to mathematically prove the absence of reentrancy under specified invariants, providing the highest level of security assurance. Receive a detailed, actionable report that classifies findings by severity (Critical, High, Medium), provides exploit PoC code, and delivers clear remediation guidance with patched code examples.
After you implement fixes, we re-run our full detection suite on the updated code to verify the vulnerability is resolved, ensuring no new issues were introduced during the patching process. We integrate our detection engine into your CI/CD pipeline to automatically scan every pull request and deployment, preventing reentrancy bugs from reaching production.
Get clear answers on our automated reentrancy detection service, from methodology to pricing and support. Our system performs a multi-layered static and dynamic analysis of your Solidity code. It uses symbolic execution to trace state changes, pattern matching for known attack vectors (like the classic DAO pattern), and custom heuristics for novel reentrancy variants. We analyze the entire call graph, checking for violations of the Checks-Effects-Interactions pattern and unsafe low-level calls. The final report categorizes findings by severity (Critical, High, Medium) with precise line numbers and remediation steps.
For a standard protocol (e.g., a DEX, lending platform, or NFT mint), the full engagement takes 7-10 business days . This includes 3-5 days for automated scanning and initial report generation, followed by 2-3 days for manual review and validation by our senior security engineers, and 1-2 days for client review and final report delivery. Complex protocols with custom logic or multiple integrations may extend this to 2-3 weeks. We provide a firm timeline after the initial code review.
We offer transparent, fixed-price packages based on the size and complexity of your codebase. A typical audit for a protocol with 1-5 core contracts and under 2,000 lines of code starts at $8,000 . For larger deployments, pricing scales based on SLOC (Source Lines of Code) and protocol complexity, with most projects falling in the $15,000 - $50,000 range. The quote includes the full automated scan, manual verification, a detailed report, and a remediation review session.
Delivery is not the end. All engagements include 30 days of post-audit support . This means we schedule a walkthrough of the report, answer developer questions, and review your fixes for the identified vulnerabilities at no extra cost. For critical issues, we prioritize re-scanning. We also offer extended support SLAs with guaranteed response times (e.g., 4-hour for Critical issues) for ongoing development cycles.
While our service is optimized for deep reentrancy detection, our analysis engines concurrently check for a broad range of critical vulnerabilities . This includes logic errors, access control flaws, integer overflows/underflows, unsafe ERC standards usage, and gas optimization issues. You receive a comprehensive security report, with reentrancy threats highlighted. Our tools are built on experience from securing over $500M+ in TVL across 50+ DeFi projects.
We primarily audit EVM-compatible smart contracts written in Solidity (versions 0.8.x+) for Ethereum, Polygon, Arbitrum, Optimism, Base, and other L2s. We support Foundry, Hardhat, and Truffle project structures. For non-EVM chains (e.g., Solana, Cosmos, Starknet), we offer a manual security review service by our specialists. We recommend submitting your code with the standard development environment for the most accurate analysis.
Security is our first principle. All code is analyzed in our isolated, air-gapped sandbox environments . We sign comprehensive NDAs before any code transfer. Our team operates on a strict need-to-know basis, and all analysts have undergone background checks. We never reuse or reference client code in other projects. Our internal systems are SOC 2 Type II compliant, and we can accommodate specific security protocols for enterprise clients.
Yes. We offer a CI/CD integration package that allows you to run targeted reentrancy checks on every pull request. This uses a lightweight version of our scanner to catch regressions and new vulnerabilities early. It plugs directly into GitHub Actions, GitLab CI, or other platforms, providing pass/fail gates and inline code comments. This is separate from our full audit service and is typically priced as an annual subscription based on scan volume.
Production systems our engineers design, build and run, scoped to what you are working on. Smart contracts, DeFi, wallets, tokenization and infrastructure across the ecosystems teams choose today, plus other networks on request. Reentrancy is the vulnerability class that taught Ethereum developers to distrust external calls. In June 2016, an attacker drained approximately 3.6 million ETH from The DAO (then the largest crowdfunded project in history) by exploiting a single recursive call path in a withdraw function. The fork that returned the funds split Ethereum into ETH and ETC, and reentrancy entered the permanent canon of smart contract security risks.
Nearly a decade later, reentrancy vulnerabilities still appear in audit reports and post-mortem analyses. The attack surface has grown more nuanced ( cross-function reentrancy exploits shared state across multiple entry points, and read-only reentrancy uses view functions as a window into mid-execution protocol state), but the root cause is identical in every variant: an external call is made before the contract's own state is finalised, and a malicious callback exploits the inconsistency.
Reentrancy is no longer the dominant loss driver it once was, 2024's aggregated incident data puts it at roughly 8% of documented DeFi exploits and 5% of dollar losses, well behind access control and logic-error failures , but the Penpie incident that year shows the pattern remains fully exploitable whenever a callback path is left unguarded. See reentrancy exploits and historic loss totals in our DeFi incident index for documented cases across protocol generations.
Reentrancy occurs when a Solidity function makes an external call to another contract, and that contract calls back into the original function (or a related one) before the first invocation has returned. Because Solidity state changes are not committed until a function fully executes, the re-entering call observes the contract's old state, typically a balance or accounting variable that has not yet been decremented.
The vulnerability is not in the callback mechanism itself (external calls are necessary for any useful protocol) but in the ordering of state changes relative to external calls. The checks-effects-interactions (CEI) pattern is the primary architectural defence against reentrancy. It mandates a specific ordering for every function that makes an external call: When the balance update happens before the external call, a re-entering withdraw() sees a zero balance on the second invocation and reverts. CEI is language-agnostic and applies equally to Vyper, Rust (Solana anchor), and Move. Review the checks-effects-interactions pattern definition and canonical code examples for the full formal treatment.
A reentrancy guard is a boolean mutex that reverts if a protected function is entered while it is already executing. OpenZeppelin's ReentrancyGuard is the standard implementation: The modifier should be applied to every external function that modifies balances or interacts with other contracts. Guards cost approximately 2,300 gas per call due to the storage read and write on _status , but the EIP-1153 transient storage opcode ( TSTORE / TLOAD ) introduced in the Dencun upgrade reduces this to around 100 gas for protocols that adopt it.
CEI and a reentrancy guard together are defence-in-depth: CEI makes the state consistent before any external call, and the guard prevents re-entry even if a developer inadvertently violates CEI in a refactor. Using only a guard without CEI leaves a window for certain cross-function reentrancy patterns that the mutex alone does not block if the re-entrant function is unguarded.
Cross-function reentrancy occurs when the attacker's callback calls a different function than the one currently executing, but both functions share the same state variable. A nonReentrant modifier on withdraw() alone does not prevent a malicious callback from calling deposit() or transfer() if those functions are not also protected. Example: a lending protocol's liquidate() function calls the collateral token's transfer() , which triggers a callback in a malicious token. The callback calls the protocol's borrow() using stale collateral accounting (not yet updated by the ongoing liquidation), securing an undercollateralised loan.
The mitigation requires consistent application of the guard and CEI ordering across all functions that access shared state, not just the function that makes the external call. Auditors map the protocol's state dependency graph to identify which functions share write access to the same variables, then verify that all paths enforce the same ordering and locking discipline. The Penpie 2024 $27M exploit demonstrates exactly this failure mode: cross-protocol batch reentrancy missed because the vulnerable registerPenpiePool function was added to the codebase after Watch Pug and Zokyo audits closed , and the reward-harvesting reentrancy path required cross-function state reasoning across the full integration graph.
2. System Architecture & Core Working Principles Read-only reentrancy is a variant where the malicious callback does not write to the victim contract at all: instead, it calls staticcall into a view function on the victim, reading state that is mid-update and therefore inconsistent. The nonReentrant guard cannot be applied to view functions (they are state-read-only by definition and the standard guard pattern stores state). If an external protocol reads a price or balance from a view function during a callback window, it observes stale or inconsistent data.
How a compiler-level reentrancy bug triggered $73M in losses across the Curve ecosystem is the canonical read-only reentrancy case study. In July 2023, a Vyper compiler bug reintroduced missing reentrancy locks in certain pool contracts. Protocols that read Curve pool state during their own callback flows received corrupted prices, enabling attackers to drain funds from those protocols indirectly.
Mitigations include: avoid reading state from external contracts during callback-exposed flows, use time-weighted or checkpoint-based price reads instead of spot view calls, or adopt the EIP-1153 transient storage pattern to create view-compatible reentrancy locks that persist only within a transaction. OpenZeppelin Contracts v5.1 shipped a ready-made implementation of this pattern, ReentrancyGuardTransient , which adds a nonReentrantView modifier alongside the standard nonReentrant one: a protocol can guard its own view functions so they revert (rather than return stale data) when queried mid-reentrancy. The modifier only protects networks where EIP-1153 is available (post-Dencun EVM chains), and it only closes the window for view functions on the contract that adopts it, so external protocols reading a different , unguarded contract's views remain exposed.
Several token standards define mandatory callbacks that execute arbitrary code during a transfer: Any protocol that initiates one of these token operations before completing its own state updates is exposed to reentrancy through the callback. ERC-777 is particularly dangerous because it fires hooks on both the sender and recipient; a malicious token registered as an ERC-777 can use the send hook to re-enter the protocol before the balance check updates. Many protocols now explicitly blocklist ERC-777 tokens. The Cream Finance 2021 $18.8M exploit via the ERC-1820 AMP token transfer hook is the clearest illustration of this class: a Compound v2 fork did not account for the ERC-1820 callback AMP triggers during transferFrom, enabling a 17-step flash loan reentrancy cycle that drained the pool before the balance accounting could catch it.
For complete ERC-20, ERC-721, and ERC-1155 token audit scope (including which callback patterns auditors verify against reentrancy and how custom tokenomics expand the attack surface) see the token contract security audit guide covering fee-on-transfer tokens, approval flows, and integration risks . Reentrancy detection combines automated and manual analysis. How static analysis and fuzzing tools surface reentrancy vulnerabilities explains the tooling in detail; the short version: Static analysis : Slither's reentrancy-eth , reentrancy-no-eth , and reentrancy-events detectors are the starting point, but they produce false positives . Manual review is required to confirm that flagged patterns are genuinely exploitable rather than safe-by-CEI-ordering.
Cross-function graph : Auditors construct a call graph identifying every function that: (a) writes a shared state variable, and (b) makes an external call. Every pairing of such functions that shares a state variable is a potential cross-function reentrancy surface. Read-only reentrancy audit : Auditors trace which view functions are called by other protocols on-chain during transaction execution. Any view function that can return stale data during a reentrancy window, particularly price or balance views, is flagged as a protocol integration risk even if the contract itself is hardened.
Proof-of-concept : Confirmed reentrancy findings are always accompanied by a working exploit PoC to demonstrate exploitability and confirm the proposed fix fully closes the window. Reentrancy describes any situation where a smart contract performs an external call (to another contract or address), and the callee can call back into the original contract before the first invocation has completed and state has been fully updated. If the caller is not designed to be reentrancy-safe, the callback can observe stale state and exploit it—e.g., withdrawing more than the caller’s balance, double-counting rewards, or manipulating accounting across complex multi-step flows.
This affects all contract types that perform external calls: DeFi (token transfers, DEX swaps, vault deposits/withdrawals, flash loan callbacks), NFTs (transfers with ERC-721/ERC-1155 receiver hooks, marketplace payouts), DAOs (proposal execution that invokes external contracts), bridges (message relay, asset transfers), and composable protocols (ERC-777 hooks, ERC-4626 deposit/withdraw hooks). Reentrancy can be single-function (same function called recursively), cross-function (callback into a different function), or cross-contract (callback traverses multiple contracts). On non-EVM chains, analogous patterns exist wherever cross-program invocations can recurse.
A DeFi protocol loses money to a reentrancy bug almost every month in 2026, and the pattern barely changes. GMX V1 lost $42 million in July 2025 to a reentrancy flaw in its order-execution logic. Solv Protocol lost $2.7 million in March 2026 the same way. FutureSwap, Ekubo, and a handful of smaller protocols followed with losses ranging from $74,000 to $1.4 million, all tracing back to external calls made before internal state got updated. According to OWASP’s 2026 Smart Contract Top 10, reentrancy remains one of the most common root causes of exploited code, right alongside access-control mistakes and logic errors.
None of this is exotic. Reentrancy has had a name and a fix since the DAO hack in 2016. What’s changed is the tooling: static analyzers like Slither now catch most reentrancy patterns before deployment, and test frameworks like Foundry make it fast to write an actual exploit against your own contract before someone else does. This tutorial walks through setting up that workflow end to end — from a vulnerable contract, to a static-analysis pass, to a working proof-of-concept exploit test, to the fix, to a CI pipeline that keeps the bug from coming back.
You’ll build a small vault contract with an intentional reentrancy bug, break it with a real attacker contract inside a Foundry test, patch it three different ways, and wire Slither into GitHub Actions so the next contributor can’t reintroduce the same mistake. By the end you’ll have a repository you can reuse as a template for every contract you ship after this one. Add Shattered once in the Google app and our stories show up in your news suggestions.
Reentrancy happens when a contract calls out to an external address (another contract, or an EOA via a fallback function) before it finishes updating its own state. If that external call hands control back to the attacker, the attacker’s code can call back into the original function while the first call is still mid-execution — withdrawing funds, minting tokens, or opening positions multiple times against a balance that hasn’t been decremented yet.
The 2025-2026 incident list shows the pattern hasn’t gone away just because it’s well documented. GMX V1’s $42 million loss came from executeDecreaseOrder accepting an attacker-controlled address as a refund recipient, then transferring control to it mid-transaction, per Halborn’s post-mortem and OWASP’s own case study. Yearn’s yETH pool lost roughly $9 million on November 30, 2025 after an attacker minted 235 septillion yETH from just 16 wei of input, a related class of accounting bug documented by Check Point Research. Smaller, less headline-grabbing hits kept landing through the first half of 2026: FutureSwap lost $74,000 on January 14 in a straightforward reentrancy attack on Arbitrum, and an unverified Ethereum mainnet contract lost about $11,000 on March 23 to the same bug class, according to BlockSec’s weekly incident roundup.
What ties these together isn’t a lack of awareness — every Solidity course covers the checks-effects-interactions pattern — it’s that manual review misses the interaction under time pressure, and small or mid-size teams often ship without running a static analyzer or writing an actual exploit test. This tutorial fixes both gaps. Reentrancy isn’t even the single biggest category of DeFi losses right now. A smart contract audit landscape report covering 2026 attributes $953.2 million in losses to access-control vulnerabilities, versus $63.8 million to logic errors and $35.7 million to reentrancy specifically, per Blockeden’s analysis. That ranking matters for how you should prioritize your own review time: reentrancy testing catches a well-understood, well-tooled bug class, but it’s one item on a longer checklist that also needs to cover who’s allowed to call privileged functions and whether your math handles edge-case inputs correctly. The table below lines up a sample of 2025-2026 incidents so you can see how the loss sizes and root causes compare.
Every one of these was, in hindsight, a known bug class with a known fix. None of them needed a novel attack technique. That’s the argument for building the workflow in this tutorial into your normal development loop rather than treating it as a pre-launch checkbox. You don’t need prior smart contract security experience, but you should be comfortable writing basic Solidity and running commands in a terminal. Install the following before you start: Foundry is the primary tool here because its Solidity-native tests make writing an actual attacker contract fast — no separate JavaScript test harness needed. We’ll also touch on Hardhat 3.14.0 near the end for teams already standardized on it.
Start with a clean Foundry project. Run forge init to generate the standard layout with src/ , test/ , and lib/ directories. Confirm the compiler version pin in foundry.toml so builds are reproducible across machines: Delete the default src/Counter.sol and its test file — you won’t need the boilerplate example for this exercise. Create src/VulnerableVault.sol . This is a simple ETH deposit/withdraw vault with the classic bug: it sends ETH to the caller before it zeroes out their balance.
The bug is on the line ordering: call fires before balances[msg.sender] = 0 runs. If the recipient is a contract with a receive() function, that function executes during the call, and it can call withdraw() again while the original balance is still non-zero. Before writing a single test, run Slither against the contract. Static analysis catches this class of bug in seconds, without needing to simulate an attack.
Slither 0.11.5 flags exactly the line that matters: a state variable written after an external call. This is the same class of finding Slither’s reentrancy-eth and reentrancy-no-eth detectors would raise on GMX V1’s code, per OWASP’s writeup of that incident. Getting a clean Slither run doesn’t guarantee a contract is safe, but a flagged reentrancy warning on a fund-moving function should never ship without review.
Static analysis tells you where to look. A proof-of-concept exploit tells you whether it’s actually exploitable, and how bad the damage is. Create src/Attacker.sol : The attacker deposits a small amount, calls withdraw() , and its receive() fires mid-transfer — re-entering withdraw() up to five more times before the first call ever gets to zero out the balance.
Now prove it in a test, using Foundry’s cheatcodes to fund accounts and assert on balances. Create test/Reentrancy.t.sol : The trace shows the attacker’s receive() calling back into withdraw() before the first call ever reaches the line that zeroes the balance. Both Alice’s and Bob’s deposits get drained even though the attacker only put in 1 ETH. The cheapest fix costs nothing in gas or dependencies: reorder the function so state updates happen before the external call.
Create src/SafeVaultCEI.sol : Now the attacker’s receive() still fires, but when it calls withdraw() again, balances[msg.sender] is already zero, so the require(amount > 0) check reverts the reentrant call. Checks-effects-interactions is the fix, but a modifier-based guard is cheap insurance against a future contributor reordering the function by accident. OpenZeppelin’s ReentrancyGuard uses a transient-storage-backed lock as of Contracts v5.4.0.
Belt-and-suspenders here matters because real incidents keep showing up in code that had the checks-effects-interactions pattern in most functions but missed it in one. Use both: order state updates correctly, and add nonReentrant on every function that moves value. Update the test file to target both patched contracts and confirm the attack now fails.
Run the full suite and confirm both the original exploit passes (proving the bug exists) and the patched versions revert on the reentrant call: A single exploit test proves one attack path. Foundry’s fuzzer and invariant testing catch paths you didn’t think to write by hand. Add a fuzz test that randomizes deposit amounts: For invariant testing, define a handler contract that randomly deposits, withdraws, and attacks across many pseudo-random call sequences, then assert the invariant that address(vault).balance >= sum of all balances never breaks across thousands of runs. Foundry's default invariant run count in foundry.toml is controlled by [invariant] runs = 256 and depth = 15 — raise both for contracts handling real funds.
A local scan is only as good as the discipline to run it every time. Wire both tools into GitHub Actions so every pull request gets scanned automatically. Create .github/workflows/security.yml : 3. Software Implementation, Frameworks & Protocols The --fail-high and --fail-medium flags make the CI job exit non-zero when Slither finds high- or medium-severity issues, blocking the merge until someone reviews the finding. Low- and informational-severity findings still print in the job log but won't block the merge, which keeps the gate useful without turning every style nit into a blocked pull request. Adjust the thresholds as your team's tolerance changes — a protocol handling real user funds should eventually run with --fail-medium on by default, while an early prototype might start with only --fail-high to avoid noise while the codebase is still shifting.
Add a second job to the same workflow file that runs on a schedule rather than per-PR, since a full Mythril pass or an extended fuzz run ( forge test --fuzz-runs 50000 ) is often too slow to run on every commit but is worth doing nightly against the main branch. The vault example above covers classic reentrancy, where the attacker drains funds directly. A subtler variant, read-only reentrancy, doesn't touch the vulnerable contract's own funds at all — it exploits a view function that returns a stale, mid-transaction state to a second, integrated protocol (like a price oracle reading a pool's reserves mid-swap). A DEV Community security writeup flagged read-only reentrancy as a contributing factor in several of the roughly $86 million in DeFi losses tracked across January 2026 alone.
To test for it, write a Foundry test where a second "consumer" contract reads a price or exchange-rate view function from inside the attacker's receive() callback, and assert that the value returned matches the post-settlement state, not a mid-transaction snapshot. Slither's reentrancy-no-eth detector flags some of these cases, but not all — manual test coverage on any function another contract might call as an oracle is still necessary.
No single static analyzer catches everything. Slither is fast and has a low false-positive rate on reentrancy specifically, but pairing it with a symbolic-execution tool like Mythril adds coverage for bugs that need path exploration rather than pattern matching (integer issues, unchecked external call return values, complex access-control logic). Mythril runs slower than Slither because it explores execution paths symbolically rather than just parsing the AST, so most teams run Slither on every commit and Mythril on a scheduled nightly job or before a release, not on every push.
The Slither and Foundry setup you just built isn't a single-purpose reentrancy scanner. Once it's wired into your repository, the same commands surface several other vulnerability classes that show up just as often in the 2025-2026 incident data, sometimes for bigger dollar amounts than reentrancy itself. Access control gaps were the single largest loss category in the Blockeden report cited above, at $953.2 million. Slither's arbitrary-send-erc20 and unprotected-upgrade detectors flag functions that move funds or change implementation addresses without an onlyOwner -style check. Write a Foundry test that calls every state-changing function from a random, non-privileged address with vm.prank(makeAddr("attacker")) and assert it reverts — this single pattern would have caught the KiloEx exploit, where an unprotected MinimalForwarder contract let an attacker drain roughly $7 million across three chains in April 2025.
Integer and rounding errors cost Truebit $26.2 million in January 2026 through an overflow in a bonding curve, and contributed to Balancer V2's $128 million loss the previous November. Solidity 0.8.x reverts on overflow by default, but bonding-curve and AMM math often uses unchecked blocks or fixed-point libraries where the checked-arithmetic safety net doesn't apply. Foundry's fuzzer is the right tool here: run forge test --fuzz-runs 10000 against any function doing multiplication before division, and watch for reverts or unexpected zero results at extreme input values.
Unverified or unaudited third-party calls are a growing target specifically because attackers know smaller teams skip Slither's more expensive checks on contracts they call but don't own. Chainalysis flagged this pattern directly, noting that attackers increasingly target unverified contracts precisely because their bytecode hasn't been through public review. Add slither . --exclude-dependencies to focus scans on your own code, but don't skip a manual review of every external contract address your protocol calls before mainnet deployment.
Both frameworks can run the exact test pattern above. The difference is language and speed of the reentrancy-simulation loop. If your team already has a Hardhat 3 deployment pipeline, you don't need to migrate everything to Foundry just for security testing — Hardhat 3 added first-class Solidity test support specifically to close this gap, per Nomic Foundation's own release notes. But writing the attacker contract and its callback logic is still faster in a Solidity-native test, which is why most audit firms use Foundry for exploit proof-of-concepts regardless of which framework the production repo uses.
Once the basic workflow is running, a few upgrades pay off on any contract that will hold real value. First, add a differential test that runs the same exploit scenario against both the vulnerable and patched versions in a single test function, asserting the vulnerable one loses funds and the patched one doesn't. This documents the fix's effectiveness directly in the test suite, which is useful evidence during an external audit.
Second, use Foundry's forge coverage to check that your reentrancy tests actually exercise the vulnerable line, not just the surrounding function. A test suite with 90% line coverage can still miss the one branch where the bug lives. Third, if the contract will hold significant value, budget for a professional audit on top of this workflow, not instead of it. Firms like Trail of Bits and OpenZeppelin publish their own reentrancy checklists (Trail of Bits' own analysis of the Balancer V2 incident is a good example); running Slither and Foundry tests before an audit engagement means the auditors spend their time on the logic bugs a tool can't catch, instead of re-discovering issues automated tooling would have found for free.
Fourth, consider the Ethereum Foundation's bug bounty structure as a backstop, not a substitute. The Foundation raised its maximum bug bounty to $1,000,000 for critical protocol-level vulnerabilities, per Cryptorank's reporting on the program — a strong incentive that exists precisely because pre-launch testing, however thorough, doesn't catch every path. Fifth, keep a written record of every finding you triage and dismiss, whether from Slither, Mythril, or a human reviewer. When Slither flags something as a false positive in your slither.config.json , note why in a comment next to the entry. Six months later, when a new contributor reopens the same question, that one-line note saves a re-investigation and keeps institutional knowledge from walking out the door with whoever made the original call.
Testing before deployment reduces risk, but it doesn't eliminate the value of watching your contract in production. Several of the 2026 incidents in the table above involved attackers probing a contract for days or weeks before finding a working exploit path, which means monitoring can sometimes catch an attack in progress before it drains the full balance. Set up a simple alert using Foundry's cast tool to watch for unusually deep call stacks or repeated calls to the same function within a single transaction. A basic version uses an event emitted on every withdrawal, then a script that flags any block where the same address triggers the event more than twice in one transaction hash: For production systems, most teams graduate from a homemade cast script to a dedicated monitoring service (Forta, OpenZeppelin Defender, or an in-house indexer) that can page an on-call engineer and, in some setups, automatically pause the contract through a circuit-breaker function. If you add a pausable pattern, test the pause function itself for reentrancy and access-control issues with the exact same workflow covered above — a broken emergency stop is its own category of incident.
Run forge test -vv && slither . --fail-high --fail-medium one more time before committing, and you have a repeatable template: drop in a new contract, write the attacker, prove the exploit, patch, and re-prove the fix, every time. No. Slither is very good at catching the classic pattern of an external call followed by a state write, but it can miss logic-level reentrancy that spans multiple functions or contracts. Pair it with an actual exploit test in Foundry, and consider a second analyzer like Mythril for symbolic-execution coverage.
It prevents single-function reentrancy, where the attacker re-enters the same function. It does not automatically prevent cross-function reentrancy, where shared state is manipulated through a different function during the callback. Combine it with a nonReentrant guard for defense in depth. What's the gas cost difference between checks-effects-interactions and a ReentrancyGuard? Checks-effects-interactions costs nothing extra; it's just reordering existing statements.
OpenZeppelin's transient-storage-backed ReentrancyGuard in Contracts v5.4.0 adds a modest gas overhead per protected call for the lock write and check, which is worth it on any function moving user funds. Foundry's Solidity-native tests and built-in fuzzing make writing exploit proof-of-concepts faster, which is why most audit firms default to it. Hardhat 3.14.0 added first-class Solidity test support, so teams already standardized on Hardhat's TypeScript deployment tooling don't need to migrate their whole stack just to run these tests.
Run it on every pull request via CI, and again whenever Slither ships a new detector release, since new detectors can flag patterns in code that passed a scan months earlier. Slither 0.11.5, released in January 2026, added a new reentrancy-balance detector as one example. Read-only reentrancy exploits a view function that returns stale mid-transaction state to an external protocol reading it as a price or exchange-rate oracle. It doesn't drain the vulnerable contract's own funds, so standard reentrancy tests can miss it.
Write a separate test where a second contract reads your view function from inside a reentrant callback and assert the value is correct. No, they're complementary. Running Slither and writing exploit tests before an audit means auditors spend their limited engagement time on subtler logic bugs instead of re-finding issues automated tooling already caught for free, which typically improves the value of the audit rather than replacing the need for one.
Does OpenZeppelin's ReentrancyGuard protect against reentrancy across different contracts I deploy? No. Each contract needs its own guard instance and its own nonReentrant modifiers on value-moving functions. A guard on Contract A doesn't protect Contract B, even if they share state through an external call. Use both; they catch different things. Slither reads your code without executing it and flags known dangerous patterns in seconds, which makes it cheap to run on every commit. Foundry tests actually execute an attack against a running contract state, proving whether a flagged pattern is truly exploitable and confirming your fix works. A clean Slither report with no exploit tests is a false sense of security; a passing exploit test suite that never ran a static analyzer risks missing bug classes you didn't think to write a test for.
Marcus Bell covers applied security: authentication, TLS, phishing, and the everyday decisions that keep accounts and data safe. He focuses on turning advice people usually ignore into steps they will actually follow. Reentrancy is the classic smart contract vulnerability for a reason: it teaches one of the most important audit lessons in Web3 security.
Every external call is a control-flow handoff. If a contract sends execution to an untrusted address before finalizing balances, shares, debt, rewards, or other accounting state, the attacker may be able to re-enter the system while it still believes the old state is true. This guide breaks down how reentrancy works, why the DAO hack changed Ethereum, how modern variants such as cross-function and read-only reentrancy appear in DeFi, and how auditors should test for them in real code.
A reentrancy attack happens when a smart contract makes an external call to an untrusted address before updating relevant internal state, such as a user's balance. If the recipient is a malicious contract, it can call back into the vulnerable contract while the old state is still visible. Repeated calls may pass the same checks and withdraw more than the attacker's recorded balance.
A reentrancy vulnerability is the unsafe design: the contract exposes stale state during an external call. A reentrancy attack is the exploit path that uses that stale state to withdraw, mint, borrow, vote, liquidate, or otherwise change protocol accounting more than once. This distinction matters in audits. A function can look safe in isolation but become vulnerable when a token hook, callback, router, vault, bridge adapter, or another protocol contract can call back into the system before all effects are finalized.
The bank teller hands you $1,000 in cash before updating the account ledger. If you could request another withdrawal before the ledger changed, the old balance would pass the same check again. Repeated withdrawals could empty the bank before the first ledger update. A reentrancy attack exploits the equivalent ordering error in contract code.
Nearly a decade after The DAO, reentrancy still ranks in the top 5 smart contract vulnerability classes reported in 2025. Beyond these three types, read-only reentrancy matters in DeFi protocols because a view function can return stale data during an ongoing state transition. Token standards with callback hooks, including ERC-777 ( tokensReceived ) and ERC-1155 ( onERC1155Received ), also introduce reentrancy paths during transfers.
4. Practical Deployment, Analysis & Case Studies Before marking a protocol safe from reentrancy, do not stop at "it has nonReentrant ". Work through the full call graph: Map every external interaction: ETH transfers, ERC20 transfers, ERC721/ERC1155 safe transfers, ERC777 hooks, callbacks, low-level calls, and arbitrary target calls.
Check state-update order. Balances, shares, debt, reward indexes, collateral flags, and nonce/accounting fields should be updated before control leaves the contract. Look for shared state across functions. A guard on withdraw() does not protect claimRewards() , borrow() , or liquidate() if they read the same stale accounting.
Trace cross-contract flows. Reentrancy can enter through another contract in the same protocol, especially routers, vaults, strategies, hooks, or token adapters. Test read-only reentrancy. View functions used by other protocols should not expose temporarily inconsistent prices, share values, or reserves during state transitions.
Review token standards with callbacks. ERC777, ERC721 safe transfers, ERC1155 safe transfers, and custom hooks can all hand execution back to attacker-controlled code. Verify emergency controls. Pausing, withdrawal caps, and circuit breakers should still work if an attacker reaches an unexpected callback path.
If a finding depends on temporarily stale balances or share prices, also review the related oracle manipulation and flash loan attack patterns because DeFi exploits often chain these assumptions together. For privileged pause, upgrade, and emergency-response paths, review access control attacks as well. The DAO hack exposed a reentrancy flaw that led to the diversion of roughly $60 million in ETH and contributed to Ethereum's 2016 hard fork. It remains an important case because the technical exploit and the response both shaped smart contract security practice.
Launched in April 2016, The DAO was a blockchain-based investment fund governed by token holders. Investors received DAO tokens, voted on funding proposals, and shared returns. The system relied on contract code and token-holder governance rather than centralized management. The attacker used a reentrancy vulnerability in The DAO's withdrawal function to divert 3.6 million ETH (roughly $50-60 million at the time) into a child DAO under their control.
Several security researchers warned about recursive-call vulnerabilities before the exploit, but the required fixes were not deployed in time. The attacker did not bypass the EVM's rules. The vulnerable contract executed its withdrawal logic as written, which intensified the debate about how the community should respond.
In an ecosystem where "code is law" was a common principle, the incident raised a difficult question: should the network preserve the original execution or intervene to return funds? Option A: preserve the original chain history and accept the loss as a consequence of immutability. Option B: change the protocol state through a hard fork so affected users could recover funds.
After extensive debate, the community adopted a hard fork that moved the diverted funds into a recovery contract. The network officially forked on July 20, 2016, at block 1,920,000. Participants who rejected the fork continued operating the original chain, now known as Ethereum Classic (ETC). The incident divided the community and made protocol governance, immutability, and emergency response central security concerns.
The attacker creates a contract with a receive() or fallback() function that calls back into the vulnerable contract's withdraw function. The attacker deposits funds normally, then calls withdraw() . The contract sends ETH before updating the balance. The attacker's receive() function triggers automatically and immediately calls withdraw() again. The balance check still passes because state hasn't updated.
The cycle repeats until gas runs out or the vault is empty. State finally updates - but it's too late. The vault has been completely drained. The attacker can call withdraw() again before line 15 ( balances[msg.sender] = 0 ) ever executes. In a real attack the loop keeps running past the attacker's own deposit and takes every ETH the contract holds.
Preventing reentrancy requires correct state-update order, explicit guards, and review of the full call graph. By updating state before making external calls, even if an attacker re-enters, the state already reflects the completed transaction. Implement a mutex lock that prevents recursive calls. OpenZeppelin's ReentrancyGuard is the industry standard: Warning: This is a weak defense - gas costs can change in network upgrades. Always combine with other protections.
What it does: Ensures all state changes (effects) happen before any external calls (interactions). When to use: Apply this pattern to contracts that send ETH or hand control to external contracts. Limitation: Requires developer discipline - easy to accidentally violate when refactoring. When to use: All payable and state-changing functions in contracts that interact externally.
Limitation: Only protects the contract it's deployed on - cross-contract reentrancy bypasses it. What it does: Uses transfer() or send() which forward only 2300 gas - not enough for a reentrant call. Limitation: Gas costs change with EIPs. This defense broke with the Istanbul fork and is now considered unreliable. The following example combines Checks-Effects-Interactions with OpenZeppelin's ReentrancyGuard .
Zeroing the balance before the external call is exactly the line The DAO's withdrawal function was missing in 2016. Forwards only 2300 gas but is a deprecated defense. Gas costs change with EIPs - the Istanbul fork broke this approach. Never rely on gas limits alone. Mutex lock prevents single-contract reentrancy but doesn't protect against cross-contract or read-only variants. Necessary but insufficient alone.
Checks-Effects-Interactions and ReentrancyGuard address common callback paths. Full protocol review is still required for cross-function, cross-contract, and read-only variants. Any function that makes an external call before updating state is vulnerable - including token transfers, flash loan callbacks, and cross-contract interactions.
ReentrancyGuard only protects functions within the same contract. Cross-contract and read-only reentrancy can bypass it entirely. 5. Performance Evaluation & Extended Technical Observations Solidity 0.8+ only adds overflow protection. Reentrancy is a logic flaw - not an arithmetic one. You still need CEI pattern and ReentrancyGuard.
Read-only reentrancy exploits view functions that read stale state during an ongoing transaction, causing other protocols to make incorrect decisions based on wrong data. Reentrancy can be combined with other exploit techniques. Flash loan attacks can provide temporary capital for an exploit path that depends on protocol accounting or collateral state. The bZx incidents combined borrowed liquidity with callback and accounting weaknesses.
Reentrancy is also related to call attacks and delegatecall vulnerabilities . Reentrancy uses callbacks to observe stale state, while delegatecall vulnerabilities arise from executing external code in the caller's context. Both require careful review of where control leaves the contract. A reentrancy attack is when a malicious contract repeatedly calls a vulnerable function before it finishes executing - like making multiple withdrawals before the bank updates your balance. The attacker drains funds by exploiting the gap between sending ETH and updating state.
Over $200 million has been stolen through reentrancy vulnerabilities since 2016. The DAO hack alone accounted for $60 million, and the 2023 Curve Finance exploit drained over $70 million. No single mechanism covers every variant. Use Checks-Effects-Interactions, apply a reentrancy guard where appropriate, and review cross-function, cross-contract, callback, and read-only paths. These controls provide defense-in-depth but still require protocol-specific testing.
No. ReentrancyGuard protects the functions where it is applied, but cross-contract reentrancy, unguarded sibling functions, read-only reentrancy, and callback-based token flows can still expose stale protocol state. Auditors still need to trace the full call graph. Read-only reentrancy happens when a callback reads a protocol's temporary, inconsistent state through a view function and another contract trusts that value. The view function does not modify state, but the stale price, share value, or reserve value can still cause bad downstream decisions.
No. Any blockchain platform allowing external calls during execution can be vulnerable - including Vyper, Rust (Solana via CPI), CosmWasm, and Move-based chains. The concept applies wherever contracts can call each other mid-execution. If still in development, fix it immediately. If the contract is live: pause it, contact a security firm for emergency response, prepare an upgrade or migration plan, and inform users transparently. Time is critical - attackers scan for known vulnerabilities continuously.
Reading about reentrancy gives you the pattern. Exploiting it in a lab gives you the instinct. Common reentrancy variants are preventable with disciplined design, but complex DeFi variants require full call-graph review. Checks-Effects-Interactions and ReentrancyGuard are starting points, not substitutes for understanding the protocol's state model.
The Smart Contract Hacking course includes hands-on reentrancy exercises along with flash loans , oracle manipulation , access control , and other audit-critical vulnerability classes. If you want to see how the training works first, start with the free lesson or browse the course curriculum . Build your auditing skills with guided exploit exercises in the Smart Contract Hacking course.
Thanks for signing up. We'll email your trial onboarding details within 2-3 business days. Reentrancy is the bug that started it all. The 2016 DAO hack drained roughly $60 million in ETH using exactly this flaw, and a decade later it still shows up in fresh audit reports and post-mortems. An industry review published by Blockeden.xyz in January 2026 attributes a $40 million loss on GMX V1 to a reentrancy exploit, and in March 2026 Solv Protocol’s BitcoinReserveOffering contract was drained of 38.05 SolvBTC (about $2.7 million) after an attacker repeated the same callback trick 22 times in a row. The contract had no formal audit and no bug bounty program, which is exactly the kind of gap this tutorial is meant to help you close.
This is a hands-on walkthrough, not a theory lecture. You’ll scaffold a Foundry project, write a genuinely vulnerable vault contract, build an attacker contract that drains it, watch the exploit succeed in a test run, then patch the bug and prove the patch holds. By the end you’ll have a working project you can drop into any Solidity repo as a template for your own security testing, plus a checklist of the mistakes that make reentrancy tests unreliable. If you’ve already worked through our guides on ERC-4626 inflation attack testing or proxy storage collision testing , this one slots into the same Foundry-based testing habit, just aimed at a different attack class.
Add Shattered once in the Google app and our stories show up in your news suggestions. A reentrancy attack exploits the gap between an external call and a state update. Picture a withdraw function that sends ETH to the caller first and only updates the user’s recorded balance afterward. If the recipient is a contract instead of a plain wallet, its fallback or receive function fires the moment it gets the ETH, and that code can call withdraw again before the first call ever reaches the line that zeroes out the balance. The contract still thinks the attacker has funds left, so it pays out again. And again, until the vault is empty or the attacker’s gas runs out.
The classic version above is called single-function reentrancy, but it’s not the only shape the bug takes. Cross-function reentrancy happens when the re-entry calls a different function that shares the same unguarded state. Cross-contract reentrancy spans two or more contracts that trust each other’s state without rechecking it. Read-only reentrancy is the sneakiest variant: it doesn’t drain funds directly, it just returns a stale or manipulated value from a view function during the callback window, which a second protocol then trusts for a price or collateral check. The Smart Contract Weakness Classification registry catalogs the base case as SWC-107 , and every variant above is a descendant of that same root cause: untrusted external calls happening before state settles.
Why does this keep happening in 2026, nine years after the DAO hack made it famous? Partly because new primitives keep reopening old doors. ERC-777 hooks, ERC-721 and ERC-1155 receiver callbacks, flash loan repayment hooks, and cross-chain bridge message handlers all hand control back to an external address mid-transaction, and each one is a fresh opportunity to reintroduce the bug in code that looks nothing like the original DAO contract. A public incident database tracked by the securitymath/defi-incident-db project logs seven reentrancy incidents totaling $89 million across 2024 and 2025, and a separate estimate from coinlaw.io puts cumulative reentrancy losses since January 2024 above $300 million. Those are dataset estimates rather than a single authoritative count, but the direction is consistent: the bug hasn’t gone away, it’s just moved to new call patterns.
The DAO hack is also why Solidity itself changed. Early Ethereum developers leaned on a 2,300 gas stipend attached to the plain .transfer() and .send() functions, on the theory that such a small gas allowance couldn’t possibly fund a malicious callback. Attackers eventually found ways around that assumption, and the language community shifted its advice toward low-level .call{value: amount}(“”) combined with explicit checks, which is why the vault contract in this tutorial uses .call instead of .transfer. The gas stipend trick bought a few years of false comfort, not a real fix, because the actual bug was always the call-before-state-update ordering, not the gas amount attached to the call.
It’s worth sitting with why audited contracts still get hit. The GMX V1 and Solv Protocol cases above didn’t happen because nobody had heard of reentrancy, they happened because the vulnerable path wasn’t the obvious one. A contract can apply checks-effects-interactions correctly on nine functions and miss it on a tenth that was added later, during a feature update, by a developer who wasn’t thinking about the original audit’s scope. That’s the real argument for writing your own exploit tests rather than relying solely on a point-in-time audit report: tests run again on every future commit, an audit report doesn’t.
You don’t need a blockchain node, a testnet faucet, or real ETH for any of this. Everything runs locally against Foundry’s built-in EVM. Here’s exactly what to have installed before you start. If Foundry isn’t installed yet, run curl -L https://foundry.paradigm.xyz | bash followed by foundryup , then confirm the version with forge --version . Everything below assumes that command prints 1.8.4 or later. If you’re on an older release, run foundryup again before continuing, since gas numbers and trace formatting have shifted across recent Foundry releases, and you want your output to match what’s shown here.
Start with a clean project and pull in OpenZeppelin as a dependency right away, since you’ll need it later for the patched version of the contract. Open foundry.toml and pin the compiler version so your results are reproducible on any machine, then add a remapping so imports resolve cleanly.
Delete the default Counter.sol and Counter.t.sol files that forge init generates. They’re useful as a smoke test that your toolchain works, but they’ll clutter the project once you start adding vault contracts and exploit tests. Create src/VulnerableVault.sol. This is a deliberately broken ETH vault: deposits work normally, but withdraw sends ETH before it updates the caller’s balance, which is the exact pattern that made the DAO hack possible and that still appears in audits today.
Look closely at the withdraw function. The external call on line 11 happens two lines before the balance gets decremented. That gap is the entire vulnerability. If msg.sender is a contract with a receive or fallback function, that function runs during the call{value: amount}(“”) line, while balances[msg.sender] still shows the original, undiminished amount. Now build the contract that exploits the gap. Create src/ReentrancyAttacker.sol. It deposits a small amount, calls withdraw once, and uses its receive function to call withdraw again before the first call finishes.
The reentryCount cap at 10 isn’t a security feature, it’s a safety valve so your own test doesn’t loop until it runs out of gas. Real exploits, like the Solv Protocol case where the attacker repeated the same call 22 times, size that loop to match however much liquidity sits in the target contract. Create test/Reentrancy.t.sol. This test funds the vault with other users’ deposits, funds the attacker, runs the attack, and asserts that the attacker walked away with more ETH than it put in.
You should see a pass, plus a call trace where withdraw appears nested inside itself multiple times before the function ever returns the first time. That nesting is the fingerprint of reentrancy. A typical output looks like this: Numbers matter when you’re writing up a finding for a client or a bug bounty submission. Foundry’s snapshot command captures exact gas usage so you can show reviewers the cost of the exploit, not just a pass or fail result.
That file gives you a single line like ReentrancyTest:testReentrancyDrainsVault() (gas: 187432) that you can diff against future runs. If gas usage suddenly drops after you patch the contract, it’s usually because the exploit loop no longer executes, which is exactly the signal you want to see. Don’t skip this step: reviewers and auditors treat a gas snapshot as evidence, not a test log line they have to take your word for.
Commit the .gas-snapshot file to version control alongside your tests. That turns it into a lightweight regression check on its own: if a teammate’s pull request changes the number without a clear explanation in the diff, that’s worth a second look before merging, even before you read the rest of the code change. There are two fixes you should apply together, not as alternatives. The first is the checks-effects-interactions pattern: update state before making the external call, so there’s nothing left to exploit even if the call triggers a callback. The second is OpenZeppelin’s ReentrancyGuard, which blocks any nested call into a function marked nonReentrant, as a defense-in-depth backstop for cases you didn’t anticipate.
Notice the order swap: balances[msg.sender] -= amount now happens before the call{value: amount}(“”) line, not after. Even without the nonReentrant modifier, an attacker calling back in would see a balance that’s already been zeroed out and hit the require check on the next line. The modifier is there in case a future code change accidentally reorders things again, which happens more often in real codebases than anyone likes to admit.
One detail worth flagging for upgradeable contracts: OpenZeppelin’s newer releases mark ReentrancyGuard and ReentrancyGuardTransient as stateless and no longer transpile them automatically into the upgradeable package. If you’re working in an upgradeable proxy setup, pull the guard from @openzeppelin/contracts-upgradeable directly and call the matching initializer, rather than assuming the import path from the non-upgradeable package still works.
A patch without a test proving it holds is just a hope. Add a test that runs the exact same attack against SafeVault and asserts it fails. Run forge test --match-test testReentrancyBlockedOnSafeVault -vvv and confirm it passes because the attack call reverts, not because nothing happened. If you see a silent pass with zero reverts, double check that the attacker contract is actually calling withdraw and not failing earlier for an unrelated reason, like a missing vm.deal on the attack caller.
The single-function case above is the easiest to catch because the vulnerable and re-entered function are the same line of code. Cross-function reentrancy hides better: function A updates shared state after an external call, and the attacker re-enters through function B, which reads that same state before A ever finishes. To test for it, write a second attacker contract whose receive function calls a different public function on the target instead of calling the same withdraw function again, then check whether that second function trusts stale state.
Harvested Online Documentation & Reference Sources • https://chainscorelabs.com/services/smart-contract-security/automated-security-scanning/reentrancy-attack-automated-dete ction • https://www.smartcontractaudit.com/guides/reentrancy-attack-prevention-guide • https://scs.owasp.org/sctop10/SC08-ReentrancyAttacks/ • https://shattered.io/reentrancy-testing-slither-foundry-2026/ • https://smartcontractshacking.com/attacks/reentrancy • https://shattered.io/reentrancy-attack-testing-foundry-2026/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Automated Reentrancy Attack Detection In Smart Contracts.
[*] Metasploit Scan Running on Target Subnet for Automated Reentrancy Attack Detection In Smart Contracts... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |