Complete Technical Paper Content — Automated Security Operations Center Alert Triage Tool
Overview & System Context
Automated Security Operations Center Alert Triage Tool: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9610 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background In medicine, triage (, ; French: [tIiaI]) is a process by which care providers, such as medical professionals and those with first aid knowledge, determine the order of priority for providing treatment to injured individuals and/or inform the rationing of limited supplies so that they go to those who can most benefit from it. Triage is usually relied upon when there are more injured individuals than available care providers (known as a mass casualty incident) or when there are more injured individuals than supplies to treat them.
The methodologies of triage vary by institution, locality, and country, but have the same universal underlying concepts. In most cases, the triage process places the most injured and most able to be helped as the first priority, with the most terminally injured the last priority (except in the case of reverse triage). Triage systems vary dramatically based on a variety of factors, and can follow specific, measurable metrics, like trauma scoring systems, or can be based on the medical opinion of the provider. Triage is an imperfect practice, and can be largely subjective, especially when based on general opinion rather than a score. This is because triage needs to balance multiple and sometimes contradictory objectives simultaneously, most of them being fundamental to personhood: likelihood of death, efficacy of treatment, patients' remaining lifespan, ethics, and religion.
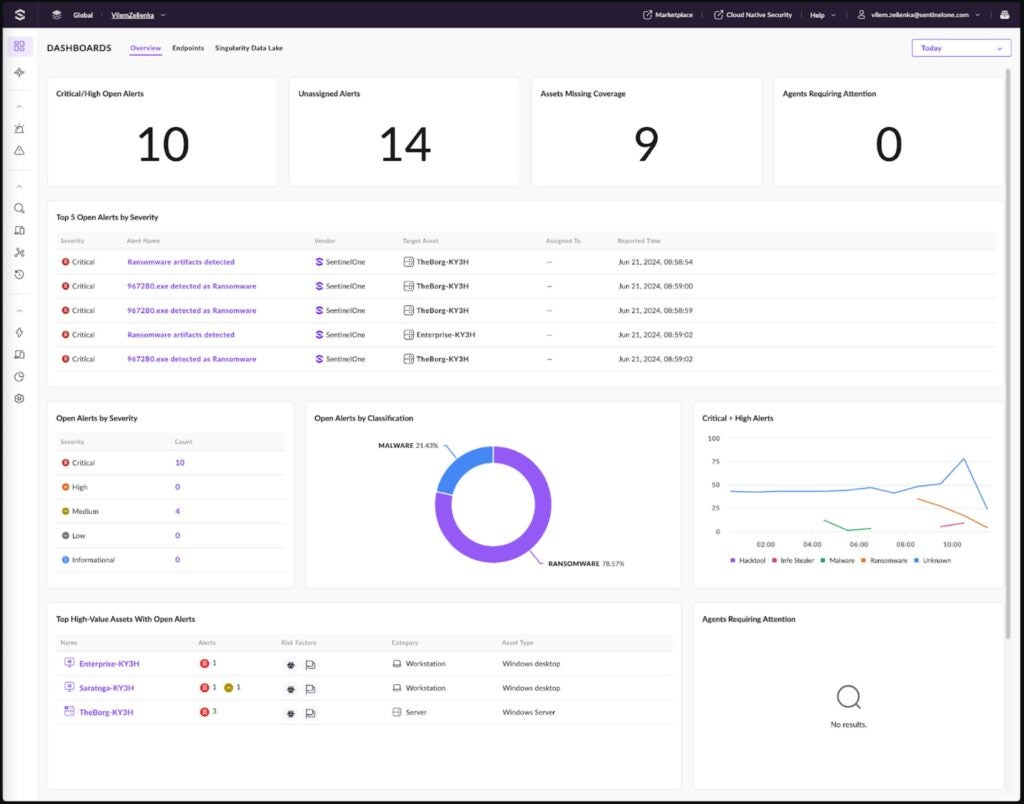
An ABCDE assessment (other variations include ABC, ABCD, ABCDEF, and many others, including those localized to non-English) is rapid patient assessment designed to check bodily function in order of importance. A triage tag is a premade label placed on each patient that serves to accomplish several objectives: Figure 1: Singularity Operations Center | Unified Security Operations for Rapid ...
identify the patient. bear record of assessment findings. identify the priority of the patient's need for medical treatment and transport from the emergency scene. track the patients' progress through the triage process. identify additional hazards such as contamination. Triage tags take a variety of forms. Some countries use a nationally standardized triage tag, while in other countries commercially available triage tags are used, which vary by jurisdictional choice. In some cases, international organizations also have standardized tags, as is the case with NATO. The most commonly used commercial systems include the METTAG, the SMARTTAG, E/T LIGHT and the CRUCIFORM systems. More advanced tagging systems incorporate special markers to indicate whether or not patients have been contaminated by hazardous materials, and also tear off strips for tracking the movement of patients through the process.
"A medical condition I can heal" "A medical condition I intend to fight with." "A medical condition that cannot be healed." Those who are likely to live, regardless of what care they receive; Those who are unlikely to live, regardless of what care they receive; Those for whom immediate care may make a positive difference in outcome. From that delineation, aid workers would follow the Ordre de Triage: In the first order of triage, the injured would be evacuated to clearing stations in the night, when darkness offered maximum protection from the German forces.
Figure 2: Advanced Security Operations Center Displaying Critical Alerts and Risk ... In 1947, the Texas City Disaster occurred when the SS Grandcamp exploded in Texas City, Texas, killing 600 people and injuring thousands more. The entire fire department was killed in the blast, and what followed was a massive informal triage of the victims. Drug stores, clinics, and homes were opened as makeshift triage stations. As the city has no hospital, they had to evacuate casualties to area facilities, including those in Galveston and Houston, with at least one doctor relying on skills he had learned in World War II to inform care decisions.
Most simply, the general purpose of triage is to sort patients by level of acuity to inform care decisions; so that the most people possible can be saved. Although a multitude of systems, color codes, codewords, and categories exist to help direct it, in all cases, triage follows the same basic process. In all systems, patients are first assessed for injuries, then, they are categorized based on the severity of those injuries. Although the number of categories differs from system to system, all have at least three in common; high severity, low severity, and deceased. Some systems involve features like scoring systems, such as the Revised Trauma Score, the Injury Severity Score, and the Trauma and Injury Severity Score, the latter of which has been shown to be most effective at determining outcome.
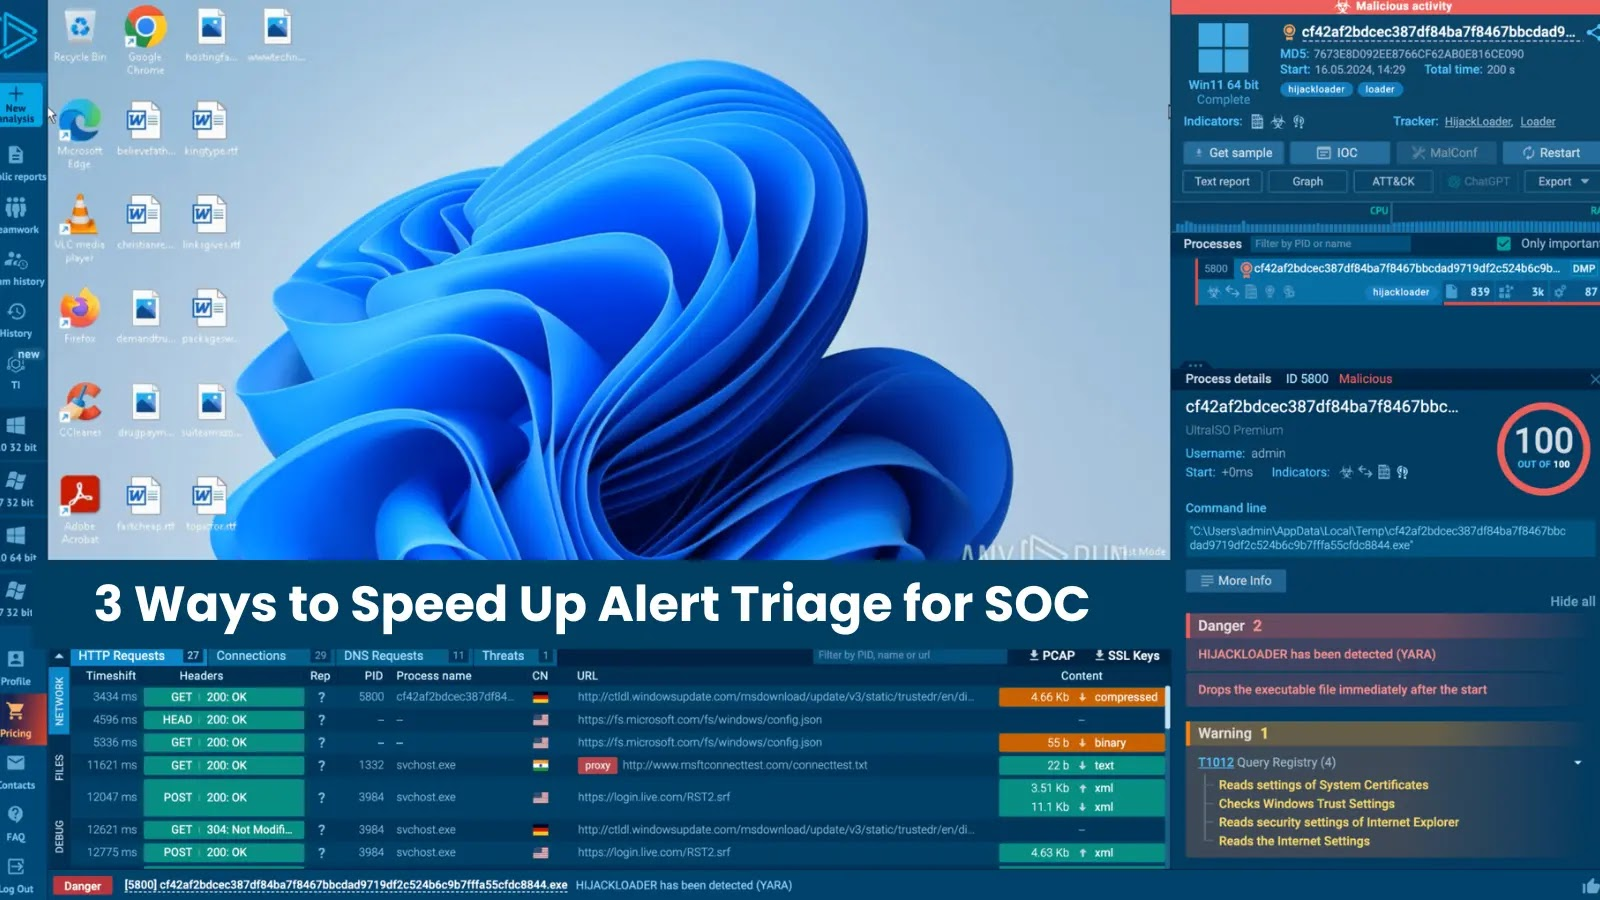
S.T.A.R.T. (Simple Triage and Rapid Treatment) is a simple triage system that can be performed by lightly trained lay and emergency personnel in emergencies. It was developed at Hoag Hospital in Newport Beach, California for use by emergency services in 1983. Triage separates the injured into four groups: The expectant who are beyond help The injured who can be helped by immediate transportation The injured whose transport can be delayed Those with minor injuries who need help less urgently Triage also sets priorities for evacuation and transport as follows: Figure 3: 3 Best Ways to Speed Up Alert Triage for SOC Team: Use Cases Deceased are left where they fell. These include those who are not breathing and repositioning their airway efforts were unsuccessful. Immediate or Priority 1 (red) evacuation to a medical facility as they need advanced medical care at once or within one hour. These people are in critical condition and would die without immediate assistance. Delayed or Priority 2 (yellow) can have their medical evacuation delayed until all immediate people have been transported. These people are in stable condition but require medical assistance. Minor or Priority 3 (green) are not evacuated until all immediate and delayed persons have been evacuated. These will not need advanced medical care for at least several hours. Continue to re-triage in case their condition worsens. These people are able to walk and may only need bandages and antiseptic.
The JumpSTART pediatric triage MCI triage tool is a variation of the S.T.A.R.T. model. Both systems are used to sort patients into categories at mass casualty incidents (MCIs). However, JumpSTART was designed specifically for triaging children in disaster settings. Though JumpSTART was developed for use in children from infancy to age 8, where age is not immediately obvious, it is used in any patient who appears to be a child (patients who appear to be young adults are triaged using START).
The Emergency Severity Index (ESI) is a five-level emergency department triage algorithm, initially developed in 1998 by emergency physicians Richard Wurez and David Eitel, along with emergency nurses Nicki Gilboy, Taula Tanabe, and Debbie Travers. ESI triage is based on the acuity (severity) of patients' medical conditions in acute care settings and the number of resources their care is anticipated to require. This algorithm is practiced by paramedics and registered nurses primarily in hospitals.
In field settings, various standardized triage systems are used, and there is no area wide standard. Décédé (deceased), or urgence dépassée (beyond urgency) Extrême urgence (extreme urgency): requiring care within a half hour. Urgence absolue (absolute urgency): requiring care within an hour. Urgence relative (relative urgency): requiring care, but not immediately. Blessé léger (slightly injured) Impliqué (involved, but not directly injured) This triage is performed by a physician called médecin trieur (sorting medic).
The Manchester Triage System has also been introduced in Germany in 2004, in addition to its German-speaking neighbour countries. The MTS was introduced in Austria in 2009 and in German-speaking parts of Switzerland in 2011 (see also Manchester-Triage-System (in German). Category I: Used for viable victims with potentially life-threatening conditions. Category II: Used for victims with non-life-threatening injuries, but who urgently require treatment. Category III: Used for victims with minor injuries that do not require ambulance transport. Category 0: Used for victims who are dead, or whose injuries make survival unlikely.
The Sistema Estructurado de Triaje (SET), which is an adaptation of the Model Andorrà de Triatge (MAT). The system uses 650 reasons for medical appointment in 32 symptomatic categories, that together with some patient information and basic exploratory data, classifies the emergency within 5 levels of urgency. The "Manchester", based on the system with the same name in the UK, use 51 reasons for consultation. Through some yes/no questions, addressed in a diagram, it classifies the emergency in 5 severities. In mass casualty incidents, the Modelo Extrahospitalario de Triaje Avanzado (META) (Advanced Triage Out of Hospital Model) system is used. META is a seven-stage system, classifying patients as: Red 1st, Red 2nd, Red 3rd, Yellow 1st, Yellow 2nd, Green, and Deceased. The system aligns with the ABCDE framework.
P1 – Patients who have catastrophic bleeding, a penetrating injury or those who are unconscious P2 – Patients who are unable to walk but are conscious P3 – Patients who are able to walk Not Breathing – Patients who are not breathing (this replaces the deceased category) P1 – Life-threatening injury P2 – Unconscious but breathing P3 – Non-life-threatening injury Dead – No signs of life or non-survivable injury lacking the clear goal of maximizing the number of lives saved, as well as the focus, design and objective methodology to accomplish that goal (a protocol of taking the worst Immediate – lowest chances for survival – first can be statistically invalid and dangerous) using trauma measures that are problematic (e.g., capillary refill) and grouping into broad color-coded categories that are not in accordance with injury severities, medical evidence and needs. Categories do not differentiate among injury severities and survival probabilities, and are invalid based on categorical definitions and evacuation priorities ordering (prioritization) and allocating resources subjectively within Immediate and Delayed categories, which are neither reproducible nor scalable, with little chance of being optimal not considering/addressing size of incident, resources, and injury severities and prioritization within its categories – e.g., protocol does not change whether 3, 30 or 3,000 casualties require its use, and regardless of available resources to be rationed not considering differences in injury severities and survival probabilities between types of trauma (blunt versus penetrating, etc.) and ages resulting in inconsistent tagging and prioritizing/ordering of casualties and substantial overtriage Research indicates there are wide ranges and overlaps of survival probabilities of the Immediate and Delayed categories, and other START limitations. The same physiologic measures can have markedly different survival probabilities for blunt and penetrating injuries. For example, a START Delayed (second priority) can have a survival probability of 63% for blunt trauma and a survival probability of 32% for penetrating trauma with the same physiological measures – both with expected rapid deterioration, while a START Immediate (first priority) can have survival probabilities that extend to above 95% with expected slow deterioration. Age categories exacerbate this. For example, a geriatric patient with a penetrating injury in the Delayed category can have an 8% survival probability, and a pediatric patient in the Immediate category can have a 98% survival probability. Issues with the other START categories have also been noted. In this context, color-coded tagging accuracy metrics are not scientifically meaningful. Poor assessments, invalid categories, no objective methodology and tools for prioritizing casualties and allocating resources, and a protocol of worst first triage provide some challenges for emergency and disaster preparedness and response. These are clear obstacles for efficient triage and resource rationing, for maximizing savings of lives, for best practices and National Incident Management System (NIMS) compatibilities, and for effective response planning and training. Inefficient triage also provides challenges in containing health care costs and waste. Field triage is based upon the notion of up to 50% overtriage as being acceptable. There have been no cost-benefit analyses of the costs and mitigation of triage inefficiencies embedded in the healthcare system. Such analyses are often required for healthcare grants funded by taxpayers, and represent normal engineering and management science practice. These inefficiencies relate to the following cost areas: tremendous investment in time and money since 9/11 to develop and improve responders' triage skills cited benefits from standardization of triage methodology, reproducibility and interoperability, and NIMS compatibilities avoided capital costs for taxpayer investment in additional EMS and trauma infrastructure wasteful daily resource utilization and increased operating costs from acceptance of substantial levels of overtriage prescribed values of a statistical life and estimated savings in human lives that could reasonably be expected using evidence-based triage practices ongoing performance improvements that could reasonably be expected from a more objective optimization-based triage system and practices Combat stress reaction Glasgow coma scale Hospital emergency codes Mass decontamination Remote patient monitoring Wilderness first aid SOC automation uses AI-powered systems and rule-based logic to streamline security operations by integrating technologies such as SIEM, SOAR, and cloud-detection tools to automate workflows from alert triage to incident response.
Organizations receive an average of 960 security alerts per day ,with larger enterprises often exceeding 3,000 alerts, leaving nearly 40% uninvestigated due to limited analyst capacity. Grammarly cut its investigation time by 90% using Wiz's AI-enabled workflows, reducing tier-1 triage from up to 45 minutes to just four minutes per ticket.
Automation amplifies analyst expertise through a human-in-the-loop model , where security teams oversee sensitive decisions while automation handles high-volume, repetitive tasks. 2. System Architecture & Core Working Principles Security operations center (SOC) automation streamlines operations using rule-based logic and AI-powered systems to unify security information and event management (SIEM), security orchestration, automation, and response (SOAR), cloud detection and response (CDR), cloud security posture management (CSPM), threat intelligence platforms, ticketing tools, and AI SecOps agents. Automated workflows manage tasks from alert triage to incident response.
Modern SOC automation leverages AI-driven agents that simulate human investigations. AI ingests and analyzes vast datasets, identifies suspicious patterns, and recommends or executes responses based on predefined playbooks. Put AI-driven SOC workflows into practice with ready-to-use prompts for triage, investigation, and response. SOCs face overwhelming alert volumes that often exceed what their team can handle. According to a 2025 industry survey, organizations reported receiving an average of 960 security alerts per day , though larger enterprises often exceeded 3,000.
Nearly 40% of these alerts go uninvestigated due to limited analyst capacity. A growing backlog creates blind spots that allow real threats to slip through undetected. As cyberattacks become more sophisticated and frequent, manual approaches can’t keep pace. Security teams risk SLA breaches, missed incidents, and growing fatigue when relying on manual workflows. SOC automation addresses these challenges by filtering out false positives, prioritizing high-risk alerts, and coordinating response actions across tools and environments.
AI-powered SOC automation augments, not replaces, security analysts. While automation handles high-volume tasks, humans make the final call on complex or high-risk issues. This human-machine collaboration preserves accountability while expanding coverage and improving security outcomes. SOC automation organizes and accelerates security operations by coordinating tools and workflows across all SOC tiers, ensuring that alerts, threat intelligence, and response actions flow through a shared pipeline. Simplified pipelines allow analysts to spend less time on repetitive tasks and more on impactful decisions.
At its core, SOC automation orchestrates multiple systems—including SIEM for security alerts, SOAR for orchestration, CDR, CSPM, threat intelligence platforms, ticketing systems, and AI SecOps agents—so they work together in real time. Centralized data improves threat detection, alert triage, and response coordination without manual intervention. An event triggers an alert to initiate the SOC automation pipeline. After SIEM ingests logs and network telemetry, automation tools enrich each alert with contextual threat data and historical patterns. AI-driven systems then correlate alert context to prioritize alerts, reducing noise and allowing security teams to focus on meaningful risk.
Once automation prioritizes alerts, automated playbooks guide actions such as containment, threat hunting, and escalation. For example, when the system detects suspicious lateral movement, automation may trigger a script to quarantine the affected endpoint and generate a ticket for analyst review. Automation accelerates workflows and improves consistency in incident response at every step.
Tier 2 investigators focus on complex correlations and deeper exploration of threats that automation flags as high risk. Tier 3 experts manage escalated incidents, conduct advanced threat hunting, and refine playbooks in response to emerging threat intelligence. Automation performs many tasks that once consumed Tier 1 and Tier 2 cycles, enabling human analysts to concentrate on judgment-driven work.
When choosing what to automate first, distinguish among tasks your system can execute autonomously, those that require human confirmation, and those that need analyst approval. Focus on these candidates for early automation: However, workflows involving irreversible changes, such as deactivating production identities or shutting down critical workloads, should require explicit human approval.
Human analysts are essential, especially for high-risk decisions and ambiguous scenarios. While SOC automation speeds investigation and containment, security teams provide oversight and judgment that automation can’t replicate. Security teams manage tasks such as: When automation flags a suspicious cloud login, the system enriches the alert with login history and geolocation before recommending actions. Analysts then review the recommendation, confirm legitimacy, and execute a containment workflow if necessary.
A typical automated workflow manages a flagged cloud login attempt by sequencing a set of remediation actions. A user logs in from an unfamiliar location, triggering a SIEM rule. Automation enriches the alert with context by analyzing historical login patterns, VPN activity, and threat intelligence on known malicious IPs. An AI agent then correlates the behavior with recent phishing campaigns and elevates the alert’s priority. That correlation triggers a containment playbook that automatically issues multi-factor authentication challenges and restricts access to risky sessions.
Afterward, the analyst reviews the incident with full context, validates the response, and authorizes deeper remediation, including account suspension or an escalated investigation. The end-to-end flow enables rapid detection and response while keeping analysts focused on critical decisions that require human oversight. Security teams leverage SOC automation to accelerate threat detection, reduce manual workloads, and strengthen incident response. The following three high-value use cases show how automation improves outcomes for security teams within cloud-native environments: Security teams face thousands of daily alerts from SIEM, endpoint detection and response (EDR), and cloud telemetry.
Automated workflows enrich each alert with contextual data, such as user behavior history, threat intelligence, and asset criticality. An AI agent then correlates these signals to prioritize real threats over noise, allowing analysts to focus on alerts that matter. Automation reduces investigation times, lowers alert fatigue, and increases efficiency across every workflow. Manual incident response drains valuable time as analysts gather logs, run queries, and execute containment actions.
Automated SOC playbooks trigger containment steps in real time, including isolating compromised endpoints, blocking malicious IP addresses, and enforcing multi-factor authentication challenges. Automating routine response tasks improves mean time to respond (MTTR) and reduces repetitive workloads, allowing analysts to address complex threats more quickly.
Automation continuously evaluates cloud configurations, network policies, identity permissions, and runtime behavior to identify vulnerabilities before attackers exploit them. When threats cross these risk thresholds, automated workflows escalate issues to SOC teams, generate tickets, and recommend mitigation steps. Continuous risk assessments help security teams maintain better visibility into their security posture and adapt to changes in cloud environments without manual intervention.
As Grammarly scaled from a consumer platform to an enterprise solution, its lean security team faced rising cloud complexity and pressure to maintain high standards. To streamline operations, Grammarly integrated Wiz and later adopted the MCP Server for Wiz to power its AI-enabled workflows. Integrating Wiz’s deep cloud context with natural language pipelines enables the team to pull ticket data, enrich it with context, and orchestrate actions using AI agents to automate alert triage.
Grammarly cut tier-1 investigation times from up to 45 minutes to just four—a 90% efficiency gain. These gains freed its engineers to focus on strategic efforts like threat hunting and detection engineering. 3. Software Implementation, Frameworks & Protocols Grammarly’s success stems from a human-in-the-loop approach: starting small, iterating with real data, and scaling automation gradually. The result was faster response times, improved consistency, and more time for higher-value security work.
See how Wiz Defend automates detection, investigation, and response with full cloud context. Effective SOC automation integrates multiple technologies to ingest data, trigger workflows, and take real-time action. Modern automation stacks feature these foundational tools: SIEM: SIEMs centralize and analyze security data organization-wide. They trigger automation workflows using defined detection rules and integrate with downstream tools for investigation and response.
Extended detection and response (XDR): XDR platforms integrate data from endpoints, networks, cloud workloads, and identity systems to enable automation across a broader threat surface using advanced analytics and context-aware detections. SOAR: SOAR platforms serve as the workflow engine for SOC automation, allowing teams to build and manage playbooks that standardize incident response, enrich alerts, and trigger actions across integrated systems.
Cloud-native security tools: Modern SOCs rely on cloud-native solutions for real-time visibility into cloud workloads, containers, and identities. Cloud-native automation ties directly to ephemeral infrastructure, including runtime detection, misconfiguration management, and cloud forensics. AI agents and large language models: AI technologies automate tasks like alert triage, root cause analysis, and incident summarization. Generative AI agents reason through detection data, summarize incident scope, or suggest next steps in natural language to augment analysts without replacing their judgment.
These technologies form a layered architecture that supports end-to-end automation from detection through remediation. Selecting the right combination depends on your team’s size, maturity, and cloud footprint. SOC automation delivers value across nearly every security role, with benefits that vary by team size, maturity, and operational needs. The following roles see a significant business impact : Security analysts gain efficiency by offloading repetitive tasks like alert triage, log correlation, and evidence gathering.
Automation reduces burnout and enables teams to focus on high-value investigations that require human insight. Incident responders move faster with enriched alerts and standardized playbooks. Automated containment allows teams to shift their attention to verifying impact, coordinating stakeholders, and completing root cause analysis. Security engineers and architects benefit from reduced complexity and increased consistency as automation minimizes configuration drift, improves detection coverage, and standardizes responses.
SOC managers and leaders achieve measurable gains in throughput and coverage without scaling headcount. Automation enables teams to respond to more alerts, lower their mean time to detect (MTTD) and MTTR, and maintain visibility, even with staffing constraints. Cloud security teams benefit from automation that aligns with dynamic infrastructure, as automated checks for misconfigurations, identity misuse, or cloud-native threats help them keep pace with modern attack surfaces.
Automation delivers maximum value to teams struggling with alert volume, limited staffing, or hybrid cloud environments. SOC automation enhances and accelerates established frameworks without requiring teams to abandon current processes. Automated workflows strengthen how teams implement these standards: MITRE ATT&CK : Automation maps alerts and behaviors directly to ATT&CK techniques, which helps teams track adversary tactics more precisely. Automated mapping also supports faster validation and response to behaviors across the kill chain.
NIST Cybersecurity Framework: Automation drives all five functions: Identify, Protect, Detect, Respond, and Recover. Automated systems help teams detect threats in real time, respond with predefined actions, and maintain accurate records for recovery and compliance. Zero Trust architecture : Zero trust models depend on rapid detection and enforcement. Automation enables real-time policy enforcement, identity-based segmentation, and continuous monitoring to align operational reality with zero trust principles.
By integrating into existing frameworks, SOC automation amplifies security posture without friction, ensuring faster and more consistent application of best practices across the threat detection and response lifecycle. Scale your SOC automation using a clear roadmap that aligns with your security objectives, workflows, and team structure. A thoughtful strategy reduces risk, builds trust, and ensures automation delivers measurable outcomes.
Inventory and map your current SOC workflows by documenting existing tools, data sources, alert types, and response processes. Establishing a baseline reveals time-intensive tasks and highlights data quality or integration gaps to address. Prioritize high-impact automation candidates starting with high-volume, repetitive tasks such as alert triage, enrichment, containment for known bad indicators, and correlation across SIEM, endpoint, and cloud logs. Document expected benefits, including faster MTTD, reduced false positives, and improved security posture, to measure success.
Design and test playbooks with human approval gates that include clear execution conditions, required data inputs, and defined actions. Build in approval gates for irreversible decisions, such as disabling production identities or blocking network segments, and verify the logic in a staging environment before going live. Roll out, measure, and iterate by deploying in phases and tracking metrics like alert backlog reduction, time saved per analyst, and MTTR improvement. Use analyst feedback to refine playbooks and address false positives over time.
Automation delivers strong benefits, but it also introduces risks that teams must plan for. Manage common challenges with solid preparation and governance: Security tools that produce inconsistent or incomplete data lead to poor automated decisions. Address these gaps by improving log normalization, standardizing data formats, and strengthening integrations across SIEM, CDR, EDR, and cloud sources. Establish validation checks to ensure automated workflows act on accurate and complete information.
Aggressive automation surfaces unwanted actions or erodes analyst trust. Preserve human judgment by embedding approval gates and defining when automation recommends actions or executes them. Regularly review automated actions and revise playbooks based on feedback from human analysts. 4. Practical Deployment, Analysis & Case Studies Your teams may lack the skills to design, test, and maintain automated workflows, so invest in training on automation tools, playbook development, and analyst-friendly scripting. Encourage cross-team collaboration so security analysts, engineers, and automation specialists can share knowledge and reduce change fatigue.
AI capabilities introduce unique risks, including unexpected behavior and opaque reasoning. Mitigate these risks by requiring explainability, tracking decision-making, and logging actions for auditing. Communicate openly with stakeholders about AI activity, why you chose it, and how analysts retain control over it. Establish clear responsibility for AI-driven decisions so humans remain accountable.
Following a phased approach and planning for common challenges enables your SOC to implement automation that improves outcomes, boosts analyst confidence, and strengthens overall security posture. Wiz automates SOC workflows by connecting cloud context with runtime detection signals. Rather than treating alerts as isolated events, Wiz correlates findings across identity, infrastructure, and workload layers to surface threats that actually matter. With Wiz Agents & Workflows , teams can take SOC automation to the next level through AI-powered investigation and orchestration that removes manual bottlenecks while maintaining human control over critical decisions. Here's how this works in practice: High-fidelity detection: Wiz CDR correlates runtime signals with cloud context through the Security Graph, which maps relationships between resources, identities, and data. This correlation eliminates false positives by showing whether a detected threat actually has a path to sensitive assets.
Automated investigation: Leveraging insights from the Security Graph, Wiz presents analysts with detected events alongside associated incidents. With the Blue Agent, every threat is automatically investigated using AI that reasons through cloud telemetry, runtime signals, and identity context to produce transparent verdicts with full evidence trails. This AI-powered investigation removes the manual pivoting that typically slows down triage, allowing analysts to review pre-investigated threats with clear reasoning and confidence levels. This way, Wiz removes time-consuming repetitive tasks like the manual querying that would ordinarily have been required to piece the details of attacks together and gather additional context.
Automatic correlation between runtime and cloud activity: The Wiz Runtime Sensor links container and workload events to control plane activity, so you can trace an attacker's movement from initial access through lateral movement across your cloud environment. AI-driven containment recommendations: Wiz lets you define autonomous containment actions that are triggered when threats are detected. Through Agentic Workflows, teams can orchestrate how AI operates within their environment, from automated enrichment and correlation to human-in-the-loop approval for sensitive actions. For example, workflows can automatically trigger Blue Agent investigations, route high-confidence findings to automated containment, or request human approval via Slack before taking action on production workloads. And Wiz's AI-driven remediation guidelines take you through threat resolution step-by-step, without missing a beat.
Proactive risk validation and remediation: Beyond reactive response, the Red Agent continuously validates application logic to uncover complex vulnerabilities that traditional scanners miss, while the Green Agent investigates high-risk issues to identify root causes and generate environment-specific remediation guidance. This creates a continuous loop where risks are discovered, investigated, and resolved before they can be exploited.
SOC automation transforms how security teams operate, shifting focus from manual alert processing to proactive threat hunting. The key is ensuring your automation has the cloud context needed to prioritize real risks over noise. With Wiz Agents & Workflows bringing AI-powered decision support and orchestration into the platform, teams can now automate not just the repetitive tasks but also the complex reasoning and investigation that previously required manual effort, all while maintaining transparency and control. Ready to see how AI-powered SOC automation transforms your cloud security operations? Get a demo to experience how Wiz Defend unifies detection, investigation, and response with full cloud context.
Explore how Wiz connects cloud context with runtime detection to automate investigation and response across your environment. Automated SOC solutions help organizations maintain continuous compliance by enforcing consistent logging, detection, and response standards across cloud environments. They automatically generate audit trails, ensure critical alerts receive timely attention, and streamline evidence collection for frameworks such as HIPAA, PCI DSS, and ISO 27001. Automation also reduces the risk of human error in compliance-related workflows.
Yes, most SOC automation platforms offer flexible configurations that let teams adapt playbooks, approval workflows, and data residency settings to align with local regulations, including GDPR in Europe and CCPA in California. Wiz supports region-specific data handling and customizable alerting to assist organizations with regional cybersecurity and privacy requirements.
Integrating automation into existing SOC workflows improves detection speed, reduces manual triage effort, and enhances scalability. Security teams respond to more threats faster without burnout while maintaining oversight of high-risk decisions. Platforms like Wiz integrate with existing SIEM, SOAR, and ticketing systems to augment, not replace, human decision-making.
A security alert in isolation is just noise . A suspicious login attempt is a low-priority event until you know the user has privileged access and failed a phishing simulation yesterday. Without this context, your SOC is flying blind , unable to distinguish a minor anomaly from a precursor to a major breach. True security intelligence comes from correlating data across siloed domains. This comprehensive view is the foundation for effective automated alert triage and enrichment without soar .
This guide shows you how to connect these signals to build a proactive defense based on a true understanding of risk. SOC automation uses technology to execute common security tasks within a Security Operations Center (SOC). Instead of relying on analysts to manually perform every step, automated systems can analyze data, identify anomalies, and initiate response protocols. This approach doesn't aim to replace human expertise, but rather to augment it. By handling the high-volume, repetitive tasks like initial alert triage and data collection, automation frees up your security team to focus on complex threat investigation and strategic defense planning.
The primary goal is to accelerate the entire security workflow, from detection to resolution. When a potential threat emerges, automated tools can instantly gather relevant context from various sources, correlate events, and present a clear picture to an analyst. This significantly shortens the time an attacker has to operate within your network. It also introduces a level of consistency and precision that is difficult to maintain with purely manual processes, directly helping to reduce human risk and the potential for critical errors. Ultimately, SOC automation allows your team to manage a greater volume of security events with higher accuracy and speed.
The conversation around SOC automation often frames it as a choice between machines and people, but the reality is a partnership. The goal isn't to replace skilled analysts but to augment their expertise. Automation excels at executing high-volume, repetitive tasks with speed and consistency, such as initial alert triage or data gathering. This process frees your team from the manual work that leads to fatigue and burnout, allowing them to apply their critical thinking to more complex challenges like threat hunting and incident investigation.
True augmentation happens when automation provides analysts with the right context at the right time. An effective Human Risk Management platform enriches security alerts by correlating data across employee behavior, identity systems, and real-time threat intelligence. Instead of just seeing a suspicious login, an analyst sees the full story: the user recently failed a phishing test, has privileged access, and is being targeted by a known threat actor. This is how you transform a simple alert into a prioritized, actionable insight, enabling your team to make faster, more informed decisions.
Advancing your SOC's capabilities is a journey, not a destination. A maturity model provides a roadmap for strategically implementing automation to move from a reactive to a proactive security posture. The key is to build trust in the system through a phased approach. Start by automating low-risk, well-defined workflows where the outcomes are predictable. As your team gains confidence, you can gradually introduce more complex autonomous actions, always maintaining an "AI with human oversight" model for critical decisions.
As your SOC matures, the focus shifts from simply responding to alerts to predicting and preventing incidents. By automating initial triage and response, you reduce alert noise and allow your team to focus on strategic defense. This evolution is central to effective Human Risk Management . A mature SOC doesn't just react to human error; it uses predictive intelligence to identify risk trajectories and intervene before a mistake turns into a breach, creating a more resilient and secure organization.
An automated SOC is built on a foundation of specialized technologies working in concert. Key components include Security Information and Event Management (SIEM) systems, which aggregate and correlate log data from across your entire IT environment. Security Orchestration, Automation, and Response (SOAR) platforms then take this data and use playbooks to automate response actions.
These tools are enriched by automated threat intelligence platforms that provide up-to-date information on new threats and indicators of compromise (IOCs). Together, these components create a powerful system for enhancing your security operations , enabling faster threat detection, improving team efficiency, and reducing operational costs by handling tasks like alert triage, vulnerability management, and initial incident response.
An automated workflow enables a SOC to identify and act on threats with incredible speed. The process begins with tools that continuously scan and analyze data from networks, endpoints, and cloud services to spot potential security issues before they escalate. When an alert is triggered, the automation pipeline takes over. It aligns IOCs with threat intelligence feeds, removes duplicate alerts, and scores the threat based on its source and recency.
This builds a unified timeline of events for the analyst, eliminating the need to manually pivot between different tools. The result is a streamlined process that leads to fewer hours spent on routine investigation and enables faster, higher-quality decisions when an incident requires human intervention. Even the most advanced Security Operations Center (SOC) is vulnerable to its most unpredictable element: people. Human error isn’t a sign of a weak team; it’s an inevitable outcome of a high-pressure environment burdened by manual processes and an overwhelming volume of data. When analysts are forced to make critical decisions in seconds, sift through thousands of daily alerts, and perform repetitive tasks by hand, mistakes are bound to happen. These aren't just minor slip-ups. They are cracks in your security posture that attackers are ready to exploit. Understanding the root causes of these errors, from simple mistakes under pressure to the systemic drag of manual work and alert fatigue, is the first step toward building a more resilient security operation. By addressing the human factor directly, you can move from a reactive stance to a proactive one, preventing incidents before they escalate.
In a high-stakes SOC environment, pressure is constant, and even the most skilled analysts can make mistakes. A simple typo in a firewall configuration, a misinterpretation of a log entry, or overlooking a subtle indicator of compromise during a hectic shift can have significant consequences. These aren't failures of expertise but natural human responses to stress and cognitive overload. When an analyst is juggling multiple incidents, the risk of error increases dramatically. A system that can provide a second look or automate routine checks acts as a crucial safety net. The Living Security platform helps by correlating signals from behavior, identity, and threat data to surface the most critical risks, allowing analysts to focus their attention where it's needed most.
Manual security tasks are a major drain on your most valuable resource: your team’s time and expertise. Repetitive actions like manually triaging alerts, creating tickets, and gathering contextual data for investigations consume countless hours that could be spent on proactive threat hunting. This constant reactive cycle not only drives up operational costs but also limits your team's strategic impact. When analysts are buried in routine work, they are always a step behind attackers. This operational drag prevents them from identifying emerging threats and strengthening defenses. Adopting a Human Risk Management strategy helps organizations identify and automate these inefficient workflows, freeing up analysts to perform the high-value work that truly secures the enterprise.
Modern security tools generate a staggering number of alerts, and SOC teams are drowning in the noise. Research shows that security teams receive thousands of alerts daily, and a majority of them are never even investigated. This constant flood of notifications leads to alert fatigue, a state where analysts become desensitized and start to tune out or dismiss warnings. As a result, critical alerts indicating a genuine threat can easily be lost in the shuffle. This isn't just an efficiency problem; it's a direct path to a security breach. By intelligently filtering and prioritizing risks, solutions like Unify SAT+ help cut through the noise, reducing analyst burnout and ensuring that your team can quickly identify and respond to the threats that matter.
5. Performance Evaluation & Extended Technical Observations The cybersecurity skills gap is more than a buzzword; it's an operational reality that leaves security teams stretched thin. Threats are evolving far too quickly for organizations to handle them with manual processes alone, especially when there aren't enough qualified analysts to hire. This staffing shortage creates a high-pressure environment where your existing team is forced to manage an overwhelming volume of alerts. SOC automation acts as a critical force multiplier in this scenario. By taking on the high-volume, repetitive tasks that consume analyst time, it allows your skilled professionals to apply their expertise to what matters most: complex threat investigation and strategic defense planning. This shift not only makes your team more effective but also helps streamline incident response when every second counts.
As organizations move to the cloud, the traditional security perimeter disappears, replaced by a complex web of interconnected services, applications, and data stores. Manually monitoring these dynamic environments is not just impractical; it's impossible. The sheer scale makes it difficult to watch everything, and the cost of manual security oversight can quickly become prohibitive. This complexity also introduces significant compliance challenges. Automation helps enforce security policies consistently across all cloud assets and provides a clear, auditable trail of every action taken. By automating data collection and initial triage, you can ensure nothing slips through the cracks, helping you maintain both a strong security posture and continuous compliance with industry regulations .
Focusing your automation efforts on the right tasks is key to reducing human error and improving your security posture. By targeting repetitive, high-volume, and time-sensitive processes, you can free up your security analysts to concentrate on more complex threats. Automating specific workflows not only accelerates response times but also introduces a level of consistency that manual processes often lack. This strategic approach allows your team to operate more effectively, minimizing the risk of mistakes that can lead to significant security incidents.
SOCs are flooded with alerts, and manually sifting through them is a recipe for burnout and missed threats. Automation can act as your first line of defense, instantly analyzing and categorizing incoming alerts. By using predefined rules and machine learning, automated systems can distinguish between low-priority noise and credible threats, escalating only the most critical issues for human review. This process enables SOCs to "quickly identify and address threats, reducing the time attackers have to cause damage." With an automated platform , your team can stop wasting time on false positives and focus their expertise on genuine incidents before they escalate.
Traditionally, alert triage is a painstaking manual effort. An analyst receives an alert and begins the slow process of gathering context. This involves jumping between different security tools to pull logs, check network traffic, and review endpoint data. The goal is to review, check, and prioritize each alert to determine if it’s a genuine threat or just noise. This fragmented approach places a heavy cognitive burden on your team, forcing them to piece together a puzzle with missing pieces. Under pressure, it's easy to misinterpret data or miss a critical connection, leading to either a delayed response or a completely overlooked incident. This reactive cycle keeps your SOC constantly on the back foot, responding to events rather than getting ahead of them.
Automated data enrichment transforms the triage process from a manual investigation into an instant analysis. When an alert containing a suspicious IP address or URL comes in, an automated system immediately queries multiple threat intelligence feeds. It gathers crucial context, such as the IP's reputation, geographic location, and any known associations with malicious campaigns. This information is automatically correlated and presented to the analyst in a unified timeline, eliminating the need to manually pivot between tools. A truly effective SOC automation strategy goes even further, correlating this external threat data with internal signals across user behavior and identity systems. This provides a complete picture, showing not just that an IP is suspicious, but that it’s targeting a high-privilege user who recently failed a phishing test, enabling a far more accurate and predictive risk assessment.
When a real threat is identified, every second counts. Manual incident response can be slow and inconsistent, especially under pressure. Automating your response workflows ensures that predefined actions, like isolating an endpoint or blocking an IP address, are executed immediately. This approach transforms security operations by "eliminating manual alert investigation, reducing response times, and handling security threats 24/7." Implementing automated playbooks for common incidents creates a standardized process that minimizes human error and dramatically shortens the window of opportunity for attackers. This is a core component of modern SOC and IR solutions.
Keeping up with the constant stream of new vulnerabilities is an impossible task for any security team. When analysts manually prioritize patching based on CVSS scores alone, they lack the context to see the true risk. A medium-severity vulnerability might be ignored, even if it exists on a critical system accessed by a high-risk user. Automation changes this by enriching vulnerability data with real-time intelligence. By correlating signals across user behavior, identity and access systems, and active threat feeds, an automated system can identify which vulnerabilities pose the most immediate danger.
This data-driven approach allows your team to focus on patching the threats that matter most, creating a truly proactive human risk management strategy. Effective threat hunting requires connecting disparate data points to uncover hidden patterns. Automation excels at this, correlating indicators of compromise (IOCs) with threat intelligence feeds and internal data logs to build a comprehensive view of an attack. It can stitch together process trees, DNS lookups, and authentication logs into a unified timeline, saving analysts from hours of manual correlation. By integrating signals across user behavior, identity, and threat data , automation provides the context needed for faster, higher-quality decisions, allowing your team to proactively hunt for threats rather than just reacting to them.
Maintaining compliance and generating audit reports is a critical but often tedious task. Manual documentation is prone to errors and inconsistencies, which can lead to failed audits and regulatory fines. Automation can streamline this entire process by continuously logging all security actions, generating detailed reports, and maintaining a clear audit trail. This not only ensures accuracy but also demonstrates due diligence to auditors and stakeholders. As experts note, SOC automation "supports compliance requirements and threat-focused operations," helping organizations maintain robust and provable cybersecurity defenses with far less manual effort.
Traditional SOC automation is designed to help teams react faster. It takes known threats and established playbooks and executes them at machine speed. While this is a clear improvement over manual processes, it still keeps security teams on the defensive, waiting for an incident to occur. The core limitation is that it acts on events that have already happened. Predictive intelligence fundamentally changes this dynamic. Instead of just speeding up reactions, it allows your SOC to anticipate and neutralize threats before they can escalate into full-blown incidents.
This approach moves beyond simple, rule-based triggers that fire after the fact. It uses advanced analytics and machine learning to identify the subtle precursors to an attack, which are often rooted in human or AI agent behavior. By analyzing patterns and risk trajectories, predictive systems can flag a user who is likely to cause a breach, not just one who has already clicked a malicious link. This transforms the SOC from a reactive fire-fighting unit into a proactive risk mitigation engine. It gives your team the foresight to act before damage is done, effectively getting ahead of threats by understanding the human and machine behaviors that precede them. This shift is critical for managing the complex, distributed workforces of modern enterprises, where risk is dynamic and constantly evolving. By focusing on leading indicators of risk, you can move from a posture of incident response to one of incident prevention, which is a far more efficient and effective way to protect your organization.
The primary goal of predictive intelligence is to shift your security posture from reactive to proactive. Legacy automation helps you respond to an alert in minutes instead of hours, but the alert has still been triggered. A proactive model aims to prevent that alert from ever being generated. It works by continuously scanning and analyzing data across your environment to identify potential security threats before they become active breaches. This means looking for leading indicators of risk, such as an employee with elevated access privileges who starts exhibiting unusual data access patterns after failing a phishing test. By spotting this convergence of risk factors, you can intervene early with targeted training or access reviews, effectively neutralizing the threat before it materializes.
A predictive model is only as good as the data it analyzes. The real power comes from correlating signals across multiple domains that are traditionally siloed. Instead of just looking at network logs or endpoint alerts, a predictive system integrates data from human behavior, identity and access management tools, and external threat intelligence feeds. This comprehensive view is the foundation of modern Human Risk Management . It allows the system to understand context and intent, distinguishing between a benign anomaly and a genuine threat. For example, it can see that a user who recently traveled to a high-risk country is now trying to access sensitive data from an unfamiliar device, creating a clear risk profile that demands immediate attention.
Many security tools have added AI features, but an AI-native platform is built differently from the ground up. It uses AI as its core operating system, not just a feature. This architecture allows it to continuously learn from new data and adapt its analysis without relying on rigid, pre-programmed playbooks. An AI-native platform can autonomously triage, investigate, and even remediate low-level risks, freeing up human analysts to focus on complex threats. By leveraging AI to accelerate response times and standardize operations, security leaders can transform their SOC from an overwhelmed, reactive center to an efficient, proactive function that significantly reduces organizational risk and maximizes the impact of limited security resources.
Complex investigations demand more than just faster data retrieval; they require a deep understanding of context that traditional automation often misses. This is where Agentic AI transforms the process. Instead of just executing playbooks, it acts as an intelligent partner to your analysts, autonomously connecting the dots between seemingly unrelated events. By correlating signals across employee behavior, identity and access systems, and real-time threat intelligence , it builds a complete narrative of a potential attack. This allows your team to move beyond chasing individual alerts and see the full risk trajectory, enabling them to solve complex cases with greater speed and precision.
Security Operations Centers rely on a suite of tools to manage the immense volume of security data and alerts. While no single tool can eliminate human error, several categories of technology are designed to automate repetitive tasks, standardize response procedures, and provide analysts with better context. These platforms help reduce the cognitive load on security teams, allowing them to focus on more complex threats. By automating key functions, these tools create a more consistent and less error-prone security posture. However, it's important to remember that these tools primarily focus on technical signals. A truly proactive strategy also requires correlating this data with insights from behavior and identity to understand the full picture of human risk .
Security Information and Event Management (SIEM) platforms are foundational to the SOC, collecting and correlating log data from across the organization to spot potential threats. When an issue is identified, Security Orchestration, Automation, and Response (SOAR) platforms take over. As security frameworks have evolved, SOAR platforms introduced playbook-based workflows that could coordinate actions across multiple security tools. This integration automates the response process, from creating a ticket to quarantining a device. By codifying response procedures into automated playbooks, SOAR tools reduce the risk of analysts missing a critical step or making a mistake under pressure, ensuring a consistent and compliant response every time.
SOAR stands for Security Orchestration, Automation, and Response. It represents a collection of technologies designed to help security teams manage and respond to security alerts more efficiently. Think of it as a force multiplier for your SOC. The system integrates your existing security tools, automates repetitive tasks, and provides a structured framework for incident response. By standardizing these processes, SOAR platforms help organizations streamline their security operations, allowing them to handle a higher volume of threats with greater speed and consistency. This approach is critical for reducing the manual burden on analysts and minimizing the potential for human error in high-pressure situations.
The power of SOAR lies in its three core components. Orchestration is the connective tissue, integrating your various security tools—from firewalls to endpoint detection—into a single, cohesive system. This allows for a seamless flow of information and coordinated actions. Automation is the engine that drives efficiency, taking over the manual, time-consuming tasks that lead to analyst burnout. This includes everything from initial alert enrichment to checking user access logs. Finally, Response provides a structured, playbook-driven approach to incident management, ensuring that every action is deliberate and based on a comprehensive understanding of the threat, not just an isolated alert.
Two key features define most SOAR platforms: visual playbooks and case management. A visual playbook builder allows security teams to create step-by-step automated workflows for responding to specific types of incidents. These playbooks codify your team’s best practices, ensuring a consistent response every time. Case management capabilities centralize all data and actions related to an incident into a single view. This automates the entire process, from ticket creation to device quarantine, creating a clear audit trail and ensuring no critical steps are missed. Together, these features help reduce human error by replacing manual, inconsistent processes with reliable, automated workflows.
Modern threats evolve quickly, and manually tracking indicators of compromise (IOCs) is an impossible task. Automated threat intelligence systems continuously pull in data from multiple feeds, enriching internal security alerts with external context. These systems automatically align IOCs with threat intel feeds, deduplicate the information, and score threats by recency and source reputation. This process transforms a flood of raw data into a prioritized stream of actionable intelligence. By automating this analysis, you free your team from the manual, error-prone task of vetting threat data. This allows them to focus their expertise on investigating the most relevant and high-risk threats identified by the Living Security platform .
Endpoint Detection and Response (EDR) tools provide deep visibility into workstations and servers, monitoring for signs of compromise. When an EDR agent detects suspicious activity, it can trigger automated actions to contain the threat immediately. This could involve isolating the endpoint from the network or terminating a malicious process before it can spread. With this level of automation, Tier 1 analysts can become investigation specialists while the AI handles initial enrichment and timeline creation. This rapid, automated containment minimizes the window of opportunity for an attacker and reduces the chance of human error during the critical first moments of an incident, such as a phishing attack .
Extended Detection and Response (XDR) platforms represent a significant step forward in breaking down data silos within the SOC. By integrating security signals from endpoints, networks, cloud services, and email, XDR provides a more unified view of potential threats. This correlation allows analysts to see the connections between seemingly isolated events, helping them spot complex attacks that might otherwise go unnoticed. For security teams, this means less time spent manually piecing together data from different tools, which directly reduces the opportunity for human error during an investigation. The goal is to provide richer context around alerts, enabling faster and more accurate decision making when every second is critical.
While XDR excels at correlating technical data, it often overlooks the most critical variable: human behavior. A complete understanding of risk requires more than just machine data. This is where a Human Risk Management platform complements XDR by integrating signals from user behavior and identity systems. By correlating an XDR alert with data showing that the involved user has elevated access and recently failed a phishing simulation, you get a far more accurate picture of the actual risk. This holistic view allows your SOC to move beyond just technical indicators and proactively address threats rooted in human action.
Vulnerability management tools are essential for proactively identifying and prioritizing weaknesses across your systems and software. They automate the scanning process, freeing analysts from the tedious and error-prone task of manual checks. Similarly, Cloud Security Posture Management (CSPM) tools continuously monitor your cloud environments for misconfigurations and compliance gaps. Given the complexity and dynamic nature of the cloud, automating this oversight is crucial for preventing security breaches caused by simple configuration mistakes. Both tools help reduce the attack surface by ensuring foundational security hygiene is maintained with consistency and precision.
These tools are excellent at identifying potential weaknesses, but they lack the context to prioritize them effectively. A critical vulnerability on a server is a problem, but it becomes an immediate crisis when the primary user of that server is being actively targeted by phishing campaigns. The Living Security platform provides this crucial context by correlating technical vulnerabilities from these tools with real-time human risk signals. This allows your team to prioritize remediation efforts not just on technical severity, but on the actual likelihood of exploitation, ensuring you fix the most dangerous problems first.
While specialized tools like SOAR and EDR are powerful, they don’t always cover every unique process within a SOC. No-code automation platforms fill this gap, allowing security teams to build custom workflows without needing to write code. These platforms use simple drag-and-drop interfaces to connect different tools and automate specific tasks. Using low-code security automation helps teams quickly respond to any threat by bringing down the mean time to resolution (MTTR) and reducing errors during the investigation process. This empowers analysts to automate their own repetitive tasks, creating efficiencies and reducing the risk of mistakes in niche but critical workflows.
While foundational for its time, traditional Security Orchestration, Automation, and Response (SOAR) technology has reached its limits. These first-generation platforms were designed to automate linear, predictable tasks, but they struggle with the complexity and ambiguity of modern threats. Security operations require more than just faster reactions; they need intelligent, predictive capabilities that can anticipate risk before it leads to an incident. The industry is now shifting toward a more advanced model that integrates AI-driven analysis to automate the complex "thinking" tasks that traditional SOAR could never handle.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Triage • https://www.wiz.io/academy/detection-and-response/soc-automation • https://www.livingsecurity.com/blog/automating-soc-response-error
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Automated Security Operations Center Alert Triage Tool.
[*] Metasploit Scan Running on Target Subnet for Automated Security Operations Center Alert Triage Tool... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |