Complete Technical Paper Content — Automated Security Scanner For Wordpress Sites Python
Overview & System Context
Automated Security Scanner For Wordpress Sites Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8155 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Google Cloud is a suite of cloud computing services offered by Google that provides a series of modular cloud services including computing, data storage, data analytics, and machine learning, alongside a set of management tools. It runs on the same infrastructure that Google uses internally for its end-user products, such as Google Search, Gmail, and Google Docs, according to Verma et al. Registration requires a credit card or bank account details. Google Cloud provides infrastructure as a service, platform as a service, and serverless computing environments. In April 2008, Google announced App Engine, a platform for developing and hosting web applications in Google-managed data centers, which was the first cloud computing service from the company. The service became generally available in November 2011. Since the announcement of App Engine, Google added multiple cloud services to the platform. Google Cloud includes Google Cloud public cloud infrastructure, as well as Google Workspace (G Suite), enterprise versions of Android and ChromeOS, and application programming interfaces (APIs) for machine learning and enterprise mapping services. Since at least 2022, Google's official materials have stated that "Google Cloud" is the new name for "Google Cloud Platform," which may cause naming confusion.
For those familiar with other notable cloud service providers, a comparison of similar services may be helpful in understanding Google Cloud Platform's offerings. April 2008 – Google App Engine announced in preview May 2010 – Google Cloud Storage launched May 2010 – Google BigQuery and Prediction API announced in preview October 2011 – Google Cloud SQL is announced in preview June 2012 – Google Compute Engine is launched in preview May 2013 – Google Compute Engine is released to GA August 2013 – Cloud Storage begins automatically encrypting each Storage object's data and metadata under the 128-bit Advanced Encryption Standard (AES-128), and each encryption key is itself encrypted with a regularly rotated set of master keys February 2014 – Google Cloud SQL becomes GA May 2014 – Stackdriver is acquired by Google June 2014 – Kubernetes is announced as an open source container manager June 2014 – Cloud Dataflow is announced in preview October 2014 – Google acquires Firebase November 2014 – Alpha release Google Kubernetes Engine (formerly Container Engine) is announced January 2015 – Google Cloud Monitoring based on Stackdriver goes into Beta March 2015 – Google Cloud Pub/Sub becomes available in Beta April 2015 – Google Cloud DNS becomes generally available April 2015 – Google Dataflow launched in beta July 2015 – Google releases v1 of Kubernetes; Hands it over to The Cloud Native Computing Foundation August 2015 – Google Cloud Dataflow, Google Cloud Pub/Sub, Google Kubernetes Engine, and Deployment Manager graduate to GA November 2015 – Bebop is acquired, and Diane Greene joins Google February 2016 – Google Cloud Functions becomes available in Alpha September 2016 – Apigee, a provider of application programming interface (API) management company, is acquired by Google September 2016 – Stackdriver becomes generally available November 2016 – Qwiklabs, an EdTech company is acquired by Google February 2017 – Cloud Spanner, highly available, globally-distributed database is released into Beta March 2017 – Google acquires Kaggle, world's largest community of data scientists and machine learning enthusiasts April 2017 – MIT professor Andrew Sutherland breaks the record for the largest ever Compute Engine cluster with 220,000 cores on Preemptible VMs. May 2017 – Google Cloud IoT Core is launched in Beta November 2017 – Google Kubernetes Engine gets certified by the CNCF February 2018 – Google Cloud IoT Core becomes generally available February 2018 – Google announces its intent to acquire Xively February 2018 – Cloud TPUs, ML accelerators for Tensorflow, become available in Beta May 2018 – Google Cloud Memorystore becomes available in Beta April 2019 – Google Cloud Run (fully managed) Beta release April 2019 – Google Anthos announced November 2019 – Google Cloud Run (fully managed) General availability release March 2020 – Due to the COVID-19 pandemic, Google Cloud postponed the online streaming version of its Google Cloud Next mega-conference, two weeks after it canceled the in-person version. October 2020 – Google Cloud announced that it will become a block producer candidate for the EOS network and EOS.IO protocol. Currently the top block producers are cryptocurrency exchanges like OKEx and Binance. February 2021 – Google Kubernetes Engine Autopilot is introduced. May 2021 – Vertex AI announced at Google.io June 2021 – In 2021, Apple was Google Cloud's biggest customer. April 2022 – MobiledgeX acquired and joins Google Cloud. March 2023 – Google brings generative AI capabilities to Google Cloud. May 2024 Google Cloud partnered with Airtel. April 2025 – At Google Cloud Next 2025 in Las Vegas, Google announced the seventh-generation Tensor Processing Unit, named Ironwood, claiming 3,600 times better performance than its first publicly available TPU. Google also announced Cloud Wide Area Network (Cloud WAN), making its private global network available to enterprise customers, and introduced Gemini 2.5 and Gemini 2.5 Flash reasoning models.
April 2026 – At Google Cloud Next '26, Sundar Pichai announced expanded AI infrastructure investments, including the introduction of Trillium TPUs (8th generation) and the Gemini Enterprise Agent Platform, with Google reporting that 75% of new internal code was AI-generated. This is a list of free and open-source software (FOSS) packages, computer software licensed under free software licenses and open-source licenses. Software that fits the Free Software Definition may be more appropriately called free software; the GNU project in particular objects to their works being referred to as open-source. For more information about the philosophical background for open-source software, see free software movement and Open Source Initiative. However, nearly all software meeting the Free Software Definition also meets the Open Source Definition and vice versa. A small fraction of the software that meets either definition is listed here. Some of the open-source applications are also the basis of commercial products, shown in the List of commercial open-source applications and services.
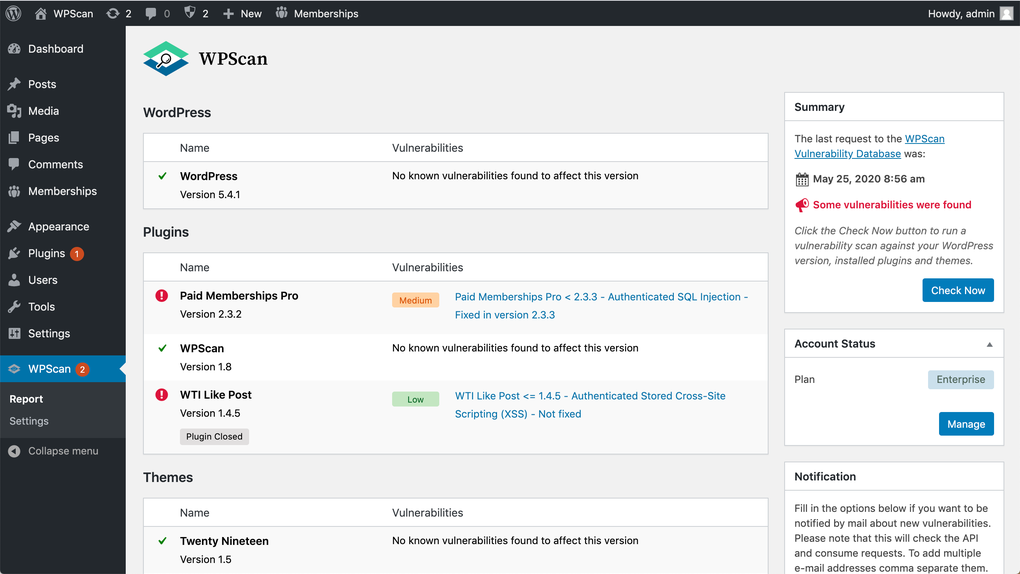
Figure 1: WPScan – WordPress Security Scanner (WordPress) - Descargar Cline – AI coding agent for IDEs and the command line. Codex CLI – AI coding agent and command-line interface developed by OpenAI. Command Code — CLI and desktop AI agent DeepSeek Coder – large language model designed for code generation and AI-assisted software development. Eclipse Theia – integrated development environment and framework with AI-assisted software development features. goose – AI coding agent for the desktop and command line. Kilo Code — CLI and IDE extension developed by Anaconda OpenCode — CLI, desktop app, web app, and IDE extensions OpenHands — AI software development agent Oh My Pi – terminal-based AI coding agent developed as a fork of Pi. Pi – terminal-based AI coding agent. Zed – source-code editor with integrated AI-assisted development and agentic coding features.
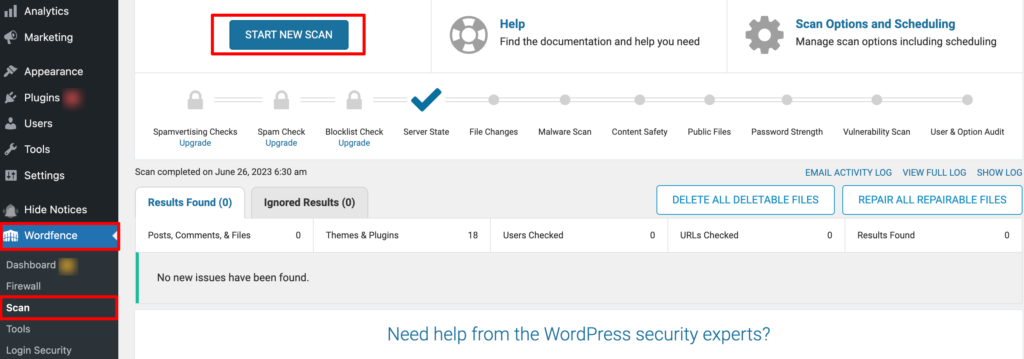
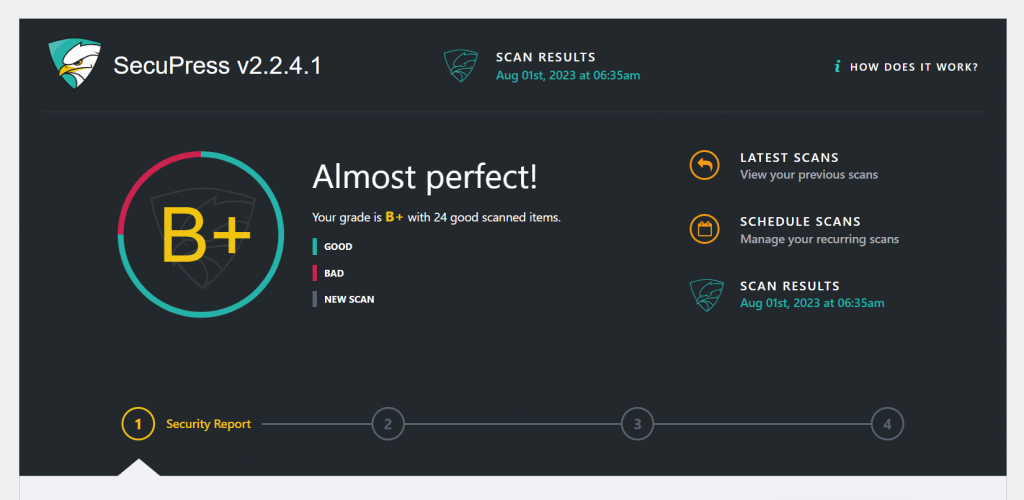
Apertus – Swiss National AI Initiative LLM BERT – Google LLM BLOOM – BigScience multilingual LLM Cerebras-GPT – Cerebras Systems LLMs DeepSeek – R1 and V3 models Gemma 4 – Google LLM GLM-4.5 and later versions – Z.ai LLMs GPT-1, GPT-2, and GPT-OSS – OpenAI LLMs GPT-J, GPT-Neo, and GPT-NeoX – EleutherAI LLMs Hy – Tencent open-weight LLM Granite – IBM LLMs Grok-1 – xAI LLM Inkling – Thinking Machines Kimi (some versions) – Moonshot AI LLMs MiMo (some versions) – Xiaomi LLMs Mistral (some versions) Muse Glimmer — Meta Superintelligence Labs LLM Nemotron 3 – Nvidia open-weight models OLMo – Allen Institute for AI LLM Phi – Microsoft LLMs Qwen (some versions) – Alibaba Cloud LLMs Sarvam-M, Sarvam-105B and Sarvam-30B – Sarvam AI LLMs SmolLM – Hugging Face small language models (SLMs) Step-3.7Flash – StepFun LLM T5 – Google LLM XLNet – Google LLM ArduPilot CoppeliaSim Gazebo Mobile Robot Programming Toolkit OpenRTM-aist Paparazzi Project Player Project Python Robotics Robot Operating System (ROS) TurtleBot UBtech Thinker Webots – robot simulator Archimedes (CAD) Art of Illusion Blender BRL-CAD – constructive solid geometry (CSG) solid modeling computer-aided design (CAD) system FreeCAD – parametric 3D CAD modeler with a focus on mechanical engineering, BIM, and product design LeoCAD — beginner Lego 3D modeler LibreCAD – 2D CAD software using AutoCAD-like interface and file format MakeHuman MeshLab Open Cascade Technology (OCCT) – CAD kernel for 3D CAD, CAM, CAE OpenSCAD – scripting-based 3D CAD software QCAD SolveSpace – 2D and 3D CAD, constraint-based parametric modeler with simple mechanical simulation abilities Sweet Home 3D Wings 3D Figure 2: How to Detect and Remove Malware from a WordPress Site - weDevs Electric FreePCB Fritzing – CAD software for the design of electronics hardware to build more permanent circuits from prototypes gEDA GNU Circuit Analysis Package (Gnucap) Icarus Verilog KiCad – suite for electronic design automation (EDA) for schematic capture, PCB layout, manufacturing file viewing, SPICE simulation, and engineering calculation KTechLab Magic Ngspice pcb-rnd Oregano Quite Universal Circuit Simulator (QUCS) Verilator XCircuit Blender – 3D computer graphics software toolset used for creating animated films, visual effects, art, 3D printed models, and motion graphics FreeCAD – equivalent of Blender geared toward mechanical engineers OpenFOAM – software used for computational fluid dynamics (or CFD) FlightGear – atmospheric and orbital flight simulator with a flight dynamics engine (JSBSim) that was used in a 2015 NASA benchmark to judge new simulation code to space industry standards SimPy – queue-theoretic event-based simulator written in Python Salome – generic platform for Pre- and Post-Processing for numerical simulation OpenPGP – open-source version of Pretty Good Privacy GNU Privacy Guard – replacement for PGP OpenSSL – library for applications that provide secure communications over computer networks NaCl (software) – crypto library Libsodium – fork of NaCl VeraCrypt – disk encryption software forked from TrueCrypt LUKS – standard for disk encryption on Linux systems Nym (mixnet) – mix network that uses noise and random packet timing for obfsucation, overlay network for NymVPN Tor (network) – free overlay network for enabling anonymous communication Tails (operating system) – security-focused Linux distro using Tor by default Signal (software) – secure messaging app Off-the-Record Messaging – protocol for secure instant messaging GPGTools – macOS suite for GnuPG-based encryption Aircrack-ng – Wi-Fi security auditing tool BackTrack – predecessor to Kali Linux Burp Suite Community Edition – security assessment and penetration testing of web applications Ghidra – software reverse engineering suite developed by the NSA Hashcat – password recovery utility High Orbit Ion Cannon – DDoS hping3 — packet crafting and network penetration-testing utility Hydra (software) – login cracker supporting numerous protocols John the Ripper – password cracking tool Kali Linux – penetration testing Linux distribution Metasploit Project – framework for developing and executing exploit code Netcat – network utility for reading/writing data across networks Nikto (vulnerability scanner) – web server vulnerability scanner Nmap – network scanning, port scanner, and auditing tool OpenSSH – implementation of the SSH protocol Radare2 – reverse engineering framework Snort (software) – network intrusion detection system sqlmap – automated SQL injection and database takeover tool Suricata (software) – network threat detection engine Volatility (memory forensics) – memory forensics framework for incident response Wireshark – network protocol analyzer YARA – tool to identify and classify malware Figure 3: Top 10 WordPress Malware Scanner Plugins + How to Use Them qBittorrent – BitTorrent client Transmission (BitTorrent client) – lightweight BitTorrent client IPFS – InterPlanetary File System for decentralized storage and sharing RetroShare – secure communication platform with file sharing Zerocoin – privacy-focused cryptocurrency protocol Zcash – cryptocurrency based on Zerocoin using zk-SNARKs Monero – privacy-focused cryptocurrency using ring signatures NYM — Nym mixnet privacy- and security-focused token Tornado Cash — Cryptocurrency tumbler ClamAV – cross-platform antimalware toolkit written in C and C++, able to detect many types of malware including viruses ClamWin – antivirus tool for Windows and written in C, C++ Lynis – security audit tool (set of shell scripts) for Unix and Linux Bouncy Castle GnuPG GnuTLS KGPG NaCl OpenSSL Seahorse Signal stunnel TextSecure wolfCrypt 7-Zip Snort – network intrusion detection system (IDS) and intrusion prevention system (IPS) Suricata – network threat detection engine OpenVAS – software framework of several services and tools offering vulnerability scanning and vulnerability management Nmap – network scanner, port scanner, and security auditing tool Nikto – web server vulnerability scanner Volatility – memory forensics framework for incident response Cyberduck – macOS and Windows client (since version 4.0) Lsh – server and client, with support for SRP and Kerberos authentication OpenSSH – client and server PuTTY – client-only Apache Cassandra – NoSQL database from Apache Software Foundation offers support for clusters spanning multiple datacenter Apache CouchDB – NoSQL database from Apache Software Foundation with multi-master replication MariaDB – community-developed relational database management system with pluggable storage engines and commercial support PostGIS – adds support for geographic objects to the PostgreSQL as per Open Geospatial Consortium (OGC) PostgreSQL – relational database management system emphasizes on extensibility and SQL compliance and available for Windows, Linux, FreeBSD, and OpenBSD ATutor – web-based Learning Content Management System (LCMS) Canvas LMS – web-based, open, extensible learning management system Chamilo – web-based e-learning and content management system Claroline – collaborative Learning Management System DoceboLMS – SAAS/cloud platform for learning eFront – icon-based learning management system H5P – framework for creating and sharing interactive HTML5 content IUP Portfolio – educational platform for Swedish schools ILIAS – web-based learning management system (LMS) Moodle – learning management system OLAT – web-based Learning Content Management System Omeka – content management system for online digital collections Sakai Project – web-based learning management system SWAD – web-based learning management system Kiwix – offline web browser that allows users to download Wikipedia's entire content and use it for offline learning. Later it was expanded with repositories for Wikimedia Foundation, public domain texts from Project Gutenberg, many of the Stack Exchange sites, and other resources OpenStreetMap – OpenStreetMap was developed in 2004. It uses Open data and users data input through Crowdsourcing and Web mapping to create a complete and downloadable alternative to other online maps.
This allow users to enter data when there is no data available due to lack of governance and economic interest or due to lower population of the places mapped Advanced Simulation Library ASCEND Calcpad Calculix CHEMKIN – chemical kinetics COCO simulator – chemical process simulator CP2K – quantum chemistry and solid-state physics DWSIM – chemical process simulator General Mission Analysis Tool (GMAT) – space mission analysis GNU Octave – numerical-analysis GROMACS – simulations of proteins, lipids, and nucleic acids JSBSim – flight dynamics engine LAMMPS – Molecular dynamics Open Babel – chemical informatics OpenModelica – chemical process simulator OpenSees – earthquake engineering OpenVSP – parametric aircraft geometry tool Pyomo – mathematical optimization QBlade – wind turbine design and aerodynamic simulation software REFPROP – reference Fluid Thermodynamic and Transport Properties XFOIL – analysis of subsonic isolated airfoils .apng – Animated Portable Network Graphics .avif – AV1 Image File Format .bpg – Better Portable Graphics .exr – OpenEXR .fits – Flexible Image Transport System primarily for Astronomy .flif – Free Lossless Image Format .gif – Graphics Interchange Format .iff / .lbm – InterLeaved BitMap .jng – JPEG Network Graphics .jpg or .jpeg – Joint Photographic Experts Group .jxl – JPEG XL .mng – Multiple-image Network Graphics .miff / .mi – Magick Image File Format .pam, .pbm, .pgm, .ppm, .pnm – Netpbm file formats .pgf – Progressive Graphics File .png – Portable Network Graphics .qoi – Quite OK Image Format .tiff – Tag Image File Format .wbmp – Wireless Application Protocol Bitmap Format .webp .xbm – X BitMap .xcf – GIMP .xpm – X PixMap .adoc – AsciiDoc .epub – ebook format .latex – LaTeX, macro package built on top of TeX for simplification .md – Markdown .odt – OpenDocument .rtf – Rich Text Format .tex – high-quality typography for mathematical notation, physics, chemistry, engineering/scientific notation .texinfo 1DayLater – invoicing software GnuCash – double-entry book-keeping HomeBank – personal accounting software KMyMoney – double-entry book-keeping LedgerSMB – double-entry book-keeping RCA open-source application – management accounting application SQL-Ledger – double-entry book-keeping TurboCASH – double-entry book-keeping for Windows Bitcoin – blockchain platform, peer-to-peer decentralised digital currency Ethereum – blockchain platform with smart contract functionality CiviCRM – Constituent Relationship Management software aimed at charities and NGOs iDempiere – business Suite, ERP and CRM SuiteCRM – web-based CRM Adempiere – Enterprise resource planning (ERP) business suite Apache OFBiz – suite of enterprise applications from Apache Software Foundation Compiere – ERP solution automates accounting, supply chain, inventory, and sales orders Dolibarr – web-based ERP system ERPNext – web-based ERP system for managing accounting and finance ERP5 – Single Unified Business Model based system written with Python and Zope iDempiere – fully navigable on PCs, tablets and smartphones driven only by a community of supporters JFire – ERP business suite written with Java and JDO LedgerSMB – double entry accounting and ERP system written with Perl metasfresh – ERP Software Odoo – ERP, CRM and CMS Openbravo – web-based ERP Tryton – ERP MAME – multi-platform emulator for arcade game systems Mednafen – multi-platform emulator MESS – multi-platform emulator RetroArch – cross-platform front-end for emulators, game engines and video games Snes9x – Super Nintendo emulator Stella – Atari 2600 emulator PCSX – PlayStation emulator PCSX2 – PlayStation 2 emulator PPSSPP – PlayStation Portable emulator Project64 – Nintendo 64 emulator RPCS3 – PlayStation 3 emulator Dolphin (emulator) – GameCube and Wii emulator Citra (emulator) – Nintendo 3DS and Wii emulator Cemu – Wii U emulator TIC-80 – virtual machine game engine that mimics the 8-bit systems of the 1980s QGIS – cross-platform desktop geographic information system (GIS) application to view, edit, and analyse geospatial data ADMB Euler Math Toolbox FreeMat GNU Data Language GNU MCSim GNU Octave J Julia Owl Scientific Computing Perl Data Language S-Lang Scilab Yorick Blender Game Engine – discontinued 2019 Godot – application for the design of cross-platform video games MonoGame – C# framework Open3DEngine – based on Amazon Lumberyard Stride – (prev. Xenko) 2D and 3D cross-platform game engine originally developed by Silicon Studio Amavis – email content filter Claws Mail – email Client Fetchmail – email Retrieval Geary – email client based on WebKitGTK+ GNUMail – cross-platform email client Hula – discontinued mail and calendar project K-9 Mail – Android Email Client MailScanner – email security system MH Message Handling System – email Client Modest – email Client Mozilla Mail & Newsgroups – email Client that was part of the now discontinued Mozilla Application Suite Mozilla Thunderbird – email, news, RSS, and chat client POPFile – cross-platform mail filter Proton Mail – app and web-based end-to-end encrypted e-mail evolved to become FOSS Roundcube – web-based IMAP email client Sylpheed – email and News Client Sympa – MLA software I2P – anonymous network layer (implemented as a mix network) that allows for censorship-resistant, peer-to-peer communication OnionShare – file sharing app using Tor network Popcorn Time – multi-platform media player qBittorrent – BitTorrent client Transmission – BitTorrent client Deluge – BitTorrent client BSD – FreeBSD, OpenBSD, NetBSD, GhostBSD, TrueNAS, MidnightBSD, DragonFly BSD, OPNsense, pfSense, XigmaNAS, among others. GrapheneOS – Privacy- and security-focused, Android-based mobile operating system Kali NetHunter Linux – Debian, Ubuntu, Manjaro, Fedora, openSUSE, antiX, NixOS, Kali, Alpine, Tails, Mageia, Slackware, Gentoo, BlackArch, among others (List of Linux distributions). LineageOS – Android-based operative system for tablets and mobile phones GNU Hurd Mobian Nura Plasma Mobile PureOS Ubuntu Touch Redox OS FreeDOS – OS compatible with IBM PC DOS and Microsoft's MS-DOS ReactOS – OS intended to run the same software as Windows, originally designed to simulate Windows NT 4.0, later aiming at Windows 7 compatibility. It has been in the development stage since 1996.
AppleWin DOSBox – DOS programs emulator (including PC games) GNOME Boxes Hercules (emulator) Kernel-based Virtual Machine (KVM) QEMU VirtualBox – hosted hypervisor for x86 virtualization DTrace – dynamic tracing framework for analyzing and troubleshooting running applications and operating systems Memtest86 – stress-tests RAM on x86 machines strace – diagnostic utility for tracing system calls and signals Valgrind – debugging and profiling tool for detecting memory and threading errors Xnee – record and replay tests 2. System Architecture & Core Working Principles Acceleo – model-to-text code generator Apache Velocity – Java-based template engine used for code generation Babel – JavaScript transcompiler Bison CodeSynthesis XSD – XML Data Binding compiler for C++ CodeSynthesis XSD/e – validating XML parser/serializer and C++ XML Data Binding generator for mobile and embedded systems Flex lexical analyser – generates lexical analyzers Open Scene Graph – 3D graphics application programming interface OpenSCDP – Open Smart Card Development Platform SableCC – parser generator for Java and .NET SWIG – Simplified Wrapper and Interface Generator for several languages Umple – modeling and programming language with source code generation xmlbeansxx – XML Data Binding code generator for C++ YAKINDU Statechart Tools – Statechart code generator for C++ and Java Apache Flink – stream and batch data processing framework Apache Hadoop – distributed storage and processing framework Apache Mahout – scalable machine learning library Apache Spark – unified analytics engine Dask – parallel computing for analytics in Python ELKI – data analysis algorithms library GNU Octave – numerical computing environment JASP – GUI program for data analytics, data science, and machine learning Jupyter Notebook – interactive computing Keras – neural network library KNIME – data analytics platform Matplotlib – data visualization library MLlib – machine learning library for Apache Spark NumPy – numerical computing library Orange – data mining tool pandas – data manipulation library PyTorch – machine learning and deep learning framework Python R – statistical computing language SageMath – mathematics and data analysis environment SciPy – scientific computing library scikit-learn – Python machine learning library TensorFlow – machine learning framework WEKA – machine learning and data analysis suite 3G Bridge – grid interoperability Advanced Resource Connector – middleware BOINC – volunteer computing HTCondor – high-throughput computing Simple Grid Protocol – grid computing UNICORE – middleware CP2K – atomistic and molecular simulation of solid-state, liquid, molecular, and biological systems Open-source software Open-source license Comparison of file synchronization software § Open-source GNOME Core Applications List of concept- and mind-mapping software § Free and open-source List of formerly proprietary software List of GNU packages List of HDL simulators § Free and open-source simulators List of KDE applications List of open-source hardware projects List of optimization software § Free and open-source software List of public domain projects List of spreadsheet software § Free and open-source software List of Unix commands This Python script scans a WordPress website for common vulnerabilities and logs the findings into a CSV file. It checks for several WordPress-specific security issues, including version disclosure, exposed configuration files, REST API exposure, and more.
Edit the target_url variable in the script to specify the WordPress website you want to scan: python Copy code target_url = "http://example.com" # Replace with the target WordPress URL The results of the scan will be saved to a CSV file ( wordpress_vulnerability_report.csv by default). The file includes the URL, type of vulnerability, and additional details.
Adjust the user_id range in the user enumeration section for a more thorough scan: python Copy code for user_id in range(1, 50): # Adjust range as needed This script is for educational purposes only. The author is not responsible for any misuse of this script. A Python script to scan WordPress sites for vulnerabilities like version disclosure, exposed wp-config.php, XML-RPC issues, REST API exposure, user enumeration, and outdated plugins/themes. Logs results to a CSV file for easy analysis. For educational use only.
WPSeku (pronounced âIIW-P-SekuâII ) is a Python-based, open-source vulnerability scanner focused on WordPress environments. Developed by Momo Outaadi, it detects security flaws in WordPress core, plugins, and themes by comparing site components against a curated database of known vulnerabilities. WPSeku sends HTTP requests to the target WordPress site and analyzes responses to identify: Note: Only scan sites you own or have explicit permission to test (ethical hacking rules apply).
WPSeku is a powerful, free tool for WordPress security. Its open-source nature and focus on WordPress vulnerabilities make it ideal for proactive security. Combine it with regular updates, strong passwords, and a layered security approach (e.g., firewall, backup) to reduce your siteâIIs risk. Remember: security is ongoingâIIscan regularly and stay updated! Our company comprises seasoned professionals, each an expert in their field. Customer satisfaction is our top priority, exceeding clients' needs. We ensure competitive pricing and quality in web and mobile development without compromise.
In today's digital landscape , WordPress powers over 40% of websites on the internet, making it a popular target for hackers. Ethical hacking, or penetration testing, involves identifying and fixing security vulnerabilities to protect websites from malicious attacks . This blog will guide you through ethically hacking WordPress sites to enhance their security using Python. Python, known for its simplicity and power, is a popular language for ethical hacking. It offers numerous libraries and frameworks that simplify the hacking process. Its extensive ecosystem, ease of use, and strong community support make it an ideal choice for security professionals.
Install Python : If not already installed, download and install Python from python.org . Gathering information about the target site is the first step in ethical hacking. You can use Python to automate this process. Test for weak passwords using a brute force attack script. Note: This should only be done with explicit permission and within legal boundaries.
Check for SQL injection vulnerabilities. This example checks if a vulnerable parameter can be found in the site's URL. Document your findings and provide a detailed report to the site owner. Include the following in your report: This guide is intended for educational purposes only. Unauthorised testing, hacking, or accessing websites is illegal and unethical. You'll always need explicit permission from the website owner before conducting any security testing. The author and publisher of this guide are not responsible for any misuse or damage caused by the information provided here.
I also lost about $75,000 to an IQ option broker and 2 fake binary option websites as well but I am sharing my experience here to enlighten and educate everyone who is losing money or has lost money to a scam including binary options dating scams Recover all your lost money to Bitcoin and other Cryptocurrency mortgage real estate scams and fake ICOs. However I have been able to recover all the money I lost to the scammers with the help of a recovery professional and I am pleased to inform you that there is hope for everyone who has lost money to scam You can reach out to them at recoveryexpert326 at gmail dot com Whether you're a curious newbie entering the world of programming or an experienced developer looking to extend your skill set, this Python Series is your entryway to harnessing Python's potential.
ByteScrum’s business acumen fills performance gaps, delivering tailored solutions in web and mobile development, transforming emerging technologies, meeting deadlines, and ensuring quality. Python tool for scanning wordpress websites and checking the security level on the website Python tool for scanning wordpress websites and checking the security level on the website In modern web security testing, automation plays a critical role in quickly identifying potential vulnerabilities and misconfigurations. Instead of manually running multiple tools one by one, I built a Python-based automated scanner that integrates widely used Linux security tools into a single workflow.
This project combines the capabilities of Nmap, WhatWeb, and Nikto to analyze a target website efficiently and present results in both technical and human-readable formats. This approach is particularly useful for beginners, students, and developers who want to understand web security without getting overwhelmed by raw command-line outputs.
The system is designed using Python as the orchestration layer. It interacts with external security tools using the subprocess module and processes their outputs programmatically. * 1. Nmap – Port and Service Discovery * Nmap is used to identify open ports and exposed services on the target system. One of the key features of this project is not just running scans, but making the results understandable.
Instead of overwhelming users with raw logs, the scanner produces a structured explanation: Fast scanning modes for all tools Limited scan scope where possible Reduced unnecessary checks Silent subprocess execution 3. Software Implementation, Frameworks & Protocols Despite using multiple tools, the scanner maintains a balance between speed and accuracy.
These challenges were addressed through controlled command execution and output parsing strategies. This project demonstrates how traditional command-line security tools can be transformed into a programmable and automated security solution using Python. By combining tools like Nmap, WhatWeb, and Nikto, and adding intelligent parsing and reporting, we can build a system that is both technically powerful and user-friendly.
Automation in cybersecurity is not just about speed—it’s about making complex data accessible, actionable, and scalable. This blog presents the concept, workflow, and output of my automated scanner. The implementation includes Python-based subprocess execution, result parsing, and structured reporting. Neat idea for automating scans! One thing I've wrestled with when orchestrating tools via subprocess is how brittle regex can be for parsing their outputs, especially when Nmap, WhatWeb, or Nikto update. Have you thought about using existing Python wrappers for these tools? Might make parsing a bit more resilient.
I used subprocess with regex mainly to keep things simple and easy to understand, especially for beginners. But yeah, I agree it can be fragile if tools like Nmap, WhatWeb, or Nikto change their output format. Using structured outputs or Python wrappers would definitely make it more reliable. I’m planning to explore that next to improve the project.
II Legal and Ethical Warning Use this suite only on websites you own or have explicit permission to test . Unauthorized testing is illegal and unethical. Exploitation mode ( --exploit ) may trigger security plugins (e.g., Wordfence), affect live users, or violate hosting terms. Always test in a staging environment and back up your site before running tests. website_security_scanner.py Scans vulnerabilities and generates detailed reports using Anthropic's Claude model, ideal for in-depth analysis.
sql_injection_tester.py Tests for SQL Injection vulnerabilities, targeting WordPress tables like wp_users and wp_options . csrf_attack_tester.py Identifies CSRF vulnerabilities by checking for missing nonces and simulating unauthorized form submissions. (If requirements.txt is not provided, install libraries individually as shown in the Prerequisites section.) Each script can be run independently, with options for verbose output, exploitation mode, and specific tests. Below are detailed instructions for each.
Note: Ensure your Anthropic API key is valid and has sufficient credits. Claude’s responses may vary based on model availability. Please ensure your code follows PEP 8 guidelines and includes appropriate documentation or comments. If you find this project helpful and would like to support its development, you can contribute through the following methods: Secure your WordPress site today! Run the suite, fix vulnerabilities, and stay safe from attackers. Happy testing! I WordPress Security Testing Suite, a robust collection of Python scripts designed to identify, exploit, and analyze vulnerabilities in WordPress websites.
WPSeku is a black box WordPress vulnerability scanner that can be used to scan remote WordPress installations to find security issues. – Plecost – WordPress Fingerprinting Tool – CMSmap – Content Management System Security Scanner – WPScan – WordPress Vulnerability Scanner CMS Detection and Exploitation suite - Scan WordPress, Joomla, Drupal and over 180 other CMSs Fast and stealth WordPress scanner, no api-key, no limitation. Use the top-notch free open-source API www.wpvulnerability.net I'm looking for contributors helping me to dev an auto-exploit module.
uscan is a web scanner designed to target systems such as WordPress, Joomla, Drupal, and Vbulletin. It uses automation to identify vulnerabilities in a target system, making it a more efficient and effective Advanced web fuzzing tool with 16 curated dictionaries, automatic response analysis, and professional report generation. Made for pentesters.
Nemoscan is a script For Get Information About Targets Using Online API That Perform Speed Nmap, geoip ,dnslookup,whois,reverse_ip_lookup include In a directory-fuzzer Bulk WordPress discovery tool. Generate domain lists, scan in parallel, find WP sites. Modular, AI-powered, and powerful WordPress auditing and scanning tool for security, and configuration checks. I Scopex is a lightweight, passive-first reconnaissance tool designed to identify WordPress attack surfaces safely and efficiently, while strictly respecting scope boundaries.
A lightweight directory/file scanner using custom payloads (inurl, filetype, intitle, etc.) for security testing on authorized targets. To associate your repository with the wordpress-scanner topic, visit your repo's landing page and select "manage topics." Defensive WordPress security scanner. 294 checks, CVE feed aggregated nightly from up to 8 public sources, AI-assisted remediation (BYO key), check-level compliance mappings for 12 frameworks, Sigstore-signed releases with GitHub build-provenance attestations, 9 report formats plus 14 exports, a sites registry, batch scans, a --daemon scheduler, and a token-protected --api-server with a target allowlist. Authorized testing only.
WPSecScan is a defensive security tool. Use it only on sites you own or sites whose owner has given you written permission to test. Unauthorised scanning is illegal in most jurisdictions (e.g. the US Computer Fraud and Abuse Act, the UK Computer Misuse Act 1990, the EU Network and Information Security Directive). The maintainers accept no liability for misuse. By using this software you confirm you have the required authorisation for every target you scan.
294 checks (31 of them aggressive) plus an authenticated check that runs when you supply credentials. CVE feed aggregated nightly from up to 8 public sources; per-source counts are in the feed header. Sigstore-signed releases with GitHub build-provenance attestations. Aggressive checks run passive unless the target is marked as owned (see Safety ). Distribution: PyPI ( pip install wpsecscan ), the GitHub release assets ( wpsecscan.exe , wpsecscan-gui.exe , wheel, sdist), or a source install. The Dockerfile in this repo is for building an image yourself; no pre-built image is published.
Ships as two standalone Windows binaries — no Python required on the machine you run them on. 4. Practical Deployment, Analysis & Case Studies For the optional GUI minimize-to-tray feature, install with the [ui] extra (pulls in Pillow + pystray): Other optional extras: [pdf] (reportlab for true PDF exec reports), [browser] (playwright for headless DOM-XSS), [yaml] (pyyaml for daemon config), [ops] (redis for the shared CVE-DB cache), or [all] to install everything.
Each release also carries SHA256SUMS.txt , Sigstore .sig / .pem files and a CycloneDX SBOM; see docs/verify-release.md to check them. The first time you run them, Windows SmartScreen may warn that the publisher is unknown (the binaries aren't code-signed). Click More info → Run anyway .
This creates a virtualenv in .venv\ , installs the project and PyInstaller ( pip install -e . ), and runs PyInstaller. Output: Exit codes : 0 = clean / info only · 1 = medium findings · 2 = critical or high findings · 130 = Ctrl+C. Passive checks always run; aggressive checks need --aggressive and a target marked as owned (see Safety ). Round fifty-four added the checks and non-check tooling below (the current registry total is given in the heading of the previous section): Every sensitive flag — --auth-pass , --auth-app-password , --companion-token , --proxy-auth , --wpscan-token , --patchstack-token , --hibp-token , --vt-token , --abuseipdb-token , --github-search-token — reads from a matching WPSECSCAN_
"Windows protected your PC" SmartScreen warning — click More info → Run anyway . The binaries aren't code-signed. Defender quarantines wpsecscan.exe with Backdoor:JS/Chopper.GG!dha — known false positive. This is a defensive scanner: to detect webshells (China Chopper, c99, r57) on your sites it ships references to those attack patterns. Defender's pattern-matching heuristic flags the .exe even though it never executes any of those patterns locally. The same kind of detection trips sqlmap, Metasploit, nuclei, and Gophish — all legitimate security tools.
In the GUI : a dialog pops up on first launch with an "Add exclusion now (UAC)" button. You can also open it any time via Tools → Add Windows Defender exclusion... To restore a quarantined file : Windows Security → Virus & threat protection → Protection history → Allow . "DB: not loaded — click Refresh" in the GUI — click Refresh vuln DB . Or from the CLI: wpsecscan.exe --update-db .
Multi-target scan freezes for one bad URL — each URL has its own per-request timeout. If one consistently hangs, drop it from the list. Cron / scheduled-task entries pile up — list them with schtasks /Query /TN WPSecScan_* and remove individually with schtasks /Delete /TN
GUI crashes immediately on launch — check C:\Users\
AGPL network clause : if you run a modified WPSecScan as a hosted service (SaaS, web UI, paid scanning tier), you must publish your modified source under the same AGPLv3+ terms. Private internal use and modifications stay private. For commercial-distribution licensing terms outside AGPLv3, contact bryaninbangkok@gmail.com . This tool is for defensive use on sites you own. Use against third-party sites without explicit written permission is illegal in most jurisdictions under the Computer Fraud and Abuse Act (US) / Computer Misuse Act (UK) / equivalent laws elsewhere.
GNU Affero General Public License v3 or later (AGPLv3+) (GNU AFFERO GENERAL PUBLIC LICENSE ) GNU Affero General Public License v3 or later (AGPLv3+) (GNU AFFERO GENERAL PUBLIC LICENSE ) For a detailed explanation of source distributions (sdists) and built distributions (wheels), please see the package formats documentation .
Elementor, WooCommerce, Wordfence, Contact Form 7, WP File Manager, LayerSlider, Yoast SEO, Classic Editor, Akismet, Jetpack, wpAutomatic, Fancy Product Designer, WP Activity Log, Custom CSS-JS-PHP, Chatbot with ChatGPT, The Events Calendar, Pix for WooCommerce, Blocksy Companion Pro, WPvivid Backup & Migration, WP User Manager, Remote API, and more.
This tool is intended for authorized security testing only. Always obtain proper written authorization before scanning or exploiting any system. The authors are not responsible for misuse or damage. Aipatch Security Scanner is a modular security audit engine built for site owners, developers, and AI-powered agents who need deep visibility into WordPress security posture — without the bloat of all-in-one security suites.
Most WordPress security plugins are either too simple to be useful or too heavy to be practical. Aipatch takes a different approach: Aipatch runs 36 automated checks across 8 categories — core, plugins, themes, users, configuration, server, access control, and malware surface: Every finding includes a severity (critical / high / medium / low / info), confidence score, human-readable explanation, and actionable recommendation.
A logarithmic scoring engine computes an overall security score and per-area breakdown across six risk dimensions: software, access control, configuration, infrastructure, malware surface, and vulnerability exposure. Severity weights and confidence multipliers ensure the score reflects actual risk, not just issue count. A three-layer file scanner (content 55%, context 25%, integrity 20%) with 27 detection signatures, Shannon entropy analysis, and malware family classification detects: Scanning runs in batches via an async job system with configurable batch sizes — safe for shared hosting.
Files are classified into 11 malware families (web shell, obfuscated loader, dropper, persistence backdoor, cloaked PHP, code injector, and more) with confidence scores and remediation hints. Verifies every core file against official checksums from api.wordpress.org. Detects modified core files (checksum mismatch), missing core files, and unexpected files planted in wp-admin/ or wp-includes/. Core tampering findings are automatically escalated to critical severity with zero false-positive likelihood.
Build a known-good hash baseline of all PHP files in your installation. Diff against it at any time to detect modified, deleted, or newly added files. Origin detection distinguishes core, plugin, theme, and upload files. A local knowledge base of known plugin, theme, and core vulnerabilities with a database-backed caching layer for fast lookups. Provider architecture allows extending with external feeds.
Apply fixes directly from findings — change WordPress options, delete suspicious files, rename files, patch file contents, or add .htaccess rules. Every automated action stores a full rollback payload so you can reverse any change. Manual remediations can be logged for audit trails. 5. Performance Evaluation & Extended Technical Observations Six supported action types: wp_option , delete_file , rename_file , file_patch , htaccess_rule , manual .
All audit findings persist in a dedicated database table with automatic deduplication by fingerprint. Track findings over time — dismissed findings stay dismissed across scans; resolved findings reopen if the issue reappears. Every scan, hardening change, remediation, and significant event is logged to a dedicated table. Logs are filterable by severity and exportable as CSV.
Adds 6 security tests to the built-in Site Health screen: file editor, debug mode, XML-RPC, admin username, SSL, and overall security score. Built-in performance profiling to identify slow queries, high memory usage, and resource bottlenecks related to security operations.
10 authenticated endpoints under the aipatch-security-scanner/v1 namespace for triggering scans, retrieving summaries, toggling hardening, exporting logs, and running performance diagnostics. Aipatch exposes 23 structured abilities via the WordPress Abilities API — making your site’s security surface fully accessible to external AI agents, coding assistants, and orchestration tools: By default, only aipatch/audit-site is enabled. You can enable additional abilities from Aipatch Security Scanner -> Settings -> MCP Abilities .
20 abilities are read-only; only 3 (dismiss, apply-remediation, rollback) modify site state. All abilities include typed input/output schemas, permission checks ( manage_options ), and structured error responses. For AI agent integration, ensure the WordPress Abilities API is available and connect your agent to the aipatch/audit-site ability.
36 automated checks across 8 categories: WordPress core, plugins, themes, users, configuration, server, access control, and malware surface. Each finding includes severity, confidence, evidence, and a specific recommendation. No. Aipatch adds nothing to the frontend. Audits run on demand, via WP-Cron, or through the REST API. The malware file scanner uses a job-based batch system so it never monopolizes server resources.
No. Everything runs locally with zero external dependencies. The vulnerability provider architecture supports optional external feeds for extended coverage. Yes. The multi-layer file scanner uses 27 detection signatures covering code execution, obfuscation, backdoor patterns, and WordPress-specific threats, plus Shannon entropy analysis for encoded payloads. Files are classified as clean, suspicious, risky, or malicious with a 0–100 risk score and assigned to one of 11 malware families (web shell, obfuscated loader, dropper, backdoor, etc.) with confidence levels. WordPress core files are additionally verified against official checksums from api.wordpress.org.
Every automated remediation stores full rollback data. You can reverse any change — restored files include original content and permissions, reversed options include the previous value, removed .htaccess rules are cleanly deleted. Manual remediations are tracked but not auto-reversible. Yes. Aipatch focuses on auditing, scanning, and remediation — not request filtering. It coexists with firewalls like Wordfence, Sucuri, or Cloudflare without conflicts.
MCP (Model Context Protocol) is the standard for AI agents to interact with tools. Aipatch exposes 23 structured abilities via the WordPress Abilities API, allowing AI agents to audit your site, scan for malware, verify core integrity, track findings over time, and apply fixes — all through typed, permissioned tool calls. 20 are read-only; only 3 modify site state. Audit findings, scan history, file baselines, scan results, remediation records, vulnerability cache, job state, hardening preferences, settings, and event logs — all in your WordPress database. Nothing leaves your server.
“Aipatch Security Scanner” is open source software. The following people have contributed to this plugin. > your AI agent picks dependencies from memory; give it dated facts — try starlog.dev I vet your agent's deps I vibe-coding is fine. vibe-importing isnâIIt. — try starlog.dev I vibe-importing isnâIIt fine I your agent has never seen your private packages — try starlog.dev I facts for private packages I a linter for the dependencies your AI agent picks — try starlog.dev I a linter for agent deps I whois is redacted, cdns mask the rest âII get the real operator — try whoisgeni.us I who really runs that domain I domain attribution that shows its work âII full evidence chain — try whoisgeni.us I domain intel w/ evidence I Metrics below are heuristic approximations computed from repository structure, not authoritative measurements.
Most security teams scan for hundreds of vulnerabilities. This repository scans for 74,000âIIand updates itself every single day without human intervention. WordPress powers 43% of the internet, making it the world's largest attack surface for web applications. Security teams face an impossible challenge: tracking vulnerabilities across 60,000+ plugins, thousands of themes, and WordPress core itself.
Wordfence maintains comprehensive threat intelligence, but their data sits in an APIâIIuseful for their commercial scanner but inaccessible to teams using open-source tools like Nuclei. Meanwhile, ProjectDiscovery's official nuclei-templates repository contains excellent coverage for general web vulnerabilities but only a few hundred WordPress-specific checks. The topscoder/nuclei-wordfence-cve repository bridges this gap with radical automation. Instead of manually curating templates, it treats Wordfence's API as a data source and programmatically generates Nuclei YAML templates for every vulnerability they track. The result is a living, breathing vulnerability database that transforms 70,000+ WordPress CVEs into scannable templates, updated daily via GitHub Actions. For security engineers managing WordPress fleets or bug bounty hunters targeting WordPress sites, this repository eliminates the manual work of tracking plugin vulnerabilities and translates threat intelligence directly into actionable scans.
The architecture centers on a Python ETL pipeline that runs daily in GitHub Actions. The core script fetches two JSON feeds from Wordfence: production vulnerabilities (CVE-assigned) and candidate vulnerabilities (not yet assigned CVEs). It parses each entry, extracts metadata like affected versions, vulnerability types, and CVSS scores, then generates structured Nuclei YAML templates with proper matchers and metadata fields.
The template generation logic is where this project shines. A typical auto-generated template looks like this: The severity recalibration engine is particularly clever. Wordfence assigns severity based purely on CVSS scores, but the pipeline implements business logic to adjust ratings. For example, an authenticated SQL injection in an admin panel might get downgraded from critical to high, while an unauthenticated remote code execution in a plugin with 5 million installations stays critical. This recalibration happens in the transformation layer, using pattern matching against vulnerability descriptions and affected component metadata.
The repository organization reflects real-world scanning needs. Templates are separated into /production/ (CVE-assigned, verified vulnerabilities) and /candidates/ (reported but unverified). Within each, there are subdirectories for /plugins/ , /themes/ , and /core/ , enabling targeted scans. A security team auditing a specific WordPress installation can scan just the plugins they've identified, rather than running all 74,000 templates.
The GitHub Actions workflow is the heartbeat of the system. Every 24 hours, it fetches fresh data from Wordfence, diffs against existing templates, generates new ones for discovered vulnerabilities, updates existing templates if severity changes, and commits everything back to the repository. This means users who clone the repo and pull daily get zero-day WordPress vulnerability coverage with near-zero latency after Wordfence publishes intel.
The automation is pure infrastructure-as-codeâIIno databases, no servers, just Git as the storage layer and GitHub Actions as the compute engine.
For integration into CI/CD pipelines, the workflow is straightforward. Clone the repo in your pipeline, use Nuclei's -t flag to point at the template directory, and parse the JSON output for vulnerability matches. Many teams schedule weekly scans against their WordPress staging environments, filtering for high/critical severities only, and automatically create Jira tickets from Nuclei's JSON output.
The biggest limitation is detection accuracy versus exploitation reality. These templates primarily work by fingerprinting plugin and theme versions through readme.txt files or version strings in source code. If a WordPress site has disabled readme.txt file access (a common security hardening step), hidden version information through custom code, or implemented a Web Application Firewall that blocks version enumeration requests, the templates will fail to detect vulnerabilitiesâIIeven if they exist. You're not exploiting vulnerabilities; you're detecting potential exposure based on version matching.
The auto-generation process also means template quality varies significantly. A manually crafted Nuclei template by a security researcher will include multiple detection methods, edge case handling, and verified exploitation paths. These auto-generated templates are more like version checkers with CVE metadata attached. For critical infrastructure scanning, you'll want to manually review and enhance templates for your most important checks rather than trusting the automated output blindly.
Additionally, the sheer volume creates noiseâII74,000 templates take time to run even with Nuclei's concurrency, and you'll need robust filtering strategies to avoid spending hours scanning for vulnerabilities in plugins you don't even use. The repository provides the raw materials, but you need to curate your own subset for practical scanning workflows. Use if: You're managing WordPress security at scale (multiple sites, WordPress-focused penetration testing, or bug bounty programs), you need comprehensive coverage of the WordPress plugin/theme ecosystem, you're comfortable with automated detection and have processes to triage results, or you're building security automation pipelines where daily-updated vulnerability intelligence provides value. This is the definitive WordPress vulnerability template collection for Nuclei users. Skip if: You're securing non-WordPress applications, you need exploitation frameworks rather than detection (check WPSploit instead), you require manually vetted templates for compliance or high-assurance environments, or you're scanning hardened WordPress installations where version fingerprinting is blocked. Also skip if you lack the infrastructure to handle 74,000 templatesâIIthis isn't a lightweight tool, and you'll need filtering discipline to extract value without drowning in scan time and false positives.
Inside the Uncensored AI Arsenal: A Critical Look at Offensive Security Model Repositories Flowsint: Building a Graph-Based OSINT Platform That Doesn't Choke on Async Enrichment Inside the Uncensored AI Arsenal: A Critical Look at Offensive Security Model Repositories Flowsint: Building a Graph-Based OSINT Platform That Doesn't Choke on Async Enrichment Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Google%20Cloud%20Platform • https://en.wikipedia.org/wiki/List%20of%20free%20and%20open-source%20software%20packages • https://github.com/taleblou/WordPressVulnerabilityScanner_Python • https://www.dotlinux.net/blog/wpseku-a-vulnerability-scanner-to-find-security-issues-in-wordpress/ • https://blog.bytescrum.com/ethical-hacking-wordpress-sites-using-python-a-step-by-step-guide • https://github.com/kodkodcyber/wordpress-security-scan • https://dev.to/ganesh_hari_18/building-a-fast-automated-web-security-scanner-using-python-and-open-source-linux-tools-n7 m • https://github.com/RaheesAhmed/WordPress-Security-Testing-Suite • https://www.blackmoreops.com/wpseku-wordpress-security-scanner/ • https://github.com/topics/wordpress-scanner?l=python
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Automated Security Scanner For Wordpress Sites Python.
[*] Metasploit Scan Running on Target Subnet for Automated Security Scanner For Wordpress Sites Python... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |