Complete Technical Paper Content — Automated SQL Injection Scanner And Exploiter Tool Python
Overview & System Context
Automated Sql Injection Scanner And Exploiter Tool Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~7396 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background This is a list of free and open-source software (FOSS) packages, computer software licensed under free software licenses and open-source licenses. Software that fits the Free Software Definition may be more appropriately called free software; the GNU project in particular objects to their works being referred to as open-source. For more information about the philosophical background for open-source software, see free software movement and Open Source Initiative. However, nearly all software meeting the Free Software Definition also meets the Open Source Definition and vice versa. A small fraction of the software that meets either definition is listed here. Some of the open-source applications are also the basis of commercial products, shown in the List of commercial open-source applications and services.
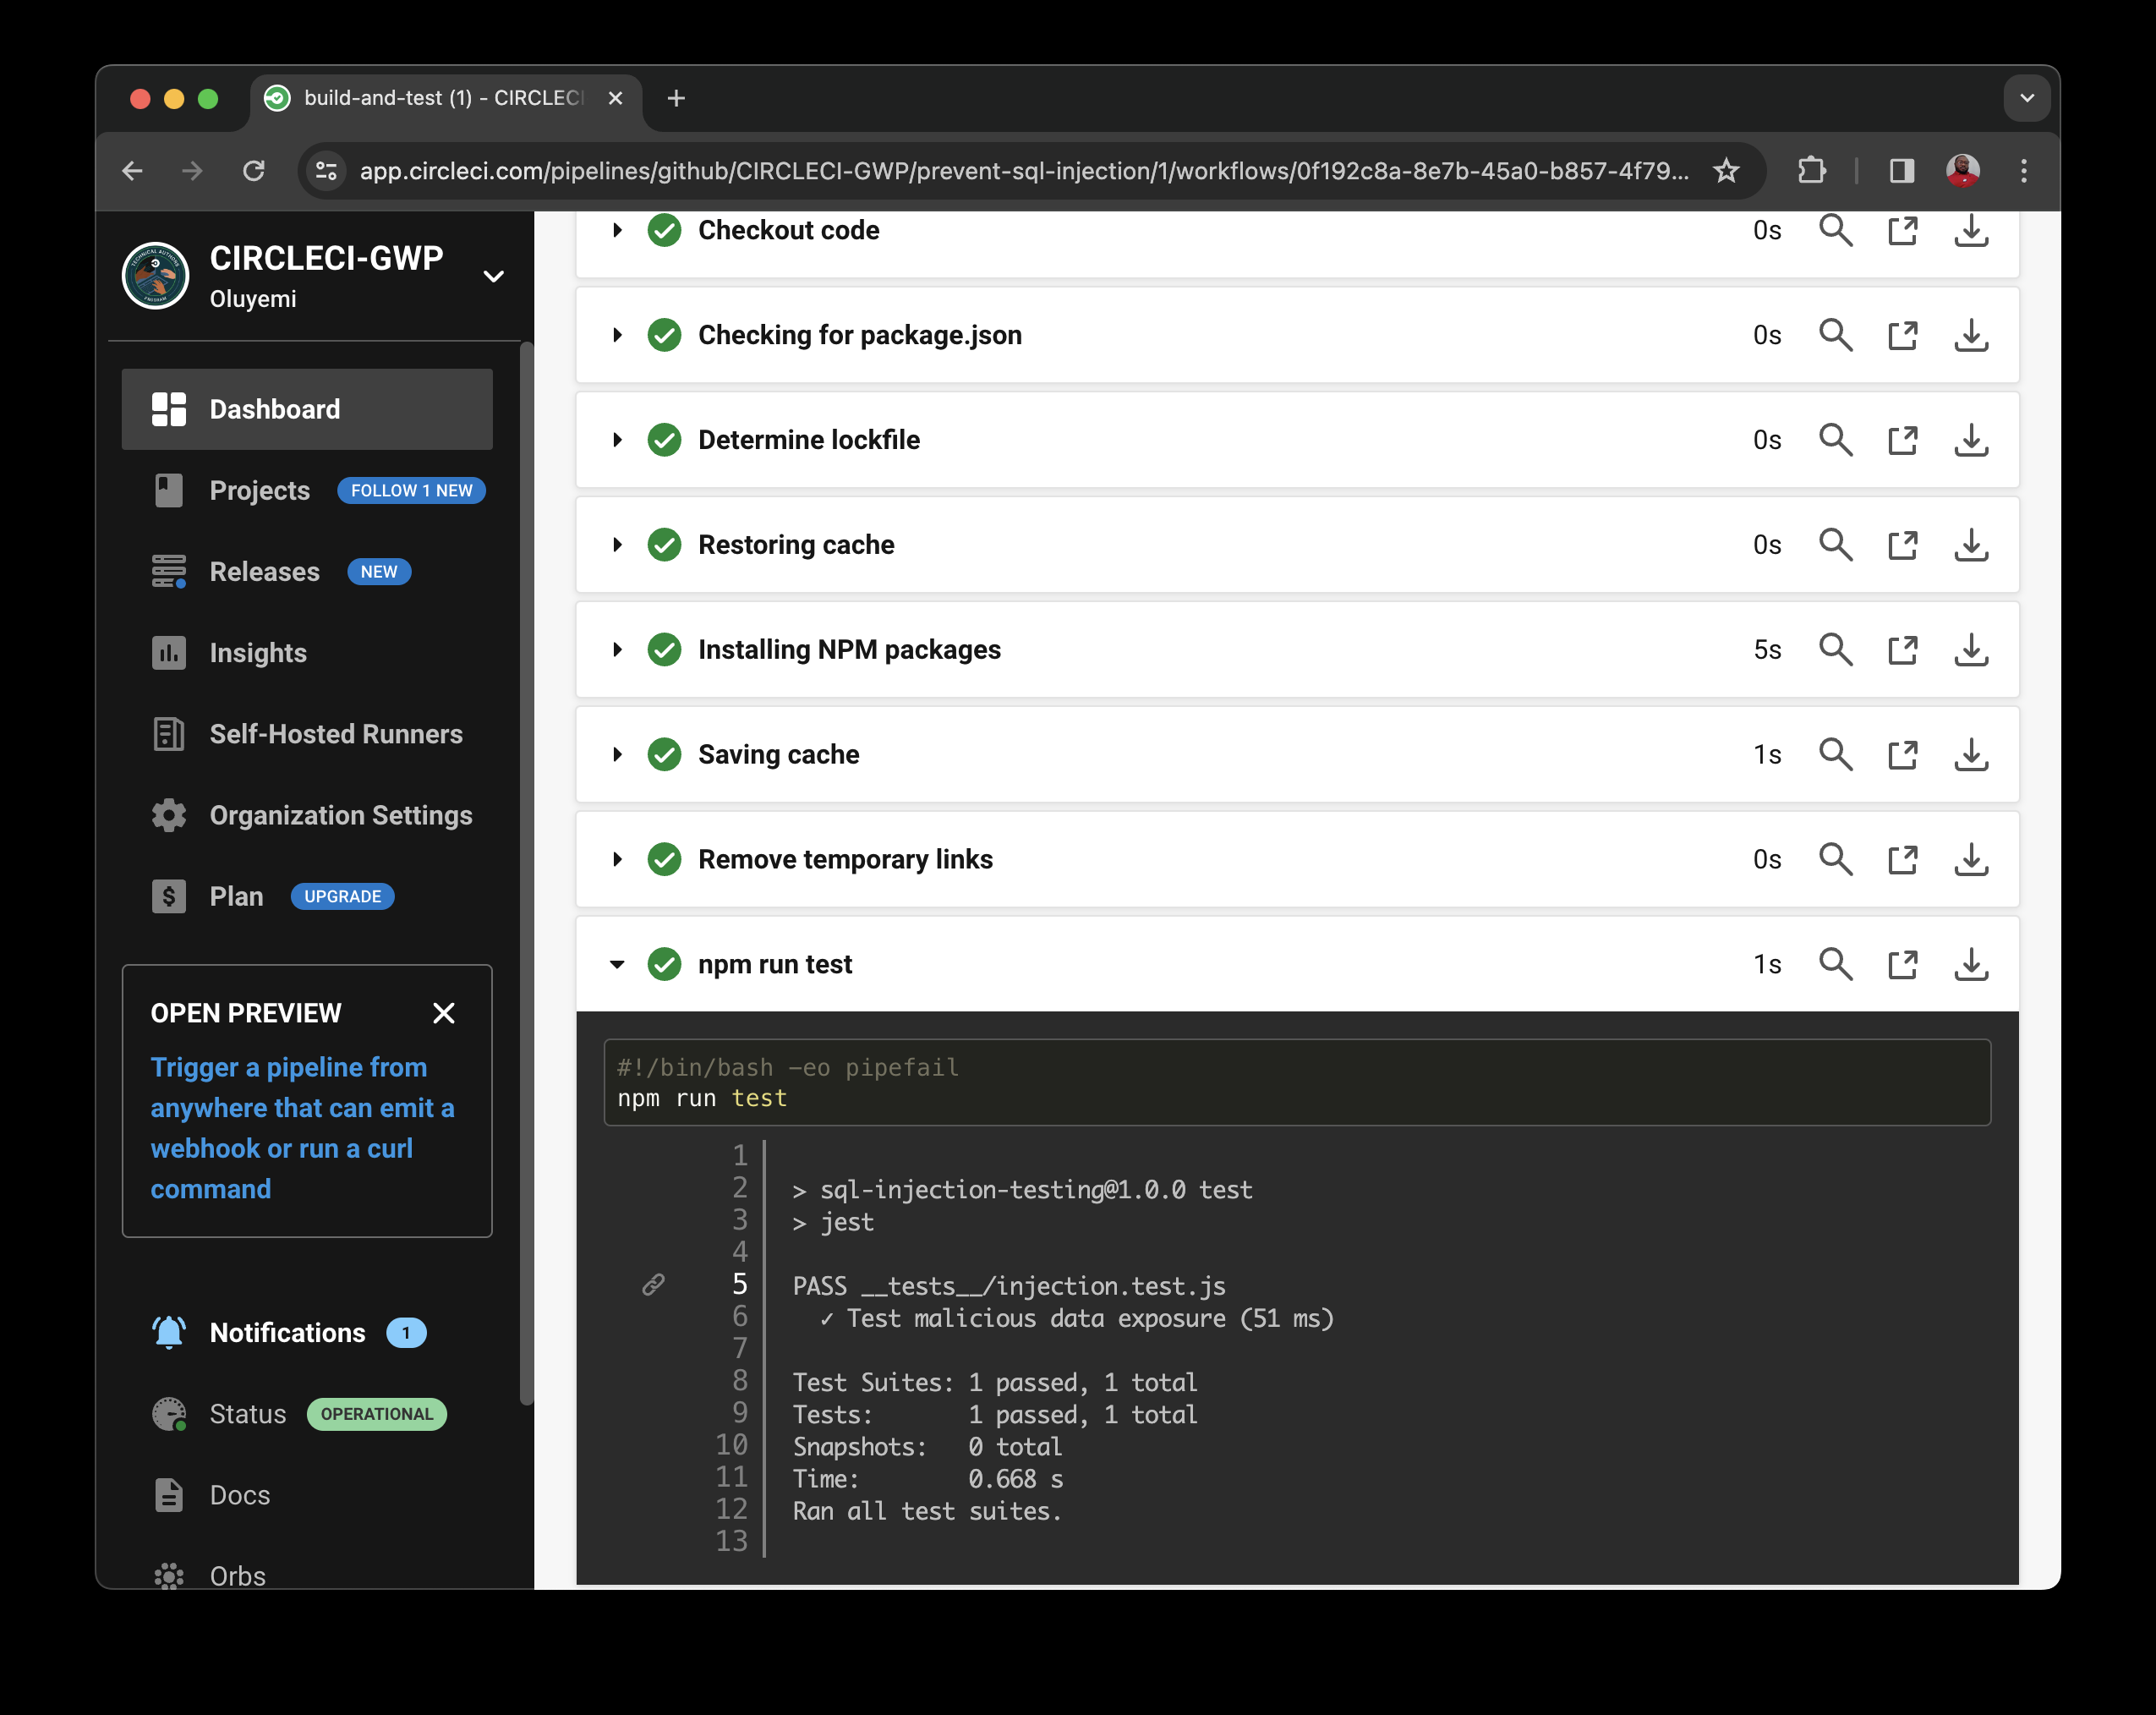
Cline – AI coding agent for IDEs and the command line. Codex CLI – AI coding agent and command-line interface developed by OpenAI. Command Code — CLI and desktop AI agent DeepSeek Coder – large language model designed for code generation and AI-assisted software development. Eclipse Theia – integrated development environment and framework with AI-assisted software development features. goose – AI coding agent for the desktop and command line. Kilo Code — CLI and IDE extension developed by Anaconda OpenCode — CLI, desktop app, web app, and IDE extensions OpenHands — AI software development agent Oh My Pi – terminal-based AI coding agent developed as a fork of Pi. Pi – terminal-based AI coding agent. Zed – source-code editor with integrated AI-assisted development and agentic coding features.
Apertus – Swiss National AI Initiative LLM BERT – Google LLM BLOOM – BigScience multilingual LLM Cerebras-GPT – Cerebras Systems LLMs DeepSeek – R1 and V3 models Gemma 4 – Google LLM GLM-4.5 and later versions – Z.ai LLMs GPT-1, GPT-2, and GPT-OSS – OpenAI LLMs GPT-J, GPT-Neo, and GPT-NeoX – EleutherAI LLMs Hy – Tencent open-weight LLM Granite – IBM LLMs Grok-1 – xAI LLM Inkling – Thinking Machines Kimi (some versions) – Moonshot AI LLMs MiMo (some versions) – Xiaomi LLMs Mistral (some versions) Muse Glimmer — Meta Superintelligence Labs LLM Nemotron 3 – Nvidia open-weight models OLMo – Allen Institute for AI LLM Phi – Microsoft LLMs Qwen (some versions) – Alibaba Cloud LLMs Sarvam-M, Sarvam-105B and Sarvam-30B – Sarvam AI LLMs SmolLM – Hugging Face small language models (SLMs) Step-3.7Flash – StepFun LLM T5 – Google LLM XLNet – Google LLM ArduPilot CoppeliaSim Gazebo Mobile Robot Programming Toolkit OpenRTM-aist Paparazzi Project Player Project Python Robotics Robot Operating System (ROS) TurtleBot UBtech Thinker Webots – robot simulator Figure 1: Preventing SQL injection attacks with automated testing | CircleCI Archimedes (CAD) Art of Illusion Blender BRL-CAD – constructive solid geometry (CSG) solid modeling computer-aided design (CAD) system FreeCAD – parametric 3D CAD modeler with a focus on mechanical engineering, BIM, and product design LeoCAD — beginner Lego 3D modeler LibreCAD – 2D CAD software using AutoCAD-like interface and file format MakeHuman MeshLab Open Cascade Technology (OCCT) – CAD kernel for 3D CAD, CAM, CAE OpenSCAD – scripting-based 3D CAD software QCAD SolveSpace – 2D and 3D CAD, constraint-based parametric modeler with simple mechanical simulation abilities Sweet Home 3D Wings 3D Electric FreePCB Fritzing – CAD software for the design of electronics hardware to build more permanent circuits from prototypes gEDA GNU Circuit Analysis Package (Gnucap) Icarus Verilog KiCad – suite for electronic design automation (EDA) for schematic capture, PCB layout, manufacturing file viewing, SPICE simulation, and engineering calculation KTechLab Magic Ngspice pcb-rnd Oregano Quite Universal Circuit Simulator (QUCS) Verilator XCircuit Blender – 3D computer graphics software toolset used for creating animated films, visual effects, art, 3D printed models, and motion graphics FreeCAD – equivalent of Blender geared toward mechanical engineers OpenFOAM – software used for computational fluid dynamics (or CFD) FlightGear – atmospheric and orbital flight simulator with a flight dynamics engine (JSBSim) that was used in a 2015 NASA benchmark to judge new simulation code to space industry standards SimPy – queue-theoretic event-based simulator written in Python Salome – generic platform for Pre- and Post-Processing for numerical simulation OpenPGP – open-source version of Pretty Good Privacy GNU Privacy Guard – replacement for PGP OpenSSL – library for applications that provide secure communications over computer networks NaCl (software) – crypto library Libsodium – fork of NaCl VeraCrypt – disk encryption software forked from TrueCrypt LUKS – standard for disk encryption on Linux systems Nym (mixnet) – mix network that uses noise and random packet timing for obfsucation, overlay network for NymVPN Tor (network) – free overlay network for enabling anonymous communication Tails (operating system) – security-focused Linux distro using Tor by default Signal (software) – secure messaging app Off-the-Record Messaging – protocol for secure instant messaging GPGTools – macOS suite for GnuPG-based encryption Figure 2: SQL Injection — MySQL for Python Developers — PlanetScale Aircrack-ng – Wi-Fi security auditing tool BackTrack – predecessor to Kali Linux Burp Suite Community Edition – security assessment and penetration testing of web applications Ghidra – software reverse engineering suite developed by the NSA Hashcat – password recovery utility High Orbit Ion Cannon – DDoS hping3 — packet crafting and network penetration-testing utility Hydra (software) – login cracker supporting numerous protocols John the Ripper – password cracking tool Kali Linux – penetration testing Linux distribution Metasploit Project – framework for developing and executing exploit code Netcat – network utility for reading/writing data across networks Nikto (vulnerability scanner) – web server vulnerability scanner Nmap – network scanning, port scanner, and auditing tool OpenSSH – implementation of the SSH protocol Radare2 – reverse engineering framework Snort (software) – network intrusion detection system sqlmap – automated SQL injection and database takeover tool Suricata (software) – network threat detection engine Volatility (memory forensics) – memory forensics framework for incident response Wireshark – network protocol analyzer YARA – tool to identify and classify malware qBittorrent – BitTorrent client Transmission (BitTorrent client) – lightweight BitTorrent client IPFS – InterPlanetary File System for decentralized storage and sharing RetroShare – secure communication platform with file sharing Zerocoin – privacy-focused cryptocurrency protocol Zcash – cryptocurrency based on Zerocoin using zk-SNARKs Monero – privacy-focused cryptocurrency using ring signatures NYM — Nym mixnet privacy- and security-focused token Tornado Cash — Cryptocurrency tumbler ClamAV – cross-platform antimalware toolkit written in C and C++, able to detect many types of malware including viruses ClamWin – antivirus tool for Windows and written in C, C++ Lynis – security audit tool (set of shell scripts) for Unix and Linux Figure 3: How to Use MySQL Database in Python - Python Code Bouncy Castle GnuPG GnuTLS KGPG NaCl OpenSSL Seahorse Signal stunnel TextSecure wolfCrypt 7-Zip Snort – network intrusion detection system (IDS) and intrusion prevention system (IPS) Suricata – network threat detection engine OpenVAS – software framework of several services and tools offering vulnerability scanning and vulnerability management Nmap – network scanner, port scanner, and security auditing tool Nikto – web server vulnerability scanner Volatility – memory forensics framework for incident response Cyberduck – macOS and Windows client (since version 4.0) Lsh – server and client, with support for SRP and Kerberos authentication OpenSSH – client and server PuTTY – client-only Apache Cassandra – NoSQL database from Apache Software Foundation offers support for clusters spanning multiple datacenter Apache CouchDB – NoSQL database from Apache Software Foundation with multi-master replication MariaDB – community-developed relational database management system with pluggable storage engines and commercial support PostGIS – adds support for geographic objects to the PostgreSQL as per Open Geospatial Consortium (OGC) PostgreSQL – relational database management system emphasizes on extensibility and SQL compliance and available for Windows, Linux, FreeBSD, and OpenBSD ATutor – web-based Learning Content Management System (LCMS) Canvas LMS – web-based, open, extensible learning management system Chamilo – web-based e-learning and content management system Claroline – collaborative Learning Management System DoceboLMS – SAAS/cloud platform for learning eFront – icon-based learning management system H5P – framework for creating and sharing interactive HTML5 content IUP Portfolio – educational platform for Swedish schools ILIAS – web-based learning management system (LMS) Moodle – learning management system OLAT – web-based Learning Content Management System Omeka – content management system for online digital collections Sakai Project – web-based learning management system SWAD – web-based learning management system Kiwix – offline web browser that allows users to download Wikipedia's entire content and use it for offline learning. Later it was expanded with repositories for Wikimedia Foundation, public domain texts from Project Gutenberg, many of the Stack Exchange sites, and other resources OpenStreetMap – OpenStreetMap was developed in 2004. It uses Open data and users data input through Crowdsourcing and Web mapping to create a complete and downloadable alternative to other online maps.
This allow users to enter data when there is no data available due to lack of governance and economic interest or due to lower population of the places mapped Advanced Simulation Library ASCEND Calcpad Calculix CHEMKIN – chemical kinetics COCO simulator – chemical process simulator CP2K – quantum chemistry and solid-state physics DWSIM – chemical process simulator General Mission Analysis Tool (GMAT) – space mission analysis GNU Octave – numerical-analysis GROMACS – simulations of proteins, lipids, and nucleic acids JSBSim – flight dynamics engine LAMMPS – Molecular dynamics Open Babel – chemical informatics OpenModelica – chemical process simulator OpenSees – earthquake engineering OpenVSP – parametric aircraft geometry tool Pyomo – mathematical optimization QBlade – wind turbine design and aerodynamic simulation software REFPROP – reference Fluid Thermodynamic and Transport Properties XFOIL – analysis of subsonic isolated airfoils .apng – Animated Portable Network Graphics .avif – AV1 Image File Format .bpg – Better Portable Graphics .exr – OpenEXR .fits – Flexible Image Transport System primarily for Astronomy .flif – Free Lossless Image Format .gif – Graphics Interchange Format .iff / .lbm – InterLeaved BitMap .jng – JPEG Network Graphics .jpg or .jpeg – Joint Photographic Experts Group .jxl – JPEG XL .mng – Multiple-image Network Graphics .miff / .mi – Magick Image File Format .pam, .pbm, .pgm, .ppm, .pnm – Netpbm file formats .pgf – Progressive Graphics File .png – Portable Network Graphics .qoi – Quite OK Image Format .tiff – Tag Image File Format .wbmp – Wireless Application Protocol Bitmap Format .webp .xbm – X BitMap .xcf – GIMP .xpm – X PixMap .adoc – AsciiDoc .epub – ebook format .latex – LaTeX, macro package built on top of TeX for simplification .md – Markdown .odt – OpenDocument .rtf – Rich Text Format .tex – high-quality typography for mathematical notation, physics, chemistry, engineering/scientific notation .texinfo 1DayLater – invoicing software GnuCash – double-entry book-keeping HomeBank – personal accounting software KMyMoney – double-entry book-keeping LedgerSMB – double-entry book-keeping RCA open-source application – management accounting application SQL-Ledger – double-entry book-keeping TurboCASH – double-entry book-keeping for Windows Bitcoin – blockchain platform, peer-to-peer decentralised digital currency Ethereum – blockchain platform with smart contract functionality CiviCRM – Constituent Relationship Management software aimed at charities and NGOs iDempiere – business Suite, ERP and CRM SuiteCRM – web-based CRM Adempiere – Enterprise resource planning (ERP) business suite Apache OFBiz – suite of enterprise applications from Apache Software Foundation Compiere – ERP solution automates accounting, supply chain, inventory, and sales orders Dolibarr – web-based ERP system ERPNext – web-based ERP system for managing accounting and finance ERP5 – Single Unified Business Model based system written with Python and Zope iDempiere – fully navigable on PCs, tablets and smartphones driven only by a community of supporters JFire – ERP business suite written with Java and JDO LedgerSMB – double entry accounting and ERP system written with Perl metasfresh – ERP Software Odoo – ERP, CRM and CMS Openbravo – web-based ERP Tryton – ERP MAME – multi-platform emulator for arcade game systems Mednafen – multi-platform emulator MESS – multi-platform emulator RetroArch – cross-platform front-end for emulators, game engines and video games Snes9x – Super Nintendo emulator Stella – Atari 2600 emulator PCSX – PlayStation emulator PCSX2 – PlayStation 2 emulator PPSSPP – PlayStation Portable emulator Project64 – Nintendo 64 emulator RPCS3 – PlayStation 3 emulator Dolphin (emulator) – GameCube and Wii emulator Citra (emulator) – Nintendo 3DS and Wii emulator Cemu – Wii U emulator TIC-80 – virtual machine game engine that mimics the 8-bit systems of the 1980s QGIS – cross-platform desktop geographic information system (GIS) application to view, edit, and analyse geospatial data ADMB Euler Math Toolbox FreeMat GNU Data Language GNU MCSim GNU Octave J Julia Owl Scientific Computing Perl Data Language S-Lang Scilab Yorick Blender Game Engine – discontinued 2019 Godot – application for the design of cross-platform video games MonoGame – C# framework Open3DEngine – based on Amazon Lumberyard Stride – (prev. Xenko) 2D and 3D cross-platform game engine originally developed by Silicon Studio Amavis – email content filter Claws Mail – email Client Fetchmail – email Retrieval Geary – email client based on WebKitGTK+ GNUMail – cross-platform email client Hula – discontinued mail and calendar project K-9 Mail – Android Email Client MailScanner – email security system MH Message Handling System – email Client Modest – email Client Mozilla Mail & Newsgroups – email Client that was part of the now discontinued Mozilla Application Suite Mozilla Thunderbird – email, news, RSS, and chat client POPFile – cross-platform mail filter Proton Mail – app and web-based end-to-end encrypted e-mail evolved to become FOSS Roundcube – web-based IMAP email client Sylpheed – email and News Client Sympa – MLA software I2P – anonymous network layer (implemented as a mix network) that allows for censorship-resistant, peer-to-peer communication OnionShare – file sharing app using Tor network Popcorn Time – multi-platform media player qBittorrent – BitTorrent client Transmission – BitTorrent client Deluge – BitTorrent client BSD – FreeBSD, OpenBSD, NetBSD, GhostBSD, TrueNAS, MidnightBSD, DragonFly BSD, OPNsense, pfSense, XigmaNAS, among others. GrapheneOS – Privacy- and security-focused, Android-based mobile operating system Kali NetHunter Linux – Debian, Ubuntu, Manjaro, Fedora, openSUSE, antiX, NixOS, Kali, Alpine, Tails, Mageia, Slackware, Gentoo, BlackArch, among others (List of Linux distributions). LineageOS – Android-based operative system for tablets and mobile phones GNU Hurd Mobian Nura Plasma Mobile PureOS Ubuntu Touch Redox OS FreeDOS – OS compatible with IBM PC DOS and Microsoft's MS-DOS ReactOS – OS intended to run the same software as Windows, originally designed to simulate Windows NT 4.0, later aiming at Windows 7 compatibility. It has been in the development stage since 1996.
2. System Architecture & Core Working Principles AppleWin DOSBox – DOS programs emulator (including PC games) GNOME Boxes Hercules (emulator) Kernel-based Virtual Machine (KVM) QEMU VirtualBox – hosted hypervisor for x86 virtualization DTrace – dynamic tracing framework for analyzing and troubleshooting running applications and operating systems Memtest86 – stress-tests RAM on x86 machines strace – diagnostic utility for tracing system calls and signals Valgrind – debugging and profiling tool for detecting memory and threading errors Xnee – record and replay tests Acceleo – model-to-text code generator Apache Velocity – Java-based template engine used for code generation Babel – JavaScript transcompiler Bison CodeSynthesis XSD – XML Data Binding compiler for C++ CodeSynthesis XSD/e – validating XML parser/serializer and C++ XML Data Binding generator for mobile and embedded systems Flex lexical analyser – generates lexical analyzers Open Scene Graph – 3D graphics application programming interface OpenSCDP – Open Smart Card Development Platform SableCC – parser generator for Java and .NET SWIG – Simplified Wrapper and Interface Generator for several languages Umple – modeling and programming language with source code generation xmlbeansxx – XML Data Binding code generator for C++ YAKINDU Statechart Tools – Statechart code generator for C++ and Java Apache Flink – stream and batch data processing framework Apache Hadoop – distributed storage and processing framework Apache Mahout – scalable machine learning library Apache Spark – unified analytics engine Dask – parallel computing for analytics in Python ELKI – data analysis algorithms library GNU Octave – numerical computing environment JASP – GUI program for data analytics, data science, and machine learning Jupyter Notebook – interactive computing Keras – neural network library KNIME – data analytics platform Matplotlib – data visualization library MLlib – machine learning library for Apache Spark NumPy – numerical computing library Orange – data mining tool pandas – data manipulation library PyTorch – machine learning and deep learning framework Python R – statistical computing language SageMath – mathematics and data analysis environment SciPy – scientific computing library scikit-learn – Python machine learning library TensorFlow – machine learning framework WEKA – machine learning and data analysis suite 3G Bridge – grid interoperability Advanced Resource Connector – middleware BOINC – volunteer computing HTCondor – high-throughput computing Simple Grid Protocol – grid computing UNICORE – middleware CP2K – atomistic and molecular simulation of solid-state, liquid, molecular, and biological systems Open-source software Open-source license Comparison of file synchronization software § Open-source GNOME Core Applications List of concept- and mind-mapping software § Free and open-source List of formerly proprietary software List of GNU packages List of HDL simulators § Free and open-source simulators List of KDE applications List of open-source hardware projects List of optimization software § Free and open-source software List of public domain projects List of spreadsheet software § Free and open-source software List of Unix commands The Multi-Vulnerability and Token Security Scanner is a comprehensive Python-based utility designed for security analysts, penetration testers, and developers to identify and assess a wide spectrum of vulnerabilities in web applications and authentication tokens. This tool automates the detection of injection vulnerabilities, including SQL Injection (SQLi), NoSQL Injection, GraphQL Injection, Cross-Site Scripting (XSS), Command Injection (CI), LDAP Injection, and XML External Entity (XXE) Injection. It utilizes diverse detection techniques, such as error-based analysis, boolean-based blind testing, and time-based blind testing, to reveal vulnerabilities even in applications that do not display explicit error messages. In addition, the tool features specialized modules for scrutinizing authentication tokens, including JSON Web Tokens (JWT), OAuth 2.0 access tokens, SAML assertions, and OpenID Connect ID tokens. These modules evaluate for common security flaws, such as algorithm weaknesses, signature misconfigurations, key confusion, expiration and issuance time issues, replay vulnerabilities, and more.
The scanner functions by dispatching carefully constructed payloads to target URLs via GET parameters or POST forms and examining the responses for vulnerability indicators. For token analysis, it decodes, validates, and alters tokens to detect potential exploitation vectors. All testing is intended for ethical and authorized use, with a strong emphasis on obtaining explicit permission prior to any assessment to comply with legal and professional standards.
Wide-Ranging Vulnerability Detection : Identifies SQL Injection using error-based, union-select, blind boolean, and time-based methods, supporting various databases like MySQL, PostgreSQL, MSSQL, and Oracle. Extends coverage to NoSQL Injection (error-based and blind time-based), GraphQL Injection (error-based with introspection leakage checks, blind boolean and time-based), XSS (reflected through script alert indicators), Command Injection (time-based via response delays and output-based via echoed unique markers), LDAP Injection (error-based and blind boolean), and XML Injection (XXE with indicators of file disclosure or out-of-band data exfiltration).
Customizable Payloads and Indicators : Permits the loading of custom payloads and error indicators from text files for each vulnerability category (one per line), allowing testers to adapt the tool to specific application behaviors, database types, or newly discovered exploit patterns. This flexibility ensures the scanner can be fine-tuned for targeted assessments or integration into custom security workflows.
Advanced Blind Detection Logic : Offers configurable blind testing modes (boolean, time, or both) for SQL/NoSQL, LDAP (boolean only), and GraphQL, with adjustable delay durations for time-based tests and similarity thresholds for boolean comparisons (using difflib to measure response content differences). This optimization reduces false positives and enhances detection in silent or rate-limited environments.
HTTP Method and Form Handling : Directly tests GET query parameters and automatically detects HTML forms for POST submissions (requiring BeautifulSoup for parsing). Includes support for custom request timeouts to handle slow networks, user-agent strings for evasion or compliance, and verbosity levels for output control (minimal for quick overviews, detailed for in-depth analysis, debug for full traces).
Progress Monitoring and User Feedback : Employs tqdm for visual progress bars during multi-payload tests, aiding in tracking long scans. Verbosity settings allow tailored output, from high-level vulnerability alerts to verbose debugging with request/response details. Ethical Design Principles : Built exclusively for authorized security assessments, with documentation emphasizing legal compliance, permission requirements, and responsible disclosure. The tool avoids any exploitative or destructive actions, focusing solely on detection.
Below is a Mermaid diagram illustrating the high-level architecture of the scanner tool, showing how the web vulnerability scanning components interact with the token testing modules. The diagram depicts the main flows: input processing, vulnerability testing branches, token analysis paths, and output reporting. This diagram represents the tool's modular structure, where web scanning and token testing are separate but share reporting mechanisms. The HTTP engine handles web interactions, while token modules focus on parsing and manipulation.
To set up the scanner, ensure the following prerequisites are met for optimal performance. Install Python 3 : The tool requires Python 3.8 or higher. Download and install from the official Python website (python.org) if not already present. Confirm the version by executing python --version in a terminal. Install Required Libraries : Use pip to install the necessary dependencies. Run the command below in a terminal: Save the Script : Copy the full script code into a file named vuln_scanner.py . On Linux or macOS, make it executable with chmod +x vuln_scanner.py for convenience.
Additional Notes : The tool does not require root privileges or special permissions. For token tests involving remote endpoints (e.g., JWKS, introspection), ensure network connectivity. If using in a virtual environment, activate it before installing libraries. The scanner is invoked via the command line, supporting web scanning on URLs and independent token testing. For web scans, provide a URL with query parameters or forms. For token tests, specify the token and supporting parameters without a URL.
This sends built-in SQLi payloads to the 'id' parameter and checks for error indicators like "sql syntax" or "unexpected end of sql". This enables all vulnerability types, blind modes, with a 10-second delay for time-based tests, 90% similarity threshold for boolean, detailed output, and 20-second timeout.
This uses custom files for SQLi and XSS payloads, error indicators, and a custom User-Agent. This decodes the token, tests none algorithm (generates and submits a none token to the test URL), checks for weak HS secrets if applicable, notes KID risks, and if RS256, performs key confusion by using the public key as an HS secret for verification and testing a modified HS256 token on the URL.
This introspects the token for activity and tests the authorization endpoint for PKCE by requesting a code without code_challenge, reporting if non-PKCE is allowed. This parses the SAML, validates structure/signature/expiration, tests an unsigned version, applies signature wrapping with a malicious duplicate assertion, and checks for replay by double-submitting.
This checks OpenID claims and runs JWT tests, reporting mismatches or expiration issues. This tool is developed and distributed for ethical security research, authorized penetration testing, and educational purposes only. Users are solely responsible for ensuring all activities comply with applicable laws, regulations, and ethical standards. Obtain explicit, documented permission from system owners before scanning any URL or testing tokens. Unauthorized use may infringe on privacy rights, breach contracts, or violate laws like the Computer Fraud and Abuse Act (CFAA) in the United States, the Computer Misuse Act in the United Kingdom, or similar international statutes, potentially resulting in legal consequences.
The tool's creators disclaim all liability for misuse, including any damages, data loss, or legal issues arising from its application. Promote responsible disclosure: If vulnerabilities are found, notify affected parties promptly and allow reasonable time for remediation before public release. Reference resources like the OWASP Cheat Sheet Series or NIST guidelines for best practices in vulnerability testing and token security. By using this tool, you agree to these terms.
3. Software Implementation, Frameworks & Protocols Permission is hereby granted, free of charge, to any person obtaining a copy of this software and associated documentation files (the "Software"), to deal in the Software without restriction, including without limitation the rights to use, copy, modify, merge, publish, distribute, sublicense, and/or sell copies of the Software, and to permit persons to whom the Software is furnished to do so, subject to the following conditions: The above copyright notice and this permission notice shall be included in all copies or substantial portions of the Software.
THE SOFTWARE IS PROVIDED "AS IS", WITHOUT WARRANTY OF ANY KIND, EXPRESS OR IMPLIED, INCLUDING BUT NOT LIMITED TO THE WARRANTIES OF MERCHANTABILITY, FITNESS FOR A PARTICULAR PURPOSE AND NONINFRINGEMENT. IN NO EVENT SHALL THE AUTHORS OR COPYRIGHT HOLDERS BE LIABLE FOR ANY CLAIM, DAMAGES OR OTHER LIABILITY, WHETHER IN AN ACTION OF CONTRACT, TORT OR OTHERWISE, ARISING FROM, OUT OF OR IN CONNECTION WITH THE SOFTWARE OR THE USE OR OTHER DEALINGS IN THE SOFTWARE.
The Advanced SQL Injection Scanner is a sophisticated, Python-based tool crafted for security analysts and penetration testers. It automates the detection of SQL Injection vulnerabilities in web applications by sending varied SQLi payloads to specified URLs and analyzing the responses for signs of injectable parameters. A sophisticated SQL injection detection and exploitation tool designed for comprehensive web application security testing and bug bounty hunting.
This scanner provides automated detection and exploitation of SQL injection vulnerabilities across various database management systems. It incorporates advanced techniques for bypassing modern security controls and Web Application Firewalls (WAFs). This advanced SQL injection scanner provides comprehensive testing capabilities with modern evasion techniques and detailed reporting for professional security assessments.
This tool is designed for authorized security testing only. Users must ensure proper authorization before testing any applications. SQLiScan Pro is an advanced, asynchronous, and highly efficient SQL Injection vulnerability scanner and exploitation tool developed in Python. Designed for security professionals, penetration testers, and developers, it automates the process of detecting various types of SQL Injection flaws in web applications and, where possible, facilitates data extraction.
Leveraging asynchronous programming, sophisticated payload management, and comprehensive detection techniques, SQLiScan Pro provides robust and reliable vulnerability assessment. I Modular Architecture: Easily extendable classes: RequestHandler , PayloadManager , etc. I Advanced SQL Injection vulnerability scanner & exploitation tool built in Python with asynchronous engine, Tor support, WAF bypass, and multi-mode payload injection.
SQL injection remains one of the most critical security vulnerabilities plaguing web applications today. As Python developers and cybersecurity enthusiasts, creating a robust SQL injection scanner is not just an interesting project—it's a crucial skill in the modern security toolbox. This comprehensive guide will walk you through constructing a powerful and flexible SQL injection scanner using Python, incorporating best practices and advanced techniques.
Before diving into the code, it's essential to grasp the severity and prevalence of SQL injection vulnerabilities. According to the OWASP Top 10, injection flaws, particularly SQL injection, are still among the most dangerous web application security risks. A successful SQL injection attack can lead to unauthorized data access, data manipulation, and even complete system compromise.
This would return all user records, effectively bypassing authentication. The implications of such vulnerabilities in real-world applications are severe, emphasizing the need for robust detection tools. To begin our journey in building a SQL injection scanner, we'll need to set up a proper Python environment. This project requires Python 3.x and several key libraries. Here's how to get started: These libraries provide the foundation for web scraping, HTTP requests, and HTML parsing, which are crucial for our scanner's functionality.
Our SQL injection scanner will be built around a modular, object-oriented design. This approach ensures flexibility, maintainability, and extensibility. The core structure will consist of several key components: This foundation sets up our scanner with customizable parameters, session management, and logging capabilities. The first critical step in our scanner is to thoroughly crawl the target website and identify all forms that could potentially be vulnerable to SQL injection. We'll implement a depth-limited crawler to ensure we cover a significant portion of the site without getting stuck in infinite loops: This crawler efficiently navigates the website, respecting the max_depth parameter to prevent excessive crawling while ensuring comprehensive coverage.
Once we've identified the forms, we need to analyze them and prepare payloads for injection. This process involves understanding the structure of each form and crafting appropriate payloads: This payload generator provides a diverse set of SQL injection attempts, covering various database types and injection techniques.
To improve our scanner's accuracy, we'll implement both error-based and time-based SQL injection detection: These methods allow us to detect both immediate error responses and delayed responses indicative of successful time-based SQL injections. To significantly improve the efficiency of our scanner, we'll leverage Python's concurrent.futures module for parallel processing: This implementation allows multiple forms to be scanned simultaneously, significantly reducing the overall scan time for large websites.
To make our scanner more useful in real-world scenarios, we'll implement a detailed reporting system: This report provides a clear overview of all scanned forms, their vulnerabilities, and relevant details, facilitating easy analysis and follow-up actions. It's crucial to emphasize that this SQL injection scanner should only be used on systems you have explicit permission to test.
Unauthorized scanning or exploitation of vulnerabilities is illegal and unethical. Always practice responsible disclosure if you discover vulnerabilities in systems you don't own. We've constructed a robust SQL injection scanner that incorporates advanced techniques such as concurrent scanning, sophisticated payload generation, and multi-faceted vulnerability detection. This tool provides a solid foundation for identifying SQL injection vulnerabilities in web applications.
By understanding and creating tools like this SQL injection scanner, you're not only improving your Python skills but also contributing to a safer digital ecosystem. Remember, the field of cybersecurity is ever-evolving, and staying current with the latest threats and defense mechanisms is crucial. 4. Practical Deployment, Analysis & Case Studies As you use and refine this tool, always prioritize ethical considerations and legal compliance. Your goal should be to improve security, not to exploit vulnerabilities. With great power comes great responsibility, and as skilled developers, it's our duty to use our abilities to protect and strengthen digital infrastructures.
Continue learning, stay curious, and always use your skills responsibly. The world of cybersecurity is vast and ever-changing, offering endless opportunities for growth and innovation. Your journey in creating this SQL injection scanner is just the beginning of what could be a fascinating career in cybersecurity and ethical hacking. Python's object-oriented programming capabilities shine brightest when developers harness the full power of inheritance. At the heart of this lies the ability to call parent class methods effectively. This comprehensive guide will take you on a journey through the intricacies of parent class method calls, exploring techniques, best practices, and real-world applications that will elevate…
Introduction
Two Titans of Programming In the ever-evolving landscape of software development, Python and Java stand as two of the most influential and widely-used programming languages. As a passionate Python enthusiast and experienced developer who has worked extensively with both languages, I'm excited to take you on a comprehensive journey through their similarities, differences, and… In the realm of data analysis and programming, the ability to efficiently handle CSV (Comma Separated Values) files is an indispensable skill for any Python developer. This comprehensive guide will take you on a journey from the fundamentals of CSV manipulation to advanced techniques, empowering you to tackle diverse data processing challenges with confidence and… Introduction In the realm of data manipulation and analysis, Python stands out as a versatile and powerful tool. One common task that often arises is finding the minimum K records from a list of tuples. This operation has wide-ranging applications, from data analysis to algorithm design, and understanding how to implement it efficiently can significantly… As Python continues to dominate the world of data science and scientific computing, mastering advanced matrix manipulation techniques becomes increasingly valuable. One such technique is incremental range initialization – a powerful method for creating matrices with values that increase by a specified range. This article will explore the nuances of this approach, diving deep into… Image processing is a fascinating field that combines art and science, and one of the most fundamental techniques in this domain is the Gaussian blur. As a Python enthusiast and image processing aficionado, I'm excited to take you on a comprehensive journey through the world of Gaussian filters, exploring their mathematical foundations, practical implementations, and… Ready to take Python coding to a new level? Explore our Python Code Generator . The perfect tool to get your code up and running in no time. Start now! SQL injection is a code injection technique that is used to execute SQL queries via the user input data to the vulnerable web application. It is one of the most common and dangerous web hacking techniques.
Introduction Synonym
A successful SQL injection exploit can cause a lot of harmful damage to the database and web application in general. For example, it can read sensitive data such as user passwords from the database, insert, modify and even delete data. In this tutorial, you will learn how to build a simple Python script to detect SQL injection vulnerability in web applications. Since SQL injection is all about user inputs, we will need to extract web forms first. Luckily for us, I've already written a tutorial about extracting and filling forms in Python . We gonna need the below functions: get_all_forms() uses BeautifulSoup library to extract all form tags from HTML and returns them as a Python list, whereas get_form_details() function gets a single form tag object as an argument and parses useful information about the form, such as action (the target URL), method ( GET , POST , etc) and all input field attributes ( type , name and value ).
Introduction to Sociology
Next, we define a function that tells us whether a web page has SQL errors in it, this will be handy when checking for SQL injection vulnerability: Obviously, I can't define errors for all database servers. For more reliable checking, you need to use regular expressions to find error matches. Check this XML file which has many of them (used by the sqlmap utility).
Introduction Tarkov
Now that we have all the tools, let's define the main function that searches for all forms in the web page and tries to place quote and double quote characters in input fields: Before extracting forms and submitting them, the above function checks for the vulnerability in the URL first, as the URL itself may be vulnerable. This is simply done by appending a quote character to the URL.
Introduction to Psychology
We then make the request using requests library and check whether the response content has the errors that we're searching for. After that, we parse the forms and make submissions with quote characters on each form found, here is my run after testing on a known vulnerable web page: As you can see, this was vulnerable in the URL itself, but a fter I tested this on my local vulnerable server ( DVWA ), I got this output: Note: If you want to test the script on local vulnerable web applications like DVWA , you must log in first. I've provided the code for logging to DVWA in the script here , and you'll find it as a commented code in the beginning.
Introduction Paragraph
Note that I've tested this script on many vulnerable websites, and it works just fine. However, if you want a more reliable SQL injection tool, consider using sqlmap , it is written in Python language as well, and it automates the process of detecting as well as exploiting SQL injection flaws. You can extend this code by adding an exploitation feature; this cheat sheet can help you use the right SQL commands. Or you may want to extract all website links and check for vulnerability on all site pages. You can do it as well! In our Ethical Hacking with Python Ebook , we build 35+ hacking tools from scratch using Python. Make sure to check it out here if you're interested! Take the stress out of learning Python. Meet our Python Code Assistant – your new coding buddy. Give it a whirl! Building a Python script that detects XSS vulnerability in web pages using requests and BeautifulSoup.
Introduction to the Devout Life
Learn how you can scrape forms from web pages, as well as filling and submitting them using requests html and beautiful soup in Python. Sniffing and printing HTTP packet information, such as the url and raw data ( passwords, search queries, etc. ) in case the method is POST.
Introduction Meaning
Got a coding query or need some guidance before you comment? Check out this Python Code Assistant for expert advice and handy tips. It's like having a coding tutor right in your fingertips! SQL injection is a common and critical security vulnerability in web applications. It occurs when database queries are constructed directly from user input, allowing attackers to manipulate the system. This article provides a step-by-step guide on creating a simple Python tool to detect SQL injection vulnerabilities, helping developers and security experts identify potential security risks in their applications.
Introduction to Statistics
Why SQL injection is dangerous and how attackers exploit it. How to build a Python tool to detect security vulnerabilities in web applications. The process of creating a vulnerable web application using Flask and SQLite. 5. Performance Evaluation & Extended Technical Observations The goal of this project is to develop a simple Python tool that can detect SQL injection vulnerabilities in web applications. By identifying vulnerable areas, this tool will aid in the secure development of applications and provide a deeper understanding of how SQL injection works.
Introduction to Poetry by Billy Collins
We will first create a simple web application using Flask that is intentionally vulnerable to SQL injection. Then, we’ll develop a Python tool using the requests library to detect these vulnerabilities by sending specific HTTP POST requests and analyzing the server's responses. This basic tool helps detect SQL injection vulnerabilities in web applications. For more comprehensive security testing, advanced tools and methodologies should be used to identify and address these risks effectively. For the full article, visit here .
If your organization or your clients rely on the Visual Composer Website Builder plugin, please take immediate note of… The Domain Name System (DNS) remains the quiet, indispensible backbone of global internet infrastructure. However, when… I Critical Vulnerability Alert: CVE-2026-76461 in Cisco Secure Email Gateway Exploited in the Wild A critical zero-day security flaw identified as CVE-2026-76461 has been uncovered in Cisco Secure Email Gateway… Security teams and platform engineers managing self-managed GitLab infrastructure face an immediate operational risk… Relational databases and web application frameworks often communicate seamlessly, but subtle type mismatches can… In the modern cybersecurity landscape, understanding your organization’s exposed digital footprint is no longer… Security engineers and system administrators managing Proxmox Virtual Environment (PVE) need to be aware of a critical… JFrog Artifactory serves as the central backbone for enterprise software pipelines, managing proprietary binaries… Stepping into the cybersecurity industry often feels like facing a brick wall. You open a job portal, search for… Social engineering attacks are undergoing a major tactical shift. A sophisticated campaign identified by Microsoft… SQL injection is a common and highly risky security vulnerability encountered in web applications. This vulnerability typically arises when database queries are constructed directly from user input, allowing malicious users to manipulate the system. SQL injection can lead to serious consequences such as data leakage, user account compromise, and complete system takeover. In this article, we will walk through the steps to develop a simple tool using Python to detect SQL injection vulnerabilities. This tool will guide developers and security experts in identifying security weaknesses in their applications. If you’ve been curious about SQL Injection Detection with Python, keep reading to learn more.
The aim of this project is to develop a simple Python tool that can detect SQL injection vulnerabilities in web applications. Common security vulnerabilities like SQL injection often result from the unsafe construction of database queries. With this tool, we will identify vulnerable points, enabling a more secure application development process. Additionally, by the end of the project, we will have a deeper understanding of how SQL injection works and how it can be prevented, SQL Injection: Understanding the Threat and Prevention. SQL Injection Detection with Python becomes intuitive with this comprehensive guide.
The first step of the project is to create a web application vulnerable to SQL injection attacks. Then, we will develop a Python tool to test for these vulnerabilities, focusing on SQL Injection Detection with Python. To demonstrate SQL injection attacks and test our detection tool, we will create a simple Flask-based web application. This application will contain a login form that allows users to authenticate using an SQLite database. However, user input will be directly embedded in the SQL query, making the application vulnerable to SQL injection attacks.
The above application creates a simple login form that accepts username and password input. However, since these inputs are directly incorporated into the SQL query, the application is vulnerable to SQL injection attacks. A user can manipulate the SQL query with improperly structured inputs to gain unauthorized access to the database. Now, we will develop a basic Python tool to detect SQL injection vulnerabilities in web applications. This tool will use the requests library to send specific HTTP POST requests and analyze the server’s responses, Using SQLMap: A Comprehensive Guide for SQL Injection Testing .
This tool sends SQL injection test payloads to the target application and analyzes the response. If the response indicates a successful login, an SQL injection vulnerability has been detected. This simple tool can help developers and security experts identify basic SQL injection vulnerabilities in web applications and discover the vulnerable areas. SQL Injection Detection with Python can be efficiently implemented using this approach.
In this article, we developed a simple tool using Python to detect SQL injection vulnerabilities. Identifying and fixing such vulnerabilities in web applications is crucial for ensuring security. The tool presented here provides a basic level of testing. For more comprehensive security testing, advanced security tools and methodologies should be used, and appropriate improvements should be made for each identified security vulnerability. Hence, mastering SQL Injection Detection with Python is essential for any web developer or security professional.
Let’s embark on this journey together, where you will learn to use Python not just as a programming language, but as a powerful weapon in the fight against cyber threats I recently read Mastering Python for Ethical Hacking, and this article aligns perfectly with the concepts covered in the book. It’s great to see practical applications of the techniques discussed Excellent article! The step-by-step approach makes it easy to understand how SQL injection vulnerabilities work and how to detect them using Python. Great work! Mastering Python for Ethical Hacking was a game changer for me and provided me with in-depth knowledge on building various security tools. This article complements the book’s teachings by providing a hands-on approach to detecting SQL injection vulnerabilities, and I would also like to point out that it would be appreciated if you could occasionally quote the book and share it here. My advice for beginners would be to buy Denizhalil’s book and follow the site as it continues.
SQL injection vulnerabilities are one of the OWASP Top 10 security risks for web applications, highlighting their prevalence and the need for secure coding practices. The tool can be enhanced by adding more sophisticated payloads, testing multiple input fields simultaneously, and integrating with a proxy tool like Burp Suite for deeper analysis. Additionally, logging results and exporting them in various formats like JSON or CSV would improve usability.
A custom-built, automated vulnerability scanner written in Python. This tool is designed to detect basic SQL Injection (SQLi) vulnerabilities in web application forms. It was developed as a hands-on cybersecurity portfolio project to demonstrate practical skills in offensive security tool development. This scanner is designed to be used against its companion project, the Secure Blog App , which contains both a vulnerable and a patched version of the code.
A Python tool to automatically detect SQL Injection vulnerabilities. Built as a portfolio project Kazmi, Muhammad Ali Naqi (2019) SQL injection detection and exploitation framework for penetration testing. Doctoral thesis, London Metropolitan University. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/List%20of%20free%20and%20open-source%20software%20packages • https://github.com/exfil0/SQLi-Advanced-Scanner • https://gauravsingh-cybersecurity.github.io/projects/sql-injection-scanner/ • https://github.com/burakcanbalta/SQLiScan-Pro • https://www.bomberbot.com/python/building-a-robust-sql-injection-scanner-in-python/ • https://thepythoncode.com/article/sql-injection-vulnerability-detector-in-python • https://www.linkedin.com/pulse/detecting-sql-injection-vulnerabilities-python-halil-iIbrahim-deniz-fewrf • https://denizhalil.com/2024/10/11/sql-injection-detection-python/ • https://github.com/UdayKumar5313/sql-injection-scanner • https://repository.londonmet.ac.uk/7345/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Automated SQL Injection Scanner And Exploiter Tool Python.
[*] Initializing Burp Suite Spider & Vulnerability Engine for Automated SQL Injection Scanner And Exploiter Tool Python... [✓] Burp Extender / Macro Automation Hook Synced ──────────────────────────────────────────────────────────────────────── [11:42:01.104] AUDIT Crawled dynamic endpoints | Injecting input vectors [11:42:01.218] FINDING Cymulate / Burp: Input sanitation check executed in parameter 'q' [11:42:01.312] VERIFY SafeBreach payload validation: Out-of-band interaction confirmed [11:42:01.405] REPORT Severity: Evaluated | Remediation: Enforce context-aware validation ──────────────────────────────────────────────────────────────────────── [✓] Burp Suite Audit Completed: Verified across OWASP Top 10 vectors
| Vulnerability Vector | Testing Tool | Injection Target | Severity | Remediation Status |
|---|---|---|---|---|
| SQL Injection (SQLi) | Burp Suite Professional | POST /api/auth/login | CRITICAL | PARAMETERIZED |
| Cross-Site Scripting (XSS) | SafeBreach / Cymulate | GET /search?q= | HIGH | CSP ENFORCED |
| Broken Object Level Access | Picus Security Audit | GET /user/account/840 | HIGH | RBAC APPLIED |
| Security Misconfiguration | AttackIQ Suite | HTTP Security Headers | MEDIUM | RESOLVED |