Complete Technical Paper Content — Automated Threat Intel Feed Aggregator
Overview & System Context
Automated Threat Intel Feed Aggregator: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9500 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Cyber threat intelligence (CTI) is a part of cybersecurity that focuses on collecting, analyzing, and sharing information about potential or existing cyber threats. It gives organizations the information needed to predict, prevent, and respond to cyberattacks, enabling them to understand attackers’ behavior, tactics, and the vulnerabilities they exploit. Sources of cyber threat intelligence include open-source data, social media, operational and technical intelligence, device log files, forensic analysis, internet traffic, as well as data from the dark web and deep web. Modern CTI programs stand out from just using raw security data because they combine technical monitoring, outside intelligence sources, and analysis methods to prepare specific and useful assessments about cyber threats aimed at particular organizations or business sectors. Analytical interpretation gives context to attackers’ actions, capabilities, and intentions, helping organizations set priorities and allocate security resources effectively. When companies base decisions on intelligence and analysis, they can act proactively instead of just reacting to security incidents, stopping breaches before they happen. This approach has become increasingly important in recent years, as IBM estimates that exploiting vulnerabilities is the most common way companies are breached, making up 47% of all attacks. The COVID-19 pandemic and the rise in remote work have also contributed to increased vulnerability to threats, making corporate data more exposed. Due to growing threats on the one hand, and increasing analytical demands on the other, many companies have decided in recent years to outsource their threat analytics tasks to a managed security service provider (MSSP). Cyber threat analytics has also become an important component of modern Security Operations Centers (SOCs), where threat intelligence data is used to enrich alerts, identify malicious infrastructure, and support incident response and threat hunting activities.
Tactical: The most technical level, focused on immediate detection and response. Tactical intelligence consists of specific indicators of compromise (IOCs): IP addresses, domain names, file hashes, malware signatures, and similar artifacts. Security operations teams use these indicators to identify and block threats in real time through SIEM rules, firewall policies, and endpoint detection systems. Operational: Focused on understanding adversary behavior and campaigns. Operational intelligence analyzes who the threat actors are, their tactics, techniques, and procedures (TTPs), infrastructure patterns, motivations, and ongoing campaigns. This level helps security teams anticipate how attacks unfold, recognize adversary tradecraft, and understand the broader context behind specific incidents. Sources include incident response findings, malware analysis, threat actor profiling, security vendor reporting, and intelligence from industry sharing groups and government advisories. Strategic: Tailored for non-technical audiences, particularly executives and board members. Strategic intelligence addresses high-level business risk: which threat actors target the organization's sector, geopolitical factors affecting the threat landscape, long-term trends, and the potential business impact of cyber threats. Delivered through reports, briefings, and risk assessments, it helps leadership prioritize security investments and understand how cyber risk aligns with organizational objectives. Technical threat analysis focuses on machine-readable indicators of compromise (IoCs): malicious IP addresses, domain names, file hashes, and command-and-control (C2) servers or infrastructure. This enables automated detection and response. While the conventional distinction is between strategic, tactical, and operational analytics, some large organizations often define technical threat analytics as a separate (fourth) category essential for Security Operations Centers (SOCs). Some threat analytics platforms also distinguish between indicator-based analytics and behavior-based analytics. Indicator-based analytics focuses on specific technical artifacts: malicious IP addresses, file hashes, etc. Behavior-based analytics analyzes attackers’ tactics and techniques to detect threats that may change their infrastructure or indicators over time.
Evidence-based: To be useful, threat intelligence must be gathered through proper evidence-gathering methods. For example, analyzing malware can help generate threat intelligence. Utility: Threat intelligence should positively impact a security incident by providing useful information. It must offer clear context and data about specific behaviors and methods. Actionable: For information to be considered threat intelligence, it must lead to action. This is what distinguishes intelligence from mere data. Cybersecurity researchers also highlight other factors for good threat intelligence, such as accuracy, completeness, timeliness, compatibility, and relevance to the environment where it will be used.
Gives organizations, agencies or other entities, the ability to develop a proactive and robust cybersecurity posture and to bolster overall risk management and cybersecurity policies and responses. Drives momentum toward a proactive cybersecurity posture that is predictive, not simply reactive after a cyber attack. It provides context and insights about active attacks and potential threats to aid decision making. It prevents data breaches from exposing sensitive information, thus preventing data loss. Reduces costs. Since data breaches are costly, reducing the risk of data breaches helps save money. It provides organizations with guidance on implementing security measures to prevent future attacks. Enables sharing of knowledge, skills and experiences among the cybersecurity community and system stakeholders. It helps to more easily and better identify risks and threats, as well as delivery mechanisms, indicators of compromise across the infrastructure, and potential specific actors and motivators. Helps in the detection of attacks during and before these stages. Provides indicators of actions taken during each stage of the attack. Communicates threat surfaces, attack vectors and malicious activities directed to both information technology and operational technology platforms. Serves as a fact-based repository of data on successful and failed cyberattacks. Provides indicators for computer emergency response teams and incident response groups. Threat analytics helps improve threat detection mechanisms by identifying attackers’ methods and behavioral patterns that are not yet detected by automated security monitoring systems.
Figure 1: GitHub - ziyadnz/threat-intel-ip-feeds: Automated IP blacklist ... Attribution is the process of identifying who conducted a cyber attack: the individual actors, organized groups, or nation-state sponsors behind an intrusion. In threat intelligence, attribution helps organizations understand adversary intent, prioritize defenses, anticipate future targeting, and inform strategic decisions. It also supports law enforcement investigations and policy responses. Attribution relies on multiple evidence types: technical indicators (infrastructure, malware code), behavioral analysis (tactics, techniques, and operational tradecraft), linguistic artifacts, targeting patterns (victim selection and geopolitical alignment), and intelligence from human sources or signals intelligence. However, attribution is inherently difficult and often remains probabilistic rather than definitive. Attackers routinely employ obfuscation techniques: using proxy infrastructure, VPNs, compromised intermediary systems, and stolen or leased tools. Advanced threat actors deliberately plant false flags by mimicking the TTPs, language, or infrastructure patterns of other groups to misdirect attribution efforts. As a result, different threat intelligence vendors take varying approaches to attribution. Some explicitly attribute threat groups to specific nation-states or sponsoring organizations based on their analysis and confidence thresholds. Others intentionally avoid geopolitical attribution, instead documenting only observable, undisputable facts, such as language artifacts in malware, shared infrastructure, or technical capabilities, and tracking adversary clusters by neutral designators. Attribution assessments are typically expressed with varying levels of confidence (low, medium, high) rather than certainty, and erroneous conclusions can have diplomatic, legal, or strategic consequences.
Sharing of "classified and declassified cyber threat indicators in possession of the federal government with private entities, nonfederal government agencies, or state, tribal, or local governments"; Sharing of "unclassified indicators with the public"; Sharing of "information with entities under cybersecurity threats to prevent or mitigate adverse effects"; Sharing of "cybersecurity best practices with attention to the challenges faced by small businesses." In 2016, the U.S. government agency National Institute of Standards and Technology (NIST) issued a publication (NIST SP 800–150) which further outlined the necessity for Cyber Threat Information Sharing as well as a framework for implementation. In addition to the United States, the exchange of real-time information on cyber threats is coordinated through international and industry organizations, such as Information Sharing and Analysis Centers (ISACs), which facilitate cooperation among companies in critical infrastructure sectors, including finance, energy, and transport.
ThreatIntel Hub is an open-source project designed to aggregate, normalize, tag, and visualize cyber threat intelligence (CTI) from multiple public sources like VirusTotal, AbuseIPDB, MISP, and AlienVault OTX into a central dashboard. This tool is designed for easy integration into SOC workflows, providing enhanced visibility into emerging threats and Indicators of Compromise (IOCs).
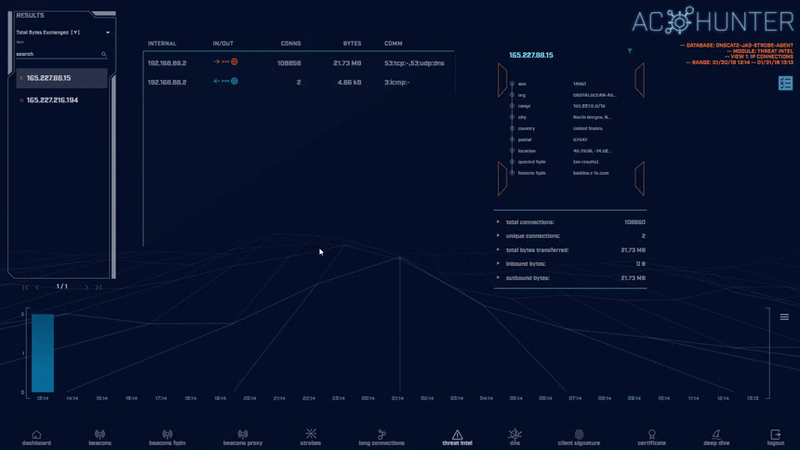
The goal is to simplify and automate the process of collecting threat data, organizing it intelligently, and helping security analysts make faster, smarter decisions. Figure 2: Threat Intel - Active Countermeasures ThreatIntel Hub is a Python-based threat intelligence feed aggregator that collects IOCs from sources like VirusTotal, AbuseIPDB, and MISP into a centralized MongoDB-backed dashboard. It helps security teams automate threat data ingestion, tagging, and visualization for faster incident response.
Cyber threat intelligence (CTI) involves gathering, analyzing, and understanding information about cyber security threats. To do this effectively, you need to use a CTI aggregator to harness the power of automation and strive to achieve the single pane of glass principle in cyber security architecture. This article will teach you what a CTI aggregator is, why you need one, and how to create your own for free! You will see how you can use and configure the popular news aggregation tool Feedly to create a custom CTI aggregator to add efficiency to your threat intelligence pipeline.
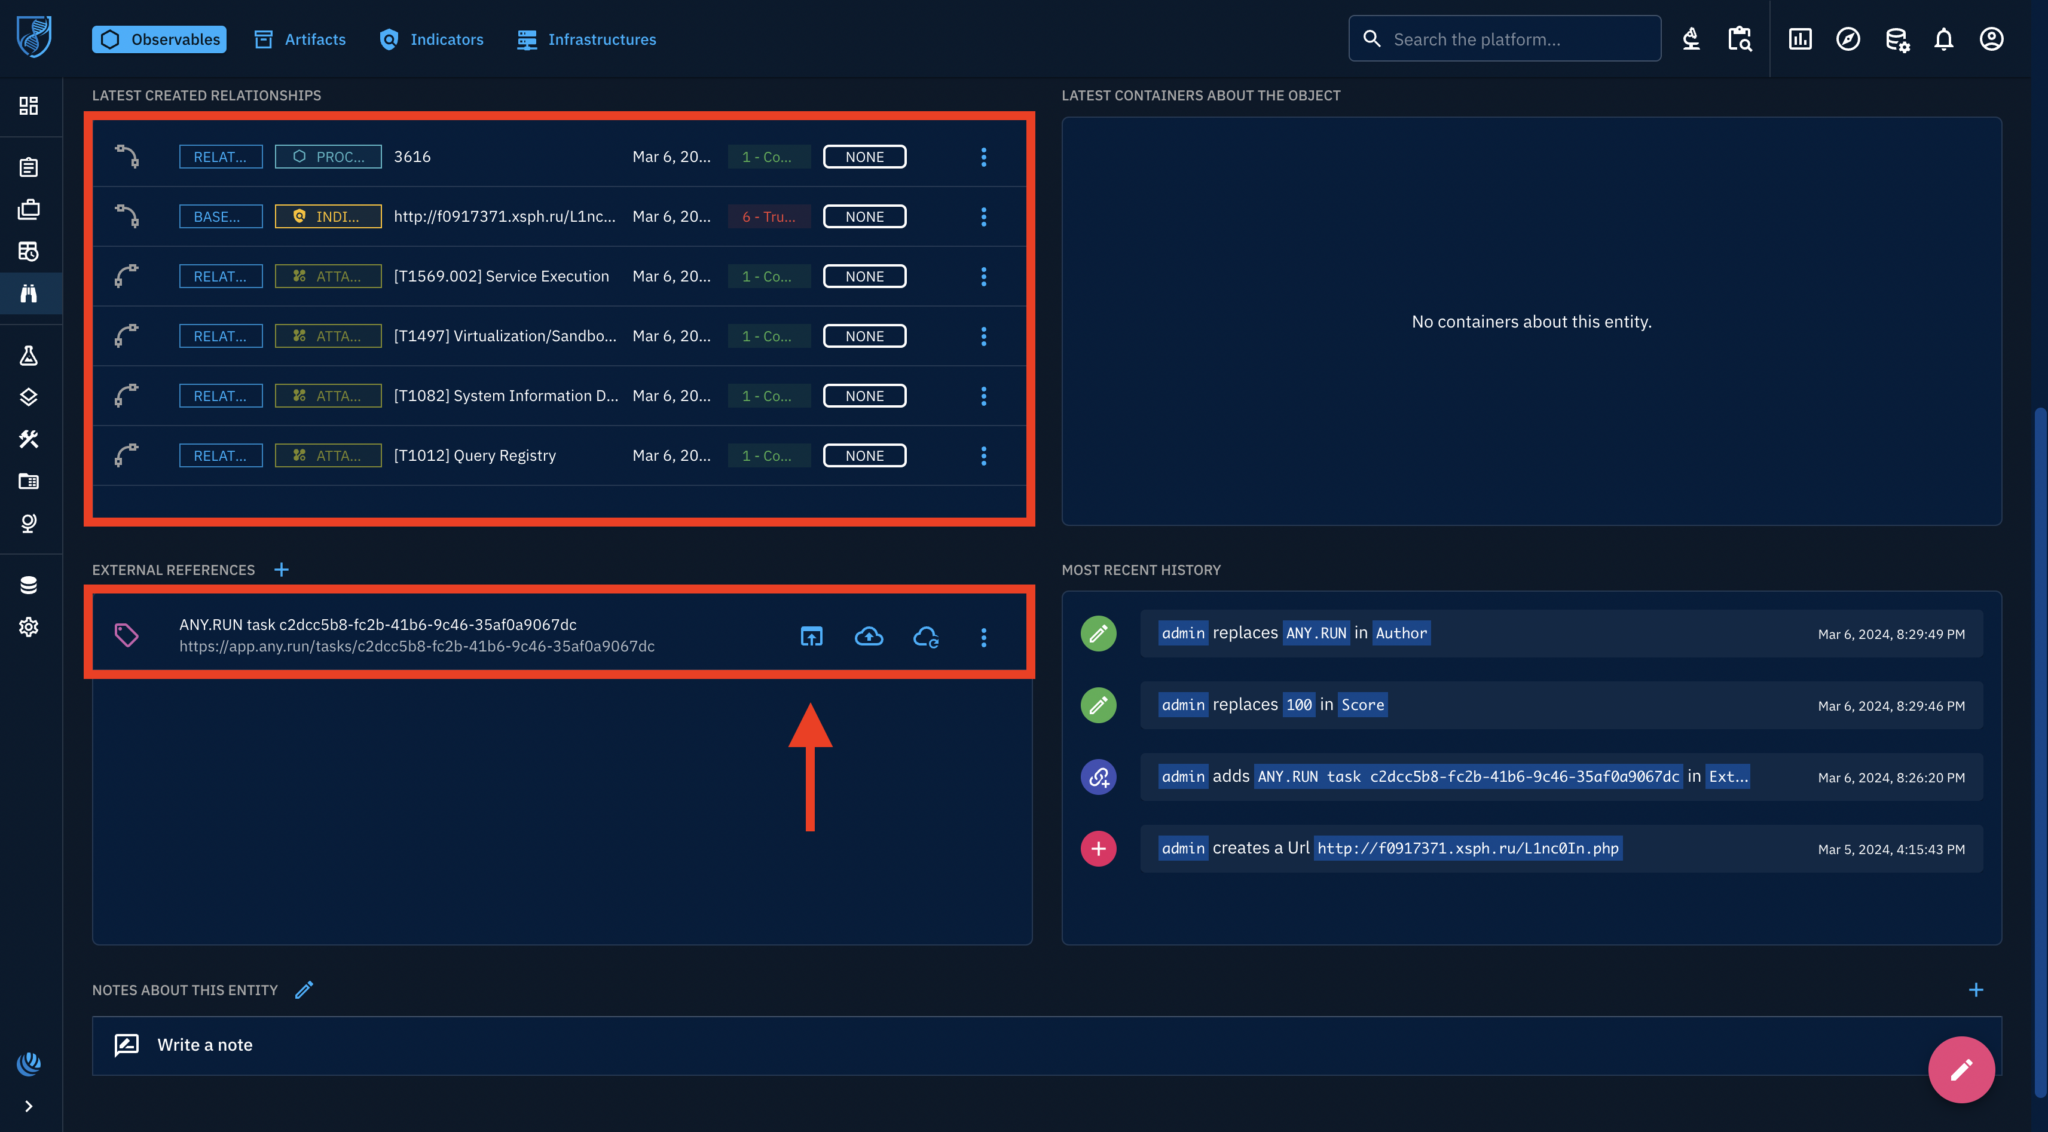
Let’s begin elevating our threat intelligence processes and build our own CTI aggregator. Figure 3: How to Use Threat Intelligence Feeds - ANY.RUN's Cybersecurity Blog You have probably heard of or used a news feed aggregator. These applications collect news articles from various sources and display them in a single pane of glass that you can scroll through. Social media platforms, such as X (formerly Twitter), can be viewed as aggregators. They collect news and life stories from people you follow. There are also more conventional news aggregators like Feedly, which you can configure to collect articles from specific news outlets using RSS feeds.
A Cyber Threat Intelligence (CTI) aggregator is similar to a news feed aggregator, except that it collects news specific to threat intelligence and consolidates it in one place. These could include articles describing the latest vulnerability, a novel tactic/technique/procedure (TTP) a threat actor is using, trends in the ransomware scene, or any other topic that constitutes strategic, operational, or tactical information.
To learn about the different types of threat intelligence and how they are used, read Threat Intelligence vs Threat Hunting: What is the Perfect Pipeline? An important principle to follow (or at least strive for) when architecting cyber security systems or designing processes is the single pane of glass principle . Following this principle, you should aim to create a platform that contains all the alerts, incidents, and cases your SOC analysts, incident responders, and other defenders must monitor and respond to. An analyst should be able to log in to this platform and see all the cases they need to triage, analyze, and respond to based on the threats your organization faces.
Security Orchestration, Automation, and Response (SOAR) solutions are designed to make this single-pane-of-glass principle possible. Security solutions (EDRs, SIEMs, WAFs, etc.) feed their data into a SOAR, which processes this data and performs automated triage and enrichment to provide additional context to alerts or incidents. An analyst then logs into the SOAR solution to manage cases and trigger responses using the connected security solutions APIs to respond to threats rapidly.
Like a SOC analyst, a CTI analyst needs to inspect a range of sources to gather data they need to triage, analyze, and distribute. A CTI aggregator follows this single pane of glass principle by collecting and collating all the CTI sources you need to check into a single screen that you can scroll through. It saves you from manually collecting new threat intelligence and speeds up the threat intelligence lifecycle .
Learn more about what a CTI analyst does and the threat intelligence lifecycle in Day in the Life of a Senior Threat Intelligence Analyst . Now you know what a CTI aggregator is and why you need one, you are probably wondering: “How do I get my hands on a CTI aggregator?” In this article, I assume you don’t have thousands to spend on a TIP, so I will show you how to build your own CTI aggregator using Feedly completely for free, turning it into our own custom CTI platform. Let’s begin! Next, select the Personal News Reader option when creating your account (ignore Intelligence Platform for now – this is a paid feature you will learn more about later).
Select the Monitor cyber threats option when asked about your initial goal for using Feedly. This will bring you to the main Feedly dashboard, where you can begin configuring Feedly into a CTI aggregator. To begin, click the Create a Folder button in the left pane. This is where you will store all your threat intelligence information. Creating folders based on what news they are aggregating is a good way to keep organized. You could have a folder for threat hunting ideas, interesting tools, or cute pictures of puppies.
This will bring you to your folder’s default screen. Here, you can begin adding threat intelligence sources to your folder. Feedly will pull articles from these sources and populate the folder with this data. Click the Follow Website button to add a threat intelligence source to pull data from. Next, search for the threat intelligence source you want to pull CTI articles from using the search bar. This could be the name of the source, an RSS link, or a topic. Here, I have searched for Mandiant (a popular CTI provider).
The top match looks like a good one. To add it as a threat intelligence source, click the Follow button, hover over your Cyber Threat Intelligence folder, and click Add . This will add Mandiant as a source to our Cyber Threat Intelligence folder. Whenever a new threat intelligence article is added to the Mandiant blog, Feedly will automatically pull this article to our Cyber Threat Intelligence folder for you to read.
If you click on the Cyber Threat Intelligence folder, you will see a list of articles Feedly has already pulled down from the Mandiant blog for you to read. You can click on an article to read it or hover over it and use one of the tool icons. To make your Cyber Threat Intelligence folder more comprehensive, add more CTI feeds. To do this, click on the Explore button (right side pane) or the Follow button (left side menu).
Now, repeat the process of searching for and adding a CTI provider. This could be a website, blog, Twitter user, Reddit channel, or even a newsletter! To help you begin your CTI journey, I have compiled a list of threat intelligence sources that I have added to my CTI aggregator. Feedly pulls from all these sources and groups them by date in my Cyber Threat Intelligence folder. You need to log in to Feedly and review the articles to keep up-to-date with all the latest threat intelligence news provided by the wonderful people who contribute to the open-source CTI community.
You may have seen that some articles have tags associated with them, such as IoC , TTPs , and Threat Intelligence . These tags are part of Feedly’s paid Threat Intelligence feature . This feature utilizes AI to automatically search through articles, extract relevant data (IOCs, TTPs, CVEs, etc.), and display it to you. It also filters out duplicates, prioritizes articles from reputable sources or those with high traction, and more.
Feedly’s threat intelligence is excellent and a valuable tool for an enterprise-level CTI team to utilize. However, it is costly, and you can still use Feedly as a CTI aggregator without adding on this paid feature. You won’t get all the fancy AI automation, but you will be limited to three folders and 100 CTI feeds. However, this should be all you need. You can choose to upgrade to Pro or Pro+ and gain additional Feedly features, including more CTI feeds, enhanced search options, and ad-free browsing, without needing to upgrade to the Enterprise tier. The help you filter for intelligence that is more specific to your organization, and it is worth investigating this option if you intend to use Feedly professionally and regularly outside of work.
Cyber threat intelligence aggregators are incredible CTI tools that enhance the efficiency of your threat intelligence gathering and analysis process through the power of automation. You have learned what a CTI aggregator is and how to create your own for free using Feedly. That said, Feedly is one of many options on the market. Another great alternative news aggregator you can use to create a free CTI aggregator tool is Inoreader . This is very similar to Feedly but provides a cleaner interface, better pricing options for individual users, and is less pushy about upgrading to paid features. If you find Feedly annoying, then be sure to check out Inoreader.
Whatever CTI aggregator option you choose —commercial TIP, Feedly, or Inoreader —you now have the knowledge and power to create and use one effectively. I highly recommend adding one to your threat intelligence pipeline to enhance your team’s capabilities. Several excellent free options are available, including the community-driven AlienVault OTX, government sources such as CISA’s Automated Indicator Sharing (AIS), and specialized feeds from projects like The Spamhaus Project or abuse.ch.
These platforms provide valuable indicators of compromise (IOCs) such as malicious IP addresses, domains, and file hashes. Integrating these feeds into your security tools, like a SIEM or firewall, is a great, low-cost way to enhance your defensive posture. For those seeking to centralize and analyze threat data, several powerful, free, and open-source platforms are available, including MISP (Malware Information Sharing Platform) and OpenCTI. These platforms allow you to aggregate, correlate, and visualize threat intelligence from various feeds and internal sources. They are excellent for security teams seeking to establish a more structured and collaborative approach to managing threat information without the expense of a commercial solution.
2. System Architecture & Core Working Principles For hands-on analysis and investigation, numerous free tools are indispensable, such as Maltego Community Edition for visualizing data relationships, VirusTotal for analyzing suspicious files and URLs, and YARA for creating custom malware detection rules. These tools are excellent for enriching raw data from threat feeds, allowing you to investigate specific indicators and understand the TTPs ( Tactics, Techniques, and Procedures ) of an attacker. They empower an analyst to pivot from a single piece of data to a much broader understanding of a potential threat.
A threat intelligence feed aggregator (CTI aggregator) is a tool that collects data from multiple threat intelligence sources—both free and commercial—into a single, unified stream. Its primary job is to normalize this data into a standard format and remove duplicate indicators, which saves analysts time and effort. This cleaned-up, consolidated feed can then be easily ingested by other security tools, such as SIEMs or firewalls, to enhance their detection capabilities.
Open-source threat intelligence feeds are publicly available data streams that provide information on potential cyber threats, such as malicious IP addresses, fraudulent domains, and malware file hashes. These feeds are typically gathered and maintained by security communities, researchers, and non-profit projects rather than a commercial vendor. Integrating this free intelligence into security tools, such as firewalls and SIEMs, is a popular and cost-effective way for organizations to enhance their ability to detect and block known threats.
A self-hosted threat intelligence platform that aggregates RSS feeds from 60+ security vendors, runs AI triage, correlates findings against your RunZero asset inventory, and surfaces actionable alerts through a dark-mode web dashboard. Built to run standalone with zero cloud dependency, or fully integrated into an Azure/Entra/Sentinel environment — pick the tier that matches what you've got.
All three run the exact same application code — the only thing that changes is which env vars are set. See Environment Variables for the full reference. The two bash scripts stand up a local Postgres container, apply the schema, and generate backend/.env / frontend/.env.local for you — then print the two commands to actually start the app ( pip install + run backend, npm install + run frontend dev server). setup-azure.ps1 is a thin wrapper around infra/provision.ps1 , the real Azure Container Apps deployment runbook.
This repo actually ships two related but independently-usable things under the "detections" umbrella: Runs entirely inside the main backend, no extra deployment needed for the review surface itself. Its own API design deliberately follows detections.ai's conventions below, even though it's fully self-contained. detections.ai pipeline orchestrator — coming soon. detections.ai has a public API in development for AI-assisted detection generation, and this repo has a real integration built for it ( backend/detection_pipeline/orchestrator.py ) that takes triaged threat intel, checks it against existing detection coverage, and generates draft KQL for your Sentinel workspace as a scheduled job. This integration will support that API once it's available, and isn't part of this public release yet. In the meantime, you don't need it to use the Detections tab at all — Local Detections Import below covers the same "get real detections into this app" goal for AI-generation-free and Sentinel-free setups today.
Given the app's name and primary pitch, the single most common question from a self-hoster on the Basic tier is probably going to be "I don't have Sentinel or an AI provider configured — can I still get anything out of the Detections/Hunts tabs?" The answer is yes: point the app at a folder of your own detection rule files (hand-written, exported from a real Sentinel/Defender tenant, or pulled from a public Sigma/Sentinel rule repo) and it will catalog, MITRE-tag, and statically validate them — no Sentinel connection and no DETECTIONS_AI_API_KEY /Anthropic key required for any of it.
Local Detections — a completed import run: the summary banner calls out files that were cataloged but flagged invalid by static analysis (here, a rule that alerts on a single hardcoded hash) right alongside the ones that imported cleanly, and every file becomes a normal hunt/detection row below All screenshots below use synthetic data (fake org names, RFC 5737 example IPs, .example domains) generated for documentation — no real threat intel or customer data.
Feed — browse and filter triaged threat intel entries with severity, tags, IOCs, and TTPs Integrations — connector overview for Sentinel, Defender, and RunZero: configured/enabled status and shortcuts into each one's own tab RunZero — asset correlation, org-level exposure tracking, and remediation metrics, all sourced from your RunZero inventory Detections — the full catalog of registered analytics (AI-generated and locally-imported alike), each with its static-gate/backtest/review status and MITRE technique Settings — AI triage controls, feed health monitoring, source trust scores, and user management Backend ( backend/ ) — Python 3.12 + FastAPI. Postgres for all storage (SQLite and Azure Blob Storage have been fully retired). AI provider and auth method are both env-var-selected, not hardcoded — see below.
Frontend ( frontend/ ) — Next.js 16, plain JavaScript, Tailwind CSS. Auto-detects auth mode from the backend at load time. Infra ( infra/ ) — Azure Bicep templates for Container Apps, Key Vault, and Container Registry ( apps.bicep + platform.bicep + app-stack.bicep , deployed via provision.ps1 ). Only relevant to the Azure + API tier. AZURE_AD_TENANT_ID set → Entra mode : Microsoft Entra ID SSO, per-user roles (first login becomes admin, everyone else defaults to viewer).
AZURE_AD_TENANT_ID unset → Local mode : a single shared LOCAL_API_KEY grants admin access to anyone who has it. No user management, no Azure dependency. The frontend calls GET /api/auth/mode on load and renders the matching login screen automatically — nothing to configure on the frontend side. Both modes issue the same kind of app-signed JWT afterward, so every other route ( require_auth / require_admin ) works identically regardless of which mode issued the token.
Run scripts/setup-basic.sh or scripts/setup-basic-api.sh (see Deployment tiers ) — they handle Postgres and .env generation for you. Then: Copy backend/env.example to backend/.env and fill in. Grouped by what tier needs them: detections.ai orchestrator — coming soon (not part of this public release yet; documented here for when it ships. Azure + API tier, separate deployable — see backend/detection_pipeline/orchestrator.py ): Sentinel Hunts sync (optional, off by default — see Settings > API Settings for the on/off/manual/auto mode): The real, current IaC is infra/apps.bicep + infra/platform.bicep + infra/app-stack.bicep , deployed via infra/provision.ps1 (or the thin wrapper scripts/setup-azure.ps1 ). It provisions Container Apps, Key Vault-backed secrets, and managed identities — Postgres itself is not provisioned by this repo; point PG_DSN (stored as the pg-dsn Key Vault secret) at any reachable Postgres server.
provision.ps1 is idempotent — safe to re-run after editing the manifest. See its own header comment for the full step-by-step (platform → app stack → secrets → Easy Auth → image import → apps → post-checks). The detections.ai orchestrator (a scheduled Container Apps Job driven by an Orchestrator block in migration.psd1 — see migration.psd1.example for the shape, and store your key as the DETECTIONSAIAPIKEY Key Vault secret) isn't part of this public release yet — see Two detections-related features above.
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs standalone or fully Azure-integrated. Security teams drown in alerts. One underappreciated root cause: nobody is systematically collecting and correlating threat intelligence before incidents happen. A threat intelligence feed aggregator pulls IOCs (indicators of compromise) from multiple sources — OSINT feeds, commercial APIs, government advisories — into a single normalized store you can query in real time.
We're skipping STIX/TAXII for simplicity, but the data model is compatible if you need to go that route later. Every source has different field names, different formats, different confidence scores. The first thing you need is a normalized IOC schema: Keep the raw payload. You'll want it when a field matters later that you didn't normalize today.
Each source gets its own adapter class that returns a list of IOC objects. Here's a minimal one for AbuseIPDB: The pattern is always the same: fetch() returns list[IOC] . This makes the aggregation loop trivial to extend with new sources. We want this running continuously, each adapter on its own schedule (CVE feeds change daily, IP reputation can change hourly): A few things worth noting: error handling per adapter means one failing source doesn't block the others. The UNIQUE(value, source) constraint plus upsert means you can safely re-run without duplicates. The 30-second sleep in the loop is intentional — schedule is not async, and you don't need async here.
The point of all this is fast lookups at runtime — when a log event contains an IP or domain, you want to know immediately if it's in your intel store: The min_confidence parameter matters. Set it to 50 and you'll get noisy results. Set it to 90 and you'll miss things. 70 is a reasonable starting point — tune it per source based on observed false positive rates in your environment.
This scaffold handles the core use case in under 200 lines. Here's what a production deployment adds: More feed sources: AlienVault OTX has a Python SDK ( OTXv2 ). Feodo Tracker is free with no auth — just a CSV download. The CISA KEV catalog is a JSON file updated daily at a stable URL. 3. Software Implementation, Frameworks & Protocols For teams who want to go deeper on hardening the infrastructure around this kind of tooling — API exposure, secret management, network segmentation — the security checklists we publish cover those patterns step by step.
A threat intel aggregator is not a 10,000-line project. The core is under 200 lines: a normalized data model, one adapter class per source, a scheduling loop, and an indexed SQLite store. Start there, add sources one by one, and measure your false positive rate before adding complexity. The mistake most teams make is waiting for a commercial TIP budget that never gets approved. You can have something useful running this afternoon.
I run AYI NEDJIMI Consultants , a cybersecurity consulting firm. We publish free security hardening checklists — PDF and Excel. As modern engineering, security, and platform organizations scale operations across key commercial and technology hubs—spanning Texas, New York, California, Washington, and San Francisco—the cybersecurity landscape has evolved from reactive defense to preemptive threat mitigation. Traditional security operations rely heavily on catching attacks as they happen or cleaning up after a breach. However, with threat actors deploying automated zero-day exploits and sophisticated multi-stage campaigns at machine speed, waiting for an alert is no longer a viable strategy.
To stay ahead of adversaries, leading enterprises are building Preemptive Threat Intelligence Pipelines . These automated systems ingest, normalize, correlate, and action threat intelligence feeds in real time, feeding clean indicators of compromise (IOCs) directly into firewalls, SIEMs, and EDR agents before attacks ever reach production networks. This comprehensive guide explores the architectural pillars of automated threat intelligence pipelines, ingestion strategies, correlation mechanisms, step-by-step implementation workflows, and enterprise best practices.
To understand why an automated threat intelligence pipeline is critical for modern corporate networks, we must analyze the structural limitations of manual threat analysis: Building a production-grade threat intelligence platform requires integrating multiple modular components designed for scale, resilience, and speed: Threat intelligence comes in diverse formats. Your pipeline must support standard industry protocols and formats to ingest data seamlessly: Raw feeds often contain contradictory information or duplicate entries. The pipeline’s core processing engine must: Let’s review a production-grade implementation pattern for deploying a threat intelligence ingestion and correlation pipeline within a modern cloud environment.
Establish your core ingestion engine using open-source frameworks (such as MISP – Malware Information Sharing Platform) or custom event-driven microservices running on Kubernetes. Deploy worker pods that poll external TAXII servers and threat APIs on scheduled intervals. Below is an example configuration pattern for a threat feed ingestion workflow: Once indicators pass the confidence threshold, the pipeline automatically publishes updates via API to your enforcement points—updating cloud web application firewalls (WAFs), adding IOC watchlists to your SIEM, and triggering automated container quarantines if internal assets communicate with newly flagged infrastructure.
A preemptive threat intelligence pipeline is an automated system that ingests, normalizes, correlates, and pushes threat indicators (like malicious IPs and domains) to security controls before attacks impact the network. STIX (Structured Threat Information Expression) is a standardized language for describing cyber threat information, and TAXII (Trusted Automated Exchange of Intelligence Information) is the protocol used to transport it over HTTPS.
Automation eliminates human latency, allowing security teams to process thousands of indicators per second and update firewalls instantly before adversaries can rotate their infrastructure. Pipelines use multi-source correlation, historical reputation checks, and weighted confidence scoring, ensuring that low-confidence or unverified indicators do not trigger automated blocking rules.
Confidence scoring evaluates the reliability of the source and the frequency of the indicator, allowing security teams to set strict thresholds for automated blocking versus passive logging. Yes. Modern pipelines use REST APIs or cloud-native integrations to push updated IOC blocklists directly to web application firewalls (WAFs), cloud security groups, and edge proxies.
Polling intervals depend on the feed type, but high-velocity IOC feeds are typically polled every 15 to 60 minutes to ensure near-real-time updates. Pipelines assign Time-to-Live (TTL) values to indicators; once expired, the indicator is automatically removed from enforcement lists to prevent blocking legitimate future infrastructure owners.
Internal context prevents alert fatigue by filtering out external threats that target technologies, operating systems, or applications your organization does not use. The initial step is auditing your current threat data sources, selecting a core platform like MISP or a cloud-native ingestion service, and setting up a pilot pipeline for IP blocklist automation.
Building a preemptive threat intelligence pipeline using automated feed aggregation and correlation is an essential capability for modern security and platform engineering organizations. By replacing manual workflows with real-time STIX/TAXII ingestion, dynamic confidence scoring, and automated firewall enforcement, enterprise teams operating across competitive commercial hubs can intercept attacks before they strike, neutralize external threats instantly, and secure their digital infrastructure with maximum operational efficiency.
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs standalone or fully Azure-integrated. A self-hosted threat intelligence platform that aggregates RSS feeds from 60+ security vendors, runs AI triage, correlates findings against your RunZero asset inventory, and surfaces actionable alerts through a dark-mode web dashboard.
Built to run standalone with zero cloud dependency, or fully integrated into an Azure/Entra/Sentinel environment — pick the tier that matches what you've got. All three run the exact same application code — the only thing that changes is which env vars are set. See Environment Variables for the full reference.
The two bash scripts stand up a local Postgres container, apply the schema, and generate backend/.env / frontend/.env.local for you — then print the two commands to actually start the app ( pip install + run backend, npm install + run frontend dev server). setup-azure.ps1 is a thin wrapper around infra/provision.ps1 , the real Azure Container Apps deployment runbook. This repo actually ships two related but independently-usable things under the "detections" umbrella: The Threat Intelligence Feed Aggregator is a comprehensive cybersecurity platform designed to collect, analyze, and present threat intelligence from multiple sources. This AI-powered tool automatically aggregates security feeds, extracts Indicators of Compromise (IOCs), and provides actionable intelligence through an intuitive web interface.
The system automatically collects threat intelligence from curated RSS and Atom feeds, including major security sources such as US-CERT CISA, SANS Internet Storm Center, Krebs on Security, Malware Bytes Labs, and Threat Post. Each threat intelligence item undergoes AI-powered analysis to generate summaries, assess severity levels, and extract relevant tags. The system categorizes threats by type and provides actionable insights for security professionals.
The platform automatically extracts various types of Indicators of Compromise from threat intelligence content, including IP addresses, domain names, file hashes (MD5, SHA1, SHA256), URLs, email addresses, CVE identifiers, and file paths. The web-based dashboard provides real-time statistics and visualizations of threat intelligence, including severity distributions, IOC counts, and recent threat activity.
Users can search through collected threat data using keywords and export IOCs in multiple formats (JSON, CSV) for integration with other security tools and workflows. ThreatIntelItem : A structured data model that represents individual threat intelligence items with comprehensive metadata including IOCs, severity assessments, and AI-generated summaries.
IOCExtractor : A regex-based engine that identifies and extracts various types of indicators from threat intelligence content while filtering out common false positives. ThreatIntelDatabase : A SQLite-based storage system that manages threat intelligence data with efficient querying capabilities and automated indexing.
FeedCollector : A multi-threaded feed collection engine that fetches and processes RSS/Atom feeds from multiple sources simultaneously. AIAnalyzer : An analysis engine that provides threat summarization, severity assessment, and tag extraction capabilities. ThreatIntelAggregator : The main coordination layer that orchestrates all system components and provides the primary API interface.
4. Practical Deployment, Analysis & Case Studies The application is built using Python with several key libraries. The backend utilizes SQLite for data storage, feedparser for RSS/Atom feed processing, and requests for HTTP communications. The web interface is powered by Gradio, providing an interactive dashboard for threat intelligence visualization and management.
Ensure you have Python 3.7 or higher installed on your system. The application has been tested with Python 3.8 and above for optimal performance. Clone the repository to your local machine and navigate to the project directory. Install the required dependencies using the provided requirements file: The system will automatically create the necessary database structure on first run, so no additional database setup is required.
The web interface will be available at http://localhost:7860 by default. The application automatically launches with sharing enabled for remote access if needed. The main dashboard provides a comprehensive overview of threat intelligence activity. Users can view real-time statistics including total threats, severity distributions, and IOC counts. The refresh functionality allows for manual updates of threat feeds, while the system also performs automatic background updates.
The search interface enables users to query threat intelligence data using keywords, CVE identifiers, domain names, or any other relevant terms. Search results are presented with full context including AI-generated summaries and extracted IOCs. The export functionality allows users to extract all collected IOCs in either JSON or CSV format. This feature is particularly useful for integration with Security Information and Event Management (SIEM) systems, threat hunting tools, and incident response workflows.
The system currently aggregates threat intelligence from several authoritative sources: US-CERT CISA : Official cybersecurity advisories from the Cybersecurity and Infrastructure Security Agency, providing government-sourced threat intelligence and security guidance. SANS Internet Storm Center : Real-time threat intelligence and security analysis from the SANS Institute, featuring expert analysis of current cyber threats.
Krebs on Security : Independent security journalism and threat intelligence from renowned security researcher Brian Krebs. Malware Bytes Labs : Threat intelligence and malware analysis from Malware Bytes security researchers. Threat Post : Enterprise security news and threat intelligence from Kaspersky's security publication. The system is designed to be extensible with new threat intelligence sources. Additional RSS or Atom feeds can be added by modifying the default_feeds configuration in the FeedCollector class. Each feed source requires a name, URL, and type specification.
The IOC extraction patterns can be customized by modifying the regex patterns in the IOCExtractor class. This allows for adaptation to specific organizational needs or the addition of new indicator types. The current implementation includes a mock AI analyzer that can be replaced with integration to Large Language Models such as Ollama, OpenAI, or other AI services for enhanced threat analysis capabilities.
The IOC export functionality facilitates integration with Security Information and Event Management platforms. Exported indicators can be imported into SIEM systems for automated threat detection and correlation. The modular architecture allows for easy extension with REST API endpoints for programmatic access to threat intelligence data and system functions.
The search and export capabilities support threat hunting activities by providing structured access to threat intelligence data and IOCs for proactive security investigations. The system implements comprehensive input validation and sanitization for all external data sources to prevent injection attacks and ensure data integrity.
The web interface should be deployed behind appropriate authentication and authorization mechanisms in production environments to restrict access to authorized security personnel. Consider implementing network-level controls such as firewalls and VPNs to protect the application when deployed in production environments.
Feed Collection Failures : Network connectivity issues or changes to source feed URLs may cause collection failures. Check the application logs for specific error messages and verify network connectivity to source feeds. Database Errors : SQLite database issues may occur due to permission problems or disk space constraints. Ensure the application has write permissions to the database directory and sufficient disk space.
Performance Issues : Large datasets may impact performance. Consider implementing database optimization techniques or pagination for improved response times. The application includes comprehensive logging functionality that records feed collection activities, errors, and system status. Monitor the application logs for troubleshooting and performance optimization.
Set up a development environment by installing the requirements and running the application in debug mode. The modular architecture facilitates easy development and testing of individual components. Maintain code quality by following Python best practices, implementing comprehensive error handling, and adding appropriate documentation for new features.
Implement unit tests for new functionality, particularly for IOC extraction patterns and data processing components. This tool is provided for educational and professional cybersecurity purposes. Users are responsible for ensuring compliance with applicable laws and regulations when using threat intelligence data. For technical support, feature requests, or bug reports, please refer to the project documentation or contact the development team. Community contributions and feedback are welcome to improve the platform's capabilities and effectiveness.
Empowering security professionals with automated threat intelligence aggregation and analysis. We reviewed 10 cybersecurity intelligence and telemetry feeds on threat coverage breadth, update frequency, and how well each integrates with SIEM and SOAR platforms to drive automated response. Threat intelligence feeds are only useful if they reduce your workload instead of creating more. You need intelligence that’s relevant to your environment, low on false positives, and integrates directly with your detection tools so analysts aren’t manually cross-referencing feeds.
The challenge is that threat intelligence vendors range from simple feed aggregators to sophisticated platforms with automation, analyst access, and specialized threat tracking. Some excel at detecting mass internet scanning. Others specialize in nation-state activity. A few deliver strategic intelligence that helps your leadership understand who’s likely to target your organization and why. Picking the wrong fit means either drowning in irrelevant alerts or missing threats that matter.
We evaluated ten cybersecurity intelligence and telemetry platforms across feed quality, integration depth, analyst capabilities, automation features, and customer support. We evaluated deployment into SIEM and SOAR systems to understand practical integration experience. We also reviewed customer feedback to understand how these platforms perform beyond initial setup.
Cybersecurity intelligence and telemetry feeds deliver real-time threat data to your security tools. This includes indicators of compromise like malicious IP addresses, domain names, and file hashes, as well as information about threat actor tactics and active campaigns. Your SIEM or SOAR platform ingests this data to enrich alerts, prioritize investigations, and trigger automated responses. The goal is to give your security team timely, relevant threat context without adding manual work.
Threat intelligence feeds operate across three tiers: tactical feeds deliver machine-readable indicators of compromise in standardized formats like STIX 2.1 and TAXII for automated ingestion into SIEMs, SOARs, and EDR platforms. Operational intelligence covers active campaigns, malware families, and threat actor infrastructure with enough context to inform detection engineering and hunting queries. Strategic intelligence provides analyst-curated assessments of adversary motivations, targeting patterns, and geopolitical factors that shape your organization's threat landscape. The strongest platforms combine all three tiers with primary-source collection from the deep and dark web, sensor-verified telemetry, and human intelligence that automated crawling alone cannot replicate. Feed value depends on freshness, accuracy, deduplication, confidence scoring, and how directly the intelligence maps to your specific environment and industry.
The table below compares the 10 cybersecurity intelligence and telemetry feeds we reviewed across key capability areas. We evaluated ten cybersecurity intelligence and telemetry platforms focusing on feed quality and relevance, integration depth with SIEM and SOAR systems, automation capabilities, and ease of deployment. We reviewed customer feedback and spoke with product teams about architecture decisions and known limitations. This article was researched and written by Alex Zawalnyski, with technical review by Laura Iannini. Read our full methodology ESET Threat Intelligence is a CTI platform purpose-built for security teams tracking advanced persistent threats, with particular strength in threats originating from Russia, China, and North Korea. We think ESET is a strong option for organizations in critical infrastructure or high-risk sectors that need curated APT intelligence with direct analyst access, without building an in-house research team.
Customers praise the real-time updates and notification system, and the reporting features make producing monthly threat summaries straightforward. Setup and deployment get positive marks for speed. Something to be aware of is that the dashboard can feel cluttered; some users flag nested menus that slow down daily navigation. There’s also an initial learning curve before your team reaches full effectiveness with the platform.
We were impressed by the quality of the APT intelligence, particularly for threats originating from high-risk regions. If your organization faces targeted threats from nation-state actors or you operate in critical infrastructure, ESET Threat Intelligence delivers expert-level intelligence at a level that would be difficult to replicate with an in-house team. The tiered APT reporting structure makes it accessible to organizations of different sizes, which is good to see.
5. Performance Evaluation & Extended Technical Observations Talos Intelligence is Cisco’s threat research and intelligence division, backed by one of the largest commercial telemetry networks in cybersecurity. We think Talos is a strong fit for organizations already invested in the Cisco security ecosystem, where threat intelligence flows automatically into firewalls, endpoints, email, and DNS security without manual intervention.
Customers highlight the early threat detection that comes from Talos’ telemetry scale, and the automatic updates across the Cisco stack reduce the operational burden on security teams. Something to be aware of is that the full value of Talos intelligence requires integration with the Cisco ecosystem. Organizations running multi-vendor security stacks can still benefit from Talos’ published research and reputation data, but the automated response advantages are most pronounced within Cisco environments.
We were impressed by the volume of telemetry driving Talos’ intelligence, processing 800 billion security events daily is a scale that very few threat intelligence teams can match. If you’re running a Cisco-heavy security stack, the closed-loop defense where intelligence automatically updates your firewalls, email security, and DNS is a real operational advantage. For multi-vendor environments, the intelligence is still valuable but the automation benefits are reduced.
CrowdStrike Adversary Intelligence is a threat intelligence platform built for enterprise SOCs managing sophisticated adversaries, with detailed profiles of over 281 tracked threat actors. We think CrowdStrike is a strong choice for organizations already in the Falcon ecosystem or building a centralized CTI operation that needs adversary profiling, dark web monitoring, and sandbox analysis in one place.
Customers praise the actionable intelligence and the direct EDR integration with Falcon. Frequent threat report updates keep teams ahead of emerging campaigns. Something to be aware of is the cost; premium intelligence tiers carry significant pricing that may be out of reach for smaller organizations. Some users also flag a steep learning curve before analysts can make full use of the platform’s depth and data volume.
We were impressed by the depth of adversary profiling, with 281+ tracked actors and detailed TTPs that give SOC analysts immediate context during investigations. If you’re already running CrowdStrike Falcon or building a dedicated CTI function, the platform goes beyond feeds into active remediation, which is a meaningful differentiator. The 2026 Global Threat Report highlighted that average eCrime breakout time dropped to just 29 minutes, which underscores why having this level of adversary context directly connected to your EDR matters.
GreyNoise is a threat intelligence platform that identifies what’s actively scanning and attacking your infrastructure, using a global sensor network rather than aggregated third-party feeds. We think GreyNoise is a strong option for SOC teams managing large internet-facing attack surfaces where alert fatigue from mass scanning is a real problem. Customers highlight the platform’s simplicity and its ability to reduce alert noise significantly. The UI and integration options get positive feedback, and support quality stands out as a consistent strength. Something to be aware of is that GreyNoise doesn’t go deep on threat actor attribution; if your team needs detailed adversary profiling, you’d want to pair it with a different platform. Some users also want more context around specific IOCs beyond what the platform currently provides.
We were impressed by the sensor-backed approach, where intelligence comes from actual observed attack traffic rather than aggregated feeds. If your SOC is drowning in alerts from internet noise and your analysts are spending time filtering out benign scanners, GreyNoise directly tackles that problem. The Global Observation Grid with 5,000 sensors across 80 countries gives the platform a breadth of visibility that’s hard to replicate. The C2 Detection module, launched in April 2026, adds an important layer by surfacing active compromise earlier in the kill chain.
Flashpoint Ignite is a CTI platform that spans cyber threats, physical security, and vulnerability intelligence, pulling from over 3.6 petabytes of primary-source data across the open, deep, and dark web. We think Flashpoint is a strong fit for large enterprises, critical infrastructure operators, and national security teams that need unified cyber and physical threat visibility in a single platform.
Customers praise the platform as user-friendly for analysts consuming and processing data, and the training and webinars on emerging tradecraft get strong marks. Support responsiveness stands out as a consistent positive. Something to be aware of is that the portal presents a lot of information and new users need time to learn navigation. Custom analyst research requires formal RFI submission unless your contract tier includes it, so it’s worth clarifying which modules and analyst services you’re getting upfront.
We were impressed by the depth of primary-source collection from the deep and dark web, which surfaces threats that aggregation-based platforms typically miss. If your risk picture includes both digital and physical threats, the geo-enriched physical security intelligence is a capability that very few CTI platforms offer. The board-ready finished intelligence reports are also a strong point for teams that need to communicate threat context to executive leadership.
Intel 471 Verity471 is a unified cyber intelligence platform launched in July 2025 that combines automated data collection with deep Cyber HUMINT to deliver actionable insights into sophisticated threat actors and underground marketplace activity. We think Verity471 is a strong option for enterprise security teams and threat intelligence analysts in high-risk sectors that need visibility into adversary behavior beyond what automated feeds alone can provide.
Customers value the depth of intelligence that comes from the HUMINT-backed approach and the way finished intelligence reports are tailored for different audiences, including security operations, executive, and GRC teams. Something to be aware of is that the platform delivers the most value when you use the full portfolio across threat exposure, intelligence, and hunting. Organizations looking for a single intelligence feed rather than a full platform may find it broader than their requirements.
We think the combination of automated collection and Cyber HUMINT is what sets Verity471 apart from most CTI platforms. If your organization needs to understand not just what threats exist but who is behind them, why they’re targeting your sector, and what they’re planning, Verity471 delivers that level of context. The platform won the 2025 CyberSecurity Breakthrough Award for Security-as-a-Service Innovation of the Year, which reflects the differentiated approach. For teams willing to use the full portfolio, the intelligence depth is strong.
IBM X-Force Threat Intelligence is an analyst-driven CTI service that combines human expertise with global telemetry to deliver malware reverse engineering, dark web research, and strategic threat assessments. We think X-Force is a strong choice for enterprise security teams in finance, government, energy, and healthcare that need strategic intelligence on who’s likely to target them and why, not just tactical IOC feeds.
Customers highlight the threat database as current and well-maintained, with quick response times and continuous monitoring getting positive marks. The coverage of threat groups, industries, and malware families helps teams prioritize effectively. Something to be aware of is the pricing; X-Force sits at enterprise-level pricing, and some users note that the AI-powered response capabilities still have room for improvement. Full value also requires integration across your security stack rather than standalone deployment.
We were impressed by the strategic depth of X-Force’s intelligence, particularly the ability to identify which adversaries are most likely to target your specific organization. If your security program is intelligence-led and your planning requires understanding adversary mindset and targeting rationale, X-Force delivers that context with a depth that lighter, feed-only platforms can’t match. For teams focused purely on automated IOC feeds without strategic analysis needs, lighter options exist.
Unit 42 is Palo Alto Networks’ threat intelligence and incident response team, offering hands-on security services rather than a standalone platform. We think Unit 42 is a strong fit for large enterprises and critical infrastructure operators that want intelligence-driven security services with board-level communication built in, including red teaming, compromise assessments, and strategic advisory.
Customers highlight excellent responsiveness and ease of working with the team, and for organizations with smaller security staff, the 24/7 coverage fills real gaps. The information provided during incidents gets strong marks for usefulness. Something to be aware of is that the service works best if your environment runs primarily on Palo Alto technology. Some users also flag inconsistency in how ad-hoc requests are handled outside of structured engagements.
We think Unit 42 stands out because it’s a services engagement rather than a platform subscription, which makes it a different kind of investment. If you need expert practitioners to assess, test, and advise, with the added ability to translate technical risk into language your board understands, this model works well. The board-level risk communication capability is a differentiator that most threat intelligence providers don’t offer. For organizations that need a feed or platform rather than a services team, Unit 42 isn’t the right fit.
Mandiant Threat Intelligence, now part of Google Cloud, delivers curated cyber threat intelligence backed by over 500 global analysts and more than 200,000 annual incident response hours. We think Mandiant is a strong choice for enterprise security teams and SOCs in high-risk sectors that need authoritative, practitioner-backed intelligence with AI augmentation through Google’s Gemini models.
Customers praise the quality of the curated intelligence and the depth that comes from Mandiant’s frontline breach experience. The Gemini-powered summaries help teams that need to synthesize large volumes of intelligence quickly. Something to be aware of is that the most valuable capabilities sit in the higher-tier subscription packages. Organizations with simpler intelligence needs may find the platform scope broader than required.
We were impressed by the combination of frontline incident response experience and Gemini AI augmentation, which gives Mandiant a depth-plus-speed advantage that most CTI platforms can’t match. If you need intelligence that comes from analysts who have actually responded to breaches, backed by AI that can synthesize and surface relevant threats rapidly, Mandiant delivers that. The Sec-Gemini model, integrating Google Threat Intelligence with the OSV database, adds another layer of capability for vulnerability impact analysis and root cause work.
Recorded Future is a CTI platform built around automation and contextualized intelligence at scale, now owned by Mastercard following a $2.65 billion acquisition completed in December 2024. We think Recorded Future is a strong option for SOC teams in high-risk sectors that need automation to manage alert volume without growing headcount, with direct integrations that turn intelligence into action.
Customers praise the interface and risk scoring for making prioritization straightforward, and the AI-powered research capabilities help teams quickly pull context on vendor breaches and emerging threats. Something to be aware of is that the identity module has drawn criticism for high false positive rates on compromised credentials in some environments. Some users also report that IOC severity changes mid-workflow can slow resolution processes.
We think Recorded Future’s automation capabilities are its strongest selling point. If your analysts spend too much time on manual correlation and you have the integrations to take advantage of automated response, the platform reduces that burden. The risk scoring and executive reporting capabilities are also a positive for teams that need to communicate threat intelligence to leadership. The Mastercard acquisition adds a unique dimension for organizations in the financial sector, though the platform remains broadly applicable across industries.
Threat intelligence platform pricing varies significantly by module, data volume, and analyst access requirements. Most platforms in this category are quote-based, with pricing dependent on your organization's size, sector, and the intelligence tiers you need. These are the evaluation and deployment steps we recommend when selecting a threat intelligence platform.
Tactical feeds automate detection; strategic intelligence informs planning and resource allocation. Most organizations need a mix, but the ratio determines which platforms fit. Intelligence that requires manual import or custom development to reach your detection tools loses most of its operational value.
Stale indicators generate false positives; feeds without confidence scoring force analysts to validate every alert manually. A platform focused on nation-state activity delivers limited value if your primary threats are financially motivated ransomware groups, and vice versa. Direct analyst access is a differentiator, but it's often limited to premium tiers or charged separately, so clarify what you're getting upfront.
Automated blocking and credential reset reduce response time, but false positives in automation create operational disruption that's worse than manual triage. Most CTI platforms have a learning curve; budget time for your team to learn navigation, query syntax, and reporting before expecting full operational value.
Security leadership increasingly needs to translate threat intelligence into business risk language for the board; platforms that generate board-ready reports save significant preparation time. Not all platforms collect from the same sources; primary-source collection from forums, marketplaces, and chat channels surfaces threats that aggregation-based tools miss.
Some platforms price by feed count, others by data volume or user count; know which cost drivers will grow as your security program matures. Threat intelligence platform selection depends on your primary pain point: threat actor expertise, alert noise reduction, or analyst automation.
For APT-focused teams tracking nation-state activity, ESET Threat Intelligence delivers curated feeds with APT reports, direct analyst access, and low false positives. Integration with SIEM/SOAR is straightforward. If your SOC drowns in alerts from internet noise, GreyNoise directly tackles alert fatigue by identifying what’s actively attacking your infrastructure.
For CrowdStrike environments wanting tight EDR integration with threat actor intelligence, CrowdStrike Adversary Intelligence profiles 250+ actors with direct Falcon integration. If automation and workflow integration are critical, Recorded Future integrates directly with SIEM, SOAR, and identity tools to reduce analyst workload. Automatic credential reset and risk scoring accelerate response.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Cyber%20threat%20intelligence • https://github.com/parthlakhalani/Threat_Intelligence_Feed_Integrator • https://kravensecurity.com/creating-your-own-cti-aggregator-for-free/ • https://github.com/Ethan-Andrews/ThreatIntel-Aggregator • https://dev.to/ayinedjimi-consultants/how-to-build-a-real-time-threat-intelligence-feed-aggregator-in-python-3nm6 • https://www.sdnia.com/how-to-build-a-preemptive-threat-intelligence-pipeline-using-automated-feed-aggregation-and-correl ation/ • https://kitploit.com/en/tools/github/ethan-andrews/threatintel-aggregator • https://github.com/Chandangowdag/threat-intelligence-feed--aggregator • https://expertinsights.com/security-operations/top-cybersecurity-intelligence-telemetry-feeds
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Automated Threat Intel Feed Aggregator.
[*] Metasploit Scan Running on Target Subnet for Automated Threat Intel Feed Aggregator... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |