Complete Technical Paper Content — Automated Threat Intelligence Extraction From Security Blogs
Overview & System Context
Automated Threat Intelligence Extraction From Security Blogs: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9516 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background The cybersecurity industry isn’t short on threat intelligence – it’s overwhelmed by it. Every day, security teams sift through a growing flood of advisories from vendor blogs, Really Simple Syndication (RSS) feeds, premium threat providers, and opensource Indicators of Compromise (IOC) repositories. The challenge is no longer having access to intelligence, but the ability to operationalize it fast enough to reduce real risk.
When a critical advisory is published, security teams are often pushed into a slow, manual process spanning days of work reading reports, extracting indicators, and hunting across multiple tools to determine whether the organization is affected. Meanwhile, attackers are already on the move exploiting the window between intelligence publication and defender action. Fragmented feeds, inconsistent formats, and vendor-specific constraintsI only widen this gap, making timely, actionable detection one of the hardest challenges in modern security operations.
At Adobe, our Cybersecurity Threat Research & Intelligence (CTRI) team built an AI-powered threat intelligence platform on a Lakehouse architecture to move swiftly and close the gap between intelligence and action. In this blog, I will demonstrate how security teams can use agentic architecture and AI workflows to transform threat intelligence into timely detection and response at scale.
Figure 1: Threat Intelligence Dashboard | Devpost Rather than building another standalone threat intelligence platform or relying on a single vendor feed, we architected a unified, production-grade orchestration layer on a Lakehouse architecture. This layer ingests threat intelligence from any source, normalizes it into a consistent schema, and automatically hunts across enterprise telemetry in minutes.
At the core of our platform is an agentic security model: instead of relying on analyst hours to manually read advisories, extract indicators, and initiate hunts, AI agents autonomously ingest, interpret, and act on new intelligence as soon as it becomes available. Large language models (LLMs) extract IOCs from unstructured content, regardless of source format or taxonomy, which are then validated, enriched, and used to trigger coordinated hunts across the environment.
Altogether, the platform operates continuously at scale, dramatically reducing the time from intelligence publication to detection and enabling faster, more accurate response to emerging threats. Once new threat intelligence is published, the platform orchestrates a fully automated flow through the following steps: Figure 2: Threat Intelligence Dashboard | Devpost By automating the end-to-end flow from intelligence ingestion through detection, this agentic approach reduces reliance on manual processes and enables security teams to operate with greater speed and consistency. The result is a more resilient threat intelligence operation, one that enables detection and response at speed without increasing operational complexity for analysts.
While every organization’s environment is different, the core architectural patterns behind an agentic threat intelligence platform are broadly applicable. Below is a highIlevel view of how security teams can approach building a similar system, without relying on a single tool, vendor, or feed: By grounding the architecture in unified data, AIIdriven interpretation, coordinated workflows, and strong guardrails, security teams can move toward an agentic model that scales with both intelligence volume and operational demands. When introducing agentic detection, running the system alongside existing processes can help teams build trust in autonomous decisions over time, easing the transition from verification to investigation.
Every organization faces the same challenge: an overwhelming volume of threat intelligence and too little time to act on it. By rethinking how existing data infrastructure is used, security teams can connect the tools they already have into a unified, production-grade pipeline that enables agentic, automated operations. Figure 3: Threat Intelligence Dashboard | Devpost At Adobe, this shift has enabled us to move towards quicker threat detection and intelligence capabilities. The goal isn’t to replace analysts, but to eliminate the repetitive, mechanical work that slows them down, freeing teams to focus on mission-critical investigations and response. Agentic, AI-powered workflows offer a practical path for organizations looking to operationalize threat intelligence at scale and keep pace with a fast-moving threat landscape.
Don’t miss out! Get the latest Adobe security news and exclusive content delivered straight to your inbox. This study introduces an innovative approach to automating Cyber Threat Intelligence (CTI) processes in industrial environments by leveraging Microsoft’s AI-powered security technologies. Historically, CTI has heavily relied on manual methods for collecting, analyzing, and interpreting data from various sources such as threat feeds. This study introduces an innovative approach to automating CTI processes in industrial environments by leveraging Microsoft’s AI-powered security technologies. Historically, CTI has heavily relied on manual methods for collecting, analyzing, and interpreting data from various sources such as threat feeds, security logs, and dark web forums—a process prone to inefficiencies, especially when rapid information dissemination is critical. By employing the capabilities of GPT-4o and advanced one-shot fine-tuning techniques for large language models, our research delivers a novel CTI automation solution. The outcome of the proposed architecture is a reduction in manual effort while maintaining precision in generating final CTI reports. This research highlights the transformative potential of AI-driven technologies to enhance both the speed and accuracy of CTI and reduce expert demands, offering a vital advantage in today’s dynamic threat landscape.
Cyber Threat Intelligence (CTI) collects, analyzes, and disseminates information about current and potential cyber threats. CTI involves data collection from various sources, such as security logs, threat feeds, and incident reports, to identify Indicators of Compromise (IoC) and understand the Tactics, Techniques, and Procedures (TTPs) used by threat actors [ 1 ] . CTI is crucial in cybersecurity as it enables organizations to proactively defend against cyber attacks by providing actionable insights that inform security measures, enhance incident response, and facilitate identifying and mitigating vulnerabilities [ 2 , 3 , 4 ] .
Unlike measurement data, which is automatically gathered, threat intelligence requires meticulous manual analysis by expert analysts [ 5 , 6 ] . These professionals use their expertise and intuition to extract IoCs and attack patterns. An IoC could be any observable element linked to an attack, such as a file (identified by its name or hash), a URL, or an IP address. To decode the attack pattern of an attack group, analysts identify several IoCs related to a malicious campaign and ascertain the role of each one—for instance, determining if a URL is an exploitation site or a command-and-control server. This carefully curated threat intelligence is published in technical blogs and industry reports. Moreover, commercial or open-source IoC feeds share some of the identified indicators essential for detecting security threats, conducting forensic investigations after breaches, and attributing attacks to specific threat actors [ 2 , 7 , 3 ] .
In today’s rapidly evolving cybersecurity landscape, the promptness and accuracy of CTI reports are crucial for safeguarding digital infrastructures by enabling immediate responses to security risks. However, the current methodologies for generating these reports predominantly rely on manual human efforts, which introduces significant challenges affecting their efficiency and effectiveness. The manual approach to report generation is inherently time-consuming, labour-intensive, and susceptible to human error. Threat Intelligence Analysts must sift through vast amounts of data from multiple sources, synthesize the information, and compile comprehensive reports, all of which demand substantial expertise and meticulous attention to detail [ 8 , 9 ] .
2. System Architecture & Core Working Principles In the cybersecurity community, several standard methods are used to automate CTI processes involving open-source tools, custom scripting, platform integration, and AI-based methods, which still demand CTI specialists [ 10 , 11 , 12 ] . This study addresses CTI automation using AI-powered Microsoft security products, including Microsoft Copilot for Security (MCS), Logic Apps, and Azure AI, within an industrial-scale environment. The proposed method offers significant benefits, including faster threat detection, improved response times, and more accurate threat intelligence. Out method facilitates CTI processes and reduces manual efforts, ultimately strengthening cybersecurity defences. The experimental results, along with interviews with security experts, have revealed a significant impact of these technologies. We present a detailed architectural design for deploying this method within an industrial environment, highlighting how this approach can enhance security efficiency and effectiveness.
Many organizations today rely on manual and semi-automated approaches to collect, analyze, and generate CTI reports. These methods often involve threat analysts gathering threat data from disparate sources, such as security logs, threat feeds, vulnerability databases, and social media platforms. Analysts must then filter through this data and manually correlate it to identify patterns and assess the potential impact on the organization’s security posture. This process may involve using essential tools, but in many cases, it still requires a significant amount of manual work, including writing the final report [ 13 ] .
The manual nature of these methods introduces several challenges. The gathering, analyzing, and reporting process can take days or weeks, delaying the response to emerging threats. Due to the complexity of modern threats, manual processing increases the likelihood of missing critical insights or introducing errors. Different analysts may interpret threat data differently, leading to inconsistencies in reporting. As the volume and complexity of threats increase, manual processes struggle to keep pace, leading to bottlenecks in threat detection and mitigation efforts [ 13 , 6 ] .
In response to these challenges, automation and using AI offers promising solutions. Organizations can significantly reduce the time and effort required to generate final CTI reports by automating the collection and analysis of threat data. AI-powered systems can ingest vast amounts of threat data in real-time, correlate patterns across multiple sources, and identify emerging threats with high accuracy. Machine learning models can learn continuously from new data, improving their detection capabilities and reassuring organizations of their adaptability to new threats as they evolve [ 8 , 9 ] . Despite these advancements, many organizations are hesitant to adopt fully automated CTI processes due to concerns about the reliability of AI-driven systems, particularly in complex or high-stakes environments. They may worry about false positives, the inability of machines to interpret nuanced threat information, or the lack of transparency in how AI makes decisions [ 11 ] .
This research aims to address the gap by exploring the limitations of current manual CTI report generation processes and investigating how automated solutions, including AI, can enhance these reports’ overall quality, speed, and accuracy. By identifying which tasks within the manual process can be effectively automated—such as data collection, correlation, and preliminary analysis—this study aims to lay the groundwork for developing more advanced automated CTI systems. These systems will not replace threat intelligence analysts. However, they will better support them by minimizing the manual effort required in report creation, thus enabling faster and more consistent dissemination of threat intelligence. Applying the proposed method, in turn, will allow organizations to respond more rapidly to emerging threats and implement defensive measures promptly. This research offers a practical solution to the critical shortage of highly skilled cyber threat analysts worldwide, particularly impacting medium-sized cybersecurity companies that provide CTI services.
Numerous studies have proposed automating the final extraction of CTI using AI-based methods, including Natural Language Processing (NLP), Information Retrieval (IR), and Machine Learning (ML) approaches such as Neural Networks (NN) [ 9 , 12 , 16 , 11 ] . Husari et al. [ 9 ] proposed the pioneer model TTPDrill to automatically extract threat actions and map them to attack patterns, techniques, and phases of the cyber kill chain from unstructured CTI reports. The tool combines NLP and IR techniques, using an ontology derived from MITRE ATT&CK and CAPEC repositories—Common Attack Pattern Enumeration and Classification or CAPEC [ 17 ] , is a comprehensive database maintained by MITRE Corporation—to map extracted TTPs to recognized cyber threat patterns. The repository aims to provide a structured and detailed understanding of how attacks are executed, which helps cybersecurity professionals anticipate threats, design effective defences, and communicate about security issues more effectively. TTPDrill aims to facilitate timely, cost-effective cyber defence by converting unstructured CTI into structured threat information, significantly improving the precision and recall of TTP extraction.
Zhao et al. [ 12 ] presents TIMiner, an automated framework designed to extract and categorize CTI from unstructured social media data. The framework uses a Convolutional Neural Network (CNN) to classify CTIs into specific domains such as finance, government, IoT, and Industrial Control Systems (ICS). The study employs a hierarchical IoC extraction method that leverages word embedding and syntactic dependency to identify known and unknown types of IoCs. TIMiner also introduces a novel metric, Threat-Index, which quantifies the severity of threats across different domains by analyzing attack frequency, exploited vulnerabilities, and risk levels.
Satvat et al. [ 16 ] introduce an EXTRACTOR tool, which automates the extraction of concise attack behaviour from unstructured CTI reports. EXTRACTOR generates provenance graphs that capture the relationships between entities, actions, and system artifacts in a cyber attack. The tool leverages NLP techniques like Semantic Role Labeling (SRL) to process complex CTI texts and infer who did what to whom in an attack. The study addresses verbosity, syntactic complexity, and the need to capture causal and temporal dependencies between actions. EXTRACTOR generates actionable intelligence, simplifying threat-hunting tasks by focusing on attack behaviour that can be observed in system audit logs. The tool was evaluated against real-world CTI reports and DARPA adversarial engagements, showing high precision and utility in detecting cyber threats using automatically generated graphs.
Jo et al. [ 11 ] present a CTI system called Vulcan, which automates the extraction of diverse CTI data, including TTPs, from unstructured sources like security reports and blogs. Vulcan employs a fine-tuned language model to perform Named Entity Recognition (NER) and Relation Extraction (RE), accurately identifying CTI entities (e.g., attack vectors, tools) and their relationships. The extracted CTI data are stored in a graph database, accessible via APIs, enabling applications such as threat evolution tracking and profiling. Liu et al. [ 15 ] introduce a system to extract actionable CTI from unstructured cybersecurity reports automatically. TriCTI uses a trigger—enhanced neural network model that incorporates campaign triggers —to classify IoCs based on the cyber kill chain stages. By leveraging NLP and data augmentation techniques, TriCTI improves classification accuracy and generates actionable intelligence that can be integrated into intrusion detection systems.
You et al. [ 14 ] introduce the TIM framework designed to mine and classify TTPs from unstructured threat data such as security analysis reports. The framework uses a TCENet (Threat Context Enhanced Network) model that leverages textual descriptions and specific TTP-related elements (e.g., IPs, CVEs, file hashes) to classify TTP. The lack of available sentence-level TTP datasets and the complexity of accurately classifying TTP descriptions is addressed in this study. In a recent study, Le et al. [ 8 ] introduced LADDER, a framework designed for knowledge extraction that identifies text-based attack patterns from CTI reports. LADDER automates the extraction of TTPs and other essential data related to malware and APTs from CTI sources. The framework organizes the extracted information using an ontology—a structured representation of knowledge domains in information science—to aid in meaningful information organization. Combined with the TTPClassifier, this ontology integrates the information into a comprehensive knowledge graph (KG). The KG, formatted as triples (subject, predicate, object), includes domain-specific information, facilitating predictive analysis. In contrast to our research, the author proposed a method to automate only attack pattern extraction. Our work not only automates the whole CTI generation but also produces a comprehensive report, including strategic and operational CTI.
Li et al. [ 10 ] introduce AttacKG, a novel system designed to automatically extract structured attack behaviour graphs from unstructured CTI reports and aggregate them to form a Technique Knowledge Graph (TKG). This approach addresses the challenge of manually recovering attack behaviours from CTI reports, often written in natural language. By parsing multiple CTI reports, AttacKG identifies and integrates diverse attack techniques, creating comprehensive knowledge graphs that summarize various aspects of attack patterns. The system outperforms existing tools in accuracy, providing valuable intelligence for security tasks like APT detection and cyber attack reconstruction.
Recent advancements in AI-driven CTI extraction, such as LADDER and AttacKG, employ a combination of NLP techniques and open-source pre-trained LLMs, including BERT [ 18 ] , RoBERTa [ 19 ] , and XLM-RoBERTa [ 20 ] , to identify relevant sentences, determine if they describe an attack, and map these attacks to the corresponding Tactics, Techniques, and Procedures (TTPs) in the MITRE ATT&CK framework [ 11 , 12 , 2 , 3 , 7 ] . Despite their effectiveness, these approaches still demand specialized expertise for model implementation, limiting their practicality in environments without such resources. In contrast, our study introduces the first fully automated CTI extraction methodology that eliminates the need for domain-specific expertise. Additionally, our approach autonomously generates comprehensive CTI reports, covering IoCs and TTPs, mapping attack behaviours to the MITRE framework, and recommending mitigation strategies. These reports are organized into two primary sections: strategic reports, offering high-level summaries for executives, and technical reports, delivering detailed operational intelligence.
This study introduces a fully automated, end-to-end process for generating CTI reports using AI built within the Microsoft enterprise ecosystem. Key technologies include PowerShell scripting, Azure Logic Apps, MCS, Azure AI Studio, and Azure DevOps. The automation begins with a PowerShell script, which gathers essential data from the user and manages the workflow. Azure Logic Apps then orchestrate the report generation by dividing it into multiple sections. Each section is produced through customized prompts directed to MCS or Azure AI. Once all sections are completed, the Logic Apps and PowerShell script merges them into a final, cohesive report that is automatically stored in the Azure DevOps repository. The proposed architecture is shown in Figure 1 . The segmentation approach ensures precise control over the prompt creation, allowing for customization of each section. The generated final CTI report comprises the following seven sections: The first and second sections include strategic CTI information for executive-level decision-making, while the remaining sections fall under the technical CTI report category. The Metadata and Overview section provides general information about the report, including the report title, creation date, attacker details, and a threat intelligence summary. The Overview briefly describes the scope of the threat, including the affected sectors, systems, or technologies, and the severity or priority level of the threat, offering a high-level snapshot to set the context for the rest of the report. The MITRE Summary Table section presents a structured summary of the identified TTPs used in the threat, mapped to the MITRE ATT&CK framework, including specific techniques leveraged by attackers and highlighting the associated adversarial tactics. The table serves as a quick reference for understanding the threat actors’ behaviour and operational methodologies.
The Data Extraction section contains all relevant data points related to the observed threat. This section typically includes IoCs information, such as IP addresses, file hashes, domain names, and other artifacts that may assist in identifying or tracking a threat. This section focuses on the factual data collected from various sources during the investigation. The Tools and Malware section details any tools, exploits, or malware observed in the attack, including the descriptions of how these tools are used by threat actors and their potential impact on compromised systems. The analysis often highlights known or new malware variants, software used in the attack chain, and the relationships between the tools and broader campaigns.
The Defense Recommendations section provides actionable recommendations to mitigate or respond to threats. This section covers suggested defensive measures, including patches, configurations, detection rules, and long-term strategies to protect against similar future threats. It may also highlight gaps in current defences that organizations should address. The References section lists all the sources used to create the CTI report, including but not limited to academic papers, threat feeds, public and private security advisories, and other research material relevant to the threat. Finally, the Tags section contains keywords or phrases that categorize the threat for easier indexing and retrieval. Tags may include the malware family name, associated adversaries, affected industries, geographic regions, TTPs, or specific vulnerabilities exploited. These tags help in searching and cross-referencing the report with other similar threats.
The PowerShell script acts as the main user interface, orchestrating the initialization of all the underlying systems, including Azure Logic Apps and Azure DevOps. This component integrates various functionalities such as user input, file validation, HTTP requests, and monitoring mechanisms to ensure a smooth and automated workflow. As illustrated in Figure 2 , the script’s tasks are divided into four main functions: Based on artifact similarities, the threat types are categorized as follows: Campaign, Threat Actor, Vulnerability, or Malware/Tool. The user input and validation functions collect intelligence data and verify the threat type. The script then prompts the user to provide essential intelligence information and select a specific threat type, ensuring the chosen threat meets predefined criteria for validity. The file existence check ensures the uniqueness of the CTI report’s file name. To start, the user is prompted to input a file name checked against the Azure DevOps repository to avoid duplicates. If a file with the same name already exists, the user is notified and asked to provide a new name. The Trigger Logic Apps function initiates the CTI report creation process by collecting all user-provided data and sending an HTTP request to the Logic Apps. This data is passed as a JSON request body, and the function ensures the request is successfully sent while handling potential errors.
The report monitoring and retrieval components continuously monitor the Azure DevOps repository for the CTI report’s creation. The script checks for recent commits every two minutes until the CTI report is located. Once the report is successfully generated, the user is notified that it is available in the repository. Azure Logic Apps defines a cloud service that helps users automate workflows and integrate applications, data, and services across organizations. It allows the creation of automated workflows to connect different services and applications and offers numerous pre-built connectors for services. Users can create custom workflows using a visual designer or code and trigger workflows based on specific events or schedules. Azure Logic Apps automates business processes and tasks, integrates disparate systems and data sources, manages enterprise workflows and data flows, and builds complex integration scenarios with minimal coding.
3. Software Implementation, Frameworks & Protocols The Azure Logic Apps workflow serves as the core engine of the process, orchestrating the generation of the CTI report by integrating MCS, Azure AI Studio, and Azure DevOps—a Cloud-based platform from Microsoft that offers tools for managing the entire software development lifecycle, including version control, project tracking, and collaboration. This workflow is designed to manage various types of threat intelligence, including campaigns, threat actors, vulnerabilities, and malware/tools.
Depending on the threat type, the workflow branches into sub-workflows, employing Azure AI and MCS where applicable. The process is initiated by an HTTP request from a PowerShell script, which sends JSON-formatted data containing key parameters such as intelligence information, threat type, and file name. A variable, Merge Sections , is created to store the context of the report sections. The Logic Apps workflow then assesses the threat type (Campaign, Threat Actor, Vulnerability, or Malware/Tool) and redirects the process accordingly, as illustrated in Figure 3 . The figure provides the Campaign threat type as an example for clarity without loss of generality.
The CTI report is organized into distinct sections based on the threat type (elaborated in Section III-A ). Logic Apps initiates Azure AI or MCS to generate each section accordingly, appending the results to the Merge Sections variable. Once all sections are compiled, Logic Apps retrieves the latest commit details from the Azure DevOps repository. The response is parsed to extract the most recent commit ID, which is required to initiate a new commit via the DevOps API. Finally, the fully compiled CTI report, stored within the Merge Sections variable, is uploaded to the Azure DevOps repository under the specified file name using the DevOps API.
Azure AI Studio facilitates the development of prompt flows, empowering developers to design, debug, and deploy AI-driven applications using customizable prompts and Python scripts. In this architecture, these flows are integrated with Azure Logic Apps. Our design leverages OpenAI’s GPT-4o model to extract, analyze, and generate specific sections of the CTI report. As depicted in Figure 4 , the workflow is structured into two main prompt flow deployments: one dedicated to generating the MITRE summary table and performing data extraction, and the other focused on generating the Tags section. In the first prompt flow, a spreadsheet containing the complete MITRE ATT&CK enterprise matrix is uploaded into the Azure AI environment to facilitate prompt flow deployment. This file provides a comprehensive reference for ATT&CK techniques and sub-techniques. The process initiates when intelligence information (Intel Info), received through an HTTP request from Logic Apps, is sent to Azure AI Studio. A Python script is subsequently employed to extract relevant text from a specified URL or article, which is the basis for further analysis and data extraction.
The retrieved text is processed by prompting GPT-4o to generate a summary table of MITRE ATT&CK techniques. In this step, GPT-4o is tasked with creating a section explaining the techniques and sub-techniques relevant to the specific campaign. Subsequently, a Python script parses the outputs from the earlier steps and merges the results of Section 2 (MITRE Summary Table) and Section 3 (Data Extraction). After the first prompt flow, the combined output is returned as an HTTP response to the corresponding Logic Apps action. The second prompt flow deployment handles the generation of tags for CTI reports based on their content. The process begins with the input of a report containing Sections 1-6 into the Azure AI Studio. Then Azure AI prompts GPT-4o to generate tags for Section-7 of the CTI report, based on the content from Sections 1-6. At the end of the second flow, a Python script parses the output generated by Azure AI.
MCS is an AI-powered assistant designed to enhance cybersecurity operations by providing real-time insights and recommendations. MCS, powered by machine learning, efficiently analyzes threat data and provides actionable insights, helping security teams respond to threats more effectively with guided steps and automation. MSC assists proactive threat hunting by analyzing vast amounts of security data to integrate the outcome with existing Microsoft security tools such as Microsoft Defender and Sentinel. In the proposed architecture, MCS is integrated with Azure Logic Apps, which provide a built-in action to facilitate direct interaction with MCS, enabling prompts to be sent and responses to be received within the workflow. Additionally, Azure Logic Apps allows the specification of skills , which are capabilities that enhance prompt processing. These skills enable extended functionality, such as accessing web URLs or retrieving threat intelligence from Microsoft Defender for threat intelligence. In this architecture, MCS generates four essential sections of the report: Metadata and Overview, Tools or Malware, Defense Recommendations, and References. From this point on, we use AI, LLM, and GPT-4.0 interchangeably to refer to systems that receive prompts and generate outputs. Specific distinctions will be made when necessary.
At this stage, the prompt directs the AI to extract detailed information about a threat campaign from a URL. Then, it is tasked with populating a pre-defined CTI report template in markdown format, ensuring accuracy and thoroughness. The critical elements, such as the campaign name, threat type, associated threat groups, and targeted industries, are filled in based on the data retrieved from the source. Additionally, the AI generates a strategic campaign summary to enhance accessibility for a wider audience. This structured process ensures the creation of consistent, detailed CTI reports while minimizing the risk of human error.
To generate this section, the prompt concentrating on identifying malicious software, tools, or malware employed in a cyber threat campaign. The AI generates a detailed technical report using data from a provided URL and the Microsoft Defender CTI Platform. A structured markdown template captures specific sections for each identified tool or malware. For each entry, the AI delivers a description and an example of how the threat actors utilize the tool or malware. This approach ensures the report is technically comprehensive and accurate, leveraging authoritative sources for in-depth analysis.
In this section, the prompt identifies malicious software, tools, or malware employed in a cyber threat campaign. The LLM generates a detailed technical report using data from a provided URL and the Microsoft Defender CTI Platform. A structured markdown template captures specific sections for each identified tool or malware. For each entry, the AI delivers a description and an example of how the threat actors utilize the tool or malware. This approach ensures the report is technically comprehensive and accurate, leveraging authoritative sources for in-depth analysis.
The LLM first compiles a list of references specific to a given threat campaign in this prompt. It gathers data from the provided URL and other publicly available sources. A structured markdown template populates these references as a list of URLs related to the threat campaign, ensuring the accurate collection and citation of relevant sources. This process provides comprehensive references to substantiate the report’s findings.
We evaluated the proposed approach from two perspectives: performance and cost. Initially, we conducted experiments comparing the reports generated manually by CTI analysts with those produced by AI. This phase focused on a Campaign threat type, comparing eight attack campaigns created by both methods, which are extracted from hundreds of reports, news, blogs, and other open and closed CTI resources. Lastly, we assessed and presented the cost associated with AI-based report generation using the proposed method.
We selected Cosine Similarity and BERT (Bidirectional Encoder Representations from Transformers) to compare the AI-generated report with the manual counterpart. BERT can process up to 512 tokens at a time, allowing it to handle relatively long documents [ 21 , 22 , 23 ] . BERT can be used to compare two documents by representing each document as a numerical vector (embedding) and then measuring the similarity between these vectors. The process involves encoding the documents’ text into high-dimensional embeddings that capture the text’s semantic meaning, allowing for a meaningful comparison. BERT starts by breaking down the text of each document into tokens (typically words) and converting words into a sequence of token IDs that BERT can process. Then, it adds unique tokens like [CLS] at the start of each document and [SEP] at the end to signify the boundaries of the input. Each token is then mapped to a pre-trained embedding vector using BERT’s embedding layer. These embeddings are contextual, meaning that the representation of a word depends on the words around it. BERT uses multiple layers of bidirectional transformers to process the input sequence and generate contextualized embeddings for each token. The embeddings capture the meaning of the words considering the surrounding context rather than treating them as isolated entities.
After processing the document through BERT, each document is represented as a high-dimensional vector (embedding). These vectors capture the meanings of individual words and their relationships in the document’s context. Once both documents have been transformed into vectors, we compare them using a Cosin Similarity. We also use Cosine Similarity to capture the similarity between the vocabulary of the two documents. The formula for cosin similarity between two vectors A A and B B is: where A ⋅ B A\cdot B is the dot product of the two vectors, and I A I \|A\| and I B I \|B\| are the magnitudes (or norms) of vectors A A and B B , respectively. The expanded formula then becomes: Cosine similarity measures the cosine of the angle between two non-zero vectors. A result of 1 indicates the vectors point in the same direction (maximum similarity), 0 means the vectors are orthogonal (no similarity), and -1 indicates the vectors point in opposite directions (maximum dissimilarity) [ 21 ] .
As an example, comparing “According to a new report by Trustwave, cybercriminals have developed an innovative phishing method that involves the use of encrypted RPMSG attachments.” with “The article from Trustwave discusses a phishing campaign that uses Microsoft Encrypted Restricted Permission Messages to deliver phishing attacks.” results in a 89% and 22% similarity using BERT and Cosine Similarity. While BERT captures the context, the latter indicates more sensitivity to the wording. Table II represent a comparison between the two metrics.
The final CTI reports provide multiple sections to cater to different stakeholders. Two key sections are the executive (or strategic) summaries, designed to support informed decision-making at the executive level. The remaining sections offer a technical analysis, equipping the security operations team with the necessary information to implement specific security measures. Our experiments have validated the precision of each report tier. As illustrated in Figure 5 , we compared the strategic-level sections of threat reports using BERT and Cosine Similarity metrics. While the average Cosine Similarity was 43%, the BERT model achieved an 89% score, demonstrating that the reports effectively conveyed the same context even with different terminologies.
The second experiment evaluates the extraction of attack patterns by comparing the manual methods versus AI models. We used Accuracy to report the performance of the model. where the term Total Number of Predictions refers to the complete set of TTPs that should have been detected, while Number of Correct Predictions represents the TTPs successfully identified using the AI method. Figure 6 illustrates the performance of the AI models, demonstrating an average accuracy of 79%.
4. Practical Deployment, Analysis & Case Studies The next set of experiments assesses the performance of technical CTI generation. In this experiment, we compared the most critical elements within the CTI reports, focusing on Indicators of Compromise (IoCs), Tactics, Techniques, and Procedures (TTPs), and Advanced Persistent Threats (APT). IoCs are data points that identify potential threats or breaches, including IP addresses, file hashes, and domain names associated with malicious activity. They are typically actionable and offer immediate insights into ongoing or past threats [ 4 ] . TTPs represent the strategies and methodologies used by threat actors.
This contextual information helps analysts understand not just what happened but how the attack was carried out, enabling more proactive defence measures [ 8 ] . APTs are sophisticated, long-term cyber threat campaigns by highly skilled (typically state-sponsored) threat actors. Identifying APTs within a CTI report provides critical intelligence on the threat’s origin, intent, and resources [ 1 ] . While IoCs provide direct evidence of compromise, TTPs offer a deeper understanding of the attack methodology. Each element serves a unique role in comprehensive CTI generation.
Table III presents the results of technical CTI reports generated using AI, comparing them to their human-generated counterparts. The table’s first and second columns (IoC and TTP) represent percentage performance accuracy. In contrast, the APT column indicates whether this element is included in the AI-generated reports. The designation N/A signifies that the component is absent in both reports, likely due to its unavailability in the original artifacts. IoC and APT demonstrated the highest performance among the technical indicators, achieving 90.2% and 85.7% accuracy, respectively. In contrast, TTP showed relatively lower performance compared to the manually generated reports, with averages of 79.5% accuracy.
While this research indicates the proof of concept, the system successfully automates the development of CTI reports, significantly speeding up the process and reducing the need for manual effort while maintaining the intelligence’s accuracy. However, this efficiency comes with a cost—each report’s creation requires substantial computational resources. These resources are primarily consumed by the AI tools employed, such as MCS and Azure AI Studio, which contribute to the environment’s overall complexity and resource demands.
Azure AI Studio: The computational cost in Azure AI Studio is determined based on the Compute Instance (CI) specifications and the online endpoint where the prompt flow is deployed. The CI functions similarly to a Virtual Machine (VM) instance, with pricing in Azure based on the instance type and the number of hours it operates. All AI computations, such as prompt processing, are executed using the allocated computational resources, including the number of CPU cores, RAM, and storage space provided by the instance type. Each deployment functions like a web server, offering a URL endpoint that handles HTTP requests to trigger the prompt flow, returning the AI-generated output. Since the deployment endpoint is integrated into Logic Apps for automated HTTP requests, the compute instance must remain active 24/7. Azure AI Studio hosts two prompt flow deployments in this setup—one for processing Sections 2 and 3 of the report and another for Section 7. Each deployment is equipped with a 2-core CPU and 8GiB of RAM. The combined monthly cost for both deployments is approximately $290, which breaks down to $0.20 per hour per deployment (assuming a 30-day month with 720 hours).
Microsoft Copilot for Security: The usage cost for MCS is measured in Security Compute Units (SCUs), which are consumed during prompt processing and output generation. Two key factors influence the consumption of SCUs: the size of the prompt (the number of characters submitted to the model) and the utilization of specific skills within MCS. This implementation optimizes prompt sizes to reduce SCU usage by summarizing explanations and eliminating unnecessary spaces and line breaks. While there is no precise measurement for SCU consumption based on the use of skills, observations during development indicate that skills accessing Microsoft Threat Defender tend to consume more SCUs. Since our system primarily relies on the campaign blog URL as the primary intelligence source, the skill that accesses web URLs (i.e., FetchURL) is used more frequently. For a typical report generation involving 4 out of 7 prompts, SCU usage ranges between 3.0 and 3.5 SCUs. Given the cost per SCU of $5.60, the total cost for generating a single report using MCS is approximately $18.50 ($5.60 x 3.3 SCU). Despite the variability in AI outputs, the overall costs remain relatively consistent. However, enterprises must also consider the additional cost of human intervention required to ensure report quality.
The cost and SCU usage are approximate due to the inherent variability in each output generated by the AI, which differs in terms of length and word choice. Both Azure AI and MCS utilize OpenAI’s GPT-4o model for prompt processing [ 24 ] . This model is designed to introduce an element of randomness, ensuring that identical prompts, input values, and parameters do not result in the same output on different occasions [ 25 ] . Despite this variability, the overall quality and intent of the generated content remain consistent. Due to the minor inconsistencies and the continuous advancements in AI technology, the outputs generated by the system cannot be considered final without human oversight. Human analysts must review and refine the AI-generated reports to meet the quality standards of manually produced reports. The primary goal of this research project was to accelerate the report creation process and reduce manual effort rather than completely eliminate the need for human involvement.
To report the acceleration of the AI-based model, we interviewed the Threat Intelligence team at our industrial partner site. Based on the survey outcome, the manually produced CTI report from raw data typically required an average of 8 hours of effort, depending on the threat’s complexity. With the introduction of AI automation, the manual effort needed by an analyst has been reduced to approximately 1 to 2 hours. This remaining work primarily involves refining the AI-generated content by correcting minor inaccuracies, enhancing the language, and verifying the information. As a result, this approach increases report creation speed by reducing manual endeavours. The main limitations of AI-driven report generation stem from the inherent variability and minor inconsistencies in AI-generated outputs due to the randomness introduced by OpenAI’s GPT-4o model. This variability requires human intervention to review and refine the reports, ensuring they meet the quality standards of manually produced ones. Furthermore, human oversight remains crucial for maintaining the accuracy and reliability of AI technology.
This study presents an architecture for automating Cyber Threat Intelligence (CTI) report generation using AI-powered tools within the Microsoft ecosystem. The primary objective was to accelerate the CTI generation process, enabling faster sharing of intelligence and enhancing attack detection and prevention for stakeholders. This objective was successfully achieved by integrating Microsoft Copilot for Security, Azure DevOps, and Azure AI Studio. Our evaluation of the proposed architecture, comparing manually generated and AI-generated reports, demonstrated high performance across both technical and executive-level reporting. Notably, while AI performed equally well in generating executive summaries, human intervention is still crucial in the more complex technical sections of the report. This necessity underscores the value of human expertise in maintaining the level of precision necessary for effective decision-making and implementation by security teams.
Future research will focus on evaluating the proposed method with larger datasets, incorporating both manually and AI-generated reports. Additionally, an in-depth analysis of other threat types beyond campaign threat intelligence will be conducted to assess performance and other factors, including cost. While GPT-4o was the primary language model used for prompt engineering, future work will explore the use of alternative models to compare their effectiveness. The experiments further indicated that combining AI-driven processes with human input yields the highest performance. As a next step, we propose developing a hybrid model that integrates other AI-based methods with proprietary security products. This model promises to further refine CTI report generation and enhance the overall quality of the final output, instilling optimism about the future of CTI report generation.
We appreciate the collaborative efforts and support from Difenda throughout this project. This study was made possible by the resources provided by our industrial partner, for which we are grateful. This research has been supported by research fund FR124652. Operational cyber threat intelligence platform combining BERT NER, ensemble classification, severity prediction, and real-time analysis—delivering 89.2% classification accuracy and subIsecond processing for SOC workflows.
An intelligent cyber threat intelligence system that leverages Natural Language Processing (NLP) and AI-based classification to extract meaningful cyber threat indicators from unstructured text, categorize threat types, predict severity levels, and visualize insights through an interactive web interface. In today’s rapidly evolving cyber threat landscape, security analysts are overwhelmed with vast amounts of unstructured threat intelligence data from blogs, forums, reports, and social media. This project addresses the critical need for automated threat analysis by developing a comprehensive AI system that delivers: This project demonstrates the practical application of cutting-edge AI/ML techniques in cybersecurity, providing immediate operational value while contributing to the advancement of automated threat intelligence systems.
This site looks amazing in desktop view! Would you like to switch to desktop view for the best experience? In order to identify cybersecurity risks at an early stage, NEC’s intelligence analysts daily gather, accumulate, and analyze cybersecurity information. However, the scope of information to be gathered has expanded beyond cyberattacks, including information about political, economic, social, and technological trends. As a result, one of the challenges is how to appropriately narrow down sources of information and conduct an analysis while gathering information from a wider range of fields. NEC is working to automate the generation of cyber threat intelligence using generative AI for high-accuracy and rapid analyses. This paper presents NEC’s cyber threat intelligence initiatives and challenges as well as an extraction and summarization pipeline under development for cyber threat information and a search and analysis pipeline for cyber threat-related information.
Cyber threat intelligence refers to the collection and analysis of information about cyber threats as a process as well as a deliverable 1) . In general, there are three types of intelligence: tactical, operational, and strategic 2) . Each of these types has a different position, purpose, and user. In particular, strategic intelligence supports management teams in making decisions on cybersecurity risks by analyzing from a variety of angles not only cyber threats and cyberattacks surrounding the organization but also political, economic, social and technological factors in the external environment. Information—mainly in regard to strategic intelligence—is written in a variety of formats including reports, blogs, articles, news, and social media, and different descriptions or expressions might be used by those sending out the information. Therefore, it is not easy to gather and organize the information. This is why intelligence analysts have been required to be highly knowledgeable and experienced. However, in the future, we will need to gather information even more broadly to find the desired information. To achieve this, we cannot rely solely on skilled analysts and we need to move away from overly relying on people to gather information. In some cases, reports might be required within a few days or even a few hours after receiving a request for collection and analysis. To meet the expectations of the management team, speed is important to provide accurate and relevant information to enable decision making in a timely manner. Against this background, we need to automate and save labor in the intelligence generation process to reduce the workload of analysts and to improve their analytical capabilities.
Users of strategic intelligence require information on what problems are currently occurring, what the situation is in other similar organizations, and what decisions are required to be made. Intelligence analysts gather necessary facts and use their knowledge to analyze them and formulate hypotheses, thereby meeting the expectations of management teams. The series of steps required to gather and analyze information upon request from decision makers and to generate the information necessary to take actions is called an intelligence cycle 3) . There are several variations of the intelligence cycle. The cycle described here includes the following steps: requirement definition, collection, processing, analysis/production, dissemination, and feedback ( Fig. 1 ).
5. Performance Evaluation & Extended Technical Observations On the other hand, if you start to gather information from scratch only after receiving a request and then organize and categorize it, you will never complete it by the expected time if you consider that you must further analyze and appropriately organize the information that contributes to the decision making. It is thus important to gather and accumulate information on a daily basis and have it readily available for immediate use. In addition, it is also key to monitor information on a daily basis in order to be aware of emerging threats and changes in threats as soon as possible. Therefore, NEC stores the information about cyber threats that is daily gathered and organized by intelligence analysts in a database. However, the scope of collection is no longer limited to cyber threat information but has expanded to include information regarding trends in politics, economy, society, and technology. Therefore, the challenge was to make the process of gathering, organization, and storage as labor-free as possible and to cover a wider range of fields in the information. Furthermore, when investigating cyber threats, a vast amount of information sources must be read when searching for relevant information before collecting and analyzing the necessary facts. However, it can be difficult to find where the necessary information lays. For example, if the information matches at the keyword level but is not the specific information you are looking for, you cannot use it and end up wasting all that effort. Therefore, another challenge is to appropriately narrow down sources of information to precisely identify the ones required. To solve these challenges, this paper presents a pipeline for extracting and summarizing cyber threat information, using the generative AI being developed by NEC, and an integrated pipeline for analyzing cyber threat-related information.
3. Policy on Achieving Automation of Cyber Threat Intelligence Generation Using Generative AI Considering the importance of strategic intelligence, it is most important to solve the following challenges: As a solution to the first challenge, a generative AI model can be used as a reasoning tool. Specifically, the generative AI model is instructed to answer using solely the information explicitly provided in the input from outside sources. A verification process that would check the accuracy of answers given by the generative AI model is also introduced. This process includes a variety of approaches, including verification through external sources of information as well as self-review and reasoning steps that are conducted through interaction with the AI model. As a solution to the second challenge, a preliminary processing step can be introduced before sending long texts to the generative AI model. In this phase, the original texts will be analyzed and only the contents that are highly relevant to the task at hand will be selected and extracted from the texts. This process of narrowing down the information can be adjusted upon request from the intelligence analysts and changed in accordance with the tasks to be automated.
When gathering and organizing information from a variety of non-structured sources of information such as reports, blogs, articles, news, and social media, the intelligent analysts must manually read and make sense of a huge number of documents and then convert the information into a structured format that is appropriate and easily accessible in the database. NEC’s pipeline for extracting and summarizing cyber threat information aims to automate these tasks and make them more efficient.
This pipeline consists of three elements ( Fig. 2 ). The downloader/parser converts input reports in a variety of unstructured formats such as HTML into a text-only format. For specific well-known sources of information, plugins to handle the formatting should be created in advance. These converted text documents are the only source of knowledge to be later used by the generative AI. The preprocessor performs iterative filtering to identify relevant information. First, input texts are divided into short paragraphs, and each paragraph is adjusted to have a couple of sentences overlap with the previous paragraph to ensure that the context will not be lost. Then, generative AI is used to select relevant information from the newly formed paragraphs. The specific types of relevant information required by the intelligence analysts can be easily configured with instructions that can be written in a natural language. For example, an instruction such as “Identify information about the economic impact of the attack” can be issued. Only the texts that are highly relevant to the task will be selected from the original texts and compiled into a group of relevant information. Finally, after receiving the information compiled in the previous step as input, the extractor stage extracts information by using generative AI and outputs it in a format that is consistent with the structured format to be used in the designated database. In this way, the extracted information is accumulated.
The pipeline for extracting and summarizing cyber threat information has two important features. One feature is that it is possible to discern relevant information and focus the generative AI-assisted extraction on these details. In fact, when manually analyzing threat reports, the intelligence analyst must determine what to omit and what to include at the time of extracting information while maintaining the report’s perspective. This determination generally involves considerations about the level of confidence as well as the level of detail of the information stated in the report. NEC’s generative AI technology can easily be instructed to automatically perform analyses and select relevant texts like the analysts do. Another feature is that the pipeline can be used to swiftly adjust the format of the extracted information before outputting it in accordance with the required task or the requirements of the final recipient platform. By adjusting the instructions given to generative AI, this can be achieved both in the case of extracting specific information from texts and in the case of summarizing information.
This pipeline is used to monitor a set of information sources and extract structured information. Specific information is extracted from texts and summarized, and events are classified in accordance with the storage format of the database. This reduces the time required for a junior analyst to gather and summarize threat information by 50% from approximately two hours to one hour ( Fig. 3 ).
The intelligence analyst’s job is to process information from various sources of information, extract appropriate events, and correlate events and data from different documents and tools. The pipeline for acquiring and analyzing cyber threat-related information is designed to support the process used by the analyst and automate the operation as much as possible. This pipeline consists of three different elements ( Fig. 4 ).
The search and retrieval module takes as input intelligence analysis queries expressed in natural language. For example, queries such as “Tell me about all attacks related to a specific threat actor” or “Is this file hash associated with threat actor X?” are accepted. Based on the first query, generative AI is utilized to perform retrieval augmented generation (RAG) over external sources of information. A variety of threat knowledge bases can be used as external sources for this purpose. For example, proprietary threat databases, knowledge graphs that represent knowledge connections in a graph structure, vector stores indexed in vector form, and trustworthy publicly available information on the web are some types of such information that might be included. These documents are input into the next module (relevance verification/extraction module) to verify if the searched documents are actually related to and relevant for the first query. If the relevance is confirmed, information from respective documents is extracted as a concise summary covering all the information related to the first query while keeping the original perspectives of the documents. Finally, the relevance is checked, and the summarized documents are passed to the analysis module. In this module, generative AI is used as a reasoner that correlates information in the relevant summaries and generates an answer to the first query. External tools can be called in at this stage to further confirm the inferred analysis results. For example, services that analyze malware hashes and verification using threat databases are available.
The main feature of this pipeline is to enable document analysis across highly reliable information sources by searching and processing a vast volume of information from a variety of threat databases and multiple documents. It identifies the relevance between the analysis query and documents and then summarizes the contents while maintaining the original perspective, making it possible to give a highly accurate answer. The accuracy will further improve by verifying the given answer with external tools or sources of information.
Currently, the pipeline for searching and analyzing cyber threat related information has been internally verified in NEC. Intelligence analysts can interact with a system that incorporates generative AI through a web interface to acquire the automatically captured information and the analysis results ( Fig. 5 ). Initial feedback indicates that it accelerates CTI operations while delivering accurate information.
In order to identify cybersecurity risks at an early stage, NEC’s intelligence analysts gather, accumulate, and analyze cybersecurity information on a daily basis. NEC is working to automate and improve efficiency, using generative AI to further expand its sources of information and strengthen its analytical capability. This paper presented an extraction and summarization pipeline for cyber threat information that can solve the challenges of hallucinations and long context for generative AI as well as a search and analysis pipeline for cyber threat-related information. We have verified some aspects and will continue to verify unproven areas. By promoting further incorporation of the analytical know-how developed by NEC, we plan to proceed with technological development to enable a more flexible and diverse threat analysis. NEC will continue through its initiatives in cyber intelligence to contribute to solving social issues and creating social value in the form of fairness and efficiency.
KAKUMARU Takahiro Director and certified information systems security professional (CISSP) Cyber Security Strategy Department TAKAHASHI Wataru Cyber Security Strategy Department KATSUSE Riku Cyber Security Strategy Department SIRACUSANO Giuseppe Principal Research Scientist NEC Laboratories Europe SANVITO Davide Senior Research Scientist NEC Laboratories Europe BIFULCO Roberto Senior Manager NEC Laboratories Europe This project implements a comprehensive pipeline for analyzing Cyber Threat Intelligence (CTI) reports using Natural Language Processing (NLP) and Large Language Models (LLMs). The pipeline automatically extracts indicators of compromise (IOCs), tags MITRE ATT&CK techniques, builds knowledge graphs from unstructured CTI reports, and provides an API for integration with security tools.
An automated cybersecurity threat intelligence analysis pipeline that extracts indicators of compromise (IOCs), maps MITRE ATT&CK techniques, and builds knowledge graphs from unstructured CTI reports using NLP and LLMs. Features cross-platform compatibility and RESTful API for integration. Every week, threat hunt teams are faced with a steady flow of blogs, advisories, and DFIR reports containing valuable intelligence about adversary behaviors, tactics, techniques, and procedures. The challenge is turning that intelligence into repeatable, behavior-based hunting logic quickly enough to be useful. Indicators of compromise still have value, but they age quickly. Behavioral detections give defenders a better way to look for how attackers operate, rather than relying only on what they leave behind.
To help solve this, Rapid7’s Internal Security team built an automated threat hunting pipeline that transforms threat intelligence reporting into structured, executable hunt plans. The pipeline uses large language models to extract adversary behaviors, map them to MITRE ATT&CK techniques, generate detection queries across multiple tools, and support analyst-ready briefings in minutes rather than days.
Harvested Online Documentation & Reference Sources • https://blog.adobe.com/security/building-an-agentic-ai-powered-threat-intelligence-platform • https://arxiv.org/html/2410.20287v1 • https://sanjanb.github.io/work/cti-nlp-system/ • https://www.nec.com/en/global/techrep/journal/g23/n02/230207.html • https://github.com/AnandBinuArjun/threat-intelligence-cti-analysis • https://www.rapid7.com/blog/post/ai-automated-threat-hunting-turns-threat-intelligence-into-executable-hunt-plans/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
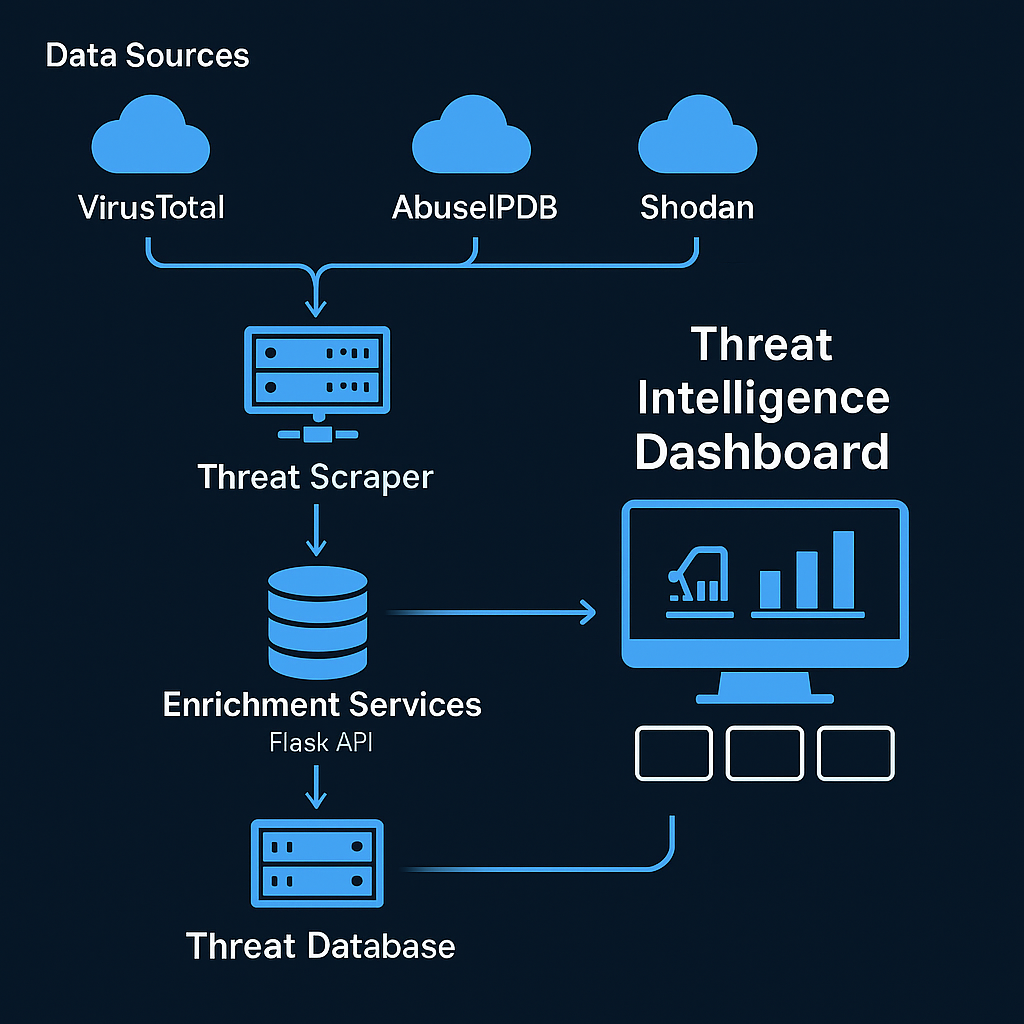
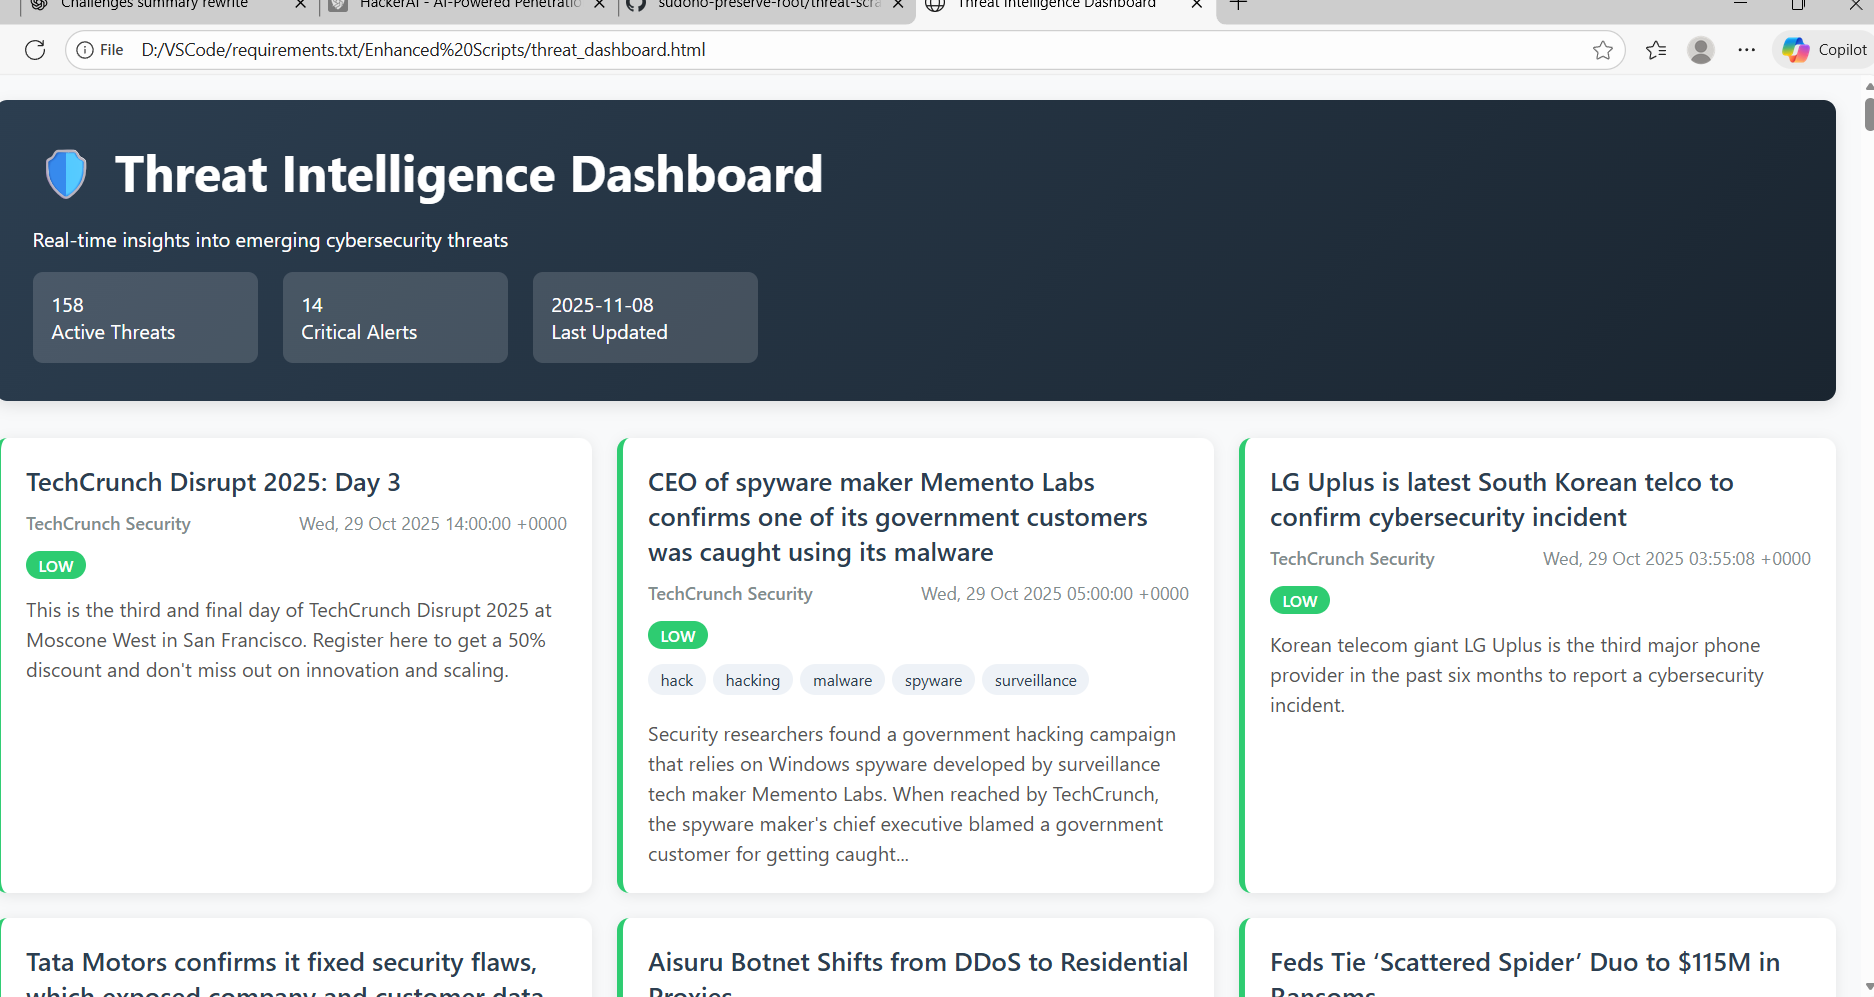
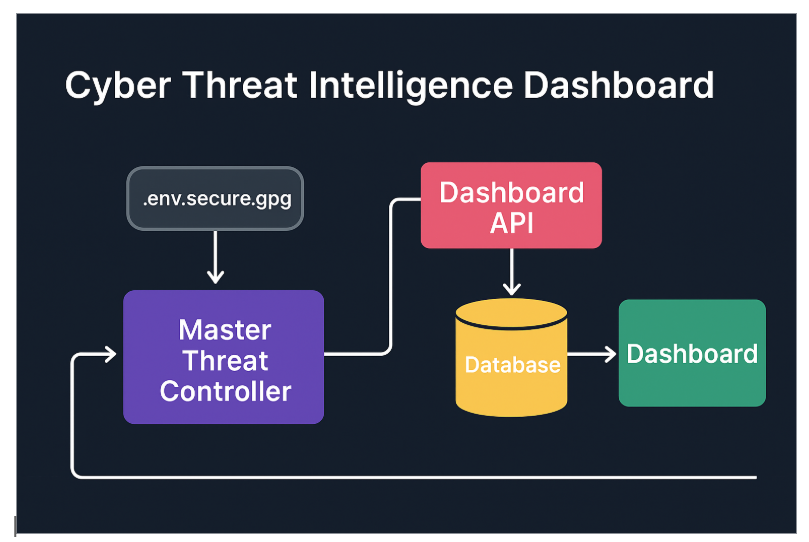
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Automated Threat Intelligence Extraction From Security Blogs.
[*] Metasploit Scan Running on Target Subnet for Automated Threat Intelligence Extraction From Security Blogs... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |