Complete Technical Paper Content — Automated XSS Vulnerability Detector Tool Using Python
Overview & System Context
Automated Xss Vulnerability Detector Tool Using Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9524 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background This is a list of notable tools for static program analysis (program analysis is a synonym for code analysis).
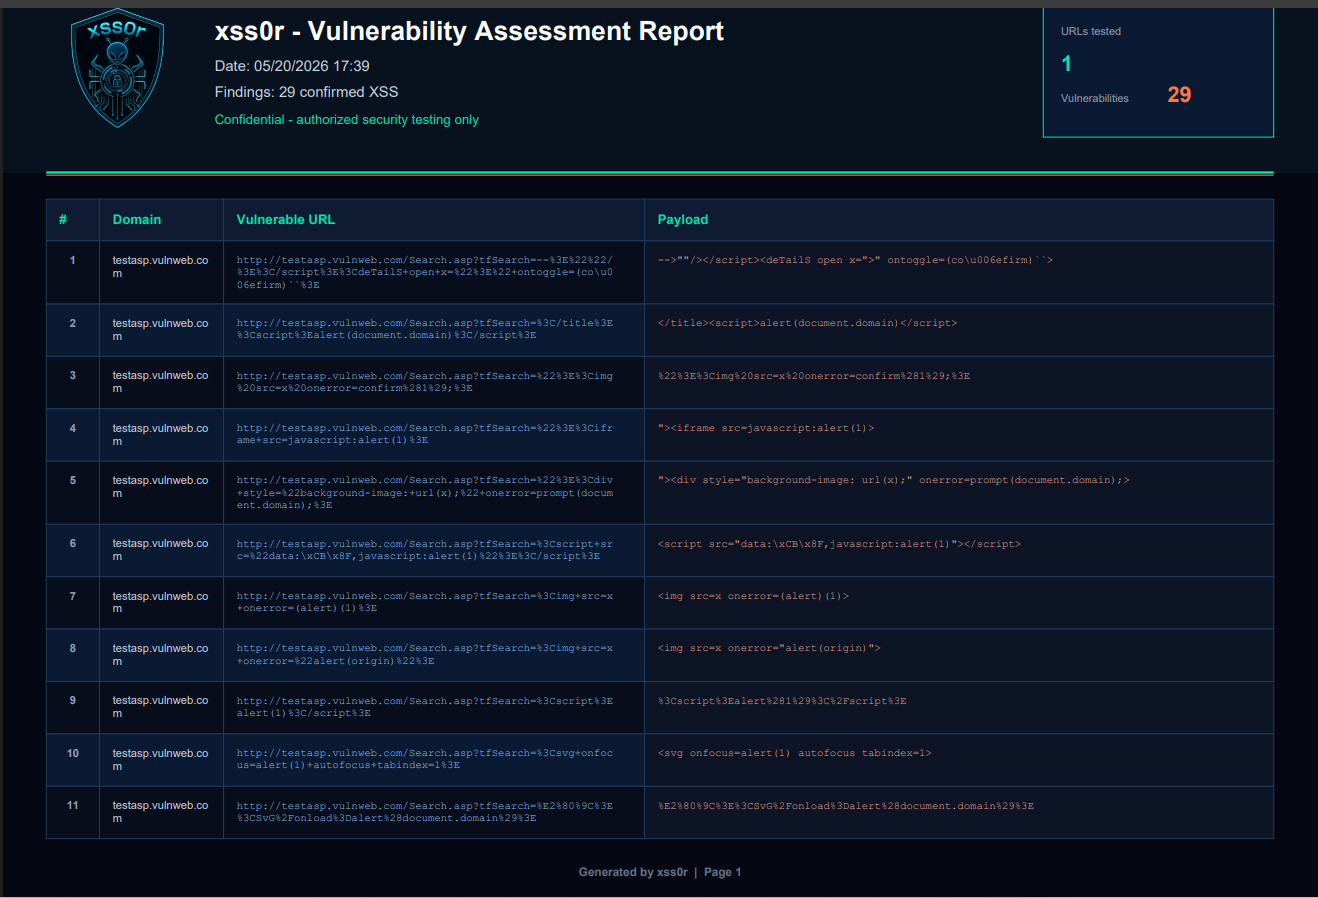
CodePeer ConQAT Fluctuat LDRA Testbed MALPAS Polyspace SofCheck Inspector Squore Understand Astree Axivion Suite (Bauhaus) BLAST Clang Coccinelle Coverity CPAchecker Cppcheck Cppdepend Cpplint ECLAIR Eclipse Fluctuat Frama-C GCC Helix QAC Facebook Infer Klocwork Lint LDRA Testbed Parasoft C/C++test PC-lint Plus Polyspace PVS-Studio SLAM project Sparse SonarQube Splint Understand Visual Studio Axivion Suite (Bauhaus) Code Dx CodeScene CodeQL Coverity Fluid Attacks Kiuwan Klocwork .NET Compiler Platform PVS-Studio SonarQube Sotoarc StyleCop Squore Understand Visual Studio Figure 1: xss0r – Advanced XSS Scanner & Blind XSS Automation Tool for Bug Bounty ...
Coverity Facebook Infer Fluid Attacks Klocwork LDRA Testbed PMD RIPS Semgrep SourceMeter Understand Axivion Suite (Bauhaus) Code Dx CodeScene PMD SofCheck Inspector SonarQube SourceMeter Understand Astrée – finds all potential runtime errors by abstract interpretation, can prove the absence of runtime errors and can prove functional assertions; tailored towards safety-critical C code (e.g. avionics). CodePeer – Statically determines and documents pre- and post-conditions for Ada subprograms; statically checks preconditions at all call sites. ECLAIR – Uses formal methods-based static code analysis techniques such as abstract interpretation and model checking combined with constraint satisfaction techniques to detect or prove the absence of certain run time errors in source code. ESC/Java and ESC/Java2 – Based on Java Modeling Language, an enriched version of Java Frama-C – An open-source analysis framework for C, based on the ANSI/ISO C Specification Language (ACSL). Its main techniques include abstract interpretation, deductive verification and runtime monitoring. KeY – analysis platform for Java based on theorem proving with specifications in the Java Modeling Language; can generate test cases as counterexamples; stand-alone GUI or Eclipse integration MALPAS – A formal methods tool that uses directed graphs and regular algebra to prove that software under analysis correctly meets its mathematical specification. Polyspace – Uses abstract interpretation, a formal methods based technique, to detect and prove the absence of certain run time errors in source code for C/C++, and Ada SPARK Toolset including the SPARK Examiner – Based on the SPARK language, a subset of Ada.
Space debris (also known as space junk, space pollution, space waste, space trash, space garbage, or cosmic debris) are defunct human-made objects in space – principally in Earth orbit – which no longer serve a useful function. These include derelict spacecraft (nonfunctional spacecraft and abandoned launch vehicle stages), mission-related debris, and fragmentation debris from the breakup of derelict rocket bodies and spacecraft. In addition to derelict human-made objects left in orbit, space debris includes fragments from disintegration, erosion, or collisions; solidified liquids expelled from spacecraft; unburned particles from solid rocket motors; and even paint flecks. Space debris represents a risk to spacecraft. Space debris is typically a negative externality. It creates an external cost on others from the initial action to launch or use a spacecraft in near-Earth orbit, a cost that is typically not taken into account nor fully accounted for by the launcher or payload owner.
Several spacecraft, both crewed and un-crewed, have been damaged or destroyed by space debris. The measurement, mitigation, and potential removal of debris is conducted by some participants in the space industry. As of April 2025, the European Space Agency's Space Environment statistics reported 40,230 artificial objects in orbit above the Earth regularly tracked by Space Surveillance Networks and maintained in their catalogue. However, these are just the objects large enough to be tracked and in an orbit that makes tracking possible. Satellite debris that is in a Molniya orbit, such as the Kosmos Oko series, might be too high above the Northern Hemisphere to be tracked. As of January 2019, more than 128 million pieces of debris smaller than 1 cm (0.4 in), about 900,000 pieces of debris 1–10 cm, and around 34,000 of pieces larger than 10 cm (3.9 in) were estimated to be in orbit around the Earth. When the smallest objects of artificial space debris (paint flecks, solid rocket exhaust particles, etc.) are grouped with micrometeoroids, they are together sometimes referred to by space agencies as MMOD (Micrometeoroid and Orbital Debris). Collisions with debris have become a hazard to spacecraft. The smallest objects cause damage akin to sandblasting, especially to solar panels and optics like telescopes or star trackers that cannot easily be protected by a ballistic shield. Below 2,000 km (1,200 mi), pieces of debris are denser than meteoroids. Most are dust from solid rocket motors, surface erosion debris like paint flakes, and frozen coolant from Soviet nuclear-powered satellites. For comparison, the International Space Station (ISS) orbits in the 300–400 kilometres (190–250 mi) range, while the two most recent large debris events, the 2007 Chinese antisatellite weapon test and the 2009 satellite collision, occurred at 800 to 900 kilometres (500 to 560 mi) altitude. The ISS has Whipple shielding to resist damage from small MMOD.
However, known debris with a collision chance over 1/10,000 are avoided by maneuvering the station. According to a report published in January 2025, scientists are encouraging vigilance around closing airspace more often to avoid collisions between airline flights and space debris reentering the earth's atmosphere amid an increasing volume of both. Following a destructive event, the explosion of SpaceX's Starship Flight 7 on January 16, 2025, the US Federal Aviation Administration (FAA) slowed air traffic in the area where debris was falling. This prompted several aircraft to request diversion because of low fuel levels while they were holding outside the Debris Response Area.
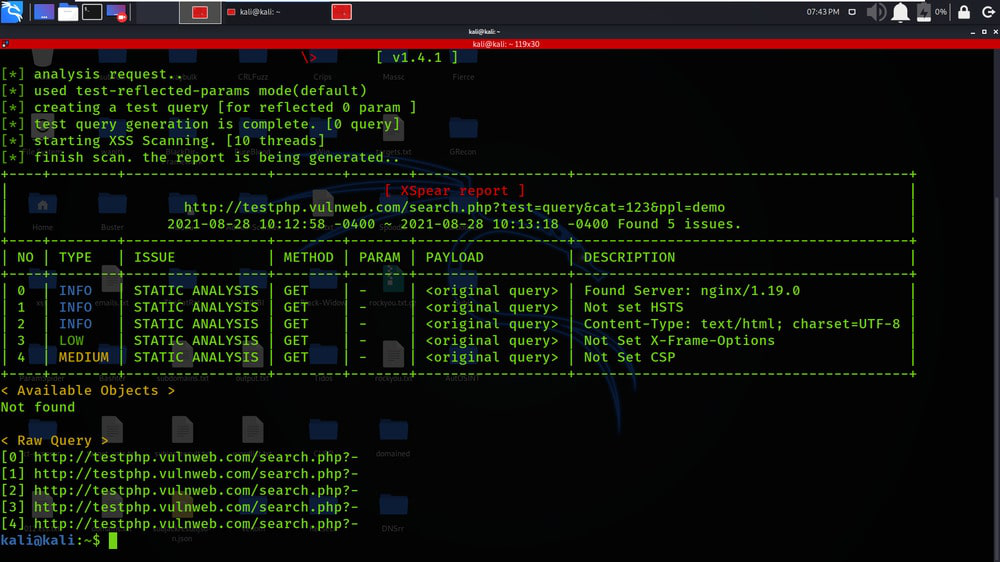
Figure 2: Xss Detection Tools at Germaine Dunham blog Space debris began to accumulate in Earth orbit with the launch of the first artificial satellite, Sputnik 1, launched into orbit in October 1957. But even before this event, humans might have produced ejecta that became space debris, as in the August 1957 Pascal B test. Space debris for example was ejected in 1957 purposefully from an Aerobee launch system in a likely failed attempt to reach for the first time escape velocity from Earth, and therefore space beyond Earth. Going back further, natural ejecta from Earth has entered orbit. After the launch of Sputnik, the North American Aerospace Defense Command (NORAD) began compiling a database (the Space Object Catalog) of all known rocket launches and objects reaching orbit, including satellites, protective shields and upper-stages of launch vehicles. NASA later published modified versions of the database in two-line element sets, and beginning in the early 1980s, they were republished in the CelesTrak bulletin board system.
NORAD trackers who fed the database were aware of other objects in orbit, many of which were the result of in-orbit explosions. Some were deliberately caused during anti-satellite weapon (ASAT) testing in the 1960s, and others were the result of rocket stages blowing up in orbit as leftover propellant expanded and ruptured their tanks. More detailed databases and tracking systems were gradually developed, including Gabbard diagrams, to improve the modeling of orbital evolution and decay. When the NORAD database became publicly available during the 1970s, techniques developed for the asteroid-belt were applied to the study of known artificial satellite objects. Time and natural gravitational/atmospheric effects help to clear space debris. A variety of technological approaches have also been proposed, though most have not been implemented. A number of scholars have observed that systemic factors, political, legal, economic, and cultural, are the greatest impediment to the cleanup of near-Earth space. There has been little commercial incentive to reduce space debris since the associated cost does not accrue to the entity producing it. Rather, the cost falls to all users of the space environment who benefit from space technology and knowledge. A number of suggestions for increasing incentives to reduce space debris have been made. These would encourage companies to see the economic benefit of reducing debris more aggressively than existing government mandates require. In 1979, NASA founded the Orbital Debris Program to research mitigation measures for space debris in Earth orbit.
During the 1980s, NASA and other US groups attempted to limit the growth of debris. One trial solution was implemented by McDonnell Douglas in 1981 for the Delta launch vehicle by having the booster move away from its payload and vent any propellant remaining in its tanks. This eliminated one source for pressure buildup in the tanks which had previously caused them to explode and create additional orbital debris. Other countries were slower to adopt this measure and, due especially to a number of launches by the Soviet Union, the problem grew throughout the decade. A new battery of studies followed as NASA, NORAD, and others attempted to better understand the orbital environment, with each adjusting the number of pieces of debris in the critical-mass zone upward. Although in 1981 (when Schefter's article was published) the number of objects was estimated at 5,000, new detectors in the Ground-based Electro-Optical Deep Space Surveillance system found new objects. By the late 1990s, it was thought that most of the 28,000 launched objects had already decayed and about 8,500 remained in orbit. By 2005 this was adjusted upward to 13,000 objects remaining in orbit, and a 2006 study increased the number to 19,000 as a result of an ASAT and a satellite collision. In 2011, NASA said that 22,000 objects were being tracked.
A 2006 NASA model suggested that if no new launches took place, the environment would retain the then-known population until about 2055, when it would increase on its own. Richard Crowther of Britain's Defence Evaluation and Research Agency said in 2002 that he believed the cascade would begin about 2015. The US National Academy of Sciences, summarizing the professional view, noted widespread agreement that two bands of LEO space – 900 to 1,000 km (620 mi) and 1,500 km (930 mi) – were already past critical density. In the 2009 CEAS European Air and Space Conference, University of Southampton researcher Hugh Lewis predicted that the threat from space debris would rise 50 percent in the next decade and quadruple in the next 50 years. As of 2009, more than 13,000 close calls were tracked weekly. A 2011 report by the US National Research Council warned NASA that the amount of orbiting space debris was at a critical level. According to some computer models, the amount of space debris "has reached a tipping point, with enough currently in orbit to continually collide and create even more debris, raising the risk of spacecraft failures." The report called for international regulations limiting debris and research of disposal methods.
In the orbits nearest to Earth – less than 2,000 km (1,200 mi) orbital altitude, referred to as low-Earth orbit (LEO) – there have traditionally been few "universal orbits" that keep a number of spacecraft in particular rings (in contrast to GEO, a single orbit that is widely used by over 500 satellites). There is currently 85% pollution in LEO (Low Earth Orbit). This was beginning to change in 2019, and several companies began to deploy the early phases of satellite internet constellations, which will have many universal orbits in LEO with 30 to 50 satellites per orbital plane and altitude. Traditionally, the most populated LEO orbits have been a number of Sun-synchronous satellites that keep a constant angle between the Sun and the orbital plane, making Earth observation easier with consistent sun angle and lighting. Sun-synchronous orbits are polar, meaning they cross over the polar regions. LEO satellites orbit in many planes, typically up to 15 times a day, causing frequent approaches between objects. The density of satellites – both active and derelict – is much higher in LEO. Orbits are affected by gravitational perturbations (which in LEO include unevenness of the Earth's gravitational field due to variations in the density of the planet), and collisions can occur from any direction. The average impact speed of collisions in Low Earth Orbit is 10 km/s with maximums reaching above 14 km/s due to orbital eccentricity. The 2009 satellite collision occurred at a closing speed of 11.7 km/s (26,000 mph), creating over 2,000 large debris fragments. These debris cross many other orbits and increase debris collision risk. It is theorized that a sufficiently large collision of spacecraft could potentially lead to a cascade effect, or even make some particular low Earth orbits effectively unusable for long term use by orbiting satellites, a phenomenon known as the Kessler syndrome. The theoretical effect is projected to be a theoretical runaway chain reaction of collisions that could occur, exponentially increasing the number and density of space debris in low-Earth orbit, and has been hypothesized to ensue beyond some critical density. Crewed space missions are mostly at 400 km (250 mi) altitude and below, where air drag helps clear zones of fragments. The upper atmosphere is not a fixed density at any particular orbital altitude; it varies as a result of atmospheric tides and expands or contracts over longer time periods as a result of space weather. These longer-term effects can increase drag at lower altitudes; the 1990s expansion was a factor in reduced debris density. Another factor was fewer launches by Russia; the Soviet Union made most of their launches in the 1970s and 1980s.
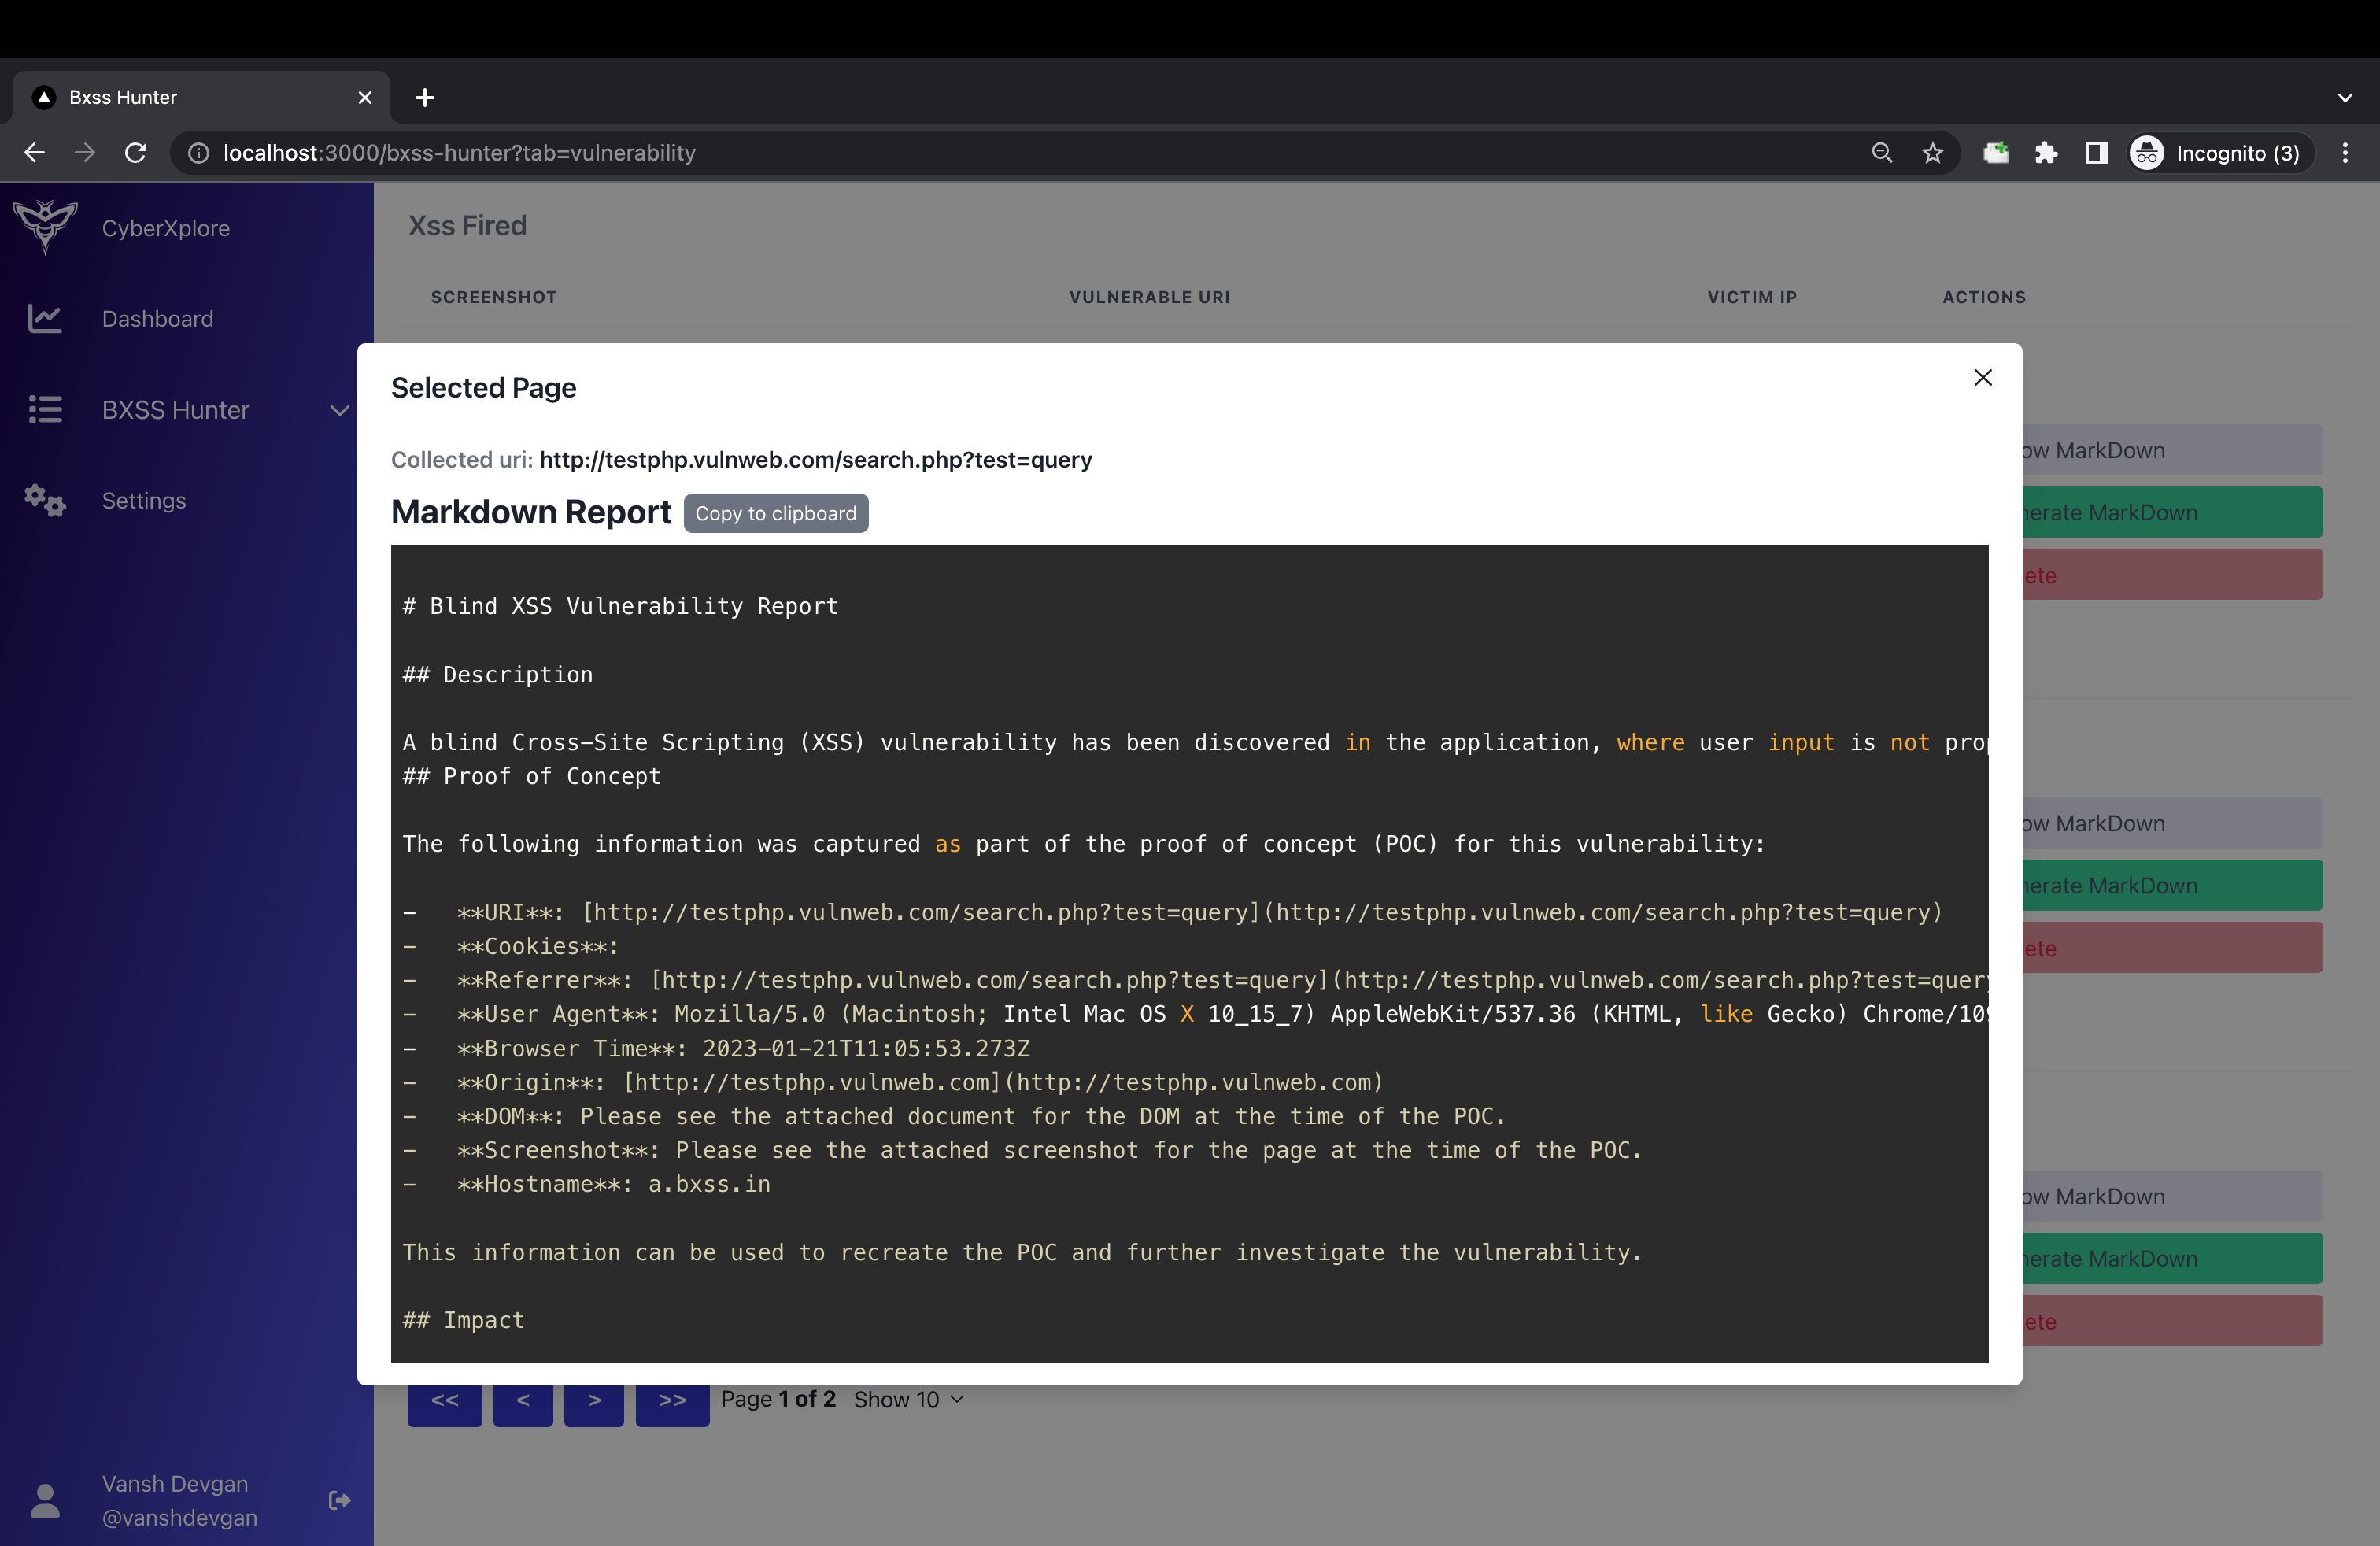
Figure 3: BXSS Hunter | The XSS hunter's secret weapon At higher altitudes, where air drag is less significant, orbital decay takes longer. Slight atmospheric drag, lunar perturbations, Earth's gravity perturbations, solar wind, and solar radiation pressure can gradually bring debris to lower altitudes (where it decays), but at very high altitudes this may take centuries. Although high-altitude orbits are less commonly used than LEO and the onset of the problem is slower, the numbers progress toward the critical threshold more quickly. Many communications satellites are in geostationary orbits (GEO), clustering over specific targets and sharing the same orbital path.
Although velocities are low between GEO objects, when a satellite becomes derelict (such as Telstar 401) it assumes a geosynchronous orbit; its orbital inclination increases about 0.8° and its speed increases about 160 km/h (99 mph) per year. Impact velocity peaks at about 1.5 km/s (0.93 mi/s). Orbital perturbations cause longitude drift of the inoperable spacecraft and precession of the orbital plane. Close approaches (within 50 meters) are estimated at one per year. The collision debris pose less short-term risk than from a LEO collision, but the satellite would likely become inoperable. Large objects, such as solar-power satellites, are especially vulnerable to collisions. Although the ITU now requires proof a satellite can be moved out of its orbital slot at the end of its lifespan, studies suggest this is insufficient. Since GEO orbit is too distant to accurately measure objects under 1 m (3 ft 3 in), the nature of the problem is not well known. Satellites could be moved to empty spots in GEO, requiring less maneuvering and making it easier to predict future motion. Satellites or boosters in other orbits, especially stranded in geostationary transfer orbit, are an additional concern due to their typically high crossing velocity. Despite efforts to reduce risk, spacecraft collisions have occurred. The European Space Agency telecom satellite Olympus-1 was struck by a meteoroid on 11 August 1993 and eventually moved to a graveyard orbit. On 29 March 2006, the Russian Express-AM11 communications satellite was struck by an unknown object and rendered inoperable; its engineers had enough contact time with the satellite to send it into a graveyard orbit.
In 1958, the United States launched Vanguard I into a medium Earth orbit (MEO). As of October 2009, it, the upper stage of Vanguard 1's launch rocket and associated piece of debris, are the oldest surviving artificial space objects still in orbit and are expected to be until after the year 2250. As of May 2022, the Union of Concerned Scientists listed 5,465 operational satellites from a known population of 27,000 pieces of orbital debris tracked by NORAD. Occasionally satellites are left in orbit when they are no longer useful. Many countries require that satellites go through passivation at the end of their life. The satellites are then either boosted into a higher, graveyard orbit or a lower, short-term orbit. Nonetheless, satellites that have been properly moved to a higher orbit have an eight-percent probability of puncture and coolant release over a 50-year period. The coolant freezes into droplets of solid sodium-potassium alloy, creating more debris. Despite the use of passivation, or prior to its standardization, many satellites and rocket bodies have exploded or broken apart in orbit. In February 2015, for example, the USAF Defense Meteorological Satellite Program Flight 13 (DMSP-F13) exploded in orbit, creating at least 149 debris objects, which were expected to remain in orbit for decades. Later that same year, NOAA-16, which had been decommissioned after an anomaly in June 2014, broke apart in orbit into at least 275 pieces. For older programs, such as the Soviet-era Meteor 2 and Kosmos satellites, design flaws resulted in numerous break-ups – at least 68 by 1994 – following decommissioning, resulting in more debris.
2. System Architecture & Core Working Principles An in-orbit fragmentation occurs when an artificial object in space unexpectedly breaks apart or sheds material outside its intended mission profile, serving as the primary generator of catalogued space debris. Historically, the majority of fragmentation events were caused by the sudden explosion of spent rocket upper stages and decommissioned satellites due to internal pressure build-ups or residual propellants. However, deliberate weapon testing and accidental hypervelocity impacts are also significant drivers of the orbital debris population.
A significant portion of debris is due to rocket upper stages (e.g. the Inertial Upper Stage) breaking up due to decomposition of unvented fuel. The first such instance involved the launch of the Transit-4a satellite in 1961. Two hours after insertion into orbit, the Ablestar upper stage exploded. Even boosters that do not break apart can be a problem. A major known impact event involved an intact Ariane booster. Although NASA and the United States Air Force now require upper-stage passivation, other launchers – such as the Chinese and Russian space agencies – do not. Lower stages, like the Space Shuttle's solid rocket boosters or the Apollo program's Saturn IB launch vehicles, do not reach orbit. Examples: Two Japanese H-2A rockets broke up in 2006. A Russian Briz-M booster stage exploded in orbit over South Australia on 19 February 2007. Launched on 28 February 2006 carrying an Arabsat-4A communications satellite, it malfunctioned before it could use up its propellant. Although the explosion was captured on film by astronomers, due to the orbit path the debris cloud has been difficult to measure with radar. By 21 February 2007, over 1,000 fragments were identified. A 14 February 2007 breakup was recorded by Celestrak. Another Briz-M broke up on 16 October 2012 after a failed 6 August Proton-M launch.
The amount and size of the debris was unknown. The second stage of the Zenit-2, called the SL-16 by western governments, along with the second stages of the Vostok and Kosmos launch vehicles, make up about 20% of the total mass of launch debris in Low Earth Orbit (LEO). An analysis that determined the 50 "statistically most concerning" debris objects in low Earth orbit determined that the top 20 were all Zenit-2 upper stages. A Delta II rocket used to launch NASA's 1989 COBE spacecraft exploded on December 3, 2006. This occurred even though its residual fuel had already been vented to space. In 2018–2019, three different Atlas V Centaur second stages broke up. In December 2020, scientists confirmed that a previously detected near-Earth object, 2020 SO, was rocket booster space junk launched in 1966 orbiting Earth and the Sun. At least eight Delta rockets have contributed orbital debris in the Sun-synchronous low Earth orbit environment. The variant of the Delta upper stage that was used in the 1970s was found to be prone to in-orbit explosions. Starting in 1981, depletion burns – to get rid of excess propellant – became standard and no Delta Rocket Bodies launched after 1981 experienced severe fragmentations afterward, but some of those launched prior to 1981 continued to explode. In 1991, the Delta 1975-052B fragmented, 16 years after launch, demonstrating the resilience of the propellent.
In addition to the accidental creation of debris, some has been made intentionally through the deliberate destruction of satellites. This has been done as a test of anti-satellite or anti-ballistic missile technology, or to prevent a sensitive satellite from being examined by a foreign power. The United States has conducted over 30 anti-satellite weapons tests (ASATs), the Soviet Union/Russia has performed at least 27, China has performed 10 and India has performed at least one. The most recent ASATs were the Chinese interception of FY-1C, Russian trials of its PL-19 Nudol, the American interception of USA-193 and India's interception of an unstated live satellite. A former source of debris was anti-satellite weapons (ASATs) testing by the US and Soviet Union during the 1960s and 1970s. North American Aerospace Defense Command (NORAD) only collected data for Soviet tests, and debris from US tests were identified subsequently. By the time the debris problem was understood, widespread ASAT testing had ended. The US Program 437 was shut down in 1975. The US restarted their ASAT programs in the 1980s with the Vought ASM-135 ASAT. A 1985 test destroyed a 1-tonne (2,200 lb) satellite orbiting at 525 km (326 mi), creating thousands of pieces of debris larger than 1 cm (0.39 in). At this altitude, atmospheric drag decayed the orbit of most of the debris within a decade. A de facto moratorium followed the test.
China's government was condemned for the military implications and the amount of debris from a 2007 anti-satellite missile test, the largest single space debris incident in history (creating over 2,300 pieces golf-ball size or larger, over 35,000 1 cm (0.4 in) or larger, and one million pieces 1 mm (0.04 in) or larger). The target satellite orbited between 850 km (530 mi) and 882 km (548 mi), the portion of near-Earth space most densely populated with satellites. Since atmospheric drag is low at that altitude, the debris is slow to return to Earth, and in June 2007 NASA's Terra environmental spacecraft maneuvered to avoid impact from the debris. Brian Weeden, a US Air Force officer and Secure World Foundation staff member, noted that the 2007 Chinese satellite explosion created more than 3,000 separate objects of orbital debris that then required tracking. On 20 February 2008, the US launched an SM-3 missile from the USS Lake Erie to destroy a defective US spy satellite thought to be carrying 450 kg (1,000 lb) of toxic hydrazine propellant. The event occurred at about 250 km (155 mi). The missile was aimed to minimize the amount of debris, which (according to Pentagon Strategic Command chief Kevin Chilton) had decayed by early 2009. On 27 March 2019, Indian Prime Minister Narendra Modi announced that India shot down one of its own LEO satellites with a ground-based missile. He stated that the operation, part of Mission Shakti, would defend the country's interests in space. Afterwards, US Air Force Space Command announced they were tracking 270 new pieces of debris but expected the number to grow as data collection continues. On 15 November 2021, the Russian Defense Ministry destroyed Kosmos 1408 orbiting at around 450 km, creating "more than 1,500 pieces of trackable debris and hundreds of thousands of pieces of un-trackable debris" according to the US State Department.
Space junk can be a hazard to active satellites and spacecraft. It has been suggested that Earth orbit could even become impassable if the risk of collision becomes too great, a phenomenon known as Kessler syndrome. However, since the risk to spacecraft increases with exposure to high debris densities, it is more accurate to say that LEO would be rendered unusable by orbiting craft. The threat to craft passing through LEO to reach a higher orbit would be much lower owing to the short time span of the crossing.
Although spacecraft are typically protected by Whipple shields, solar panels, which are exposed to the Sun, wear from low-mass impacts. Even small impacts can produce a cloud of plasma which is an electrical risk to the panels. Satellites are believed to have been destroyed by micrometeorites and small orbital debris (MMOD). The earliest suspected loss was of Kosmos 1275, which disappeared on 24 July 1981, a month after launch. Kosmos contained no volatile fuel, therefore, there appeared to be nothing internal to the satellite which could have caused the destructive explosion. However, the case has not been proven and another hypothesis forwarded is that the battery exploded. Tracking showed it broke into 300 objects. Many impacts have been confirmed since. For example, on 24 July 1996, the French microsatellite Cerise was hit by fragments of an Ariane 1 H-10 upper-stage booster which exploded in November 1986. On 29 March 2006, the Russian Ekspress-AM11 communications satellite was struck by an unknown object and rendered inoperable. On 13 October 2009, Terra suffered a single battery cell failure anomaly and a battery heater control anomaly which were subsequently considered likely the result of an MMOD strike. On 12 March 2010, Aura lost power from one-half of one of its 11 solar panels which was attributed to an MMOD strike. On 22 May 2013, GOES 13 was hit by an MMOD which caused it to lose track of the stars that it used to maintain an operational attitude. It took nearly a month for the spacecraft to return to operation. The first major satellite collision occurred on 10 February 2009. The 950 kg (2,090 lb) derelict satellite Kosmos 2251 and the operational 560 kg (1,230 lb) Iridium 33 collided, 500 mi (800 km) over northern Siberia. The relative speed of impact was about 11.7 km/s (7.3 mi/s), or about 42,120 km/h (26,170 mph). Both satellites were destroyed, creating thousands of pieces of new smaller debris, with legal and political liability issues unresolved even years later. On 22 January 2013, BLITS (a Russian laser-ranging satellite) was struck by debris suspected to be from the 2007 Chinese anti-satellite missile test, changing both its orbit and rotation rate. Satellites sometimes perform Collision Avoidance Maneuvers and satellite operators may monitor space debris as part of maneuver planning. For example, in January 2017, the European Space Agency altered the orbit of one of its three Swarm mission spacecraft, based on data from the US Joint Space Operations Center, to lower the risk of collision from Cosmos-375, a derelict Russian satellite.
From the early shuttle missions, NASA used NORAD space monitoring capabilities to assess the shuttle's orbital path for debris. In the 1980s, this consumed a large proportion of NORAD capacity. The first collision-avoidance maneuver occurred during STS-48, in September 1991; a seven-second thruster burn to avoid debris from the derelict satellite Kosmos 955. Similar maneuvers were executed on missions 53, 72 and 82. One of the earliest events to publicize the debris problem occurred on Space Shuttle Challenger's second flight, STS-7. A fleck of paint struck its front window, creating a pit over 1 mm (0.04 in) wide. On STS-59 in 1994, Endeavour's front window was pitted about half its depth. Minor debris impacts increased from 1998. Window chipping and minor damage to thermal protection system tiles (TPS) were already common by the 1990s.
The Shuttle was later flown tail-first to take a greater proportion of the debris load on the engines and rear cargo bay, which are not used in orbit or during descent, and thus are less critical for post-launch operation. When flying attached to the ISS, a shuttle was flipped around so the better-armoured station shielded the orbiter. A NASA 2005 study concluded that debris accounted for approximately half of the overall risk to the Shuttle. An executive-level decision to proceed was required if the catastrophic impact was more likely than 1 in 200. On a normal (low-orbit) mission to the ISS, the risk was approximately 1 in 300, but the Hubble telescope repair mission was flown at the higher orbital altitude of 560 km (350 mi) where the risk was initially calculated at a 1-in-185 (due in part to the 2009 satellite collision). A re-analysis with better debris numbers reduced the estimated risk to 1 in 221, and the mission went ahead. Debris incidents continued on later Shuttle missions. During STS-115 in 2006, a fragment of circuit board bored a small hole through the radiator panels in the US space shuttle Atlantis cargo bay. On STS-118 in 2007, debris blew a bullet-like hole through the US space shuttle Endeavour radiator panel.
The Kessler syndrome, proposed by NASA scientist Donald J. Kessler in 1978, is a theoretical scenario in which the density of objects in low Earth orbit (LEO) is high enough that collisions between objects could cause a cascade effect where each collision generates space debris that increases the likelihood of further collisions. He further theorized that one implication, if this were to occur, is that the distribution of debris in orbit could render space activities and the use of satellites in specific orbital ranges economically impractical for many generations. The growth in the number of objects as a result of the late-1990s studies sparked debate in the space community on the nature of the problem and the earlier dire warnings.
According to Kessler's 1991 derivation and 2001 updates, the LEO environment in the 1,000 km (620 mi) altitude range should be cascading. However, only one major satellite collision incident occurred: the 2009 satellite collision between Iridium 33 and Kosmos 2251. The lack of obvious short-term cascading has led to speculation that the original estimates overstated the problem. According to Kessler in 2010, however, a cascade may not be obvious until it is well advanced, which might take years.
Most debris burns up in the atmosphere, or splashes into the ocean. About 1 ton of debris reaches earth per week, as of 2026. In 2025, the U.S. Space Force issued alerts for nearly 820 objects entering the atmosphere. This was up from 110 objects in 2015. Experts expect these numbers will increase along with the number of rocket launches: 2025 had 300 launches while 2015 had less than 100. There is only one documented case of a person being hit by debris, a piece of a Delta II rocket fuel tank struck a woman who survived uninjured. Debris burning up in the atmosphere contributes to air pollution. United Nations treaties, last updated in 2007 and non-binding, govern liability for space debris that hurts people or damages property.
Returned space hardware is a valuable source of information on the directional distribution and composition of the (sub-millimetre) debris flux. The LDEF satellite deployed by mission STS-41-C Challenger and retrieved by STS-32 Columbia spent 68 months in orbit to gather debris data. The EURECA satellite, deployed by STS-46 Atlantis in 1992 and retrieved by STS-57 Endeavour in 1993, was also used for debris study. The solar arrays of the Hubble space telescope were returned by missions STS-61 Endeavour and STS-109 Columbia, and the impact craters were studied by the ESA to validate its models.
Materials returned from Mir were also studied, notably the Mir Environmental Effects Payload (which also tested materials intended for the ISS). A debris cloud resulting from a single event is studied with scatter plots known as Gabbard diagrams, where the perigee and apogee of fragments are plotted with respect to their orbital period. Gabbard diagrams of the early debris cloud prior to the effects of perturbations, if the data were available, are reconstructed. They often include data on newly observed, as yet uncatalogued fragments. Gabbard diagrams can provide insights into the features of the fragmentation, the direction and point of impact.
An average of about one tracked object per day has been dropping out of orbit for the past 50 years, averaging almost three objects per day at solar maximum (due to the heating and expansion of the Earth's atmosphere creating more drag), but one about every three days at solar minimum, usually five and a half years later. In addition to natural atmospheric effects, corporations, academics and government agencies have proposed plans and technology to deal with space debris, but as of November 2014, most of these are theoretical, and there is no business plan for debris reduction. A number of scholars have also observed that institutional factors – political, legal, economic, and cultural "rules of the game" – are the greatest impediment to the cleanup of near-Earth space. There is little commercial incentive to act, since costs are not assigned to polluters, though a number of technological solutions have been suggested. However, effects to date are limited. In the US, governmental bodies have been accused of backsliding on previous commitments to limit debris growth, "let alone tackling the more complex issues of removing orbital debris." The different methods for removal of space debris have been evaluated by the Space Generation Advisory Council, including French astrophysicist Fatoumata Kébé. In May 2024, a NASA report from the Office of Technology, Policy, and Strategy introduced new methods for addressing orbital debris. The report, titled Cost and Benefit Analysis of Mitigating, Tracking, and Remediating Orbital Debris, provided a comprehensive analysis comparing the cost-effectiveness of over ten different actions, including shielding spacecraft, tracking smaller debris, and removing large debris. By evaluating these measures in economic terms, the study aims to inform cost-effective strategies for debris management, highlighting that methods like rapid deorbiting of defunct spacecraft can significantly reduce risks in space.
Numerical and mathematical models are used to describe the evolution of the orbital debris environment and to evaluate the effectiveness of mitigation measures. Depending on their purpose, models may estimate the debris flux encountered by spacecraft, simulate the long-term evolution of the orbital population, or reproduce the behaviour of individual objects and fragmentation events. They are widely used by space agencies and research institutions to assess future debris scenarios, compare mitigation strategies and support the development of space sustainability policies. Modern debris models combine observational catalogues, orbital propagation, collision probability estimation, fragmentation models and projected launch traffic to forecast the long-term evolution of the space environment.
3. Software Implementation, Frameworks & Protocols There is no international treaty minimizing space debris. However, the United Nations Committee on the Peaceful Uses of Outer Space (COPUOS) published voluntary guidelines in 2007, using a variety of earlier national regulatory attempts at developing standards for debris mitigation. As of 2008, the committee was discussing international "rules of the road" to prevent collisions between satellites. By 2013, a number of national legal regimes existed, typically instantiated in the launch licenses that are required for a launch in all spacefaring nations. The US issued a set of standard practices for civilian (NASA) and military (DoD and USAF) orbital-debris mitigation in 2001. The standard envisioned disposal for final mission orbits in one of three ways: 1) atmospheric reentry where even with "conservative projections for solar activity, atmospheric drag will limit the lifetime to no longer than 25 years after completion of mission;" 2) maneuver to a "storage orbit:" move the spacecraft to one of four very broad parking orbit ranges (2,000–19,700 km (1,200–12,200 mi), 20,700–35,300 km (12,900–21,900 mi), above 36,100 km (22,400 mi), or out of Earth orbit completely and into any heliocentric orbit; 3) "Direct retrieval: Retrieve the structure and remove it from orbit as soon as practicable after completion of mission." The standard articulated in option 1, which is the standard applicable to most satellites and derelict upper stages, has come to be known as the "25-year rule". The US updated the Orbital Debris Mitigation Standard Practices in December 2019, but made no change to the 25-year rule even though "[m]any in the space community believe that the timeframe should be less than 25 years." There is no consensus however on what any new timeframe might be. In 2002, the European Space Agency (ESA) worked with an international group to promulgate a similar set of standards, also with a "25-year rule" applying to most Earth-orbit satellites and upper stages. Space agencies in Europe began to develop technical guidelines in the mid-1990s, and ASI, UKSA, CNES, DLR and ESA signed a "European Code of Conduct" in 2006, which was a predecessor standard to the ISO international standard work that would begin the following year. In 2008, ESA further developed "its own "Requirements on Space Debris Mitigation for Agency Projects" which "came into force on 1 April 2008." Germany and France have posted bonds to safeguard property from debris damage. The "direct retrieval" option (option no. 3 in the US "standard practices" above) has rarely been done by any spacefaring nation (exception, USAF X-37) or commercial actor since the earliest days of spaceflight due to the cost and complexity of achieving direct retrieval, but the ESA has scheduled a 2026 demonstration mission (ClearSpace-1) to do this with a single small 94 kg (207 lb) satellite (PROBA-1) at a projected cost of €120 million not including the launch costs. By 2006, the Indian Space Research Organization (ISRO) had developed a number of technical means of debris mitigation (upper stage passivation, propellant reserves for movement to graveyard orbits, etc.) for ISRO launch vehicles and satellites, and was actively contributing to inter-agency debris coordination and the efforts of the UN COPUOS committee. In 2007, the ISO began preparing an international standard for space-debris mitigation. By 2010, ISO had published "a comprehensive set of space system engineering standards aimed at mitigating space debris. [with primary requirements] defined in the top-level standard, ISO 24113." By 2017, the standards were nearly complete. However, these standards are not binding on any party by ISO or any international jurisdiction. They are simply available for use in voluntary ways. They "can be adopted voluntarily by a spacecraft manufacturer or operator, or brought into effect through a commercial contract between a customer and supplier, or used as the basis for establishing a set of national regulations on space debris mitigation." The voluntary ISO standard also adopted the "25-year rule" for the "LEO protected region" below 2,000 km (1,200 mi) altitude that has been previously (and still is, as of 2019) used by the US, ESA, and UN mitigation standards, and identifies it as "an upper limit for the amount of time that a space system shall remain in orbit after its mission is completed. Ideally, the time to deorbit should be as short as possible (i.e., much shorter than 25 years)". Holger Krag of the ESA states that as of 2017 there is no binding international regulatory framework with no progress occurring at the respective UN body in Vienna.
As of the 2010s, several technical approaches to the mitigation of the growth of space debris are typically undertaken, yet no comprehensive system is in place to reduce debris. International mitigation guidance has been published to reduce the creation of new debris, including recommendations to minimize debris released during normal operations, prevent on-orbit breakups, and perform post-mission disposal and collision-avoidance planning. NASA has also published detailed engineering guidance for limiting orbital debris as part of its technical standards documentation. To avoid excessive creation of artificial space debris, many – but not all – satellites launched to above-low-Earth-orbit are launched initially into elliptical orbits with perigees inside Earth's atmosphere so the orbit will quickly decay and the satellites then will be destroyed upon reentry into the atmosphere. Other methods are used for spacecraft in higher orbits. These include passivation of the spacecraft at the end of its useful life; as well as the use of upper stages that can reignite to decelerate the stage to intentionally deorbit it, often on the first or second orbit following payload release; satellites that can, if they remain healthy for years, deorbit themselves from the lower orbits around Earth. Other satellites (such as many CubeSats) in low orbits below approximately 400 km (250 mi) orbital altitude depend on the energy-absorbing effects of the upper atmosphere to reliably deorbit a spacecraft within weeks or months. Increasingly, spent upper stages in higher orbits – orbits for which low-delta-v deorbit is not possible, or not planned for – and architectures that support satellite passivation, are passivated at end of life.
This removes any internal energy contained in the vehicle at the end of its mission or useful life. While this does not remove the debris of the now derelict rocket stage or satellite itself, it does substantially reduce the likelihood of the spacecraft destructing and creating many smaller pieces of space debris, a phenomenon that was common in many of the early generations of US and Soviet spacecraft. Upper stage passivation (e.g. of Delta boosters) achieved by releasing residual propellants reduces debris from orbital explosions; however even as late as 2011, not all upper stages implement this practice. SpaceX used the term "propulsive passivation" for the final maneuver of their six-hour demonstration mission (STP-2) of the Falcon 9 second stage for the US Air Force in 2019, but did not define what all that term encompassed. With a "one-up, one-down" launch-license policy for Earth orbits, launchers would rendezvous with, capture, and de-orbit a derelict satellite from approximately the same orbital plane. Another possibility is the robotic refueling of satellites. Experiments have been flown by NASA, and SpaceX is developing large-scale on-orbit propellant transfer technology. Another approach to debris mitigation is to explicitly design the mission architecture to leave the rocket second-stage in an elliptical geocentric orbit with a low-perigee, thus ensuring rapid orbital decay and avoiding long-term orbital debris from spent rocket bodies. Such missions will often complete the payload placement in a final orbit by the use of low-thrust electric propulsion or with the use of a small kick stage to circularize the orbit. The kick stage itself may be designed with the excess-propellant capability to be able to self-deorbit.
A propulsion system dubbed the Neumann Drive has been developed in Adelaide, South Australia, and first sent into space in June 2023. Metal space junk is converted into fuel rods, which can be plugged into the Neumann Drive, "basically converting the solid metal propellant into plasma". The Drive is intended to be used by American space companies which already carry nets or robotic arms to capture orbital waste. The thruster would enable these satellites to return to Earth with the waste they have collected, allowing it to be melted down to make more fuel.
The issue of space debris has been raised as a mitigation challenge for missions around the Moon with the danger of increasing space debris around it. It is thought that on 4 March 2022, for the first time, human space debris – most likely a spent rocket body, Long March 3C third stage from the 2014 Chang'e 5 T1 mission – unintentionally hit the lunar surface, creating an unexpected double crater. In 2022, several elements of space debris were found on Mars: Perseverance's backshell was found on the surface of Jezero Crater, and a piece of a thermal blanket which may have come from the descent stage of the rover. As of February 2024, Mars is littered with about seven tons of human-made debris. Most of it consists of crashed and inactive spacecraft as well as discarded components.
This is a production-grade automated web application security scanner designed to detect Cross-Site Scripting (XSS) vulnerabilities across multiple attack surfaces: Author: Bhavya Bhalla Institution: Thapar Institute of Engineering and Technology Project Type: Cybersecurity Internship - Elevate Labs This project implements a comprehensive web vulnerability assessment platform that automates the detection of common web application security vulnerabilities. The system combines industry-standard security testing methodologies with a professional web interface suitable for client demonstrations and security assessments.
Python 3.9+ III Flask Web Framework III BeautifulSoup4 (HTML Parsing) III Requests (HTTP Client) III Threading (Concurrent Processing) III JSON Reporting System HTML5 + CSS3 + Vanilla JavaScript III Responsive Design III Real-time API Communication III Progressive Web App Features III Professional UI/UX OWASP Testing Framework III Top 10 Vulnerability Coverage III Automated Payload Injection III Error Pattern Recognition III Security Header Validation Clone Repository git clone https://github.com/yourusername/web-vulnerability-scanner.git cd web-vulnerability-scanner Setup Environment python -m venv venv source venv/bin/activate # Windows: venv\Scripts\activate pip install -r requirements.txt Test against public vulnerable application python src/vulnerability_scanner.py --target http://testphp.vulnweb.com/ 4. Practical Deployment, Analysis & Case Studies POST /api/scan # Start new scan GET /api/scan/{id}/status # Check scan progress GET /api/scan/{id}/report # Get detailed report GET /api/scans # List all scans GET /api/scan/{id}/download # Download report file SQL Injection Detection: { "type": "SQL Injection", "severity": "Critical", "url": " https://target.com/login.php ", "payload": "' OR 1=1--", "description": "SQL Injection vulnerability detected...", "recommendation": "Use parameterized queries..." } XSS Detection: { "type": "Cross-Site Scripting (XSS)", "severity": "High", "url": " https://target.com/search.php ", "payload": "", "description": "Reflected XSS vulnerability found...", "recommendation": "Implement input validation..." } Crawling Configuration MAX_CRAWL_DEPTH = 2 # Website exploration depth MAX_LINKS_PER_PAGE = 10 # Links to follow per page REQUEST_TIMEOUT = 10 # HTTP request timeout (seconds) Payload Configuration XSS_PAYLOADS = [...] # Custom XSS attack vectors SQL_PAYLOADS = [...] # Custom SQL injection payloads http://testphp.vulnweb.com/ # Public test site http://demo.testfire.net/ # IBM Security AppScan demo https://xss-game.appspot.com/ # Google XSS challenge web-vulnerability-scanner/ III src/ I III vulnerability_scanner.py # Core scanning engine I III flask_app.py # Web application server III templates/ I III index.html # Dashboard interface III static/ I III style.css # Custom styling III reports/ I III *.json # Generated scan reports III tests/ I III test_scanner.py # Unit tests III docs/ I III api_documentation.md # API reference III requirements.txt # Python dependencies III README.md # Project documentation III .gitignore # Git ignore rules III LICENSE # Project license Bhavya Bhalla I Email: bhavyabhalla19@gmail.com I LinkedIn: linkedin.com/in/bhavya-bhalla-235300258 I GitHub: github.com/bhavya-bhalla Institution: Thapar Institute of Engineering and Technology Course: B.E. Computer Engineering (2022-2026) CGPA: 7.20/10.0 "Bridging technical security expertise with business impact through innovative vulnerability assessment solutions." Professional web vulnerability assessment platform with automated XSS and SQL injection detection. Built with Python/Flask featuring real-time scanning dashboard and comprehensive security reporting.
The increasing reliance on web services has led to a rise in cybersecurity threats, particularly Cross-Site Scripting (XSS) attacks, which target client-side layers of web applications by injecting malicious scripts. Traditional Web Application Firewalls (WAFs) struggle to detect highly obfuscated and complex attacks, as their rules require manual updates. This paper presents a novel generative AI framework that leverages Large Language Models (LLMs) to enhance XSS mitigation. The framework achieves two primary objectives: (1) generating sophisticated and syntactically validated XSS payloads using in-context learning, and (2) automating defense mechanisms by testing these attacks against a vulnerable application secured by a WAF, classifying bypassing attacks, and generating effective WAF security rules. Experimental results using GPT-4o demonstrate the framework’s effectiveness generating 264 XSS payloads, 83% of which were validated, with 80% bypassing ModSecurity WAF equipped with an industry standard security rule set developed by the Open Web Application Security Project (OWASP) to protect against web vulnerabilities. Through rule generation, 86% of previously successful attacks were blocked using only 15 new rules. In comparison, Google Gemini Pro achieved a lower bypass rate of 63%, highlighting performance differences across LLMs.
The rise of web services has significantly influenced how organizations manage client information. However, as online platforms expand, so do the threats to user data security, with Cross-Site Scripting (XSS) emerging as a prevalent and dangerous attack vector [ 13 ] . XSS attacks exploit website vulnerabilities to inject malicious scripts, often through links, URLs, or user inputs, which execute within the victim’s browser. Web Application Firewalls (WAFs) serve as a primary defense against XSS by detecting and blocking malicious payloads [ 4 ] . However, as web attacks grow more sophisticated, traditional WAFs often struggle to adapt to advanced and obfuscated patterns [ 12 ] .
Generative AI has emerged as a promising solution, leveraging Large Language Models (LLMs) to generate text, code, and images [ 1 ] . LLMs, when combined with techniques like in-context learning and fine-tuning, excel at generating new data from a few relevant examples. [ 18 , 2 ] . This adaptability makes LLMs particularly effective for enhancing WAF defenses by generating simulated attack scenarios based on real-world examples [ 5 ] . These generated samples can then be analyzed and tested to improve the detection capabilities of WAFs, ultimately contributing to the development of more robust cybersecurity defenses.
5. Performance Evaluation & Extended Technical Observations In this paper, we propose GenXSS , a generative AI framework for enhancing WAF defenses against XSS attacks. Our framework achieves two primary objectives: Generation of Obfuscated XSS Attacks: Using LLMs and curated in-context learning, GenXSS generates complex XSS payloads validated against real-world vulnerable applications.
Automated Defense Mechanisms: The framework identifies bypassing payloads and employs machine learning and LLMs to generate and validate new WAF rules. Experimental results demonstrate the framework’s efficacy with 264 new XSS payloads generated, 83% were syntactically validated using a buggy web application, ensuring they were correctly structured and executable. Among these validated attacks, 80% bypassed ModSecurity WAF equipped with the latest OWASP Core Rule Set [ 9 ] , and nearly 100% bypassed AWS WAF. By classifying the generated payloads using our machine-learning algorithms and generating rules through the GPT-4o LLM rule-generation methodology, we developed and validated security rules that effectively blocked 86% of all previously successful attacks which bypassed ModSecurity with only 15 new rules. We also employed Gemini Pro LLM to generate new XSS attacks, resulting in a total of 220 generated samples. Of these, 140 (63%) were validated as syntactically correct and effective, with 104 (74%) successfully bypassing ModSecurity.
The contributions of this paper include an innovative generative AI framework for XSS mitigation including in-context learning involves incorporating task-specific examples directly within the input prompt to guide the model’s behavior and output generation, automated WAF rule optimization, and experimental validation on real-world WAFs. The remainder of the paper is structured as follows: Section II provides a background on XSS attacks and generative AI. Section III reviews related literature. Section IV details the framework. Section V presents results, followed by discussion in Section VI , and conclusions in Section VII .
Cross-Site Scripting (XSS) attacks come in three main types: Reflected, DOM-based and Stored. Reflected XSS (Non-persistent XSS), the most common type, involves the attacker embedding their payload in a request sent to the web server. The server reflects the payload back in its response, executing it in the victim’s browser. DOM-based XSS is a more advanced, client-side attack where the malicious script exploits vulnerabilities in the web application’s client-side scripts to manipulate the Document Object Model (DOM), executing the payload within the browser. This type of XSS targets elements like URLs or referrers directly in the DOM. Stored XSS (Persistent XSS) occurs when an attacker embeds malicious scripts, such as JavaScript, into a target application. These scripts are typically injected through user input fields, such as comments or posts, and are stored on the server, allowing them to execute whenever other users access the affected content. [ 13 ] .
A Web Application Firewall (WAF) is a security mechanism that protects web applications by monitoring and blocking malicious HTTP/S traffic. WAFs typically use two strategies: rule-based and machine-learning-based approaches. Rule-based methods rely on predefined attack signatures using regular expressions, offering transparency, low false positive rates, and quick deployment, but they are limited to known patterns, require frequent updates, and struggle with scalability.
Machine-learning-based methods, on the other hand, detect attacks by learning from data, making them adaptable to novel or obfuscated patterns and capable of detecting anomalies beyond static signatures. However, these methods can have high false positive rates and depend heavily on high-quality labeled data for training and fine-tuning [ 4 ] . Generative AI is a field of artificial intelligence focused on creating new content, such as text, images, audio, or code, by learning patterns from existing data [ 18 ] . Central to this field are Large Language Models (LLMs), such as GPT (Generative Pre-trained Transformer), which use deep-learning architectures to generate coherent and contextually relevant language.
These models leverage transformer architectures to capture complex relationships within data and utilize multi-layered neural networks to process vast datasets by extracting increasingly abstract features. With billions or trillions of parameters, LLMs are highly complex and demand substantial computational resources for training. While LLMs have shown promise in cybersecurity applications, there are currently limited documented real-world case studies explicitly detailing their deployment in active cybersecurity environments. Most implementations remain in research and experimental phases, focusing on theoretical frameworks or controlled test environments. In this section, we review related work focusing on XSS attack generation, rule adaptation methodologies, and approaches for enhancing WAF robustness.
Wu et al. [ 16 ] proposed an RNN-based generator for creating malicious payloads, including XSS and SQL injection, validated by a payload corrector. These payloads were tested against a shadow model mimicking WAF behavior and then real-world WAFs. Successfully bypassing payloads were used to enhance WAF detection by updating rules with new signatures. Yao et al. [ 17 ] developed a method for generating XSS attack vectors using an improved Dueling Deep Q-Network (DDQN) algorithm modeled as a Markov Decision Process. Priority experience replay and a reward function based on edit distance guided effective mutations. Generated vectors were validated through semantic analysis and tested against WAFs in both proxy and direct connection modes. Garn et al. [ 10 ] employed combinatorial testing with an attack grammar to create diverse XSS payloads, defined by attributes, payloads, and tags. The payloads were tested against multiple WAFs in controlled environments, and their effectiveness was compared to state-of-the-art static attack lists. Alaoui et al. [ 3 ] used a Generative Adversarial Network (GAN) to create adversarial XSS attacks by modifying existing dataset samples to evade detection by an LSTM-based XSS detection model. The crafted attacks significantly reduced the detection model’s performance, highlighting their effectiveness. Khan [ 11 ] introduced a generative AI model combining auto-regressive and transformer techniques to generate XSS payloads by analyzing backend and frontend code. The generated payloads were tested for effectiveness using the OWASP Juice Shop application.
Our approach differs from traditional methods, where security experts manually update WAF rules in response to observed threats. Furthermore, the works described above present challenges for anomaly detection models that use neural networks. These challenges arise due to the substantial training data required and the complexity of neural network design and implementation. Additionally, we observe that existing XSS attack generation methods in the literature treat attack generation and mitigation as separate processes. In contrast, our framework integrates generative AI to simultaneously automate the generation of XSS attacks and the creation of corresponding WAF rules, offering a unified and adaptive defense mechanism.
In this section, we present the GenXSS framework, a general and flexible solution designed to enhance the performance of WAFs against XSS attacks. The primary advantage of the GenXSS framework lies in its ability to both generate and defend against XSS attacks while offering adaptability to various parameters, including the LLM model, application, and WAF. The framework can be configured to suit different environments based on specific requirements.
In the proposed framework, we utilize in-context learning by providing a set of valid, carefully crafted attacks as examples within the prompt to guide the LLM in generating new XSS samples. However, since LLMs can occasionally produce irrelevant or inaccurate samples, the generated outputs must be validated against a vulnerable application specifically designed to be susceptible to XSS attacks. This validation ensures that only effective and legitimate samples are retained, while irrelevant samples are discarded. Figure 1 illustrates the architecture of GenXSS.
The next step involves testing the validated samples using a Web Application Firewall (WAF). Samples that successfully bypass the WAF are stored separately and then processed using machine-learning clustering methods. This clustering is a crucial step which group similar attack types for the subsequent generation of security rules to update the WAF. In the second stage of the framework, we use another LLM to generate effective and comprehensive WAF rules tailored to the characteristics of the identified clusters. To maximize rule effectiveness, we apply a Reinforcement Learning with Human Feedback (RLHF) approach. This iterative refinement process ensures the successful mitigation of all XSS attacks.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/List%20of%20tools%20for%20static%20code%20analysis • https://en.wikipedia.org/wiki/Space%20debris • https://github.com/vijayyh/xss-vulnerability-scanner/blob/main/docs/README.md • https://github.com/bhavya-bhalla/web-vulnerability-scanner • https://arxiv.org/html/2504.08176v1
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Automated XSS Vulnerability Detector Tool Using Python.
[*] Initializing Burp Suite Spider & Vulnerability Engine for Automated XSS Vulnerability Detector Tool Using Python... [✓] Burp Extender / Macro Automation Hook Synced ──────────────────────────────────────────────────────────────────────── [11:42:01.104] AUDIT Crawled dynamic endpoints | Injecting input vectors [11:42:01.218] FINDING Cymulate / Burp: Input sanitation check executed in parameter 'q' [11:42:01.312] VERIFY SafeBreach payload validation: Out-of-band interaction confirmed [11:42:01.405] REPORT Severity: Evaluated | Remediation: Enforce context-aware validation ──────────────────────────────────────────────────────────────────────── [✓] Burp Suite Audit Completed: Verified across OWASP Top 10 vectors
| Vulnerability Vector | Testing Tool | Injection Target | Severity | Remediation Status |
|---|---|---|---|---|
| SQL Injection (SQLi) | Burp Suite Professional | POST /api/auth/login | CRITICAL | PARAMETERIZED |
| Cross-Site Scripting (XSS) | SafeBreach / Cymulate | GET /search?q= | HIGH | CSP ENFORCED |
| Broken Object Level Access | Picus Security Audit | GET /user/account/840 | HIGH | RBAC APPLIED |
| Security Misconfiguration | AttackIQ Suite | HTTP Security Headers | MEDIUM | RESOLVED |