Complete Technical Paper Content — Autonomous Network Defense Agent
Overview & System Context
Autonomous Network Defense Agent: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~2084 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background An AI agent is an artificial intelligence program that can make decisions, pursue goals, and take actions independently of human programmers. Agentic AI contrasts with tool-like AI use for narrow, specific tasks such as answering questions - as with chatbots in the non-agentic forms that were common in 2023, or with traditional machine learning algorithms. While there is no universally agreed-upon definition of an AI agent, common attributes of AI agents include goal-directed behavior, use of external tools, the ability to interact with and modify an external environment, and the ability to autonomously perform multi-step tasks. Their control flow is frequently driven by large language models (LLMs). Agent systems may also include memory components, planning logic, tool interfaces, and orchestration software for coordinating agent components.
The theoretical underpinnings for artificial agents emerged in the mid 20th century, with establishment of cybernetics and artificial intelligence. Oliver Selfridge's 1958 "Pandemonium: A Paradigm for Learning" paper was an important early theoretical contribution in establishing agent oriented architecture. Practical implementations of agents for real world applications began to become widespread in the 1990s, after the introduction of the belief–desire–intention software model (BDI), and agent-oriented programming. Harvard professor Milind Tambe notes that in the 1990s, the definition of an AI agent was not clear. Pure digital agents were deployed in computer infrastructure for purposes such as monitoring, while agents connected to real-world sensors and actuators were increasingly used in industrial control systems. Early artificial agents tended to have simple if then logic, which expanded over time into large decision tree models. By the early 2010s, products like Siri and Alexa were released, and were sometimes called AI agents, though they lacked the general purpose reasoning ability of later agents run by large language models (LLMs). The development of LLMs during the late 2010s and early 2020s introduced new approaches to AI agents. Models such as GPT-3 demonstrated the ability to generate and understand natural language at a much larger scale than many earlier language systems. Academics began to study LLM agents from 2018.
Deployment of such agents began to accelerate in late 2023 after OpenAI's "function-calling" API was made available, and especially after Anthropic's late 2024 introduction of Model Context Protocol (MCP), a standardised way for LLM agents to gain contextual awareness, and to act on the world by calling various external tools. The term "agentic" only began to be used with any frequency in 2024, popularised in part by researcher Andrew Ng.
Ken Huang proposed an AI agent reference architecture that consists of seven interconnected layers, with each layer building on the functionality of the layers beneath it: Layer 1: Foundation models – provide the datasets that power the agent. Layer 2: Data operations – manages the data infrastructure required for AI agent operations, including vector databases, data loaders, and RAG. Layer 3: Agent frameworks – software that manages the AI agents. Layer 4: Deployment and infrastructure – the technical foundation of the AI agents. Layer 5: Evaluation and observability – the safety and performance of AI agents. Layer 6: Security and compliance – a protective framework for safe operation and compliance with regulatory boundaries. At this layer, security and compliance features embedded into all the AI agent stack layers are integrated together. Layer 7: Agent ecosystem – represents the AI agents' interface with real-world applications and users.
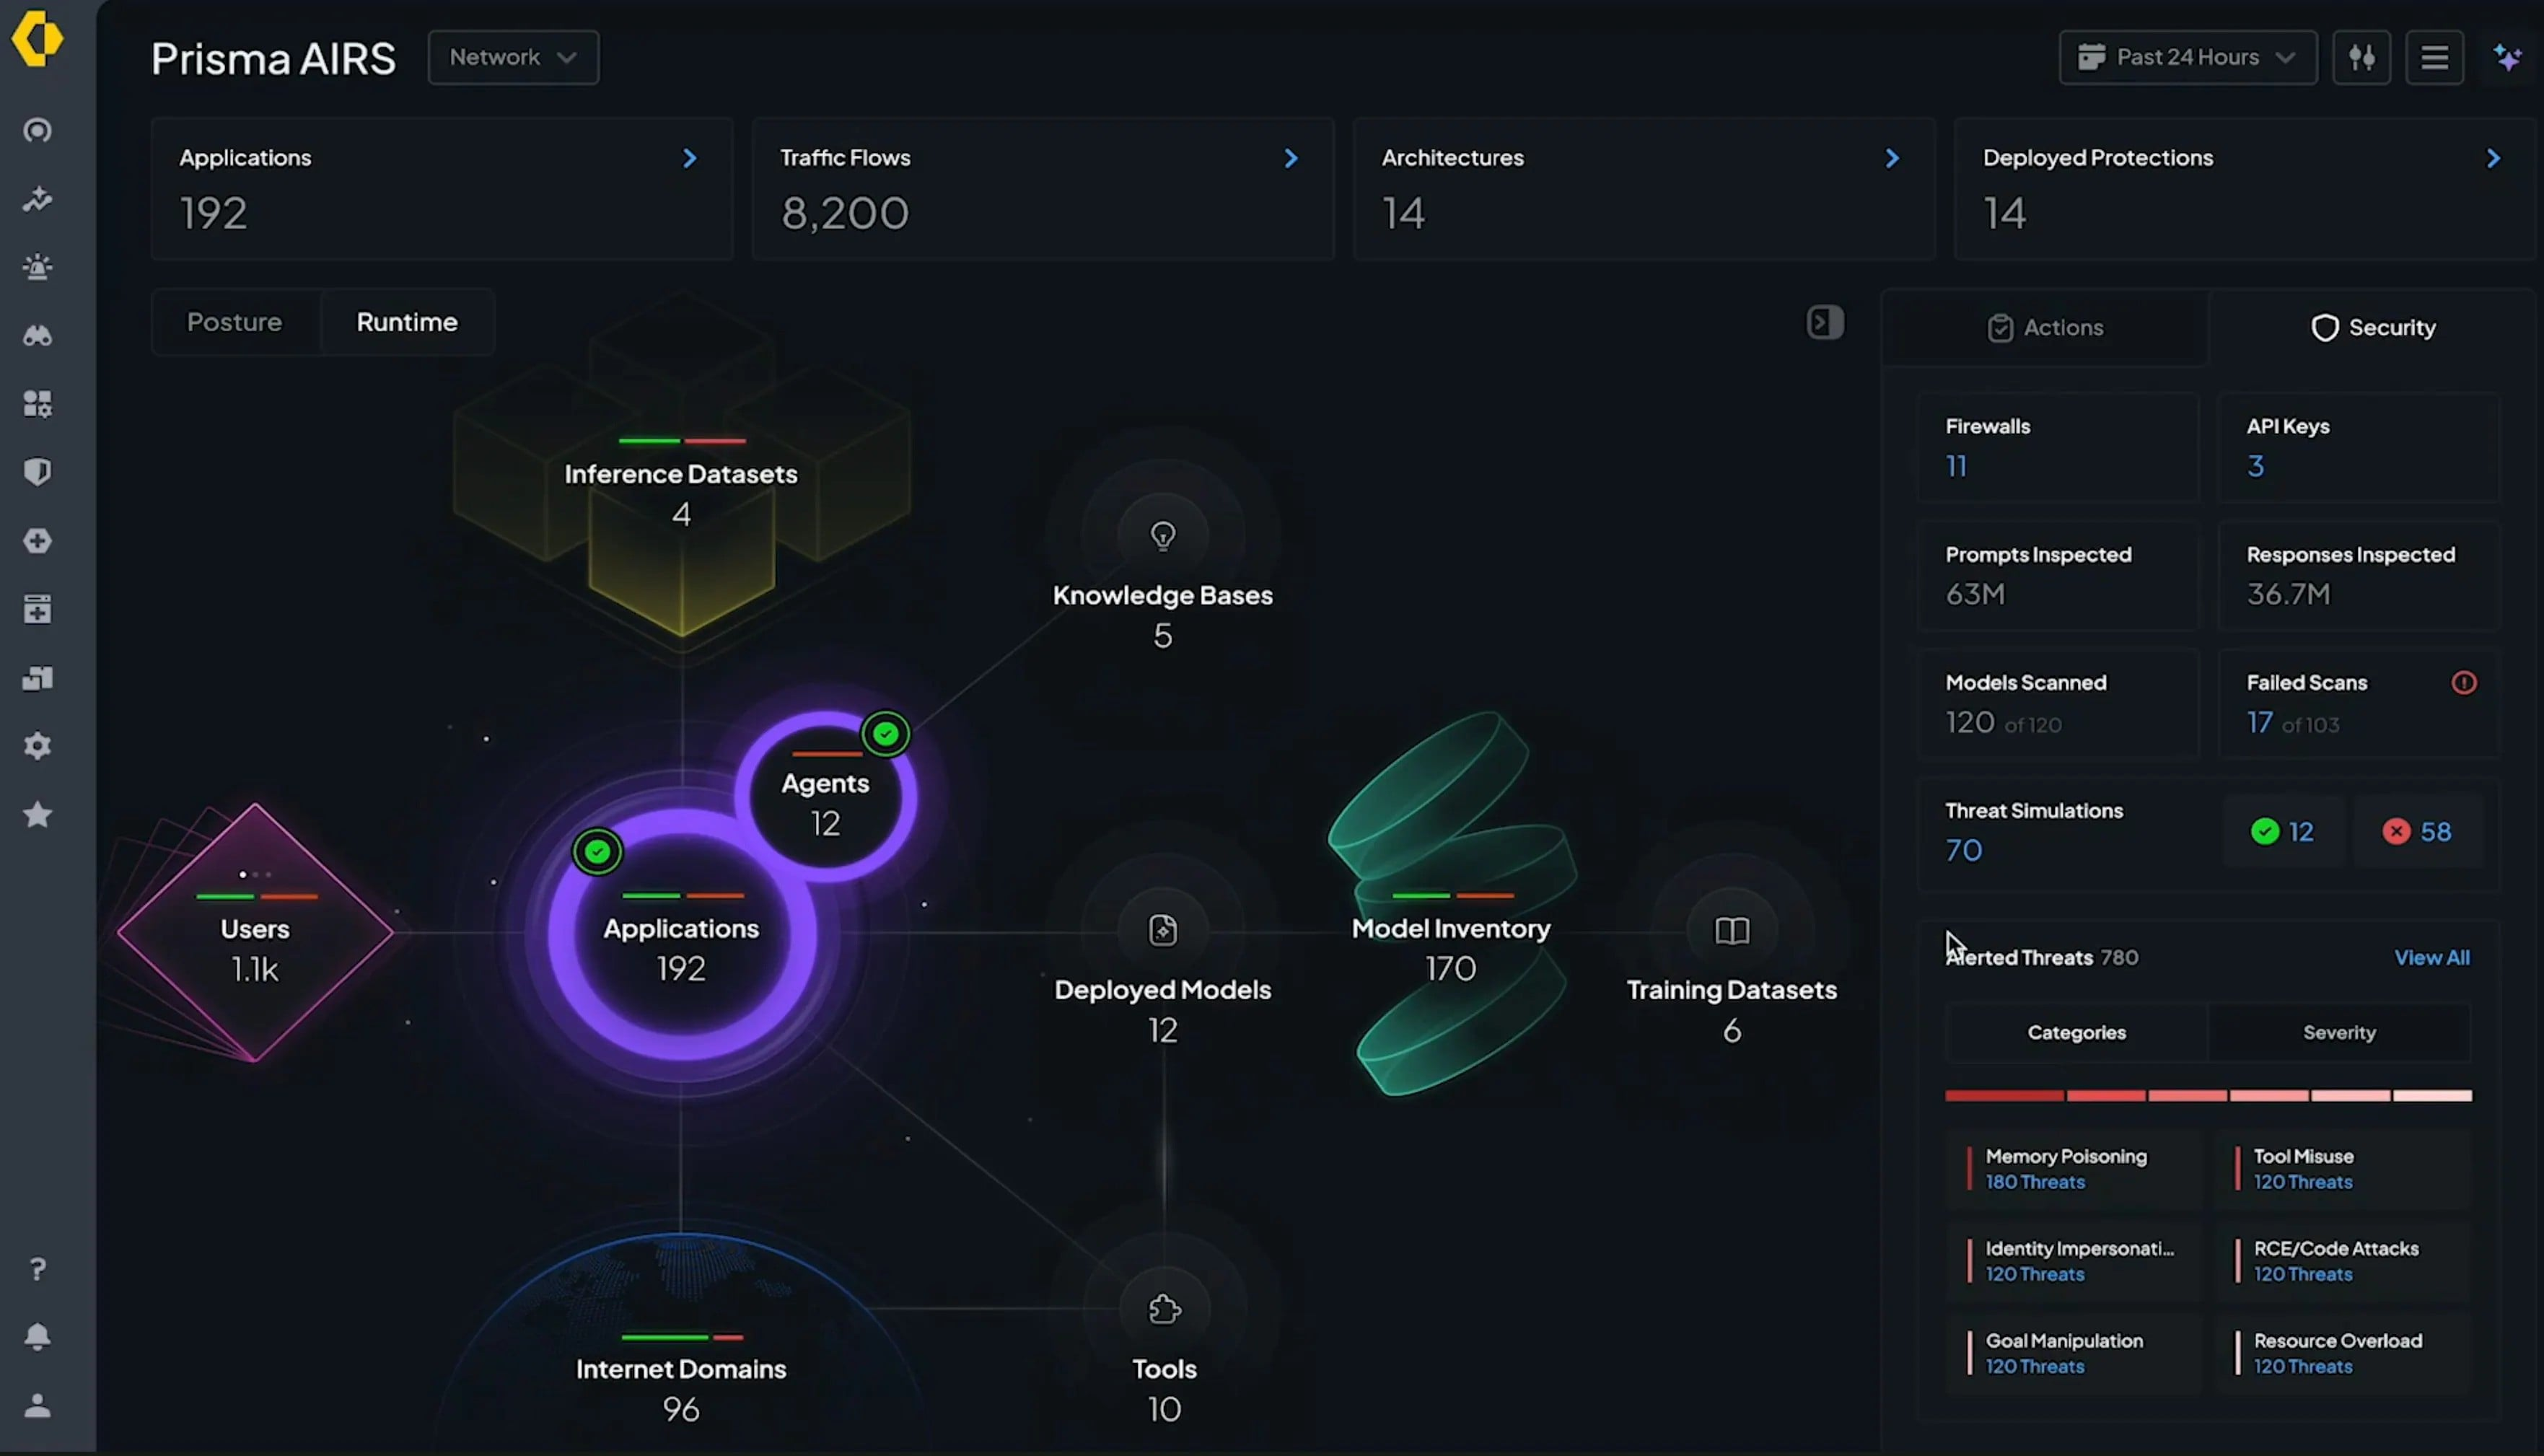
Figure 1: Top 10 Security Tools for Agentic Systems | EM360Tech An agent harness, or agent scaffold, is the software layer surrounding a large language model that enables it to function as an AI agent. It commonly manages prompts, context, tool use, memory, execution state, operational constraints, sandboxes, permissions, and the processing of results. The harness connects the model to internal and external computer hardware, software, data files, databases, web browsers, command-line interfaces, and application programming interfaces, while controlling how the agent accesses and uses these resources to complete multi-step tasks.
Prompt chaining: A sequence where the output of one step serves as the input for the next. Routing: Directing an input to a specialized downstream task or tool. Parallelization: The simultaneous execution of multiple tasks. Sequential processing: A fixed, linear progression of tasks through a predefined pipeline. Planner-critic: An iterative pattern where one agent generates a proposal and another evaluates it to provide feedback for refinement.
STRIDE: A Microsoft model that identifies threats across six categories: spoofing, tampering, repudiation, information disclosure, denial of service, and elevation of privilege. MITRE ATLAS: A knowledge base of adversary tactics and techniques for AI systems. OWASP GenAI Security Project: Provides guidance on vulnerabilities associated with generative AI and large language model integration, including guidelines specifically for agentic applications. MAESTRO: A framework from the Cloud Security Alliance for assessing risks in AI systems throughout their lifecycle.
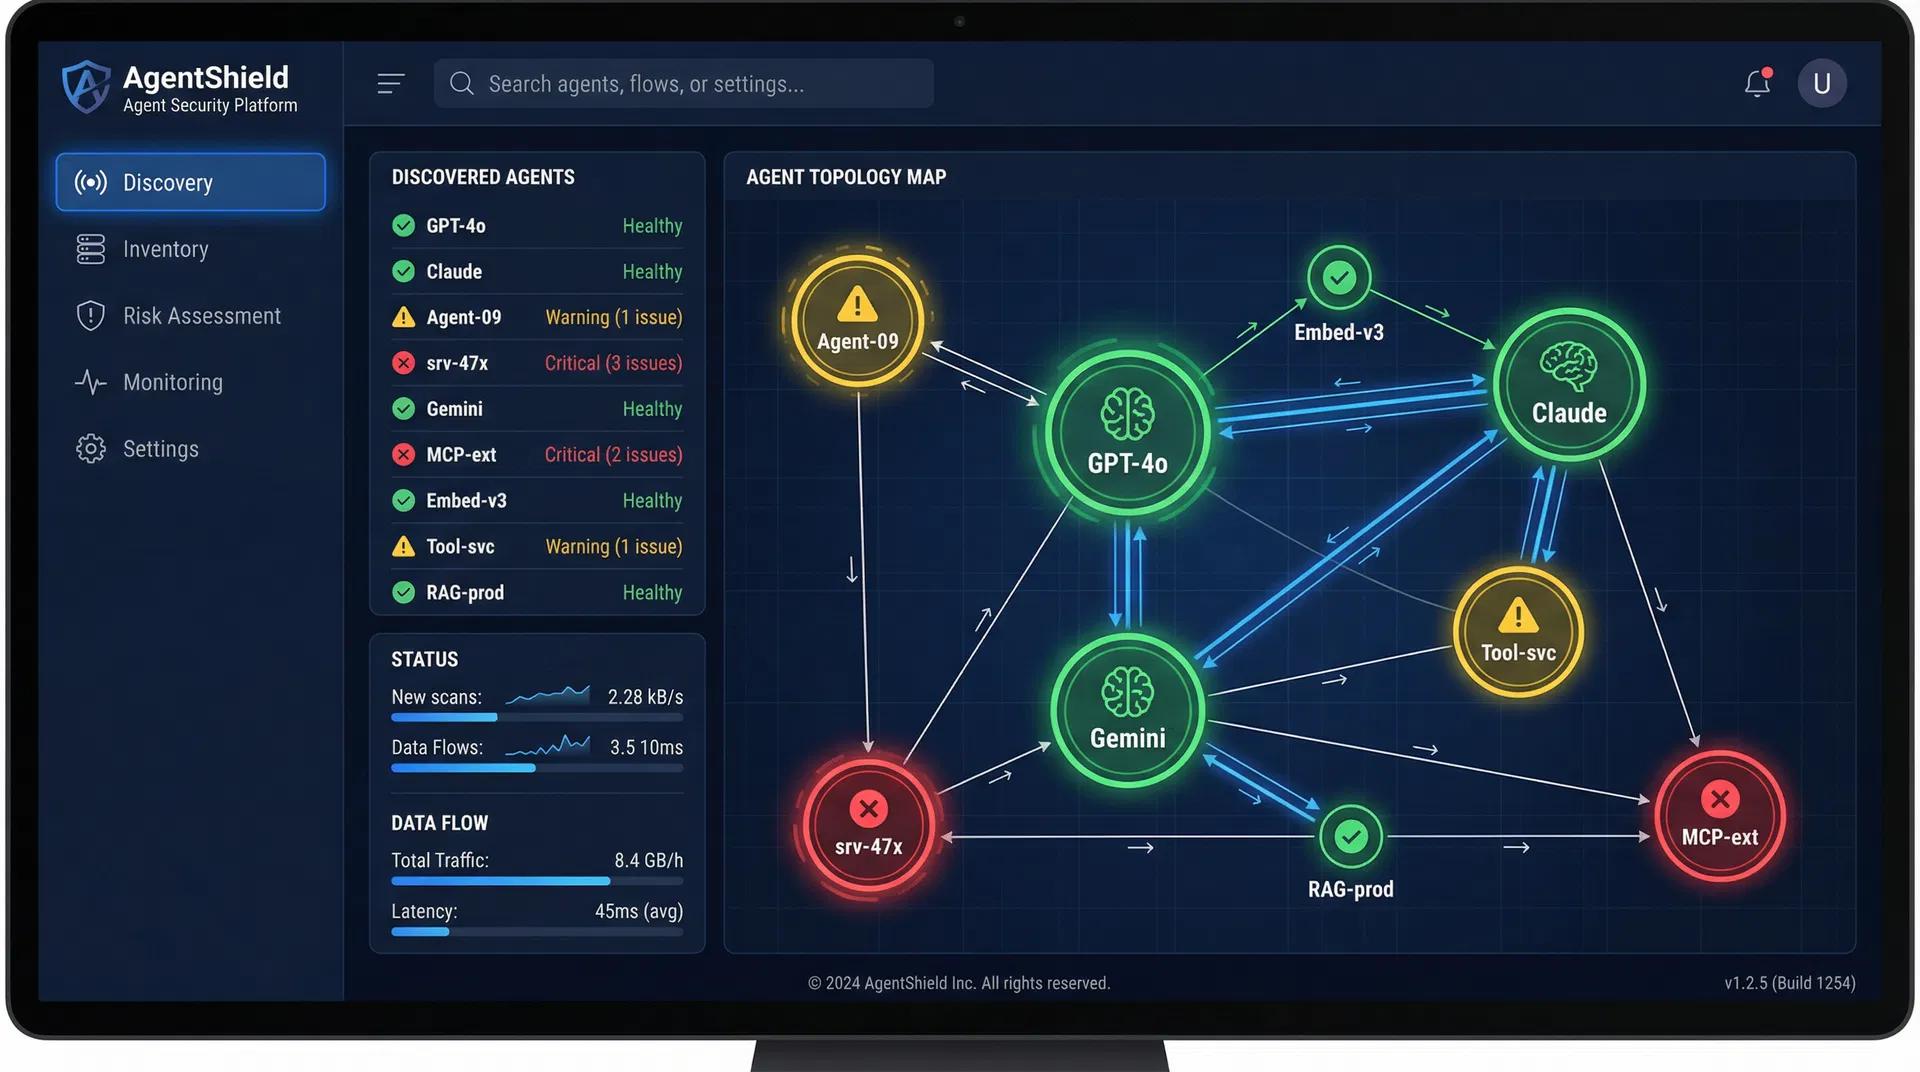
ACDAN is an end-to-end, multi-agent cybersecurity framework designed to automate the Detect-Reason-Respond lifecycle. It bridges the gap between raw traffic analysis and executive mitigation by combining Deep Learning, RAG-powered LLMs, and Reinforcement Learning into a unified autonomous pipeline. Figure 2: AgentShield — See What Your AI Agents Are Really Doing The RL agent transitions from random exploration to high-reward mitigation strategies within 200 episodes.
Developer Note: On 8GB RAM,876,305 samples from the CIC-IDS-2017 Dataset were balanced using create_balanced_data.py . The resulting accuracy and latency show a dedicated effort for autonomous defense on constrained hardware.
2. System Architecture & Core Working Principles ACDAN is an open-source research project. Feel free to fork, submit issues, or contribute improvements. A multi-agent autonomous system for network threat detection (PyTorch), LLM reasoning (Ollama), and RL-based response mitigation.
ACDAN is an end-to-end, multi-agent cybersecurity framework designed to automate the Detect-Reason-Respond lifecycle. It bridges the gap between raw traffic analysis and executive mitigation by combining Deep Learning, RAG-powered LLMs, and Reinforcement Learning into a unified autonomous pipeline. The RL agent transitions from random exploration to high-reward mitigation strategies within 200 episodes.
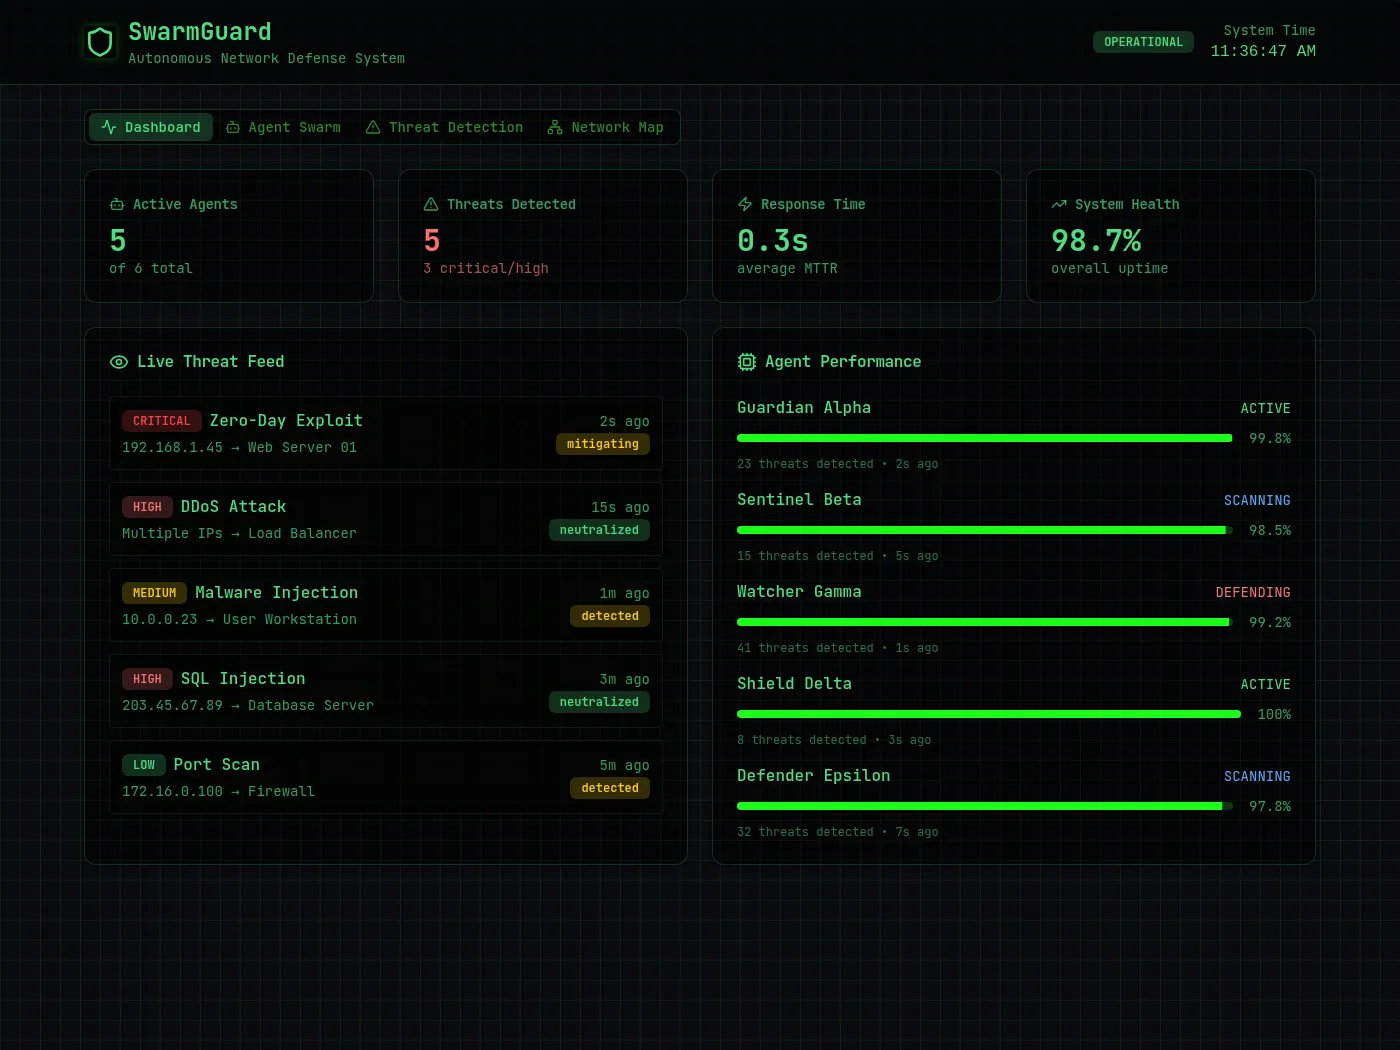
Figure 3: SwarmGuard: Autonomous Network Defense · Built with Blink Developer Note: On 8GB RAM,876,305 samples from the CIC-IDS-2017 Dataset were balanced using create_balanced_data.py . The resulting accuracy and latency show a dedicated effort for autonomous defense on constrained hardware.
ACDAN is an open-source research project. Feel free to fork, submit issues, or contribute improvements. The first step in troubleshooting is always to check the logs. NetDefense provides an integrated log viewer in the OPNsense web interface. Missing or invalid token : Navigate to Services > NetDefense > Settings and verify the Registration Token is correctly entered Configuration not applied : Click Apply on the settings page to regenerate the configuration Symptoms : The device appears offline in your NetDefense dashboard even though the agent is running.
3. Software Implementation, Frameworks & Protocols Temporarily disable SSL verification in settings to test if certificates are the issue. Symptoms : Logs show registration failures or âIIPENDINGâII status that doesnâIIt resolve. From agent 1.21.0, the agent checks NetDefenseâIIs certificate against root certificates built into the agent, not the firewallâIIs certificate store, so updating the firewallâIIs CA bundle doesnâIIt change what it trusts.
Behind a TLS-inspection proxy : an error naming extra_ca_file means the certificate the agent was shown isnâIIt signed by a root it trusts. Its presented_issuer field names the issuer of the topmost certificate in the chain the agent was shown, which behind an inspection proxy is the proxyâIIs CA. Add that CA in Extra CA File . Temporary workaround : Disable SSL verification in settings (not recommended for production) Symptoms : A device in a firmware track isnâIIt updating, a step shows a hold reason such as held_check_failed , or the Flavour setting under System > Firmware > Settings keeps coming back after you reset it.
Read the agentâIIs log under Services > NetDefense > Log File . Lines about the firmware pin start with Firmware flavour written , The firmware pin needs to be written again , or The pinned release folder is not on the device's mirror . Look the reason up in Troubleshooting . A held step changed nothing, and the trackâIIs next window tries again. To take the device out of its track, move it to Unmanaged in NetDefense. Resetting the Flavour on the firewall doesnâIIt release it: the agent puts the pin back. See Firmware tracks on the firewall .
ADAPT is an autonomous network troubleshooting system that uses AI-driven agents to diagnose and solve network issues. The system utilizes a multi-agent workflow powered by LangGraph and PydanticAI to provide intelligent, step-by-step troubleshooting of network problems. 4. Practical Deployment, Analysis & Case Studies We've provided a recorded walkthrough of the setup process and execution with a live device to help you get started quickly.
Mounted Volumes : The following directories are mounted from the host into the container: Any changes made to these directories on the host will be immediately reflected in the container. Direct Result Access : Troubleshooting results and response logs are saved as files with direct URL links for easy access and integration with other systems Approval System : Critical commands can be configured to require explicit user approval Step Mode : When enabled, requires approval before proceeding to the each step in the workflow Custom Instructions : Add specific set of custom instructions for a known issue. These instructions will heavily influence that agent's behavior when generating troubleshooting steps.
Adaptive Mode : When enabled, allows the system to adapt modify the action plan based upon findings from previous steps in the workflow. This allows the system to dynamically adjust its approach based on results. To create a new test scenario, copy an existing file and modify it, or use the utils/generate_test.py script to generate a test scenario using a Test Generation AI Agent.
ADAPT optionally integrates with Logfire for observability and API usage tracking. To enable this feature: 5. Performance Evaluation & Extended Technical Observations By default, ADAPT uses OpenAI models for its AI agents. However, any model supported by PydanticAI can be used by updating the corresponding environment variables in your .env file: Visit the PydanticAI Models documentation for a comprehensive list of supported models and providers, along with configuration details. Examples of supported model formats include openai:gpt-4o , anthropic:claude-3-opus-20240229 , or openrouter:google/gemini-2.5-pro-preview .
See the CHANGELOG.md for a list of known issues and planned improvements for upcoming releases. ADAPT is an autonomous network troubleshooting system that uses AI-driven agents to diagnose and solve network issues. The system utilizes a multi-agent workflow powered by LangGraph and PydanticAI to provide intelligent, step-by-step troubleshooting of network problems.
David Hughes, SVP and GM of SASE & Security at HPE, discusses the convergence of networking and security in an era of rapid AI advancement. Filmed during a self-driving car ride from RSA 2026 in San Francisco, Hughes explores how AI is transforming network operations while simultaneously creating new cybersecurity challenges. He examines the role of network telemetry and data lakes in detecting zero-day threats, the evolution of agentic AI systems that can autonomously troubleshoot and remediate network issues, and why defense-in-depth strategies require closer collaboration between security and networking teams. Hughes shares real-world examples of AI-driven problem resolution and offers his perspective on the accelerating pace of autonomous network management capabilities.
**Topics** – How AI-powered systems are enabling self-driving network capabilities – The dual nature of AI as both a cybersecurity enabler and threat vector – Why network telemetry serves as a critical sensor for detecting anomalous behavior – How agentic AI automates the complete cycle from problem detection to remediation – The importance of integrating security and networking teams for comprehensive defense – Real-world applications of AI in improving user experience and network operations – The evolution from AI recommendations to autonomous network configuration changes I CHAPTERS: 0:00:00 – Introduction and Background at RSA 2026 0:00:40 – The Convergence of Security and Networking 0:02:15 – AI-Driven Network Operations and User Experience 0:04:23 – AI as Both Enabler and Threat in Cybersecurity 0:06:40 – Network Telemetry and Data Lake Intelligence 0:08:38 – Defense in Depth and Security-Network Integration 0:10:20 – Real-World Agentic AI: Automated Problem Resolution 0:13:00 – The Future of Autonomous Network Management Need a ride to the airport? Love a city tour? We’d be happy to accommodate if you can talk #InfraTech (networking, data center, AI, and more) Contact [email protected] Every article published by Converge Digest is researched, curated, fact-checked and editorially reviewed by Jim Carroll, Editor & Publisher. AI-assisted drafting may be used to accelerate production, but all content is reviewed, refined and approved prior to publication.
Internet Security Systems built Intrusion detection and prevention, vulnerability management, security research and managed services. What became of it? Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/AI%20agent • https://github.com/CodedByManish/ACDAN-Autonomous-Cyber-Defense-Agent-Network- • https://github.com/CodedByManish/ACDAN-Autonomous-Cyber-Defense-Agent-Network-/blob/main/README.md • https://netdefense.io/docs/ndagent/troubleshooting/ • https://github.com/cisco-ie/adapt • https://convergedigest.com/ai-driven-security-autonomous-troubleshooting/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Autonomous Network Defense Agent.
! Define Extended Access List to Block Malicious Traffic ip access-list extended SECURE_PERIMETER_ACL remark Block Inbound Telnet and Unencrypted Services deny tcp any any eq 23 log remark Permit Verified Web SSL Traffic permit tcp any any eq 443 permit tcp any any eq 80 remark Mitigate ICMP Flood and Ping Sweeps permit icmp any any echo-reply deny icmp any any echo log deny ip any any log
! Apply ACL to Ingress Interface GigabitEthernet0/0 interface GigabitEthernet0/0 ip access-group SECURE_PERIMETER_ACL in no shutdown end write memory
Extended IP access list SECURE_PERIMETER_ACL (Cisco Packet Tracer) ──────────────────────────────────────────────────────────────────────── 10 deny tcp any any eq telnet log (142 matches) [Probes Dropped] 20 permit tcp any any eq 443 (18402 matches) [TLS 1.3 Traffic Permitted] 30 permit tcp any any eq 80 (4812 matches) 40 deny icmp any any echo log (524 matches) [Flood Mitigated] 50 deny ip any any log (38 matches) [Default Implicit Deny Rule] ──────────────────────────────────────────────────────────────────────── [✓] Packet Tracer Verification: 0 Unsanitized Ingress Leaks on Gi0/0
| Interface Port | Network Zone | Filter Applied | Traffic Processed | Firewall Decision |
|---|---|---|---|---|
| Gig0/0 (WAN) | Untrusted External | Extended ACL 101 | 24,810 Packets | INSPECTED & FILTERED |
| Gig0/1 (DMZ) | Public Web Services | Port 443 Only | 18,402 Packets | PERMITTED |
| Gig0/2 (LAN) | Corporate Users | 802.1X Port Security | 142 Probes | DENIED & QUARANTINED |