Complete Technical Paper Content — Autonomous Vehicle Lane Security Against Spoofing
Overview & System Context
Autonomous Vehicle Lane Security Against Spoofing: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9511 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background An inertial navigation system (INS; also inertial guidance system, inertial instrument) is a navigation device that uses motion sensors (accelerometers), rotation sensors (gyroscopes) and a computer to continuously calculate by dead reckoning the position, the orientation, and the velocity (direction and speed of movement) of a moving object without the need for external references. Often the inertial sensors are supplemented by a barometric altimeter and sometimes by magnetic sensors (magnetometers) and/or speed measuring devices. INSs are used on mobile robots and on vehicles such as ships, aircraft, submarines, guided missiles, and spacecraft. Older INS systems generally used an inertial platform as their mounting point to the vehicle and the terms are sometimes considered synonymous.
Inertial navigation systems were originally developed for rockets. American rocketry pioneer Robert Goddard experimented with rudimentary gyroscopic systems. Goddard's systems were of great interest to contemporary German pioneers including Wernher von Braun. The systems entered more widespread use with the advent of spacecraft, guided missiles, and commercial airliners. Early German World War II V2 guidance systems combined two gyroscopes and a lateral accelerometer with a simple analog computer to adjust the azimuth for the rocket in flight. Analog computer signals were used to drive four graphite rudders in the rocket exhaust for flight control. The GN&C (Guidance, Navigation, and Control) system for the V2 provided many innovations as an integrated platform with closed loop guidance. At the end of the war von Braun engineered the surrender of 500 of his top rocket scientists, along with plans and test vehicles, to the Americans. They arrived at Fort Bliss, Texas in 1945 under the provisions of Operation Paperclip and were subsequently moved to Huntsville, Alabama, in 1950 where they worked for U.S. Army rocket research programs. In the early 1950s, the US government wanted to insulate itself against over-dependency on the German team for military applications, including the development of a fully domestic missile guidance program. The MIT Instrumentation Laboratory (later to become the Charles Stark Draper Laboratory, Inc.) was chosen by the Air Force Western Development Division to provide a self-contained guidance system backup to Convair in San Diego for the new Atlas intercontinental ballistic missile (Construction and testing were completed by Arma Division of AmBosch Arma). The technical monitor for the MIT task was engineer Jim Fletcher, who later served as NASA Administrator.
The Atlas guidance system was to be a combination of an on-board autonomous system and a ground-based tracking and command system. The self-contained system finally prevailed in ballistic missile applications for obvious reasons. In space exploration, a mixture of the two remains. In the summer of 1952, Dr. Richard Battin and Dr, J. Halcombe "Hal" Laning, Jr., researched computational based solutions to guidance and undertook the initial analytical work on the Atlas inertial guidance in 1954. Other key figures at Convair were Charlie Bossart, the Chief Engineer, and Walter Schweidetzky, head of the guidance group. Schweidetzky had worked with von Braun at Peenemünde during World War II. The initial Delta guidance system assessed the difference in position from a reference trajectory. A velocity to be gained (VGO) calculation is made to correct the current trajectory with the objective of driving VGO to zero. The mathematics of this approach were fundamentally valid, but dropped because of the challenges in accurate inertial guidance and analog computing power. The challenges faced by the Delta efforts were overcome by the Q system (see Q-guidance) of guidance. The Q system's revolution was to bind the challenges of missile guidance (and associated equations of motion) in the matrix Q. The Q matrix represents the partial derivatives of the velocity with respect to the position vector. A key feature of this approach allowed for the components of the vector cross product (v, xdv, /dt) to be used as the basic autopilot rate signals—a technique that became known as cross-product steering. The Q-system was presented at the first Technical Symposium on Ballistic Missiles held at the Ramo-Wooldridge Corporation in Los Angeles on 21 and 22 June 1956. The Q system was classified information through the 1960s. Derivations of this guidance are used for today's missiles.
In February 1961 NASA awarded MIT a contract for preliminary design study of a guidance and navigation system for the Apollo program. MIT and the Delco Electronics Div. of General Motors Corp. were awarded the joint contract for design and production of the Apollo Guidance and Navigation systems for the Command Module and the Lunar Module. Delco produced the IMUs (Inertial Measurement Units) for these systems, Kollsman Instrument Corp. produced the Optical Systems, and the Apollo Guidance Computer was built by Raytheon under subcontract. For the Space Shuttle, open loop guidance was used to guide the Shuttle from lift-off until Solid Rocket Booster (SRB) separation. After SRB separation the primary Space Shuttle guidance is named PEG (Powered Explicit Guidance). PEG takes into account both the Q system and the predictor-corrector attributes of the original "Delta" System (PEG Guidance). Although many updates to the Shuttle's navigation system had taken place over the last 30 years (ex. GPS in the OI-22 build), the guidance core of the Shuttle GN&C system had evolved little. Within a crewed system, there is a human interface needed for the guidance system. As astronauts are the customer for the system, many new teams were formed that touch GN&C as it is a primary interface to "fly" the vehicle.
INSs contain Inertial Measurement Units (IMUs) which have angular and linear accelerometers (for changes in position); some IMUs include a gyroscopic element (for maintaining an absolute angular reference). Angular accelerometers measure how the vehicle is rotating in space. Generally, there is at least one sensor for each of the three axes: pitch (nose up and down), yaw (nose left and right) and roll (clockwise or counter-clockwise from the cockpit). Linear accelerometers measure non-gravitational accelerations of the vehicle. Since it can move in three axes (up and down, left and right, forward and back), there is a linear accelerometer for each axis. A computer continually calculates the vehicle's current position. First, for each of the six degrees of freedom (x,y,z and θx, θy and θz), it integrates over time the sensed acceleration, together with an estimate of gravity, to calculate the current velocity. Then it integrates the velocity to calculate the current position. Inertial guidance is difficult without computers. The desire to use inertial guidance in the Minuteman missile and Project Apollo drove early attempts to miniaturize computers. Inertial guidance systems are now usually combined with satellite navigation systems through a digital filtering system. The inertial system provides short term data, while the satellite system corrects accumulated errors of the inertial system. An inertial guidance system that will operate near the surface of the earth must incorporate Schuler tuning so that its platform will continue pointing towards the center of the Earth as a vehicle moves from place to place.
Figure 1: GitHub - nqkhanh2002/ADAS-LDWS-LKAS-FCWS: Development of a lane ... Some systems place the linear accelerometers on a gimballed gyrostabilized platform. The gimbals are a set of three rings, each with a pair of bearings initially at right angles. They let the platform twist about any rotational axis (or, rather, they let the platform keep the same orientation while the vehicle rotates around it). There are two gyroscopes (usually) on the platform.
Two gyroscopes are used to cancel gyroscopic precession, the tendency of a gyroscope to twist at right angles to an input torque. By mounting a pair of gyroscopes (of the same rotational inertia and spinning at the same speed in opposite directions) at right angles the precessions are cancelled and the platform will resist twisting. This system allows a vehicle's roll, pitch and yaw angles to be measured directly at the bearings of the gimbals. Relatively simple electronic circuits can be used to add up the linear accelerations, because the directions of the linear accelerometers do not change. The big disadvantage of this scheme is that it uses many expensive precision mechanical parts. It also has moving parts that can wear out or jam and is vulnerable to gimbal lock. The primary guidance system of the Apollo spacecraft used a three-axis gyrostabilized platform, feeding data to the Apollo Guidance Computer. Maneuvers had to be carefully planned to avoid gimbal lock.
Less-expensive navigation systems, intended for use in automobiles, may use a vibrating structure gyroscope to detect changes in heading and the odometer pickup to measure distance covered along the vehicle's track. This type of system is much less accurate than a higher-end INS, but it is adequate for the typical automobile application where GPS is the primary navigation system and dead reckoning is only needed to fill gaps in GPS coverage when buildings or terrain block the satellite signals.
If a standing wave is induced in a hemispheric resonant structure and then the resonant structure is rotated, the spherical harmonic standing wave rotates through an angle different from the quartz resonator structure due to the Coriolis force. The movement of the outer case with respect to the standing wave pattern is proportional to the total rotation angle and can be sensed by appropriate electronics. The system resonators are machined from fused quartz due to its excellent mechanical properties. The electrodes that drive and sense the standing waves are deposited directly onto separate quartz structures that surround the resonator. These gyros can operate in either a whole angle mode (which gives them nearly unlimited rate capability) or a force rebalance mode that holds the standing wave in a fixed orientation with respect to the gyro housing (which gives them much better accuracy). This system has almost no moving parts and is very accurate. However it is still relatively expensive due to the cost of the precision ground and polished hollow quartz hemispheres. Northrop Grumman currently manufactures IMUs (inertial measurement units) for spacecraft that use HRGs. These IMUs have demonstrated extremely high reliability since their initial use in 1996. Safran manufactures large numbers of HRG based inertial navigation systems dedicated to a wide range of applications.
These products include "tuning fork gyros". Here, the gyro is designed as an electronically driven tuning fork, often fabricated out of a single piece of quartz or silicon. Such gyros operate in accordance with the dynamic theory that when an angle rate is applied to a translating body, a Coriolis force is generated. This system is usually integrated on a silicon chip. It has two mass-balanced quartz tuning forks, arranged "handle-to-handle" so forces cancel. Aluminum electrodes evaporated onto the forks and the underlying chip both drive and sense the motion. The system is both manufacturable and inexpensive. Since quartz is dimensionally stable, the system can be accurate. As the forks are twisted about the axis of the handle, the vibration of the tines tends to continue in the same plane of motion. This motion has to be resisted by electrostatic forces from the electrodes under the tines. By measuring the difference in capacitance between the two tines of a fork, the system can determine the rate of angular motion. Current state-of-the-art non-military technology (as of 2005) can build small solid-state sensors that can measure human body movements. These devices have no moving parts and weigh about 50 grams (2 ounces). Solid-state devices using the same physical principles are used for image stabilization in small cameras or camcorders. These can be extremely small, around 5 millimetres (0.20 inches) and are built with microelectromechanical systems (MEMS) technologies.
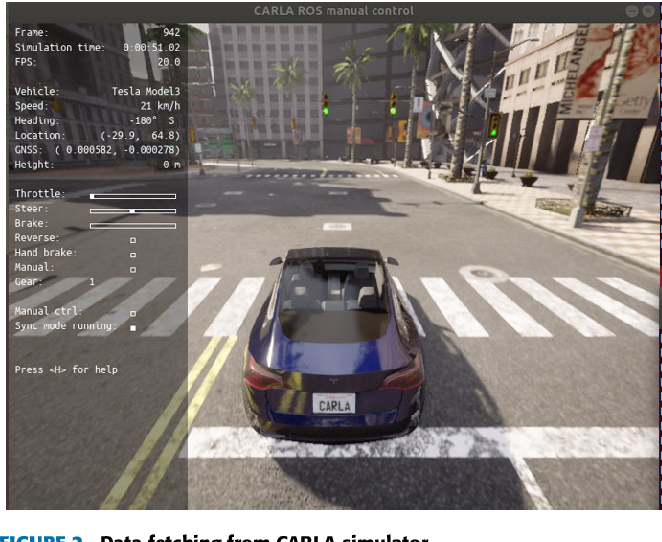
Figure 2: Figure 2 from Securing Autonomous Vehicles Against GPS Spoofing Attacks ... MEMS gyroscopes typically rely on the Coriolis effect to measure angular velocity. It consists of a resonating proof mass mounted in silicon. The gyroscope is, unlike an accelerometer, an active sensor. The proof mass is pushed back and forth by driving combs. A rotation of the gyroscope generates a Coriolis force that is acting on the mass which results in a motion in a different direction. The motion in this direction is measured by electrodes and represents the rate of turn.
A ring laser gyro (RLG) splits a beam of laser light into two beams in opposite directions through narrow tunnels in a closed circular optical path around the perimeter of a triangular block of temperature-stable Cervit glass with reflecting mirrors placed in each corner. When the gyro is rotating at some angular rate, the distance traveled by each beam will differ—the shorter path being opposite to the rotation. The phase shift between the two beams can be measured by an interferometer and is proportional to the rate of rotation (Sagnac effect). In practice, at low rotation rates the output frequency can drop to zero as the result of backscattering causing the beams to synchronise and lock together. This is known as a lock-in, or laser-lock. The result is that there is no change in the interference pattern and therefore no measurement change. To unlock the counter-rotating light beams, laser gyros either have independent light paths for the two directions (usually in fiber optic gyros), or the laser gyro is mounted on a piezo-electric dither motor that rapidly vibrates the laser ring back and forth about its input axis through the lock-in region to decouple the light waves. The shaker is the most accurate, because both light beams use exactly the same path. Thus laser gyros retain moving parts, but they do not move as far.
A more recent variation on the optical gyroscope, the fiber optic gyroscope (FOG), uses an external laser and two beams going opposite directions (counter-propagating) in long spools (several kilometers) of fiber optic filament, with the phase difference of the two beams compared after their travel through the spools of fiber. The basic mechanism, monochromatic laser light travelling in opposite paths and the Sagnac effect, is the same in a FOG and a RLG, but the engineering details are substantially different in the FOG compared to earlier laser gyros. Precise winding of the fiber-optic coil is required to ensure the paths taken by the light in opposite directions are as similar as possible. The FOG requires more complex calibrations than a laser ring gyro making the development and manufacture of FOG's more technically challenging that for a RLG.
However FOG's do not suffer from laser lock at low speeds and do not need to contain any moving parts, increasing the maximum potential accuracy and lifespan of a FOG over an equivalent RLG. The basic, open-loop accelerometer consists of a mass attached to a spring. The mass is constrained to move only in line with the spring. Acceleration causes deflection of the mass and the offset distance is measured. The acceleration is derived from the values of deflection distance, mass and the spring constant. The system must also be damped to avoid oscillation. A closed-loop accelerometer achieves higher performance by using a feedback loop to cancel the deflection, thus keeping the mass nearly stationary. Whenever the mass deflects, the feedback loop causes an electric coil to apply an equally negative force on the mass, canceling the motion. Acceleration is derived from the amount of negative force applied. Because the mass barely moves, the effects of non-linearities of the spring and damping system are greatly reduced. In addition, this accelerometer provides for increased bandwidth beyond the natural frequency of the sensing element. Both types of accelerometers have been manufactured as integrated micro-machinery on silicon chips.
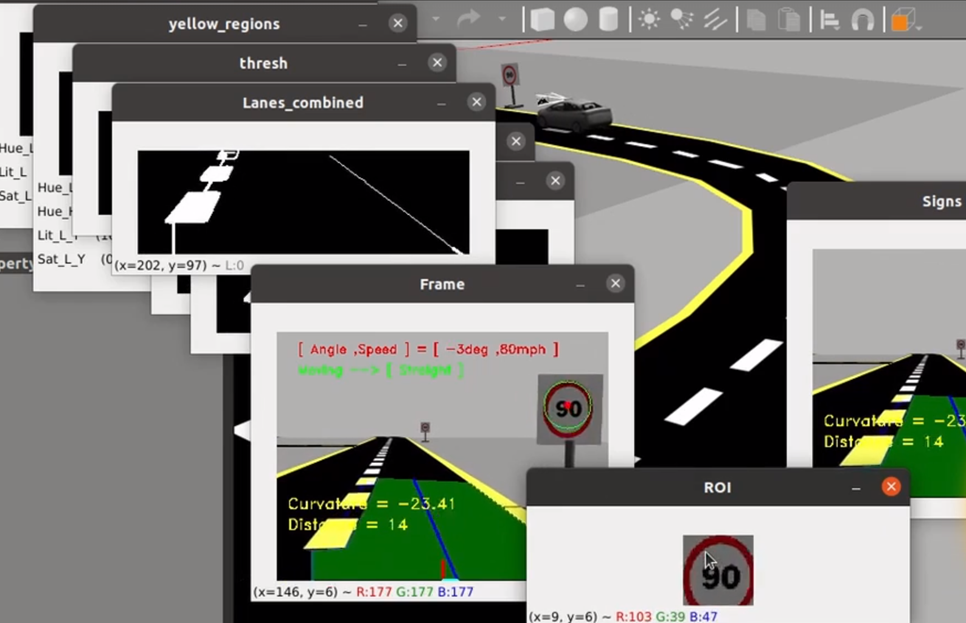
Figure 3: GitHub - suyog800/Autonomous-vehicle-using-ROS: In this project, we ... Where f is specific force, ω {\displaystyle \omega } is angular rate, a is acceleration, R is position, R I {\displaystyle {\dot {R}}} and V are velocity, Ω {\displaystyle \Omega } is the angular velocity of the earth, g is the acceleration due to gravity, Φ , λ {\displaystyle \Phi ,\lambda } and h are the NED location parameters. Also, super/subscripts of E, I and B are representing variables in the Earth centered, inertial or body reference frame, respectively and C is a transformation of reference frames.
Autonomous vehicles (AVs) are poised to revolutionize modern transportation, offering enhanced safety, efficiency, and convenience. However, the increasing complexity and connectivity of AV systems introduce significant cybersecurity challenges. This paper provides a comprehensive survey of AV security with a focus on threat modeling frameworks, including STRIDE, DREAD, and MITRE ATT&CK, to systematically identify and mitigate potential risks. The survey examines key components of AV architectures, such as sensors, communication modules, and electronic control units (ECUs), and explores common attack vectors like wireless communication exploits, sensor spoofing, and firmware vulnerabilities. Through case studies of real-world incidents, such as the Jeep Cherokee and Tesla Model S exploits, the paper highlights the critical need for robust security measures. Emerging technologies, including blockchain for secure Vehicle-to-Everything (V2X) communication, AI-driven threat detection, and secure Over-The-Air (OTA) updates, are discussed as potential solutions to mitigate evolving threats. The paper also addresses legal and ethical considerations, emphasizing data privacy, user safety, and regulatory compliance. By combining threat modeling frameworks, multi-layered security strategies, and proactive defenses, this survey offers insights and recommendations for enhancing the cybersecurity of autonomous vehicles.
Autonomous vehicles (AVs) represent a transformative shift in transportation technology, promising increased safety, efficiency, and convenience in modern mobility systems. These vehicles rely on a combination of sensors, machine learning, and real-time decision-making algorithms to navigate and interact with their environment without human intervention. According to the Society of Automotive Engineers (SAE), AVs are classified into six levels of automation, ranging from Level 0 (no automation) to Level 5 (full automation), with varying degrees of driver involvement and autonomy across levels [ 1 ] . As AVs progress toward higher levels of autonomy, their reliance on interconnected systems such as Vehicle-to-Vehicle (V2V), Vehicle-to-Infrastructure (V2I), and Vehicle-to-Everything (V2X) communication increases [ 2 ] . These communication protocols allow AVs to share information, enhance situational awareness, and improve overall driving decisions. However, this interconnectivity also exposes AVs to a wide range of cybersecurity threats, making security a critical aspect of their deployment and adoption [ 3 ] .
The evolution of AV technology has been paralleled by a growing complexity in cybersecurity challenges. Early vehicles with limited connectivity relied on isolated in-vehicle networks such as the Controller Area Network (CAN), which were susceptible primarily to physical attacks [ 4 ] . As AVs adopted more sophisticated communication protocols and incorporated cloud-based and edge computing systems, they became increasingly vulnerable to remote attacks via wireless communication channels such as WiFi, Bluetooth, and cellular networks [ 5 ] Recent advancements in Artificial Intelligence (AI) and the Internet of Things (IoT) have further complicated AV security landscapes. AI-based models enhance AV capabilities in perception, decision-making, and anomaly detection but are also vulnerable to adversarial attacks that exploit system blind spots [ 6 ] . IoT integration has expanded attack surfaces, allowing cyber adversaries to target not only AV systems but also interconnected devices and infrastructure [ 2 ] .
The security of autonomous vehicles is paramount, as vulnerabilities in AV systems can lead to catastrophic outcomes. Cyberattacks targeting AVs may compromise the vehicle’s control, navigation, or decision-making systems, posing risks not only to passengers but also to other road users and infrastructure [ 7 ] . Incidents such as remote hijacking of vehicle systems, sensor spoofing, and unauthorized access to critical networks have underscored the potential dangers associated with AV security breaches [ 8 , 4 ] . In addition to safety concerns, the financial and reputational damage to automakers and service providers can be substantial if they fail to adequately protect their AV systems from cyber threats. Furthermore, the integration of personal data and location-based services into AVs raises significant privacy concerns, which must be addressed through robust security measures [ 3 ] .
This survey paper provides an in-depth review of autonomous vehicle (AV) security, with a primary focus on threat modeling to identify and categorize potential risks to AV systems. It systematically examines the threats and vulnerabilities that affect AVs, leveraging threat modeling frameworks like STRIDE and DREAD to assess the likelihood and impact of attacks on key components such as sensors, GPS systems, and communication modules. The survey also reviews security countermeasures, from cryptographic methods and secure protocols to AI-based anomaly detection systems, highlighting how each aligns with specific threat models. In addition to technical solutions, the paper discusses regulatory considerations, emphasizing the importance of proactive threat modeling in shaping secure AV standards. Covering both in-vehicle systems and external infrastructure, this survey identifies open problems and proposes future research directions focused on advancing robust, threat-model-driven security strategies for autonomous vehicles.
The remainder of this paper is organized as follows: Section II presents an overview of autonomous vehicle architectures, detailing key components such as sensors, communication systems, and Electronic Control Units (ECUs). Case studies of various vehicle architectures, including the Jeep Cherokee, Lexus, and Tesla, are provided to illustrate the technological underpinnings of modern AV systems. Section III analyzes the primary cybersecurity threats faced by AVs. It examines common attack vectors such as wireless communication exploits, sensor spoofing, and firmware vulnerabilities. Real-world case studies are included to demonstrate the practical implications of these security challenges. Section IV introduces and evaluates prominent threat modeling frameworks, including attack-centric, asset-centric, and software-centric approaches. It also discusses methodologies such as attack trees and the MITRE ATT&CK framework for systematically identifying and categorizing potential threats and vulnerabilities. Section V applies the STRIDE and DREAD threat modeling frameworks to AV architectures. Threats are categorized and assessed for impact, and a comprehensive risk evaluation table is presented to prioritize mitigation strategies based on severity and exploitability. Section VI provides a comparative analysis of STRIDE, DREAD, and MITRE ATT&CK frameworks. The strengths, limitations, and applicability of each approach to AV security are discussed, with recommendations for integrating multiple frameworks to achieve a comprehensive threat assessment. Section VII addresses the legal and ethical challenges associated with AV security, including data privacy, user safety, transparency, and regulatory compliance. Relevant standards and regulations, such as GDPR, ISO/SAE 21434, and UNECE WP.29, are examined in the context of AV development and deployment. Section VIII explores emerging technologies and research directions in AV security, including blockchain-based V2X communication, AI-driven threat detection, and secure Over-The-Air (OTA) update mechanisms. Practical recommendations for AV developers, policymakers, and researchers are proposed.
Section IX synthesizes the key findings and contributions of the paper, emphasizing the importance of robust cybersecurity measures and identifying future research opportunities to enhance AV security. 2. System Architecture & Core Working Principles This section introduces Autonomous Vehicles (AVs) and their architectures and presents a case study of three vehicles, namely, Jeep Cherokee, Lexus and Tesla, under complex cyber-attacks. Vehicles are rapidly advancing toward full autonomy by integrating sensors and vehicular networks into their control systems. The Society of Automotive Engineers (SAE), in its J3016 standard [ 9 , 10 ] , defines six levels of autonomy, ranging from level 0 (no autonomy) to level 5 (complete autonomy), as outlined in Table I . With the growing autonomy of vehicles, there is an increasing reliance on situational awareness, which is achieved through data-driven machine learning algorithms and artificial intelligence, powered by onboard sensor networks and external communications [ 11 , 12 ] . Policymakers predict that the global autonomous vehicle (AV) market could reach $7 trillion by 2050, leading to enhanced transportation efficiency, fewer accidents, improved safety, and reduced environmental impact [ 13 ] .
Contrary to popular belief, most modern vehicles are equipped with connected technologies, placing them between Level 2 and Level 4 autonomy. Even basic cars today contain at least 30 Electronic Control Units (ECUs), while luxury models may have up to 100 ECUs, managing over 100 million lines of code [ 14 , 15 ] . Each ECU [ 16 ] functions as a standalone computer, featuring a microprocessor and interfacing with sensors, actuators, and communication networks to perform various tasks, from operating turn signals to regulating the engine’s air-fuel ratio. These ECUs communicate via different buses, such as the Controller Area Network (CAN), Ethernet, FlexRay, and Local Interconnect Network (LIN), which vary in specifications, speed, and cost depending on the control requirements. In addition, modern vehicles are equipped with satellite communications (for satellite radio and navigation systems), cellular networks, WiFi, and Bluetooth. These features, typically managed through an infotainment system or head unit [ 17 ] , offer drivers enhanced comfort and seamless control.
Semi-autonomous vehicles also include embedded SIMs (eSIMs) that transmit telematics data to cloud servers, enabling vehicle owners to manage, track, and operate their cars using smartphone applications. These cloud-based features facilitate large-scale data collection and continual vehicle improvements, boosting performance and capabilities. The inclusion of eSIMs also allows for over-the-air (OTA) software updates, enabling manufacturers to enhance a vehicle’s functionality over time as technology evolves and components age. Researchers and automotive developers are working on Vehicle-to-Everything (V2X) communication systems, utilizing 802.11p (Wireless Local Area Network (WLAN)) and C-V2X, a cellular-based system powered by 5G and future technologies. All these technologies, integrated through the head unit, provide users with unprecedented access and control over their vehicles [ 5 , 18 , 4 ] Autonomous vehicle (AV) architectures have evolved significantly, incorporating advanced technologies such as high-performance computing, artificial intelligence, and robust communication networks. This section provides an updated overview of AV architectures, highlighting developments in sensor integration, network infrastructure, and connectivity solutions that support advanced driving functions.
Multi-Sensor Fusion and High-Resolution Sensing Layer: Modern AVs use a complex array of sensors, including LiDAR, radar, cameras, and ultrasonic sensors, to build a comprehensive environmental model. Sensor fusion, which combines data from multiple sources, allows AVs to achieve greater accuracy and reliability in object detection and environmental awareness. Recent architectures incorporate AI-based sensor fusion algorithms that dynamically adjust to changing road conditions, reducing noise and inaccuracies in real-time [ 19 ] . Example: Tesla’s FSD (Full Self-Driving) architecture has evolved to process multiple video frames from an array of onboard cameras, utilizing neural networks that allow the system to predict object trajectories. By fusing radar and camera data, Tesla’s architecture minimizes reliance on LiDAR, favoring a vision-based approach to environmental perception [ 6 ] .
igh-Performance Computing and AI Processing Units: Current AVs integrate specialized high-performance computing (HPC) units designed to handle complex data processing for real-time decision-making. These HPC systems often contain GPUs, TPUs, or dedicated AI processors optimized for deep learning tasks, allowing for rapid processing of sensor data and execution of driving algorithms. Example: Nvidia’s DRIVE AGX platform is widely used in AV architectures for its powerful AI processing capabilities, handling tasks like perception, mapping, and path planning. By incorporating real-time parallel processing, DRIVE AGX enables AVs to make instantaneous decisions, even in highly dynamic environments [ 20 ] .
Enhanced Intra-Vehicle Network Architecture: The Controller Area Network (CAN) bus, traditionally used for intra-vehicle communication, is increasingly being supplemented or replaced by high-speed Ethernet networks that support the substantial data throughput required by modern AVs. Automotive Ethernet reduces latency and enhances data exchange rates, making it suitable for real-time processing and communication between critical subsystems like sensors, AI processors, and control modules. Example: Tesla’s architecture leverages Automotive Ethernet, which allows efficient data exchange between various Electronic Control Units (ECUs) and the centralized computing unit. This setup facilitates rapid processing of high-bandwidth data, essential for advanced functionalities such as autonomous navigation and over-the-air (OTA) updates [ 21 ] .
V2X (Vehicle-to-Everything) Communication Layer: V2X technology is now a critical component in AV architectures, enabling AVs to interact with infrastructure (V2I), other vehicles (V2V), pedestrians (V2P), and networks (V2N). This layer enhances situational awareness and supports cooperative driving, improving traffic efficiency and safety. V2X technology is often built on 5G and Cellular V2X (C-V2X) networks, which provide the low latency and high data transfer rates required for real-time data exchange. Example: Ford and other automakers are integrating C-V2X as part of their AV communication infrastructure, leveraging 5G for fast and secure data exchange that enables vehicles to respond proactively to road hazards and traffic signals. V2X communication also improves data sharing in complex environments, enabling better route planning and situational awareness [ 22 ] .
Cloud-Based and Edge Computing Integration:1 To manage the vast data generated by AVs, modern architectures are increasingly integrating cloud and edge computing. The cloud allows for large-scale data storage and analysis, enabling long-term learning and system updates, while edge computing provides localized data processing, reducing latency and improving responsiveness. This hybrid approach enables AVs to perform real-time decision-making with minimal delays while accessing cloud-stored data for high-level insights and updates. Example: Waymo utilizes a cloud-edge architecture where critical, low-latency tasks are processed locally on the AV, while non-urgent data, like map updates and historical driving data, is stored and processed in the cloud. This setup allows for a balance between immediate data processing needs and centralized learning for continuous improvements [ 23 ] .
Applications Layer: AI-Driven Decision-Making and Control: At the highest level, AVs use AI-driven systems to support applications like perception, localization, decision-making, and control. Advanced machine learning models process data from the sensing and network layers to understand the vehicle’s environment, predict potential hazards, and make real-time driving decisions. Reinforcement learning and neural networks are increasingly employed to optimize driving strategies, allowing AVs to learn from experience and improve over time. Example: AI models in AVs like those used by Waymo and Uber’s autonomous fleets support real-time path planning and adaptive control systems, allowing these vehicles to navigate safely and adapt to unexpected conditions on the road. These systems are designed to improve over time through self-learning mechanisms that enhance driving behavior with each trip [ 19 ] .
The evolution of AV architectures reflects the increasing complexity of autonomous driving technology. By integrating high-speed networks, advanced AI processors, multi-sensor fusion, and robust V2X communication systems, these architectures support the computational and communication demands of modern AV systems. This layered approach enables AVs to perform intricate perception, planning, and decision-making tasks necessary for safe and efficient autonomous navigation in real-world environments.
A vehicle network interlinks all the Electronic Control Units (ECUs) within a vehicle, executing essential functions such as managing the engine and transmission. In autonomous vehicles, this network facilitates autonomous operations by enabling data sharing and the integration of advanced AI-driven sensors into the vehicle’s systems. Semi- and fully autonomous vehicles are equipped with head units that connect to various vehicle networks, providing WiFi, Bluetooth, and cellular communications. The architecture of vehicle networks is highly varied, depending on the manufacturer, vehicle features, and pricing. Figure 1 illustrates the network architecture of a Jeep Cherokee (Level 2-3 Autonomy), which features a Controller Area Network Critical (CAN-C), a Controller Area Network Interior High Speed (CAN-IHS), and a Local Interconnect Network (LIN). The CAN-C network connects all critical Electronic Control Units (ECUs), such as the Anti-lock Braking System (ABS) unit and engine control systems, managing essential vehicle operations. The Body Control Module (BCM) interfaces with both the CAN-C and LIN, controlling sensors and actuators on the vehicle’s body based on inputs from the CAN. Additionally, the CAN-C interconnects with the head unit through the CAN-IHS.
Figure 2 presents the network architecture of a Lexus (Level 3-4 Autonomy), which differs from that of the Jeep Cherokee depicted in Figure 1 The Lexus features a Central Gateway ECU that connects various Controller Area Network (CAN) networks. Specifically, the Lexus includes: Body Electrical CAN: This network connects to the Main Body ECU, which manages all body functions of the vehicle via a Local Interconnect Network (LIN).
Powertrain CAN: This network facilitates communication among all systems involved in the powertrain, encompassing components that generate energy for the vehicle, such as the engine and transmission. Infotainment CAN: This network links entertainment units within the vehicle, connecting the head unit, clock, touchpad, etc., while also providing WiFi, Bluetooth, and cellular connectivity.
Figure 3 illustrates the network architecture of a Tesla (Level 4-5 Autonomy), which differs significantly from the architectures of both the Lexus and the Jeep. Tesla employs Automotive Ethernet to interconnect all its Electronic Control Units (ECUs). This standard is specifically designed to meet the requirements of automotive applications, offering low susceptibility to electromagnetic and radio emissions, high bandwidth, and low latency. Additionally, Tesla utilizes a Linux-based NVIDIA head unit that manages all vehicle operations through a Controller Area Network (CAN) bus.
Figure 4 depicts the complexity of a vehicle’s wiring harness at automation levels 2 or 3. The wiring harness has become increasingly intricate due to the integration of sensors and networks, reflecting the growing demands of modern automotive technology. As discussed in previous sections, semi- and fully autonomous vehicles feature complex network architectures that differ based on the level of autonomy and price range. These architectures will only grow more intricate as vehicles become increasingly autonomous and interconnected. Furthermore, the earlier sections illustrate that even well-designed vehicles can harbor vulnerabilities, which attackers can exploit either in person or remotely to cause catastrophic failures. This underscores the critical need for a structured threat model to address the evolving security challenges in the automotive industry.
This section introduces a generic architecture for autonomous vehicles (AVs) (Figure 5 ) to support threat modeling. This architecture is organized into four layers: End Devices Layer: This layer consists of Electronic Control Units (ECUs) that manage and control various physical processes within the vehicle. These ECUs are physically connected to sensors, which monitor the vehicle, and actuators, which control its functions. The ECUs communicate over various intra-vehicle networks, such as CAN bus, LIN, MOST, and FlexRay.
3. Software Implementation, Frameworks & Protocols Intra-Vehicle Networking Layer: This layer facilitates communication between the vehicle’s ECUs to support management and control of operations. It consists of: Gateway ECU: Handles all communication with intra-vehicle networking buses (CAN, LIN, MOST, and FlexRay), ensuring message conformance to standards and preventing direct application access to the buses.
Mainboard ECU: Manages the head unit and handles functions like navigation, display, and network management, using Universal Asynchronous Receiver Transmitter (UART) for sending and receiving CAN messages and commands. Telematics Gateway ECU: Manages data switching between the telematics modules and the head unit. OBD-II: Provides vehicle diagnostics and allows users to observe messages on the buses (such as the CAN bus). Through the OBD-II port, users can also send messages to control vehicle behavior.
Vehicle Networks: Networks such as the CAN bus facilitate communication between ECUs controlling critical vehicle functions like the engine and transmission. Inter-Vehicle Networks Layer: This layer connects the AV to external systems like smartphones and cloud services. It includes: Satellite Communications: Provides media broadcasts, real-time traffic updates, and navigation data.
Bluetooth and WiFi: Allows connectivity with smartphones and hotspots, enabling media playback and Over-the-Air (OTA) updates. These networks are managed via the head unit. Applications Layer: This layer consists of cloud services and other applications that provide critical functions for the vehicle’s autonomous operations.
The growing complexity and interconnectedness of modern vehicles make them increasingly vulnerable to cyberattacks. Legacy vehicles that relied on CAN and LIN networks were susceptible to attacks targeting their limited onboard sensors and ECUs. With the introduction of Vehicle-to-Everything (V2X) communications in semi- and fully autonomous vehicles, the range of potential attack vectors has expanded, exposing vehicles to remote cyberattacks in addition to traditional ones that target sensors and in-vehicle networks. Connected vehicles primarily use wireless communication (with exceptions such as electric vehicles during charging), which presents easy targets for attackers. By exploiting wireless channels, such as WiFi, Bluetooth, or cellular connections, attackers can compromise an ECU and escalate to more sophisticated vehicle cyberattacks.
Researchers have already demonstrated successful breaches of vehicles via vulnerabilities in these wireless communication systems. This section examines several real-world security incidents involving autonomous vehicles (AVs), providing insights into evolving threats and highlighting critical vulnerabilities across different AV systems. The analysis includes both historical and recent cases, including the Jeep Cherokee and Tesla Model S attacks, as well as recent vulnerabilities in Tesla Autopilot and Vehicle-to-Everything (V2X) communication systems.
Autonomous vehicles (AVs) rely on interconnected systems, real-time communication, and sophisticated software, making them vulnerable to a wide range of cybersecurity attacks. One major category of attacks is through wireless communication channels such as Wi-Fi [ 25 , 26 , 27 ] , Bluetooth [ 28 , 29 ] , and cellular networks. Exploiting vulnerabilities in these channels allows attackers to execute remote exploits, gaining unauthorized control over vehicle functions. The widely publicized Jeep Cherokee hack by Miller and Valasek (2015) demonstrated how attackers could take control of braking, steering, and acceleration through cellular network vulnerabilities [ 4 ] . Similarly, Vehicle-to-Everything (V2X) communication, which enables AVs to interact with infrastructure (V2I) and other vehicles (V2V), is susceptible to message spoofing, replay attacks, and man-in-the-middle (MITM) attacks, which compromise situational awareness and lead to unsafe decisions [ 7 ] . Sensor spoofing and jamming represent another significant threat [ 30 ] . AVs depend on multiple sensors, including LiDAR, radar, cameras, and GPS, for perception and navigation. Attackers can exploit these sensors by injecting false signals or obstructing genuine signals. For instance, LiDAR spoofing can create phantom obstacles, causing the vehicle to brake suddenly or change lanes unnecessarily [ 31 ] . GPS spoofing attacks can manipulate the vehicle’s geolocation data, resulting in incorrect navigation or route deviations [ 32 ] . Additionally, radar and camera sensors are vulnerable to jamming or blinding attacks that disrupt data collection and processing, impairing the vehicle’s ability to detect objects accurately [ 33 ] . The Controller Area Network (CAN) bus is a critical component in AVs, facilitating communication between Electronic Control Units (ECUs). Due to its lack of encryption and authentication mechanisms, the CAN bus is vulnerable to injection attacks that allow adversaries to send malicious commands to control essential functions like steering, braking, and acceleration. A well-documented example of this vulnerability is the ability to manipulate vehicle behavior through physical access to the CAN bus interface [ 34 ] . These attacks highlight the need for enhanced security protocols within internal vehicle networks. Another vector is firmware and software vulnerabilities, particularly through Over-the-Air (OTA) updates. While OTA updates are crucial for maintaining and improving vehicle software, insecure update mechanisms can be exploited to install malicious firmware. If proper encryption, code-signing, and integrity verification are absent, attackers can compromise the update process to gain persistent control over vehicle functions [ 35 ] . This vulnerability underscores the importance of robust end-to-end encryption and authenticated update procedures to protect against malicious updates [ 36 ] .
As AV technology evolves, new cybersecurity threats are emerging, requiring proactive defenses. AI adversarial attacks pose a significant challenge to AV perception systems, which rely on machine learning models for object recognition and decision-making. In these attacks, adversaries introduce subtle perturbations to sensor inputs, such as images from cameras, causing the AV to misinterpret road signs or fail to detect obstacles [ 37 ] . For example, slight modifications to a stop sign can cause an AV to perceive it as a speed limit sign, potentially leading to dangerous driving behavior [ 38 ] . This vulnerability highlights the need for developing robust and resilient AI models capable of detecting and mitigating adversarial inputs in real-time. Supply chain vulnerabilities also present a growing concern. AVs rely on complex supply chains for hardware components and software systems, often sourced from multiple vendors across different regions. Compromises in the supply chain, such as inserting malicious code during manufacturing or embedding hardware backdoors, can undermine vehicle security [ 39 ] . Recent incidents have demonstrated how vulnerabilities in third-party components can be exploited to bypass security controls, emphasizing the need for rigorous supply chain verification and secure development practices [ 40 ] . Cloud and edge computing vulnerabilities further complicate AV cybersecurity. AVs increasingly depend on cloud-based services and edge computing for data processing, storage, and decision-making. These infrastructures are susceptible to Distributed Denial-of-Service (DDoS) attacks, data breaches, and unauthorized access [ 41 ] . Disruptions to cloud services can lead to delays or failures in critical AV functions, affecting safety and performance. Ensuring secure communication channels, implementing redundancy, and adopting blockchain-based solutions can help mitigate these risks [ 42 ] . Finally, insider threats remain a persistent concern, where individuals with authorized access to AV systems exploit their privileges for malicious purposes. Such threats can arise from disgruntled employees, contractors, or malicious insiders who introduce vulnerabilities or exfiltrate sensitive data [ 43 ] . Implementing zero-trust architectures, multi-factor authentication, and continuous monitoring can help mitigate insider threats by minimizing the potential for unauthorized actions [ 9 ] . Addressing these diverse cybersecurity threats requires a multi-layered approach, combining traditional security measures with emerging technologies like blockchain, AI-driven threat detection, and comprehensive threat modeling frameworks such as STRIDE and MITRE ATT&CK [ 3 , 44 ] . Collaboration between AV developers, cybersecurity researchers, and policymakers is essential to developing robust security strategies that keep pace with evolving threats and ensure the safety and reliability of autonomous vehicles.
Encryption and Authentication: Use end-to-end encryption and mutual authentication protocols like Transport Layer Security (TLS) for all wireless communication [ 3 ] . Network Isolation: Segregating infotainment systems from critical vehicle controls minimizes the impact of wireless exploits [ 4 ] .
Dynamic Watermarking: Embed unique identifiers in sensor signals to detect tampering [ 45 ] . Adversarial Training: Expose AI models to adversarial scenarios during training to increase robustness against manipulated inputs [ 6 ] . Cross-Sensor Validation: Integrate data from multiple sensors (e.g., radar, LiDAR, cameras) to cross-check and validate environmental information [ 22 ] .
Redundancy and Validation: Use diverse sensors to ensure comprehensive cross-validation of sensor data [ 46 ] . Blockchain Technology: Utilize decentralized ledgers to validate V2X messages and prevent spoofing attacks [ 47 ] . 4. Practical Deployment, Analysis & Case Studies Public-Key Infrastructure (PKI): Deploy PKI to ensure the authenticity and integrity of transmitted messages [ 2 ] .
Enhanced Authentication: Implement multi-factor authentication mechanisms for V2X endpoints [ 48 ] . Secure OTA Updates: Use code-signing mechanisms to verify the integrity of over-the-air updates [ 4 ] . Static and Dynamic Analysis: Regularly test AV software for vulnerabilities using automated analysis tools [ 49 ] . Secure Boot Mechanisms: Ensure only authenticated firmware can be executed during system boot-up [ 36 ] .
Runtime Monitoring: Continuously validate system integrity during operation to detect malicious activity [ 44 ] . Intrusion Detection Systems (IDS): Deploy IDS to monitor network traffic and identify anomalous activity [ 3 ] . Message Authentication Codes (MACs): Use MACs to verify the authenticity of messages transmitted over the CAN bus [ 47 ] .
Transparent Communication: Provide detailed updates to users following an attack, explaining the mitigation measures to rebuild trust [ 50 ] . Driver-AI Collaboration Models: Design AV systems that adaptively recalibrate trust levels post-attack through user interaction and feedback mechanisms [ 51 ] .
In 2015, cybersecurity researchers exploited a vulnerability in the Jeep Cherokee’s UConnect infotainment system, remotely gaining control over critical functions, such as braking and steering. By using an exposed port to access the Controller Area Network (CAN) bus, the attackers were able to inject malicious CAN messages that disabled essential safety features. This attack underscored the importance of secure communication channels and authentication in vehicular networks [ 4 ] . Figure 6 illustrates the attack chain. The Jeep Cherokee’s head unit, powered by an Arm Cortex A8 processor with UConnect, provides connectivity through WiFi, Bluetooth, USB, and cellular networks (Sprint 3G), linking the vehicle to external systems. The researchers demonstrated that, with physical access, an attacker could compromise and reprogram the head unit via USB.
Additionally, the researchers targeted the head unit’s WiFi and Bluetooth connections by cracking the password, granting unauthorized access to the vehicle’s network when within visual range. They also discovered that Jeep UConnect, through Sprint’s 3G network, used port 6667 to run D-Bus message daemons, allowing the transmission of unauthenticated commands through Telnet and enabling command-line injection of supported Remote Procedure Call (RPC) methods. Sprint’s 3G network further allowed Sprint devices to communicate over vast distances, creating a nationwide Wide Area Network (WAN). This WAN setup, in conjunction with the exposed port 6667, enabled the creation of a network worm capable of infecting all vulnerable Jeep Cherokees with exposed port 6667.
The researchers developed a worm targeting the Jeep Cherokee’s head unit, which used a Renesas V850 microprocessor, disguising it as a legitimate firmware update. Through this worm, they were able to inject arbitrary CAN messages onto the vehicle’s CAN bus, gaining access to vendor-specific CAN messages used on the CAN-C network (Figure 1 ). This enabled them to remotely control critical vehicle functions, such as killing the engine, disabling the brakes, and disengaging the steering wheel.
Response to Jeep Cherokee Exploit: After the Jeep Cherokee exploit, automakers took steps to isolate critical vehicle control functions from infotainment systems and other non-essential communication channels. Security updates included closing exposed network ports and implementing strict access controls to the CAN bus. These measures aimed to prevent external manipulation of essential vehicle controls through enhanced network segmentation and control channel isolation [ 4 ] .
In 2016, researchers at Tencent Keen Security Lab compromised a Tesla Model S by exploiting vulnerabilities in its onboard WiFi connection and browser. By manipulating the web browser’s access, they gained control over the CAN bus, enabling them to execute commands that affected steering and braking. This attack demonstrated the risk of unsecured wireless communication channels and the potential for remote compromise if external access is not properly managed. They discovered that all Tesla vehicles are configured to automatically connect to the SSID "Tesla Guest," a WiFi hotspot used by Tesla superchargers and body shops. Additionally, the researchers found that the Tesla Model S uses a WebKit-based web browser engine running on a Linux system. The attackers set up a rogue access point named "Tesla Guest," causing the car to automatically connect to their controlled network. Once connected, the attackers exploited a known Linux kernel vulnerability, CV2013-6282 [ 52 ] , to escalate privileges within the WebKit browser. By further targeting vulnerabilities in WebKit, they were able to gain remote shell access and execute custom shellcode. With this elevated WebKit access, the researchers gained control of Tesla’s Central Information Display (CID), which provided access to the Instrument Cluster (IC), as well as the Bluetooth and WiFi modules via Telnet, and the CAN bus through a custom backdoor. To create the CAN bus backdoor, the researchers observed that the Tesla Gateway (Figure 3 ) is enabled for over-the-air (OTA) updates and uses port 3500 for diagnostics, while ports 20100 and 20101 are used for sending CAN messages. By extracting the OTA firmware package from the CID through their privileged access, they modified its Cyclic Redundancy Check (CRC) to bypass the integrity verification. The compromised firmware was then installed on the Gateway via the diagnostics port 3500, enabling the researchers to send malicious CAN messages over User Datagram Protocol (UDP). Figure 7 outlines the entire attack chain.
Additionally, Tesla ECUs have a special diagnostic mode that halts the ECU from sending CAN messages and responding to diagnostic requests. With control over the compromised Gateway, the researchers were able to force any ECU into this diagnostic mode, effectively disabling critical vehicle systems. This allowed them to deactivate essential safety features such as the Electronic Stability Program (ESP), the Anti-lock Braking System (ABS), and the power-assisted chassis, rendering these systems non-functional. Tesla’s Mitigation for Model S Wireless Exploit: In response to the wireless exploit, Tesla deployed over-the-air (OTA) updates to secure the WiFi and browser components of its vehicles, limiting external access to critical systems. Tesla also introduced stricter network access controls and improved the authentication protocols to prevent unauthorized access to CAN bus commands, reinforcing protection against remote attacks on the vehicle’s control systems In 2021, researchers demonstrated how Tesla’s Autopilot could be misled through adversarial attacks on the vehicle’s visual recognition systems. By subtly altering road signs or lane markings, attackers could influence the Autopilot system to misinterpret inputs, causing unsafe lane changes or sudden stops. This exploit illustrated the vulnerability of AVs to image-based manipulation and the need for robust AI training against adversarial inputs [ 6 ] Countermeasures for Adversarial Attacks on Tesla Autopilot: To counteract adversarial threats, Tesla began enhancing its AI models through adversarial training, exposing the system to manipulated inputs to make it more resilient to subtle image-based distortions. Tesla also implemented cross-sensor validation, where visual data is cross-referenced with radar or LiDAR inputs, adding an additional layer of verification before actions like lane changes or braking are executed [ 6 ] .
Vehicle-to-Everything (V2X) communication systems facilitate data exchange between AVs and infrastructure (such as traffic lights and road signs), improving traffic management and safety. However, these systems are vulnerable to spoofing attacks, where attackers inject false information into the network. In a V2X spoofing scenario, a vehicle could receive a false warning about obstacles or phantom vehicles, prompting unsafe braking or swerving. This attack highlights the critical need for V2X message authentication to ensure data integrity and secure communication [ 47 ] . Defenses Against V2X Communication Spoofing: To mitigate V2X communication attacks, researchers are exploring the use of blockchain and public-key infrastructure (PKI) for secure message authentication. Blockchain can offer a tamper-resistant ledger to validate message authenticity, while PKI can secure V2X data exchanges, ensuring that only legitimate data influences AV responses. These cryptographic solutions aim to safeguard V2X networks from spoofing and tampering, allowing AVs to communicate securely with infrastructure and other vehicles [ 22 ] .
Threat modeling is a structured process to assess potential actions attackers might take, identify security vulnerabilities and threats within a system or its components, and determine which assets could be exploited. This process provides valuable insights for protecting the target system or sub-system against attacks and helps develop realistic and effective security requirements [ 53 ] .
Various methods of conducting threat modeling on a system emphasize different aspects such as assets, attackers, software, or system vulnerabilities. The following are some of the key threat modeling approaches that can be applied to a system: Attack-centric modeling focuses on understanding attackers’ goals, motivations, and required skills to target a specific system [ 53 ] . By analyzing the attacker’s perspective, we can gain insight into their objectives, identify the most vulnerable assets, and design effective mitigation strategies to counter their actions. A notable example of an attack-centric threat model is the Intel Threat Agent Library (TAL) [ 54 ] . TAL standardizes a set of agents that pose threats to IT systems and classifies them based on eight key questions: 1) the outcome of the threat, 2) the resources available to the attacker, 3) whether the attacker intends to cause harm, 4) the limitations that could hinder the attack, 5) the attacker’s objective, 6) the identity of the threat, 7) the skills required to carry out the attack, and 8) the attacker’s goals. Another example of threat modeling is Intel’s Threat Agent Risk Assessment (TARA) [ 54 ] . TARA helps identify all potential attacks on a system and determines the most likely attack scenarios based on the Intel Threat Agent Library (TAL). This method provides a focused approach to assessing risks and prioritizing mitigation strategies by evaluating the probability of specific threats.
5. Performance Evaluation & Extended Technical Observations Asset-centric threat modeling focuses on the system’s assets and how to protect them from various attacks [ 54 ] . This approach involves identifying attack surfaces, assessing vulnerabilities, and pinpointing critical assets whose compromise would cause the most harm to the system. An example of asset-centric threat modeling is the Operationally Critical Threat, Asset, and Vulnerability Evaluation (OCTAVE) [ 55 ] , which includes the following four phases: 1) defining risk measurement criteria, 2) profiling critical assets, 3) identifying threats to those assets, and 4) conducting risk analysis and developing mitigation strategies. Another example is the Threat, Vulnerability, and Risk Analysis (TVRA) [ 56 ] . The TVRA model outlines the security requirements and objectives for each asset in the system, performs vulnerability scanning, and assesses the likelihood of potential threats.
In threat-centric and vulnerability modeling, high-priority vulnerabilities are identified, and mitigation techniques are developed to address them [ 54 , 49 ] . An example of this approach is Skybox Threat-Centric Vulnerability Management (TCVM), which generates a comprehensive list of vulnerabilities and then prioritizes them based on their potential impact and likelihood of exploitation. This method helps focus mitigation efforts on the most critical vulnerabilities.
Software-centric threat modeling, also known as design-centric threat modeling, focuses on the software components of a system during the design phase. This approach helps identify potential threats to each component [ 54 ] . A well-known example of software-centric threat modeling is Microsoft’s STRIDE model, which stands for Spoofing, Tampering, Repudiation, Information Disclosure, Denial of Service, and Elevation of Privilege. STRIDE is used to identify and address potential threats across these categories, making it particularly useful for systems like autonomous vehicles.
An attack tree is a visual representation of an attack, structured like a tree [ 57 ] . The root node represents the attacker’s primary goal, while the intermediate nodes, or sub-goals, illustrate the various stages of the attack. For the attack to succeed, all sub-goals in a particular branch must be achieved. The leaf nodes represent atomic attacks—individual actions required to complete an attack. Each attack scenario is composed of the minimum set of nodes. Attack trees are useful for representing multiple possible attack paths on a system, aiding in risk analysis, and identifying potential attack surfaces that an attacker could exploit.
MITRE ATT&CK (Adversarial Tactics, Techniques, and Common Knowledge) is a publicly accessible knowledge base of adversary tactics and techniques, derived from real-world observations of cyberattacks [ 58 ] . It serves as a foundation for developing threat models and methodologies across various sectors, including government, private companies, and the cybersecurity product and service community. MITRE ATT&CK catalogs strategies that attackers use to execute successful attacks and lists the techniques that can implement these strategies. **Tactics** represent what an attacker aims to achieve, while **techniques** describe how the attacker accomplishes these objectives.
ATT&CK for Enterprise focuses on adversarial behavior across Windows, macOS, Linux, and cloud environments. ATT&CK for ICS addresses adversarial behavior in Industrial Control Systems (ICS) networks. In ATT&CK for ICS, approximately 300 attack tactics are organized in the knowledge base and categorized by threats, attack processes, and techniques. The relationship between tactics and techniques is visually represented through the ATT&CK matrix [ 59 ] .
A threat model provides a structured approach to analyzing a system by examining each threat and identifying appropriate mitigation techniques. For this threat model, we use both the STRIDE and DREAD models to perform threat analysis and develop countermeasures. STRIDE is a widely used threat modeling framework introduced in 1999 and popularized by Microsoft in 2002. The acronym STRIDE stands for six categories of threats that the model focuses on to evaluate a system’s security: S: Spoofing - Attacks where an attacker impersonates someone or something else, compromising system authentication.
T: Tampering - Attacks where an attacker alters or modifies data, either on disks, networks, or in memory, compromising data integrity. R: Repudiation - Attacks where entities deny performing actions, often due to inadequate logging, making it difficult to trace actions.
I: Information Disclosure - Attacks where unauthorized access to sensitive information occurs, breaching system confidentiality. D: Denial of Service - Attacks where an attacker exhausts system resources (computing or networking), reducing its functionality.
E: Elevation of Privilege - Attacks where an attacker gains unauthorized access to higher-level functionalities or capabilities within the system, compromising authorization. The STRIDE model helps identify various threats targeting a system. Once these threats are identified, mitigating them involves several steps: 1) restructuring the system, 2) developing Intrusion Detection and Prevention Systems, 3) investing time, and 4) allocating money. Prioritizing threats is crucial to address the most damaging ones first and the less impactful ones later. The DREAD model aids in prioritizing these threats by evaluating their impact. The acronym DREAD stands for: By assessing these factors, the DREAD model helps prioritize threats from most critical to least significant.
In the threat modeling process, each threat is categorized using the STRIDE model to determine the type of attack. This helps in answering the following questions: Next,the impact of each threat is assessed using the DREAD model, where each threat is rated in three impact categories: High impact (3 points), Medium impact (2 points), and Low impact (1 point). The overall risk rating for a threat is calculated by summing the DREAD impacts. The risk levels are categorized as follows: Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Inertial%20navigation%20system • https://arxiv.org/html/2412.15348v1
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Autonomous Vehicle Lane Security Against Spoofing.
[*] Metasploit Scan Running on Target Subnet for Autonomous Vehicle Lane Security Against Spoofing... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |