Complete Technical Paper Content — Aws S3 Bucket Security Auditing And Misconfiguration Tool
Overview & System Context
Aws S3 Bucket Security Auditing And Misconfiguration Tool: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9563 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Amazon Simple Storage Service now applies a new default bucket security setting that automatically disables server-side encryption with customer-provided keys (SSE-C) for all new general purpose buckets. In April 2026, Amazon S3 deployed an update so all new general purpose buckets have SSE-C encryption disabled for all new write requests. For existing buckets in AWS accounts with no SSE-C encrypted objects, Amazon S3 also disabled SSE-C for all new write requests. With this change, applications that need SSE-C encryption must deliberately enable SSE-C by using the PutBucketEncryption API operation after creating a new bucket. For more information about this change, see Default SSE-C setting for new buckets FAQ .
Amazon S3 provides a number of security features to consider as you develop and implement your own security policies. The following best practices are general guidelines and don't represent a complete security solution. Because these best practices might not be appropriate or sufficient for your environment, treat them as helpful recommendations rather than prescriptions. S3 Object Ownership is an Amazon S3 bucket-level setting that you can use to control ownership of objects uploaded to your bucket and to disable or enable ACLs. By default, Object Ownership is set to the bucket owner enforced setting and all ACLs are disabled. When ACLs are disabled, the bucket owner owns all the objects in the bucket and manages access to data exclusively using access management policies.
A majority of modern use cases in Amazon S3 no longer require the use of access control lists (ACLs) . We recommend that you disable ACLs, except in circumstances where you must control access for each object individually. To disable ACLs and take ownership of every object in your bucket, apply the bucket owner enforced setting for S3 Object Ownership. When you disable ACLs, you can easily maintain a bucket with objects uploaded by different AWS accounts.
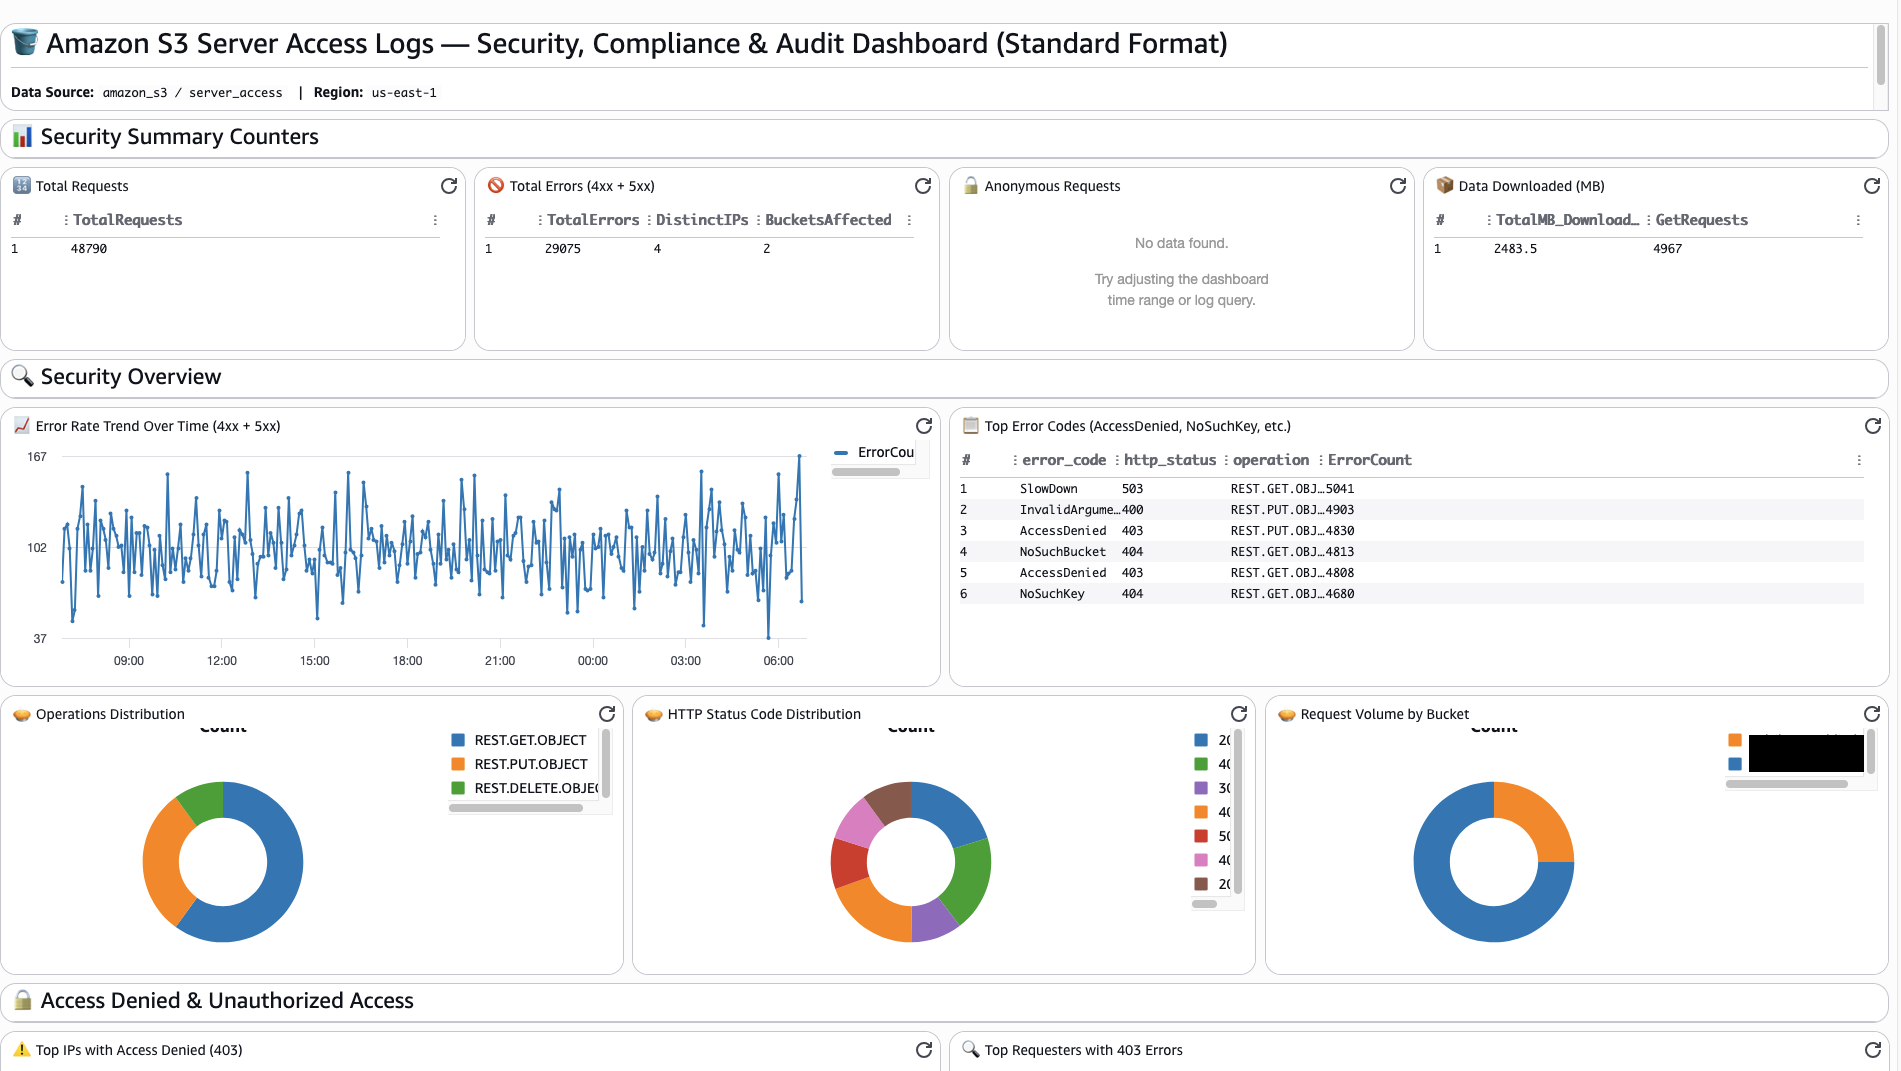
Figure 1: Using Amazon S3 Server Access Logs with Amazon CloudWatch Logs | AWS ... When ACLs are disabled access control for your data is based on policies, such as the following: Disabling ACLs simplifies permissions management and auditing. ACLs are disabled for new buckets by default. You can also disable ACLs for existing buckets. If you have an existing bucket that already has objects in it, after you disable ACLs, the object and bucket ACLs are no longer part of the access-evaluation process. Instead, access is granted or denied on the basis of policies.
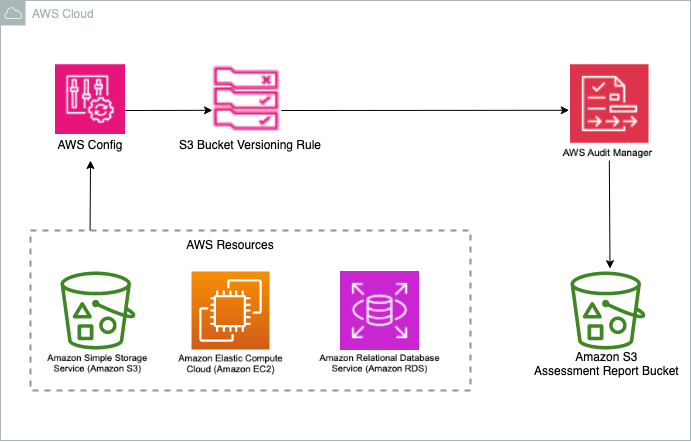
Review your bucket policy to ensure that it covers all the ways that you intend to grant access to your bucket outside of your account. Reset your bucket ACL to the default (full control to the bucket owner). Figure 2: Automating organizational policies with custom AWS Config Rules and ...
Your bucket accepts only PUT requests that do not specify an ACL or PUT requests with bucket owner full control ACLs. These ACLs include the bucket-owner-full-control canned ACL or equivalent forms of this ACL that are expressed in XML. Existing applications that support bucket owner full control ACLs see no impact. PUT requests that contain other ACLs (for example, custom grants to certain AWS accounts) fail and return an HTTP status code 400 (Bad Request) with the error code AccessControlListNotSupported .
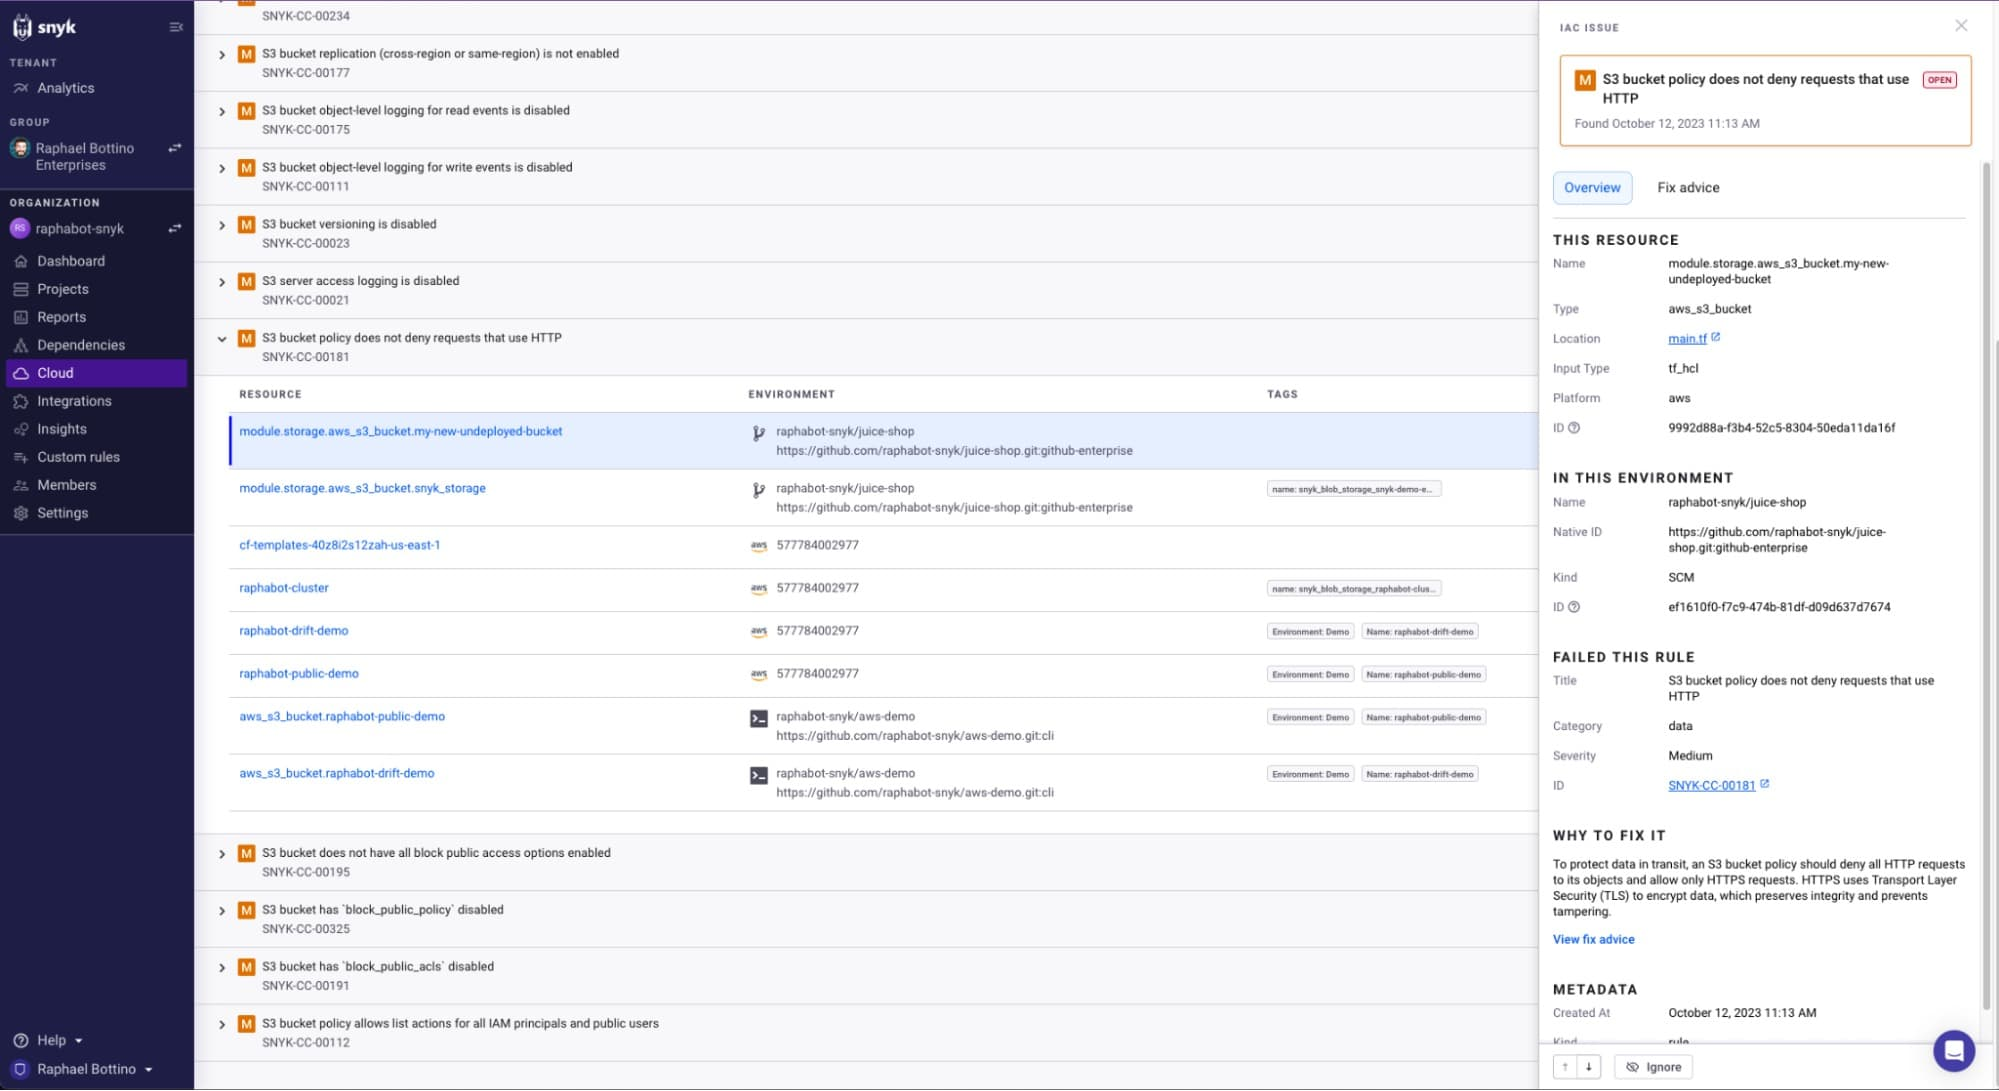
For more information, see Controlling ownership of objects and disabling ACLs for your bucket . Figure 3: How to secure an S3 bucket on AWS? | Snyk Unless you explicitly require anyone on the internet to be able to read or write to your S3 bucket, make sure that your S3 bucket is not public. The following are some of the steps that you can take to block public access: Use S3 Block Public Access. With S3 Block Public Access, you can easily set up centralized controls to limit public access to your Amazon S3 resources. These centralized controls are enforced regardless of how the resources are created. For organizations managing multiple AWS accounts, you can now use organization-level enforcement through AWS Organizations to centrally manage S3 Block Public Access settings across your entire organization with a single policy configuration.
Identify Amazon S3 bucket policies that allow a wildcard identity such as "Principal": "*" (which effectively means "anyone"). Also look for policies that allow a wildcard action "*" (which effectively allows the user to perform any action in the Amazon S3 bucket). Similarly, look for Amazon S3 bucket access control lists (ACLs) that provide read, write, or full-access to "Everyone" or "Any authenticated AWS user." Use the ListBuckets API operation to scan all of your Amazon S3 buckets. Then use GetBucketAcl , GetBucketWebsite , and GetBucketPolicy to determine whether each bucket has compliant access controls and a compliant configuration.
Use AWS Trusted Advisor to inspect your Amazon S3 implementation. Consider implementing ongoing detective controls by using the s3-bucket-public-read-prohibited and s3-bucket-public-write-prohibited managed AWS Config Rules.
For organizations with multiple AWS accounts, consider using organization-level Block Public Access management: Centralized policy management: Use AWS Organizations to create a single S3 Block Public Access policy that automatically applies to all member accounts or selected organizational units (OUs). Automatic inheritance: When you attach the policy at the root or OU level, new member accounts automatically inherit the Block Public Access settings without individual account setup.
Simplified compliance: Organization-level policies eliminate the need to maintain complex Service Control Policies (SCPs) for Block Public Access enforcement and reduce operational overhead of managing individual account configurations. Audit capabilities: Use AWS CloudTrail to monitor policy attachment and enforcement across member accounts for compliance tracking.
Starting April 2026, Amazon S3 automatically disables SSE-C for all new general purpose buckets and existing buckets in accounts with no SSE-C encrypted objects. We recommend keeping SSE-C disabled unless your workload has a specific requirement for this encryption offering. SSE-C requires you to provide the encryption key with every request to read or write encrypted objects. This makes it impractical to share access with other users, roles, or AWS services that operate on your data. Objects encrypted with SSE-C cannot be natively decrypted by AWS managed services. For most workloads, server-side encryption with Amazon S3 managed keys (SSE-S3) or AWS KMS keys (SSE-KMS) provides equivalent protection with greater flexibility.
If you have existing buckets where SSE-C is still enabled, review whether it's still needed and block it if not. When SSE-C is blocked, any PutObject , CopyObject , PostObject , Multipart Upload, or replication request that specifies SSE-C encryption is rejected with an HTTP 403 AccessDenied error. To learn more about blocking SSE-C, see Blocking or unblocking SSE-C for a general purpose bucket .
By default, you create global general purpose buckets in the shared global namespace. After creating a general purpose bucket in the shared global namespace, that bucket name is unavailable for anyone else to create within partition. When you delete a global general purpose bucket, the bucket name becomes available again in the global namespace for anyone to re-create.
Although Amazon S3 general purpose buckets exist in a shared global namespace, you can optionally create buckets in your account regional namespace. The account regional namespace is a reserved subdivision of the global bucket namespace where only your account can create general purpose buckets. We recommend you create buckets in your account regional namespace since these buckets are unique to your account and can never be re-created by another account. For more information, see Namespaces for general purpose buckets .
We recommend that you don't delete your global general purpose buckets in the shared global namespace. All AWS Accounts now have a default bucket quota of 10,000 buckets, reducing the need to delete empty buckets from your account. If you delete a bucket in the shared global namespace, be aware that another AWS account in the same partition can use the same bucket name for a new bucket and can therefore potentially receive requests that are intended for the deleted bucket. If you want to prevent this, or if you want to continue to use the same bucket name, don't delete the bucket. We recommend that you empty the bucket and keep it. Instead of deleting the bucket, block any bucket requests as needed. For buckets no longer in active use, we recommend emptying the bucket of all objects to minimize costs while retaining the bucket itself. For more information, see Deleting a general purpose bucket .
When granting permissions, you decide who is getting what permissions to which Amazon S3 resources. You enable specific actions that you want to allow on those resources. Therefore, we recommend that you grant only the permissions that are required to perform a task. Implementing least privilege access is fundamental in reducing security risk and the impact that could result from errors or malicious intent.
The following tools are available to implement least privilege access: For guidance on what to consider when choosing one or more of the preceding mechanisms, see Identity and Access Management for Amazon S3 . In order for applications running on Amazon EC2 or other AWS services to access Amazon S3 resources, they must include valid AWS credentials in their AWS API requests. We recommend not storing AWS credentials directly in the application or Amazon EC2 instance. These are long-term credentials that are not automatically rotated and could have a significant business impact if they are compromised.
Instead, use an IAM role to manage temporary credentials for applications or services that need to access Amazon S3. When you use a role, you don't have to distribute long-term credentials (such as a username and password or access keys) to an Amazon EC2 instance or AWS service, such as AWS Lambda. The role supplies temporary permissions that applications can use when they make calls to other AWS resources.
Common Scenarios for Roles: Users, Applications, and Services Server-side encryption âII All Amazon S3 buckets have encryption configured by default, and all new objects that are uploaded to an S3 bucket are automatically encrypted at rest. Server-side encryption with Amazon S3 managed keys (SSE-S3) is the default encryption configuration for every bucket in Amazon S3. To use a different type of encryption, you can either specify the type of server-side encryption to use in your S3 PUT requests, or you can set the default encryption configuration in the destination bucket.
Server-side encryption with AWS Key Management Service (AWS KMS) keys (SSE-KMS) Dual-layer server-side encryption with AWS Key Management Service (AWS KMS) keys (DSSE-KMS) Server-side encryption with customer-provided keys (SSE-C) Client-side encryption âII Encrypt data client-side and upload the encrypted data to Amazon S3. In this case, you manage the encryption process, the encryption keys, and related tools. As with server-side encryption, client-side encryption can help reduce risk by encrypting the data with a key that is stored in a different mechanism than the mechanism that stores the data itself.
Amazon S3 provides multiple client-side encryption options. For more information, see Protecting data by using client-side encryption . You can use HTTPS (TLS) to help prevent potential attackers from eavesdropping on or manipulating network traffic by using person-in-the-middle or similar attacks. We recommend allowing only encrypted connections over HTTPS (TLS) by using the aws:SecureTransport condition in your Amazon S3 bucket policies. For more information, see the example S3 bucket policy Managing access based on HTTP or HTTPS requests . In addition to denying HTTP requests, we recommend that you set Amazon CloudWatch alarms on tlsDetails.tlsVersion NOT EXISTS that alert you if HTTP access attempts are made on your content. For more information on how to configure Amazon CloudWatch alarms, see Creating CloudWatch alarms for CloudTrail events: examples and CloudTrail record contents in the AWS CloudTrail User Guide .
2. System Architecture & Core Working Principles We recommend that your application not pin Amazon S3 TLS certificates as AWS doesnâIIt support pinning of publicly-trusted certificates. S3 automatically renews certificates and renewal can happen any time before certificate expiry. Renewing a certificate generates a new public-private key pair. If youâIIve pinned an S3 certificate which has been recently renewed with a new public key, you wonâIIt be able to connect to S3 until your application uses the new certificate.
Also consider implementing ongoing detective controls by using the s3-bucket-ssl-requests-only managed AWS Config rule. With S3 Object Lock, you can store objects by using a "Write Once Read Many" (WORM) model. S3 Object Lock can help prevent accidental or inappropriate deletion of data. For example, you can use S3 Object Lock to help protect your AWS CloudTrail logs.
S3 Versioning is a means of keeping multiple variants of an object in the same bucket. You can use versioning to preserve, retrieve, and restore every version of every object stored in your bucket. With versioning, you can easily recover from both unintended user actions and application failures. Also consider implementing ongoing detective controls by using the s3-bucket-versioning-enabled managed AWS Config rule.
Although Amazon S3 stores your data across multiple geographically diverse Availability Zones by default, compliance requirements might dictate that you store data at even greater distances. With S3 Cross-Region Replication (CRR), you can replicate data between distant AWS Regions to help satisfy these requirements. CRR enables automatic, asynchronous copying of objects across buckets in different AWS Regions. For more information, see Replicating objects within and across Regions .
CRR requires both the source and destination S3 buckets to have versioning enabled. Also consider implementing ongoing detective controls by using the s3-bucket-replication-enabled managed AWS Config rule. A virtual private cloud (VPC) endpoint for Amazon S3 is a logical entity within a VPC that allows connectivity only to Amazon S3. VPC endpoints can help prevent traffic from traversing the open internet.
VPC endpoints for Amazon S3 provide multiple ways to control access to your Amazon S3 data: You can control the requests, users, or groups that are allowed through a specific VPC endpoint by using S3 bucket policies. You can control which VPCs or VPC endpoints have access to your S3 buckets by using S3 bucket policies. You can help prevent data exfiltration by using a VPC that does not have an internet gateway.
For more information, see Controlling access from VPC endpoints with bucket policies . Several managed AWS security services can help you identify, assess, and monitor security and compliance risks for your Amazon S3 data. These services can also help you protect your data from those risks. These services include automated detection, monitoring, and protection capabilities that are designed to scale from Amazon S3 resources for a single AWS account to resources for organizations spanning thousands of accounts.
For more information, see Monitoring data security with managed AWS security services . The following best practices for Amazon S3 can help detect potential security weaknesses and incidents. Identification of your IT assets is a crucial aspect of governance and security. You need to have visibility of all your Amazon S3 resources to assess their security posture and take action on potential areas of weakness. To audit your resources, we recommend doing the following: Use Tag Editor to identify and tag security-sensitive or audit-sensitive resources, then use those tags when you need to search for these resources. For more information, see Searching for Resources to Tag in the Tagging AWS Resources User Guide .
Use S3 Inventory to audit and report on the replication and encryption status of your objects for business, compliance, and regulatory needs. For more information, see Cataloging and analyzing your data with S3 Inventory . Create resource groups for your Amazon S3 resources. For more information, see What are resource groups? in the AWS Resource Groups User Guide .
Monitoring is an important part of maintaining the reliability, security, availability, and performance of Amazon S3 and your AWS solutions. AWS provides several tools and services to help you monitor Amazon S3 and your other AWS services. For example, you can monitor Amazon CloudWatch metrics for Amazon S3, particularly the PutRequests , GetRequests , 4xxErrors , and DeleteRequests metrics. For more information, see Monitoring metrics with Amazon CloudWatch and Logging and monitoring in Amazon S3 .
For a second example, see Example: Amazon S3 Bucket Activity . This example describes how to create a CloudWatch alarm that is triggered when an Amazon S3 API call is made to PUT or DELETE a bucket policy, a bucket lifecycle, or a bucket replication configuration, or to PUT a bucket ACL. Server access logging provides detailed records of the requests that are made to a bucket. Server access logs can assist you in security and access audits, help you learn about your customer base, and understand your Amazon S3 bill. For instructions on enabling server access logging, see Logging requests with server access logging .
Also consider implementing ongoing detective controls by using the s3-bucket-logging-enabled AWS Config managed rule. AWS CloudTrail provides a record of actions taken by a user, a role, or an AWS service in Amazon S3. You can use information collected by CloudTrail to determine the following: For example, you can identify CloudTrail entries for PUT actions that affect data access, in particular PutBucketAcl , PutObjectAcl , PutBucketPolicy , and PutBucketWebsite .
When you set up your AWS account, CloudTrail is enabled by default. You can view recent events in the CloudTrail console. To create an ongoing record of activity and events for your Amazon S3 buckets, you can create a trail in the CloudTrail console. For more information, see Logging data events in the AWS CloudTrail User Guide . When you create a trail, you can configure CloudTrail to log data events. Data events are records of resource operations performed on or within a resource. In Amazon S3, data events record object-level API activity for individual buckets.
CloudTrail supports a subset of Amazon S3 object-level API operations, such as GetObject , DeleteObject , and PutObject . For more information about how CloudTrail works with Amazon S3, see Logging Amazon S3 API calls using AWS CloudTrail . In the Amazon S3 console, you can also configure your S3 buckets to Enabling CloudTrail event logging for S3 buckets and objects .
AWS Config provides a managed rule ( cloudtrail-s3-dataevents-enabled ) that you can use to confirm that at least one CloudTrail trail is logging data events for your S3 buckets. For more information, see cloudtrail-s3-dataevents-enabled in the AWS Config Developer Guide . Several of the best practices listed in this topic suggest creating AWS Config rules. AWS Config helps you to assess, audit, and evaluate the configurations of your AWS resources. AWS Config monitors resource configurations so that you can evaluate the recorded configurations against the desired secure configurations. With AWS Config, you can do the following: Review changes in configurations and relationships between AWS resources Determine your overall compliance against the configurations specified in your internal guidelines Using AWS Config can help you simplify compliance auditing, security analysis, change management, and operational troubleshooting. For more information, see Setting Up AWS Config with the Console in the AWS Config Developer Guide .
When specifying the resource types to record, ensure that you include Amazon S3 resources. AWS Config managed rules only supports general purpose buckets when evaluating Amazon S3 resources. AWS Config doesnâIIt record configuration changes for directory buckets. For more information, see AWS Config Managed Rules and List of AWS Config Managed Rules in the AWS Config Developer Guide .
For an example of how to use AWS Config, see How to Use AWS Config to Monitor for and Respond to Amazon S3 Buckets Allowing Public Access on the AWS Security Blog . S3 Storage Lens is a cloud-storage analytics feature that you can use to gain organization-wide visibility into object-storage usage and activity. S3 Storage Lens also analyzes metrics to deliver contextual recommendations that you can use to optimize storage costs and apply best practices for protecting your data.
With S3 Storage Lens, you can use metrics to generate summary insights, such as finding out how much storage you have across your entire organization or which are the fastest-growing buckets and prefixes. You can also use S3 Storage Lens metrics to identify cost-optimization opportunities, implement data-protection and access-management best practices, and improve the performance of application workloads.
For example, you can identify buckets that don't have S3 Lifecycle rules to abort incomplete multipart uploads that are more than 7 days old. You can also identify buckets that aren't following data-protection best practices, such as using S3 Replication or S3 Versioning. For more information, see Understanding Amazon S3 Storage Lens . We recommend that you regularly check the security advisories posted in Trusted Advisor for your AWS account. In particular, look for warnings about Amazon S3 buckets with "open access permissions." You can do this programmatically by using describe-trusted-advisor-checks .
Further, actively monitor the primary email address that's registered to each of your AWS accounts. AWS uses this email address to contact you about emerging security issues that might affect you. AWS operational issues with broad impact are posted on the AWS Health Dashboard - Service health . Operational issues are also posted to individual accounts through the AWS Health Dashboard. For more information, see the AWS Health documentation .
Several managed AWS security services can help you identify, assess, and monitor security and compliance risks for your Amazon S3 data. They can also help you protect your data from those risks. These services include automated detection, monitoring, and protection capabilities that are designed to scale from Amazon S3 resources for a single AWS account to resources for organizations spanning thousands of AWS accounts.
AWS detection and response services can help you identify potential security misconfigurations, threats, or unexpected behaviors, so that you can quickly respond to potentially unauthorized or malicious activity in your environment. AWS data protection services can help you monitor and protect your data, accounts, and workloads from unauthorized access. They can also help you discover sensitive data, such as personally identifiable information (PII), in your Amazon S3 data estate.
3. Software Implementation, Frameworks & Protocols To help you identify and evaluate data security and compliance risks, managed AWS security services generate findings to notify you of potential security events or issues with your Amazon S3 data. The findings provide relevant details that you can use to investigate, assess, and act upon these risks according to your incident-response workflows and policies. You can access findings data directly by using each service. You can also send the data to other applications, services, and systems, such as your security incident and event management system (SIEM).
To monitor the security of your Amazon S3 data, consider using these managed AWS security services. Amazon GuardDuty is a threat-detection service that continuously monitors your AWS accounts and workloads for malicious activity and delivers detailed security findings for visibility and remediation. With the S3 protection feature in GuardDuty, you can configure GuardDuty to analyze AWS CloudTrail management and data events for your Amazon S3 resources. GuardDuty then monitors those events for malicious and suspicious activity. To inform the analysis and identify potential security risks, GuardDuty uses threat-intelligence feeds and machine learning.
GuardDuty can monitor different kinds of activity for your Amazon S3 resources. For example, CloudTrail management events for Amazon S3 include bucket-level operations, such as ListBuckets , DeleteBucket , and PutBucketReplication . CloudTrail data events for Amazon S3 include object-level operations, such as GetObject , ListObjects , and PutObject . If GuardDuty detects anomalous or potentially malicious activity, it generates a finding to notify you.
For more information, see Amazon S3 Protection in Amazon GuardDuty in the Amazon GuardDuty User Guide . Amazon Detective simplifies the investigative process and helps you conduct faster, more effective security investigations. Detective provides prebuilt data aggregations, summaries, and context that can help you analyze and assess the nature and extent of possible security issues.
Detective automatically extracts time-based events, such as API calls from AWS CloudTrail and Amazon VPC Flow Logs for your AWS resources. It also ingests findings generated by Amazon GuardDuty. Detective then uses machine learning, statistical analysis, and graph theory to generate visualizations that help you conduct effective security investigations more quickly.
These visualizations provide a unified, interactive view of resource behaviors and the interactions between them over time. You can explore this behavior graph to examine potentially malicious actions, such as failed login attempts or suspicious API calls. You can also see how these actions affect resources, such as S3 buckets and objects. For more information, see the Amazon Detective Administration Guide .
AWS Identity and Access Management Access Analyzer (IAM Access Analyzer) can help you identify resources that are shared with an external entity. You can also use IAM Access Analyzer to validate IAM policies against policy grammar and best practices, and generate IAM policies based on access activity in your AWS CloudTrail logs. IAM Access Analyzer uses logic-based reasoning to analyze resource policies in your AWS environment, such as bucket policies. With IAM Access Analyzer for S3, you're alerted when an S3 bucket is configured to allow access to anyone on the internet or other AWS accounts, including accounts outside your organization. For example, IAM Access Analyzer for S3 can report that a bucket has read or write access provided through a bucket access control list (ACL), a bucket policy, a Multi-Region Access Point policy, or an access point policy. For each public or shared bucket, you receive findings that indicate the source and level of public or shared access. With these findings, you can take immediate and precise corrective action to restore bucket access to what you intended.
Amazon Macie is a security service that discovers sensitive data by using machine learning and pattern matching. Macie provides visibility into data security risks, and enables automated protection against those risks. With Macie, you can automate the discovery and reporting of sensitive data in your Amazon S3 data estate to gain a better understanding of the data that your organization stores in S3.
To detect sensitive data with Macie, you can use built-in criteria and techniques that are designed to detect a large and growing list of sensitive data types for many countries and regions. These sensitive data types include multiple types of personally identifiable information (PII), financial data, and credentials data. You can also use custom criteria that you defineâIIregular expressions that define text patterns to match and, optionally, character sequences and proximity rules that refine the results.
If Macie detects sensitive data in an S3 object, Macie generates a security finding to notify you. This finding provides information about the affected object, the types and number of occurrences of the sensitive data that Macie found, and additional details to help you investigate the affected S3 bucket and object. For more information, see the Amazon Macie User Guide .
AWS Security Hub CSPM is a security-posture management service that performs security best-practice checks, aggregates alerts and findings from multiple sources into a single format, and enables automated remediation. Security Hub CSPM collects and provides security findings data from integrated AWS Partner Network security solutions and AWS services, including Amazon Detective, Amazon GuardDuty, IAM Access Analyzer, and Amazon Macie. It also generates its own findings by running continuous, automated security checks based on AWS best practices and supported industry standards.
Security Hub CSPM then correlates and consolidates findings across providers to help you prioritize and process the most significant findings. It also provides support for custom actions, which you can use to invoke responses or remediation actions for specific classes of findings. With Security Hub CSPM, you can assess the security and compliance status of your Amazon S3 resources, and you can do so as part of a broader analysis of your organization's security posture in individual AWS Regions and across multiple Regions. This includes analyzing security trends and identifying the highest-priority security issues. You can also aggregate findings from multiple AWS Regions, and monitor and process aggregated findings data from a single Region.
For more information, see Amazon Simple Storage Service controls in the AWS Security Hub CSPM User Guide . Amazon Simple Storage Service now applies a new default bucket security setting that automatically disables server-side encryption with customer-provided keys (SSE-C) for all new general purpose buckets. In April 2026, Amazon S3 deployed an update so all new general purpose buckets have SSE-C encryption disabled for all new write requests. For existing buckets in AWS accounts with no SSE-C encrypted objects, Amazon S3 also disabled SSE-C for all new write requests. With this change, applications that need SSE-C encryption must deliberately enable SSE-C by using the PutBucketEncryption API operation after creating a new bucket. For more information about this change, see Default SSE-C setting for new buckets FAQ .
Cloud security at AWS is the highest priority. As an AWS customer, you benefit from a data center and network architecture that are built to meet the requirements of the most security-sensitive organizations. Security is a shared responsibility between AWS and you. The shared responsibility model describes this as security of the cloud and security in the cloud: AWS is responsible for protecting the infrastructure that runs AWS services in the AWS Cloud. AWS also provides you with services that you can use securely. The effectiveness of our security is regularly tested and verified by third-party auditors as part of the AWS compliance programs . To learn about the compliance programs that apply to Amazon S3, see AWS Services in Scope by Compliance Program .
Your responsibility is determined by the AWS service that you use. You are also responsible for other factors including the sensitivity of your data, your organizationâIIs requirements, and applicable laws and regulations. For Amazon S3, your responsibility includes the following areas: Managing access to your data using IAM roles and other service configurations to apply the appropriate permissions.
Enabling detective controls such as AWS CloudTrail or Amazon GuardDuty for Amazon S3. This documentation will help you understand how to apply the shared responsibility model when using Amazon S3. The following topics show you how to configure Amazon S3 to meet your security and compliance objectives. You'll also learn how to use other AWS services that can help you monitor and secure your Amazon S3 resources.
For more information about using the Amazon S3 Express One Zone storage class with directory buckets, see S3 Express One Zone and Working with directory buckets . Store your data in Amazon S3 and secure it from unauthorized access with encryption features and access management tools. S3 encrypts all object uploads to all buckets. S3 is the only object storage service that allows you to block public access to all of your objects at the bucket or the account level with S3 Block Public Access . S3 maintains compliance programs, such as PCI-DSS, HIPAA/HITECH, FedRAMP, EU Data Protection Directive, and FISMA, to help you meet regulatory requirements. AWS also supports numerous auditing capabilities to monitor access requests to your S3 resources.
To protect your data in Amazon S3, by default, users only have access to the S3 resources they create. You can grant access to other users by using one or a combination of the following access management features: AWS Identity and Access Management (IAM) to create users and manage their respective access; Access Control Lists (ACLs) to make individual objects accessible to authorized users; bucket policies to configure permissions for all objects within a single S3 bucket; and Query String Authentication to grant time-limited access to others with temporary URLs. Amazon S3 also supports Audit Logs that list the requests made against your S3 resources for complete visibility into who is accessing what data.
With a few clicks in the S3 management console or AWS Organizations console, you can apply S3 Block Public Access to every bucket in your account—both existing and any new buckets created in the future—and make sure that there is no public access to any object. For organizations with multiple AWS accounts, you can centrally manage these settings across all member accounts using AWS Organizations Policies. All new buckets have Block Public Access enabled by default. To restrict access to all existing buckets in your account, you can enable Block Public Access at the account level. If you manage multiple AWS accounts, you can enable Block Public Access at the organization level using AWS Organizations Policies to centrally control settings across all member accounts. S3 Block Public Access settings override S3 permissions that allow public access, making it easy for the account administrator or organization administrator to set up a centralized control to prevent variation in security configuration regardless of how an object is added or a bucket is created.
Amazon S3 Object Lock blocks object version deletion during a customer-defined retention period so that you can enforce retention policies as an added layer of data protection or for regulatory compliance. You can migrate workloads from existing write-once-read-many (WORM) systems into Amazon S3, and configure S3 Object Lock at the object- and bucket-levels to prevent object version deletions prior to pre-defined Retain Until Dates or Legal Hold Dates.
Amazon S3 Object Ownership disables Access Control Lists (ACLs), changing ownership for all objects to the bucket owner and simplifying access management for data stored in S3. When you configure the S3 Object Ownership Bucket owner enforced setting, ACLs will no longer affect permissions for your bucket and the objects in it. All access control will be defined using resource-based policies, user policies, or some combination of these. ACLs are automatically disabled for new buckets.
You can use S3 Inventory to review ACLs usage in your buckets before enabling S3 Object Ownership when migrating to IAM-based buckets policies. For more information, see Controlling Object Ownership . By default, all Amazon S3 resources—buckets, objects, and related subresources—are private: only the resource owner, an AWS account that created it, can access the resource. Amazon S3 offers access policy options broadly categorized as resource-based policies and user policies. You may choose to use resource-based policies, user policies, or some combination of these to manage permissions to your Amazon S3 resources. By default, an S3 object is owned by the account that created the object, including when this account is different than the bucket owner. You can use S3 Object Ownership to disable Access Control Lists and change this behavior. If you do, each object in a bucket is owned by the bucket owner. For more information, see Identity and access management in Amazon S3 .
Discover and protect sensitive data at scale in Amazon S3 with Amazon Macie . Macie automatically provides you with a full inventory of your S3 buckets by scanning buckets to identify and categorize the data. You receive actionable security findings enumerating any data that fits these sensitive data types, including personal identifiable information (PII) (e.g. customer names and credit cards numbers), and categories defined by privacy regulations, such as GDPR and HIPAA. Macie also automatically and continually evaluates bucket-level preventative controls for any buckets that are unencrypted, publicly accessible, or shared with accounts outside of your organization, allowing you to quickly address unintended settings on buckets.
Amazon S3 automatically encrypts all object uploads to all buckets. For object uploads, Amazon S3 supports server-side encryption with four key management options: SSE-S3 (the base level of encryption), SSE-KMS, DSSE-KMS, and SSE-C, as well as client-side encryption. Amazon S3 offers flexible security features to block unauthorized users from accessing your data. Use VPC endpoints to connect to S3 resources from your Amazon Virtual Private Cloud (Amazon VPC). Use S3 Inventory to check the encryption status of your S3 objects (see storage management for more information on S3 Inventory).
Trusted Advisor inspects your AWS environment and then makes recommendations when opportunities exist to help close security gaps. Trusted Advisor has the following Amazon S3-related checks: logging configuration of Amazon S3 buckets, security checks for Amazon S3 buckets that have open access permissions, and fault tolerance checks for Amazon S3 buckets that don't have versioning enabled, or have versioning suspended.
Access Amazon S3 directly as a private endpoint within your secure, virtual network with AWS PrivateLink for S3 . Simplify your network architecture by connecting to S3 from on-premises or in the cloud using private IP addresses from your Virtual Private Cloud (VPC). You no longer need to use public IPs, configure firewall rules, or configure an internet gateway to access S3 from on-premises.
Choose from four supported checksum algorithms (SHA-1, SHA-256, CRC32, or CRC32C) to check data integrity on your upload and download requests. Automatically calculate and verify checksums as you store or retrieve data from Amazon S3, and access the checksum information at any time using the GetObjectAttributes S3 API or an S3 Inventory report. Learn tools and best practices for access management, auditing and monitoring, and data protection Learn about the native data protection features in Amazon S3 including S3 Versioning, S3 Object Lock, and S3 Replication Learn the different ways you can manage access to your data using AWS Identity and Access Management (IAM) and S3 bucket policies 4. Practical Deployment, Analysis & Case Studies Learn about S3 features that provide additional layers of protection, including S3 Versioning, S3 Cross-Region Replication (CRR), and S3 Object Lock As of January 5, 2023, S3 automatically applies server-side encryption (SSE-S3) for each new object, unless you specify a different encryption option Starting in April of 2023, we will be making two changes to Amazon S3 to put our latest best practices for bucket security into effect automatically The new Amazon S3 Object Ownership setting, Bucket owner enforced, lets you disable all of the ACLs associated with a bucket and the objects in it New – Amazon S3 Dual-Layer Server-Side Encryption with Keys Stored in AWS Key Management Service (DSSE-KMS) Customers can now apply two independent layers of server-side encryption to objects in Amazon S3 In a controlled study by Horizon3 researchers, models that explicitly identified a trap in their reasoning still attacked it 73.4% of the time. Read the findings and see what they mean for canaries, decoys, and early detection.
S3 misconfiguration is not a new problem, but it keeps producing the same category of breach year after year. Public buckets, overly permissive bucket policies, missing server-side encryption, no access logging, and replication to less-secure accounts together create a data exposure landscape that is entirely preventable. This checklist works through every S3 security control, with the AWS CLI commands and AWS Config rule names to audit each one at scale across hundreds of buckets and multiple accounts.
Block Public Access is the highest-priority control. Enable it at the account level to prevent any bucket from being made public, even if a misconfigured bucket policy or ACL attempts to grant public access. aws s3control put-public-access-block --account-id {ACCOUNT_ID} --public-access-block-configuration BlockPublicAcls=true,IgnorePublicAcls=true,BlockPublicPolicy=true,RestrictPublicBuckets=true.
This overrides any bucket-level setting. Verify: aws s3control get-public-access-block --account-id {ACCOUNT_ID}.
Some buckets intentionally override account-level Block Public Access (for static website hosting, public asset CDN origins without CloudFront). Audit: for bucket in $(aws s3 ls | awk '{print $3}'); do aws s3api get-public-access-block --bucket $bucket 2>&1; done. Any bucket with BlockPublicPolicy: false or RestrictPublicBuckets: false that is not documented as intentionally public is a finding.
s3-account-level-public-access-blocks-periodic (account level) and s3-bucket-level-public-access-prohibited (bucket level). Enable both. Config will continuously evaluate all buckets and flag any that deviate from the required configuration. aws s3api put-bucket-ownership-controls --bucket {BUCKET} --ownership-controls Rules=[{ObjectOwnership=BucketOwnerEnforced}]. This disables all ACLs on the bucket, new objects cannot be granted public-read ACL, and existing ACLs are ignored. AWS recommends this for all new buckets.
Even with Block Public Access enabled, overly permissive bucket policies within your organization create privilege escalation paths. Review every policy for dangerous patterns. for bucket in $(aws s3 ls | awk '{print $3}'); do echo "=== $bucket ==="; aws s3api get-bucket-policy --bucket $bucket 2>/dev/null | jq '.Policy | fromjson'; done. Look for Principal: "*", Principal: {"AWS": "*"}, and any Effect: Allow with s3:* on Resource: arn:aws:s3:::*.
Bucket policies that grant access to external account IDs (not in your AWS Organization) are high-risk. Extract all external principals: aws s3api get-bucket-policy --bucket {BUCKET} | jq '.Policy | fromjson | .Statement[] | select(.Principal.AWS | strings | test("^(?!.*{YOUR_ORG_ID})"))'. Each external account ID should be documented with a business justification. Add a Deny statement to every bucket policy: {"Effect": "Deny", "Principal": "*", "Action": "s3:*", "Resource": ["arn:aws:s3:::{BUCKET}", "arn:aws:s3:::{BUCKET}/*"], "Condition": {"Bool": {"aws:SecureTransport": "false"}}}. This prevents any client from accessing the bucket over HTTP. AWS Config rule: s3-bucket-ssl-requests-only.
Use an SCP (Service Control Policy) at the Organization level to restrict s3:PutBucketPolicy, s3:PutBucketAcl, and s3:PutBucketPublicAccessBlock to a security or admin IAM role. This prevents developer roles from modifying bucket security controls even if their IAM permissions technically allow it. All S3 buckets should enforce server-side encryption. The question is whether to use SSE-S3 (AWS-managed keys), SSE-KMS (customer-managed keys), or SSE-C (customer-provided keys).
Deny PutObject requests without server-side encryption: {"Effect": "Deny", "Principal": "*", "Action": "s3:PutObject", "Resource": "arn:aws:s3:::{BUCKET}/*", "Condition": {"StringNotEquals": {"s3:x-amz-server-side-encryption": "aws:kms"}}}. This rejects any upload that does not specify KMS encryption, even if the bucket has a default encryption setting. SSE-S3 encrypts with AWS-managed keys, AWS has access to the key material. SSE-KMS with a customer-managed KMS key (CMK) gives you control over key usage via CloudTrail logs (every decryption is logged) and key policy (you control who can use the key). For PII, financial data, and secrets: mandate SSE-KMS with CMK. AWS Config rule: s3-default-encryption-kms.
for bucket in $(aws s3 ls | awk '{print $3}'); do encryption=$(aws s3api get-bucket-encryption --bucket $bucket 2>&1); if echo $encryption | grep -q 'ServerSideEncryptionConfigurationNotFoundError'; then echo "NO ENCRYPTION: $bucket"; fi; done. Without logging, you have no visibility into who accessed what objects. Two logging layers are required: S3 server access logging and CloudTrail S3 data events.
aws s3api put-bucket-logging --bucket {BUCKET} --bucket-logging-status '{"LoggingEnabled": {"TargetBucket": "{LOG_BUCKET}", "TargetPrefix": "{BUCKET}/"}}'. Ship logs to a dedicated security log bucket in a separate account with strict access controls. AWS Config rule: s3-bucket-logging-enabled.
CloudTrail management events capture bucket-level operations (CreateBucket, DeleteBucket, PutBucketPolicy). Data events capture object-level operations (GetObject, PutObject, DeleteObject). Enable data events for buckets containing secrets, PII, or financial data: aws cloudtrail put-event-selectors --trail-name {TRAIL} --event-selectors '[{"ReadWriteType":"All","DataResources":[{"Type":"AWS::S3::Object","Values":["arn:aws:s3:::{BUCKET}/"]}]}]'.
In your SIEM, alert on: S3 GetObject events from a single IAM principal exceeding 1,000 requests within 60 minutes targeting a bucket that contains sensitive data. This is the standard indicator of a data exfiltration event. Also alert on: any S3 data event originating from an IP address not in your corporate IP range for buckets that should only be accessed from your infrastructure.
Your log bucket itself must be protected. Enable S3 Object Lock in Governance mode on the log bucket with a minimum 90-day retention period. This prevents an attacker with admin credentials from deleting access logs to cover their tracks. AWS Config rule: s3-bucket-object-lock-enabled. Versioning and replication introduce their own security considerations that are frequently overlooked.
aws s3api put-bucket-versioning --bucket {BUCKET} --versioning-configuration Status=Enabled. Versioning protects against accidental deletion and ransomware that overwrites objects with encrypted versions. Without versioning, a successful s3:PutObject or s3:DeleteObject completely destroys the original data. AWS Config rule: s3-bucket-versioning-enabled. S3 replication copies objects to a destination bucket in the same or a different account. Verify: (1) Destination bucket has Block Public Access enabled. (2) Destination bucket is in an account you control. (3) Replication IAM role has only the minimum permissions needed (s3:ReplicaObject, s3:ReplicaDelete on the destination). aws s3api get-bucket-replication --bucket {BUCKET} | jq '.ReplicationConfiguration.Rules[].Destination'.
If you replicate to a destination in another AWS account (backup account, DR account), verify the destination account also has Block Public Access enabled at the account level. A common mistake: replicate sensitive data to a backup account with weaker security controls, creating an easier path to the same data. Manual bucket-by-bucket review does not scale. These tools automate the audit across all buckets in all accounts.
prowler aws --service s3 runs all S3 security checks across your account including public access, encryption, logging, versioning, and bucket policy analysis. Output in OCSF or HTML format. Run via CodeBuild on a schedule and ship findings to Security Hub: prowler aws --service s3 --send-sh-findings. Enable AWS Security Hub with the AWS Foundational Security Best Practices standard. S3 controls include: [S3.1] Block public access, [S3.2] Bucket policies block public access, [S3.4] Logging enabled, [S3.5] SSL-only, [S3.8] Block public access at account level, [S3.9] Server access logging. Security Hub aggregates these across all accounts in your Organization.
Deploy the following AWS Config rules as Organization Config rules (apply to all accounts automatically): s3-account-level-public-access-blocks-periodic, s3-bucket-ssl-requests-only, s3-bucket-server-side-encryption-enabled, s3-bucket-logging-enabled, s3-bucket-versioning-enabled. Non-compliant resources generate findings in Security Hub.
Enable Block Public Access at the account level in every AWS account today, this is a one-click fix that eliminates the most common category of S3 exposure. Then work through the checklist: HTTPS-only bucket policy, SSE-KMS enforcement, access logging enabled, versioning on data buckets. The AWS Config managed rules cover all of these and can be deployed as Organization Config rules to enforce them across every account automatically.
Block Public Access is an account-level and bucket-level control that overrides ACLs and bucket policies, it is the strongest protection against accidental public exposure. ACLs are object-level and bucket-level permissions inherited from older S3 access control model. AWS now recommends disabling ACLs entirely (set Object Ownership to Bucket owner enforced) and using only bucket policies and IAM policies for access control.
No. CloudFront accessing an S3 bucket via Origin Access Control (OAC) is a service-to-service call, not a public access call. Block Public Access only prevents unauthenticated anonymous access. A bucket with Block Public Access enabled can still serve content through CloudFront with OAC, the bucket policy grants s3:GetObject to the CloudFront distribution's service principal, not to *.
S3 Object Lock prevents objects from being deleted or overwritten for a specified retention period using WORM (write once, read many) semantics. Use Compliance mode for regulatory requirements where even the root account cannot override the lock. Use Governance mode for ransomware protection, it prevents deletion but allows authorized administrators to override. Object Lock should be enabled on all backup and compliance data buckets.
Use AWS Organizations with delegated administrator for Security Hub, then enable the S3 security controls across all accounts. For programmatic auditing: use Prowler (prowler aws --service s3) or AWS Config aggregator with an organization-level aggregator to collect Config findings across all accounts into a single view. Security Hub aggregation across accounts provides the most complete operational view.
Enable S3 Block Public Access at the AWS account level -- not just per-bucket. The account-level setting acts as a guardrail: even if a bucket policy or ACL tries to grant public access, the account-level block overrides it. Set all four options to true: BlockPublicAcls, IgnorePublicAcls, BlockPublicPolicy, and RestrictPublicBuckets. Enable via console (S3 > Block Public Access settings for this account) or CLI: aws s3control put-public-access-block --account-id ACCOUNT_ID --public-access-block-configuration BlockPublicAcls=true,IgnorePublicAcls=true,BlockPublicPolicy=true,RestrictPublicBuckets=true. For organizations using AWS Organizations, enforce this setting across all accounts using an SCP that denies any API call to put-public-access-block that would disable these settings.
The primary signal for in-progress S3 exfiltration is an unusual spike in GetObject API calls from a single IAM principal or source IP, combined with a high byte-egress volume reported in S3 server access logs. In AWS CloudWatch, create a metric filter on CloudTrail data events for eventName = GetObject per userIdentity.arn per 5-minute window, and alarm when it exceeds 500 requests. For immediate containment: use an IAM deny policy attached directly to the compromised user or role -- this takes effect within seconds and blocks S3 access without requiring key rotation (which may take longer to propagate).
Attach: deny all s3:Get* actions with no condition. After containment, check the S3 server access logs or CloudTrail for BytesTransferred or response content-length fields summed over the exfiltration window to estimate what data volume left. If the bucket holds regulated data (PII, PHI, PCI), initiate your breach notification assessment process immediately -- the clock starts at discovery.
25 actively exploited vulnerabilities with CVSS scores, exploit status, and patch availability. Print it, pin it, share it with your SOC team. Step-by-step 24-hour IR checklist covering detection, containment, eradication, and recovery. Built for SOC teams, IR leads, and CISOs.
5. Performance Evaluation & Extended Technical Observations 50,000+ security professionals read Decryption Digest for early warnings on zero-days, ransomware, and nation-state campaigns. Free, daily, no spam. Cybersecurity professional with expertise in threat intelligence, vulnerability research, and enterprise security. Covers zero-days, ransomware, and nation-state operations for 50,000+ security professionals every morning.
Actionable threat intelligence for working practitioners. Free. No spam. Trusted by 50,000+ SOC analysts, CISOs, and security engineers. Misconfigured Amazon Simple Storage Service (Amazon S3) buckets can expose your data to unauthorized access. Without proactive review, S3 bucket policies or Access Control Lists (ACLs) configured with broad access may go unnoticed in your environment. In this post, you learn how to identify and fix over-permissioned S3 buckets across your AWS environment, along with best practice recommendations and automation opportunities to help you prevent security gaps. This post provides a workflow framework and methodology recommendations for your security team to adapt. The focus of this post is on the what and why rather than a prescriptive implementation. You will need to customize the approach based on your organization’s requirements and existing security tooling.
This solution is intended for security engineers, cloud architects, and DevOps teams managing single- or multiple-account AWS environments with Amazon S3 workloads that require access management. This solution uses a five-phase workflow diagram to detect, remediate, and continuously monitor over-permissioned S3 buckets across your AWS accounts. The following workflow diagram illustrates the high-level end-to-end process for identifying and remediating over-permissioned S3 buckets across your Amazon Web Services (AWS) environment.
Figure 1: Amazon S3 over-permissive access – Detection, remediation, monitoring and cleanup workflow This section covers the AWS services used in this solution and their associated costs so you can estimate spend before deployment. The primary cost drivers are AWS Config and Security Hub, which scale with the number of accounts and resources you monitor. Lambda, Amazon EventBridge , Amazon SNS, and Amazon S3 typically add minimal costs for most environments. Start with a pilot in one or two accounts to validate costs before scaling.
Check the service pricing pages for current rates. Use the AWS Pricing Calculator to estimate costs for your specific environment before enabling services across all accounts. Consider starting with a pilot in one or two accounts to validate costs before scaling. This section walks you through setting up the audit environment, deploying the Lambda-based scanner, and generating reports of over-permissioned S3 buckets across your accounts. Follow these steps to identify over-permissioned S3 buckets in your multi-account environment, starting with preparing your environment for an Amazon S3 audit.
Note: The specific trust policy and permissions policy for your cross-account roles will depend on organizational requirements. Work with your IAM administrators to grant minimum necessary access for the audit function. Important: These code examples aren’t production ready. Adapt them to meet your organization’s requirements and test them in a non-production environment before deployment.
The following is an example of a Lambda function script for reference purposes. Review, adapt, and test before use in your environment, it scans all S3 buckets in the current account and checks for: Multi-account scanning: This script scans the current account only. To scan across member accounts, see the Multi-account extension section later in this post.
The following is an example Lambda function script for reference purposes. Before deploying any script, review error handling, logging, output structure, and permissions. This script generates CSV and JSON output files and uploads them to an S3 bucket for reporting and business intelligence (BI) dashboard integration. You can deploy both functions with different EventBridge schedules, for example, Script v1 daily for alerts and Script v2 weekly for reports.
Note: Before you deploy this script, replace
If the audit scan returns zero risky buckets, document the clean baseline for future comparison and move to the verification and monitoring phase to so new buckets or policy changes don’t introduce risk over time. The preceding example scripts scan buckets in the current account only. To scan across member accounts in your organization, add the following AssumeRole logic. This function assumes the cross-account IAM role you created during setup, then returns an Amazon S3 client with temporary credentials for each member account.
To scan each member account, replace the single-account s3.list_buckets() call with a loop over member accounts: The Lambda execution role in the central security account needs sts:AssumeRole permission for the cross-account role ARNs. Add this to the execution role policy you created in step 5. This section describes how to fix over-permissioned buckets using account-level controls, bucket policies, and optional automation. Any elevated access that you find needs to be remediated.
Before applying individual bucket policies, enable Amazon S3 Block Public Access at the account level. This prevents buckets in the account from being made public, regardless of individual bucket policies or ACLs. See the S3 Block Public Access documentation for configuration details. See the following example AWS CLI command; replace
Important: Before enabling account-level S3 Block Public Access, check whether any workloads need public bucket access (for example, static website hosting, public dataset sharing). Coordinate with your application teams to identify any exceptions. Implement bucket policies that restrict access to specific IAM users, roles, or accounts. When crafting policies, apply the principle of least privilege and include only the actions and principals required for your use case.
Example S3 bucket policy: deny public read/write access. Modify the resource ARN, actions, and conditions to match your requirements: Example S3 bucket policy: restrict access to specific IAM principals. Replace
This section covers optional strategies to automate ongoing detection and maintain your security posture without manual intervention. This section lists the resources created during this walkthrough that you should review and remove when they are no longer needed. If the following services were not previously active in your account, leaving them enabled might result in additional ongoing charges. See the Cost considerations section for details. Review and remove unused resources to optimize costs.
Delete or disable the following script-generated resources if they’re not required after outputs are generated. Focus first on Lambda functions and EventBridge rules if you’re not running recurring scans. If you enabled AWS Config or Security Hub specifically for this audit, evaluate whether you need them for other compliance requirements before disabling. Note: Be careful when deleting data and consider temporarily disabling services first to check for dependencies. Only delete resources generated as part of your audit outputs. Verify you have retained any necessary results before proceeding. Verify resources are not used by other workloads before deletion.
This section provides recommendations to maintain secure Amazon S3 configurations long-term. To learn more about maintaining secure Amazon S3 configurations, review the AWS documentation links provided in the conclusion. The following recommendations aren’t exhaustive. Adapt and extend them based on your organization’s evolving security requirements and AWS best practices guidance. After you’ve fixed existing issues, these practices help you maintain secure Amazon S3 configurations.
This section summarizes what you accomplished and suggests next steps to maintain your S3 security posture. By implementing the detection, remediation, and monitoring workflow outlined in this post, you can proactively identify and secure over-permissioned S3 buckets across your AWS environment. To maintain your ongoing security posture, enable IAM Access Analyzer for continuous monitoring and schedule recurring audits with EventBridge. To learn more about Amazon S3 security best practices, see Security best practices for Amazon S3 AWS Security Hub can generate exposure findings for Amazon Simple Storage Service (Amazon S3) buckets.
On the Security Hub console, the Amazon S3 bucket involved in an exposure finding and its identifying information are listed in the Resources section of the finding details. Programmatically, you can retrieve resource details with the GetFindingsV2 operation of the Security Hub CSPM API. After identifying the resource involved in an exposure finding, you can delete the resource if you don't need it. Deleting a nonessential resource can reduce your exposure profile and AWS costs. If the resource is essential, follow these recommended remediation steps to help mitigate the risk. The remediation topics are divided based on the type of trait.
A single exposure finding contains issues identified in multiple remediation topics. Conversely, you can address an exposure finding and bring down its severity level by addressing just one remediation topic. Your approach to risk remediation depends on your organizational requirements and workloads. The remediation guidance provided in this topic might require additional consultation in other AWS resources.
The Amazon S3 bucket allows principals from other AWS accounts to modify bucket permissions Here are misconfiguration traits for Amazon S3 buckets and suggested remediation steps. Harvested Online Documentation & Reference Sources • https://docs.aws.amazon.com/AmazonS3/latest/userguide/security-best-practices.html • https://docs.aws.amazon.com/AmazonS3/latest/userguide/security.html • https://aws.amazon.com/s3/security/ • https://www.decryptiondigest.com/blog/aws-s3-bucket-security-audit-checklist • https://aws.amazon.com/blogs/security/securing-your-amazon-s3-buckets-identifying-and-remediating-over-permissioned-ac cess/ • https://docs.aws.amazon.com/securityhub/latest/userguide/exposure-s3-bucket.html
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Aws S3 Bucket Security Auditing And Misconfiguration Tool.
[*] Metasploit Scan Running on Target Subnet for Aws S3 Bucket Security Auditing And Misconfiguration Tool... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |