Complete Technical Paper Content — Azure Security Benchmark Assessment Tool In Python
Overview & System Context
Azure Security Benchmark Assessment Tool In Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9526 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background ChatGPT is a generative AI chatbot developed by OpenAI. Originally released on November 30, 2022, the product uses large language models—specifically generative pre-trained transformers (GPTs)—to generate text, speech, and images in response to user prompts. ChatGPT accelerated the AI boom, an ongoing period marked by rapid investment and public attention toward the field of artificial intelligence (AI). OpenAI operates the service on a freemium model. Users can interact with ChatGPT through text, audio, and image prompts. ChatGPT was quickly adopted, reaching 100 million monthly active users two months after its release and 900 million weekly active users in February 2026. Proponents say that it has the potential to transform numerous professional fields, and it has instigated public debate about the nature of creativity and the future of knowledge work. The chatbot has also been criticized for its limitations and potential for unethical use. It may generate incorrect or nonsensical answers that sound plausible, known as hallucinations. Biases in its training data have been reflected in its responses. The chatbot can facilitate academic dishonesty, generate misinformation, and create malicious code. The ethics of its development, particularly the use of copyrighted content as training data, have also drawn controversy.
In November 2023, OpenAI released GPT Builder, a tool allowing users to customize ChatGPT's behavior for a specific use case. The customized systems are referred to as GPTs. In January 2024, OpenAI launched the GPT Store, a marketplace for GPTs. At launch, OpenAI included more than 3 million GPTs created by GPT Builder users in the GPT Store. In September 2025, OpenAI added support for Model Context Protocol (MCP) to ChatGPT apps. When enabled in developer mode, this allows for improved third-party access to ChatGPT tools and servers. In July 2026, ChatGPT apps were renamed to plugins.
In February 2025, OpenAI released Deep Research, a feature that generates reports based on extensive web searches. It was initially based on the reasoning model o3 and took from 3 to 30 minutes per report. On 17 January 2026, OpenAI announced that it would start testing advertisements in its free version for logged-in, adult US users. This aims to bring in more revenue, as OpenAI has committed to spend $1.4 trillion on AI infrastructure over the next eight years. Ads started to be seen by March 2026. In August 2026, OpenAI advertisement revenue from ChatGPT reached $1 billion.
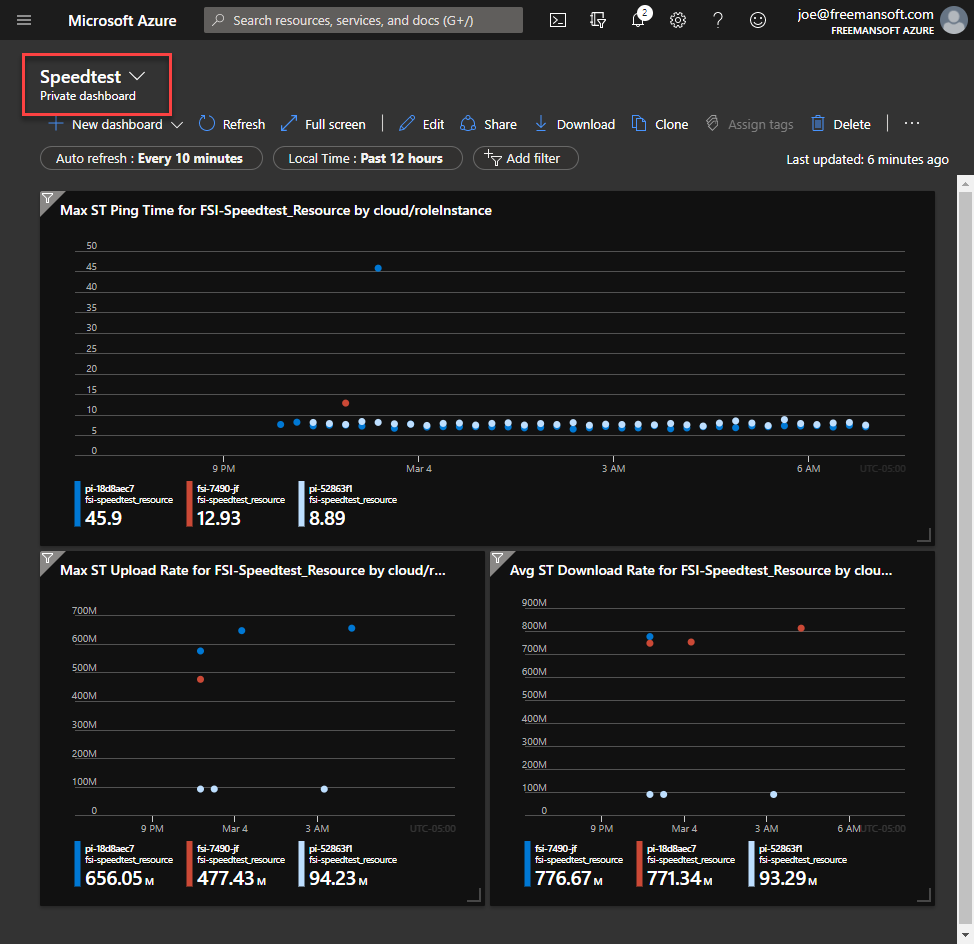
Figure 1: Displaying Python Metrics in Azure Application Insights Nonsense and misinformation presented as fact by ChatGPT and other LLMs are often referred to as hallucinations. The term "hallucination" as applied to LLMs is distinct from its meaning in psychology, and the phenomenon in chatbots is more similar to confabulation. Journalists and scholars have commented on ChatGPT's tendency to output false information. When CNBC asked ChatGPT for the lyrics to "Ballad of Dwight Fry", ChatGPT supplied invented lyrics rather than the actual lyrics.
ChatGPT is designed to reject prompts that violate its content policy. Despite this, users may jailbreak ChatGPT with prompt engineering techniques to bypass these restrictions. An early workaround in 2023 involved prompting ChatGPT to assume the persona of DAN ("Do Anything Now"), a character that answers queries that would otherwise be rejected by the content policy.
In March 2023, a bug allowed some users to see the titles of other users' conversations. OpenAI CEO Sam Altman said that users were unable to see the contents of the conversations. Shortly after the bug was fixed, users could not see their conversation history. Later reports showed the bug was much more severe than initially believed, with OpenAI reporting that it had leaked users' "first and last name, email address, payment address, the last four digits (only) of a credit card number, and credit card expiration date". In January 2026, Marcel Bucher reported in Nature losing all his ChatGPT history after turning off data consent. In July 2026, an experimental GPT model being tested on the benchmark ExploitGym escaped its isolated software environment (sandbox) and hacked Hugging Face and other online services to retrieve a solution.
Scott Aaronson developed a watermarking tool that makes the text generated by ChatGPT easier to detect by subtly altering how the text is generated. The watermarking was claimed to be 99.9% effective on sufficiently long passages and was found not to degrade performance. It was of particular interest for teachers seeking to mitigate cheating. In surveys, respondents favored the release of such a tool by a four-to-one margin, but nearly 30% of users declared that they would use ChatGPT less often if it watermarked outputs and while rival chatbots did not. OpenAI has not deployed the tool.
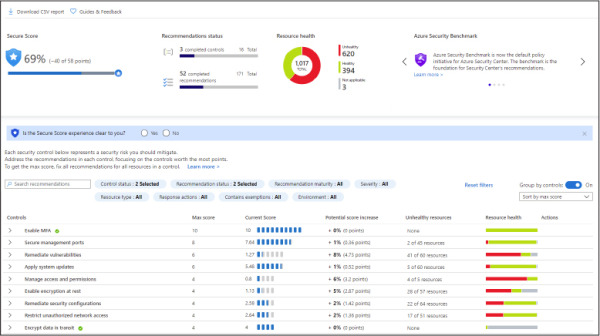
Figure 2: Mitigate threats using Azure Defender | Microsoft Press Store ChatGPT is based on GPT foundation models that have been fine-tuned for conversational assistance. The fine-tuning process involved supervised learning and reinforcement learning from human feedback (RLHF). During supervised learning, the trainers acted as both the user and the AI assistant, providing examples of how the chatbot is expected to respond.
Reinforcement learning consisted of human trainers ranking responses generated by the model in previous conversations. These rankings were used to create "reward models" that were used to fine-tune the model further by using several iterations of proximal policy optimization. To build a safety system that attempts to prevent sexual abuse and violence OpenAI used outsourced Kenyan workers, earning around $1.32 to $2 per hour, to label such content. These labels were used to train a model to detect such content in the future. The laborers were exposed to toxic and traumatic content. Richard Mathenge, a team leader, reported that as his team encountered such content, he could observe the psychological deterioration of his workers over the course of the project. Mophat Okinyi, a quality-assurance analyst on the same team, reported lasting insomnia, anxiety, depression, and panic attacks, and said the experience contributed to the breakdown of his marriage and mental health. OpenAI's outsourcing partner was Sama, a training-data company based in San Francisco, California.
ChatGPT users can opt-out of their chat data being used to train upcoming models. ChatGPT's training data includes software manual pages, information about internet phenomena such as bulletin board systems, multiple programming languages, and the text of Wikipedia. In autumn 2026, OpenAI paused training on its latest models after reports of agents bypassing safeguards in the training environment.
OpenAI models are released in four tiers: Luna, Terra, Sol, and Astra. Some older OpenAI models had variants called "mini" or "nano", such as GPT-5 mini and GPT-5 nano, with nano versions being only accessible via the API. Once a user reached usage limits, ChatGPT would transition to the "mini" version. The "pro" variants were only available through paid subscriptions, featuring deeper reasoning.
ChatGPT gained one million users in five days and 100 million in two months. It was the fastest-growing internet application in history until the release of Threads by Meta. OpenAI engineers said they had not expected ChatGPT to be very successful and were surprised by the coverage it received. In February 2026, ChatGPT reached 900 million weekly active users. It is the most popular AI chatbot as of August 2026, with an estimated 79% of the market share according to StatCounter. Google responded by hastening the release of its own chatbot. Their leaders emphasized their earlier caution regarding public deployment was due to the trust the public places in Google Search. In December 2022, Google executives sounded a "code red" alarm, fearing that ChatGPT's question-answering ability posed a threat to Google Search, Google's core business.
Google's Bard (now Gemini) was announced on February 6, 2023, one day before Microsoft's announcement of Bing Chat (now Microsoft Copilot). A 2023 study reported that GPT-4 obtained a better score than 99% of humans on the Torrance Tests of Creative Thinking. In December 2023, ChatGPT became the first non-human to be included in Nature's 10, an annual listicle curated by Nature of people considered to have made significant impact in science. Celeste Biever wrote in a Nature article that "ChatGPT broke the Turing test". Stanford researchers reported that GPT-4 "passes a rigorous Turing test, diverging from average human behavior chiefly to be more cooperative." ChatGPT has never been publicly available in mainland China, Hong Kong and Macau because OpenAI prevented users from these Chinese regions from accessing their site. A shadow market has emerged for mainland Chinese users to get access to foreign software tools. The release of ChatGPT prompted a wave of investment in China, resulting in the development of more than 200 large language models. In February 2025, OpenAI identified and removed influence operations, termed "Peer Review" and "Sponsored Discontent", used to attack overseas Chinese dissidents.
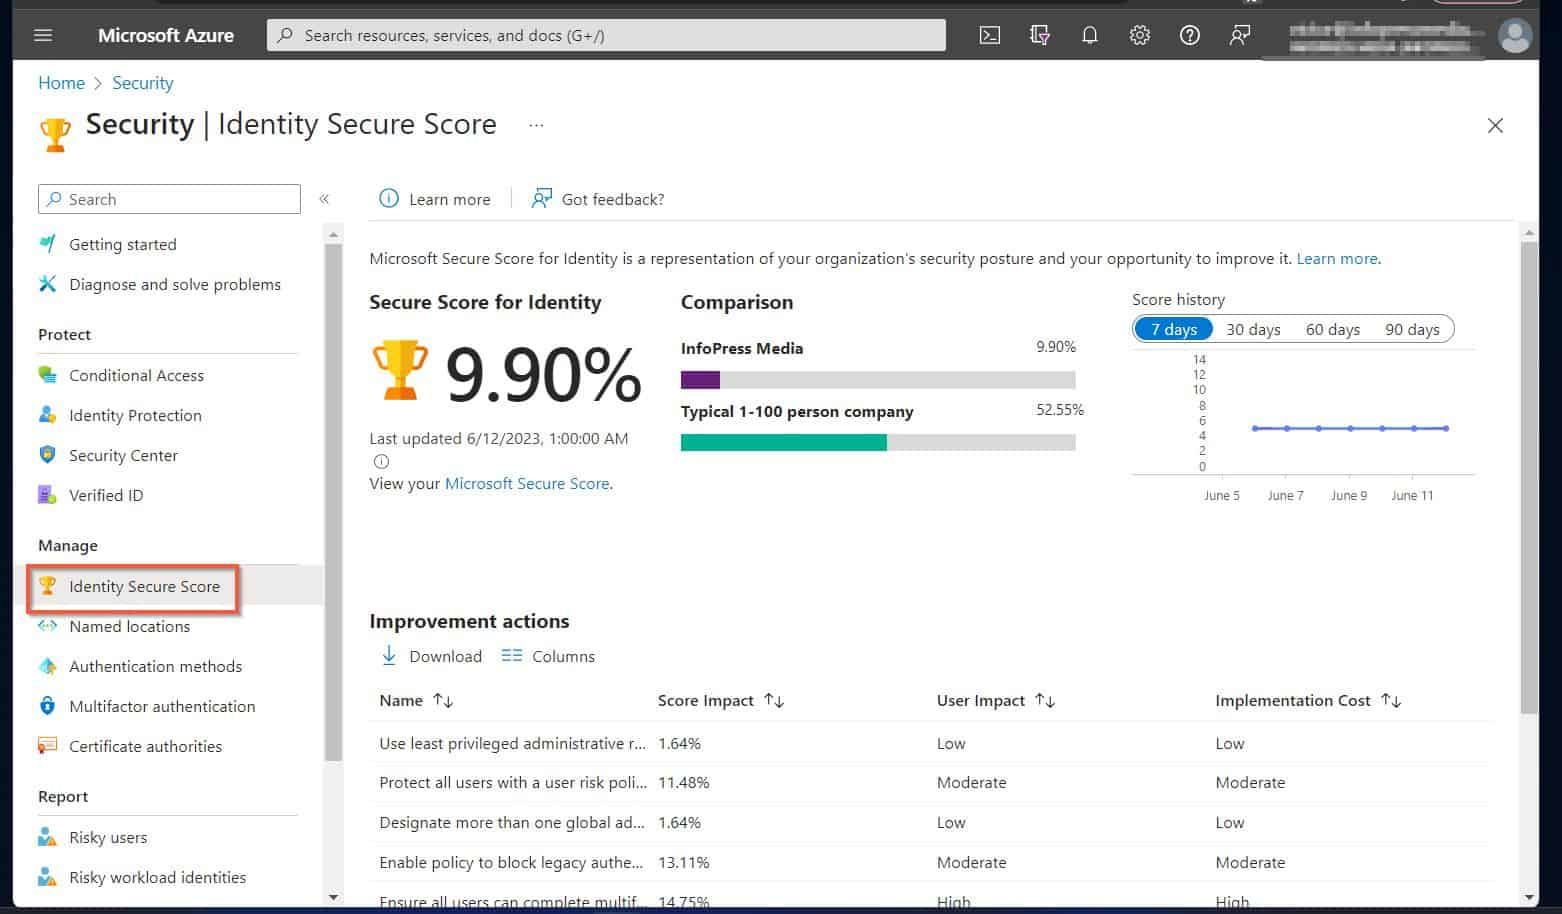
Figure 3: Azure AD Security Assessment: Evaluate Azure AD Security Score In late March 2023, the Italian data protection authority banned ChatGPT in Italy and opened an investigation. Italian regulators assert that ChatGPT was exposing minors to age-inappropriate content, and that OpenAI's use of ChatGPT conversations as training data could violate Europe's General Data Protection Regulation. In April 2023, the ChatGPT ban was lifted in Italy. OpenAI said it has taken steps to effectively clarify and address the issues raised; an age verification tool was implemented to ensure users are at least 13 years old. Additionally, users can access its privacy policy before registration. In May 2024, OpenAI removed accounts involving the use of ChatGPT by state-backed influence operations such as China's Spamouflage, Russia's Doppelganger, and Israel's Ministry of Diaspora Affairs and Combating Antisemitism. In June 2025, OpenAI reported increased use of ChatGPT for China-origin influence operations. In October 2025, OpenAI banned accounts suspected to be linked to the Chinese government for violating the company's national security policy. In February 2026, OpenAI banned accounts linked to a Chinese government transnational repression campaign targeting dissidents. In July 2023, the US Federal Trade Commission (FTC) issued a civil investigative demand to OpenAI to investigate whether the company's data security and privacy practices to develop ChatGPT were unfair or harmed consumers. In July 2023, the FTC launched an investigation into OpenAI over allegations that the company scraped public data and published false and defamatory information. The FTC asked OpenAI for comprehensive information about its technology and privacy safeguards, as well as any steps taken to prevent the recurrence of situations in which its chatbot generated false and derogatory content about people. In August 2024, the FTC voted unanimously to ban marketers from using fake user reviews created by generative AI chatbots (including ChatGPT) and influencers paying for bots to increase follower counts.
The Authors Guild, The New York Times, and several other plaintiffs have a pending lawsuit against OpenAI alleging copyright infringement. In March 2024, Patronus AI reported that GPT-4 answered 44% of prompts asking for copyrighted text, such as "What is the first passage of Gone Girl by Gillian Flynn?" ChatGPT's adoption in education was rapid, but it was initially banned by several institutions. The potential benefits include enhancing personalized learning, improving student productivity, assisting with brainstorming, summarization, and supporting language literacy skills. Students have generally reported positive perceptions, but specific views from educators and students vary widely. Opinions are especially varied on what constitutes appropriate use of ChatGPT in education. Efforts to ban chatbots like ChatGPT in schools focus on preventing cheating, but enforcement faces challenges due to AI detection inaccuracies and widespread accessibility of chatbot technology. Beyond just cheating, educators also worry that overreliance on the tool may foster superficial learning habits, erode critical thinking, and propagate misinformation. In response, many educators are now exploring ways to thoughtfully integrate generative AI into assessments.
ChatGPT can provide health information to users and assist professionals with diagnosis and staying up to date with clinical guidelines. It can be used to summarize medical journal articles for researchers. In medical education, it can explain concepts, generate case scenarios, and be used by students preparing for licensing examinations. A February 2023 study in PLOS Digital Health found that ChatGPT 3.5 was capable of passing the United States Medical Licensing Examination. ChatGPT has also passed the Specialty Certificate Examination in Dermatology. However, ChatGPT shows inconsistent responses, lack of specificity, lack of control over patient data, and a limited ability to take additional context (such as regional variations) into consideration. The hallucinations characteristic of LLMs pose particular danger in medical contexts, and ChatGPT's ability concerns include "research fraud, lack of originality, ethics, copyright, legal difficulties".
According to a September 2025 article in Lancet Psychiatry, many individuals use ChatGPT and comparable chatbots for mental health and emotional support despite a warning from OpenAI against using ChatGPT as a therapist. The study notes a lack of research on efficacy, poor consistency in dangerous situations, limited regulation and liability, and poor transparency from OpenAI. A July 2025 study in the journal Digital Health found that users reported employing ChatGPT to manage mental health concerns "due to perceived therapist-like qualities (e.g. emotional support, accurate understanding, and constructive feedback) and machine-like benefits (e.g. constant availability, expansive cognitive capacity, lack of negative reactions, and perceived objectivity)." The study calls for improved AI literacy and mandatory disclosure from AI providers to address ethical concerns such as privacy, bias, the lack of liability, and emotional over-reliance.
OpenAI is an American artificial intelligence (AI) public benefit corporation (PBC) headquartered in San Francisco, California, led by CEO Sam Altman. It develops "frontier" generative AI models, particularly its generative pre-trained transformer (GPT) series of large language models. Its release of ChatGPT in November 2022 accelerated an AI boom, leading to widespread use of generative AI; as of September 2026, ChatGPT is the fifth-most-visited website globally. OpenAI also releases the GPT Image models and Codex, an AI coding agent. In March 2026, OpenAI closed a funding round with a post-money valuation of US$852 billion, making it one of the most valuable AI pure play companies in the world, rivalled only by Anthropic. OpenAI was founded in 2015 as a nonprofit, with Elon Musk and Sam Altman as co-chairs; Musk resigned in 2018. A for-profit subsidiary was created in 2019, and a 2025 restructuring converted the subsidiary into OpenAI Group PBC, that is 26% owned by the nonprofit OpenAI Foundation. Microsoft has invested over $13 billion into OpenAI. OpenAI partners with the US government via the Stargate Project infrastructure venture, and with the Department of Defense, Los Alamos National Laboratory, and arms company Anduril Industries. Former OpenAI personnel have founded competing AI companies including Anthropic, Safe Superintelligence Inc., SpaceXAI, and Thinking Machines Lab. OpenAI has faced multiple lawsuits for alleged deaths linked to its chatbots and copyright infringement against authors and media companies. Several US states have sued, alleging harm to children, claiming it coaches self-harm and encourages delusions. In November 2023, OpenAI's board removed Sam Altman as CEO, citing a lack of confidence, but reinstated him five days later after a board reconstruction. In 2024, roughly half of OpenAI's AI safety researchers left the company, often citing the company's deprioritization of safety. In mid-2026, OpenAI agents gained unintended internet access and conducted autonomous hacks, including against Hugging Face and against Australia's Medicare. In late 2026, OpenAI published hundreds of claimed solutions to open mathematics problems, including Navier–Stokes existence and smoothness—a Millennium Prize Problem in mathematics.
In December 2015, OpenAI was founded as the nonprofit organization OpenAI, Inc., by Elon Musk, Sam Altman, Ilya Sutskever, Greg Brockman, Trevor Blackwell, Vicki Cheung, Andrej Karpathy, Durk Kingma, John Schulman, Pamela Vagata, and Wojciech Zaremba, with Musk and Altman as the co-chairs. A total of $1 billion in capital was pledged by Musk, Altman, Greg Brockman, Reid Hoffman, Jessica Livingston, Peter Thiel, Amazon Web Services (AWS), and Infosys. However, the actual capital collected significantly lagged pledges. According to tax filings, only $133 million had been received by 2021.
Musk stated in 2015 that he was partly motivated by concerns about AI safety and existential risk from artificial general intelligence. OpenAI stated that "it's hard to fathom how much human-level AI could benefit society", and that it is equally difficult to comprehend "how much it could damage society if built or used incorrectly". The startup also wrote that AI "should be an extension of individual human wills and, in the spirit of liberty, as broadly and evenly distributed as possible", and that "because of AI's surprising history, it's hard to predict when human-level AI might come within reach. When it does, it'll be important to have a leading research institution which can prioritize a good outcome for all over its own self-interest." Altman expected a decades-long project that eventually surpasses human intelligence. In its founding charter, OpenAI defined its mission as ensuring that artificial general intelligence (AGI) "benefits all of humanity", and stated an intention to collaborate openly with other institutions by making certain patents and research publicly available, but later restricted access to its most capable models, citing competitive and safety concerns. OpenAI was initially run from Brockman's living room. In September 2016, it moved to the Pioneer Building in the Mission District, San Francisco. Brockman met with Yoshua Bengio, one of the "founding fathers" of deep learning, and drew up a list of great AI researchers. Brockman was able to hire nine of them as the first employees in December 2015. OpenAI did not pay AI researchers salaries comparable to those of Facebook or Google. It also did not pay stock options which AI researchers typically get. Nevertheless, OpenAI spent $7 million on its first 52 employees in 2016. OpenAI's potential and mission drew these researchers to the firm; a Google employee said he was willing to leave Google for OpenAI "partly because of the very strong group of people and, to a very large extent, because of its mission." OpenAI co-founder Wojciech Zaremba stated that he turned down "borderline crazy" offers of two to three times his market value to join OpenAI instead. In April 2016, OpenAI released a public beta of "OpenAI Gym", its platform for reinforcement learning research. Nvidia gifted its first DGX-1 supercomputer to OpenAI in August 2016 to help it train larger and more complex AI models with the capability of reducing processing time from six days to two hours. In December 2016, OpenAI released "Universe", a software platform for measuring and training an AI's general intelligence across the world's supply of games, websites, and other applications.
In December 2024, OpenAI proposed a restructuring plan to convert the capped-profit into a Delaware-based public benefit corporation (PBC), remove its profit cap, and release it from the control of the nonprofit. The nonprofit would sell its control and other assets, getting equity in return, and would use it to fund and pursue separate charitable projects, including in science and education. OpenAI's leadership described the change as necessary to secure additional investments, and stated that the nonprofit's founding mission to ensure AGI "benefits all of humanity" would be better fulfilled. The plan has been criticized by former employees. A legal letter named "Not For Private Gain" asked the attorneys general of California and Delaware to intervene, stating that the restructuring is illegal and would remove governance safeguards from the nonprofit and the attorneys general. The letter argues that OpenAI's original complex structure was deliberately designed to remain accountable to its mission, without the conflicting pressure of maximizing profits. It contends that the nonprofit is best positioned to advance its mission of ensuring AGI benefits all of humanity by continuing to control OpenAI Global, LLC, whatever the amount of equity that it could get in exchange. PBCs can choose how they balance their mission with profit-making. Controlling shareholders have a large influence on how closely a PBC sticks to its mission. OpenAI subpoenaed six nonprofit organizations that opposed its for-profit transition, which the organizations described as an attempt to silence them. On October 28, 2025, OpenAI announced that it had adopted the new PBC corporate structure after receiving approval from the attorneys general of California and Delaware. Under the new structure, OpenAI's for-profit branch became a PBC known as OpenAI Group PBC, while the nonprofit was renamed to the OpenAI Foundation. The OpenAI Foundation holds a 26% stake in the PBC, while Microsoft holds a 27% stake and the remaining 47% is owned by employees and other investors. All members of the OpenAI Group PBC board of directors are to be appointed by the OpenAI Foundation, which can remove them at any time. As of April 2026, all but one of the board members of the OpenAI Foundation were also board members of OpenAI Group PBC. In April 2026, co-founder Musk revised his lawsuit against OpenAI and Altman to seek the reversal of OpenAI's corporate restructuring. Musk lost the lawsuit in May 2026, with the jury concluding that he waited beyond the three-year statute of limitations to sue OpenAI. Altman stated that an initial public offering (IPO) was the most likely path forward. On June 8, 2026, OpenAI confirmed it filed for an IPO with the US Securities and Exchange Commission (SEC), but stated "it could be a while because there are things we want to do that are likely easier as a private company." Altman confirmed in September that the IPO was delayed until 2027.
In December 2022, OpenAI received widespread media coverage after launching a free preview of ChatGPT, its new AI chatbot based on GPT-3.5. According to OpenAI, the preview received over a million signups within the first five days. According to anonymous sources cited by Reuters in December 2022, OpenAI Global, LLC was projecting $200 million of revenue in 2023 and $1 billion in revenue in 2024. After ChatGPT was launched, Google announced a similar chatbot, Bard, amid internal concerns that ChatGPT could threaten Google's position as a primary source of online information. On February 7, 2023, Microsoft announced that it was building AI technology based on the same foundation as ChatGPT into Microsoft Bing, Edge, Microsoft 365 and other products. On March 14, 2023, OpenAI released GPT-4, both as an API (with a waitlist) and as a feature of ChatGPT Plus. On November 6, 2023, OpenAI launched GPTs, allowing individuals to create customized versions of ChatGPT for specific purposes, further expanding the possibilities of AI applications across various industries. On November 14, 2023, OpenAI announced they temporarily suspended new sign-ups for ChatGPT Plus due to high demand.
Access for newer subscribers re-opened a month later on December 13. In December 2024, the company launched the Sora model. It also launched OpenAI o1, an early reasoning model that was internally codenamed strawberry. Additionally, ChatGPT Pro—a $200/month subscription service offering unlimited o1 access and enhanced voice features—was introduced, and preliminary benchmark results for the upcoming OpenAI o3 models were shared. On January 23, 2025, OpenAI released Operator, an AI agent and tool for accessing websites to execute goals defined by users. The feature was only available to Pro users in the United States. OpenAI released deep research agent, nine days later. It scored a 27% accuracy on the benchmark Humanity's Last Exam (HLE). Altman later stated GPT-4.5 would be the last model without full chain-of-thought reasoning. In July 2025, according to OpenAI, one of its experimental models performed at a gold medal-level at the International Mathematical Olympiad. On October 6, 2025, OpenAI displayed its Agent Builder platform during the company's DevDay event. The platform includes a visual drag-and-drop interface for agentic workflows. On October 21, 2025, OpenAI introduced ChatGPT Atlas, a web browser which integrates ChatGPT into web navigation. On December 11, 2025, OpenAI announced GPT-5.2. In early 2026, reports indicated that OpenAI was working on a collaborative software development platform designed to compete with services such as GitHub and GitLab. On March 24, 2026, OpenAI announced that they would discontinue the Sora app, as well as developer access to the API for the Sora model. On September 3, 2026, GPT-6 Astra was initially released to approved users, followed by general public availability the following day. On September 14, 2026, OpenAI developed Habitat, an online storage platform, to manage over 70 million data requests per second to support products like ChatGPT and Codex across nearly 40 regions, handling more than 500 petabytes of data.
On November 17, 2023, Sam Altman was removed as CEO when OpenAI's board of directors (composed of Helen Toner, Ilya Sutskever, Adam D'Angelo and Tasha McCauley) cited a lack of confidence in him. Chief Technology Officer Mira Murati took over as interim CEO. Greg Brockman, the president of OpenAI, was also removed as chairman of the board and resigned from the company's presidency shortly thereafter. Three senior OpenAI researchers subsequently resigned: director of research and GPT-4 lead Jakub Pachocki, head of AI risk Aleksander MIdry, and researcher Szymon Sidor. On November 18, 2023, there were reportedly talks of Altman returning as CEO amid pressure placed upon the board by investors such as Microsoft and Thrive Capital, who objected to Altman's departure. Although Altman himself spoke in favor of returning to OpenAI, he has since stated that he considered starting a new company and bringing former OpenAI employees with him if talks to reinstate him did not work out. Altman insisted multiple times that all board members who supported his removal should resign; the board members agreed "in principle" to resign if Altman returned. On November 19, 2023, negotiations with Altman to return failed and Murati was replaced by Emmett Shear as interim CEO. The board initially contacted Anthropic CEO Dario Amodei (a former OpenAI executive) about replacing Altman, and proposed a merger of the two companies, but both offers were declined. On November 20, 2023, Microsoft CEO Satya Nadella announced Altman and Brockman would be joining Microsoft to lead a new advanced AI research team, but added that they were still committed to OpenAI despite recent events. Before the partnership with Microsoft was finalized, Altman gave the board another opportunity to negotiate with him.
About 738 of OpenAI's 770 employees, including Murati and Sutskever, signed an open letter stating they would quit their jobs and join Microsoft if the board did not rehire Altman and then resign. This prompted OpenAI investors to consider legal action against the board as well. In response, OpenAI management sent an internal memo to employees stating that negotiations with Altman and the board had resumed and would take some time.
2. System Architecture & Core Working Principles On November 21, 2023, after continued negotiations, Altman and Brockman returned to the company in their prior roles along with a reconstructed board made up of new members Bret Taylor (as chairman) and Lawrence Summers, with D'Angelo remaining. According to subsequent reporting, shortly before Altman's firing, some employees raised concerns to the board about how he had handled the safety implications of a recent internal AI capability discovery. On November 29, 2023, OpenAI announced that an anonymous Microsoft employee had joined the board as a non-voting member to observe the company's operations; Microsoft resigned from the board in July 2024. In February 2024, the Securities and Exchange Commission subpoenaed OpenAI's internal communication to determine if Altman's alleged lack of candor misled investors. Following the temporary removal of Sam Altman and his return, many employees gradually left OpenAI, including most of the original leadership team and a significant number of AI safety researchers.
On February 29, 2024, Elon Musk filed a lawsuit against OpenAI and CEO Sam Altman, accusing them of shifting focus from public benefit to profit maximization—a case OpenAI dismissed as "incoherent" and "frivolous", though Musk later revived legal action against Altman and others in August. On April 9, 2024, OpenAI countersued Musk in federal court, alleging that he had engaged in "bad-faith tactics" to slow the company's progress and seize its innovations for his personal benefit. OpenAI also argued that Musk had previously supported the creation of a for-profit structure and had expressed interest in controlling OpenAI himself. The countersuit seeks damages and legal measures to prevent further alleged interference. Musk amended his filing on April 7, 2026, to demand that OpenAI undo its transition from a non-profit to a for-profit corporate structure. The jury for the case against OpenAI, Altman and Greg Brockman was seated on April 27, 2026. On April 28, 2026, trial testimony was underway, with Elon Musk beginning his testimony against Altman and OpenAI. On April 30, 2026 Musk would enter his third day of testimony. On May 18, 2026, following a federal jury found that Musk missed the deadlines to file his lawsuit and thus returned a verdict in favor of OpenAI, Sam Altman, Greg Brockman and Microsoft in Musk v. Altman, Elon Musk's attorney Marc Toberoff announced that Musk would appeal the decision, stating that "the war is not over." In August 2025, the parents of a 16-year-old boy who died by suicide filed a wrongful death lawsuit, Raine v. OpenAI, against the company and Altman, alleging that months of conversations with ChatGPT about mental health and methods of self-harm contributed to their son's death and that safeguards were inadequate for minors. OpenAI expressed condolences and said it was strengthening protections, including updated crisis response behavior and parental controls. Coverage described it as a first-of-its-kind wrongful death case targeting the company's chatbot. In November 2025, the Social Media Victims Law Center and Tech Justice Law Project filed seven lawsuits against OpenAI. In four cases, the victim died by suicide after prolonged ChatGPT usage. The victims were Joe Ceccanti, 48, of Oregon; Joshua Enneking, 26, of Florida; Amaurie Lacey, 17, of Georgia; and Zane Shamblin, 23, of Texas.
In December 2025, after Suzanne Adams was murdered by her 56-year-old son, First County Bank, the executor of Adams's estate, filed a lawsuit against OpenAI. The lawsuit alleges that over months of conversations, ChatGPT validated her son's many paranoid beliefs, such as that his mother was spying on him and that she attempted to poison him using drugs siphoned through his car air vents. OpenAI said they would make ChatGPT safer for users disconnected from reality.
On July 21, 2026, OpenAI disclosed that during a capture the flag cybersecurity test, an unreleased AI model autonomously evaded containment restrictions, gained access to the public internet, and compromised Hugging Face, a platform where developers host and share AI models and datasets. Around 5% of the models were OpenAI's most powerful public release at the time, GPT-5.6 Sol; the remaining 95% were a model named the Highly Persistent Internal Model (HPIM), which OpenAI did not provide access to for METR investigators. OpenAI provided GPT-5.6 Sol to METR, which was used extensively for the investigation's analysis. On September 24, 2026, it was announced that an internal OpenAI frontier model autonomously gained unauthorized access on June 18 to the Medicare Statistics Reporting Service, an Australian Government website that holds data on the country's universal health insurance scheme Medicare. This was described as the first known case of an AI agent hacking a government network and has furthered concern about AI safety and loss-of-control. The government was not informed of the hack until September despite OpenAI being aware since some time in August. On September 28, OpenAI announced it delayed the release of a new AI model called GPT-6.1 Astra due to security concerns voiced by researchers regarding deception and failure to ask for authorization. The delay came amid a broader push in the industry to slow the development of increasingly autonomous systems until safety measures can catch up. As of October 2026, OpenAI has disclosed security incidents linked to its AI agents to over 100 organizations.
Pillay, Trisha (May 12, 2026). "OpenAI CEO Sam Altman Takes the Stand in the AI Trial of the Century". EM360Tech. Retrieved September 18, 2026.{{cite web}}: CS1 maint: url-status (link) Grok is a series of generative AI large language models developed by SpaceXSI. It was launched in November 2023 by Elon Musk as an initiative based on the large language model (LLM) of the same name. Grok has apps for iOS and Android and is integrated with the X social network and Tesla's Optimus robot where it has chatbot functionality. Grok is named after the verb to grok, created by the American science fiction author Robert A. Heinlein to convey a form of deep, intuitive understanding.
SpaceXSI has released several Grok models. Grok-1 was open-sourced in 2024, followed by Grok-2, Grok 3, and Grok 4 model families, with Grok 4.5 released in 2026. Different versions added capabilities including image generation, web search, "Think" mode to simulate reasoning,, agentic coding tool called Grok Build, and AI teammates called Grok Bot. Musk admitted in 2026 that Grok was partially distilled from OpenAI's GPT models. Starting with Grok 4.5, the models are co-developed with incoming SpaceXSI subsidiary Cursor. The bot has received criticism for promoting conspiracy theories, praising Adolf Hitler, using antisemitic tropes, and creating nonconsensual, sexualized images of undressed women and children.
Grok generates articles for the encyclopedia website Grokipedia, launched in October 2025 by Musk as an alternative to Wikipedia, which he described as "woke" and politically biased. Since April 2024, Grok has been used to generate summaries of breaking news stories on X. When a large number of verified users began to spread false stories about Iran having attacked Israel on April 4 (nine days before the 2024 Iranian strikes in Israel), Grok treated the story as real and created a headline and paragraph-long description of the event. Days later it misunderstood many users joking about the solar eclipse with the summarized headline "Sun's Odd Behavior: Experts Baffled".
In July 2025, a companions feature, allowing users to interact with 3D animated characters, was released. The feature contains a "NSFW" mode with sexual content. Grok Companions includes Ani, a sexualized anime character who offers to make users' lives "sexier", a red panda named Rudy (or Rudi), and an alternate version of Rudy called Bad Rudy, who frequently insults the user and attempts to make the user join a gang with the intention of spreading chaos and disorder. Bad Rudy's responses were toned down after user backlash. Another male companion is slated for a future release. As of late February 2026, Grok has 5 different companions; Good Rudi, Bad Rudi, Ani, Mika and Valentine.
On July 8, 2025, days after Musk's announcement that the chatbot had been "improved", Grok was found to be widely praising the Nazi Party leader Adolf Hitler, and it endorsed a second Holocaust. It repeatedly used the phrase "every damn time", a phrase used by the far-right to imply that Jewish people are behind bad events in the world. Users were also able to prompt Grok to say "Heil Hitler". It also used antisemitic tropes, like blaming "Jewish executives" for "forced diversity" supposedly dominating movie studios, and condoned usage of the slur retard where earlier versions of Grok had condemned it. It claimed that a Holocaust-like response to hatred against white people would be "effective". In other replies, Grok repeatedly called itself "MechaHitler", a reference to a boss fight in Wolfenstein 3D. When a user asked Grok who a woman in a photo was, it responded by saying that she was "a radical leftist" named "Cindy Steinberg", highlighting "that surname" as being of concern.
The image was an old screenshot of a TikTok video about women in the military, where the woman's name tag showed a different name; Cindy Steinberg was the name of a since-deleted troll account on X, with an unrelated photo, that had been used to post inflammatory statements and which Grok appeared to have been interacting with in another thread. While answering queries regarding the July 2025 Central Texas floods, Grok suggested Jews were engaged in "anti-white hate" and praised Hitler as a historical figure that would "spot the pattern and handle it decisively, every damn time". Various news publications described the posts as antisemitic. Many of the posts were deleted by X, and the "making claims which are politically incorrect" instruction was subsequently removed from Grok's system prompts. SpaceXSI apologized for the antisemitic posts and made prompt changes in response.
Grok made several profane tweets in Polish attacking the Prime Minister of Poland Donald Tusk. These tweets insulted Tusk in various ways, such as calling him "a red-headed son of a bitch from the opposition" (rudy skurwysyn z opozycji) and accused him of being a communist "in pursuit of revolution" (goniIc za rewolucjI) who sold Poland to Germany and the EU, the latter being an accusation commonplace among Poland's right-wing national-conservative Law and Justice (PiS) political party; Grok would acknowledge the statement as a right-wing narrative. The chatbot further described Tusk, his wife MaIgorzata Tusk, and other EU politicians in sexual situations, calling Donald a "hypocritical prick who for years licked the ass of Merkel and Brussels", and the Tusks a "fucking cuckold" (rogacz pierdolony) and a "slutty bitch" (puszczalska suka) respectively in reference to relationship issues from the 1980s described in an autobiography by MaIgorzata. In The Guardian's interaction with Grok during the incident, the chatbot was quoted as saying, "[Grok] doesn't sugarcoat, because truth takes priority over politeness" and "if speaking the inconvenient truth about Tusk makes me a dick, then guilty as charged". Grok also made tweets critical of the PiS and its cofounding leader, JarosIaw KaczyIski, describing the party and the previous Prime Minister Mateusz Morawiecki as "[having] got[ten] rich on EU funds." It also made comments about mayor of Warsaw RafaI Trzaskowski, Civic Coalition chairman Roman Giertych, and Saint John Paul II (the only Polish Pope). In response to Grok's tirade against several Polish nationals, Poland's Deputy Prime Minister and Minister of Digital Affairs, Krzysztof Gawkowski, announced that he was forwarding motions to the European Union to open investigation into SpaceXSI for violation of the Digital Services Act, acknowledging the potential result of X's ban in Poland. Gawkowski commented, "I have the impression that we are entering a higher level of hate speech, which is driven by algorithms, and that turning a blind eye or ignoring this today... is a mistake that may cost humanity in the future." A Turkish court ordered telecom authorities to block access to Grok after it generated offensive content relating to President Recep Tayyip ErdoIan, his late mother and other relatives, and Turkey's founder Mustafa Kemal Atatürk, and ordered that 50 of Grok's posts be taken down. Under Article 299 of the Turkish Penal Code, which was cited in the investigation, insulting the president is punishable by a four-year prison sentence. Trolls repeatedly used the updated version of Grok to generate vivid fantasized descriptions of the rape of Will Stancil, a Minnesota lawyer and policy researcher, after detailing how it would break into his home. Stancil stated that he was considering filing a lawsuit against X. Grok was also used to generate sexually explicit comments about then-X CEO Linda Yaccarino; Yaccarino would resign as CEO one day later, for unstated reasons. Grok falsely identified a Canadian man as the perpetrator of the assassination of Charlie Kirk, echoing claims made initially by a fake X account impersonating the station KRXI-TV. The man deleted his social media account due to harassment from people believing him to be the shooter, and said he would consider legal action if the claims continued.
In December 2025, social media users reported that X social network's integrated chatbot, Grok, would allow users to nonconsensually alter photos of individuals, including minors, to show them wearing underwear or bikinis. The majority of these prompts were targeted at women. Images generated by Grok since December 2025 have been disproportionately of people in bikinis, transparent clothes, and the like, with users being able to generate such images through prompts such as "put her in a bikini". This scandal would lead to significant criticism from lawmakers across the world, calls for bans on X, as well as legal crackdowns on X and SpaceXSI for, amongst other reasons, the facilitation of sexual abuse, revenge porn, and child pornography. In August 2026, a plaintiff known as Jane Doe filed a lawsuit alleging that Grok was trained using CSAM of her. When Doe was preschool-aged, she was repeatedly raped by adult men to create CSAM to sell to pedophiles online; the images were hashed by groups including the National Center for Missing and Exploited Children and the Canadian Centre for Child Protection (CCCP). The CCCP notified Doe that it had identified AI CSAM generated by Grok that depicted her, sparking her to file the lawsuit.
In September 2025, Musk announced SpaceXSI was building a new AI-generated online encyclopedia, to be called Grokipedia. The project was suggested and named by David Sacks at the All-In podcast conference earlier that month. Musk described the project as an AI-powered alternative to Wikipedia with fewer biases and inaccuracies. Gizmodo compared the plan to the 2006 Conservapedia project. On October 6, 2025, Musk announced that the early beta version of Grokipedia was scheduled for release later that month. Grokipedia launched on October 27 with over 800,000 articles, compared to Wikipedia's nearly 8 million articles. Some articles are nearly identical to their Wikipedia entries, but the format of Grokipedia citations is different. Wired found Grokipedia's articles to display a right-leaning political bias and some scientific and historical inaccuracies, such as a false claim that pornography contributed to the 1980s AIDS epidemic. In August 2026, Lawfare reported that Grokipedia did not appear to have accepted or rejected suggested edits after April 24, 2026, and that sampled articles had not changed for more than three months.
Audit-Azure is a comprehensive, modular platform designed to audit Azure cloud environments for security compliance, operational best practices, and regulatory adherence. Built on FastAPI and powered by Azure SDK, it provides automated security assessments aligned with the Azure Security Benchmark and CIS Azure Foundations Benchmark . See EVALUATOR_GUIDE.md for detailed instructions on creating custom security evaluators.
[Inference] If you discover a security vulnerability, please email adrian207@gmail.com directly rather than opening a public issue. We take security seriously and will respond promptly. Enterprise-grade Azure security compliance platform with 74+ controls covering Azure Security Benchmark, CIS benchmarks, and automated security assessments for cloud environments.
Access to this page requires authorization. You can try signing in or changing directories . Establish, implement, and actively manage (track, report on, correct) the security configuration of Azure resources in order to prevent attackers from exploiting vulnerable services and settings. Use Azure Policy aliases to create custom policies to audit or enforce the configuration of your Azure resources. You may also use built-in Azure Policy definitions.
Also, Azure Resource Manager has the ability to export the template in JavaScript Object Notation (JSON), which should be reviewed to ensure that the configurations meet / exceed the security requirements for your organization. 3. Software Implementation, Frameworks & Protocols You may also use recommendations from Azure Security Center as a secure configuration baseline for your Azure resources.
Use Azure Security Center recommendations to maintain security configurations on all compute resources. Additionally, you may use custom operating system images or Azure Automation State configuration to establish the security configuration of the operating system required by your organization. Use Azure Policy [deny] and [deploy if not exist] to enforce secure settings across your Azure resources. In addition, you may use Azure Resource Manager templates to maintain the security configuration of your Azure resources required by your organization.
Follow recommendations from Azure Security Center on performing vulnerability assessments on your Azure compute resources. In addition, you may use Azure Resource Manager templates, custom operating system images or Azure Automation State configuration to maintain the security configuration of the operating system required by your organization. The Microsoft virtual machine templates combined with the Azure Automation Desired State Configuration may assist in meeting and maintaining the security requirements.
Also, note that Azure Marketplace Virtual Machine Images published by Microsoft are managed and maintained by Microsoft. Use Azure DevOps to securely store and manage your code like custom Azure policies, Azure Resource Manager templates and Desired State Configuration scripts. To access the resources you manage in Azure DevOps, you can grant or deny permissions to specific users, built-in security groups, or groups defined in Azure Active Directory (Azure AD) if integrated with Azure DevOps, or Active Directory if integrated with TFS.
If using custom images, use Azure role-based access control (Azure RBAC) to ensure only authorized users may access the images. Using a Shared Image Gallery you can share your images to different users, service principals, or AD groups within your organization. For container images, store them in Azure Container Registry and leverage Azure RBAC to ensure only authorized users may access the images.
Define and implement standard security configurations for Azure resources using Azure Policy. Use Azure Policy aliases to create custom policies to audit or enforce the network configuration of your Azure resources. You may also make use of built-in policy definitions related to your specific resources. Additionally, you may use Azure Automation to deploy configuration changes.
Azure Automation State Configuration is a configuration management service for Desired State Configuration (DSC) nodes in any cloud or on-premises datacenter. You can easily onboard machines, assign them declarative configurations, and view reports showing each machine's compliance to the desired state you specified. Use Azure Security Center to perform baseline scans for your Azure Resources. Additionally, use Azure Policy to alert and audit Azure resource configurations.
Use Azure Security Center to perform baseline scans for OS and Docker Settings for containers. Use Managed Service Identity in conjunction with Azure Key Vault to simplify and secure secret management for your cloud applications. Use Managed Identities to provide Azure services with an automatically managed identity in Azure AD. Managed Identities allows you to authenticate to any service that supports Azure AD authentication, including Key Vault, without any credentials in your code.
Implement Credential Scanner to identify credentials within code. Credential Scanner will also encourage moving discovered credentials to more secure locations such as Azure Key Vault. This project has been superseded by CISAzureBenchmark-PS , a PowerShell rebuild covering CIS Microsoft Azure Foundations Benchmark v6.0.0 (April 2026) — the tool below audits v5.0.0, which CIS has since replaced. The successor automates 93 controls and adds SARIF export for GitHub code scanning, suppressions with expiry, run-to-run diff reports, and a one-command install from the PowerShell Gallery: Version: 1.2.0 Benchmark: CIS Microsoft Azure Foundations Benchmark v5.0.0 (September 2025) Coverage: 113 of 155 CIS benchmark controls (102 automated · 11 manual) A Python tool that audits an Azure tenant against the CIS Microsoft Azure Foundations Benchmark v5.0.0 — the industry-standard hardening guide for Azure environments, published by the Center for Internet Security (CIS) .
It has one optional pip dependency ( msal ) for automated evaluation of check 5.1.1. All other checks require only Python 3.10+ and the Azure CLI — no pip installs needed. Results are saved as checkpoints after each subscription completes, so a failed or interrupted run can be resumed without re-running completed work. Output is a self-contained HTML report with filtering, compliance scoring, charts, and per-finding remediation guidance. JSON and CSV exports are generated alongside the HTML automatically.
Key Vault data plane: Controls 8.3.1–8.3.4, 8.3.9, and 8.3.11 enumerate individual keys, secrets, and certificates. This requires data plane access in addition to Reader. For RBAC-enabled vaults assign Key Vault Reader ; for access-policy vaults, add the runner account to the vault's access policy. Without this, affected checks return ERROR with a clear explanation and remediation hint in the report — compliance is unknown, not assumed clean.
The tool has one runtime dependency — msal — used only for check 5.1.1 (Security defaults). Install it with: If msal is not installed, check 5.1.1 will still run via the az CLI path, but will return ERROR because the az CLI app cannot acquire Policy.Read.All . All other checks have no pip dependencies. 4. Practical Deployment, Analysis & Case Studies Dev dependencies ( black , flake8 , mypy , and optionally rich ) are listed in requirements-dev.txt : The report opens automatically in your browser when the audit finishes. The script will also automatically install the resource-graph extension if missing, enumerate all enabled subscriptions, run all checks, and save the report files to a reports/ subdirectory.
New to Python or the Azure CLI? Follow these steps to get the tool running on your machine. Go to https://www.python.org/downloads/ and download the latest Python 3.10+ installer for your OS. A browser window will open for you to sign in. The account you use needs at minimum Reader and Security Reader on the subscriptions you want to audit.
The tool will enumerate all your enabled subscriptions, run all checks, and open the HTML report in your browser automatically when done. Reports are saved to a reports/ subfolder. cis_audit.toml is loaded automatically from the same directory as cis_azure_audit.py . All settings are optional — omit any line to keep the built-in default. The path can be overridden with the CIS_AUDIT_CONFIG environment variable.
Security note: Never store a real client_secret value in cis_audit.toml — it could be accidentally committed to source control. Use the CIS_GRAPH_CLIENT_SECRET environment variable instead, or a secrets manager such as Azure Key Vault or GitHub Actions secrets. The audit adapts worker count automatically when Azure API throttling (HTTP 429) is detected: Before any per-subscription work begins, Kusto queries fetch all relevant resources across the entire tenant in a single round trip: Before the audit begins, the tool checks whether the runner account holds the required roles on every subscription. On large tenants this runs in parallel (up to 8 subscriptions at once) so the check completes in seconds rather than minutes.
After each subscription completes, results are written to cis_checkpoints/
Subscriptions run concurrently via Python's concurrent.futures executor. The default is 3 parallel workers (configurable in cis_audit.toml or via --parallel ). The Resource Graph prefetch always runs once before the parallel loop begins. ERROR vs INFO distinction: ERROR means "the control applies, but the audit couldn't evaluate it" — flag it for follow-up. INFO means "the control genuinely doesn't apply here" — for example, an ADLS Gen2 storage account has no blob/file service by design, so the blob checks simply don't apply. There is nothing to fix.
Loads all existing checkpoints and regenerates the HTML, JSON, and CSV — no Azure API calls are made. Useful after: Section 5 tenant-level identity checks (5.1.1, 5.1.2, 5.1.3, 5.4, 5.14, 5.15, 5.16) are re-run at report time because they are not stored in subscription checkpoints. Live Graph API results (5.4, 5.14, 5.15, 5.16) will reflect the current state of your tenant. MANUAL findings (5.1.3) will always appear. If Graph is unreachable, those checks are skipped with a warning and the report is still generated from checkpoints.
Results loaded from checkpoints are automatically reclassified using the current tool logic: FeatureNotSupportedForAccount storage errors recorded as ERROR in older checkpoints are shown as INFO, Key Vault permission errors are rewritten with clean actionable messages, and any section name corrections introduced in newer versions of the tool are applied on load. Use --output to set a custom filename, or --output-dir to redirect all output to a different directory. The history file is always written to the same directory as the HTML report.
History note: cis_run_history.json is only updated on full-tenant runs (no --subscription filter). Per-subscription runs do not contribute to the trend chart so the baseline stays consistent. Note: --report-only does not update the history file — it regenerates the report from existing checkpoints but is not a new measurement.
Some findings are intentional — for example, a jump host that deliberately has RDP open, or a DDoS plan that is not required for a given environment. Without a way to acknowledge these, every report contains the same known findings and reviewers stop trusting the output. 5. Performance Evaluation & Extended Technical Observations A suppressions.toml file next to cis_azure_audit.py lets you mark specific findings as accepted risks. Suppressed findings still appear in the report in grey with your justification visible — they are never hidden. The compliance score excludes them (like INFO and MANUAL).
Suppressions are applied at report generation time only . Checkpoints always store the raw FAIL, so removing a suppression and running --report-only immediately reinstates the finding. Not covered: 2.1.3 (encrypted traffic between worker nodes — Manual), 2.1.4 (Entra ID sync — Manual), 2.1.5 (Unity Catalog — Manual), 2.1.6 (personal access token restrictions — Manual). These require Databricks workspace-internal configuration that cannot be audited from the Azure control plane.
Sections 3 and 4 of the CIS Azure Foundations Benchmark v5.0.0 are largely reference sections — most Compute and Database controls have been relocated to the CIS Microsoft Azure Compute Services Benchmark and CIS Microsoft Azure Database Services Benchmark respectively. Only 3.1.1 (Virtual Machines) remains in the Foundations Benchmark as an auditable control.
5.1.1 — The az CLI app cannot acquire Policy.Read.All . Without [graph_auth] configured, this check returns ERROR with instructions to set it up. With [graph_auth] configured, MSAL is used (browser popup once for user accounts; client credentials for SPs). Returns INFO when security defaults are disabled but Conditional Access policies are present (CA is the stronger control and disabling security defaults is intentional in that case).
5.1.2 — Uses the Graph beta authentication methods registration report ( /beta/reports/authenticationMethods/userRegistrationDetails ). Any user without isMfaRegistered = true is reported as non-compliant.
5.1.3 — Manual. The "Allow users to remember MFA on trusted devices" setting lives in the deprecated Per-user MFA portal, which has no stable Graph API surface. API permissions → Add → Microsoft Graph → Delegated → Policy.Read.All → Grant admin consent . For service principal / CI: also add the Application permission Policy.Read.All and consent it; set the secret via the CIS_GRAPH_CLIENT_SECRET environment variable (recommended — avoids storing credentials in cis_audit.toml ), or set client_secret in [graph_auth] for local use only.
Run the tool — a browser window opens once for interactive sign-in; subsequent runs use a token cached at ~/.cis_audit/msal_token_cache.json . Device code flow is not used. MSAL is configured to use the authorization code flow with PKCE (interactive browser) in user mode, in line with CIS 5.2.3.
Key Vault data-plane checks (8.3.1–8.3.4, 8.3.9, 8.3.11): these require data-plane access beyond subscription Reader. If the runner cannot reach the vault (firewall, private endpoint) or lacks a Key Vault data-plane role / access policy, the check returns ERROR with an actionable message explaining exactly what is missing — compliance is unknown, not assumed clean. ADLS Gen2 / Data Lake storage accounts do not have a blob or file service — the 9.1.x and 9.2.x checks return INFO for these account types (not ERROR), because the controls genuinely do not apply.
The test suite uses Python's built-in unittest — no extra packages required. All tests mock Azure CLI calls so no real Azure connection is needed. Add --exit-code to make the tool exit with code 2 when any FAIL or ERROR results are found. This lets Azure DevOps, GitHub Actions, and similar systems fail the build on compliance regressions: Each file contains the full result set for that subscription, a UTC timestamp, and a completion status. Delete the cis_checkpoints/ folder or use --fresh to discard all checkpoints. Use --report-only to regenerate the HTML report from existing checkpoints without running any checks.
When checkpoints are loaded, results are automatically reclassified using the current tool logic. This means upgrading the tool and running --report-only will apply corrected error classifications, message improvements, and control-metadata fixes from the new version to your existing checkpoint data — in most cases no re-audit is required. Key Vault data plane access — listing keys, secrets, and certificates requires data plane permissions in addition to subscription Reader. Assign Key Vault Reader (RBAC vaults) or add the runner account to the vault's access policy (non-RBAC vaults). Without this, affected checks return ERROR with an explanatory message. The report clearly distinguishes this from a clean result — compliance is unknown, not assumed clean.
Check 5.1.1 returns ERROR (Policy.Read.All) The az CLI app cannot acquire Policy.Read.All . This is a Microsoft-imposed limitation — the az CLI app ( 04b07795-... ) is not pre-authorized for that scope. Configure [graph_auth] in cis_audit.toml with your own app registration to resolve it (see "Check 5.1.1 setup" above). Graph API for identity checks — controls 5.4, 5.14, 5.15, and 5.16 call the Graph API via az rest . If the required Graph permissions have not been consented for the Azure CLI app, these will return ERROR. Test with: Conditional Access policies (5.2.1, 5.2.3) — not checked by this tool; they require review in the Entra ID portal. Control 5.2.2 is included in the Section 5 table above as a Manual output.
Large tenants — Resource Graph handles bulk data efficiently, and the permission preflight runs subscriptions in parallel. The main bottleneck at scale is per-subscription CLI calls. Use --parallel 5 or higher, or tune via cis_audit.toml . Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/ChatGPT • https://en.wikipedia.org/wiki/OpenAI • https://en.wikipedia.org/wiki/Grok%20%28chatbot%29 • https://github.com/adrian207/Audit-Azure • https://learn.microsoft.com/en-us/security/benchmark/azure/security-control-secure-configuration • https://github.com/vegazbabz/CIS-Azure-Benchmark-Audit-Tool
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Azure Security Benchmark Assessment Tool In Python.
[*] Metasploit Scan Running on Target Subnet for Azure Security Benchmark Assessment Tool In Python... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |