Complete Technical Paper Content — Badusb Attack Mitigation Tool For Operating Systems
Overview & System Context
Badusb Attack Mitigation Tool For Operating Systems: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~4537 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background A penetration test, colloquially known as a pentest, is an authorized simulated cyberattack on a computer system, performed live to evaluate the security of the system. The test is performed to identify weaknesses (or vulnerabilities), including the potential for unauthorized parties to gain access to the system's features and data, as well as strengths, enabling a full risk assessment to be completed. The process typically identifies the target systems and a particular goal, then reviews available information and undertakes various means to attain that goal. A penetration test target may be a white box (about which background and system information are provided in advance to the tester) or a black box (about which only basic information other than the company name is provided). A gray box penetration test is a combination of the two (where limited knowledge of the target is shared with the auditor). There are different types of penetration testing, depending on the goal of the organization which include: Network (external and internal), Wireless, Web Application, Social Engineering, and Remediation Verification. A penetration test can help identify a system's vulnerabilities to attack and estimate how vulnerable it is. The UK National Cyber Security Center describes penetration testing as: "A method for gaining assurance in the security of an IT system by attempting to breach some or all of that system's security, using the same tools and techniques as an adversary might." Penetration tests are a component of a full security audit. For example, the Payment Card Industry Data Security Standard requires penetration testing on a regular schedule, and after system changes. Penetration testing also can support risk assessments as outlined in the NIST Risk Management Framework SP 800-53. Several standard frameworks and methodologies exist for conducting penetration tests. These include the Open Source Security Testing Methodology Manual (OSSTMM), the Penetration Testing Execution Standard (PTES), the NIST Special Publication 800-115, the Information System Security Assessment Framework (ISSAF) and the OWASP Testing Guide. CREST, a not for profit professional body for the technical cyber security industry, provides its CREST Defensible Penetration Test standard that provides the industry with guidance for commercially reasonable assurance activity when carrying out penetration tests. Since 2017 the terms Penetration Testing as a Service (PTaaS) has become popular. This involves using a platform to invoke a test as an alternative to using consultants.
Find an exploitable vulnerability. Design an attack around it. Test the attack. Seize a line in use. Enter the attack. Exploit the entry for information recovery. Over time, Anderson's description of general computer penetration steps helped guide many other security experts, who relied on this technique to assess time-sharing computer system security. In the following years, computer penetration as a tool for security assessment became more refined and sophisticated. In the early 1980s, the journalist William Broad briefly summarized the ongoing efforts of tiger teams to assess system security. As Broad reported, the DoD-sponsored report by Willis Ware "...showed how spies could actively penetrate computers, steal or copy electronic files and subvert the devices that normally guard top-secret information. The study touched off more than a decade of quiet activity by elite groups of computer scientists working for the Government who tried to break into sensitive computers. They succeeded in every attempt." While these various studies may have suggested that computer security in the U.S. remained a major problem, the scholar Edward Hunt has more recently made a broader point about the extensive study of computer penetration as a security tool. Hunt suggests in a recent paper on the history of penetration testing that the defense establishment ultimately "...created many of the tools used in modern day cyberwarfare," as it carefully defined and researched the many ways that computer penetrators could hack into targeted systems.
BlackArch based on Arch Linux BackBox based on Ubuntu Kali Linux (replaced BackTrack December 2012) based on Debian Parrot Security OS based on Debian Pentoo based on Gentoo WHAX based on Slackware Many other specialized operating systems facilitate penetration testing—each more or less dedicated to a specific field of penetration testing. A number of Linux distributions include known OS and application vulnerabilities, and can be deployed as targets to practice against. Such systems help new security professionals try the latest security tools in a lab environment. Examples include Damn Vulnerable Linux (DVL), the OWASP Web Testing Environment (WTW), and Metasploitable.
Proxmark3 — multi-purpose hardware tool for radio-frequency identification (RFID) security analysis. BadUSB — toolset for exploiting vulnerabilities in USB devices to inject malicious keystrokes or payloads. Flipper Zero — portable, open-source multi-functional device pentesting wireless protocols such as Sub-GHz, RFID, NFC, Infrared and Bluetooth. Raspberry Pi — a compact, versatile single-board computer commonly used in penetration testing for tasks like network reconnaissance and exploitation. SDR (Software-defined Radio)— versatile tool for analyzing and attacking radio communications and protocols, including intercepting, emulating, decoding, and transmitting signals. ChipWhisperer — specialized hardware tool for side-channel attacks, allowing analysis of cryptographic implementations and vulnerabilities through power consumption or electromagnetic emissions.
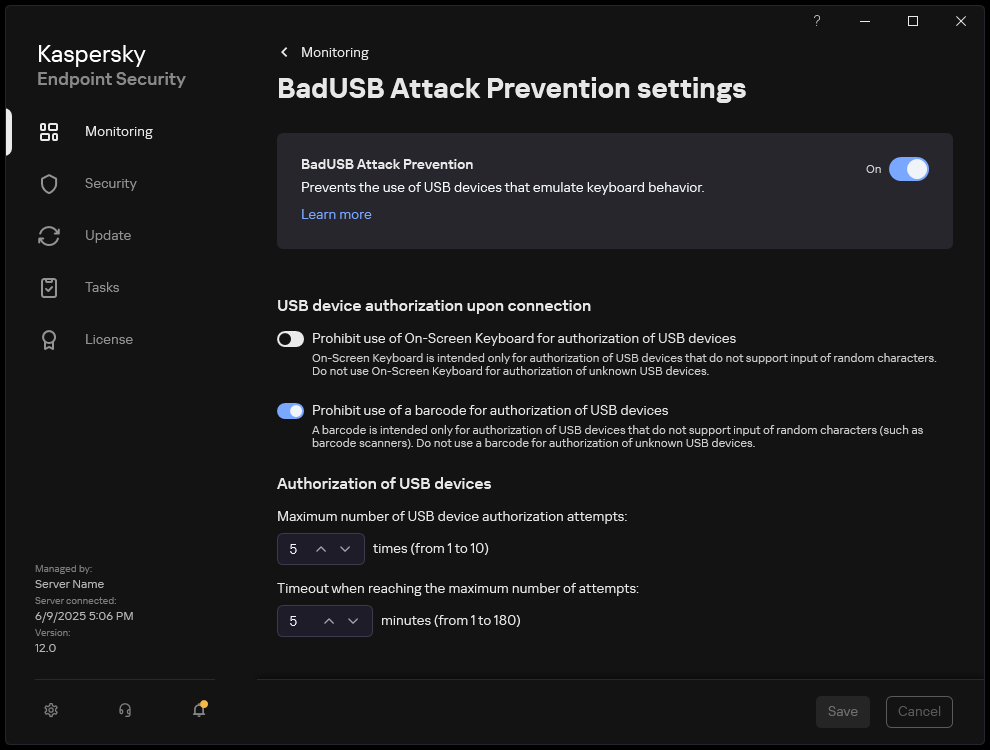
Figure 1: Enabling and disabling BadUSB Attack Prevention Reconnaissance: The act of gathering important information on a target system. This information can be used to better attack the target. For example, open source search engines can be used to find data that can be used in a social engineering attack. Scanning: Uses technical tools to further the attacker's knowledge of the system. For example, Nmap can be used to scan for open ports. Gaining access: Using the data gathered in the reconnaissance and scanning phases, the attacker can use a payload to exploit the targeted system. For example, Metasploit can be used to automate attacks on known vulnerabilities.
Once an attacker has exploited one vulnerability they may gain access to other machines so the process repeats i.e. they look for new vulnerabilities and attempt to exploit them. This process is referred to as pivoting. Maintaining access: Maintaining access requires taking the steps involved in being able to be persistently within the target environment in order to gather as much data as possible. Covering tracks: The attacker must clear any trace of compromising the victim system, any type of data gathered, log events, in order to remain anonymous. Reporting: Vulnerabilities are classified via risk matrix and documented in a report which contains executive summary, vulnerability description, and recommendations for remediation.
Remediation & Re-testing: Once the target organization assesses the penetration test report and remediates items based on their internal risk appetite, a re-test of those vulnerabilities is performed in order to confirm remediation was successful, and a cut down re-test report is provided showing the results. Red team exercises are an extension of penetration testing in which a dedicated adversarial team (the red team) simulates a sophisticated, sustained attack against an organisation's people, processes, and technology — without the defending team (the blue team) being fully aware of the timing or scope. This differs from a standard penetration test in that it focuses on testing the organisation's detection and response capabilities, not just its technical vulnerabilities. Purple team exercises involve the red and blue teams working collaboratively, such as by sharing information in real time.
BadUSB controls for engineering teams have a hard constraint: engineers plug in more hardware than anyone — keyboards, docks, debuggers, dev boards, SDRs — so a blanket USB block breaks real work and gets disabled within a week. The controls that survive are allowlist-based: permit known-good devices by hardware ID, block new unknown HID devices, and alert on the rest. This guide ships the device-control architecture (USBGuard on Linux, device-installation policy on Windows) plus the detection that catches a malicious device without stopping legitimate engineering.
A BadUSB device — a USB Rubber Ducky , a malicious cable, or a Flipper Zero in BadUSB mode — is a hardware addition: MITRE ATT&CK T1200 — Hardware Additions , with injected commands mapping to T1059.001 . Figure 2: O que é BadUSB e como se proteger contra esse tipo de ataque? | Device ... BadUSB abuses the implicit trust the operating system grants to a USB device’s declared class. A device can claim to be a keyboard and inject keystrokes, a network adapter and reroute traffic, or storage — and the OS believes it. The USB Rubber Ducky detection patterns post covers the behavioral detection; this post is about the controls that prevent it at scale.
The engineering-team challenge is that the obvious control — block USB — is a non-starter. Developers need keyboards, KVMs, docks, JTAG/SWD debuggers, dev boards, and SDRs. A policy that blocks them all gets exception-requested into uselessness. The answer is precision: allow the known, block the novel. The pattern that works for engineers: allowlist what they use, block new HID keyboards by default, and let application allowlisting backstop the payload — so even a permitted-looking device cannot run an arbitrary command.
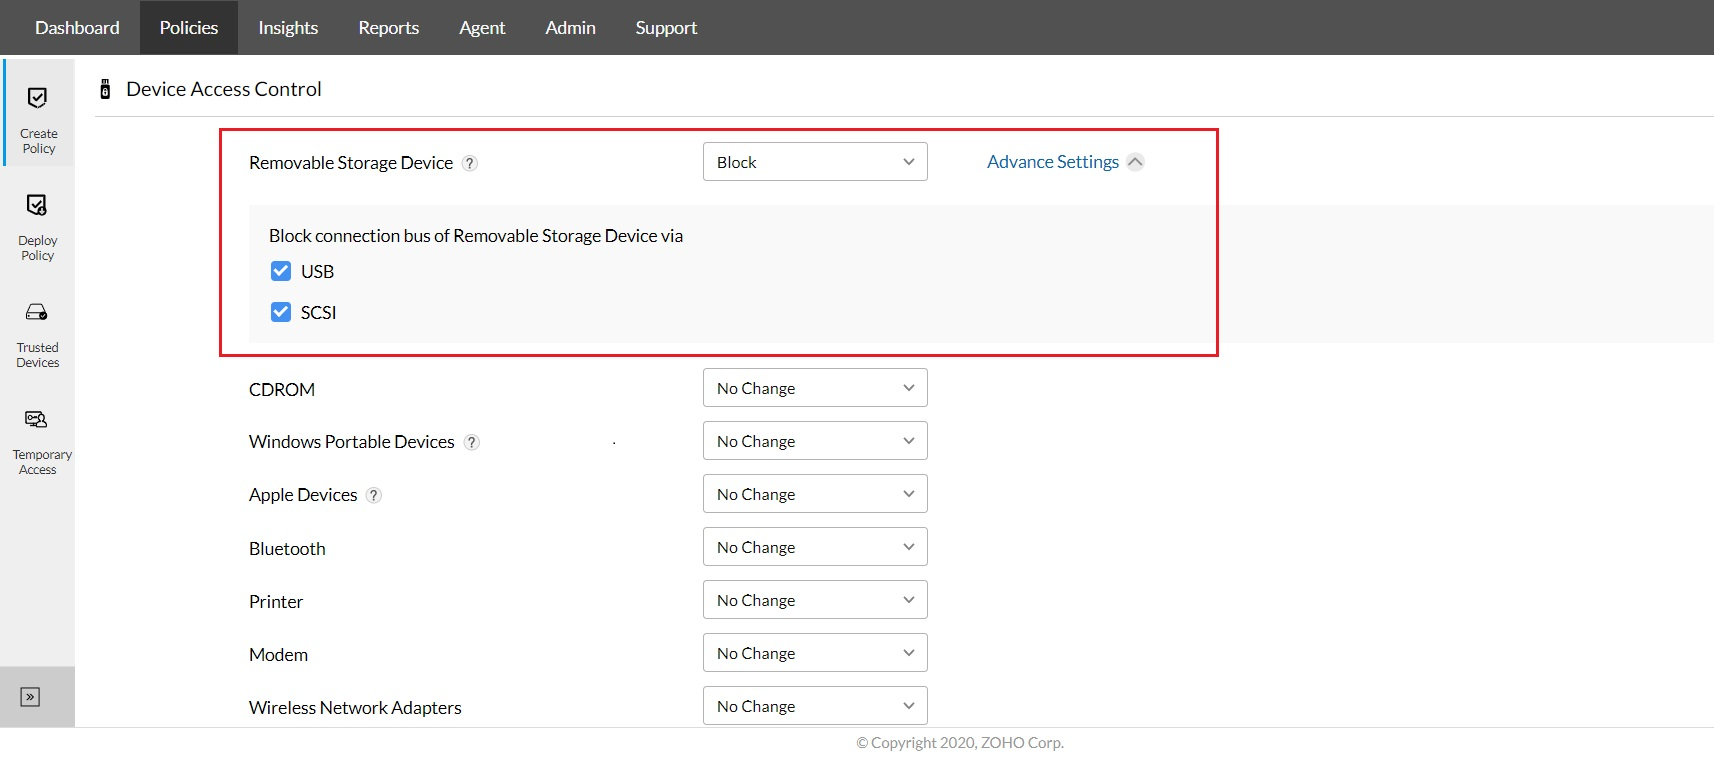
On Linux, USBGuard authorizes devices by attribute. Start from your current, trusted devices and block anything new by default: Figure 3: What is BadUSB | How to Protect Against BadUSB Attacks - ManageEngine ... On Windows, use device-installation restrictions (Group Policy / Intune) to allow known device IDs and block new HID classes, and pair it with WDAC so an injected command cannot run an unsigned payload. The detection layer then alerts on anything that slips the policy.
BadUSB discussion defaults to keyboards, and the keyboard is one of several classes a device can claim. Your allowlist and your alerting need to know the others. 2. System Architecture & Core Working Principles The network-adapter case is the one most often missed, and it is worse than the keyboard. A device that declares itself a USB Ethernet adapter typically becomes an active network interface the moment it is attached — commonly a preferred one, because operating systems tend to favour a freshly connected wired link. The device then answers DHCP, naming itself as gateway and DNS server, and traffic from the host starts flowing through hardware the attacker controls. Credential material follows, because a great deal of software authenticates to network resources without being asked.
Alert on new network interfaces appearing over USB , and treat a device presenting a CDC class on an engineering laptop with the same seriousness as a new keyboard. On the control side, blocking class 02 / 0A except for the specific docks and adapters your organisation issues is usually easy, because that list is genuinely short. A USB-C port is frequently also a Thunderbolt port, and Thunderbolt carries PCIe. That means a malicious device can request direct memory access to the host — reading and writing system memory without going through the operating system at all.
This is a different category from everything else in this guide. Device-class allowlisting does not address it, because the attack does not need to impersonate a device class. Application allowlisting does not address it, because no application runs. The mitigations are firmware and platform features: Verify which of your fleet actually has Kernel DMA Protection enabled rather than assuming it. This is one of the few controls where hardware age genuinely determines your exposure, and the answer is usually a straightforward inventory query.
The Windows device-installation restrictions are the right control and their evaluation order surprises people. By default, prevent policies take precedence over allow policies , across all matching criteria. So a configuration that blocks a broad device setup class and separately allows a specific device ID within that class results in the device being blocked — the allow entry is not consulted, and nothing reports an error. The administrator concludes the allowlist is broken.
Windows added an option to apply a layered order of evaluation , which makes the more specific match win — allowing the intuitive pattern of “block this class, permit these specific devices inside it.” Enable it deliberately, and know that your policy behaves differently depending on whether it is on. USBGuard is the correct Linux control and it has failure modes worth knowing before you deploy it fleet-wide.
You can lock yourself out. A default-deny policy that does not permit the machine’s own keyboard leaves you at a login prompt that will not accept input. Always generate the initial policy from the currently attached devices, always confirm the keyboard and any KVM are in it, and always test on one machine you can physically recover before pushing to a fleet. Internal devices are USB too. Laptop webcams, fingerprint readers, Bluetooth radios, and internal card readers frequently sit on the USB bus. A default-deny policy that only considered external peripherals will disable hardware users assume is part of the machine, and the reports will arrive as “the camera broke” rather than as a policy problem.
Ordering matters and the daemon must start early. Rules are evaluated in order, so a broad block placed above a specific allow wins. And the daemon needs to be running before a user can reach a login prompt, or the policy is not applied to devices present at boot. Screen-lock integration is worth configuring. USBGuard can be configured to refuse newly attached devices while the screen is locked, which directly addresses the walk-past scenario while leaving normal working behaviour untouched. It is the highest-value setting in the whole configuration and it is not on by default.
Every control in this guide depends on an exception process, and a bad one guarantees the policy gets hollowed out. Design it deliberately: 3. Software Implementation, Frameworks & Protocols The measure of this control is not how much it blocks. It is whether it is still enforced in a year — and that depends almost entirely on how the exception path feels to the people subject to it.
One policy across the whole estate is why this control usually fails. Engineering laptops and reception kiosks have nothing in common, and a policy strict enough for one is unworkable on the other while a policy loose enough for the other is pointless on the first. Fixed-function endpoints — kiosks, reception machines, shared terminals, point-of-sale, digital signage, and servers. These legitimately never receive new hardware. Default-deny with a frozen allowlist, no new HID devices at all, physical port blockers where the machine is publicly accessible, and Thunderbolt disabled in firmware. Support cost is close to zero because nothing ever changes, and these are the most exposed machines you own — publicly reachable, frequently unattended, and rarely audited.
Standard corporate endpoints — most laptops and desktops. Allowlist by device class rather than by individual device, so mice, keyboards, headsets, and issued docks work without a ticket. Block network-adapter classes except for issued docks, refuse new devices while the screen is locked, and alert on anything outside the allowlist. This is where the population is, so the policy has to be quiet.
Engineering endpoints — the hard case this guide is named for. A broader allowlist covering debuggers, dev boards, SDRs, and programmers, granted by role rather than per request. Keep the detection layer at full strength here even though enforcement is looser, because these are the machines with the most credentials and the most source-code access. And keep Kernel DMA Protection on: engineers use Thunderbolt docks constantly, which is exactly the exposure.
The tiering does two things. It makes the strict settings deployable, because they land only where nothing breaks. And it makes the loose settings defensible, because the exception is scoped to a population with a stated reason rather than being the de facto standard everywhere. Decide where a machine sits at provisioning time , from its role, and re-evaluate when the role changes. A tier assigned per-request drifts to the loosest setting within a year, which is the same failure as having no tiers at all.
BadUSB controls for engineering teams work when they are allowlist-based: permit the hardware engineers actually use, block new unknown HID devices, layer application allowlisting for the payload, and alert on the novel. Precision is what keeps the control deployed. Continue with USB Rubber Ducky detection patterns and Flipper Zero NFC risk , or browse the full Hardware Security pillar.
Disclosure: Some links below are affiliate links. If you buy through them, darkpwn may earn a commission at no extra cost to you. We only recommend training and tools we actually use in our own lab, and affiliate links never influence editorial coverage. BadUSB is a class of attack where a USB device's firmware makes it impersonate a trusted device class — most commonly a keyboard (HID) that injects keystrokes, but also network adapters or storage. Because the OS trusts the device class, antivirus and USB mass-storage policy do not stop it. A USB Rubber Ducky and a malicious cable are examples.
Use device control that allowlists known-good devices by hardware ID rather than blanket-blocking USB, which breaks legitimate engineering work. USBGuard on Linux and Windows device-installation policy (or WDAC) let you permit existing keyboards, docks, and debuggers while blocking new, unknown HID devices and alerting on them. No. A BadUSB device injects keystrokes or presents a trusted device class; it runs no malicious file of its own, so signature antivirus has nothing to scan. The controls are device allowlisting plus application allowlisting to stop whatever the keystrokes try to run.
USBGuard is a Linux framework that enforces a device-authorization policy: you define allowed USB devices by attributes (vendor, product, serial, interface class) and it blocks devices that do not match. It is the Linux counterpart to Windows device-installation restrictions for BadUSB control. USB Rubber Ducky detection patterns for blue teams — spotting HID injection with Sigma, USB device control and AppLocker hardening, and MITRE ATT&CK mapping.
4. Practical Deployment, Analysis & Case Studies Evil twin access point defenses for blue teams — detect rogue APs with a WIDS, why 802.1X server-cert validation and WPA3 matter, plus a captive-portal DNS signal. A WiFi deauthentication detection guide — spot deauth floods with a WIDS, why 802.11w PMF and WPA3 help (and where they fall short, CVE-2023-21061), plus hardening.
The ubiquitous USB port, a gateway for productivity, has become a critical attack vector for cyber threats. BadUSB attacks leverage seemingly innocent devices like flash drives and charging cables to impersonate human interface devices (HIDs), executing pre-programmed keystrokes to compromise systems in seconds. This article provides a comprehensive technical guide to hardening your endpoints against these insidious hardware-based attacks.
The first line of defense is endpoint protection software capable of enforcing device control policies. Checkpoint Harmony uses a feature called Port Protection to manage this. Policy Objective: To block any unauthorized external keyboard from being recognized by the operating system.
Implementation
This is configured within the Harmony Endpoint management console. Administrators create a new security policy under the ‘Port Protection’ section, specifically denying the ‘Keyboard’ device class. The policy can be set to block all or allow only specific, company-approved devices based on their hardware ID. Why it Works: By preventing the OS from loading the driver for an unauthorized HID, the malicious device is rendered inert. It cannot execute its keystroke injection payload because the system never acknowledges its existence.
Implementation Synonym
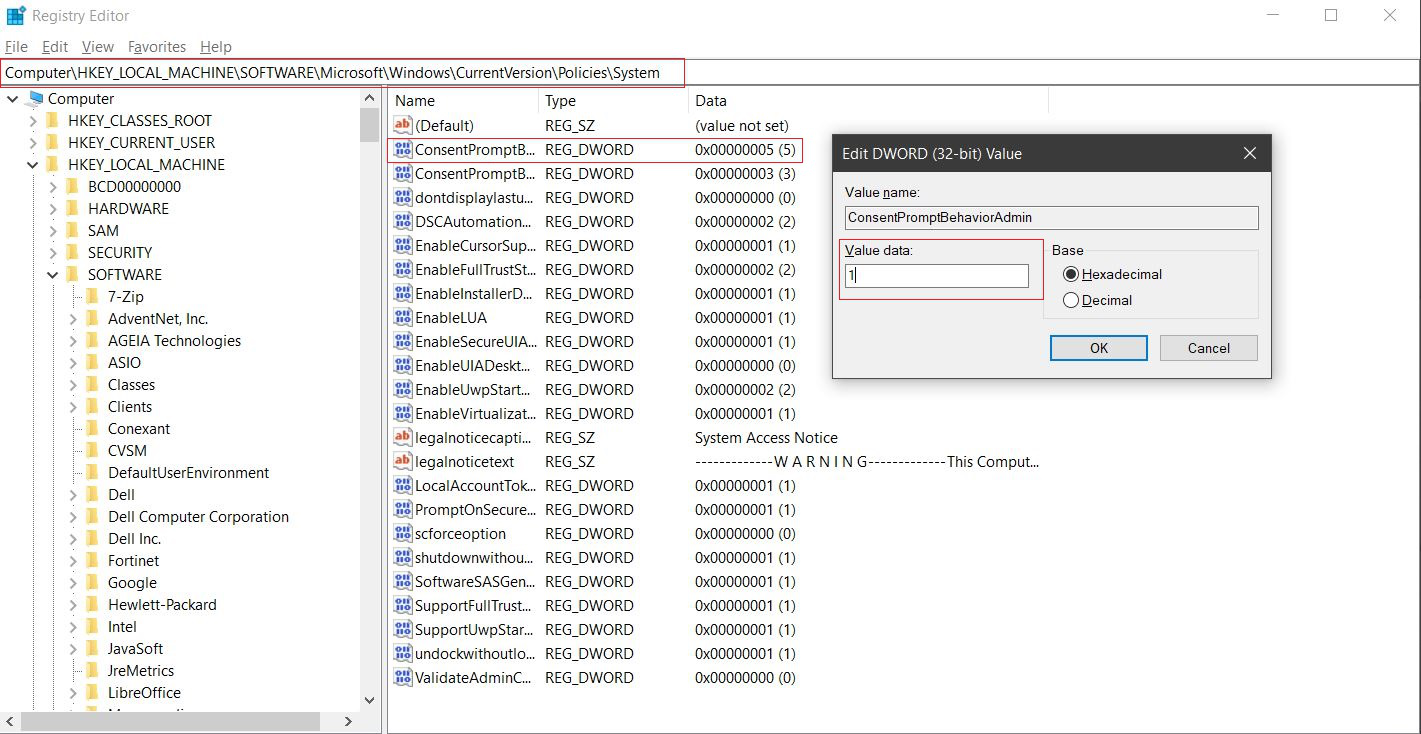
Attackers often use the Windows Login screen’s accessibility features (like Utilman) to launch a command prompt and gain system access. Hardening the registry prevents this. Windows Group Policy for Enhanced Login Security (Pro/Enterprise) For enterprise environments, Group Policy provides a more centralized and manageable method for login screen hardening.
Implementation Meaning
A deny-all policy can be disruptive. A more refined approach is to whitelist specific, authorized devices by their hardware ID. Use PowerShell to audit currently connected HID devices and monitor for potential threats. Step-by-Step Guide: Run this command in an administrative PowerShell window. It will list all active Human Interface Devices along with their instance IDs. Regularly auditing this list can help you establish a baseline of normal devices and identify unknown or suspicious hardware that has been connected to the system.
Implementation Science
The BadUSB threat extends to mobile devices. Modern smartphones include features to mitigate this risk. Configuration: On supported Samsung devices, navigate to Settings -> Security and Privacy -> More security settings -> Auto Blocker. Step-by-Step Guide: Enable the Auto Blocker feature. Among other protections, this setting blocks commands from external USB devices that are attempting to control the phone or execute unauthorized software, providing a crucial layer of defense when using public charging stations.
Implementation Specialist
For ultra-secure environments handling classified information, the most robust mitigation is physical.
Implementation Definition
Replace all USB keyboards with older PS/2 connection keyboards. Why it Works: The PS/2 port is a purely legacy input interface. It does not support the USB protocol and is therefore completely immune to any form of USB-based device spoofing or BadUSB attack. This creates an air-gap style defense for the primary input method. 5. Performance Evaluation & Extended Technical Observations The analysis underscores a shift in defensive strategy from purely digital to physical-digital hybrid warfare. Relying solely on software-based detection is insufficient against attacks that impersonate legitimate hardware. A multi-layered approach combining endpoint device control, OS hardening, user education on physical threats (“don’t plug that in”), and, for high-security needs, legacy hardware is the only effective defense. This moves the needle from simply detecting a breach to preventing its initial execution vector entirely.
Implementation Manager
The future of hardware-borne threats will evolve beyond simple keystroke injection. We will see the emergence of “smart cable” attacks that are undetectable by current device control policies, as they will present as genuine charging cables while passively exfiltrating data or injecting payloads via powerline communication. Furthermore, AI-generated social engineering tactics will be used to increase the success rate of baiting attacks, making found malicious devices even more convincing.
Implementation Consultant
Defense will require AI-powered behavioral analysis on endpoints to detect anomalous peripheral communication patterns, not just static device IDs, heralding a new era of intelligent device control. Reported By: Nir Roitman – Hackers Feeds Extra Hub: Undercode MoN Basic Verification: Pass I We do not sell your personal data. If you wish to exercise your rights under applicable privacy laws, please visit our Do Not Sell My Personal Information page.
Implementation Intentions
It is important to note that there is no perfect mitigation for a BadUSB attack. However, in the case where we want to open the door of a vault remotely, there are several mitigation techniques that can be implemented to enhance security. Two such techniques are Multi-Factor Authentication (MFA) and TLS encryption with a passphrase-protected key. We can implement MFA so that when the badUSB triggers the connection, the user receives a 6-digit password on his phone (since we are separated from the internet, we use the LCD of the vault) that he will input to successfully open the door. More information can be found in the fix-server-mfa.py file.
Implementation Engineers
Note: The specific factors used in the MFA setup can vary but typically involve a combination of something the user knows (such as a password or PIN), something the user has (such as a smart card or token), or something the user is (biometric attributes other than fingerprints). Important: Please note that the fix-server-mfa.py implementation is designed for Python 2.7. If you are using a different version of Python, ensure compatibility or consider adapting the code accordingly.
Another good mitigation found for this attack is to use Transport Layer Security (TLS) encryption with passphrase-protected keys. This adds an additional layer of security by encrypting the TLS keys used for communication with the Raspberry Pi server. To implement this mitigation, follow the instructions provided in the Prerequisites folder and refer to the specific guidelines mentioned in the README file.
In this post, I break down how the BadUSB attack works—starting from its origin at Black Hat 2014 to a hands-on implementation using an Arduino UNO and custom HID firmware. The attack exploits the USB protocol's lack of strict device type enforcement, allowing a USB stick to masquerade as a keyboard and inject malicious commands without user interaction. The write-up covers: * How USB device firmware can be repurposed for attacks * Step-by-step guide to converting an Arduino UNO into a BadUSB The BadUSB attack exploits fundamental weaknesses in the USB protocol, specifically the lack of strict enforcement regarding device types and behaviors. Originally demonstrated at Black Hat 2014, the attack involves reprogramming the firmware of USB devices, such as flash drives, to impersonate other types of USB peripherals—most notably keyboards. By masquerading as a Human Interface Device (HID), the compromised USB device can inject arbitrary keystrokes and commands into a target system without requiring any user interaction. This capability allows attackers to execute a wide range of malicious activities, including launching command shells, downloading malware, or altering system configurations silently and rapidly. The described implementation uses an Arduino UNO microcontroller flashed with custom HID firmware to replicate this attack, illustrating how accessible and low-cost hardware can be weaponized for such purposes. The attack leverages the inherent trust operating systems place in USB devices and the absence of firmware validation or authentication mechanisms in USB protocols. Because the attack occurs at the hardware/firmware level, traditional antivirus or endpoint detection systems often fail to detect or prevent it. The write-up provides a detailed technical breakdown of the attack principles, firmware modification steps, and practical defense strategies, emphasizing the need for hardware-level security controls and user awareness.
For European organizations, the BadUSB attack presents a significant threat vector due to the widespread use of USB devices in corporate environments. The ability of an attacker to execute commands without user interaction can lead to rapid compromise of sensitive systems, data exfiltration, installation of persistent malware, or lateral movement within networks. Given the stealthy nature of the attack, it can bypass conventional security controls, leading to prolonged undetected breaches. Industries with high reliance on USB devices, such as manufacturing, finance, healthcare, and government agencies, are particularly vulnerable. The attack undermines confidentiality by enabling unauthorized data access and integrity by allowing unauthorized system modifications. Availability may also be impacted if critical systems are disrupted or ransomware is deployed via this vector. The threat is exacerbated by the difficulty in detecting malicious USB firmware and the common practice of employees using personal or unvetted USB devices, increasing the attack surface. Additionally, the attack can be leveraged in targeted espionage or sabotage campaigns against European critical infrastructure or strategic enterprises.
To mitigate BadUSB attacks effectively, European organizations should implement a multi-layered defense strategy beyond generic advice: 1) Enforce strict USB device usage policies, including whitelisting approved USB devices based on hardware IDs and cryptographic device authentication where possible. 2) Deploy endpoint security solutions capable of monitoring USB device behaviors, including HID emulation detection and anomalous input patterns. 3) Utilize hardware-based USB firewalls or data diodes that can block unauthorized device types or commands. 4) Educate employees about the risks of using unknown or untrusted USB devices and establish secure procedures for USB device provisioning and disposal. 5) Implement network segmentation to limit the impact of compromised endpoints and monitor for unusual command execution patterns indicative of BadUSB activity. 6) Where feasible, disable unused USB ports or use physical port blockers in sensitive environments. 7) Collaborate with hardware vendors to explore firmware signing and validation mechanisms to prevent unauthorized firmware modifications. 8) Regularly audit and update security policies to incorporate emerging threats related to USB device exploitation.
Crowdsource mitigation strategies, share intel context, and vote on the most helpful responses. Sign in to add your voice and help keep defenders ahead. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Penetration%20test • https://darkpwn.com/posts/badusb-controls-for-engineering-teams/ • https://undercodetesting.com/the-silent-threat-in-your-usb-port-how-to-stop-badusb-attacks-dead-in-their-tracks/ • https://cs394x.readthedocs.io/en/latest/BadUSB/Mitigations/README.html • https://radar.offseq.com/threat/badusb-attack-explained-from-principles-to-practic-51dd1a5d
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Badusb Attack Mitigation Tool For Operating Systems.
[*] Metasploit Scan Running on Target Subnet for Badusb Attack Mitigation Tool For Operating Systems... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |