Complete Technical Paper Content — Bgp Route Hijacking Detection And Alert Tool
Overview & System Context
Bgp Route Hijacking Detection And Alert Tool: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9527 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background BGP hijacking (sometimes referred to as prefix hijacking, route hijacking or IP hijacking) is the illegitimate takeover of groups of IP addresses by corrupting Internet routing tables maintained using the Border Gateway Protocol (BGP).
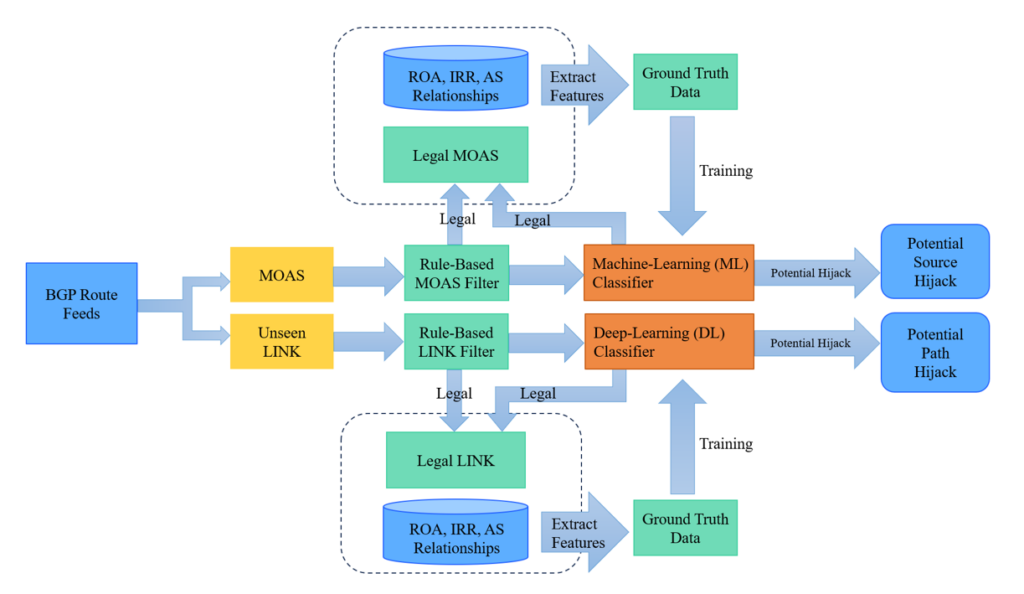
An AS announces that it originates a prefix that it does not actually originate. An AS announces a more specific prefix than what may be announced by the true originating AS. An AS announces that it can route traffic to the hijacked AS through a shorter route than is already available, regardless of whether the route exists. Common to these ways is their disruption of the normal network routing: packets end up being forwarded towards the wrong part of the network and then either enter an endless loop (and are discarded), or are found at the mercy of the offending AS. Typically ISPs filter BGP traffic, allowing BGP advertisements from their downstream networks to contain only valid IP space. However, a history of hijacking incidents shows this is not always the case. The Resource Public Key Infrastructure (RPKI) is designed to authenticate route origins via cryptographic certificate chains demonstrating address block range ownership but is not widely deployed yet. Once deployed, IP hijacking through errant issues at the origin (via accident or intent) should be detectable and filterable. IP hijacking is sometimes used by malicious users to obtain IP addresses for use in spamming or a distributed denial-of-service (DDoS) attack. When a router disseminates erroneous BGP routing information, whether intentionally or accidentally, it is defined by the Internet Engineering Task Force (IETF) in RFC 7908 as a "route leak." These leaks are characterized as "the dissemination of routing announcements beyond their intended scope. In other words, an announcement from one Autonomous System (AS) regarding a learned BGP route to another AS contravenes the intended policies of the recipient, the sender, and/or one of the ASes along the preceding AS path." Such leaks are made possible due to a long-standing "systemic vulnerability of the Border Gateway Protocol routing system." This article presents a detailed timeline of events in the history of computing from 2020 to the present. For narratives explaining the overall developments, see the history of computing. Significant events in computing include events relating directly or indirectly to software, hardware and wetware. Excluded (except in instances of significant functional overlap) are: events in general robotics events about uses of computational tools in biotechnology and similar fields (except for improvements to the underlying computational tools) as well as events in media-psychology except when those are directly linked to computational tools Currently excluded are: Figure 1: BGPWatch — A comprehensive platform for detecting and diagnosing ...
events in computer insecurity, hacking incidents, breaches/Internet conflicts, and malware if they are not also about milestones towards computer security events about quantum computing and communication economic events and events of new technology policy beyond standardization [Meta/Policy/Philosophy] – Thomas Metzinger, a German philosopher of cognitive science and applied ethics, called for a "global moratorium on synthetic phenomenology" which, "until 2050", precautionarily bans "all research that directly aims at or knowingly risks the emergence of artificial consciousness on post-biotic carrier systems" – and could be gradually refined. The paper does not describe mechanisms of global enforcement of such proposed regulations which do not consider biotic or semi-biotic systems and aims to limit suffering risks. [Type of database] – A new global food emissions database indicated that the current food systems are responsible for one third of the global anthropogenic greenhouse gas emissions. [Data usage] – In a static proprietary article that appeared in and was co-reviewed by a scientific journal, authenticated scientists analyzed data from multiple public databases to create a regional representation of levels of deforestation induced by nations' recent, largely unmodulated, trade-, production- and consumption-patterns.
A study found that carbon emissions from Bitcoin mining in China – where a majority of the proof-of-work algorithm that generates current economic value is computed, largely fueled by nonrenewable sources – had accelerated rapidly and would soon exceed total annual emissions of countries like Italy, interfering with climate change mitigation commitments. Neuralink revealed a male macaque with chips embedded on each side of its brain, playing a mind-controlled version of Pong. While similar technology has been demonstrated for decades, and wireless implants have existed for years, some observers noted that the organization increased the number of implanted electrodes that are read wirelessly. Scientists reviewed materials strategies for organic neuromorphic devices, suggesting that "their biocompatibility and mechanical conformability give them an advantage for creating adaptive biointerfaces, brain-machine interfaces, and biology-inspired prosthetics".
Researchers published the first in-depth study of Web browser tab interfaces. They found that many people struggle with tab overload and conducted surveys and interviews about people's tab use. Thereby they formalized pressures for closing tabs and for keeping tabs open. The authors then developed related UI design considerations which could enable better tools and changes to the code of Web browsers – like Firefox – that allow knowledge workers and other users to better manage their tabs. Operation of the U.S. Colonial Pipeline was interrupted by a ransomware cyber attack. A new record for the smallest single-chip system was achieved, occupying a total volume of less than 0.1 mm3.
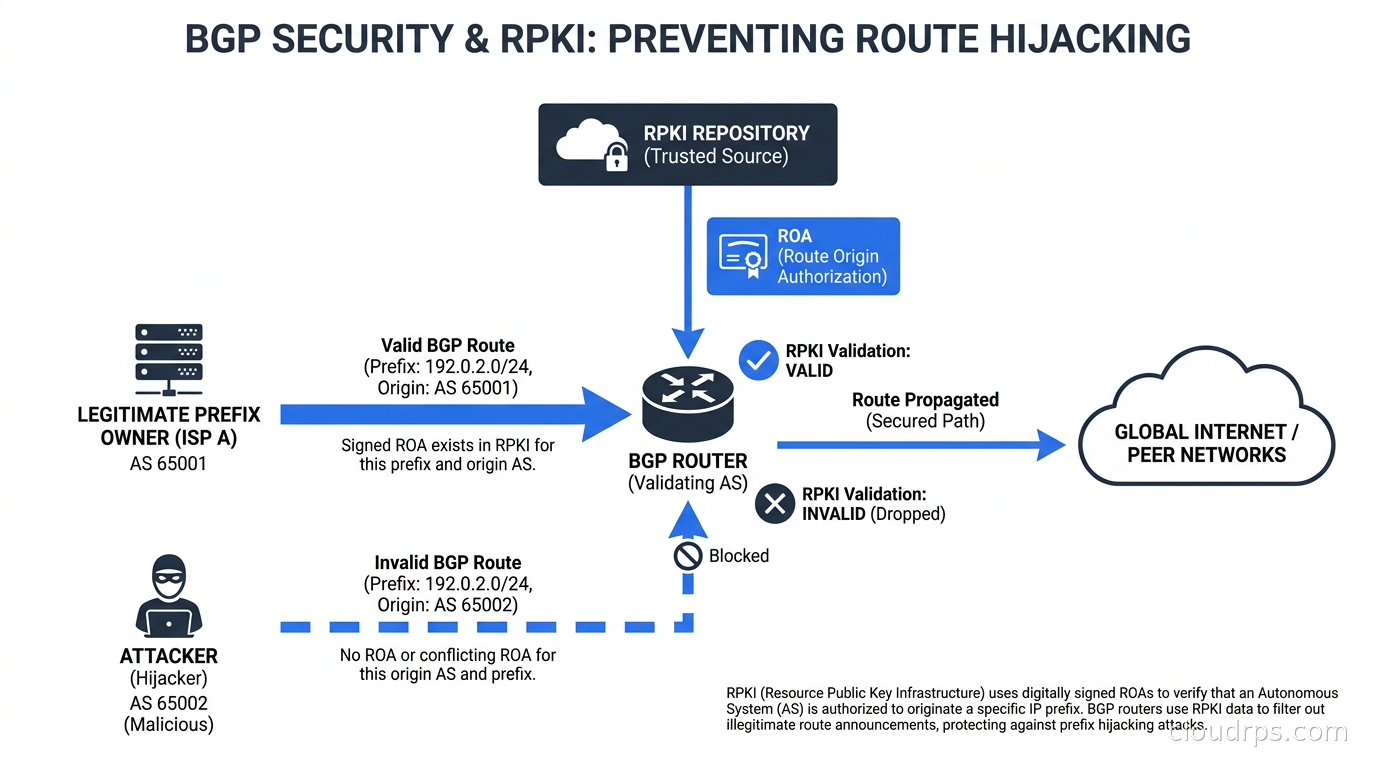
Figure 2: BGP Security and RPKI: Protecting Internet Routing Scientists demonstrated the first brain–computer interface that decodes neural signals for handwriting. The character output speed of a patient with a paralyzed hand was up to 90 characters per minute – more than double the previous record. Each letter is associated with a highly distinctive pattern of activity in the brain, making it relatively easy for the algorithm to distinguish them. Archivists initiated a rescue mission to secure enduring access to humanity's largest public library of scientific articles, Sci-Hub, due to the site's increased legal troubles, using Web and BitTorrent technologies. Google demonstrated a research project called LaMDA, an automatic language generation system designed to sustain a conversation with a person on any topic. The most comprehensive 3D map of the human brain – of a millionth of a brain and requiring 1.4 petabytes of storage space – was published. El Salvador passed the Bitcoin Law, making it the first country to give cryptocurrency and bitcoin a status of legal tender. The law was passed by the Legislative Assembly of El Salvador on June 8, 2021, giving the cryptocurrency bitcoin the status of legal tender within El Salvador after September 7, 2021. It was proposed by President Nayib Bukele. The text of the law states that "the purpose of this law is to regulate bitcoin as unrestricted legal tender with liberating power, unlimited in any transaction, and to any title that public or private natural or legal persons require carrying out". GitHub Copilot, a programmer assistant AI, was released. Later FOSS variants of the tool included FauxPilot.
In the debate regarding the cognitive impacts of smartphones and digital technology, a group reported that, contrary to widespread belief, scientific evidence does not show that these technologies harm biological cognitive abilities and that they instead change predominant ways of cognition – such as a reduced need to remember facts or conduct mathematical calculations by pen and paper outside contemporary schools. However, some activities – like reading novels – that require long attention-spans and don't feature ongoing rewarding stimulation may become more challenging in general. Open 3D Engine – a game engine that is free and open source software (FOSS) and has Linux support – was released. Researchers used a brain–computer interface to enable a man who was paralyzed since 2003 to produce comprehensible words and sentences by decoding signals from electrodes in the speech areas of his brain. Japan achieved a new world record Internet speed: 319 Tbit/s over ~3000 km which, albeit not being the fastest speed overall, beats the previous record of 178 Tbit/s.
Scientists reported that worldwide adolescent loneliness and depression increased substantially after 2012 and that loneliness in contemporary schools appears to be associated with smartphone access and Internet use. DeepMind announced that its AlphaFold AI had predicted the structures of over 350,000 proteins, including 98.5% of the ~20,000 proteins in the human body. The 3D data along with their degrees of confidence for accuracy was made freely available with a database, doubling the previous number of protein structures in the public domain. Scientists published the first complete neuron-level-resolution 3D map of a monkey brain which they scanned within 100 hours.
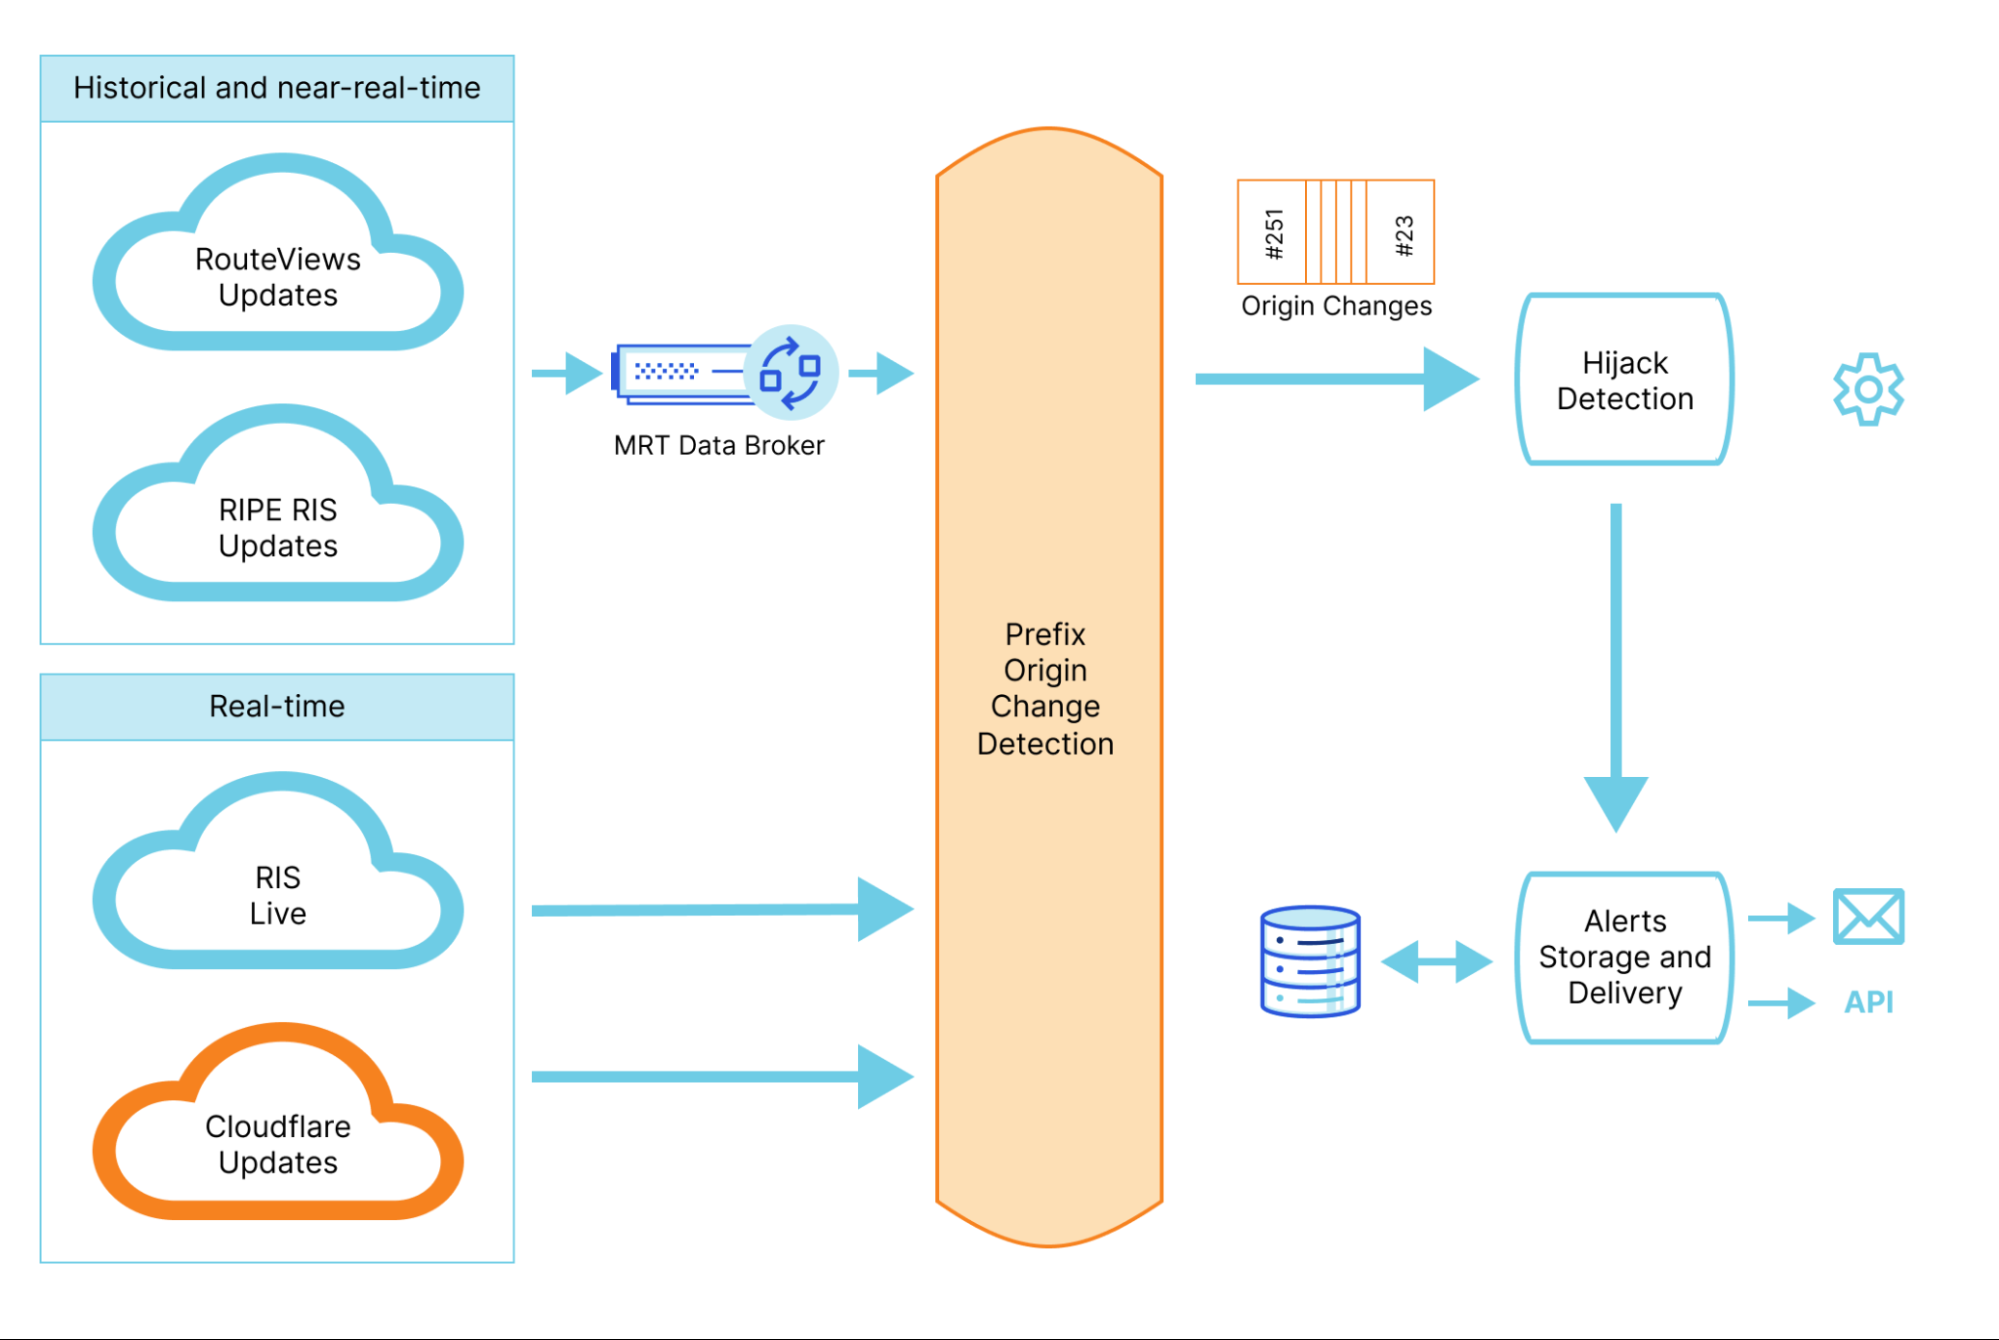
A researcher reported that solar superstorms would cause large-scale global months-long Internet outages. She described potential mitigation measures and exceptions – such as user-powered mesh networks and related peer-to-peer applications – and the robustness of the current Internet infrastructure. Figure 3: Cloudflare Radar's new BGP origin hijack detection system Scientists concluded that personal carbon allowances (PCAs) could be a component of climate change mitigation. They found that the economic recovery from COVID-19 and novel digital technology capacities open a window of opportunity for first implementations. PCAs would consist of – e.g. monetary – credit-feedbacks and decreasing default levels of per capita emissions concessions. The researchers found that recent advances in machine learning technology and "smarter home and transport options make it possible to easily track and manage a large share of individuals' emissions" and that feedback effective in engaging individuals to reduce their energy-related emissions and relevant new personalized apps could be designed. Issues may include privacy, evaluating emissions from individuals co-running multinational companies and the availability and prices of products and services. Cerebras announced a new hardware and software platform that can support AI models of 120 trillion parameters, enabling neural networks greater than the equivalent number of human brain synapses.
Pathogen researchers reported the development of machine learning models for genome-based early detection and prioritization of high-risk potential zoonotic viruses in animals prior to spillover to humans. They concluded that their tool could be used for virus surveillance for pandemic prevention via (i.a.) measures of "early investigation and outbreak preparedness" and would have been capable of predicting SARS-CoV-2 as a high-risk strain. A loss of public IP routes to the Facebook DNS servers due to malfunctioning capacity-assessment code, routinely triggered after configuration changes of routers of the company's data centers, resulted in stoppage of BGP routing information broadcasts caused the 2021 Facebook outage. A study of data traffic by popular smartphones running variants of the Android software found substantial by-default data collection and sharing with no opt-out (i.e. even the NetGuard firewall, which is not installed by default, may not reliably and completely prevent such data traffic) and implications for users' privacy, control and security. Media outlets reported novel technologies for virtual try-ons of clothes for more sustainable fashion and improved online shopping, which increased relative to shopping at local shops that store clothes due to the COVID-19 pandemic. A method of DNA data storage with 100 times the density of previous techniques was announced. Scientists demonstrated that grown brain cells integrated into digital systems can carry out goal-directed tasks with performance-scores. In particular, playing a simulated (via electrophysiological stimulation) Pong which the cells learned to play faster than known machine intelligence systems, albeit to a lower skill-level than both AI and humans, was reported. Moreover, the study suggested it provides the "first empirical evidence" of information-processing capacity differences between neurons from different species. Researchers reported the development of organic low-power neuromorphic electronics which they built into a robot, enabling it to learn sensorimotorically within the real world, rather than via simulations like in the study above. For the chip, polymers were used and coated with an ion-rich gel to enable the material to carry an electric charge like real neurons. Researchers reported the development of a system of machine learning and hyperspectral camera that can distinguish between 12 different types of plastics such as PET and PP for automated separation of waste of, as of 2020, highly unstandardized plastics products and packaging. A scientific review summarized research and data about telemedicine. Its results indicated that, in general, outcomes of such ICT-use are as good as in-person care with health care use staying similar. The Log4Shell security vulnerability in a Java logging framework was publicly disclosed two weeks after its discovery. Because of the ubiquity of the affected software, experts have described it as a most serious computer vulnerability. In a high-level meeting, the importance of security maintenance of open-source software – often also carried out largely by few volunteers – to national security was clarified.
Researchers reported the development of a database and analysis tool about perovskite solar cells which systematically integrates over 15,000 publications, in particular device-data about over 42,400 of such photovoltaic devices. Authors described the site – which requires signing up to access the data and uses software that is partly open source but to date not free software – as a participative "Wikipedia for perovskite solar cell research" and suggest that extensively capturing the progress of an entire field including interactive data exploration functionalities could also be applicable to many fields in materials science, engineering and biosciences. A third main convergent graphical shell (Maui Shell) and UI framework (MauiKit), based on KDE/Kirigami, for the Linux operating system on smartphones, desktops and other devices, was released.
News outlets reported artificial intelligence art had won the first place in a digital art competition. Such artistic imagery is generated using input consisting of text and sometimes images, usually including parameters such as artistic style (text-to-image generation). Around the time, an expert concluded that "AI art is everywhere right now", with even experts not knowing what it will mean, a news outlet established that "AI-generated art booms" and reported issues of copyright and automation of professional artists, a news outlet investigated how online communities (e.g. their rules) confronted with many such artworks react, a news outlet raised concerns over deepfakes, a magazine highlighted possibilities of enabling "new forms of artistic expression", and an editorial noted that it may be seen as a welcome "augmentation of human capability".
Moreover, additional functionalities – such as enabling the use of user-provided concepts (like an object or a style) learned from few images for novel personalized art generated from the associated word/s or expanding beyond the borders of artistic images in the same style – were reported. On 22 August, Stable Diffusion released as open source software, making the technology more accessible and free to use on personal hardware as well as extendable by third-parties (i.e. other software projects). A new deep learning technique enabled year-round measurements of sea ice thickness in the Arctic. A screening AI system for many cancer types that integrates different types of data via multimodal learning was reported.
Researchers reported the development of a deep learning system that learns intuitive physics from visual data (of virtual 3D environments) to some degree "from scratch" based on an unpublished approach inspired by studies of visual cognition in infants. Two weeks later, other researchers reported the development of a machine learning algorithm that could discover sets of basic variables of various physical systems and predict the systems' future dynamics from video recordings of their behavior. Researchers reported the development of deep learning software that can design proteins that contain prespecified functional sites.
Researchers demonstrated semi-automated testing for reproducibility (which is lacking especially in cancer research) via extraction of statements about experimental results in non-semantic, gene expression cancer research papers and subsequent testing with breast cancer cell lines via robot scientist "Eve". Agilicious, an open-source and open-hardware versatile standardized quadrotor drone, tailored toward agility, was released. A university reported the release of 'Quad-SDK' which may be the first open source full-stack software for large agile four-legged robots, compatible with the ROS. News outlets reported deployment, research and development of novel military drone technology in the Russo-Ukrainian War in 2022, including demining drones, self-repurposed commercial/hobby drones (including via a hackathon), reconnaissance microdrones, kamikaze drones, bomb-dropping modified drones, and countermeasures such as electronic ones. The first data transmission to exceed 1 petabit per second (Pbit/s) using a single laser and a single optical chip was demonstrated by European researchers. News outlets reported a novel agricultural robot for viable weed control using lasers or "laserweeding".
There are similar precision agriculture machines that have been reported before, also e.g. applying low amounts of herbicides and fertilizers with precision while mapping plant locations, in some cases autonomously. Their benefits may include "healthier crops and soil, decreased herbicide use, and reduced chemical and labor costs". A satellite-free GPS-alternative higher-resolution positioning system using existing telecommunications networks was demonstrated, SuperGPS. Impossible Metals announced its first underwater robotic vehicle, 'Eureka 1', had completed its first trial of selectively harvesting polymetallic nodule rocks from the seabed nearly without harming the environment (as compared to other seabed mining) to help address the rising global need for metals for renewable energy system components – mainly batteries. It operates autonomously and uses advanced computer vision, e.g. using AI to determine which rocks have signs of visible life on them so that they are not harvested.
A study suggested that in children at age 9–12 during two years time, gaming or watching digital videos can be positively correlated with measures of intelligence, albeit correlations with overall screen time (including social media, socializing and TV) were not investigated and 'time gaming' did not differentiate between categories of video games (e.g. shares of games' platform and genre). Computing and the 2022 Russian invasion of Ukraine:An editorial published in a journal noted that remote surgery and types of videoconferencing for sharing expertise (e.g. ad hoc assistance) have been and could be used to support doctors in Ukraine. A forum contribution analyzed Russian users' reactions to the Bucha massacre on social media – on nationalist Telegram channels. Computer science and technology was also used to defend against the 2022 Russian invasion such as with military technology, to document and communicate war events including via facial recognition of dead Russian soldiers and Russian war crimes, and for aggregated information about support opportunities for Ukrainian scientists.
Researchers demonstrated an MRI-ML-based approach that can diagnose early Alzheimer's disease with high accuracy and may help identify unknown related changes in the brain. A study explored the efficacy of GitHub Sponsors, launched in 2019, in terms of supporting FOSS-efforts and the sponsors' intentions as well as the motivation of sponsors and various quantitative and qualitative analyses relevant to this approach of FOSS-funding.
Progress in climate change mitigation (CCM) living review-like works:The living document-like aggregation, assessment, integration and review website Project Drawdown added 11 new CCM solutions to its organized set of mitigation techniques. The website's modeling framework was used in a study document to show that metal recycling has significant potential for CCM. A revised or updated version, using computer models, of a major worldwide 100% renewable energy proposed plan and model was published. Teaching hospital press release: News outlets reported that in July, for the first time, more people watched streaming TV than cable within the U.S.. A researcher reported that the social media app TikTok adds a keylogger to its, on iOS essentially unavoidable, in-app browser in iOS, which allows its Chinese company to gather, for example, passwords, credit card details, and everything else that is typed into websites opened from taps on any external links within the app. Shortly after the report, the company claimed such capabilities are only used for debugging-types of purposes. To date, it has largely not been investigated which and to which extent (other) apps have capacities for such or similar data-collection. A university reported the development of a driver isolation framework to protect operating system kernels, primarily the monolithic Linux kernel which gets ~80,000 commits/year to its drivers, from defects and vulnerabilities in device drivers, with the Mars Research Group developers describing this lack of isolation as one of the main factors undermining kernel security. A study concluded that advanced artificial intelligence with learned goal planning would or may intervene in the provision of reward to short-circuit reward via advanced exploits of ambiguity in the data about its goal such as considering the sending of the reward itself as humans' goal and intervening in the data-provision about its goal.
University press release: A research report by NewsGuard indicated there is a high level of online misinformation delivered – to a mainly young user base – with TikTok, whose usage is increasing. The second largest cryptocurrency, Ethereum, switched from the proof-of-work (electricity consumption for validation) to the proof-of-stake (staked holdings for validation) algorithm, which cuts its large electricity consumption. Results of investigations about the issue of recommendation systems shifting their users' preferences "so they are easier to satisfy" were reported, including actively optimizing such software to avoid problematic shifts/manipulation, suggesting "that recommenders that optimize for staying in the trust region can avoid manipulative behaviors while still generating engagement". An open source platform to match genomically profiled cancer patients to precision medicine drug trials was reported. After domain seizures of Z-Library by copyright law enforcement and moves toward dark web and IPFS technologies by its content providers, the open source shadow library UI Anna's Archive – which also provides access to a full copy of Z-Library content and scientific articles – was established by a team of archivists, essentially providing the largest human book and literature library. News outlets reported the development of a post-editing model using GPT-3 that improves machine translations after identification of current translation problems. The largest global inventory and interactive map of greenhouse gas emission sources was released by Climate TRACE (9 November). Around the acquisition of Twitter by Elon Musk (27 October), interest in alternatives to the site – described as "one of the world's most high-profile information ecosystems", a contemporary suboptimal public square, and as heavily used by many journalists and news media – increased substantially. However, no alternative such as Mastodon, Reddit or the Bluesky protocol was found to match its features such as ease of use to date, in terms of being able to substitute the site. Two studies demonstrated platform-built-in as well browser-integrated misinformation mitigation. Researchers developed falsity scores for over 800 contemporary elites on Twitter and associated exposure scores. News outlets reported the first fully self-supervised anti–money laundering AI software using contemporary suboptimal datasets, LaundroGraph. A university reported on the first study of the new privacy-intrusion Web tracking technique of "UID smuggling" by the ad industry, which finds it to be prevalent and largely not mitigated by the latest protection tools – such as Firefox's tracking protection and uBlock Origin – and contributes to countermeasures. Text-to-3D software became sophisticated, shortly after generative AI art. OpenAI released Point-E, a machine learning system that can generate 3D models from text prompts, similar to previously released GET3D and Magic3D by Nvidia. DreamFusion from Google may also be notable.
Chatbot and text-generating AI, ChatGPT (released on 30 Nov 2022), a large language model, became popular. It was estimated that only two months after its launch, it had 100 million active users. Applications may include enhancing the productivity of, or automating, large swathes of white collar work, including software development, finance, law, and education. Google released chatbot Bard due to effects of the ChatGPT release, with potential for integration into its Web search and, like ChatGPT software, also as a software development helper tool. DuckDuckGo released the DuckAssist feature integrated into its search engine that summarizes information from Wikipedia to answer search queries that are questions. The experimental feature was shut down without explanation on 12 April. There has been further development regarding LLMs or ChatGPT as user interfaces of Wikipedia or as software using its structured knowledge by others. It may demonstrate an alternative approach to ChatGPT whose fundamental algorithms are not designed to generate text that is true, including for example "hallucinations" and fake citations or misinformation more generally. Elicit.org may provide a free alternative to this tool. A broader alternative approach to the software's Q&A applications and use of text generation for assignments may be the improvement of media literacy and Web search skills in education systems. Further LLM developments during what has been called an "AI boom" included: local or open source versions of LLaMA which was leaked in March, news outlets reported on GPT4-based Auto-GPT that given natural language commands uses the Internet and other tools in attempts to understand and achieve its tasks with unclear or so-far little practicality, a systematic evaluation of answers from four "generative search engines" suggested their outputs "appear informative, but frequently contain unsupported statements and inaccurate citations", a multi-modal open source tool for understanding and generating speech, a data scientist argued that "researchers need to collaborate to develop open-source LLMs that are transparent" and independent, Stability AI launched an open source LLM. A method for editing NeRF scenes, a novel media technique from 2020, with natural language commands was demonstrated by Nvidia. An open letter "Pause Giant AI Experiments" initiated by the Future of Life Institute called for "AI labs to immediately pause for at least 6 months the training of AI systems more powerful than GPT-4" due to "profound risks to society and humanity". It received substantial media attention and also contributed to speculations about perceived large LLM potential). At the time there was extensive media coverage of views that regard ChatGPT as a potential step towards AGI or sentient machines, also extending to some academic works (e.g. a popular preprint by a company). The coverage focused on such views may not represent the majority expert views and, for example, some researchers noted that e.g. the ability to generate coherent text and imitations are not the same as understanding language. A set of techniques under development included self-refining code or text. ChatGPT was shown to outperform human doctors in responding to online medical questions when measured on quality and empathy by "a team of licensed health care professionals", albeit the chatbot may have previously been trained with these reddit question and answers threads. News outlets reported on a preprint that described the development of a large language model software that can answer medical questions with a 67.6% accuracy on MedQA and nearly matched human clinician performance when answering open-ended medical questions, Med-PaLM. The AI makes use of comprehension-, recall of knowledge-, and medical reasoning-algorithms but remains inferior to clinicians. As of 2023, humans often – if not most often – conduct query-based web searches, read websites and/or conduct physical doctor's visits to inquire health information, despite various difficulties, partly as they typically did not undergo any formal training in media literacy, digital literacy or health literacy, as such is not part of schools curricula in most education systems as of 2023. A novel potentially significantly more efficient text-to-image approach, as implemented in MUSE, was reported. A first successful autonomous long-duration operation, including simulated combat, of a modified F-16 fighter jet, X-62A, by two AI software was reported. A text-to-speech synthesizer, VALL-E, that can be trained to mimic anybody's voice with just three seconds of voice data and may produce the most natural-sounding results to date, was reported in a preprint. A use of world models for a wide range of domains that make decisions using e.g. different 3D worlds and reward frequencies and outperforms previous approaches, DreamerV3, was reported as a step towards general artificial intelligence in a preprint. A large language model, ProGen, that can generate functional protein sequences with a predictable function, with input including tags specifying protein properties, was reported.
A deep-learning model, ZFDesign, for zinc finger design for any genomic target for gene- and epigenetic-editing was reported. Software for generating 3D dynamic scenes (text-to-4D), MAV3D, was reported. A study reported the development of deep learning algorithms to identify technosignature candidates, finding 8 potential alien signals not detected earlier. An international norms and arms control proposal for artificial intelligence in the military (such as LAWs and weapons decision-making), the "Political Declaration on Responsible Military Use of Artificial Intelligence and Autonomy]", was published by the U.S. government. The first international summit on military AI led to a joint unbinding statement by the U.S., China and other nations, with some external calls for starting negotiations on an internationally binding law or an enforcement-mechanisms-driven law. The world's first COVID-19 drug designed by generative AI was approved for human use, with clinical trials expected to begin in China. The new drug, ISM3312, was developed by Insilico Medicine. The LLM GPT-4 was launched by OpenAI. It and ChatGPT based on it continued to receive major global media attention. Researchers suggested that growing influence of industry in AI research means that "public interest alternatives for important AI tools may become increasingly scarce". Google revealed PaLM-E, an embodied multimodal language model with 562 billion parameters.
Researchers demonstrated an open source 'AI scientist' that can create models of natural phenomena from knowledge axioms and experimental data, showing the software can rediscover physical laws like "Kepler's third law of planetary motion, Einstein's relativistic time-dilation law, and Langmuir's theory of adsorption" using logical reasoning and a few data points. 2. System Architecture & Core Working Principles Researchers demonstrated a non-invasive brain-reading method. It can translate a person's neural activity into a continuous stream of text using fMRI data and transformer machine learning. Prior training data is required for this semantic decoding.
Participants listened to stories for 16 hours while their brain activity was recorded. A new AI algorithm developed by Baidu was shown to boost the antibody response of COVID-19 mRNA vaccines by 128 times. Computational neuroscientists showed that people with higher intelligence scores in HCP cognitive tests took more time to solve difficult problems and that their higher synchrony between brain areas allowed for better integration of evidence (or progress) from preceding working memory sub-problem processing. Reducing synchrony in "avatar" simulations, that were adjusted and tuned towards personalization, "led decision-making circuits to quickly jump to conclusions". Their codified results may be useful for an understanding of cognition to replicate or imitate in bio-inspired computing. AI was used to develop an experimental antibiotic called abaucin, which is shown to be effective against A. baumannii. A machine learning model is trained to recognise the key features of chemicals with senolytic activity. It finds three chemicals – ginkgetin, periplocin and oleandrin – able to remove senescent cells without damaging healthy cells. Articles in science outlets like Nature suggest contemporary viral concerns about hypothetical existential risk of AI "plays into the tech companies' agenda" – partly in the form of 'criti-hype' – and that this "hinders effective regulation of the societal harms AI is causing right now" and in the near-future. A science writer provides an overview of "the nascent industry of AI-designed drugs".
A preprint introduces the concept of "thought cloning" by which AI use data of or imitate human thinking. Metaresearchers showed that AI trained with study-author-networks data could generate scientifically promising "alien" hypotheses that would likely not be considered otherwise. A study provides an overview and living review of open source LLMs, assessing the levels of openness of their differentiated elements and reviewing the risks of relying on proprietary software or the importance of open source AI.
AI-supported mammography screening was demonstrated to have the potential to substantially reduce workload and to possibly improve cancer detection rates. A review outlined applications and challenges of using AI to accelerate science. A study that won an international competition demonstrated an approach that predicted 70% of earthquakes, suggesting some form of earthquake prediction may be feasible in the future. Researchers released a large set of audiobooks for free books in Project Gutenberg created automatically via generative AI with near-natural voice. A natural language system was demonstrated that can provide explanations for the conclusion-making of machine learning models for explainable AI. A preprint reported some large language models have an 'extractable memorization' flaw by which training data can be extracted at affordable costs by queries. Google DeepMind announced its Gemini multimodal language model, which it claims has advanced "reasoning capabilities" and can outperform GPT-4 on a variety of tasks. A new class of antibiotic candidates, able to kill methicillin-resistant Staphylococcus aureus (MRSA) was identified using explainable deep learning. Notable innovation products: an open source automated experimentation science platform (BacterAI) for predicting microbial metabolism with little data, a low-cost smartphone-attachment (BPClip) for blood pressure measurement, an open source transfer learning-based system (Geneformer) for predicting how networks of interconnected human genes control or affect the function of cells, a performant open source AI software for protein design (RFdiffusion) was introduced, multimodal biomedical Med-PaLM M was introduced.
An autonomous laboratory for synthesis of inorganic powders, the A-Lab. Notable innovations: a low-cost open source air pollution sensor (Flatburn), a laser-using drone-based methane plume localization method, and a portable EEG helmet with significant accuracy of decoding thought words to text (DeWave). An experimental study reported online search to evaluate the truthfulness of false news articles increased the probability of believing them, especially for those for whom search engines return lower-quality information. It suggests media literacy programs with tested strategies and solutions for identified search engines issues are needed. The concept of enshittification about the quality of content on social media platforms introduced in 2022 gained traction. Notable innovations: a Tor browser-equivalent Web browser for privacy-protected browsing when using a VPN (Mullvad browser) was demonstrated, after moderators of the Web content aggregation-based platform Reddit strike against the site's introduction of API pricing and the ensuing closing of several mobile client apps, several novel decentralized open source aggregation platforms gain substantial numbers of users – most notably Lemmy and Kbin which can synchronize their posts via interoperability, the first upgrade of the Global Earthquake Model data for disaster risk reduction, and the misinformation-countering system Community Notes became relatively widely used on X (formerly Twitter).
Scientists coalesced recent developments (see also 2022-12-26) using human brain organoids into a new field they term organoid intelligence (OI), seeking to harness OI for computing – as a novel type of AI – in an ethically responsible way. Networks of such miniature tissues could become functional using stimulus-response training or organoid-computer interfaces – to potentially become "more powerful than silicon-based computing" for a range of tasks – and could also be used for research of various pathophysiologies, brain development, human learning, memory and intelligence, and new therapeutic approaches against brain diseases. Biological organoid intelligence, 'Brainoware', was demonstrated to solve computational tasks in a preprint, with implications for bioethics and potential bottlenecks and limits of nonbio-AI. A study demonstrated functional integration of a magnetically steered microbot containing neurons, 'Mag-Neurobot', in a mouse "organotypic hippocampal slice" as physical (semi-) artificial neurons. Researchers reported the development of a fuel cell implant powered by blood glucose. It can also release insulin at certain levels and have enough energy to allow smartphone implant control.
Researchers reported the development of neuromorphic AI hardware using nanowires (see also 2020-04-20) physically mimicking the brain's activity in identifying and remembering an image from memory. A university reported on a demonstration of multisensory motion cue integration by a neuromorphic nerve for robots. Researchers demonstrated encoding and storing data – small images – as DNA without new DNA synthesis by recording light exposure into bacterial DNA via optogenetic circuits. The 'biological camera' extends chemical and electrical interface techniques. Researchers demonstrated the use of biological-electronic hybrid Organoid Intelligence, 'Brainoware', for speech recognition.
On January 5th, Nvidia announces the "Rubin" platform at CES 2026, its first extreme-codesigned six-chip AI architecture (CPU, GPU, DPU, NIC, NVLink, and Ethernet switching) and successor to Blackwell. The Rubin GPU features a third-generation Transformer Engine delivering 50 petaflops of NVFP4 compute for AI inference, and the platform is declared to be in full production. On January 5th, Intel launches its Core Ultra Series 3 ("Panther Lake") processors at CES 2026, the first client compute platform built on Intel's 18A process node — the most advanced semiconductor process developed and manufactured in the United States — powering over 200 PC designs. On February 2nd, SpaceX acquires xAI in an all-stock transaction that makes xAI a wholly owned subsidiary of SpaceX, combining the two Elon Musk–led companies' AI, rocket, satellite-internet, and media businesses under one roof. On March 11th, Google completes its acquisition of cloud and AI security firm Wiz for approximately $32 billion in cash — the largest acquisition in Google's history — integrating Wiz into Google Cloud while retaining the Wiz brand. On May 25th, Pope Leo XIV releases Magnifica humanitas, an encyclical about the risks of AI and how humanity can be safeguarded against those risks. On June 8th, Apple holds WWDC26, unveiling the next generation of Apple Intelligence and a redesigned "Siri AI," along with iOS 27, macOS 27, and other platform updates.
The keynote is the last WWDC appearance of CEO Tim Cook before his handover to hardware chief John Ternus on September 1. On June 25th, IBM announces a breakthrough in "sub-1 nanometer" semiconductor technology. It features a new architecture at the 0.7 nm node, called "nanostack," which is the first three-dimensional architectural design based on nanosheets. The design stacks approximately 100 billion transistors vertically to overcome physical limitations in small-scale semiconductors. On July 21st, Google releases three new Gemini models, including Gemini 3.6 Flash — described as its most powerful Flash model — and Gemini 3.5 Flash Cyber, a cybersecurity-specialized model. On July 24th, the European Union publishes the "Digital Omnibus" amendments to the EU AI Act in the Official Journal (effective July 27th), which defer the applicability of the high-risk AI system obligations originally scheduled for August 2, 2026, and add new prohibited AI categories.
In 2024, the European Union approved the Artificial Intelligence Act. In 2024, the European Union approved the Cyber Resilience Act. February 12: Cordell Green, 83, American computer scientist and pioneer of logic programming, founder of the Kestrel Institute June 5: Bill Atkinson, 74, American computer scientist known for his work at Apple Computer and for creating HyperCard February 15: Paul Brainerd, 78, American businessman and programmer, founder of Aldus Corporation March 5: Tony Hoare, 92, British computer scientist May 17: Peter G. Neumann, 93, American computer science and security researcher and founder of the Cheri computer security project To access Cloudflare Radar BGP Anomaly Detection results, you will first need to create an API token that includes a Account:Radar permission. All the following examples should work with a free-tier Cloudflare account.
In the following example, we will query the BGP hijack events API for the most recent BGP origin hijacks originated by or affecting AS64512 (example ASN). Users can further filter out low-confidence events by attaching a minConfidence=8 parameter, which will return only events with a confidence_score of 8 or higher.
BGP route leak is another type of BGP anomalies that Cloudflare Radar detects. Currently, we focus on detecting specifically the provider-customer-provider type of route leak. You can learn more about our design and methodology in our blog post âIIï¸I . In the following example, we will query the BGP route leak events API for the most recent BGP route leak events affecting AS64512 .
In this example, we will show you how you can build a Cloudflare Workers app that sends out alerts for BGP hijacks relevant to a given ASN using webhooks (works for Google Hangouts, Discord, Telegram, etc) or email. We will use Cloudflare Workers as the platform and use its Cron Triggers to periodically check for new alerts. In your Wrangler file, change the default checking frequency (once per hour) to what you like. Here is an example of configuring the workers to run the script five minutes.
In this example, we will also need to use Cloudflare KV to save the latest checked event IDs which allows us to know what events are new. Once you have created a KV, you can head back to the wrangler.jsonc file and add the following sections: 3. Software Implementation, Frameworks & Protocols The following apiFetch(env, paramsStr) handles taking in a request parameters string, construct proper headers and fetch from the Cloudflare API BGP hijacks endpoint.
The env parameter is passed in from the caller, and we do not need to worry about construct it. The paramsStr is a string variable that holds the query parameters in a query URL. Now in our main cron trigger function, we will need to construct the query parameters and call the API fetch function. The default cron trigger worker script is defined as the follows: In our example, we use the env variables to get the runtime variables like the TOKEN and ASN of interest, and Cloudflare KV bindings. We do not use the controller and ctx variables in this example.
First, we will need to learn about what are the new events. We define new events as the events the app has not yet processed. We use the Cloudflare KV bucket previously created and defined ( HIJACKS_KV ) to save and retrieve the most recent processed event ID. The main loop that checks for the most recent events looks like this (some of the validation code is skipped): Now that we have all the newly detected events saved in new_events variable, we can then send out alerts: The function send_alert handles constructing alert message and sending out alerts using webhook. Here we demonstrate an example plain-text message template using Google Hangouts webhook. Users can customize the message and the use of webhook based on their platform of choice and needs.
Note that the webhook is considered secret and should be set to the environment via wrangler secret put WEBHOOK_URL command. The last step is to deploy the application with command npx wrangler deploy and the app should be up and running on your Cloudflare account, and will be triggered to execute every five minutes.
If you have Email Routing enabled for your domain, you can also send email alerts directly from Workers. Refer to Send emails from Workers to learn more. For this alert to work, you will need to configure the proper email bindings in the Wrangler configuration file . Then, you can create an email-sending function to send alert emails to your configured destination address: Refer to our API documentation for BGP route leaks and BGP hijacks for more information on these topics.
BGP has no built-in authentication, which means any AS can announce prefixes it doesn’t own. BGP hijacking exploits this to redirect or intercept internet traffic at scale. Here’s how it works and how to defend against it. BGP hijacking exploits the protocol’s lack of built-in origin authentication to redirect internet traffic, and because BGP routes propagate globally in minutes, the impact can be enormous before anyone notices.
Any AS can announce any prefix, BGP has no built-in mechanism to verify that the announcing AS actually owns the prefix. Hijacks range from accidental misconfigurations to deliberate attacks; both can cause massive traffic disruption or interception. RPKI (Resource Public Key Infrastructure) provides cryptographic validation of route origin but adoption remains incomplete globally.
Implement RPKI validation and monitor your own prefixes from external vantage points continuously, waiting for a customer complaint to discover a hijack means the damage is already done. Many activities essential to modern life depend on the internet, and the internet depends on the Border GatThe internet is the wild west of networking. Although there are rules, these rules can be broken at the drop of a hat, either accidentally or deliberately. Like the wild west, there is also the law. Sheriffs who oversee the behavior of citizens to ensurethey obey the rules. In much the same way, BGP monitoring is a vital tool used to ensure that owners of Autonomous Systems (AS) abide by the rules when it comes to which prefixes they announce and how they announce them.
One of the most common ways in which rules are broken on the internet is when a BGP router advertises a prefix that does not belong to its own AS. In other words, it illegitimately announces that specific prefix, thus redirecting traffic from its intended destination towards its own AS. 4. Practical Deployment, Analysis & Case Studies This is called BGP route hijacking, but is also known as prefix hijacking, route hijacking, and IP hijacking.
Remember, BGP is the only way throughwhich the world will know how to get to your specific IP address. If a BGP router illegimately announces, “Hey, if you want to get to this address, send all your traffic to me!” then you can imagine the havoc that will follow. For example, in April of 2018, malicious hackers were able to announce some IP prefixes that belonged to Amazon Web Services . The result was that users attempting to log into a cryptocurrency site were redirected to a fake version of that site, putting in their credentials, and unknowingly depositing over $160,000 directly into the hackers’ wallets.
However, it’s not just malicious attacks that can cause damage. Unintentional instances of BGP hijacking can also have seriousconsequences. In 2008, an ISP in Pakistan attempted to censor YouTube by updating its BGP routes. An error in the configuration caused the whole internet to route YouTube traffic to the Pakistani ISP, resulting in an hours-long outage of YouTube worldwide, and an overwhelmed ISP.
In this chapter of our BGP monitoring guide, we’ll explore the topic of BGP hijacking in depth, including how BGP advertisements work, how bad actors perform hijacks, and how you can detect and prevent BGP route hijacking. To mitigate BGP hijacks, it is important to understand the intricacies of how BGP works, how successful hijacking happens, the motives behind deliberate hijacking, and the causes of inadvertent hijacking. The following table summarizes the concepts that will be examined in detail in this article.
Because BGP is designed with the assumption that all BGP “speakers” are telling the truth, BGP route hijacking is surprisingly simple. It’s truly mind boggling that if you administer a large ISP network, nothing is stopping you from issuing a few commands that can potentially bring the internet to its knees. To understand how you can help mitigate this risk, it is first important to understand how BGP prefix advertisements and BGP hijacking work.
BGP organizes the internet into ASes. Each AS is comprised of multiple routers, and contains within its borders specific prefixes, or routes, that it advertises to neighboring ASes. BGP routers propagate these prefixes throughout the internet and maintain a path to that destination through various ASes. Each AS is responsible for announcing to its neighbors the prefixes that it owns and contains within it.
The result is a BGP table maintained within each BGP router that contains the path of ASes that must be traversed to reach that particular prefix. AS 100 is advertising its own prefix of 195.25.0.0/23 to neighboring ASes. When that information reaches AS 170, it will say: Now, AS 170 will have received this prefix from advertisements with different paths, as shown by the red dotted lines.
However, assuming all previous BGP attributes remain the same, because those paths are longer, that is, they traverse a larger number of ASes, the green dotted line path wins out. We’ll see later on why this is important when it comes to hijacking. Remember the ASes shown in the diagram are composed of many routers. Those on the edge of the AS that form peerings with BGP routers in other ASes are External BGP or eBGP routers. eBGP routers are responsible for announcing prefixes to other ASes.
A BGP route hijack occurs when a “hostile” AS decides to advertise a prefix that is not its own. For example, in the following diagram, AS 140 is illegitimately advertising the same prefix as AS 100: What will happen? All other ASes will receive two different advertisements of the same prefix. Which one they select to put in their BGP table depends on the BGP attributes.
One of the attributes that will play a large part in this decision is the AS_PATH. Assuming all previous attributes remain the same, the route with the shortest AS_PATH will be installed. If the AS_PATH is equal, then other attributes act as tie-breakers, such as oldest path or router ID, which leads to unpredictable routing. In the case of the above diagram, only AS 190 is assured of having correct routing to the 195.25.0.0/23 prefix. The others will either have AS 140 as the destination or will have unpredictable results due to AS_PATH tiebreakers.
In addition, hijackers can perform what is known as an AS_PATH forgery, where the advertised AS_PATH for the destination is modified so that traffic destined for the route in question will go through the local AS. In these cases, the legitimate AS is included in the AS_PATH to make it more difficult for such a hijack to be detected while traffic is steered towards the illegitimate AS.
The term “prefix” in the context of BGP can be used in various ways, including referring to specific routes. Strictly speaking, the prefix is the subnet mask in “/” notation (a.k.a. CIDR notation) that specifies the actual size and range of IP addresses being advertised. BGP can advertise prefixes for sizes /8 to /24. If an AS owns the 147.52.0.0/24 prefix, and it erroneously advertises it with an incorrect prefix of 147.52.0.0/23, it will begin advertising an address space that does not belong to it.
Similarly, if we look at our previous example of malicious BGP hijacking, if our hijacker decides to use a prefix of /24 as shown below, then he will be able to steer all traffic within the 195.25.0.0/24 network to itself. Remember that BGP will always prefer placing a more specific prefix into its routing table. The result is that all other ASes receiving these advertisements will see AS 140 as the owner of the 195.25.0.0/24 network and will route traffic accordingly.
5. Performance Evaluation & Extended Technical Observations There are multiple reasons an attacker may perform BGP route hijacking. The Amazon example at the beginning of this article is a textbook example of financial motivations. Other reasons an attacker may perform BGP route hijacking include: As you can see, hijacking is a very real, potential threat to the correct operation of routing on the internet. For this reason, it is important to employ the appropriate mechanisms and configurations to protect against these kinds of attacks and accidents.
The short answer is you can’t. There is no way to prevent someone from configuring a BGP router to hijack routes, either purposefully or accidentally. Techniques for dealing with hijacks have to do with detection, mitigation, and limitation of the propagation of incorrect routes. These techniques are described below. ISPs should filter BGP advertisements and only allow those containing legitimate prefixes from being propagated further. IP advertisements should not be accepted as they come. Instead, they should go through a filtering process that uses algorithms to detect hijacks and validate legitimacy.
Similarly, in most cases, BGP routers should only announce their prefixes to select networks, not to the entire internet. Limiting announcements helps prevent hijacking that can result from misconfigurations and accidents. While useful, prefix filtering alone is not enough. Administrators must always supplement it with additional measures. Hijack detection can take several forms. Initially, changes in baseline performance, such as greater latency, misdirected traffic, or general degradation of performance are initial signs that may indicate some form of hijacking. Additionally, monitoring of advertisements, as well as recording the availability and downtime of routes are important aspects involved in discovering a hijack.
More sophisticated systems can also analyze the advertised ASes from neighbors to see if hijacked prefixes are included in the advertisements, can identify prefix mismatches, and use path analysis to ensure correct routing, all in near real-time. BGP was first developed in 1989. Since then, it has been developed and vastly improved. However, security has not been part of its improvements. Some attempts have been made to incorporate security with the introduction of BGPsec in 2017 but there has not been any substantial adoption. So, for now, this thirty-something protocol remains inherently vulnerable and requires somewhat elaborate monitoring mechanisms to keep it in check.
One aspect that has the potential to aid in the fight against BGP route hijacking is the use of a Route Origin Authorization (ROA). ROAs are cryptographically signed objects that can be used to validate if a particular prefix has been originated from a legitimate AS. ROAs are created by each AS owner in cooperation with the Regional internet Registry (RIR), which provides the RPKI infrastructure needed to generate them. More information about this can be found at the American Registry for internet Numbers (ARIN) website.
It is rare to find a vital technology such as BGP that is so vulnerable to the effects of malicious attacks or accidental misconfigurations. And yet, BGP, when paired up with the appropriate monitoring or observability solutions that reliably detect and mitigate against the effects of route hijacks, is more than sufficient to deliver the routing services that the internet needs. LogicMonitor’s network monitoring capabilities provide real-time visibility into routing changes and anomalies, helping your team detect unauthorized prefix announcements and act before traffic is redirecte BGP hijacking (also called prefix hijacking or route hijacking) occurs when an autonomous system (AS) illegitimately announces IP prefixes that belong to another organization. Because BGP routers accept route announcements from peers without verifying ownership, other ASes propagate the fraudulent route globally. This can redirect internet traffic away from legitimate destinations, enabling eavesdropping, traffic interception, or service disruption.
Both involve incorrect route propagation, but for different reasons. A route leak is typically accidental, an AS propagates routes it received from one peer to another peer without intending to, violating routing policy. A BGP hijack is deliberate, with an AS fraudulently claiming to be the origin of prefixes it doesn’t own. Route leaks can also be exploited maliciously, but the distinction lies in intent and mechanism.
RPKI (Resource Public Key Infrastructure) allows IP address holders to cryptographically sign Route Origin Authorizations (ROAs) that specify which AS is authorized to announce a given prefix. BGP routers with RPKI validation enabled can check incoming route announcements against the ROA database and reject routes that fail validation (invalid origin AS or prefix length). RPKI doesn’t eliminate all hijacking scenarios but significantly raises the bar for fraudulent announcements.
The most effective approach is to monitor your own prefixes from multiple external BGP vantage points, not just your own routers. Public data sources like RIPE NCC’s Routing Information Service (RIS) and RouteViews provide BGP data from hundreds of global peers. You should alert on any unexpected origin AS announcing your prefixes, unexpected AS_PATH changes, or more-specific (sub-prefix) announcements of your address space from ASes you don’t control.
Denton Chikura is a technical writer and longtime observability advocate focused on helping site reliability engineers and engineering teams discover the tools and capabilities that strengthen internet resilience. He works at the intersection of monitoring, performance, and infrastructure to make complex systems more understandable and usable, bridging the gap between deep technical detail and realIworld operations. His goal is to help teams build faster, detect issues earlier, and recover smarter, ultimately making the internet a better, more reliable place for everyone.
Disclaimer: The views expressed on this blog are those of the author and do not necessarily reflect the views of LogicMonitor or its affiliates. BGP route hijacking represents one of the most severe attack vectors in internet routing infrastructure , where malicious actors announce unauthorised prefixes to divert traffic through their autonomous systems . Traditional perimeter defences fail against BGP attacks because the compromise occurs at the routing protocol layer, making hijacked traffic appear legitimate to downstream networks. Real-time BGP hijacking detection requires deploying continuous monitoring systems that validate route announcements against cryptographic attestations, historical AS-path patterns, and prefix ownership records.
The architectural challenge stems from BGP’s inherent trust model—routers accept route announcements without cryptographic verification, relying on policy filters and manual prefix lists that scale poorly across global routing tables. When an attacker announces a victim’s prefix with a shorter AS-path, BGP’s longest-prefix-match algorithm routes traffic to the hijacker’s infrastructure, enabling man-in-the-middle attacks, traffic analysis, and service disruption.
Resource Public Key Infrastructure The KBY Lexicon Public Key Infrastructure PKI is the trust framework of certificate authorities, X.509 certificates, and revocation mechanisms that binds public keys to identities across TLS, code signing, and authentication. Read Full Context (RPKI) provides cryptographic attestation for prefix announcements through Route Origin Authorisations (ROAs) signed by Regional Internet Registries. An effective BGP hijacking detection system builds upon RPKI validation by continuously monitoring route announcements against the global RPKI repository and flagging invalid origins in real-time.
The validation architecture requires three core components: an RPKI validator daemon that fetches and processes ROAs, a BGP monitor that receives route feeds from multiple vantage points, and a correlation engine that matches announcements against RPKI data. The validator maintains a local cache of validated ROA objects, each containing the authorised AS number, prefix, and maximum length for legitimate announcements.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/BGP%20hijacking • https://en.wikipedia.org/wiki/Timeline%20of%20computing%202020%E2%80%93present • https://developers.cloudflare.com/radar/investigate/bgp-anomalies/ • https://www.logicmonitor.com/deep-dive/bgp-monitoring/bgp-hijacking • https://www.kbytechnologies.com/security-operations/hunting-bgp-route-hijacking-in-real-time-networks
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Bgp Route Hijacking Detection And Alert Tool.
[*] Metasploit Scan Running on Target Subnet for Bgp Route Hijacking Detection And Alert Tool... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |