Complete Technical Paper Content — Biometric Multi Factor Authentication Web Application
Overview & System Context
Biometric Multi Factor Authentication Web Application: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9530 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Multi-factor authentication (MFA), also known as two-factor authentication (2FA), is an electronic authentication method in which a user is granted access to a website or application only after successfully presenting two or more distinct types of evidence (or factors) to an authentication mechanism. MFA protects personal data—which may include personal identification or financial assets—from being accessed by an unauthorized third party that may have been able to discover, for example, a single password. Usage of MFA has increased in recent years. Security issues which can cause the bypass of MFA are fatigue attacks, phishing and SIM swapping. Accounts with MFA enabled are significantly less likely to be compromised.
Something the user has: Any physical object in the possession of the user, such as a security token (possibly shaped like a USB stick), a bank card, a key, a phone that can be reached at a certain number, etc. Something the user knows: Certain knowledge only known to the user, such as a password, PIN, PUK, etc. Something the user is: Some physical characteristic of the user (biometrics), such as a fingerprint, eye iris, voice, typing speed, pattern in key press intervals, etc. An example of two-factor authentication is the withdrawing of money from an ATM; only the correct combination of a physically present bank card (something the user possesses) and a PIN (something the user knows) allows the transaction to be carried out. Two other examples are to supplement a user-controlled password with a one-time password (OTP) or code generated or received by an authenticator (e.g. a security token or smartphone) that only the user possesses. An authenticator app enables two-factor authentication in a different way, by showing a randomly generated and constantly refreshing code, rather than sending an SMS or using another method. This code is a Time-based one-time password (a TOTP), and the authenticator app contains the key material that allows the generation of these codes.
Knowledge factors ("something only the user knows") are a form of authentication. In this form, the user is required to prove knowledge of a secret in order to authenticate. A password is a secret word or string of characters that is used for user authentication. This is the most commonly used mechanism of authentication. Many multi-factor authentication techniques rely on passwords as one factor of authentication. Variations include both longer ones formed from multiple words (a passphrase) and the shorter, purely numeric, PIN commonly used for ATM access. Traditionally, passwords are expected to be memorized, but can also be written down on a hidden paper or text file.
Possession factors ("something only the user has") have been used for authentication for centuries, in the form of a key to a lock. The basic principle is that the key embodies a secret that is shared between the lock and the key, and the same principle underlies possession factor authentication in computer systems. A security token is an example of a possession factor. Disconnected tokens have no connections to the client computer. They typically use a built-in screen to display the generated authentication data, which is manually typed in by the user. This type of token mostly uses a one-time password that can only be used for that specific session.
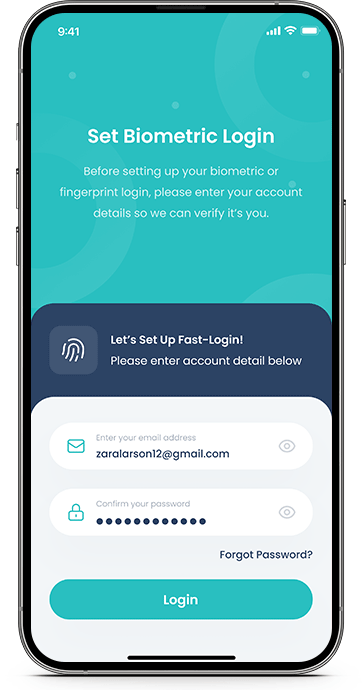
Figure 1: Biometric Software Connected tokens are devices that are physically connected to the computer to be used. Those devices transmit data automatically. There are a number of different types, including USB tokens, smart cards and wireless tags. Increasingly, FIDO2 capable tokens, supported by the FIDO Alliance and the World Wide Web Consortium (W3C), have become popular, with mainstream browser support beginning in 2015. A software token (a.k.a. soft token) is a type of two-factor authentication security device that may be used to authorize the use of computer services. Software tokens are stored on a general-purpose electronic device such as a desktop computer, laptop, PDA, or mobile phone and can be duplicated – contrast hardware tokens, where the credentials are stored on a dedicated hardware device and therefore cannot be duplicated, absent physical invasion of the device. A soft token may not be a device the user interacts with. Typically an X.509v3 certificate is loaded onto the device and stored securely to serve this purpose. Multi-factor authentication can also be applied in physical security systems, where it is typically deployed through the use, firstly, of a physical possession (such as a fob, keycard, or QR-code displayed on a device) which acts as the identification credential, and secondly, a validation of one's identity such as facial biometrics or retinal scan (facial verification or facial authentication), or a PIN.
No additional tokens are necessary because it uses mobile devices that are (usually) carried all the time. As they are constantly changed, dynamically generated passcodes are safer to use than fixed (static) log-in information. Depending on the solution, passcodes that have been used are automatically replaced in order to ensure that a valid code is always available, transmission/reception problems do not, therefore, prevent logins. Disadvantages: Users may still be susceptible to phishing attacks. An attacker can send a text message that links to a spoofed website that looks identical to the actual website - a Man-in-the-middle attack. The attacker can then get the authentication code, user name and password. A mobile phone is not always available—it can be lost, stolen, have a dead battery, or otherwise not work. In particular, lost devices unrelated to a security incident is a major weakness of mass-adoption (in comparison with a lost device and not using MFA.) Answers to solve this weakness often introduce further complexities to MFA adoption. Despite their growing popularity, some users may not even own a mobile device, and take umbrage at being required to own one as a condition of using some service on their home PC. The SS7 system underlying mobile phone roaming has vulnerabilities, and SMS messages may be redirected to attackers. Mobile phone reception is not always available—large areas, particularly outside of towns, lack coverage. SIM cloning gives hackers access to mobile phone connections. SIM swap attacks and Social-engineering attacks against mobile-operator companies have resulted in the handing over of duplicate SIM cards to criminals. Text messages to mobile phones using SMS are insecure and can be intercepted by IMSI-catchers. Thus third parties can steal and use the token. Account recovery typically bypasses mobile-phone two-factor authentication. Modern smartphones are used both for receiving email and SMS. So if the phone is lost or stolen and is not protected by a password or biometric, all accounts for which the email is the key can be taken over as the phone can receive the second factor. Mobile carriers may charge the user messaging fees.
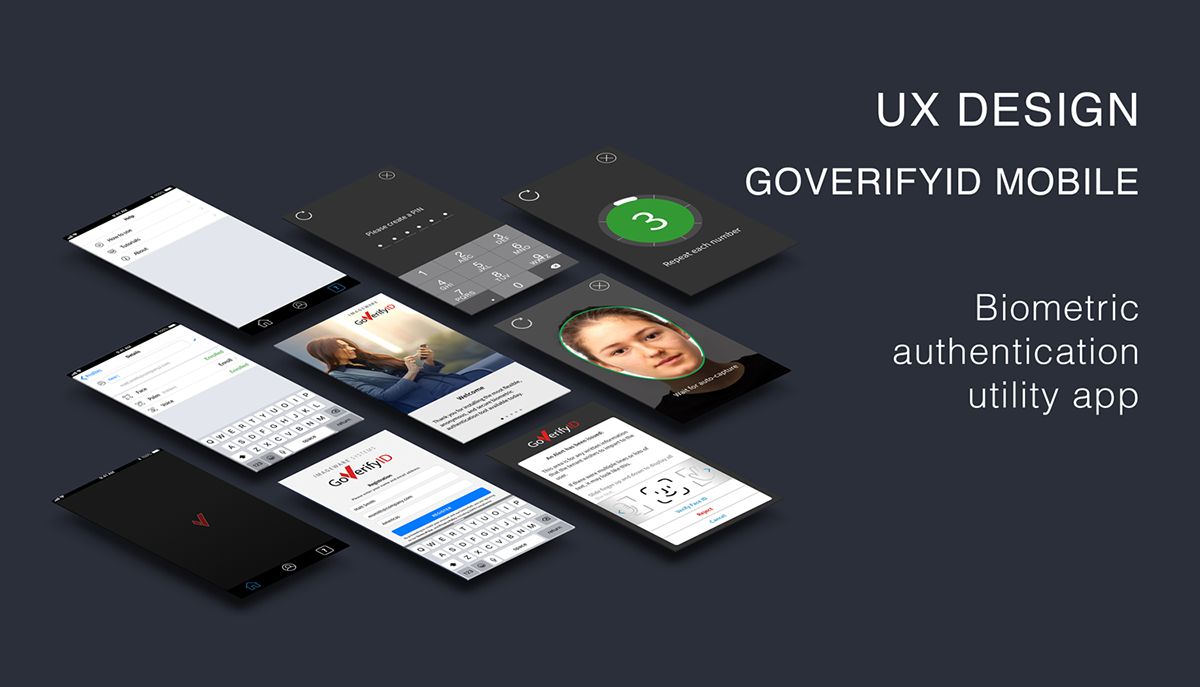
In 2013, Kim Dotcom claimed to have invented two-factor authentication in a 2000 patent, and briefly threatened to sue all the major web services. However, the European Patent Office revoked his patent in light of an earlier 1998 U.S. patent held by AT&T. Figure 2: UI/UX Biometric authentication app :: Behance TwoFactorAuth.org - TwoFactorAuth.org - An in-depth online resource for (2FA) and all it entails Attackers breached the servers of RSA and stole information that could be used to compromise the security of two-factor authentication tokens used by 40 million employees (register.com, 18 Mar 2011) Banks to Use Two-factor Authentication by End of 2006, (slashdot.org, 20 Oct 2005) Microsoft to abandon passwords, Microsoft preparing to dump passwords in favour of two-factor authentication in forthcoming versions of Windows (vnunet.com, 14 Mar 2005) Authentication (from Greek: αIθεντικIς authentikos, "real, genuine", from αIθIντης authentes, "author") is the act of proving an assertion, such as the identity of a computer system user. In contrast with identification, the act of indicating a person or thing's identity, authentication is the process of verifying that identity. Authentication is relevant to multiple fields. In art, antiques, and anthropology, a common problem is verifying that a given artifact was produced by a certain person, or in a certain place (i.e. to assert that it is not counterfeit), or in a given period of history (e.g. by determining the age via carbon dating). In computer science, verifying a user's identity is often required to allow access to confidential data or systems. It might involve validating personal identity documents.
Authentication can be considered to be of three types: The first type of authentication is accepting proof of identity given by a credible person who has first-hand evidence that the identity is genuine. When authentication is required for art or physical objects, this proof could be a friend, family member, or colleague attesting to the item's provenance, perhaps by having witnessed the item in its creator's possession. With autographed sports memorabilia, this could involve someone attesting that they witnessed the object being signed. A vendor selling branded items implies authenticity, while they may not have evidence that every step in the supply chain was authenticated. The second type of authentication is comparing the attributes of the object itself to what is known about objects of that origin. For example, an art expert might look for similarities in the style of painting, check the location and form of a signature, or compare the object to an old photograph. An archaeologist, on the other hand, might use carbon dating to verify the age of an artifact, do a chemical and spectroscopic analysis of the materials used, or compare the style of construction or decoration to other artifacts of similar origin. The physics of sound and light, and comparison with a known physical environment, can be used to examine the authenticity of audio recordings, photographs, or videos. Documents can be verified as being created on ink or paper readily available at the time of the item's implied creation.
Attribute comparison may be vulnerable to forgery. In general, it relies on the facts that creating a forgery indistinguishable from a genuine artifact requires expert knowledge, that mistakes are easily made, and that the amount of effort required to do so is considerably greater than the amount of profit that can be gained from the forgery. In art and antiques, certificates are of great importance for authenticating an object of interest and value. Certificates can, however, also be forged, and the authentication of these poses a problem. For instance, the son of Han van Meegeren, the well-known art-forger, forged the work of his father and provided a certificate for its provenance as well. Criminal and civil penalties for fraud, forgery, and counterfeiting can reduce the incentive for falsification, depending on the risk of getting caught. Currency and other financial instruments commonly use this second type of authentication method. Bills, coins, and cheques incorporate hard-to-duplicate physical features, such as fine printing or engraving, distinctive feel, watermarks, and holographic imagery, which are easy for trained receivers to verify. The third type of authentication relies on documentation or other external affirmations. In criminal courts, the rules of evidence often require establishing the chain of custody of evidence presented. This can be accomplished through a written evidence log, or by testimony from the police detectives and forensics staff that handled it. Some antiques are accompanied by certificates attesting to their authenticity. Signed sports memorabilia is usually accompanied by a certificate of authenticity. These external records have their own problems of forgery and perjury and are also vulnerable to being separated from the artifact and lost.
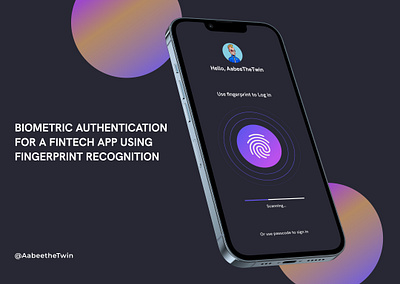
Taggant fingerprinting – uniquely coded microscopic materials that are verified from a database Encrypted micro-particles – unpredictably placed markings (numbers, layers and colors) not visible to the human eye Holograms – graphics printed on seals, patches, foils or labels and used at the point of sale for visual verification Micro-printing – second-line authentication often used on currencies Serialized barcodes UV printing – marks only visible under UV light Track and trace systems – use codes to link products to the database tracking system Water indicators – become visible when contacted with water DNA tracking – genes embedded onto labels that can be traced Color-shifting ink or film – visible marks that switch colors or texture when tilted Tamper evident seals and tapes – destructible or graphically verifiable at point of sale 2d barcodes – data codes that can be tracked RFID chips NFC chips Figure 3: Browse thousands of Biometric Authentication images for design ...
A difficult-to-reproduce physical artifact, such as a seal, signature, watermark, special stationery, or fingerprint. A shared secret, such as a passphrase, in the content of the message. An electronic signature; public-key infrastructure is often used to cryptographically guarantee that a message has been signed by the holder of a particular private key. The opposite problem is the detection of plagiarism, where information from a different author is passed off as a person's own work. A common technique for proving plagiarism is the discovery of another copy of the same or very similar text, which has different attribution. In some cases, excessively high quality or a style mismatch may raise suspicion of plagiarism.
The ways in which someone may be authenticated fall into three categories, based on what is known as the factors of authentication: something the user knows, something the user has, and something the user is. Each authentication factor covers a range of elements used to authenticate or verify a person's identity before being granted access, approving a transaction request, signing a document or other work product, granting authority to others, and establishing a chain of authority. Security research has determined that for a positive authentication, elements from at least two, and preferably all three, factors should be verified. The three factors (classes) and some of the elements of each factor are: Knowledge: Something the user knows (e.g., a password, partial password, passphrase, personal identification number (PIN), challenge–response (the user must answer a question or pattern), security question). Ownership: Something the user has (e.g., wrist band, ID card, security token, implanted device, cell phone with a built-in hardware token, software token, or cell phone holding a software token). Inherence: Something the user is or does (e.g., fingerprint, retinal pattern, DNA sequence (there are assorted definitions of what is sufficient), signature, face, voice, unique bio-electric signals, or other biometric identifiers). Historically, fingerprints have been used as the most authoritative method of authentication, but court cases in the US and elsewhere have raised fundamental doubts about fingerprint reliability. Outside of the legal system as well, fingerprints are easily spoofable, with British Telecom's top computer security official noting that "few" fingerprint readers have not already been tricked by one spoof or another. Hybrid or two-tiered authentication methods offer a compelling solution, such as private keys encrypted by fingerprint inside of a USB device.
Multi-factor authentication involves two or more authentication factors (something you know, something you have, or something you are). Two-factor authentication is a special case of multi-factor authentication involving exactly two factors. For example, using a bank card (something the user has) along with a PIN (something the user knows) provides two-factor authentication. Business networks may require users to provide a password (knowledge factor) and a pseudorandom number from a security token (ownership factor). Access to a very-high-security system might require a mantrap screening of height, weight, facial, and fingerprint checks (several inherence factor elements) plus a PIN and a day code (knowledge factor elements), but this is still a two-factor authentication.
Enrollment – an individual applies to a credential service provider (CSP) to initiate the enrollment process. After successfully proving the applicant's identity, the CSP allows the applicant to become a subscriber. Authentication – After becoming a subscriber, the user receives an authenticator e.g., a token and credentials, such as a user name. He or she is then permitted to perform online transactions within an authenticated session with a relying party, where they must provide proof that he or she possesses one or more authenticators. Life-cycle maintenance – the CSP is charged with the task of maintaining the user's credential over the course of its lifetime, while the subscriber is responsible for maintaining his or her authenticator(s).
The authentication of information can pose special problems with electronic communication, such as vulnerability to man-in-the-middle attacks, whereby a third party taps into the communication stream, and poses as each of the two other communicating parties, in order to intercept information from each. Extra identity factors can be required to authenticate each party's identity.
Biometrics are body measurements and calculations related to human characteristics and features. Biometric authentication (or realistic authentication) is used in computer science as a form of identification and access control. It is also used to identify individuals in groups that are under surveillance. Biometric identifiers are the distinctive, measurable characteristics used to label and describe individuals. Biometric identifiers are often categorized as physiological characteristics which are related to the shape of the body. Examples include, but are not limited to fingerprint, palm veins, face recognition, DNA, palm print, hand geometry, iris recognition, retina, odor/scent, voice and shape of ears. Behavioral characteristics are related to the pattern of behavior of a person, including but not limited to mouse movement, typing rhythm, gait, signature, voice, and behavioral profiling. Some researchers have coined the term "Behaviometrics" (behavioral biometrics) to describe the latter class of biometrics. More traditional means of access control include token-based identification systems, such as a driver's license or passport, and knowledge-based identification systems, such as a password or personal identification number. Since biometric identifiers are unique to individuals, they are more reliable in verifying identity than token and knowledge-based methods; however, the collection of biometric identifiers raises privacy concerns.
Universality: Every person using a system should possess the trait. Uniqueness: The trait should be sufficiently different for individuals in the relevant population such that they can be distinguished from one another. Permanence: The manner in which a trait varies over time. More specifically, a trait with good permanence will be reasonably invariant over time with respect to the specific matching algorithm. Measurability (collectability): The ease of acquisition or measurement of the trait. In addition, acquired data should be in a form that permits subsequent processing and extraction of the relevant feature sets.
Performance: The accuracy, speed, and robustness of technology used (see performance section for more details). Acceptability: How well individuals in the relevant population accept the technology such that they are willing to have their biometric trait captured and assessed. Circumvention: The ease with which a trait might be imitated using an artifact or substitute. Proper biometric use is application dependent. Certain biometrics will be more suitable than others based on the required levels of convenience and security. No single biometric will meet all the requirements of every possible application.
The block diagram illustrates the two basic modes of a biometric system. First, in verification (or authentication) mode the system performs a one-to-one comparison of a captured biometric with a specific template stored in a biometric database in order to verify the individual is the person they claim to be. Three steps are involved in the verification of a person. In the first step, reference models for all the users are generated and stored in the model database. In the second step, some samples are matched with reference models to generate the genuine and impostor scores and calculate the threshold. The third step is the testing step. This process may use a smart card, username, or ID number (e.g. PIN) to indicate which template should be used for comparison. Positive recognition is a common use of the verification mode, "where the aim is to prevent multiple people from using the same identity".
Second, in identification mode the system performs a one-to-many comparison against a biometric database in an attempt to establish the identity of an unknown individual. The system will succeed in identifying the individual if the comparison of the biometric sample to a template in the database falls within a previously set threshold. Identification mode can be used either for positive recognition (so that the user does not have to provide any information about the template to be used) or for negative recognition of the person "where the system establishes whether the person is who she (implicitly or explicitly) denies to be". The latter function can only be achieved through biometrics since other methods of personal recognition, such as passwords, PINs, or keys, are ineffective. The first time an individual uses a biometric system is called enrollment. During enrollment, biometric information from an individual is captured and stored. In subsequent uses, biometric information is detected and compared with the information stored at the time of enrollment. Note that it is crucial that storage and retrieval of such systems themselves be secure if the biometric system is to be robust. The first block (sensor) is the interface between the real world and the system; it has to acquire all the necessary data. Most of the time it is an image acquisition system, but it can change according to the characteristics desired. The second block performs all the necessary pre-processing: it has to remove artifacts from the sensor, to enhance the input (e.g. removing background noise), to use some kind of normalization, etc. In the third block, necessary features are extracted. This step is an important step as the correct features need to be extracted in an optimal way. A vector of numbers or an image with particular properties is used to create a template. A template is a synthesis of the relevant characteristics extracted from the source. Elements of the biometric measurement that are not used in the comparison algorithm are discarded in the template to reduce the file size and to protect the identity of the enrollee. However, depending on the scope of the biometric system, original biometric image sources may be retained, such as the PIV-cards used in the Federal Information Processing Standard Personal Identity Verification (PIV) of Federal Employees and Contractors (FIPS 201). During the enrollment phase, the template is simply stored somewhere (on a card or within a database or both). During the matching phase, the obtained template is passed to a matcher that compares it with other existing templates, estimating the distance between them using any algorithm (e.g. Hamming distance). The matching program will analyze the template with the input. This will then be output for a specified use or purpose (e.g. entrance in a restricted area), though it is a fear that the use of biometric data may face mission creep. Selection of biometrics in any practical application depending upon the characteristic measurements and user requirements. In selecting a particular biometric, factors to consider include, performance, social acceptability, ease of circumvention and/or spoofing, robustness, population coverage, size of equipment needed and identity theft deterrence. The selection of a biometric is based on user requirements and considers sensor and device availability, computational time and reliability, cost, sensor size, and power consumption.
False match rate (FMR, also called FAR = False Accept Rate): the probability that the system incorrectly matches the input pattern to a non-matching template in the database. It measures the percent of invalid inputs that are incorrectly accepted. In case of similarity scale, if the person is an imposter in reality, but the matching score is higher than the threshold, then he is treated as genuine. This increases the FMR, which thus also depends upon the threshold value. False non-match rate (FNMR, also called FRR = False Reject Rate): the probability that the system fails to detect a match between the input pattern and a matching template in the database. It measures the percent of valid inputs that are incorrectly rejected. Receiver operating characteristic or relative operating characteristic (ROC): The ROC plot is a visual characterization of the trade-off between the FMR and the FNMR. In general, the matching algorithm performs a decision based on a threshold that determines how close to a template the input needs to be for it to be considered a match. If the threshold is reduced, there will be fewer false non-matches but more false accepts. Conversely, a higher threshold will reduce the FMR but increase the FNMR. A common variation is the Detection error trade-off (DET), which is obtained using normal deviation scales on both axes. This more linear graph illuminates the differences for higher performances (rarer errors). Equal error rate or crossover error rate (EER or CER): the rate at which both acceptance and rejection errors are equal. The value of the EER can be easily obtained from the ROC curve. The EER is a quick way to compare the accuracy of devices with different ROC curves. In general, the device with the lowest EER is the most accurate. Failure to enroll rate (FTE or FER): the rate at which attempts to create a template from an input is unsuccessful. This is most commonly caused by low-quality inputs. Failure to capture rate (FTC): Within automatic systems, the probability that the system fails to detect a biometric input when presented correctly.
Template capacity: the maximum number of sets of data that can be stored in the system. An early cataloguing of fingerprints dates back to 1885 when Juan Vucetich started a collection of fingerprints of criminals in Argentina. Josh Ellenbogen and Nitzan Lebovic argued that Biometrics originated in the identification systems of criminal activity developed by Alphonse Bertillon (1853–1914) and by Francis Galton's theory of fingerprints and physiognomy.
Historian Keith Breckenridge note that Galton's travels in South Africa reinforced his early racial prejudices and inspired his later commitment to classifying human difference scientifically. According to Lebovic, Galton's work "led to the application of mathematical models to fingerprints, phrenology, and facial characteristics", as part of "absolute identification" and "a key to both inclusion and exclusion" of populations. Accordingly, "the biometric system is the absolute political weapon of our era" and a form of "soft control". The theoretician David Lyon showed that during the past two decades biometric systems have penetrated the civilian market, and blurred the lines between governmental forms of control and private corporate control.
Kelly A. Gates identified 9/11 as the turning point for the cultural language of our present: "in the language of cultural studies, the aftermath of 9/11 was a moment of articulation, where objects or events that have no necessary connection come together and a new discourse formation is established: automated facial recognition as a homeland security technology." It is possible that data obtained during biometric enrollment may be used in ways for which the enrolled individual has not consented. For example, most biometric features could disclose physiological and/or pathological medical conditions (e.g., some fingerprint patterns are related to chromosomal diseases, iris patterns could reveal sex, hand vein patterns could reveal vascular diseases, most behavioral biometrics could reveal neurological diseases, etc.). Moreover, second generation biometrics, notably behavioral and electro-physiologic biometrics (e.g., based on electrocardiography, electroencephalography, electromyography), could be also used for emotion detection. There are three categories of privacy concerns: Unintended functional scope: The authentication goes further than authentication, such as finding a tumor. Unintended application scope: The authentication process correctly identifies the subject when the subject did not wish to be identified.
Covert identification: The subject is identified without seeking identification or authentication, i.e. a subject's face is identified in a crowd. In terms of recognition or identification performance for a given trait, a biometric system should not exhibit accuracy differences across demographic groups. Disparities in accuracy can lead to uneven error rates for populations defined by gender, race, age, or other attributes. Therefore, biometric systems should be designed and evaluated to ensure demographic fairness, providing equitable performance for all users.
To ensure we can shut down terrorist networks before they ever get to the United States, we must also take the lead in driving international biometric standards. By developing compatible systems, we will be able to securely share terrorist information internationally to bolster our defenses. Just as we are improving the way we collaborate within the U.S. Government to identify and weed out terrorists and other dangerous people, we have the same obligation to work with our partners abroad to prevent terrorists from making any move undetected. Biometrics provide a new way to bring terrorists' true identities to light, stripping them of their greatest advantage—remaining unknown. According to an article written in 2009 by S. Magnuson in the National Defense Magazine entitled "Defense Department Under Pressure to Share Biometric Data" the United States has bilateral agreements with other nations aimed at sharing biometric data. To quote that article: 2. System Architecture & Core Working Principles Miller [a consultant to the Office of Homeland Defense and America's security affairs] said the United States has bilateral agreements to share biometric data with about 25 countries. Every time a foreign leader has visited Washington during the last few years, the State Department has made sure they sign such an agreement.
GDPR in the European Union became law in 2018 LGPD in Brazil became law in 2020 Protection of Personal Information Act in South Africa came into force in 2020 Personal Data Protection Act in Sri Lanka implementation started in 2023 Countries using biometrics include Australia, Brazil, Bulgaria, Canada, Cyprus, Greece, China, Gambia, Germany, India, Iraq, Ireland, Israel, Italy, Malaysia, Netherlands, New Zealand, Nigeria, Norway, Pakistan, Poland, South Africa, Saudi Arabia, Tanzania, Turkey, Ukraine, United Arab Emirates, United Kingdom, United States and Venezuela. Among low to middle income countries, roughly 1.2 billion people have already received identification through a biometric identification program.
There are also numerous countries applying biometrics for voter registration and similar electoral purposes. According to the International IDEA's ICTs in Elections Database, some of the countries using (2017) Biometric Voter Registration (BVR) are Armenia, Angola, Bangladesh, Bhutan, Bolivia, Brazil, Burkina Faso, Cambodia, Cameroon, Chad, Colombia, Comoros, Congo (Democratic Republic of), Costa Rica, Ivory Coast, Dominican Republic, Fiji, Gambia, Ghana, Guatemala, India, Iraq, Kenya, Lesotho, Liberia, Malawi, Mali, Mauritania, Mexico, Morocco, Mozambique, Namibia, Nepal, Nicaragua, Nigeria, Panama, Peru, Philippines, Senegal, Sierra Leone, Solomon Islands, Somaliland, Swaziland, Tanzania, Uganda, Uruguay, Venezuela, Yemen, Zambia, and Zimbabwe.
Compromised credentials continue to be the top cause of data breaches. Many online services still use a password as the single factor to authenticate users. In response, some have moved to two-factor authentication (2FA) but have faced user experience challenges and found that weak 2FA options are still vulnerable to phishing attacks. Developers must implement security measures to protect user passwords in transit and at rest. Meanwhile, users must remain ever vigilant to remember their password, rotate it, and ensure it meets complexity and uniqueness requirements. Enterprises and consumer facing services continue to seek a simple, secure, and scalable user authentication experience.
Strong passwords can be difficult to remember, and users often reuse passwords on multiple sites Even properly salted and hashed passwords can be cracked by offline dictionary attacks if database is leaked FIDO2/WebAuthn offers a strong Multi-Factor Authentication (MFA) framework to minimize or replace the use of passwords with scoped public key-based credentials that are resistant to phishing, replay, and server breach attacks. User gestures such as PINs, touch, or biometrics are used to authorize use of FIDO2 credentials.
MFA is a method of granting access to a system only after two or more pieces of evidence have been presented. These pieces of evidence, also known as factors, prove your identity. This could be something you know (secret password or PIN), something you have (mobile phone or security key), or something you are (biometrics: fingerprint or face). YouâIIve probably already used MFA in some form if you have withdrawn money from an ATM.
FIDO2/WebAuthn credentials provide strong authentication that is resistant to phishing, replay, and server breach attacks. Strong authentication is defined as having at least one cryptographically backed factor. FIDO2 provides strong, attested, scoped public key-based credentials for authenticating users. FIDO2/WebAuthn authentication is decentralized. Users are authenticated locally on an authenticator. The online service validates the authentication ceremony was properly conducted before allowing user access. The online service only needs publicly available information to validate the local authentication. This reduces the value of attacking the server because it has no user authentication secrets and user credentials are also not transferable between services.
Attestation becomes important now that authentication is decentralized. The online service must trust that the authenticator reliably conducts FIDO2 ceremonies. FIDO2 provides a mechanism for authenticators to present an attestation statement so that an online service can verify it is a genuine device. FIDO2 credentials can provide MFA by employing user verification authorization gestures. This could be a PIN or biometric, for example. This user verification stays on the authenticator, it is never sent over the network like a password. If MFA is not required, then a simple test of user presence through an authorization gesture, e.g. tap and go, can show that the user gave consent for the credential to be used.
In general, a credential is data that proves a personâIIs identity or qualification. This credential is used to authenticate to an online service, also known as a Relying Party (RP). FIDO2 uses public-key cryptography to authenticate users. An RP-specific credential key pair, i.e., a private key and a public key, is generated on the authenticator. The public key is sent to the RP at registration time. The private key never leaves the authenticator. When the user makes the request to login, the authenticator sends an assertion that proves the user possesses the private key. The RP uses the public key to validate the assertion before allowing the user to login.
FIDO2 introduces the concept of a discoverable credential, which is/are stored on the authenticator instead of encrypted and stored on the server. Discoverable credentials also enable passwordless authentication scenarios, at the expense of consuming limited storage space on the authenticator. FIDO2/WebAuthn credentials with MFA should be used whenever possible, especially when it comes to sensitive data, like your primary email, financial accounts, and health records.
FIDO2 is built on top of two open standards: the Web Authentication API (WebAuthn) and the Client to Authenticator Protocol (CTAP2). The two work together and are required to achieve a strong authentication experience. The earlier FIDO U2F protocol working with external authenticators is now renamed CTAP1 in the FIDO specifications. FIDO2 and WebAuthn are backwards compatible with U2F authenticators.
FIDO2/WebAuthn authentication consists of a registration ceremony and an authentication ceremony. Assuming a user has already created an account with the online service, the user registers one or more authenticators against that identity. The authenticator could be a mobile phone, laptop, or YubiKey. Any authenticator that is compliant with CTAP1 or CTAP2 will work.
During the registration ceremony the authenticator creates a FIDO2 credential by generating a private key and public key. The private key stays in the hardwareâIIs secure element while the public key is given to the online service. Possession of this authenticator in combination with a gesture to unlock the use of the credential is now proof of your identity. Unlike a password which is sent over the network and stored on a remote server, neither the private key nor the gesture ever leave the authenticator. They are not sent over the network nor stored on a remote server. Only the public key is stored by the online service.
Authentication happens locally on the authenticator and is verified by the online service. First, a user will make a request to login. The online service will send the client a challenge, which the client wraps in its client data . Next, the client requests cryptographic proof of user authentication. With the userâIIs consent, the authenticator will return an assertion. This assertion provides evidence that the authenticator is in possession of the private key by signing the client data with the private key. The server then verifies that the client data contains the correct challenge and uses the public key to verify the signature.
Passwordless single factor: FIDO2 discoverable credential (a âIIdiscoverable credentialâII stores user data on the authenticator) In general, a FIDO2/WebAuthn authentication architecture involves a conversation between a computing environment controlled by a Relying Party and one controlled by the user to be authenticated.
The user environment may consist of a client computing device with internal FIDO2 authenticator. The user may also have an external FIDO2 authenticator, such as a YubiKey, which can roam between devices. The authenticator makes credentials, generates cryptographic proof of user authentication, and manages the PIN. The client is the bridge between the authenticator and the RP. It implements CTAP2 and client-side WebAuthn API, and verifies the identity of the RP to prevent phishing attacks. The client could be a browser exposing the WebAuthn API to web applications, or an OS subsystem exposing a platform-specific FIDO API to native applications such as mobile or desktop apps.
The Relying PartyâIIs environment consists conceptually of at least a web server and the server-side portions of a web application, plus a WebAuthn server. The WebAuthn server has a trust store, containing the (public) trust anchors for the attestation of FIDO2 Authenticators. Note: a trust store is needed only if the RP cares about attestation metadata. The identity provider validates user identity and maps a FIDO2 credential public key to a user account during the registration step 3. Software Implementation, Frameworks & Protocols FIDO2 credentials can be generated in hardware devices (e.g. security keys, mobile phones, laptops, etcâI¦) or software, based on policy.
Authentication uses a cryptographic key tied to an authenticator and, optionally, something that the person knows (a PIN) or something that the person is (biometric gesture). PINs and biometric gestures do not roam between authenticators and are not shared with the server; they are stored locally on an authenticator. The userâIIs private key never leaves an authenticator. The authenticating server has a public key that is mapped to the user account during the registration process.
PIN entry, biometric gesture, or touch trigger the authenticator to unlock the private key to cryptographically sign data that is sent to the identity provider in the assertion. This signed data also indicates whether or not a PIN or biometric was used. The authentication request is allowed to proceed after the identity provider verifies the assertion. Biometric authentication represents a significant leap forward in securing and streamlining user access in web applications.
As businesses seek more robust security frameworks, integrating biometric data (such as fingerprints, facial recognition, and voice patterns) provides a compelling solution. This guide dives into the technicalities, benefits, and challenges of deploying biometric authentication in your web applications. Biometric authentication uses unique physical characteristics of individuals to verify their identity. This method offers a higher level of security compared to traditional password-based systems, majorly minimizing risks associated with stolen or weak credentials.
Integrating biometric authentication in banking apps can significantly enhance security. It allows users to access their accounts and perform transactions with the assurance that their identity is securely verified. Biometric data is sensitive, and its handling must be carefully managed to comply with global privacy regulations like the GDPR and HIPAA. Encryption of biometric data, both at rest and in transit, is crucial.
Biometric authentication is generally more secure as it uses unique physiological characteristics that are difficult to replicate or steal, unlike passwords. While biometric systems are highly secure, no system is entirely invulnerable. However, with robust security protocols, the risk can be greatly minimized.
When you configure Multi-Factor Authentication (MFA) to use biometrics as an authentication factor, your users will have to use their face or fingerprint to complete the login transaction. This interaction implies that your users can prove their digital identity by providing: Biometrics are measurable and unique human traits that applications can use to verify a person's identity, such as a person's face or fingerprints.
Biometrics can serve as a secure and convenient authentication factor, making Multi-Factor Authentication (MFA) as easy and fast as possible . The availability of mobile devices capable of reliably measuring human traits has grown exponentially, increasing the popularity of biometric authentication in enterprise and customer applications. Developers enable end-users to use biometrics on web applications by implementing the Web Authentication API (WebAuthn) , which is part of the FIDO2 standard . End-users can register their biometric devices with any application that supports the standard.
When users authenticate with WebAuthn, they can use something they are as an authentication factor, such as their face or fingerprint. Auth0 supports using biometrics to perform MFA. Let's see that in action! You need a device that can use your biometric information for access, such as a mobile device with face recognition or a fingerprint reader.
If you already have an Auth0 account, you can log in to your tenant and continue to the next step. During the sign-up process, you create something called an Auth0 Tenant , representing the product or service to which you are adding authentication. Before you start, it's important to note that biometrics are currently tied to a physical device. For example, if you use your smartphone to log in using its fingerprint reader, you can only use that smartphone to log in that way. In the context of MFA, if a biometric is the only second factor that your users have available to complete the authentication process, they won't be able to log in if they don't have the physical device that registered their biometric.
You can achieve a balance between security and usability by offering your users an alternative MFA factor whenever their device biometrics are unavailable. For that reason, Auth0 requires you to enable at least one other factor before enabling "WebAuthn with FIDO Device Biometrics" as an authentication factor. You are all set up if you have already completed any of our other MFA labs. Otherwise, please complete either the "Enable MFA with SMS" or the "WebAuthn with FIDO Security Keys" lab.
Once you have configured your MFA factor, click the "Back to Multi-factor Authentication" link at the top of the page. Once you are back on the "Multi-factor Authentication" page, scroll past the "Factors" section and locate the "Define policies" section. Recall that an MFA policy determines when Auth0 will prompt your users to provide additional authentication factors to log in successfully. You must define a policy to enforce MFA in your applications.
Looking at the "Require Multi-factor Auth" , you'll notice that "Never" is the default selection. This selection means that Auth0 will never require users to authenticate using an additional factor for any application registered under your Auth0 tenant. For this exercise, select "Always" to always require an additional authentication factor to log in. Then, click the "Save" button. You may see a modal warning you about the possible consequences of always requiring MFA: All new and existing users who are not enrolled in Multi-factor Authentication will be required to enroll using one of the enabled factors the next time they log in. This will apply across all applications within your tenant.
4. Practical Deployment, Analysis & Case Studies The Auth0 Universal Login page should prompt you to use two authentication factors to complete your login—or sign-up: You have effectively set up MFA, reducing the likelihood of many cyber-attacks. It's common for third parties to steal usernames and passwords or programmatically attack user accounts. An additional MFA factor, such as WebAuthn with FIDO Device Biometrics, impedes these violations, protecting the data and privacy of your users.
You can also configure the Auth0 Universal Login to let users authenticate using WebAuthn with Device Biometrics instead of a password . Try it out! Multifactor authentication is increasingly used and recommended by organizations to strengthen the security of authenticating people and protecting data. By requiring more than one method of user identification, the multifactor authentication becomes a more secure and effective alternative to fraud.
In practice, however, the process ends up being limited to identification by what the user knows (passwords, security questions) and what the user has (mobile phone, email). This method may prove inadequate for critical data. For example, if someone gains access to your mobile phone, they will most likely have one of your authentication factors and access to password recovery for multiple accounts (including banks).
With this in mind, it is important to consider a third means of identification: the user's biometrics . Biometric identification is harder to spoof, and when used with multifactor authentication, it strengthens security. In this article, you'll learn how to implement multifactor authentication with biometrics using BioPass ID's Multibiometrics package .
The Multibiometrics API package allows you to build multifactor authentication using more than one biometric option. By using it in your application, you can enjoy the following benefits: Multibiometrics is a Rest API that provides a set of operations for building applications with biometric authentication. The solution is simple and easy to implement, requires minimal knowledge of biometrics on the client's part, and allows implementation at a low cost, in less time and with less effort.
Multibiometrics currently supports two types of biometrics: face and fingerprint. The system provides all the necessary infrastructure to manage the registration, storage, and authentication of identities. This includes the registration, deletion, updating and verification of individuals' biometric data . The platform also provides the entire biometric database infrastructure without additional cost. Customers can also choose to implement their own infrastructure.
Now that you know about multibiometrics, it's time to learn. You can use the BioPass ID documentation to implement the package operation requests. Follow the step-by-step instructions to apply multifactor authentication with multibiometrics: To access and use the Multibiometrics Package operations, you must create an account in the BioPass ID system and generate an application key. This key will be used for all Multibiometrics operations. You can find the step-by-step process for obtaining it in the first section of the article 4 Steps for Integrating a Biometric API into BioPass ID .
The documentation for the Multibiometrics package is available at this link . In the file, you will find a description of the operations already performed, as well as the information needed to use it: On the right side of the documentation, you can see a practical example of how to implement each operation in a programming language. The programming language and the associated library can be set in the Language section at the top left of the tab: The headers required to make the request and the input and output data structures are also provided in the documentation: Please note that the fields marked with double curly brackets will have to be replaced by the programmer.
The input and output structures described in the package documentation are encoded in JSON format. It is therefore possible to automatically convert them to a programming language using an online conversion tool such as JSON2CSharp . This tool can convert to C#, Java, Dart, and Python. With the input and output classes in hand, attention must be paid to communication with the Multibiometrics endpoints. This process is done using strings. Therefore, the input and output objects must be serialized and deserialized, respectively, transforming them into JSON strings (serialization) and objects (deserialization).
In this way, all that remains is to make the necessary adaptations in the codes provided in the documentation to include the input duly filled, with images encoded in base64 string according to the guidelines in the documentation , and with the access key associated with the Ocp-Apim-Subscription-Key header. To implement the process of biometric multifactor authentication with multibiometrics, the application must be able to meet the following requirements: To meet the first two requirements, simply use Multibiometrics' CRUD operations: register , delete , update , and verify . To use them, assign an identifier to the registered individual and enter the biometric images when necessary.
It is worth noting that it is possible to choose the type of biometric to be registered and verified. Depending on the business rule, only facial biometrics may be required for registration/verification. Alternatively, fingerprint biometrics can be verified, or even both if a higher level of security is desired. It is important to be aware of the risk of attempted fraud in this process. While it is difficult to obtain fingerprint images of a specific person, it is relatively easy to obtain facial images from photographs.
To prevent identity theft, it is advisable to use the 2D liveness operation in addition to the CRUD operations. This operation verifies that the face capture is legitimate and detects any fraudulent acts. 5. Performance Evaluation & Extended Technical Observations It should also be noted that for the process to work optimally, the photo analyzed by Liveness 2D must be the same one used in the registration, update, and verification operations. Another important point regarding the implementation of the process is the protection of the access key. It is necessary to avoid direct requests to Multibiometrics in the same application that the user is using.
Finally, we need to discuss a fundamental issue: the collection of an individual's biometrics. For biometric analysis to work properly, it is necessary to ensure that the biometrics are captured at a minimum acceptable quality. In addition, fingerprint capture is highly dependent on the equipment used. For this reason, different implementations are recommended for different sensors.
However, the importance of the BioPass ID capture SDKs stands out. The solution is designed to support the use of the multibiometrics package and provide a customized, user-friendly interface. For more information about the Face Capture SDK, see the Face SDK article. As for fingerprint capture, you can visit the official Fingerprint SDK page, which provides technology for capturing fingerprints from a mobile phone camera.
In this article, we explained how multibiometric analysis can be included in the multifactor authentication process to increase the security of applications using the BioPass ID multibiometric technology. Additionally, we described how to implement multibiometric operations and what operations must be performed for the process to operate properly. To wrap things up, we introduced two products that help with the biometrics capture process, a requirement for using the Multibiometrics package.
If you have any questions, please check the FAQ on our support page and contact our team via chat. Learn how BioPass ID's Fingerprint SDK provides advanced biometric authentication, flexible integration, and maximum security for businesses. Check out the step-by-step guide to obtaining high-quality biometric images using the BioPass ID Capture SDK.
Learn what the AMIS system is and understand the role of the ABIS system in biometric identification. Multifactor authentication increases security in digital environments. Discover BioPass ID's multibiometrics for data protection. Understand the match between biometrics, using the BioPass ID feature set and the Postman platform to make API requests. WebAuthn (Web Authentication API) fundamentally redefines biometric security by shifting from client-side template matching to server-side verification of asymmetric cryptographic proofs. This architecture eliminates the transmission of raw biometric data and prevents replay attacks by ensuring that biometric sensors unlock private keys rather than sending secret templates.
In this article, Part 5 of the Passwordless & Next-Gen Authentication Series, we examine how the protocol binds cryptographic keys to specific domains, enabling secure logins via Face ID, Touch ID, and Windows Hello without ever exposing the private key to the web server or the network. The security of the WebAuthn system begins during the registration phase, where a unique key pair is generated for a specific relying party (RP). When a user attempts to set up biometric login, the browser initiates the process by calling the navigator.credentials.create() method. The server responds with a PublicKeyCredentialCreationOptions object containing a random challenge (nonce) and the RP ID, which is typically the domain name.
The browser then queries the operating system. On macOS, the OS intercepts this request and prompts the user for Face ID; on Windows, it triggers Windows Hello. Crucially, the OS generates a new key pair specifically for this RP ID. The public key is returned to the browser, while the private key is stored securely in the hardware security module, such as the TPM, Secure Enclave, or Trusted Platform Module. The browser then packages this public key along with an attestationObject and sends it back to the server.
The attestationObject is critical because it contains a signature from the authenticator proving that the key was generated by a genuine device and not a software emulator. The server stores this public key. If a hacker steals this public key, they cannot log in because they do not possess the private key. Furthermore, the key is bound to the RP ID. If the same key pair is extracted and attempted on a different domain, the authentication will fail because the RP ID hash in the authenticatorData will not match the one expected by the server.
During login, the mechanism shifts to a challenge-response protocol. A user visits the application and enters their username. The server retrieves the user's stored public key and generates a new random challenge, sending it to the client via navigator.credentials.get() . The browser again invokes the OS biometric prompt. When the user places their finger on the sensor or looks at the camera, the OS performs two checks: If both checks pass, the OS signs the challenge using the private key. The resulting signature is returned to the browser, which forwards it to the server. The server does not need to know the user's biometric data. It simply uses the stored public key to verify the signature against the challenge it sent. If the signature is valid, the user is authenticated.
This flow ensures that the private key is never exposed to the browser's JavaScript or the network. Even if the website is compromised, the attacker cannot extract the private key or replay the signature because the challenge is unique to every session. The authenticatorData within the assertion also includes flags indicating whether a biometric was used ( UV flag) and whether the user was present ( UP flag).
To understand why this is resistant to phishing, one must look at the authenticatorData . This binary blob is part of the assertion and is signed by the private key. It contains: If a phishing site tries to trick a user into logging in, the browser detects the domain mismatch. The authenticatorData will contain the phishing site's RP ID hash. When the server for the legitimate site receives this assertion, it expects a signature over the legitimate site's challenge and RP ID hash. The verification will fail because the signature was created over a different context. This mechanism effectively neutralizes the primary vector for credential theft: the phishing site cannot trick the authenticator into signing a request for the wrong domain.
The shift to WebAuthn-based biometrics addresses the fundamental flaws of password-based systems. Passwords are susceptible to brute-force attacks, reuse across sites, and social engineering. Biometric data itself is not a password; it is a key to unlock a cryptographic key. This separation means that even if a database is breached, the attacker only gets public keys, which are useless without the private key.
However, this architecture introduces specific tradeoffs. Recovery becomes more complex. If a user loses their device, the private key is lost. Unlike passwords, there is no "forgot password" link that resets a biometric credential. The system relies on backup methods, such as recovery codes or multiple registered authenticators. Additionally, the reliance on the operating system means that browser compatibility and OS updates can occasionally introduce friction. For instance, older versions of browsers or operating systems might not support the latest FIDO2 specifications, requiring fallback mechanisms.
From a protocol perspective, the FIDO2 standard is a composite of two distinct specifications. The FIDO Alliance defines the CTAP (Client to Authenticator Protocol), which governs the communication between the authenticator (e.g., a fingerprint sensor) and the client software. The W3C defines the WebAuthn API, which serves as the interface between the client software (browser) and the web application. Together, these standards ensure that a Touch ID sensor on an iPhone works identically to a Windows Hello fingerprint reader on a laptop. This standardization prevents vendor lock-in and ensures that the security properties—specifically the isolation of the private key and the domain binding—are consistent across the ecosystem.
Implementing WebAuthn biometrics requires navigating several architectural pitfalls that can compromise security or usability. For advanced engineering teams, adopting WebAuthn biometrics involves strategic considerations beyond simple API integration. Q: Can biometric data be stolen from the server? A: No. The server never receives or stores the biometric data. It only stores the public key and the attestation object. The biometric verification happens locally on the device's secure hardware.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Multi-factor%20authentication • https://en.wikipedia.org/wiki/Authentication • https://en.wikipedia.org/wiki/Biometrics • https://developers.yubico.com/WebAuthn/WebAuthn_Developer_Guide/index.html • https://www.techidevs.com/articles/biometric-authentication-in-web-applications • https://developer.auth0.com/resources/labs/authentication/webauthn-with-biometrics • https://www.biopassid.com/post/multifactor-authentication-data-security • https://ashishsrivastav.com/blog/biometric-authentication-web-applications
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Biometric Multi Factor Authentication Web Application.
[*] Initializing Burp Suite Spider & Vulnerability Engine for Biometric Multi Factor Authentication Web Application... [✓] Burp Extender / Macro Automation Hook Synced ──────────────────────────────────────────────────────────────────────── [11:42:01.104] AUDIT Crawled dynamic endpoints | Injecting input vectors [11:42:01.218] FINDING Cymulate / Burp: Input sanitation check executed in parameter 'q' [11:42:01.312] VERIFY SafeBreach payload validation: Out-of-band interaction confirmed [11:42:01.405] REPORT Severity: Evaluated | Remediation: Enforce context-aware validation ──────────────────────────────────────────────────────────────────────── [✓] Burp Suite Audit Completed: Verified across OWASP Top 10 vectors
| Vulnerability Vector | Testing Tool | Injection Target | Severity | Remediation Status |
|---|---|---|---|---|
| SQL Injection (SQLi) | Burp Suite Professional | POST /api/auth/login | CRITICAL | PARAMETERIZED |
| Cross-Site Scripting (XSS) | SafeBreach / Cymulate | GET /search?q= | HIGH | CSP ENFORCED |
| Broken Object Level Access | Picus Security Audit | GET /user/account/840 | HIGH | RBAC APPLIED |
| Security Misconfiguration | AttackIQ Suite | HTTP Security Headers | MEDIUM | RESOLVED |