Complete Technical Paper Content — Blockchain Based Decentralized Public Key Infrastructure
Overview & System Context
Blockchain Based Decentralized Public Key Infrastructure: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~7383 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Decentralized finance (often stylized as DeFi) provides financial instruments and services through smart contracts on a programmable, permissionless blockchain. This approach reduces the need for intermediaries such as brokerages, exchanges, or banks. DeFi platforms enable users to lend or borrow funds, speculate on asset price movements using derivatives, trade cryptocurrencies, insure against risks, and earn interest in savings-like accounts. The DeFi ecosystem is built on a layered architecture and highly composable building blocks. While some applications offer high interest rates, they carry high risks. Coding errors and hacks are a common challenge in DeFi. DeFi protocols exhibit varying degrees of decentralization, with truly decentralized protocols potentially acting as neutral infrastructure, while false decentralization leaves protocols open to manipulation and fraud or to being regulated as financial intermediaries. A core principle of DeFi is its accessibility. By operating on public blockchains, DeFi applications (commonly referred to as "dApps") enable users from across the globe to access financial services without the need for a centralized authority or compliance with traditional Know Your Customer (KYC) and Anti-Money Laundering (AML) regulations. DeFi also introduces programmability and composability to finance. Developers can create interoperable financial products by combining different DeFi protocols like building blocks, a concept often referred to as "money Legos".
Decentralized exchanges (abbreviated DEXs) are alternative payment ecosystems that use new protocols for financial transactions. They emerged within decentralized finance (DeFi), a sector of blockchain technology and fintech. Centralized exchanges (CEXs), DEXs and DEX aggregators are all built on a multi-layered DeFi architecture, with each layer serving a well-defined purpose. (See Figure: Multi-layered Architecture of the DeFi Stack). While they share common components of the first four layers, such as the Settlement layer, Asset layer, Protocol layer and Application layer, DEX aggregators have an additional component or Aggregator layer, which allows them to connect and interact with other DEXs via smart contracts. The Ethereum blockchain popularized smart contracts, which are the basis of DeFi, in 2017. Other blockchains have since implemented smart contracts. Alternative Layer 1 protocols, such as Radix, have been developed utilizing sharded consensus mechanisms to attempt to resolve scalability issues inherent in earlier blockchains. As of 2021, MakerDAO was a prominent lending DeFi platform based on a stablecoin that was established in 2017. It allowed users to borrow DAI, a token pegged to the US dollar. Through a set of smart contracts that govern the loan, repayment, and liquidation processes, MakerDAO aimed to maintain the stable value of DAI in a decentralized and autonomous manner. In September 2024, MakerDAO rebranded as Sky, and its stablecoin DAI was renamed USDS. In June 2020, Compound Finance, a decentralized finance protocol enabling users to lend or borrow cryptocurrency assets and which provides typical interest payments to lenders, started rewarding lenders and borrowers with a cryptocurrency called Comp. This token, which is used for running Compound, can also be traded on cryptocurrency exchanges. Other platforms followed suit, leading to stacked investment opportunities known as "yield farming" or "liquidity mining", where speculators shift cryptocurrency assets between pools in a platform and between platforms to maximize their total yield, which includes not only interest and fees but also the value of additional tokens received as rewards. In July 2020, The Washington Post described decentralized finance techniques and the risks involved. In September 2020, Bloomberg said that DeFi made up two-thirds of the cryptocurrency market in terms of price changes and that DeFi collateral levels had reached $9 billion. Ethereum saw a rise in developers during 2020 due to the increased interest in DeFi. DeFi has attracted venture capitalists such as Andreessen Horowitz and Michael Novogratz. The Economist regarded the future of digital finance in 2022 as a "three-way fight" between: Big Tech, such as Facebook with its digital wallet; "big rich countries" that have been testing their own digital currencies; and software developers "building all sorts of applications" to decentralize finance. Handling the risks presented by crypto-assets already valued at $2.5 trillion was a particular challenge for US regulators. The evolution of Decentralized Finance (DeFi) began with Bitcoin in 2009 and matured with Ethereum’s 2015 launch, which introduced smart contracts and enabled decentralized applications. By 2021, DeFi protocols such as MakerDAO, Compound, Aave, and Uniswap had driven total value locked (TVL) to over $180 billion. The 2022 crypto market crash, which followed events like the collapse of Terra/LUNA and FTX, exposed critical vulnerabilities in the DeFi space and triggered a downturn. In 2023, DeFi began recovering. A key trend was the tokenization of real-world assets (RWA) such as treasury bills, real estate, and carbon credits. Platforms like MakerDAO and Centrifuge enabled institutional investors to access on-chain yield tied to off-chain assets. Layer 2 scaling solutions such as Arbitrum and Optimism also gained traction, reducing transaction fees and increasing throughput on top of Ethereum. This period also marked the rise of intent-based DeFi, allowing users to specify desired outcomes, with protocols handling transaction logic (Bankless, 2023). In 2024, regulatory developments shaped DeFi's evolution. The European Union’s MiCA framework (Markets in Crypto-Assets Regulation) came into effect, impacting stablecoin issuers and custodial services. In response, many DeFi projects began adopting hybrid models, combining decentralized architecture with off-chain compliance layers to navigate legal requirements.
Meanwhile, interoperability improved with the deployment of cross-chain bridges like Wormhole V2 and Chainlink CCIP, enabling liquidity to flow between Ethereum, Solana, Avalanche, and other ecosystems. A blockchain is a distributed ledger with growing lists of records (blocks) that are securely linked together via cryptographic hashes. Each block contains a cryptographic hash of the previous block, a timestamp, and transaction data (generally represented as a Merkle tree, where data nodes are represented by leaves). Since each block contains information about the previous block, they effectively form a chain (viz. linked list data structure), with each additional block linking to the ones before it. Consequently, blockchain transactions are resistant to alteration because, once recorded, the data in any given block cannot be changed retroactively without altering all subsequent blocks and obtaining network consensus to accept these changes. Blockchains are typically managed by a peer-to-peer (P2P) computer network for use as a public distributed ledger, where nodes collectively adhere to a consensus algorithm protocol to add and validate new transaction blocks.
Although blockchain records are not unalterable, since blockchain forks are possible, blockchains may be considered secure by design and exemplify a distributed computing system with high Byzantine fault tolerance. A blockchain was created by a person (or group of people) using the name (or pseudonym) Satoshi Nakamoto in 2008 to serve as the public distributed ledger for bitcoin cryptocurrency transactions, based on previous work by Stuart Haber, W. Scott Stornetta, and Dave Bayer.
The implementation of the blockchain within bitcoin made it the first digital currency to solve the double-spending problem without the need for a trusted authority or central server. The bitcoin design has inspired other applications and blockchains that are readable by the public and are widely used by cryptocurrencies. The blockchain may be considered a type of payment rail. Private blockchains have been proposed for business use. Computerworld called the marketing of such privatized blockchains without a proper security model "snake oil"; however, others have argued that permissioned blockchains, if carefully designed, may be more decentralized and therefore more secure in practice than permissionless ones.
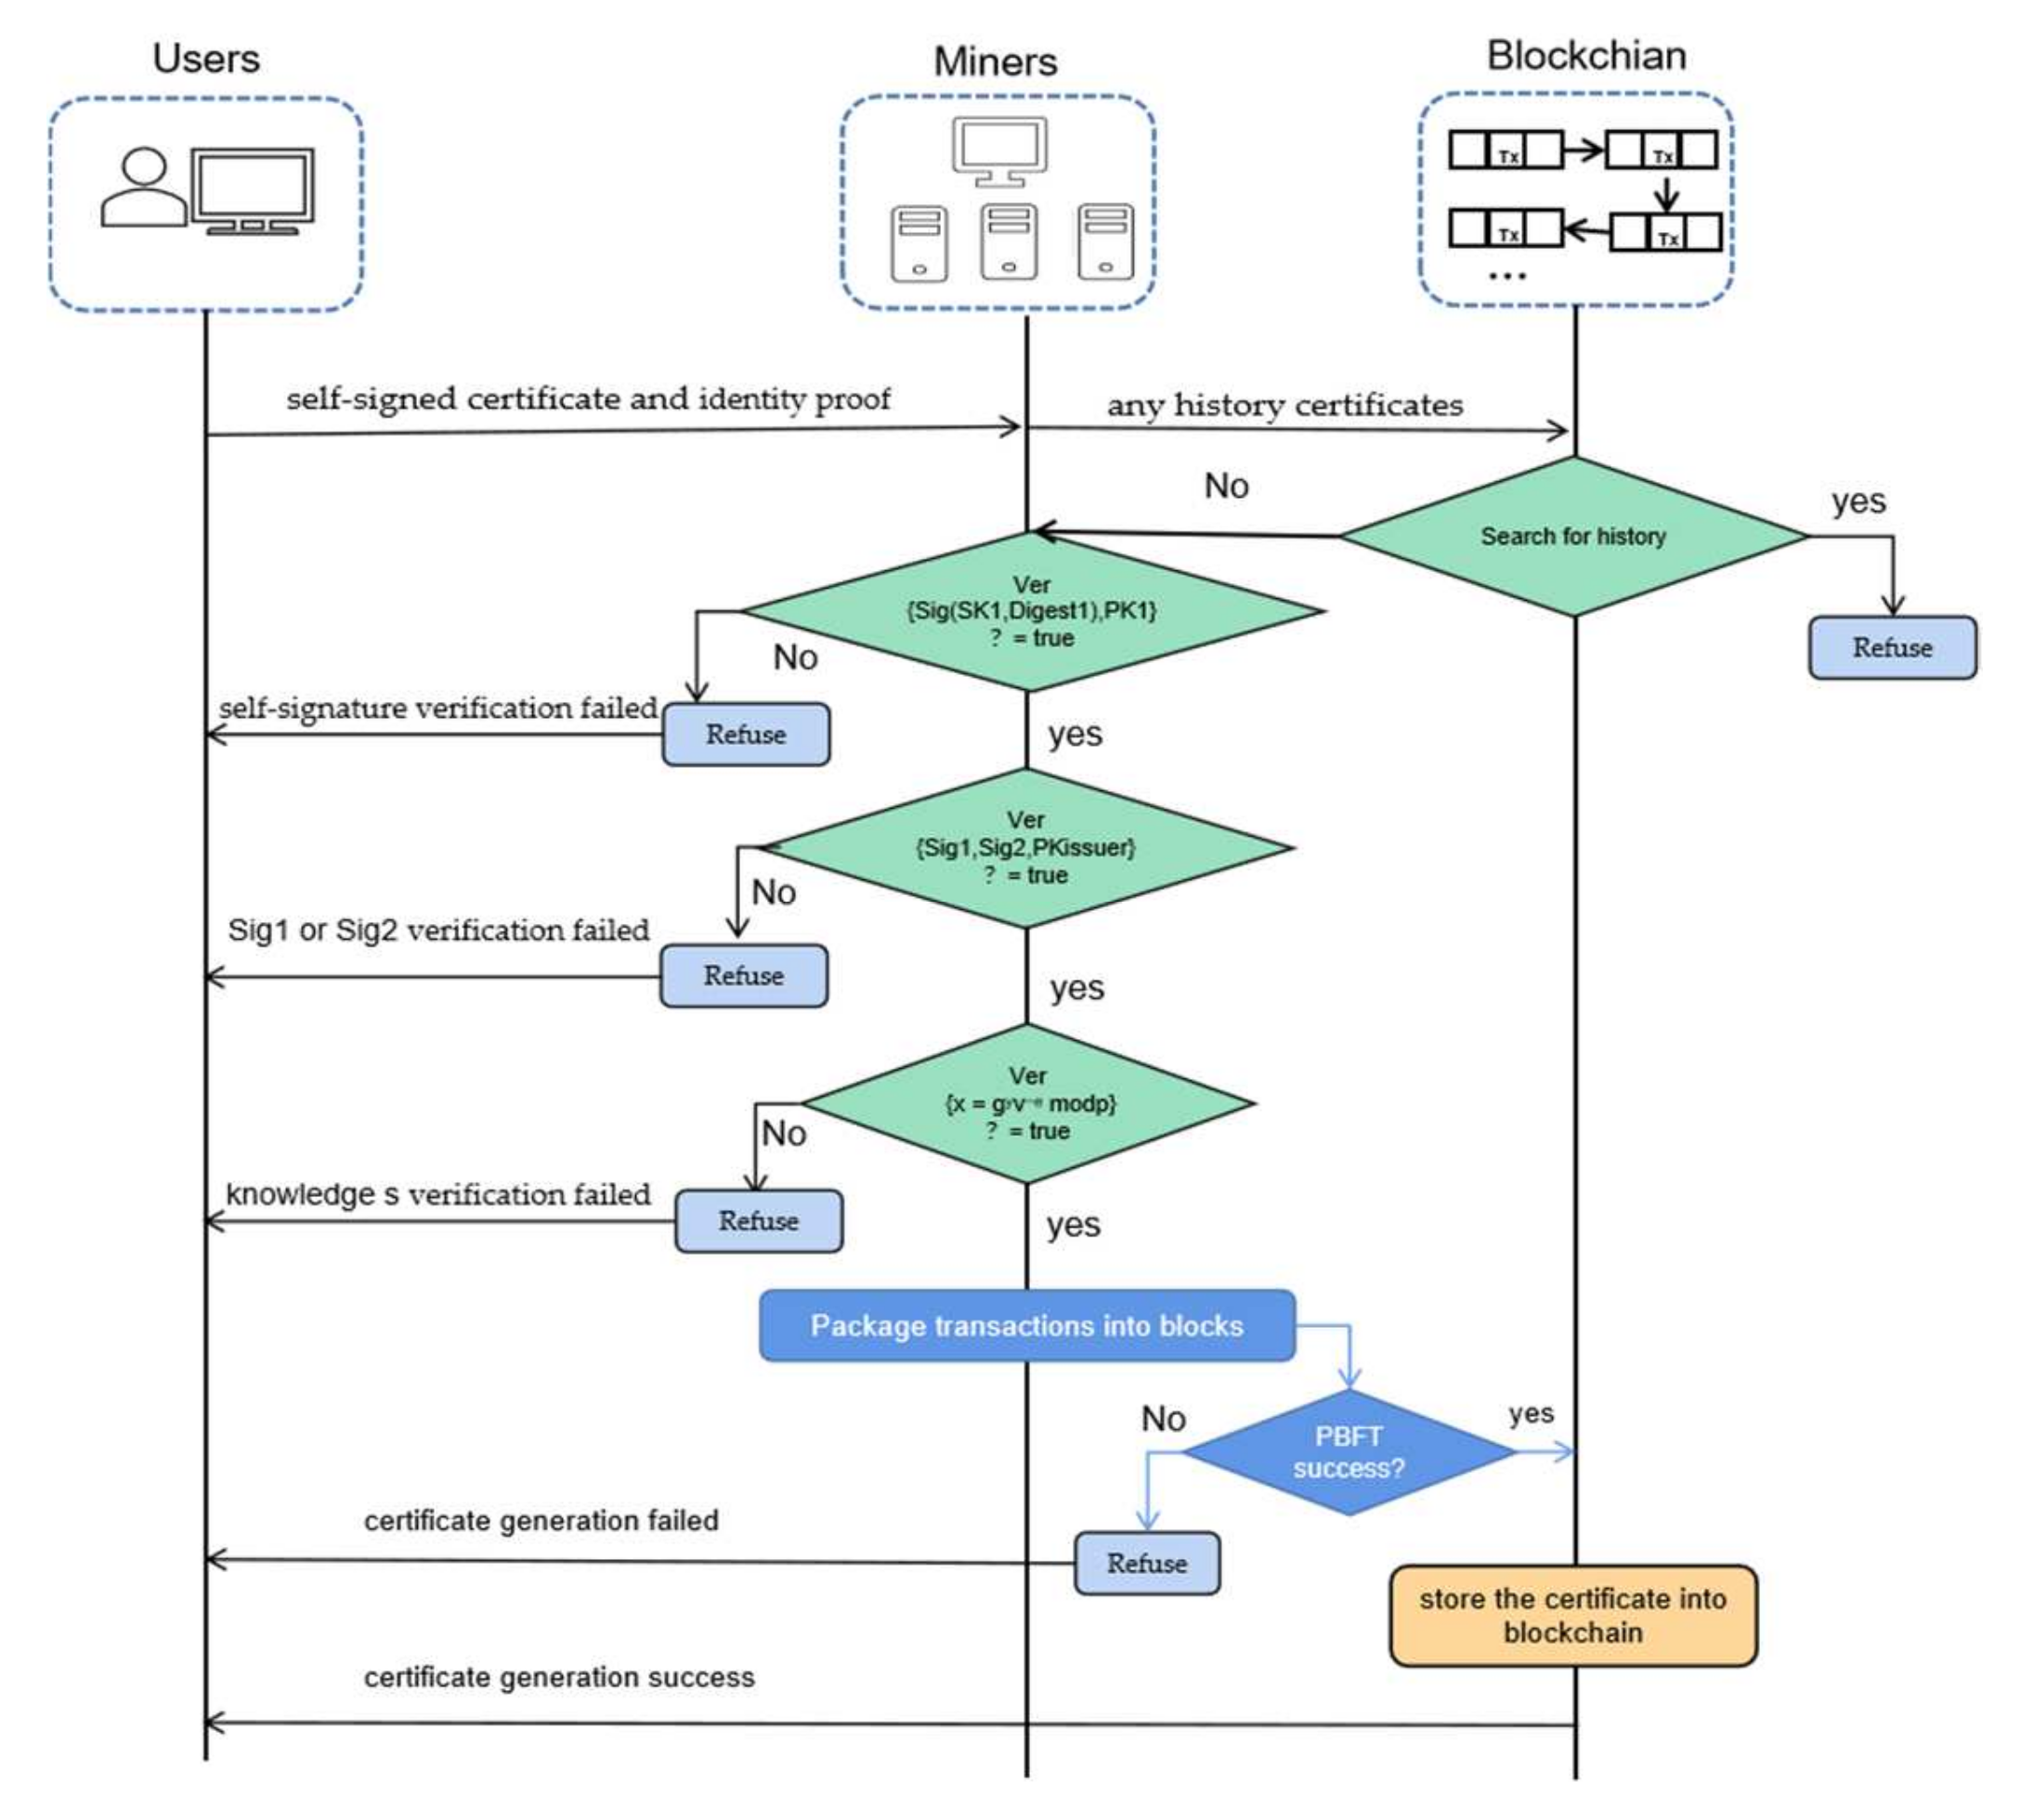
A blockchain is a decentralized, distributed, and often public, digital ledger consisting of records called blocks that are used to record transactions across many computers so that any involved block cannot be altered retroactively, without the alteration of all subsequent blocks. This allows the participants to verify and audit transactions independently and relatively inexpensively. A blockchain database is managed autonomously using a peer-to-peer network and a distributed timestamping server. They are authenticated by mass collaboration powered by collective self-interests. Such a design facilitates robust workflow where participants' uncertainty regarding data security is marginal. The use of a blockchain removes the characteristic of infinite reproducibility from a digital asset. It confirms that each unit of value was transferred only once, solving the long-standing problem of double-spending. A blockchain has been described as a value-exchange protocol. Logically, a blockchain can be seen as consisting of several layers: Figure 1: A Blockchain-Based Decentralized Public Key Infrastructure for ...
infrastructure (hardware) networking (node discovery, information propagation and verification) consensus (proof of work, proof of stake) data (blocks, transactions) application (smart contracts/decentralized applications, if applicable) Permissioned blockchains use an access control layer to govern who has access to the network. It has been argued that permissioned blockchains can guarantee a certain level of decentralization, if carefully designed, as opposed to permissionless blockchains, which are often centralized in practice.
Blockchain-based smart contracts are contracts that can be partially or fully executed or enforced without human interaction. One of the main objectives of a smart contract is automated escrow. A key feature of smart contracts is that they do not need a trusted third party (such as a trustee) to act as an intermediary between contracting entities — the blockchain network executes the contract on its own. This may reduce friction between entities when transferring value and could subsequently open the door to a higher level of transaction automation. An IMF staff discussion from 2018 reported that smart contracts based on blockchain technology might reduce moral hazards and optimize the use of contracts in general, but "no viable smart contract systems have yet emerged." Due to the lack of widespread use, their legal status was unclear.
Blockchain technology, such as cryptocurrencies and non-fungible tokens (NFTs), has been used in video games for monetization. Many live-service games offer in-game customization options, such as character skins or other in-game items, which the players can earn and trade with other players using in-game currency. Some games also allow for trading of virtual items using real-world currency, but this may be illegal in some countries where video games are seen as akin to gambling, and has led to gray market issues such as skin gambling, and thus publishers typically have shied away from allowing players to earn real-world funds from games. Blockchain games typically allow players to trade these in-game items for cryptocurrency, which can then be exchanged for money. The first known game to use blockchain technologies was CryptoKitties, launched in November 2017, where the player would purchase NFTs with Ethereum cryptocurrency, each NFT consisting of a virtual pet that the player could breed with others to create offspring with combined traits as new NFTs. The game made headlines in December 2017 when one virtual pet sold for more than US$100,000. CryptoKitties also illustrated scalability problems for games on Ethereum when it created significant congestion on the Ethereum network in early 2018 with approximately 30% of all Ethereum transactions being for the game. By the early 2020s, there had not been a breakout success in video games using blockchain, as these games tend to focus on using blockchain for speculation instead of more traditional forms of gameplay, which offers limited appeal to most players. Such games also represent a high risk to investors as their revenues can be difficult to predict. However, limited successes of some games, such as Axie Infinity during the COVID-19 pandemic, and corporate plans towards metaverse content, refueled interest in the area of GameFi, a term describing the intersection of video games and financing typically backed by blockchain currency, in the second half of 2021.
Several major publishers, including Ubisoft, Electronic Arts, and Take Two Interactive, have stated that blockchain and NFT-based games are under serious consideration for their companies in the future. In October 2021, Valve Corporation banned blockchain games, including those using cryptocurrency and NFTs, from being hosted on its Steam digital storefront service, which is widely used for personal computer gaming, claiming that this was an extension of their policy banning games that offered in-game items with real-world value. Valve's prior history with gambling, specifically skin gambling, was speculated to be a factor in the decision to ban blockchain games. Journalists and players responded positively to Valve's decision as blockchain and NFT games have a reputation for scams and fraud among most PC gamers, and Epic Games, which runs the Epic Games Store in competition to Steam, said that they would be open to accepted blockchain games in the wake of Valve's refusal.
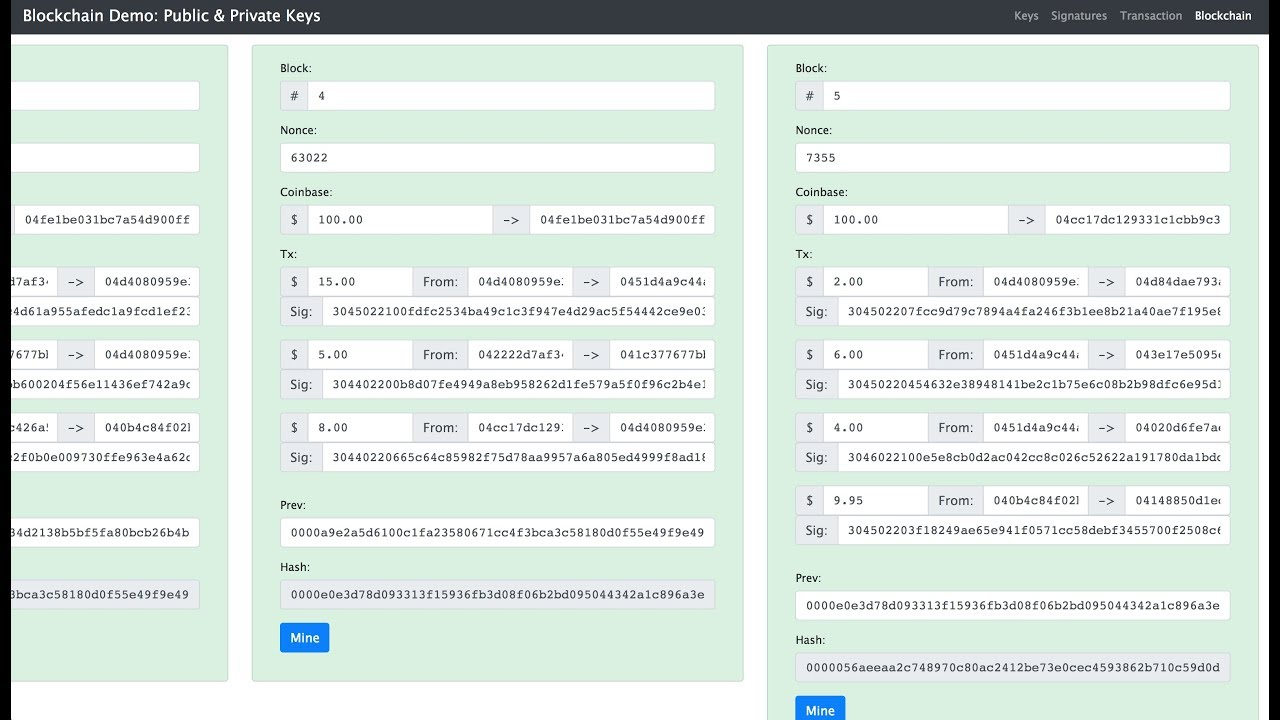
Figure 2: Blockchain 101 - Part 2 - Public / Private Keys and Signing - YouTube There have been several different efforts to employ blockchains in supply chain management. Precious commodities mining — Blockchain technology has been used for tracking the origins of gemstones and other precious commodities. In 2016, The Wall Street Journal reported that the blockchain technology company Everledger was partnering with IBM's blockchain-based tracking service to trace the origin of diamonds to ensure that they were ethically mined. As of 2019, the Diamond Trading Company (DTC) has been involved in building a diamond trading supply chain product called Tracer. Food supply — As of 2018, Walmart and IBM were running a trial to use a blockchain-backed system for supply chain monitoring for lettuce and spinach – all nodes of the blockchain were administered by Walmart and located on the IBM cloud. Fashion industry — There is an opaque relationship between brands, distributors, and customers in the fashion industry, which prevents the sustainable and stable development of the fashion industry. Blockchain could make this information transparent, assisting sustainable development of the industry. Motor vehicles — Mercedes-Benz and partner Icertis developed a blockchain prototype used to facilitate consistent documentation of contracts along the supply chain so that the ethical standards and contractual obligations required of its direct suppliers can be passed on to second tier suppliers and beyond. In another project, the company uses blockchain technology to track the emissions of climate-relevant gases and the amount of secondary material along the supply chain for its battery cell manufacturers.
Blockchain technology can be used to create a permanent, public, transparent ledger system for compiling data on sales, tracking digital use and payments to content creators, such as wireless users or musicians. The Gartner 2019 CIO Survey reported 2% of higher education respondents had launched blockchain projects and another 18% were planning academic projects in the next 24 months. In 2017, IBM partnered with ASCAP and PRS for Music to adopt blockchain technology in music distribution. Imogen Heap's Mycelia service has also been proposed as a blockchain-based alternative "that gives artists more control over how their songs and associated data circulate among fans and other musicians." New distribution methods are available for the insurance industry such as peer-to-peer insurance, parametric insurance and microinsurance following the adoption of blockchain. The sharing economy and IoT are also set to benefit from blockchains because they involve many collaborating peers. The use of blockchain in libraries is being studied with a grant from the U.S. Institute of Museum and Library Services. Other blockchain designs include Hyperledger, a collaborative effort from the Linux Foundation to support blockchain-based distributed ledgers, with projects under this initiative including Hyperledger Burrow (by Monax) and Hyperledger Fabric (spearheaded by IBM). Another is Quorum, a permissioned private blockchain by JPMorgan Chase with private storage, used for contract applications. Oracle introduced a blockchain table feature in its Oracle 21c database.
Blockchain is also being used in peer-to-peer energy trading. Blockchain and distributed ledger technologies have been investigated for managing access permissions, consent, provenance and audit trails in health care. A 2026 scoping review of 892 studies found that most involved prototypes or simulated evaluations, while evidence of sustained real-world implementation remained limited. Lightweight blockchains, or simplified blockchains, are more suitable for internet of things (IoT) applications than conventional blockchains. One experiment suggested that a lightweight blockchain-based network could accommodate up to 1.34 million authentication processes every second, which could be sufficient for resource-constrained IoT networks. Blockchain could be used in detecting counterfeits by associating unique identifiers to products, documents and shipments, and storing records associated with transactions that cannot be forged or altered. It is however argued that blockchain technology needs to be supplemented with technologies that provide a strong binding between physical objects and blockchain systems, as well as provisions for content creator verification ala KYC standards.
The EUIPO established an Anti-Counterfeiting Blockathon Forum, with the objective of "defining, piloting and implementing" an anti-counterfeiting infrastructure at the European level. The Dutch Standardisation organisation NEN uses blockchain together with QR Codes to authenticate certificates. Beijing and Shanghai are among the cities designated by China to trial blockchain applications as January 30, 2022. In Chinese legal proceedings, blockchain technology was first accepted as a method for authenticating internet evidence by the Hangzhou Internet Court in 2019 and has since been accepted by other Chinese courts.
In October 2014, the MIT Bitcoin Club, with funding from MIT alumni, provided undergraduate students at the Massachusetts Institute of Technology access to $100 of bitcoin. The adoption rates, as studied by Catalini and Tucker (2016), revealed that when people who typically adopt technologies early are given delayed access, they tend to reject the technology. Many universities have founded departments focusing on crypto and blockchain, including MIT, in 2017. In the same year, Edinburgh became "one of the first big European universities to launch a blockchain course", according to the Financial Times.
Figure 3: Blockchain platform UI redesign :: Behance The need for internal audits to provide effective oversight of organizational efficiency will require a change in the way that information is accessed in new formats. Blockchain adoption requires a framework to identify the risk of exposure associated with transactions using blockchain. The Institute of Internal Auditors has identified the need for internal auditors to address this transformational technology. New methods are required to develop audit plans that identify threats and risks. The Internal Audit Foundation study, Blockchain and Internal Audit, assesses these factors. The American Institute of Certified Public Accountants has outlined new roles for auditors as a result of blockchain.
In September 2015, the first peer-reviewed academic journal dedicated to cryptocurrency and blockchain technology research, Ledger, was announced. The inaugural issue was published in December 2016. The journal covers aspects of mathematics, computer science, engineering, law, economics and philosophy that relate to cryptocurrencies. The journal encourages authors to digitally sign a file hash of submitted papers, which are then timestamped into the bitcoin blockchain.
Authors are also asked to include a personal bitcoin address on the first page of their papers for non-repudiation purposes. Changelog – a record of all notable changes made to a project Checklist – an informational aid used to reduce failure Economics of digitization Git – a version control system where the commit hash value depends on the previous commit hash value, also with Merkle tree inside List of blockchains Privacy and blockchain Real-World Assets Version control – a record of all changes (mostly of software project) in a form of a graph A decentralized identifier (DID) is a type of globally unique identifier that enables an entity to be identified in a manner that is verifiable, persistent (as long as the DID controller desires), and does not require the use of a centralized registry. DIDs enable a new model of decentralized digital identity that is often referred to as a self-sovereign identity (SSI). This emerging model of digital identity, based on DIDs and SSIs, puts users in full control of their identity data and addresses key limitations of centralized and federated identity providers, including security vulnerabilities, large-scale data breaches, limited privacy protections, and insufficient user control. The DIDs are an important component of decentralized web applications. A decentralized identity management system based on Decentralized Identifiers and Self-Sovereign Identity principles, usually starts from a reference architecture involving Issuers, Holders, and Verifiers, with digital wallets or agents acting on behalf of identity subjects, and a specific identity infrastructure that supports issuance, validation and revocation of credentials.
The name of the DID method (which must appear between the first and second colon, e.g., did:example:). The structure of the unique identifier that must follow the second colon. The technical specifications for how a DID resolver can apply the CRUD operations to create, read, update, and deactivate a DID document using that method. The W3C DID Working Group maintains a registry of DID methods.
Step-by-step guide to replacing traditional PKI with blockchain-anchored DPKI using DIDs as certificate roots. Includes key rotation policies, recovery mechanisms without custodians, and certificate transparency logs anchored to Ethereum. Certificate Authority breaches at DigiNotar and WoSign exposed fundamental flaws in traditional PKI. Decentralized Public Key Infrastructure replaces single points of failure with blockchain-anchored DIDs, enabling autonomous key rotation, cryptographic recovery, and transparent audit trails.
Traditional PKI depends entirely on Certificate Authorities acting as trusted third parties. When a CA is compromised, every certificate it issued becomes suspect. The 2011 DigiNotar breach allowed attackers to issue fraudulent certificates for Google, Yahoo, and Mozilla, enabling man-in-the-middle attacks against 300,000 Iranian Gmail users. In 2016, WoSign was found backdating SHA-1 certificates and mis-issuing certificates for domains they did not control, leading Mozilla and Google to permanently distrust their root certificates. These are not edge cases. They are the predictable failure mode of centralized trust.
The core problem is structural: a CA can issue a certificate for any domain without the domain owner's consent. This capability is a feature of the Web PKI design, not a bug. Every CA in the root store, currently over 140 organizations across 50+ countries, holds the power to compromise any TLS connection. The CA/Browser Forum baseline requirements add procedural controls, but they cannot eliminate the risk that a nation-state adversary or insider threat will compromise a CA's signing keys.
Certificate Transparency logs, introduced in 2013, provide post-hoc detection but not prevention. Decentralized PKI (DPKI) replaces the CA hierarchy with a blockchain-anchored identity layer. Instead of a CA signing a certificate binding a domain to a public key, the domain owner registers a W3C Decentralized Identifier (DID) on a blockchain like Ethereum. The DID document contains the domain's current public keys and service endpoints. When a client connects, it resolves the DID from the blockchain, fetches the associated DID document, and verifies the server's key directly against the on-chain record. No third party can issue a fraudulent binding because only the DID controller, proven by a blockchain transaction, can update the DID document.
2. System Architecture & Core Working Principles Key rotation in DPKI is autonomous and cryptographically enforced. In traditional PKI, rotating a compromised certificate requires the CA to issue a new one and revoke the old via CRL or OCSP, processes that fail open if the revocation infrastructure is unreachable. In DPKI, the domain owner submits a transaction updating the DID document's verificationMethod array. The old key is invalidated at the protocol level once the transaction confirms. Clients can verify the rotation by checking the blockchain state, eliminating reliance on revocation checking infrastructure that studies show fails 30-40% of the time in practice.
Recovery without custodians is another structural advantage. Traditional PKI offers no native recovery mechanism. If a server's private key is lost, the operator must re-key through the CA, proving domain control again. DPKI supports social recovery and threshold recovery directly in the DID architecture. A DID document can specify a set of recovery guardians, each holding a share of a recovery key generated via Shamir Secret Sharing. If the primary key is lost, a threshold of guardians can authorize a DID document update to rotate to a new key. No CA, no escrow agent, no single party holds the power to recover or compromise the identity.
The audit trail in DPKI is inherent to the blockchain. Every key rotation, DID document update, and delegation change is recorded as an immutable transaction with a timestamp and sender address. Security teams can monitor these events in real time, detecting unauthorized changes within seconds rather than waiting for Certificate Transparency log audits that operate on hour-plus delays. For organizations subject to compliance requirements like SOC 2 or ISO 27001, this provides cryptographic proof of key lifecycle management without relying on CA-provided audit reports that may themselves be compromised.
Decentralized Public Key Infrastructure replaces centralized Certificate Authorities with four composable primitives anchored to a blockchain. Each component addresses a specific failure mode of traditional PKI: single points of compromise, opaque revocation, and custodial key recovery. Replace X.509 hierarchical trust chains with DID documents controlled by the entity they identify. A DID like did:ethr:0x...
resolves to a JSON document containing public keys and service endpoints, eliminating the need for a root CA. Key material lives on-chain or in verifiable data registries. Compromise of a single CA no longer cascades across the entire trust fabric. Traditional Certificate Transparency (CT) logs rely on centralized log operators. DPKI anchors Merkle root commitments to Ethereum or similar chains, creating an immutable, censorship-resistant audit trail.
This mirrors RFC 6962 CT architecture but replaces the gossip layer with on-chain finality. A rogue CA cannot split-view the log because the chain provides a single source of truth. CRLs and OCSP responders introduce latency and privacy leaks. DPKI uses StatusList2021 bitstring registries or smart contract revocation maps that verifiers query directly.
Revocation becomes a single sstore operation. No OCSP stapling, no CRL distribution points, no responder infrastructure to maintain. DPKI eliminates custodial key escrow by distributing recovery authority across a guardian network . A user designates 3-5 guardians who can collectively authorize key rotation after a time-locked delay.
Argent and Loopring wallets use variants of this pattern. The guardian set can include hardware wallets, friends, or institutional services without any single party holding full recovery power. Deploy an ERC-1056 registry contract to replace traditional X.509 certificate authorities with a decentralized trust anchor. Each DID document functions as a self-managed certificate, binding public keys to an identifier controlled entirely by the holder.
In a traditional Public Key Infrastructure (PKI), a Certificate Authority (CA) signs an X.509 certificate to bind a public key to an identity. This creates a single point of failure and a centralized trust model. Decentralized PKI (DPKI) replaces the CA with a blockchain-anchored registry. The core primitive is a Decentralized Identifier (DID) registered in an ERC-1056 smart contract. Instead of a CA-issued certificate, a DID document stored on-chain or referenced via IPFS contains verificationMethod entries that list valid public keys and their intended purposes.
The ERC-1056 registry acts as a lightweight mapping layer. It stores only the essential state: the DID owner's address, a list of delegated controllers, and a pointer to the full DID document. This design keeps on-chain storage costs low while maintaining the integrity of the identity binding. When a verifier needs to validate a signature, they resolve the DID to its document, extract the relevant verificationMethod , and perform standard cryptographic verification. The blockchain's consensus mechanism provides the trust anchor, eliminating the need to trust a third-party CA.
Deploy the EthereumDIDRegistry contract from the did-ethr-resolver repository. The contract is minimal and has been audited across multiple production deployments on Ethereum mainnet, Gnosis Chain, and Polygon. After deployment, create a DID by calling identityOwner(address identity, address owner, uint256 validity) to establish initial control. The resulting DID follows the format did:ethr:
A DID document without verificationMethod entries is an empty certificate. Add key material by calling setAttribute(address identity, bytes32 name, bytes value, uint256 validity) . For an Ed25519 key used for authentication, set the name parameter to a path like did/pub/Ed25519/veriKey/auth and the value to the hex-encoded 32-byte public key. For a secp256k1 key used for assertion or capability invocation, use did/pub/secp256k1/veriKey/assert . The resolver constructs the full DID document by interpreting these attribute paths according to the DID Ethr Method specification .
Unlike an X.509 certificate that requires re-issuance by a CA to change keys, a DPKI allows the identity owner to rotate keys autonomously. Call revokeAttribute on the old key's attribute path, then setAttribute for the new key. For recovery without custodians, delegate a set of trusted addresses as controllers using changeOwner . A threshold of controllers can collectively rotate keys if the primary owner's key is lost. This pattern mirrors certificate revocation lists but operates without a centralized revocation authority, relying instead on the smart contract's state transitions as the source of truth.
Key architectural differences between centralized PKI and blockchain-anchored DPKI across trust model, key management, and auditability dimensions. Implement a verification API that resolves DIDs, fetches DID documents, validates signatures against public keys, and checks transparency log inclusion proofs. Includes caching strategies for DID resolution and handling revoked or expired keys.
A certificate verification service is the operational core of a decentralized PKI. Unlike traditional X.509 validation, which chains up to a root CA, DPKI verification resolves a did:ethr or did:key identifier to its corresponding DID document, extracts the verificationMethod entries, and uses the embedded public keys to check a credential's proof. The service must also validate that the signing key was active at the time of issuance by inspecting the assertionMethod relationship and cross-referencing any updated or deleted timestamps in the DID document's version history.
Start by building a resolution endpoint that accepts a DID and returns a normalized DID document. Use the did-resolver library with the ethr-did-resolver driver for Ethereum-anchored DIDs. The resolver should first check a local cache—Redis with a configurable TTL of 5 minutes works well for most use cases—before querying the Ethereum provider. Cache misses trigger an RPC call to fetch the current DIDLog events from the registry contract. To prevent stale data attacks, include a versionId parameter in your cache key and invalidate entries when the on-chain changed event fires for that DID.
3. Software Implementation, Frameworks & Protocols The signature verification flow operates in two phases. First, extract the proof object from the verifiable credential, which contains the verificationMethod reference, the proofValue (the actual signature), and the created timestamp. Resolve the verification method to its public key material—typically a secp256k1 or Ed25519 key in JWK or multibase format. Second, reconstruct the signing input by canonicalizing the credential using JSON-LD URDNA2015 or a simpler JWT-style base64url-encoded payload, then verify the signature with the elliptic or noble-ed25519 library. Reject any proof where the created date falls outside the key's validity window as defined by the DID document's validFrom and validUntil properties.
Transparency log verification adds a second layer of trust. When a credential includes a certificateTransparency proof, your service must fetch the corresponding SCT (Signed Certificate Timestamp) from a log like certificate-transparency-go or a custom Ethereum-anchored log contract. Validate the SCT signature against the log's public key, verify the Merkle audit path to an on-chain root hash, and confirm the log entry's timestamp is consistent with the credential's issuance date. Implement this as an asynchronous verification step: return a provisional acceptance immediately and emit a webhook or update a status endpoint once the inclusion proof is confirmed within the log's Maximum Merge Delay (MMD).
Handling revoked and expired keys requires maintaining a revocation status cache. For did:ethr , revoked keys are indicated by a deactivated event on the registry contract. Your service should poll for DIDDeactivated events every 2 minutes and update a local revocation set. For StatusList2021 credentials, fetch the compressed bitstring from the credential's credentialStatus.statusListCredential URL, decompress it, and check the bit at the credential's index. Cache the decompressed bitstring with a TTL equal to the list's ttl property to avoid re-fetching on every verification. If a key is revoked or expired, return a structured error with the reason field set to revoked or expired and include the timestamp of the status change.
For client-side verification, provide a lightweight library that performs the same checks without server infrastructure. The client resolves DIDs against a public gateway like https://resolver.identity.foundation , verifies signatures locally using WebAssembly-compiled cryptographic primitives, and checks transparency log proofs via a bundled SPV (Simple Payment Verification) mode that only downloads Merkle proofs rather than the full log. This dual-path architecture—server-side for high-throughput API verification and client-side for user-held credential wallets—ensures verification can happen anywhere without sacrificing the trust model.
Solutions for frequent problems encountered when deploying and operating DPKI infrastructure. Covers DID resolution failures, key rotation conflicts, certificate transparency log anchoring errors, and recovery mechanism debugging. This error occurs when the Ethereum transaction nonce is out of sync with the ERC-1056 registry contract. Each DID document update increments an internal nonce tracked by the registry. If your client submits a transaction with a nonce that does not match the expected value, the contract reverts.
Fix: Query the current nonce directly from the registry contract using identityOwner(didAddress) and nonce(didAddress) before constructing your update. Implement retry logic with nonce refresh on failure. For high-frequency rotation policies, use a single-threaded update queue per DID to prevent race conditions. Stale keys in DID resolution typically stem from caching layers or incomplete event indexing. The ERC-1056 resolver relies on DIDAttributeChanged events to reconstruct the current DID document state.
Common fix: Force a cache invalidation by calling the resolver with a versionId parameter set to the latest block hash. For production systems, set a maximum cache TTL of 30 seconds for frequently rotated keys. On-chain CT log verification failures usually result from mismatched Merkle proof formats or incorrect root hash anchoring. Ethereum-anchored CT logs like CertLocker or EthCT store log roots in a smart contract that verifiers query.
Fix: Use the log's official proof generation library rather than implementing RFC 6962 from scratch. Test proofs against a local log instance before submitting on-chain verification transactions. Social recovery mechanisms depend on a threshold of guardians approving a key rotation. When guardians become unresponsive, the recovery process stalls. This is a known failure mode in guardian-based DPKI designs.
Prevention: Configure guardian sets with redundancy. Use a 3-of-5 threshold rather than 3-of-3. Include at least one institutional guardian with an SLA. Implement guardian rotation so inactive guardians can be replaced before an emergency occurs. Last resort: If the recovery contract supports admin override (for enterprise deployments), the contract owner may force recovery. This breaks self-sovereignty but prevents permanent key loss.
High gas consumption during key rotation often comes from inefficient DID document storage patterns or unnecessary on-chain writes. ERC-1056 attribute changes cost ~50,000 gas per attribute update, but costs multiply with poor design. Benchmark: A single-attribute rotation costs ~80,000 gas. A batch-encoded rotation with 5 keys costs ~120,000 gas. Off-chain referenced rotation costs ~60,000 gas regardless of key count.
Signature verification failures in DPKI credential flows typically trace to algorithm mismatches, incorrect public key resolution, or canonicalization errors. Tooling: Use did-jwt or did-ethr-resolver libraries to programmatically verify signatures. These handle canonicalization and key resolution automatically. Test with known-good credentials before debugging custom implementations.
Missing events in DID history queries indicate gaps in event indexing or log pruning by the Ethereum node. Full archive nodes retain all historical logs, but many RPC providers prune logs older than a configurable threshold. A compromised delegate key can issue credentials or sign on behalf of the DID, but cannot transfer ownership if the delegate was properly scoped. ERC-1056 supports time-bound and scope-limited delegations.
Prevention: Set expiration timestamps on all delegations. Use delegateType scoping to limit permissions. Monitor delegate activity with an event listener that alerts on unexpected transactions. Use mature DID libraries, audited contract patterns, transparency logs, and monitoring services to reduce the custom code required for a decentralized public key infrastructure deployment.
4. Practical Deployment, Analysis & Case Studies ethr-did-registry is the reference contract behind the did:ethr method and is a practical starting point when Ethereum addresses act as DPKI trust anchors. For production DPKI, avoid putting certificate material or personal data directly in contract storage. Store only identifiers, hashes, controller relationships, and event history. Resolve the DID document from chain events, then fetch off-chain certificate metadata from IPFS, HTTPS, or a controlled transparency log.
Veramo provides a modular TypeScript agent for decentralized identity systems. It is useful when your DPKI needs wallet-side and server-side components that can manage DIDs, sign messages, issue credentials, and resolve trust roots. Treat Veramo as an orchestration layer. Keep consensus-critical registry rules in contracts and use the agent to coordinate signing, resolution, and credential lifecycle automation.
SpruceID's SSI tooling is useful for teams that need W3C DID and Verifiable Credential support in Rust-based services, gateways, or verification backends. For a DPKI stack, these libraries can sit behind an API that receives a presented certificate, resolves the issuer DID, validates the public key binding, checks revocation state, and returns a deterministic trust decision. This is especially useful for high-throughput verifier services where correctness and language-level safety matter more than browser compatibility.
OpenZeppelin Contracts should be the baseline for custom DPKI registry contracts, especially when you add issuer governance, emergency controls, or upgrade paths around a DID registry. Use these patterns to separate identity ownership from protocol administration. A root DID controller should rotate its own keys, while registry governance should only manage system-level rules such as approved issuer lists, schema IDs, dispute processes, or transparency-log anchoring intervals.
Rekor is a transparency log used in the Sigstore ecosystem. While it is not blockchain-native, it provides a practical model for append-only certificate or key-event logging that can be periodically anchored to Ethereum. This pattern reduces gas costs because the full event stream remains off-chain, while Ethereum stores compact commitments. It also gives auditors a deterministic way to prove that a key binding existed before a given block and was not silently rewritten later.
OpenZeppelin Defender can monitor DPKI contracts and trigger alerts or automated workflows when key infrastructure changes occur. For production use, route alerts to Slack, PagerDuty, or webhook-based incident systems. Pair monitoring with runbooks: when a high-value root DID rotates unexpectedly, your verifier fleet should temporarily reduce trust, require additional confirmations, or check an out-of-band transparency log before accepting new signatures.
Answers to common developer questions about decentralized PKI architecture, security trade-offs, and migration paths from traditional certificate authorities. A DPKI replaces centralized CAs with blockchain-anchored DID documents that serve as trust roots. Instead of relying on a CA's private key to sign certificates, each entity controls its own DID on a registry like did:ethr . The DID document contains public keys and service endpoints. When you issue a certificate, you sign it with a key referenced in your DID document, and verifiers resolve the DID on-chain to validate the key's authenticity. This eliminates single points of failure: compromising one CA in traditional PKI can poison the entire trust store, but in DPKI, an attacker must compromise each entity individually.
Certificate transparency is built in through on-chain event logs rather than requiring separate CT log servers. Gas costs vary significantly by DID method and storage strategy. Using did:ethr with the ERC-1056 registry, a DID creation costs approximately 50,000-80,000 gas (roughly $3-8 at 30 gwei). Key rotations cost 30,000-50,000 gas each. Service endpoint updates run 25,000-40,000 gas . To reduce costs, use: For enterprise deployments with millions of DIDs, expect $0.50-2.00 per DID-year on L2s versus $50-200 on Ethereum mainnet.
Key rotation in DPKI requires maintaining backward compatibility for credentials issued under previous keys. The standard approach uses key versioning in DID documents: When rotating, add the new key and mark old keys with an expires timestamp rather than removing them immediately. Verifiers check the DID document state at the time of credential issuance using version_id or block number anchoring. For long-lived credentials, implement a key attestation chain : when rotating, sign a statement with the old key authorizing the new key, creating a verifiable lineage that verifiers can traverse.
For enterprise deployments, combine social recovery with a recovery policy that requires both guardian approval and a mandatory delay period (e.g., 7 days) before rotation takes effect, giving the legitimate owner time to cancel malicious recovery attempts. Migration follows a hybrid trust model that maintains backward compatibility during transition: On-chain DIDs create a public, immutable audit trail of key rotations and service endpoint updates. This exposes: The trade-off is between auditability and privacy. Public DIDs maximize transparency; private DIDs require additional infrastructure for trust establishment.
5. Performance Evaluation & Extended Technical Observations In DPKI, certificate transparency is achieved through on-chain event logs rather than separate CT log servers. When a DID controller issues a credential or rotates keys, the transaction emits events that are permanently recorded on-chain: For off-chain credentials, implement a transparency service that batches credential hashes into Merkle trees and anchors the root on-chain. This follows the same pattern as Certificate Transparency RFC 6962 but uses smart contracts as the log server. The contract enforces append-only semantics: once a Merkle root is anchored, it cannot be modified or deleted.
This approach eliminates the need for trusted CT log operators since the blockchain itself provides immutability guarantees. Hybrid approach : Store DID documents off-chain for fast resolution, but anchor a content hash on-chain for tamper detection. Verifiers check the on-chain hash periodically (e.g., every 5 minutes) and use the off-chain document for real-time operations. If the hash doesn't match, fall back to on-chain resolution.
For latency-sensitive applications like payment verification, use did:key which requires zero network calls: the DID itself encodes the public key. Production systems our engineers design, build and run, scoped to what you are working on. Smart contracts, DeFi, wallets, tokenization and infrastructure across the ecosystems teams choose today, plus other networks on request.
This repository contains the source code and reproducible experiments for Blockchain-Based Decentralized Public Key Infrastructure Modeling and Analysis . It includes the lab-built Omnilink blockchain, a main-side chain deployment, four authentication platforms, real-system experiment runners, retained measurements, and the scripts used to produce the paper figures.
The experiment package is tested on 64-bit Windows with PowerShell 5.1. The following tools must be available on PATH : Python dependencies are declared in requirements.txt : NumPy, pandas, SciPy, Matplotlib, Pillow, and their dependencies. The Node.js runner uses the pinned web3 and solc versions in blockchain/dpki-experiment/package-lock.json . For an existing compatible Omnilink build, -SkipOmnilinkBuild skips only the Go build. -SkipPython and -SkipNode skip their corresponding installation steps. All required commands must still be present on PATH .
Omnilink is a lab-built blockchain system developed by our research group. It is implemented in Go and provides configurable PoW consensus, KV smart-contract support, and an EVM-compatible Solidity execution path. This repository contains the source needed to build the executable used by the experiments. The PoW launcher exposes meanBlockMs , difficultyBits , and empty-block mining as controlled inputs. Experiment scripts generate a TOML configuration for each node, start the processes, wait for RPC readiness, and archive the effective configurations and logs.
All four implementations use the same host, cryptographic libraries, request driver, and blockchain configuration. The registry in blockchain/platform_registry.js exposes a common experiment interface while preserving the mechanism-specific workflow. blockchain/platforms/proposed-dpki/ implements certificate management, intra-domain off-chain authentication, intra-domain on-chain authentication, and cross-domain authentication. It combines X.509 verification with MPT proof generation and verification. Management stores the complete certificate and repository state on chain. On-chain authentication additionally commits the authentication record and reads the recorded state. Cross-domain authentication checks the service-CA certificate state through the relayed MPT root. Each request includes its signed assertion exchange.
blockchain/platforms/centralized-pki/ is the conventional PKI baseline. It uses OpenSSL for key and CSR generation, certificate issuance, X.509 path verification, OCSP-style certificate-status validation, and signed assertions. It is an off-chain baseline and therefore deploys no contract. Cross-domain authentication performs the configured PKI trust-chain verification hops.
blockchain/platforms/multi-ca-dpki/ implements a 4-of-6 Multi-CA baseline. Six CA requests are issued concurrently, and authentication succeeds after four valid certificate/status responses. Management aggregates committee evidence and commits the certificate and validator evidence. The associated contract rejects duplicate validators and requires four distinct approvals.
blockchain/platforms/full-contract-dpki/ implements certificate management and authentication through a smart contract. Management stores CSR, certificate, status, and repository-root material. Authentication executes certificate/status and assertion checks, stores a validation digest, and writes the final audit result. The runner also performs the corresponding real OpenSSL certificate-path operation; it does not insert a fixed synthetic delay.
Each directory below contains a run_experiment.ps1 public entrypoint. The entrypoint starts the main chain and both sidechains, initializes their certificates and contracts, runs the selected workload, captures console and blockchain logs, and stops the processes on completion. Use -PaperScale to select the paper grid and request count for that experiment. During execution, the terminal prints generated certificate information, PEM content, transaction hashes, receipt status, block numbers, contract operations, and per-stage request measurements.
The archive contains the console transcript, generated chain configurations, logs from all three chains, transaction and receipt records, request samples, certificate artifacts, and the run manifest. Runtime databases are excluded because they are large and are regenerated by the launcher. MATLAB is not required to execute the blockchain experiments. It is needed only for the final MATLAB export. Existing retained data can be replotted without rerunning the experiments: Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Decentralized%20finance • https://en.wikipedia.org/wiki/Blockchain • https://en.wikipedia.org/wiki/Decentralized%20identifier • https://chainscorelabs.com/guides/trust-and-verification-systems/decentralized-identity-architecture/setting-up-a-decentraliz ed-public-key-infrastructure • https://github.com/RayJ9/Blockchain-based-DPKI-prototype
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Blockchain Based Decentralized Public Key Infrastructure.
[*] Metasploit Scan Running on Target Subnet for Blockchain Based Decentralized Public Key Infrastructure... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |