Complete Technical Paper Content — Blockchain Based Secure Cloud Data Audit System
Overview & System Context
Blockchain Based Secure Cloud Data Audit System: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~7193 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background A blockchain is a distributed ledger with growing lists of records (blocks) that are securely linked together via cryptographic hashes. Each block contains a cryptographic hash of the previous block, a timestamp, and transaction data (generally represented as a Merkle tree, where data nodes are represented by leaves). Since each block contains information about the previous block, they effectively form a chain (viz. linked list data structure), with each additional block linking to the ones before it. Consequently, blockchain transactions are resistant to alteration because, once recorded, the data in any given block cannot be changed retroactively without altering all subsequent blocks and obtaining network consensus to accept these changes. Blockchains are typically managed by a peer-to-peer (P2P) computer network for use as a public distributed ledger, where nodes collectively adhere to a consensus algorithm protocol to add and validate new transaction blocks.
Although blockchain records are not unalterable, since blockchain forks are possible, blockchains may be considered secure by design and exemplify a distributed computing system with high Byzantine fault tolerance. A blockchain was created by a person (or group of people) using the name (or pseudonym) Satoshi Nakamoto in 2008 to serve as the public distributed ledger for bitcoin cryptocurrency transactions, based on previous work by Stuart Haber, W. Scott Stornetta, and Dave Bayer.
The implementation of the blockchain within bitcoin made it the first digital currency to solve the double-spending problem without the need for a trusted authority or central server. The bitcoin design has inspired other applications and blockchains that are readable by the public and are widely used by cryptocurrencies. The blockchain may be considered a type of payment rail. Private blockchains have been proposed for business use. Computerworld called the marketing of such privatized blockchains without a proper security model "snake oil"; however, others have argued that permissioned blockchains, if carefully designed, may be more decentralized and therefore more secure in practice than permissionless ones.
A blockchain is a decentralized, distributed, and often public, digital ledger consisting of records called blocks that are used to record transactions across many computers so that any involved block cannot be altered retroactively, without the alteration of all subsequent blocks. This allows the participants to verify and audit transactions independently and relatively inexpensively. A blockchain database is managed autonomously using a peer-to-peer network and a distributed timestamping server. They are authenticated by mass collaboration powered by collective self-interests. Such a design facilitates robust workflow where participants' uncertainty regarding data security is marginal. The use of a blockchain removes the characteristic of infinite reproducibility from a digital asset. It confirms that each unit of value was transferred only once, solving the long-standing problem of double-spending. A blockchain has been described as a value-exchange protocol. Logically, a blockchain can be seen as consisting of several layers: infrastructure (hardware) networking (node discovery, information propagation and verification) consensus (proof of work, proof of stake) data (blocks, transactions) application (smart contracts/decentralized applications, if applicable) Permissioned blockchains use an access control layer to govern who has access to the network. It has been argued that permissioned blockchains can guarantee a certain level of decentralization, if carefully designed, as opposed to permissionless blockchains, which are often centralized in practice.
Figure 1: Smart Contract Audits & Blockchain Security | Hashlock Blockchain-based smart contracts are contracts that can be partially or fully executed or enforced without human interaction. One of the main objectives of a smart contract is automated escrow. A key feature of smart contracts is that they do not need a trusted third party (such as a trustee) to act as an intermediary between contracting entities — the blockchain network executes the contract on its own. This may reduce friction between entities when transferring value and could subsequently open the door to a higher level of transaction automation. An IMF staff discussion from 2018 reported that smart contracts based on blockchain technology might reduce moral hazards and optimize the use of contracts in general, but "no viable smart contract systems have yet emerged." Due to the lack of widespread use, their legal status was unclear.
Blockchain technology, such as cryptocurrencies and non-fungible tokens (NFTs), has been used in video games for monetization. Many live-service games offer in-game customization options, such as character skins or other in-game items, which the players can earn and trade with other players using in-game currency. Some games also allow for trading of virtual items using real-world currency, but this may be illegal in some countries where video games are seen as akin to gambling, and has led to gray market issues such as skin gambling, and thus publishers typically have shied away from allowing players to earn real-world funds from games. Blockchain games typically allow players to trade these in-game items for cryptocurrency, which can then be exchanged for money. The first known game to use blockchain technologies was CryptoKitties, launched in November 2017, where the player would purchase NFTs with Ethereum cryptocurrency, each NFT consisting of a virtual pet that the player could breed with others to create offspring with combined traits as new NFTs. The game made headlines in December 2017 when one virtual pet sold for more than US$100,000. CryptoKitties also illustrated scalability problems for games on Ethereum when it created significant congestion on the Ethereum network in early 2018 with approximately 30% of all Ethereum transactions being for the game. By the early 2020s, there had not been a breakout success in video games using blockchain, as these games tend to focus on using blockchain for speculation instead of more traditional forms of gameplay, which offers limited appeal to most players. Such games also represent a high risk to investors as their revenues can be difficult to predict. However, limited successes of some games, such as Axie Infinity during the COVID-19 pandemic, and corporate plans towards metaverse content, refueled interest in the area of GameFi, a term describing the intersection of video games and financing typically backed by blockchain currency, in the second half of 2021.
Several major publishers, including Ubisoft, Electronic Arts, and Take Two Interactive, have stated that blockchain and NFT-based games are under serious consideration for their companies in the future. In October 2021, Valve Corporation banned blockchain games, including those using cryptocurrency and NFTs, from being hosted on its Steam digital storefront service, which is widely used for personal computer gaming, claiming that this was an extension of their policy banning games that offered in-game items with real-world value. Valve's prior history with gambling, specifically skin gambling, was speculated to be a factor in the decision to ban blockchain games. Journalists and players responded positively to Valve's decision as blockchain and NFT games have a reputation for scams and fraud among most PC gamers, and Epic Games, which runs the Epic Games Store in competition to Steam, said that they would be open to accepted blockchain games in the wake of Valve's refusal.
There have been several different efforts to employ blockchains in supply chain management. Precious commodities mining — Blockchain technology has been used for tracking the origins of gemstones and other precious commodities. In 2016, The Wall Street Journal reported that the blockchain technology company Everledger was partnering with IBM's blockchain-based tracking service to trace the origin of diamonds to ensure that they were ethically mined. As of 2019, the Diamond Trading Company (DTC) has been involved in building a diamond trading supply chain product called Tracer. Food supply — As of 2018, Walmart and IBM were running a trial to use a blockchain-backed system for supply chain monitoring for lettuce and spinach – all nodes of the blockchain were administered by Walmart and located on the IBM cloud. Fashion industry — There is an opaque relationship between brands, distributors, and customers in the fashion industry, which prevents the sustainable and stable development of the fashion industry. Blockchain could make this information transparent, assisting sustainable development of the industry. Motor vehicles — Mercedes-Benz and partner Icertis developed a blockchain prototype used to facilitate consistent documentation of contracts along the supply chain so that the ethical standards and contractual obligations required of its direct suppliers can be passed on to second tier suppliers and beyond. In another project, the company uses blockchain technology to track the emissions of climate-relevant gases and the amount of secondary material along the supply chain for its battery cell manufacturers.
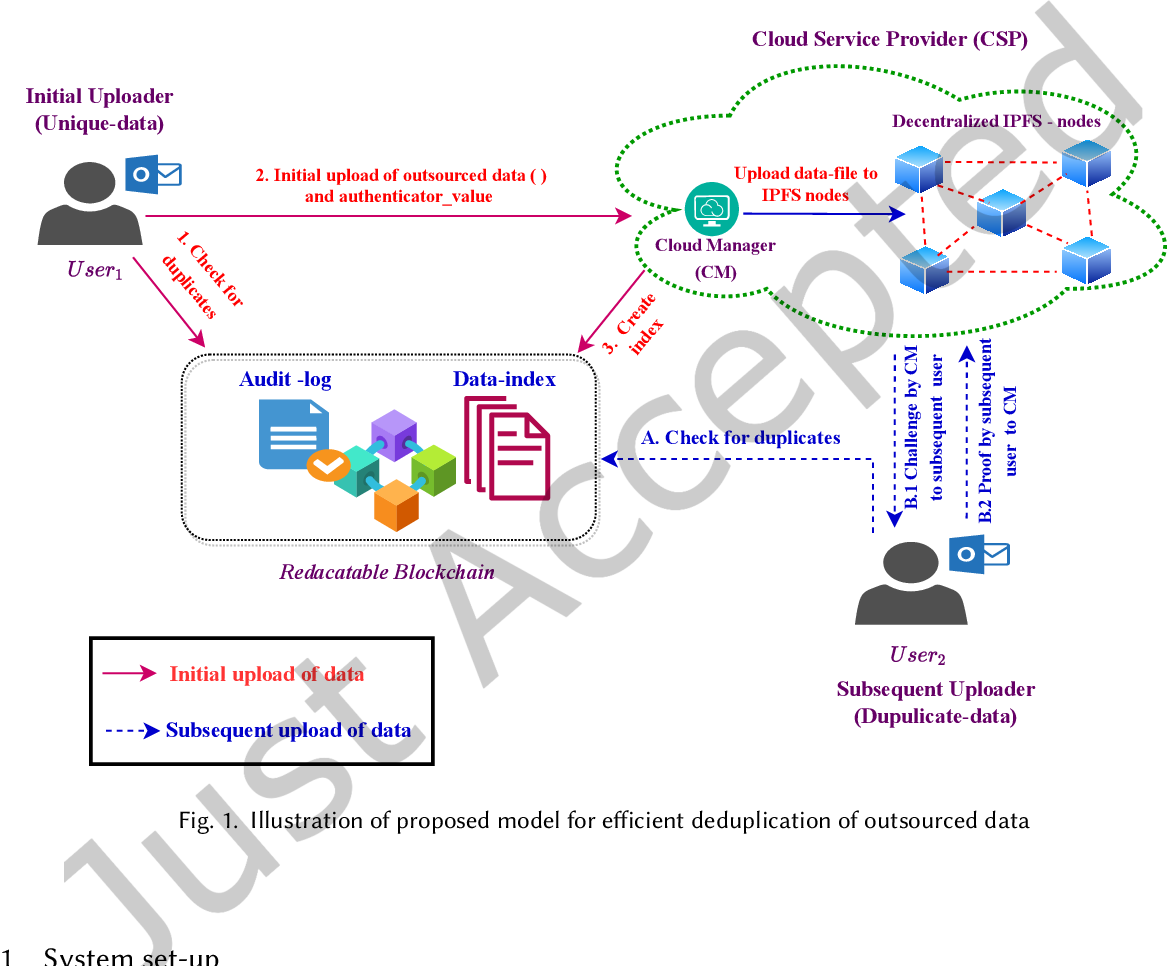
Figure 2: Figure 1 from Enabling Efficient Deduplication and Secure Decentralized ... Blockchain technology can be used to create a permanent, public, transparent ledger system for compiling data on sales, tracking digital use and payments to content creators, such as wireless users or musicians. The Gartner 2019 CIO Survey reported 2% of higher education respondents had launched blockchain projects and another 18% were planning academic projects in the next 24 months. In 2017, IBM partnered with ASCAP and PRS for Music to adopt blockchain technology in music distribution. Imogen Heap's Mycelia service has also been proposed as a blockchain-based alternative "that gives artists more control over how their songs and associated data circulate among fans and other musicians." New distribution methods are available for the insurance industry such as peer-to-peer insurance, parametric insurance and microinsurance following the adoption of blockchain. The sharing economy and IoT are also set to benefit from blockchains because they involve many collaborating peers. The use of blockchain in libraries is being studied with a grant from the U.S. Institute of Museum and Library Services. Other blockchain designs include Hyperledger, a collaborative effort from the Linux Foundation to support blockchain-based distributed ledgers, with projects under this initiative including Hyperledger Burrow (by Monax) and Hyperledger Fabric (spearheaded by IBM). Another is Quorum, a permissioned private blockchain by JPMorgan Chase with private storage, used for contract applications. Oracle introduced a blockchain table feature in its Oracle 21c database.
Blockchain is also being used in peer-to-peer energy trading. Blockchain and distributed ledger technologies have been investigated for managing access permissions, consent, provenance and audit trails in health care. A 2026 scoping review of 892 studies found that most involved prototypes or simulated evaluations, while evidence of sustained real-world implementation remained limited. Lightweight blockchains, or simplified blockchains, are more suitable for internet of things (IoT) applications than conventional blockchains. One experiment suggested that a lightweight blockchain-based network could accommodate up to 1.34 million authentication processes every second, which could be sufficient for resource-constrained IoT networks. Blockchain could be used in detecting counterfeits by associating unique identifiers to products, documents and shipments, and storing records associated with transactions that cannot be forged or altered. It is however argued that blockchain technology needs to be supplemented with technologies that provide a strong binding between physical objects and blockchain systems, as well as provisions for content creator verification ala KYC standards.
The EUIPO established an Anti-Counterfeiting Blockathon Forum, with the objective of "defining, piloting and implementing" an anti-counterfeiting infrastructure at the European level. The Dutch Standardisation organisation NEN uses blockchain together with QR Codes to authenticate certificates. Beijing and Shanghai are among the cities designated by China to trial blockchain applications as January 30, 2022. In Chinese legal proceedings, blockchain technology was first accepted as a method for authenticating internet evidence by the Hangzhou Internet Court in 2019 and has since been accepted by other Chinese courts.
In October 2014, the MIT Bitcoin Club, with funding from MIT alumni, provided undergraduate students at the Massachusetts Institute of Technology access to $100 of bitcoin. The adoption rates, as studied by Catalini and Tucker (2016), revealed that when people who typically adopt technologies early are given delayed access, they tend to reject the technology. Many universities have founded departments focusing on crypto and blockchain, including MIT, in 2017. In the same year, Edinburgh became "one of the first big European universities to launch a blockchain course", according to the Financial Times.
The need for internal audits to provide effective oversight of organizational efficiency will require a change in the way that information is accessed in new formats. Blockchain adoption requires a framework to identify the risk of exposure associated with transactions using blockchain. The Institute of Internal Auditors has identified the need for internal auditors to address this transformational technology. New methods are required to develop audit plans that identify threats and risks. The Internal Audit Foundation study, Blockchain and Internal Audit, assesses these factors. The American Institute of Certified Public Accountants has outlined new roles for auditors as a result of blockchain.
In September 2015, the first peer-reviewed academic journal dedicated to cryptocurrency and blockchain technology research, Ledger, was announced. The inaugural issue was published in December 2016. The journal covers aspects of mathematics, computer science, engineering, law, economics and philosophy that relate to cryptocurrencies. The journal encourages authors to digitally sign a file hash of submitted papers, which are then timestamped into the bitcoin blockchain.
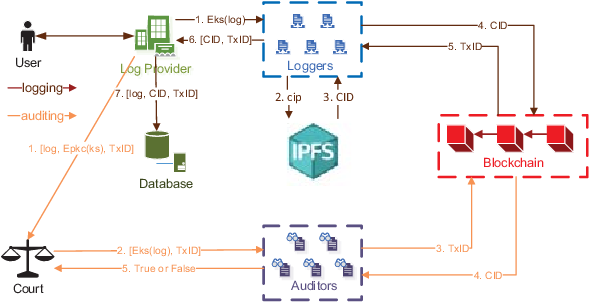
Authors are also asked to include a personal bitcoin address on the first page of their papers for non-repudiation purposes. Figure 3: Figure 2 from A Secure and Reliable Blockchain-based Audit Log System ... Changelog – a record of all notable changes made to a project Checklist – an informational aid used to reduce failure Economics of digitization Git – a version control system where the commit hash value depends on the previous commit hash value, also with Merkle tree inside List of blockchains Privacy and blockchain Real-World Assets Version control – a record of all changes (mostly of software project) in a form of a graph A blockchain security audit is only as comprehensive as the controls it actually checks.
Most audit reports list findings. This guide lists what should have been checked to find them. Every item below is a specific, verifiable control with a defined pass condition, evidence requirement, and pre-classified severity. This is not a high-level framework. It is an operational tool: work through it before an audit to identify gaps, use it during an engagement to track coverage, and apply it after remediation to verify that fixes hold before re-audit.
These controls verify that deployed contract code is free from known vulnerability classes and behaves correctly according to its specification. For the full audit framework that contextualizes these controls within a complete blockchain audit , the overview guide covers the system-level security picture.
These controls verify that blockchain node infrastructure is hardened against the most common attack vectors. For the complete node security assessment methodology covering each of these controls in depth, the blockchain node security guide covers the full review process. These controls verify that the application layer built on the blockchain system does not introduce vulnerabilities that undermine on-chain security.
For the complete blockchain application security framework covering each of these areas in depth, the dedicated application security guide covers the full review methodology. 2. System Architecture & Core Working Principles These controls verify that the governance mechanisms controlling protocol parameters, upgrades, and treasury are secure against manipulation.
These controls verify that cryptographic implementation is correct and meets applicable standards. For the complete cryptography-specific control set, apply the dedicated cryptography audit checklist alongside this one. These controls verify that the audit produces documented, reproducible evidence that can support regulatory review, investor due diligence, and re-audit verification.
The evidence requirements guide covers the full assurance methodology for blockchain audit evidence collection and documentation. For the governance-specific controls referenced in governance audit engagements, the governance checklist covers the governance domain in greater depth alongside this general security checklist.
Based on documented blockchain security audits across protocol types, these items fail most frequently: A comprehensive blockchain security audit checklist covers smart contract vulnerability classes, node and network infrastructure controls, application and API security, governance and access control mechanisms, cryptographic implementation, and evidence and documentation requirements. Missing any domain leaves material risk unassessed.
A smart contract audit checklist focuses on contract code only. This blockchain security audit checklist covers the full system: contracts, nodes, applications, governance, and cryptography. Both are needed for a complete security picture. The contract checklist goes deeper on code-level vulnerability classes. This checklist covers the broader system. Yes, and it should be. Self-assessment before an audit identifies obvious gaps without paying auditor rates to document them.
However, self-assessment does not replace third-party audit. Independent review applies adversarial judgment, tests assumptions, and finds issues that internal teams with shared assumptions consistently miss. At every significant release, after any infrastructure change, and whenever new vulnerability classes are documented for the contract types or node clients in use. Security standards evolve. A checklist that reflects best practices today may be incomplete in 18 months.
Domain 1 (smart contract security) and Domain 4 (governance) are the highest-priority domains for DeFi protocols. Contract code vulnerabilities create the most direct path to fund loss. Governance vulnerabilities create the most direct path to protocol takeover. Both must pass before any protocol holds significant TVL. Passing all items means documented controls exist for all known risk categories. It does not mean the system is free from all vulnerabilities. A qualified auditor will find context-specific issues that no generic checklist anticipates. This checklist is the foundation. A third-party audit with expert judgment is what provides meaningful security assurance.
A blockchain security checklist is the difference between auditing with a plan and auditing with a hope. It ensures every known control area is examined with documented evidence. What it cannot provide is the adversarial creativity of a skilled security researcher who does not know what they are supposed to find and looks everywhere anyway. Master blockchain security audits in 2025 with our comprehensive guide. Learn audit types, processes, benefits, and emerging trends for robust digital systems.
The world of auditing is changing, and fast. New tech like blockchain is shaking things up, making old ways of doing things feel a bit… well, old. We need to get smart about how we check the books and make sure everything is on the up and up. This article is all about understanding the big picture of blockchain auditing and what it means for auditors today and tomorrow. Let's figure out how to get ahead of the curve.
A blockchain audit is basically a thorough check of a blockchain system. It’s about making sure the technology is working right, is secure, and follows all the necessary rules. Auditors look at things like transaction records, the code that runs automatic agreements (smart contracts), and how the whole system is set up. The goal is to confirm that everything is accurate and in line with any regulations that apply. It’s like being a detective for digital systems, making sure no one’s cheating the system or that there aren’t any hidden flaws. The world of auditing is changing, and fast. New tech like blockchain is shaking things up, making old ways of doing things feel a bit… well, old.
Why bother with all this checking? Well, blockchain systems, while powerful, aren't automatically perfect. They can have bugs in their code, security weak spots, or might not be following the laws. Auditing helps catch these problems before they cause major issues, like losing money or breaking trust. It’s about building confidence in the digital infrastructure we rely on. For example, blockchains are often open-source, allowing anyone to view their code. This transparency enables auditors to review cryptocurrencies like Bitcoin, ensuring their integrity and security. Without audits, these systems would be much riskier to use. You can find professional firms that specialize in these checks.
When we talk about auditing blockchain, a few core ideas are super important. Think of these as the rules auditors follow: Auditing in the blockchain space requires a blend of traditional accounting skills and new technical know-how. It’s not just about numbers anymore; it’s about understanding the code, the network, and how decentralized systems operate. This fundamental concept underpins its utility in various applications requiring secure and verifiable record-keeping.
Look, in 2025, just checking the code once isn't really cutting it anymore. We're seeing a shift towards what you could call 'defense in depth' for blockchain systems. This means a lot more than just a quick scan for common bugs. Think automated checks that run constantly, followed by actual humans who know their stuff digging through the code line by line. Then there are simulated attacks, trying to break the system before the bad guys do, and something called fuzz testing, which basically throws random data at it to see if it freaks out. It’s a more thorough approach because, let's face it, the tech is getting more complex, and so are the ways people try to mess with it.
Remember when blockchains were mostly their own little islands? Those days are fading fast. Now, we've got applications that jump between different blockchains, and all sorts of Layer 2 solutions popping up. This creates new headaches for security. An audit can't just focus on one chain anymore; it has to look at how these different chains interact and what security risks pop up when data or assets move between them. It’s like checking the security of your house, but also making sure the bridge connecting it to your neighbor's property is just as secure.
This is probably the most significant shift. Back in the day, you could maybe get away with a bit of a gray area when it came to rules. Not anymore. Regulators worldwide are really cracking down. We're seeing massive fines for companies that aren't playing by the book. For instance, financial institutions saw penalties jump by over 400% in early 2025 compared to the year before. It’s not just about avoiding trouble; it’s about building trust. Demonstrating compliance is becoming a key differentiator for projects looking to gain mainstream acceptance and attract serious investment.
3. Software Implementation, Frameworks & Protocols When we talk about checking blockchain systems, it's not a one-size-fits-all situation. Different parts of the blockchain ecosystem need their own specific kind of inspection. Think of it like inspecting a building; you'd check the foundation, the electrical system, and the plumbing separately. Blockchain is similar, with specialized audits for financial records, network security, the automated code (smart contracts), and making sure everything plays by the rules.
This type of audit zeroes in on the money aspects. It's all about making sure the financial information stored on the blockchain is accurate and can be trusted. Auditors will look at transactions, account balances, and how financial data is handled to confirm it matches accounting standards and company policies. The main goal here is to verify that assets are properly accounted for and that all financial dealings are legitimate. This builds confidence for everyone involved, from investors to business partners. It’s about making sure the digital money trail makes sense.
Security audits act like a digital security guard for your blockchain network. They dig deep into all the security measures in place to find any weak spots or potential threats. This includes checking things like: The aim is to patch up any holes before bad actors can exploit them. A strong security audit is key to maintaining the integrity of the blockchain. You can find professional firms that specialize in these checks.
Smart contracts are the automated agreements that run on blockchains. Because they execute automatically when certain conditions are met, any mistake in their code can lead to big problems. A smart contract audit specifically examines the code itself. It's like a code review, but with a sharp focus on finding bugs, vulnerabilities, or ways someone could trick the contract into doing something unintended. This is really important for decentralized applications to work correctly and safely. Auditing smart contracts is vital for preventing financial loss and maintaining user trust.
Compliance audits make sure the blockchain system is playing by all the relevant laws and regulations. This can be complex because rules vary by location and industry. Auditors check if the system handles data privacy correctly, adheres to anti-money laundering (AML) laws, and meets any other legal requirements. It’s about ensuring the blockchain operates within the legal framework, which is becoming increasingly important as more businesses adopt this technology. This helps avoid legal trouble and builds a reputation for responsible operation. blockchain technology and its impact is a good place to start understanding this.
So, you've got this blockchain system, and you want to make sure it's not going to fall apart or get hacked. That's where the actual audit process comes in. It's not just a quick look-over; it's a structured way to check everything. Think of it like getting your car inspected, but for your digital ledger. We're talking about digging into the data, figuring out what it all means, and then telling you what we found.
First things first, we need the raw materials. This means gathering all the relevant data from the blockchain. It's not as simple as just downloading a file, though. We need to access transaction histories, smart contract code, network configurations, and any associated off-chain data that might be relevant. Sometimes, this data is spread out, or it's in a format that's hard to work with. So, a big part of this stage is cleaning it up and getting it ready for analysis. We're looking for consistency and completeness, making sure we're not missing any crucial pieces of the puzzle. This initial step is vital for any successful cryptocurrency audit .
Once we have the data prepped, we start digging in. This is where the real detective work happens. We're examining transaction patterns to spot anything unusual, like sudden spikes in activity or transactions that don't make sense. We're also scrutinizing the smart contract code itself. Are there any bugs? Any loopholes that someone could exploit? We use various tools and techniques to test these contracts under different scenarios.
After all the digging and checking, we put together a report. This isn't just a list of problems; it's a clear explanation of what we found, why it matters, and what you can do about it. We'll detail any security risks, compliance issues, or operational inefficiencies we uncovered. Then, we provide practical, actionable recommendations to fix these problems. The goal is to give you a clear roadmap to improve your blockchain system's security, reliability, and overall health. We want to make sure you understand the risks and how to mitigate them effectively.
So, why go through the whole process of a detailed blockchain audit? It might seem like a lot of extra work, but honestly, it really pays off. Think of it like getting your car checked out before a long road trip – you want to know it’s safe and sound, right? Auditing your blockchain system does the same thing for your digital operations. It’s not just about finding problems; it’s about building a solid foundation for whatever you’re doing on the blockchain.
This is probably the biggest win. Audits dig deep into your system to find any weak spots that hackers could exploit. We're talking about checking everything from how transactions are processed to the code that runs your smart contracts. By catching these vulnerabilities early, you significantly lower the risk of data breaches and theft. This proactive approach means your users and partners can feel more confident using your platform, knowing their assets and information are better protected. It’s like putting up stronger locks on your digital doors.
Blockchain is already known for being transparent, but an audit takes that a step further. It provides an independent look at your system, confirming that everything is running as it should. Auditors verify transaction records and the flow of data, making it clear where everything is coming from and going to. This level of clarity is super important, especially if you're dealing with supply chains or financial transactions where knowing the exact path of an item or a fund is key. It helps build a reputation for honesty.
Rules and regulations are always changing, and staying on the right side of them can be tricky, especially with new tech like blockchain. A compliance audit specifically checks if your system meets all the necessary legal requirements for your industry and location. This could be anything from data privacy laws to financial reporting standards. Getting this right means you avoid hefty fines and legal headaches down the line. Plus, by identifying potential risks before they become actual problems, you cut down on the chances of financial loss or damage to your company's name.
Beyond security and rules, audits also make sure your blockchain system actually works well. This means checking that your smart contracts execute correctly and that transactions are processed accurately and efficiently. It’s about making sure the technology is reliable and does what it's supposed to do, without glitches or errors. Think of it as a quality check to make sure everything is built to last and performs as expected, reducing the likelihood of disputes or operational hiccups.
So, you've got a blockchain system, and you want to make sure it's solid. It's not just about picking any auditor; it's about being smart about how you approach the whole process. Getting this right means your system stays safe and sound. Choosing who will look over your blockchain is a big deal. You don't want just anyone; you want a team that really gets what you're doing. Look for a partner whose methods line up with what's considered good practice in the industry. Do they have experience with the specific type of blockchain project you have, like DeFi or NFTs? Also, check if they understand the rules and regulations that apply to your situation. A good partner will have a solid history of successful audits and know their way around smart contract code, cryptography, and how to test for weaknesses.
A good audit isn't just a quick look-over. It needs a structured plan. This usually involves several key steps: These days, technology can really help with audits, especially when it comes to following the rules. Automated tools can keep an eye on transactions in real-time, flagging anything that looks suspicious. This is super helpful because regulators are also using advanced tech to monitor things. Think about using software that can automatically check if transactions meet certain criteria or help with customer identification processes. These tools can save a lot of time and reduce the chance of human error, making your compliance efforts more efficient and reliable.
The world of checking blockchain systems is always shifting, and some new things are really starting to stand out. It’s not just about looking at old transaction logs anymore. We’re seeing a move towards checking how eco-friendly these networks are and making sure the digital tokens themselves are solid. More and more, people are asking about the environmental footprint of blockchain. Sustainability audits are becoming a thing, looking at how much energy a network uses and if there are ways to make it more efficient. Think of it like checking if a factory is polluting too much. Then there are token audits. Tokens are basically digital assets on a blockchain, and they can represent all sorts of things. Auditing them means looking at how they're designed, how they get handed out, and if they're being used in a way that makes sense and doesn't cause problems later on.
Blockchains are known for being open, but sometimes you need to keep things private, especially in business. New ways of auditing are popping up that try to check systems while still protecting sensitive data. It’s a tricky balance. Also, instead of just one audit firm doing all the work, we're seeing more collaboration. This could mean multiple auditors working together, or even the community getting involved. The idea is that more eyes can spot more issues, making the whole system more trustworthy.
4. Practical Deployment, Analysis & Case Studies DeFi is a huge area now, basically financial services built on blockchain. Auditing DeFi is pretty complex because it’s so new and can involve intricate smart contracts that manage loans, trading, and other financial activities. Making sure these contracts are safe and work as intended is a big deal for anyone using these services. It’s a rapidly growing field that needs a lot of careful checking to keep users safe.
So, we've covered a lot about blockchain audits, from what they are to why they matter and what the future might hold. It's pretty clear that as more companies get into blockchain, checking these systems is going to be a really big deal. It's not just about making sure the tech works right, but also about keeping things honest and secure for everyone involved. Auditors will need to keep learning new skills, especially with things like AI becoming more common, to stay relevant. It’s definitely a learning curve, for sure, but getting this right means we can all trust the digital world a bit more. If you're using blockchain, getting it checked out by the pros isn't just a good idea, it's pretty much a must-do to keep everything running smoothly and safely.
Imagine a blockchain audit as a super thorough check-up for digital systems that use blockchain, like for digital money or tracking goods. It's like being a detective to make sure the system is safe, works correctly, and follows all the important rules. We carefully examine the digital records to ensure they haven't been tampered with and that everything is fair and honest. Blockchain is like a very secure digital diary that everyone involved can see, and once something is written, it's really hard to change. This makes it easier to trust the information. Auditing helps catch problems like secret flaws or rule-breaking before they cause big trouble, like losing money or damaging trust. It helps everyone feel more confident using these digital tools.
Auditors check a few main things. They make sure the system is secure and can't be easily hacked. They also check if the digital records are accurate and haven't been changed in sneaky ways. On top of that, they ensure the system follows all the necessary laws and rules, like keeping private information private. Yes, there are! Some audits focus on checking the money side of things, making sure financial records are accurate. Others are all about security, finding weak spots that hackers could use. There are also audits specifically for smart contracts, which are like automated agreements, and audits to make sure the system follows all the legal rules.
It starts with gathering all the necessary information, like transaction histories and the code used. Then, auditors carefully examine this data, looking for anything unusual or risky. They use special tools and methods to test the system. Finally, they put together a report explaining what they found and suggesting ways to fix any problems. Doing an audit makes your blockchain system much safer and helps people trust it more. It makes things clearer and easier to track, which is great for business. It also helps you follow the law and avoid costly mistakes or legal issues. Basically, it ensures your system is reliable, secure, and trustworthy for everyone.
Cryptocurrency custody services: How they protect digital assets and help institutions manage risk Blockchain Security Auditing & Vulnerability Assessment is now a baseline control for Web3 products, not a checkbox before launch. If your system holds assets, signs transactions, runs validators, controls governance, or exposes RPC endpoints, you need a structured way to find weaknesses before attackers do.
The reason is simple. Blockchain failures are expensive and public. Industry analyses of DeFi and blockchain incidents estimate that more than 10 billion USD has been stolen from platforms since 2018, with smart contract bugs, bridge failures, access control mistakes, and key compromise showing up again and again. One widely cited audit guide places smart contract hack losses at about 2.81 billion USD in 2022 alone. That is not a rounding error. It is a risk category.
Blockchain Security Auditing & Vulnerability Assessment is the systematic review of a blockchain system's code, architecture, infrastructure, and operations. The goal is to find security flaws, classify their impact, and give the team a clear path to remediation. A serious audit looks beyond a single Solidity file. Depending on the project, the scope can include: Think of it as threat modeling plus code review plus infrastructure assessment. Automated scanners help, but they are not enough. The bugs that drain protocols are often business logic errors, not syntax mistakes.
Blockchain software has a harsh failure model. Once a vulnerable contract is deployed on Ethereum mainnet, chain ID 1, you cannot quietly patch the historical state. If the contract is immutable, the fix may require migration, user coordination, and a public explanation. If it is upgradeable, the proxy pattern itself becomes part of the audit scope. Small defaults matter. Solidity 0.8.x checks arithmetic overflow and underflow by default, which removed a class of bugs common in older versions. But it did not remove logic errors, unsafe external calls, incorrect access control, oracle manipulation, or broken economic assumptions. I have seen test suites pass while the first owner-only function call in a fork test fails with: VM Exception while processing transaction: reverted with reason string 'Ownable: caller is not the owner' . That is not an exotic vulnerability. It is a deployment and permissions mistake, and it can block upgrades during an incident.
The blockchain security market is projected by industry research to grow from 3.15 billion USD in 2024 to 58.86 billion USD by 2032, a 44.20 percent compound annual growth rate. That growth reflects more than DeFi anxiety. Banks, supply chain networks, gaming platforms, tokenization projects, and enterprise consortia now have to prove that their blockchain systems can withstand technical and operational attacks.
Veridise analyzed 100 security audits across smart contracts, blockchain implementations, and zero-knowledge systems, covering 1,605 issues. The average project had 16.1 issues. Zero-knowledge audits averaged 18.0 issues and were twice as likely to contain a critical issue compared with other audit types. The most common serious bug type was logic error, and logic errors accounted for 41 percent of severe issues.
That matches what working auditors already know. The dangerous bugs often live in the rules of the protocol, not in a tool's warning output. SlowMist's Blockchain Common Vulnerability List maps weaknesses across network, consensus, wallet, and smart contract layers. Examples include exposed administrative RPC endpoints, unsafe peer-to-peer assumptions, weak randomness, flawed signing workflows, and poor key storage.
Do not ignore infrastructure. A perfectly audited contract can still be at risk if the deployment key sits in a developer's browser wallet, the validator API is exposed to the internet, or a multisig policy requires only one compromised signer. Start with assets and adversaries. What can be stolen, frozen, minted, burned, or governed? Who can attack you: users, validators, admins, MEV searchers, bridge operators, compromised insiders, or external service providers? 5. Performance Evaluation & Extended Technical Observations For a DeFi protocol, the scope may cover ERC-20 integrations, AMM math, lending collateral rules, liquidation logic, governance, oracle feeds, and upgrade controls. For an enterprise blockchain, it may cover identity, chaincode permissions, data integrity, and node operations.
Auditors need architecture diagrams, specifications, deployment scripts, dependency lists, threat models, and test instructions. Hand over only a GitHub repository and say "please audit," and you should expect delays and missed context. Good documentation also exposes design contradictions. A spec may claim that only governance can pause a protocol, while the code lets a single guardian wallet pause withdrawals. That gap matters.
Use tools early, not at the end. Common choices include Slither for Solidity static analysis, Mythril for symbolic analysis, Echidna for property-based fuzzing, and Foundry or Hardhat for unit, fork, and invariant tests. Infrastructure teams may add configuration scanners, secret detection, dependency checks, and RPC exposure checks. Automation is fast. It is also noisy. Slither may correctly flag reentrancy risk in a function that is protected elsewhere, or miss an economic attack because the math is valid but the incentive design is broken. Treat tools as triage, not judgment.
This is where most high-value findings appear. Review state transitions, trust boundaries, privilege paths, rounding behavior, external calls, oracle assumptions, and failure modes. Ask blunt questions: A useful report includes severity, impact, affected components, reproduction steps, proof-of-concept scenarios, and specific remediation guidance. Severity should reflect exploitability and business impact. A low-complexity bug that allows fund theft is critical. A theoretical issue in unreachable code is not.
Fix critical and high-risk findings first. Then retest. For upgradeable systems, verify storage layout compatibility. For immutable contracts, consider redeployment, migration plans, or risk acceptance, and only when the remaining issue is genuinely low impact. The OWASP Smart Contract Top 10: 2026 gives developers and auditors a shared checklist for major smart contract risk categories. It is not a full audit methodology, but it is a helpful baseline for training, code review, and internal security gates.
Academic surveys of Ethereum smart contract security show a recurring problem. Vulnerability names are not fully standardized. The same underlying weakness may appear under different labels across tools, papers, and audit firms. That makes consistent reporting important. If your internal team uses OWASP categories, SlowMist's BCVL, and a clear severity model, future audits become easier to compare.
Typical blockchain security audit costs often fall between 5,000 and 50,000 USD, depending on code size, complexity, documentation quality, and audit depth. Complex cross-chain bridges, zero-knowledge circuits, Layer 1 protocol changes, and high-value DeFi systems can cost more. Cheap audits are risky when they are mostly automated scans with a polished PDF attached. To be blunt, if a protocol secures significant funds, a shallow audit is a false economy. You need manual review, threat modeling, retesting, and a clear remediation process.
If you are a developer, security engineer, architect, or compliance professional, build from fundamentals before jumping into advanced exploit research. Learn Solidity 0.8.x behavior, ERC-20 and ERC-721 standards, EIP-1559 gas mechanics, wallet signing flows, and common proxy patterns. Then practice with tools such as Foundry, Hardhat, Slither, and Echidna. Blockchain Council learners can connect this path with related programs such as Certified Blockchain Expert™ , Certified Blockchain Developer™ , and Certified Smart Contract Auditor™ . For teams working on AI-assisted security tooling or Web3 risk automation, Blockchain Council's AI and cybersecurity certifications can support broader security engineering skills.
Start with one concrete action: audit a small Solidity project yourself. Write the threat model, run Slither, add Foundry tests, identify access control paths, and produce a short report with severity and fixes. Then compare your findings against the OWASP Smart Contract Top 10: 2026. If your organization is preparing a mainnet launch, major upgrade, bridge deployment, or institutional blockchain rollout, treat Blockchain Security Auditing & Vulnerability Assessment as part of the development lifecycle. Scope it early, budget for remediation, and verify fixes before production exposure. That is the difference between security as paperwork and security as engineering.
Learn how Blockchain Distributed Systems Engineering combines consensus, fault tolerance, smart contracts, security, and software process for real-world systems. Learn how Blockchain AI Integration and Autonomous Agents combine AI decision-making, smart contracts, wallets, audit trails, and AgentFi infrastructure.
Product Discovery for Blockchain Products: A Step-by-Step Guide for Web3 Product Managers A practical Web3 product discovery guide covering wallet behavior, token validation, governance, security, metrics, and testnet pilots. The next generation of DeFi protocols aims to connect traditional banking with decentralized finance ecosystems.
Learn how to install Claude Code on macOS, Linux, and Windows using the native installer, plus verification, authentication, and troubleshooting tips. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Blockchain • https://tech-audit.org/blockchain-audit/blockchain-security-audit-checklist/ • https://www.veritasprotocol.com/blog/mastering-blockchain-security-audits-a-comprehensive-guide-for-2025 • https://www.blockchain-council.org/blockchain/blockchain-security-auditing-vulnerability-assessment/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Blockchain Based Secure Cloud Data Audit System.
[*] Metasploit Scan Running on Target Subnet for Blockchain Based Secure Cloud Data Audit System... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |