Complete Technical Paper Content — Blowfish Encryption Algorithm Implementation For Large Files
Overview & System Context
Blowfish Encryption Algorithm Implementation For Large Files: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~4911 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Blowfish is a symmetric-key block cipher, designed in 1993 by Bruce Schneier and included in many cipher suites and encryption products. Blowfish provides a good encryption rate in software, and no effective cryptanalysis of it has been found to date for smaller files. It is recommended Blowfish should not be used to encrypt files larger than 4GB in size, in which case Twofish should be used instead. Blowfish has a 64-bit block size and therefore it could be vulnerable to Sweet32 birthday attacks. Schneier designed Blowfish as a general-purpose algorithm, intended as an alternative to the aging DES and free of the problems and constraints associated with other algorithms. At the time Blowfish was released, many other designs were proprietary, encumbered by patents, or were commercial or government secrets. Schneier has stated that "Blowfish is unpatented, and will remain so in all countries. The algorithm is hereby placed in the public domain, and can be freely used by anyone." Notable features of the design include key-dependent S-boxes and a highly complex key schedule.
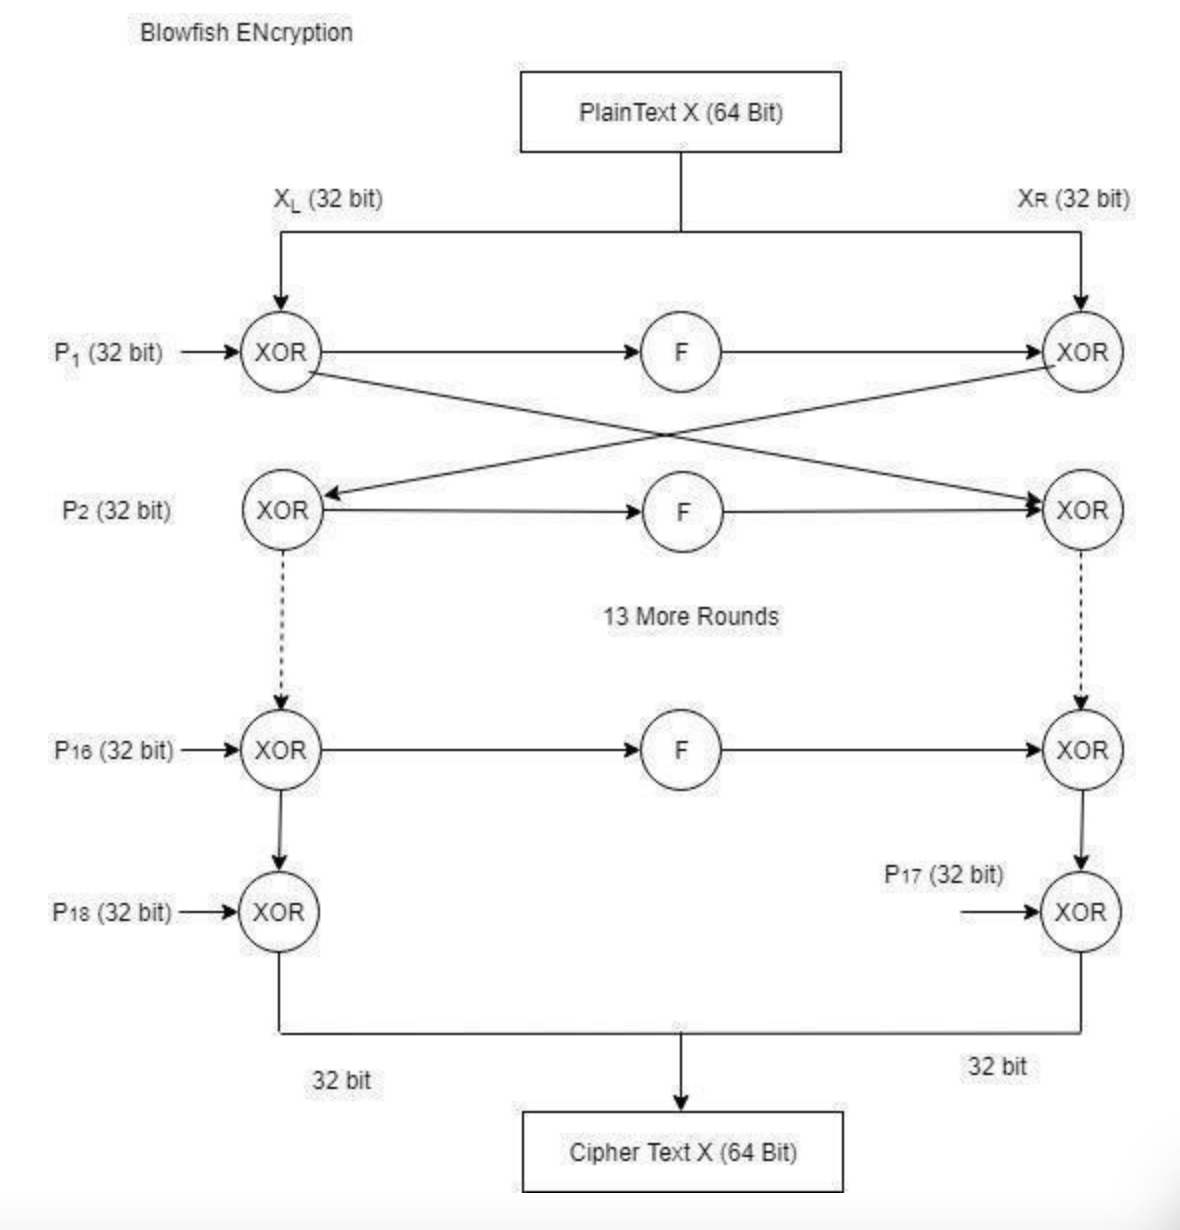
The adjacent diagram shows Blowfish's encryption routine. Each line represents 32 bits. There are five subkey-arrays: one 18-entry P-array (denoted as K in the diagram, to avoid confusion with the Plaintext) and four 256-entry S-boxes (S0, S1, S2 and S3). Every round r consists of 4 actions: The F-function splits the 32-bit input into four 8-bit quarters and uses the quarters as input to the S-boxes. The S-boxes accept 8-bit input and produce 32-bit output. The outputs are added modulo 232 and XORed to produce the final 32-bit output (see image in the upper right corner). After the 16th round, undo the last swap, and XOR L with K18 and R with K17 (output whitening). Decryption is exactly the same as encryption, except that P1, P2, ..., P18 are used in the reverse order. This is not so obvious because xor is commutative and associative. A common misconception is to use inverse order of encryption as decryption algorithm (i.e. first XORing P17 and P18 to the ciphertext block, then using the P-entries in reverse order).
Blowfish's key schedule starts by initializing the P-array and S-boxes with values derived from the hexadecimal digits of pi, which contain no obvious pattern (see nothing up my sleeve number). The secret key is then, byte by byte, cycling the key if necessary, XORed with all the P-entries in order. A 64-bit all-zero block is then encrypted with the algorithm as it stands. The resultant ciphertext replaces P1 and P2. The same ciphertext is then encrypted again with the new subkeys, and the new ciphertext replaces P3 and P4. This continues, replacing the entire P-array and all the S-box entries. In all, the Blowfish encryption algorithm will run 521 times to generate all the subkeys – about 4 KB of data is processed. Because the P-array is 576 bits long, and the key bytes are XORed through all these 576 bits during the initialization, many implementations support key sizes up to 576 bits. The reason for that is a discrepancy between the original Blowfish description, which uses 448-bit keys, and its reference implementation, which uses 576-bit keys. The test vectors for verifying third-party implementations were also produced with 576-bit keys. When asked which Blowfish version is the correct one, Bruce Schneier answered: "The test vectors should be used to determine the one true Blowfish". Another opinion is that the 448 bits limit is present to ensure that every bit of every subkey depends on every bit of the key, as the last four values of the P-array don't affect every bit of the ciphertext. This point should be taken in consideration for implementations with a different number of rounds, as even though it increases security against an exhaustive attack, it weakens the security guaranteed by the algorithm. And given the slow initialization of the cipher with each change of key, it is granted a natural protection against brute-force attacks, which doesn't really justify key sizes longer than 448 bits.
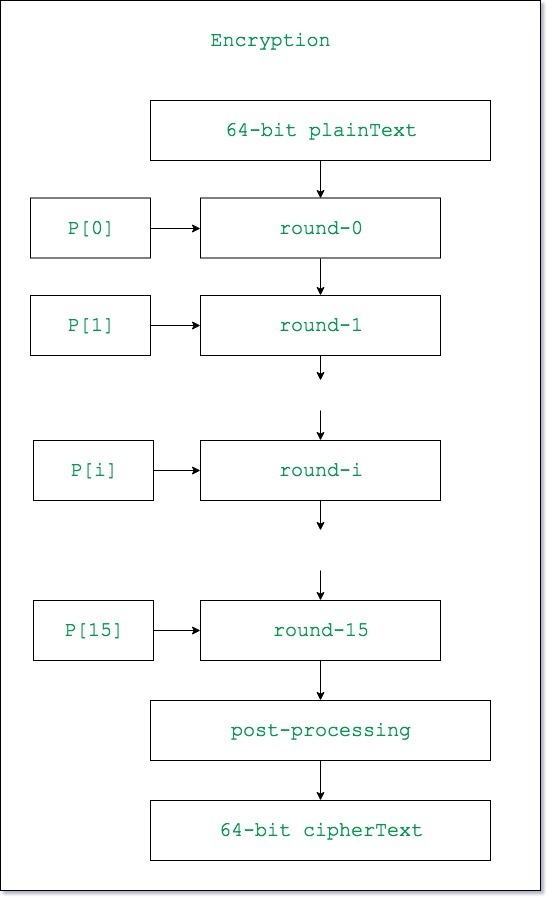
function f(x): // Calculates a function f on a 32-bit input x, using S-boxes and bit manipulation high_byte := (x shifted right by 24 bits) second_byte := (x shifted right by 16 bits) AND 0xff third_byte := (x shifted right by 8 bits) AND 0xff low_byte := x AND 0xff Figure 1: Blowfish Algorithm with Examples - GeeksforGeeks h := S[0][high_byte] + S[1][second_byte] return (h XOR S[2][third_byte]) + S[3][low_byte] procedure blowfish_encrypt(L, R): // Encrypts two 32-bit halves L and R using the P-array and function f over 16 rounds for round := 0 to 15: L := L XOR P[round] R := f(L) XOR R swap values of L and R swap values of L and R R := R XOR P[16] L := L XOR P[17] procedure blowfish_decrypt(L, R): // Decrypts two 32-bit halves L and R using the P-array and function f over 16 rounds in reverse for round := 17 down to 2: L := L XOR P[round] R := f(L) XOR R swap values of L and R swap values of L and R R := R XOR P[1] L := L XOR P[0] // Initializes the P-array and S-boxes using the provided key, followed by key expansion // Initialize P-array with the key values key_position := 0 for i := 0 to 17: k := 0 for j := 0 to 3: k := (k shifted left by 8 bits) OR key[key_position] key_position := (key_position + 1) mod key_length P[i] := P[i] XOR k // Blowfish key expansion (521 iterations) L := 0, R := 0 for i := 0 to 17 by 2: blowfish_encrypt(L, R) P[i] := L P[i + 1] := R Figure 2: GitHub - Anuhya101/Email_Cryptography_Blowfish_Algorithm: Encrypting a ...
// Fill S-boxes by encrypting L and R for i := 0 to 3: for j := 0 to 255 by 2: blowfish_encrypt(L, R) S[i][j] := L S[i][j + 1] := R Bruce Schneier. "The Blowfish Encryption Algorithm". Bruce Schneier. "Products that Use Blowfish". "Standard Cryptographic Algorithm Naming: Blowfish". ZIP is an archive file format that supports lossless data compression. A ZIP file may contain one or more files or directories that may have been compressed. The ZIP file format permits a number of compression algorithms, though DEFLATE is the most common. This format was originally created in 1989 and was first implemented in PKWARE, Inc.'s PKZIP utility, as a replacement for the previous ARC compression format by Thom Henderson. The ZIP format was then quickly supported by many software utilities other than PKZIP. The ZIP format is natively supported on major operating systems (e.g. Android, ChromeOS, iOS, Linux, macOS, and Windows). It is typically built into an operating system's file management application. ZIP files generally use the file extensions .zip or .ZIP and the MIME media type application/zip. ZIP is used as a base file format by many programs, usually under a different name. When navigating a file system via a user interface, graphical icons representing ZIP files often appear as a document or other object prominently featuring a zipper.
2.0: (1993) File entries can be compressed with DEFLATE and use traditional PKWARE encryption (ZipCrypto). 2.1: (1996) Deflate64 compression support (claimed in APPNOTE 6.1.0 published much later). APPNOTE may not have been published for 2.1. 2.5: PKWARE DCL Implode compression. APPNOTE may not have been published for 2.5. 2.5: Deflate64 compression support (claimed in later user manuals, e.g. in 2004.) 4.0: (2000) Deflate64 compression support (according to information provided by Jim Peterson, Chief Scientist, PKWARE, to the Library of Congress; and APPNOTE 4.0). 4.5: (2001) Documented 64-bit zip format. 4.6: (2001) BZIP2 compression (not published online until the publication of APPNOTE 5.2) 5.0: (2002) SES: DES, Triple DES, RC2, RC4 supported for encryption (not published online until the publication of APPNOTE 5.2) 5.2: (2003) AES encryption support for SES (defined in APPNOTE 5.1 that was not published online) and AES from WinZip ("AE-x"); corrected version of RC2-64 supported for SES encryption. 6.1: (2004) Documented certificate storage.
6.2.0: (2004) Documented Central Directory Encryption. 6.3.0: (2006) Documented Unicode (UTF-8) filename storage. Expanded list of supported compression algorithms (LZMA, PPMd+), encryption algorithms (Blowfish, Twofish), and hashes. 6.3.1: (2007) Corrected standard hash values for SHA-256/384/512. 6.3.2: (2007) Documented compression method 97 (WavPack). 6.3.3: (2012) Document formatting changes to facilitate referencing the PKWARE Application Note from other standards using methods such as the JTC 1 Referencing Explanatory Report (RER) as directed by JTC 1/SC 34 N 1621.
6.3.4: (2014) Updates the PKWARE, Inc. office address. 6.3.5: (2018) Documented compression methods 16, 96 and 99, DOS timestamp epoch and precision, added extra fields for keys and decryption, as well as typos and clarifications. 6.3.6: (2019) Corrected typographical error. 6.3.7: (2020) Added Zstandard compression method ID 20. 6.3.8: (2020) Moved Zstandard compression method ID from 20 to 93, deprecating the former. Documented method IDs 94 and 95 (MP3 and XZ respectively). 6.3.9: (2020) Corrected a typo in Data Stream Alignment description. 6.3.10: (2022) Added several z/OS attribute values for APPENDIX B. Added several additional 3rd party Extra Field mappings. WinZip, starting with version 12.1, uses the extension .zipx for ZIP files that use compression methods newer than DEFLATE; specifically, methods BZip, LZMA, PPMd, Jpeg and Wavpack. The last 2 are applied to appropriate file types when "Best method" compression is selected.
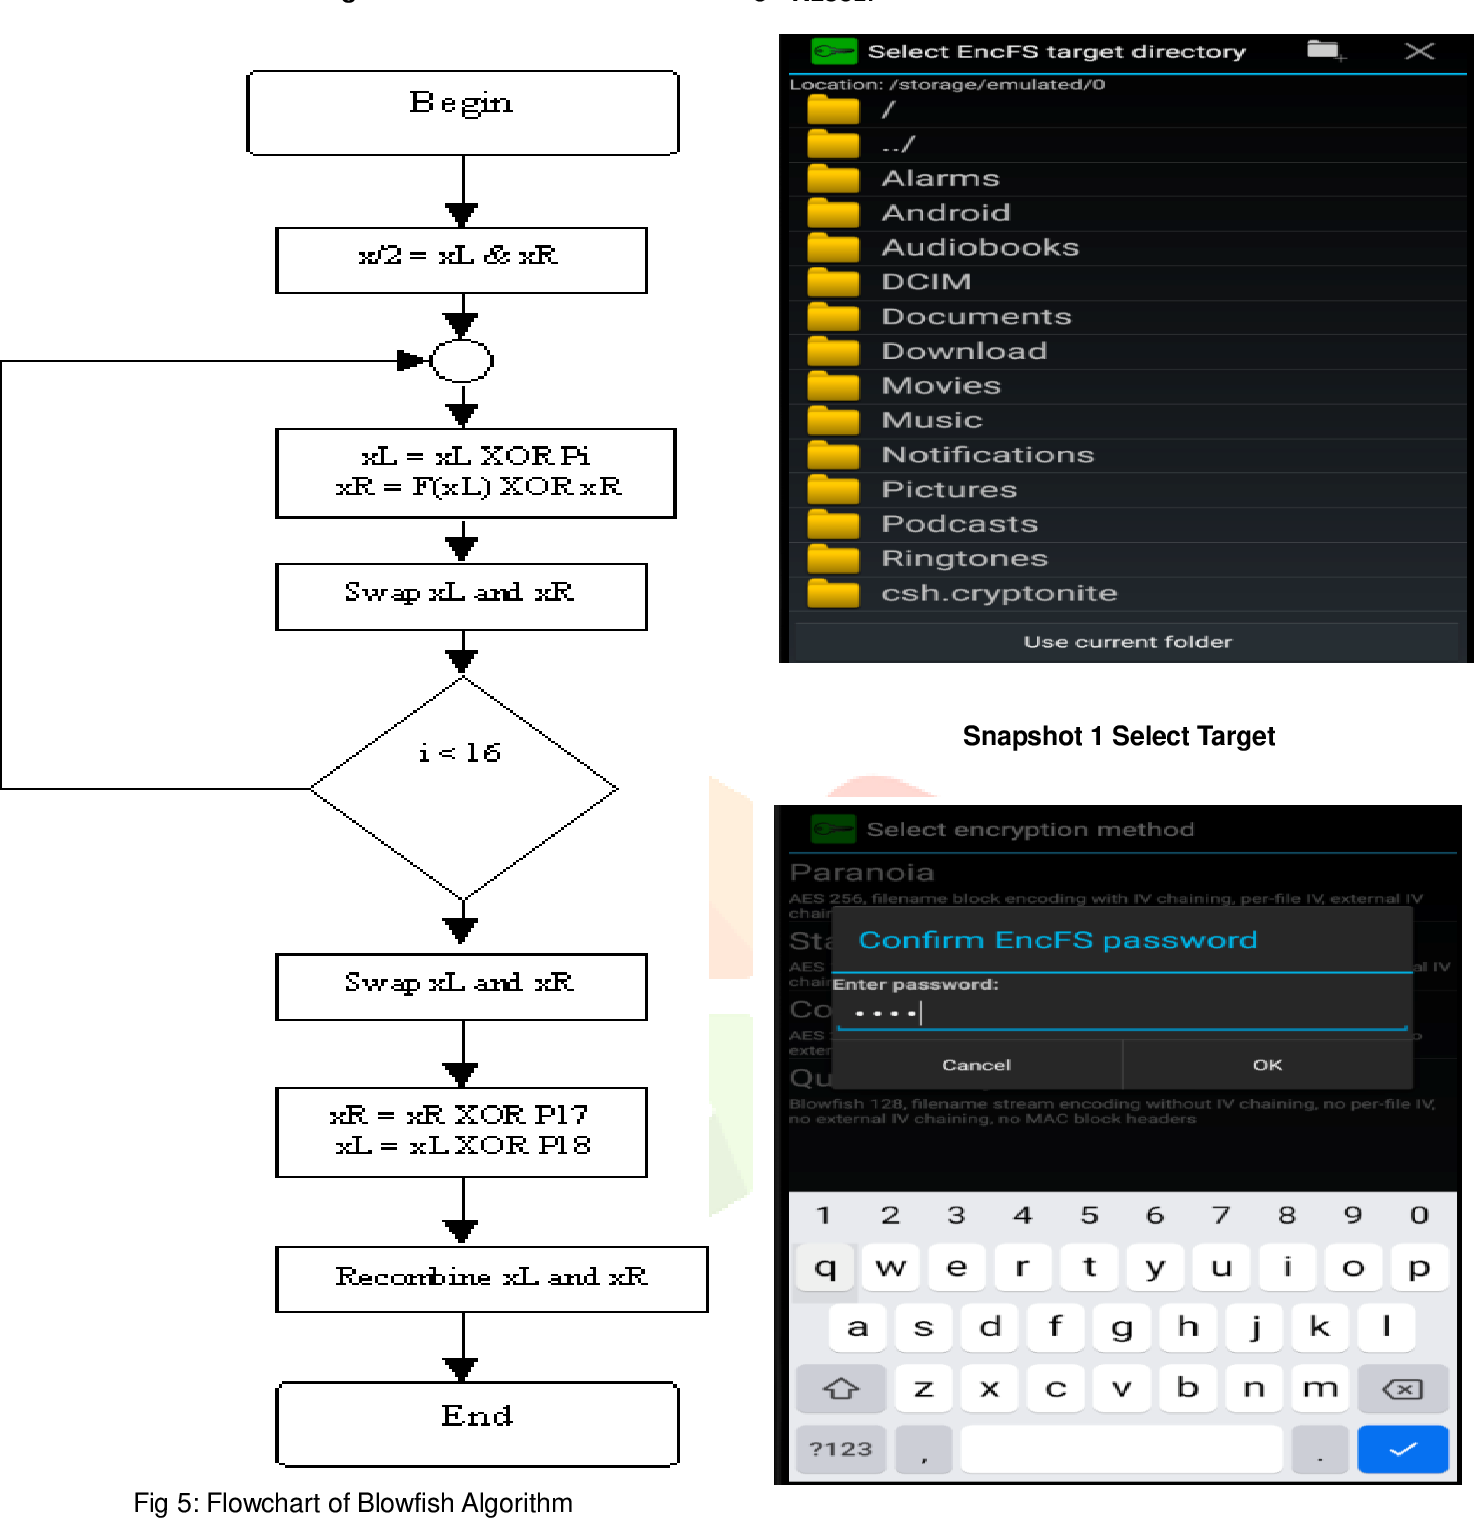
Figure 3: Figure 5 from Optimizing an Encryption File System On Android through ... Files in ZIP archives may only be stored uncompressed, or using the "deflate" compression (i.e. compression method may contain the value "0" - stored or "8" - deflated). The patent on the core "deflate" compression method expired in late 2010. The encryption features are prohibited. The digital signature features (from SES) are prohibited. The "patched data" features (from PKPatchMaker) are prohibited. Archives may not span multiple volumes or be segmented.
2. System Architecture & Core Working Principles A ZIP file is correctly identified by the presence of an end of central directory record which is located at the end of the archive structure in order to allow the easy appending of new files. If the end of central directory record indicates a non-empty archive, the name of each file or directory within the archive should be specified in a central directory entry, along with other metadata about the entry, and an offset into the ZIP file, pointing to the actual entry data. This allows a file listing of the archive to be performed relatively quickly, as the entire archive does not have to be read to see the list of files. The entries within the ZIP file also include this information, for redundancy, in a local file header. Because ZIP files may be appended to, only files specified in the central directory at the end of the file are valid. Scanning a ZIP file for local file headers is invalid (except in the case of corrupted archives), as the central directory may declare that some files have been deleted and other files have been updated. For example, we may start with a ZIP file that contains files A, B and C. File B is then deleted and C updated. This may be achieved by just appending a new file C to the end of the original ZIP file and adding a new central directory that only lists file A and the new file C. When ZIP was first designed, transferring files by floppy disk was common, yet writing to disks was very time-consuming. If you had a large zip file, possibly spanning multiple disks, and only needed to update a few files, rather than reading and re-writing all the files, it would be substantially faster to just read the old central directory, append the new files then append an updated central directory. The order of the file entries in the central directory need not coincide with the order of file entries in the archive. Each entry stored in a ZIP archive is introduced by a local file header with information about the file such as the comment, file size and file name, followed by optional "extra" data fields, and then the possibly compressed, possibly encrypted file data. The "Extra" data fields are the key to the extensibility of the ZIP format. "Extra" fields are exploited to support the ZIP64 format, WinZip-compatible AES encryption, file attributes, and higher-resolution NTFS or Unix file timestamps. Other extensions are possible via the "Extra" field. ZIP tools are required by the specification to ignore Extra fields they do not recognize. The ZIP format uses specific 4-byte "signatures" to denote the various structures in the file. Each file entry is marked by a specific signature. The end of central directory record is indicated with its specific signature, and each entry in the central directory starts with the 4-byte central file header signature. There is no BOF or EOF marker in the ZIP specification. Conventionally the first thing in a ZIP file is a ZIP entry, which can be identified easily by its local file header signature. However, this is not necessarily the case, as this is not required by the ZIP specification - most notably, a self-extracting archive will begin with an executable file header. Tools that correctly read ZIP archives must scan for the end of central directory record signature, and then, as appropriate, the other, indicated, central directory records. They must not scan for entries from the top of the ZIP file, because (as previously mentioned in this section) only the central directory specifies where a file chunk starts and that it has not been deleted. Scanning could lead to false positives, as the format does not forbid other data to be between chunks, nor file data streams from containing such signatures. However, tools that attempt to recover data from damaged ZIP archives will most likely scan the archive for local file header signatures; this is made more difficult by the fact that the compressed size of a file chunk may be stored after the file chunk, making sequential processing difficult. Most of the signatures end with the short integer 0x4b50, which is stored in little-endian ordering. Viewed as an ASCII string this reads "PK", the initials of the inventor Phil Katz. Thus, when a ZIP file is viewed in a text editor the first two bytes of the file are usually "PK". (DOS, OS/2 and Windows self-extracting ZIPs have an EXE before the ZIP so start with "MZ"; self-extracting ZIPs for other operating systems may similarly be preceded by executable code for extracting the archive's content on that platform.) The .ZIP specification also supports spreading archives across multiple file-system files.
Originally intended for storage of large ZIP files across multiple floppy disks, this feature is now used for sending ZIP archives in parts over email, or over other transports or removable media. The FAT filesystem of DOS has a timestamp resolution of only two seconds; ZIP file records mimic this. As a result, the built-in timestamp resolution of files in a ZIP archive is only two seconds, though extra fields can be used to store more precise timestamps. The ZIP format has no notion of time zone, so timestamps are only meaningful if it is known what time zone they were created in. In September 2006, PKWARE released a revision of the ZIP specification providing for the storage of file names using UTF-8, finally adding Unicode compatibility to ZIP.
The extra field contains a variety of optional data such as OS-specific attributes. It is divided into records, each with at minimum a 16-bit signature and a 16-bit length. A ZIP64 local file extra field record, for example, has the signature 0x0001 and a length of 16 bytes (or more) so that two 64-bit values (the uncompressed and compressed sizes) may follow. Another common local file extension is 0x5455 (or "UT") which contains 32-bit UTC UNIX timestamps. This is immediately followed by the compressed data.
This ordering allows a ZIP file to be created in one pass, but the central directory is also placed at the end of the file in order to facilitate easy removal of files from multiple-part (e.g. "multiple floppy-disk") archives, as previously discussed. On the other hand, the format of EOCD for ZIP64 is slightly different from the normal ZIP version. The EOCD64 is not necessarily the last record in the file. It is followed by a 20 byte End of Central Directory Locator, and the classic EOCD record.
The File Explorer in Windows XP does not support ZIP64, but the Explorer in Windows Vista and later do. Likewise, some extension libraries support ZIP64, such as DotNetZip, QuaZIP and IO::Compress::Zip in Perl. Python's built-in zipfile supports it since 2.5 and defaults to it since 3.4. OpenJDK's built-in java.util.zip supports ZIP64 from version Java 7. Android Java API support ZIP64 since Android 6.0. Mac OS Sierra's Archive Utility notably does not support ZIP64, and can create corrupt archives when ZIP64 would be required. However, the ditto command shipped with Mac OS will unzip ZIP64 files. More recent versions of Mac OS ship with info-zip's zip and unzip command line tools which do support Zip64: to verify run zip -v and look for "ZIP64_SUPPORT".
Check for the presence of the Unicode Path Extra Field, and if it exists, use the filename from it, encoded in UTF-8. Check for the presence of flag 11 in the General purpose bit flag field, and if it is set, consider the filename encoding in the "File name" field to be UTF-8. If the "packing OS" field contains the value 11 (NTFS, Windows), and the "version of the packer" field value is greater than or equal to 20, consider the filename encoding in the "File name" field to be the ANSI (Windows) encoding corresponding to the system locale if one can be determined; otherwise, use CP437. If the "packing OS" field contains the value 0 (FAT, DOS), and the "version of the packer" field value is between 25 and 40 inclusive, consider the filename encoding in the local header's "File name" field to be ANSI (Windows) encoding, and in the central header's "File name" field to be OEM (DOS) encoding, corresponding to the system locale if one can be determined; otherwise, use CP437. In other cases, if the "OS packing" field contains the value 0 (FAT, DOS), 6 (HPFS, OS/2), or 11 (NTFS, Windows), consider the filename encoding in the "File name" field to be OEM (DOS) encoding, corresponding to the system locale if one can be determined; otherwise, use CP437. In all other cases, consider the filename encoding in the "File name" field to be the system encoding of operating system the unpacker is running on. If the wrong encoding is used to decode the file names, users end up seeing a chaotic set of characters, known as "mojibake", instead of letters of the national alphabet. The above algorithm tries its best to avoid such a result. Instead of the "system locale" and "system encoding", some programs let the user select the desired non-Unicode encoding. In 2016, this problem was solved in the far2l file and archive manager for Linux, BSD and Mac. In 2024, similar solution was added to the version of 7zip used in the Debian distribution and its derivatives, and to the version of unzip used in the Ubuntu distribution and its derivatives.
ISO/IEC 21320-1:2015 — Document Container File — Part 1: Core Zip Files: History, Explanation and Implementation Shrink, Reduce, and Implode: The Legacy Zip Compression Methods APPNOTE.TXT mirror Structure of PKZip file Format specifications, graphical tables EncFS is a Free (LGPL) FUSE-based cryptographic filesystem. It transparently encrypts files, using an arbitrary directory as storage for the encrypted files. Two directories are involved in mounting an EncFS filesystem: the source directory, and the mountpoint. Each file in the mountpoint has a specific file in the source directory that corresponds to it. The file in the mountpoint provides the unencrypted view of the one in the source directory. Filenames are encrypted in the source directory.
Files are encrypted using a volume key, which is stored either within or outside the encrypted source directory. A password is used to decrypt this key. EncFS has been declared dormant with no further updates by Valient Gough, the developer, on its GitHub page in May 2024. They recommend using gocryptfs instead. EncFS is probably safe as long as the adversary only gets one copy of the ciphertext and nothing more. EncFS is not safe if the adversary has the opportunity to see two or more snapshots of the ciphertext at different times. EncFS attempts to protect files from malicious modification, but there are serious problems with this feature.
Disk encryption Filesystem-level encryption List of cryptographic file systems List of file systems Blowfish is a symmetric block cipher that can be used as a drop-in replacement for DES or IDEA. It takes a variable-length key, from 32 bits to 448 bits, making it ideal for both domestic and exportable use. Blowfish was designed in 1993 by Bruce Schneier as a fast, free alternative to existing encryption algorithms. Since then it has been analyzed considerably, and it is slowly gaining acceptance as a strong encryption algorithm. Blowfish is not patented and license-free, and is available free for all uses.
Blowfish 2 was released in 2005. It has exactly the same design but has twice as many S tables and uses 64-bit integers instead of 32-bit integers. It no longer works on 64-bit blocks but on 128-bit blocks like AES. 128-bit block, 64 rounds, key up to 4224 bits. 3. Software Implementation, Frameworks & Protocols You may fork it and use it like any other source file in your project. You only need blowfish.hpp and blowfish.cpp files. Just modify the header as per your convenience.
If you are using CMake, the work is lot easier. You can add this as a git submodule. It isolates your project from this dependency. This library has no dependencies on any other code. Just a C++ compiler should be enough to build this. Although this library is supposed to be used under some other project, sometimes you may need to build this. Here are the prerequisites: A comprehensive Computer Security project demonstrating the Blowfish encryption algorithm through two distinct implementations: an educational manual walkthrough and a production-ready secure implementation .
Blowfish's 64-bit block size makes it vulnerable to birthday attacks (e.g., Sweet32) after ~32GB of data. Modern applications should always prefer AES-GCM or ChaCha20-Poly1305. The key schedule is the most mathematically intensive part of Blowfish. It ensures key sensitivity : changing one bit of the key affects roughly 50% of the subkey bits.
A dual-implementation of the Blowfish algorithm for Computer Security education. Features a from-scratch Feistel Network implementation and a production-grade secure version using PyCryptodome. Blowfish is an encryption technique designed by Bruce Schneier in 1993 as an alternative to the DES Encryption Technique . It is significantly faster than DES and provides a good encryption rate with no effective cryptanalysis technique found to date.
It is one of the first secure block ciphers not subject to any patents and hence freely available for anyone to use. It is a symmetric block cipher algorithm. P[0] = P[0] xor 1st 32-bits of input key P[1] = P[1] xor 2nd 32-bits of input key . . . P[i] = P[i] xor (i+1)th 32-bits of input key (roll over to 1st 32-bits depending on the key length) . . . P[17] = P[17] xor 18th 32-bits of input key (roll over to 1st 32-bits depending on key length) The resultant P-array holds 18 subkeys that is used during the entire encryption process The decryption process is similar to that of encryption and the subkeys are used in reverse{P[17] - P[0]}. The entire decryption process can be elaborated as: P[0] = P[0] xor 1st 32-bits of input key P[1] = P[1] xor 2nd 32-bits of input key . . . P[i] = P[i] xor (i+1)th 32-bits of input key (roll over to 1st 32-bits depending on the key length) . . . P[17] = P[17] xor 18th 32-bits of input key (roll over to 1st 32-bits depending on key length) The resultant P-array holds 18 subkeys that is used during the entire encryption process 4. Practical Deployment, Analysis & Case Studies Blowfish encryption algorithm, a symmetric key block cipher known for its simplicity and security.
Blowfish operates on 64-bit blocks and supports key lengths ranging from 32 to 448 bits. This implementation includes key generation, encryption, and the core Blowfish operations, such as the Feistel function and the P-array and S-boxes initialization. Through test cases and comparison with a reference Java implementation(GFG) the code demonstrates the correctness and reliability of the Blowfish encryption algorithm in a simplified form. Blowfish’s flexibility and efficiency make it a valuable choice for various secure data encryption applications.
The result of encrypting "123456abcd132536" with the key "aabb09182736ccdd" using the Blowfish encryption algorithm is a ciphertext. When decrypted, the ciphertext yields the original plaintext. Run the .ipynb file(blowfish_encrypt_decrypt.ipynb), while running the decrypt function, There may not be the desired decrypted text. just Run only the decrypt function again to get the desired result.
Developed a application for Image Encryption and Decryption. The Folder IMAGE_ENCRYPTION consists the files give the password.jpg as input or you can replace with any other jpg/jpeg file. the code processesss and saves the following files (Compressed_password.jpg, encode.bin, cipher.txt, decrpted_password.jpg) which are uploaded to the folder for reference. Make sure the jpg/jpeg and py/ipynb are in the same directory.
This implementation showcases the practical application of the Blowfish algorithm in securing audio data. The key initialization, generation, and encryption processes collectively contribute to enhancing the confidentiality and integrity of audio files. Key Initialization The Blowfish algorithm for audio encryption begins with initializing substitution boxes (S-Boxes) and permutation boxes (P-Boxes) essential for the encryption process. These boxes are initialized with predefined hexadecimal values and derived from the digits of pi. The folder AUDIO_ENCRYPTION consists the files after compiling This implementation showcases the practical application of the Blowfish algorithm in securing video data. The key initialization, generation, and encryption processes collectively contribute to enhancing the confidentiality and integrity of video files. The folder VIDEO_ENCRYPTION consista the files after compiling Blowfish is a popular choice for several reasons, It has undergone rigorous testing and proven its security. It achieves speed by leveraging built-in instructions on contemporary microprocessors for fundamental bit manipulation operations. Blowfish is open-source and available in the public domain.
Blowfish encryption algorithm, a symmetric key block cipher known for its simplicity and security. The key schedule is often considered the most complex and security-critical part of Blowfish. It pre-processes the user-supplied key to generate 18 subkeys (stored in a P-array, P[1] to P[18] ) and four 32-bit S-boxes (each with 256 entries: S[0][0] to S[3][255] ).
Initialization: The P-array and S-boxes are first initialized with a fixed string of digits from the mathematical constant ÏI (pi) . This provides a known, non-random, and non-secret starting point. This extensive process ensures that the S-boxes are key-dependent, a feature designed to strengthen the algorithm against certain types of cryptanalysis. The slowness of this key schedule is actually a security feature, making brute-force and dictionary key searches more time-consuming.
Once the subkeys are generated, encrypting a 64-bit plaintext block is relatively straightforward. The process is a classic 16-round Feistel network. 5. Performance Evaluation & Extended Technical Observations Let's denote the 64-bit plaintext block as two 32-bit halves: Left (L) and Right (R) .
Decryption is exactly the same process as encryption, but the subkeys (P-array entries) are used in reverse order ( P[18] down to P[1] ). This symmetry is the elegance of the Feistel network structure. The heart of Blowfish's non-linearity is the F-function . It takes a 32-bit input (e.g., R in a given round) and produces a 32-bit output. It works by dividing the 32-bit input into four 8-bit quarters: a, b, c, d .
The output is calculated as: F(R) = ( (S[0][a] + S[1][b] mod 2³²) XOR S[2][c] ) + S[3][d] mod 2³² This combination of addition modulo 2³² and XOR operations, applied to data from key-dependent S-boxes, provides strong confusion and diffusion. Since Blowfish is a block cipher, it must be used with a mode of operation to encrypt data longer than 64 bits.
Best Practice Recommendation: Prefer AES (AES-128, AES-192, or AES-256) for all new projects. The following example uses the cryptography library in Python, which provides a safe and high-level interface. Note that you must install the library first: pip install cryptography . Blowfish was a groundbreaking algorithm that served the cryptography community well for many years. Its design, featuring a complex key schedule and key-dependent S-boxes, was innovative and provided robust security against the threats of its time. Its speed and free license were key drivers for its adoption.
However, cryptography is a constantly evolving field. The primary limitation of BlowfishâIIits 64-bit block sizeâIIhas become a critical liability for modern applications that process large volumes of data. For this reason, Blowfish should be considered a legacy algorithm. When building new systems, the AES algorithm is the unequivocally recommended choice. It addresses the shortcomings of older ciphers and is supported by a global standard and ubiquitous hardware acceleration. Understanding Blowfish remains valuable for historical context and maintaining existing systems, but for forward-looking security, AES is the path forward.
This tutorial book is a collection of notes and sample codes written by the author while he was learning Blowfish cipher himself. Topics basic concepts of cipher and encryption; introduction of Blowfish cipher algorithm; 8366 Hex Digits of PI; Perl Crypt::Blowfish and Crypt::CBC, Crypt::CFB modules; OpenSSL Blowfish ciphers: bf-ecb, bf-cbc, bf-cfb, bf-ofb; PHP Mcrypt extension; Blowfish CFB-8 and OFB-8 operation modes. Updated in 2024 (Version v2.04) with minor changes.
Blowfish Cipher Tutorials - Herong's Tutorial Examples - Updated in 2024, by Herong Yang Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Blowfish%20%28cipher%29 • https://en.wikipedia.org/wiki/ZIP%20%28file%20format%29 • https://en.wikipedia.org/wiki/EncFS • https://github.com/avinal/blowfish • https://github.com/samayine/blowfish-encryption-demo • https://www.geeksforgeeks.org/java/blowfish-algorithm-with-examples/ • https://github.com/RakhilML/BLOWFISH_ALGORITHM • https://www.javathinking.com/blog/blowfish-encryption-algorithm/ • https://www.herongyang.com/Blowfish/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Blowfish Encryption Algorithm Implementation For Large Files.
[*] Metasploit Scan Running on Target Subnet for Blowfish Encryption Algorithm Implementation For Large Files... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |