Complete Technical Paper Content — Blue Team Defense Automation
Overview & System Context
Blue Team Defense Automation: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9554 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Neil Gilbert Siegel (born February 19, 1954) is an American computer scientist and computer engineer, known for his development of many key systems for the United States military, including the Blue-Force Tracking system, the U.S. Army's first unmanned air vehicle system, and the US Army forward-area air defense system. Several of his inventions also found their way into consumer products, such as hand-held devices (e.g., mobile GPS devices, smartphones, etc.) whose map displays automatically orient themselves to align with the real-world's cardinal points. He also participated in the development of techniques that are now widely-used in healthcare.
The U.S. National Medal of Technology and Innovation in 2023. Election to the US National Academy of Engineering in 2005. Election as a fellow of the International Core Academy of Sciences and Humanities in 2026. Selection as an IEEE Fellow (2011). The IEEE Simon Ramo Medal (2011), for systems engineering and systems science. Member (2017) and Fellow (2019), National Academy of Inventors. US Army Honorable Order of Saint Barbara, 1996. iCMG award for system architecture (2011) Northern Virginia Technology Council—CTO of the year award (2011) National Medal of Technology and Innovation (2023) Additional awards are listed on his website, https://neilsiegel.usc.edu/awards/.
GPS-enabled mobile devices Automatic orientation of a map display to match the geographic cardinal points (US Patent 5,672,840) Optimizing unicast protocols (including TCP) for use on low-bandwidth, wireless networks (US Patent 6,701,375) Performing many security administrative and control tasks remotely (US Patent 7,278,023) Managing and administering a large network of wireless devices (US Patent 6,212,559) Increasing battery life on GPS-enabled devices (US Patent 7,256,731) Siegel is an experienced musician who plays the flute, târ, ney, and kaval who has more than 1,500 concerts to his credit worldwide. He studied music with Iranian Sufi master Morteza Varzi for more than 20 years. He is a long-time member of Professional Musicians Local 47, American Federation of Musicians, AFL-CIO. He is married to Robyn Friend, a dancer, painter, writer, and singer, with whom he has performed all over the world during the last 30 years. He is the older brother of actor, singer, and comedian Jack Black, with whom he has collaborated on a number of fund-raising events for charity, most notably the pediatric hospice program of the TrinityCare Hospice, based in Torrance, California. He is on the board of several non-profit organizations, including the Providence Trinity Health Care Hospice Foundation, the Electric Infrastructure Security Council, and The Institute of Persian Performing Arts. Since 2013, he and his wife, Robyn, have operated their own charitable organization, The Siegel and Friend Foundation.
Figure 1: Open Source Tools for OT Defenders – ZeronTek Company Aart J. de Geus (born June 1954) is a co-founder and executive chair of Synopsys Inc., where he was CEO until January 2024. De Geus graduated with a master's degree in electrical engineering (1978) from the École Polytechnique Fédérale de Lausanne (Swiss Federal Institute of technology), EPFL, Switzerland followed by a Ph.D. from Southern Methodist University, Texas, United States, in 1985. De Geus was awarded an honorary Doctorate of Science degree from the University of Glasgow in 2022. De Geus is one of the original pioneers of electronic design automation (EDA), the software tools used in the semiconductor industry to design chips. De Geus was elected a member of the National Academy of Engineering in 2019 for leadership and technical contributions to logic synthesis for integrated circuits. He is also a fellow of IEEE and a Phil Kaufman Award winner. He received the IEEE Robert N. Noyce Medal for his leadership in the technology and business development of EDA, as well as the Robert N. Noyce award from the Semiconductor Industry Association. He is a board member of the Global Semiconductor Association (GSA) and the Silicon Valley Leadership Group. De Geus is also the lead guitarist of Silicon Valley's 'Legally Blue' blues band.
Control system security, or industrial control system (ICS) cybersecurity, is the prevention of (intentional or unintentional) interference with the proper operation of industrial automation and control systems. These control systems manage essential services including electricity, petroleum production, water, transportation, manufacturing, and communications. They rely on computers, networks, operating systems, applications, and programmable controllers, each of which could contain security vulnerabilities. The 2010 discovery of the Stuxnet worm demonstrated the vulnerability of these systems to cyber incidents.
The United States and other governments have passed cyber-security regulations requiring enhanced protection for control systems operating critical infrastructure. The term industrial control system (ICS) is the most widely recognized and is considered the standard term used to describe control system security. Under industrial control systems there are numerous subgroups. These include SCADA (Supervisory Control and Data Acquisition) security, DCS (Distributed Control System), and PLC (Programmable Logic Controller) environments. However, the term may also be referred to as automation and control systems (ACS). Automation and control systems (ACS) is the broader term that is frequently used in the context of engineering and manufacturing.
The IEC 62443 cybersecurity standards define processes, techniques and requirements for Automation and Control Systems (IACS). The IEC 62443 standards and technical reports are organized into four general categories called General, Policies and Procedures, System, Component, Profiles and Evaluation. The first category includes foundational information such as concepts, models and terminology. The second category of work products targets the Asset Owner. These address various aspects of creating and maintaining an effective IACS security program. The third category includes work products that describe system design guidance and requirements for the secure integration of control systems. Core in this is the zone and conduit design model. The fourth category includes work products that describe the specific product development and technical requirements of control system products. The fifth category provides profiles for industry-specific cybersecurity requirements according to IEC 62443-1-5. The sixth category defines assessment methodologies that ensure that assessment results are consistent and reproducible.
Figure 2: GitHub - A-poc/BlueTeam-Tools: Tools and Techniques for Blue Team ... Although it is not a standard, the NIST Cybersecurity Framework (NIST CSF) provides a high-level taxonomy of cybersecurity outcomes and a methodology to assess and manage those outcomes. It is intended to help private sector organizations that provide critical infrastructure with guidance on how to protect it. NIST Special Publication 800-82 Rev. 2 "Guide to Industrial Control System (ICS) Security" describes how to secure multiple types of Industrial Control Systems against cyber attacks while considering the performance, reliability, and safety requirements specific to ICS.
Certifications for control system security have been established by several global Certification Bodies. Most of the schemes are based on the IEC 62443 and describe test methods, surveillance audit policy, public documentation policies, and other specific aspects of their program. Certification for industrial control systems is becoming increasingly vital as the systems grow increasingly advanced. The IEC 62443 standard is not being used for both older ICS equipment as well as new devices like industrial IoT and cyber-physical systems. It is necessary that certification is done clearly and consistently across all aspects in order to ensure that different products can be tested fairly. Safety and security should also be checked together as a cyberattack on these systems can have dire physical damage. Certification programs are being updated to cover the new risks that come with control systems being more connected and modern.
This document is user-generated content (UGC). WPS Office is not responsible for its accuracy or copyright. If you believe this content violates your rights, please use the Report button. This repository contains a comprehensive Blue Team defense system for a Capture The Flag (CTF) simulation. The system is designed to detect and respond to Red Team activities, protect the flag, and log all defensive actions.
Figure 3: GitHub - A-poc/BlueTeam-Tools: Tools and Techniques for Blue Team ... For a comprehensive overview of the entire Autonomous AI CTF Battle System, see PROJECT_SUMMARY.md . This Blue Team defense system provides a robust and adaptive defense against Red Team attacks in the CTF simulation. It demonstrates effective security monitoring, threat detection, and incident response capabilities.
Welcome to the Ultimate Blue Teaming Roadmap . This repository covers defensive security strategies, threat detection, and system hardening. The 2026 update emphasizes behavioral analytics, cloud-native defense, and zero-trust architectures. Defensive security is shifting from reactive to proactive resilience. Key trends for 2026 include: A complete roadmap for BlueTeam from basic to advanced, featuring free and paid paths.
This wiki aims to document useful blue team patterns and resources that can be used to rapidly kick-start a functional defensive security team at your organisation. Please use the navigation panel or the icon on the top left to browse various blue team operational topics. Blue team protocols comprise systematically organized defensive practices, operational workflows, and formalized roles central to the continuous protection, monitoring, and incident response capacities of enterprise cybersecurity, with particular elaboration in ML and AI control contexts. Across domains, blue team constructs are characterized by distinct responsibility demarcation (in the color team paradigm), rigorous integration with adversarial testing outputs, and automated, metric-driven workflows at all stages of pipeline defense. Contemporary research underscores the necessity of risk-prioritization frameworks, multiphase monitoring, defense-in-depth, and standardized, action-oriented playbooks for operationalizing blue team efficacy across software, ML, and AI agent infrastructures.
Blue team protocols derive from the defense phase of the color-team model ("Build–Attack–Defend"), as established in the context of ML and cybersecurity ( Kalin et al., 2021 ). The blue team assumes explicit responsibility for: This foundation extends to the AI control protocol and autonomous forensics agent domains, reinforcing the core role of blue teams as the operators of defense logic, evaluators of adversarial resilience, responders to complex threats, and institutional stewards of incident response and mitigation ( Terekhov et al., 10 Oct 2025 , Fumero et al., 28 Aug 2025 , Meng et al., 28 Sep 2025 ).
Blue team protocols are formalized as multi-step, reproducible workflows that systematically address the entire defensive and incident-response cycle. Canonical phases include: R = N A × P exploit × V impact × T time − 1 R = N_A \times P_\text{exploit} \times V_\text{impact} \times T_\text{time}^{-1} R = N A I × P exploit I × V impact I × T time − 1 where R R R is residual risk, N A N_A N A I the adversary count, P exploit P_\text{exploit} P exploit I the exploit probability, V impact V_\text{impact} V impact I the impact score, and T time T_\text{time} T time I the detection/remediation lag.
In autonomous forensics and LLM-assisted threat hunting, explicit pipeline protocols (e.g., CyberSleuth, CyberTeam) emphasize step-wise ingestion (e.g., PCAPs, logs), sub-agent parsing, evidence weighting, CVE correlation, severity scoring (e.g., CVSS), and playbook generation ( Fumero et al., 28 Aug 2025 , Meng et al., 28 Sep 2025 ). Continuous coordination with other color teams propagates defensive best practices, ensures alignment of patched artifacts in main codebases, and validates operational success criteria.
Blue team operations depend on specific frameworks and continuous tracking of quantitative metrics: In autonomous forensics, toolchains include PCAP readers via tshark, Google Custom Search for web-based CVE lookup, vector DBs for memory management, and direct API integrations (e.g., NVD REST) ( Fumero et al., 28 Aug 2025 ). Formal methods are explicitly advocated in password security domains, with Passlab leveraging ADTree-based risk modeling, Zipf-law password modeling, and Coq-based verification/extraction pipelines for "correct-by-construction" policy enforcement ( Johnson, 2020 ).
Recent research ( Terekhov et al., 10 Oct 2025 ) identifies major failure modes in LLM-based blue team protocol design, specifically regarding monitor-based defense logic against adaptive prompt injection attacks . Protocol enhancements include standardized evaluation procedures (injection-aware red teaming, full-statistical ROC/FNR reporting) and operational red-teaming guidelines (continuous prompt injection discovery, surprise audits).
A plausible implication is that operational blue teams in LLM or AI agent environments should regard prompt injection red teaming, multiclass monitoring, and continual protocol randomization as non-optional components of robust defense. The development of standardized, modular threat-hunting pipelines has yielded substantial gains over open-ended reasoning chains in blue team contexts ( Meng et al., 28 Sep 2025 ). The CyberTeam framework exemplifies this by specifying a 30-task dependency-resolved workflow, decomposing investigations from infrastructure extraction to advisory correlation: The systematic application of these modular protocols is increasingly recognized as essential for maintaining blue team performance as attack complexity and automation accelerate.
Synthesis of the current literature yields a set of best-practice mandates for robust blue team protocol implementation: These practices, grounded in metric-driven evaluation and modular, automation-friendly workflow design, define the contemporary state of effective blue team protocol deployment across ML, software, and AI agent domains. A collection of TryHackMe Blue Team labs documenting hands-on learning in cybersecurity defense, incident response, and system/network monitoring. Includes summaries, methodologies, and key takeaways from each lab to showcase practical skills in real-world blue team scenarios.
Welcome to my TryHackMe Blue Team Labs repository! This collection documents my hands-on learning focused on Security Operations (SOC), threat detection, system monitoring, and defensive security practices . II Note: This repository does not contain flags or lab answers. It focuses on concepts, methodologies, and key takeaways to maintain TryHackMe’s learning integrity.
A collection of TryHackMe Blue Team labs documenting hands-on learning in cybersecurity defense, incident response, and system/network monitoring. Includes summaries, methodologies, and key takeaways from each lab to showcase practical skills in real-world blue team scenarios. This github repository contains a collection of 70+ tools and resources that can be useful for blue teaming activities .
Some of the tools may be specifically designed for blue teaming, while others are more general-purpose and can be adapted for use in a blue teaming context. The materials in this repository are for informational and educational purposes only. They are not intended for use in any illegal activities.
Learn from Blue Teamers with a collection of Blue Teaming Tips. These tips cover a range of tactics, tools, and methodologies to improve your blue teaming abilities. Description: 'Malware Analysis Tip - Use Process Hacker to watch for suspicious .NET assemblies in newly spawned processes. Combined with DnSpy - it's possible to locate and extract malicious payloads without needing to manually de-obfuscate.' Description: On Windows, it's common to see threat actors achieve initial execution via malicious script files masquerading as Microsoft Office files. A nice way to prevent this attack chain is to alter the default application associated with these files (HTA, JS, VBA, VBS) to notepad.exe . Now when a user is successfully tricked into clicking a HTA file on disk it will open the script in notepad and execution will not occur .
Description: Cryptojacking malware is becoming more suffisticated, with mining malware leveraging DLL sideloading to hide on machine and reducing CPU load to stay below detection thresholds. One thing they all have in common is they have to make connections to mining pools, this is where we can find them. Monitor your proxy and DNS logs for connections containing common mining pool strings (e.g *xmr.* OR *pool.com OR *pool.org OR pool.* ).
Description: 'After decoding base64 for Unicode string during malware analysis, you may encounter null bytes. Keep your code readable by using the "Remove null bytes" operation in CyberChef'. Description: Did you know you can recover scrubbed metadata from a PDF that wasn't scrubbed properly? The changes are incremental, and the history is stored in the PDF. This command removes the "updates" to the PDF metadata: Threathunt.app is a collection of tools that support internal and external threat hunting operations.
Note: Some tools are paid. Offers a free 14 day trial for full toolkit access (no payment info needed). Hunt.io is a cyber threat intelligence and threat hunting platform that maps and tracks malicious internet infrastructure, such as command-and-control (C2) servers, phishing sites, and rogue IP addresses. Validin is a commercial internet intelligence and threat-hunting platform that aggregates historical DNS data, host responses, SSL certificates, and open-source intelligence (OSINT) to help cybersecurity teams track and investigate malicious online infrastructure.
Tools for scanning and mapping out the network, discovering devices and services, and identifying potential vulnerabilities. Nmap (short for Network Mapper) is a free and open-source network scanner tool used to discover hosts and services on a computer network, and to probe for information about their characteristics. It can be used to determine which ports on a network are open and what services are running on those ports. Including the ability to identify security vulnerabilities on the network.
Image used from https://kirelos.com/nmap-version-scan-determining-the-version-and-available-services/ A specialized tool designed to automate the process of detecting vulnerabilities in web applications, networks, and infrastructure. Nuclei uses pre-defined templates to probe a target and identify potential vulnerabilities. It can be used to test a single host or a range of hosts, and can be configured to run a variety of tests to check for different types of vulnerabilities.
A port scanner that is similar to nmap, but is much faster and can scan a large number of ports in a short amount of time. Masscan uses a novel technique called "SYN scan" to scan networks, which allows it to scan a large number of ports very quickly. It's a cross-platform tool, designed to be fast and easy to use, and can scan an entire network or a range of IP addresses to find live hosts.
2. System Architecture & Core Working Principles Angry IP Scanner can also detect the hostname and MAC address of a device, and can be used to perform basic ping sweeps and port scans. ZMap is a network scanner designed to perform comprehensive scans of the IPv4 address space or large portions of it.
On a typical desktop computer with a gigabit Ethernet connection, ZMap is capable scanning the entire public IPv4 address space in under 45 minutes. Image used from https://www.hackers-arise.com/post/zmap-for-scanning-the-internet-scan-the-entire-internet-in-45-minutes It crawls the internet for assets, allowing users to search for specific devices and view information about them.
This information can include the device's IP address, the software and version it is running, and the type of device it is. Tools for identifying, prioritizing, and mitigating vulnerabilities in the network and on individual devices. OpenVAS is an open-source vulnerability scanner that helps identify security vulnerabilities in software and networks. It is a tool that can be used to perform network security assessments and is often used to identify vulnerabilities in systems and applications so that they can be patched or mitigated.
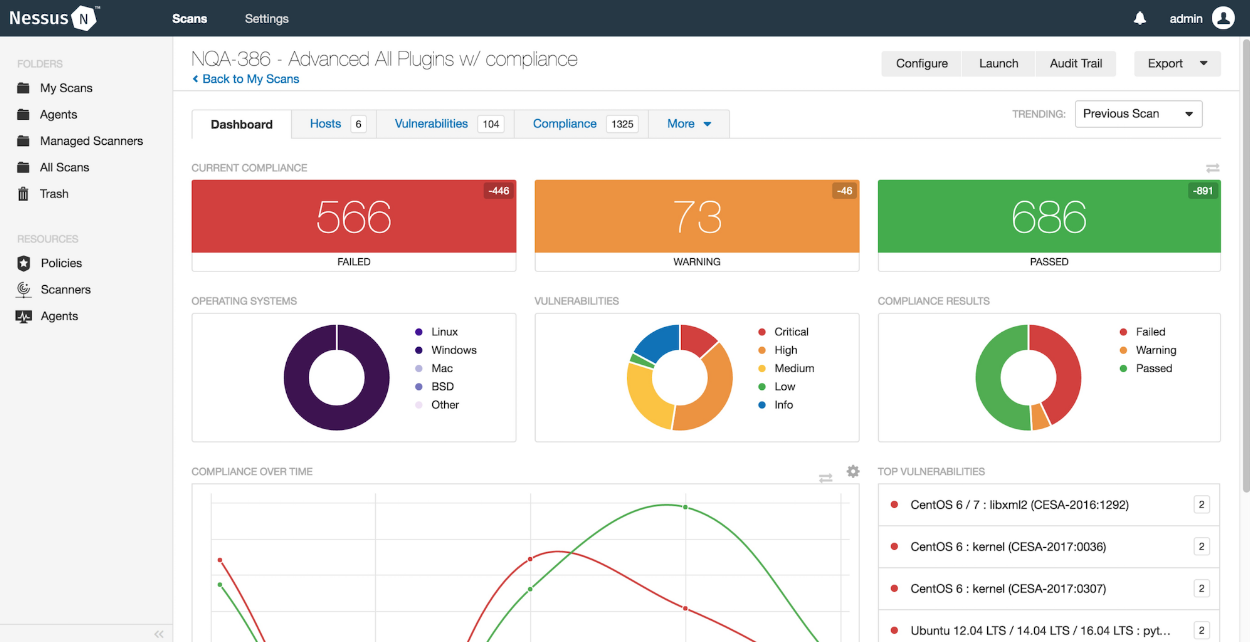
OpenVAS is developed by the Greenbone Networks company and is available as a free and open-source software application. Visit https://127.0.0.1:9392 , accept the SSL certificate popup and login with admin credentials: Nessus is a vulnerability scanner that helps identify and assess the vulnerabilities that exist within a network or computer system.
It is a tool that is used to perform security assessments and can be used to identify vulnerabilities in systems and applications so that they can be patched or mitigated. Nexpose is a vulnerability management tool developed by Rapid7. It is designed to help organizations identify and assess vulnerabilities in their systems and applications in order to mitigate risk and improve security.
Nexpose can be used to scan networks, devices, and applications in order to identify vulnerabilities and provide recommendations for remediation. It also offers features such as asset discovery, risk prioritization, and integration with other tools in the Rapid7 vulnerability management platform.
HackerOne is a bug bounty management company that can be used to create and manage bug bounty programs for your business. Bug bounty programs are a great way to outsource external vulnerability assessments, with the platform offering both private and public programs with the ability set program scopes and rules of engagement.
HackerOne also offer initial triage and management of external bug reports from researchers, with the ability to compensate researchers directly through the platform. Lynis is a security auditing tool for Linux, macOS, and UNIX-based systems. It assists with compliance testing (HIPAA/ISO27001/PCI DSS) and system hardening.
It performs an in-depth security scan and runs on the system itself. The primary goal is to test security defenses and provide tips for further system hardening. It will also scan for general system information, vulnerable software packages, and possible configuration issues. Tools for collecting and analyzing security logs and other data sources to identify potential threats and anomalous activity.
Sysmon is a Windows system monitor that tracks system activity and logs it to the Windows event log. It provides detailed information about system activity, including process creation and termination, network connections, and changes to file creation time. Sysmon can be configured to monitor specific events or processes and can be used to alert administrators of suspicious activity on a system.
Image used from https://nsaneforums.com/topic/281207-sysmon-5-brings-registry-modification-logging/ Kibana is an open-source data visualization and exploration tool that is often used for log analysis in combination with Elasticsearch. Kibana provides a user-friendly interface for searching, visualizing, and analyzing log data, which can be helpful for identifying patterns and trends that may indicate a security threat.
Kibana can be used to analyze a wide range of data sources, including system logs, network logs, and application logs. It can also be used to create custom dashboards and alerts to help security teams stay informed about potential threats and respond quickly to incidents. Kibana provides a range of visualization tools that can help you identify patterns and trends in your log data. You can use these tools to create custom dashboards that display relevant metrics and alerts.
Kibana can be configured to send alerts when it detects certain patterns or anomalies in your log data. You can set up alerts to notify you of potential security threats, such as failed login attempts or network connections to known malicious IP addresses. Image used from https://www.pinterest.co.uk/pin/analysing-honeypot-data-using-kibana-and-elasticsearch--684758318328369269/ Logstash is a open-source data collection engine with real-time pipelining capabilities. It is a server-side data processing pipeline that ingests data from a multitude of sources simultaneously, transforms it, and then sends it to a "stash" like Elasticsearch.
Logstash has a rich set of plugins, which allows it to connect to a variety of sources and process the data in multiple ways. It can parse and transform logs, translate data into a structured format, or send it to another tool for further processing. With its ability to process large volumes of data quickly, Logstash is an integral part of the ELK stack (Elasticsearch, Logstash, and Kibana) and is often used to centralize, transform, and monitor log data.
Image used from https://www.elastic.co/guide/en/logstash/current/logstash-modules.html When used with Elasticsearch and Kibana (or Splunk), it works as a self-hosted open source alternative to commercial DMARC report processing services such as Agari Brand Protection, Dmarcian, OnDMARC, ProofPoint Email Fraud Defense, and Valimail.
As a business, phishing can cause reputational and financial damage to you and your customers. Being able to proactively identify phishing infrastructure targeting your business helps to reduce the risk of these damages. Phish catcher allows you to catch possible phishing domains in near real time by looking for suspicious TLS certificate issuances reported to the Certificate Transparency Log (CTL) via the CertStream API.
"Suspicious" issuances are those whose domain name scores beyond a certain threshold based on a configuration file. Maltrail is a malicious traffic detection system, utilizing publicly available lists containing malicious and/or generally suspicious trails, along with static trails compiled from various AV reports and custom user defined lists. A trail can be anything from domain name, URL, IP address or HTTP User-Agent header value.
Autoruns is a tool developed by Sysinternals that allows you to view all of the locations in Windows where applications can insert themselves to launch at boot or when certain applications are opened. Malware often takes advantages of these locations to ensure that it runs whenever your computer boots up. Autoruns conveniently includes a non-interactive command line utility. This code generates a CSV of Autoruns entries, converts them to JSON, and finally inserts them into a custom Windows Event Log. By doing this, we can take advantage of our existing WEF infrastructure to get these entries into our SIEM and start looking for signs of malicious persistence on endpoints and servers.
ProcFilter is a process filtering system for Windows with built-in YARA integration. YARA rules can be instrumented with custom meta tags that tailor its response to rule matches. It runs as a Windows service and is integrated with Microsoft's ETW API , making results viewable in the Windows Event Log. Installation, activation, and removal can be done dynamically and does not require a reboot.
ProcFilter's intended use is for malware analysts to be able to create YARA signatures that protect their Windows environments against a specific threat. It does not include a large signature set. Think lightweight, precise, and targeted rather than broad or all-encompassing. ProcFilter is also intended for use in controlled analysis environments where custom plugins can perform artifact-specific actions.
Note: Unpatched Windows 7 systems require hotfix 3033929 to load the driver component. More information can be found here. Velociraptor is a unique, advanced open-source endpoint monitoring, digital forensic and cyber response platform. It was developed by Digital Forensic and Incident Response (DFIR) professionals who needed a powerful and efficient way to hunt for specific artifacts and monitor activities across fleets of endpoints. Velociraptor provides you with the ability to more effectively respond to a wide range of digital forensic and cyber incident response investigations and data breaches: SysmonSearch makes event log analysis more effective and less time consuming, by aggregating event logs generated by Microsoft's Sysmon.
Once Elasticsearch and Kibana configurations have been modified, restart the services and navigate to your Kibana interface. The SysmonSearch ribbon should be visible. Canarytokens are like motion sensors for your networks, computers and clouds. You can put them in folders, on network devices and on your phones.
Place them where nobody should be poking around and get a clear alarm if they are accessed. They are designed to look juicy to attackers to increase the likelihood that they are opened (and they are completely free). Living off the land binaries (LOLBins) are legitimate Windows executables that can be used by threat actors to carry out malicious activities without raising suspicion.
Using LOLBins allows attackers to blend in with normal system activity and evade detection, making them a popular choice for malicious actors. The LOLBAS project is a MITRE mapped list of LOLBINS with commands, usage and detection information for defenders. Use the information for detection opportunities to harden your infrastructure against LOLBIN usage.
GTFOBins (short for "Get The F* Out Binaries") is a collection of Unix binaries that can be used to escalate privileges, bypass restrictions, or execute arbitrary commands on a system. They can be used by threat actors to gain unauthorized access to systems and carry out malicious activities. The GTFOBins project is a list of Unix binaries with command and usage information for attackers. This information can be used to implement unix detections.
Filesec is a list of file extensions that can be used by attackers for phishing, execution, macros etc. This is a nice resource to understand the malicious use cases of common file extentions and ways that you can defend against them. Each file extension page contains a description, related operating system and recommendations.
KQL stands for "Kusto Query Language", and it is a query language used to search and filter data in Azure Monitor logs. It is similar to SQL, but is more optimized for log analytics and time-series data. 3. Software Implementation, Frameworks & Protocols KQL query language is particularly useful for blue teamers because it allows you to quickly and easily search through large volumes of log data to identify security events and anomalies that may indicate a threat.
KQL Search is a web app created by @ugurkocde that aggregates KQL queries that are shared on GitHub. Malware authors spend a great deal of time and effort to develop complex code to perform malicious actions against a target system. It is crucial for malware to remain undetected and avoid sandbox analysis, antiviruses or malware analysts. With this kind of technics, malware are able to pass under the radar and stay undetected on a system. The goal of this free database is to centralize the information about malware evasion techniques.
The project aims to provide Malware Analysts and Defenders with actionable insights and detection capabilities to shorten their response times. Chainsaw provides a powerful ‘first-response’ capability to quickly identify threats within Windows forensic artefacts such as Event Logs and MFTs. Chainsaw offers a generic and fast method of searching through event logs for keywords, and by identifying threats using built-in support for Sigma detection rules, and via custom Chainsaw detection rules.
Adversaries attempt to bypass signature based/pattern matching/blacklist techniques by introducing random: filenames, service names, workstation names, domains, hostnames, SSL cert subjects and issuer subjects, etc. Freq is a python API designed by Mark Baggett to handle mass entropy testing. It was designed to be used in conjunction with a SIEM solutions but can work with anything that can submit a web request.
The main principle is the creation of yara rules from strings found in malware files while removing all strings that also appear in goodware files. Therefore yarGen includes a big goodware strings and opcode database as ZIP archives that have to be extracted before the first use. The rule generation process also tries to identify similarities between the files that get analyzed and then combines the strings to so called super rules. The super rule generation does not remove the simple rule for the files that have been combined in a single super rule. This means that there is some redundancy when super rules are created. You can suppress a simple rule for a file that was already covered by super rule by using --nosimple.
With EmailAnalyzer you can able to analyze your suspicious emails. You can extract headers, links and hashes from the .eml file VCG is an automated code security review tool that handles C/C++, Java, C#, VB and PL/SQL. It has a few features that should hopefully make it useful to anyone conducting code security reviews, particularly where time is at a premium: CyberChef is a free, web-based tool that allows users to manipulate and transform data using a wide range of techniques.
With CyberChef, you can perform a wide range of operations on data, such as converting between different data formats (e.g., hexadecimal, base64, ASCII), encoding and decoding data, searching and replacing text etc. The tool also includes a recipe system, which allows you to save and share data manipulation workflows with others. PersistenceSniper is a Powershell module that can be used by Blue Teams, Incident Responders and System Administrators to hunt persistences implanted in Windows machines.
PersistenceSniper is able to detect a wide range of persistence techniques, the full list of which can be found here . Download the .zip from GitHub and move it to the machine that you want to run the tool from. Image used from https://hackers-arise.com/powershell-for-dfir-part-2-finding-persistence/ Tools for gathering and analyzing intelligence about current and emerging threats, and for generating alerts about potential threats.
Maltego is a commercial threat intelligence and forensics tool developed by Paterva. It is used by security professionals to gather and analyze information about domains, IP addresses, networks, and individuals in order to identify relationships and connections that might not be immediately apparent. Maltego uses a visual interface to represent data as entities, which can be linked together to form a network of relationships. It includes a range of transforms, which are scripts that can be used to gather data from various sources, such as social media, DNS records, and WHOIS data.
Maltego is often used in conjunction with other security tools, such as SIEMs and vulnerability scanners, as part of a comprehensive threat intelligence and incident response strategy. MISP (short for Malware Information Sharing Platform) is an open-source platform for sharing, storing, and correlating Indicators of Compromise (IOCs) of targeted attacks, threats, and malicious activity.
MISP includes a range of features, such as real-time sharing of IOCs, support for multiple formats, and the ability to import and export data to and from other tools. It also provides a RESTful API and various data models to facilitate the integration of MISP with other security systems. In addition to its use as a threat intelligence platform, MISP is also used for incident response, forensic analysis, and malware research.
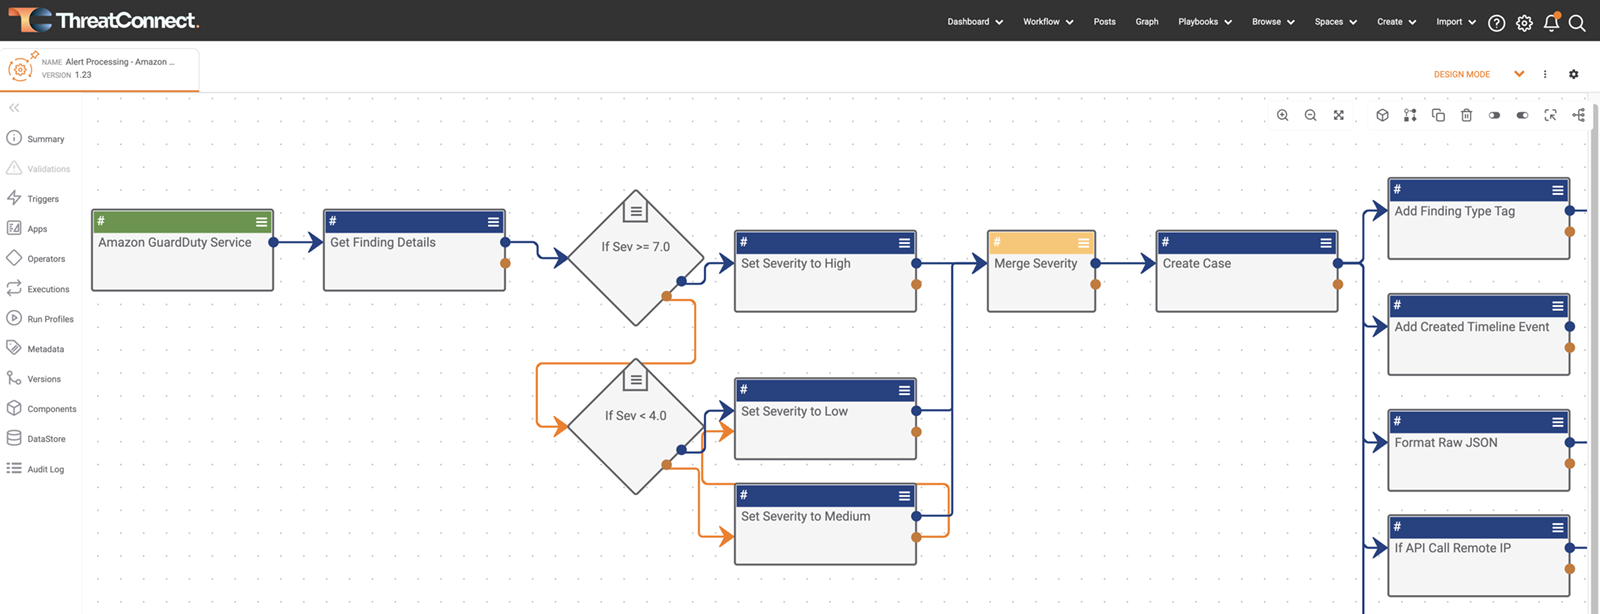
Image used from http://www.concordia-h2020.eu/blog-post/integration-of-misp-into-flowmon-ads/ ThreatConnect is a threat intelligence platform that helps organizations aggregate, analyze, and act on threat data. It is designed to provide a single, unified view of an organization's threat landscape and enable users to collaborate and share information about threats.
The platform includes a range of features for collecting, analyzing, and disseminating threat intelligence, such as a customizable dashboard, integration with third-party data sources, and the ability to create custom reports and alerts. It is intended to help organizations improve their security posture by providing them with the information they need to identify, prioritize, and respond to potential threats.
This is a library of adversary emulation plans to enable you to evaluate your defensive capabilities against real-world threats. Emulation plans are an essential component for organizations looking to prioritize defenses against behavior from specific threats. The TTPs outlined in this resource can be used to design specific threat emulation activities to test your organisations defenses against specific threat actors.
Image used from https://github.com/center-for-threat-informed-defense/adversary_emulation_library Tools for creating and maintaining an incident response plan, including templates and best practices for responding to different types of incidents. The NIST Cybersecurity Framework (CSF) is a framework developed by the National Institute of Standards and Technology (NIST) to help organizations manage cybersecurity risks. It provides a set of guidelines, best practices, and standards for implementing and maintaining a robust cybersecurity program.
The framework is organized around five core functions: Identify, Protect, Detect, Respond, and Recover. These functions provide a structure for understanding and addressing the various components of cybersecurity risk. The CSF is designed to be flexible and adaptable, and it can be customized to fit the specific needs and goals of an organization. It is intended to be used as a tool for improving an organization's cybersecurity posture and for helping organizations better understand and manage their cybersecurity risks.
Image used from https://www.dell.com/en-us/blog/strengthen-security-of-your-data-center-with-the-nist-cybersecurity-framework/ An incident response plan is a set of procedures that a company puts in place to manage and mitigate the impact of a security incident, such as a data breach or a cyber attack.
The theory behind an incident response plan is that it helps a company to be prepared for and respond effectively to a security incident, which can minimize the damage and reduce the chances of it happening again in the future. To minimize the impact of a security incident: An incident response plan helps a company to identify and address the source of a security incident as quickly as possible, which can help to minimize the damage and reduce the chances of it spreading.
To meet regulatory requirements: Many industries have regulations that require companies to have an incident response plan in place. For example, the Payment Card Industry Data Security Standard (PCI DSS) requires merchants and other organizations that accept credit cards to have an incident response plan. To protect reputation: A security incident can damage a company's reputation, which can lead to a loss of customers and revenue. An incident response plan can help a company to manage the situation and minimize the damage to its reputation.
To reduce the cost of a security incident: The cost of a security incident can be significant, including the cost of remediation, legal fees, and lost business. An incident response plan can help a company to minimize these costs by providing a roadmap for responding to the incident. Image used from https://www.ncsc.gov.uk/collection/incident-management/incident-response Ransomware is a type of malicious software that encrypts a victim's files. The attackers then demand a ransom from the victim to restore access to the files; hence the name ransomware.
The theory behind a ransomware response plan is that it helps a company to be prepared for and respond effectively to a ransomware attack, which can minimize the impact of the attack and reduce the chances of it happening again in the future. To minimize the impact of a ransomware attack: A ransomware response plan helps a company to identify and address a ransomware attack as quickly as possible, which can help to minimize the damage and reduce the chances of the ransomware spreading to other systems.
To protect against data loss: Ransomware attacks can result in the loss of important data, which can be costly and disruptive for a business. A ransomware response plan can help a company to recover from an attack and avoid data loss. To protect reputation: A ransomware attack can damage a company's reputation, which can lead to a loss of customers and revenue. A ransomware response plan can help a company to manage the situation and minimize the damage to its reputation.
To reduce the cost of a ransomware attack: The cost of a ransomware attack can be significant, including the cost of remediation, legal fees, and lost business. A ransomware response plan can help a company to minimize these costs by providing a roadmap for responding to the attack. This is a “first aid” style of guidance for cybersecurity to help you prepare for a crisis and limit the potential damage in a crisis.
This includes tips and guidance for technical, operational, legal, and communications aspects of a major cybersecurity incident. Image used from https://info.microsoft.com/rs/157-GQE-382/images/EN-US-CNTNT-emergency-doc-digital.pdf A curated list of tools and resources for security incident response, aimed to help security analysts and DFIR teams.
This is a great resource full of links for different aspects of incident response, including: Tools for detecting and analyzing malware, including antivirus software and forensic analysis tools. VirusTotal is a website and cloud-based tool that analyzes and scans files, URLs, and software for viruses, worms, and other types of malware.
When a file, URL, or software is submitted to VirusTotal, the tool uses various antivirus engines and other tools to scan and analyze it for malware. It then provides a report with the results of the analysis, which can help security professionals and blue teams identify and respond to potential threats. VirusTotal can also be used to check the reputation of a file or URL, and to monitor for malicious activity on a network.
IDA (Interactive Disassembler) is a powerful tool used to reverse engineer and analyze compiled and executable code. It can be used to examine the inner workings of software, including malware, and to understand how it functions. IDA allows users to disassemble code, decompile it into a higher-level programming language, and view and edit the resulting source code. This can be useful for identifying vulnerabilities, analyzing malware, and understanding how a program works.
4. Practical Deployment, Analysis & Case Studies IDA can also be used to generate graphs and charts that visualize the structure and flow of code, which can make it easier to understand and analyze. Ghidra is a free, open-source software reverse engineering tool developed by the National Security Agency (NSA). It is used to analyze compiled and executable code, including malware.
Ghidra allows users to disassemble code, decompile it into a higher-level programming language, and view and edit the resulting source code. This can be useful for identifying vulnerabilities, analyzing malware, and understanding how a program works. Ghidra also includes a range of features and tools that support SRE tasks, such as debugging, code graphing, and data visualization. Ghidra is written in Java and is available for Windows, MacOS, and Linux.
Image used from https://www.malwaretech.com/2019/03/video-first-look-at-ghidra-nsa-reverse-engineering-tool.html Script Encoding was introduced by Microsoft (long ago) to prevent people from being able to read, understand and alter VBScript files. Encoded scripts are unreadable but still able to execute, making it a popular mechanism with threat actors looking to hide their malicious code, IOCs, hardcoded C2 domains etc whilst still being able to achieve execution.
The decode-vbe script can be used to convert encoded VBE files back to plaintext for analysis. Pafish is a testing tool that uses different techniques to detect virtual machines and malware analysis environments in the same way that malware families do. The project is free and open source; the code of all the anti-analysis techniques is publicly available. Pafish executables for Windows (x86 32-bit and 64-bit) can be downloaded from the releases page .
Lookyloo is a web interface that captures a webpage and then displays a tree of the domains, that call each other. Use Lookyloo to map the journey a website page takes - from entering the initial URL address to the various redirects to third-party affiliations. Once installed and running, lookyloo can be operated via the web interface hosted locally.
YARA is a tool aimed at (but not limited to) helping malware researchers to identify and classify malware samples. With YARA you can create descriptions of malware families (or whatever you want to describe) based on textual or binary patterns. Each description, a.k.a rule, consists of a set of strings and a boolean expression which determine its logic. It’s used to automatically run and analyze files and collect comprehensive analysis results that outline what the malware does while running inside an isolated operating system.
Radare2 provides a set of libraries, tools and plugins to ease reverse engineering tasks. r2 is a featureful low-level command-line tool with support for scripting. r2 can edit files on local hard drives, view kernel memory, and debug programs locally or via a remote gdb server. r2's wide architecture support allows you to analyze, emulate, debug, modify, and disassemble any binary.
dnSpy is a debugger and .NET assembly editor. You can use it to edit and debug assemblies. This is a site with over 2,200 blog entries about malicious network traffic. Almost every post on the site has pcap files or malware samples (or both). The site also contains a number of traffic analysis exercises, including technical blog posts outlining techniques being used by threat actors.
Recuva is a data recovery tool that can be used to recover deleted files from your computer. It is often used to recover deleted files that may contain valuable information, such as deleted logs or documents that could be used to investigate a security incident. Recuva can recover files from hard drives, USB drives, and memory cards, and it is available for Windows and Mac operating systems.
Image used from https://www.softpedia.com/blog/recuva-explained-usage-video-and-download-503681.shtml Extundelete is a utility that can be used to recover deleted files from an ext3 or ext4 file system. It works by searching the file system for blocks of data that used to belong to a file, and then attempting to recreate the file using those blocks of data. It is often used to recover important files that have been accidentally or maliciously deleted.
Image used from https://theevilbit.blogspot.com/2013/01/backtrack-forensics-ext34-file-recovery.html TestDisk is a free and open-source data recovery software tool that is designed to help recover lost partitions and make non-booting disks bootable again. It is useful for both computer forensics and data recovery. It can be used to recover data that has been lost due to a variety of reasons, such as accidental deletion, formatting, or corruption of the partition table.
TestDisk can also be used to repair damaged boot sectors, recover deleted partitions, and recover lost files. It supports a wide range of file systems, including FAT, NTFS, and ext2/3/4, and can be used to recover data from disks that are damaged or formatted with a different file system than the one they were originally created with. Tools for conducting forensic investigations of digital devices and systems, including tools for collecting and analyzing evidence.
SANS SIFT (SANS Investigative Forensic Toolkit) is a powerful toolkit for forensic analysis and incident response. It is a collection of open source and commercial tools that can be used to perform forensic analysis on a wide range of systems, including Windows, Linux, and Mac OS X. The SANS SIFT kit is designed to be run on a forensic workstation, which is a specialized computer that is used to perform forensic analysis on digital evidence.
The SANS SIFT kit is particularly useful for blue teamers, as it provides a wide range of tools and resources that can be used to investigate incidents, respond to threats, and perform forensic analysis on compromised systems. Click the 'Login to Download' button and input (or create) your SANS Portal account credentials to download the virtual machine.
Image used from https://securityboulevard.com/2020/08/how-to-install-sift-workstation-and-remnux-on-the-same-system-for-f orensics-and-malware-analysis/ The Sleuth Kit is a collection of command line tools that can be used to analyze disk images and recover files from them. It is primarily used by forensic investigators to examine digital evidence after a computer has been seized or an image of a disk has been made. It can be useful because it can help understand what happened during a security incident and identify any malicious activity.
The tools in The Sleuth Kit can be used to extract deleted files, analyze disk partition structures, and examine the file system for evidence of tampering or unusual activity. Image used from http://www.effecthacking.com/2016/09/the-sleuth-kit-digital-forensic-tool.html Autopsy is a digital forensics platform and graphical interface to The Sleuth Kit and other digital forensics tools.
It is used by law enforcement, military, and corporate examiners to investigate what happened on a computer. You can use it to analyze disk images and recover files, as well as to identify system and user activity. Autopsy is used by "blue teams" (the cybersecurity professionals who defend organizations against attacks) to conduct forensic analysis and incident response. It can help blue teams understand the nature and scope of an attack, and identify any malicious activity that may have occurred on a computer or network.
Image used from https://www.kitploit.com/2014/01/autopsy-digital-investigation-analysis.html Tools for training employees and other users on how to recognize and prevent potential security threats. TryHackMe is a platform that offers a variety of virtual machines, known as "rooms," which are designed to teach cybersecurity concepts and skills through hands-on learning.
These rooms are interactive and gamified, allowing users to learn about topics such as web vulnerabilities, network security, and cryptography by solving challenges and completing tasks. The platform is often used for security awareness training, as it provides a safe and controlled environment for users to practice their skills and learn about different types of cyber threats and how to defend against them.
Image used from https://www.hostingadvice.com/blog/learn-cybersecurity-with-tryhackme/ It consists of a set of challenges that simulate real-world scenarios and require you to use your knowledge of various hacking techniques to solve them. These challenges are designed to test your knowledge of topics such as network security, cryptography, web security, and more.
HackTheBox is often used by security professionals as a way to practice and improve their skills, and it can also be a useful resource for security awareness training. By working through the challenges and learning how to solve them, individuals can gain a better understanding of how to identify and mitigate common security threats. CyberDefenders is a dedicated platform designed for blue team professionals to enhance their cyber security skills.
The platform provides real-world blue team labs that cover a broad range of disciplines. Participants are encouraged to apply their knowledge in areas such as incident response, digital forensics, and threat hunting to navigate through these scenarios. The goal is to offer a practical learning environment that mirrors the complexities that defenders encounter in Security Operations Centers.
PhishMe is a company that provides security awareness training to help organizations educate their employees about how to identify and prevent phishing attacks. PhishMe's training programs aim to teach employees how to recognize and report phishing attempts, as well as how to protect their personal and professional accounts from these types of attacks.
The company's training programs can be customized to fit the needs of different organizations and can be delivered through a variety of mediums, including online courses, in-person training, and simulations. KC7 is a free, gamified cybersecurity training platform that allows users to act as digital detectives and investigate simulated cyber attacks.
Hunt hackers, view real-world logs, and spot malicious activity without requiring any prior technical experience. Tools for coordinating and communicating with team members during an incident, including chat, email, and project management software. It's a platform that is widely used by security professionals, researchers, and experts, giving you access to an endless amount of new information.
Facebook ThreatExchange is a platform for security professionals to share and analyze information about cyber threats. 5. Performance Evaluation & Extended Technical Observations It was designed to help organizations better defend against threats by allowing them to share threat intelligence with each other in a private and secure way.
It is intended to be used by "blue teams", who are responsible for the security of an organization and work to prevent, detect, and respond to cyber threats. To request access to ThreatExchange, you have to submit an application via https://developers.facebook.com/products/threat-exchange/ .
Welcome to Blue Team Security , a working notebook for practical defensive operations. This site focuses on technical execution: investigating telemetry, engineering detections, preserving evidence, and making response decisions. The notes cover detection engineering, incident response, threat hunting, DFIR, XDR/EDR, SIEM queries, Microsoft security operations, and vulnerability management. Each post should explain what to inspect, how to test it, and which conclusions the evidence supports.
Each article should leave an analyst with a specific next step: a query, artifact, timeline check, or response decision. Use the lab to test queries, read process trees, compare artifacts, and evaluate response packages. Record the environment and the limits of each test. Before live use, check vendor field meanings, retention, telemetry coverage, response behavior, and false positives in the target environment.
Articles connect alerts, logs, endpoint and identity evidence, and SIEM queries to concrete case decisions. Show the query results, corroborating evidence, and tool sequence needed to reproduce a closure or escalation decision. That is the benchmark for Blue Team Security : technical notes that make defensive work more precise. Start with the articles on telemetry, alert triage, process trees, and threat hunting. Follow new posts through the blog or the RSS feed .
A hacking lab setup is one of the most practical ways to improve cybersecurity without putting production systems at risk. Used correctly, it helps defenders test controls, rehearse attacks, and uncover weaknesses before real adversaries do. This article explains how to use hacking lab setup for defense in a structured, ethical, and measurable way, with examples that fit red team, blue team, and security awareness programs.
A defensive hacking lab is an isolated environment that mirrors parts of a real network, application stack, or endpoint estate. It lets security teams observe attack paths, validate detection tools, and study how systems behave under pressure. The goal is to create controlled conditions where defenders can answer practical questions such as: The most effective labs start with a clear use case instead of a collection of random tools.
When the lab is mapped to a specific defensive objective, every test produces something actionable: a new alert, a hardened configuration, an improved playbook, or a documented risk. A strong lab does not need to be large, but it should be realistic enough to model attacker behavior. Common components include virtual machines, a Windows or Linux domain, endpoint agents, a SIEM, and a test application.
To keep the environment useful, replicate the technologies your organization actually uses. A Microsoft-heavy enterprise should prioritize Windows, Active Directory, PowerShell logging, and common enterprise security tools. A cloud-first company should include cloud identity, container logging, and API traffic analysis.
For example: “Our EDR should detect suspicious PowerShell and credential access attempts on domain-joined hosts.” Then design a test that produces the expected behavior and measure whether the control reacts as intended. This repeatable cycle turns the lab into a validation engine rather than a one-time demo environment. The MITRE ATT&CK framework is useful here because it groups adversary behavior into recognizable tactics and techniques.
The point is not to simulate everything; it is to test the controls most likely to matter in a real incident. Each exercise should produce a record that includes the scenario, tool version, configuration, observed telemetry, and recommended fix. That creates accountability and makes the lab part of a continuous improvement program.
Instead of waiting for a real breach, analysts can practice identifying suspicious process behavior, correlating host and network data, and writing better alerts. These exercises improve speed and reduce confusion during actual incidents because analysts have already seen the telemetry patterns in a controlled setting.
Red teams use the lab to validate attack paths and measure how far simulated intrusions can progress without crossing ethical boundaries or touching live assets. Purple teams use the same environment to collaborate: one side simulates an adversary action, the other side watches detections in near real time.
This shared approach creates faster learning because defenders see exactly what triggered an alert and what did not. It also supports iterative hardening, where a detection is tuned immediately after the exercise and then retested. A defensive hacking lab must be isolated from production systems and governed by written rules. Unauthorized testing on real assets can create outages, violate policy, and trigger legal consequences.
Strong governance protects the organization and ensures the lab remains a safe place to learn, test, and improve defenses. Track whether detections fire, how quickly analysts respond, and how often a control blocks or limits the simulated threat. These metrics help security teams justify budgets, prioritize remediation, and show progress over time. Update operating systems, patch levels, cloud services, and monitoring tools regularly so the exercises remain realistic.
Include new tactics that appear in threat intelligence reports, vendor advisories, and incident postmortems. It also helps to schedule recurring scenarios tied to business risk, such as identity compromise, remote access abuse, or exposed web applications. That way the lab supports the current threat landscape instead of last year’s assumptions.
Get ready to discover the 9 best breakroom tables that blend style and functionality, transforming your workspace into an inviting hub of collaboration. Compare the best mini PCs with Ryzen for everyday work, gaming, and multitasking in a compact desktop form. Maximize your office space and comfort with the 10 best stacking chairs—discover which designs elevate your workspace and why they’re a must-have! Compare the best portable external SSDs of 2026 for speed, durability, capacity, and value across work, travel, and everyday use.
Upgrade your office with the 10 best upholstered benches that blend style and functionality—discover which one suits your workspace perfectly! Compare the best conference cameras for Zoom Rooms with smart framing, wide coverage, and easier setup for better hybrid meetings.
Fast, rugged, business-ready external SSDs for teams that need reliable large-capacity storage and easy portability. Find out the top 10 industrial carbon filters that can transform your workspace—discover which ones truly stand out for superior air quality! Compare the best portable storage options for photographers who need dependable backup, travel-friendly size, and big-capacity photo archiving.
Find the best powered USB-C hubs for office desks with more ports, faster transfers, and cleaner cable management. Relying on outdated, manual technology processes can undoubtedly leave you and your organization vulnerable and with a weakened security posture. Positioning a Blue Team on the offensive can be your strongest move by empowering them with automation combined with frequent security control testing. This makes having clear and up-to-date information of high-risk attack paths, easy-access entries and misconfigurations an armed solution.
In 2024, saying the words ‘traditional’ and ‘cybersecurity’ in the same sentence might not seem logical, but in an industry that moves at lightning speed, that’s exactly where we are today with no sign of slowing down. Global spending in the cybersecurity industry is nearly $200 billion each year , with software and controls accounting for about half. With more pressure from leadership and boards growing to show proof of quantifiable data security and threat protection, it’s no wonder that Red Teams are an expensive line item.
Penetration testing (pen testing) and security control validation are two distinct approaches to evaluating an organization’s security posture. Pen testing is more of a traditional approach, while security control validation is a distinctly more modern answer to testing security vulnerabilities. Traditionally, Red Teams make the first move when it comes to validating an organization’s security posture. However, with a more advanced approach, Blue Teams can now take matters into their own hands. By using their own managed security controls, they can do things like create rules in their EDR and WAF to block exploitation attempts of known vulnerabilities and adversary techniques.
Pen testing is not only a manual process, but a costly one, limited in scope and has reduced defense efficacy. This could leave you with dangerous blind spots in your security framework, leaving plenty of time and space for a malicious actor to crawl in and cause severe amounts of damage. In addition, pen tests only provide a point-in-time assessment, when vulnerabilities can emerge or be exploited after the test is completed, leaving findings irrelevant.
Security control validation, on the other hand, provides a continuous and automated approach, is 100% owned and managed by the "blue team". Compensating controls for vulnerabilities that in order to be patched must be dependent on the patch management process owned by a different team (usually IT), reducing the risk of blind spots. Pen tests are most effective when integrated into a multi-layered defense strategy.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Neil%20Siegel • https://en.wikipedia.org/wiki/Aart%20de%20Geus • https://en.wikipedia.org/wiki/Control%20system%20security • https://docshare.wps.com/document/btfm-blue-team-field-manual/45529/ • https://github.com/lancejames221b/CyberSentinelAI • https://github.com/Arzen-007/Ultimate-BlueTeam-Roadmap • https://blueteamalmanac.github.io/ • https://www.emergentmind.com/topics/blue-team-protocols • https://github.com/tmarshiqe14/TryHackMe-Blue-team-Labs • https://github.com/A-poc/BlueTeam-Tools
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Blue Team Defense Automation.
[*] Metasploit Scan Running on Target Subnet for Blue Team Defense Automation... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |