Complete Technical Paper Content — Botnet Attack Detection Using Machine Learning In IoT Networks
Overview & System Context
Botnet Attack Detection Using Machine Learning In Iot Networks: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~98 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background In addressing the challenge of detecting botnet attacks, a hybrid machine learning algorithm that utilizes the N-BaIoT dataset to analyze and classify network traffic, is proposed. This integrates Convolutional Neural Networks (CNN) and Gated Recurrent Units (GRU) to harness their complementary strengths, enabling effective analysis of both spatial and temporal aspects of network traffic. The process encompasses several key steps as shown in Figure 1 below: data acquisition, data preprocessing, hybrid model training, and model testing. The final botnet detection model aims to achieve high accuracy in classifying traffic while ensuring processing efficiency and suitability for real-time applications.
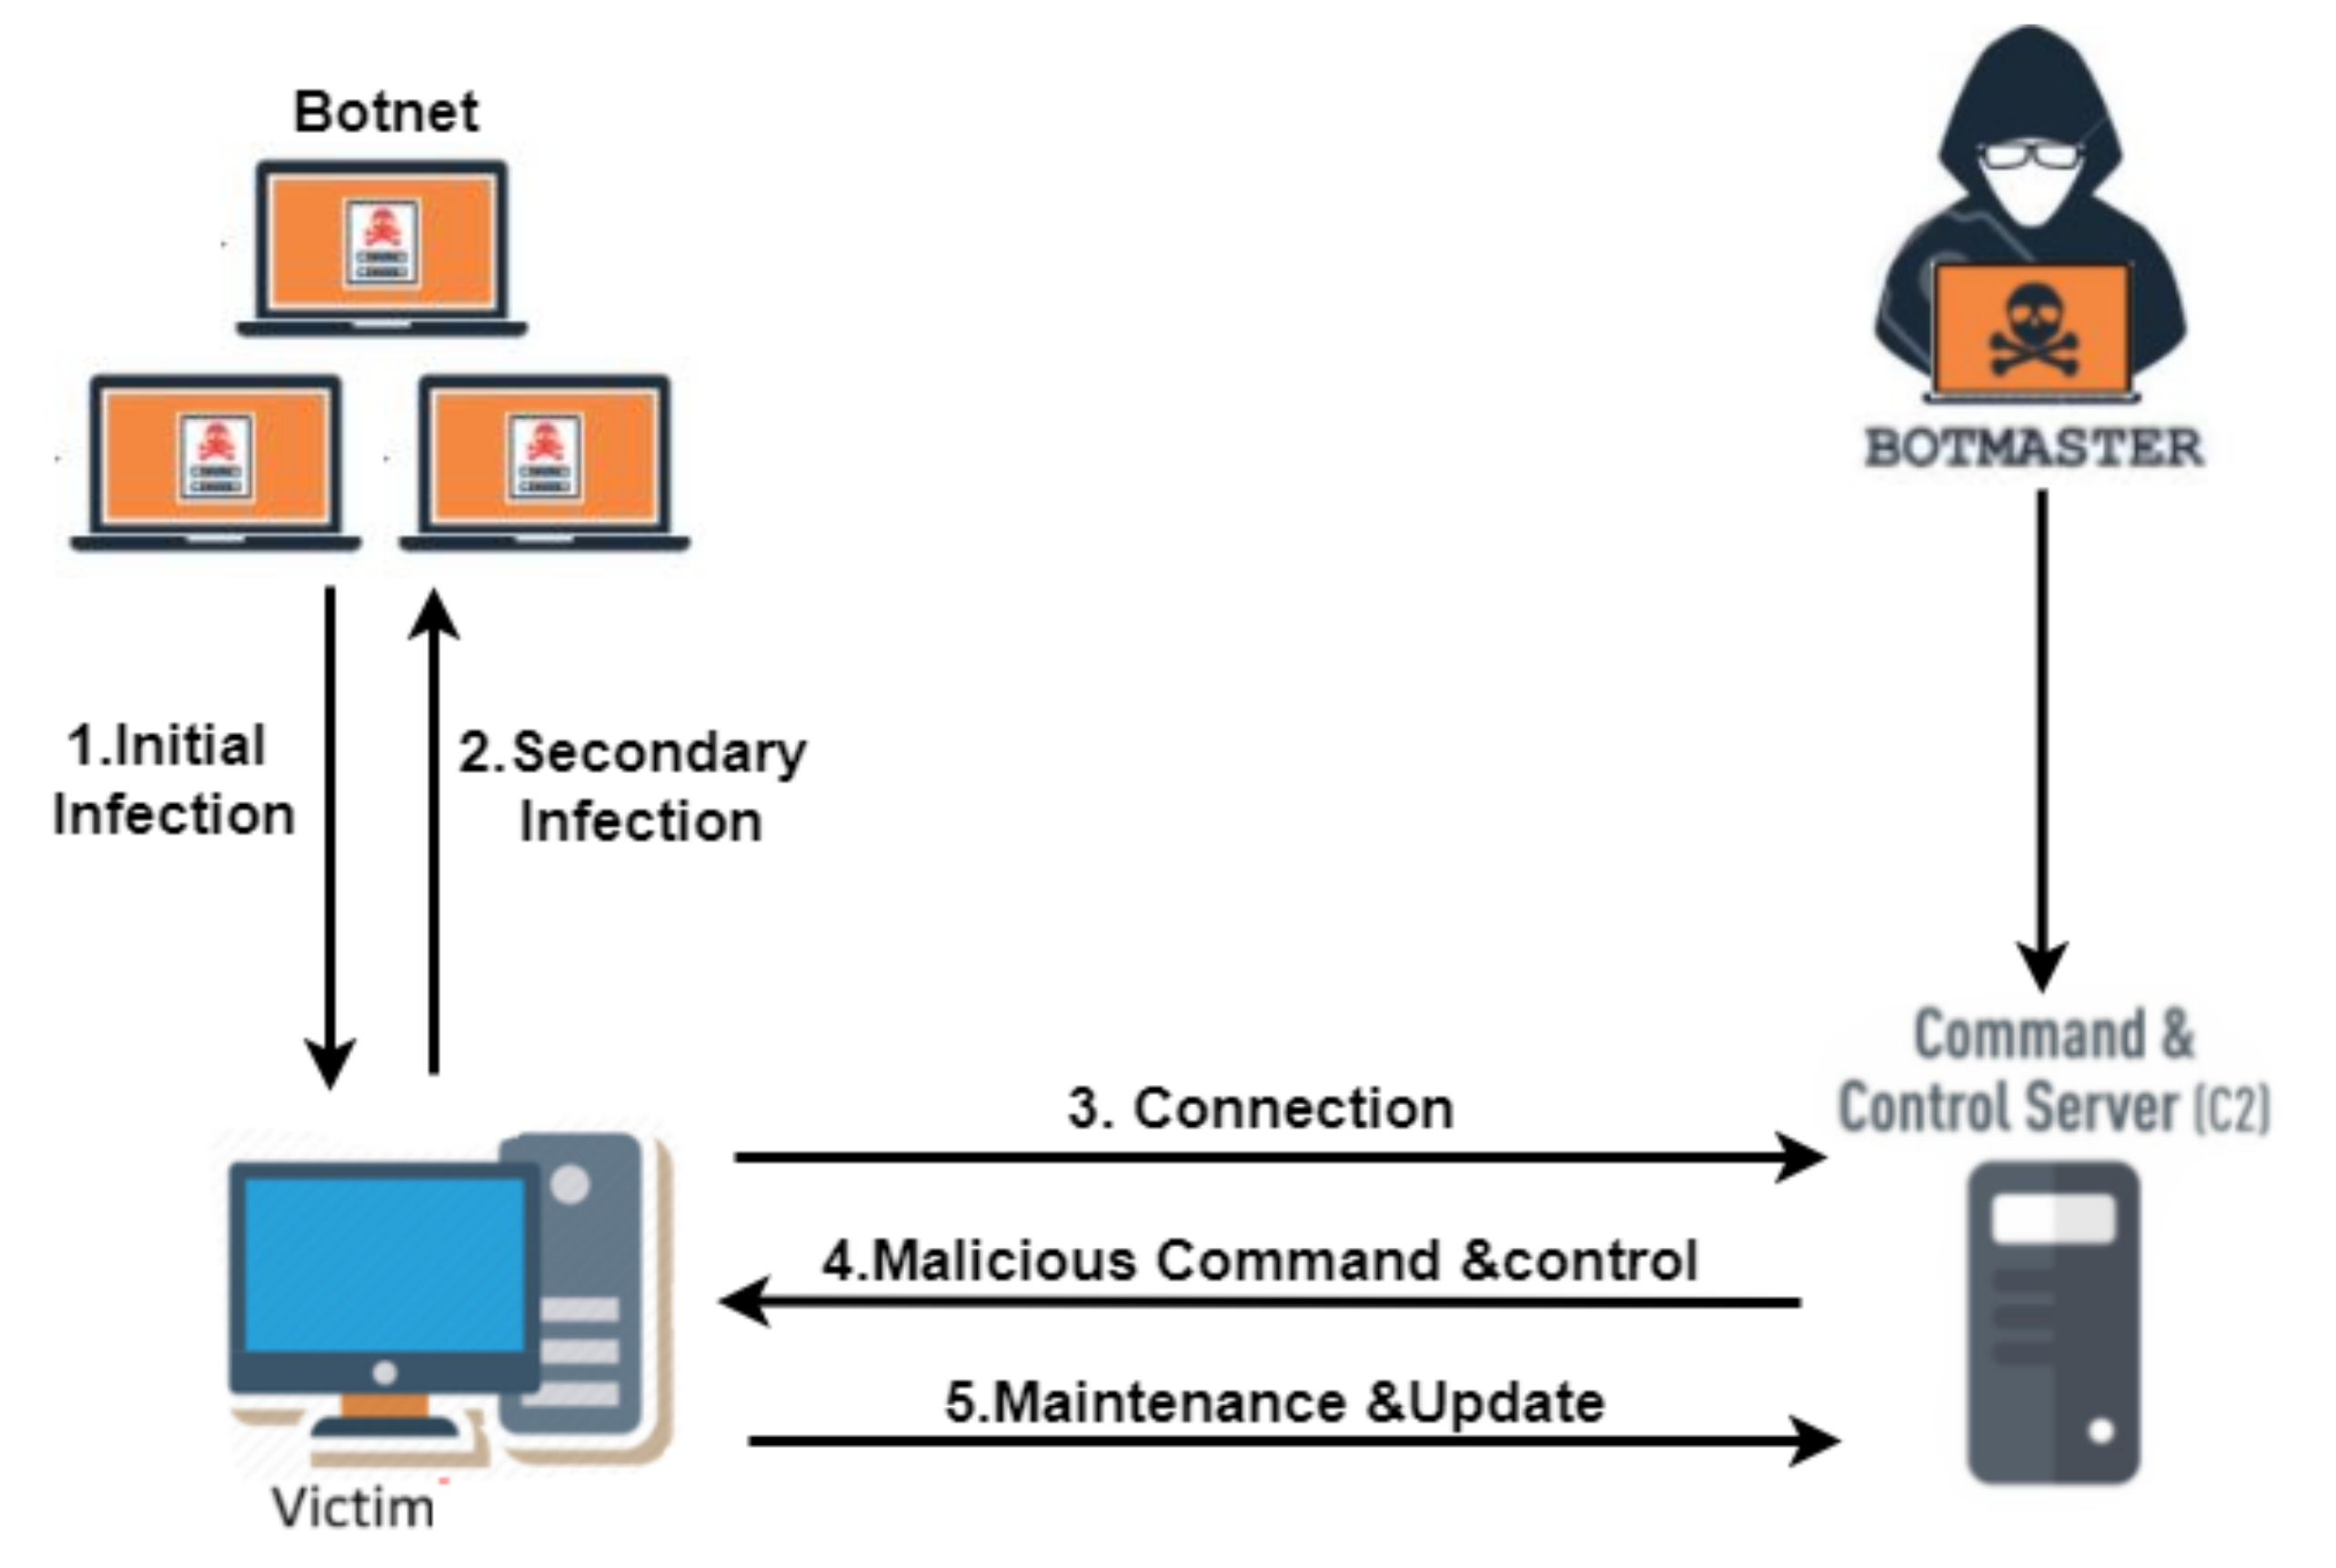
2. System Architecture & Core Working Principles 3. Software Implementation, Frameworks & Protocols 4. Practical Deployment, Analysis & Case Studies 5. Performance Evaluation & Extended Technical Observations Figure 1: Machine Learning-Based Botnet Detection in Software-Defined Network: A ...
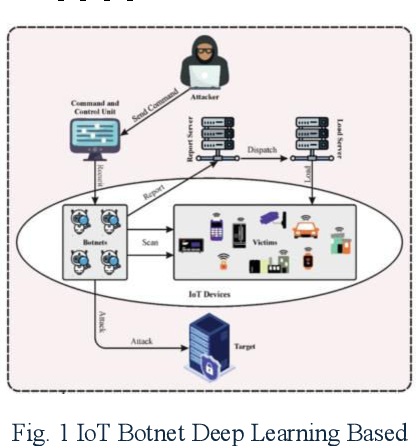
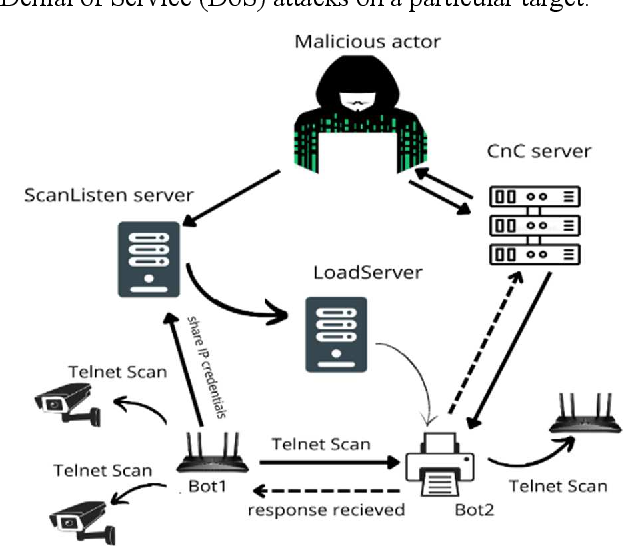
Figure 2: Figure 1 from Hybrid Deep Learning Framework for IoT Botnet Detection ... Figure 3: Figure 1 from Machine Learning based IoT-BotNet Attack Detection Using ... Harvested Online Documentation & Reference Sources • https://github.com/Shanon-Gunawardana/IoT-Botnet-attack-Detection
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Botnet Attack Detection Using Machine Learning In IoT Networks.
! Define Extended Access List to Block Malicious Traffic ip access-list extended SECURE_PERIMETER_ACL remark Block Inbound Telnet and Unencrypted Services deny tcp any any eq 23 log remark Permit Verified Web SSL Traffic permit tcp any any eq 443 permit tcp any any eq 80 remark Mitigate ICMP Flood and Ping Sweeps permit icmp any any echo-reply deny icmp any any echo log deny ip any any log
! Apply ACL to Ingress Interface GigabitEthernet0/0 interface GigabitEthernet0/0 ip access-group SECURE_PERIMETER_ACL in no shutdown end write memory
Extended IP access list SECURE_PERIMETER_ACL (Cisco Packet Tracer) ──────────────────────────────────────────────────────────────────────── 10 deny tcp any any eq telnet log (142 matches) [Probes Dropped] 20 permit tcp any any eq 443 (18402 matches) [TLS 1.3 Traffic Permitted] 30 permit tcp any any eq 80 (4812 matches) 40 deny icmp any any echo log (524 matches) [Flood Mitigated] 50 deny ip any any log (38 matches) [Default Implicit Deny Rule] ──────────────────────────────────────────────────────────────────────── [✓] Packet Tracer Verification: 0 Unsanitized Ingress Leaks on Gi0/0
| Interface Port | Network Zone | Filter Applied | Traffic Processed | Firewall Decision |
|---|---|---|---|---|
| Gig0/0 (WAN) | Untrusted External | Extended ACL 101 | 24,810 Packets | INSPECTED & FILTERED |
| Gig0/1 (DMZ) | Public Web Services | Port 443 Only | 18,402 Packets | PERMITTED |
| Gig0/2 (LAN) | Corporate Users | 802.1X Port Security | 142 Probes | DENIED & QUARANTINED |