Complete Technical Paper Content — Browser History And Cache Forensic Analysis Tool Python
Overview & System Context
Browser History And Cache Forensic Analysis Tool Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8776 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Tor is a free overlay network for enabling anonymous communication. It is built on free and open-source software run by over seven thousand volunteer-operated relays worldwide, as well as by millions of users who route their internet traffic via random paths through these relays. This technique is called onion routing. Using Tor makes it more difficult to trace a user's internet activity by preventing any single point on the internet (other than the user's device) from being able to view both where traffic originated from and where it is ultimately going to at the same time. This conceals a user's location and usage from anyone performing network surveillance or traffic analysis from any such point, protecting the user's freedom and ability to communicate confidentially.
In 2004, the Naval Research Laboratory released the code for Tor under a free license, and the Electronic Frontier Foundation (EFF) began funding Dingledine and Mathewson to continue its development. In 2006, Dingledine, Mathewson, and five others founded The Tor Project, a Massachusetts-based 501(c)(3) research-education nonprofit organization responsible for maintaining Tor. The EFF acted as The Tor Project's fiscal sponsor in its early years, and early financial supporters included the U.S. Bureau of Democracy, Human Rights, and Labor and International Broadcasting Bureau, Internews, Human Rights Watch, the University of Cambridge, Google, and Netherlands-based Stichting NLnet. Over the course of its existence, various Tor vulnerabilities have been discovered and occasionally exploited. Attacks against Tor are an active area of academic research that is welcomed by The Tor Project itself.
Tor enables its users to surf the Internet, chat and send instant messages anonymously, and is used by a wide variety of people for both licit and illicit purposes. Tor has, for example, been used by criminal enterprises, hacktivism groups, and law enforcement agencies at cross purposes, sometimes simultaneously; likewise, agencies within the U.S. government variously fund Tor (the U.S. State Department, the National Science Foundation, and – through the Broadcasting Board of Governors, which itself partially funded Tor until October 2012 – Radio Free Asia) and seek to subvert it. Tor was one of a dozen circumvention tools evaluated by a Freedom House-funded report based on user experience from China in 2010, which include Ultrasurf, Hotspot Shield, and Freegate. Tor is not meant to completely solve the issue of anonymity on the web. Tor is not designed to completely erase tracking but instead to reduce the likelihood for sites to trace actions and data back to the user. Tor can also be used for illegal activities. These can include censorship circumvention, as well as distribution of child abuse content, drug sales, or malware distribution. Tor has been described by The Economist, in relation to Bitcoin and Silk Road, as being "a dark corner of the web". It has been targeted by the American National Security Agency and the British GCHQ signals intelligence agencies, albeit with marginal success, and more successfully by the British National Crime Agency in its Operation Notarise. At the same time, GCHQ has been using a tool named "Shadowcat" for "end-to-end encrypted access to VPS over SSH using the Tor network". Tor can be used for anonymous defamation, unauthorized news leaks of sensitive information, copyright infringement, distribution of illegal sexual content, selling controlled substances, weapons, and stolen credit card numbers, money laundering, bank fraud, credit card fraud, identity theft and the exchange of counterfeit currency; the black market utilizes the Tor infrastructure, at least in part, in conjunction with Bitcoin. It has also been used to brick IoT devices. In its complaint against Ross William Ulbricht of Silk Road, the US Federal Bureau of Investigation acknowledged that Tor has "known legitimate uses". According to CNET, Tor's anonymity function is "endorsed by the Electronic Frontier Foundation (EFF) and other civil liberties groups as a method for whistleblowers and human rights workers to communicate with journalists". EFF's Surveillance Self-Defense guide includes a description of where Tor fits in a larger strategy for protecting privacy and anonymity. In 2014, the EFF's Eva Galperin told Businessweek that "Tor's biggest problem is press. No one hears about that time someone wasn't stalked by their abuser. They hear how somebody got away with downloading child porn." The Tor Project states that Tor users include "normal people" who wish to keep their Internet activities private from websites and advertisers, people concerned about cyber-spying, and users who are evading censorship such as activists, journalists, and military professionals. In November 2013, Tor had about four million users. According to the Wall Street Journal, in 2012 about 14% of Tor's traffic connected from the United States, with people in "Internet-censoring countries" as its second-largest user base. Tor is increasingly used by victims of domestic violence and the social workers and agencies that assist them, even though shelter workers may or may not have had professional training on cyber-security matters. Properly deployed, however, it precludes digital stalking, which has increased due to the prevalence of digital media in contemporary online life. Along with SecureDrop, Tor is used by news organizations such as The Guardian, The New Yorker, ProPublica and The Intercept to protect the privacy of whistleblowers. In March 2015, the Parliamentary Office of Science and Technology released a briefing which stated that "There is widespread agreement that banning online anonymity systems altogether is not seen as an acceptable policy option in the U.K." and that "Even if it were, there would be technical challenges." The report further noted that Tor "plays only a minor role in the online viewing and distribution of indecent images of children" (due in part to its inherent latency); its usage by the Internet Watch Foundation, the utility of its onion services for whistleblowers, and its circumvention of the Great Firewall of China were touted. Tor's executive director, Andrew Lewman, also said in August 2014 that agents of the NSA and the GCHQ have anonymously provided Tor with bug reports. The Tor Project's FAQ offers supporting reasons for the EFF's endorsement: Criminals can already do bad things. Since they're willing to break laws, they already have lots of options available that provide better privacy than Tor provides... Tor aims to provide protection for ordinary people who want to follow the law. Only criminals have privacy right now, and we need to fix that...
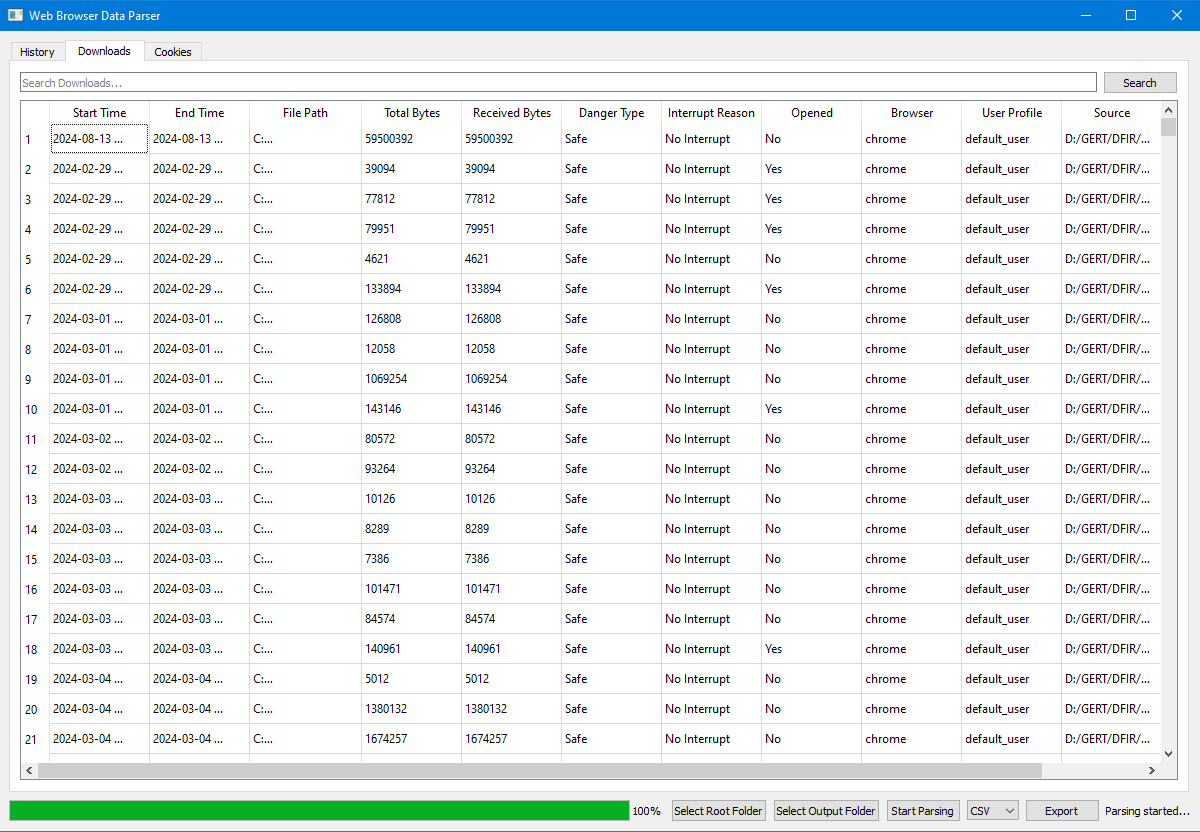
Figure 1: GitHub - jdmastermy/BrowserForensicsToolkit: BrowserForensicsToolkit is ... So yes, criminals could in theory use Tor, but they already have better options, and it seems unlikely that taking Tor away from the world will stop them from doing their bad things. At the same time, Tor and other privacy measures can fight identity theft, physical crimes like stalking, and so on.
Tor aims to conceal its users' identities and their online activity from surveillance and traffic analysis by separating identification and routing. It is an implementation of onion routing, which encrypts and then randomly bounces communications through a network of relays run by volunteers around the globe. These onion routers employ encryption in a multi-layered manner (hence the onion metaphor) to ensure perfect forward secrecy between relays, thereby providing users with anonymity in a network location. That anonymity extends to the hosting of censorship-resistant content by Tor's anonymous onion service feature. Furthermore, by keeping some of the entry relays (bridge relays) secret, users can evade Internet censorship that relies upon blocking public Tor relays. Because the IP address of the sender and the recipient are not both in cleartext at any hop along the way, anyone eavesdropping at any point along the communication channel cannot directly identify both ends. Furthermore, to the recipient, it appears that the last Tor node (called the exit node), rather than the sender, is the originator of the communication.
Tor can also provide anonymity to websites and other servers. Servers configured to receive inbound connections by connecting to Tor are called onion services (formerly, hidden services). Rather than revealing a server's IP address (and thus its network location), an onion service is accessed through its onion address, usually via the Tor Browser or some other software designed to use Tor. The Tor network understands these addresses by looking up their corresponding public keys and introduction points from a distributed hash table within the network. It can route data to and from onion services, even those hosted behind firewalls or network address translators (NAT), while preserving the anonymity of both parties. Tor is necessary to access these onion services. Because the connection never leaves the Tor network, and is handled by the Tor application on both ends, the connection is always end-to-end encrypted. Onion services were first specified in 2003 and have been deployed on the Tor network since 2004. They are unlisted by design, and can only be discovered on the network if the onion address is already known, though a number of sites and services do catalog publicly known onion addresses. Popular sources of .onion links include Pastebin, Twitter, Reddit, other Internet forums, and tailored search engines. While onion services are often discussed in terms of websites, they can be used for any TCP service, and are commonly used for increased security or easier routing to non-web services, such as secure shell remote login, chat services such as IRC and XMPP, or file sharing. They have also become a popular means of establishing peer-to-peer connections in messaging and file sharing applications. Web-based onion services can be accessed from a standard web browser without client-side connection to the Tor network using services like Tor2web, which remove client anonymity. In 2023, the Tor Project unveiled a new defense mechanism to safeguard onion services against denial-of-service (DoS) attacks. With the release of Tor 0.4.8, this proof-of-work (PoW) defense promises to prioritize legitimate network traffic while deterring malicious attacks.
2. System Architecture & Core Working Principles Tor makes no attempt to conceal the IP addresses of exit relays, or hide from a destination server the fact that a user is connecting via Tor. Operators of Internet sites therefore have the ability to prevent traffic from Tor exit nodes or to offer reduced functionality for Tor users. For example, Wikipedia generally forbids all editing when using Tor or when using an IP address also used by a Tor exit node, and the BBC blocks the IP addresses of all known Tor exit nodes from its iPlayer service. Apart from intentional restrictions of Tor traffic, Tor use can trigger defense mechanisms on websites intended to block traffic from IP addresses observed to generate malicious or abnormal traffic. Because traffic from all Tor users is shared by a comparatively small number of exit relays, tools can misidentify distinct sessions as originating from the same user, and attribute the actions of a malicious user to a non-malicious user, or observe an unusually large volume of traffic for one IP address. Conversely, a site may observe a single session connecting from different exit relays, with different Internet geolocations, and assume the connection is malicious, or trigger geo-blocking. When these defense mechanisms are triggered, it can result in the site blocking access, or presenting captchas to the user.
In July 2014, the Tor Project issued a security advisory for a "relay early traffic confirmation" attack, disclosing the discovery of a group of relays attempting to de-anonymize onion service users and operators. A set of onion service directory nodes (i.e., the Tor relays responsible for providing information about onion services) were found to be modifying traffic of requests. The modifications made it so the requesting client's guard relay, if controlled by the same adversary as the onion service directory node, could easily confirm that the traffic was from the same request. This would allow the adversary to simultaneously know the onion service involved in the request, and the IP address of the client requesting it (where the requesting client could be a visitor or owner of the onion service). The attacking nodes joined the network on 30 January, using a Sybil attack to comprise 6.4% of guard relay capacity, and were removed on 4 July. In addition to removing the attacking relays, the Tor application was patched to prevent the specific traffic modifications that made the attack possible. In November 2014, there was speculation in the aftermath of Operation Onymous, resulting in 17 arrests internationally, that a Tor weakness had been exploited. A representative of Europol was secretive about the method used, saying: "This is something we want to keep for ourselves. The way we do this, we can't share with the whole world, because we want to do it again and again and again." A BBC source cited a "technical breakthrough" that allowed tracking physical locations of servers, and the initial number of infiltrated sites led to the exploit speculation. A Tor Project representative downplayed this possibility, suggesting that execution of more traditional police work was more likely. In November 2015, court documents suggested a connection between the attack and arrests, and raised concerns about security research ethics. The documents revealed that the FBI obtained IP addresses of onion services and their visitors from a "university-based research institute", leading to arrests.
Reporting from Motherboard found that the timing and nature of the relay early traffic confirmation attack matched the description in the court documents. Multiple experts, including a senior researcher with the ICSI of UC Berkeley, Edward Felten of Princeton University, and the Tor Project agreed that the CERT Coordination Center of Carnegie Mellon University was the institute in question. Concerns raised included the role of an academic institution in policing, sensitive research involving non-consenting users, the non-targeted nature of the attack, and the lack of disclosure about the incident.
The main implementation of Tor is written primarily in C. Starting in 2020, the Tor Project began development of a full rewrite of the C Tor codebase in Rust. The project, named Arti, was publicly announced in July 2021. Standard: All website functions supported by Tor Browser, such as JavaScript, fonts, and multimedia, are enabled. Safer: Some features known to be common attack vectors are disabled. JavaScript is disabled on all websites not secured by TLS; some fonts and mathematical symbols are disabled; videos and audio are click-to-play. Safest: Only features necessary for static websites and basic services are enabled. JavaScript is disabled globally; some fonts, icons, math symbols, and images are disabled; videos and audio are click-to-play. To allow download from places where accessing the Tor Project URL may be risky or blocked, a GitHub repository is maintained with links for releases hosted in other domains.
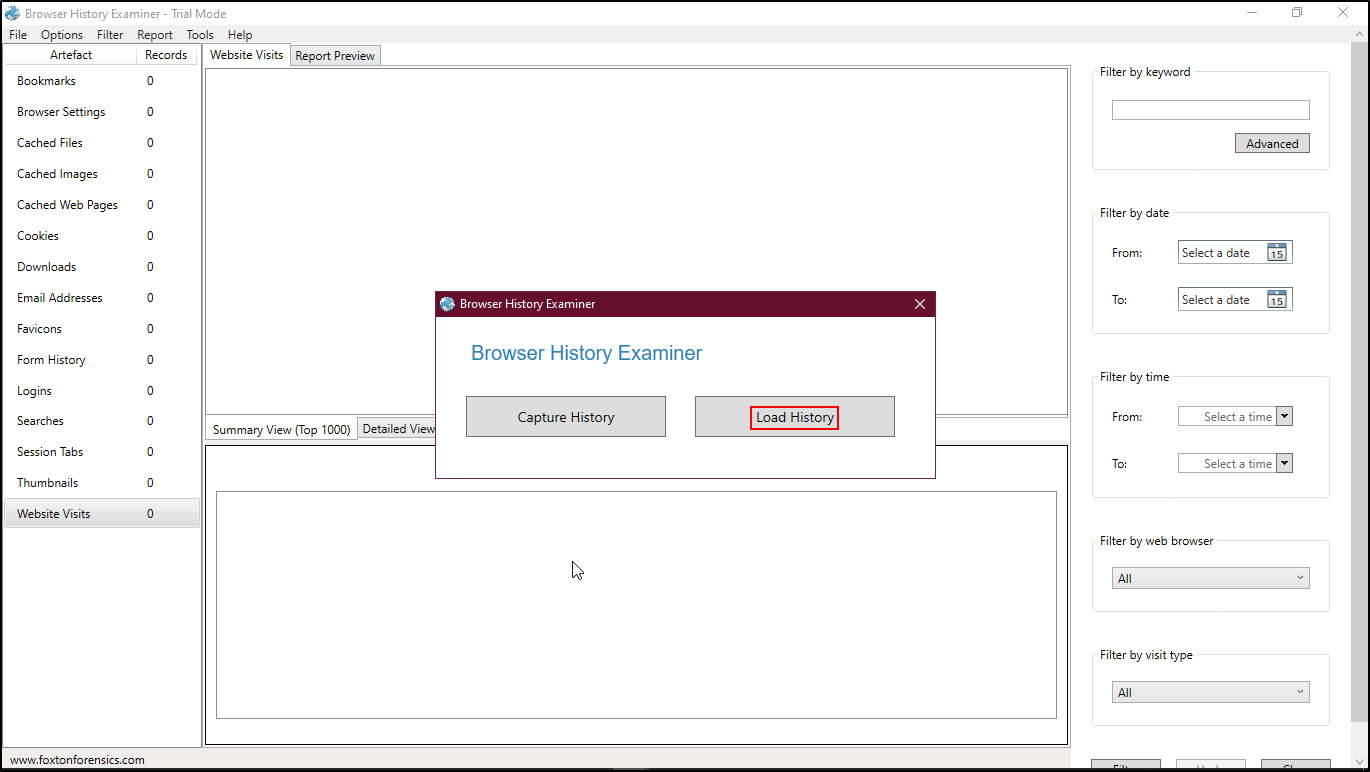
Figure 2: Browser & Blockchain Forensics | Oste's Blog Tor has been praised for providing privacy and anonymity to vulnerable Internet users such as political activists fearing surveillance and arrest, ordinary web users seeking to circumvent censorship, and people who have been threatened with violence or abuse by stalkers. The U.S. National Security Agency (NSA) has called Tor "the king of high-secure, low-latency Internet anonymity", and BusinessWeek magazine has described it as "perhaps the most effective means of defeating the online surveillance efforts of intelligence agencies around the world". Other media have described Tor as "a sophisticated privacy tool", "easy to use" and "so secure that even the world's most sophisticated electronic spies haven't figured out how to crack it". Advocates for Tor say it supports freedom of expression, including in countries where the Internet is censored, by protecting the privacy and anonymity of users. The mathematical underpinnings of Tor lead it to be characterized as acting "like a piece of infrastructure, and governments naturally fall into paying for infrastructure they want to use". The project was originally developed on behalf of the U.S. intelligence community and continues to receive U.S. government funding, and has been criticized as "more resembl[ing] a spook project than a tool designed by a culture that values accountability or transparency". As of 2012, 80% of The Tor Project's $2M annual budget came from the United States government, with the U.S. State Department, the Broadcasting Board of Governors, and the National Science Foundation as major contributors, aiming "to aid democracy advocates in authoritarian states". Other public sources of funding include DARPA, the U.S. Naval Research Laboratory, and the Government of Sweden. Some have proposed that the government values Tor's commitment to free speech, and uses the darknet to gather intelligence. Tor also receives funding from NGOs including Human Rights Watch, and private sponsors including Reddit and Google. Dingledine said that the United States Department of Defense funds are more similar to a research grant than a procurement contract. Tor executive director Andrew Lewman said that even though it accepts funds from the U.S. federal government, the Tor service did not collaborate with the NSA to reveal identities of users. Critics say that Tor is not as secure as it claims, pointing to U.S. law enforcement's investigations and shutdowns of Tor-using sites such as web-hosting company Freedom Hosting and online marketplace Silk Road. In October 2013, after analyzing documents leaked by Edward Snowden, The Guardian reported that the NSA had repeatedly tried to crack Tor and had failed to break its core security, although it had had some success attacking the computers of individual Tor users. The Guardian also published a 2012 NSA classified slide deck, entitled "Tor Stinks", which said: "We will never be able to de-anonymize all Tor users all the time", but "with manual analysis we can de-anonymize a very small fraction of Tor users".
When Tor users are arrested, it is typically due to human error, not to the core technology being hacked or cracked. On 7 November 2014, for example, a joint operation by the FBI, ICE Homeland Security Investigations and European Law enforcement agencies led to 17 arrests and the seizure of 27 sites containing 400 pages. A late 2014 report by Der Spiegel using a new cache of Snowden leaks revealed, however, that as of 2012 the NSA deemed Tor on its own as a "major threat" to its mission, and when used in conjunction with other privacy tools such as OTR, Cspace, ZRTP, RedPhone, Tails, and TrueCrypt was ranked as "catastrophic," leading to a "near-total loss/lack of insight to target communications, presence..." "No adversary is truly global, but no adversary needs to be truly global," he says. "Eavesdropping on the entire Internet is a several-billion-dollar problem. Running a few computers to eavesdrop on a lot of traffic, a selective denial of service attack to drive traffic to your computers, that's like a tens-of-thousands-of-dollars problem." At the most basic level, an attacker who runs two poisoned Tor nodes—one entry, one exit—is able to analyse traffic and thereby identify the tiny, unlucky percentage of users whose circuit happened to cross both of those nodes. In 2016 the Tor network offers a total of around 7,000 relays, around 2,000 guard (entry) nodes and around 1,000 exit nodes. So the odds of such an event happening are one in two million (1⁄2000 × 1⁄1000), give or take." Tor does not provide protection against end-to-end timing attacks: if an attacker can watch the traffic coming out of the target computer, and also the traffic arriving at the target's chosen destination (e.g. a server hosting a .onion site), that attacker can use statistical analysis to discover that they are part of the same circuit. A similar attack has been used by German authorities to track down users related to Boystown.
Facebook is an American social networking service owned by the American technology conglomerate Meta Platforms. It was founded in 2004 by Mark Zuckerberg, along with his Harvard College roommates and fellow students Eduardo Saverin, Andrew McCollum, Dustin Moskovitz, and Chris Hughes. The name Facebook derives from the face book directories often given to American university students. The service was initially targeted to Harvard students only before gradually expanding to other universities in North America. Since 2006, Facebook has permitted registration by individuals aged 13 and older, with the exception of South Korea, Spain, and Quebec, where the minimum age is 14. As of December 2023, Facebook reported approximately 3.07 billion monthly active users worldwide. As of July 2025, it was ranked as the third-most-visited website in the world, with 23 percent of its traffic originating from the United States. It was the most downloaded mobile application of the 2010s. Facebook can be accessed from devices with Internet connectivity, such as personal computers, tablets and smartphones. After registering, users can create a profile revealing personal information about themselves. They can post text, photos, and multimedia which are shared either publicly or exclusively with other users who have agreed to be their friend, depending on privacy settings. Users can also communicate directly with each other with Messenger, edit messages (within 15 minutes after sending), join common-interest groups, and receive notifications on the activities of their Facebook friends and the pages they follow. Facebook has often been criticized over issues such as user privacy (as with the Facebook–Cambridge Analytica data scandal), political manipulation (as with the 2016 U.S. elections) and mass surveillance.
The company has also been subject to criticism over its psychological effects such as addiction and low self-esteem, and over content such as fake news, conspiracy theories, copyright infringement, and hate speech. Commentators have accused Facebook of willingly facilitating the spread of such content, as well as overemphasizing its number of users to appeal to advertisers.
3. Software Implementation, Frameworks & Protocols The history of Facebook traces its growth from a college networking site to a global social networking service. While attending Phillips Exeter in the early 2000s, Zuckerberg met Kris Tillery. Tillery, a one-time project collaborator with Zuckerberg, would create a school-based social networking project called Photo Address Book. Photo Address Book was a digital face book, created through a linked database composed of student information derived from the official records of the Exeter Student Council. The database contained linkages such as name, dorm-specific landline numbers, and student headshots. Mark Zuckerberg built a website called "Facemash" in 2003 while attending Harvard University. The site was comparable to Hot or Not and used photos from online face books, asking users to choose the 'hotter' person". Zuckerberg was reported and faced expulsion, but the charges were dropped. A "face book" is a student directory featuring photos and personal information. In January 2004, Zuckerberg coded a new site known as "TheFacebook", stating, "It is clear that the technology needed to create a centralized Website is readily available ... the benefits are many." Zuckerberg met with Harvard student Eduardo Saverin, and each agreed to invest $1,000. On February 4, 2004, Zuckerberg launched "TheFacebook". Membership was initially restricted to students of Harvard College. Dustin Moskovitz, Andrew McCollum, and Chris Hughes joined Zuckerberg to help manage the growth of the site. It became available successively to most universities in the US and Canada. In 2004, Napster co-founder Sean Parker became company president and the company moved to Palo Alto, California. PayPal co-founder Peter Thiel gave Facebook its first investment. In 2005, the company dropped "the" from its name after purchasing the domain name Facebook.com. In 2006, Facebook opened to everyone at least or only 13 years old with a valid email address. Facebook introduced key features like the News Feed, which became central to user engagement. By late 2007, Facebook had 100,000 pages on which companies promoted themselves. Facebook had surpassed MySpace in global traffic and became the world's most popular social media platform. Microsoft announced that it had purchased a 1.6% share of Facebook for $240 million ($373 million in 2025 dollars), giving Facebook an implied value of around $15 billion ($23.3 billion in 2025 dollars). Facebook focused on generating revenue through targeted advertising based on user data, a model that drove its rapid financial growth. In 2012, Facebook went public with one of the largest IPOs in tech history. Acquisitions played a significant role in Facebook's dominance. In 2012, it purchased Instagram, followed by WhatsApp and Oculus VR in 2014, extending its influence beyond social networking into messaging and virtual reality. The Facebook–Cambridge Analytica data scandal in 2018 revealed misuse of user data to influence elections, sparking global outcry and leading to regulatory fines and hearings. Facebook's role in global events, including its use in organizing movements like the Arab Spring and its impact on events like the Rohingya genocide in Myanmar, highlighted its dual nature as a tool for both empowerment and harm. In 2021, Facebook rebranded as Meta, reflecting its shift toward building the "metaverse" and focusing on virtual reality and augmented reality technologies.
On March 20, 2014, Facebook announced a new open-source programming language called Hack. Before public release, a large portion of Facebook was already running and "battle tested" using the new language. Each registered user on Facebook has a personal profile that shows their posts and content. The format of individual user pages was revamped in September 2011 and became known as "Timeline", a chronological feed of a user's stories, including status updates, photos, interactions with apps and events. The layout let users add a "cover photo". Users were given more privacy settings. In 2007, Facebook launched Facebook Pages for brands and celebrities to interact with their fanbases. In June 2009, Facebook introduced a "Usernames" feature, allowing users to choose a unique nickname used in the URL for their personal profile, for easier sharing. In February 2014, Facebook expanded the gender setting, adding a custom input field that allows users to choose from a wide range of gender identities. Users can also set which set of gender-specific pronoun should be used in reference to them throughout the site. In May 2014, Facebook introduced a feature to allow users to ask for information not disclosed by other users on their profiles. If a user does not provide key information, such as location, hometown, or relationship status, other users can use a new "ask" button to send a message asking about that item to the user in a single click.
News Feed appears on every user's homepage and highlights information including profile changes, upcoming events and friends' birthdays. This enabled spammers and other users to manipulate these features by creating illegitimate events or posting fake birthdays to attract attention to their profile or cause. Another issue is that the birthday of Leap-Day babies (those born on February 29 in leap years) is neglected three years out of four, along with memories of that day. Initially, the News Feed caused dissatisfaction among Facebook users; some complained it was too cluttered and full of undesired information, others were concerned that it made it too easy for others to track individual activities (such as relationship status changes, events, and conversations with other users). Zuckerberg apologized for the site's failure to include appropriate privacy features. Users then gained control over what types of information are shared automatically with friends. Users are now able to prevent user-set categories of friends from seeing updates about certain types of activities, including profile changes, Wall posts and newly added friends. On February 23, 2010, Facebook was granted a patent on certain aspects of its News Feed.
The patent covers News Feeds in which links are provided so that one user can participate in the activity of another user. The sorting and display of stories in a user's News Feed is governed by the EdgeRank algorithm. The Photos application allows users to upload albums and photos. Each album can contain 200 photos. Privacy settings apply to individual albums. Users can "tag", or label, friends in a photo. The friend receives a notification about the tag with a link to the photo. This photo tagging feature was developed by Aaron Sittig, now a Design Strategy Lead at Facebook, and former Facebook engineer Scott Marlette back in 2006 and was only granted a patent in 2011. On June 7, 2012, Facebook launched its App Center to help users find games and other applications. On May 13, 2015, Facebook in association with major news portals launched "Instant Articles" to provide news on the Facebook news feed without leaving the site. In January 2017, Facebook launched Facebook Stories for iOS and Android in Ireland. The feature, following the format of Snapchat and Instagram stories, allows users to upload photos and videos that appear above friends' and followers' News Feeds and disappear after 24 hours. On October 11, 2017, Facebook introduced the 3D Posts feature to allow for uploading interactive 3D assets. On January 11, 2018, Facebook announced that it would change News Feed to prioritize friends/family content and de-emphasize content from media companies. In February 2020, Facebook announced it would spend $1 billion ($1.24 billion in 2025 dollars) to license news material from publishers for the next three years; a pledge coming as the company falls under scrutiny from governments across the globe over not paying for news content appearing on the platform. The pledge would be in addition to the $600 million ($746 million in 2025 dollars) paid since 2018 through deals with news companies such as The Guardian and Financial Times. In March and April 2021, in response to Apple announcing changes to its iOS device's Identifier for Advertisers policy, which included requiring app developers to directly request to users the ability to track on an opt-in basis, Facebook purchased full-page newspaper advertisements attempting to convince users to allow tracking, highlighting the effects targeted ads have on small businesses. Facebook's efforts were ultimately unsuccessful, as Apple released iOS 14.5 in late April 2021, containing the feature for users in what has been deemed "App Tracking Transparency". Moreover, statistics from Verizon Communications subsidiary Flurry Analytics show 96% of all iOS users in the United States are not permitting tracking at all, and only 12% of worldwide iOS users are allowing tracking, which some news outlets deem "Facebook's nightmare", among similar terms. Despite the news, Facebook stated that the new policy and software update would be "manageable".
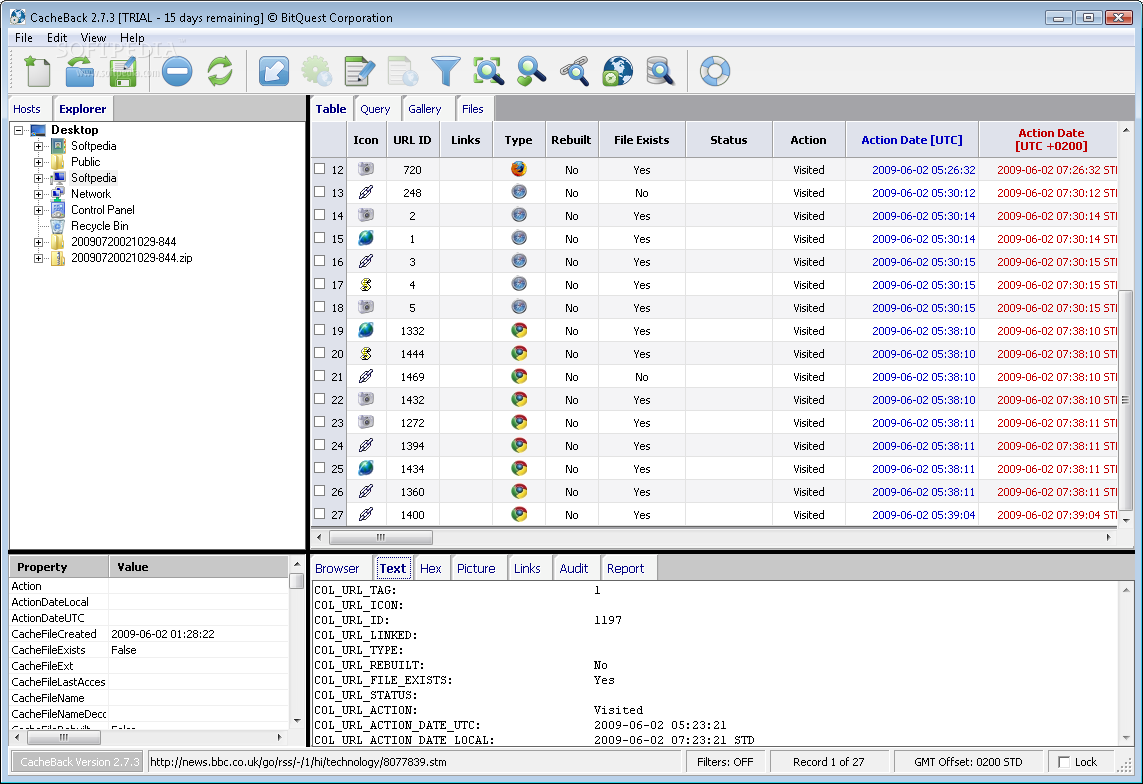
Figure 3: Browser forensics and the case of Casey Anthony The "like" button, stylized as a "thumbs up" icon, was first enabled on February 9, 2009, and enables users to easily interact with status updates, comments, photos and videos, links shared by friends, and advertisements. Once clicked by a user, the designated content is more likely to appear in friends' News Feeds. The button displays the number of other users who have liked the content. The like button was extended to comments in June 2010. In February 2016, Facebook expanded Like into "Reactions", allowing users to choose from five pre-defined emotions: "Love", "Haha", "Wow", "Sad", or "Angry". In late April 2020, during the COVID-19 pandemic, a new "Care" reaction was added.
Facebook Messenger is an instant messaging service and software application. It began as Facebook Chat in 2008, was revamped in 2010 and eventually became a standalone mobile app in August 2011, while remaining part of the user page on browsers. Complementing regular conversations, Messenger lets users make one-to-one and group voice and video calls. Its Android app has integrated support for SMS and "Chat Heads", which are round profile photo icons appearing on-screen regardless of what app is open, while both apps support multiple accounts, conversations with optional end-to-end encryption and "Instant Games". Some features, including sending money and requesting transportation, are limited to the United States.
In 2017, Facebook added "Messenger Day", a feature that lets users share photos and videos in a story-format with all their friends with the content disappearing after 24 hours; Reactions, which lets users tap and hold a message to add a reaction through an emoji; and Mentions, which lets users in group conversations type @ to give a particular user a notification. In April 2020, Facebook began rolling out a new feature called Messenger Rooms, a video chat feature that allows users to chat with up to 50 people at a time. In July 2020, Facebook added a new feature in Messenger that lets iOS users to use Face ID or Touch ID to lock their chats. The feature is called App Lock and is a part of several changes in Messenger regarding privacy and security. On October 13, 2020, the Messenger application introduced cross-app messaging with Instagram, which was launched in September 2021. In addition to the integrated messaging, the application announced the introduction of a new logo, which will be an amalgamation of the Messenger and Instagram logo. Businesses and users can interact through Messenger with features such as tracking purchases and receiving notifications, and interacting with customer service representatives. Third-party developers can integrate apps into Messenger, letting users enter an app while inside Messenger and optionally share details from the app into a chat. Developers can build chatbots into Messenger, for uses such as news publishers building bots to distribute news. Businesses like respond.io, Twilio, and Manychat also used the APIs to develop chatbots and automation platforms for commercial use. The M virtual assistant (U.S.) scans chats for keywords and suggests relevant actions, such as its payments system for users mentioning money. Group chatbots appear in Messenger as "Chat Extensions". A "Discovery" tab allows finding bots, and enabling special, branded QR codes that, when scanned, take the user to a specific bot.
Facebook's data policy outlines its policies for collecting, storing, and sharing user's data. Facebook enables users to control access to individual posts and their profile through privacy settings. The user's name and profile picture (if applicable) are public. Facebook's revenue depends on targeted advertising, which involves analyzing user data to decide which ads to show each user. Facebook buys data from third parties, gathered from both online and offline sources, to supplement its own data on users. Facebook maintains that it does not share data used for targeted advertising with the advertisers themselves. The company states: 4. Practical Deployment, Analysis & Case Studies "We provide advertisers with reports about the kinds of people seeing their ads and how their ads are performing, but we don't share information that personally identifies you (information such as your name or email address that by itself can be used to contact you or identifies who you are) unless you give us permission. For example, we provide general demographic and interest information to advertisers (for example, that an ad was seen by a woman between the ages of 25 and 34 who lives in Madrid and likes software engineering) to help them better understand their audience. We also confirm which Facebook ads led you to make a purchase or take an action with an advertiser." As of October 2021, Facebook claims it uses the following policy for sharing user data with third parties: Apps, websites, and third-party integrations on or using our Products. When you choose to use third-party apps, websites, or other services that use, or are integrated with, our Products, they can receive information about what you post or share. For example, when you play a game with your Facebook friends or use a Facebook Comment or Share button on a website, the game developer or website can receive information about your activities in the game or receive a comment or link that you share from the website on Facebook. Also, when you download or use such third-party services, they can access your public profile on Facebook, and any information that you share with them. Apps and websites you use may receive your list of Facebook friends if you choose to share it with them. But apps and websites you use will not be able to receive any other information about your Facebook friends from you, or information about any of your Instagram followers (although your friends and followers may, of course, choose to share this information themselves). Information collected by these third-party services is subject to their own terms and policies, not this one. Devices and operating systems providing native versions of Facebook and Instagram (i.e. where we have not developed our own first-party apps) will have access to all information you choose to share with them, including information your friends share with you, so they can provide our core functionality to you.
Note: We are in the process of restricting developers' data access even further to help prevent abuse. For example, we will remove developers' access to your Facebook and Instagram data if you haven't used their app in 3 months, and we are changing Login, so that in the next version, we will reduce the data that an app can request without app review to include only name, Instagram username and bio, profile photo and email address. Requesting any other data will require our approval.
Facebook will also share data with law enforcement if needed to. Facebook's policies have changed repeatedly since the service's debut, amid a series of controversies covering everything from how well it secures user data, to what extent it allows users to control access, to the kinds of access given to third parties, including businesses, political campaigns and governments. These facilities vary according to country, as some nations require the company to make data available (and limit access to services), while the European Union's GDPR regulation mandates additional privacy protections.
On July 29, 2011, Facebook announced its Bug Bounty Program that paid security researchers a minimum of $500 ($716.00 in 2025 dollars) for reporting security holes. The company promised not to pursue "white hat" hackers who identified such problems. This led researchers in many countries to participate, particularly in India and Russia. In many countries the social networking sites and mobile apps have been blocked temporarily, intermittently, or permanently, including: Brazil, China, Iran, Vietnam, Pakistanc, Syria, and North Korea. In May 2018, the government of Papua New Guinea announced that it would ban Facebook for a month while it evaluated the website's impact on the country, though no ban has since occurred. In 2019, Facebook announced it would start enforcing its ban on users, including influencers, promoting any vape, tobacco products, or weapons on its platforms.
Facebook's importance and scale has led to criticisms in many domains. Issues include Internet privacy, excessive retention of user information, its facial recognition software, DeepFace its addictive quality and its role in the workplace, including employer access to employee accounts. Facebook has been criticized for electricity usage, tax avoidance, real-name user requirement policies, censorship and its involvement in the United States PRISM surveillance program. According to The Express Tribune, Facebook "avoided billions of dollars in tax using offshore companies". Facebook is alleged to have harmful psychological effects on its users, including feelings of jealousy and stress, a lack of attention and social media addiction.
According to Kaufmann et al., mothers' motivations for using social media are often related to their social and mental health. European antitrust regulator Margrethe Vestager stated that Facebook's terms of service relating to private data were "unbalanced". Facebook has been criticized for allowing users to publish illegal or offensive material. Specifics include copyright and intellectual property infringement, hate speech, incitement of rape and terrorism, fake news, and crimes, murders, and livestreaming violent incidents. Commentators have accused Facebook of willingly facilitating the spread of such content. Sri Lanka blocked both Facebook and WhatsApp in May 2019 after anti-Muslim riots, the worst in the country since the Easter Sunday bombing in the same year as a temporary measure to maintain peace in Sri Lanka. Facebook removed 3 billion fake accounts only during the last quarter of 2018 and the first quarter of 2019; in comparison, the social network reports 2.39 billion monthly active users. In late July 2019, the company announced it was under antitrust investigation by the Federal Trade Commission. The consumer advocacy group Which? claimed individuals were still utilizing Facebook to set up fraudulent five-star ratings for products. The group identified 14 communities that exchange reviews for either money or complimentary items such as watches, earbuds, and sprinklers. Facebook and its parent Meta have been subject to regulatory actions and fines over past privacy failures, including a substantial fine by the Irish Data Protection Commission for a severe 2018 breach affecting millions of accounts. Earlier, Facebook's role in the Facebook–Cambridge Analytica data scandal exposed the personal data of tens of millions of users without proper consent, leading to global criticism and legal actions. Moreover, investigative reports have highlighted ongoing issues with fraudulent and scam advertisements on Facebook platforms, revealing that the company earned significant revenue from such content even as enforcement efforts have lagged, drawing regulatory pressure worldwide.
Facebook has experienced a steady stream of controversies over how it handles user privacy, repeatedly adjusting its privacy settings and policies. Since 2009, Facebook has been participating in the PRISM secret program, sharing with the US National Security Agency audio, video, photographs, e-mails, documents and connection logs from user profiles, among other social media services. On November 29, 2011, Facebook settled Federal Trade Commission charges that it deceived consumers by failing to keep privacy promises. In August 2013 High-Tech Bridge published a study showing that links included in Facebook messaging service messages were being accessed by Facebook. In January 2014 two users filed a lawsuit against Facebook alleging that their privacy had been violated by this practice. On June 7, 2018, Facebook announced that a bug had resulted in about 14 million Facebook users having their default sharing setting for all new posts set to "public". Its data-sharing agreement with Chinese companies such as Huawei came under the scrutiny of US lawmakers, although the information accessed was not stored on Huawei servers and remained on users' phones. On April 4, 2019, half a billion records of Facebook users were found exposed on Amazon cloud servers, containing information about users' friends, likes, groups, and checked-in locations, as well as names, passwords and email addresses. The phone numbers of at least 200 million Facebook users were found to be exposed on an open online database in September 2019. They included 133 million US users, 18 million from the UK, and 50 million from users in Vietnam. After removing duplicates, the 419 million records have been reduced to 219 million. The database went offline after TechCrunch contacted the web host. It is thought the records were amassed using a tool that Facebook disabled in April 2018 after the Cambridge Analytica controversy. A Facebook spokeswoman said in a statement: "The dataset is old and appears to have information obtained before we made changes last year...There is no evidence that Facebook accounts were compromised." Facebook's privacy problems resulted in companies like Viber Media and Mozilla discontinuing advertising on Facebook's platforms. A January 2024 study by Consumer Reports found that among a self-selected group of volunteer participants, each user is monitored or tracked by over two thousand companies on average. LiveRamp, a San Francisco-based data broker, is responsible for 96 per cent of the data. Other companies such as Home Depot, Macy's, and Walmart are involved as well. In March 2024, a court in California released documents detailing Facebook's 2016 "Project Ghostbusters". The project was aimed at helping Facebook compete with Snapchat and involved Facebook trying to develop decryption tools to collect, decrypt, and analyze traffic that users generated when visiting Snapchat and, eventually, YouTube and Amazon. The company eventually used its tool Onavo to initiate man-in-the-middle attacks and read users' traffic before it was encrypted.
5. Performance Evaluation & Extended Technical Observations Facebook customer Global Science Research sold information on over 87 million Facebook users to Cambridge Analytica, a political data analysis firm led by Alexander Nix. While approximately 270,000 people used the app, Facebook's API permitted data collection from their friends without their knowledge. At first Facebook downplayed the significance of the breach, and suggested that Cambridge Analytica no longer had access. Facebook then issued a statement expressing alarm and suspended Cambridge Analytica. Review of documents and interviews with former Facebook employees suggested that Cambridge Analytica still possessed the data. This was a violation of Facebook's consent decree with the Federal Trade Commission. This violation potentially carried a penalty of $40,000 ($51,285 in 2025 dollars) per occurrence, totalling trillions of dollars. According to The Guardian, both Facebook and Cambridge Analytica threatened to sue the newspaper if it published the story. After publication, Facebook claimed that it had been "lied to". On March 23, 2018, the English High Court granted an application by the Information Commissioner's Office for a warrant to search Cambridge Analytica's London offices, ending a standoff between Facebook and the Information Commissioner over responsibility. On March 25, Facebook published a statement by Zuckerberg in major UK and US newspapers apologizing over a "breach of trust".
You may have heard about a quiz app built by a university researcher that leaked Facebook data of millions of people in 2014. This was a breach of trust, and I'm sorry we didn't do more at the time. We're now taking steps to make sure this doesn't happen again. We've already stopped apps like this from getting so much information. Now we're limiting the data apps get when you sign in using Facebook. We're also investigating every single app that had access to large amounts of data before we fixed this. We expect there are others. And when we find them, we will ban them and tell everyone affected. Finally, we'll remind you which apps you've given access to your information – so you can shut off the ones you don't want anymore.
Thank you for believing in this community. I promise to do better for you. On March 26, the Federal Trade Commission opened an investigation into the matter. The controversy led Facebook to end its partnerships with data brokers who aid advertisers in targeting users. On April 24, 2019, Facebook said it could face a fine between $3 billion ($3.78 billion in 2025 dollars) to $5 billion ($6.3 billion in 2025 dollars) as the result of an investigation by the Federal Trade Commission. On July 24, 2019, the FTC fined Facebook $5 billion, the largest penalty ever imposed on a company for violating consumer privacy.
Additionally, Facebook had to implement a new privacy structure, follow a 20-year settlement order, and allow the FTC to monitor Facebook. Cambridge Analytica's CEO and a developer faced restrictions on future business dealings and were ordered to destroy any personal information they collected. Cambridge Analytica filed for bankruptcy. Facebook also implemented additional privacy controls and settings in part to comply with the European Union's General Data Protection Regulation (GDPR), which took effect in May. Facebook also ended its active opposition to the California Consumer Privacy Act. Some, such as Meghan McCain, have drawn an equivalence between the use of data by Cambridge Analytica and the Barack Obama's 2012 campaign, which, according to Investor's Business Daily, "encouraged supporters to download an Obama 2012 Facebook app that, when activated, let the campaign collect Facebook data both on users and their friends." Carol Davidsen, the Obama for America (OFA) former director of integration and media analytics, wrote that "Facebook was surprised we were able to suck out the whole social graph, but they didn't stop us once they realised that was what we were doing". PolitiFact has rated McCain's statements "Half-True", on the basis that "in Obama's case, direct users knew they were handing over their data to a political campaign" whereas with Cambridge Analytica, users thought they were only taking a personality quiz for academic purposes, and while the Obama campaign only used the data "to have their supporters contact their most persuadable friends", Cambridge Analytica "targeted users, friends and lookalikes directly with digital ads." After acquiring Onavo in 2013, Facebook used its Onavo Protect virtual private network (VPN) app to collect information on users' web traffic and app usage. This allowed Facebook to monitor its competitors' performance, and motivated Facebook to acquire WhatsApp in 2014. Media outlets classified Onavo Protect as spyware. In August 2018, Facebook removed the app in response to pressure from Apple, who asserted that it violated their guidelines. The Australian Competition and Consumer Commission sued Facebook on December 16, 2020, for "false, misleading or deceptive conduct" in response to the company's unauthorized use of personal data obtained from Onavo for business purposes in contrast to Onavo's privacy-oriented marketing. In 2016, Facebook Research launched Project Atlas, offering some users between the ages of 13 and 35 up to $20 per month ($27.00 in 2025 dollars) in exchange for their personal data, including their app usage, web browsing history, web search history, location history, personal messages, photos, videos, emails and Amazon order history.
In January 2019, TechCrunch reported on the project. This led Apple to temporarily revoke Facebook's Enterprise Developer Program certificates for one day, preventing Facebook Research from operating on iOS devices and disabling Facebook's internal iOS apps. Ars Technica reported in April 2018 that the Facebook Android app had been harvesting user data, including phone calls and text messages, since 2015. In May 2018, several Android users filed a class action lawsuit against Facebook for invading their privacy. In January 2020, Facebook launched the Off-Facebook Activity page, which allows users to see information collected by Facebook about their non-Facebook activities. The Washington Post columnist Geoffrey A.
Fowler found that this included what other apps he used on his phone, even while the Facebook app was closed, what other web sites he visited on his phone, and what in-store purchases he made from affiliated businesses, even while his phone was completely off. In November 2021, a report was published by Fairplay, Global Action Plan and Reset Australia detailing accusations that Facebook was continuing to manage their ad targeting system with data collected from teen users. The accusations follow announcements by Facebook in July 2021 that they would cease ad targeting children.
Facebook relies on its users to generate the content that bonds its users to the service. The company has come under criticism both for allowing objectionable content, including conspiracy theories and fringe discourse, and for prohibiting other content that it deems inappropriate. Facebook has been criticized as a vector for fake news, and has been accused of bearing responsibility for the conspiracy theory that the United States created ISIS, false anti-Rohingya posts being used by Myanmar's military to fuel genocide and ethnic cleansing, enabling climate change denial and Sandy Hook Elementary School shooting conspiracy theorists, and anti-refugee attacks in Germany. The government of the Philippines has also used Facebook as a tool to attack its critics. In 2017, Facebook partnered with fact checkers from the Poynter Institute's international fact-checking network to identify and mark false content, though most ads from political candidates are exempt from this program. As of 2018, Facebook had over 40 fact-checking partners across the world, including The Weekly Standard. Critics of the program have accused Facebook of not doing enough to remove false information from its website. Facebook has repeatedly amended its content policies. In July 2018, it stated that it would "downrank" articles that its fact-checkers determined to be false, and remove misinformation that incited violence. Facebook stated that content that receives "false" ratings from its fact-checkers can be demonetized and suffer dramatically reduced distribution. Specific posts and videos that violate community standards can be removed on Facebook. In May 2019, Facebook banned a number of "dangerous" commentators from its platform, including Alex Jones, Louis Farrakhan, Milo Yiannopoulos, Paul Joseph Watson, Paul Nehlen, David Duke, and Laura Loomer, for allegedly engaging in "violence and hate". In May 2020, Facebook agreed to a preliminary settlement of $52 million ($64.7 million in 2025 dollars) to compensate U.S.-based Facebook content moderators for their psychological trauma suffered on the job.
Other legal actions around the world, including in Ireland, await settlement. In September 2020, the Government of Thailand utilized the Computer Crime Act for the first time to take action against Facebook and Twitter for ignoring requests to take down content and not complying with court orders. According to a report by Reuters, beginning in 2020, the United States military ran a propaganda campaign to spread disinformation about the Sinovac Chinese COVID-19 vaccine, including using fake social media accounts to spread the disinformation that the Sinovac vaccine contained pork-derived ingredients and was therefore haram under Islamic law. The campaign was described as "payback" for COVID-19 disinformation by China directed against the U.S. In summer 2020, Facebook asked the military to remove the accounts, stating that they violated Facebook's policies on fake accounts and on COVID-19 information. The campaign continued until mid-2021. In 2025, Meta announced the replacement of fact-checking on Facebook and Instagram with a "community notes" feature. Steven Brill, co-founder of news reliability rating company NewsGuard, criticized this decision, and described Facebook's prior fact-checking efforts as having failed to prevent misinformation.
As a dominant social-web service with massive outreach, Facebook has been used by identified or unidentified political operatives to affect public opinion. Some of these activities have been done in violation of the platform policies, creating "coordinated inauthentic behavior", support or attacks. These activities can be scripted or paid. Various such abusive campaign have been revealed in recent years, best known being the Russian interference in the 2016 United States elections.
In 2021, former Facebook analyst within the Spam and Fake Engagement teams, Sophie Zhang, reported more than 25 political subversion operations and criticized the general slow reaction time, oversightless, laissez-faire attitude by Facebook. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Tor%20%28network%29 • https://en.wikipedia.org/wiki/Facebook • https://en.wikipedia.org/wiki/Telegram%20%28software%29
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Browser History And Cache Forensic Analysis Tool Python.
[*] Metasploit Scan Running on Target Subnet for Browser History And Cache Forensic Analysis Tool Python... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |