Complete Technical Paper Content — Client Side Security Auditing Tool Using Javascript
Overview & System Context
Client Side Security Auditing Tool Using Javascript: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9524 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Web-based SSH is the provision of Secure Shell (SSH) access through a web browser. SSH is a secure network protocol that is commonly used to remotely control servers, network devices, and other devices. With web-based SSH, users can access and manage these devices using a standard web browser, without the need to install any additional software. Web-based SSH clients are typically implemented using JavaScript and either Ajax or WebSockets. These clients communicate with the SSH server through a proxy, which allows them to bypass firewalls and other network security measures that may block SSH traffic. This makes web-based SSH a convenient and secure way to access remote servers and devices from any location with an internet connection. Web-based SSH is useful for a variety of purposes, including system administration, network management, and remote development. It is often used by IT professionals and developers to remotely access and manage servers, as well as by individuals who need to access their home or office computers from a remote location.
Accessibility: Web-based SSH as described in this article requires no local installation of client software. It is thus possible to access SSH servers through a web browser from anywhere. As communication is based on HTTP or HTTPS it is also possible to access SSH servers from behind a firewall or proxy that restricts Internet access to only ports 80 (HTTP) or 443 (HTTPS). Anonymous Access: As SSH access is tunneled through an intermediary web application server it is this server which actually communicates with the SSH server. This means that the SSH server will only be aware of the IP address of the web application server, keeping the actual client's IP address hidden. Auditability: Because all communication between the client and the SSH server must pass through the web application server this communication can be logged. This prevents a malicious client from deleting logs of their activities. The situation is exactly the same as with traditional SSH server.
Resuming Sessions: Some web-based SSH implementations allow the user to resume their SSH sessions after being disconnected. This is not possible with a traditional SSH client. Embeddable: Web-based SSH implementations can be embedded into any web page allowing them to be integrated into other web-based applications. Unique Features: Many web-based SSH tools have unique features such as the ability to share terminals with other users, can display images within terminals, and other useful capabilities.
Security: It is important to make sure that HTTPS is used when communicating with the web application server. Otherwise all data being sent would be readable by use of simple packet sniffers which could reveal sensitive information. Trust: The data being sent to the web application server is decrypted there. This is necessary in order to forward the issued commands to the actual SSH server. Even though the operators of web-based SSH solutions usually don't log sensitive data the data is theoretically available to them in plain form. It is unlikely that this will cause a security issue when the web application server and the SSH server are run on the same server or are controlled by the same entity. Tunneling: Unlike most traditional, application based SSH clients, web-based SSH clients are unable to tunnel ("forward") TCP traffic. For example, running an X session over a web-based SSH session is not possible. However, the lack of ability is caused by implementation issues, and not inherent in some way.
Google Chrome is a cross-platform web browser developed by Google. It was launched in September 2008 for Microsoft Windows, built with free and open-source (FOSS) components from Apple WebKit and Mozilla Firefox. Versions for Linux, macOS, iOS, iPadOS, and Android were later released, and Chrome became the default browser on Android devices. It is also the main component of ChromeOS, on which it serves as the platform for web applications. Most of Chrome's source code comes from Google's FOSS software project known as Chromium, but Chrome is licensed as proprietary freeware.
Having originally used WebKit as the rendering engine for Chrome, Google eventually forked it to create the Blink engine; every version of Chrome uses Blink as of 2017, except for the version on iOS. As of March 2026, StatCounter estimates that Chrome has a 75.23% worldwide browser market share on personal computers. It is the most used browser on tablets having an estimated 48% market share. Chrome is also dominant on smartphones with around 67% market share. With a market share of 71.22% across all platforms combined as of December 2025, Chrome is the most used web browser in the world.
Chrome has approximately 3.62 billion users as of March 2026. Google chief executive Eric Schmidt was previously involved in the "browser wars" (a part of U.S. corporate history) and opposed the expansion of the company into such a new area. However, Google co-founders, Sergey Brin and Larry Page, spearheaded a software demonstration that pushed Schmidt into making Chrome a core business priority, which resulted in it becoming a commercial success. Because of the proliferation of Chrome, Google has expanded the "Chrome" brand name to other products. This includes ChromeOS, Chromecast, Chromebook, Chromebit, Chromebox, and Chromebase.
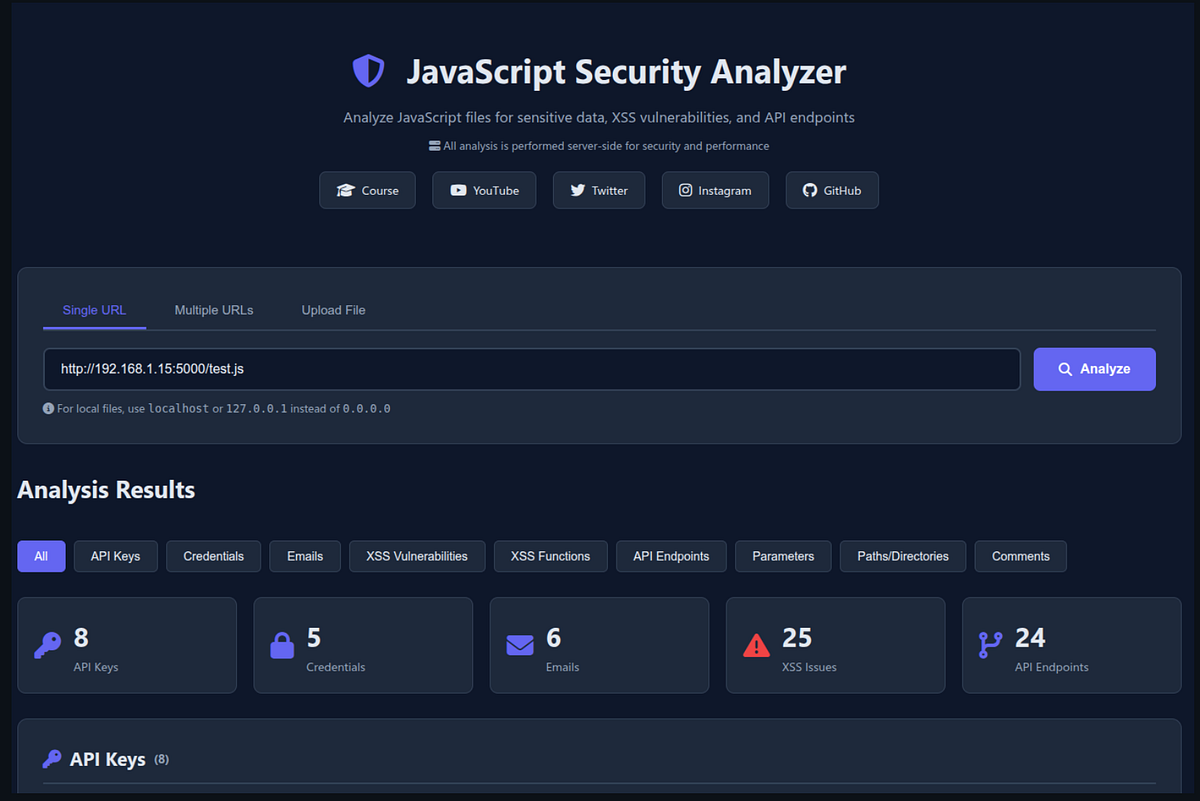
Figure 1: JavaScript Security Analyzer — The Ultimate Tool for Detecting Bugs and ... Google chief executive Eric Schmidt opposed the development of an independent web browser for six years. He stated that "at the time, Google was a small company", and he did not want to go through "bruising browser wars". Company co-founders Sergey Brin and Larry Page hired several Mozilla Firefox developers and built a demonstration of Chrome. Afterward, Schmidt said, "It was so good that it essentially forced me to change my mind." In September 2004, rumors of Google building a web browser first appeared. Online journals and U.S. newspapers stated at the time that Google was hiring former Microsoft web developers, among others. It also came shortly after the release of Mozilla Firefox 1.0, which was surging in popularity and taking market share from Internet Explorer, which had noted security problems. Chrome is based on the open-source code of the Chromium project. Development of the browser began in 2006, spearheaded by Sundar Pichai. Google has since become the world's most popular search engine. 90% of searches on search engines come from Google users.
The release announcement was originally scheduled for September 3, 2008, and a comic by Scott McCloud was to be sent to journalists and bloggers explaining the features within the new browser. Copies intended for Europe were shipped early, and German blogger Philipp Lenssen of Google Blogoscoped made a scanned copy of the 38-page comic available on his website after receiving it on September 1, 2008. Google subsequently made the comic available on Google Books, and mentioned it on their official blog along with an explanation for the early release. The product was named "Chrome" as an initial development project code name, because it is associated with fast cars and speed. Google kept the development project name as the final release name, as a "cheeky" or ironic moniker, as one of the main aims was to minimize the user interface chrome.
The browser was first publicly released, officially as a beta version, on September 2, 2008, for Windows XP and newer, and with support for 43 languages, and later as a "stable" public release on December 11, 2008. On that same day, a CNET news item drew attention to a passage in the Terms of Service statement for the initial beta release, which seemed to grant Google a license to all content transferred via the Chrome browser. This passage was inherited from the general Google terms of service. Google responded to this criticism immediately by stating that the language used was borrowed from other products, and removed this passage from the Terms of Service. Chrome quickly gained about 1% usage share. After the initial surge, usage share dropped until it hit a low of 0.69% in October 2008. It then started rising again and by December 2008, Chrome again passed the 1% threshold. In early January 2009, CNET reported that Google planned to release versions of Chrome for macOS and Linux in the first half of the year. The first official macOS and Linux developer previews of Chrome were announced on June 4, 2009, with a blog post saying they were missing many features and were intended for early feedback rather than general use. In December 2009, Google released beta versions of Chrome for macOS and Linux. Google Chrome 5.0, announced on May 25, 2010, was the first stable release to support all three platforms. Chrome was one of the twelve browsers offered on BrowserChoice.eu to European Economic Area users of Microsoft Windows in 2010.
By default, the main user interface includes back, forward, refresh/cancel, and menu buttons. A home button is not shown by default, but can be added through the Settings page to take the user to the new tab page or a custom home page. Tabs are the main component of Chrome's user interface and have been moved to the top of the window rather than below the controls. This subtle change contrasts with many existing tabbed browsers, which are based on windows and contain tabs. Tabs, with their state, can be transferred between window containers by dragging. Each tab has its own set of controls, including the Omnibox. The Omnibox is a URL box that combines the functions of both the address bar and search box. If a user enters the URL of a site previously searched from, Chrome allows pressing Tab to search the site again directly from the Omnibox.
When a user starts typing in the Omnibox, Chrome provides suggestions for previously visited sites (based on the URL or in-page text), popular websites (not necessarily visited before – powered by Google Instant), and popular searches. Although Instant can be turned off, suggestions based on previously visited sites cannot be turned off. Chrome will also autocomplete the URLs of sites visited often. If a user types keywords into the Omnibox that do not match any previously visited websites and presses enter, Chrome will conduct the search using the default search engine. One of Chrome's differentiating features is the New Tab Page, which can replace the browser home page and is displayed when a new tab is created. Originally, this showed thumbnails of the nine most visited websites, along with frequent searches, recent bookmarks, and recently closed tabs; similar to Internet Explorer and Firefox with Google Toolbar, or Opera's Speed Dial. In Google Chrome 2.0, the New Tab Page was updated to allow users to hide thumbnails they did not want to appear. Starting in version 3.0, the New Tab Page was revamped to display thumbnails of the eight most visited websites. The thumbnails could be rearranged, pinned, and removed. Alternatively, a list of text links could be displayed instead of thumbnails. It also features a "Recently closed" bar that shows recently closed tabs and a "tips" section that displays hints and tricks for using the browser. Starting with Google Chrome 3.0, users can install themes to alter the appearance of the browser. Many free third-party themes are provided in an online gallery, accessible through a "Get themes" button in Chrome's options. Chrome includes a bookmarks submenu that lists the user's bookmarks, provides easy access to Chrome's Bookmark Manager, and allows the user to toggle a bookmarks bar on or off. On January 2, 2019, Google introduced Native Dark Theme for Chrome on Windows 10. In 2023, it was announced that Chrome would be completely revamped, using Google's Material You design language, the revamp would include more rounded corners, Chrome colors being swapped out for a similar dynamic color system introduced in Android 12, a revamped address bar, new icons, and tabs, and a more simplified 3 dot menu.
Figure 2: Best Client-Side Security Tools for Compliance Reporting Starting with Google Chrome 4.1, the application added a built-in translation bar using Google Translate. Language translation is currently available for 52 languages. When Chrome detects a foreign language other than the user's preferred language set during the installation time, it asks the user whether to translate. Chrome allows users to synchronize their bookmarks, history, and settings across all devices with the browser installed by sending and receiving data through a chosen Google Account, which in turn updates all signed-in instances of Chrome. This can be authenticated either through Google credentials or a sync passphrase. For web developers, Chrome has an element inspector that allows users to look inside any web page's Document Object Model (DOM) structure and examine the code elements that make up the webpage. Chrome has special URLs that load application-specific pages instead of websites or files on disk. Chrome also has a built-in ability to enable experimental features. Originally called about:labs, the address was changed to about:flags to make it less obvious to casual users. The desktop edition of Chrome can save pages as HTML with assets in a "_files" subfolder, or as an unprocessed HTML-only document. It also offers an option to save in the MHTML format.
Announced on May 19, 2010, the Chrome Web Store allows users to install web applications as extensions to the browser, although most of these extensions function simply as links to popular web pages or games, some of the apps, like Springpad, do provide extra features like offline access. The themes and extensions have also been tightly integrated into the new store, allowing users to search the entire catalog of Chrome extras. The Chrome Web Store was opened on December 7, 2010.
In October 2018, Google announced a major future update to Chrome's extension API, known as "Manifest V3" (in reference to the manifest file contained within extensions). Manifest V3 is intended to modernize the extension architecture and improve the security and performance of the browser; it adopts declarative APIs to "decrease the need for overly-broad access and enable more performant implementation by the browser", replaces background pages with feature-limited "Service Workers" to reduce resource usage, and prohibits remotely-hosted code. Google faced criticism for this change since it limits the number of rules and types of expressions that may be checked by ad blockers. Additionally, the prohibition of remotely-hosted code will restrict the ability for ad-blocking filter lists to be updated independently of the extension itself.
Chrome periodically retrieves updates of two blacklists (one for phishing and one for malware), and warns users when they attempt to visit a site flagged as potentially harmful. This service is also made available for use by others via a free public API called "Google Safe Browsing API". Chrome uses a process-allocation model to sandbox tabs. Using the principle of least privilege, each tab process cannot interact with critical memory functions (e.g. OS memory, user files) or other tab processes – similar to Microsoft's "Protected Mode" used by Internet Explorer 9 or greater. The Sandbox Team is said to have "taken this existing process boundary and made it into a jail". This enforces a computer security model whereby there are two levels of multilevel security (user and sandbox) and the sandbox can only respond to communication requests initiated by the user. On Linux sandboxing uses the seccomp mode. In January 2015, TorrentFreak reported that using Chrome when connected to the internet using a VPN can be a serious security issue due to the browser's support for WebRTC. On September 9, 2016, it was reported that starting with Chrome 56, users will be warned when they visit insecure HTTP websites to encourage more sites to make the transition to HTTPS. On December 4, 2018, Google announced its Chrome 71 release with new security features, including a built-in ad-blocking system. In addition, Google also announced its plan to crack down on websites that make people involuntarily subscribe to mobile subscription plans. On September 2, 2020, with the release of Chrome 85, Google extended support for Secure DNS in Chrome for Android. DNS-over-HTTPS (DoH) was designed to improve safety and privacy while browsing the web. Under the update, Chrome automatically switches to DNS-over-HTTPS (DoH) if the current DNS provider supports the feature.
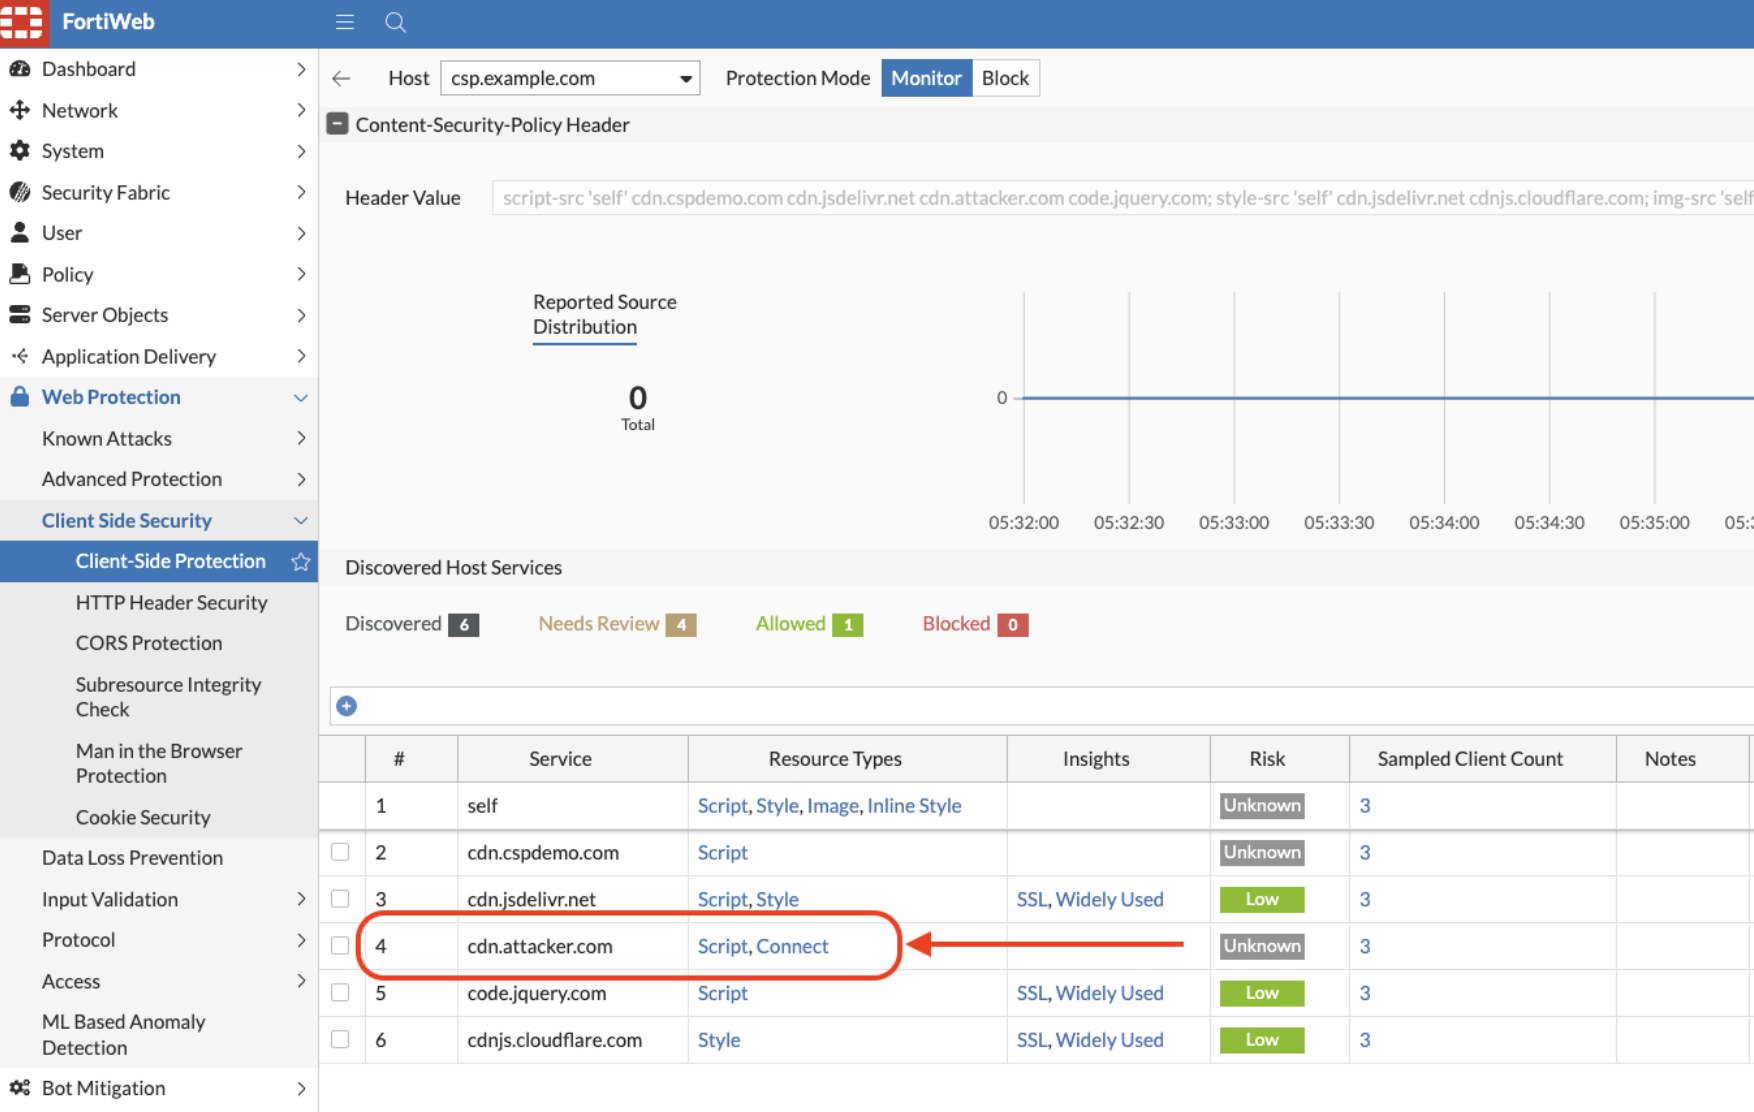
Figure 3: Blog Técnico FORTINET: Client-Side Protection en FortiWeb 8.0.x The private browsing feature called Incognito mode prevents the browser from locally storing any history information, cookies, site data, or form inputs. Downloaded files and bookmarks will be stored. In addition, user activity is not hidden from visited websites or the Internet service provider. Incognito mode is similar to the private browsing feature in other web browsers. The iOS version of Chrome also supports the optional ability to lock incognito tabs with Face ID, Touch ID, or the device's passcode. In 2022, Google began to implement this feature into Android versions of Chrome. From 2023, this feature is available for Android 12 devices and above, when the hardware allows it. In 2024, Google agreed to destroy billions of records to settle a lawsuit claiming it secretly tracked the internet use of people who thought they were browsing privately in incognito mode.
A multi-process architecture is implemented in Chrome where, by default, a separate process is allocated to each site instance and plugin. This procedure is termed process isolation, and raises security and stability by preventing tasks from interfering with each other. An attacker successfully gaining access to one application gains access to no others, and failure in one instance results in a Sad Tab screen of death, similar to the well-known Sad Mac, but only one tab crashes instead of the whole application. This strategy exacts a fixed per-process cost up front, but results in less memory bloat over time as fragmentation is confined to each instance and no longer needs further memory allocations. This architecture was later adopted in Safari and Firefox. Chrome includes a process management utility called Task Manager which lets users see what sites and plugins are using the most memory, downloading the most bytes, and overusing the CPU and provides the ability to terminate them. Chrome Version 23 ensures its users an improved battery life for the systems supporting Chrome's GPU accelerated video decoding.
On July 22, 2010, Google announced it would ramp up the speed at which it releases new stable versions; the release cycles were shortened from quarterly to six weeks for major Stable updates. Beta channel releases now come roughly at the same rate as Stable releases, though approximately one month in advance, while Dev channel releases appear roughly once or twice weekly, allowing time for basic release-critical testing. This faster release cycle also brought a fourth channel: the "Canary" channel, updated daily from a build produced at 09:00 UTC from the most stable of the last 40 revisions. The name refers to the practice of using canaries in coal mines, so if a change "kills" Chrome Canary, it will be blocked from migrating down to the Developer channel, at least until fixed in a subsequent Canary build. Canary is "the most bleeding-edge official version of Chrome and somewhat of a mix between Chrome dev and the Chromium snapshot builds". Canary releases run side by side with any other channel; it is not linked to the other Google Chrome installation and can therefore run different synchronization profiles, themes, and browser preferences. This ensures that fallback functionality remains even when some Canary updates may contain release-breaking bugs. It does not natively include the option to be the default browser, although on Windows and macOS it can be set through System Preferences. Canary was Windows-only at first; a macOS version was released on May 3, 2011. The Chrome beta channel for Android was launched on January 10, 2013; like Canary, it runs side by side with the stable channel for Android. Chrome Dev for Android was launched on April 29, 2015. All Chrome channels are automatically distributed according to their respective release cycles. The mechanism differs by platform. On Windows, it uses Google Update, and auto-update can be controlled via Group Policy. Alternatively, users may download a standalone installer of a version of Chrome that does not auto-update. On macOS, it uses Google Update Service, and auto-update can be controlled via the macOS "defaults" system. On Linux, it lets the system's normal package management system supply the updates. This auto-updating behavior is a key difference from Chromium, the non-branded open-source browser which forms the core of Google Chrome. Because Chromium also serves as the pre-release development trunk for Chrome, its revisions are provided as source code, and buildable snapshots are produced continuously with each new commit, requiring users to manage their own browser updates. In March 2021, Google announced that starting with Chrome 94 in the third quarter of 2021, Google Chrome Stable releases would be made every four weeks, instead of six weeks as they had been since 2010.
Also, Google announced a new release channel for system administrators and browser embedders with releases every eight weeks. Five years later, it was announced that Chrome would follow Firefox in moving to its two-week development schedule, with the upcoming release of Chrome 153 on September 8. Major.minor reflects scheduling policy Build.patch identifies content progression Major represents a product release. These are scheduled 7–8 per year, unlike other software systems where the major version number updates only with substantial new content. Minor is usually 0. References to version 'x' or 'x.0', e.g., 42.0, refer to this major.minor designation. Build is ever-increasing. For a release cycle, e.g., 42.0, there are several builds in the Canary and Developer periods. The last build number from Developer is kept throughout Beta and Stable and is locked with the major.minor for that release. Patch resets with each build, incrementing with each patch. The first patch is 0, but usually the first publicly released patch is somewhat higher. In Beta and Stable, only patch increments. Chromium and Chrome release schedules are linked through Chromium (Major) version Branch Point dates, published annually. The Branch Points precede the final Chrome Developer build (initial) release by 4 days (nearly always) and the Chrome Stable initial release by roughly 53 days. Example: The version 42 Branch Point was February 20, 2015. Developer builds stopped advancing at build 2311 with release 42.0.2311.4 on February 24, 4 days later. The first Stable release, 42.0.2311.90, was April 14, 2015, 53 days after the Branch Point.
Chrome supports color management by using the system-provided ICC v2 and v4 support on macOS, and from version 22 supports ICC v2 profiles by default on other platforms. In Chrome, when not connected to the Internet and an error message displaying "No internet" is shown, on the top, an "8-bit" Tyrannosaurus rex is shown, but when pressing the space bar on a keyboard, mouse-clicking on it or tapping it on touch devices, the T-Rex instantly jumps once and starts dashing across a cactus-ridden desert, revealing it to be an Easter egg in the form of a platform game. The game itself is an infinite runner, and there is no time limit in the game as it progresses faster and periodically tints to a black background. A school or enterprise manager can disable the game.
Windows 10 or later Windows Server 2016 or later macOS Ventura or later 64-bit versions of Ubuntu 18.04+, Debian 10+, openSUSE 15.5+, and Fedora 39+ Android 10 or later iOS 18 or later iPadOS 18 or later As of April 2016, stable 32-bit and 64-bit builds are available for Windows, with only 64-bit stable builds available for Linux and macOS. 64-bit Windows builds became available in the developer channel and as canary builds on June 3, 2014, in the beta channel on July 30, 2014, and in the stable channel on August 26, 2014. 64-bit macOS builds became available as canary builds on November 7, 2013, in the beta channel on October 9, 2014, and in the stable channel on November 18, 2014. Starting with the release of version 89, Chrome will only be supported on Intel/Intel x86 and AMD processors with the SSE3 instruction set.
A beta version for Android 4.0 devices was launched on February 7, 2012, available for a limited number of countries from Google Play. Notable features: synchronization with desktop Chrome to provide the same bookmarks and view the same browser tabs, page pre-rendering, hardware acceleration. Many of the latest HTML5 features: almost all of the Web Platform's features: GPU-accelerated canvas, including CSS 3D Transforms, CSS animations, SVG, WebSocket (including binary messages), Dedicated Workers; it has overflow scroll support, strong HTML5 video support, and new capabilities such as IndexedDB, web workers, Application Cache and the File APIs, date- and time-pickers, parts of the Media Capture API. Also supports mobile oriented features such as Device Orientation and Geolocation. Mobile customizations: swipe gesture tab switching, link preview allows zooming in on (multiple) links to ensure the desired one is clicked, font size boosting to ensure readability regardless of the zoom level. Features missing in the mobile version include sandboxed tabs, Safe Browsing, apps or extensions, Adobe Flash (now and in the future), Native Client, and the ability to export user data such a list of their opened tabs or their browsing history into portable local files. Development changes: remote debugging, part of the browser layer has been implemented in Java, communicating with the rest of the Chromium and WebKit code through Java Native Bindings. The code of Chrome for Android is a fork of the Chromium project. It is a priority to upstream most new and modified code to Chromium and WebKit to resolve the fork. The April 17, 2012, update included availability in 31 additional languages and in all countries where Google Play is available. A desktop version of a website can also be requested, as opposed to a mobile version. In addition, Android users can now add bookmarks to their Android home screens if they choose and decide which apps should handle links opened in Chrome. On June 27, 2012, Google Chrome for Android exited beta and became stable.
Chrome 18.0.1026311, released on September 26, 2012, was the first version of Chrome for Android to support mobile devices based on Intel x86. Starting from version 25, the Chrome version for Android is aligned with the desktop version, and usually new stable releases are available at the same time for both the Android and the desktop versions. Google released a separate Chrome for Android beta channel on January 10, 2013, with version 25. As of 2013 a separate beta version of Chrome is available in the Google Play Store – it can run side by side with the stable release.
Chrome is available on Apple's mobile iOS and iPadOS operating systems. Released in the Apple App Store on June 26, 2012, it supports the iPad, iPhone, and formerly the iPod touch; the current version requires that the device has iOS 17.0 or greater or iPadOS 17.0 or greater installed. In accordance with Apple's requirements for browsers released through their App Store, this version of Chrome uses the iOS WebKit – which is Apple's own mobile rendering engine and components, developed for their Safari browser – therefore it is restricted from using Google's own V8 JavaScript engine. Chrome is the default web browser for the iOS and iPadOS Gmail application. In a review by Chitika, Chrome was noted as having 1.5% of the iOS web browser market as of July 18, 2012. In October 2013, Chrome had 3% of the iOS browser market.
Google Chrome is the basis of Google's ChromeOS operating system that ships on specific hardware from Google's manufacturing partners. The user interface has a minimalist design resembling the Google Chrome browser. ChromeOS is aimed at users who spend most of their computer time on the Web; the only applications on the devices are a browser incorporating a media player and a file manager. Google announced ChromeOS on July 7, 2009.
Google Chrome was met with acclaim upon release. In 2008, Matthew Moore of The Daily Telegraph summarized the verdict of early reviewers: "Google Chrome is attractive, fast and has some impressive new features..." Initially, Microsoft reportedly played down the threat from Chrome and predicted that most people would embrace Internet Explorer 8. Opera Software said that "Chrome will strengthen the Web as the biggest application platform in the world". But by February 25, 2010, BusinessWeek had reported that "For the first time in years, energy and resources are being poured into browsers, the ubiquitous programs for accessing content on the Web. Credit for this trend – a boon to consumers – goes to two parties. The first is Google, whose big plans for the Chrome browser have shaken Microsoft out of its competitive torpor and forced the software giant to pay fresh attention to its own browser, Internet Explorer. Microsoft all but ceased efforts to enhance IE after it triumphed in the last browser war, sending Netscape to its doom. Now it's back in gear." Mozilla said that Chrome's introduction into the web browser market comes as "no real surprise", that "Chrome is not aimed at competing with Firefox", and furthermore that it would not affect Google's revenue relationship with Mozilla.
Chrome's design bridges the gap between desktop and so-called "cloud computing". At the touch of a button, Chrome lets you make a desktop, Start menu, or QuickLaunch shortcut to any Web page or Web application, blurring the line between what's online and what's inside your PC. For example, I created a desktop shortcut for Google Maps. When you create a shortcut for a Web application, Chrome strips away all of the toolbars and tabs from the window, leaving you with something that feels much more like a desktop application than like a Web application or page. With its dominance in the web browser market, Google has been accused of using Chrome and Blink development to push new web standards that are proposed in-house by Google and subsequently implemented by its services first and foremost. These have led to performance disadvantages and compatibility issues with competing browsers, and in some cases, developers intentionally refusing to test their websites on any other browser than Chrome. Tom Warren of The Verge went as far as comparing Chrome to Internet Explorer 6, the default browser of Windows XP that was often targeted by competitors due to its similar ubiquity in the early 2000s. In 2021, computer scientist and lawyer Jonathan Mayer stated that Chrome has increasingly become an agent for Google LLC than a user agent, as it is "the only major web browser that lacks meaningful privacy protections by default, shoves users toward linking activity with a Google Account, and implements invasive new advertising capabilities." In January 2021, Google stated it was making progress on developing privacy-friendly alternatives that would replace third-party cookies currently being used by advertisers and companies to track browsing habits. Google then promised to phase out the use of cookies in its web browser in 2022, implementing its FLoC technology instead. The announcement triggered antitrust concerns from multiple countries for abusing the Chrome browser's market monopoly, with the U.K.'s Competition and Markets Authority and the European Commission both opening formal probes. The FLoC proposal also drew criticism from DuckDuckGo, Brave, and the Electronic Frontier Foundation for underestimating the ability of the API to track users online. On January 25, 2022, Google announced it had killed off development of its FLoC technologies and proposed the new Topics API to replace it. Topics is similarly intended to replace cookies, using one's weekly web activity to determine a set of five interests. Topics are supposed to refresh every three weeks, changing the type of ads served to the user and not retaining the gathered data.
Chrome overtook Firefox in November 2011 in worldwide usage. As of January 2026, according to StatCounter, Google Chrome had 71% worldwide global usage share, and, according to Cloudflare, it was 68%, making it the most widely used web browser. It was reported by StatCounter, a web analytics company, that for the single day of Sunday, March 18, 2012, Chrome was the most used web browser in the world for the first time. Chrome secured 32.7% of the global web browsing on that day, while Internet Explorer followed closely behind with 32.5%. From May 14–21, 2012, Google Chrome was for the first time responsible for more Internet traffic than Microsoft's Internet Explorer, which had long held its spot as the most used web browser in the world. According to StatCounter, 31.88% of web traffic was generated by Chrome for a sustained period of one week and 31.47% by Internet Explorer. Though Chrome had topped Internet Explorer for a single day's usage in the past, this was the first time it had led for one full week. At the 2012 Google I/O developers' conference, Google claimed that there were 310 million active users of Chrome, almost double the number in 2011, which was stated as 160 million active users. In June 2013, according to StatCounter, Chrome overtook Internet Explorer for the first time in the US. In August 2013, Chrome was used by 43% of internet users worldwide. This study was done by Statista, which also noted that in North America, 36% of people use Chrome, the lowest in the world.
2. System Architecture & Core Working Principles In September 2008, Google released a large portion of Chrome's source code as an open-source project called Chromium. This move enabled third-party developers to study the underlying source code and to help port the browser to the macOS and Linux operating systems. The Google-authored portion of Chromium is released under the permissive BSD license. Other portions of the source code are subject to a variety of open-source licenses. Chromium is similar to Chrome, but lacks built-in automatic updates and a built-in Flash player, as well as Google branding and has a blue-colored logo instead of the multicolored Google logo. Chromium does not implement user RLZ tracking. Initially, the Google Chrome PDF viewer, PDFium, was excluded from Chromium, but was later made open-source in May 2014. PDFium can be used to fill PDF forms.
Browser wars – Competition between web browsing applications for share of worldwide usage Google Chrome Experiments – Online showroom of web browser based experiments Google Chrome Frame – Plug-in designed for Internet Explorer based on the open-source Chromium project Google Workspace – Productivity and collaboration software History of web browsers List of Google products List of Google Easter eggs List of web browsers Widevine – Digital rights management technology Official website Google I/O 2009 - Exploring Chrome Internals on YouTube, presented by Darin Fisher, a member of the Chrome team Google I/O 2010 - Chrome at Google I/O 2010 (recap / Chrome team sessions & demos from that year). Google I/O 2011 -Chrome-focused day / keynote segments and Chrome sessions are in the 2011 video uploads Google I/O 2012 - Official I/O sessions listings (includes web/Chrome sessions). Google I/O 2013 - Sessions page and Chrome team deep dives Google I/O 2014 - I/O 2014 host page + specific Chrome/web talks Google I/O 2015 - I/O 2015 site and videos include Polymer / modern web API sessions Google I/O 2016 - Web and Chrome at Google I/O 2016 — dedicated playlist and many Chrome/web sessions Google I/O 2017 - I/O 2017 all-sessions playlist + many Chrome/web technical talks. Google I/O 2018 - Chrome & Web at Google I/O 2018 playlist (DevTools, performance, web platform features). Google I/O 2022 — All Google I/O 2022 Sessions and playlists include Web/Chrome updates - see the I/O 2022 sessions playlist and the "Web" track.
Google I/O 2023 — ChromeOS and Web playlists (dedicated ChromeOS playlist and Web sessions for I/O 2023). Google I/O 2024 — All sessions (I/O 2024) and a "Web at I/O 2024" playlist highlighting Chrome and web platform updates. Google I/O 2025 — I/O 2025 explore page and the All Sessions (2025) playlist — includes the Web track and Chrome/ChromeOS sessions (privacy, performance, DevTools, AI features in the browser).
In cryptography and computer security, a man-in-the-middle (MITM) attack, or on-path attack, is a cyberattack where the attacker secretly relays and possibly alters the communications between two parties who believe that they are directly communicating with each other, where in actuality the attacker has inserted themselves between the two user parties. One example of a MITM attack is active eavesdropping, in which the attacker makes independent connections with the victims and relays messages between them to make them believe they are talking directly to each other over a private connection, when in fact the entire conversation is controlled by the attacker. In this scenario, the attacker must be able to intercept all relevant messages passing between the two victims and inject new ones. This is straightforward in many circumstances; for example, an attacker within range of a Wi-Fi access point hosting a network without encryption could insert themselves as a man in the middle. As it aims to circumvent mutual authentication, a MITM attack can succeed only when the attacker impersonates each endpoint sufficiently well to satisfy their expectations. Most cryptographic protocols include some form of endpoint authentication specifically to prevent MITM attacks. For example, TLS can authenticate one or both parties using a mutually trusted certificate authority.
Suppose Alice wishes to communicate with Bob. Meanwhile, Mallory wishes to intercept the conversation to eavesdrop (breaking confidentiality) with the option to deliver a false message to Bob under the guise of Alice (breaking non-repudiation). Mallory would perform a man-in-the-middle attack as described in the following sequence of events. Alice sends a message to Bob, which is intercepted by Mallory: Alice "Hi Bob, it's Alice. Give me your key." → Mallory Bob Mallory relays this message to Bob; Bob cannot tell it is not really from Alice: Alice Mallory "Hi Bob, it's Alice. Give me your key." → Bob Bob responds with his encryption key: Alice Mallory ← [Bob's key] Bob Mallory replaces Bob's key with her own, and relays this to Alice, claiming that it is Bob's key: Alice ← [Mallory's key] Mallory Bob Alice encrypts a message with what she believes to be Bob's key, thinking that only Bob can read it: Alice "Meet me at the bus stop!" [encrypted with Mallory's key] → Mallory Bob However, because it was actually encrypted with Mallory's key, Mallory can decrypt it, read it, modify it (if desired), re-encrypt with Bob's key, and forward it to Bob: Alice Mallory "Meet me at the park!" [encrypted with Bob's key] → Bob Bob thinks that this message is a secure communication from Alice. This example shows the need for Alice and Bob to have a means to ensure that they are truly each using each other's public keys, and not the public key of an attacker.
Otherwise, such attacks are generally possible, in principle, against any message sent using public-key technology. HTTPS spoofing: The attacker tricks the victim into believing their connection is secure by substituting a fake SSL/TLS certificate. SSL/TLS stripping: Downgrades HTTPS traffic to HTTP, intercepting and reading unencrypted data. ARP spoofing: Sends fake ARP messages to associate the attacker's MAC address with a target IP, intercepting local network traffic. DNS spoofing or poisoning: Redirects DNS queries to malicious servers, leading victims to fake websites. Session hijacking: Steals session cookies or tokens to impersonate a legitimate user in an active session. Man-in-the-browser (MITB): Malware alters browser activity, intercepting or manipulating transactions in real-time. Wi-Fi MITM (evil twin attack): Creates a fake Wi-Fi hotspot to intercept communications from connected devices. Email hijacking: Intercepts email exchanges to manipulate or steal sensitive information. Replay attacks: Captures and retransmits valid data to repeat actions or disrupt communication.
Fake certificate authority (CA): Uses a fraudulent CA to sign fake certificates, tricking victims into trusting malicious connections. IP address of the server DNS name of the server X.509 certificate of the server Whether the certificate has been self signed Whether the certificate has been signed by a trusted certificate authority Whether the certificate has been revoked Whether the certificate has been changed recently Whether other clients, elsewhere on the Internet, received the same certificate DSniff – the first public implementation of MITM attacks against SSL and SSHv1 Fiddler2 HTTP(S) diagnostic tool NSA impersonation of Google Superfish malware Forcepoint Content Gateway – used to perform inspection of SSL traffic at the proxy Comcast uses MITM attacks to inject JavaScript code to 3rd party web pages, showing their own ads and messages on top of the pages 2015 Kazakhstan man-in-the-middle attack Secure coding in client-side JavaScript is essential because every line of frontend code runs in a user-controlled environment.
That means attackers can probe, manipulate, and exploit weak points directly in the browser. The most common and damaging risk is cross-site scripting (XSS), but it’s far from the only one. Protecting apps requires disciplined practices like strict input validation, enforcing content security policies, and leveraging built-in framework defenses. These techniques turn common attack vectors into dead ends for attackers.
Keep reading to learn how secure JavaScript coding prevents XSS and helps protect your application from real-world threats. We still remember the first time we opened a browser console and saw our JavaScript printed out like an open diary. That moment made it real: our code lives right there in plain sight. And that means anything we miss—any little crack—can be a way in. So, when we write JavaScript on the frontend, we aren’t just coding; we’re building a line of defense.
We treat every line of code like it might be used against us. Because sometimes it is. We steer clear of functions like eval() and new Function(). They open the door for attackers to run code they shouldn’t. If we ever think we need them, it’s worth asking twice (and probably thrice) if there’s another way. Usually, there is. These safer alternatives give us control and remove ambiguity—something attackers thrive on.
When we leave variables lying around globally, it’s like leaving our front door wide open. We can’t always see who or what will walk through. That’s why we scope everything tightly. Modules help. So do Immediately Invoked Function Expressions (IIFEs). It’s not optional. Serving scripts over HTTP is a gamble we won’t take. Without HTTPS, someone could change the script between server and browser (man-in-the-middle). Then it’s game over.
We use third-party tools, but we don’t trust them blindly. Every library brings risk, so we: Sometimes it feels tedious, but a stale package is a weak link. And attackers look for those. We try not to show our hand. Error messages, if they’re too detailed, can teach attackers how our app works. We log full errors on the server, but on the client, we keep it vague. Something went wrong. Please try again. ( 1 ) XSS is a sneaky kind of beast. It shows up in places we forget to watch—search bars, comments, form fields. We’ve learned that validating input is only half the battle. Sanitizing it is just as important.
First, we check if the input makes sense. Is it an email? A number? We validate it. But that’s not enough. We also clean it—sanitize it—so that even if someone slips in a script tag, it won’t execute. Sometimes, we want to take user input and show it on the page. Seems harmless, right? But if we use innerHTML, we’ve basically given permission to run whatever’s inside.
We keep scripts out of our HTML. Inline onClick handlers might be convenient, but they’re a goldmine for attackers. DOM manipulation is powerful. But unchecked, it’s also dangerous. We touch the DOM carefully, like we’re defusing something sensitive. ( 2 ) 3. Software Implementation, Frameworks & Protocols When we build DOM elements, we start with document.createElement() and assign text using textContent. These don’t parse HTML, so scripts inside them don’t run.
If we absolutely must allow HTML from users (say, in a rich text editor), we sanitize it. That means stripping scripts, removing dangerous attributes, and validating tags. APIs like insertAdjacentHTML or outerHTML can be trouble when used with user data. We try not to use them. If we have to, we make sure the input is squeaky clean.
Validation helps users fix mistakes quickly. But we never trust it alone. It’s more about experience than security. Regex is our friend, but it’s a blunt one. We write tight patterns that only allow what we expect. We always do both. Validation without sanitization is like checking someone’s ID but not their bag. We know, the name says it all. It’s dangerous. If we must use it, we scrub the content first with a sanitizer.
Props carry data, sometimes from users or external APIs. We validate them, sanitize them, and document what they should be. Things go wrong. React lets us catch errors with boundaries so one crash doesn’t take the whole app with it. Angular tries to help by sanitizing automatically. But we can undo that help without meaning to.
We never use bypassSecurityTrustHtml unless we absolutely have to. And when we do, we audit it twice. We update often. Not because we like updates, but because each one might fix a hole we don’t even know exists. They’re handy. But they’re not safe. We don’t store sensitive info in localStorage or sessionStorage. We don’t keep passwords, tokens, or PII in these storages. They’re too easy to access.
We put tokens in headers. Never in URLs. URLs get cached, logged, and sometimes shared. Error responses don’t need to say too much. 401 Unauthorized. 403 Forbidden. That’s enough. We obscure our code to slow attackers down. Minification helps, too. It’s not bulletproof, but it’s friction. This watches our app while it runs. If something weird happens, it steps in. Like a bodyguard for code.
We take pride in secure code. Because behind every app, there are people. And we owe them safety. We drill this into every developer who comes through our program: secure JavaScript isn’t about fancy tools — it’s about solid habits. Our graduates learn to spot vulnerabilities before writing a single line of code. Through our hands-on labs, they practice defending against real-world attacks we’ve seen in the field.
When students leave our bootcamp, they carry these security reflexes into their development teams. That’s how we’re building a safer web, one developer at a time. Ready to level up your frontend security skills? I Join the Secure Coding Practices Bootcamp — a 2-day, hands-on training designed by experts to help developers write safer code from the start.
Client-side security monitoring is the process of observing and analyzing what scripts do within the user's browser when they visit your website. This includes how JavaScript executes, what data it accesses, and whether it interacts with external systems. Modern websites rely heavily on third-party scripts for marketing, analytics, personalization, and UX features. These scripts operate outside of direct server control and can be changed or compromised without notice. That creates a blind spot for security and compliance — especially if sensitive user data is processed on the page.
This concern is not limited to technical teams. Digital marketers, e-commerce operators, and compliance leads all share responsibility for third-party tools and browser-based behavior. The Payment Card Industry Data Security Standard (PCI DSS) v4.0 , in particular, mandates the monitoring of all scripts that load on payment pages (Requirement 6.4.3). General privacy frameworks like GDPR and CCPA also require controls around personal data handling — including what scripts are collecting and transmitting.
Client-side monitoring helps detect unauthorized script changes, flag risky behavior, and document compliance efforts. Tools like Spider AF SiteScan are purpose-built for this, offering visibility into script activity and providing reporting that supports data protection goals. 4. Practical Deployment, Analysis & Case Studies This guide will explain what client-side monitoring involves, why it matters, how it compares to other forms of observability, and how to evaluate tools for your own website.
You can start with a free website security check from Spider AF SiteScan to see which scripts are currently active on your site and whether any risks are present. Client-side monitoring refers to the observation of script behavior in the user’s browser. This includes third-party and first-party scripts, network requests, and how the page DOM is modified during a session.
Many attacks, such as formjacking and data exfiltration, occur entirely in the browser and may not appear in server logs. Real User Monitoring measures performance (e.g. page speed, load time). Client-side security monitoring measures behavior and risk (e.g. what scripts are doing, where they send data). They serve different goals but can complement each other. Malicious code is injected into a page to run in the user’s browser. In DOM-based XSS , the payload is inserted entirely client-side. These attacks can capture session data or alter the page experience.
Malicious scripts intercept form inputs, especially on checkout pages. These are often delivered via compromised third-party libraries. A well-known example is Magecart, which has affected large retailers by stealing credit card data from unsuspecting users. Scripts hosted by vendors or CDNs may change without the site owner's knowledge. This “drift” can introduce functionality that wasn't originally approved — including tracking, redirect behavior, or insecure data handling.
Some scripts may unintentionally expose form data, session information, or proprietary frontend logic. If not monitored, these interactions can violate data privacy obligations. Monitoring helps mitigate risk and support compliance in a script-heavy web environment. I Third-party scripts often load from external servers and can be updated without your involvement. If a provider is compromised, your site may unknowingly serve malicious content. Monitoring tools identify new or changed scripts that may pose risk.
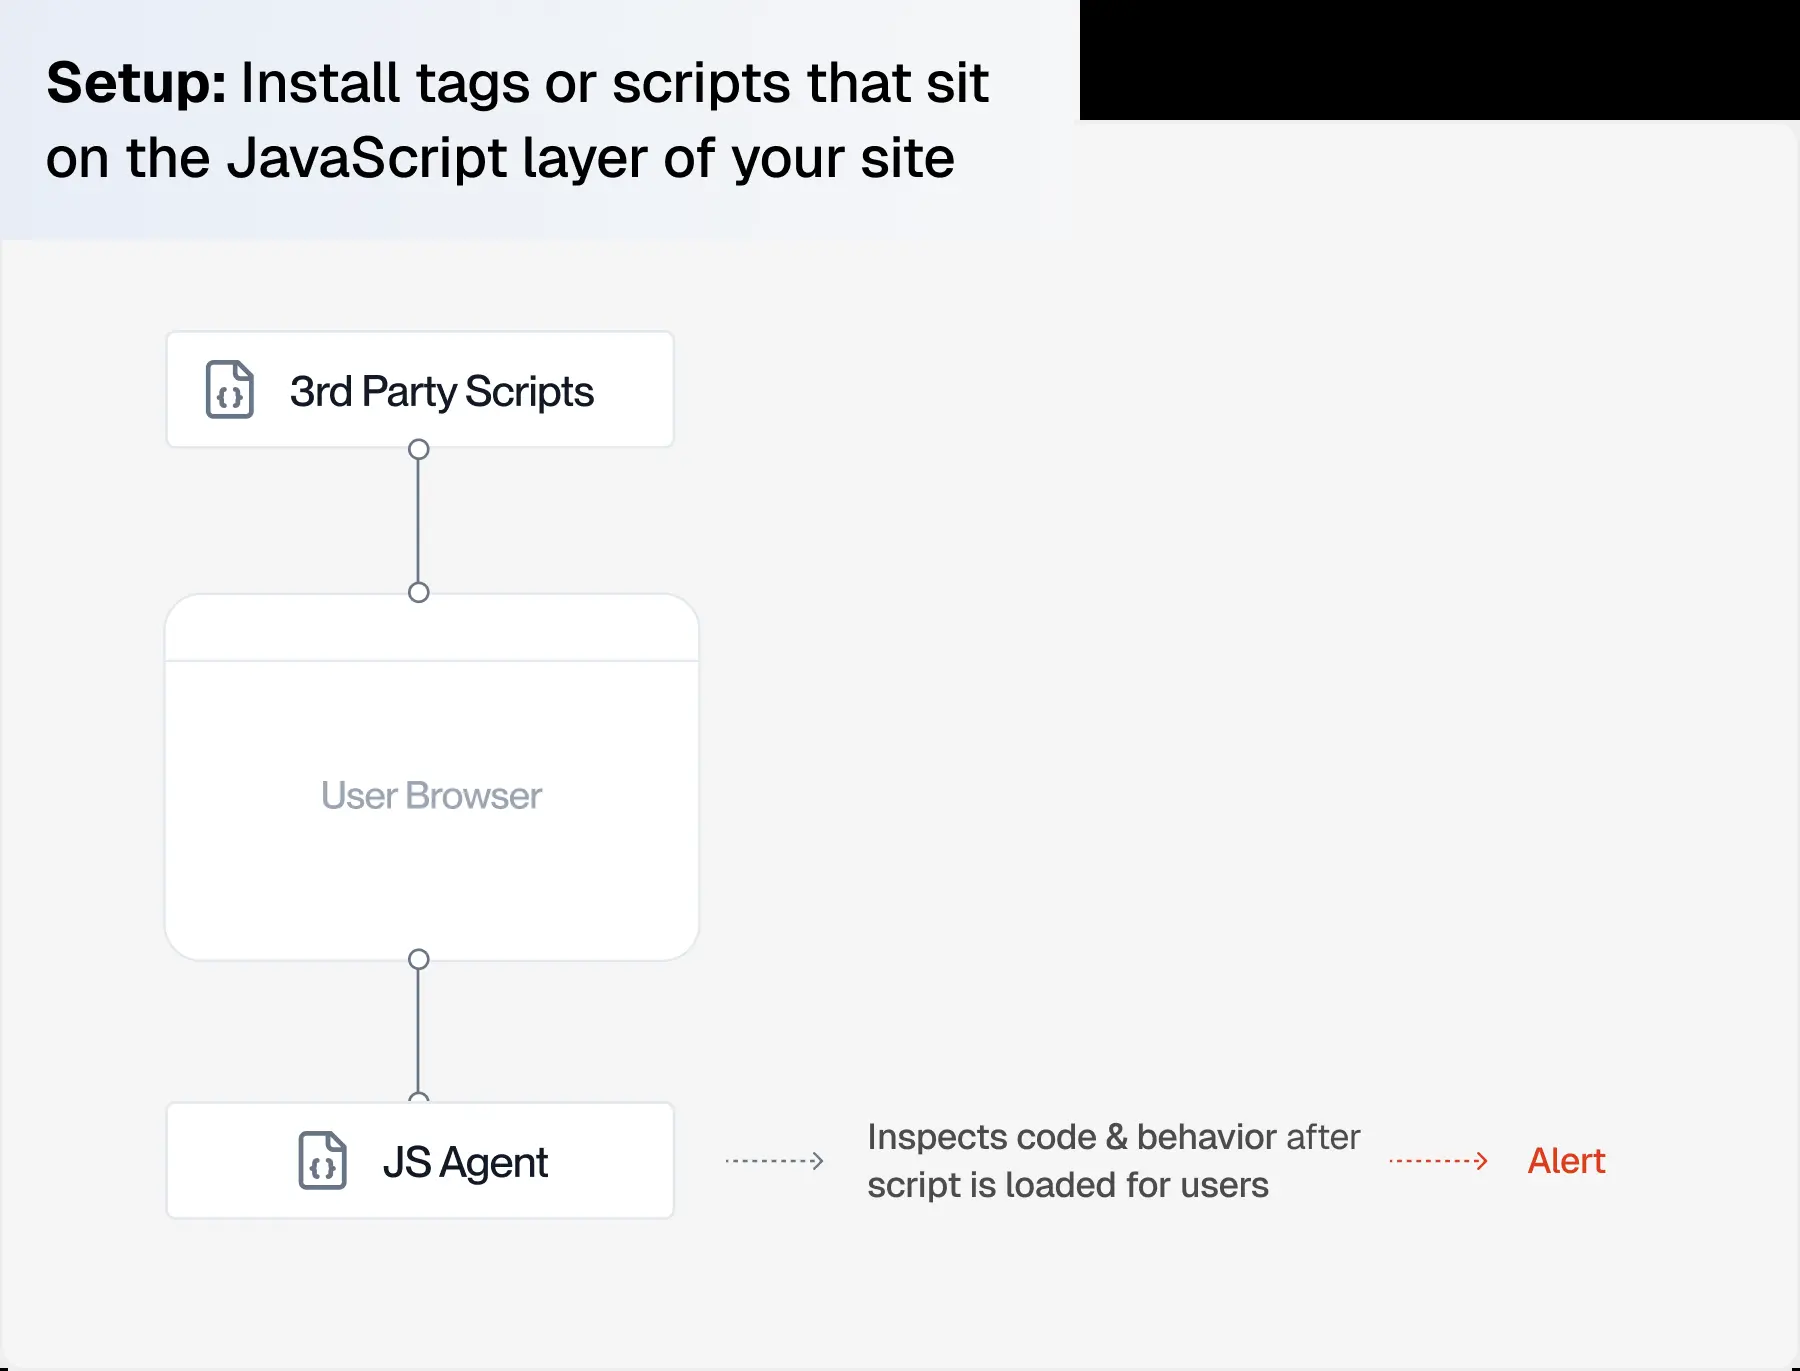
Client-side threats often execute immediately when a user visits the page. Security tools that monitor scripts in real time can detect: Monitoring helps provide documentation and real-time insight to meet these expectations. Spider AF SiteScan includes a script behavior overview, helping organizations quickly identify changes or potential anomalies.
Content Security Policy (CSP) restricts script sources. Subresource Integrity (SRI) validates content. These reduce the risk of script manipulation. Keep an approval process in place for new vendors and regularly audit changes to existing tools. Use insights from actual user sessions to adjust detection thresholds and reduce false positives.
A mid-sized retailer observed abnormal checkout behavior. Client-side monitoring revealed that a third-party analytics script had been modified upstream to capture form inputs. Quick remediation prevented further exposure. A payment services company used script inventory tracking and change monitoring to meet PCI DSS v4.0 script requirements. Having clear audit trails and reports simplified the assessment process.
Recent research (see arXiv and industry whitepapers) shows that compact AI models can run in the browser to analyze: These models can help analyze behavior without exporting raw data , preserving user privacy and reducing latency. They are not widely deployed yet but show potential for augmenting existing tools. Q: What is client-side security monitoring? A: It's the practice of tracking and analyzing scripts running in the browser to detect anomalies or malicious activity.
Q: Does client-side monitoring help with PCI DSS v4.0? A: Yes. It supports Requirement 6.4.3, which mandates monitoring of payment page scripts. Q: Can I monitor scripts without affecting performance? A: Most tools, including SiteScan, are designed to load asynchronously and minimize impact.
Q: How can I get started? A: You can run a free website security check with Spider AF SiteScan . Client-side monitoring helps protect against real-world browser threats and improves compliance with modern security and privacy standards. For digital businesses, gaining visibility into script behavior is now as important as protecting backend infrastructure.
5. Performance Evaluation & Extended Technical Observations Spider AF SiteScan provides visibility into third-party scripts, behavior tracking, and reporting features that help organizations detect issues early and stay audit-ready. I Start now with a free website security check to evaluate your site’s browser-side risks.
Spider AF detects and blocks invalid traffic in real time — before it wastes your spend. MFA growth, AI-driven fraud risks, and how top advertisers are protecting their budgets. Free PDF! Spider AF blocks click farms, bot traffic, and invalid clicks in real time — so every yen of your ad budget works harder. JavaScript security is the practice of protecting JavaScript and TypeScript applications, in the browser and on the server, against vulnerabilities such as cross-site scripting, injection, prototype pollution, and compromised npm packages through secure coding, hardened configuration, and automated code scanning.
JavaScript runs in more places than any other language: browsers, Node.js, Deno, Bun, edge runtimes, Electron apps, mobile wrappers, and serverless functions. That reach is exactly why it is such a productive target. The same language that renders your UI also handles authentication, database queries, and file access on the server, and it pulls in hundreds of transitive npm packages along the way.
This guide is the JavaScript companion to our Python security best practices and Rust security best practices guides. It covers the JavaScript threat model, the vulnerabilities that show up most often in real JS and TS codebases (each with a vulnerable snippet and a fixed one), a best-practices checklist, framework-specific notes, and a comparison of JavaScript security scanners, including how Corgea AI SAST scans frontend and backend JavaScript differently.
Before you can secure JavaScript you need to know which JavaScript you are securing. The same file extension can describe three very different security contexts. Server-side code handles secrets, sessions, databases, and the file system. The threat model looks like any other backend language: SQL and NoSQL injection, command injection, path traversal, SSRF, insecure deserialization, broken authentication and authorization, and business logic flaws. Node.js adds a few language-specific twists, such as prototype pollution, ReDoS in a single-threaded event loop, and the size of the npm dependency graph. Our Node.js security best practices guide goes deeper on Express and API hardening.
Next.js, Nuxt, SvelteKit, Remix, and Astro blur the line. A single repository contains React components that render in the browser, server components and route handlers that run on the server, middleware at the edge, and server actions callable over HTTP. A .ts file that looks like a UI helper may execute with database credentials. Frameworks also introduce their own footguns: environment variables accidentally exposed to the client ( NEXT_PUBLIC_ ), server actions that skip authorization checks, and dangerouslySetInnerHTML in components that receive user content.
This is also why JavaScript static analysis is harder than it looks. A scanner that treats every file the same either floods you with browser findings in server code (and vice versa) or misses context-specific bugs. Corgea’s JavaScript scanning whitepaper describes how it classifies each file as frontend or backend using framework signatures, import statements, and code patterns before choosing the right ruleset.
The following vulnerabilities account for most of the exploitable findings we see in JavaScript and TypeScript codebases. Each includes a vulnerable example and a fixed one. The fixes are deliberately small; the goal is to show the pattern, not a full library. XSS is the signature JavaScript vulnerability. It happens whenever untrusted data is interpreted as code by the browser.
There are three variants: Other sinks to watch: outerHTML , insertAdjacentHTML , document.write , element.setAttribute("href", ...) with javascript: URLs, jQuery’s .html() and $() with untrusted strings, and template engines with escaping disabled ( <%- %> in EJS, {{{ }}} in Handlebars, the | safe filter in Nunjucks).
Prototype pollution is unique to JavaScript. Because almost every object inherits from Object.prototype , an attacker who can write to it (usually through a recursive merge, deep clone, or “set by path” helper that accepts keys like __proto__ or constructor.prototype ) can inject properties that appear on every object in the process. The consequences range from authorization bypass ( isAdmin suddenly defaulting to true ) to denial of service to remote code execution through gadget chains.
Prefer a maintained library ( lodash.merge in a patched version, or a structured schema parser) over hand-written merge helpers, and use Map or Object.create(null) for dictionaries keyed by user input. Injection is a family of bugs with one root cause: untrusted data concatenated into something that will be interpreted. Read our SQL injection guide for ORM-specific pitfalls such as raw query helpers in Prisma, Sequelize, and Knex.
new Function , setTimeout("string") , vm.runInNewContext (which is not a security sandbox), and template engines such as lodash _.template fed with user input are all eval in disguise. Corgea’s benchmark against Aikido includes a lodash template code injection that the competing scanner missed. JSON.parse is safe on its own: it produces plain data and never executes code. The problem is what happens next. Libraries that deserialize into live objects ( node-serialize , serialize-javascript misuse, js-yaml with unsafe schemas in older versions, funcster ) or code that revives functions from strings will execute attacker-controlled payloads.
Sign or encrypt anything you store client-side and deserialize on the server, and treat YAML, XML, and binary formats with the same suspicion. SSRF occurs when your server fetches a URL supplied by the user. In cloud environments the classic target is the instance metadata service ( 169.254.169.254 ), which can hand an attacker your IAM credentials.
Allowlist hosts, block private and link-local ranges after DNS resolution, disable automatic redirects, and put outbound fetches behind an egress proxy where possible. Note that express.static and res.sendFile with the root option already normalize paths; the bug appears when you build paths yourself.
Node.js is single-threaded. A regular expression with catastrophic backtracking, applied to attacker-controlled input, can pin the event loop and take down the whole process. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Web-based%20SSH • https://en.wikipedia.org/wiki/Google%20Chrome • https://en.wikipedia.org/wiki/Man-in-the-middle%20attack • https://securecodingpractices.com/secure-coding-in-javascript-client-side/ • https://spideraf.com/articles/client-side-security-monitoring-detect-script-threats • https://corgea.com/learn/javascript-security-best-practices
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Client Side Security Auditing Tool Using Javascript.
[*] Metasploit Scan Running on Target Subnet for Client Side Security Auditing Tool Using Javascript... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |