Complete Technical Paper Content — Cloud Access Security Broker Simulation Using Python
Overview & System Context
Cloud Access Security Broker Simulation Using Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9511 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Cloud management refers to the administration and oversight of cloud computing products and services. Public clouds are managed by cloud service providers, which operate the underlying infrastructure such as servers, storage, networking, and data center facilities. Users may also opt to manage their public cloud services with a third-party cloud management tool.
Users of public cloud services can generally select from three basic cloud provisioning categories: User self-provisioning: Customers purchase cloud services directly from the provider, typically through a web form or console interface. The customer pays on a per-transaction basis. Advanced provisioning: Customers contract in advance a predetermined amount of resources, which are prepared in advance of service. The customer pays a flat fee or a monthly fee.
Dynamic provisioning: The provider allocates resources when the customer needs them, then decommissions them when they are no longer needed. The customer is charged on a pay-per-use basis. Managing a private cloud requires software tools to help create a virtualized pool of compute resources, provide a self-service portal for end users and handle security, resource allocation, tracking and billing. Management tools for private clouds tend to be service driven, as opposed to resource driven, because cloud environments are typically highly virtualized and organized in terms of portable workloads. In hybrid cloud environments, compute, network and storage resources must be managed across multiple domains, so a good management strategy should start by defining what needs to be managed, and where and how to do it. Policies to help govern these domains should include configuration and installation of images, access control, and budgeting and reporting. Access control often includes the use of Single sign-on (SSO), in which a user logs in once and gains access to all systems without being prompted to log in again at each of them.
Provisioning and orchestration: create, modify, and delete resources as well as orchestrate workflows and management of workloads Automation: Enable cloud consumption and deployment of app services via infrastructure-as-code and other DevOps concepts Security and compliance: manage role-based access of cloud services and enforce security configurations Service request: collect and fulfill requests from users to access and deploy cloud resources. Monitoring and logging: collect performance and availability metrics as well as automate incident management and log aggregation Inventory and classification: discover and maintain pre-existing brownfield cloud resources plus monitor and manage changes Cost management and optimization: track and rightsize cloud spend and align capacity and performance to actual demand Migration, backup, and DR: enable data protection, disaster recovery, and data mobility via snapshots and/or data replication Organizations may group these criteria into key use cases including Cloud Brokerage, DevOps Automation, Governance, and Day-2 Life Cycle Operations. Enterprises with large-scale cloud implementations may require more robust cloud management tools which include specific characteristics, such as the ability to manage multiple platforms from a single point of reference, or intelligent analytics to automate processes like application lifecycle management. High-end cloud management tools should also have the ability to handle system failures automatically with capabilities such as self-monitoring, an explicit notification mechanism, and include failover and self-healing capabilities.
On-premises private cloud - Where the cloud environment exists within the customer organization. Platforms such as VMWare and OpenStack as well as integrated systems such as those from Nutanix, HPE, and others should be integrated to manage private cloud resources. Capabilities should also include integration with container orchestrators such as Kubernetes. CSP hosted private cloud – Sometimes called dedicated or managed cloud. Private hosted cloud resources are managed via APIs made available by the private cloud provider, in much the same way as public cloud resources and often include additional staffing to fully manage day to day operations. Public cloud service – The CMP must integrate with required public cloud services such as Amazon Web Services (AWS), Microsoft Azure, Google Cloud Platform (GCP), IBM Cloud, Oracle, etc to enable management of resources residing in public cloud services. Integration can be achieved by use of the public APIs of the target cloud service, or by an agent running within the public cloud service environment. IT Service Management – It is typical for CMPs to rely on existing enterprise management systems to provide capabilities such as incident management, configuration management, asset management, and financial management. Service Automation – Organizations may consider CMP integration with existing automation tools to simplify resource management. Integration with configuration management tools such as Chef and Puppet, and deployment tools such as Terraform are key considerations.
Figure 1: 11 Best Cloud Access Security Broker Software (CASB) - 2026 Numerix is an American capital markets analytics and risk management technology company headquartered in New York City. It develops pricing, risk management, and portfolio analytics software for financial derivatives, structured products, fixed income securities, and convertible securities, serving sell-side institutions including banks and broker-dealers, and buy-side participants including asset managers, insurance companies, and hedge funds. The company's platform ecosystem spans derivatives pricing and XVA analytics through Numerix Oneview and CrossAsset, fixed income and asset-liability management through PolyPaths, convertible securities analytics through Kynex, and cross-asset quantitative analytics libraries through the FINCAD Analytics Suite and NxCore. Its software supports regulatory capital calculations including SA-CCR, FRTB, and ISDA SIMM (initial margin), as well as counterparty credit risk, real-time market risk, and structured product valuation across rates, FX, equity, credit, commodities, inflation, and hybrid instruments. Numerix was ranked #14 in the Chartis RiskTech100® 2026, an annual independent ranking of the world's leading risk and compliance technology providers, and received category awards for Front Office Risk Management and XVA for two consecutive years.
Chartis Quantitative Analytics50 2026: Ranked #1 overall; Category Awards for OTC Derivatives, Equity Derivatives, XVA, CVA, MVA, and OTC Derivatives Pricing Chartis RiskTech100® 2026: Ranked #14 overall; Category Awards for Front Office Risk Management, XVA, OTC Derivatives, and Equity Derivatives Chartis BuySideRisk50 2025: Ranked #5 overall; Category Awards for Cross-Context Analytics, Structured Note Analytics, and RMBS Analytics Risk Awards 2025: Technology Vendor of the Year; Counterparty Risk Product of the Year (Numerix Oneview for XVA) GlobalCapital Derivatives Awards 2025: Pricing and Valuation Provider of the Year; Risk Management Provider of the Year GlobalCapital Americas Derivatives Awards 2024: Global Pricing and Valuation Provider of the Year WatersTechnology Buy-Side Technology Awards 2025: Best Buy-Side Risk Management Product WatersTechnology Sell-Side Technology Awards 2023: Best Sell-Side Market Risk Product WatersTechnology Waters Rankings 2025: Best Market Risk Solution Provider Risk Markets Technology Awards 2024: Counterparty Risk Product of the Year (Numerix Oneview for XVA) Risk Markets Technology Awards 2023: XVA Calculation Product of the Year Asian Private Banker Technology Awards 2024: Best Risk Solution (fifth consecutive year); Most Innovative Solution (second consecutive year) FTF News Technology Innovation Awards 2025: Best Cloud-Native Computing Platform (NxCore) FTF News Technology Innovation Awards 2024: Best Cutting-Edge Solution (Numerix Oneview) FinTech Breakthrough Awards 2023: Best Risk Management Platform (Numerix Oneview) Risk.net Cloud Solution Provider of the Year 2022 Robot as a service or robotics as a service (RaaS) is a cloud computing unit that facilitates the seamless integration of robots and embedded devices into Web and cloud computing environments. In terms of service-oriented architecture (SOA), a RaaS unit includes services for performing functionality, a service directory for discovery and publishing, and service clients for user's direct access. The current RaaS implementation facilitates SOAP and RESTful communications between RaaS units and the other cloud computing units. Hardware support and standards are available to support RaaS implementation. Devices Profile for Web Services (DPWS) defines implementation constraints to enable secure web service messaging, discovery, description, and eventing on resource-constrained devices between web services and devices. RaaS can be considered a unit of the internet of things (IoT), internet of intelligent things (IoIT) that deal with intelligent devices that have adequate computing capacity, cyber-physical system (CPS) that is a combination of a large computational and communication core and physical elements that can interact with the physical world, and autonomous decentralized system (ADS) whose components are designed to operate in a loosely coupled manner and data are shared through a content-oriented protocol. The more common usage of the term robot as a service (RaaS) is as a financial model for the purchase and use of a physical industrial or service robot. In a RaaS purchase contract, the buyer is paying for the use of the physical device through a subscription-based contract. RaaS is differentiated from a lease contract in that the original manufacturer continues to own the physical robotic device and carries the machine as an asset on its books. RaaS is becoming popular for many robotics equipment providers as the buyer can purchase the equipment through operating expense budgets rather than through a capital expenditure. The service contract for RaaS requires that the original manufacturer update and maintain the robot in good working order throughout the contract life. All parts and labor for preventative maintenance is also included in the RaaS contract. The original manufacturer may swap out the physical robot with another, equivalent machine at any time. In addition, the original manufacturer may provide remote service, via the Web, to remotely monitor, triage and repair, or recover the system. RaaS takes its name from the software as a service (SaaS) business model, popularized in the enterprise software market.
A RaaS cloud unit is a service provider: Each unit hosts a repository of preloaded services. A developer or a client can deploy new services into or remove service from a robot. The services can be used by this robot and can also be shared with other robots. A RaaS cloud contains a set of applications deployed: A developer or client can compose a new application (functionality) based on the services available in the unit and outside the unit. A RaaS unit is a service broker: a client can look up the services and applications available in the unit's directory. A client can search and discover the applications and services deployed on the robot by browsing the directory. The services and applications can be organized in a hierarchy of classes to facilitate the discovery. The main components of a RaaS unit and typical applications and services deployed. RaaS units are designed for the cloud computing environment. The services in RaaS will communicate with the drivers and other operating system components, which further communicate with the devices and other hardware components. The RaaS units can directly communicate with each other through Wi-Fi, if the wireless infrastructure is available or through ad hoc wireless network otherwise. The communication between RaaS and other services in the cloud are through standard service interface WSDL enabled by DPWS or RESTful service overall HTTP. A few prototypes of RaaS have been implemented, which include both Web interface and physical devices. Dependability, including reliability and security are critical in RaaS design.
Collaborating RaaS units can be scheduled for redundant execution, backing up each other's operations. The redundant design can also address the instruction-level attack such as code injection and Return Oriented Programming (ROP) attacks. As the redundant RaaS units are independent of each other, instruction-level gadget programming is likely to generate different sequences in different devices. These differences in behaviors can be detected by the collaboration among the RaaS units. The major challenge in designing RaaS is to deal with the diversity of the networks, applications, and the environments or end users. In cloud computing, the network and communication protocols are limited to a few standards such WSDL, SOAP, HTTP, and RESTful architecture. In RaaS, HTTP, SOAP, and WSDL standards and robotics applications are the main design considerations.
Figure 2: Top 5 use cases to help you make the most of your Cloud Access Security ... Organizations now run core operations on dozens of SaaS applications, IaaS platforms, and PaaS services simultaneously. Every new cloud service introduces another entry point for data to leave corporate control and another authentication surface for attackers to probe. Traditional network perimeter security cannot see traffic that never touches the corporate network, let alone enforce policy on it. A cloud access security broker (CASB) fills that gap by acting as a policy enforcement point between users and cloud providers. This guide explains what a CASB is, how its architecture works, the deployment models available, and where it fits in a modern cloud security stack.
A cloud access security broker (CASB) is a software tool or cloud-delivered service that sits between an organization’s users and its cloud service providers to enforce security policies. Gartner coined the term in 2012 as organizations began adopting SaaS applications faster than security teams could audit them. The original CASB category addressed a growing disconnect: corporate data was flowing to cloud services that existing security tools could not inspect or control.
The core problem a CASB solves is lack of visibility. When employees sign up for a file-sharing service, a collaboration tool, or an AI assistant without IT approval, that is shadow IT. The security team does not know which data is being uploaded, who has access, or whether the service meets compliance requirements. A CASB discovers every cloud application in use, classifies each one by risk, and enforces policies that govern how data moves between users and those applications.
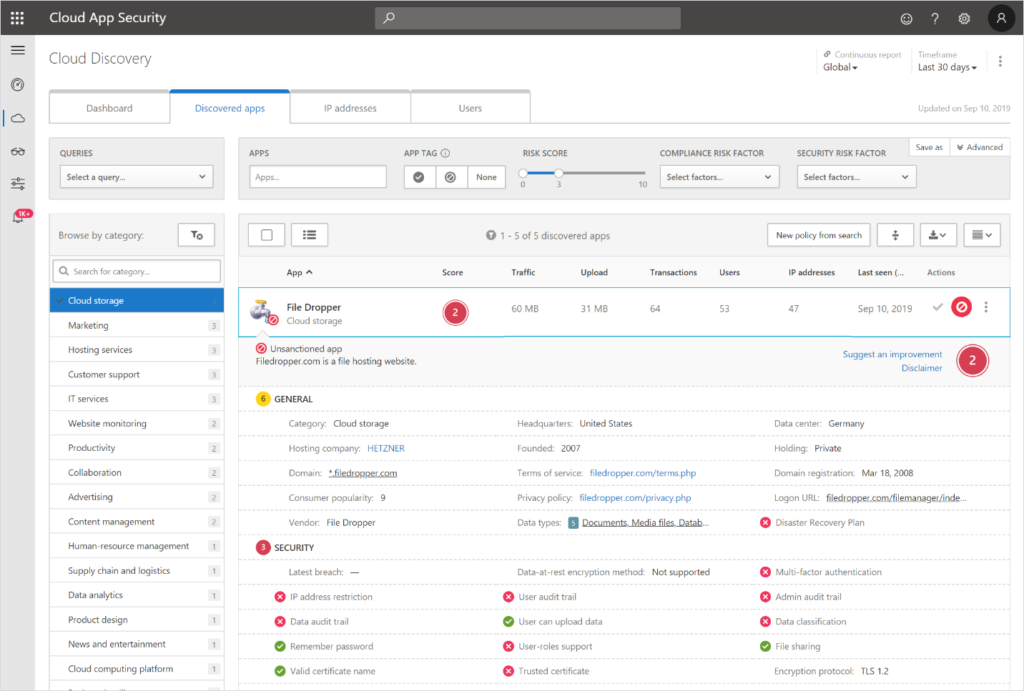
Gartner defined CASB capabilities through four pillars that remain the standard framework for evaluating CASB solutions today. Figure 3: 7 Best Cloud Access Security Brokers (CASB) 2026 (Paid & Free) Visibility. A CASB discovers all cloud services accessed from the corporate network or managed devices. It catalogs sanctioned applications, tolerated services, and unsanctioned shadow IT. This telemetry tells security teams which cloud apps employees use, how much data each one holds, and which users access each service.
Compliance. Regulated industries must demonstrate that data stored in cloud services meets requirements such as HIPAA, GDPR, PCI DSS, or SOC 2. A CASB maps cloud usage against these frameworks, generates compliance reports, and enforces access policies that prevent data handling practices that would violate regulations. Data security. CASBs extend data loss prevention (DLP) controls into cloud environments where traditional DLP tools do not reach. They inspect data in transit and at rest, apply encryption or tokenization, and block uploads or shares that violate policy. This includes preventing sensitive data from being pasted into unsanctioned AI tools or shared externally through cloud storage.
Threat protection. CASBs detect anomalous user behavior, compromised accounts, and malware in cloud-stored files. Behavioral analytics profiles normal activity for each user and flags deviations such as a sudden mass download or a login from an unfamiliar location. When the CASB detects a threat, it can quarantine files, block access, or trigger automated response workflows.
A CASB enforces policy through a three-phase process that runs continuously across the organization’s cloud footprint: discovery, classification, and remediation. In the discovery phase, the CASB identifies every cloud application in use. It monitors network traffic to detect connections to cloud services, integrates with the organization’s firewall or proxy logs, and can use API integrations with major SaaS platforms to enumerate connected third-party apps. The result is a complete inventory of cloud services that includes applications the security team did not know existed.
In the classification phase, the CASB evaluates each discovered application against risk criteria. Factors include the type of data the application handles, its compliance certifications, its security track record, and community trust ratings from threat intelligence feeds. Each application receives a risk score that determines what policies apply. In the remediation phase, the CASB enforces policies based on the risk classification. Actions range from blocking access entirely to applying conditional controls such as read-only access on unmanaged devices, encryption of sensitive files, or alerts when a user shares data externally.
An inline proxy CASB sits directly in the data path between the user and the cloud service. Every request passes through the CASB, which inspects the traffic, applies policy, and either allows, blocks, or modifies the transaction in real time. This architecture provides the strongest enforcement because the CASB can intercept and change traffic before it reaches the cloud provider.
The primary trade-off is latency. Every request must round-trip through the CASB before reaching its destination. Inline proxies also require traffic redirection, which can be complex to configure for all cloud services, especially mobile users operating outside the corporate network. Organizations typically deploy inline proxy CASBs alongside a secure web gateway or as part of a SASE platform that handles traffic steering.
An API-based CASB connects directly to cloud service providers through their published APIs. Rather than intercepting traffic, the CASB queries the cloud service to enumerate users, files, permissions, and activity logs. It enforces policy by calling the cloud service’s own API to apply labels, revoke sharing, quarantine files, or disable compromised accounts. API-based CASBs introduce no latency because they do not sit in the data path. They provide visibility into data already stored in cloud services, including files that were uploaded before the CASB was deployed. The limitation is that API-based enforcement depends on what each cloud provider exposes through its API. Some actions, such as blocking a file upload in real time, are not possible through API-based controls because the transaction has already completed by the time the API call returns.
Most enterprise CASB deployments now use a hybrid multimode approach that combines inline proxy and API-based methods. The inline proxy handles real-time traffic inspection and blocking for web-based cloud access. The API-based integration provides deep visibility into data at rest, retrospective analysis of historical activity, and enforcement actions such as file quarantine and permission revocation. Multimode CASB deployments cover both data in motion through the proxy and data at rest through API connections.
CASB solutions address several distinct security problems in organizations that use cloud services at scale. The most common deployments target shadow IT visibility, SaaS data protection, compliance automation, and threat detection. The average enterprise uses hundreds of cloud services, and security teams typically approve only a fraction of them. CASB auto-discovery surfaces every cloud application in use, regardless of whether IT sanctioned it. Once discovered, the CASB applies a governance model that categorizes each service as sanctioned, tolerated, or blocked.
This capability matters because unsanctioned cloud services store corporate data without any security controls enforced on them. A marketing team using an unapproved file-sharing tool may store customer lists and campaign data in an environment the security team cannot monitor. The CASB discovers that tool, assesses its risk, and applies an appropriate policy such as blocking access from managed devices or alerting the security team.
Enterprise DLP tools that inspect email and web traffic often cannot see data inside SaaS applications. A CASB extends DLP controls into those applications by monitoring what users upload, download, and share. When a user attempts to share a file containing payment card information or protected health information through a cloud storage service, the CASB can block the share, quarantine the file, or encrypt it before it leaves corporate control.
The rise of generative AI tools has made CASB DLP especially relevant. Employees paste proprietary code, customer data, and internal strategy documents into AI chat interfaces. A CASB that integrates with those services can detect sensitive data in prompts and block the transmission before it reaches the AI provider. Organizations subject to regulatory frameworks use CASBs to demonstrate continuous compliance across cloud services.
The CASB scans cloud storage for data types covered by relevant regulations, verifies that access controls meet regulatory standards, and generates audit-ready reports. For healthcare organizations under HIPAA, the CASB can confirm that ePHI stored in cloud services is encrypted and that access logs are complete. For financial services firms under PCI DSS, the CASB can validate that cardholder data in cloud environments is properly segmented and access-controlled.
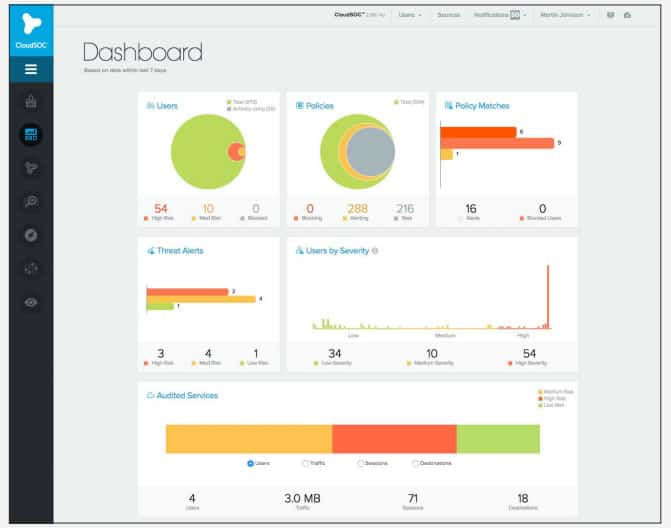
CASBs profile normal user behavior across cloud applications and detect anomalies that signal a compromised account. A user who typically accesses five files per day who suddenly downloads 500 files from a document management system triggers an alert. The CASB can automatically revoke that user’s access, force a password reset, or quarantine downloaded files for forensic analysis.
Choosing the right CASB deployment approach depends on the organization’s cloud architecture, user distribution, and security requirements. Three models dominate the market. Forward proxy deployment routes all user traffic through the CASB before it reaches the internet. This model works best for organizations with centralized network traffic and controlled endpoints. The CASB inspects all outbound requests and enforces policy on every cloud service transaction. The main limitation is that traffic from mobile devices and remote users outside the corporate network must be tunneled back through the proxy, which increases complexity and can degrade performance.
Reverse proxy deployment places the CASB in front of specific sanctioned cloud applications. Users connect to the CASB instead of directly to the cloud service, and the CASB forwards authenticated requests to the provider. This model provides granular control over sanctioned applications but does not discover or control unsanctioned shadow IT. API-based deployment connects the CASB to cloud services through their management APIs. It provides visibility and control without traffic redirection, making it suitable for organizations with distributed workforces and mobile users. API-based CASBs cannot block threats in real time because they operate on data after the transaction completes, but they excel at data classification, compliance scanning, and retrospective threat hunting.
Most organizations at scale choose a multimode approach that deploys an API-based CASB for data-at-rest protection and a proxy-based CASB for inline threat blocking. The proxy component handles user-facing web traffic, and the API component provides deep integration with critical SaaS applications such as Microsoft 365, Google Workspace, and Salesforce. CASB is one component of a complete cloud security program, and organizations often evaluate it alongside or in combination with complementary tools. Understanding the boundaries between these tools prevents both overlap and blind spots.
2. System Architecture & Core Working Principles A secure web gateway (SWG) protects users from web-based threats by filtering internet traffic, blocking malicious URLs, and enforcing acceptable use policies. An SWG operates at the network layer and inspects all web traffic, not just traffic to cloud applications. A CASB operates at the application layer and enforces policies specific to cloud services, such as who can share a file in a SaaS application or whether sensitive data can be uploaded. The two tools are complementary and increasingly converge in SASE platforms.
Cloud security posture management (CSPM) focuses on misconfigurations in IaaS and PaaS environments. A CSPM scans cloud infrastructure for settings that create risk, such as publicly accessible storage buckets, overly permissive IAM roles, or unencrypted databases. A CASB focuses on user behavior and data protection across SaaS applications. An organization running workloads in AWS or Azure needs both: a CSPM to prevent infrastructure misconfigurations and a CASB to monitor how users interact with SaaS services and protect data moving to and from those services.
Zero trust network access (ZTNA) replaces traditional VPNs by granting users access to specific applications based on identity and device posture rather than network location. ZTNA controls access to private applications hosted in data centers or cloud environments. A CASB controls access to SaaS applications and enforces data-level policies. In a SASE framework, ZTNA and CASB work together: ZTNA secures access to internal applications, and CASB secures access to external cloud services.
CASB has evolved from a standalone security tool into a core component of secure access service edge (SASE) and security service edge (SSE) architectures. Gartner identified CASB as one of the foundational elements of SSE, alongside secure web gateway and zero trust network access. In a SASE architecture, the CASB function is delivered as part of a unified cloud platform that bundles networking and security services. The platform handles traffic steering, applies policy based on user identity and device posture, and enforces data protection rules across all cloud services. This convergence eliminates the operational overhead of managing separate proxy configurations, API integrations, and policy consoles for each security tool.
The MarketsandMarkets 2026 SASE market report projects the global SASE market will grow from USD 19.19 billion in 2026 to USD 68.06 billion by 2032 at a CAGR of 28.8 percent, with CASB cited as a key SSE component driving adoption. Organizations transitioning from legacy VPN and web gateway architectures to SASE platforms are effectively adopting CASB capabilities as part of that migration.
Zero trust principles map directly to CASB functions. The zero trust model assumes no user or device is trusted by default, even if connected to the corporate network. A CASB enforces this by verifying user identity, assessing device posture, and applying least-privilege access to cloud resources on every request, regardless of where the request originates. A cloud access security broker provides the visibility, data protection, and threat detection capabilities that organizations need as their operations shift to cloud services. The four pillars of CASB functionality — visibility, compliance, data security, and threat protection — address specific security gaps that traditional tools cannot close. Deployment via inline proxy, API integration, or a hybrid multimode approach gives organizations flexibility to match the CASB architecture to their environment. As CASB capabilities converge with secure web gateways and zero trust network access in SASE platforms, the distinction between standalone CASB tools and integrated cloud security platforms will continue to blur. Organizations that have not yet deployed CASB capabilities should prioritize it as part of their cloud security strategy, starting with shadow IT discovery and progressing toward full data protection and threat detection across all cloud services.
Access to this page requires authorization. You can try signing in or changing directories . In today's digital age, educational institutions face unique challenges in securing cloud access and protecting sensitive data. This article provides an overview of the Cloud Access Security Broker (CASB) solutions available with Microsoft 365 A3 license for education. It highlights the features, benefits, and best practices for implementing Microsoft Defender for Cloud Apps and Office 365 Cloud App Security to ensure a secure and compliant cloud environment for schools and universities.
Microsoft Defender for Cloud App Discovery is a powerful tool tailored to enhance cybersecurity in educational institutions by providing comprehensive visibility into cloud application usage. In the context of education, where various cloud-based tools and applications are often employed to facilitate teaching, learning, and administration, the need for secure and compliant application usage is paramount. Defender for Cloud App Discovery enables educational IT administrators to detect shadow IT by identifying unsanctioned applications being accessed by students, teachers, or staff. It offers actionable insights into user activity, data movement, and potential risks associated with noncompliant apps. This helps institutions enforce policies that safeguard sensitive data, such as student records or intellectual property, while ensuring compliance with regulations like FERPA. By integrating with Microsoft 365, it empowers schools and universities to foster a secure digital learning environment, protecting both users and data.
Office 365 Cloud App Security (MCAS) is a robust tool designed to enhance cybersecurity in educational institutions by providing visibility, control, and protection over cloud-based applications and services. It empowers schools and universities to safeguard sensitive student and staff data while ensuring compliance with regulatory requirements like FERPA. With advanced threat detection, it identifies and mitigates risks such as unauthorized access, data leaks, and malware attacks. The platform's real-time monitoring and analytics allow IT administrators to track user activities, detect suspicious behavior, and enforce policies like conditional access and data loss prevention (DLP). By integrating seamlessly with Office 365 and other applications, MCAS supports a secure learning environment, enabling educators and students to collaborate effectively without compromising data security.
App governance in Defender for Cloud Apps is a set of security and policy management capabilities designed for OAuth-enabled apps registered on Microsoft Entra ID, Google, and Salesforce. This feature is beneficial in educational environments where the use of various applications and platforms is prevalent. Read this topic to learn how to configure CASB on your firewalls to enable inline activity control for the selected set of cloud applications.
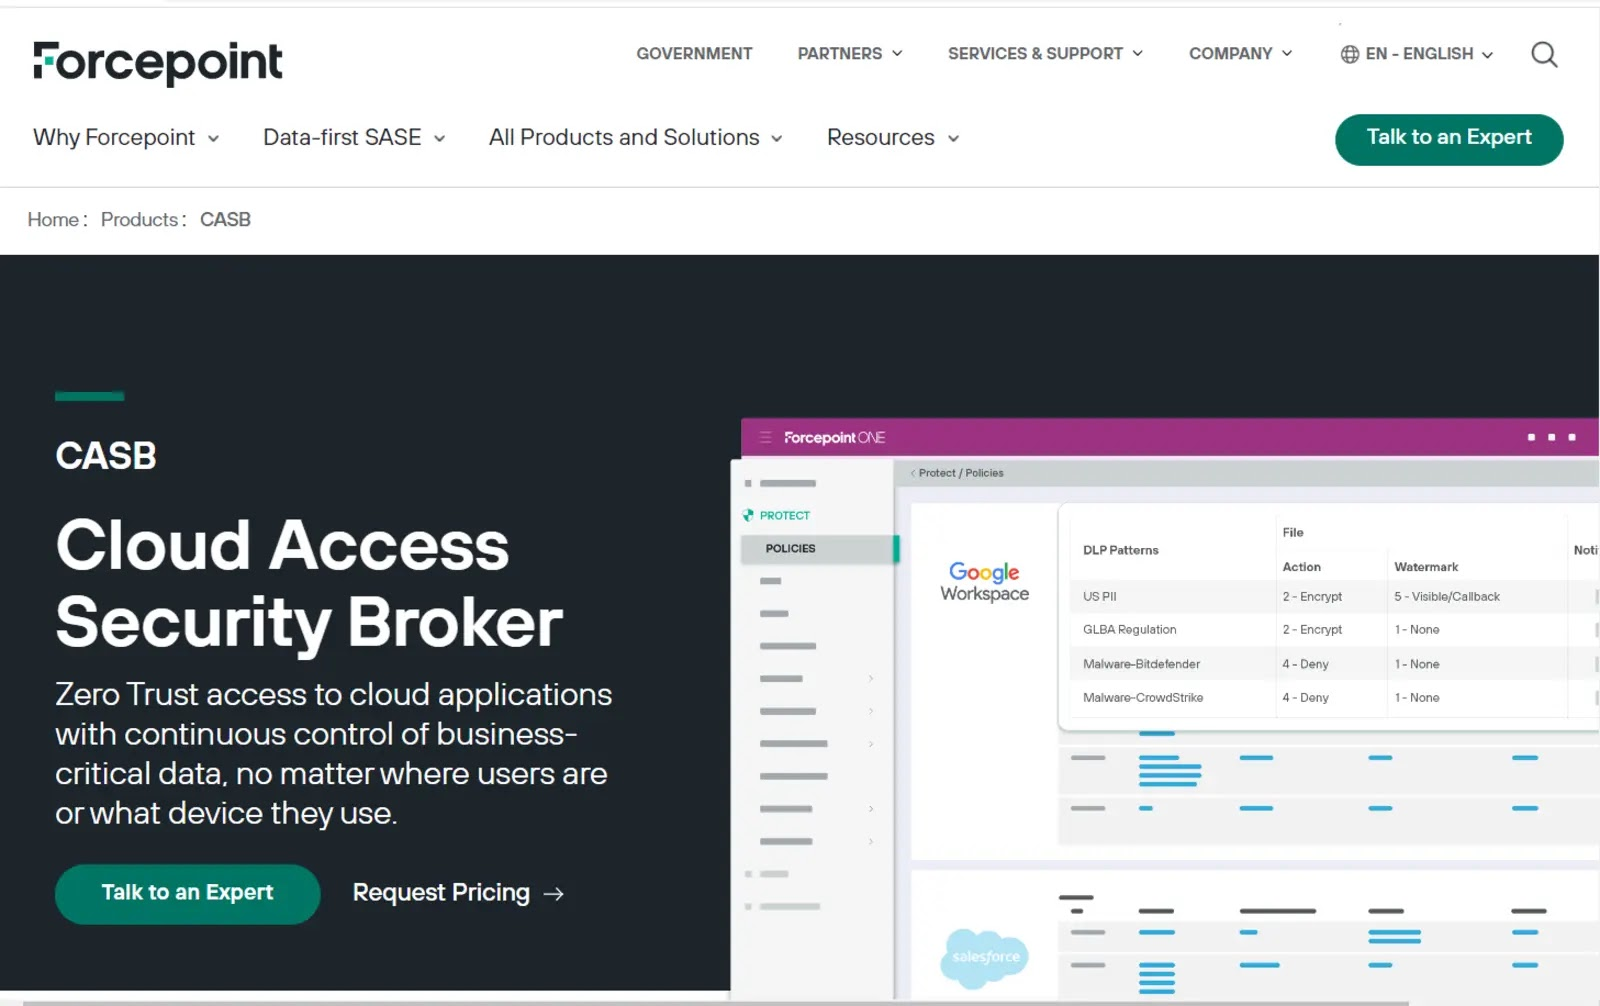
Cloud Access Security Broker (CASB) serves as a critical security checkpoint positioned between enterprise users and cloud service providers. Its primary role is to enforce security policies to protect and control access to cloud applications. CASB is a new Layer 7 service which provides inline application activity control. CASB's policy engine allows you to refine access conditions. You can specify rules for accessing, downloading, and uploading files for a set of cloud applications for use within your organization.
To use CASB on your firewalls, you must configure CASB policies and apply CASB policy rules in a security policy. Application such as Dropbox, Google Docs, OneDrive or application group such as FileSharing, chat, email. Activities such as login , download , and upload . However, not all applications support every activity. When configuring an application, ensure that you only select activities that are supported by that specific application. For a comprehensive view of the mapping between applications and their associated activities, see Table 1 .
You can configure activity-parameters for share-activity option. You can configure this optional statement to have even more granular control over traffic. Create an application instance for CASB. For CASB, to differentiate between corporate and non-corporate SaaS application instances, administrators need to configure access policies using the instance parameter. To identify an instance, CASB requires instance ID, domain, and type (optional). Table 2 provides application instance setting options.
(Required) Application instance name. For example, dropbox123. (Required) Application instance ID. It refers to unique URL to access SaaS service Each application can have its own instance ID. For the following example URLs, common string acmecorp07 as the instance ID taken from application's SaaS URLs: OneDrive or SharePoint URLâIIacmecorp07ms-my.sharepoint.com SlackâIISlack URL is acmecorp-zoy8730.slack.com and instance ID is acmecorp-zoy8730.
Following applications have generic URLs and instance ID is not applicable. (Required) Enter the domain address. It refers to email domain. For example, acmecorp07.com is an organization domain. Box, Dropbox, Google Docs, Salesforce, Gmail, and Slack uses the same domain for all the users.
OneDrive and SharePoint domain value is acmecorp07ms.onmicrosoft.com. (Optional) Enter one of the following values to map a type with an application instance: You must configure the type of value for Dropbox. For other applications, this configuration is optional. (Optional) Enter one of the following values to map a tagging with an application instance: SanctionedâIIApplication instances sanctioned by your organization.
UnsanctionedâIIApplication instances unsanctioned by your organization. Define policy action. Each policy has a set of actions (allow/deny and log-action) that the system performs upon success of all matching conditions. Configure a default rule. The default rule is matched if none of the other rules are matched, or if there are no other rules in the policy. Configuring a default rule is mandatory.
Apply CASB policies in the security policy as application services for the permitted traffic. 3. Software Implementation, Frameworks & Protocols Arrange your CASB rules in sequential order to handle specific match criteria for applications or activities. Set up a default CASB policy for the unified policy configuration. This default policy applies to the session until a dynamic application match occurs. Once the final application match is available for the security policy, the corresponding CASB policy will be applied. If no CASB policy is explicitly configured in the final firewall policy, the CASB service disengages for the session.
Install an application identification feature license. See Managing Junos OS Licenses . Download and install the Junos OS application signature package. Downloading and Installing the Junos OS Application Signature Package . The following sample shows configuration of CASB policy to allow users to share to SharePoint application with given domain only.
In the process of configuring a CASB policy, both application and activity are required components, whereas param-value is an optional element that allows you to specify finer-grained options within the policy. Apply CASB policies in the security policy as application-services. The following CASB policy denies downloads from all file sharing applications.
Apply CASB policies in the security policy as application-services. The default policy is required for unified policies. In case, if no default policy configured, the system displays an error message during commit. Use CASB Feature Explorer to confirm platform and release support for specific features.
Feature support is determined by the platform and release you are using. Use Feature Explorer to determine if a feature is supported on your platform. Implementing a Cloud Access Security Broker (CASB) is usually where cloud security stops being theoretical and starts dealing with real problems: shadow IT , data leakage, excessive sharing, and access that nobody can explain during an audit.
If your organization uses SaaS, IaaS, or PaaS at scale, a CASB gives you visibility and control without forcing every team back into a locked-down, on-prem model. The catch is that a CASB only works when it is deployed with clear goals, the right architecture, and actual operational ownership. Learn essential ethical hacking skills to identify vulnerabilities, strengthen security measures, and protect organizations from cyber threats effectively Implementing a CASB effectively means inventorying cloud services, defining security goals, choosing the right deployment model, integrating identity and data classification, piloting carefully, and continuously tuning policies. Done well, CASB improves cloud security, data control, and threat detection while reducing shadow IT and compliance risk.
The first step in effective CASB implementation is simple: find out what cloud services people are already using. That includes sanctioned SaaS platforms, unsanctioned apps, IaaS workloads, and PaaS environments. If you do not have that inventory, your cloud security program will always be reacting after the fact. Cloud security is only useful when it is tied to business context. You need to know who uses each service, what data lives there, and how damaging an outage, leak, or compromise would be. A marketing file-sharing app used by a small team does not deserve the same treatment as a finance platform holding customer records and payment-related information.
Build a service inventory from CASB discovery tools, firewall logs, proxy logs, DNS logs, SSO records, and cloud provider activity reports. This is where shadow IT usually shows up: an app that nobody formally approved but everybody uses because it is convenient. In many environments, the first CASB win is simply proving how much cloud activity was invisible. Map each service to business ownership and data sensitivity. A practical way to do this is to classify applications by usage, data type, and criticality: The U.S. Bureau of Labor Statistics notes continued growth in information security-related roles, reflecting the sustained need for better visibility and control in cloud-heavy environments; see BLS Occupational Outlook Handbook . For governance context, align your inventory approach with NIST Cybersecurity Framework functions such as Identify and Protect, because a CASB is strongest when it is part of a broader security architecture.
A CASB does not fix a cloud problem you have not defined. It exposes the problem, enforces the policy, and gives you evidence for decisions. A CASB fails when one team owns the tool and everyone else lives with the consequences. Security needs visibility and enforcement. IT needs manageable operations. Compliance needs audit evidence. Legal and privacy need data handling rules. Business units need workflows that still let people do their jobs.
Governance is the difference between a working CASB and an expensive dashboard. You need clearly assigned owners for policy approval, exception handling, incident response, and ongoing review. If there is no decision path, the CASB turns into a ticket queue and policy exceptions become permanent. Start by identifying a sponsor and a working group. Include security operations, identity and access management, compliance, privacy, legal, cloud application owners, and representatives from high-usage business teams. In practice, the app owner often knows the workflow impact better than the central security team, which is why early involvement prevents expensive rework later.
For workforce and governance mapping, the NICE Workforce Framework is a good way to structure responsibilities across people, tasks, and outcomes. It helps translate “someone should own this” into real operational role definitions. For implementation discipline, the MITRE ATT&CK knowledge base can also help teams understand what kinds of cloud behaviors a CASB should detect and control.
Document ownership in writing. If policy approval, exception handling, or incident escalation is only understood verbally, the first real audit or incident will expose the gap. The right CASB architecture depends on whether you need visibility, inline control, or both. API-based CASB connects directly to cloud services through vendor APIs. Proxy-based CASB sits in the path of user traffic and can enforce controls in real time.
Log-based CASB consumes logs from existing platforms and is usually the least disruptive, but also the least immediate. There is no universal best model. If you need fast deployment for sanctioned SaaS monitoring, API-based coverage is often the easiest starting point. If you need live blocking for uploads, downloads, or session behavior, proxy-based controls matter more. If your goal is broad visibility with limited change risk, log-based integration can get you useful detection data quickly.
For cloud architecture decisions, compare deployment to your session-risk needs, remote access patterns, and mobile workforce requirements. If your biggest problem is one user sharing a sensitive file externally, proxy control may be worth the complexity. If your biggest problem is unknown SaaS usage, API discovery and log ingestion may deliver value sooner. For official technical guidance, vendor documentation such as Microsoft Learn and Cisco design references are useful when you need to understand identity, networking, and access paths that influence CASB placement. That is especially important when cloud security has to fit into an existing security architecture instead of replacing it.
The fastest way to get value from CASB is to focus on high-risk data and behavior first. Start with sensitive file sharing, external collaboration, unmanaged devices, and unknown app usage. These are the places where data control problems become visible quickly and where risk reduction is easiest to explain to leadership. Data control is not just about blocking files. It is about deciding who can share, download, sync, or forward content based on context and sensitivity. If the same policy treats a public brochure and a customer database the same way, the controls will either be too weak or too disruptive.
For compliance mapping, use the official PCI Security Standards Council guidance when payment data is in scope, and pair that with NIST guidance for broader control design. If your environment handles personal data across borders, GDPR concepts and privacy review become part of the CASB policy discussion, not an afterthought. Do not start by blocking everything. Early over-enforcement creates policy workarounds, user resistance, and exception sprawl that are harder to fix later than the original risk.
A CASB becomes much more effective when it has context. Identity and access management tells the CASB who the user is, what group they belong to, and whether the login was trusted. Data classification tells the CASB what the content is worth and how sensitive it should be treated. Without both, the platform sees activity but not intent. Connect the CASB to your identity provider so it can use single sign-on, group membership, and conditional access decisions.
Then sync attributes such as department, region, contractor status, and privilege level. Those attributes let you enforce different rules for finance users, third-party users, and administrators without building separate policies for every app. Contextual signals matter. Device posture, location, authentication strength, and session risk can all change the policy decision. For example, a file download from a managed laptop on a corporate network may be allowed, while the same action from an unknown device on public Wi-Fi should trigger step-up verification or blocking.
For formal control design, ISACA COBIT is useful when translating technical integration into governance objectives. It helps security teams justify why identity, classification, and logging should not be treated as separate projects when the goal is workable cloud security. 4. Practical Deployment, Analysis & Case Studies This is where a CASB either becomes useful or becomes annoying. Policies must translate business and compliance requirements into specific actions that the platform can actually enforce. “Protect sensitive data” is too vague. “Block public sharing of files labeled confidential outside the corporate tenant” is enforceable.
Threat detection improves when policies are precise enough to generate meaningful alerts. If every event becomes an alert, analysts stop trusting the system. If nothing is blocked or flagged, the CASB becomes passive reporting software instead of a control point. For privacy-sensitive monitoring, involve legal and privacy teams before enabling session recording or broad content inspection. For security standards, reference NIST CSF and SP 800 guidance when defining control intent, because a policy tied to an explicit framework is easier to defend during audits and incident reviews.
Policy exceptions are necessary, but they should be time-bound and visible. Permanent exceptions are often just undocumented risk acceptance. A strong CASB program treats exceptions as a controlled process, not a side door. A pilot is where most CASB implementations succeed or fail. A controlled rollout lets you measure usability, identify false positives, and confirm that enforcement does what you expect without breaking normal work. If the pilot is skipped, the first real users become your test group, and that is usually the wrong population.
The pilot should include a limited set of users, one or two critical applications, and a clearly defined policy set. Start with alerting where possible, especially for high-visibility workflows. That gives you data without immediately disrupting work. Look at login friction, blocked legitimate activity, policy hit rates, and latency if inline controls are used. A policy can look strong on paper and still fail if it interrupts uploads, sync operations, or mobile collaboration. The point of testing is to learn what normal cloud usage actually looks like in your environment.
Many organizations also use the OWASP guidance on application and access risk concepts to help frame what “good enough” testing looks like. That matters because CASB tuning is not only about security outcomes; it is also about preserving usability. A control users bypass is not a control. Run the pilot with a support channel ready on day one. Fast response to blocked-but-legitimate work is the difference between measured adoption and a backlash.
CASB deployment is not complete until people know how to live with it. End users need to understand why the controls exist, what actions are restricted, and how to request access when a block is legitimate. Security staff need to know how to investigate alerts, interpret logs, and tune policies without waiting for vendor support every time. Incident Response is part of CASB operations because policy violations often reveal actual security events. A sensitive file sent to an external address or a sudden burst of downloads may be a mistake, or it may be a compromise. Your team needs playbooks that connect CASB alerts to triage, containment, and escalation.
Create short guidance for common scenarios: blocked sharing, risky device access, uploading restricted data, and reporting suspicious activity. Long policy documents do not help a user who just got blocked from sending a file to a partner. A one-page decision tree or quick-reference guide is usually more effective. For broader workforce alignment, the SHRM perspective on role clarity and internal communication is useful when rolling out controls that affect business teams. On the technical side, the course content in Certified Ethical Hacker (CEH) v13 is relevant here because understanding attacker behavior helps security teams explain why certain cloud behaviors are restricted in the first place.
A CASB is not a one-time project. It is an operating capability that has to evolve with cloud services, user behavior, and threat patterns. If the implementation is not continuously measured, the policies will drift and the visibility value will decay. The right metrics tell you whether the CASB is actually improving cloud security . Track shadow IT discovered, sensitive data exposures prevented, policy violations, repeated risky behavior, and the average time it takes to investigate an alert. These numbers tell a better story than raw alert counts because they show whether the program is reducing risk or just generating noise.
For broader risk context, reference the Verizon Data Breach Investigations Report and IBM Cost of a Data Breach Report when explaining why visibility and data control matter. These reports consistently show that human behavior, credential abuse, and data exposure remain central breach drivers. A CASB is valuable because it gives you control points in the exact places where those risks show up.
Periodic audits should also cover integration health, stale exceptions, and policy review cycles. The best CASB programs treat every exception as temporary until someone proves it should stay. That discipline keeps the platform aligned with actual business risk instead of last quarter’s assumptions. Effective CASB implementation is a program, not a product setting. The strongest outcomes come from phased rollout, precise policy design, identity and data integration, and continuous tuning based on real usage.
Learn essential ethical hacking skills to identify vulnerabilities, strengthen security measures, and protect organizations from cyber threats effectively Implementing a CASB effectively comes down to strategy, governance, and phased execution. If you start with a clear inventory, define real security outcomes, choose the right deployment model, and integrate identity and data controls, the platform can improve cloud security without grinding collaboration to a halt.
The practical path is straightforward: assess your cloud environment, build the right team, prioritize high-risk data flows, define policies carefully, test in a pilot, and keep tuning based on what the logs and users tell you. That approach strengthens data control, improves threat detection, and gives you better visibility into how cloud services are actually being used. If your team is preparing for hands-on cloud and security work, the Certified Ethical Hacker (CEH) v13 course is a useful complement because it reinforces the attacker mindset behind cloud misuse, data leakage, and access abuse. The next step is to apply the roadmap, measure the results, and keep the CASB aligned with business reality.
CompTIA®, Cisco®, Microsoft®, AWS®, EC-Council®, ISC2®, ISACA®, and PMI® are trademarks of their respective owners. Security+™, CEH™, CISSP®, and PMP® are trademarks of their respective owners. Implementing a CASB begins with clearly defining your organization’s security goals and understanding the specific cloud services in use. This helps tailor the deployment to address shadow IT, data security, and compliance requirements effectively.
Next, conduct an extensive assessment of existing cloud usage, identifying risk points and access patterns. Selecting a CASB solution that aligns with your infrastructure and security policies is crucial. Proper planning also involves integrating the CASB with existing security tools and establishing policies for data access and sharing. A CASB provides visibility into cloud data flows and user activities, enabling organizations to monitor and enforce data security policies. It allows for real-time detection of risky behaviors, such as unauthorized sharing or downloading of sensitive information.
By applying data loss prevention (DLP) policies, encryption, and access controls, a CASB minimizes the risk of data leakage. It also enforces compliance with regulations by auditing data access and sharing activities, thereby reducing the chance of inadvertent or malicious data breaches. Yes, a well-implemented CASB is designed to integrate seamlessly with existing security tools such as identity providers, SIEM platforms, and DLP solutions. Integration ensures comprehensive security coverage and centralized policy enforcement across cloud and on-premises environments.
Proper integration involves configuring APIs, connectors, or gateways that allow data sharing between systems. This integration enhances visibility, simplifies management, and enables automated responses to security incidents, making the CASB a vital component of your security architecture. One common misconception is that deploying a CASB alone will automatically secure all cloud data. In reality, it requires complementary policies, training, and ongoing management to be effective.
Another misconception is that a CASB can be deployed quickly without planning. Successful implementation demands thorough assessment, tailored policy development, and integration efforts, which can take time but are essential for reliable security outcomes. Establish clear objectives and align the CASB deployment with overall cloud security strategies. Engage stakeholders from different departments to ensure policies cover all use cases.
Regularly monitor and update security policies based on usage patterns and emerging threats. Training teams on best practices and maintaining continuous compliance checks are also vital for maximizing the benefits of your CASB solution. A Cloud Access Security Broker (CASB) is an on-premises or cloud-hosted policy enforcement center positioned between cloud service consumers and cloud service providers. CASBs combine four core security pillars: Visibility (discovering Shadow IT and scoring SaaS risks), Data Security (enforcing cross-cloud Data Loss Prevention and blocking public sharing links), Threat Protection (preventing malware distribution and account takeovers via UEBA), and Compliance (auditing configurations against GDPR, HIPAA, SOC 2, and ISO 27001). Enterprises deploy CASBs using a hybrid model that pairs out-of-band API integrations for deep retroactive data governance with inline forward/reverse proxies for real-time access and upload control.
As modern organizations migrate critical workloads to Software-as-a-Service (SaaS) and Infrastructure-as-a-Service (IaaS) platforms, traditional on-premises perimeter defenses become obsolete. Business data no longer resides exclusively behind corporate firewalls; it is distributed across multi-tenant cloud ecosystems including Microsoft 365, Google Workspace, Salesforce, Slack, GitHub, and ServiceNow. Securing this dynamic ecosystem requires Cloud Access Security Brokers (CASB) operating as policy enforcement engines between users and cloud applications.
To successfully implement a CASB, security architects must understand the three primary deployment topologies: API-Based (Out-of-Band) , Inline Forward Proxy , and Inline Reverse Proxy . In modern enterprise environments, industry best practice mandates a Multimode CASB Architecture . Organizations leverage API connections for deep repository governance, security configuration management, and retroactive DLP audits, while deploying Inline Forward/Reverse proxies within a broader Security Service Edge (SSE) framework to control real-time unmanaged device access and block unauthorized data egress.
For more architectural insights on zero trust access and network defenses, review our guide on Insider Threat Detection & Behavioral Governance and examine Data Leakage Protection (DLP): Enterprise Implementation Guide . 5. Performance Evaluation & Extended Technical Observations One of the primary security risks facing enterprises is Shadow IT —the proliferation of unsanctioned cloud applications, generative AI tools, and file-sharing utilities adopted by employees without IT or security oversight. Employees frequently upload proprietary source code, customer rosters, and financial models to unvetted cloud services to streamline daily workflows, introducing massive compliance and intellectual property leakage risks.
While on-premises DLP focuses on intercepting USB writes and email attachments, Cloud DLP addresses the complex collaboration mechanisms native to SaaS environments: public link generation, cross-tenant file sharing, external guest invites, and automated API webhook exfiltration. CASB API engines continuously traverse cloud storage file trees (SharePoint, Google Drive, Box), detecting files shared with "Anyone with the link" (public anonymous access) or shared with external consumer domains ( @gmail.com , @yahoo.com ).
Automated remediation rules instantly downgrade sharing permissions to internal company members only. Policy enforcement varies based on user context, device posture, and network trust. When a user connects from a managed corporate laptop via corporate VPN, full read/write and download privileges are granted. When the same user connects from an unmanaged home PC or mobile device (BYOD), the CASB reverse proxy enforces Browser-Only View Mode with dynamic watermarking, completely blocking local file downloads, clipboard copying, and printing.
Modern CASB engines integrate with browser extensions and inline proxies to perform real-time content analysis on prompts submitted to AI platforms (ChatGPT, Claude, Gemini). Prompts containing proprietary code snippets, API keys, or customer PII are redacted or blocked before transmission. Cloud governance frameworks must also comply with global data protection mandates (GDPR, CCPA, HIPAA) and civil litigation discovery rules. When CASB systems perform automated quarantine actions, they must maintain complete audit logs and integrate with legal hold repositories to prevent spoliation of discoverable Electronically Stored Information (ESI) under FRCP Rule 37(e) .
For detailed guidance on orchestrating defensible litigation holds across cloud repositories, explore our comprehensive guide on Legal Hold Automation Process: Workflows, Software & Templates and see Enterprise Legal Tech Stack Architecture . Below is a production-ready Python script demonstrating how enterprise security teams can build an automated SaaS repository scanner to audit file sharing permissions, detect exposed sensitive data patterns, and generate structured remediation tickets: Deploying automated scripts of this nature within serverless orchestration pipelines (AWS Lambda, Azure Functions, Cloud Composer) ensures that newly created external shares and public URLs are audited and remediated within seconds.
Cloud Access Security Brokers (CASBs) have evolved from standalone point products into indispensable cornerstones of modern enterprise security architectures and Security Service Edge (SSE) frameworks. By providing unified visibility, content-aware data protection, advanced threat prevention, and continuous compliance auditing across multi-tenant SaaS ecosystems, CASBs empower organizations to accelerate cloud adoption while maintaining robust data governance.
NGFWs inspect network layer traffic at the perimeter boundary. CASBs operate at the application and API layers, understanding granular SaaS actions (e.g., distinguishing between viewing a document in Google Drive vs. sharing it with an external personal email). The four foundational pillars are: 1) Visibility (Shadow IT discovery and SaaS inventory), 2) Data Security (Cloud DLP and collaboration governance), 3) Threat Protection (UEBA, malware defense, and credential protection), and 4) Compliance (regulatory auditing and configuration posture).
API CASBs connect directly to cloud services via REST APIs to audit data at rest, user permissions, and configurations out-of-band without latency. Inline CASBs sit directly in the traffic flow (as forward or reverse proxies) to inspect and block actions in real-time. Shadow IT refers to unapproved cloud apps used by employees without security oversight. CASBs discover Shadow IT by ingesting proxy, firewall, and DNS logs to identify cloud application traffic and calculate risk ratings.
By integrating with Single Sign-On (SSO) as a Reverse Proxy. When an unmanaged device authenticates, traffic is routed through the CASB proxy, which can restrict users to web-only viewing and block file downloads or copy-paste actions. CASB is a core component of Security Service Edge (SSE), which also includes Secure Web Gateways (SWG) and Zero Trust Network Access (ZTNA). When SSE is converged with software-defined WAN (SD-WAN), it forms Secure Access Service Edge (SASE).
Cloud DLP inspects content using regular expressions, Exact Data Matching (EDM), and document fingerprinting, automatically blocking public link creation, revoking unauthorized external shares, or encrypting sensitive files. Yes. CASBs inspect files uploaded to cloud storage using anti-malware engines and sandboxing, quarantining infected files before they synchronize across enterprise user endpoints.
SSPM continuously monitors and audits configuration settings across SaaS applications (e.g., ensuring MFA is enforced and legacy protocols are disabled). Many modern CASBs include built-in SSPM capabilities. Inline forward proxies perform SSL/TLS inspection by terminating client connections, decrypting and inspecting the payload against DLP policies, and re-encrypting the connection before forwarding it to the SaaS destination.
Tenant restriction allows organizations to permit access to corporate M365 or Google Workspace instances while blocking users from logging into personal or unapproved external instances on corporate devices. CASB UEBA engines detect anomalous activities such as impossible travel logins (e.g., logins from New York and Tokyo within 30 minutes), sudden bulk file downloads, or administrative privilege escalation.
API-based CASBs introduce zero latency because they operate out-of-band. Modern cloud-native inline proxies deployed across global edge points of presence (PoPs) introduce negligible latency (typically < 15–25ms). By identifying EU citizen PII stored in unauthorized SaaS apps, enforcing geographical data residency restrictions, and auditing third-party apps for GDPR-compliant contractual commitments.
Yes. Inline CASB proxies can inspect user prompts sent to AI platforms (e.g., ChatGPT, Claude), blocking confidential code snippets, API keys, or personal customer data from being submitted. 16. What is the difference between a CASB and a Cloud Workload Protection Platform (CWPP)? CASB focuses on SaaS application governance and user data interactions. CWPP focuses on securing virtual machines, containers, and serverless compute workloads in IaaS environments like AWS, Azure, and GCP.
Start with API connectors for core SaaS apps in audit-only mode, discover Shadow IT via firewall log ingestion, refine DLP policies to eliminate false positives, and gradually enable inline blocking and BYOD reverse proxies. Content is reviewed against applicable legal, forensic, and digital-evidence standards. Learn more about our SME Practice Team or review our Editorial Standards .
A technical guide to Quality Assurance Protocols for ESI Ingestion & Load File Delivery. Learn quality assurance protocols for esi ingestion & load file delivery and... Defensible playbook for Defensible Mass Production Packaging & Delivery Verification. Covers defensible mass production packaging & delivery verification...
A technical guide to Cross-Custodian De-duplication vs Single-Custodian Deduplication Mechanics. Learn cross-custodian de-duplication vs single-custodian... Saas applications offer a flexible, scalable, and cost-effective approach to business operations, enabling employees to work and access data regardless of location or device. However, this increased accessibility also brings new risks.
To protect against cloud security threats, organizations are implementing various strategies, best practices, and technologies. One of the most popular solutions is implementing a Cloud Access Security Broker (CASB) to monitor data between Saas applications and end users. CASBs filter cloud traffic and enforce security policies to increase control over business data that leaves on-prem infrastructure. They offer four main advantages: Unfortunately, to access these benefits and extend your security policies beyond on-prem infrastructure, you have to overcome various challenges during cloud access security broker implementation. Defining how users interact with SaaS tools and ensuring robust access controls across sprawling cloud-based software environments is a difficult task.
You can implement several CASB best practices to overcome these challenges while maximizing security and minimizing the impact on your operations. CASB deployment strategies have to find a way to maintain security without significantly impacting user experience. By following CASB best practices, you can deliver SaaS security protections in a way that enables and does not hinder end users. This includes promoting approved SaaS applications and streamlining security mechanisms from the user’s point of view. Poor CASB implementation can end up driving users to unapproved cloud services, increasing shadow IT, reducing visibility, and generating new security concerns.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Cloud%20management • https://en.wikipedia.org/wiki/Numerix • https://en.wikipedia.org/wiki/Robot%20as%20a%20service • https://dailysecurityreview.com/cyber-security/cloud-access-security-broker-casb-explained-architecture-and-uses/ • https://learn.microsoft.com/en-us/microsoft-365/education/guide/3-standard/security/standard-security-cloud-access • https://www.juniper.net/documentation//us/en/software/junos/application-identification/topics/topic-map/casb-security-device s.html • https://www.ituonline.com/blogs/implementing-a-cloud-access-security-broker-effectively-a-step-by-step-guide/ • https://discoverytechlab.com/casb-cloud-security-saas-governance-guide/ • https://www.checkpoint.com/cyber-hub/cloud-security/what-is-casb/5-casb-implementation-best-practices/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Cloud Access Security Broker Simulation Using Python.
[*] Metasploit Scan Running on Target Subnet for Cloud Access Security Broker Simulation Using Python... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |