Complete Technical Paper Content — Cloud Based Intrusion Detection System Using Deep Learning
Overview & System Context
Cloud Based Intrusion Detection System Using Deep Learning: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~630 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Stopping cloud breaches has never been easier. Take advantage of our free 15-day trial and experience CrowdStrike Falcon® Cloud Security today.
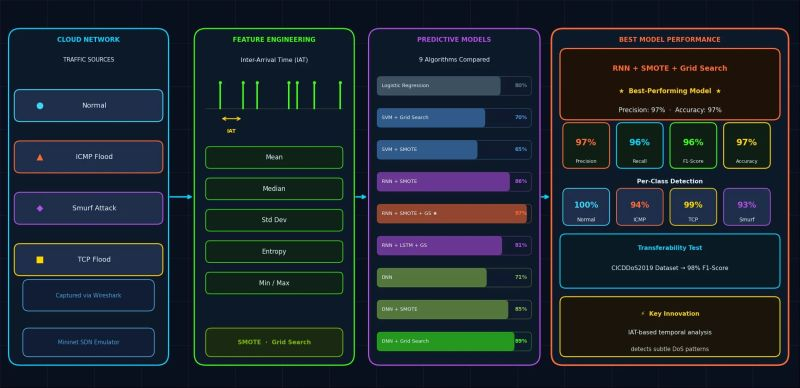
Detect activity across the cloud control plane and workloads with updates in just seconds. Correlate and analyze risk across cloud infrastructure, identities, apps, data, and AI layers. Confirmation of access and next steps will be emailed within 24 hours of your request. Figure 1: Enhanced Detection of Intrusion Detection System in Cloud Networks ...
Unfortunately our free trial is designed for direct use and is not intended for consultants, partners, MSSP, etc.. Your client can request a trial directly or you may also be interested in our partner program. Become a partner 2. System Architecture & Core Working Principles Unfortunately our free trial is designed for direct use and is not intended for consultants, partners, MSSP, etc.. Your client can request a trial directly or you may also be interested in our partner program.
Detect and respond to cloud control plane attacks in real-time. Block threats on your systems while capturing and recording activity as it happens to detect threats fast. Get up and running in minutes. Connect CrowdStrike to your environments to discover everything you run in the cloud. Deploy the lightweight Falcon® sensor for in-depth real-time visibility across hosts, containers, and Kubernetes workloads.
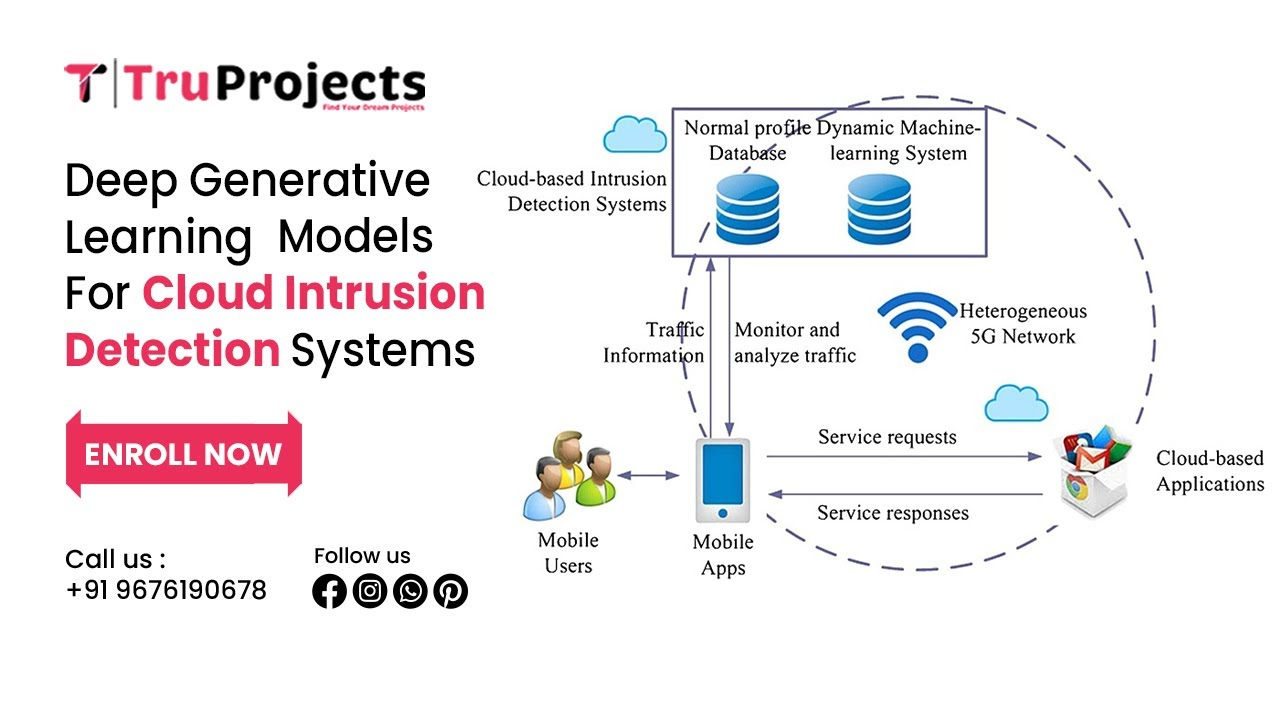
Go beyond siloed misconfiguration detections and identify combinations of risk factors that form breach pathways. Prioritize the risks that CrowdStrike automatically correlates to real-world adversary behavior. Figure 2: Deep Generative Learning Models for Cloud Intrusion Detection Systems ... 1. Prepare for installation: For optimal performance, uninstall or disable other antivirus solutions before installing the Falcon sensor.
3. Software Implementation, Frameworks & Protocols 2. Activate your account via the email instructions sent within 24 hours of your trial request. 3. Log in and install sensors to your devices by following the instructions on the mainview. You’ll find video guides on how to install sensors for your particular OS. You can also find instructions here .
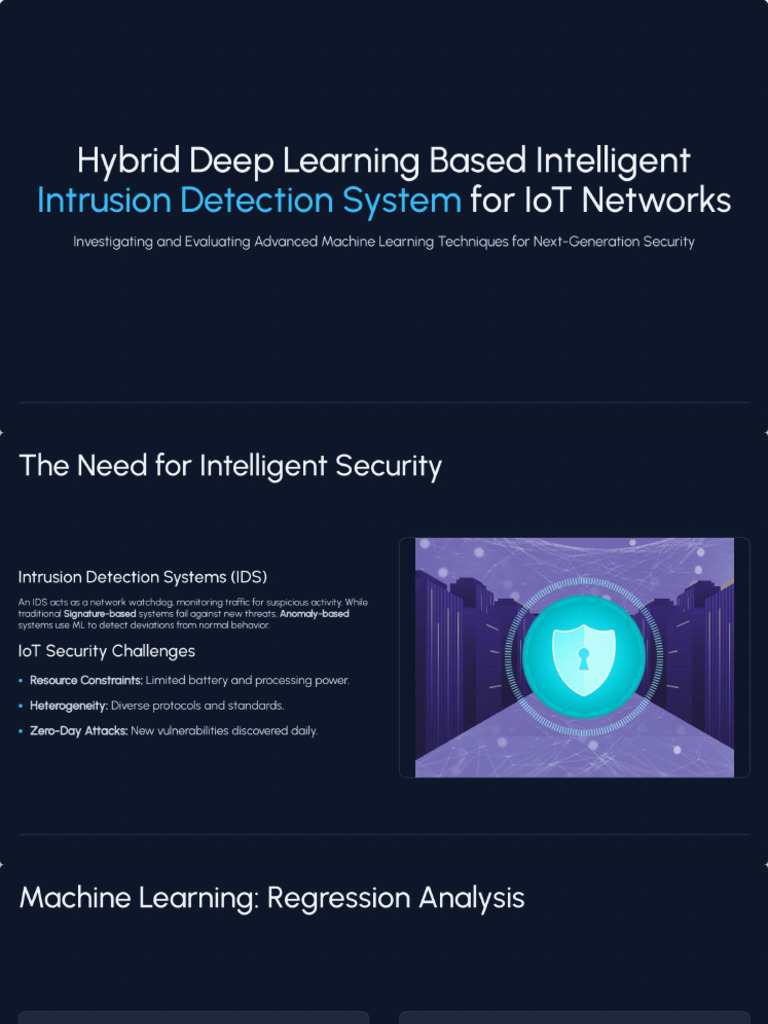
Stopping cloud breaches has never been easier. Take advantage of our free 15-day trial and experience CrowdStrike Falcon® Cloud Security today. An email confirming access and next steps will be sent shortly after your request is submitted. Figure 3: Hybrid Deep Learning Based Intelligent Intrusion Detection System For ...
Detect and respond to cloud control plane attacks in real -time. Block threats on your systems while capturing and recording activity as it happens to detect threats fast. 4. Practical Deployment, Analysis & Case Studies Get up and running in minutes. Connect CrowdStrike to your environments to discover everything you run in the cloud. Deploy the lightweight Falcon® sensor for in-depth real-time visibility across hosts, containers, and Kubernetes workloads.
Go beyond siloed misconfiguration detections and identify combinations of risk factors that form breach pathways. Prioritize the risks that CrowdStrike automatically correlates to real-world adversary behavior. The Forrester TEI study quantifies financial and operational benefits of Falcon Cloud Security Quickly start your trial using built-in step-by-step guidance. Agentless onboarding connects CrowdStrike to your cloud environment for full-coverage visibility. The intelligent Falcon® sensor provides official protection for your cloud hosts, containers, and Kubernetes workloads.
Once you’re in, you can see asset inventory, analyze high-risk misconfigurations, and review detections to see how CrowdStrike Falcon Cloud Security protects your cloud environment. 5. Performance Evaluation & Extended Technical Observations " With CrowdStrike, we can remediate any cloud intrusion in less than 16 minutes, which puts our minds at ease, while ensuring a great user experience for our clients. ” " We can see exactly what services are running in Kubernetes ... If something is malicious, it’s blocked immediately by CrowdStrike. 90% of alerts are resolved automatically, so we rarely have to step in. ” " CrowdStrike Falcon® Cloud Security extends prevention and detection to containerized workloads, while shared telemetry across modules delivers seamless visibility across every environment. ” The trial includes access to all Falcon Cloud Security capabilities. You can trial further features in the Falcon platform by going to the CrowdStrike store and requesting trials for the products you'd like to test.
The Falcon platform is a 100% cloud-based solution, offering security as a service (SaaS) to customers. Harvested Online Documentation & Reference Sources • https://www.bing.com/aclick?ld=e8IEbbhZeRQiwNi1pXLo5XrjVUCUxuN3Lg10OH4JayNdOAO1_ofXB6eotHh0_9Z1Qd5dMr 8uaeakSw3CsYTU78HyLm9geP8IsKU03xIbSShN2xPpkPWg2PkJ8O6bLJQW9izo4rqCpp8WoYJoZ88hNHv4-s906hq_jeER8 PL2zkJ1ze8j9LcsRo7dxnAaP3C7uzOnL5aA&u=aHR0cHMlM2ElMmYlMmZ3d3cuY3Jvd2RzdHJpa2UuY29tJTJmZW4tdXMlM mZwcm9kdWN0cyUyZnRyaWFscyUyZnRyeS1mYWxjb24tY2xvdWQtc2VjdXJpdHklMmYlM2Z1dG1fY2FtcGFpZ24lM2RjbG9 kJTI2dXRtX2NvbnRlbnQlM2RjcndkLXNhaWEtYW1lci11cy1lbi1wc3AteC10cmwtZmNsdHItdGN0X3hfeF94LXgteCUyNnV0bV 9tZWRpdW0lM2RzZW0lMjZ1dG1fc291cmNlJTNkYmluZyUyNnV0bV90ZXJtJTNkY2xvdWQlMjUyMHNlY3VyaXR5JTI1MjBtZ WFzdXJlcyUyNnV0bV9sYW5ndWFnZSUzZCUyNmNxX2NtcCUzZDQ0Njk0NDAzMiUyNmNxX3BsYWMlM2QlMjZtc2Nsa2lkJ TNkYjEyZTNjZTM4YTA0MWU1YTA1MDU1NjM3NmU0NDdmZmM&rlid=b12e3ce38a041e5a050556376e447ffc • https://www.bing.com/aclick?ld=e8B2qWQ0Ss6PNqrrw-VDu4dTVUCUyNantUSB_loXB6WAnSudFnKMXRWGEblIOJyYeH- Het9TWoDEwJiX6xSKdApMZngdHyGAX9P6xBd5hBej-bbzyMSyP737wRAoZcz2ne-6VN_1GWR-X-AydpHGh3it8h2feAKw0d kbRWdXWjRbo6HBe-cg0STkenmymOj5xsDbpcFA&u=aHR0cHMlM2ElMmYlMmZnby5jcm93ZHN0cmlrZS5jb20lMmZjbmFwc C1jbG91ZC10cmlhbC1yZXF1ZXN0Lmh0bWwlM2Z1dG1fY2FtcGFpZ24lM2RjbG9kJTI2dXRtX2NvbnRlbnQlM2RjcndkLXNha WEtYW1lci11cy1lbi1wc3AteC10cmwtZmNsdHItdGN0X3hfeF94LXgteCUyNnV0bV9tZWRpdW0lM2RzZW0lMjZ1dG1fc291cm NlJTNkYmluZyUyNnV0bV90ZXJtJTNkY2xvdWQlMjUyMHRocmVhdCUyNTIwaW50ZWxsaWdlbmNlJTI2dXRtX2xhbmd1YWdl JTNkJTI2Y3FfY21wJTNkNDQ2OTQ0MDMyJTI2Y3FfcGxhYyUzZCUyNm1zY2xraWQlM2RlZjRmODc4OTZkN2YxYTZkNzkx YWVkNWQ4OTNiZjI5Nw&rlid=ef4f87896d7f1a6d791aed5d893bf297
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Cloud Based Intrusion Detection System Using Deep Learning.
[*] Metasploit Scan Running on Target Subnet for Cloud Based Intrusion Detection System Using Deep Learning... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |