Complete Technical Paper Content — Cloud Based Security Information And Event Management Tool
Overview & System Context
Cloud Based Security Information And Event Management Tool: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9519 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Security information and event management (SIEM) is a field within computer security that combines security information management (SIM) and security event management (SEM) to enable real-time analysis of security alerts generated by applications and network hardware. SIEM systems are central to security operations centers (SOCs), where they are employed to detect, investigate, and respond to security incidents. SIEM technology collects and aggregates data from various systems, allowing organizations to meet compliance requirements while safeguarding against threats. NIST's definition for a SIEM tool is an application that provides the ability to gather security data from information system components and present that data as actionable information via a single interface. SIEM tools can be implemented as software, hardware, or managed services. SIEM systems log security events and generate reports to meet regulatory frameworks such as the Health Insurance Portability and Accountability Act (HIPAA) and the Payment Card Industry Data Security Standard (PCI DSS). The integration of SIM and SEM within SIEM provides organizations with a centralized approach for monitoring security events and responding to threats in real-time. First introduced by Gartner analysts Mark Nicolett and Amrit Williams in 2005, the term SIEM has evolved to incorporate advanced features such as threat intelligence and behavioral analytics, which allow SIEM solutions to manage complex cybersecurity threats, including zero-day vulnerabilities and polymorphic malware. In recent years, SIEM has become increasingly incorporated into national cybersecurity initiatives. For instance, Executive Order 14028 signed in 2021 by U.S. President Joseph Biden mandates the use of SIEM technologies to improve incident detection and reporting in federal systems. Compliance with these mandates is further reinforced by frameworks such as NIST SP 800-92, which outlines best practices for managing computer security logs. Modern SIEM platforms are aggregating and normalizing data not only from various Information Technology (IT) sources, but from production and manufacturing Operational Technology (OT) environments as well.
Log management: Focus on simple collection and storage of log messages and audit trails. Security information management (SIM): Long-term storage as well as analysis and reporting of log data. Security event manager (SEM): Real-time monitoring, correlation of events, notifications and console views. Security information and event management (SIEM): Combines SIM and SEM and provides real-time analysis of security alerts generated by network hardware and applications. Managed Security Service: (MSS) or Managed Security Service Provider: (MSSP): The most common managed services appear to evolve around connectivity and bandwidth, network monitoring, security, virtualization, and disaster recovery. Security as a service (SECaaS): These security services often include authentication, anti-virus, anti-malware/spyware, intrusion detection, penetration testing and security event management, among others. In practice many products in this area will have a mix of these functions, so there will often be some overlap – and many commercial vendors also promote their own terminology.
Oftentimes commercial vendors provide different combinations of these functionalities which tend to improve SIEM overall. Log management alone doesn't provide real-time insights on network security, SEM on its own won't provide complete data for deep threat analysis. When SEM and log management are combined, more information is available for SIEM to monitor. A key focus is to monitor and help manage user and service privileges, directory services and other system-configuration changes; as well as providing log auditing and review and incident response.
SIEM architectures may vary by vendor; however, generally, essential components comprise the SIEM engine. The essential components of a SIEM are as follows: A data collector forwards selected audit logs from a host (agent based or host based log streaming into index and aggregation point) An ingest and indexing point aggregation point for parsing, correlation, and data normalization A search node that is used for visualization, queries, reports, and alerts (analysis take place on a search node) A basic SIEM infrastructure is depicted in the image to the right.
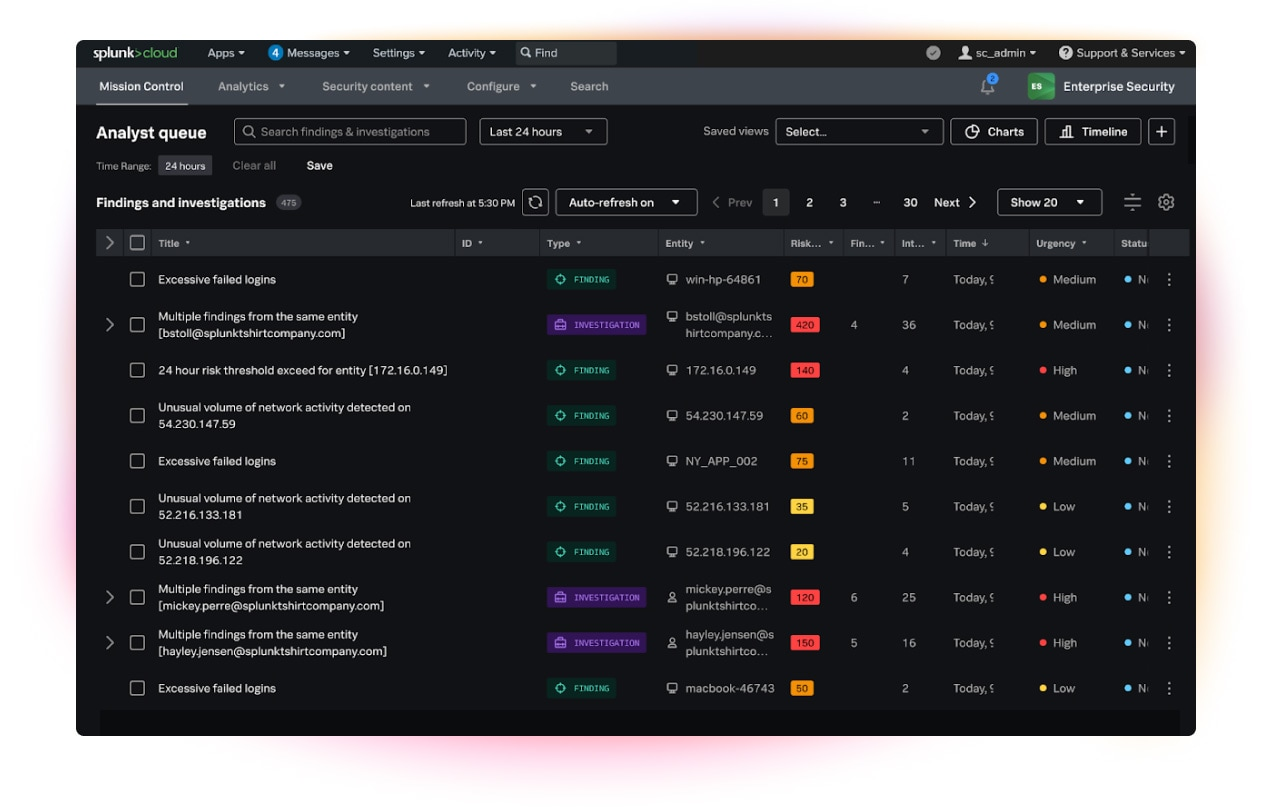
Figure 1: SIEM: Security Information & Event Management Explained | Splunk SIEM visibility and anomaly detection could help detect zero-days or polymorphic code. Primarily due to low rates of anti-virus detection against this type of rapidly changing malware. Parsing, log normalization and categorization can occur automatically, regardless of the type of computer or network device, as long as it can send a log. Visualization with a SIEM using security events and log failures can aid in pattern detection. Protocol anomalies that can indicate a misconfiguration or a security issue can be identified with a SIEM using pattern detection, alerting, baseline and dashboards. SIEMS can detect covert, malicious communications and encrypted channels. Cyberwarfare can be detected by SIEMs with accuracy, discovering both attackers and victims. Modern SIEM platforms support not only detection, but response too. The response can be manual or automated including AI based response.
SIEM systems can have hundreds and thousands of correlation rules. Some of these are simple, and some are more complex. Once a correlation rule is triggered the system can take appropriate steps to mitigate a cyber attack. Usually, this includes sending a notification to a user and then possibly limiting or even shutting down the system. Cloud computing security or cloud security refers to a broad set of policies, technologies, applications, and controls used to protect data, applications, services, and the associated infrastructure of cloud computing. It is a sub-domain of computer security, network security and, more broadly, information security.
Deterrent controls Administrative mechanisms intended to reduce attacks by informing attackers of consequences. Preventive controls Controls designed to reduce vulnerabilities and prevent unauthorized access. Detective controls Controls that detect and respond to security events. Includes monitoring, SIEM, IDS/IPS, malware detection. Corrective controls Controls that reduce the impact of an incident and restore systems.
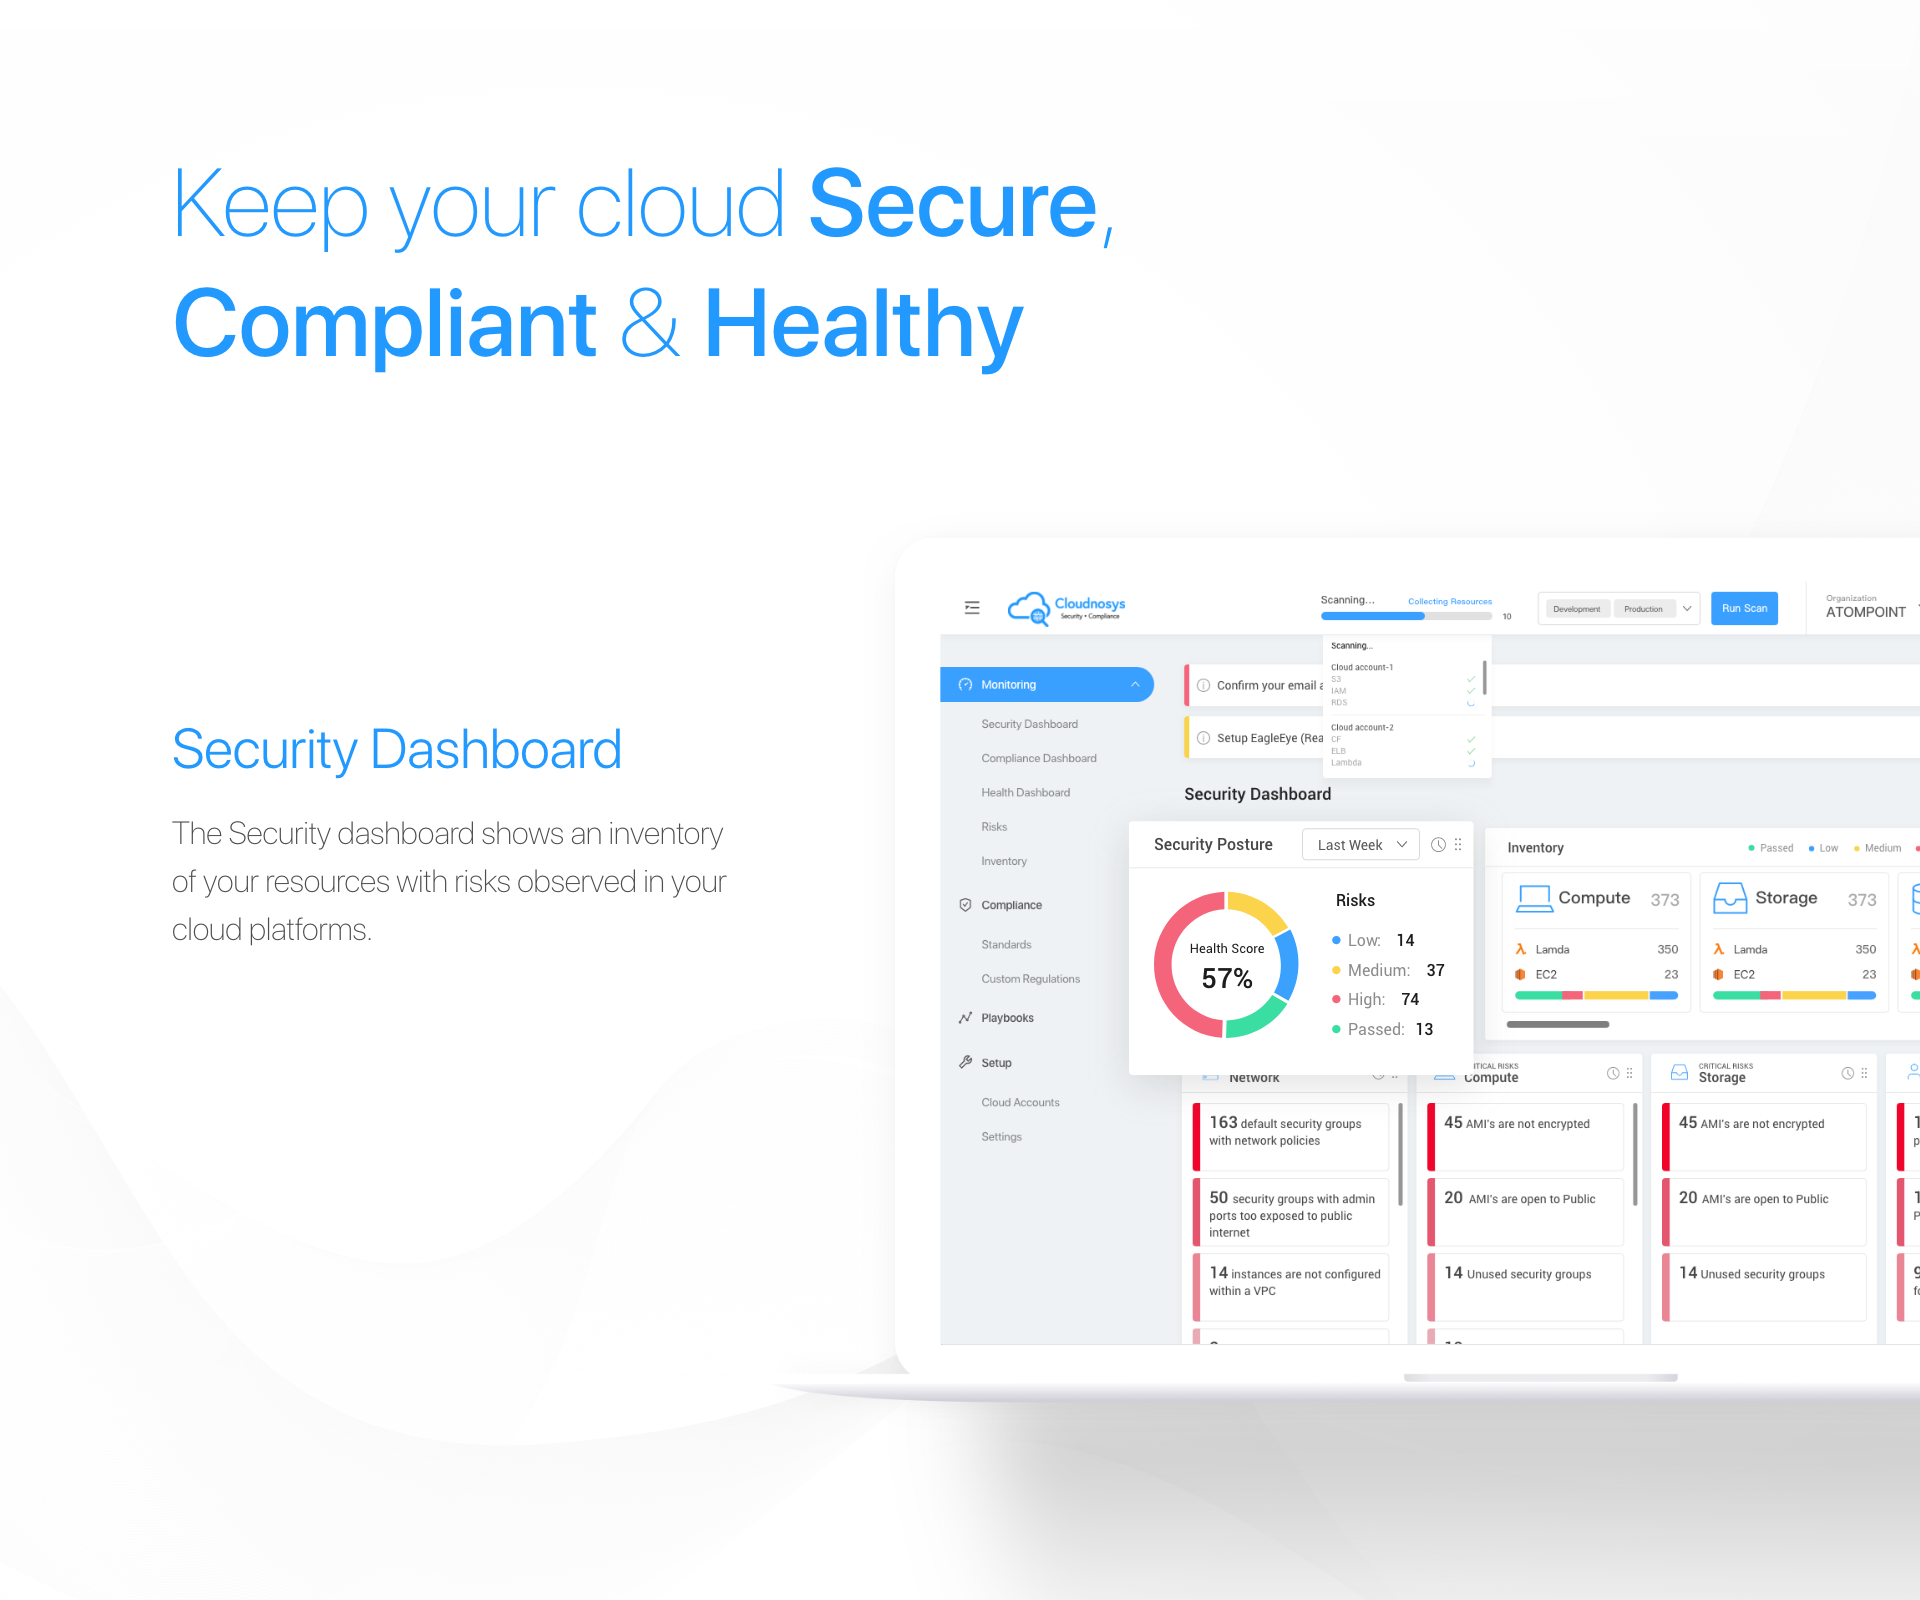
Figure 2: Cloud Security Dashboard UI/UX & Product Design :: Behance Business continuity and data recovery Cloud providers have business continuity and data recovery plans in place to ensure service continuity and data protection. Log and audit trail In addition to producing logs and audit trails, cloud providers work with their customers to secure these logs and ensure they're accessible for forensic investigation (e.g., eDiscovery). Unique compliance requirements In addition to the requirements on customers, data centers used by cloud providers may be subject to additional compliance obligations. Using a cloud service provider (CSP) can lead to extra security concerns around data jurisdiction since customer or tenant data may not remain in the same location or provider's cloud.
Aside from the security and compliance issues already discussed, cloud providers and their customers negotiate terms around liability (stipulating how incidents involving data loss or compromise will be resolved, for example), intellectual property, and end-of-service (when data and applications are ultimately returned to the customer). These issues are typically addressed in service-level agreements (SLAs).
Information security (infosec) is the practice of protecting information by mitigating information risks. It is part of information risk management. It typically involves preventing or reducing the probability of unauthorized or inappropriate access to data or the unlawful use, disclosure, disruption, deletion, corruption, modification, inspection, recording, or devaluation of information. It also involves actions intended to reduce the adverse impacts of such incidents. Protected information may take any form, e.g., electronic or physical, tangible (e.g., paperwork), or intangible (e.g., knowledge). Information security's primary focus is the balanced protection of data confidentiality, integrity, and availability (known as the CIA triad, unrelated to the US government organization) while maintaining a focus on efficient policy implementation but without hampering organization productivity. This is largely achieved through a structured risk management process. To standardize this discipline, academics and professionals collaborate to offer guidance, policies, and industry standards on passwords, antivirus software, firewalls, encryption software, legal liability, security awareness and training, and so forth. This standardization may be further driven by a wide variety of laws and regulations that affect how data is accessed, processed, stored, transferred, and destroyed. While paper-based business operations are still prevalent, requiring their own set of information security practices, enterprise digital initiatives are increasingly being emphasized, with information assurance dealt with by information technology (IT) security specialists. These specialists apply information security to technology (most often some form of computer system). IT security specialists are hired by major enterprises and establishments to keep company technology secure from malicious attacks seeking to acquire critical private information or gain control of the internal systems. There are many specialized roles in Information Security including securing networks and allied infrastructure, securing applications and databases, security testing, information systems auditing, business continuity planning, electronic record discovery, and digital forensics.
Information security standards are guidelines generally outlined in published materials that aim to protect a user's or an organization's cyber environment from threats. This environment includes the users themselves, hardware such as devices and networks, software such as applications or services, and any information in storage or transit. These standards comprise security concepts, technologies, and guidelines to deal with an adverse event. They may also include assessment criteria and certification for organizations implementing a minimum level of security. These standards are developed by various international and national bodies to prevent or mitigate cyber-attacks, ensure consistency among developers, and establish a minimum standard in industries susceptible to an attack. The ISO/IEC 27000 family, published by the International Organization for Standardization (ISO) and the International Electrotechnical Commission (IEC), provides information about the guidelines and requirements for an Information Security Management System (ISMS). The Common Criteria (ISO/IEC 15408) provides guidelines on evaluating and certifying the security of a system. The IEC 62443 establishes security standards for automation and control systems. Similarly, the ISO/SAE 21434, ETSI EN 303 645, and EN 18031 provide standards for road vehicles, the Internet of Things, and radio-based systems respectively. The NIST Cybersecurity Framework (NIST CSF) is a set of guidelines developed by the U.S. National Institute of Standards and Technology to help organizations with risk management. NIST also publishes various Federal Information Processing Standards (FIPS) and Special Publications. The United Kingdom has introduced Cyber Essentials, which is a certification scheme to protect organizations against common security threats. The Australian Cyber Security Centre publishes the Essential Eight mitigation strategies. The Payment Card Industry Data Security Standard (PCI DSS) regulates handling of cardholder data in order to reduce credit card fraud. UL has published standards related to specific industries such as UL 2900-2-3 for security and life safety signaling systems and UL-2900-2-1 for healthcare and wellness systems.
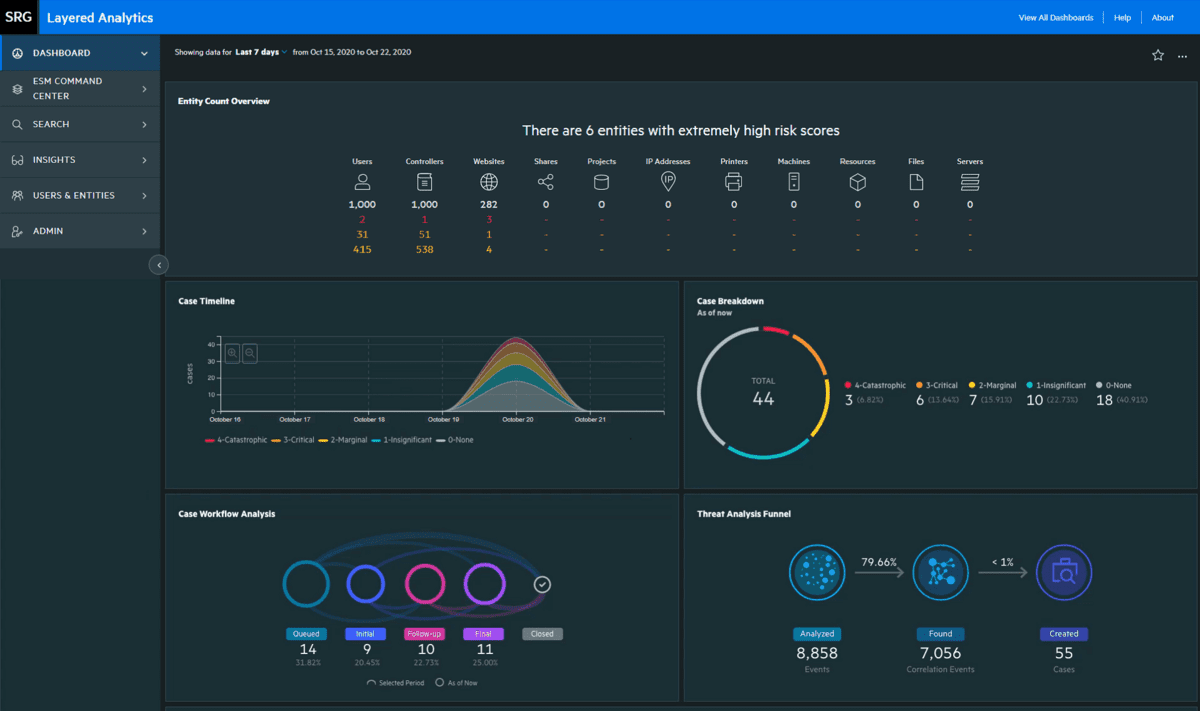
Figure 3: Siem Und Security-Analytics | SIEM vs Security Analytics: What’s the ... Information security threats come in many different forms. Some of the most common threats today are software attacks, theft of intellectual property, theft of identity, theft of equipment or information, sabotage, and information extortion. Viruses, worms, phishing attacks, and Trojan horses are a few common examples of software attacks. The theft of intellectual property has also been an extensive issue for many businesses. Identity theft is the attempt to act as someone else usually to obtain that person's personal information or to take advantage of their access to vital information through social engineering. Sabotage usually consists of the destruction of an organization's website in an attempt to cause loss of confidence on the part of its customers. Information extortion consists of theft of a company's property or information as an attempt to receive a payment in exchange for returning the information or property back to its owner, as with ransomware. One of the most functional precautions against these attacks is to conduct periodical user awareness. Governments, military, corporations, financial institutions, hospitals, non-profit organizations, and private businesses amass a great deal of confidential information about their employees, customers, products, research, and financial status. Should confidential information about a business's customers or finances or new product line fall into the hands of a competitor or hacker, a business and its customers could suffer widespread, irreparable financial loss, as well as damage to the company's reputation. From a business perspective, information security must be balanced against cost; the Gordon-Loeb Model provides a mathematical economic approach for addressing this concern. For the individual, information security has a significant effect on privacy, which is viewed very differently in various cultures.
The end of the twentieth century and the early years of the twenty-first century saw rapid advancements in telecommunications, computing hardware and software, and data encryption. The availability of smaller, more powerful, and less expensive computing equipment made electronic data processing within the reach of small business and home users. The establishment of Transfer Control Protocol/Internetwork Protocol (TCP/IP) in the early 1980s enabled different types of computers to communicate. These computers quickly became interconnected through the internet. The rapid growth and widespread use of electronic data processing and electronic business conducted through the internet, along with numerous occurrences of international terrorism, fueled the need for better methods of protecting the computers and the information they store, process, and transmit. The academic disciplines of computer security and information assurance emerged along with numerous professional organizations, all sharing the common goals of ensuring the security and reliability of information systems.
The "CIA triad" of confidentiality, integrity, and availability is at the heart of information security. The concept was introduced in the Anderson Report in 1972 and later repeated in The Protection of Information in Computer Systems. The abbreviation was coined by Steve Lipner around 1986. In information security, confidentiality "is the property, that information is not made available or disclosed to unauthorized individuals, entities, or processes." While similar to "privacy", the two words are not interchangeable. Rather, confidentiality is a component of privacy that is implemented to protect data from unauthorized viewers. Examples of confidentiality of electronic data being compromised include laptop theft, password theft, or sensitive emails being sent to the incorrect individuals. In IT security, data integrity means maintaining and assuring the accuracy and completeness of data. This means that data cannot be modified in an unauthorized or undetected manner. More broadly, integrity is an information security principle that involves human/social, process, and commercial integrity, as well as data integrity. As such it touches on aspects such as credibility, consistency, truthfulness, completeness, accuracy, timeliness, and assurance. For any information system to serve its purpose, the information must be available when it is needed. This means the computing systems used to store and process the information, the security controls used to protect it, and the communication channels used to access it must be functioning correctly. Ensuring availability may also involve preventing denial-of-service attacks, such as a flood of incoming messages to the target system, essentially forcing it to shut down. In addition to the classic CIA triad of security goals, some organisations may want to include security goals such as authenticity, accountability, non-repudiation, and reliability. The merits of the Parkerian Hexad are a subject of debate amongst security professionals.
Risk is the likelihood that something bad will happen that causes harm to an informational asset (or the loss of the asset). A vulnerability is a weakness that could be used to endanger or cause harm to an informational asset. A threat is anything (man-made or act of nature) that has the potential to cause harm. The likelihood that a threat will use a vulnerability to cause harm creates a risk. When a threat does use a vulnerability to inflict harm, it has an impact. In the context of information security, the impact is a loss of availability, integrity, and confidentiality, and possibly other losses (lost income, loss of life, loss of real property). The Certified Information Systems Auditor (CISA) Review Manual 2006 defines risk management as "the process of identifying vulnerabilities and threats to the information resources used by an organization in achieving business objectives, and deciding what countermeasures, if any, to take in reducing risk to an acceptable level, based on the value of the information resource to the organization." There are two things in this definition that may need some clarification.
First, the process of risk management is an ongoing, iterative process. It must be repeated indefinitely. The business environment is constantly changing and new threats and vulnerabilities emerge every day. Second, the choice of countermeasures (controls) used to manage risks must strike a balance between productivity, cost, effectiveness of the countermeasure, and the value of the informational asset being protected. Furthermore, these processes have limitations as security breaches are generally rare and emerge in a specific context which may not be easily duplicated. Thus, any process and countermeasure should itself be evaluated for vulnerabilities. It is not possible to identify all risks, nor is it possible to eliminate all risk. The remaining risk is called "residual risk". A risk assessment is carried out by a team of people who have knowledge of specific areas of the business. Membership of the team may vary over time as different parts of the business are assessed. The assessment may use a subjective qualitative analysis based on informed opinion, or where reliable dollar figures and historical information is available, the analysis may use quantitative analysis. Research has shown that the most vulnerable point in most information systems is the human user, operator, designer, or other human. The ISO/IEC 27002:2005 Code of practice for information security management recommends the following be examined during a risk assessment: security policy, organization of information security, asset management, human resources security, physical and environmental security, communications and operations management, access control, information systems acquisition, development, and maintenance, information security incident management, business continuity management regulatory compliance. In broad terms, the risk management process consists of: Identification of assets and estimating their value. Include: people, buildings, hardware, software, data (electronic, print, other), supplies. Conduct a threat assessment. Include: Acts of nature, acts of war, accidents, malicious acts originating from inside or outside the organization. Conduct a vulnerability assessment, and for each vulnerability, calculate the probability that it will be exploited. Evaluate policies, procedures, standards, training, physical security, quality control, technical security.
Calculate the impact that each threat would have on each asset. Use qualitative analysis or quantitative analysis. Identify, select and implement appropriate controls. Provide a proportional response. Consider productivity, cost effectiveness, and value of the asset. Evaluate the effectiveness of the control measures. Ensure the controls provide the required cost effective protection without discernible loss of productivity. For any given risk, management can choose to accept the risk based upon the relative low value of the asset, the relative low frequency of occurrence, and the relative low impact on the business. Or, leadership may choose to mitigate the risk by selecting and implementing appropriate control measures to reduce the risk. In some cases, the risk can be transferred to another business by buying insurance or outsourcing to another business. The reality of some risks may be disputed. In such cases leadership may choose to deny the risk.
Selecting and implementing proper security controls will initially help an organization bring down risk to acceptable levels. Control selection should follow and should be based on the risk assessment. Controls can vary in nature, but fundamentally they are ways of protecting the confidentiality, integrity or availability of information. ISO/IEC 27001 has defined controls in different areas. Organizations can implement additional controls according to requirement of the organization. ISO/IEC 27002 offers a guideline for organizational information security standards.
Defense in depth is a fundamental security philosophy that relies on overlapping security systems designed to maintain protection even if individual components fail. Rather than depending on a single security measure, it combines multiple layers of security controls both in the cloud and at network endpoints. This approach includes combinations like firewalls with intrusion-detection systems, email filtering services with desktop anti-virus, and cloud-based security alongside traditional network defenses. The concept can be implemented through three distinct layers of administrative, logical, and physical controls, or visualized as an onion model with data at the core, surrounded by people, network security, host-based security, and application security layers. The strategy emphasizes that security involves not just technology, but also people and processes working together, with real-time monitoring and response being crucial components.
In the business sector, labels such as: Public, Sensitive, Private, Confidential. In the government sector, labels such as: Unclassified, Unofficial, Protected, Confidential, Secret, Top Secret, and their non-English equivalents. In cross-sectoral formations, the Traffic Light Protocol, which consists of: White, Green, Amber, and Red. In the personal sector, one label such as Financial. This includes activities related to managing money, such as online banking. All employees in the organization, as well as business partners, must be trained on the classification schema and understand the required security controls and handling procedures for each classification. The classification of a particular information asset that has been assigned should be reviewed periodically to ensure the classification is still appropriate for the information and to ensure the security controls required by the classification are in place and are followed in their right procedures.
2. System Architecture & Core Working Principles Access to protected information must be restricted to people who are authorized to access the information. The computer programs, and in many cases the computers that process the information, must also be authorized. This requires that mechanisms be in place to control the access to protected information. The sophistication of the access control mechanisms should be in parity with the value of the information being protected; the more sensitive or valuable the information the stronger the control mechanisms need to be. The foundation on which access control mechanisms are built start with identification and authentication. Access control is generally considered in three steps: identification, authentication, and authorization.
Something one knows: things such as a PIN, a password, or one's mother's maiden name Something one has: a driver's license or a magnetic swipe card Something one is: biometrics, including palm prints, fingerprints, voice prints, and retina (eye) scans Strong authentication requires providing more than one type of authentication information (two-factor authentication). The username is the most common form of identification on computer systems today and the password is the most common form of authentication. Usernames and passwords have served their purpose, but they are increasingly inadequate. Usernames and passwords are slowly being replaced or supplemented with more sophisticated authentication mechanisms such as time-based one-time password algorithms.
Information security uses cryptography to transform usable information into a form that renders it unusable by anyone other than an authorized user; this process is called encryption. Information that has been encrypted (rendered unusable) can be transformed back into its original usable form by an authorized user who possesses the cryptographic key, through the process of decryption. Cryptography is used in information security to protect information from unauthorized or accidental disclosure while the information is in transit (either electronically or physically) and while information is in storage.
Cryptography provides information security with other useful applications as well, including improved authentication methods, message digests, digital signatures, non-repudiation, and encrypted network communications. Older, less secure applications such as Telnet and File Transfer Protocol (FTP) are slowly being replaced with more secure applications such as Secure Shell (SSH) that use encrypted network communications. Wireless communications can be encrypted using protocols such as WPA/WPA2 or the older (and less secure) WEP. Wired communications (such as ITUIT G.hn) are secured using AES for encryption and X.1035 for authentication and key exchange. Software applications such as GnuPG or PGP can be used to encrypt data files and email. Cryptography can introduce security problems when it is not implemented correctly.
Cryptographic solutions need to be implemented using industry-accepted solutions that have undergone rigorous peer review by independent experts in cryptography. The length and strength of the encryption key is also an important consideration. A key that is weak or too short will produce weak encryption. The keys used for encryption and decryption must be protected with the same degree of rigor as any other confidential information. They must be protected from unauthorized disclosure and destruction, and they must be available when needed. Public key infrastructure (PKI) solutions address many of the problems that surround key management.
"Due care are steps that are taken to show that a company has taken responsibility for the activities that take place within the corporation and has taken the necessary steps to help protect the company, its resources, and employees." And, [Due diligence are the] "continual activities that make sure the protection mechanisms are continually maintained and operational." Attention should be made to two important points in these definitions. First, in due care, steps are taken to show; this means that the steps can be verified, measured, or even produce tangible artifacts. Second, in due diligence, there are continual activities; this means that people are actually doing things to monitor and maintain the protection mechanisms, and these activities are ongoing. Organizations have a responsibility with practicing duty of care when applying information security. The Duty of Care Risk Analysis Standard (DoCRA) provides principles and practices for evaluating risk. It considers all parties that could be affected by those risks. DoCRA helps evaluate safeguards if they are appropriate in protecting others from harm while presenting a reasonable burden. With increased data breach litigation, companies must balance security controls, compliance, and its mission.
Computer security incident management is a specialized form of incident management focused on monitoring, detecting, and responding to security events on computers and networks in a predictable way. Organizations implement this through incident response plans (IRPs) that are activated when security breaches are detected. These plans typically involve an incident response team (IRT) with specialized skills in areas like penetration testing, computer forensics, and network security.
Change management is a formal process for directing and controlling alterations to the information processing environment. This includes alterations to desktop computers, the network, servers, and software. The objectives of change management are to reduce the risks posed by changes to the information processing environment and improve the stability and reliability of the processing environment as changes are made. It is not the objective of change management to prevent or hinder necessary changes from being implemented. Any change to the information processing environment introduces an element of risk. Even apparently simple changes can have unexpected effects. One of management's many responsibilities is the management of risk. Change management is a tool for managing the risks introduced by changes to the information processing environment. Part of the change management process ensures that changes are not implemented at inopportune times when they may disrupt critical business processes or interfere with other changes being implemented. Not every change needs to be managed. Some kinds of changes are a part of the everyday routine of information processing and adhere to a predefined procedure, which reduces the overall level of risk to the processing environment. Creating a new user account or deploying a new desktop computer are examples of changes that do not generally require change management. However, relocating user file shares, or upgrading the Email server pose a much higher level of risk to the processing environment and are not a normal everyday activity. The critical first steps in change management are (a) defining change (and communicating that definition) and (b) defining the scope of the change system. Change management is usually overseen by a change review board composed of representatives from key business areas, security, networking, systems administrators, database administration, application developers, desktop support, and the help desk. The tasks of the change review board can be facilitated with the use of automated work flow application. The responsibility of the change review board is to ensure the organization's documented change management procedures are followed. The change management process is as follows Request: Anyone can request a change. The person making the change request may or may not be the same person that performs the analysis or implements the change. When a request for change is received, it may undergo a preliminary review to determine if the requested change is compatible with the organizations business model and practices, and to determine the amount of resources needed to implement the change. Approve: Management runs the business and controls the allocation of resources therefore, management must approve requests for changes and assign a priority for every change. Management might choose to reject a change request if the change is not compatible with the business model, industry standards or best practices. Management might also choose to reject a change request if the change requires more resources than can be allocated for the change. Plan: Planning a change involves discovering the scope and impact of the proposed change; analyzing the complexity of the change; allocation of resources and, developing, testing, and documenting both implementation and back-out plans. Test: Every change must be tested in a safe test environment, which closely reflects the actual production environment, before the change is applied to the production environment. The backout plan must also be tested. Schedule: Part of the change review board's responsibility is to assist in the scheduling of changes by reviewing the proposed implementation date for potential conflicts with other scheduled changes or critical business activities.
Communicate: Once a change has been scheduled it must be communicated. The communication is to give others the opportunity to remind the change review board about other changes or critical business activities that might have been overlooked when scheduling the change. The communication also serves to make the help desk and users aware that a change is about to occur. Another responsibility of the change review board is to ensure that scheduled changes have been properly communicated to those who will be affected by the change or otherwise have an interest in the change. Implement: At the appointed date and time, the changes must be implemented. Part of the planning process was to develop an implementation plan, testing plan and, a back out plan. If the implementation of the change should fail or, the post implementation testing fails or, other "drop dead" criteria have been met, the back out plan should be implemented.
Document: All changes must be documented. The documentation includes the initial request for change, its approval, the priority assigned to it, the implementation, testing and back out plans, the results of the change review board critique, the date/time the change was implemented, who implemented it, and whether the change was implemented successfully, failed or postponed. Post-change review: The change review board should hold a post-implementation review of changes. It is particularly important to review failed and backed out changes. The review board should try to understand the problems that were encountered, and look for areas for improvement. Change management procedures that are simple to follow and easy to use can greatly reduce the overall risks created when changes are made to the information processing environment. Good change management procedures improve the overall quality and success of changes as they are implemented. This is accomplished through planning, peer review, documentation, and communication.
Business continuity management (BCM) concerns arrangements aiming to protect an organization's critical business functions from interruption due to incidents, or at least minimize the effects. BCM is essential to any organization to keep technology and business in line with current threats to the continuation of business as usual. The BCM should be included in an organizations risk analysis plan to ensure that all of the necessary business functions have what they need to keep going in the event of any type of threat to any business function. It encompasses: Analysis of requirements, e.g., identifying critical business functions, dependencies and potential failure points, potential threats and hence incidents or risks of concern to the organization; Architecture and design, e.g., an appropriate combination of approaches including resilience (e.g. engineering IT systems and processes for high availability, avoiding or preventing situations that might interrupt the business), incident and emergency management (e.g., evacuating premises, calling the emergency services, triage/situation assessment and invoking recovery plans), recovery (e.g., rebuilding) and contingency management (generic capabilities to deal positively with whatever occurs using whatever resources are available); Implementation, e.g., configuring and scheduling backups, data transfers, etc., duplicating and strengthening critical elements; contracting with service and equipment suppliers; Testing, e.g., business continuity exercises of various types, costs and assurance levels; Management, e.g., defining strategies, setting objectives and goals; planning and directing the work; allocating funds, people and other resources; prioritization relative to other activities; team building, leadership, control, motivation and coordination with other business functions and activities (e.g., IT, facilities, human resources, risk management, information risk and security, operations); monitoring the situation, checking and updating the arrangements when things change; maturing the approach through continuous improvement, learning and appropriate investment; Assurance, e.g., testing against specified requirements; measuring, analyzing, and reporting key parameters; conducting additional tests, reviews and audits for greater confidence that the arrangements will go to plan if invoked. Whereas BCM takes a broad approach to minimizing disaster-related risks by reducing both the probability and the severity of incidents, a disaster recovery plan (DRP) focuses specifically on resuming business operations as quickly as possible after a disaster. A disaster recovery plan, invoked soon after a disaster occurs, lays out the steps necessary to recover critical information and communications technology (ICT) infrastructure. Disaster recovery planning includes establishing a planning group, performing risk assessment, establishing priorities, developing recovery strategies, preparing inventories and documentation of the plan, developing verification criteria and procedure, and lastly implementing the plan.
Below is a partial listing of governmental laws and regulations in various parts of the world that have, had, or will have, a significant effect on data processing and information security. Important industry sector regulations have also been included when they have a significant impact on information security. The UK Data Protection Act 1998 makes new provisions for the regulation of the processing of information relating to individuals, including the obtaining, holding, use or disclosure of such information. The European Union Data Protection Directive (EUDPD) requires that all E.U. members adopt national regulations to standardize the protection of data privacy for citizens throughout the E.U. The Computer Misuse Act 1990 is an Act of the U.K. Parliament making computer crime (e.g., hacking) a criminal offense. The act has become a model upon which several other countries, including Canada and Ireland, have drawn inspiration from when subsequently drafting their own information security laws. The E.U.'s Data Retention Directive (annulled) required internet service providers and phone companies to keep data on every electronic message sent and phone call made for between six months and two years. The Family Educational Rights and Privacy Act (FERPA) (20 U.S.C. § 1232 g; 34 CFR Part 99) is a U.S. Federal law that protects the privacy of student education records. The law applies to all schools that receive funds under an applicable program of the U.S. Department of Education. Generally, schools must have written permission from the parent or eligible student in order to release any information from a student's education record. The Federal Financial Institutions Examination Council's (FFIEC) security guidelines for auditors specifies requirements for online banking security. The Health Insurance Portability and Accountability Act (HIPAA) of 1996 requires the adoption of national standards for electronic health care transactions and national identifiers for providers, health insurance plans, and employers. Additionally, it requires health care providers, insurance providers and employers to safeguard the security and privacy of health data. The Gramm–Leach–Bliley Act of 1999 (GLBA), also known as the Financial Services Modernization Act of 1999, protects the privacy and security of private financial information that financial institutions collect, hold, and process. Section 404 of the Sarbanes–Oxley Act of 2002 (SOX) requires publicly traded companies to assess the effectiveness of their internal controls for financial reporting in annual reports they submit at the end of each fiscal year. Chief information officers are responsible for the security, accuracy, and the reliability of the systems that manage and report the financial data. The act also requires publicly traded companies to engage with independent auditors who must attest to, and report on, the validity of their assessments. The Payment Card Industry Data Security Standard (PCI DSS) establishes comprehensive requirements for enhancing payment account data security. It was developed by the founding payment brands of the PCI Security Standards Council — including American Express, Discover Financial Services, JCB, MasterCard Worldwide, and Visa International — to help facilitate the broad adoption of consistent data security measures on a global basis. The PCI DSS is a multifaceted security standard that includes requirements for security management, policies, procedures, network architecture, software design, and other critical protective measures. State security breach notification laws (California and many others) require businesses, nonprofits, and state institutions to notify consumers when unencrypted "personal information" may have been compromised, lost, or stolen. The Personal Information Protection and Electronics Document Act (PIPEDA) of Canada supports and promotes electronic commerce by protecting personal information that is collected, used or disclosed in certain circumstances, by providing for the use of electronic means to communicate or record information or transactions and by amending the Canada Evidence Act, the Statutory Instruments Act and the Statute Revision Act. Greece's Hellenic Authority for Communication Security and Privacy (ADAE) (Law 165/2011) establishes and describes the minimum information security controls that should be deployed by every company which provides electronic communication networks and/or services in Greece in order to protect customers' confidentiality. These include both managerial and technical controls (e.g., log records should be stored for two years). Greece's Hellenic Authority for Communication Security and Privacy (ADAE) (Law 205/2013) concentrates around the protection of the integrity and availability of the services and data offered by Greek telecommunication companies. The law forces these and other related companies to build, deploy, and test appropriate business continuity plans and redundant infrastructures. The US Department of Defense (DoD) issued DoD Directive 8570 in 2004, supplemented by DoD Directive 8140, requiring all DoD employees and all DoD contract personnel involved in information assurance roles and activities to earn and maintain various industry Information Technology (IT) certifications in an effort to ensure that all DoD personnel involved in network infrastructure defense have minimum levels of IT industry recognized knowledge, skills and abilities (KSA). Andersson and Reimers (2019) report these certifications range from CompTIA's A+ and Security+ through the ICS2.org's CISSP, etc.
Attitudes: employees' feelings and emotions about the various activities that pertain to the organizational security of information. Behaviors: actual or intended activities and risk-taking actions of employees that have direct or indirect impact on information security. Cognition: employees' awareness, verifiable knowledge, and beliefs regarding practices, activities, and self-efficacy relation that are related to information security. Communication: ways employees communicate with each other, sense of belonging, support for security issues, and incident reporting. Compliance: adherence to organizational security policies, awareness of the existence of such policies and the ability to recall the substance of such policies. Norms: perceptions of security-related organizational conduct and practices that are informally deemed either normal or deviant by employees and their peers, e.g. hidden expectations regarding security behaviors and unwritten rules regarding uses of information-communication technologies. Responsibilities: employees' understanding of the roles and responsibilities they have as a critical factor in sustaining or endangering the security of information, and thereby the organization. Andersson and Reimers (2014) found that employees often do not see themselves as part of the organization Information Security "effort" and often take actions that ignore organizational information security best interests. Research shows information security culture needs to be improved continuously. In Information Security Culture from Analysis to Change, authors commented, "It's a never ending process, a cycle of evaluation and change or maintenance." To manage the information security culture, five steps should be taken: pre-evaluation, strategic planning, operative planning, implementation, and post-evaluation.
Pre-evaluation: to identify the awareness of information security within employees and to analyze current security policy Strategic planning: to come up a better awareness-program, we need to set clear targets. Clustering people is helpful to achieve it Operative planning: create a good security culture based on internal communication, management buy-in, security awareness, and training programs Implementation: should feature commitment of management, communication with organizational members, courses for all organizational members, and commitment of the employees Post-evaluation: to better gauge the effectiveness of the prior steps and build on continuous improvement DoD IA Policy Chart Archived 2011-09-06 at the Wayback Machine on the DoD Information Assurance Technology Analysis Center web site. patterns & practices Security Engineering Explained IWS – Information Security Chapter Archived 2019-11-08 at the Wayback Machine Ross Anderson's book "Security Engineering" Security information and event management (SIEM) deployment involves setting up and configuring a system to aggregate security event logs across an organization’s infrastructure.
Security information and event management (SIEM) is integral to the current trend in modern cybersecurity, assisting an organization in maintaining a platform to collect, analyze, and respond to real-time security threats. This, in turn, mandates detailed planning in terms of infrastructure integration as well as deploying the best measures for ongoing management. The following section elucidates the optimal procedure to undertake the proper SIEM deployment as well as guidelines for performance improvement.
The process for the deployment of SIEM involves setting up and configuring a system that would collect security event logs within the infrastructure of an organization. SIEM tools correlate such events, give real-time monitoring, and allow immediate detection of a potential threat by security teams. This highlights all aspects of a network for potential anomalies that might indicate cyberattacks or breaches.
Organizations must decide whether to deploy SIEM on-premises or to use a cloud-based solution. Both approaches have distinct advantages and drawbacks: To ensure a smooth deployment, it’s crucial to assess the organization’s infrastructure needs. Both on-prem and cloud-based SIEMs require the following considerations: 3. Software Implementation, Frameworks & Protocols Effective SIEM deployment begins with detailed planning. Organizations should take the following steps: Preparation is key to a successful deployment. Organizations should follow these steps: A successful SIEM deployment is not a “set it and forget it” process. It needs to be maintained constantly to be effective. After the SIEM system has been deployed, follow these best practices to keep it current: Target threats in real time and streamline day-to-day operations with the world’s most advanced AI SIEM from SentinelOne.
It is a daunting yet essential task for any serious organization looking to secure its cybersecurity through the installation of an SIEM solution. Right planning, cautious implementation, and subsequent support are what make all the difference, ensuring that SIEM delivers real-time detection, effective responses, and response to threats as promised. Efficiency is maximized when organizations start small and use adequate data collection while updating the rules about threat detection regularly.
On-prem SIEM has better control but requires a lot of infrastructure. Cloud-based SIEM is scalable and much easier to manage since the provider handles updates and maintenance. The time required to deploy will depend on the size and complexity of an organization. Smaller deployments might take only a week or two, while large or complex infrastructures may take months.
SIEM should integrate data from firewalls, intrusion detection/prevention systems, servers, endpoint protection tools, and application logs to provide comprehensive coverage. Policies, use cases, and threat intelligence feeds must change with the changing threats. We need to continue to monitor performance and train the staff continually.
One way you might avoid false positives is by tweaking alert thresholds, and correlation rules, and including threat intelligence. The only way you’d truly be able to keep accuracy would be to review and adjust those settings constantly. A cloud SIEM ( Security Information and Event Management ) is a cloud-based platform that helps organizations collect, monitor, and analyze security data to identify and respond to threats in real time. It’s a security solution delivered as a service, offering centralized monitoring, analysis, and management of security events across an organization’s IT infrastructure.
Unlike traditional SIEMs that require on-premises hardware and software, cloud SIEMs leverage the scalability and flexibility of cloud environments. An example of a cloud SIEM is Exabeam New-Scale SIEM. Cloud-native SIEM also takes advantage of the speed and economies of scale to grow and take advantage of innovations without disruption.
Organizations can leverage cloud SIEM technology to gain better visibility into distributed workloads. Cloud SIEM can help monitor all assets, including servers, devices, infrastructure components, and users connected to the network — through a single cloud-based dashboard. Cloud SIEM offers faster deployment and easier scalability compared to traditional on-premises SIEMs. Organizations can begin ingesting and analyzing data almost immediately without provisioning hardware or performing complex setups.
Its centralized visibility enables security teams to monitor hybrid and multi-cloud environments from a single interface. This unified view helps detect lateral movement, data exfiltration, and identity-based threats more effectively. Cloud SIEM platforms also reduce the burden of infrastructure maintenance. Providers handle updates, uptime, and performance optimization, freeing internal teams to focus on threat analysis and response.
Additionally, modern cloud SIEMs integrate with a wide range of data sources and threat intelligence feeds. This extensibility supports faster correlation of events, improved detection accuracy, and automation of incident response workflows. Cloud SIEM can help organizations to centralize event data from multiple sources, including on-premises and cloud assets. This is especially beneficial for hybrid deployments, which need to combine information on activities and events occurring in multiple data centers.
In this model, the organization is responsible for deploying and managing the SIEM software on its own cloud infrastructure. The SIEM platform may be installed on a public cloud like AWS, Azure, or Google Cloud but remains under the control of the customer. This setup provides flexibility and customization. Organizations can tailor integrations, policies, and analytics pipelines to their specific needs. However, it also requires in-house expertise for managing scalability, availability, and security, which can increase operational complexity and cost.
4. Practical Deployment, Analysis & Case Studies Cloud-hosted SIEM refers to traditional SIEM software that vendors offer as a hosted service in the cloud. The core platform is managed and maintained by the vendor, but the architecture is typically a lift-and-shift of on-premises systems rather than re-engineered for the cloud.
This model offers some benefits of cloud — such as reduced hardware dependency and easier access — but may lack the elasticity, integration depth, and automation capabilities found in cloud-native SIEM solutions. Performance and scaling can still depend on older architectural constraints. A cloud-native SIEM is built from the ground up for cloud environments. It uses cloud-native technologies such as containerization, serverless processing, and scalable storage, and is designed to handle modern data velocity, volume, and variety.
These platforms are highly scalable, offer built-in integrations with cloud services, and often include advanced analytics, machine learning, and automation. Cloud-native SIEMs are ideal for organizations with dynamic, hybrid, or multi-cloud workloads that need real-time insights without infrastructure overhead. This deployment model involves outsourcing the operation and monitoring of a cloud SIEM platform to a managed security service provider (MSSP). The provider handles setup, tuning, threat detection, and even incident response depending on the service level agreement.
Managed service models are attractive for organizations with limited security staff or expertise. They offer rapid deployment and 24/7 coverage, but may reduce visibility or control over configurations, requiring careful coordination with the MSSP. When you implement SIEM, you can deploy the solution in the cloud or on-premises. A cloud solution provider will manage the provisioning and often help with initial configuration — or offer expert professional services to speed deployment — which allows you to start operations immediately. An on-premises implementation requires in-house installation and configuration, so it will likely be longer until you can start using it. Some final advantages of cloud-native SIEMs are faster updates, fewer limits to storage (and thus lower long-term storage costs), and lower total cost of ownership.
In-house IT teams can be short on staff (two-thirds of companies have an IT skills shortage), so it is important to consider giving in-house teams fewer responsibilities because IT teams may be short staffed. A cloud SIEM, especially from a managed service provider, allows you to outsource expertise to maintain security. Your required level of control over SIEM and log data is another important consideration. An on-premises implementation like LogRhythm typically offers deep visibility, robust customization, and greater control, which can be critical for highly regulated industries or environments handling restricted or sensitive data. However, the maintenance and start up costs are higher and may be out of reach for smaller organizations seeking rapid deployment or cloud-native scalability.
The overall cost of implementation can vary widely for cloud SIEM, as there are lower upfront costs, but ongoing subscription and per-usage costs. This enables scalability but can be less cost effective for consistently resource-hungry workloads. On-premises SIEM tends to have higher upfront costs, with the technical debt paid over time. However, upgrades and expansions can also add to costs, as they require installing additional hardware and downtime for upgrades.
There are several practices that organizations should consider when working with a cloud SIEM. When choosing a cloud SIEM solution, prioritize platforms built natively for the cloud rather than traditional systems retrofitted into hosted environments. Cloud-native SIEMs are designed to integrate deeply with cloud service providers like AWS, Azure, and Google Cloud using their native APIs, event sources, and identity systems.
This native integration allows the SIEM to ingest and process logs from services such as AWS CloudTrail, Azure Monitor, and Google Cloud Audit Logs with minimal configuration. It also enables support for ephemeral resources, such as containers and serverless functions, that traditional SIEMs struggle to track. A cloud-native SIEM automatically adapts to dynamic cloud workloads, ensuring that telemetry coverage scales as infrastructure changes.
Strong integration also supports fine-grained access control, making it easier to enforce least-privilege policies and improve monitoring of account-level activity, IAM role assumptions, and API usage. The result is faster setup, greater visibility, and more relevant detection capabilities across hybrid and multi-cloud environments. Effective detection depends on aligning SIEM rules and use cases with your organization’s unique threat landscape and business context. While most SIEMs come with default rule sets, these are often too generic to provide meaningful coverage out of the box.
Start by assessing your organization’s specific risks, such as targeted threat actors, compliance obligations, or technology stack. Use this analysis to build custom detection logic tailored to real-world attack scenarios, such as privilege escalation attempts in cloud IAM, unusual data access in SaaS applications, or lateral movement across hybrid networks. Regularly tune and test detection rules using threat intelligence feeds, red team exercises, and past incident data. Use thresholds, correlation logic, and context enrichment to reduce false positives and prioritize the most critical alerts. Maintain a feedback loop where SOC analysts document rule performance and suggest improvements.
Create use-case libraries that map alerts to known MITRE ATT&CK techniques, regulatory controls, and operational risk categories. This structured approach improves coverage, response prioritization, and auditability. Cloud SIEMs often include or integrate with SOAR platforms, enabling security teams to automate detection-to-response workflows. Automation is critical for reducing mean time to respond (MTTR), especially when dealing with high alert volumes and limited staff.
Begin by identifying common, high-volume incident types that are well-suited for automation — such as brute-force attacks, phishing emails, or malware alerts. Build response playbooks that automate repetitive tasks like enrichment (e.g., IP reputation checks), stakeholder notification, ticket creation, and even containment actions like disabling user accounts or blocking network traffic.
Use conditional logic and approval workflows to strike a balance between full automation and analyst oversight. For example, you might automate triage and enrichment steps but require manual approval before isolating a host. 5. Performance Evaluation & Extended Technical Observations Document all automated actions and provide transparency through dashboards and audit logs. Regularly review workflow performance, refine playbooks based on incident outcomes, and extend automation coverage incrementally. A mature automation strategy improves consistency, reduces analyst burnout, and accelerates incident resolution.
Cloud SIEMs play a key role in helping organizations meet security and privacy regulations by centralizing visibility, enforcing policy controls, and generating audit evidence. To ensure compliance, configure the SIEM to collect and retain all relevant logs, including authentication activity, data access events, and configuration changes. Set up role-based access controls (RBAC) to restrict log access and administrative functions. Use tamper-proof storage options and digital signatures to ensure the integrity of log data. Many SIEMs support compliance modules or templates for standards such as PCI-DSS, HIPAA, SOC 2, and ISO 27001. Leverage these templates to align configurations and generate audit-ready reports.
Schedule periodic compliance assessments and integrate your SIEM with governance, risk, and compliance (GRC) tools to automate evidence collection and control mapping. Maintain continuous monitoring for misconfigurations, unauthorized changes, or suspicious behavior that could indicate policy violations. New-Scale SIEM is a next-generation AI-driven security operations platform that unifies threat detection, investigation, and response (TDIR) into one intuitive solution security teams actually want to use. By combining behavioral analytics, automation, and open integrations, it closes the SIEM effectiveness gap and delivers limitless scale to ingest, parse, store, search, and report on petabytes of data from anywhere. Pre-built with hundreds of integrations and the ability to onboard new log sources in minutes, it helps analysts work smarter by reducing alert fatigue by up to 60% and cutting investigation times by as much as 80%. With more than 100 pre-built correlation rules, integrated threat intelligence, and AI-assisted timelines that surface critical incidents faster, security teams can detect and respond to 90% of insider threats before other vendors can catch them while lowering total cost of ownership by up to 35%.
The platform includes Exabeam Nova, a collection of six specialized AI agents embedded across the Exabeam New-Scale SIEM and Security Log Management products. These agents work alongside security analysts to automate complex tasks, accelerate investigations, and improve detection accuracy. From natural language search and automated visualizations to correlation rule building, incident triage, and executive-ready security posture reporting, Nova brings speed, precision, and consistency to every stage of threat detection, investigation, and response.For more information on the cutting edge changes in the SIEM space, we recommend watching this webcast called Agentic AI – Reimagine Threat Detection, Investigation, and Response .
Learn about the Exabeam platform and expand your knowledge of information security with our collection of white papers, podcasts, webinars, and more. In 2023, there were 2,365 cyberattacks that affected over 343 million people. The numbers keep climbing. If you're starting a Security Information and Event Management (SIEM) implementation, you're making the right call.
SIEM has been around since the early 2000s and has become a core part of any serious cybersecurity program. It handles real-time event monitoring, pattern analysis, compliance tracking, and reporting. But it only works if you set it up correctly. This SIEM implementation guide walks through the key steps, from understanding the basics to avoiding the mistakes that trip up most organizations.
Before you start, you need to know what SIEM actually does. At its core, SIEM collects and aggregates log data from across your tech infrastructure (servers, applications, network devices) and gives you a single view of your security information. It analyzes security alerts in real time to detect threats. That centralized view is what makes it useful. Instead of checking logs from dozens of systems individually, SIEM pulls everything together so you can spot patterns: repeated failed logins, unusual data transfers, access from unexpected locations. The correlation engine connects events across different systems to flag activity that might indicate a breach.
SIEM also generates the compliance reports that auditors ask for. It tracks who accessed what, when, and from where. When paired with a managed security operations center for 24/7 coverage, the combination gives your team continuous threat detection without needing to staff a security desk around the clock. Understanding these basics will help you set realistic expectations for what SIEM can and can't do before you start buying tools.
Picking the right SIEM tool comes down to matching features to your actual needs and budget. Don't overbuy. Don't underbuy. Start by looking at what your organization actually requires. When you're evaluating SIEM tools, focus on three areas: log collection, threat detection, and scalability. Correlation capabilities matter most. A good SIEM tool connects events across different data sources to identify threats that would look harmless in isolation. Test how well each tool handles this before you commit.
Compliance reporting is the other piece. Your SIEM should generate the reports you need for SOC 2, HIPAA, or whatever frameworks apply to your business. If you're spending hours manually pulling compliance data, the tool isn't doing its job. Look at the total cost of ownership, not just the sticker price. That means initial setup, licensing fees, and ongoing maintenance. A cheaper tool that requires two full-time analysts to manage isn't actually cheaper.
Compare each tool's threat detection depth, user behavior analytics, and how well it plugs into your existing security stack. Poor integration means data gaps, and data gaps mean missed threats. Check the vendor's track record on updates and support response times. SIEM tools that fall behind on patches become liabilities.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Security%20information%20and%20event%20management • https://en.wikipedia.org/wiki/Cloud%20computing%20security • https://en.wikipedia.org/wiki/Information%20security • https://www.sentinelone.com/cybersecurity-101/data-and-ai/siem-deployment/ • https://www.exabeam.com/explainers/new-scale-siem/cloud-siem-features-capabilities-and-advantages/ • https://www.networkright.com/blog/siem-implementation
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Cloud Based Security Information And Event Management Tool.
[*] Metasploit Scan Running on Target Subnet for Cloud Based Security Information And Event Management Tool... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |