Complete Technical Paper Content — Cloud Distributed Denial Of Service Mitigation System
Overview & System Context
Cloud Distributed Denial Of Service Mitigation System: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9617 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background In computing, a denial-of-service attack (DoS attack doss) is a cyberattack in which the perpetrator seeks to make a machine or network resource unavailable to its intended users by temporarily or indefinitely disrupting services of a host connected to a network. Denial of service is typically accomplished by flooding the targeted machine or resource with superfluous requests in an attempt to overload systems and prevent some or all legitimate requests from being fulfilled. The range of attacks varies widely, spanning from inundating a server with millions of requests to slow its performance or with a substantial amount of invalid data, to submitting requests with an illegitimate IP address, and launching "low and slow" attacks aimed at keeping connections open. In a distributed denial-of-service attack (DDoS attack DEE-doss), the incoming traffic flooding the victim originates from many different sources. More sophisticated strategies are required to mitigate this type of attack; simply attempting to block a single source is insufficient. A DDoS attack is analogous to a group of people crowding the entry door of a shop, making it hard for legitimate customers to enter, thus disrupting trade and losing the business money. Criminal perpetrators of DDoS attacks often target sites or services hosted on high-profile web servers such as banks or credit card payment gateways. Revenge and blackmail, as well as hacktivism, can motivate these attacks.
advanced reconnaissance (pre-attack OSINT and extensive decoyed scanning crafted to evade detection over long periods) tactical execution (attack with both primary and secondary victims but the focus is on primary) explicit motivation (a calculated end game/goal target) large computing capacity (access to substantial computer power and network bandwidth) simultaneous multi-threaded OSI layer attacks (sophisticated tools operating at layers 3 through 7) persistence over extended periods (combining all the above into a concerted, well-managed attack across a range of targets).
Some vendors provide so-called booter or stresser services, which have simple web-based front ends, and accept payment over the web. Marketed and promoted as stress-testing tools, they can be used to perform unauthorized denial-of-service attacks, and allow technically unsophisticated attackers access to sophisticated attack tools. Usually powered by a botnet, the traffic produced by a consumer stresser can range anywhere from 5-50 Gbit/s, which can, in most cases, deny the average home user internet access.
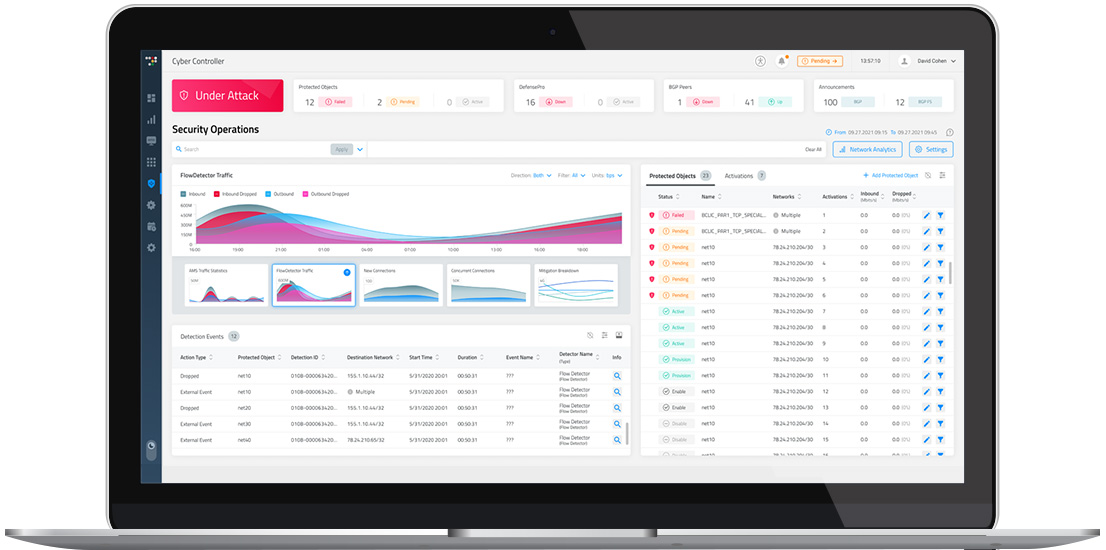
unusually slow network performance (opening files or accessing websites), unavailability of a particular website, or inability to access any website. Figure 1: Advanced DDoS Defense and Attack Mitigation | DefensePro Attackers have found a way to exploit a number of bugs in peer-to-peer servers to initiate DDoS attacks. The most aggressive of these peer-to-peer-DDoS attacks exploits the DC++ file sharing network. With peer-to-peer attacks there is no botnet and the attacker does not have to communicate with the clients it subverts. Instead, the attacker acts as a puppet master, instructing clients of large peer-to-peer file sharing hubs to disconnect from their peer-to-peer network and to connect to the victim's website instead.
DNS amplification attacks involves an attacker sending a DNS name lookup request to one or more public DNS servers, spoofing the source IP address of the targeted victim. The attacker tries to request as much information as possible, thus amplifying the DNS response that is sent to the targeted victim. Since the size of the request is significantly smaller than the response, the attacker is easily able to increase the amount of traffic directed at the target. Simple Network Management Protocol (SNMP) and Network Time Protocol (NTP) can also be exploited as reflectors in an amplification attack. An example of an amplified DDoS attack through the NTP is through a command called monlist, which sends the details of the last 600 hosts that have requested the time from the NTP server back to the requester. A small request to this time server can be sent using a spoofed source IP address of some victim, which results in a response 556.9 times the size of the request being sent to the victim. This becomes amplified when using botnets that all send requests with the same spoofed IP source, which will result in a massive amount of data being sent back to the victim. It is very difficult to defend against these types of attacks because the response data is coming from legitimate servers. These attack requests are also sent through UDP, which does not require a connection to the server. This means that the source IP is not verified when a request is received by the server.
To bring awareness of these vulnerabilities, campaigns have been started that are dedicated to finding amplification vectors which have led to people fixing their resolvers or having the resolvers shut down completely. A teardrop attack involves sending mangled IP fragments with overlapping, oversized payloads to the target machine. This can crash various operating systems because of a bug in their TCP/IP fragmentation re-assembly code. Windows 3.1x, Windows 95 and Windows NT operating systems, as well as versions of Linux before versions 2.0.32 and 2.1.63 are vulnerable to this attack. One of the fields in an IP header is the fragment offset field, indicating the starting position, or offset, of the data contained in a fragmented packet relative to the data in the original packet. If the sum of the offset and size of one fragmented packet differs from that of the next fragmented packet, the packets overlap. When this happens, a server vulnerable to teardrop attacks is unable to reassemble the packets resulting in a denial-of-service condition.
A scammer contacts the victim's banker or broker, impersonating the victim to request a funds transfer. The banker's attempt to contact the victim for verification of the transfer fails as the victim's telephone lines are being flooded with bogus calls, rendering the victim unreachable. A scammer contacts consumers with a bogus claim to collect an outstanding payday loan for thousands of dollars. When the consumer objects, the scammer retaliates by flooding the victim's employer with automated calls. In some cases, the displayed caller ID is spoofed to impersonate police or law enforcement agencies. Swatting: A scammer contacts consumers with a bogus debt collection demand and threatens to send police; when the victim balks, the scammer floods local police numbers with calls on which caller ID is spoofed to display the victim's number. Police soon arrive at the victim's residence attempting to find the origin of the calls. TDoS can exist even without Internet telephony. In the 2002 New Hampshire Senate election phone jamming scandal, telemarketers were used to flood political opponents with spurious calls to jam phone banks on election day. Widespread publication of a number can also flood it with enough calls to render it unusable, as happened by accident in 1981 with multiple +1-area code-867-5309 subscribers inundated by hundreds of calls daily in response to the song "867-5309/Jenny". TDoS differs from other telephone harassment (such as prank calls and obscene phone calls) by the number of calls originated. By occupying lines continuously with repeated automated calls, the victim is prevented from making or receiving both routine and emergency telephone calls. Related exploits include SMS flooding attacks and black fax or continuous fax transmission by using a loop of paper at the sender.
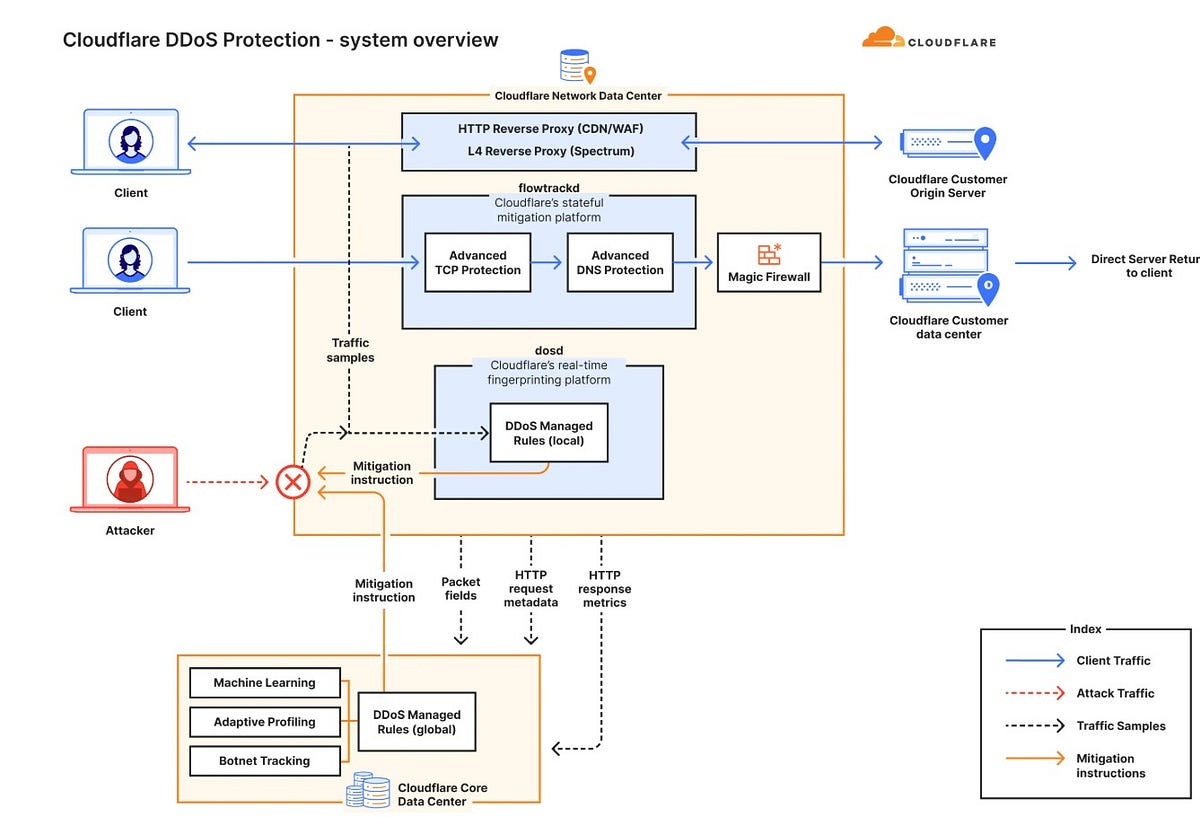
Figure 2: Disributed denial-of-service attacks — A deeper walkthrough | by ... Defensive responses to denial-of-service attacks typically involve the use of a combination of attack detection, traffic classification and response tools, aiming to block traffic the tools identify as illegitimate and allow traffic that they identify as legitimate. A list of response tools include the following.
In computer network security, backscatter is a side-effect of a spoofed denial-of-service attack. In this kind of attack, the attacker spoofs the source address in IP packets sent to the victim. In general, the victim machine cannot distinguish between the spoofed packets and legitimate packets, so the victim responds to the spoofed packets as it normally would. These response packets are known as backscatter. If the attacker is spoofing source addresses randomly, the backscatter response packets from the victim will be sent back to random destinations. This effect can be used by network telescopes as indirect evidence of such attacks. The term backscatter analysis refers to observing backscatter packets arriving at a statistically significant portion of the IP address space to determine the characteristics of DoS attacks and victims.
Many jurisdictions have laws under which denial-of-service attacks are illegal. UNCTAD highlights that 156 countries, or 80% globally, have enacted cybercrime laws to combat its widespread impact. Adoption rates vary by region, with Europe at a 91% rate, and Africa at 72%. In the US, denial-of-service attacks may be considered a federal crime under the Computer Fraud and Abuse Act with penalties that include years of imprisonment. The Computer Crime and Intellectual Property Section of the US Department of Justice handles cases of DoS and DDoS. In one example, in July 2019, Austin Thompson, aka DerpTrolling, was sentenced to 27 months in prison and $95,000 in restitution by a federal court for conducting multiple DDoS attacks on major video gaming companies, disrupting their systems for hours to days. In European countries, committing criminal denial-of-service attacks may, as a minimum, lead to arrest. The United Kingdom is unusual in that it specifically outlawed denial-of-service attacks and set a maximum penalty of 10 years in prison with the Police and Justice Act 2006, which amended Section 3 of the Computer Misuse Act 1990. In January 2019, Europol announced that "actions are currently underway worldwide to track down the users" of Webstresser.org, a former DDoS marketplace that was shut down in April 2018 as part of Operation PowerOFF. Europol said UK police were conducting a number of "live operations" targeting over 250 users of Webstresser and other DDoS services. On January 7, 2013, Anonymous posted a petition on the whitehouse.gov site asking that DDoS be recognized as a legal form of protest similar to the Occupy movement, the claim being that the similarity in the purpose of both is same.
DDoS mitigation is a set of network management techniques and tools for resisting or mitigating the impact of distributed denial-of-service (DDoS) attacks on networks attached to the Internet by protecting the target and relay networks. DDoS attacks are a constant threat to businesses and organizations, delaying service performance or shutting down websites entirely. DDoS mitigation works by identifying baseline conditions for network traffic by analyzing "traffic patterns" to allow threat detection and alerting. DDoS mitigation also requires identifying incoming traffic to separate human traffic from human-like bots and hijacked web browsers. This process involves comparing signatures and examining different attributes of the traffic, including IP addresses, cookie variations, HTTP headers, and browser fingerprints. After the attack is detected, the next process is filtering. Filtering can be done through anti-DDoS technology like connection tracking, IP reputation lists, deep packet inspection, blacklisting/whitelisting, or rate limiting. One technique is to pass network traffic addressed to a potential target network through high-capacity networks, with "traffic scrubbing" filters. Manual DDoS mitigation is no longer recommended due to the size of attacks often outstripping the human resources available in many firms/organizations. Other methods to prevent DDoS attacks can be implemented such as on-premises or cloud-based solution providers. On-premises mitigation technology (most commonly a hardware device) is often placed in front of the network. This would limit the maximum bandwidth available to what is provided by the Internet service provider. Common methods involve hybrid solutions, by combining on-premises filtering with cloud-based solutions.
Figure 3: Comprehensive Approaches for Detecting and Mitigating Distributed ... UDP floods target random ports with UDP packets, causing the host to repeatedly search for non-existent applications and reply with ICMP errors. ICMP floods overwhelm the target with ping requests, exhausting available processing power and bandwidth. DNS amplification involves exploiting open DNS resolvers to send amplified traffic to the victim using spoofed requests. Protocol attacks These focus on exhausting resources of network infrastructure by misusing communication protocol behavior.
SYN floods exploit the TCP handshake by initiating multiple half-open connections, overwhelming the server's connection table. Ping of Death uses oversized or malformed ping packets to crash or destabilize systems. Smurf attacks send spoofed ICMP requests to broadcast addresses, prompting all devices on the network to respond to the victim’s IP. Application layer attacks These attacks mimic legitimate traffic to deplete application server resources, making them particularly difficult to detect.
HTTP floods send large numbers of GET or POST requests, overloading servers with processing demands. Slowloris maintains many open connections to a web server by sending partial requests slowly, exhausting server threads. DNS query floods overwhelm DNS servers with rapid requests, preventing legitimate domain resolution. Fastly, Inc. is an American company based in San Francisco, which describes itself as a cloud computing company. Fastly provides content delivery network services, image optimization, and load balancing services. Fastly's cloud security services include denial-of-service attack protection, bot mitigation, and a web application firewall.
In 2024, Fastly introduced Bot Management, which classifies automated traffic at the network edge and provides controls to allow, challenge, or block bots. Fastly also offers API Security, Client-Side Protection, and DDoS Protection. In 2025, Fastly reported that its Next-Gen WAF and Bot Management products protected more than 130,000 applications and APIs and inspected over 6.5 trillion requests per month.
Cloudflare automatically detects and mitigates distributed denial-of-service (DDoS) attacks via our autonomous DDoS systems. These systems include multiple dynamic mitigation rules exposed as DDoS attack protection managed rulesets . You can customize the mitigation rules included in these rulesets to optimize and tailor the protection to your needs.
Protect against a variety of DDoS attacks across layers 3/4 (network layer) and layer 7 (application layer) of the OSI model. Get increased protection against sophisticated DDoS attacks on layer 7 and layers 3/4. Detect and mitigate sophisticated out-of-state TCP attacks such as randomized and spoofed ACK floods, or SYN and SYN-ACK floods.
Protect against DNS-based DDoS attacks, specifically sophisticated and fully randomized DNS attacks such as random prefix attacks. Deploy custom eBPF packet logic across Cloudflare's network to inspect and mitigate DDoS attacks against UDP-based Layer 7 protocols.
A network security and performance solution that offers DDoS protection, traffic acceleration, and more for on-premise, cloud-hosted, and hybrid networks. Get automatic protection from vulnerabilities and the flexibility to create custom rules. For more than 20 years, F5 has worked with customers to defend their applications against distributed denial-of-service (DDoS) attacks. Over time F5 has developed core product capabilities to help applications and services maintain resiliency against DDoS attacks. Many high-profile attacks since 2018 have prompted service providers and managed service providers (MSPs), financial organizations, and enterprises to redesign their networks to include DDoS protection. Working with these customers, F5 has developed a DDoS Protection reference architecture that includes both cloud and on-premises components.
The reference architecture includes multiple tiers of on-premises defenses to protect layers 3 through 7. The network defense tier protects DNS and layers 3 and 4. Freed from the noise of network attacks, the application defense tier can use its CPU resources to protect the high-layer applications. This design enables organizations to defend against all types of DDoS attacks and provides benefits across the organization’s data centers. Finally, the cloud component of the DDoS Protection solution works as a failsafe for volumetric attack mitigation.
While the DDoS threat landscape is constantly evolving, F5 has found that attacks continue to fall within four attack types with the following characteristics: Defensive mechanisms have evolved to deal with these different categories, and high-profile organizations have learned to deploy them in specific arrangements to maximize their security posture. By working with these companies and fine-tuning their components, F5 has developed a recommended DDoS mitigation architecture that can accommodate specific data center scale and industry requirements.
The following DDoS Protection reference architecture is built around well-known industry components. Some may be provided by other vendors and suppliers, but some are specific F5 components. Figure 1 maps DDoS architecture components to the four DDoS attack categories they mitigate. A cloud-based DDoS scrubbing service is a critical component of any DDoS mitigation architecture. When an attacker is sending 50 Gbps of data at an organization’s 1 Gbps ingress point, no amount of on-premises equipment is going to solve that problem. The cloud service, hosted either from a true public cloud or within the organization’s bandwidth service provider, solves the problem by sorting out the obvious bad from the likely good.
The network firewall has been the keystone of perimeter security for a long time. However, many network firewalls are not resistant to DDoS attacks at all. In fact, many of the best-selling firewalls can be disabled with the simplest layer 4 attacks. Sheer throughput is not the answer if the firewall does not recognize and mitigate the attack. 2. System Architecture & Core Working Principles For a layer 3- and 4-based security control device, F5 recommends that architects choose a high-capacity, DDoS-aware network firewall. Specifically, architects should be looking to support millions (not thousands) of simultaneous connections and be able to repel various attacks (e.g., SYN floods) without affecting legitimate traffic.
Application Delivery Controllers (ADCs) provide strategic points of control in the network. When chosen, provisioned, and controlled properly, they can significantly strengthen a DDoS defense. For example, the full-proxy nature of the F5 ADC reduces computational and vulnerability-based threats by validating common protocols such as HTTP and DNS. For these reasons, F5 recommends a full-proxy ADC.
The web application firewall is a higher-level component that understands and enforces the security policy of the application. This component can see and mitigate application-layer attacks whether they are volumetric HTTP floods or vulnerability-based attacks. Several vendors provide web application firewalls. For an effective DDoS architecture, however, F5 recommends only its own web application firewall module for the following reasons: Intrusion detection and prevention systems (IDS/IPS) can play an important role in DDoS mitigation. F5 recommends that IDS/IPS functionality should not be deployed only in a single location (for example, integrated into a layer 4 firewall). Rather, IDS/IPS should be deployed in strategic instances in front of back-end components that may need specific, additional protection, such as a database or specific web server. Nor is an IPS a replacement for a web application firewall. Securing infrastructure and applications is analogous to peeling an onion. An IPS is designed to stop attacks at the top layer—protocols—while WAFs are designed to protect at lower layers (applications).
An IP reputation database helps defend against asymmetric denial-of-service attacks by preventing DDoS attackers from using known scanners to probe an application for later exploitation and penetration. An IP reputation database may be generated internally or come from an external subscription service. F5 IP reputation solutions combine intelligence from open-source intelligence (OSINT), F5 data, and third-party feeds to provide wide coverage of malicious domains.
F5 recommends a hybrid cloud/on-premises DDoS solution. Volumetric attacks will be mitigated by F5 Silverline DDoS Protection—a service delivered via the F5 Silverline cloud-based platform. Silverline DDoS Protection will analyze and remove the bulk of attack traffic. Sometimes, a DDoS campaign may include application layer attacks that must be addressed on the premises. These asymmetric and computational attacks can be mitigated using the network defense and application defense tiers. The network defense tier is composed of L3 and L4 network firewall services and simple load balancing to the application defense tier. The application defense tier consists of more sophisticated (and more CPU-intensive) services including SSL termination and a web application firewall stack.
There are compelling benefits to separating network defense and application defense for the on-premises portion of the DDoS Protection architecture. Figure 3 shows components needed to provide specific capabilities. The F5 components of the DDoS Protection reference architecture include: While the multi-tier architecture is preferred in high-bandwidth environments, F5 understands that for many customers, building multiple DDoS tiers may be overkill for a low-bandwidth environment. These customers are deploying a DDoS mitigation perimeter device that consolidates application delivery with network and web application firewall services.
The recommended practices here still apply. References to network and application defense tiers can simply be applied to the single, consolidated tier in the alternate architecture. Organizations are at risk of experiencing large-scale volumetric DDoS attacks that are capable of overwhelming their Internet-facing, ingress bandwidth capacity. To defend against these attacks, they may effect a route change (with a BGP route announcement) to direct incoming traffic to high-bandwidth data centers that can scrub malicious traffic and send the clean, scrubbed traffic back to the organization’s origin data center.
Factors that may influence the choice of a cloud DDoS provider include the geographic location of scrubbing facilities, bandwidth capacity, latency, time to mitigate, and solution value. As Figure 4 indicates, DDoS attacks may reach bandwidth consumption that is measured in hundreds of Gbps, placing an infrastructure at peril of being completely overwhelmed. In some instances, additional time may be added to incoming requests when a cloud scrubber does not have a scrubbing center in proximity to the organization’s data center. To reduce potential latency, MSPs and other global enterprises should utilize cloud scrubbers that are strategically placed within the regions where they have operations that can be impacted by attacks.
Maintaining availability against volumetric attacks depends on both global coverage—data centers in North America, Europe, and Asia—and terabits of global capacity or hundreds of gigabits per center. Organizations will say that the true value of a cloud scrubber is realized only after the attack campaign. Questions that determine their satisfaction include: Organizations can use the Silverline DDoS Protection Always Available subscription to route traffic through F5 Silverline when a DDoS attack is detected. Alternately, the Silverline DDoS Protection Always On subscription can route traffic through F5 Silverline at all times to ensure greater availability of the organization’s networks and applications.
Silverline DDoS Protection has two main deployment models: routed mode and proxy mode. Routed mode is for enterprises that need to protect their entire network infrastructure. Silverline DDoS Protection employs the Border Gateway Protocol (BGP) to route all the traffic to its scrubbing and protection center and utilizes a Generic Routing Encapsulation (GRE) tunnel/L2 VPN/Equinix Cloud Exchange to send the clean traffic back to the origin network. The routed mode is a scalable design for enterprises with large network deployments. It does not require any application-specific configuration and provides an easy option to turn on or off Silverline DDoS Protection.
Proxy mode is for enterprises that need to protect their applications from volumetric DDoS attacks but do not have a public Class C network. DNS is used to route all traffic to F5 Silverline scrubbing centers. Clean traffic is sent over the public Internet to the application origin servers. Figure 4 shows that in 2019–2020, the record for the world’s largest DDoS attack was broken several times. In order to reach such bandwidth consumption these attacks used a combination of flood attacks (e.g., ACK, NTP, RESET, SSDP, SYN, and UDP) along with TCP Anomaly, UDP Fragment, and CLDAP Reflection from thousands of unwitting public Internet posts to an intended victim.
The network defense tier is built around the network firewall. It is designed to mitigate computational attacks such as SYN floods and ICMP fragmentation floods. This tier also mitigates volumetric attacks up to the congestion of the ingress point (typically 80 to 90 percent of the rated pipe size). Many organizations integrate their IP reputation databases at this tier and have controls to IP addresses by source during a DDoS attack.
Some organizations pass DNS through the first tier to a DNS server in the DMZ. In this configuration, with the right layer 4 controls they can validate DNS packets before sending them on to the server. For organizations with a virtualization-first strategy, it can be challenging to mitigate DDoS attacks that target their virtualized infrastructure without purpose-built hardware. Virtualized security solutions running on x86 COTS servers often lack the high-performance attributes of custom appliances, making effective software-centric DDoS mitigation nearly impossible in many cases.
The F5 solution to this challenge utilizes a new generation of network interface cards (NICs)— known as SmartNICs—to bolster the BIG-IP AFM virtual edition (VE) solution. By programming an embedded, high performance FPGA within these SmartNICs to detect and block DDoS attacks before they reach BIG-IP VE and applications servers, F5 is able to block attacks orders of magnitude larger—up to 300 times larger—than any comparable software-only solution to keep apps online.
Offloading DDoS mitigation from BIG-IP AFM VE to a SmartNIC not only frees up VE CPU cycles for optimizing other security functionality (such as WAF or SSL) but can also reduce TCO by up to 47 percent. As layer 4 attacks, TCP connection floods can affect any stateful device on the network, especially firewalls that are not DDoS-resistant. The attack is designed to consume the memory of the flow connection tables in each stateful device. Often these connection floods are empty of actual content. They can be absorbed into high-capacity connection tables in the network tier or mitigated by full-proxy firewalls.
SSL connection floods are designed specifically to attack the devices that terminate encrypted traffic. Due to the cryptographic context that must be maintained, each SSL connection can consume 50,000 to 100,000 bytes of memory. This makes SSL attacks especially painful. F5 recommends both capacity and the full-proxy technique for mitigating TCP and SSL connection floods. Figure 7 shows the connection capacity of F5-based network firewalls.
The application defense tier is where F5 recommends deploying application-aware, CPU-intensive defense mechanisms like login walls, web application firewall policies, and dynamic security context using F5 iRules. Often these components will share rack space with targeted IDS/IPS devices at this tier. This is also where SSL termination typically takes place. While some organizations terminate SSL at the network defense tier, it is less common due to the sensitivity of SSL keys and policies against keeping them at the security perimeter.
Recursive GETs and POSTs are among today’s most pernicious attacks. They can be very hard to distinguish from legitimate traffic. GET floods can overwhelm databases and servers, and they can also cause a “reverse full pipe.” F5 recorded one attacker that was sending 100 Mbps of GET queries into a target and bringing out 20 Gbps of data. The configuration and setup for these strategies can be found in the F5 DDoS Recommended Practices documentation.
DNS is the second-most targeted service after HTTP. When DNS is disrupted, all external data center services (not just a single application) are affected. This single point of total failure, along with the often under-provisioned DNS infrastructure, makes DNS a tempting target for attackers. DNS services have been historically under-provisioned. A significant percentage of DNS deployments are under-provisioned to the point where they are unable to withstand even small-to-medium DDoS attacks.
3. Software Implementation, Frameworks & Protocols DNS caches have become popular as they can boost the perceived performance of a DNS service and provide some resilience against standard DNS query attacks. Attackers have switched to what is called “no such domain” (or NXDOMAIN) attacks, which quickly drain the performance benefits provided by the cache.
To remedy this, F5 recommends front-ending the BIG-IP DNS Domain Name Service with the special, high-performance DNS proxy module called F5 DNS Express™. DNS Express acts as an absolute resolver in front of the existing DNS servers. It loads the zone information from the servers and resolves every single request or returns NXDOMAIN. It is not a cache and cannot be emptied via NXDOMAIN query floods.
Often the DNS service exists as its own set of devices apart from the first security perimeter. This is done to keep DNS independent of the applications it serves. For example, if part of the security perimeter goes dark, DNS can redirect requests to a secondary data center or to the cloud. Keeping DNS separate from the security and application tiers can be an effective strategy for maintaining maximum flexibility and availability.
Some large enterprises with multiple data centers serve DNS outside the main security perimeter using a combination of BIG-IP DNS with DNS Express and the BIG-IP AFM firewall module. The main benefit of this approach is that the DNS services remain available even if the network defense tier goes offline due to DDoS. Regardless of whether DNS is served inside or outside the DMZ, either BIG-IP DNS or BIG-IP AFM can validate the DNS requests before they hit the DNS server.
Following are three uses cases for the reference architecture that map to three typical customer scenarios: Each use case below contains a diagram of the deployment scenario, a short description of the specifics of the use case, and recommended F5 components within that scenario. Also see Figure 14 for additional sizing information. The MSP data center use case is all about providing security for a variety of applications while maximizing the value of data center resources. Return-on-investment (ROI) is crucial for MSPs, who would often like to do everything from one device if they can and are willing to go offline during a DDoS attack.
For this use case, the MSP is putting all of its eggs in one basket. It will get the most cost-efficient solution but will also have the largest availability challenge. On the other hand, the organization gains efficiency by focusing specialized resources with deep knowledge on a single platform. F5 provides high-availability systems, superior scale and performance, and world-class support that help further offset risk.
Certainly, financial savings is the biggest benefit of this consolidated architecture. A superior DDoS solution uses equipment that is already working to deliver revenue-generating applications every day. The consolidated environment helps save on rack space, power, and management. The large FSI data center scenario is a mature, well-recognized use case for DDoS Protection. Typically, the FSI will have multiple service providers but may forgo those providers’ volumetric DDoS offerings in favor of another scrubbing service.
Many of these may also have a backup cloud scrubber as an insurance policy against the failure of their primary cloud scrubber to mitigate volumetric DDoS attacks. The FSI data center often has few corporate staff within it, so there is no need for a next-generation firewall. FSIs have the most stringent security policy outside of federal military institutions. For example, nearly all FSIs must keep the payload encrypted through the entire data center. FSIs have the highest-value asset class (bank accounts) on the Internet, so they are frequent targets—not just for DDoS but also for hacking. The two-tier on-premises architecture enables FSI organizations to scale their CPU-intensive, comprehensive security policy at the application tier independently of their investment in the network tier.
This use case enables FSIs to create a DDoS-resistant solution while retaining (indeed, leveraging) the security equipment they already have. The firewalls at the network defense tier continue to do their jobs, and the BIG-IP devices at the application defense tier continue to prevent breaches. The enterprise anti-DDoS scenario is similar to the large FSI scenario. The primary difference is that enterprises do have staff inside the data center and therefore need the services of a next-generation firewall (NGFW). They may be tempted to use a single NGFW for both ingress and egress, but this makes them vulnerable to DDoS attacks, as NGFW aren’t designed to handle DDoS attacks that evolve or are multi-vector.
F5 recommends that enterprises obtain protection against volumetric DDoS attacks from a cloud scrubber like F5 Silverline. On the premises, the recommended enterprise architecture includes a smaller NGFW on a separate path from the ingress application traffic. By using a network defense tier and an application defense tier, enterprises can take advantage of asymmetric scaling—adding more F5 WAF devices if they find that CPU is at a premium.
Different verticals and companies have different requirements. By using F5 equipment at both tiers, the enterprise architecture enables customers to decide where it makes the most sense to decrypt (and optionally re-encrypt) the SSL traffic. For example, an enterprise can decrypt SSL at the network defense tier and mirror the decrypted traffic to a network tap that is monitoring for advanced threats.
Figure 14 shows specifications for the range of F5 hardware devices that are available to meet organizations’ scaling requirements. This recommended DDoS Protection reference architecture draws on F5’s long experience combating DDoS attacks with its customers. Service providers are finding success with a consolidated approach. Global financial services institutions are recognizing that the recommended hybrid architecture represents the ideal placement for all of their security controls.
Enterprise customers are rearranging and rearchitecting their security controls around this architecture as well. For the foreseeable future, a hybrid DDoS Protection architecture should continue to provide the flexibility and manageability that architects need to combat the modern DDoS threat. Google Cloud Armor helps protect your Google Cloud deployments from threats such as distributed denial-of-service (DDoS) attacks and application attacks like cross-site scripting (XSS) and SQL injection (SQLi). This document provides a high-level overview of the protections built in to Cloud Armor, as well as the options you can manually configure to help provide protection to your services. To use some of the features discussed in this document, you must use global external Application Load Balancers or classic Application Load Balancers. Security policies Cloud Armor security policies are collections of Cloud Armor rules that are applied to requests destined for a protected resource in the order configured by the policy. Use Cloud Armor security policies to help protect your applications and services from DDoS and other web-based attacks. Although security policies are frequently used to protect applications running behind a load balancer, they also protect other resources not running behind a load balancer, such as VM instances with external IP addresses. This protection applies whether the resources are deployed on Google Cloud, in a hybrid deployment, or in a multi-cloud architecture. You must manually configure security policies by using match conditions and actions. Cloud Armor also provides preconfigured security policies for a variety of use cases. For more information, see Cloud Armor security policy overview .
Cloud Armor security policies are collections of Cloud Armor rules that are applied to requests destined for a protected resource in the order configured by the policy. Use Cloud Armor to create rules using the custom rules language to craft complex conditions and define the action to take against matching requests. A rule takes effect when it is the highest priority rule that matches the attributes of an incoming request. For more information, see Cloud Armor custom rules language reference .
Cloud Armor preconfigured WAF rules are complex web application firewall (WAF) rules that include dozens of signatures compiled from open source industry standards. Each signature identifies a specific attack pattern within the rule set. Cloud Armor provides these rules as-is, so you can evaluate many distinct traffic signatures by referring to named rules. This approach eliminates the need to manually define each signature.
Cloud Armor preconfigured rules add a layer of protection to your web applications and services from common internet attacks and help mitigate the OWASP Top 10 risks . The preconfigured rules are based on the OWASP ModSecurity Core Rule Set (CRS) , and Cloud Armor supports CRS 4.22, 3.3, and 3.0. We recommend that you don't use a lower version than 4.22 You can tune these preconfigured rules to disable noisy or unnecessary signatures. For more information, see Tuning Cloud Armor WAF rules .
Cloud Armor managed rules protect your backend services and APIs from a wide range of web application threats by using threat signatures which are automatically kept up to date. These rules are updated to mitigate newly discovered CVEs and zero-day vulnerabilities, reducing operational overhead and manual configuration. Cloud Armor Enterprise is the managed application protection service that helps protect your web applications and services from distributed denial-of-service (DDoS) attacks and other threats from the internet. Cloud Armor Enterprise features always-on protection from Layer 3 and Layer 4 (L3 and L4) volumetric and network protocol-based DDoS attacks for your load balancer. It also provides access to Layer 7 (L7) application layer DDoS attack protection like HTTP floods through user-configured security policies.
Cloud Armor Google Threat Intelligence helps secure your traffic by allowing or blocking traffic to your global external Application Load Balancers and classic Application Load Balancers based on threat intelligence data. You configure security policy rules to match traffic against continuously updated feeds—such as Tor exit nodes or VPN providers—by using the evaluateThreatIntelligence() match expression. For more information, see Apply Google Threat Intelligence .
Adaptive Protection adds a layer of protection to your applications and services from L7 DDoS attacks by analyzing traffic patterns to your backend services and responding to sudden changes in those traffic patterns. It detects and alerts you to suspected attacks and can suggest or automatically apply rules to mitigate them. You can tune these rules to meet your needs. Enable Adaptive Protection on a per-security policy basis. You must have an active Cloud Armor Enterprise subscription to use this feature.
Cloud Armor provides always-on protection from L3 and L4 volumetric and network protocol-based DDoS attacks, with automated inline mitigations in real time and with no latency impact. This protection is for applications or services behind load balancers. Cloud Armor is able to detect and mitigate network attacks in order to allow only well-formed requests through the load balancing proxies.
Cloud Armor can help protect from L7 (Application layer) threats including L7 DDoS like HTTP floods, but this protection requires a user-configured security policy with proactive rules in place. The security policies enforce custom L7 filtering policies, including preconfigured WAF rules that mitigate OWASP top 10 web application vulnerability risks. You can attach security policies to the backend services of the following load balancers: Cloud Armor security policies allow you to permit or deny access to your deployment at the Google Cloud edge, close to the traffic source. This prevents unwanted traffic from consuming resources or entering your Virtual Private Cloud (VPC) networks.
4. Practical Deployment, Analysis & Case Studies You can use some or all of these features to help protect your application. Use security policies to match against known conditions, create WAF rules to help protect against common attacks like those in the OWASP Core Rule Set 4.22 , and use Google Cloud Armor Enterprise built-in DDoS protections. What's next Examine common use cases for Cloud Armor Learn about Cloud Armor Enterprise Learn about Adaptive Protection code samples are licensed under the Apache 2.0 License . For details, see the Google Developers Site Policies . Java is a registered trademark of Oracle and/or its affiliates.
The Cloudflare Autonomous Edge is powered by the denial-of-service daemon ( dosd ), which is a home-grown software-defined system. The flow tracking daemon, flowtrackd , is our stateful mitigation platform alongside dosd . A dosd instance runs in every single server in every one of Cloudflare global network's data centers âIIï¸I around the world. These dosd instances can detect and mitigate DDoS attacks autonomously without requiring centralized consensus. Cloudflare users can configure this system through DDoS Attack Protection managed rulesets .
Another component of Cloudflare's Autonomous Edge includes the Advanced TCP Protection system. This is Cloudflare's TCP state tracking machine for detecting and mitigating the most randomized and sophisticated TCP-based DDoS attacks in unidirectional routing topologies âII such as the case of Magic Transit . Advanced TCP Protection is able to identify the state of a TCP connection and then drops, challenges, or rate-limits packets that do not belong to a legitimate connection.
For more information, refer to our blog post A deep-dive into Cloudflare's autonomous edge DDoS protection âIIï¸I . Complementary to the Autonomous Edge, Cloudflare's entire global network is overwatched by a global version of dosd . This component protects Cloudflare's entire global network by detecting and mitigating globally distributed volumetric DDoS attacks.
The centralized systems run in Cloudflare's core data centers. They receive samples from every global network data center, analyze them, and automatically send mitigation instructions when detecting an attack. The system is also synchronized to each of our customers' web servers to identify their health and trigger any required mitigation actions. AWS Shield is a managed distributed denial of service (DDoS) protection service that is designed to safeguard applications running on AWS. It provides detection and inline mitigations that help with application downtime and latency. There are two tiers of AWS Shield: Standard and Advanced.
AWS Shield Standard is designed to defend against common, frequently occurring network and transport layer DDoS attacks that target your website or applications. AWS Shield Standard is designed to provide network flow monitoring that helps inspect incoming traffic to AWS services and apply a combination of traffic signatures, anomaly algorithms, and other analysis techniques to help detect malicious traffic.
Shield Standard is designed to set static thresholds for each AWS resource type. Mitigation techniques are built into AWS Shield Standard and designed to help protect underlying AWS services against common, frequently occurring infrastructure events. Mitigations are designed to be applied inline to help protect AWS services.
AWS Shield Advanced is designed to provide higher levels of protection against attacks targeting your applications running on protected resources. Shield Advanced is designed to provide additional detection and mitigation against large and sophisticated DDoS attacks, visibility into attacks, and integration a web application firewall. AWS Shield Advanced is designed to provide detection based on traffic patterns to your protected Amazon resources. Using region- and resource-specific monitoring techniques, AWS Shield Advanced is designed to help detect and alert you of smaller DDoS attacks. AWS Shield Advanced is also designed to help detect application layer attacks like HTTP floods or DNS query floods.
AWS Shield Advanced is designed to use the health of your applications to improve responsiveness and accuracy in attack detection and mitigation. You can define a health check and associate it with a resource that is protected by Shield Advanced. You can also apply health-based detection to resource types that Shield Advanced supports. AWS Shield Advanced is designed to provide mitigations for events targeting your applications running on protected resources. Using routing techniques, Shield Advanced is designed to deploy mitigation capacity to protect your application against DDoS events.
AWS Shield Advanced is designed to protect web applications by mitigating application layer (L7) DDoS events. AWS Shield Advanced offers proactive engagement from the SRT when a DDoS event is detected. When you activate proactive engagement, the SRT is designed to contact you if a Route 53 health check associated with your protected resource becomes unhealthy during a DDoS event.
AWS Shield Advanced enabled you to bundle resources into protection groups. Reporting can also be consumed at the protection group level. AWS Shield Advanced is designed to give you visibility into DDoS events with notification and diagnostics. You can also view a summary of prior events.
AWS Shield Advanced is designed with DDoS cost protection to help avoid scaling charges resulting from DDoS-related usage spikes on protected resources. For additional information about service controls, security features and functionalities, including, as applicable, information about storing, retrieving, modifying, restricting, and deleting data, please see https://docs.aws.amazon.com/index.html . This additional information does not form part of the Documentation for purposes of the AWS Customer Agreement available at http://aws.amazon.com/agreement , or other agreement between you and AWS governing your use of AWS’s services.
It's important to protect your business from the impact of Distributed Denial of Service (DDoS) attacks, as well as other cyberattacks. Keeping customer trust in your service by maintaining the availability and responsiveness of your application is high priority. You also want to avoid unnecessary direct costs when your infrastructure must scale in response to an attack. Amazon Web Services (AWS) is committed to providing you with the tools, best practices, and services to defend against bad actors on the internet. Using the right services from AWS helps ensure high availability, security, and resiliency.
In this whitepaper, AWS provides you with prescriptive DDoS guidance to improve the resiliency of applications running on AWS. This includes a DDoS-resilient reference architecture that can be used as a guide to help protect application availability. This whitepaper also describes different attack types, such as infrastructure layer attacks and application layer attacks. AWS explains which best practices are most effective to manage each attack type. In addition, the services and features that fit into a DDoS mitigation strategy are outlined, along with how each one can be used to help protect your applications.
This paper is intended for IT decision makers and security engineers who are familiar with the basic concepts of networking, security, and AWS. Each section has links to AWS documentation that provides more detail on the best practice or capability. AWS detects over a million DDoS attacks per year and mitigates thousands on a daily basis against our customers. AWS recommends implementing these best practices proactively, as they significantly reduce the likelihood of business impact from DDoS events.
A distributed denial-of-service (DDoS) attack is a deliberate attempt by a hostile actor to disrupt operations of publicly exposed sites, systems, and APIs, with the goal of degrading the experience of legitimate users. For workloads using regional external passthrough Network Load Balancers , protocol forwarding , or VMs with public IP addresses, Google Cloud Armor offers the following options to help protect systems against DDoS attacks: This document explains the difference between standard and advanced network DDoS protection, how advanced network DDoS protection works, and how to enable advanced network DDoS protection.
Use the following table to compare standard and advanced network DDoS protection features. Standard network DDoS protection is always enabled. You don't need to take any action to enable it. Standard protection ensures that Google Cloud infrastructure remains stable by continuously monitoring and throttling traffic that exceeds quota. It does not look for attack signatures or provide other advanced mitigations to minimize collateral damage. For targeted protection, you must enable your own security policy with Advanced DDoS protection.
You configure advanced network DDoS protection on a per-region basis. Instead of associating the network edge security policy with one or more target pools, target instances, backend services, or instances with external IP addresses, you associate it with a network edge security service in a particular region. When you enable it for that region, Cloud Armor provides always-on targeted volumetric attack detection and mitigation for regional external passthrough Network Load Balancer, protocol forwarding, and VMs with public IP addresses in that region. You can only apply advanced network DDoS protection to projects that are enrolled in Cloud Armor Enterprise.
When you configure advanced network DDoS protection, you first create a security policy of the type CLOUD_ARMOR_NETWORK in a region that you choose. Next, you update the security policy to enable advanced network DDoS protection. Finally, you create a network edge security service, a resource to which you can attach security policies of type CLOUD_ARMOR_NETWORK . Attaching the security policy to the network edge security service enables advanced network DDoS protection for all applicable endpoints in the region that you chose.
Advanced network DDoS protection measures your baseline traffic to improve its mitigation performance. When you enable advanced network DDoS protection, there is a training period of 24 hours before advanced network DDoS protection develops a reliable baseline and can use its training to enhance its mitigations. When the training period is over, advanced network DDoS protection applies additional mitigation techniques based on historical traffic.
Your project must be enrolled in Cloud Armor Enterprise to enable advanced network DDoS protection on a per-region basis. After they are activated, all regional endpoints in the activated region receive always-on advanced network DDoS protection. Ensure that there is an active Cloud Armor Enterprise subscription in your billing account, and that the current project is enrolled in Cloud Armor Enterprise. For more information about enrolling in Cloud Armor Enterprise, see Subscribing to Cloud Armor Enterprise and enrolling projects .
5. Performance Evaluation & Extended Technical Observations To configure, update, or delete a Cloud Armor edge security service, you need the following IAM permissions: The following table lists the IAM roles' base permissions and their associated API methods. For more information about the IAM permissions that you need when you use Cloud Armor, see Set up IAM permissions for Cloud Armor security policies .
Create a security policy of type CLOUD_ARMOR_NETWORK , or use an existing security policy with type CLOUD_ARMOR_NETWORK . Update the newly created or existing security policy by setting the --network-ddos-protection flag to ADVANCED . Alternatively, you can set the --network-ddos-protection flag to ADVANCED_PREVIEW to enable the security policy in preview mode .
To disable advanced network DDoS protection, you can either update or delete the security policy. Use the following command to update your security policy to set the --network-ddos-protection flag to STANDARD . Replace variables with information that is relevant to your deployment. Before you can delete a network edge security policy, you must first remove it from the network edge security service because you cannot delete in-use security policies. Use the following steps to delete your security policy: Remove your policy from the network edge security service or delete the network edge security service.
To remove your policy from the network edge security service, use the following command: Preview mode lets you monitor the effects of advanced network DDoS protection without enforcing the mitigation. To enable preview mode, you set the --ddos-protection flag to ADVANCED_PREVIEW . You can use the following example to update an existing policy.
If your security policy is in preview mode during an active attack and you want to enforce the mitigations, you can update your security policy to set the --network-ddos-protection flag to ADVANCED . The policy is enforced almost immediately, and the next MITIGATION_ONGOING logging event reflects the change. MITIGATION_ONGOING logging events occur every five minutes.
Cloud Armor generates three types of event logs when mitigating DDoS attacks: MITIGATION_STARTED , MITIGATION_ONGOING , and MITIGATION_ENDED . You can use the following log filters to view your logs by mitigation type: @type: "type.googleapis.com/google.cloud.networksecurity.cloudarmor.logging.v1.CloudArmorMitigationAlert" alertId: "11275630857957031521" mitigation_type: "MITIGATION_STARTED" target_vip: "XXX.XXX.XXX.XXX" total_volume: { pps: 1400000 bps: 140000000 } started: { total_attack_volume: { pps: 1100000 bps: 110000000 } classified_attack: { attack_type: "NTP-udp" attack_volume: { pps: 500000 bps: 50000000 } } classified_attack: { attack_type: "CHARGEN-udp" attack_volume: { pps: 600000 bps: 60000000 } } attack_sources: { top_source_asns: { asn: "ABCDEF" volume: { pps: 20000 bps: 2000000 } } top_source_asns: { asn: "UVWXYZ" volume: { pps: 20000 bps: 2000000 } } top_source_geos: { region_code: "XX" volume: { pps: 20000 bps: 2000000 } } top_source_geos: { region_code: "XY" volume: { pps: 20000 bps: 2000000 } } top_source_ips: { region_code: "xx.xx.xx.xx" volume: { pps: 20000 bps: 2000000 } } top_source_ips: { region_code: "yy.yy.yy.yy" volume: { pps: 20000 bps: 2000000 } } } } @type: "type.googleapis.com/google.cloud.networksecurity.cloudarmor.logging.v1.CloudArmorMitigationAlert" alertId: "11275630857957031521" mitigation_type: "MITIGATION_ONGOING" target_vip: "XXX.XXX.XXX.XXX" total_volume: { pps: 1500000 bps: 150000000 } ongoing: { total_attack_volume: { pps: 1100000 bps: 110000000 } classified_attack: { attack_type: "NTP-udp" attack_volume: { pps: 500000 bps: 50000000 } } classified_attack: { attack_type: "CHARGEN-udp" attack_volume: { pps: 600000 bps: 60000000 } } attack_sources: { top_source_asns: { asn: "ABCDEF" volume: { pps: 20000 bps: 2000000 } } top_source_asns: { asn: "UVWXYZ" volume: { pps: 20000 bps: 2000000 } } top_source_geos: { region_code: "XX" volume: { pps: 20000 bps: 2000000 } } top_source_geos: { region_code: "XY" volume: { pps: 20000 bps: 2000000 } } top_source_ips: { region_code: "xx.xx.xx.xx" volume: { pps: 20000 bps: 2000000 } } top_source_ips: { region_code: "yy.yy.yy.yy" volume: { pps: 20000 bps: 2000000 } } } } @type: "type.googleapis.com/google.cloud.networksecurity.cloudarmor.logging.v1.CloudArmorMitigationAlert" alertId: "11275630857957031521" mitigation_type: "MITIGATION_ENDED" target_vip: "XXX.XXX.XXX.XXX" ended: { attack_duration_seconds: 600 attack_type: "NTP-udp" } In preview mode, each of the preceding mitigation_type s are preceded by PREVIEWED_ . For example, in preview mode, MITIGATION_STARTED is instead PREVIEWED_MITIGATION_STARTED .
To view these logs, go to the Logs Explorer and view the network_security_policy resource. The Security Command Center dashboard helps you monitor and respond to volumetric DDoS attacks targeting your passthrough Network Load Balancer and virtual machines. When Cloud Armor detects an attack, a dedicated finding labeled "Volumetric DDoS Attack Attempt - Network LB/VMs" appears on the dashboard and the Cloud Armor card.
The finding includes direct links to relevant logs, and provides the following information to help you understand the attack: The finding dynamically reflects the attack status. Attack status is based on the following log events: Mitigation ongoing: as the mitigation progresses, the finding updates automatically, keeping you informed of the ongoing situation. The following screenshot shows an example active finding: Mitigation ended: when the attack subsides and mitigation ends, the finding becomes inactive, providing a record of the event.
The following screenshot shows an example inactive finding: code samples are licensed under the Apache 2.0 License . For details, see the Google Developers Site Policies . Java is a registered trademark of Oracle and/or its affiliates. In the modern, connected world, the availability and security of a website are critical to business continuity and user trust.
Distributed Denial of Service, or DDoS, attacks are among the most common and most damaging threats facing online businesses today, and effective DDoS protection has become a baseline requirement rather than an optional extra. Unlike a denial of service attack that originates from a single source, a DDoS attack uses many compromised devices, organised into what is called a botnet, to bombard a server, network, or application with an overwhelming volume of traffic. This flood consumes available resources until the target becomes unavailable to legitimate users, which is exactly the scenario DDoS protection is designed to prevent.
The impact of a successful attack without adequate DDoS protection in place can be severe. Businesses often suffer prolonged outages, lost sales, and disruption to key services. The financial burden extends beyond the attack itself, covering mitigation costs, potential recovery and troubleshooting expenses, and lost productivity across the organisation. Repeated outages erode user trust, damage brand reputation, and in some cases can expose sensitive data if the DDoS activity is part of a broader cyber campaign rather than an isolated event.
This guide provides a complete overview of DDoS protection for 2026, covering what a DDoS attack actually is, the different categories of attack, current detection techniques, prevention strategies, mitigation approaches, and the role cloud based services now play in defending modern infrastructure. It also covers what has genuinely changed in the threat landscape recently, since attack scale, cost, and frequency have all shifted meaningfully even over the past year or two.
A Distributed Denial of Service attack is a type of cyberattack designed to disrupt the availability of a website, server, or online service by bombarding it with a large volume of malicious traffic. Unlike a regular denial of service attack, which comes from a single point of origin, a DDoS attack comes from many compromised devices acting simultaneously. These devices, ranging from personal computers to IoT devices such as routers and smart cameras, are typically infected with malware that allows an attacker to control them remotely as part of a botnet.
The goal of the attack is to consume all available resources at the target, whether that is network bandwidth, CPU processing power, or application capacity. The result is a system that responds slowly, becomes unresponsive, or goes completely offline, leaving legitimate users unable to access it. DDoS attacks range from simple traffic floods to sophisticated, multi-vector campaigns that are considerably harder to detect and mitigate, which is precisely why layered DDoS protection rather than a single defensive measure has become the standard recommendation.
Understanding the actual cost of an attack helps explain why investing in DDoS protection ahead of time is almost always cheaper than recovering from an incident after the fact. Knowing the different categories of attack is the foundation for building effective DDoS protection, since each category calls for a somewhat different defensive approach.
Identifying an attack in its early stages is essential for effective DDoS protection, since the faster an anomaly is recognised, the less damage it causes before mitigation engages. Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Denial-of-service%20attack • https://en.wikipedia.org/wiki/DDoS%20mitigation • https://en.wikipedia.org/wiki/Fastly • https://developers.cloudflare.com/ddos-protection/ • https://www.f5.com/resources/white-papers/ddos-architecture-diagrams-and-white-paper • https://docs.cloud.google.com/armor/docs/cloud-armor-overview • https://developers.cloudflare.com/ddos-protection/about/components/ • https://aws.amazon.com/documentation-overview/shield/ • https://docs.aws.amazon.com/whitepapers/latest/aws-best-practices-ddos-resiliency/aws-best-practices-ddos-resiliency.html • https://docs.cloud.google.com/armor/docs/advanced-network-ddos
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Cloud Distributed Denial Of Service Mitigation System.
[*] Metasploit Scan Running on Target Subnet for Cloud Distributed Denial Of Service Mitigation System... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |