Complete Technical Paper Content — Cloud Identity And Access Management Policy Analyzer
Overview & System Context
Cloud Identity And Access Management Policy Analyzer: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9569 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Microsoft Azure, sometimes stylized Azure, and formerly Windows Azure, is the cloud computing platform developed by Microsoft. It offers management, access and development of applications and services to individuals, companies, and governments through its global infrastructure. Microsoft Azure supports multiple programming languages, tools, and frameworks, including Microsoft-specific and third-party software and systems. Azure was first introduced at the Professional Developers Conference (PDC) in October 2008 under the code name "Project Red Dog". It was officially launched as Windows Azure in February 2010 and later renamed to Microsoft Azure on March 25, 2014.
Event Hubs, which provides event and telemetry ingress to the cloud at a massive scale, with low latency and high reliability. For example, an event hub can be used to track data from cell phones such as coordinating with a GPS in real time. Queues, which allows one-directional communication. A sender application would send the message to the service bus queue and a receiver would read from the queue. Though there can be multiple readers for the queue, only one would process a single message. Topics, which provides one-directional communication using a subscriber pattern. It is similar to a queue; however, each subscriber will receive a copy of the message sent to a Topic. Optionally, the subscriber can filter out messages based on specific criteria defined by the subscriber. Relays, which provides bi-directional communication. Unlike queues and topics, a relay does not store in-flight messages in its memory; instead, it just passes them on to the destination application.
Through Azure Blockchain Workbench, Microsoft is providing the required infrastructure to set up a consortium network in multiple topologies using a variety of consensus mechanisms. Microsoft provides integration from these blockchain platforms to other Microsoft services to streamline the development of distributed applications. Microsoft supports many general-purpose blockchains, including Ethereum and Hyperledger Fabric and purpose-built blockchains like Corda.
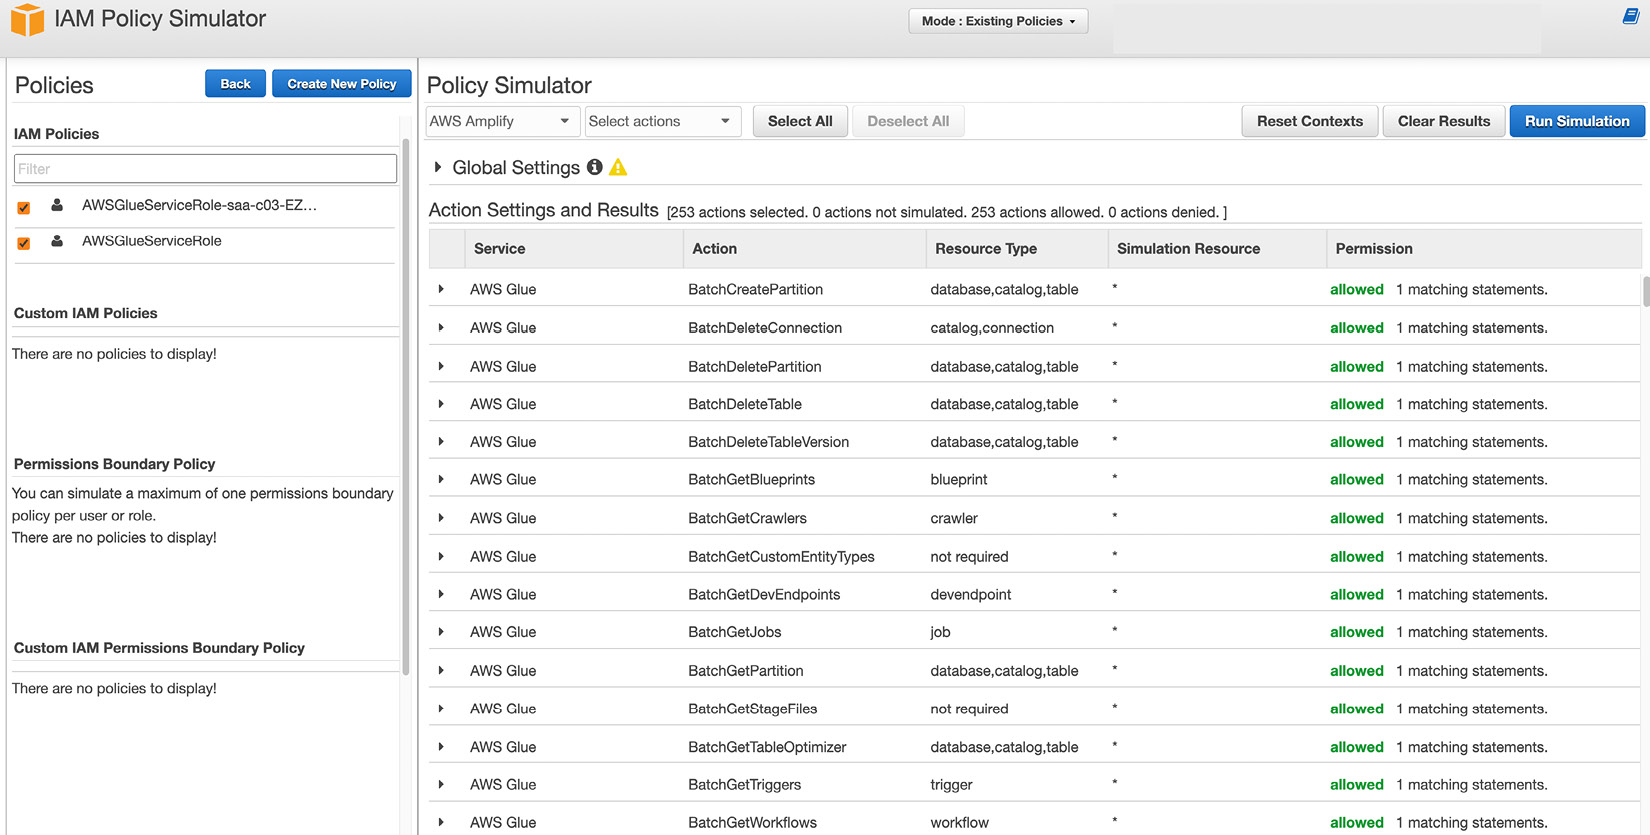
In 2005, Microsoft took over Groove Networks, and Bill Gates made Groove's founder Ray Ozzie one of his 5 direct reports as one of 3 chief technology officers. Ozzie met with Amitabh Srivastava, which let Srivastava change course. They convinced Dave Cutler to postpone his retirement, and their teams developed a cloud operating system. Figure 1: Chapter 3: Identity and Access Management | AWS Certified Solutions ...
October 2008 (PDC LA) – Announced the Windows Azure Platform. March 2009 – Announced SQL Azure Relational Database. November 2009 – Updated Windows Azure CTP, Enabled full trust, PHP, Java, CDN CTP, and more. February 1, 2010 – Windows Azure Platform commercially available. June 2010 – Windows Azure Update, .NET Framework 4, OS Versioning, CDN, SQL Azure Update. October 2010 (PDC) – Platform enhancements, Windows Azure Connect, improved Dev / IT Pro Experience. December 2011 – Traffic manager, SQL Azure reporting, HPC scheduler. June 2012 – Websites, Virtual machines for Windows and Linux, Python SDK, new portal, locally redundant storage. April 2014 – Windows Azure renamed Microsoft Azure, ARM Portal introduced at Build 2014. July 2014 – Azure Machine Learning public preview.
November 2014 – Outage affecting major websites, including MSN.com. September 2015 – Azure Cloud Switch introduced as a cross-platform Linux distribution. Currently known as SONiC. December 2015 – Azure ARM Portal (codename "Ibiza") released. March 2016 – Azure Service Fabric is generally available. November 15, 2016 – Azure Functions is generally available. May 10, 2017 – Azure Cosmos DB is generally available. May 7, 2018 – Azure Maps is generally available. July 16, 2018 – Azure Service Fabric Mesh public preview. September 24, 2018 – Microsoft Azure IoT Central is generally available.
October 10, 2018 – Microsoft joins the Linux-oriented group Open Invention Network. April 17, 2019 – Azure Front Door Service is now available. March 2020 – Microsoft said that there was a 775% increase in Microsoft Teams usage in Italy due to the COVID-19 pandemic. The company estimates there are now 44 million daily active users of Teams worldwide. January 17, 2023 – Azure OpenAI Service is generally available. At fiscal year-end 2025, Microsoft reported that Azure surpassed US$75 billion in annual revenue and operated over 400 datacenters across 70 regions.
Azure Fundamentals Azure Data Fundamentals Azure AI Engineer Associate Azure AI Fundamentals Azure Cosmos DB Developer Specialty Azure Administrator Associate Azure Data Engineer Associate Azure Data Scientist Associate Azure Database Administrator Associate Azure Developer Associate Azure Enterprise Data Analyst Associate Azure Security Engineer Associate Azure Security Operations Analyst Associate Azure Identity and Access Administrator Associate Azure Security, Compliance, and Identity Fundamentals Azure Network Engineer Associate Azure Windows Server Hybrid Administrator Associate Azure Virtual Desktop Specialty Azure for SAP Workloads Specialty Azure Customer Data Platform Specialty Azure Cybersecurity Architect Expert Azure Solutions Architect Expert Azure Power Platform Solution Architect Expert Azure DevOps Engineer Expert Azure IoT Developer Specialty Azure Stack Hub Operator Associate Azure Machine Learning Specialty Microsoft Forefront is a discontinued family of line-of-business security software by Microsoft Corporation. Microsoft Forefront products are designed to help protect computer networks, network servers (such as Microsoft Exchange Server and Microsoft SharePoint Server) and individual devices. As of 2015, the only actively developed Forefront product is Forefront Identity Manager.
Identity Manager: State-based identity management software product, designed to manage users' digital identities, credentials and groupings throughout the lifecycle of their membership of an enterprise computer system Figure 2: 20 Essential Open Source Cyber Security Tools for 2026 System Center Endpoint Protection: A business antivirus software product that can be controlled over the network, formerly known as Forefront Endpoint Protection, Forefront Client Security and Client Protection. Exchange Online Protection: A software as a service version of Forefront Protect for Exchange Server: Instead of installing a security program on the server, the customer re-routes its email traffic to the Microsoft online service before receiving them.
Unified Access Gateway: Discontinued server product that protects network assets by encrypting all inbound access request from authorized users. Supports Virtual Private Networks (VPN) and DirectAccess. Formerly called Intelligent Application Gateway. Server Management Console: Discontinued web-based application that enables management of multiple instances of Protection for Exchange, Protection for SharePoint and Microsoft Antigen from a single interface.
Protection for Exchange: A discontinued software product that detects viruses, spyware, and spam by integrating multiple scanning engines from security partners in a single solution to protect Exchange messaging environments. FPE provides an administration console that includes customizable configuration settings, filtering options, monitoring features and reports, and integration with the Forefront Online Protection for Exchange (FOPE) product. After installation, managing FPE on multiple Exchange servers can be done with the Protection Server Management Console. Additionally, FPE can be managed using Windows PowerShell, a command-line shell and task-based scripting technology that enables the automation of system administration tasks.
Protection for SharePoint: A discontinued product that protects Microsoft SharePoint Server document libraries. It enforces rules that prevent documents containing malware, sensitive information, or out-of-policy content from being uploaded. Protection Server Management Console or Windows PowerShell can be used to manage Protection for SharePoint Server on multiple servers. Security for Office Communications Server: Protects computers running Microsoft Office Communications Server from malware. Formerly called Antigen for Instant Messaging.
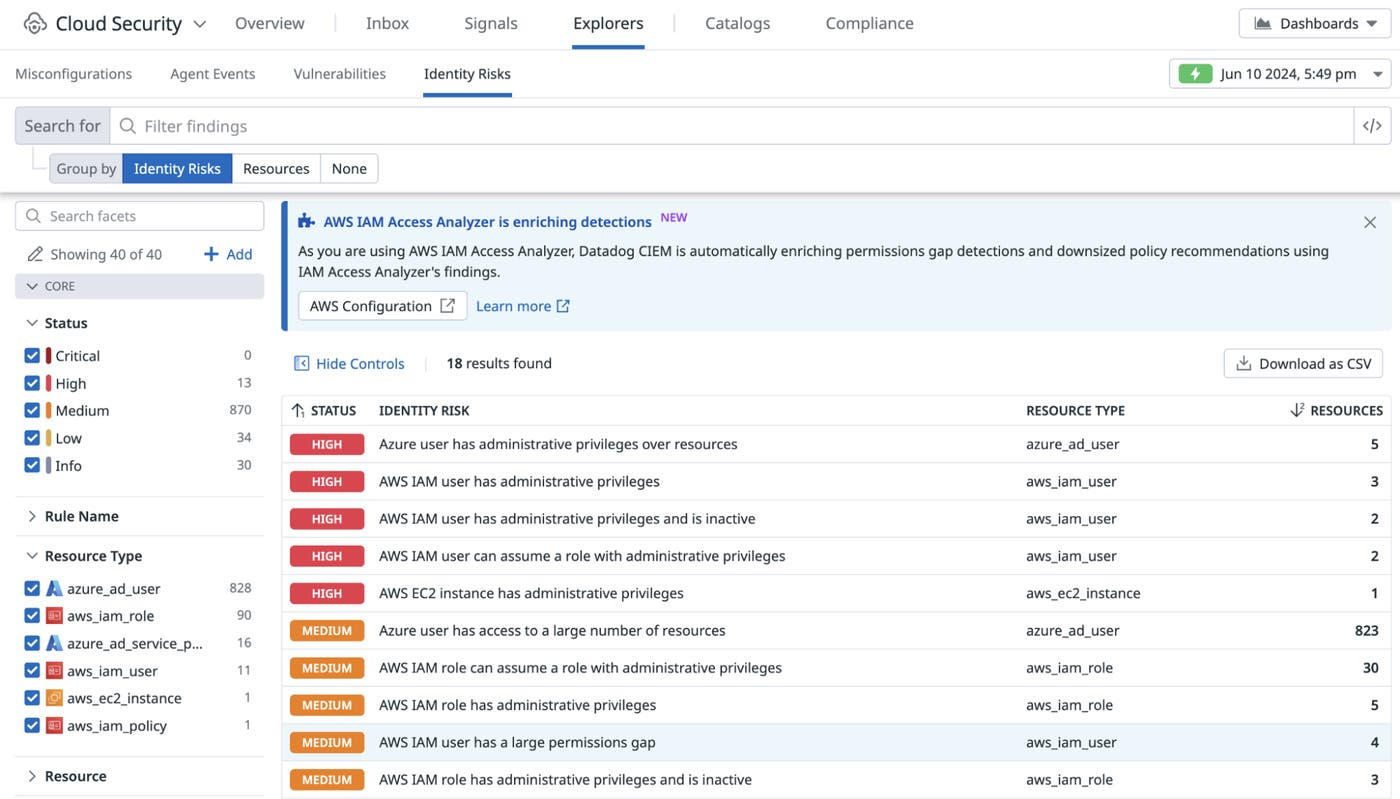
Figure 3: Identify and remediate permission gaps in AWS with Datadog Cloud ... Netwrix is a Frisco, Texas–based private IT security software company. After eight acquisitions the company's team geographically expanded to Latin America, UK, Germany, France, Asia, US as well as other countries. The company's flagship products are Netwrix Auditor and Netwrix Enterprise Auditor that help information security and governance professionals manage sensitive, regulated and business-critical data. The company operates in the United States, EMEA and Asia-Pacific.
Architecture Center: Best Practices for Security, Identity, & Compliance AWS Identity and Access Management Access Analyzer provides the following capabilities: IAM Access Analyzer external access analyzers help identify resources in your organization and accounts that are shared with an external entity.
IAM Access Analyzer internal access analyzers help identify internal access to selected resources in your organization and accounts. IAM Access Analyzer unused access analyzers help identify unused access in your organization and accounts. IAM Access Analyzer validates IAM policies against policy grammar and AWS best practices.
IAM Access Analyzer custom policy checks help validate IAM policies against your specified security standards . IAM Access Analyzer generates IAM policies based on access activity in your AWS CloudTrail logs. IAM Access Analyzer helps you identify the resources in your organization and accounts, such as Amazon S3 buckets or IAM roles, shared with an external entity. This lets you identify unintended access to your resources and data, which is a security risk. IAM Access Analyzer identifies resources shared with external principals by using logic-based reasoning to analyze the resource-based policies in your AWS environment. For each instance of a resource shared outside of your account, IAM Access Analyzer generates a finding. Findings include information about the access and the external principal granted to it.
You can review findings to determine if the access is intended and safe or if the access is unintended and a security risk. In addition to helping you identify resources shared with an external entity, you can use IAM Access Analyzer findings to preview how your policy affects public and cross-account access to your resource before deploying resource permissions. The findings are organized in a visual summary dashboard. The dashboard highlights the split between public and cross-account access findings, and provides a breakdown of findings by resource type. To learn more about the dashboard, see View the IAM Access Analyzer findings dashboard .
An external entity can be another AWS account, a root user, an IAM user or role, a federated user, an anonymous user, or another entity that you can use to create a filter. For more information, see AWS JSON Policy Elements: Principal . For instructions on getting started, see Create an IAM Access Analyzer external access analyzer . After you create an analyzer, you can Manage an IAM Access Analyzer external access analyzer .
When you enable IAM Access Analyzer, you create an analyzer for your entire organization or your account. The organization or account you choose is known as the zone of trust for the analyzer. The analyzer monitors all of the supported resources within your zone of trust. Any access to resources by principals within your zone of trust is considered trusted. Once enabled, IAM Access Analyzer analyzes the policies applied to all of the supported resources in your zone of trust. After the first analysis, IAM Access Analyzer analyzes these policies periodically. If you add a new policy or change an existing policy, IAM Access Analyzer analyzes the new or updated policy within about 30 minutes.
When analyzing the policies, if IAM Access Analyzer identifies one that grants access to an external principal that isn't within your zone of trust, it generates a finding. Each finding includes details about the resource, the external entity with access to it, and the permissions granted so that you can take appropriate action. You can view the details included in the finding to determine whether the resource access is intentional or a potential risk that you should resolve. When you add a policy to a resource, or update an existing policy, IAM Access Analyzer analyzes the policy. IAM Access Analyzer also analyzes all resource-based policies periodically.
On rare occasions under certain conditions, IAM Access Analyzer does not receive notification of an added or updated policy, which can cause delays in generated findings. IAM Access Analyzer can take up to 6 hours to generate or resolve findings if you create or delete a multi-region access point associated with an Amazon S3 bucket, or update the policy for the multi-region access point. Also, if there is a delivery issue with AWS CloudTrail log delivery or resource control policy (RCP) restriction changes, the policy change does not trigger a rescan of the resource reported in the finding. When this happens, IAM Access Analyzer analyzes the new or updated policy during the next periodic scan, which is within 24 hours. If you want to confirm a change you make to a policy resolves an access issue reported in a finding, you can rescan the resource reported in a finding by using the Rescan link in the Findings details page, or by using the StartResourceScan operation of the IAM Access Analyzer API. To learn more, see Resolve IAM Access Analyzer findings .
For external access, IAM Access Analyzer analyzes only policies applied to resources in the same AWS Region where it's enabled. To monitor all resources in your AWS environment, you must create an external access analyzer to enable IAM Access Analyzer in each Region where you're using supported AWS resources. For unused access, findings for the analyzer do not change based on Region. Creating an unused access analyzer in each Region where you have resources is not required.
For your selected business-critical resources, IAM Access Analyzer helps you identify which principals within your organization or account have access to them. This analysis supports implementing the principle of least privilege by ensuring that your specified resources can only be accessed by the intended principals within your organization. For instructions on getting started, see Create an IAM Access Analyzer internal access analyzer . After you create an analyzer, you can Manage an IAM Access Analyzer internal access analyzer .
Determine which IAM users or roles within your account or organization can access your specified resources Understand access paths between principals and resources within your AWS environment Review findings to determine if the access is intended and safe or if the access is unintended and presents a security risk IAM Access Analyzer helps you identify and review unused access in your AWS organization and accounts. IAM Access Analyzer continuously monitors all IAM roles and users in your AWS organization and accounts and generates findings for unused access. The findings highlight unused roles, unused access keys for IAM users, and unused passwords for IAM users.
For active IAM roles and users, the findings provide visibility into unused services and actions. For instructions on creating an unused access analyzer and managing its findings, see Manage an IAM Access Analyzer unused access analyzer . IAM Access Analyzer reviews last accessed information for all roles in your AWS organization and accounts to help you identify unused access. IAM action last accessed information helps you identify unused actions for roles in your AWS accounts. For more information, see Refine permissions in AWS using last accessed information .
The findings for external, internal, and unused access analyzers are organized into a visual summary dashboard. The dashboard highlights your AWS resources and AWS accounts that have the most findings and provides a breakdown of findings by type. For more information about the dashboard, see View the IAM Access Analyzer findings dashboard . You can validate your policies against IAM policy grammar and AWS best practices using the basic policy checks provided by IAM Access Analyzer policy validation. You can create or edit a policy using the AWS CLI, AWS API, or JSON policy editor in the IAM console. You can view policy validation check findings that include security warnings, errors, general warnings, and suggestions for your policy. These findings provide actionable recommendations that help you author policies that are functional and conform to AWS best practices. To learn more about validating policies using policy validation, see Validate policies with IAM Access Analyzer . For a list of the policy checks that IAM Access Analyzer performs, see Checks for validating policies .
You can validate your policies against your specified security standards using the IAM Access Analyzer custom policy checks. You can create or edit a policy using the AWS CLI, AWS API, or JSON policy editor in the IAM console. Through the console, you can check whether your updated policy grants new access compared to the existing version. Through AWS CLI and AWS API, you can also check specific IAM actions that you consider critical are not allowed by a policy. These checks highlight a policy statement that grants new access. You can update the policy statement and re-run the checks until the policy conform to your security standard. To learn more about validating policies using custom policy checks, see Validate policies with IAM Access Analyzer custom policy checks .
IAM Access Analyzer analyzes your AWS CloudTrail logs to identify actions and services that have been used by an IAM entity (user or role) within your specified date range. It then generates an IAM policy that is based on that access activity. You can use the generated policy to refine an entity's permissions by attaching it to an IAM user or role. To learn more about generating policies using IAM Access Analyzer, see IAM Access Analyzer policy generation .
IAM Access Analyzer charges for unused access analysis based on the number of IAM roles and users analyzed per analyzer per month. Creating unused access analyzers across multiple Regions will result in you being charged for each analyzer. Service-linked roles aren't analyzed for unused access activity and they aren't included in the total number of IAM roles analyzed.
IAM Access Analyzer charges for internal access analysis based on the number of resources monitored per internal access analyzer per month. 2. System Architecture & Core Working Principles IAM Access Analyzer charges for custom policy checks based on the number of API requests made to IAM Access Analyzer to check for new access.
For a complete list of prices and charges for IAM Access Analyzer, see IAM Access Analyzer pricing . To see your bill, go to the Billing and Cost Management Dashboard in the AWS Billing and Cost Management console . Your bill contains links to usage reports that provide details about your bill. To learn more about AWS account billing, see the AWS Billing User Guide Identity and Access Management (IAM) lets you create and manage permissions for Google Cloud resources. IAM unifies access control for Google Cloud services into a single system and presents a consistent set of operations.
Access 20+ free products for common use cases, including AI APIs, VMs, data warehouses, and more. Quickstarts: Quickstart: Grant an IAM role by using the Google Cloud console or Quickstart: Write an IAM policy by using client libraries These lectures, demos, and hands-on labs give you an overview of Google Cloud products and services so that you can learn the value of Google Cloud and how to incorporate cloud-based solutions into your business strategies.
This course features a combination of lectures, design activities, and hands-on labs to show you how to use proven design patterns on Google Cloud to build highly reliable and efficient solutions and operate deployments that are highly available and cost-effective. In this training course, you will learn about a variety of Google Cloud security controls and techniques. You'll explore the components of Google Cloud and deploy a secure solution on the platform. You'll also learn how to mitigate attacks at several points in a Google Cloud-based infrastructure, including distributed denial-of-service attacks, phishing attacks, and threats involving content classification and use.
Book-length deep dive into IAM, including corporate, consumer, and service identities; best practices, and how to assess, plan, and deploy. Policies Access Resource hierarchy Discusses the security controls designed to help manage data access to and prevent data exfiltration of the pipeline from your data lake to your data warehouse. KMS Organization Policy Service Helps you with planning, designing, and implementing your migration process to Google Cloud. Planning Migration code samples are licensed under the Apache 2.0 License . For details, see the Google Developers Site Policies . Java is a registered trademark of Oracle and/or its affiliates.
You can use Policy Analyzer for Identity and Access Management (IAM) policies to help you find out which principals have what access to which Google Cloud resources. To learn about how Policy Analyzer works and how to use it, see Policy Analyzer for IAM policies in the Policy Intelligence documentation.
code samples are licensed under the Apache 2.0 License . For details, see the Google Developers Site Policies . Java is a registered trademark of Oracle and/or its affiliates. Register today for the Google Cloud Security Summit: Master security at the speed of AI with insights from leading industry voices. November 4, 9-10:30am PST .
Reimagine security with Google Cloud IAM, the unified foundation for governing both human and AI agent access at scale. Consolidate identity for your entire ecosystem: Enable your workforce to securely sign in using SSO and MFA with Google Cloud Identity or syncless Workforce Identity Federation with your own identity provider. Provide first-class cryptographic identities unique to your agents and applications allowing them to securely authenticate both as themselves and on behalf of the end user .
Simplify setup with Gemini for intelligent optimization. Eliminate guesswork by using the Gemini Role Picker to generate least-privilege roles from natural language. Use the broader Policy Intelligence suite to see what your users and agents have access to with Policy Analyzer , then automatically detect and remove excessive permissions, troubleshoot access issues, and ensure your policies remain secure and optimized over time.
Establish a secure foundation for your workforce, workloads, and AI agents. Use Organization Policies to create a centralized hierarchy for all resources. Define a security baseline with custom policies that programmatically enforce guardrails, ensuring human, workload, and agent access remains compliant with corporate policies from day one. Move beyond broad roles with precise permissions. Use Principal Access Boundary to down-scope agent access from full delegated user permissions. For human administrators, use Privileged Access Manager (PAM) to grant temporary, time-bound access for sensitive tasks, ensuring elevated privileges are never permanent and the "blast radius" of any identity is strictly contained .
Enforce a comprehensive Zero Trust model with dynamic, attribute-based access. Use Access Context Manager to create fine-grained access rules based on user identity and device context. Then, enforce these rules across your applications and Google Cloud services with Identity-Aware Proxy (IAP) and VPC Service Controls to create a secure, unified perimeter. Start secure with a built-in foundation. Establish governance with custom guardrails. Assign every human and agent an Identity. Deploy defense-in-depth Access Management to dictate what they can do. Finally, evaluate Access Risk to secure the context of every session.
Start secure with a built-in foundation. Establish governance with custom guardrails. Assign every human and agent an Identity. Deploy defense-in-depth Access Management to dictate what they can do. Finally, evaluate Access Risk to secure the context of every session. Give every agent a unique, short-lived identity using the SPIFFE framework for secretless mTLS auth. Onboard users by federating your existing identity provider . Eradicate risky keys by allowing keyless multi-cloud or on-prem authentication using Workload identity Federation . Safely orchestrate OAuth flows so agents act for users without ever exposing credentials.
Configure Workforce Identity Federation to use single sign-on (SSO) to access Google Cloud Give every agent a unique, short-lived identity using the SPIFFE framework for secretless mTLS auth. Onboard users by federating your existing identity provider . Eradicate risky keys by allowing keyless multi-cloud or on-prem authentication using Workload identity Federation . Safely orchestrate OAuth flows so agents act for users without ever exposing credentials.
Configure Workforce Identity Federation to use single sign-on (SSO) to access Google Cloud Use Gemini Role Picker for roles from natural language. Use IAM Recommender in SCC to remove excessive access. Use Principal Access Boundaries to restrict agents and Organization Policy for hierarchy-wide guardrails. Apply IAM Conditions to enforce context-aware access based on time, device, or resource attributes.
Use Gemini Role Picker for roles from natural language. Use IAM Recommender in SCC to remove excessive access. Use Principal Access Boundaries to restrict agents and Organization Policy for hierarchy-wide guardrails. Apply IAM Conditions to enforce context-aware access based on time, device, or resource attributes. Ringfence Model Context Protocol (MCP) servers and data with VPC Service Controls to prevent exfiltration. Secure all agent interactions—including Agent-to-Agent (A2A) communication—by routing traffic through the Agent Gateway , where Model Armor policies block prompt injections and harmful content. Use Security Command Center (SCC) for centralized threat detection and AI posture management.
Ringfence Model Context Protocol (MCP) servers and data with VPC Service Controls to prevent exfiltration. Secure all agent interactions—including Agent-to-Agent (A2A) communication—by routing traffic through the Agent Gateway , where Model Armor policies block prompt injections and harmful content. Use Security Command Center (SCC) for centralized threat detection and AI posture management.
This page describes how Google Cloud's Identity and Access Management (IAM) system works and how you can use it to manage access in Google Cloud. IAM is a tool to manage fine-grained authorization for Google Cloud. In other words, it lets you control who can do what on which resources .
Every action in Google Cloud requires certain permissions. When someone tries to perform an action in Google Cloud—for example, create a VM instance or view a dataset—IAM first checks if they have the required permissions. If they don't, then IAM prevents them from performing the action. To give the principal permission to access the resource, you grant them a role on the resource. You grant these roles using an allow policy .
Allow policies are directly attached to some Google Cloud resources, which are organized hierarchically —for example, projects contain service-specific resources. This means that you can grant access to a single resource or a container of resources. In Google Cloud you control access for principals . Principals represent one or more identities that have authenticated to Google Cloud.
There are various types of principals in IAM, but they can be divided into two broad categories: Human users : Some IAM principal types represent human users. You use these principal types for managing your employees' access to Google Cloud resources. Principal types that represent human users include Google Accounts, Google groups, and federated identities in workforce identity pools.
Workloads : Some IAM principal types represent workloads. You use these principal types when managing your workloads' access to Google Cloud resources. Principal types that represent workloads include service accounts and federated identities in a workload identity pool. Permissions determine what operations are allowed on a resource. In IAM, permissions are typically represented in the form service . resource . verb . Often, permissions correspond one-to-one with REST API methods—for example, the resourcemanager.projects.list permission lets you list Resource Manager projects.
3. Software Implementation, Frameworks & Protocols You can't directly grant permissions to a principal . Instead, you give principals permissions by granting them roles . Roles are collections of permissions. When you grant a role to a principal, you give that principal all of the permissions in that role.
Predefined roles : Roles that are managed by Google Cloud services. These roles contain the permissions needed to perform common tasks for each given service. For example, the Pub/Sub Publisher role ( roles/pubsub.publisher ) provides access to publish messages to a Pub/Sub topic. Custom roles : Roles that you create that contain only the permissions that you specify. You have complete control over the permissions in these roles. However, they have a higher maintenance burden than predefined roles and there's a limit to the number of custom roles that you can have in your project and in your organization.
Basic roles : Highly permissive roles that provide broad access to Google Cloud services. These roles can be useful for testing purposes, but shouldn't be used in production environments. Most Google Cloud services have their own resources. For example, Compute Engine has resources like instances, disks, and subnetworks.
In IAM, you grant roles on a resource. Granting a principal a role on a resource means that the principal can use the permissions in that role to access the resource. You can grant roles on a subset of Google Cloud resources. For a full list of resources that you can grant roles on, see Resource types that accept allow policies .
Google Cloud also has container resources, including projects, folders, and organizations. These container resources are organized hierarchically, which lets child resources inherit the policies of their parent resources. This means that granting a principal a role on a container resource gives the principal access to both the container resource and the resources in that container. This feature lets you use a single role grant to manage access to multiple resources, including resources that you can't grant roles on directly. For more information, see Policy inheritance on this page.
You grant roles to principals using allow policies . In the past, these policies were referred to as IAM policies . Each allow policy contains a list of role bindings that associate IAM roles with the principals who are granted those roles. When an authenticated principal attempts to access a resource, IAM checks the resource's allow policy to determine whether the principal has the required permissions. If the principal is in a role binding that includes a role with the required permissions, then they're allowed to access the resource.
To see examples of allow policies and learn about their structure, see Understanding allow policies . Google Cloud has container resources—such as projects, folders, and organizations—that let you organize your resources in a parent-child hierarchy. This hierarchy is called the resource hierarchy . If you set an allow policy on a container resource, then the allow policy also applies to all resources in that container. This concept is called policy inheritance , because descendant resources effectively inherit their ancestor resources' allow policies.
You can use a single role binding to grant access to multiple resources. If you want to give a principal access to all resources in a container, then grant them a role on the container instead of on the resources in the container. For example, if you want to let your security administrator manage allow policies for all resources in your organization, then you could grant them the Security Admin role ( roles/iam.securityAdmin ) on the organization.
You can grant access to resources that don't have their own allow policies. Not all resources accept allow policies, but all resources inherit allow policies from their ancestors. To give a principal access to a resource that can't have its own allow policy, grant them a role on one of the resource's ancestors. For example, imagine you want to give someone permission to write logs to a log bucket. Log buckets don't have their own allow policies, so to give someone this permission, you can instead grant them the Logs Bucket Writer role ( roles/logging.bucketWriter ) on the project that contains the log bucket.
To understand who can access a resource, you need to also view all of the allow policies that affect the resource . To get a complete list of the principals that have access to the resource, you need to view the resource's allow policy and the resource's ancestors' allow policies. The union of all of these policies is called the effective allow policy . For more information about policy inheritance for allow policies, see Using resource hierarchy for access control .
In addition to allow policies, IAM provides the following access control mechanisms to help you refine who has access to what resources: Additional policy types : IAM offers the following policy types in addition to allow policies: Deny policies : Deny policies prevent principals from using certain permissions, even if they're granted a role with the permission.
Principal Access Boundary (PAB) policies : Principal Access Boundary policies define and enforce the resources a principal is eligible to access. Principals can't access resources that they're not eligible to access, even if they've been granted a role on the resource. IAM Conditions : IAM Conditions lets you define and enforce conditional, attribute-based access control. You can use conditions in various policy types. For example, you can add a condition to a role binding in an allow policy to ensure that the role is only granted if the condition is met.
You can write conditions based on attributes like the resource in the request and the time of the request. Privileged Access Manager (PAM) : With Privileged Access Manager, you can let principals request and be given temporary, auditable access to resources. For example, you could require that principals request access each time they want to view a sensitive resource instead of permanently granting them a IAM role.
You can also configure whether principals are required to provide justifications or get approvals when they request access. To learn more about Privileged Access Manager, see Privileged Access Manager overview . The IAM API is eventually consistent . In other words, if you write data with the IAM API, then immediately read that data, the read operation might return an older version of the data. The changes that you make might also take time to affect access checks.
This consistency model affects how the IAM API works. For example, if you create a service account, then immediately refer to that service account in another request, the IAM API might say that the service account couldn't be found. This behavior occurs because operations are eventually consistent; it can take time for the new service account to become visible to read requests.
If you're new to Google Cloud, create an account to evaluate how our products perform in real-world scenarios. New customers also get $300 in free credits to run, test, and deploy workloads. code samples are licensed under the Apache 2.0 License . For details, see the Google Developers Site Policies . Java is a registered trademark of Oracle and/or its affiliates.
Identity and access management (IAM ) is now the core control point of modern cybersecurity . As hybrid and multiIcloud adoption accelerates, authentication and authorization systems are increasingly becoming the primary target of attackers. Recent security analyses show a steep rise in attacks that leverage the use of valid identities. This means that adversaries no longer break in but instead simply log in using real accounts.
The IBM XIForce® Threat Intelligence Index reports a 71% yearIoverIyear surge in the use of stolen credentials. At the same time, organizations are managing identity populations that have evolved far beyond employees and customers. Today’s infrastructure contains vast numbers of nonIhuman identities (NHIs) , like service accounts, workloads, bots, API keys, devices and automated agents.
Across cloud, onIpremises and hybrid ecosystems, these NHIs outnumber human identities by fifty to one, and frequently operate with elevated permissions. Left unmanaged, NHIs create “shadow access” meaning permissions and connections that operate invisibly and disproportionately increase risk and introduce avoidable vulnerabilities. This guide provides a comprehensive blueprint for deploying a modern IAM program. It combines best practices from enterprise IAM frameworks, cloudInative patterns and fieldItested architectures. It outlines the challenges teams face and then presents actionable guidance for implementing identity services and identity governance across both legacy and modern systems. The result is an IAM solution built for the real world, focused on mitigating identityIbased attacks while supporting scalability, compliance and usability.
Join security leaders who rely on the Think Newsletter for curated news on AI, cybersecurity, data and automation. Learn fast from expert tutorials and explainers—delivered directly to your inbox twice weekly. See the IBM Privacy Statement . More than any other single control, identity determines who can do what within your systems. The expansion of cloud and remote work has drastically increased the number of entry points, making identity the most attractive target for attackers.
Reports show a significant rise in cyberattacks that rely on stolen or misused valid accounts rather than exploitIbased intrusions, driving security teams to treat identity as a firstIclass layer of defense. The IBM 2026 X-Force Threat Intelligence Index shows that 32% of initial access vectors are attributed to valid account takeover. Protecting user accounts, tokens and service credentials is critical to preventing unauthorized access and insider threats.
Therefore, organizations must treat IAM not only as an IT function but as a critical extension of their security perimeter. Authentication endpoints, token issuance systems, service account credentials and workload identities are components in a much larger trust architecture. If any of these parts are insufficiently protected or poorly monitored, they become easy channels for lateral movement and privilege escalation. Mature programs pair single signIon (SSO) and multiIfactor authentication (MFA) with strong authorization models and resilient data planes to avoid gaps that attackers can use.
Identity verification with passwords, MFA, biometric factors, certificates, OAuth / OIDC or federated identity credentials. Decide who can do what and under which conditions by using role-based access control (RBAC) or attribute-based access control (ABAC) . Be sure to consistently grant access by using least privilege principle. 4. Practical Deployment, Analysis & Case Studies Record identityIrelated activity for compliance, analytics and incident response (IR) . Make sure to produce authoritative audit trails for frameworks like GDPR, ISO 27001, SOC 2 and PCI DSS.
Service accounts, API keys, certificates, workload identities and IoT devices perform critical tasks but commonly lack clear ownership and lifecycle controls. As automation and AI multiply NHIs faster than teams can manually manage them, these identities become major gaps. A modern IAM system enforces the same governance to NHIs as it does for people. This includes ownership, purpose, least-privilege scope, rotation, monitoring and audited deprovisioning.
Whether you're a builder, defender, business leader or simply want to stay secure in a connected world, you'll find timely updates and timeless principles in a lively, accessible format. New episodes on Wednesdays at 6am EST. Multiple directories, identity providers, secrets stores and access tools often evolve independently, resulting in duplicated policies, poor user experience and administrative overhead. In fewer words, the identity environment becomes jumbled and unmanageable. It is important to integrate instead of replacing to reduce complexity and unify SSO across software as a service (SaaS) , onIpremises and multiIcloud.
Manual provisioning and deprovisioning create delays and orphaned user accounts, especially through mergers and system migrations. Role changes accumulate access over time, deviating from job functions. Automating the lifecycle with human resources information systems (HRIS) triggers, system for cross-domain identity management (SCIM) and policyIdriven workflows reduces risk and keeps access clean.
NHIs proliferate through continuous integration/continuous delivery ( CI/CD ) and platform automation. Many lack owners or permissions review, accumulating powerful identities with unclear accountability. Inventory, tagging, expirations and review cycles are essential to govern NHIs and prevent unauthorized access to sensitive data. You should integrate existing capabilities into a single IAM platform. This platform should deliver consistent SSO, OAuth/OIDC flows, PAM hooks and NHI governance across SaaS, custom apps and legacy systems.
Inventory and classify NHIs: Build a registry with identity type, owner, scope, token or secret lifetime and last rotation. Freeze escalation for identities lacking owners. These actions quickly reveal highIrisk accounts and shrink “shadow access.” Enforce MFA and conditional access: Start with admins and highIrisk cohorts and implement MFA, device posture checks and restrict legacy protocols. This will rapidly boost the security posture and aligns with zero trust principle.
Automate offboarding: For contractors and temporary NHIs, set an expiration at creation. Connect HR termination events to the IAM system to disable accounts, revoke tokens and remove privileged roles automatically. Stabilize the identity data plane: Use globally available identity data for sessions, attributes and authorization. Eliminate delays and stale state that break logins or keep access after revocation.
CloudInative IAM emphasizes global scalability, strong consistency for attributes and entitlements, standardsIbased OAuth, OIDC or federated identity and ABAC or RBAC that map cleanly to job functions and organization’s needs. IBM Cloud® IAM provides users, service IDs, access groups and trusted profiles. API key access token exchange yields shortIlived tokens that require refresh. Services like Db2® on Cloud accept IAM tokens and tokens remain valid for the connection but require renewal for new sessions. Integrate IBM Key Protect for key lifecycle management. Revoking a root key can render a database unreadable, so apply strict change control with stakeholders and security teams.
Lifecycle is foundational, and you should flow identity data from a single authoritative source (often the HRIS) into your directory, and then into applications and cloud accounts. GroupIbased provisioning streamlines entitlement mapping. Trusted profiles and policyIdriven context reduce proliferation of static service credentials. These measures meet security requirements, support GDPR data minimization, reduce manual process errors and establish a stable setup for future upgrades.
Authentication should be secure while not hindering the user experience. This can be accomplished by implementing: These choices protect sensitive data and improve user experience while aligning to zero trust. Authorization goes hand in hand with authentication and determines the flexibility and safety of user access. To ensure effective authorization, implement the following steps: Centralizing identity telemetry is crucial for generating durable audit trails that support robust security operations. This approach should encompass the collection and correlation of key events. These events include authentication and token activities, authorization decisions and associated policy snapshots, administrative actions and their lifecycle workflows, secret rotations and expiry enforcement and correlated identity events. This comprehensive telemetry will be invaluable for both incident response and forensic investigations.
A robust security posture relies heavily on comprehensive auditability. This auditability includes encompassing the collection of authentication and token events, authorization decisions with policy snapshots, administrator actions and their lifecycle management, secret rotations and expiry enforcement and correlated identity events. This centralized approach generates durable audit trails, providing critical evidence for incident response and demonstrating compliance with regulatory requirements.
It is crucial that identity and access management continues to operate during failures. You can ensure this by implementing the following measures: Sustainability depends on a clear governance operating model in which each application and NHI has a named owner accountable for access policies and validation. Changes in security, including privileged access management updates and key rotations, are subject to formal change control and require crossIfunctional review with stakeholders and security teams.
The model includes regular reviews, with quarterly access reviews, monthly NHI rotations for highIrisk systems and automated alerts to detect configuration or policy drift. The effectiveness of this model is tracked through time to provision and deprovision access, trends in orphaned accounts, the percentage of leastIprivilege entitlements, policy coverage and login success and error rates. Delivery follows a staged roadmap that prioritizes quick wins, establishes platform foundations, formalizes NHI governance, advances policyIasIcode and introduces advanced analytics. All of these being aligned to business milestones and compliance deadlines.
Priorities should include stale access caused by orphaned user accounts, unexpired NHIs and lingering entitlements after role changes. Focus should also include longIlived secrets such as static keys that lack rotation or clear ownership. Organizations also face risk from inconsistent policy enforcement. The inconsistent policy enforcement might include regional or system drift that produces different authorization outcomes and from overIpermissioned roles in which broad groups are used as shortcuts instead of a leastIprivilege design. Extra exposure comes from shadow access paths, including back door scripts, legacy agents or untracked service credentials.
Weak federation resulting from misconfigured federated identity or gaps in token validation might be another point of exposure. Identity governance controls should be mapped to established frameworks such as ISO 27001, SOC 2, PCI DSS and GDPR, with clear definition of evidence sources and accountable owners for each control. This evidence typically includes provisioning and deprovisioning logs and workflows, MFA posture and privileged access management audit logs, records of NHI ownership, rotation and expiration, authorization decision logs and access policy history and token issuance histories along with single signIon assertions and identity verification outcomes.
Accountable ownership is crucial because it ensures clear responsibility and reliable evidence for security. Evidence must be consistent across regions and explicitly tied to named stakeholders for formal signIoff. Strong data consistency reduces ambiguity during audits and strengthens the overall security posture. Unify the fabric : Integrate existing identity providers behind a single policy and token fabric by using open standards (OAuth, OIDC, SAML).
Automate lifecycle : HRIS → directory → SaaS and app provisioning and deprovisioning through SCIM and policyIasIcode. Step-up authentication : implement MFA, passwordless, biometric, conditional access and stepIup for sensitive operations. Harden authorization : Blend RBAC/ABAC, implement leastIprivilege and enforce shortIlived grants and reviews. Govern NHIs : Ownership, expirations, rotation, federation over static keys and reliable refresh logic.
Stabilize data : Strongly consistent identity attributes, entitlements and sessions across regions. Instrument and prove : Centralize logs, build durable audit trails and automate compliance validation. Integrate PAM : Tie privileged elevation to identity workflows with approvals, JIT and monitoring. Measure and iterate : Track provisioning SLAs, drift, login reliability and policy coverage. Ensure that the roadmap is refined quarterly.
Modern IAM secures both people and machines across hybrid and multicloud environments with equal precision. By integrating identity providers, identity governance workflows, secrets management and distributed data into a unified IAM platform, organizations achieve resilient access control at scale. FirstIclass NHI governance , strong multiIregion consistency, automated lifecycle processes and durable audit trails form the pillars of robust identity and access management.
These capabilities reduce vulnerabilities and ensure that humans and workloads alike receive the right permissions at the right time. All of this leads to the protection of sensitive data, alignment to security requirements and safely meeting today’s demands without sacrificing tomorrow’s goals. As AI automation scales, identity becomes a control plane for AI trust, risk, and security. Without verified identities, agents can trigger runaway loops, deepfake scams, and unauthorized actions at machine speed.
The global average cost of a data breach reached USD 4.99M while AI-driven attacks increased 56%. Explore the latest findings. Download it to learn how to align security and development workflows, prioritize real risk, and build a measurable, audit-ready remediation practice that scales.
In this webinar, learn how to use HCP Vault Radar to detect, remediate, and import exposed secrets into Vault for secure storage — before attackers can exploit them. From secrets scanning and rotation to seamless backup and recovery, this white paper breaks down the 12 capabilities every secrets management approach must have. We’ll cover how a platform-agnostic secrets manager like HashiCorp Vault gives more precise control over how secrets are stored, tracked, transmitted, accessed, rotated, and revoked — no matter where they’re located.
Download the ebook now for the inside scoop on eliminating secret sprawl without slowing down innovation. 5. Performance Evaluation & Extended Technical Observations Learn how integrated identity platforms simplify access across hybrid environments with smarter visibility, adaptive governance and AI-powered threat detection.
Learn how passwordless authentication is transforming enterprise security. Discover key market insights, leading solutions, and practical guidance to help your organization choose the right approach. Learn how IBM leads in access management with secure authentication, single sign-on (SSO) and adaptive access, recognized as a leader for the third year in a row.
AI agents and services are creating identities faster than teams can manage. See why KuppingerCole named HashiCorp an Overall Leader in Non-Human Identity Management, and how zero trust, dynamic credentials, and policy-based access control keep every identity in check. Identity orchestration connects your tools, enforces consistent security and automates processes from onboarding to offboarding, delivering seamless user experiences, stronger security and vendor flexibility.
Manage access to secrets and stop credentials from falling into the wrong hands with identity-based security for humans, machines, and the AI agents now operating across your infrastructure. Protect and manage user access with automated identity controls and risk-based governance across hybrid-cloud environments.
Enhance identity and access management (IAM) with IBM Verify for seamless hybrid access and strengthen identity protection by uncovering hidden identity-based risks with AI. There are a number of Google Cloud products and services that you can use to help your organization develop an approach for identity governance and access management for applications and workloads running on Google Cloud. This document is intended for security administrators, operations managers, and enterprise architects who work in customer teams and who want to learn about these tools and controls and how to use them.
A user account without administrative access to manage Cloud Identity groups and users. You need this account to test some of the controls that you set in the example procedures in this document. If you don't already have access to a Google Cloud project and administrative access to Cloud Identity, see Creating a Google Cloud project and Setting up Cloud Identity .
It's a best practice to remove user accounts when they are no longer needed because unused (orphaned) user accounts and service accounts can pose a security risk. You can use Google Cloud Policy Intelligence in the following ways to help your enterprise understand and reduce risk: The Identity and Access Management (IAM) recommender is part of the Policy Intelligence suite of tools and services. It uses machine learning (ML) to make smart access control recommendations to help you identify accounts that no longer need access to Google Cloud resources. You can then review the recommendations and decide whether to apply them. IAM recommender also helps you to maintain the principle of least privilege across all the members in your organization. In addition to providing recommendations, the Recommender service uses ML to provide detailed insights . Insights are findings that highlight notable patterns in resource usage. For example, you can collect additional information about permission usage in your project, identify permissions that aren't being used and are no longer needed, and identify unused service accounts .
It's possible to view and apply IAM recommendations in the Google Cloud console at an enterprise-level scale. In the following example procedure, you use BigQuery to review and rightsize access permissions in your organization. To set up the BigQuery integration, you configure an export of recommendations made by IAM recommender to a BigQuery dataset. This data can then be queried and reviewed using visualization tools such as Data Studio and Looker .
In the Google Cloud console, on the project selector page, select or create a Google Cloud project . BigQuery is automatically enabled in new projects. To activate BigQuery in a pre-existing project, enable the BigQuery API. Configure the BigQuery Data Transfer Service to pull data from IAM recommender. To learn more, see Exporting recommendations to BigQuery .
You run this query to identify the recommender_subtype subtype of IAM Recommender REMOVE_ROLE recommendations. Click Run . You use the query result to identify unused roles and rightsize IAM role bindings. You can save query results to Sheets. To learn more, see Saving query results to Sheets . Enterprise administrators need the ability to let users request access to resources. Typically, these requests go through an approval process where a designated approver or a group of approvers must approve the request before access is given.
Google Groups lets you apply an access policy to a collection of users, enabling you to follow the policy management best practice of giving access to resources based on group membership. This approach keeps policies relevant as join, move, and leave events occur through group membership changes. You can give and change access controls for a whole group with Google Groups, instead of giving or changing access controls one at a time for individual users or service accounts. You can also easily add members to and remove members from a Google group instead of updating an IAM policy to add or remove users.
You can create and manage a Google group using Cloud Identity . Cloud Identity is an identity as a service (IDaaS) solution that manages users and groups. You can also configure Cloud Identity to federate identities between Google and other identity providers, such as Active Directory and Azure Active Directory . Google Groups also lets a user request membership to a group. This request is routed to group administrators who can then approve or decline that request. To learn more, see Create a group and choose group settings .
When you create and manage a Google group to give access to Google Cloud resources, make sure to consider the implications of the settings that you select. Although we recommend that you minimize the number of users who can manage the group, we recommend that you set up more than one group administrator to always have access to the group. We also recommend that you restrict group membership to users in your organization.
In this example procedure, you create a Google group and give the viewer group access to a sample Google Cloud project. Members that you add to this group (or that you give access to upon request) are able to view the sample Google Cloud project. The following steps assume that you have Cloud Identity configured. To learn more, see Setting up Cloud Identity . Make sure that you have the permissions that you need to manage groups.
To add members to the group, click Add member , then enter the email address for the member and choose their Google Groups role . Group settings can only be managed within Google Groups. To configure group settings, click Manage this group in Google Groups . To select who can join the group, in the Who can join the group menu, select Organization users only .
In the following procedure, you use a test user account to demonstrate the steps that users in your organization use to request access to a Google group. Once access is given, the non-administrative user account that you used to make the request should be able to view the Google Cloud PROJECT_ID project that the group has Viewer access to.
There might be situations when users in your enterprise require temporary, short-term access to Google Cloud resources. Short-term access is useful when developers need temporary access to Google Cloud resources to perform certain tasks. Short-term access also offers the following advantages: Being able to give this type of access is useful for administrators when users need access to resources in emergency situations that require quick and direct intervention. However, it can be difficult to manually track short-term access permissions and ensure that they are removed in a timely manner. IAM conditional access policies let you set temporary (expiring) access to Google Cloud resources using conditional role bindings, helping to reduce this overhead for administrators.
You can add conditional role bindings to new or existing IAM policies to further control access to Google Cloud resources. Some examples of when you might use conditional role bindings to give a user or a group temporary access are as follows: When you use Google Groups to give users access to Google Cloud resources, you can use the group membership expiration feature to set expirations for group membership using the Cloud Identity Groups API. When the time that you specify has passed, users are removed from the group automatically.
You can use a conditional role binding to give developers temporary access to administer a specific Compute Engine instance. In this example, the role binding is set to expire on December 31, 2021. Replace USER_ID_TO_GIVE_TEMPORARY_ACCESS_TO with the username of the user in your organization that you want to give temporary access to.
You give temporary access to this instance to a user in your organization in the following steps. Retain the Compute Engine instance that you create. You use this instance later in this document in Managing privileged access . Alternatively, you can delete the example-instance-1 instance by running the following command: If you need to review IAM lifecycle events such as policy changes, service account creation, and service account assignments for auditing, Cloud Audit Logs can help. Administrators can use Cloud Audit Logs to look back at historical data for forensics and analysis. Analyzing audit logs can help you to understand access patterns and access anomalies. Audit log analysis can also be important for the following scenarios: Cloud Audit Logs stores information about the actions that users take, where the activity occurred, and when. Audit logs are classified as follows: We recommend that you use the following audit logs for identity and access related administrative logging: Admin Activity audit logs store changes made to Google Cloud resources such as projects, Compute Engine instances, and service accounts. The following are examples of events that Admin Activity audit logs store: Policy Denied audit logs record when a user or a service account is denied access to a Google Cloud service due to a security policy violation.
You can view audit logs in the Google Cloud console or query the logs using the Cloud Logging API or the command-line interface . Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Microsoft%20Azure • https://en.wikipedia.org/wiki/Microsoft%20Forefront • https://en.wikipedia.org/wiki/Netwrix • https://docs.aws.amazon.com/iam/ • https://docs.aws.amazon.com/IAM/latest/UserGuide/what-is-access-analyzer.html • https://cloud.google.com/iam/docs • https://docs.cloud.google.com/iam/docs/analyze-access • https://cloud.google.com/products/iam • https://docs.cloud.google.com/iam/docs/overview • https://www.ibm.com/think/topics/iam-deployment-guide
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Cloud Identity And Access Management Policy Analyzer.
[*] Metasploit Scan Running on Target Subnet for Cloud Identity And Access Management Policy Analyzer... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |