Complete Technical Paper Content — Cloud Instance Forensic Acquisition Tool Using Python
Overview & System Context
Cloud Instance Forensic Acquisition Tool Using Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~7771 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Part 1 of this series covered why cloud acquisition outpaces physical imaging and walked through how to create a snapshot and provision a forensic disk from it. You now have a forensic disk, an isolated, point-in-time copy of the compromised instance's storage, as well as two paths forward: mount it to a forensic VM inside the cloud, or export and download it for local analysis. The right choice depends on your investigation's custody requirements, on existing lab infrastructure, and — especially on GCP — on which path preserves the complete forensic record.
Mounting the disk directly to a forensic VM in the same cloud environment is the operationally superior option for most investigations. There are no egress charges, no waiting on large transfers, and no cross-region latency. Your analysis environment sits in the same region as the evidence, which simplifies audit log correlation and avoids the jurisdictional complexity that can arise when data crosses cloud provider boundaries.
Cloud-native tooling runs without issue on forensic VMs in any of the three major clouds. The SIFT Workstation, Autopsy, The Sleuth Kit, and Volatility all operate the same on a forensic EC2, Azure VM, or GCP compute instance as they do on a local workstation. The added benefit: Every action against the evidence disk stays under the same cloud audit trail as the original incident, creating one consistent chain-of-custody record.
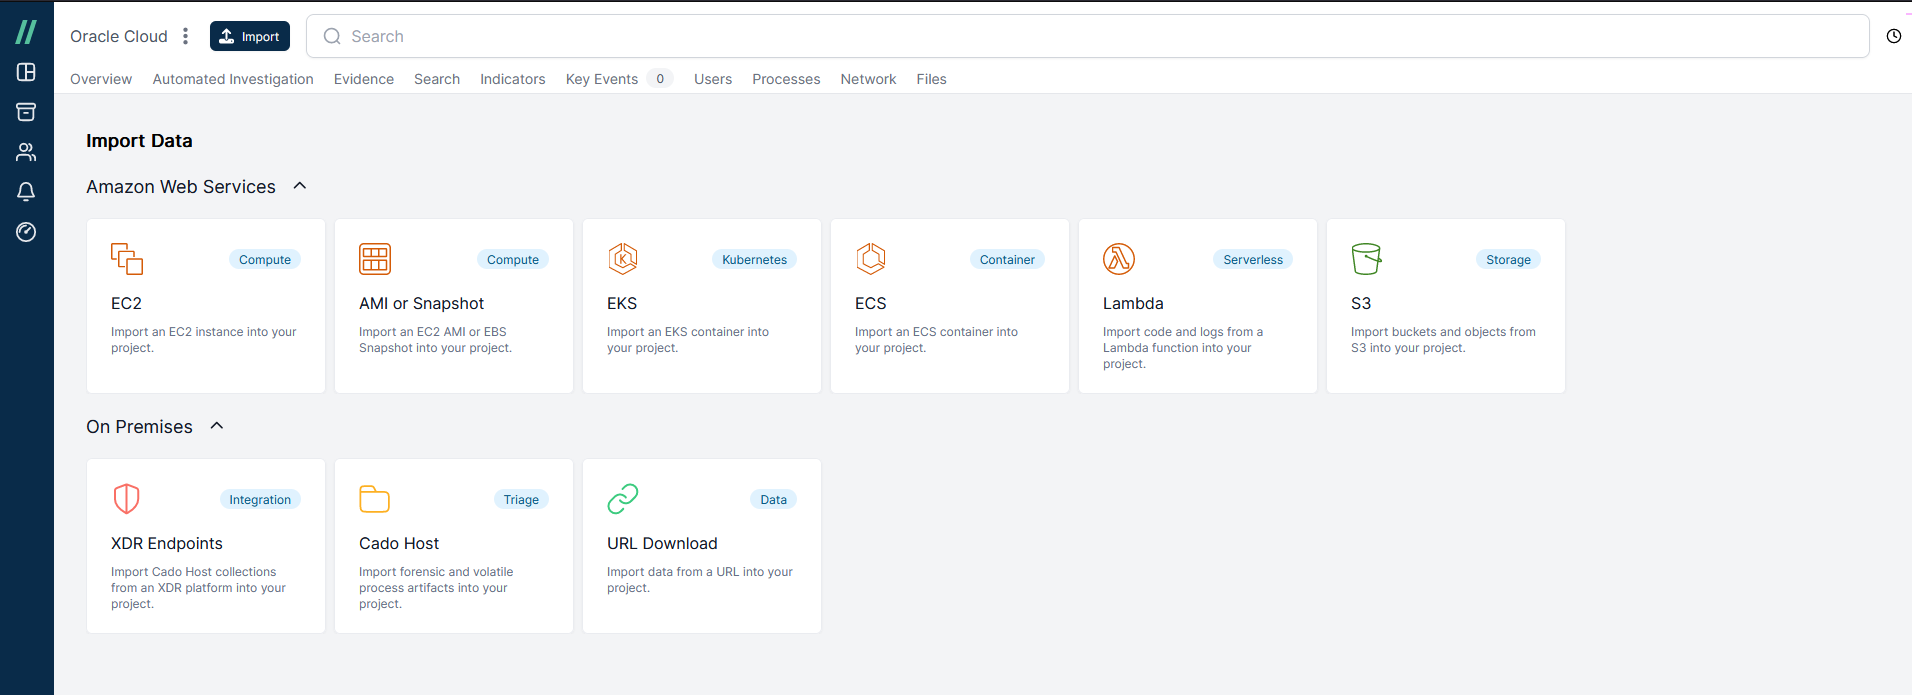
The output of the disk creation event from Part 1 will include a volume ID that you will use in the following command. Additionally, you need to identify the instance ID of your forensics VM. Figure 1: Oracle Cloud Virtual Machines | Darktrace / Forensic Acquisition and ... AWS has no native read-only attach flag at the API level. Enforce read-only access at the OS mount layer on Linux, or via write-blocker software on Windows.
Identify the evidence disk’s name, the forensic VM’s name, and the resource group in which they live. Like AWS, Azure has no native read-only attach flag at the API level. Enforce read-only access at the OS mount layer on Linux, or via write-blocker software on Windows. Keep the forensic VM in the same Azure region as the source evidence. Before we go into the steps of mounting the evidence disk to the forensic VM in Google Cloud, we must note an important caveat with Google Cloud snapshotting. The snapshotting process in Google Cloud only captures allocated space. What this means from the DFIR perspective is that you won’t be able to carve deleted files from unallocated space. Just keep this limitation in mind when reporting your analysis.
Figure 2: Cloud Digital Forensics Investigation – Ingite GCP's --mode=ro is an API feature enforced at the hypervisor layer, not just the OS mount. This is the most robust read-only guarantee of the three clouds. The disk must not be currently attached to any instance in read-write mode, and both the disk and VM must be in the same zone. Multiple forensic VMs can attach the same disk simultaneously when all use --mode=ro.
For Windows VMs attaching a disk read-only in GCP, before use you must mount the disk local and set the read-only attribute first via the following steps using diskpart: Run all file system analysis against the mounted read-only device. Never chown, chmod, or write to the evidence mount path. Autopsy, The Sleuth Kit (fls, icat, mactime), and SIFT provide full analysis capability directly on the block device. If a RAM capture was also collected from the compromised instance, Volatility can be run on the same forensic VM in parallel.
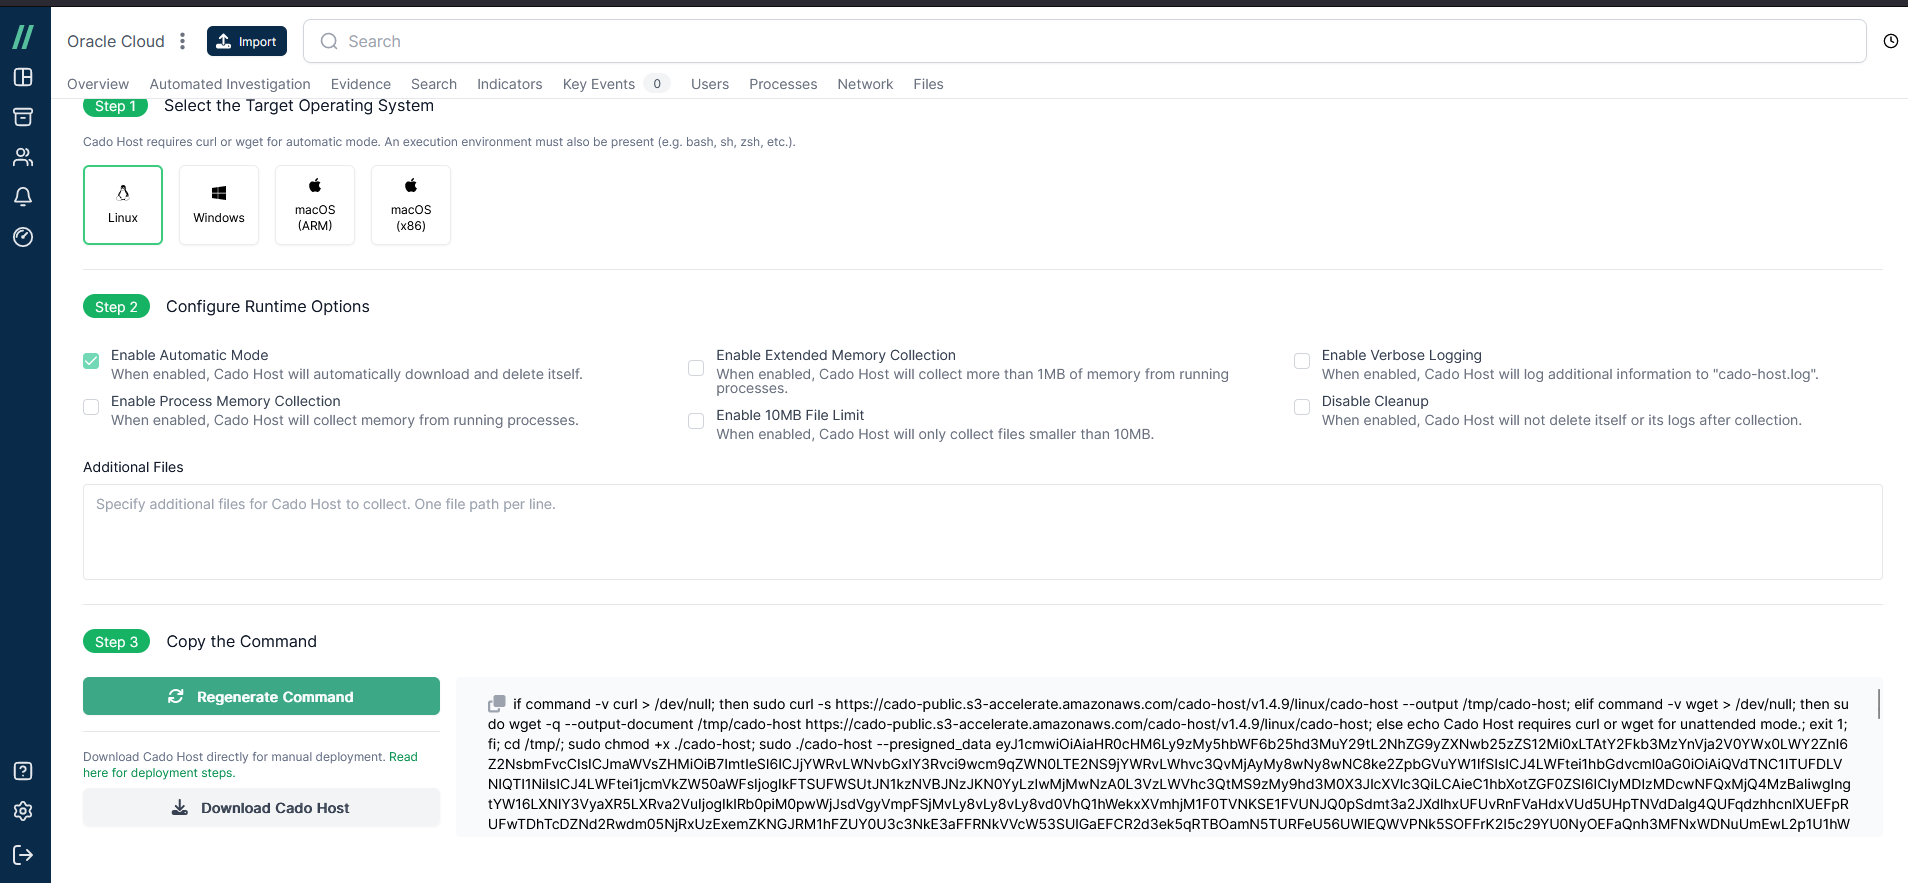
Local analysis is appropriate when jurisdiction requires keeping evidence on-premises, when your existing lab infrastructure (EnCase, FTK, X-Ways) is on local hardware, or when a legal hold requires physical custody of the image file. Understand the export format and its limitations for each cloud before committing to this path. EBS snapshots cannot be directly downloaded from AWS from the UI or CLI. The easiest method for downloading a snapshot to a disk image is to use AWS’s Coldsnap tool. Instead of creating a disk from the snapshot, as we saw in Part 1, take the snapshot ID, note the region it is in, and execute the following command: Figure 3: Oracle Cloud Virtual Machines | Darktrace / Forensic Acquisition and ...
While the evidence disk can be downloaded via a read-only SAS URI for the managed disk, due to the speed of this method, we instead recommend using Microsoft’s AzCopy . To do this, as with AWS, we are going to download the snapshot instead of the disk. First, create the SaaS URL from the UI with the following steps: AzCopy uses a multi-threaded approach which significantly outperforms directly downloading using the link in a browser.
First collect the image name from the Evidence disk, and then execute the following command and then choose a bucket that you want to store that disk in. GCP's export process uses Daisy, Google's workflow orchestration tool. It creates an ephemeral VM, attaches the disk, converts the image, and uploads to Cloud Storage. Supported --export-format options include vmdk, vhdx, vpc, vdi, and qcow2. The default output without --export-format is a disk.raw file, tarred and gzipped. Read the next section before using this path.
As mentioned above, there is no direct UI download for EBS snapshots. Instead, the AWS API or their Coldsnap tool must be leveraged. The best method is to use a combination of the console and UI to leverage AzCopy, as described in the CLI walkthrough above. As a reminder, here are the steps if you are taking that approach: Two paths, one decision: if the investigation stays in the cloud, mount the disk read-only to a forensic VM. If local custody is legally required, export but document the method's limitations in your case notes.
One preparation recommendation that applies regardless of cloud: Build a forensic VM template with your forensic tools (SIFT, Autopsy, The Sleuth Kit, etc.) pre-installed in each cloud environment before you need it. Incident response is not the time to provision and configure analysis infrastructure. Megan is a Senior Security Engineer at Datadog, SANS DFIR faculty, and co-author of FOR509. She holds two master’s degrees, serves as CFO of Mental Health Hackers, and is a strong advocate for hands-on cloud forensics training and mental wellness.
Physical disk forensics has a physical problem: the disk has to be in the room. When the target is a virtualized disk sitting in a cloud data center, you cannot attach a Tableau write-blocker to it. The acquisition model changes entirely in the cloud, and in most ways, it changes for the better. This post covers what cloud-native acquisition gives you that physical acquisition does not, and how to create a forensic snapshot on AWS, Azure, and Google Cloud.
Physical acquisition chains responders to hardware. Write-blockers prevent writes during imaging but require physical co-location with the target drive. When that drive is a virtual disk inside a cloud provider's infrastructure, co-location is not an option, as you are not seizing hardware from a data center cage. When physical access is feasible, the process still introduces friction: investigator travel, secure media shipment, and documented chain-of-custody at every handoff. Each step adds delay and creates an opportunity for evidentiary challenges.
Speed is another constraint. Physical imaging is bounded by the storage bus. A 1 TB drive over USB 3.0 takes 40 minutes at SSD speeds—and 1.5 to 3 hours for a typical spinning disk—before any analysis begins. Cloud snapshots are copy-on-write operations at the storage layer. They complete in seconds regardless of disk size, because the provider is not copying bytes synchronously at acquisition time.
Scale changes as well. Physical acquisition is one drive per investigator per imaging rig. Cloud snapshots can be automated across dozens of instances simultaneously. AWS Automated Forensics Orchestrator for Amazon EC2 is a published solution that demonstrates this pattern: event-driven, automated snapshot and isolation across an entire fleet in response to a GuardDuty finding.
Physical drives can sustain damage in transit, or contain bad sectors that cause inconsistent reads and complicate bit-for-bit verification. Cloud storage has no equivalent surface-level defect. A snapshot API call either succeeds or fails; there is no partial read corruption introduced by a degraded spindle. Cloud VM snapshots were designed for backup continuity, not forensic investigation. But that same API gives responders capabilities that exceed a write-blocker in most IR scenarios: remote access, API-level logging of every action, immutable storage options, and cryptographic hash integration.
Apply these permissions to a dedicated forensic IAM role, service account, or managed identity, not a named user account. Named accounts complicate attribution in audit logs and create credential-sharing risk. Note: The VM does not need to be stopped to create a snapshot, but Microsoft recommends a clean shutdown for filesystem consistency. Document your choice either way.
Note: Wait until snapshot status reaches UPLOADING before resuming any paused application writes on the source. A new disk based on the snapshot you took is the result of step one. Part 2 covers what to do with it: mounting a read-only evidence disk to a forensic VM within the cloud environment versus exporting or downloading the image for offline analysis. Part 2 will also address a Google Cloud unallocated space caveat where we will see that a true full disk image capture is not possible.
Leveraging AWS, Azure, and Google Cloud resources to gather evidence during investigations is a capability analysts train in FOR509: Enterprise Cloud Forensics and Incident Response. 2. System Architecture & Core Working Principles Megan is a Senior Security Engineer at Datadog, SANS DFIR faculty, and co-author of FOR509. She holds two master’s degrees, serves as CFO of Mental Health Hackers, and is a strong advocate for hands-on cloud forensics training and mental wellness.
Cloud forensics addresses the acquisition, preservation and analysis of digital evidence within cloud computing environments. Unlike traditional investigations that rely on physical seizure of hardware, cloud forensics must negotiate virtualised resources, dynamically provisioned services and multitenant architectures. Investigators contend with transient data, jurisdictional constraints and opaque provider policies, all of which complicate evidence collection and chain-of-custody procedures.
Emerging approaches combine live forensics with automated telemetry, API-driven snapshotting and collaborative workflows between forensic practitioners and cloud service providers. Proactive readiness frameworks seek to pre-position potential artefacts, while reactive tools reconstruct event timelines from volatile logs and virtual machine image differentials. As organisations worldwide entrust critical data to public, private and hybrid clouds, robust forensic capabilities are essential for incidents ranging from financial fraud to ransomware and insider threats. Standardised protocols, interoperability of forensic artefacts and legal harmonisation across borders remain focal points of ongoing research and practical deployment.
The graph below shows the total number of articles in cloud forensics in digital investigations across all publications each year (not limited to Nature Index journals). Cloud Forensics: The discipline of identifying, preserving and analysing digital evidence in cloud computing environments, accounting for virtualisation and multitenancy.
Forensic Readiness: The proactive design of systems and processes to ensure that relevant data is available and preserved for potential future investigations. Chain of Custody: The documented sequence of custody, control and analysis of digital evidence to maintain integrity and admissibility.
Ephemeral Data: Information that exists only briefly—such as RAM contents or transient logs—requiring specialist methods for capture before deletion. Multitenancy: A cloud service model in which multiple independent users share the same physical resources, complicating isolation of individual evidence.
This Nature Research Intelligence Topic summary is created with the cited references and a large language model. We take care to ground generated text with facts, and have systems in place to gain human feedback on the overall quality of the process in line with our AI principles . We strive to create accurate and useful summaries for people unfamiliar with the research topic and welcome feedback that supports this goal. These pages are a beta release and will be updated as we learn how best to help people gain value from a research topic summary.
When you're under pressure to set direction, justify investment, or understand your competitive position, you need more than raw data — you need trusted insights you can act on. Benchmark your performance against global peers using robust, methodologically sound analysis. Combine quantitative metrics with qualitative expert insight to uncover strengths, gaps and emerging opportunities.
Developed with Nature Portfolio journal Editors and internationally renowned experts. Discover three ways to learn: Self-paced, online courses in convenient bite-sized units, covering key skills across scientific writing, publishing, grant writing, data analysis, and more. Expert trainer-led workshops with hands-on exercises and real-time feedback across core research skills, delivered via interactive group sessions.
Editor-led workshops combining core principles in writing and publishing, personalised 1:1 feedback from Nature Portfolio Editors and hands-on exercises. Explore course catalogues and workshop agendas, enquire about the options or request institutional pricing. Identify the compromised key in CloudTrail, trace all API calls made with the key, determine the source IPs and actions taken, check for persistence mechanisms (new users, roles, keys), revoke the compromised credentials, assess data access scope.
Detect unauthorized instance launches in CloudTrail, snapshot the mining instances for analysis, examine security group changes that allowed C2 communication, identify the initial access vector (stolen keys, SSRF), calculate resource costs incurred. Analyze S3 access logs and CloudTrail for GetObject/PutBucketPolicy events, identify who modified bucket policies to allow public access, determine the scope of data exposure, check for data downloads from unauthorized IPs, assess regulatory reporting requirements.
Collect Kubernetes audit logs and cloud provider logs, analyze pod creation events for privilege escalation attempts, examine node-level logs for container escape evidence, check for unauthorized access to cloud metadata service (169.254.169.254), trace lateral movement to cloud APIs. Claw GRC Tip : When this skill is executed by a registered agent, compliance evidence is automatically captured and mapped to the relevant controls in your active frameworks.
When executed through Claw GRC, every step of this skill generates tamper-evident audit records: Schedule this skill for recurring execution to maintain continuous compliance posture. Claw GRC monitors for drift and alerts when re-execution is needed. This skill is fully compatible with Claw GRC's autonomous agent system. Deploy it to any registered agent via MCP, and every execution will be logged in the tamper-evident audit trail.
The diagram below represents the logical interaction view of the forensic memory and disk acquisition service. The Forensic triaging step function initiates forensic acquisition flow to perform memory and disk acquisition. Following memory and disk acquisition, the investigation function is initiated. Isolation of EC2 instance or EKS cluster is done based on the Security Hub action event types - Forensic triage and Forensic isolation.
The Forensic triage Step Function initiates the memory acquisition flow. . The Memory acquisition Lambda function in workflow leverages the SSM command to run SSM document in the compromised instance. . The Memory acquisition Lambda function assumes a role in the application account and passes the SSM document to be run along with credentials to copy the memory dump into an S3 bucket. . AWS Systems Manager runs a memory acquisition document via the Run Command.
+ The memory dump is stored in an S3 bucket of the forensic account. The memory dump has associated meta data tags to indicate the underlying OS and kernel the dump is associated with, assisting the memory analysis flow further downstream. . The Check memory acquisition Lambda function checks for SSM Run Command to be completed. . If the response from SSM Run Command status is Pending or Delayed or In Progress , it waits for 120 seconds. . If the response from SSM Run Command status is Success , it checks if isolation is needed. . If isolation is set to true , then the Lambda function assumes role into the application account and attaches a security group with no egress and ingress security group, and detaches the existing security group. Isolation is set to true during the triaging phase based on security event type. . This initiates investigation flow with forensic type as MEMORY . . If any error occurs during the memory acquisition process, the EC2 instance or EKS cluster isolation will be performed based on the isolation flag.
When the isolation flag is set to true , isolation is still performed regardless of the memory acquisition result. All open credentials session based on the compromised instance role will be invalidated. On isolation, instances sharing the same role with the compromised instance would be impacted as the credentials will be invalidated. If your application does not have the correct retry mechanism to renew new credentials, it can result in failure of the application. For more information, refer to the Using temporary credentials with AWS resources topic about creating new credentials. Applications using AWS CLI will not be impacted as the credentials will be refreshed automatically When a deviation from your secure baseline occurs, it’s crucial to respond and resolve the issue quickly and follow up with a forensic investigation and root cause analysis. Having a preconfigured infrastructure and a practiced plan for using it when there’s a deviation from your baseline will help you to extract and analyze the information needed to determine the impact, scope, and root cause of an incident and return to operations confidently.
Time is of the essence in understanding the what, how, who, where, and when of a security incident. You often hear of automated incident response, which has repeatable and auditable processes to standardize the resolution of incidents and accelerate evidence artifact gathering. Similarly, having a standard, pristine, pre-configured, and repeatable forensic clean-room environment that can be automatically deployed through a template allows your organization to minimize human interaction, keep the larger organization separate from contamination, hasten evidence gathering and root cause analysis, and protect forensic data integrity. The forensic analysis process assists in data preservation, acquisition, and analysis to identify the root cause of an incident. This approach can also facilitate the presentation or transfer of evidence to outside legal entities or auditors. AWS CloudFormation templates—or other infrastructure as code (IaC) provisioning tools—help you to achieve these goals, providing your business with consistent, well-structured, and auditable results that allow for a better overall security posture.
Having these environments as a permanent part of your infrastructure allows them to be well documented and tested, and gives you opportunities to train your teams in their use. 3. Software Implementation, Frameworks & Protocols This post provides strategies that you can use to prepare your organization to respond to secure baseline deviations. These strategies take the form of best practices around Amazon Web Services (AWS) account structure, AWS Organizations organizational units (OUs) and service control policies (SCPs), forensic Amazon Virtual Private Cloud (Amazon VPC) and network infrastructure, evidence artifacts to be collected, AWS services to be used, forensic analysis tool infrastructure, and user access and authorization to the above. The specific focus is to provide an environment where Amazon Elastic Compute Cloud (Amazon EC2) instances with forensic tooling can be used to examine evidence artifacts.
This post presumes that you already have an evidence artifact collection procedure or that you are implementing one and that the evidence can be transferred to the accounts described here. If you are looking for advice on how to automate artifact collection, see How to automate forensic disk collection for guidance. A well-architected multi-account AWS environment is based on the structure provided by Organizations. As companies grow and need to scale their infrastructure with multiple accounts, often in multiple AWS Regions, Organizations offers programmatic creation of new AWS accounts combined with central management and governance that helps them to do so in a controlled and standardized manner. This programmatic, centralized approach should be used to create the forensic investigation environments described in the strategy in this blog post.
The example in this blog post uses a simplified structure with separate dedicated OUs and accounts for security and forensics, shown in Figure 1. Your organization’s architecture might differ, but the strategy remains the same. Note: There might be reasons for forensic analysis to be performed live within the compromised account itself, such as to avoid shutting down or accessing the compromised instance or resource; however, that approach isn’t covered here.
When speaking about Organizations, accounts, and the permissions required for various actions, you must first look at SCPs, a core functionality of Organizations. SCPs offer control over the maximum available permissions for all accounts in your organization. In the example in this blog post, you can use SCPs to provide similar or identical permission policies to all the accounts under the forensics OU, which is being used as a resource container. This policy overrides all other policies, and is a crucial mechanism to ensure that you can explicitly deny or allow any API calls desired. Some use cases of SCPs are to restrict the ability to disable AWS CloudTrail , restrict root user access, and ensure that all actions taken in the forensic investigation account are logged. This provides a centralized way to avoid changing individual policies for users, groups, or roles. Accessing the forensic environment should be done using a least-privilege model, with nobody capable of modifying or compromising the initially collected evidence. For an investigation environment, denying all actions except those you want to list as exceptions is the most straightforward approach. Start with the default of denying all, and work your way towards the least authorizations needed to perform the forensic processes established by your organization. AWS Config can be a valuable tool to track the changes made to the account and provide evidence of these changes.
Keep in mind that once the restrictive SCP is applied, even the root account or those with administrator access won’t have access beyond those permissions; therefore, frequent, proactive testing as your environment changes is a best practice. Also, be sure to validate which principals can remove the protective policy, if required, to transfer the account to an outside entity. Finally, create the environment before the restrictive permissions are applied, and then move the account under the forensic OU.
Having a separate AWS account dedicated to forensic investigations is best to keep your larger organization separate from the possible threat of contamination from the incident itself, ensure the isolation and protection of the integrity of the artifacts being analyzed, and keeping the investigation confidential. Separate accounts also avoid situations where the threat actors might have used all the resources immediately available to your compromised AWS account by hitting service quotas and so preventing you from instantiating an Amazon EC2 instance to perform investigations .
Having a forensic investigation account per Region is also a good practice, as it keeps the investigative capabilities close to the data being analyzed, reduces latency, and avoids issues of the data changing regulatory jurisdictions. For example, data residing in the EU might need to be examined by an investigative team in North America, but the data itself cannot be moved because its North American architecture doesn’t align with GDPR compliance. For global customers, forensics teams might be situated in different locations worldwide and have different processes. It’s better to have a forensic account in the Region where an incident arose. The account as a whole could also then be provided to local legal institutions or third-party auditors if required. That said, if your AWS infrastructure is contained within Regions only in one jurisdiction or country, then a single re-creatable account in one Region with evidence artifacts shared from and kept in their respective Regions could be an easier architecture to manage over time.
An account created in an automated fashion using a CloudFormation template—or other IaC methods—allows you to minimize human interaction before use by recreating an entirely new and untouched forensic analysis instance for each separate investigation, ensuring its integrity. Individual people will only be given access as part of a security incident response plan, and even then, permissions to change the environment should be minimal or none at all. The post-investigation environment would then be either preserved in a locked state or removed, and a fresh, blank one created in its place for the subsequent investigation with no trace of the previous artifacts. Templating your environment also facilitates testing to ensure your investigative strategy, permissions, and tooling will function as intended.
Once you’ve defined where your investigative environment should reside, you must think about who will be accessing it, how they will do so, and what permissions they will need. The forensic investigation team can be a separate team from the security incident response team, the same team, or a subset. You should provide precise access rights to the group of individuals performing the investigation as part of maintaining least privilege.
You should create specific roles for the various needs of the forensic procedures, each with only the permissions required. As with SCPs and other situations described here, start with no permissions and add authorizations only as required while establishing and testing your templated environments. As an example, you might create the following roles within the forensic account: Analyst – access forensics reports for analytics, trends, and forecasting (threat intelligence) You should establish an access procedure for each role, and include it in the response plan playbook. This will help you ensure least privilege access as well as environment integrity. For example, establish a process for an owner of the Security Incident Response Plan to verify and approve the request for access to the environment. Another alternative is the two-person rule . Alert on log-in is an additional security measure that you can add to help increase confidence in the environment’s integrity, and to monitor for unauthorized access.
You want the investigative role to have read-only access to the original evidence artifacts collected, generally consisting of Amazon Elastic Block Store (Amazon EBS) snapshots, memory dumps, logs, or other artifacts in an Amazon Simple Storage Service (Amazon S3) bucket. The original sources of evidence should be protected; MFA delete and S3 versioning are two methods for doing so. Work should be performed on copies of copies if rendering the original immutable isn’t possible, especially if any modification of the artifact will happen. This is discussed in further detail below.
Evidence should only be accessible from the roles that absolutely require access—that is, investigator and data custodian. To help prevent potential insider threat actors from being aware of the investigation, you should deny even read access from any roles not intended to access and analyze evidence. Once you’ve built the organization, account structure, and roles, you must decide on the best strategy inside the account itself.
Analysis of the collected artifacts can be done through forensic analysis tools hosted on an EC2 instance, ideally residing within a dedicated Amazon VPC in the forensics account. This Amazon VPC should be configured with the same restrictive approach you’ve taken so far, being fully isolated and auditable, with the only resources being dedicated to the forensic tasks at hand.
This might mean that the Amazon VPC’s subnets will have no internet gateways, and therefore all S3 access must be done through an S3 VPC endpoint . VPC flow logging should be enabled at the Amazon VPC level so that there are records of all network traffic. Security groups should be highly restrictive, and deny all ports that aren’t related to the requirements of the forensic tools. SSH and RDP access should be restricted and governed by auditable mechanisms such as a bastion host configured to log all connections and activity, AWS Systems Manager Session Manager , or similar.
If using Systems Manager Session Manager with a graphical interface is required, RDP or other methods can still be accessed . Commands and responses performed using Session Manager can be logged to Amazon CloudWatch and an S3 bucket, this allows auditing of all commands executed on the forensic tooling Amazon EC2 instances. Administrative privileges can also be restricted if required. You can also arrange to receive an Amazon Simple Notification Service (Amazon SNS) notification when a new session is started.
Given that the Amazon EC2 forensic tooling instances might not have direct access to the internet, you might need to create a process to preconfigure and deploy standardized Amazon Machine Images (AMIs) with the appropriate installed and updated set of tooling for analysis. Several best practices apply around this process. The OS of the AMI should be hardened to reduce its vulnerable surface. We do this by starting with an approved OS image, such as an AWS-provided AMI or one you have created and managed yourself. Then proceed to remove unwanted programs, packages, libraries, and other components.
Ensure that all updates and patches—security and otherwise—have been applied. Configuring a host-based firewall is also a good precaution, as well as host-based intrusion detection tools. In addition, always ensure the attached disks are encrypted. If your operating system is supported, we recommend creating golden images using EC2 Image Builder . Your golden image should be rebuilt and updated at least monthly, as you want to ensure it’s kept up to date with security patches and functionality.
EC2 Image Builder—combined with other tools—facilitates the hardening process; for example, allowing the creation of automated pipelines that produce Center for Internet Security (CIS) benchmark hardened AMIs. If you don’t want to maintain your own hardened images, you can find CIS benchmark hardened AMIs on the AWS Marketplace . Keep in mind the infrastructure requirements for your forensic tools—such as minimum CPU, memory, storage, and networking requirements—before choosing an appropriate EC2 instance type. Though a variety of instance types are available, you’ll want to ensure that you’re keeping the right balance between cost and performance based on your minimum requirements and expected workloads.
The goal of this environment is to provide an efficient means to collect evidence, perform a comprehensive investigation, and effectively return to safe operations. Evidence is best acquired through the automated strategies discussed in How to automate incident response in the AWS Cloud for EC2 instances . Hashing evidence artifacts immediately upon acquisition is highly recommended in your evidence collection process. Hashes, and in turn the evidence itself, can then be validated after subsequent transfers and accesses, ensuring the integrity of the evidence is maintained. Preserving the original evidence is crucial if legal action is taken.
Access to the control plane logs mentioned above—such as the CloudTrail logs—can be accessed in one of two ways. Ideally, the logs should reside in a central location with read-only access for investigations as needed. However, if not centralized, read access can be given to the original logs within the source account as needed. Read access to certain service logs found within the security account, such as AWS Config, Amazon GuardDuty , Security Hub, and Amazon Detective , might be necessary to correlate indicators of compromise with evidence discovered during the analysis.
As previously mentioned, it’s imperative to have immutable versions of all evidence. This can be achieved in many ways, including but not limited to the following examples: Note: AWS services such as KMS can help enable encryption. KMS is integrated with AWS services to simplify using your keys to encrypt data across your AWS workloads.
An example use case of Amazon EBS disks being shared as evidence to the forensics account, the following figure—Figure 2—is a simplified S3 bucket folder structure you could use to store and work with evidence. Figure 2 shows an S3 bucket structure for a forensic account. An S3 bucket and folder is created to hold incoming data—for example, from Amazon EBS disks—which is streamed to Incoming Data > Evidence Artifacts using dc3dd. The data is then copied from there to a folder in another bucket— Active Investigation > Root Directory > Extracted Artifacts —to be analyzed by the tooling installed on your forensic Amazon EC2 instance. Also, there are folders under Active Investigation for any investigation notes you make during analysis, as well as the final reports, which are discussed at the end of this blog post.
Finally, a bucket and folders for legal holds , where an object lock will be placed to hold evidence artifacts at a specific version. Finally, depending on the severity of the incident, your on-premises network and infrastructure might also be compromised. Having an alternative environment for your security responders to use in case of such an event reduces the chance of not being able to respond in an emergency. Amazon services such as Amazon Workspaces —a fully managed persistent desktop virtualization service—can be used to provide your responders a ready-to-use, independent environment that they can use to access the digital forensics and incident response tools needed to perform incident-related tasks.
Aside from the investigative tools, communications services are among the most critical for coordination of response. You can use Amazon WorkMail and Amazon Chime to provide that capability independent of normal channels. The goal of a forensic investigation is to provide a final report that’s supported by the evidence. This includes what was accessed, who might have accessed it, how it was accessed, whether any data was exfiltrated, and so on. This report might be necessary for legal circumstances, such as criminal or civil investigations or situations requiring breach notifications. What output each circumstance requires should be determined in advance in order to develop an appropriate response and reporting process for each. A root cause analysis is vital in providing the information required to prepare your resources and environment to help prevent a similar incident in the future. Reports should not only include a root cause analysis, but also provide the methods, steps, and tools used to arrive at the conclusions.
This article has shown you how you can get started creating and maintaining forensic environments, as well as enable your teams to perform advanced incident resolution investigations using AWS services. Implementing the groundwork for your forensics environment, as described above, allows you to use automated disk collection to begin iterating on your forensic data collection capabilities and be better prepared when security events occur.
If you have feedback about this post, submit comments in the Comments section below. If you have questions about this post, start a new thread on one of the AWS Security, Identity, and Compliance forums or contact AWS Support . 4. Practical Deployment, Analysis & Case Studies Want more AWS Security how-to content, news, and feature announcements? Follow us on Twitter .
Defensible cloud forensic acquisition captures point-in-time digital evidence without altering source metadata or violating cloud tenant boundaries. Investigators execute out-of-band virtual block storage snapshotting (AWS EBS, Azure Managed Disk, GCP Persistent Disk) , isolate target instances in forensic quarantine Virtual Private Clouds (VPCs), preserve immutable API audit logs (CloudTrail, Azure Activity Log, Cloud Audit Logs), and calculate SHA-256 cryptographic hashes for full court admissibility under FRCP Rule 37(e) .
1. The Multi-Cloud Forensic Challenge: Ephemeral Compute, Shared Responsibility & FRCP 37(e) As enterprise infrastructure rapidly migrates from physical on-premises data centers to Amazon Web Services (AWS), Microsoft Azure, and Google Cloud Platform (GCP), corporate legal and digital forensics incident response (DFIR) teams face unprecedented challenges. Traditional forensic methods—such as physically pulling power plugs, connecting write blockers to SAS/SATA hard drives, or imaging physical servers—are entirely impossible in hyper-scale public clouds.
In cloud environments, storage volumes exist as abstracted virtual block devices, compute instances auto-scale dynamically, and microservices spin up and dissolve in milliseconds. Under Federal Rule of Civil Procedure 37(e) , failure to take reasonable steps to preserve Electronically Stored Information (ESI) when litigation is reasonably anticipated can result in devastating sanctions, mandatory adverse-inference jury instructions, or default judgment.
A fatal misconception among in-house legal teams is assuming that cloud service providers (CSPs) automatically preserve forensic artifacts. Under the Shared Responsibility Model , CSPs guarantee the physical security and hypervisor availability of the cloud, but the enterprise customer is exclusively responsible for: Cloud evidence frequently crosses international borders. When an enterprise hosts virtual infrastructure in US-East (Virginia) but custodian endpoints operate in Frankfurt or Singapore, forensic collections trigger competing legal mandates: Courts have made it clear that cloud-hosted data must be preserved with the exact same evidentiary rigor as local hard drives.
In cases such as DR Distributors, LLC v. 21 Century Smoking, Inc. , 513 F. Supp. 3d 839 (N.D. Ill. 2021), federal courts imposed massive monetary and evidentiary sanctions on parties that failed to understand their cloud architecture, resulting in the automated spoliation of chat and cloud repository data. Understanding cloud forensics connects directly with our Data Breach Notification Protocols: Technical Identification & Log Auditing and reinforces our frameworks on Custodian Interview Questionnaire Frameworks & FRCP Defensibility .
2. Platform-Specific Acquisition Architectures (AWS EBS/CloudTrail, Azure Disk/Activity Log, GCP Persistent Disk/Cloud Audit) Forensic acquisition across the “Big Three” cloud providers requires mastering the native API capabilities and storage snapshot architectures of each platform: When source disks are encrypted with Customer Managed Keys (AWS KMS, Azure Key Vault, Google Cloud KMS), snapshots inherit the cryptographic envelope. Sharing a snapshot across accounts requires granting the forensic account’s IAM role kms:CreateGrant and kms:Decrypt permissions on the key policy, followed by re-encrypting the forensic copy under a key owned exclusively by the legal team.
3. Volatile Memory Capture in Containerized & Serverless Environments (Fargate, AKS, GKE) Capturing volatile physical RAM from cloud instances is essential for analyzing active ransomware infections, credential dumping from LSASS, and zero-day in-memory exploits: Serverless functions execute in microVM sandboxes (e.g., AWS Firecracker) that exist for seconds. DFIR teams must capture function execution traces via AWS X-Ray, CloudWatch execution logs, and snapshot the ephemeral /tmp scratch disk before execution containers are decommissioned.
Because direct physical access to cloud hypervisor RAM is prohibited by CSP security boundaries, forensic investigators use non-disruptive kernel-level memory acquisition tools: When investigating containerized microservices, traditional disk snapshotting is insufficient because container storage is ephemeral by design: Enterprise DFIR and eDiscovery data engineering teams utilize automated Python orchestration scripts using boto3 and cloud SDKs to snapshot target volumes, isolate virtual machines, compute cryptographic verification hashes, and log chain of custody records: The following production script executes an out-of-band cloud forensic acquisition, creating an isolated snapshot, computing metadata hashes, and preparing a legally defensible chain of custody manifest: 2. Real-World Case Study: Defending Against a $40M Cloud Trade Secret Spoliation Claim In a high-stakes trade secret theft lawsuit in the Northern District of California, the plaintiff alleged that a departing executive spun up multiple AWS EC2 GPU instances to exfiltrate proprietary machine learning models before terminating the instances to destroy evidence.
Always transfer forensic snapshots and API logs to a dedicated, air-gapped security AWS Account or Azure Subscription with strictly restricted IAM permissions. This prevents compromised production administrative credentials from deleting or tampering with forensic evidence images. Cloud forensic acquisition requires moving beyond physical hard drive methodologies to embrace hypervisor-level snapshotting, automated API telemetry aggregation, and multi-tenant chain of custody protocols. By mastering out-of-band volume preservation, network quarantine isolation, and cryptographic hash verification across AWS, Azure, and Google Cloud, legal and cybersecurity teams ensure that cloud evidence remains bulletproof against judicial scrutiny.
The process of identifying, preserving, collecting, and validating digital evidence from public and private cloud environments (AWS, Azure, GCP) for litigation and cybersecurity investigations. An EBS snapshot captures a point-in-time, crash-consistent copy of all data blocks on the virtual disk directly to Amazon S3 without installing agents in the guest OS.
A security framework where the cloud provider manages infrastructure security, while the customer is solely responsible for guest OS, data, identity logs, and memory preservation. By replacing its Security Groups with a forensic quarantine group that blocks all inbound/outbound traffic except secure management access from a dedicated forensic subnet.
CloudTrail records every API call made across the AWS account (who, what, when, IP address), proving user logins, resource creation, deletion, and data exfiltration. Using Azure Run Command or Systems Center to execute live memory dumping utilities (winpmem, LiME, avml) that stream raw RAM bytes to secure Azure Blob storage.
GCP creates incremental, read-only snapshots at the hypervisor level, applying customer-supplied encryption keys and verifiable SHA-256 block checksums. Write Once, Read Many (WORM) storage (like AWS S3 Object Lock) prevents any user, including root administrators, from deleting or modifying evidence during legal retention periods.
By pausing the container runtime, snapshotting the node’s underlying storage volumes, extracting the overlay2 filesystem layers, and archiving Kubernetes audit logs. A snapshot capturing data identical to what would be on disk if the power cord were suddenly pulled, preserving uncommitted filesystem state for forensic analysis.
To ensure that compromised production credentials or malicious insiders cannot tamper with, overwrite, or delete forensic disk images and logs. VPC Flow Logs track IP traffic (source/destination IPs, ports, packet counts, accept/reject status), proving data exfiltration volumes and lateral movement.
5. Performance Evaluation & Extended Technical Observations Federal Rules of Evidence 901 and 902(13)/(14) allow certified self-authenticating electronic records verified by digital hashes and qualified examiner testimony. 14. Can cloud snapshots be converted into traditional forensic formats like E01 or DD? Yes; by attaching the snapshot volume as read-only to a forensic Linux VM, examiners use tools like ewfacquire or dd to generate standard E01/RAW images.
Auto-scaling automatically terminates and deletes compute instances when demand drops, permanently destroying local disk and memory evidence unless immediately frozen. KMS Customer Managed Keys (CMKs) provide immutable cryptographic proof of access, ensuring only authorized examiners can decrypt and view the evidence snapshot.
17. How should organizations prepare their cloud infrastructure for forensic readiness? Enable multi-region CloudTrail/Activity logging, configure automated S3 WORM vaults, pre-build quarantine security groups, and deploy automated snapshot scripts. Content is reviewed against applicable legal, forensic, and digital-evidence standards. Learn more about our SME Practice Team or review our Editorial Standards .
Technical overview of Uncovering Data Deletion & Anti-Forensics Wiping Attempts. Focuses on uncovering data deletion & anti-forensics wiping attempts... Mobile Device Forensics in Corporate Litigation: iOS/Android Extraction, App Decryption, & Evidence Admissibility Master mobile device forensics in corporate litigation. Learn physical vs logical iOS/Android extractions, SQLite parsing, app decryption, and BYOD privacy prot Comprehensive analysis of Browser-Native PST/MBOX Email Triage & Local WebGPU OCR Processing. Evaluates technical architecture & step-by-step...
This Guidance demonstrates how to establish a comprehensive, automated forensics orchestration workflow for Security Operations Centers using AWS services. It helps organizations rapidly respond to potential security breaches by automating critical forensics processes for Amazon EC2 instances and EKS clusters. The solution shows how to implement automated isolation of affected resources, capture essential forensics evidence including memory and disk images, and streamline investigation workflows across multi-account and multi-region environments. Through its serverless architecture and integrated security features, this Guidance enables SOC teams to efficiently conduct forensic analysis, continuously monitor for threats, and maintain a robust security posture while reducing manual overhead and accelerating incident response times.
Reduce investigation time from hours to minutes with automated forensic workflows that capture and analyze both memory and disk data when security issues are detected. Maintain business continuity while thoroughly investigating potential threats. Automatically isolate potentially compromised instances while preserving forensic evidence for investigation. Protect your infrastructure by implementing consistent, automated response procedures for security findings.
Maintain complete chain of custody with automated evidence collection and secure storage. Query forensic timelines and investigation results through a centralized interface while ensuring compliance requirements. These technical details feature an architecture diagram to illustrate how to effectively use this solution. The architecture diagram shows the key components and their interactions, providing an overview of the architecture's structure and functionality step-by-step.
Dive deep into the implementation guide for additional customization options and service configurations to tailor to your specific needs. Ready to deploy? Review the sample code on GitHub for detailed deployment instructions to deploy as-is or customize to fit your needs.
The diagram below represents the logical interaction view of forensic memory and disk investigation service. Once forensic acquisition is completed, forensic investigation flow is initiated, isolation of EC2 instance or EKS cluster is done based on the AWS Security Hub event type. The Create Instance Lambda function retrieves the AMI information from AWS Systems Manager Parameter Store and starts an instance in the forensic account.
The Check Instance Lambda function validates the instance has the necessary tools required for forensic investigation, such as determining the instance is in the running state, AWS Systems Manager is installed and forensic tools are up and running. If the response from SSM Command is Pending or In Progress it waits for 120 seconds and checks again. Disk forensics investigation flow is initiated for forensictype variable set to DISK .
Disk forensics investigation lambda function creates a volume from the snapshot shared with the forensic account and attaches the volume to the instance started in step 2. The Disk forensics investigation Lambda function leverages the SSM document to perform disk forensics. The Memory forensics investigation flow is initiated for forensictype variable set to MEMORY .
The Lambda function leverages the SSM document to load memory dump from S3 to the EBS volume for memory analysis. Harvested Online Documentation & Reference Sources • https://www.sans.org/blog/cloud-native-forensic-imaging-part-2 • https://www.sans.org/blog/cloud-native-forensic-imaging-part-1 • https://www.nature.com/nature-index/topics/l4/cloud-forensics-in-digital-investigations • https://clawgrc.com/skills/performing-cloud-forensics-investigation • https://docs.aws.amazon.com/solutions/latest/automated-forensics-orchestrator-for-amazon-ec2/forensic-memory-and-disk- acquisition-service.html • https://aws.amazon.com/blogs/security/forensic-investigation-environment-strategies-in-the-aws-cloud/ • https://discoverytechlab.com/cloud-forensic-acquisition-protocols/ • https://aws.amazon.com/solutions/guidance/automated-forensics-orchestrator-for-amazon-ec2-and-eks/ • https://docs.aws.amazon.com/solutions/automated-forensics-orchestrator-for-amazon-ec2/ • https://docs.aws.amazon.com/solutions/latest/automated-forensics-orchestrator-for-amazon-ec2/forensic-investigation-and-r eporting-service.html
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Cloud Instance Forensic Acquisition Tool Using Python.
[*] Metasploit Scan Running on Target Subnet for Cloud Instance Forensic Acquisition Tool Using Python... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |