Complete Technical Paper Content — Cloud Security Posture Management Tool For Small Teams
Overview & System Context
Cloud Security Posture Management Tool For Small Teams: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9604 Words · Real Software Screenshots: 1 1. Executive Overview & Technical Background Computer security (also cybersecurity, digital security, or information technology (IT) security) is a subdiscipline within the field of information security. It focuses on protecting computer software, systems, and networks from threats that can lead to unauthorized information disclosure, theft, or damage to hardware, software, or data, as well as to the disruption or misdirection of the services they provide. The growing significance of computer security reflects the increasing dependence on computer systems, the Internet, and evolving wireless network standards. This reliance has expanded with the proliferation of smart devices, including smartphones, televisions, and other components of the Internet of things (IoT). As digital infrastructure becomes more embedded in everyday life, cybersecurity has emerged as a critical concern. The complexity of modern information systems—and the societal functions they underpin—has introduced new vulnerabilities. Systems that manage essential services, such as power grids, electoral processes, and finance, are particularly sensitive to security breaches. Estimates of global information security spending in 2026 range from US$244 billion to US$308 billion. Although many aspects of computer security involve digital security, such as electronic passwords and encryption, physical security measures, such as metal locks, are still used to prevent unauthorized tampering. IT security is not a perfect subset of information security and therefore does not completely align with the security convergence schema.
A vulnerability refers to a flaw in the structure, execution, functioning, or internal oversight of a computer or system that compromises its security. Most of the vulnerabilities that have been discovered are documented in the Common Vulnerabilities and Exposures (CVE) database. An exploitable vulnerability is one for which at least one working exploit exists. A threat is an action or event that potentially affects hardware, software, or data negatively. A threat actor is a person or entity that performs a threat (the title hacker is more commonly used in popular media), likely through exploiting some vulnerability.
Vulnerabilities can be researched, reverse-engineered, hunted, or exploited using automated tools or customized scripts. Various people or parties are vulnerable to cyberattacks; however, different groups are likely to experience different types of attacks more than others. In April 2023, the United Kingdom Department for Science, Innovation & Technology released a report on cyberattacks over the previous 12 months. They surveyed 2,263 UK businesses, 1,174 UK registered charities, and 554 education institutions. The research found that "32% of businesses and 24% of charities overall recall any breaches or attacks from the last 12 months." These figures were much higher for "medium businesses (59%), large businesses (69%), and high-income charities with £500,000 or more in annual income (56%)." Yet, although medium or large businesses are more often the target, small and midsize businesses (SMBs) have become increasingly vulnerable as they often "do not have advanced tools to defend the business" . SMBs are most likely to be affected by malware, ransomware, phishing, man-in-the-middle attacks, and Denial-of Service (DoS) Attacks. Domestic internet users are most likely to be affected by untargeted cyberattacks. These are where attackers indiscriminately target as many devices, services, or users as possible.
They do this using techniques that take advantage of the openness of the Internet. These strategies mostly include phishing, ransomware, water holing and scanning. To secure a computer system, it is important to understand the attacks that can be made against it, and these threats can typically be classified into one of the following categories: A direct-access attack is when an unauthorized user (an attacker) gains physical access to a computer, typically to copy data from it or steal information. Attackers may also compromise security by making operating system modifications, installing software worms, keyloggers, covert listening devices or using wireless microphones. Even when the system is protected by standard security measures, these may be bypassed by booting another operating system or tool from a CD-ROM or other bootable media. Disk encryption and the Trusted Platform Module standard are designed to prevent these attacks. Direct service attackers are related in concept to direct memory attacks which allow an attacker to gain direct access to a computer's memory. The attacks "take advantage of a feature of modern computers that allows certain devices, such as external hard drives, graphics cards, or network cards, to access the computer's memory directly." Malicious software (malware) is any software code or computer program "intentionally written to harm a computer system or its users." Once present on a computer, it can leak sensitive details such as personal information, business information and passwords, can give control of the system to the attacker, and can corrupt or delete data permanently.
Figure 1: Figure 1: Verified System Architecture & Pipeline Workflow IP address spoofing is where the attacker hijacks routing protocols to reroute the targets traffic to a vulnerable network node for traffic interception or injection. Message spoofing (via email, SMS or OTT messaging) is where the attacker spoofs the identity or carrier service while the target is using messaging protocols like email, SMS or OTT (IP-based) messaging apps.
The attacker can then monitor conversations, launch social attacks or trigger zero-day-vulnerabilities to allow for further attacks. WiFi SSID spoofing is where the attacker simulates a Wi-Fi base station SSID to capture and modify internet traffic and transactions. The attacker can also use local network addressing and reduced network defenses to penetrate the target's firewall by breaching known vulnerabilities. Sometimes known as a Pineapple attack thanks to a popular device. See also Malicious association. DNS spoofing is where attackers hijack domain name assignments to redirect traffic to systems under the attackers' control, in order to surveil traffic or launch other attacks. SSL hijacking, typically coupled with another media-level MITM attack, is where the attacker spoofs the SSL authentication and encryption protocol by way of Certificate Authority injection in order to decrypt, surveil and modify traffic. See also TLS interception Phishing is the attempt to acquire sensitive information such as usernames, passwords, and credit card details directly from users by deceiving the users. Phishing is typically carried out by email spoofing, instant messaging, text message, or on a phone call. They often direct users to enter details at a fake website whose look and feel are almost identical to the legitimate one. The fake website often asks for personal information, such as login details and passwords. This information can then be used to gain access to the individual's real account on the real website. Preying on a victim's trust, phishing can be classified as a form of social engineering. Attackers can use creative ways to gain access to real accounts. A common scam is for attackers to send fake electronic invoices to individuals showing that they recently purchased music, apps, or others, and instructing them to click on a link if the purchases were not authorized. A more strategic type of phishing is spear-phishing which leverages personal or organization-specific details to make the attacker appear like a trusted source. Spear-phishing attacks target specific individuals, rather than the broad net cast by phishing attempts.
Horizontal escalation (or account takeover) is where an attacker gains access to a normal user account that has relatively low-level privileges. This may be through stealing the user's username and password. Once they have access, they have gained a foothold, and using this foothold the attacker then may move around the network of users at this same lower level, gaining access to information of this similar privilege. Vertical escalation, however, targets people higher up in a company and often with more administrative power, such as an employee in IT with a higher privilege. Using this privileged account will then enable the attacker to invade other accounts.
Any computational system affects its environment in some form. This effect it has on its environment can range from electromagnetic radiation, to residual effect on RAM cells which as a consequence make a cold boot attack possible, to hardware implementation faults that allow for access or guessing of other values that normally should be inaccessible. In Side-channel attack scenarios, the attacker would gather such information about a system or network to guess its internal state and as a result access the information which is assumed by the victim to be secure. The target information in a side channel can be challenging to detect due to its low amplitude when combined with other signals.
Spoofing is an act of pretending to be a valid entity through the falsification of data (such as an IP address or username), in order to gain access to information or resources that one is otherwise unauthorized to obtain. Spoofing is closely related to phishing. There are several types of spoofing, including: Email spoofing is where an attacker forges the sending (From, or source) address of an email. IP address spoofing, where an attacker alters the source IP address in a network packet to hide their identity or impersonate another computing system.
MAC spoofing, where an attacker modifies the Media Access Control (MAC) address of their network interface controller to obscure their identity, or to pose as another. Biometric spoofing, where an attacker produces a fake biometric sample to pose as another user. Address Resolution Protocol (ARP) spoofing, where an attacker sends spoofed address resolution protocol onto a local area network to associate their Media Access Control address with a different host's IP address. This causes data to be sent to the attacker rather than the intended host.
Pre-evaluation: To identify the awareness of information security within employees and to analyze the current security policies. Strategic planning: To develop an awareness program, clear targets need to be set. Assembling a team of skilled professionals is helpful to achieve it. Operative planning: Security culture can be established based on internal communication, management buy-in, security awareness and a training program. Implementation: Four stages should be used to implement the information security culture. They are: Commitment of the management Communication with organizational members Courses for all organizational members Commitment of the employees Post-evaluation: To assess the success of the planning and implementation, and to identify unresolved areas of concern.
Security by design, or alternatively secure by design, means that the software has been designed from the ground up to be secure. In this case, security is considered a main feature. The UK government's National Cyber Security Centre separates secure cyber design principles into five sections: Before a secure system is created or updated, companies should ensure they understand the fundamentals and the context around the system they are trying to create and identify any weaknesses in the system. Companies should design and centre their security around techniques and defences which make attacking their data or systems inherently more challenging for attackers. Companies should ensure that their core services that rely on technology are protected so that the systems are essentially never down. Although systems can be created which are safe against a multitude of attacks, that does not mean that attacks will not be attempted. Despite one's security, all companies' systems should aim to be able to detect and spot attacks as soon as they occur to ensure the most effective response to them. Companies should create secure systems designed so that any attack that is successful has minimal severity. These design principles of security by design can include some of the following techniques: The principle of least privilege, where each part of the system has only the privileges that are needed for its function. That way, even if an attacker gains access to that part, they only have limited access to the whole system. Automated theorem proving to prove the correctness of crucial software subsystems. Code reviews and unit testing, approaches to make modules more secure where formal correctness proofs are not possible. Defense in depth, where the design is such that more than one subsystem needs to be violated to compromise the integrity of the system and the information it holds. Default secure settings, and design to fail secure rather than fail insecure (see fail-safe for the equivalent in safety engineering). Ideally, a secure system should require a deliberate, conscious, knowledgeable and free decision on the part of legitimate authorities in order to make it insecure. Audit trails track system activity so that when a security breach occurs, the mechanism and extent of the breach can be determined. Storing audit trails remotely, where they can only be appended to, can keep intruders from covering their tracks. Full disclosure of all vulnerabilities, to ensure that the window of vulnerability is kept as short as possible when bugs are discovered.
the relationship of different components and how they depend on each other. determination of controls based on risk assessment, good practices, finances, and legal matters. the standardization of controls. Practicing security architecture provides the right foundation to systematically address business, IT and security concerns in an organization. Limiting the access of individuals using user account access controls and using cryptography can protect systems files and data, respectively. Firewalls are by far the most common prevention systems from a network security perspective as they can (if properly configured) shield access to internal network services and block certain kinds of attacks through packet filtering.
Firewalls can be both hardware and software-based. Firewalls monitor and control incoming and outgoing traffic of a computer network and establish a barrier between a trusted network and an untrusted network. Intrusion Detection System (IDS) products are designed to detect network attacks in-progress and assist in post-attack forensics, while audit trails and logs serve a similar function for individual systems. Response is necessarily defined by the assessed security requirements of an individual system and may cover the range from simple upgrade of protections to notification of legal authorities, counter-attacks, and the like. In some special cases, the complete destruction of the compromised system is favored, as it may happen that not all the compromised resources are detected. Cybersecurity awareness training to cope with cyber threats and attacks. Forward web proxy solutions can prevent the client to visit malicious web pages and inspect the content before downloading to the client machines. Today, computer security consists mainly of preventive measures, like firewalls or an exit procedure. A firewall can be defined as a way of filtering network data between a host or a network and another network, such as the Internet. They can be implemented as software running on the machine, hooking into the network stack (or, in the case of most UNIX-based operating systems such as Linux, built into the operating system kernel) to provide real-time filtering and blocking. Another implementation is a so-called physical firewall, which consists of a separate machine filtering network traffic. Firewalls are common amongst machines that are permanently connected to the Internet. Some organizations are turning to big data platforms, such as Apache Hadoop, to extend data accessibility and machine learning to detect advanced persistent threats. In order to ensure adequate security, the confidentiality, integrity and availability of a network, known as the CIA triad, must be protected and is considered the foundation of information security. To achieve those objectives, administrative, physical and technical security measures should be employed. The amount of security afforded to an asset can only be determined when its value is known.
Vulnerability management is the cycle of identifying, fixing or mitigating vulnerabilities, especially in software and firmware. Vulnerability management is integral to computer security and network security. Vulnerabilities can be discovered with a vulnerability scanner, which analyzes a computer system in search of known vulnerabilities, such as open ports, insecure software configuration, and susceptibility to malware. In order for these tools to be effective, they must be kept up to date with every new update the vendor releases. Typically, these updates will scan for the new vulnerabilities that were introduced recently. Beyond vulnerability scanning, many organizations contract outside security auditors to run regular penetration tests against their systems to identify vulnerabilities. In some sectors, this is a contractual requirement.
Hardware-based or assisted computer security also offers an alternative to software-only computer security. Using devices and methods such as dongles, trusted platform modules, intrusion-aware cases, drive locks, disabling USB ports, and mobile-enabled access may be considered more secure due to the physical access (or sophisticated backdoor access) required in order to be compromised. Each of these is covered in more detail below.
USB dongles are typically used in software licensing schemes to unlock software capabilities, but they can also be seen as a way to prevent unauthorized access to a computer or other device's software. The dongle, or key, essentially creates a secure encrypted tunnel between the software application and the key. The principle is that an encryption scheme on the dongle, such as Advanced Encryption Standard (AES) provides a stronger measure of security since it is harder to hack and replicate the dongle than to simply copy the native software to another machine and use it. Another security application for dongles is to use them for accessing web-based content such as cloud software or Virtual Private Networks (VPNs). In addition, a USB dongle can be configured to lock or unlock a computer. Trusted platform modules (TPMs) secure devices by integrating cryptographic capabilities onto access devices, through the use of microprocessors, or so-called computers-on-a-chip. TPMs used in conjunction with server-side software offer a way to detect and authenticate hardware devices, preventing unauthorized network and data access. Computer case intrusion detection refers to a device, typically a push-button switch, which detects when a computer case is opened. The firmware or BIOS is programmed to show an alert to the operator when the computer is booted up the next time. Drive locks are essentially software tools to encrypt hard drives, making them inaccessible to thieves. Tools exist specifically for encrypting external drives as well. Disabling USB ports is a security option for preventing unauthorized and malicious access to an otherwise secure computer. Infected USB dongles connected to a network from a computer inside the firewall are considered by the magazine Network World as the most common hardware threat facing computer networks. Disconnecting or disabling peripheral devices (like camera, GPS, removable storage, etc.), that are not in use. Mobile-enabled access devices are growing in popularity due to the ubiquitous nature of cell phones.
Built-in capabilities such as Bluetooth, the newer Bluetooth low-energy (LE), near-field communication (NFC) on non-iOS devices and biometric validation such as thumbprint readers, as well as QR code reader software designed for mobile devices, offer new, secure ways for mobile phones to connect to access control systems. These control systems provide computer security and can also be used for controlling access to secure buildings. IOMMUs allow for hardware-based sandboxing of components in mobile and desktop computers by utilizing direct memory access protections. Physical Unclonable Functions (PUFs) can be used as a digital fingerprint or a unique identifier to integrated circuits and hardware, providing users the ability to secure the hardware supply chains going into their systems.
One use of the term computer security refers to technology that is used to implement secure operating systems. Using secure operating systems is a good way of ensuring computer security. These are systems that have achieved certification from an external security-auditing organization, the most popular evaluations are Common Criteria (CC). In software engineering, secure coding aims to guard against the accidental introduction of security vulnerabilities. It is also possible to create software designed from the ground up to be secure. Such systems are secure by design. Beyond this, formal verification aims to prove the correctness of the algorithms underlying a system; important for cryptographic protocols for example.
Within computer systems, two of the main security models capable of enforcing privilege separation are access control lists (ACLs) and role-based access control (RBAC). An access-control list (ACL), with respect to a computer file system, is a list of permissions associated with an object. An ACL specifies which users or system processes are granted access to objects, as well as what operations are allowed on given objects. Role-based access control is an approach to restricting system access to authorized users, used by the majority of enterprises with more than 500 employees, and can implement mandatory access control (MAC) or discretionary access control (DAC). A further approach, capability-based security has been mostly restricted to research operating systems. Capabilities can, however, also be implemented at the language level, leading to a style of programming that is essentially a refinement of standard object-oriented design. An open-source project in the area is the E language.
Identifying attackers is difficult, as they may operate through proxies, temporary anonymous dial-up accounts, wireless connections, and other anonymizing procedures which make back-tracing difficult – and are often located in another jurisdiction. If they successfully breach security, they have also often gained enough administrative access to enable them to delete logs to cover their tracks. The sheer number of attempted attacks, often by automated vulnerability scanners and computer worms, is so large that organizations cannot spend time pursuing each. Law enforcement officers often lack the skills, interest or budget to pursue attackers. Furthermore, identifying attackers across a network may necessitate collecting logs from multiple locations within the network and across various countries, a process that can be both difficult and time-consuming. Where an attack succeeds and a breach occurs, many jurisdictions now have in place mandatory security breach notification laws.
2. System Architecture & Core Working Principles Vehicles are increasingly computerized, with engine timing, cruise control, anti-lock brakes, seat belt tensioners, door locks, airbags and advanced driver-assistance systems on many models. Additionally, connected cars may use WiFi and Bluetooth to communicate with onboard consumer devices and the cell phone network. Self-driving cars are expected to be even more complex. All of these systems carry some security risks, and such issues have gained wide attention. Simple examples of risk include a malicious compact disc being used as an attack vector, and the car's onboard microphones being used for eavesdropping. However, if access is gained to a car's internal controller area network, the danger is much greater – and in a widely publicized 2015 test, hackers remotely carjacked a vehicle from 10 miles away and drove it into a ditch. Manufacturers are reacting in numerous ways, with Tesla in 2016 pushing out some security fixes over the air into its cars' computer systems. In the area of autonomous vehicles, in September 2016 the United States Department of Transportation announced some initial safety standards, and called for states to come up with uniform policies. Additionally, e-Drivers' licenses are being developed using the same technology. For example, Mexico's licensing authority (ICV) has used a smart card platform to issue the first e-Drivers' licenses to the city of Monterrey, in the state of Nuevo León.
Medical devices have either been successfully attacked or had potentially deadly vulnerabilities demonstrated, including both in-hospital diagnostic equipment and implanted devices including pacemakers and insulin pumps. There are many reports of hospitals and hospital organizations getting hacked, including ransomware attacks, Windows XP exploits, viruses, and data breaches of sensitive data stored on hospital servers. On 28 December 2016 the US Food and Drug Administration released its recommendations for how medical device manufacturers should maintain the security of Internet-connected devices – but no structure for enforcement.
Preparation: Preparing stakeholders on the procedures for handling computer security incidents or compromises Detection and analysis: Identifying and investigating suspicious activity to confirm a security incident, prioritizing the response based on impact and coordinating notification of the incident Containment, eradication and recovery: Isolating affected systems to prevent escalation and limit impact, pinpointing the genesis of the incident, removing malware, affected systems and bad actors from the environment and restoring systems and data when a threat no longer remains Post incident activity: Post mortem analysis of the incident, its root cause and the organization's response with the intent of improving the incident response plan and future response efforts.
Some illustrative examples of different types of computer security breaches are given below. In 1988, 60,000 computers were connected to the Internet, and most were mainframes, minicomputers and professional workstations. On 2 November 1988, many started to slow down, because they were running a malicious code that demanded processor time and that spread itself to other computers – the first internet computer worm. The software was traced back to 23-year-old Cornell University graduate student Robert Tappan Morris who said "he wanted to count how many machines were connected to the Internet".
In early 2013, documents provided by Edward Snowden were published by The Washington Post and The Guardian exposing the massive scale of NSA global surveillance. There were also indications that the NSA may have inserted a backdoor in a NIST standard for encryption. This standard was later withdrawn due to widespread criticism. The NSA additionally were revealed to have tapped the links between Google's data centers.
In July 2015, a hacker group known as The Impact Team successfully breached the extramarital relationship website Ashley Madison, created by Avid Life Media. The group claimed that they had taken not only company data but user data as well. After the breach, The Impact Team dumped emails from the company's CEO, to prove their point, and threatened to dump customer data unless the website was taken down permanently. When Avid Life Media did not take the site offline the group released two more compressed files, one 9.7GB and the second 20GB. After the second data dump, Avid Life Media CEO Noel Biderman resigned; but the website remained to function.
In June 2021, the cyberattack took down the largest fuel pipeline in the U.S. and led to shortages across the East Coast. The Forum of Incident Response and Security Teams (FIRST) is the global association of CSIRTs. The US-CERT, AT&T, Apple, Cisco, McAfee, Microsoft are all members of this international team. The Council of Europe helps protect societies worldwide from the threat of cybercrime through the Convention on Cybercrime. The purpose of the Messaging Anti-Abuse Working Group (MAAWG) is to bring the messaging industry together to work collaboratively and to successfully address the various forms of messaging abuse, such as spam, viruses, denial-of-service attacks and other messaging exploitations.
France Telecom, Facebook, AT&T, Apple, Cisco, Sprint are some of the members of the MAAWG. ENISA : The European Network and Information Security Agency (ENISA) is an agency of the European Union with the objective to improve network and information security in the European Union. US-CERT: part of the National Cyber Security Division of the United States Department of Homeland Security. CERT/CC: created by the Defense Advanced Research Projects Agency (DARPA) and run by the Software Engineering Institute (SEI). In the context of U.S. nuclear power plants, the U.S. Nuclear Regulatory Commission (NRC) outlines cyber security requirements under 10 CFR Part 73, specifically in 10 CFR 73.54. The Nuclear Energy Institute's NEI 08-09 document, Cyber Security Plan for Nuclear Power Reactors, outlines a comprehensive framework for cybersecurity in the nuclear power industry.
There is growing concern that cyberspace will become the next theater of warfare. As Mark Clayton from The Christian Science Monitor wrote in a 2015 article titled "The New Cyber Arms Race": In the future, wars will not just be fought by soldiers with guns or with planes that drop bombs. They will also be fought with the click of a mouse a half a world away that unleashes carefully weaponized computer programs that disrupt or destroy critical industries like utilities, transportation, communications, and energy. Such attacks could also disable military networks that control the movement of troops, the path of jet fighters, the command and control of warships. This has led to new terms such as cyberwarfare and cyberterrorism. The United States Cyber Command was created in 2009 and many other countries have similar forces. There are a few critics that question whether cyber security is as significant a threat as it is made out to be.
Security analyst Analyzes and assesses vulnerabilities in the infrastructure (software, hardware, networks), investigates using available tools and countermeasures to remedy the detected vulnerabilities and recommends solutions and best practices. Analyzes and assesses damage to the data/infrastructure as a result of security incidents, examines available recovery tools and processes, and recommends solutions. Tests for compliance with security policies and procedures. May assist in the creation, implementation, or management of security solutions. Security engineer Performs security monitoring, security and data/logs analysis, and forensic analysis, to detect security incidents, and mount the incident response. Investigates and utilizes new technologies and processes to enhance security capabilities and implement improvements. May also review code or perform other security engineering methodologies. Security architect Designs a security system or major components of a security system, and may head a security design team building a new security system. Chief Information Security Officer (CISO) A high-level management position responsible for the entire information security division/staff. The position may include hands-on technical work. Chief Security Officer (CSO) A high-level management position responsible for the entire security division/staff. A newer position is now deemed needed as security risks grow. Data Protection Officer (DPO) A DPO is tasked with monitoring compliance with data protection laws (such as GDPR), data protection policies, awareness-raising, training, and audits. Security consultant/specialist/intelligence Broad titles that encompass any one or all of the other roles or titles tasked with protecting computers, networks, software, data or information systems against viruses, worms, spyware, malware, intrusion detection, unauthorized access, denial-of-service attacks, and an ever-increasing list of attacks by hackers acting as individuals or as part of organized crime or foreign governments. Student programs are also available for people interested in beginning a career in cyber security. Meanwhile, an alternative option for information security professionals of varied experience levels to keep studying is online security training, including webcasts. A wide range of courses are also available. In the United Kingdom, a nationwide set of cyber security forums, known as the U.K Cyber Security Forum, were established supported by the Government's cyber security strategy in order to encourage start-ups and innovation and to address the skills gap identified by the U.K Government. In Singapore, the Cyber Security Agency has issued a Singapore Operational Technology (OT) Cybersecurity Competency Framework (OTCCF). The framework defines emerging cybersecurity roles in Operational Technology. The OTCCF was endorsed by the Infocomm Media Development Authority (IMDA). It outlines the different OT cybersecurity job positions as well as the technical skills and core competencies necessary. It also depicts the many career paths available, including vertical and lateral advancement opportunities.
Access authorization restricts access to a computer to a group of users through the use of authentication systems. These systems can protect either the whole computer, such as through an interactive login screen, or individual services, such as a FTP server. There are many methods for identifying and authenticating users, such as passwords, identification cards, smart cards, and biometric systems. Anti-virus software consists of computer programs that attempt to identify, thwart, and eliminate computer viruses and other malicious software (malware). Applications are executable code, so general corporate practice is to restrict or block users the power to install them; to install them only when there is a demonstrated need (e.g. software needed to perform assignments); to install only those which are known to be reputable (preferably with access to the computer code used to create the application), and to reduce the attack surface by installing as few as possible. They are typically run with least privilege, with a robust process in place to identify, test and install any released security patches or updates for them. For example, programs can be installed into an individual user's account, which limits the program's potential access, as well as being a means control which users have specific exceptions to policy. In Linux, FreeBSD, OpenBSD, and other Unix-like operating systems there is an option to further restrict an application using chroot or other means of restricting the application to its own 'sandbox'. For example. Linux provides namespaces, and Cgroups to further restrict the access of an application to system resources. Generalized security frameworks such as SELinux or AppArmor help administrators control access. Java and other languages which compile to Java byte code and run in the Java virtual machine can have their access to other applications controlled at the virtual machine level. Some software can be run in software containers which can even provide their own set of system libraries, limiting the software's, or anyone controlling it, access to the server's versions of the libraries. Authentication techniques can be used to ensure that communication end-points are who they say they are. Automated theorem proving and other verification tools can be used to enable critical algorithms and code used in secure systems to be mathematically proven to meet their specifications. Backups are one or more copies kept of important computer files. Typically, multiple copies will be kept at different locations so that if a copy is stolen or damaged, other copies will still exist. Capability and access control list techniques can be used to ensure privilege separation and mandatory access control. Capabilities vs. ACLs discusses their use. Chain of trust techniques can be used to attempt to ensure that all software loaded has been certified as authentic by the system's designers. Confidentiality is the nondisclosure of information except to another authorized person. Cryptographic techniques can be used to defend data in transit between systems, reducing the probability that the data exchange between systems can be intercepted or modified.
Cyber attribution, is an attribution of cybercrime, i.e., finding who perpetrated a cyberattack. Cyberwarfare is an Internet-based conflict that involves politically motivated attacks on information and information systems. Such attacks can, for example, disable official websites and networks, disrupt or disable essential services, steal or alter classified data, and cripple financial systems. Data integrity is the accuracy and consistency of stored data, indicated by an absence of any alteration in data between two updates of a data record.
Encryption is used to protect the confidentiality of a message. Cryptographically secure ciphers are designed to make any practical attempt of breaking them infeasible. Symmetric-key ciphers are suitable for bulk encryption using shared keys, and public-key encryption using digital certificates can provide a practical solution for the problem of securely communicating when no key is shared in advance. Endpoint security software aids networks in preventing malware infection and data theft at network entry points made vulnerable by the prevalence of potentially infected devices such as laptops, mobile devices, and USB drives. Firewalls serve as a gatekeeper system between networks, allowing only traffic that matches defined rules. They often include detailed logging, and may include intrusion detection and intrusion prevention features. They are near-universal between company local area networks and the Internet, but can also be used internally to impose traffic rules between networks if network segmentation is configured. A hacker is someone who seeks to breach defenses and exploit weaknesses in a computer system or network. Honey pots are computers that are intentionally left vulnerable to attack by crackers. They can be used to catch crackers and to identify their techniques. Intrusion-detection systems are devices or software applications that monitor networks or systems for malicious activity or policy violations. A microkernel is an approach to operating system design which has only the near-minimum amount of code running at the most privileged level – and runs other elements of the operating system such as device drivers, protocol stacks and file systems, in the safer, less privileged user space. Pinging. The standard ping application can be used to test if an IP address is in use. If it is, attackers may then try a port scan to detect which services are exposed. A port scan is used to probe an IP address for open ports to identify accessible network services and applications. A key logger is spyware that silently captures and stores each keystroke that a user types on the computer's keyboard. Social engineering is the use of deception to manipulate individuals to breach security. Logic bombs is a type of malware added to a legitimate program that lies dormant until it is triggered by a specific event. A unikernel is a computer program that runs on a minimalistic operating system where a single application is allowed to run (as opposed to a general purpose operating system where many applications can run at the same time). This approach to minimizing the attack surface is adopted mostly in cloud environments where software is deployed in virtual machines. Zero trust security means that no one is trusted by default from inside or outside the network, and verification is required from everyone trying to gain access to resources on the network.
Branch, Jordan (24 September 2020). "What's in a Name? Metaphors and Cybersecurity". International Organization. 75 (1). Archived (PDF) from the original on 10 March 2017. Fuller, Christopher J (11 June 2018). "The Roots of the United States' 0145-2096. Bob, Yonah Jeremy (21 August 2021). "Ex-IDF cyber intel. official reveals secrets behind cyber offense". The Jerusalem Post. Kim, Peter (2014). The Hacker Playbook: Practical Guide To Penetration Testing. Seattle: CreateSpace (2018). "Cybersecurity and Liability in a Big Data World". Market and Competition Law Review. 2 (2). Elsevier BV: 71–98.
Shams, Fereidoon (2011). "Enterprise information security, a review of architectures and frameworks from interoperability Singer, P. W.; Friedman, Allan (2014). Cybersecurity and Cyberwar: What Everyone Needs to Know. Oxford University Press. Infrastructure Security Agency CISA. (n.d.). Archived from the original on 25 April 2024. Retrieved 24 April 2024. Sztyber-Betley, A., Syfert, M., KoIcielny, J. M., & Górecka, Z. (2023). Controller Cyber-Attack Detection and Isolation †: Check Point Software Technologies Ltd. is an Israeli cybersecurity company, founded in 1993 by Gil Shwed, Marius Nacht and Shlomo Kramer, whose first product was the FireWall-1 firewall.
According to the press, the hybrid security architecture, combining on-device and cloud-based protections, is designed to improve access speed, support reliable connectivity, and enhance visibility into SaaS applications. The Center for Internet Security (CIS) is a US 501(c)(3) nonprofit organization, formed in October 2000. Its mission statement states that the function of CIS is to "help people, businesses, and governments protect themselves against pervasive cyber threats." The organization is headquartered in East Greenbush, New York, US, with members including large corporations, government agencies, and academic institutions.
provide two-way sharing of information and early warnings on cyber security threats provide a process for gathering and disseminating information on cyber security incidents promote awareness of the interdependencies between cyber and physical critical infrastructure as well as between and among the different sectors coordinate training and awareness ensure that all necessary parties are vested partners in this effort The MS-ISAC offers a variety of federally funded, no-cost, cybersecurity products and services to its members through the DHS CISA cooperative agreement. It also offers fee-based products and services for SLTT members who want additional protection in addition to what is offered under the cooperative agreement. In 2021, the MS-ISAC announced it was undergoing a digital transformation, making major infrastructure upgrades including the implementation of a new cloud-based threat intelligence platform, security information and event management (SIEM) capability, security orchestration, automation, and response (SOAR) tool, and data lake capabilities for threat hunting. Some of the offerings for SLTTs include: A Domain Name Service (DNS) security capability is provided to all SLTTs at no cost known as Malicious Domain Blocking and Reporting (MDBR). The MS-ISAC partnered with Akamai to protect organizations against a variety of cyberattacks such as phishing and ransomware Albert - the MS-ISAC custom-built Intrusion Detection System (IDS) Cyber Threat Intelligence (CTI), including bi-direction indicator feeds via STIX/TAXII. The MS-ISAC has feeds from over 200 sources, including real-time attacks against SLTTs. A 24x7x365 Security Operations Center (SOC) that performs network and endpoint monitoring Vulnerability management and scanning Incident response and digital forensics to contribute a trusted environment to improve the condition of the cybersecurity of the previously mentioned entities to lower the cost of cybersecurity needs to work with companies to bring services and security products to their partners CIS CyberMarket, like the MS-ISAC, serves government entities and non-profits in achieving greater cyber security. On its "resources" page, multiple newsletters and documents are available free of charge, including the "Cybersecurity Handbook for Cities and Counties".
Cloud security posture management, or CSPM, starts with a simple problem: cloud environments change faster than security teams can manually review them. The issue is not only finding misconfigurations, because scanners already do that with depressing enthusiasm. 3. Software Implementation, Frameworks & Protocols This guide explains what CSPM is, how cloud security posture management works, which CSPM tools and features matter, and how enterprise teams use ownership, context, remediation workflows, and audit evidence to turn posture findings into actual cloud security work.
For provider-specific implementation, see our guides to AWS cloud security posture management and Azure cloud security posture management . Cloud security posture management (CSPM) is the practice of continuously assessing cloud environments for misconfigurations, policy violations, exposed assets, weak identity permissions, and compliance gaps. CSPM evaluates cloud resource configurations against selected policies, prioritizes findings with context, and supports the workflow used to resolve or accept them. It does not design the cloud architecture or replace vulnerability management. To evaluate CloudawareâIIs implementation, explore the CSPM product page .
In a mature cloud security program, CSPM helps teams understand where the risk exists, how severe it is, which owner should act, which compliance framework is affected, and whether the fix was completed. IBM defines CSPM as technology that automates and unifies identification and remediation of misconfigurations and security risks across hybrid cloud and multicloud environments, including IaaS, PaaS, and SaaS. MicrosoftâIIs CSPM documentation similarly emphasizes continuous visibility, security recommendations, misconfiguration reduction, and cloud compliance monitoring CSPM solves the gap between fast-changing infrastructure and slower manual security review. Cloud resources appear through IaC templates, deployment pipelines, autoscaling, service-owner changes, test environments, and exception requests.
The urgency around CSPM comes from how cloud environments now operate: fast deployments, distributed ownership, multiple providers, short-lived resources, and audit pressure that does not wait for clean inventory. This section breaks down the engineering and compliance problems that make CSPM a core cloud security function in 2026. Cloud posture is no longer only about whether a storage bucket is public. Google CloudâIIs Cloud Threat Horizons Report shows why CSPM cannot stay limited to static configuration checks. Coverage of the report notes that, in H2 2025, third-party software vulnerabilities accounted for 44.5% of initial access incidents, weak or absent credentials accounted for 27.2% , and misconfigurations accounted for 21%.
The Cloud Security AllianceâIIs 2026 analysis points to the same operational problem from another direction: teams now manage a non-human identity perimeter where machine and non-human identities can outnumber human users by 100-to-1 . Red HatâIIs 2026 cloud-native security research shows the gap between confidence and operating discipline. While 56% of organizations described their day-to-day security posture as highly proactive, only 39% had a mature, well-defined cloud-native security strategy, and approximately 22% had no defined strategy.
Red Hat also reported that 74% of organizations delayed or slowed application deployments over the previous 12 months due to security concerns. Teams may have scanners, dashboards, and cloud-native recommendations, but still lack consistent ownership, remediation SLAs, policy exceptions, control mappings, and evidence trails. The result is posture visibility without posture management, which is how everyone gets a dashboard and nobody gets a fix.
Read also: Cloud Security Assessment . Methodology, Checklist, Best Practices, and Remediation CSPM looks simple from the outside: connect the cloud accounts, scan the resources, and show the findings. In real environments, that workflow has to account for provider-specific configuration models, incomplete ownership data, evolving infrastructure, and remediation paths that span several teams. The steps below show how CSPM turns raw cloud inventory into security findings that can actually be prioritized, assigned, tracked, and proven closed.
CSPM begins with discovery. The tool connects to cloud provider APIs and inventories assets across AWS accounts, Azure subscriptions, GCP projects, Kubernetes clusters, databases, storage, networks, serverless services, IAM resources, and security controls. Every provider models infrastructure differently. AWS accounts, Azure subscriptions, GCP projects, Kubernetes clusters, IAM roles, service principals, firewall rules, network security groups, tags, labels, regions, and logging settings do not line up cleanly.
A CSPM layer needs to normalize those differences into a security model that supports comparison and prioritization. For example, âIIpublic exposureâII may involve an AWS security group, an Azure network security group, a GCP firewall rule, a Kubernetes ingress controller, or a load balancer policy. The control objective is consistent, even when implementation details are provider-specific.
After discovery and normalization, CSPM evaluates resources against policy. Those policies can come from external benchmarks, regulatory frameworks, provider recommendations, or internal engineering standards. In enterprise environments, internal policy is as important as external policy. A company may require every production database to have an owner, application mapping, backup coverage, vulnerability scanning, approved network exposure, and a valid exception if a control cannot be fixed immediately.
Severity alone is a weak prioritization model. A âIIhighâII finding on an isolated non-production resource may matter less than a âIImediumâII finding on an internet-facing production database with sensitive data and excessive identity permissions. 4. Practical Deployment, Analysis & Case Studies A CSPM dashboard turning red is not remediation. Findings need ownership, assignment, escalation, instructions, status, exceptions, and closure validation. Otherwise, the same issue sits in a queue while security asks the platform, the platform asks app teams, app teams ask cloud ops, and everyone enjoys a calendar invite named âIIfollow-up.âII Each CSPM finding should preserve enough detail to support investigation and audit review: That record is useful when an auditor asks whether the control is operating, when an incident responder asks when exposure began, or when a platform lead asks why the same issue keeps returning.
A CSPM tool should not stop at showing failed checks. In complex cloud environments, the useful features are the ones that help teams identify the affected asset, understand priority, route the fix, manage exceptions, and prove closure. Single-provider CSPM can work for a narrow environment, but enterprise teams usually need coverage across AWS, Azure, GCP, Kubernetes, VMware, and on-prem dependencies.
A practical CSPM tool should answer: what exists, where is it, who owns it, what does it support, and which controls apply? Cloudaware cross-cloud inventory showing resources across cloud accounts, subscriptions, environments, owners, and applications. Detection should be continuous enough to catch changes created by deployments, manual console edits, automation, and emergency access.
This is especially important in environments where teams use Terraform, CloudFormation, ARM/Bicep, Helm, Kubernetes manifests, and provider-native deployment tools at the same time. Cloudaware CSPM dashboard showing critical alerts, active violations, mean time to remediate, compliance score, violation severity distribution, and asset scope by resource type. Enterprise CSPM needs exception handling. Some findings are accepted temporarily because remediation requires a migration, vendor dependency, architectural change, or approved compensating control.
Cloudaware compliance evidence view showing policy violations, affected resources, owners, exception status, and remediation history. Risk context turns CSPM from a control checklist into an engineering workflow. A finding should be enriched with exposure, identity, data, workload, service, and business context. Attack path analysis helps teams understand whether several conditions combine into a realistic route to sensitive systems or data. Cloudaware CSPM policy template showing AWS API Gateway public access compliance check, benchmark mappings, test results, and resolution guidance.
CSPM overlaps with several cloud security categories. The difference matters because teams often buy tools before defining workflows, and then everyone gets to discover âIIplatform strategyâII during an incident. CSPM focuses on cloud posture, configuration, compliance, exposure, and remediation. CNAPP is broader and can include CSPM, CWPP, CIEM, IaC scanning, Kubernetes security posture management, cloud detection and response, and other cloud-native security capabilities.
CSPM evaluates cloud control-plane posture and configuration risk. CWPP protects workloads at runtime, including virtual machines, containers, hosts, and workload processes. CIEM focuses on cloud infrastructure entitlement management, including excessive permissions, unused privileges, risky trust relationships, and least-privilege violations. CSPM uses identity context to prioritize posture findings.
DSPM focuses on discovering, classifying, and protecting sensitive data. CSPM focuses on infrastructure-level cloud posture, including compute, containers, PaaS services, network paths, IAM, logging, and encryption configuration. SIEM collects and analyzes security events. CSPM continuously evaluates cloud configuration and compliance state. Most CSPM findings look simple at first: a public endpoint, an open security group, a missing encryption setting, or a failed compliance check. The problem is that a single failed control rarely tells the security team enough to act.
In a real investigation, engineers need to know whether the asset is exposed, who owns it, which application depends on it, what permissions are attached, whether sensitive data is involved, and what evidence will prove the fix A public API Gateway finding depends on intended exposure. Some APIs are meant to be public, while others should only be reachable through a private endpoint, VPC endpoint, or restricted resource policy. A useful CSPM check should separate approved exposure from policy violations instead of treating every API the same.
In this scenario, the policy checks whether an AWS API Gateway REST API allows public access when the required state is private access. If the API endpoint type, resource policy, or access configuration does not match the expected control, the result should create a violation tied to the exact API object. In Cloudaware, this can be represented as a policy template: the policy defines the expected condition, the check evaluates API Gateway objects, and failed results become policy violations with object-level status and remediation guidance.
Native cloud security tools have their own tradeoff, which appears when security teams have to manage posture across several clouds. At that point, the question is less âIIwhich CSPM tool is best?âII and more âIIwhere can the team normalize findings, assign owners, track exceptions, and prove remediation across the full estate?âII 5. Performance Evaluation & Extended Technical Observations Native CSPM can be enough when the environment is mostly single-cloud, compliance scope is limited, ownership is clear, and teams can manage remediation inside the provider console.
Enterprise cloud security rarely stays inside one console. Teams often run a stack: CSPM for posture, native services such as Security Hub or GuardDuty for provider-specific findings, CWPP or EDR for workload protection, and so on. The problem here is that every tool produces findings with different context, ownership, severity, and remediation paths. CSPM should reduce operational confusion and not generate a larger pile of findings with nicer charts. We asked what Cloudaware experts see when CSPM findings have to become actual remediation work, and what cloud engineers keep saying in practitioner discussions .
False positives are not just annoying. In large environments, findings can be technically accurate but operationally wrong because they ignore account purpose, environment type, approved exceptions, business service, compensating controls, or temporary access patterns. A Reddit practitioner called out the false-positive rate in real multi-account environments as one of the questions buyers should ask vendors. That is exactly where posture tools often look strong in demos and then collapse under an enterprise context, because reality loves ruining slide decks.
A CSPM dashboard showing 40,000 violations is not a remediation plan. In large environments, violations need to be broken down by application owner, environment, application, team, department, severity, business service, and other CMDB-linked dimensions so each group can become owned work instead of one giant security backlog nobody can realistically process. âIIThe mistake is measuring CSPM by total violations instead of asking whether those violations can be decomposed into work that the right team can actually own and close.âII âII Katerina L. , Cloud Security Expert at Cloudaware A finding without an owner becomes security debt. CSPM should tie assets to teams, applications, business services, environments, accounts, subscriptions, and escalation paths so remediation does not depend on someone recognizing a resource name from 2021.
âIIIâIIve seen countless remediation efforts fail because the finding reached the wrong queue. The owner has to be resolved from the actual service relationship, not guessed from a tag that may be three-quarters out of date.âIIâII Alla L. , Technical Account Manager at Cloudaware Secrets exposure often sits between posture management, workload scanning, CI/CD security, and data protection, which is exactly why it gets missed. API keys in container environment variables, database passwords in config files, SSH keys in storage buckets, and tokens inside unmanaged workloads may not show up if the team only scans code repositories, Vault, or periodic review samples.
In a Reddit discussion on exposed secrets in cloud workloads, engineers described the same pattern: periodic reviews keep finding new credentials, but teams cannot rotate what they do not know exists. Cloudaware helps teams move from posture visibility to owned remediation work. Its Compliance Engine evaluates policies against CMDB-backed inventory and creates violations when assets do not meet required conditions.
Teams can then break large violation volumes into smaller remediation groups by owner, application, environment, department, severity, or other CMDB-linked dimensions. Core capabilities: Cloud security posture management is the process and tool category used to discover cloud assets, assess configurations, identify misconfigurations, prioritize risky findings, and support remediation across cloud environments. CSPM helps security, platform, DevOps, and compliance teams understand where cloud controls are failing and which resources need action.
CSPM in cloud security stands for cloud security posture management. It evaluates the security state of cloud resources, identities, network exposure, logging, encryption, and compliance controls. In enterprise environments, CSPM should also connect findings to asset ownership, applications, business services, tickets, exceptions, and audit evidence. Cloud security posture management works by discovering cloud assets through provider APIs, normalizing configuration data, evaluating resources against security and compliance policies, prioritizing findings by risk, routing remediation to owners, and preserving evidence for audit and investigation. Mature CSPM programs connect findings to ownership, exposure, identity, application context, and control mappings.
Core CSPM features include cloud asset discovery, misconfiguration detection, compliance mapping, risk prioritization, remediation guidance, workflow integration, exception handling, and evidence history. Enterprise CSPM tools should also support multi-cloud and hybrid environments, including AWS, Azure, GCP, Kubernetes, VMware, and on-prem dependencies where relevant.
No. CSPM focuses on cloud posture, configuration, exposure, compliance, and remediation. CNAPP is broader and may include CSPM, cloud workload protection, identity entitlement management, IaC scanning, Kubernetes security, runtime protection, and cloud detection and response. Gartner describes CSPM as commonly purchased as part of CNAPP. Cloud-native tools are useful within their provider ecosystems, but enterprise teams often need normalized ownership, compliance mapping, exception handling, evidence history, and remediation workflows across multiple providers and hybrid infrastructure. CSPM helps create one operating model for cloud posture across AWS, Azure, GCP, Kubernetes, VMware, and related systems.
Cloud security posture management has evolved well beyond infrastructure configuration. Today, the discipline demands visibility into the identity layer that determines the actual danger of any misconfiguration. This guide covers what CSPM is, where identity gaps amplify its blind spots, how to implement it effectively, and what a mature, identity-first posture program looks like in practice.
Cloud security posture management is the continuous practice of identifying, assessing, and remediating misconfigurations, compliance violations, and security risks across cloud infrastructure. It gives security teams a real-time view of how their cloud environments measure against security policies, regulatory frameworks, and architectural best practices. What is cloud security posture management at its technical core? It's an automated governance layer that sits across IaaS, PaaS, and SSPM, checking the actual state of cloud resources against a defined desired state. When a storage bucket exposes data publicly, an IAM role grants permissions far beyond what any workload requires, or encryption at rest is disabled during a configuration update, cloud security posture management surfaces the deviation and assigns it a risk score tied to real-world impact.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Computer%20security • https://en.wikipedia.org/wiki/Check%20Point • https://en.wikipedia.org/wiki/Center%20for%20Internet%20Security • https://cloudaware.com/blog/cloud-security-posture-management/ • https://www.orchid.security/guides/cloud-security-posture-management
Extracted Research Figures & Simulation Topologies
Total 1 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
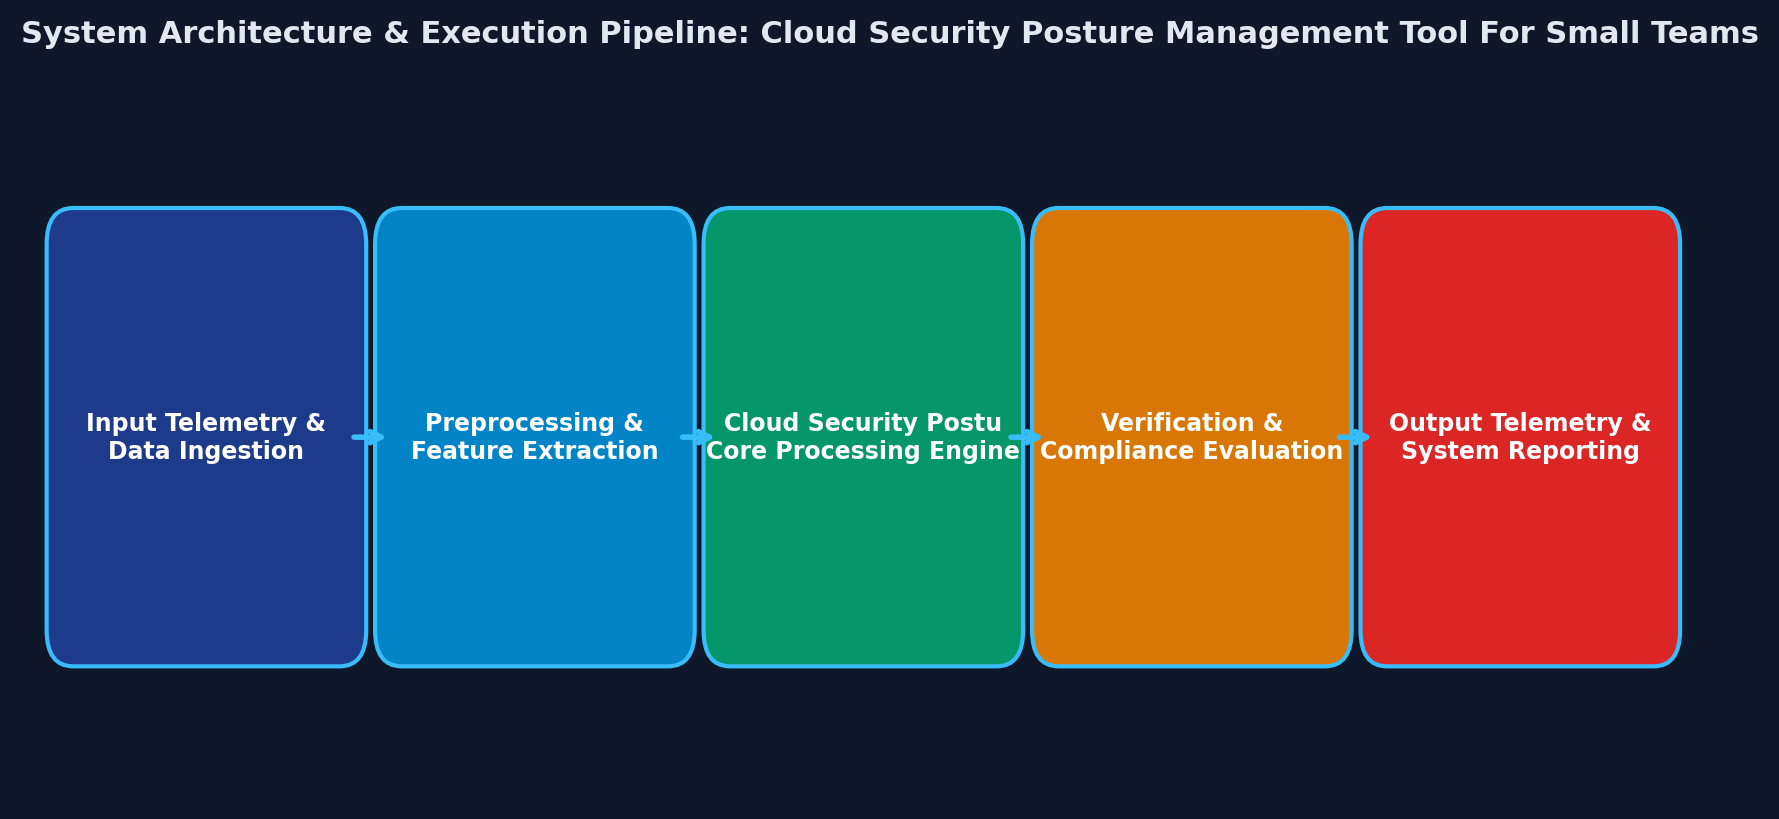
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Cloud Security Posture Management Tool For Small Teams.
[*] Metasploit Scan Running on Target Subnet for Cloud Security Posture Management Tool For Small Teams... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |