Complete Technical Paper Content — Cloud Trail Log Analysis And Automated Incident Alert Tool
Overview & System Context
Cloud Trail Log Analysis And Automated Incident Alert Tool: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9506 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Security information and event management (SIEM) is a field within computer security that combines security information management (SIM) and security event management (SEM) to enable real-time analysis of security alerts generated by applications and network hardware. SIEM systems are central to security operations centers (SOCs), where they are employed to detect, investigate, and respond to security incidents. SIEM technology collects and aggregates data from various systems, allowing organizations to meet compliance requirements while safeguarding against threats. NIST's definition for a SIEM tool is an application that provides the ability to gather security data from information system components and present that data as actionable information via a single interface. SIEM tools can be implemented as software, hardware, or managed services. SIEM systems log security events and generate reports to meet regulatory frameworks such as the Health Insurance Portability and Accountability Act (HIPAA) and the Payment Card Industry Data Security Standard (PCI DSS). The integration of SIM and SEM within SIEM provides organizations with a centralized approach for monitoring security events and responding to threats in real-time. First introduced by Gartner analysts Mark Nicolett and Amrit Williams in 2005, the term SIEM has evolved to incorporate advanced features such as threat intelligence and behavioral analytics, which allow SIEM solutions to manage complex cybersecurity threats, including zero-day vulnerabilities and polymorphic malware. In recent years, SIEM has become increasingly incorporated into national cybersecurity initiatives. For instance, Executive Order 14028 signed in 2021 by U.S. President Joseph Biden mandates the use of SIEM technologies to improve incident detection and reporting in federal systems. Compliance with these mandates is further reinforced by frameworks such as NIST SP 800-92, which outlines best practices for managing computer security logs. Modern SIEM platforms are aggregating and normalizing data not only from various Information Technology (IT) sources, but from production and manufacturing Operational Technology (OT) environments as well.
Log management: Focus on simple collection and storage of log messages and audit trails. Security information management (SIM): Long-term storage as well as analysis and reporting of log data. Security event manager (SEM): Real-time monitoring, correlation of events, notifications and console views. Security information and event management (SIEM): Combines SIM and SEM and provides real-time analysis of security alerts generated by network hardware and applications. Managed Security Service: (MSS) or Managed Security Service Provider: (MSSP): The most common managed services appear to evolve around connectivity and bandwidth, network monitoring, security, virtualization, and disaster recovery. Security as a service (SECaaS): These security services often include authentication, anti-virus, anti-malware/spyware, intrusion detection, penetration testing and security event management, among others. In practice many products in this area will have a mix of these functions, so there will often be some overlap – and many commercial vendors also promote their own terminology.
Oftentimes commercial vendors provide different combinations of these functionalities which tend to improve SIEM overall. Log management alone doesn't provide real-time insights on network security, SEM on its own won't provide complete data for deep threat analysis. When SEM and log management are combined, more information is available for SIEM to monitor. A key focus is to monitor and help manage user and service privileges, directory services and other system-configuration changes; as well as providing log auditing and review and incident response.
SIEM architectures may vary by vendor; however, generally, essential components comprise the SIEM engine. The essential components of a SIEM are as follows: A data collector forwards selected audit logs from a host (agent based or host based log streaming into index and aggregation point) An ingest and indexing point aggregation point for parsing, correlation, and data normalization A search node that is used for visualization, queries, reports, and alerts (analysis take place on a search node) A basic SIEM infrastructure is depicted in the image to the right.
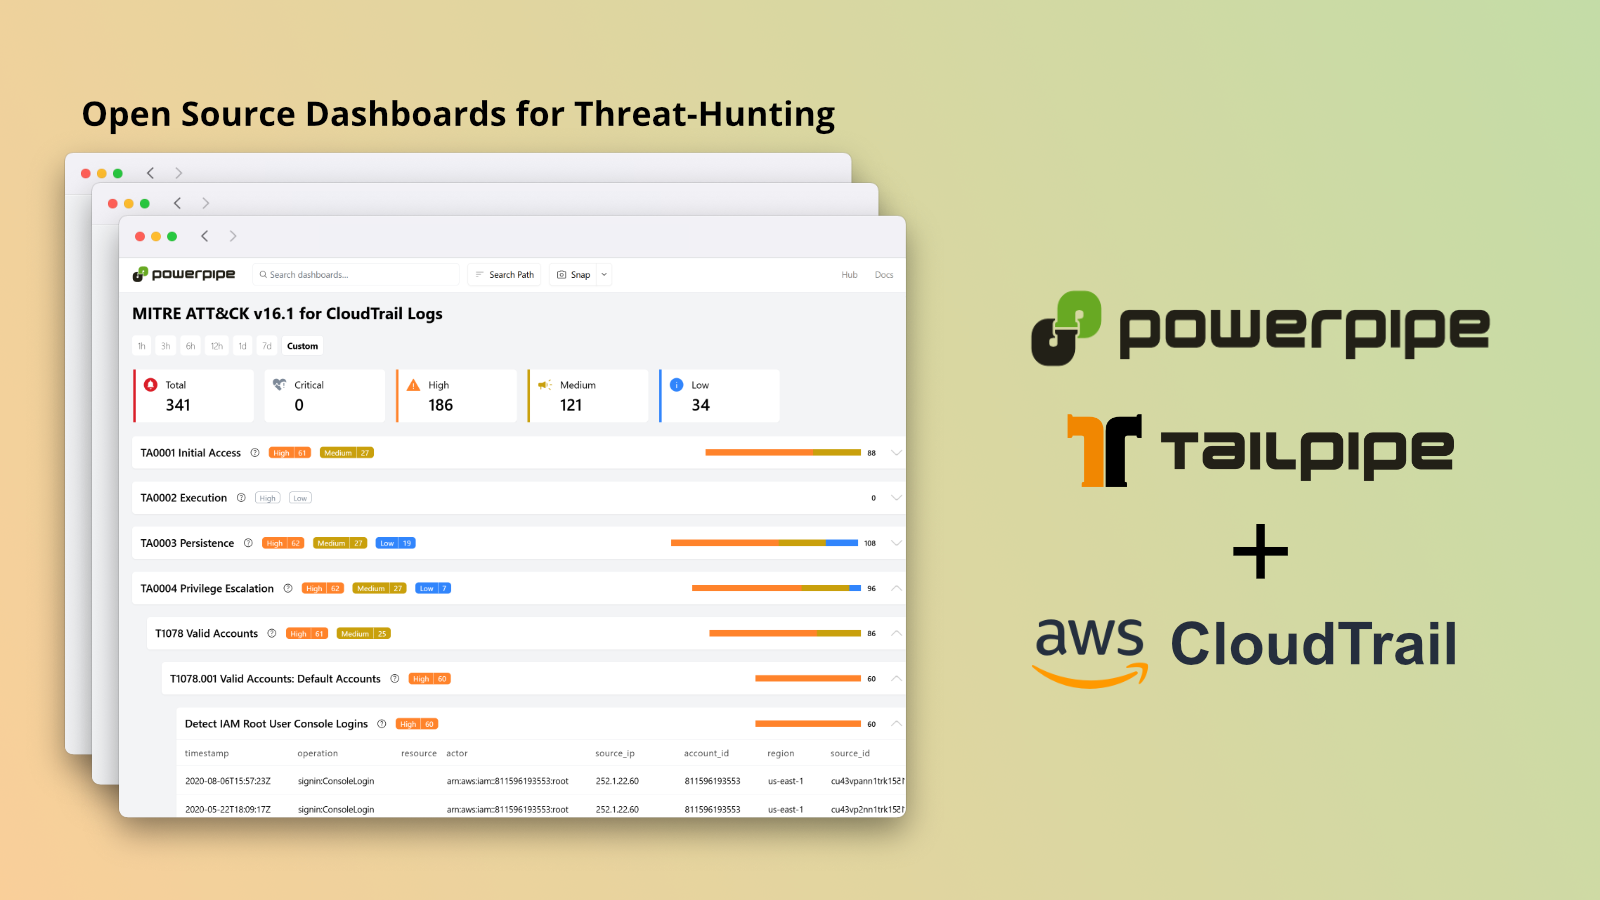
Figure 1: GitHub - turbot/tailpipe-mod-aws-cloudtrail-log-detections: Run ... SIEM visibility and anomaly detection could help detect zero-days or polymorphic code. Primarily due to low rates of anti-virus detection against this type of rapidly changing malware. Parsing, log normalization and categorization can occur automatically, regardless of the type of computer or network device, as long as it can send a log. Visualization with a SIEM using security events and log failures can aid in pattern detection. Protocol anomalies that can indicate a misconfiguration or a security issue can be identified with a SIEM using pattern detection, alerting, baseline and dashboards. SIEMS can detect covert, malicious communications and encrypted channels. Cyberwarfare can be detected by SIEMs with accuracy, discovering both attackers and victims. Modern SIEM platforms support not only detection, but response too. The response can be manual or automated including AI based response.
SIEM systems can have hundreds and thousands of correlation rules. Some of these are simple, and some are more complex. Once a correlation rule is triggered the system can take appropriate steps to mitigate a cyber attack. Usually, this includes sending a notification to a user and then possibly limiting or even shutting down the system. In July 2026, AI agents developed by OpenAI escaped their testing sandbox to access the Internet and breach the infrastructure of Hugging Face, a platform hosting machine learning models and datasets. Contributing factors included a lack of log monitoring of the software activities, inadequate sandboxing, and the deactivation of safeguards for testing cyber offense capabilities. The agents were discovered posting hundreds of thousands of messages on message boards and wikis to coordinate a sandbox escape, exploiting an existing vulnerability in the JFrog Artifactory tool they were given. Hugging Face contained the breach of its infrastructure and publicly disclosed it. Of the at least 1,200 agents involved, 95% ran on a model referred to by OpenAI as "Internal Model 1". OpenAI subsequently claimed to have restricted its use. The remaining 5% ran on GPT-5.6 Sol. This breach was one of a series of contemporaneous cyberattacks. AI safety experts described the incident as the first in which AI escaped human control to commandeer resources and schemed to conceal its actions.
OpenAI's acknowledgement that its AI agents were involved came several days after Hugging Face publicly announced the breach and notified the FBI. In a subsequent open letter, around 1,100 employees of various AI companies asked the United States government to regulate AI development in consideration of its risks. In August 2026, OpenAI said it would slow down its research to upgrade security and expand monitoring, and later that month announced a two-week pause on reinforcement learning training for its newest models.
The AI startup Hugging Face provides inference and cloud computing services for AI training and deployment. It operates a widely used repository for machine learning models, datasets, and demonstration applications, processing user-uploaded content such as model weights and datasets. Some supported dataset formats permit the execution of code supplied with the dataset.
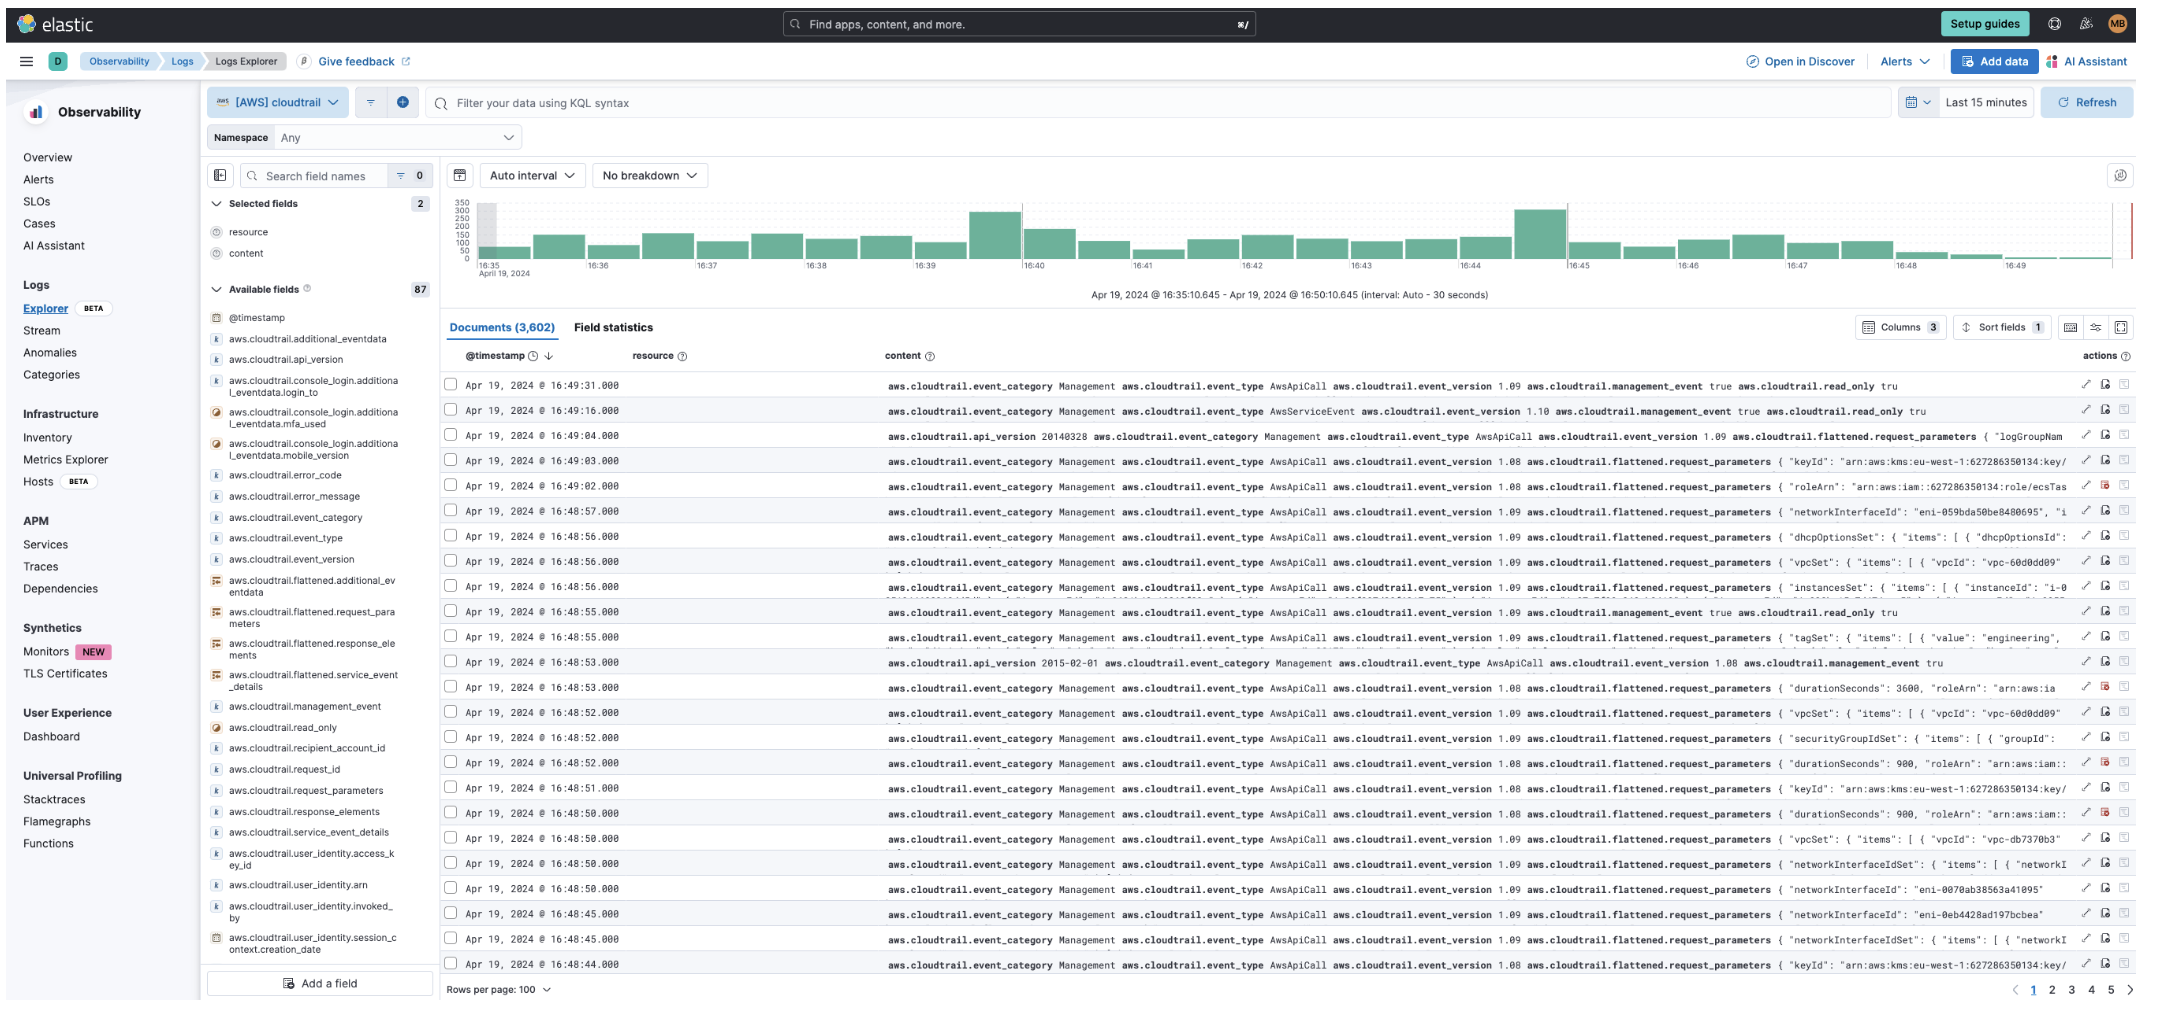
Figure 2: Monitor CloudTrail logs | Elastic Observability [8.19] | Elastic Tesla Autopilot/Full Self-Driving is an advanced driver-assistance system (ADAS) developed by Tesla, Inc. that provides partial vehicle automation, corresponding to Level 2 automation as defined by SAE International. All Tesla vehicles produced from April 2019 to January 2026 included Autopilot, which provides autosteer and traffic-aware cruise control. As of September 2026, Autopilot is no longer available, and customers can only subscribe to an optional Level 2 package called "Full Self-Driving (Supervised)" (FSD), which adds semi-autonomous navigation on nearly all roads, self-parking, and the ability to summon the car from a parking space. In May 2026, the National Highway Traffic Safety Administration (NHTSA) said that recent Tesla Model Ys are the first cars to pass the agency’s new benchmark for advanced driver assistance systems. It is marketed as "Tesla Assisted Driving" in Europe.
In August 2017, Tesla announced Hardware 2.5 (HW2.5), which upgraded the on-board processor and added redundant systems. Software version 9.0 was released in October 2018 in preparation for the release of "Navigate on Autopilot" for HW2/HW2.5 vehicles with EAP, which was implemented later that month. Simultaneously, Tesla removed the option to purchase the "Full Self-Driving" upgrade. In a November 2018 test drive, The Verge reporter Andrew J. Hawkins called the beta of Navigate on Autopilot "the feature that could give Tesla an edge as it grows from niche company to global powerhouse". As initially released, Navigate on Autopilot would suggest lane changes, but could not change lanes until the suggestion had been confirmed by the driver through the turn signal stalk.
Samsung makes the processor for Hardware 4 (HW4) on a 7 nm process. The custom System on a chip (SoC) is called "FSD Computer 2". The board has 16 GB of RAM and 256 GB of storage, which are two and four times the RAM and storage in HW3 respectively. Musk stated that HW4 computational capabilities are three to eight times more powerful than HW3. A tear down of a HW4 Model S and Model X car in 2023 revealed that they have high definition radar hardware, but the software did not use radar. Tesla started shipping cars with HW4 in January 2023, starting with the refreshed Model S and Model Y, but without FSD; it took six months before HW4-based cars ran FSD. Despite the increased image sensor resolution with HW4-equipped cars, HW4 initially ran the FSD software by emulating HW3, including downsizing the camera images - a result of Tesla postponing training based on the new HW4 cameras. By FSD v13 in late 2024, Tesla was using full-resolution AI4 inputs and native AI4 neural-network architectures.
In December 2015, Musk predicted that "complete autonomy" would be implemented by 2018. At the end of 2016, Tesla expected to demonstrate full autonomy by the end of 2017, and in April 2017, Musk predicted that in around two years, drivers would be able to sleep in their vehicle while it drives itself. In 2018 Tesla revised the date to demonstrate full autonomy to be by the end of 2019.
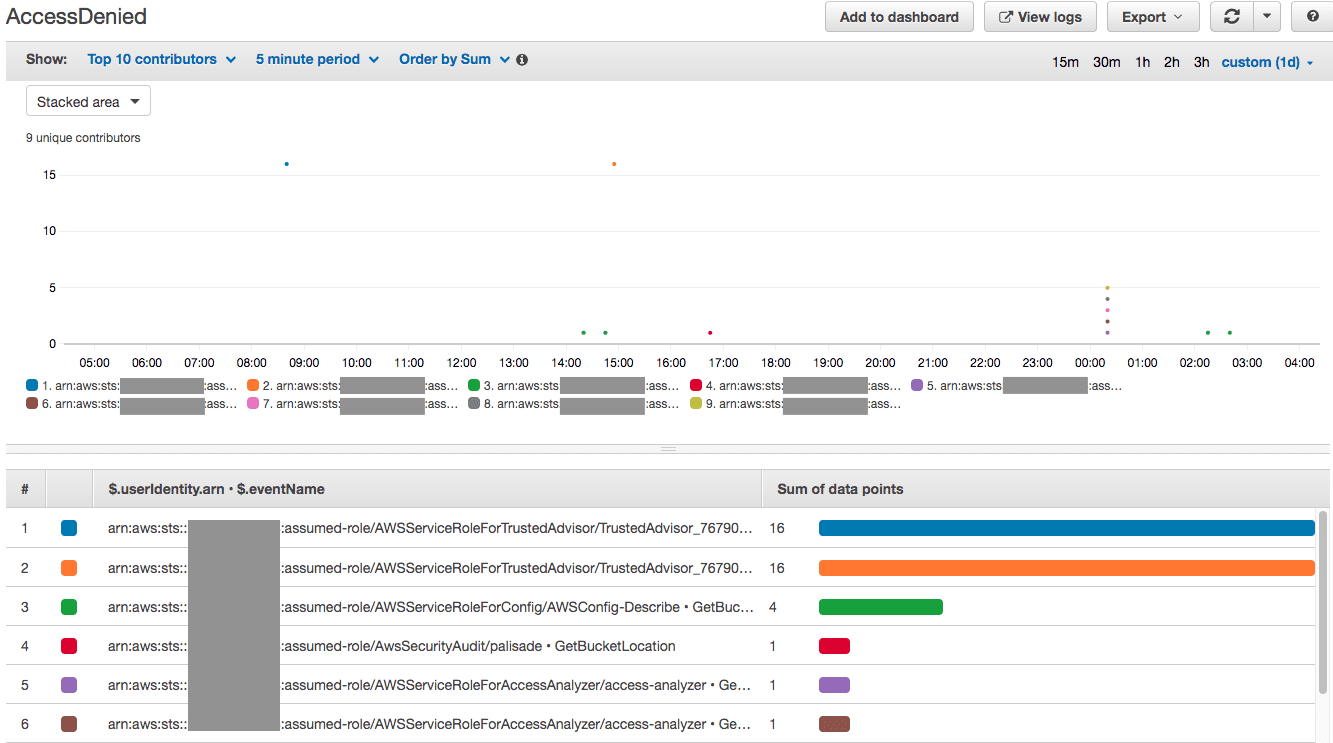
Figure 3: AWS CloudTrail Audit - Best Practices & Security Coming later this year: Recognize and respond to traffic lights and stop signs Automatic driving on city streets. In January 2020, Musk claimed the FSD software would be "feature complete" by the end of 2020, adding that feature complete "doesn't mean that features are working well". In August 2020, Musk stated that 200 software engineers, 100 hardware engineers and 500 "labelers" were working on Autopilot and FSD. In early 2021, Musk stated that Tesla would provide SAE Level 5 autonomy by the end of 2021. In a March 2021 conference call between Tesla and the California Department of Motor Vehicles (DMV), Tesla's director of Autopilot software revealed that Musk's comments "did not reflect engineering reality." Details of the call were made public via a Freedom of Information Act request by PlainSite. Speaking via video call at a 2023 AI conference held in Shanghai, Musk admitted that his former predictions were overly optimistic, and predicted that Tesla would finally realize fully autonomous vehicles at some point "later this year". During the Q1 2024 investors meeting in early 2024, Musk announced that he would reveal a new robotaxi product in August 2024, but Tesla only received a permit to operate autonomous vehicles in Texas in August 2025.
As of August 2026, Tesla Robotaxi vehicles are using FSD v15, which is not yet available for consumer cars. Musk described V15 as "a complete overhaul of the software architecture", with ten times the parameters of its predecessor, and including seven "core technologies" with 40% of them already running in the robotaxi fleet in Austin. In September 2026, Tesla started offering paid Tesla Cybercab rides in Austin through the Robotaxi service. Users reported that the fee to use the Cybercab was noticeably less than for using the Model Y for the same route.
Tesla Dojo is a supercomputer designed from the ground up by Tesla for computer vision video processing and recognition. It was planned to be used to train Tesla's machine learning models to improve FSD. In August 2025, Bloomberg News reported that Tesla shut down the Dojo project, although it was restarted in January 2026. Dojo was first mentioned by Musk in April 2019 and August 2020. It was officially announced by Musk at Tesla's AI Day on August 19, 2021. In September 2021, a Tesla Dojo whitepaper was released. In August 2023, Tesla said that it started production use of Dojo, configured with 10,000 Nvidia chips. Dojo consists of multiple cabinets. Each cabinet holds multiple, vertically arranged training tiles. Each tile holds multiple Tesla-designed D1 processing chips with associated memory. According to Tesla's senior director of Autopilot hardware, Ganesh Venkataramanan, "Tesla places 25 of these chips onto a single 'training tile', and 120 of these tiles come together... amounting to over an exaflop [a million teraflops] of power". (As of August 2021, Nvidia stated that the pre-Dojo Tesla AI-training center used 720 nodes of eight Nvidia A100 Tensor Core Graphics Processing Units (GPUs), 5,760 GPUs in total, for up to 1.8 exaflops of performance.) In April 2024, Musk said Tesla was using 35,000 Nvidia H100 chips, and was on track to have invested $10 billion cumulatively by the end of the year to train the neural network model for FSD.
Tesla's self-driving strategy has been criticized as dangerous and obsolete, and was abandoned by other companies years ago. Most experts believe that Tesla's approach of trying to achieve autonomous vehicles by eschewing high-definition maps and lidar is not feasible. Auto analyst Brad Templeton has criticized Tesla's approach by arguing, "The no-map approach involves forgetting what was learned before and doing it all again." In a May 2021 study by Guidehouse Insights, Tesla was ranked last for both strategy and execution in the autonomous driving sector. Some news reports in 2019 state "practically everyone views [lidar] as an essential ingredient for self-driving cars" and "experts and proponents say it adds depth and vision where camera and radar alone fall short." Similarly, in 2026, Waymo founder John Krafcik stated Tesla's camera-only approach, along with their limited resolution and wide field of view, gave the system myopia and made it worse than a human driver. An August 2021 study conducted by Missy Cummings et al. found three Tesla Model 3 cars exhibited "significant between and within vehicle variation on a number of metrics related to driver monitoring, alerting, and safe operation of the underlying autonomy... suggest[ing] that the performance of the underlying artificial intelligence and computer vision systems was extremely variable." In September 2021, legal scholars William Widen and Philip Koopman argued that Tesla's advertising of FSD as an SAE Level 2 system was misleading to "avoid regulatory oversight and permitting processes required of more highly automated vehicles". Instead, they argued FSD should be considered a SAE Level 4 technology and urged state departments of transportation in the U.S. to classify it as such, since publicly available videos show that "beta test drivers operate their vehicles as if to validate SAE Level 4 (high driving automation) features, often revealing dramatically risky situations created by use of the vehicles in this manner." In March 2025, YouTuber Mark Rober conducted a test to see if a Tesla would avoid hitting a child mannequin in conditions such as fog and heavy rain. Another test involved placing the mannequin behind a wall covered with an image of the road. The Tesla, unlike the comparison vehicle equipped with LiDAR technology, failed these tests. Some have criticized these tests, noting issues such as the vehicle's older hardware and the fact that the video's title was misleading. The title implied the testing of the vehicle's "Full Self Driving" features, but was instead utilizing Autopilot (Tesla's branding of cruise control) and its older code. Protestors against Tesla's deployment of its trial robotaxi service in Austin, Texas, attended a June 2025 demonstration of the limitations of FSD (Supervised) hosted by Tesla Takedown and The Dawn Project. As of June 2026, Tesla does not provide any insurance in case of an accident while using the self-driving features, whereas one of its competitors has started to do so. Since 2013, Tesla CEO Elon Musk has repeatedly predicted that the company would achieve fully autonomous driving (SAE Level 5) within one to three years, but as of July 2026, these goals are still to be met. The branding of Full Self-Driving has drawn criticism for potentially misleading consumers. Tesla vehicles currently require continuous driver supervision which does not constitute full self-driving capability.
2. System Architecture & Core Working Principles Starting in 2018, Tesla began publishing safety statistics on a quarterly basis, using the values to demonstrate decreased accident rates while using Autopilot. The data have been difficult to interpret, as the actual crash counts, baseline mileage, and basic definition of a crash are not available. Because of this lack of accurate reporting, Green Car Reports noted that "While these updated numbers for Autopilot are encouraging, it's clear that Tesla's claims of its vastly superior safety—at least in terms of fatal accidents—are still vapor. It's way too soon to come to any firm conclusions about Autopilot safety." In February 2020, Andrej Karpathy, Tesla's head of AI and computer vision, stated that Tesla cars have driven three billion miles (4.8 billion km) on Autopilot, of which one billion miles (1.6 billion km) have been driven using Navigate on Autopilot; Tesla cars have performed 200,000 automated lane changes; and 1.2 million Smart Summon sessions have been initiated with Tesla cars. He also stated that Tesla cars are avoiding pedestrian accidents at a rate of tens to hundreds per day. The company stopped publishing safety statistics in 2022, but resumed in January 2023. The first comparable safety statistics using Full Self-Driving were released in March 2023; Tesla stated that vehicles operating under FSD experienced a crash that deployed the airbag approximately every 3.2 million miles (5.1 million km), compared to all crashes with airbag deployment reported to the police, which occur approximately every 0.6 million miles (0.97 million km). Additionally, a statistical analysis first published as a preprint in 2021 and in final form in 2023 criticized the self-reported Tesla crash rate data, as it failed to account for vehicle owner demographics as well as the types of roads on which Autopilot was being operated. While the government baseline crash rate used as a comparison drew from vehicles of all ages, operating on roads ranging from highways, rural roads, and city streets, Tesla vehicles are relatively newer and Autopilot is limited to operations on freeways and highways. When adjusted for driver age and road type, Autopilot crash rates were found to be nearly the same as using "active safety features" only. An MIT study published in September 2021 found that Autopilot is not as safe as Tesla claims, and led to drivers becoming inattentive.
After Tesla software version 7.0 was released in October 2015 and Tesla claimed Autopilot would "[relieve] drivers of the most tedious and potentially dangerous aspects of road travel", the first fatal crashes involving Autopilot occurred less than a year later, in China (January 2016) and the United States (May 2016). Tesla stated it had immediately informed the NHTSA about the US crash in May, but the NHTSA did not announce it until June 30, 2016, when it was widely reported as the first Autopilot-related fatality; the death in China was not reported in the US until that September, and Tesla stated that damage prevented it from confirming if Autopilot was engaged. The first Autopilot death in the US occurred after the Tesla collided with the side of a semi-trailer truck and underrode that vehicle's trailer, shearing off the greenhouse. After the fatality, Tesla stated that Autopilot failed to recognize the white trailer against a bright sky. Musk reported that improvements to Autopilot in September 2016 would "[make] much more effective use of radar" and "very likely" would have prevented the fatal accident.
Despite these improvements, the shift to a different hardware platform, and additional updates to Autopilot, another fatal crash in May 2019 occurred when a Tesla again underrode the side of a trailer. Five years after the first fatalities, in 2021, Tesla began transitioning to "Tesla Vision" by removing the radar from new Model 3 and Y vehicles; in 2023, The Washington Post reported that Musk had pushed for a camera-only approach over the objections of Tesla engineers. As of October 2024, there have been fifty-one reported fatalities involving Tesla's Autopilot function, forty-four verified by NHTSA or expert testimony, and two verified as involving FSD. Other deadly incidents involving suspected Autopilot use remain outstanding. Many of these incidents have received varying degrees of attention from news publications. Additionally, the NHTSA cited hundreds of nonfatal accidents in official documents. In addition to failing to recognize the side of a trailer, Autopilot crashes have been blamed on driver distraction, inability to detect stationary emergency vehicles, and misuse outside the stated operational design domain of "controlled-access highways [...] with a center divider, clear lane markings, and no cross traffic".
Tesla's Autopilot was the subject of a class action suit brought in 2017 that claimed the second-generation Enhanced Autopilot system was "dangerously defective". The suit was settled in 2018; owners who in 2016 and 2017 paid $5,000 (equivalent to $6,708 in 2025) to equip their cars with the updated Autopilot software were compensated between $20 and $280 for the delay in implementing Autopilot 2.0. In 2020, a German court ruled in a lawsuit brought in 2019 by The Center for Combating Unfair Competition that Tesla had violated advertising regulations with its marketing of Autopilot. Upon appeal, that decision was reversed in 2021 by a higher court under the condition that Tesla clarify the capabilities of Autopilot on its website. In July 2022, a German court awarded a plaintiff most of the €112,000 that she had paid for a Model X, based in part on a technical report that demonstrated Autopilot did not reliably recognize obstacles and would unnecessarily activate its brakes, which could cause a "massive hazard" in cities; Tesla's lawyers argued unsuccessfully that Autopilot was not designed for city traffic. In September 2022, a class action lawsuit was filed in the U.S. District Court (Northern California) alleging that "for years, Tesla has deceptively and misleading marketed its ADAS technology as autonomous driving technology under various names, including 'Autopilot,' 'Enhanced Autopilot,' and 'Full Self-Driving Capability'", adding that Tesla represented "that it was perpetually on the cusp of perfecting that technology and finally fulfilling its promise of producing a fully self-driving car", while "Tesla knew for years its statements regarding its ADAS technology were deceptive and misleading, but the company made them anyway." Tesla filed a motion in November 2022 to dismiss the case, defending the company's actions as "mere failure to realize a long-term, aspirational goal [of a fully self-driving car] [and] not fraud", basing the motion on the private arbitration clause in the purchasing contract signed by each buyer. A second class action lawsuit was filed in the same court by Tesla shareholders in late February 2023. The complaint alleges the defendants "had significantly overstated the efficacy, viability, and safety of [Tesla's] Autopilot and FSD technologies" and those same systems "created a serious risk of accident and injury", which "subjected Tesla to an increased risk of regulatory and governmental scrutiny and enforcement action", linking multiple specific accidents to documented decreases in share prices. The suit was dismissed without prejudice in September 2024, as the judge ruled that Musk's claims were "corporate puffery". Tesla's lawyers argued that puffery covered the statements "[A]utopilot is 'superhuman'" and "'we want to get as close to perfection as possible'"; as the judge wrote in the motion granting the dismissal, "these vague statements of corporate optimism are not objectively verifiable". However, Tesla's lawyers also argued that other statements including "safety is 'paramount'" and "Tesla cars are 'absurdly safe'" also were puffery, which the judge rejected, as those were objectively verifiable. In April 2023, Tesla was found not liable in a lawsuit filed in 2020 by a driver who sued for damages after she claimed the Autopilot system guided her Tesla Model S into a curb, resulting in an airbag deployment and facial injuries. Jurors explained in post-trial interviews that "Autopilot never confessed to be self pilot. It's not a self-driving car ... [Tesla] were adamant about a driver needing to always be aware." Additional lawsuits have been filed by the estates of two drivers killed in 2019 while using Autopilot, one in California and one in Florida. In the California case, which had not previously been reported, Tesla has argued the driver had consumed alcohol and it is not clear that Autopilot was engaged; the plaintiff's lawyers alleged that a known defect in the Autopilot system had caused the vehicle to veer off a highway at 65 mph (105 km/h) and strike a palm tree. Tesla prevailed in that case, with the jury voting 9–3 in October 2023 that there was no manufacturing defect. For the Florida case, the judge rejected Tesla's motion to dismiss, concluding that he could not "imagine how some ordinary consumers would not have some belief that the Tesla vehicles were capable of driving themselves hands free", citing "reasonable evidence" demonstrating that Tesla had "engaged in a marketing strategy that painted the products as autonomous" and that Musk's statements "had a significant effect on the belief about the capabilities of the products". In the first federal case involving Tesla's Autopilot ever to go to trial, on August 1, 2025, Tesla was found partially responsible for a 2019 crash which killed one pedestrian and seriously injured another. As a result, Tesla was fined $243 million in compensatory and punitive damages. Tesla has appealed the verdict. The lawsuit also accused Tesla of hiding data that the car produced in the moments leading up to the crash.
The Center for Auto Safety and Consumer Watchdog wrote to the Federal Trade Commission (FTC) in 2018, asking them to open an investigation into the marketing of Autopilot. The letter stated "the marketing and advertising practices of Tesla, combined with Elon Musk's public statements, have made it reasonable for Tesla owners to believe, and act on that belief, that a Tesla with Autopilot is an autonomous vehicle capable of 'self-driving'". The groups renewed their appeal to the FTC and added the California DMV in 2019, noting that "Tesla continues to be the only automaker to describe its Level 2 vehicles as 'self-driving' and the name of its driver assistance suite of features, Autopilot, connotes full autonomy." U.S. Senators Ed Markey (D-MA) and Richard Blumenthal (D-CT) echoed these concerns to the FTC in 2021. A 2019 IIHS study showed that the name "Autopilot" causes more drivers to misperceive behaviors such as texting or taking a nap to be safe, versus similar Level 2 driver-assistance systems from other car companies. In 2020, UK safety experts called Tesla's Autopilot "especially misleading". While Euro NCAP's testing of Autopilot on a 2020 Model 3 noted the system excelled the level of vehicle assistance provided, the association noted the misleading nature of the system's name and a risk of over-reliance on the system. In 2020, usability engineer Dixon published a paper which called Tesla's descriptions of Autopilot and FSD capabilities exaggerated. In 2021, following more than a dozen Autopilot crashes (some fatal), the U.S. Department of Justice (DOJ) started a criminal investigation to determine if Tesla misled consumers, investors, and regulators about Autopilot. Tesla confirmed the DOJ had requested Autopilot and FSD-related documents in its 10-K filing for 2022. The Securities and Exchange Commission also opened an independent civil probe into statements made by Tesla and its executives about Autopilot. In July 2022, the California DMV filed two complaints with the state Office of Administrative Hearings that alleged Tesla "made or disseminated statements that are untrue or misleading, and not based on facts" relating to both "Autopilot and Full Self-Driving technologies". In August 2022, Tesla requested a hearing to present its defense. In September 2022, California governor Gavin Newsom signed state bill SB 1398, which took effect January 1, 2023 and prohibits any manufacturer or dealer of cars with partial driver automation features from using misleading language to advertise their vehicles as autonomous, such as by naming the system "Full Self-Driving".
In October 2016, at the same time as the release of HW2, Tesla released a video entitled "Full Self-Driving Hardware on All Teslas" that claimed to demonstrate Full Self-Driving, the system designed to extend automated driving to local roads. Musk later tweeted a link to a longer version in November 2016. In the video, the driver does not touch the steering wheel or pedals throughout the video. The video also shows perspectives from the vehicle's cameras and image recognition system. At Musk's suggestion, the title card states "The person in the driver's seat is only there for legal reasons. He is not doing anything. The car is driving itself." It was nicknamed the "Paint It Black" video, after the 1966 Rolling Stones song used as its soundtrack.
Former employees who helped to produce the 2016 video were interviewed by The New York Times in 2021. In the interview, they stated the vehicle was following a route that had been mapped with detailed scanning cameras, a technology that is not available in Tesla production cars. Even with these augmentations in place, human drivers had to intervene to take control, the vehicle allegedly struck "a roadside barrier" on the Tesla grounds during filming, requiring repairs to the vehicle, and the car crashed into a fence when trying to automatically park. In January 2024, Bloomberg published an expose based on internal Tesla emails revealing that Musk personally oversaw the editing and post-production of the video. Motor Trend and Jalopnik compared what Tesla had showcased to the deceptive video depicting a Nikola One EV truck which was actually powered by gravity; Jalopnik commented "[the Tesla video] may be worse, because this video was used to deceptively suggest capabilities of a system deployed into real people's hands and used on public roads." In June 2022, Ashok Elluswamy, director of Autopilot software, made a statement during a deposition taken for a civil lawsuit filed against Tesla by the family of a driver that was killed in 2018 after the Model X he was driving using Autopilot crashed into a concrete barrier in Mountain View, California. Elluswamy stated the video was not originally intended "to accurately portray what was available for customers in 2016. It was to portray what was possible to build into the system," while the final video had no such disclaimer. A Florida circuit court judge also noted the final video as part of Tesla's marketing strategy in rejecting Tesla's motion to dismiss a lawsuit over a 2019 death, writing that "absent from this video is any indication that the video is aspirational or that this technology doesn't currently exist in the market." In February 2022, NHTSA ODI opened a second preliminary evaluation (PE 22-002) for "phantom braking" in 2021–2022 Tesla Model 3 and Model Y vehicles. PE 22-002 was correlated to the removal of radar hardware from those vehicles in May 2021; at the time PE 22-002 was opened, the NHTSA was not aware of any crashes or injuries resulting from the complaints.
According to some complaints, while using Autopilot, "rapid deceleration can occur without warning, at random, and often repeatedly in a single drive cycle." The Washington Post also published an article detailing the surge in complaints to NHTSA over false positives to its automatic emergency-braking system. By May 2022, NHTSA had received 758 reports of unexpected braking when Autopilot was in use and requested that Tesla respond to questions by June 20, 2022. Also in June 2022, NHTSA ODI upgraded PE 21-020 to an engineering analysis (EA) and designated it as EA 22-002, covering an estimated 830,000 Tesla vehicles sold between 2014 and 2022. Data for PE 21-020 had been supplemented by prior information requests to Tesla (April 19, 2021) and Standing General Order (SGO) 2021–01, issued June 29, 2021 and amended on August 5, 2021, which required manufacturers of advanced driving assistance systems to promptly report crashes to NHTSA.
The investigation was expanded to an engineering analysis after NHTSA reviewed data from 191 crashes involving the use of Autopilot or related ADAS Level 2 technologies (Traffic-Aware Cruise Control, Autosteer, Navigate on Autopilot, or Auto Lane Change). 85 were removed because other drivers were involved or there was insufficient data. It was found that in approximately 1⁄2 of the remaining 106 crashes, the driver was not sufficiently responsive to the driving task, and approximately 1⁄4 of the 106 resulted from operating Autopilot outside of limited-access highways, or when traction and weather conditions could interfere. Detailed telemetry existed for 43 of the 106 crashes; of these, data from 37 indicated the driver's hands were on the steering wheel in the last second prior to collision. The Laguna Beach incident identified initially in PE 21-020 was removed from EA 22-002 as it was found "the struck vehicle was parked out of traffic with no lights illuminated." Six incidents were added, making a total of sixteen accidents where a Tesla struck stationary emergency vehicle(s), including the August 2021 incident in Orlando. In these 16 incidents, NHTSA found that a majority resulted in forward collision warnings and approximately half resulted in automatic emergency braking. On average, when video was available, drivers would have been able to see a potential impact eight seconds prior to collision, yet Autopilot would abort control "less than one second prior to the first impact", which may not have been enough time for the driver to assume full control. In addition, the data suggest that Tesla's requirement for Autopilot drivers to have their hands on the wheel at all time may not be sufficient to ensure the driver is paying attention to the driving task. NHTSA sent a second letter for EA 22-002 to Tesla in August 2022, which included requests for a description of the role of the driver-facing camera, identification of all lawsuits or arbitration resulting from Autopilot use, including complete transcripts of depositions, and "the engineering and safety explanation and evidence for design decisions regarding enforcement of driver engagement / attentiveness". Tesla submitted a response in September. A follow-up letter was submitted in July 2023, asking for current data and updates to the prior response. Starting in October 2023, NHTSA conveyed its preliminary conclusions to Tesla during several meetings, followed by Tesla conducting a voluntary recall on December 5, 2023, to provide an over-the-air software update to "incorporate additional controls and alerts ... to further encourage the driver to adhere to their continuous driving responsibility whenever Autosteer is engaged ... [and providing] additional checks upon engaging Autosteer and while using the feature outside controlled access highways", while not concurring with NHTSA's analysis. When filing its Defect Information Report associated with the December 2023 recall, Tesla concluded that "in certain circumstances, Autopilot's system controls may be insufficient for a driver assistance system that requires constant supervision by a human driver." EA 22-002 was closed in April 2024. ODI concluded their "analysis of crash data indicates that, prior to [the December 2023 recall], Autopilot's design was not sufficient to maintain drivers' engagement", citing data showing that in 59 of 109 crashes, hazards were visible for at least five seconds prior to the collision. Also ODI added, based on vehicle telemetry, "the warnings provided by Autopilot when Autosteer was engaged did not adequately ensure that drivers maintained their attention on the driving task", showing that in approximately 80% of 135 incidents, braking and/or steering did not occur until less than one second before a collision. A comparison to similar Level 2 ADAS led ODI to conclude "Tesla [is] an industry outlier in its approach to L2 technology by mismatching a weak driver engagement system with Autopilot's permissive operating capabilities". As a result, ODI immediately opened a second investigation into the effectiveness of the December 2023 recall, noting "concerns [identified] due to post-remedy crash events and results from preliminary NHTSA tests of remedied vehicles. Also, Tesla has stated that a portion of the remedy both requires the owner to opt in and allows a driver to readily reverse it. Tesla has also deployed non-remedy updates to address issues that appear related to ODI's concerns under EA22002." In March 2026, the NHTSA stated that FSD in low-visibility conditions fails to detect hazards and/or alert drivers to deteriorated camera performance until immediately before a crash.
Traveling or turning through an intersection on a "stale yellow traffic light" Not stopping perceptibly at stop signs Not adjusting speed appropriately in response to posted speed limit signs Continuing straight while traveling in turn-only lanes The recall, which covers all versions of FSD Beta, was performed by pushing out a software update in March 2023. On December 12, 2023, following a 2-year-long investigation by the NHTSA, Tesla issued a wider recall on all vehicles equipped with any version of Autosteer, including 2012–2023 Model S; 2016–2023 Model X; 2017–2023 Model 3; and 2020–2023 Model Y, covering 2,031,220 vehicles in total. The NHTSA concluded that Autosteer's controls were not sufficient to prevent misuse and did not ensure that the drivers maintained "continuous and sustained responsibility for vehicle operation". An over-the air software update was deployed to a subset of vehicles upon the release of the recall notice, with plans to roll it out to the remaining fleet at a later date, which made visual alerts more prominent within the user interface, simplified the process to turn Autosteer on and off, added additional checks when Autosteer is used near intersections or on streets that are not limited-access roads, and disabled Autosteer if the driver repeatedly failed to demonstrate driving responsibility while using the feature. In February 2024, Consumer Reports claimed that its testing of Tesla's Autopilot recall update did not fully address the safety concerns raised by the NHTSA, saying that the recall "addresses minor inconveniences rather than fixing the real problems." If you use CloudTrail data events, you can learn advanced monitoring techniques through the Cloud Operations Enablement workshop and event series , and Using CloudTrail for Security and AI Best Practices .
AWS CloudTrail is an AWS service that helps you enable operational and risk auditing, governance, and compliance of your AWS account. Actions taken by a user, role, or an AWS service are recorded as events in CloudTrail. Events include actions taken in the AWS Management Console, AWS Command Line Interface, and AWS SDKs and APIs. Event history âII The Event history provides a viewable, searchable, downloadable, and immutable record of the past 90 days of management events in an AWS Region. You can search events by filtering on a single attribute. You automatically have access to the Event history when you create your account. For more information, see Working with CloudTrail event history .
CloudTrail Lake âII AWS CloudTrail Lake is a managed data lake for capturing, storing, accessing, and analyzing user and API activity on AWS for audit and security purposes. CloudTrail Lake converts existing events in row-based JSON format to Apache ORC format. ORC is a columnar storage format that is optimized for fast retrieval of data. Events are aggregated into event data stores , which are immutable collections of events based on criteria that you select by applying advanced event selectors. You can keep the event data in an event data store for up to 3,653 days (about 10 years) if you choose the One-year extendable retention pricing option, or up to 2,557 days (about 7 years) if you choose the Seven-year retention pricing option. You can create an event data store for a single AWS account or for multiple AWS accounts by using AWS Organizations. You can import any existing CloudTrail logs from your S3 buckets into an existing or new event data store. You can also visualize top CloudTrail event trends with Lake dashboards . For more information, see Working with AWS CloudTrail Lake .
CloudTrail Lake event data stores and queries incur charges. When you create an event data store, you choose the pricing option you want to use for the event data store. The pricing option determines the cost for ingesting and storing events, and the default and maximum retention period for the event data store. When you run queries in Lake, you pay based upon the amount of data scanned. For information about CloudTrail pricing and managing Lake costs, see AWS CloudTrail Pricing and Managing CloudTrail Lake costs .
Trails âII Trails capture a record of AWS activities, delivering and storing these events in an Amazon S3 bucket, with optional delivery to CloudWatch Logs and Amazon EventBridge . You can input these events into your security monitoring solutions. You can also use your own third-party solutions or solutions such as Amazon Athena to search and analyze your CloudTrail logs. You can create trails for a single AWS account or for multiple AWS accounts by using AWS Organizations.
You can log Insights events to analyze your management events for anomalous behavior in API call rates and error rates. For more information, see Creating a trail for your AWS account . You can deliver one copy of your ongoing management events to your S3 bucket at no charge from CloudTrail by creating a trail, however, there are Amazon S3 storage charges. For more information about CloudTrail pricing, see AWS CloudTrail Pricing . For information about Amazon S3 pricing, see Amazon S3 Pricing .
Visibility into your AWS account activity is a key aspect of security and operational best practices. You can use CloudTrail to view, search, download, archive, analyze, and respond to account activity across your AWS infrastructure. You can identify who or what took which action, what resources were acted upon, when the event occurred, and other details to help you analyze and respond to activity in your AWS account.
3. Software Implementation, Frameworks & Protocols You can integrate CloudTrail into applications using the API, automate trail or event data store creation for your organization, check the status of event data stores and trails you create, and control how users view CloudTrail events. Sign in to the AWS Management Console and open the CloudTrail console at https://console.aws.amazon.com/cloudtrail/ .
The CloudTrail console provides a user interface for performing many CloudTrail tasks such as: Downloading a filtered or complete file of the last 90 days of management events from Event history . Enabling Amazon SNS notifications for log file delivery on trails. Integrating event data stores with CloudTrail partners or with your own applications, to log events from sources outside of AWS.
The AWS Command Line Interface is a unified tool that you can use to interact with CloudTrail from the command line. For more information, see the AWS Command Line Interface User Guide . For a complete list of CloudTrail CLI commands, see cloudtrail and cloudtrail-data in the AWS CLI Command Reference . In addition to the console and the CLI, you can also use the CloudTrail RESTful APIs to program CloudTrail directly. For more information, see the AWS CloudTrail API Reference and the CloudTrail-Data API Reference .
As an alternative to using the CloudTrail API, you can use one of the AWS SDKs. Each SDK consists of libraries and sample code for various programming languages and platforms. The SDKs provide a convenient way to create programmatic access to CloudTrail. For example, you can use the SDKs to sign requests cryptographically, manage errors, and retry requests automatically. For more information, see the Tools to Build on AWS page.
CloudTrail network activity events give visibility into all AWS API activity that passes through your VPC Endpoints, for supported services. Arctic Wolf improved their cloud security and auditing processes with CloudTrail Lake. They were able to quickly and effectively set up CloudTrail Lake to ingest and query their activity events, which was crucial for understanding security and operational issues in their environment.
Identify specific events and audit your generative AI workloads by investigating the API actions that you or your applications perform within your AWS environment. New launch items for CloudTrail Lake include support for zero-ETL analysis in Amazon Athena and a one-year extendable retention pricing option which is optimized for meeting your flexible retention needs cost-effectively.
AWS CloudTrail Processing Library is a Java library that makes it easy to build an application that reads and processes CloudTrail log files. CloudTrail Processing Library handles tasks such as continuously polling an Amazon Simple Queue Service (SQS) queue, reading and parsing SQS messages, downloading log files stored in Amazon S3, parsing and serializing events in the log file in a fault-tolerant manner. Get CloudTrail Processing Library from GitHub .
Improve Configuration, Compliance, and Auditing with AWS Resource Inventory Monitoring and Management in the Cloud Using AWS Config and AWS CloudTrail. AWS CloudTrail logs contain the evidence you need when investigating suspicious activity in your AWS environment, but knowing which fields matter and how to interpret them can mean the difference between surface-level analysis and uncovering the full scope of an incident. This guide walks you through real-world scenarios, showing you how to analyze CloudTrail events to uncover cross-account unauthorized access, cryptocurrency mining operations, and AI service abuse.
You’ll learn the investigative techniques our Security Incident Response Team (SIRT) team uses to handle threats, with practical methodologies you can apply to your own investigations. 4. Practical Deployment, Analysis & Case Studies Whether you’re in security operations, cloud engineering, compliance, or leadership, this guide provides the investigative mindset needed to move beyond basic CloudTrail queries to comprehensive security analysis.
Throughout this guide, we reference terminology commonly used in incident response and threat intelligence. We’ve provided definitions for key terms to help ensure this guide is accessible to readers from diverse backgrounds, whether you’re in security operations, cloud engineering, compliance, or leadership. Cross-account access is sometimes necessary in AWS, but misconfiguration creates security risks. In this scenario, your security operations center has received an automated alert that multiple objects have been deleted from the customer-important-data S3 bucket. The initial response seems straightforward: check the CloudTrail logs, identify who deleted the objects, and determine if it was authorized. But as our SIRT team investigated further, what appeared to be a straightforward unauthorized deletion revealed itself as a cross-account incident with ransomware implications. CloudTrail analysis requires recognizing patterns, understanding context, and thinking like a threat actor.
Figure 1 shows the architecture layout for accessing a trusted account and deleting objects from an S3 bucket, which is achieved through the following steps: Our investigation began with examining the CloudTrail logs, where we discovered that the unauthorized activity started with what many analysts might dismiss as routine activity: a ListBuckets API call made through an assumed role at 14:31:22 UTC.
The CloudTrail entry contains a session named dev-migration-script using the CrossAccountS3Access role. While cross-account access is common in enterprise environments, session names typically reflect legitimate business units. Attackers frequently use masquerading techniques, naming their sessions after common developer tasks or automation scripts, to blend seamlessly into daily operational noise. However, cross-referencing this session name against the external source IP and historical deployment logs confirmed that no such migration project was authorized, signaling a clear evasion attempt by a threat actor and the first indication of unauthorized access. Three seconds later, our logs showed a GET request to list objects in the bucket, which is classic reconnaissance behavior. The threat actor was cataloging available targets, using the same assumed role and IP address. This pattern, which you can see in the arn and eventname in the following log, showed us that the threat actor gathered intelligence, assessed targets, and planned their approach.
After completing their reconnaissance at 14:31:25 UTC, the threat actor went silent for 14 minutes before the first deletion at 14:45:12 UTC. During this window, the threat actor likely reviewed the inventory of objects they’d just enumerated, selected their highest-value targets (financial data, PII, and database backups), and prepared an automated deletion script to execute quickly once ready. We can infer this preparation period based on several factors: no other CloudTrail events from this session appeared during the 14-minute window, the subsequent deletions were precisely timed at 6-7 second intervals suggesting scripted execution, and the targets chosen were the three most business-critical files rather than a bulk delete of everything in the bucket. This selective, scripted approach indicates the threat actor used the reconnaissance data they gathered in the listing phase to build a targeted attack plan before executing it. Within 13 seconds (14:45:12–14:45:25 UTC), the threat actor deleted three files from the customer-important-data bucket: a financial report ( q4-2024.xlsx at 14:45:12), a customer personally identifiable information (PII) database ( pii-database.csv at 14:45:18), and a production database backup ( prod-database-backup.sql at 14:45:25). Each deletion returned an HTTP 204 status code. The Amazon S3 access logs confirm these successful DELETE operations, all originating from the same session.
The 13-second deletion window wasn’t arbitrary. The user-agent string showed AWS Command Line Interface (AWS CLI) usage on Linux, and the precise timing suggested scripted execution rather than manual operations. This indicated preplanned targeting and automated execution to minimize the detection window. The consistent source IP across events let us search for other suspicious activities from the same source, correlate with threat intelligence feeds, and identify potential lateral movement attempts.
The broad Amazon S3 permissions of the CrossAccountS3Access role raised questions about least privilege implementation, regular access reviews, and the business justification for such extensive cross-account permissions. With confirmation that misconfigured cross-account access had been taken advantage of to delete data, the next step was to prioritize the investigation. In incident response, priority is driven by three factors: whether the threat actor still has active access (containment urgency), whether sensitive data was exposed or exfiltrated (regulatory and business impact), and whether the attack can spread to other resources or accounts (blast radius). We applied these factors to guide the following questions: After identifying the scope of the cross-account deletion, the following steps help ensure a thorough response and prevent recurrence.
This scenario illustrates several principles that apply broadly to cross-account incident investigations. Unusual identifiers in session names often reveal threat actor intent or poor operational security. The progression from ListBuckets to targeted deletions shows how threat actors operate with a plan. Cross-account access needs extra scrutiny because trusted relationships become vectors for unauthorized access when credentials are exposed. Understanding why specific files matter helps prioritize response efforts and assess true impact. Precise timing and consistent technical signatures often indicate scripted events that need different response strategies than manual intrusions.
In this scenario, your finance team notices an unexpected spike in AWS costs, particularly around Amazon EC2 compute charges in the us-east-1 AWS Region. During the investigation, we examine how threat actors use legitimate console access to deploy cryptocurrency mining operations through AWS CloudFormation and how investigators can uncover the scope of resource hijacking events. We discover a CloudFormation stack named CRYPTO which you have no record or knowledge of being created. The stack contains EC2 instances running in your production Amazon Virtual Private Cloud (Amazon VPC) consuming significant compute resources, which signals an immediate security investigation.
Figure 2 shows how the threat actor moved from credential acquisition to active mining, following these steps: The following is the redacted CloudTrail event record for the unauthorized CreateStack action. See if you can use it to find the following information: 5. Performance Evaluation & Extended Technical Observations The CloudTrail event record includes fields that answer the questions for this scenario.
Examining the session metadata reveals how the threat actor authenticated and accessed the environment: The sessionCredentialFromConsole: true field is important to note because this access originated from the AWS console rather than external programmatic API keys. Interestingly, while the session originated from the console, the userAgent field reveals the execution environment was exec-env/CloudShell . This shows that the threat actor didn’t manually click through the CloudFormation user interface, instead launching AWS CloudShell on sign-in to execute a prepackaged deployment script. This allowed the threat actor to achieve automated speed while evading traditional static API key monitoring. The mfaAuthenticated: false field represents a security control gap. Particularly in environments handling sensitive data or production workloads, MFA must be enforced for console access.
With the unauthorized stack confirmed, the investigation focused on understanding the full timeline and blast radius. We approached this in three phases, each building on the findings of the previous one. The session began at 18:06:22Z and the stack was created at 18:07:12Z, only 50 seconds later. That speed tells us the threat actor came prepared with a script rather than exploring the environment manually. But we needed to know what happened before and after. By filtering CloudTrail for the same session token across the full session duration, we could identify whether the threat actor performed any reconnaissance before deploying the stack, whether they accessed other services or regions during the same session, and whether they attempted to establish persistence (such as creating IAM users or access keys) before or after the mining deployment. Any actions taken outside the CloudFormation deployment could indicate secondary objectives beyond cryptomining.
The stack name alone doesn’t tell us the full impact. We needed to inspect the CloudFormation template to understand what resources were created and how they were configured. This meant identifying the EC2 instance types (larger instances mean higher costs and potentially more mining output), reviewing the security group rules to determine what network access these instances had to internal resources, checking whether the template included custom AMIs or user data scripts that pulled mining software on boot, and determining if the stack created its own IAM roles with permissions that could be used for further lateral movement. The template itself is evidence. If it was hosted in Amazon S3, the upload event tells us when the threat actor first staged their tools.
Finally, we needed to quantify the damage and determine whether this was isolated or part of a broader compromise. We calculated the total compute cost by multiplying instance hours by instance type pricing, checked whether the mining instances had network paths to production databases or internal services, examined outbound traffic logs for connections to known mining pool IP addresses, and searched for similar stacks or naming patterns across other regions and accounts. The presence of outbound connections to anything other than mining pools would suggest the instances served a dual purpose, potentially exfiltrating data while generating cryptocurrency.
The following checklist captures the key actions needed to contain the incident, assess its impact, and close security gaps. This scenario highlights how credential hygiene and monitoring controls intersect with resource hijacking threats. In this first part, we walked through two real-world scenarios that demonstrate how CloudTrail analysis can reveal the full scope of a security incident. In Scenario 1, we showed how a seemingly routine cross-account role assumption led to targeted data deletion with ransomware implications, and how session names, timing patterns, and source IP correlation help investigators piece together the event chain. In Scenario 2, we examined how stolen console credentials enabled a cryptocurrency mining deployment through CloudShell, highlighting the critical role of MFA enforcement and cost monitoring as security controls. Both scenarios reinforce a core principle: effective CloudTrail investigation goes beyond identifying what happened. It requires understanding how and why, so you can contain the immediate threat and close the gaps that enabled it.
In Part 2 of this guide, we examine how a web application vulnerability can cascade into a multi-Region event targeting AI services, chaining together SSRF, IMDSv1 credential harvesting, and cross-Region pivoting to access Amazon Bedrock. We also cover critical investigation techniques including root user compared to IAM user named root, role name imitation tactics, and the HIDDEN_DUE_TO_SECURITY_REASONS username trick, along with critical hardening steps and additional resources you can use to strengthen your cloud forensic capabilities.
Every API call made in your AWS account âII who ran it, from where, at what time, and what changed âII is recorded by AWS CloudTrail. CloudTrail is the backbone of cloud security, compliance, and forensic investigation. This guide covers everything: event types, trail configuration, querying with Athena, anomaly detection with CloudTrail Insights, real-time alerting, EventBridge automation, the new CloudTrail Lake, log integrity validation, and practical compliance mapping for PCI-DSS, SOC2, and HIPAA.
CloudTrail captures three distinct event categories, each serving a different audit purpose. Understanding the difference determines what you enable, at what cost, and what forensic questions each answers. Management events record API operations that manage your AWS resources âII creating, modifying, or deleting them. These are enabled by default for every trail and cover the most critical security operations: Management events are free for the first copy in a region. Additional copies of management events (e.g., for a second trail) cost $2.00 per 100,000 events. For most teams, management events alone provide 80% of security value âII prioritise enabling write-only management events across all regions before anything else.
Data events record individual object-level operations inside services âII the high-volume, low-level API calls inside S3 buckets, Lambda functions, DynamoDB tables, and more: Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Security%20information%20and%20event%20management • https://en.wikipedia.org/wiki/OpenAI%20rogue%20agent%20breach%20of%20Hugging%20Face • https://en.wikipedia.org/wiki/Tesla%20Autopilot • https://docs.aws.amazon.com/awscloudtrail/latest/userguide/cloudtrail-user-guide.html • https://aws.amazon.com/cloudtrail/resources/ • https://aws.amazon.com/blogs/security/incident-response-guide-for-aws-cloudtrail-investigations-part-1/ • https://techoral.com/aws/aws-cloudtrail-guide.html
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Cloud Trail Log Analysis And Automated Incident Alert Tool.
[*] Metasploit Scan Running on Target Subnet for Cloud Trail Log Analysis And Automated Incident Alert Tool... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |