Complete Technical Paper Content — Connected Vehicle Intrusion Detection System Using Ml
Overview & System Context
Connected Vehicle Intrusion Detection System Using Ml: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9584 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background This repository contains the code for the project "IDS-ML: Intrusion Detection System Development Using Machine Learning".
The code and proposed Intrusion Detection System (IDSs) are general models that can be used in any IDS and anomaly detection applications. In this project, three papers have been published: This repository proposed three intrusion detection systems by implementing many machine learning algorithms, including tree-based algorithms ( decision tree, random forest, XGBoost, LightGBM, CatBoost etc. ), unsupervised learning algorithms ( k-means ), ensemble learning algorithms ( stacking, proposed LCCDE ), and hyperparameter optimization techniques ( Bayesian optimization )**.
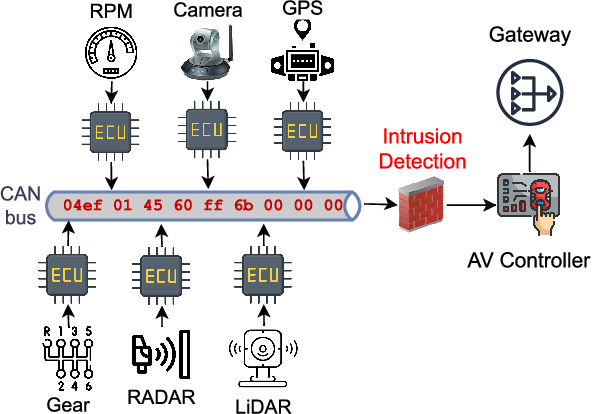
Another intrusion detection system development code using convolutional neural networks (CNNs) and transfer learning techniques can be found in: Intrusion-Detection-System-Using-CNN-and-Transfer-Learning A comprehensive hyperparameter optimization tutorial code can be found in: Hyperparameter-Optimization-of-Machine-Learning-Algorithms Figure 1: Figure 1 from Revisiting the Intrusion Detection in In-Vehicle Networks ...
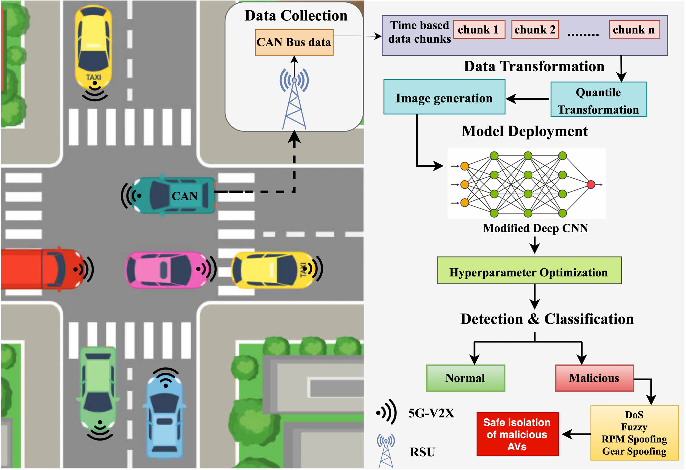
The use of autonomous vehicles (AVs) is a promising technology in Intelligent Transportation Systems (ITSs) to improve safety and driving efficiency. Vehicle-to-everything (V2X) technology enables communication among vehicles and other infrastructures. However, AVs and Internet of Vehicles (IoV) are vulnerable to different types of cyber-attacks such as denial of service, spoofing, and sniffing attacks. An intelligent IDS is proposed in this paper for network attack detection that can be applied to not only Controller Area Network (CAN) bus of AVs but also on general IoVs. The proposed IDS utilizes tree-based ML algorithms including decision tree (DT), random forest (RF), extra trees (ET), and Extreme Gradient Boosting (XGBoost).
The results from the implementation of the proposed intrusion detection system on standard data sets indicate that the system has the ability to identify various cyber-attacks in the AV networks. Furthermore, the proposed ensemble learning and feature selection approaches enable the proposed system to achieve high detection rate and low computational cost simultaneously. Paper 2: MTH-IDS: A Multi-Tiered Hybrid Intrusion Detection System for Internet of Vehicles Modern vehicles, including connected vehicles and autonomous vehicles, nowadays involve many electronic control units connected through intra-vehicle networks to implement various functionalities and perform actions. Modern vehicles are also connected to external networks through vehicle-to-everything technologies, enabling their communications with other vehicles, infrastructures, and smart devices. However, the improving functionality and connectivity of modern vehicles also increase their vulnerabilities to cyber-attacks targeting both intra-vehicle and external networks due to the large attack surfaces. To secure vehicular networks, many researchers have focused on developing intrusion detection systems (IDSs) that capitalize on machine learning methods to detect malicious cyber-attacks. In this paper, the vulnerabilities of intra-vehicle and external networks are discussed, and a multi-tiered hybrid IDS that incorporates a signature-based IDS and an anomaly-based IDS is proposed to detect both known and unknown attacks on vehicular networks. Experimental results illustrate that the proposed system can accurately detect various types of known attacks on the CAN-intrusion-dataset representing the intra-vehicle network data and the CICIDS2017 dataset illustrating the external vehicular network data. The proposed MTH-IDS framework consists of two traditional ML stages (data pre-processing and feature engineering) and four tiers of learning models: Paper 3: LCCDE: A Decision-Based Ensemble Framework for Intrusion Detection in The Internet of Vehicles Figure 2: Figure 1 from IIDS: Intelligent Intrusion Detection System for ...
Modern vehicles, including autonomous vehicles and connected vehicles, have adopted an increasing variety of functionalities through connections and communications with other vehicles, smart devices, and infrastructures. However, the growing connectivity of the Internet of Vehicles (IoV) also increases the vulnerabilities to network attacks. To protect IoV systems against cyber threats, Intrusion Detection Systems (IDSs) that can identify malicious cyber-attacks have been developed using Machine Learning (ML) approaches. To accurately detect various types of attacks in IoV networks, we propose a novel ensemble IDS framework named Leader Class and Confidence Decision Ensemble (LCCDE). It is constructed by determining the best-performing ML model among three advanced ML algorithms (XGBoost, LightGBM, and CatBoost) for every class or type of attack. The class leader models with their prediction confidence values are then utilized to make accurate decisions regarding the detection of various types of cyber-attacks. Experiments on two public IoV security datasets (Car-Hacking and CICIDS2017 datasets) demonstrate the effectiveness of the proposed LCCDE for intrusion detection on both intra-vehicle and external networks.
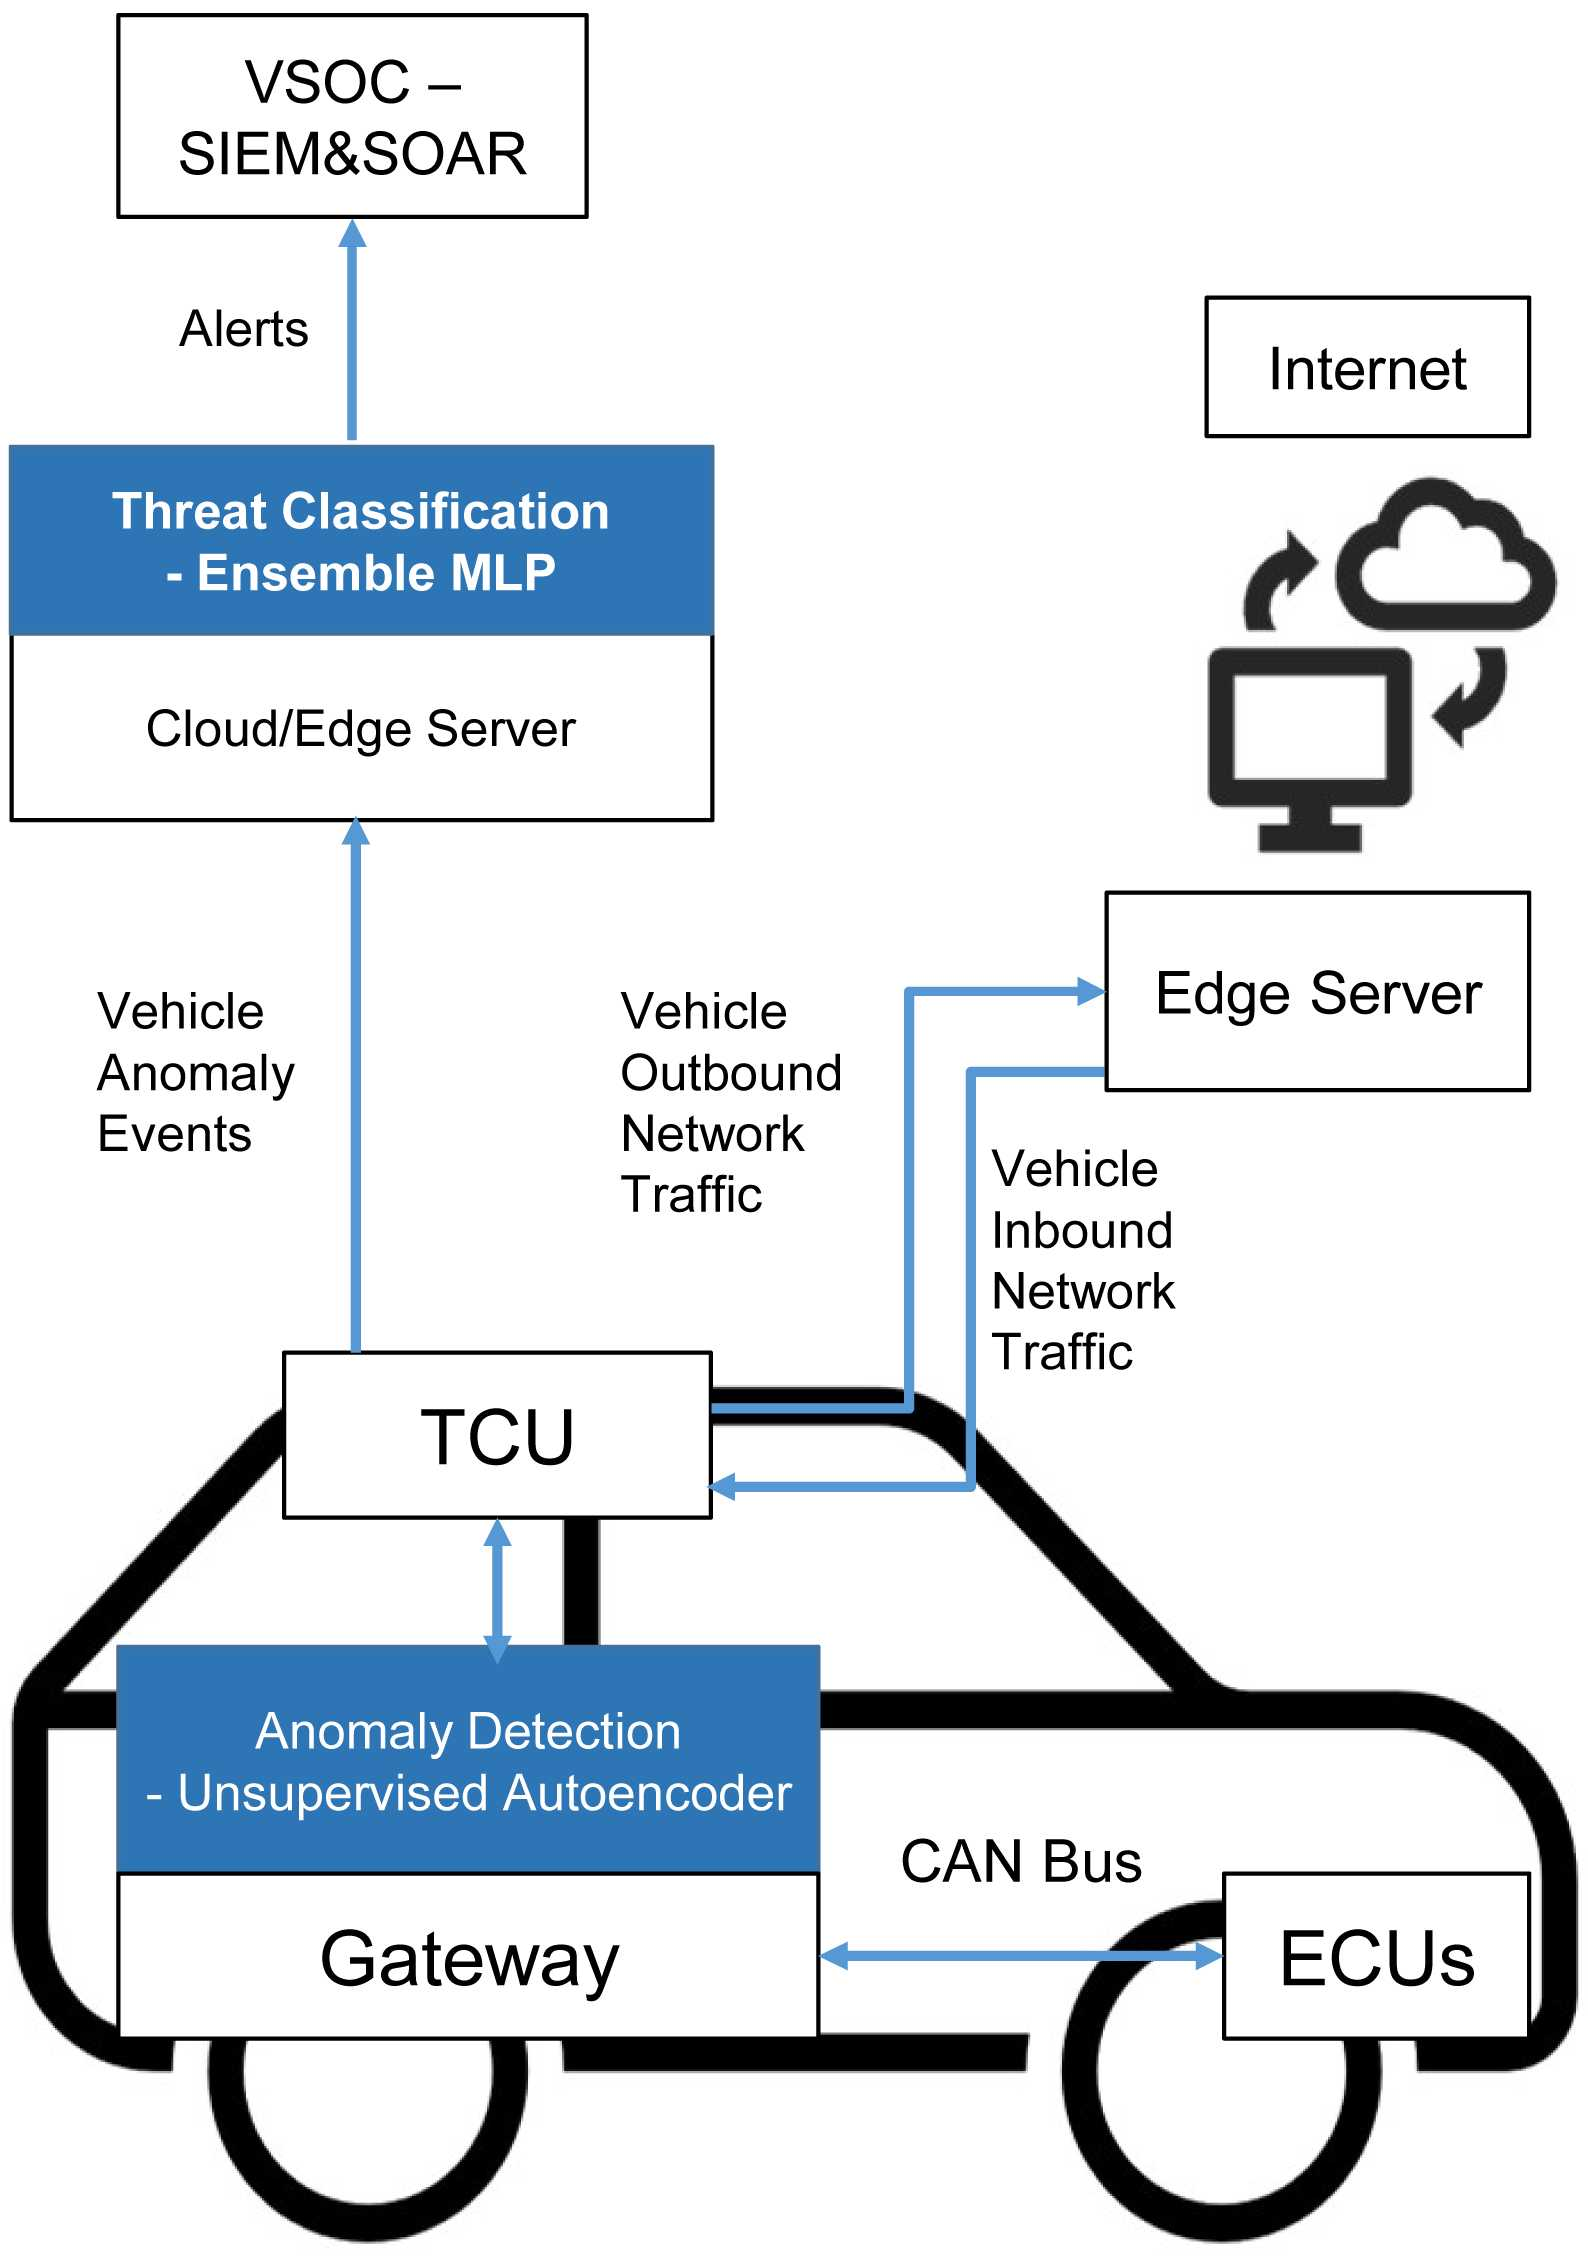
CICIDS2017 dataset, a popular network traffic dataset for intrusion detection problems CAN-intrusion dataset, a benchmark network security dataset for intra-vehicle intrusion detection If you are interested in hyperparameter tuning of machine learning algorithms, please see the code in the following link: https://github.com/LiYangHart/Hyperparameter-Optimization-of-Machine-Learning-Algorithms Figure 3: An Enhanced and Explainable Hybrid Ensemble Intrusion Detection System ...
Please feel free to contact us for any questions or cooperation opportunities. We will be happy to help. If you find this repository useful in your research, please cite one of the following two articles as: L. Yang, A. Moubayed, I. Hamieh and A. Shami, "Tree-Based Intelligent Intrusion Detection System in Internet of Vehicles," 2019 IEEE Global Communications Conference (GLOBECOM), 2019, pp.
1-6, 10.1109/GLOBECOM38437.2019.9013892. L. Yang, A. Moubayed, and A. Shami, “MTH-IDS: A Multi-Tiered Hybrid Intrusion Detection System for Internet of Vehicles,” L. Yang, A. Shami, G. Stevens, and S. DeRusett, “LCCDE: A Decision-Based Ensemble Framework for Intrusion Detection in 10.1109/GLOBECOM48099.2022.10001280.
Code for IDS-ML: intrusion detection system development using machine learning algorithms (Decision tree, random forest, extra trees, XGBoost, stacking, k-means, Bayesian optimization..) Connected and Autonomous Vehicles (CAVs) enhance mobility but face cybersecurity threats, particularly through the insecure Controller Area Network (CAN) bus. Cyberattacks can have devastating consequences in connected vehicles, including the loss of control over critical systems, necessitating robust security solutions. In-vehicle Intrusion Detection Systems (IDSs) offer a promising approach by detecting malicious activities in real time. This survey provides a comprehensive review of state-of-the-art research on learning-based in-vehicle IDSs, focusing on Machine Learning (ML), Deep Learning (DL), and Federated Learning (FL) approaches. Based on the reviewed studies, we critically examine existing IDS approaches, categorising them by the types of attacks they detect—known, unknown, and combined known-unknown attacks—while identifying their limitations. We also review the evaluation metrics used in research, emphasising the need to consider multiple criteria to meet the requirements of safety-critical systems. Additionally, we analyse FL-based IDSs and highlight their limitations. By doing so, this survey helps identify effective security measures, address existing limitations, and guide future research toward more resilient and adaptive protection mechanisms, ensuring the safety and reliability of CAVs.
Keywords CAN bus ⋅ \cdot Cyberattack ⋅ \cdot Intrusion Detection System ⋅ \cdot Anomaly Detection ⋅ \cdot Machine Learning ⋅ \cdot In-vehicle Network. 2. System Architecture & Core Working Principles Connected and Autonomous Vehicles (CAVs) are expected to become the backbone of future transportation systems [ Aloraini et al.(2024)Aloraini, Javed, and Rana ] , offering the potential to not only revolutionise mobility, but also deliver significant economic benefits. For example, the Society of Motor Manufacturers and Traders (SMMT) estimates that this technological shift could provide the United Kingdom with an annual economic boost of £62 billion by 2030 [ SMMT Driving the Motor Industry(2019) ] . However, these advancements also present significant security challenges for CAVs, making them attractive targets for emerging cyber threats [ Pickford et al.(2024)Pickford, Attale, Shaikh, Nguyen, and Harrison ] .
CAVs rely on Electronic Control Units (ECUs) to manage and control various functions. These ECUs communicate through standardised in-vehicle communication protocols, such as the Controller Area Network (CAN), FlexRay, Local Interconnect Network (LIN) and Media Oriented System Transport (MOST). Among these, the CAN bus is the protocol that is the most widely used, valued for its high speed, reliability, and ease of use [ Al-Jarrah et al.(2019)Al-Jarrah, Maple, Dianati, Oxtoby, and Mouzakitis ] . Although originally designed for industrial applications, the CAN bus has become the de facto standard for in-vehicle communication [ Althunayyan et al.(2024a)Althunayyan, Javed, and Rana ] . Despite its advantages, the CAN protocol was not designed with security in mind and lacks essential features such as sender authentication and encryption [ Paul and Islam(2021) ] .
The increasing interconnectivity of CAVs exposes them to a range of cyberattacks. The attack surfaces in modern vehicles can be accessed either physically, via ports such as the USB or the onboard diagnostic (OBD)-II port, or remotely through wireless technologies such as Bluetooth, Wi-Fi, and LTE [ Aliwa et al.(2021)Aliwa, Rana, Perera, and Burnap ] . In 2023, the number of large-scale incidents, potentially affecting thousands to millions of mobility assets, grew 2.5-fold compared to 2022.
Additionally, 95% of cyberattacks are conducted remotely, with 85% being long-range [ Ltd.(2024) ] . These vulnerabilities make vehicles susceptible to attacks that could have devastating consequences, including loss of control over critical systems like braking, steering, and acceleration [ Young et al.(2019)Young, Zambreno, Olufowobi, and Bloom ] . A recent incident [ Tindell(2023) ] involved cybersecurity researcher Ian Tabor discovering tampering on his Toyota RAV4, particularly around the front bumper and headlight area. Initially suspecting vandalism, Tabor soon realised the vehicle had been targeted by a cyberattack. Investigations revealed that attackers had accessed the car’s CAN bus through exposed wiring, allowing them to inject malicious signals. This manipulation enabled the attackers to unlock the doors and start the engine, ultimately stealing the vehicle without the need for a key. Moreover, a notorious example is the Jeep hack, where attackers remotely gained control over the vehicle’s braking and steering systems, resulting in dangerous driving conditions [ Golson(2016) ] . Similarly, vulnerabilities in BMW and Toyota Lexus models have been exploited, demonstrating the persistent threat to vehicle security [ Lab(2018) , Lab(2020) ] . Such incidents underscore the need for robust security measures to protect against both information theft and direct physical harm.
Given the severity of these threats, the security of the CAN bus has become a major area of research. According to McKinsey’s analysis, by 2030, almost 95% of the new vehicles will be connected to external networks, further highlighting the need for effective security solutions [ Bertoncello et al.(2021)Bertoncello, Martens, Möller, and Schneiderbauer ] . One promising approach is the implementation of Intrusion Detection Systems (IDSs) , which monitor network traffic for malicious activity. In the context of in-vehicle networks, an IDS is typically installed on an ECU and analyses incoming messages to detect abnormalities. However, conventional IDS technologies designed for traditional networks cannot be applied directly to in-vehicle systems due to resource constraints and the real-time requirements of automotive environments.
Research on the development of in-vehicle IDSs has expanded considerably in recent years, fueled by the discovery of various vulnerabilities and the urgent need to improve the security of in-vehicle networks and detect cyberattacks. Researchers have explored various approaches to building these systems. IDSs can be classified as either signature-based, for detecting known attacks, or anomaly-based, for identifying new, unknown attacks [ Hoppe et al.(2009)Hoppe, Kiltz, and Dittmann ] . Anomaly-based IDSs are further categorised into statistical, Machine Learning (ML), rule-based, and physical fingerprinting methods [ Rajapaksha et al.(2023a)Rajapaksha, Kalutarage, Al-Kadri, Petrovski, Madzudzo, and Cheah ] .
This survey specifically examines the development of learning-based in-vehicle IDSs, with a focus on Machine Learning (ML), Deep Learning (DL), and Federated Learning (FL) approaches. It aims to identify effective security strategies, overcome existing challenges, and guide future research toward more robust and adaptive protection mechanisms to ensure the safety and reliability of CAVs. The emphasis on ML- and DL-based approaches is driven by their strong generalization capabilities and ability to process large volumes of traffic data [ Rajapaksha et al.(2023a)Rajapaksha, Kalutarage, Al-Kadri, Petrovski, Madzudzo, and Cheah ] . Additionally, FL has recently gained attention among researchers due to its potential to enhance both security and privacy.
In this survey, we review the state-of-art research on ML-based, DL-based and FL-based in-vehicle IDSs, aiming to identify limitations and research gaps in the existing work. We present a comprehensive literature review employing a structured search strategy to systematically gather research papers published up to January 2025.
We present a systematic categorization of CAN protocol vulnerabilities by conducting an in-depth analysis of the CAN protocol, identifying its weaknesses, entry points, and potential attack scenarios. We introduce a classification framework for IDS methodologies based on the types of attacks they detect, including known, unknown, and combined known-unknown threats. Additionally, we present summary tables and highlight the limitations of each approach to identify research gaps.
We analyse the evaluation metrics used in research studies, emphasising the importance of considering multiple factors—such as performance, time complexity, and memory overhead—when developing in-vehicle IDSs to ensure they meet the requirements of safety-critical systems. We provide insights into FL-based IDSs, discussing their advantages while also identifying limitations in addressing security and privacy challenges in connected vehicle environments.
We outline key open challenges and propose future research directions to enhance the development of more effective, efficient, and resilient in-vehicle IDS solutions. The remainder of this paper is organised as follows. Section 2 provides context and background information. Section 3 reviews similar surveys and highlights our contributions. Section 4 outlines the search methodology used to collect relevant papers. Section 5 reviews existing ML- and DL-based in-vehicle IDSs, while Section 6 focuses on FL-based IDSs. Section 7 discusses future research directions. Finally, Section 8 concludes the paper.
This section provides a brief overview of in-vehicle protocols, with a particular focus on the CAN protocol, including its description, functionality, and aspects relevant to cyberattacks. In addition, it examines the vulnerabilities, entry points, and attack scenarios of CAN. The in-vehicle network is the internal network that facilitates communication between multiple ECUs within a vehicle [ Liu et al.(2020)Liu, Zhang, Song, and Letaief ] . These ECUs are interconnected embedded devices responsible for controlling various vehicle functions, such as engine management, airbag control, and climate control. The number and type of ECUs in a vehicle vary depending on the manufacturer and model, with modern vehicles incorporating up to 100 ECUs alongside basic functions [ Ahmad et al.(2024)Ahmad, Han, Jolfaei, Jabbar, Ibrar, Erbad, Song, and Alkhrijah ] . These ECUs, along with sensors, actuators, cameras, radars, and communication devices, collaborate to enhance vehicle performance, efficiency, intelligent services, and safety by collecting and interpreting various data [ Boumiza and Braham(2017) ] . ECUs communicate using standard protocols such as CAN, FlexRay, LIN, and MOST [ Kumar and Ramesh(2014) ] . Among these, CAN is considered the de facto protocol for in-vehicle communication [ Al-Jarrah et al.(2019)Al-Jarrah, Maple, Dianati, Oxtoby, and Mouzakitis ] .
The Controller Area Network (CAN) protocol, developed by Robert Bosch in 1985, was designed to reduce the weight, complexity, and cost of wiring. Due to its high speed and efficiency, CAN has become the most widely used in-vehicle communication protocol in connected and autonomous vehicles [ Al-Jarrah et al.(2019)Al-Jarrah, Maple, Dianati, Oxtoby, and Mouzakitis ] . CAN operates as a message-based broadcast protocol, where the ECUs transmit data in pre-defined frames.
Since the system uses a broadcast mechanism, each message is sent to all ECUs on the network. The CAN frame follows a specific message structure defined in a database-like file known as the DataBase CAN (DBC) file. This file is confidential and proprietary to the vehicle manufacturer, containing all the essential information about the representation of the CAN bus data [ Lokman et al.(2019)Lokman, Othman, and Abu-Bakar ] . The CAN data frame consists of seven fields that facilitate data transmission between ECUs. Figure 1 illustrates the standard CAN frame format, which consists of the following fields: Start of Frame (SOF): The purpose of this field is to synchronise the transmission of the CAN message with all nodes and to signal the initiation of its transmission.
Arbitration Field (ID): This field, also known as the CAN ID, is used to specify the destination address of the designated ECU. It also determines the priority of the message, where a lower value generally indicates a higher priority. The ID field is 11 bits in size. 3. Software Implementation, Frameworks & Protocols Data Length Code (DLC): This field provides information about the length of the data field.
Data Field: This field, also known as the payload, includes the actual vehicle parameter values, which are interpreted by the received ECU and its size can vary from 0 to 8 bytes (0-64 bits). Cyclic Redundancy Check (CRC): This field detects errors and maintains data integrity during message transmission with a fixed size of 16 bits.
Acknowledge Field (ACK): This field receives confirmation from the receiving node that the CAN message was received correctly. The CAN bus was introduced to reduce costs, simplify installation, and improve real-time communication efficiency within vehicles. However, it is vulnerable to cyberattacks due to several inherent vulnerabilities [ Aliwa et al.(2021)Aliwa, Rana, Perera, and Burnap , Carsten et al.(2015)Carsten, Andel, Yampolskiy, and McDonald , Liu et al.(2017)Liu, Zhang, Sun, and Shi ] , including the following: Lack of authentication: Due to the lack of authentication on the CAN bus, any ECU can transmit a frame using the CAN ID of another ECU [ Young et al.(2019)Young, Zambreno, Olufowobi, and Bloom ] . Each ECU broadcasts and receives all data on the bus, then determines whether a message is intended for it. However, the CAN protocol is inherently unable to prevent unauthorised devices from joining the network and sending malicious messages to all ECUs. As a result, attackers can exploit compromised ECUs to spoof and send fake CAN packets, leading to spoofing and message injection attacks [ Rajapaksha et al.(2023a)Rajapaksha, Kalutarage, Al-Kadri, Petrovski, Madzudzo, and Cheah ] .
Lack of encryption: Due to time constraints, CAN messages are not encrypted [ Aliwa et al.(2021)Aliwa, Rana, Perera, and Burnap ] , allowing cyberattackers to easily capture and analyse them for further attacks. Lack of encryption makes CAN traffic vulnerable to sniffing, spoofing, modification, and replay attacks [ Young et al.(2019)Young, Zambreno, Olufowobi, and Bloom ] .
Broadcast domain: The CAN bus functions as a broadcast domain, where all ECUs receive the transmitted frames. Each ECU then checks the data and determines whether to process or disregard it [ Ahmad et al.(2024)Ahmad, Han, Jolfaei, Jabbar, Ibrar, Erbad, Song, and Alkhrijah ] . If an ECU is compromised, it can intercept and monitor all messages transmitted across the CAN network, enabling an eavesdropping attack [ Dupont et al.(2019a)Dupont, den Hartog, Etalle, and Lekidis ] .
ID-based priority: The CAN network prioritises messages based on their IDs, with lower IDs having higher priority [ Rajapaksha et al.(2023a)Rajapaksha, Kalutarage, Al-Kadri, Petrovski, Madzudzo, and Cheah ] . Attackers can exploit this by repeatedly sending frames with low IDs, resulting in a Denial-of-Service (DoS) attack [ Lokman et al.(2019)Lokman, Othman, and Abu-Bakar ] .
Unsegmented Network: All ECUs are connected to a single shared network without segmentation [ Young et al.(2019)Young, Zambreno, Olufowobi, and Bloom ] , which is a key reason why CAN was adopted in automotive systems, as it eliminates the need for point-to-point connections. However, this shared network allows components such as infotainment systems to communicate with safety-critical vehicle systems. Although some manufacturers use separate networks for safety-critical systems, there is still cross-communication between critical and non-critical systems [ Young et al.(2019)Young, Zambreno, Olufowobi, and Bloom ] .
External Interfaces: The attack surface of the CAN bus network is expanded by external interfaces such as the OBD-II port, used for vehicle maintenance and diagnostics; the Telematics Unit, which provides connectivity to the vehicle via Wi-Fi, Bluetooth, GPS, and mobile data interfaces; and the Infotainment Unit, which delivers information and entertainment to the driver through a head display unit, including features like CD/DVD players and USB ports. These interfaces create additional entry points for potential cyberattacks [ Wu et al.(2019)Wu, Li, Xie, An, Bai, Zhou, and Li , Rajapaksha et al.(2023a)Rajapaksha, Kalutarage, Al-Kadri, Petrovski, Madzudzo, and Cheah ] .
Attackers can gain access to the CAN bus or specific ECUs either physically or remotely [ Aliwa et al.(2021)Aliwa, Rana, Perera, and Burnap , Limbasiya et al.(2022)Limbasiya, Teng, Chattopadhyay, and Zhou , Checkoway et al.(2011)Checkoway, McCoy, Kantor, Anderson, Shacham, Savage, Koscher, Czeskis, Roesner, and Kohno , Carsten et al.(2015)Carsten, Andel, Yampolskiy, and McDonald ] . These entry points serve as gateways for initiating a range of attacks, exploiting the inherent vulnerabilities described in Section 2.4 in in-vehicle networks. This section discusses the entry points attackers can exploit to access the in-vehicle network, either physically or remotely.
Physical access allows an attacker—such as a mechanic, valet, car renter, or anyone with even brief access to the vehicle—to directly interact with its internal systems. This access, even for a short time, can provide opportunities to exploit vulnerabilities through various physical entry points, including: OBD-II Port: The OBD-II port, commonly located under the dashboard in most vehicles, provides the simplest and most direct access to a vehicle’s primary CAN buses. This port offers sufficient access to potentially compromise the full range of automotive systems [ Checkoway et al.(2011)Checkoway, McCoy, Kantor, Anderson, Shacham, Savage, Koscher, Czeskis, Roesner, and Kohno ] . Designed primarily for vehicle maintenance and engine diagnostics, the OBD-II port allows mechanics to connect scanning tools and capture data packets generated by malfunctioning subsystems. Despite its intended purpose, the port’s accessibility makes it a significant security vulnerability. Attackers can easily connect to the OBD-II port to extract information or install malware onto the vehicle’s systems, disconnecting afterward to leave no physical evidence [ Koscher et al.(2010)Koscher, Czeskis, Roesner, Patel, Kohno, Checkoway, McCoy, Kantor, Anderson, Shacham, et al. ] .
Alternatively, attackers may deploy a remote device to the port, or enabling continuous data collection or exploitation over time. Since the OBD-II port is required for maintenance and diagnostics, it will always pose a security risk [ Carsten et al.(2015)Carsten, Andel, Yampolskiy, and McDonald ] . Aftermarket Components: Peripheral components such as USB ports, CD players, and third-party add-ons also pose security risks [ Liu et al.(2017)Liu, Zhang, Sun, and Shi , Carsten et al.(2015)Carsten, Andel, Yampolskiy, and McDonald ] . For example, malicious devices, including FM radios, USB connectors, or CD players purchased from unverified or aftermarket sources, can introduce malware into the vehicle’s system. While these components may be more affordable, they can compromise the vehicle’s security [ Koscher et al.(2010)Koscher, Czeskis, Roesner, Patel, Kohno, Checkoway, McCoy, Kantor, Anderson, Shacham, et al. ] .
An external attacker can exploit wireless interfaces commonly implemented in modern vehicles, such as Bluetooth, Wi-Fi, cellular networks, and GPS, without requiring physical proximity to the vehicle. Once these interfaces are accessed, the attacker can inject malicious data or commands into the CAN bus [ Aliwa et al.(2021)Aliwa, Rana, Perera, and Burnap ] . Koscher et al. [ Chockalingam et al.(2016)Chockalingam, Larson, Lin, and Nofzinger ] highlight the feasibility of executing various types of wireless attack injections on in-vehicle network systems. For example, vulnerabilities in telematics systems or vehicle-to-cloud communications can enable the remote injection of messages, disrupting the network. Specific methods include using malicious Windows Media Audio (WMA) files or sending malicious packets to the telematics unit via 3G Internet Relay Chat (IRC) [ Chockalingam et al.(2016)Chockalingam, Larson, Lin, and Nofzinger ] . Moreover, Woo et al. [ Woo et al.(2014)Woo, Jo, and Lee ] conducted a wireless attack, successfully taking control of a target vehicle by utilising malware installed on a smartphone. These examples highlight the significant security risks posed by wireless interfaces in connected vehicles.
Since an attacker can gain access to the in-vehicle network, either physically or remotely, through one of the entry points outlined in Section 2.5 , the following are common attack scenarios: Attack Definition: The goal of a DoS attack is to overwhelm the CAN bus bandwidth by transmitting large volumes of messages, leading to system malfunctions and service disruptions [ Rajapaksha et al.(2023a)Rajapaksha, Kalutarage, Al-Kadri, Petrovski, Madzudzo, and Cheah ] . Koscher et al. [ Koscher et al.(2010)Koscher, Czeskis, Roesner, Patel, Kohno, Checkoway, McCoy, Kantor, Anderson, Shacham, et al. ] demonstrated that DoS attacks can disable individual CAN bus components.
Attack Method: Since message priority is determined by the arbitration field, an attacker can exploit the CAN frame priority arbitration scheme vulnerability by sending numerous messages with low CAN IDs (high priority), such as 0x0000. This flooding of high-priority frames occupies the bus, preventing other ECUs from accessing it [ Hoang and Kim(2022) ] . Figure 2(a) illustrates how a high-priority CAN ID 0x0000 delays a lower-priority CAN ID 0x0B4.
Attack Scenario: We assume that the attacker has gained access to the in-vehicle network, either physically or remotely, through one of the entry points outlined in Section 2.5 . Leveraging this access, the attacker floods the CAN bus with high-priority messages, such as those with CAN IDs like 0x0000, without requiring prior knowledge of the CAN bus traffic. The arbitration mechanism prioritises these malicious messages, taking control of the bus and blocking critical communications, such as those from the engine control unit or braking system. For instance, while the vehicle is in motion, an attacker carrying out this attack could disable cruise control or activate emergency braking, preventing critical messages from reaching the appropriate ECU in time and creating potentially hazardous driving conditions. Within seconds, the network’s capacity becomes overwhelmed, causing delays that severely compromise vehicle safety.
4. Practical Deployment, Analysis & Case Studies Attack Impact: A successful DoS attack not only delays normal messages by occupying the bus [ Lee et al.(2017)Lee, Jeong, and Kim ] , but also prevents other ECUs from transmitting frames to the in-vehicle network, significantly impacting network availability [ Cho and Shin(2016) ] . Such attacks can lead to a complete breakdown of ECU communication and severe disruption of the entire CAN bus network system [ Hossain et al.(2020a)Hossain, Inoue, Ochiai, Fall, and Kadobayashi , Liu et al.(2017)Liu, Zhang, Sun, and Shi ] , posing significant threats to the safety of drivers, passengers, and other road users [ Fowler et al.(2018)Fowler, Bryans, Shaikh, and Wooderson ] .
Attack Definition: In a spoofing attack, an unauthorised attacker targets specific existing CAN IDs and injects fabricated messages to control particular functions. Since CAN IDs appear legitimate, distinguishing between real and spoofed messages becomes challenging, leading to system malfunctions [ Hoang and Kim(2022) ] . Attack Method: The attacker may sniff the CAN bus traffic or possess prior knowledge about the ECUs’ CAN messages. They can then use this information to inject spoofed messages into the CAN bus. Figure 2(b) illustrates a spoofing attack where an attacker, using the spoofed CAN ID 0x0B4, targets the legitimate CAN ID 0x0B4. This enables the attacker to disrupt vehicle functions by generating manipulated messages that appear legitimate.
Attack Scenario: We assume that the attacker has gained access to the in-vehicle network, either physically or remotely, through one of the entry points outlined in Section 2.5 . In this attack, we assume that the attacker has some knowledge of CAN bus traffic by implementing an impersonation attack. One method to achieve this is by connecting a malicious device to eavesdrop on all broadcast traffic, capturing data transmitted across the network. During this reconnaissance phase, the attacker analyses the traffic to identify patterns in ECU behaviour, such as specific CAN IDs, payload structures, and message transmission intervals. Armed with this knowledge, the attacker selects a target ECU, such as the speedometer, with plans to disable it from the bus later. Next, the attacker gains remote access to the internal network and crafts spoofed messages by replicating the target ECU’s CAN ID and injecting false speed readings into the bus. This activity exploits the CAN bus protocol’s error-handling mechanisms, as described in [ Iehira et al.(2018)Iehira, Inoue, and Ishida ] . By transmitting dominant bits whenever the legitimate ECU sends recessive bits, the attacker creates intentional bit conflicts. These conflicts generate repeated error frames, eventually causing the legitimate ECU to exceed its error tolerance threshold and enter a "bus-off" state. In the bus-off state, the legitimate ECU is effectively disconnected from the network, unable to send or receive critical messages. The attacker then injects maliciously crafted messages using the same CAN ID as the target ECU. For instance, they could dangerously slow the vehicle on a highway or increase its speed in restricted areas, thereby creating hazardous conditions.
Attack Impact: Spoofing attacks can cause system malfunctions and disrupt vehicle operations [ Hoang and Kim(2022) ] . They pose significant threats to personal safety, particularly when targeting critical ECUs responsible for essential functions such as braking or steering [ Iehira et al.(2018)Iehira, Inoue, and Ishida ] . Attack Definition: The goal of a frame fuzzification attack is to inject random messages into the CAN bus network, making them appear as legitimate traffic. Attackers may exploit prior knowledge of CAN IDs and payload values obtained through CAN bus sniffing, or they may perform the attack without any prior knowledge of CAN frames, treating it as a black-box attack [ Hossain et al.(2020b)Hossain, Inoue, Ochiai, Fall, and Kadobayashi ] . In this type of attack, the attacker might alter the CAN ID, the CAN payload, or both simultaneously [ Aliwa et al.(2021)Aliwa, Rana, Perera, and Burnap ] . Since the range of valid CAN packets is relatively small, even simple fuzzing of packets can cause significant damage [ Koscher et al.(2010)Koscher, Czeskis, Roesner, Patel, Kohno, Checkoway, McCoy, Kantor, Anderson, Shacham, et al. ] .
Attack Method: The attacker sends arbitrary messages into the CAN bus network, making them appear as legitimate traffic. Figure 2(c) illustrates a frame fuzzification attack, where the attacker generates and injects random CAN IDs (e.g. 0x123, 0x357, and 0x222), which are illegitimate. As a result, all ECUs receive a high volume of functional messages, leading to unintended vehicle behaviours [ Lee et al.(2017)Lee, Jeong, and Kim ] . For example, Chockalingam et al. [ Chockalingam et al.(2016)Chockalingam, Larson, Lin, and Nofzinger ] introduced Gaussian noise to create a frame fuzzification attack on CAN data. A frame fuzzification attack can disrupt the entire CAN bus network, leading to severe malfunctions such as the steering wheel shaking uncontrollably, signal lights flickering erratically, or automatic and unintended changes in the gear shift [ Hossain et al.(2020a)Hossain, Inoue, Ochiai, Fall, and Kadobayashi ] .
Attack Scenario: We assume that the attacker has gained access to the in-vehicle network, either physically or remotely, through one of the entry points outlined in Section 2.5 . Without prior knowledge of CAN frames, the attacker is able to inject random malicious CAN frames. Using techniques such as fuzzing, the attacker transmits random or malformed messages into the CAN bus to provoke unintended system behaviours or identify exploitable vulnerabilities that could be leveraged in future attacks. Additionally, through reverse engineering, the attacker monitors legitimate traffic to deduce the structure and purpose of CAN messages, enabling the creation of malicious packets to execute specific commands targeting particular ECUs.
Attack Impact: Frame fuzzification attacks can compromise ECUs, triggering unexpected vehicle behaviours such as steering wheel shaking, erratic signal lights, and unintended gear shifts [ Lee et al.(2017)Lee, Jeong, and Kim ] . These behaviours can confuse the driver, potentially resulting in poor decisions or accidents. Such attacks not only disrupt normal vehicle functions but also threaten operational integrity, compromise data privacy, and endanger personal safety, posing significant risks to passengers and other road users.
Attack Definition: In replay attacks, attackers store a valid message at a certain time and replay it at a different time without any changes [ Jo and Choi(2021) ] . For example, an attacker can store a speedometer reading and later rebroadcast it to the network [ Al-Jarrah et al.(2019)Al-Jarrah, Maple, Dianati, Oxtoby, and Mouzakitis ] . In this type of attack, the attacker might alter the ID, payload sequences, or both [ Rajapaksha et al.(2023a)Rajapaksha, Kalutarage, Al-Kadri, Petrovski, Madzudzo, and Cheah ] .
Attack Method: Attackers first observe and capture valid CAN messages while monitoring the vehicle’s CAN bus. Later, they replay these captured messages without modification to manipulate the system [ Jo and Choi(2021) ] . Consequently, the normal CAN packet in the traffic is replaced with a previously captured packet, causing the historical effects [ Lokman et al.(2019)Lokman, Othman, and Abu-Bakar ] . Figure 2(d) illustrates a replay attack, where the attacker sniffs the legitimate CAN messages (e.g., 0X0B4 and 0X0C5), and after some time, he reinjects the same messages into the network.
Attack Scenario: We assume that the attacker has gained access to the in-vehicle network, either physically or remotely, through one of the entry points outlined in Section 2.5 . In this attack, we assume that the attacker has no prior knowledge of CAN bus traffic but is able to capture legitimate CAN traffic. One method to achieve this is by connecting a malicious device to sniff the CAN bus traffic, capturing data transmitted across the network. After some time, the attacker gains access to the network and replays the sniffed messages back into the traffic.
Attack Impact: Even though this attack is easy to carry out, as it requires no prior knowledge of traffic operation, it can pose serious safety threats to both vehicles and passengers [ Rajapaksha et al.(2023a)Rajapaksha, Kalutarage, Al-Kadri, Petrovski, Madzudzo, and Cheah ] . Koscher et al. [ Koscher et al.(2010)Koscher, Czeskis, Roesner, Patel, Kohno, Checkoway, McCoy, Kantor, Anderson, Shacham, et al. ] demonstrated replay attacks to manipulate the radio and various body control module functions in the CAN bus. Although the replayed packet is a valid subsequence, the replaced packet disrupts the original packet sequence. Consequently, this can lead to severe issues such as continuous CAN packet transmission requests, deadline violations, and inversion of the CAN arbitration priority scheme. Furthermore, the altered packet sequence prevents the vehicle from functioning properly, as the packets are no longer transmitted sequentially, violating protocol requirements [ Lokman et al.(2019)Lokman, Othman, and Abu-Bakar ] .
In this section, we review existing surveys and reviews on IDS approaches in in-vehicle networks, highlighting their contributions and how our survey differs. There are several surveys in this field. Most of them review the security of in-vehicle networks in general and include IDS as one of the approaches, alongside ML and DL [ Karopoulos et al.(2022)Karopoulos, Kambourakis, Chatzoglou, Hernández-Ramos, and Kouliaridis , Aliwa et al.(2021)Aliwa, Rana, Perera, and Burnap , Dupont et al.(2019a)Dupont, den Hartog, Etalle, and Lekidis , Tomlinson et al.(2018)Tomlinson, Bryans, and Shaikh , Al-Jarrah et al.(2019)Al-Jarrah, Maple, Dianati, Oxtoby, and Mouzakitis , Wu et al.(2019)Wu, Li, Xie, An, Bai, Zhou, and Li , Rajbahadur et al.(2018)Rajbahadur, Malton, Walenstein, and Hassan , Jo and Choi(2021) , Lokman et al.(2019)Lokman, Othman, and Abu-Bakar , Loukas et al.(2019)Loukas, Karapistoli, Panaousis, Sarigiannidis, Bezemskij, and Vuong , Young et al.(2019)Young, Zambreno, Olufowobi, and Bloom , Quadar et al.(2024)Quadar, Chehri, Debaque, Ahmed, and Jeon , Lampe and Meng(2023a) , Limbasiya et al.(2022)Limbasiya, Teng, Chattopadhyay, and Zhou ] . Others focus specifically on reviewing ML and DL techniques [ Rajapaksha et al.(2023a)Rajapaksha, Kalutarage, Al-Kadri, Petrovski, Madzudzo, and Cheah , Nagarajan et al.(2023)Nagarajan, Mansourian, Shahid, Jaekel, Saini, Zhang, and Kneppers , Lampe and Meng(2023b) , Almehdhar et al.(2024)Almehdhar, Albaseer, Khan, Abdallah, Menouar, Al-Kuwari, and Al-Fuqaha , Taslimasa et al.(2023a)Taslimasa, Dadkhah, Neto, Xiong, Ray, and Ghorbani ] .
Rajapaksha et al. [ Rajapaksha et al.(2023a)Rajapaksha, Kalutarage, Al-Kadri, Petrovski, Madzudzo, and Cheah ] reviewed and classified state-of-the-art AI-based in-vehicle IDSs, collecting papers using the PRISMA (Preferred Reporting Items for Systematic Reviews and Meta-Analyses) protocol. They proposed an AI-based IDS taxonomy, reviewed benchmark datasets, and outlined the steps for developing AI-based attack detection in the CAN bus. Additionally, they identified and discussed the limitations of current approaches for securing in-vehicle networks and suggested possible future research directions.
Karopoulos et al. [ Karopoulos et al.(2022)Karopoulos, Kambourakis, Chatzoglou, Hernández-Ramos, and Kouliaridis ] compiled a meta-taxonomy that consolidates the key classification features of in-vehicle IDSs proposed in existing surveys, offering a unified perspective on their development. They reviewed available datasets for training and testing in-vehicle IDSs, along with simulators used for dataset generation or performance evaluation. Additionally, they highlighted the main challenges and future directions in this rapidly advancing field. Aliwa et al. [ Aliwa et al.(2021)Aliwa, Rana, Perera, and Burnap ] reviewed cryptographic and IDS solutions to protect vehicular data and discussed their challenges. Dupont et al. [ Dupont et al.(2019a)Dupont, den Hartog, Etalle, and Lekidis ] categorised in-vehicle IDSs based on the required message count for attack detection, the data utilised, and the design of the detection model. Tomlinson et al. [ Tomlinson et al.(2018)Tomlinson, Bryans, and Shaikh ] reviewed methods for CAN IDSs and categorised them into signature detection and anomaly detection.
The anomaly detection category was further divided into statistical, knowledge-based, and ML approaches, highlighting their implications. Al-Jarrah et al. [ Al-Jarrah et al.(2019)Al-Jarrah, Maple, Dianati, Oxtoby, and Mouzakitis ] provide an overview of intra-vehicle IDSs, categorizing them into flow-based, payload-based, and hybrid types. They discuss and identify the challenges and current gaps in the landscape of intra-vehicle IDS research. Out of the 42 reviewed papers, only 23 are ML-based IDSs. Wu et al. [ Wu et al.(2019)Wu, Li, Xie, An, Bai, Zhou, and Li ] categorised in-vehicle IDSs into four types: fingerprint-based, parameter monitoring-based, information theory-based, and ML-based. Moreover, they discussed the drawbacks and emerging research directions. However, out of the 20 reviewed papers, only 9 focused on ML-based IDSs.
Rajbahadur et al. [ Rajbahadur et al.(2018)Rajbahadur, Malton, Walenstein, and Hassan ] conducted a survey on anomaly detection for securing CAVs. They introduced a taxonomy with three main categories and nine subcategories. In addition, they classified the surveyed papers into 38 dimensions. While the study provided valuable insights, it lacks individual paper summaries and practical implementation strategies. Jo et al. [ Jo and Choi(2021) ] classified in-vehicle countermeasures into four categories: preventative protection, IDSs, authentication, and post-protection. They further divided IDS techniques into CAN packet-based and ECU hardware characteristic-based approaches. Although this survey comprehensively examines CAN attack surfaces and corresponding protection mechanisms, it does not focus on ML-based IDSs. Lokman et al. [ Lokman et al.(2019)Lokman, Othman, and Abu-Bakar ] introduced a taxonomy for classifying research papers according to four aspects: deployment strategies, attacking techniques, technical challenges, and detection approaches. They also categorised anomaly-based IDSs into frequency-based, ML-based, statistical-based, and hybrid-based. Despite its contribution, only a limited number (five) of works were discussed under the ML-based approach. Loukas et al. [ Loukas et al.(2019)Loukas, Karapistoli, Panaousis, Sarigiannidis, Bezemskij, and Vuong ] provided a comprehensive taxonomy focusing on IDS characteristics and architectures designed for different types of vehicles, such as aircraft, land vehicles, and watercraft. They classified audit techniques into statistical, ML, and rule-based IDSs, and only 13 ML-based IDSs for the CAN bus are discussed. Young et al. [ Young et al.(2019)Young, Zambreno, Olufowobi, and Bloom ] categorised CAN bus IDSs into signature-based and anomaly-based methods. However, the reviewed ML-based IDSs are limited. Lampe and Meng [ Lampe and Meng(2023b) ] provided a comprehensive overview of DL-based IDSs in automotive networks, categorizing them based on their topologies and techniques, such as DNN-based IDSs, CNN-based IDSs, LSTM-based IDSs, attention- and transformer-based IDSs, and GAN-based IDSs. They also discuss the advantages and disadvantages of each approach.
Nagarajan et al. [ Nagarajan et al.(2023)Nagarajan, Mansourian, Shahid, Jaekel, Saini, Zhang, and Kneppers ] presented a comprehensive review of ML-based IDSs for in-vehicle and inter-vehicle communications. They reviewed available datasets, summarised current testbeds, and discussed open research issues. Taslimasa et al. [ Taslimasa et al.(2023a)Taslimasa, Dadkhah, Neto, Xiong, Ray, and Ghorbani ] provided a comprehensive literature review of proposed IDSs for Internet of Vehicles (IoV) networks (inter-vehicle and intra-vehicle) that utilise ML and DL algorithms. Additionally, they discussed IDS criteria, highlighting key factors to consider when assessing IoV network security. Quadar et al. [ Quadar et al.(2024)Quadar, Chehri, Debaque, Ahmed, and Jeon ] reviewed and classified in-vehicle IDSs based on detection methods, including fingerprint-based methods, time- and frequency-based methods, and ML-based methods. However, the reviewed ML-based IDSs are limited. Lampe and Meng [ Lampe and Meng(2023a) ] reviewed automotive intrusion detection methodologies, categorising IDSs into non-learning, traditional ML, and DL. They further classified IDSs by six dimensions: analysis, deployment, detection, evaluation, learning, and monitoring modes. Open challenges and future research opportunities were also discussed.
Limbasiya et al. [ Limbasiya et al.(2022)Limbasiya, Teng, Chattopadhyay, and Zhou ] present a systematic survey that extensively analyses different Attack Detection and Prevention System (ADPS) categories for CAVs. They discuss state-of-the-art research in each category, highlighting the latest findings in this domain. Additionally, they identify crucial open security challenges that must be addressed for the secure deployment of CAVs. Almehdhar et al. [ Almehdhar et al.(2024)Almehdhar, Albaseer, Khan, Abdallah, Menouar, Al-Kuwari, and Al-Fuqaha ] categorised IDS techniques into conventional ML, DL, and hybrid models. They also explored emerging technologies such as FL and Transfer Learning. Key limitations in current methodologies and potential directions for future research were identified.
Even though existing in-vehicle surveys and reviews have made significant contributions to the field, they have certain limitations. As shown in Table 1 , few surveys follow a structured search methodology to ensure full coverage and a comprehensive review. In addition, none of these surveys review FL-based IDS, except for the work in [ Almehdhar et al.(2024)Almehdhar, Albaseer, Khan, Abdallah, Menouar, Al-Kuwari, and Al-Fuqaha ] , which briefly presents some studies in this area. Although Chellapandi et al. [ Chellapandi et al.(2023)Chellapandi, Yuan, Iak, and Wang ] provide a survey on FL for CAVs, they do not include any in-vehicle IDSs and instead focus on FL applications such as steering wheel angle prediction, vehicle trajectory prediction, object detection, motion control, and driver monitoring. Lastly, although some surveys have reviewed the performance metrics used in the reviewed papers, we provide a comprehensive review of all evaluation metrics, including performance, time, and memory requirements, emphasising the need to include these metrics to develop deployable solutions. To the best of our knowledge, this survey is the first to provide a comprehensive review of ML, DL, and FL-based IDS for in-vehicle networks. Table 1 compares this survey with other existing surveys on in-vehicle IDSs, highlighting the key contributions of this work.
To select studies for inclusion, we followed Kitchenham’s [ Kitchenham and Brereton(2013) ] method, a well-established and effective guide for identifying relevant literature. Although originally designed for the software engineering domain, this method has been widely applied in other fields, including cybersecurity [ Alhirabi et al.(2021)Alhirabi, Rana, and Perera ] . Our process began with an automatic search using Google Scholar to minimise bias towards any specific publisher [ Wohlin(2014) ] and to identify key publishers and conferences in the field. Based on this search, we compile a list of publishers and conferences for a subsequent manual search. To ensure comprehensive coverage, we employ a snowball approach to locate all related papers. After gathering a substantial number of publications, we applied filtering processes to select the most relevant ones.
Finally, we analysed the collected articles (from any time up to and including January 2025) to develop the literature review presented in this paper. Figure 3 shows the search strategy adopted. To begin, we formulated several search queries on Google Scholar using keywords that combine terms representing our area of research and those frequently found in paper keywords. These terms are listed in Table 2 . Logical operators "AND" and "OR" were utilised to ensure comprehensive results. These queries generated a range of papers, some of which were only loosely relevant. This step also provided insights into the digital libraries and journals that prioritise CAN bus security.
Subsequently, we conducted a hybrid search using more complex queries in specific journals and libraries, including IEEE Xplore, Scopus, ACM, MDPI, Springer, and ScienceDirect. Three search strategies were employed during this process: automatic, manual, and snowballing. Automatic search We carried out this stage using the advanced search function in Google Scholar, employing key terms such as "CAN bus", "controller area network", "in-vehicle", "intrusion detection system", "IDS", "anomaly detection", "unknown attacks", and "federated". These root words were chosen because Google Scholar automatically searches for variations of the same word; for instance, searching for "federated" returns results like "federated", "federated learning", "federated-based", and "federated environment". Additionally, the search was not restricted to a specific time period. Initially, using the filter "anywhere in the article," we retrieved an unwieldy number of results (53,890) (see Table 2 ). To refine this, we applied the filter "in the title of the article," reducing the results to 95 papers. Only peer-reviewed papers were included in our analysis.
5. Performance Evaluation & Extended Technical Observations Manual search In this stage, we applied more complex queries, including specific journals and libraries, such as IEEE Xplore, Scopus, ACM, MDPI, Springer, and ScienceDirect. Table 3 lists examples of queries used in the manual search. Snowballing The snowballing technique was applied to the papers identified through automatic and manual searches. This approach included both forward and backward snowballing. Forward snowballing (or citation analysis) locates papers that are cited in the papers found in the initial stages. Backward snowballing (or reference analysis) looks at the reference lists of the papers found in the initial search process. References included in the selected papers were chosen based on a review of the title, abstract, and the paper’s structure. We found that backward snowballing using critical papers was an effective means of identifying relevant papers. The set of articles selected was updated to include any additional relevant studies found by snowballing.
The selection strategy involved defining inclusion and exclusion criteria, as well as applying filtering during the search process. The steps in the selection process included applying the inclusion and exclusion criteria, followed by an additional filtering stage involving a quality assessment to ensure the selection of high-quality studies. Each of these steps is discussed below.
Filtering Irrelevant Papers : The papers collected through manual, automatic, and snowballing approaches included several that did not apply directly to our study and had to be eliminated. Elimination was conducted in two steps. In the first, papers were excluded based on the title, keywords, abstract, and sometimes the conclusion in case of any doubts. Based on this step, a decision was made regarding whether to include each paper in the next step. Eliminating was undertaken after each search (automatic, manual, and snowballing) to reduce the number of papers. When a paper passed the initial elimination step, it was subjected to the inclusion and exclusion criteria.
Inclusion and Exclusion Criteria In this process, we defined our exclusion and inclusion criteria. A paper was considered for exclusion if it met one or more criteria. The exclusion criteria for each paper were as follows: (i) not written in English; (ii) was a review or survey paper; (iii) lacked a full version (e.g., only a poster or abstract); (iv) did not employ an ML or DL approach; (v) required reverse engineering; (vi) used other data alongside CAN bus data; and (vii) employed other approaches such as statistical, rule-based, or physical fingerprinting methods. Papers that were not excluded were then evaluated according to an inclusion list of other criteria. If no inclusion criteria were met, the paper was rejected. The inclusion criteria were as follows: (i) focused on the CAN bus protocol rather than other in-vehicle protocols; and (ii) focused on attack detection as the primary goal. Non-peer-reviewed papers were included only if they were strictly relevant to the topic and had a high citation rate, or if the author was well-known in the field.
As shown in Figure 3 , reading the full paper is the final step in the search and selection process, filtering out the collected papers from the previous steps. The papers from the automatic search were reduced from 10 to 9 after filtering by reading the full text. In the manual search within journal lists and publishers, the initial 1,831 papers were filtered down to 59. For snowballing, 57 papers were initially selected and reduced through filters to 17. Thus, the total number of collected papers comprises 9 from the automatic search, 59 from the manual search, and 17 from snowballing, resulting in a total of 85 papers for analysis. Of these, 38 focused on known attack detection, 27 on unknown attack detection, 11 on IDSs capable of detecting both known and unknown attacks, and 9 on FL-based IDSs. Figure 4 illustrates the number of collected papers in each category, highlighting that known attack detection is the most researched area, while significantly less work has been conducted on IDSs capable of detecting both known and unknown attacks, as well as on FL-based IDSs.
In this section, we begin by introducing IDSs for in-vehicle networks and highlighting the differences between in-vehicle IDSs and those used for other applications. We then provide an overview of in-vehicle IDS approaches. Additionally, we categorise the collected papers into three categories: known attack detection, unknown attack detection, and work capable of detecting both known and unknown attacks for analysis. Figure 5 illustrates the categories and subcategories of the reviewed literature.
Lastly, we review all the evaluation metrics used in the reviewed papers. According to NIST SP 800-94, intrusion detection is “the process of monitoring the events occurring in a computer system or network and analysing them for signs of possible incidents” [ Hernandez-Ramos et al.(2023)Hernandez-Ramos, Karopoulos, Chatzoglou, Kouliaridis, Marmol, Gonzalez-Vidal, and Kambourakis ] . Therefore, an IDS is typically considered a software or hardware system designed to automatically detect suspicious activity in a network [ Young et al.(2019)Young, Zambreno, Olufowobi, and Bloom ] . In vehicle networks, IDSs are crucial for identifying malicious attacks [ Aliwa et al.(2021)Aliwa, Rana, Perera, and Burnap ] . They can be implemented as either host-based or network-based systems [ Young et al.(2019)Young, Zambreno, Olufowobi, and Bloom ] . Host-based IDSs are installed on each vehicle’s ECU, allowing comprehensive monitoring of internal ECU operations. In contrast, network-based IDSs are deployed within the CAN network or central gateways to oversee all network traffic. However, Host-based IDSs are not a viable solution for vehicles, as they require a change in ECUs that are not cost effective [ Aliwa et al.(2021)Aliwa, Rana, Perera, and Burnap ] . In contrast, deploying a network-based IDS as an additional node on the CAN bus is a more feasible and practical solution, as it avoids the need for any CAN bus modifications [ Rajapaksha et al.(2023a)Rajapaksha, Kalutarage, Al-Kadri, Petrovski, Madzudzo, and Cheah ] .
Unlike IDSs in other applications, in-vehicle IDSs are constrained by computing power, memory size, and communication capabilities. This is because modern ECUs in vehicles are primarily powered by 32-bit embedded processors, with limited computational performance and memory resources [ Wu et al.(2019)Wu, Li, Xie, An, Bai, Zhou, and Li ] . Research on developing in-vehicle IDSs has grown significantly in recent years, driven by the critical need to enhance the security of in-vehicle networks and detect cyberattacks. Researchers have explored various approaches to building these systems. IDSs can be classified as either signature-based, for detecting known attacks, or anomaly-based, for identifying new, unknown attacks [ Hoppe et al.(2009)Hoppe, Kiltz, and Dittmann ] . Anomaly-based IDSs are further categorised into statistical, ML, rule-based, and physical fingerprinting methods [ Rajapaksha et al.(2023a)Rajapaksha, Kalutarage, Al-Kadri, Petrovski, Madzudzo, and Cheah ] . However, this work specifically focuses on the development of in-vehicle IDSs using ML and DL approaches. This focus arises from the widespread use of ML and DL-based IDSs to process large volumes of CAN traffic data. These approaches efficiently extract and pre-process raw CAN data, which is critical as vehicle manufacturers often do not provide detailed specifications for decoding these raw data [ Rajapaksha et al.(2023a)Rajapaksha, Kalutarage, Al-Kadri, Petrovski, Madzudzo, and Cheah ] . This section is divided into three categories: known attack detection, unknown attack detection, and work capable of detecting both known and unknown attacks.
As mentioned in Section 4.1 , there are 38 papers on IDSs focusing on known attack detection. In this section, we analyse these papers and discuss the existing methodologies used to detect or classify known threats in in-vehicle networks. Detection of known attacks typically relies on supervised learning, where models are trained on labelled data. The section is organised into three subsections based on the features used to build the model: ID-based detection, payload-based detection, and CAN frame-based detection. Each subsection examines different approaches for identifying malicious activities, emphasizing their strengths and limitations. Figure 6 illustrates previous work on detecting known attacks, showing that most studies utilised a DL approach and used CAN frames as input features.
Attacks such as injecting or deleting frames alter certain properties of message ID sequences compared to normal messages. This section presents research where the authors utilised these properties and used CAN IDs solely as an input feature to develop IDSs for detecting known attacks. Song et al. [ Song et al.(2020)Song, Woo, and Kim ] utilised the sequential behaviour of CAN data to identify message injection attacks. During these attacks, frequent frame injections resulted in distinct ID pattern changes, which were leveraged for detection. The authors relied solely on the bit-wise CAN ID sequence, which was processed directly as input, eliminating the need for additional feature engineering. They introduced a deep convolutional neural network (DCNN) model that was redesigned by minimizing unnecessary complexities within the Inception-ResNet architecture to achieve an optimised input size of (29 × 29 × 1) and a binary classification output.
Refat et al. [ Refat et al.(2022)Refat, Elkhail, Hafeez, and Malik ] used graph-based techniques to extract features from the CAN IDs in in-vehicle networks. The authors converted a window of CAN IDs into a graph and extracted seven graph properties, including the number of nodes, number of edges, radius, diameter, density, reciprocity, average clustering coefficient, and assortative coefficient, to use as input features. These extracted features were then used to train two traditional ML algorithms: support vector machine (SVM) and k-nearest neighbours (KNN) models. The experimental results demonstrated that using graph-based features outperformed the traditional CAN bus features.
Nandam et al. [ Nandam et al.(2022)Nandam, Vamshi, and Sucharitha ] employed an Long Short-Term Memory (LSTM) model to detect DoS attacks on the CAN bus. The model utilises the CAN ID of incoming messages to identify potential DoS attacks. A sequence of previous messages is stored and combined with the current message to form the input, enabling the model to predict and detect DoS attacks effectively.
Rangsikunpum et al. [ Rangsikunpum et al.(2024a)Rangsikunpum, Amiri, and Ost ] introduced a Binarised Neural Network (BNN)-based IDS to identify attacks on the CAN bus. The primary objective of the proposed IDS is to deploy a ML model on a low-cost Field Programmable Gate Array (FPGA) device, optimising for low power consumption, minimal execution time, and high accuracy. By leveraging a 1-bit BNN model, the implementation is resource-efficient, making it suitable for deployment on cost-effective FPGA devices with reduced power requirements. Moreover, the IDS employs a two-stage architecture: the first stage identifies the presence of an attack, and the second stage, triggered only upon detecting an attack, performs detailed attack classification.
Wu and Tao [ Wu and Tao(2024) ] proposed a model based on ensemble learning using a Stacking integration approach. The method incorporates a meta-classifier composed of DTs, Extra Trees (ET), and extreme gradient boosting (XGBoost). Final classification predictions are made by linearly combining input features and weights through a SoftMax meta-learner. Ensemble learning in this approach utilises the prediction results as new features, along with the true labels, to train the meta-learner.
Some attacks, such as spoofing, use legitimate CAN IDs but modify the CAN payload values, depending on the characteristics of the particular attack. These changes alter the pattern of payload sequences. This section discusses IDSs that utilise this property and use the CAN payload as an input feature to detect known attacks. Kang and Kang [ Kang and Kang(2016) ] developed a deep neural network (DNN)-based IDS to defend against malicious attacks. The authors utilised the 8-byte CAN payload to extract features, employing mode and value information to achieve dimensionality reduction. The initial weights for the DNN model were obtained from a separate Deep Belief Network. They then applied a template-matching method to compare the training samples with new CAN packets for detecting malicious messages. Although the proposed model demonstrated improved detection performance, it relied on mode and value information from CAN data, which presents significant challenges, especially without access to the DBC file.
Similarly, Martinelli et al. [ Martinelli et al.(2017)Martinelli, Mercaldo, Nardone, and Santone ] utilised the eight CAN payload features to assess whether these features can effectively discriminate between attacks and normal messages. To address this question, they employed four fuzzy classification algorithms to identify four types of attacks targeting the CAN bus, including DoS, fuzzy, RPM, and gear spoofing. These algorithms include two types of fuzzy-rough KNN, the discernibility classifier, and a fuzzy unordered rule induction algorithm. The classification analysis was performed using the Weka3 tool.
Experimental results indicated that the feature vector is a potential candidate for accurately classifying between injected and normal messages. Fenzl et al. [ Fenzl et al.(2021)Fenzl, Rieke, and Dominik ] used decision trees (DTs) trained through genetic programming (GP) to detect intrusions in the CAN bus. Their approach focuses solely on message payloads, with models trained individually for each CAN ID within the CAN bus training data. The authors compared their method with artificial neural networks (ANNs). Experimental results showed that for most intrusions, the accuracy of the ANN was slightly higher, and the ANN had a significantly lower training time; however, the proposed GP method demonstrated significantly improved detection time.
Harvested Online Documentation & Reference Sources • https://github.com/Western-OC2-Lab/Intrusion-Detection-System-Using-Machine-Learning • https://arxiv.org/html/2505.11551v1
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Connected Vehicle Intrusion Detection System Using Ml.
[*] Metasploit Scan Running on Target Subnet for Connected Vehicle Intrusion Detection System Using Ml... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |