Complete Technical Paper Content — Consensus Mechanism Simulation Proof Of Work Vs Proof Of Stake
Overview & System Context
Consensus Mechanism Simulation Proof Of Work Vs Proof Of Stake: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~8517 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background Proof-of-stake (PoS) protocols are a class of consensus mechanisms for blockchains that work by selecting validators in proportion to their quantity of holdings in the associated cryptocurrency. This is done to avoid the computational cost of proof-of-work (PoW) schemes. The first functioning use of PoS for cryptocurrency was Peercoin in 2012, although its scheme, on the surface, still resembled a PoW.
committee-based PoS (a.k.a. nominated PoS, NPoS); delegated proof of stake (DPoS); liquid proof of stake (LPoS). Hash ( ProposedNewBlock | | ClockTime ) < target × StakeValue {\displaystyle {\text{Hash}}({\text{ProposedNewBlock}}\mathbin {||} {\text{ClockTime}})<{\text{target}}\times {\text{StakeValue}}} The smaller amount of calculations required for solving the puzzle for high-value stakeholders helps to avoid excessive hardware.
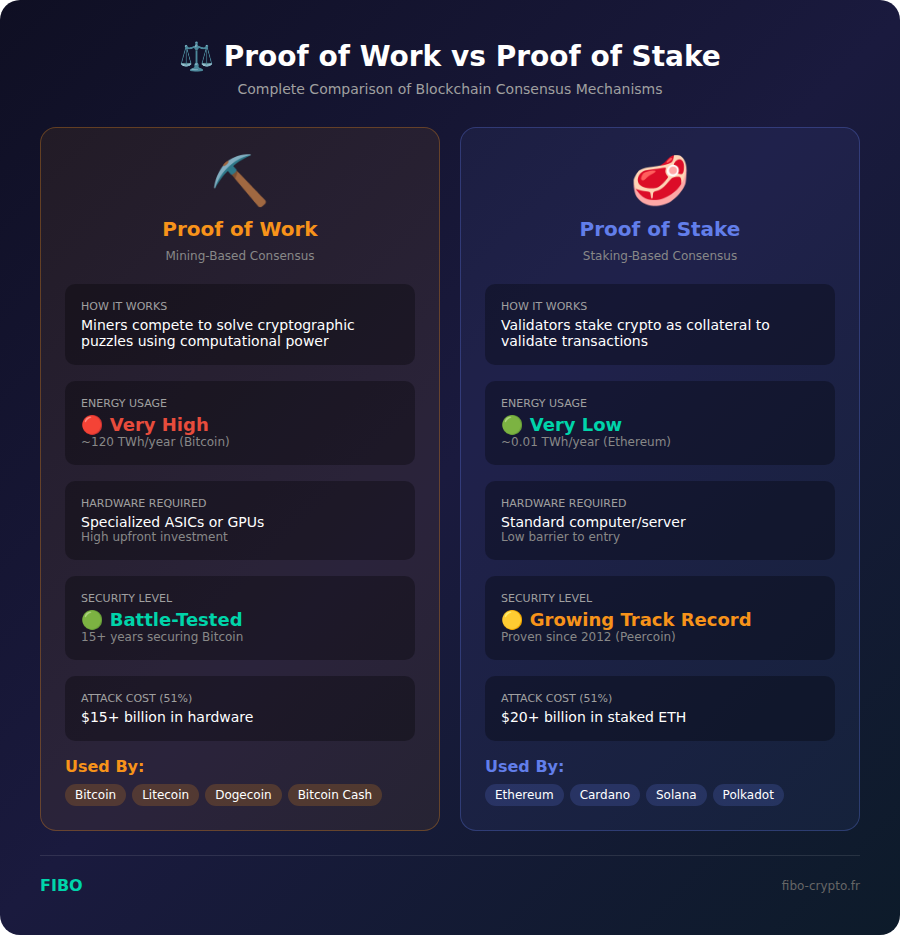
Figure 1: Consensus Mechanisms Explained: PoW vs PoS & How Blockchains Agree | Fibo A "proposer" with a "proposed block" is randomly selected by adding it to the temporary pool used to select just one consensual block; The other participants, validators, obtain the pool, validate, and vote for one; The BFT consensus is used to finalize the most-voted block. The scheme works as long as no more than a third of validators are dishonest. BFT schemes are used in Tendermint and Casper FFG.
Digital currency (digital money, electronic money or electronic currency) is any currency, money, or money-like asset that is primarily managed, stored or exchanged on digital computer systems, especially over the internet. Types of digital currencies include cryptocurrency, virtual currency and central bank digital currency. Digital currency may be recorded on a distributed database on the internet, a centralized electronic computer database owned by a company or bank, within digital files or even on a stored-value card. Digital currencies exhibit properties similar to traditional currencies, but generally do not have a classical physical form of fiat currency historically that can be held in the hand, like currencies with printed banknotes or minted coins. However, they do have a physical form in an unclassical sense coming from the computer to computer and computer to human interactions and the information and processing power of the servers that store and keep track of money.
This unclassical physical form allows nearly instantaneous transactions over the internet and vastly lowers the cost associated with distributing notes and coins: for example, of the types of money in the UK economy, 3% are notes and coins, and 79% as electronic money (in the form of bank deposits). Usually not issued by a governmental body, virtual currencies are not considered a legal tender and they enable ownership transfer across governmental borders. This type of currency may be used to buy physical goods and services, but may also be restricted to certain communities such as for use inside an online game. Digital money can either be centralized, where there is a central point of control over the money supply (for instance, a bank), or decentralized, where the control over the money supply is predetermined or agreed upon democratically.
A virtual currency has been defined in 2012 by the European Central Bank as "a type of unregulated, digital money, which is issued and usually controlled by its developers, and used and accepted among the members of a specific virtual community". The US Department of Treasury in 2013 defined it more tersely as "a medium of exchange that operates like a currency in some environments, but does not have all the attributes of real currency". The US Department of Treasury also stated that, "Virtual currency does not have legal-tender status in any jurisdiction." According to the European Central Bank's 2015 "Virtual currency schemes – a further analysis" report, virtual currency is a digital representation of value, not issued by a central bank, credit institution or e-money institution, which, in some circumstances, can be used as an alternative to money. In the previous report of October 2012, the virtual currency was defined as a type of unregulated, digital money, which is issued and usually controlled by its developers, and used and accepted among the members of a specific virtual community. According to the Bank for International Settlements' November 2015 "Digital currencies" report, it is an asset represented in digital form and having some monetary characteristics. Digital currency can be denominated to a sovereign currency and issued by the issuer responsible to redeem digital money for cash. In that case, digital currency represents electronic money (e-money). Digital currency denominated in its own units of value or with decentralized or automatic issuance will be considered as a virtual currency. As such, bitcoin is a digital currency but also a type of virtual currency. bitcoin and its alternatives are based on cryptographic algorithms, so these kinds of virtual currencies are also called cryptocurrencies.
Currency can be exchanged electronically using debit cards and credit cards using electronic funds transfer at point of sale. Figure 2: Consensus Algorithms: Proof of Work vs. Proof of Stake A number of electronic money systems use contactless payment transfer in order to facilitate easy payment and give the payee more confidence in not letting go of their electronic wallet during the transaction.
In 1994 Mondex and National Westminster Bank provided an "electronic purse" to residents of Swindon. In about 2005 Telefónica and BBVA Bank launched a payment system in Spain called Mobipay which used simple short message service facilities of feature phones intended for pay-as-you-go services including taxis and pre-pay phone recharges via a BBVA current bank account debit. In January 2010, Venmo launched as a mobile payment system through SMS, which transformed into a social app where friends can pay each other for minor expenses like a cup of coffee, rent and pay a share of the restaurant bill when one has forgotten their wallet. It is popular with college students, but has some security issues. It can be linked to a bank account, credit/debit card or have a loaded value to limit the amount of loss in case of a security breach.
Credit cards and non-major debit cards incur a 3% processing fee. On 19 September 2011, Google Wallet released in the United States to make it easy to carry all one's credit/debit cards on a phone. In 2012 Ireland's O2 (owned by Telefónica) launched Easytrip to pay road tolls which were charged to the mobile phone account or prepay credit. The UK's O2 invented O2 Wallet at about the same time. The wallet can be charged with regular bank accounts or cards and discharged by participating retailers using a technique known as 'money messages'. The service closed in 2014. On 9 September 2014, Apple Pay was announced at the iPhone 6 event. In October 2014 it was released as an update to work on iPhone 6 and Apple Watch. It is very similar to Google Wallet, but for Apple devices only.
Digital Currency has been implemented in some cases as a decentralized system of any combination of currency issuance, ownership record, ownership transfer authorization and validation, and currency storage. Per the Bank for International Settlements (BIS), "These schemes do not distinguish between users based on location, and therefore allow value to be transferred between users across borders. Moreover, the speed of a transaction is not conditional on the location of the payer and payee." Virtual currencies pose challenges for central banks, financial regulators, departments or ministries of finance, as well as fiscal authorities and statistical authorities.
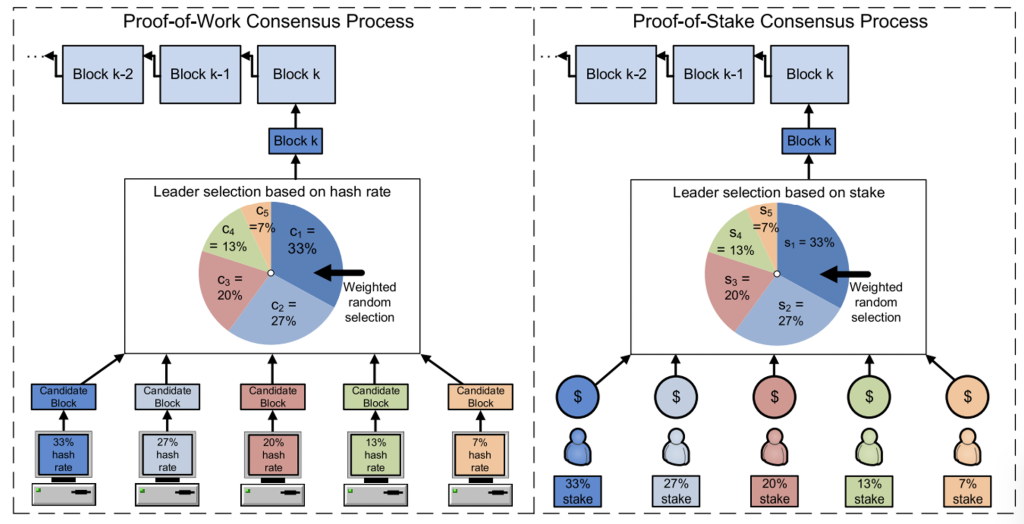
Figure 3: Fikir BirliIi MekanizmasI(Consensus Mechanism) Nedir? Hong Kong's Octopus card system: Launched in 1997 as an electronic purse for public transportation, is the most successful and mature implementation of contactless smart cards used for mass transit payments. After only 5 years, 25 percent of Octopus card transactions are unrelated to transit, and accepted by more than 160 merchants. London Transport's Oyster card system: Oyster is a plastic smartcard that can hold pay-as-you-go credit, Travelcards and Bus & Tram season tickets. An Oyster card can be used to travel on bus, Tube, tram, DLR, London Overground and most National Rail services in London.
Japan's FeliCa: A contactless RFID smart card, used in a variety of ways such as in ticketing systems for public transportation, e-money, and residence door keys. The Netherlands' Chipknip: As an electronic cash system used in the Netherlands, all ATM cards issued by the Dutch banks had value that could be loaded via Chipknip loading stations. For people without a bank, pre-paid Chipknip cards could be purchased at various locations in the Netherlands. As of 1 January 2015, payment can no longer be made with Chipknip. Belgium's Proton: An electronic purse application for debit cards in Belgium. Introduced in February 1995, as a means to replace cash for small transactions. The system was retired on 31 December 2014. In March 2018, the Marshall Islands became the first country to issue their own cryptocurrency and certify it as legal tender; the currency is called the "sovereign".
In 2016, Fan Yifei, a deputy governor of China's central bank, the People's Bank of China (PBOC), wrote that "the conditions are ripe for digital currencies, which can reduce operating costs, increase efficiency and enable a wide range of new applications". According to Fan Yifei, the best way to take advantage of the situation is for central banks to take the lead, both in supervising private digital currencies and in developing digital legal tender of their own. In October 2019, the PBOC announced that a digital renminbi would be released after years of preparation. The version of the currency, known as DCEP (Digital Currency Electronic Payment), is based on cryptocurrency which can be "decoupled" from the banking system. The announcement received a variety of responses: some believe it is more about domestic control and surveillance. In December 2020, the PBOC distributed CN¥20 million worth of digital renminbi to the residents of Suzhou through a lottery program to further promote the government-backed digital currency. Recipients of the currency could make both offline and online purchases, expanding on an earlier trial that did not require internet connection through the inclusion of online stores in the program. Around 20,000 transactions were reported by the e-commerce company JD.com in the first 24 hours of the trial.
Contrary to other online payment platforms such as Alipay or WeChat Pay, the digital currency does not have transaction fees. The Unified Payments Interface (UPI) is a real-time payment system for instant money transfers between any two bank accounts held in participating banks in India. The interface has been developed by the National Payments Corporation of India and is regulated by the Reserve Bank of India. This digital payment system is available 24 hours a day, every day of the year.
UPI is agnostic to the type of user and is used for person to person, person to business, business to person and business to business transactions. Transactions can be initiated by the payer or the payee. To identify a bank account it uses a unique Virtual Payment Address (VPA) of the type 'accountID@bankID'. The VPA can be assigned by the bank, but can also be self specified just like an email address. The simplest and most common form of VPA is 'mobilenumber@upi'. Money can be transferred from one VPA to another or from one VPA to any bank account in a participating bank using account number and bank branch details. Transfers can be inter-bank or intra-bank. UPI has no intermediate holding pond for money. It withdraws funds directly from the bank account of the sender and deposits them directly into the recipient's bank account whenever a transaction is requested. A sender can initiate and authorise a transfer using a two step secure process: login using a pass code → initiate → verify using a passcode. A receiver can initiate a payment request on the system to send the payer a notification or by presenting a QR code. On receiving the request, the payer can decline or confirm the payment using the same two step process: login → confirm → verify. The system is extraordinarily user friendly to the extent that even technophobes and barely literate users are adopting it in huge numbers.
The term 'consensus mechanism' is often used colloquially to refer to 'proof-of-stake', 'proof-of-work' or 'proof-of-authority' protocols. However, these are just components in consensus mechanisms that protect against . Consensus mechanisms are the complete stack of ideas, protocols and incentives that enable a distributed set of nodes to agree on the state of a blockchain.
To better understand this page, we recommend you first read our introduction to Ethereum . By consensus, we mean that a general agreement has been reached. Consider a group of people going to the cinema. If there is no disagreement on a proposed choice of film, then a consensus is achieved. If there is disagreement, the group must have the means to decide which film to see. In extreme cases, the group will eventually split.
In regard to the Ethereum blockchain, the process is formalized, and reaching consensus means that at least 66% of the nodes on the network agree on the global state of the network. The term consensus mechanism refers to the entire stack of protocols, incentives and ideas that allow a network of nodes to agree on the state of a blockchain.
Ethereum uses a proof-of-stake-based consensus mechanism that derives its crypto-economic security from a set of rewards and penalties applied to capital locked by stakers. This incentive structure encourages individual stakers to operate honest validators, punishes those who don't, and creates an extremely high cost to attack the network. Then, there is a protocol that governs how honest validators are selected to propose or validate blocks, process transactions and vote for their view of the head of the chain. In the rare situations where multiple blocks are in the same position near the head of the chain, there is a fork-choice mechanism that selects blocks that make up the 'heaviest' chain, measured by the number of validators that voted for the blocks weighted by their staked ether balance.
Some concepts are important to consensus that are not explicitly defined in code, such as the additional security offered by potential out-of-band social coordination as a last line of defense against attacks on the network. Miners compete to create new blocks filled with processed transactions. The winner shares the new block with the rest of the network and earns some freshly minted ETH. The race is won by the computer which is able to solve a math puzzle fastest.
This produces the cryptographic link between the current block and the block that went before. Solving this puzzle is the work in "proof-of-work". The canonical chain is then determined by a fork-choice rule that selects the set of blocks that have had the most work done to mine them. 2. System Architecture & Core Working Principles The network is kept secure by the fact that you'd need 51% of the network's computing power to defraud the chain. This would require such huge investments in equipment and energy; you're likely to spend more than you'd gain.
Validators create blocks. One validator is randomly selected in each slot to be the block proposer. Their consensus client requests a bundle of transactions as an 'execution payload' from their paired execution client. They wrap this in consensus data to form a block, which they send to other nodes on the Ethereum network. This block production is rewarded in ETH. In rare cases when multiple possible blocks exist for a single slot, or nodes hear about blocks at different times, the fork choice algorithm picks the block that forms the chain with the greatest weight of attestations (where weight is the number of validators attesting scaled by their ETH balance).
A proof-of-stake system is secure crypto-economically because an attacker attempting to take control of the chain must destroy a massive amount of ETH. A system of rewards incentivizes individual stakers to behave honestly, and penalties disincentivize stakers from acting maliciously. An explainer covering the core consensus mechanisms used in blockchains, and how they enable decentralized networks to agree on the state of transactions without a central authority.
Proof-of-work and proof-of-stake alone are not consensus protocols, but they are often referred to as such for simplicity. They are actually Sybil resistance mechanisms and block author selectors; they are a way to decide who is the author of the latest block. Another important component is the chain selection (aka fork choice) algorithm that enables nodes to pick one single correct block at the head of the chain in scenarios where multiple blocks exist in the same position.
Sybil resistance measures how a protocol fares against a Sybil attack. Resistance to this type of attack is essential for a decentralized blockchain and enables miners and validators to be rewarded equally based on resources put in. Proof-of-work and proof-of-stake protect against this by making users expend a lot of energy or put up a lot of collateral. These protections are an economic deterrent to Sybil attacks.
A chain selection rule is used to decide which chain is the "correct" chain. Bitcoin uses the "longest chain" rule, which means that whichever blockchain is the longest will be the one the rest of the nodes accept as valid and work with. For proof-of-work chains, the longest chain is determined by the chain's total cumulative proof-of-work difficulty. Ethereum used to use the longest chain rule too; however, now that Ethereum runs on proof-of-stake it adopted an updated fork-choice algorithm that measures the 'weight' of the chain. The weight is the accumulated sum of validator votes, weighted by validator staked-ether balances.
Ethereum uses a consensus mechanism known as Gasper that combines Casper FFG proof-of-stake (opens in a new tab) with the GHOST fork-choice rule (opens in a new tab) . As digital networks grow and millions join blockchain ecosystems, the need for reliable decision-making becomes even sharper. The level of coordination in a decentralized space doesn’t happen by chance. It happens because consensus mechanisms quietly manage who gets to add information and how the network agrees on it.
Today, blockchain mechanisms are not limited to crypto trading or NFTs. It is fueling supply chain management , identity systems , gaming economies, financial markets, AI-driven platforms, and data networks worldwide. In this post, I’ll discuss blockchain consensus mechanisms, how they operate, and how to select the appropriate ones for your business in 2026.
Think of a blockchain with thousands of strangers trying to update the same record at the same time. Someone has to settle who’s right. That’s exactly what consensus mechanisms do – they align everyone on the same truth without asking anyone to trust each other. Technically speaking, it’s a method that helps a decentralized network agree on which transactions are valid. Since there’s no central authority, the network relies on many independent nodes to sync the same version of the ledger.
There are many conversations around blockchain consensus 2026, to see where the tech heads next. Choosing the wrong consensus mechanism in blockchain business can slow down a project, raise costs, lower user trust, and create long-term issues that are hard to fix. Blockchain consensus mechanisms ensure that every node in a decentralized network is aware of the single valid version of the ledger, without the need for a central authority.
Overall, the consensus mechanisms ensure security, trust, and synchronization in a decentralized system. These elements determine the network’s performance, security, and decentralization for the blockchain consensus mechanism. Proof of Work is the earliest consensus mechanism, built around miners solving cryptographic puzzles to validate transactions. It offers strong decentralization and reliable blockchain consensus, but it also comes with high energy use and slower processing speeds compared to newer models.
PoW remains an important part of the ecosystem, especially for networks that prioritize censorship resistance and trustless security. Proof of Stake consensus mechanism shifts the focus from physical mining to economic staking. Validators lock up tokens, and their stake influences who gets to create the next block. If they act dishonestly, they lose part of their stake, which keeps the system fair and secure.
This model is far more energy-efficient and supports faster scaling than PoW. The global shift toward PoS became more visible after the Ethereum Merge. DPoS works like a token-based voting system where you choose a small group of delegates who validate transactions and maintain the network. It delivers high speed and strong throughput, which makes it popular for social platforms, gaming projects, and dApps that deal with heavy user activity.
PoL is gaining attention in DeFi as it rewards you (validators) based on the liquidity you provide. This creates healthier ecosystems because you have a direct incentive to support network growth. At the same time, large liquidity providers may hold more influence, which can reduce decentralization if not managed carefully. 3. Software Implementation, Frameworks & Protocols Berachain uses PoL-inspired models where liquidity providers play a central role in securing and strengthening the protocol.
PoA relies on a set of pre-approved, identifiable validators who handle transaction verification. This makes the network quick, predictable, and suitable for enterprise or consortium blockchains. VeChain uses PoA to support enterprise supply chain solutions with predictable performance. pBFT consensus mechanism helps a network reach agreement even if some nodes act maliciously. This model offers quick finality, strong consistency, and dependable performance, making it popular for permissioned blockchains and high-speed public networks.
Hyperledger Fabric uses PBFT-style mechanisms to support secure, enterprise-grade applications. PoH creates a cryptographic timestamp for every event, giving the network a built-in timeline before running any consensus mechanisms. This speeds up transactions and helps the system scale without heavy computation. It’s highly efficient and supports networks that aim for quick processing and high throughput.
Solana uses PoH along with PoS to process thousands of transactions per second with low fees. As the ecosystem continues to grow, many more experimental and hybrid models are emerging to meet performance, security, and scalability needs. Some of these are Proof of Activity, Proof of Capacity, Proof of Burn, Proof of Elapsed Time, and many more.
Bitcoin remains a strong testament to the resilience of Proof of Work (PoW) after more than a decade of continuous operation. Its security comes from requiring miners worldwide to solve cryptographic puzzles before adding blocks. Despite newer consensus models, Bitcoin shows that PoW still delivers strong security and decentralization when implemented at scale.
In 2022, Ethereum underwent one of the largest shifts in blockchain history – moving from PoW to PoS through its upgrade known as The Merge. This change reduced its energy consumption dramatically, while preserving decentralization and speeding up transactions. Ethereum’s transition shows how modern blockchain consensus mechanisms can balance performance, security, and sustainability.
Emerging networks and DeFi platforms are experimenting with PoL, and Berachain is among those pioneering this approach. These challenges will be solved to determine the maturity of blockchain based on blockchain asset management standards. Overall, consensus mechanisms will continue to secure blockchains while coordinating the economic and operational flow of entire ecosystems.
Imagine you have a dollar, a common fungible asset easily interchangeable without altering its essence. … If you’re new to crypto, you’ve probably heard the terms "coins" and "tokens" used interchangeably. … Blockchain networks rely on consensus mechanisms to validate transactions and secure the network. For developers and teams building with blockchain RPC (Remote Procedure Call) providers, understanding these mechanisms is critical. The two most prominent models – Proof of Work vs Proof of Stake – directly impact node infrastructure, RPC latency, and network scalability.
In this article, we’ll break down PoW and PoS, explain their impact on node performance, and help developers make better decisions when integrating with blockchains via RPC endpoints. Proof of Work is the original blockchain consensus model, pioneered by Bitcoin and used by Ethereum until its Merge to Proof of Stake in 2022. In PoW: Proof of Stake removes energy-heavy mining and instead uses staked cryptocurrency to secure the network. Validators propose and attest to new blocks based on their stake.
Both Proof of Work and Proof of Stake play vital roles in blockchain ecosystems. While PoW remains a pillar of Bitcoin’s security, PoS is becoming the consensus standard for next-generation blockchain networks due to its scalability and energy efficiency. For blockchain developers, choosing an RPC provider that is optimized for these consensus differences is crucial. At NOWNodes we provide fast, secure, and reliable access to decentralized networks—whether PoW or PoS powers them.
Thank you for visiting nature.com. You are using a browser version with limited support for CSS. To obtain the best experience, we recommend you use a more up to date browser (or turn off compatibility mode in Internet Explorer). In the meantime, to ensure continued support, we are displaying the site without styles and JavaScript. 4. Practical Deployment, Analysis & Case Studies Integration of renewable-energy (RE) sources of energy into local microgrids, decentralised energy markets using blockchain based peer-to-peer (P2P) energy trading is gaining more traction due to its ability to enable transparent, autonomous, and secure transactions among distributed energy resources (DERs). Due to the large variety in microgrid topologies and their respective operational constraints, a key challenge to obtaining the most effective trading framework is the choice of blockchain consensus protocol that suits a given microgrid type. Choice of consensus mechanism solely affects the reliability and security of a network. This paper presents a quantitative comprehensive evaluation of various blockchain consensus mechanisms such as Proof-of-Work (PoW), Proof-of-Stake (PoS), Delegated Proof-of-Stake (DPoS), Proof-of-Elapsed-Time (PoET), Practical Byzantine Fault Tolerance (PBFT), Raft, and Tendermint to determine their suitability for P2P energy trading in microgrids. Various metrics such as fault tolerance, energy efficiency, latency, throughput and consensus time were evaluated for multiple consensus mechanisms through simulations. This paper also studies node-scaling impact on the protocols and presents a final decision framework to match the suitable protocol with various microgrid topologies.
A secure and highly efficient blockchain PBFT consensus algorithm for microgrid power trading A scalable post quantum secure blockchain framework with adaptive time consensus in cloud environments With the increasing transformation of traditional utility-driven grids to decentralised microgrids and smart grids, there is an urgent need for a mechanism to manage and optimise the flow of power within microgrids 1 , 2 , 3 . Peer-to-peer (P2P) energy trading is one such mechanism that can manage multidirectional power flow efficiently. It enables users to exchange excess power generated through renewable energy (RE) with peers, thus reducing the reliance on centralised utility grids, and thereby enhancing local microgrid stability by balancing the demand-supply curve 4 , 5 , 6 . Consequently, there has been a significant increase in academic and commercial interest in research related to P2P energy trading. In just 7 years (2017 - 2023), the number of peer-reviewed articles has increased almost eight times, with more than 450 articles indexed in 2023 alone 7 . Figure 1 depicts the expanding research scenario pertaining to P2P energy trading 8 . This trend is also being observed by governments and policymakers in many countries like Australia, Germany, Japan and the United States of America 9 . These developments have also impacted the markets significantly, increasing the investment in this sector. The global microgrid hardware market is valued at 43 billion dollars and is projected to reach 236 billion by 2034 with a cumulative growth rate of up to 18.5%.
However, such trading mechanisms require enhanced resilience against cyberattacks, trust among peers, transparency, and tamper-proof transaction data. Blockchain is one such technology that can bridge all these gaps and facilitate cyber-secure, trusted, transparent, and tamper-resilient P2P trading. Blockchain is a decentralised, distributed, and immutable book of records (or a ledger) into which data can only be added upon consensus among all peers and not modified. Any attempts to maliciously modify the data on a blockchain would require enormous computing power to hack into all the peers on the network simultaneously, since each node has a real-time ledger of all the transactions happening in the network. Because of all the above features, blockchain technology is increasingly being deployed in the energy markets. There has been a recent surge in the energy trading software and services market, which is valued at 7.5 billion dollars and is projected to reach 12.4 billion by 2030 10 , of which blockchain-based pilot projects occupy up to 3.1 billion dollars 11 . Figure 2 shows the rapid expansion of research in this area.
Operational data from pilot projects highlights the sheer volume of transactions that the future trading mechanisms must hold. TraceX, an energy marketplace run by PowerLedger, cleared almost 1.2 million renewable energy certificate trades in January 2025 alone, which is equal to almost 167 GWh of green energy being transacted in a single month 13 . This shows that P2P trading ledgers require high scalability and low transaction times. All these factors are controlled by consensus mechanisms, algorithms based on which the distributed peers agree on the next state of the blockchain. There are various consensus protocols that exist and are very different from each other. Selecting the right consensus mechanism is of utmost importance, as it is the backbone of the entire network 14 . Otherwise, there would be a multitude of issues like throughput bottlenecks, excess latency, cost and energy overhead, weaker security, and poor scalability. For example, a suburban feeder with 250 rooftop solar households can generate up to 100 transactions per second during rapid irradiance swings; a proof of work (PoW) based blockchain can handle only up to 7 transactions per second (TPS), leading to a pile-up of transactions, thus creating a throughput bottleneck. There are other consensus mechanisms that can even handle up to 32000 TPS without any issues in their working, which would be an oversell for a 100 TPS trade.
Similarly, some consensus mechanisms like HotStuff require only 150–250 ms for transaction approval, whereas proof-of-stake (PoS) chains require as high as 2–4 min, leading to excessive latency. Power consumption of certain mechanisms (PoW) is very high, almost as much as 700 kW annually. This further increases the overall power consumption of the network participants, which goes against the main motive for energy trading 15 . Due to this enormous diversity, there is not a single consensus protocol that is the best for all microgrid topologies. The most optimal consensus algorithm for a given microgrid topology depends on the transaction frequency, regulatory risks, and a viable energy-to-computation ratio. Despite the abundance of literature in this area, there is a significant gap in identifying the best consensus protocol for a given microgrid application. This paper aims to bridge that gap by comparing major consensus protocols using a simulation environment. Various attributes such as throughput, latency, scalability, energy efficiency, security, finality, fault tolerance, and consensus time are tested for consensus protocols, and the best protocol for a given microgrid situation is analyzed. The working of consensus protocols is simulated in Python and then the results are plotted and tabulated to arrive at the best conclusion.
The remainder of the paper is organised as follows. “ Consensus mechanisms ” gives a detailed explanation about various consensus protocols considered and their working. “ Methodology ” refers to the methodology employed to calculate the various parameters discussed above. The simulation details are explained in detail in “ Simulation setup ”, whereas “ Results and analysis ” encapsulates the results obtained from the simulations and discusses the final application frameworks for each consensus protocol. “ Conclusion and future scope ” finally concludes all the findings of the manuscript and gives a direction for future applications of the manuscript.
As discussed above in “ Introduction ”, any update to the blockchain requires a consensus among the network participants. A consensus mechanism is a coordination protocol that helps nodes in a network to agree on the next state of the chain 16 . This mechanism decides whether a new block can be added to the chain and also approves transactions. The peer proposing new blocks into the system is governed by the consensus protocol chosen, which directly affects transaction throughput, energy efficiency of the chain, and chain latency. These mechanisms also control how the agreement among peers pertaining to the block proposal is reached and also verify the legitimacy of the proposal 17 , 18 . There are various consensus mechanisms and this paper compares the seven majorly used protocols as shown in Fig. 3 Introduced by Satoshi Nakamoto in 2008 19 , this protocol is the first blockchain consensus protocol and has been used in the Bitcoin blockchain ever since. To mine new blocks in this protocol, the miner must solve a cryptographic puzzle and achieve the target hash set by the chain. This involves extensive computing power to perform multiple trials and achieve the correct solution through which a new block is added. The miner who solves the puzzle faster than the others gets to mine a block. The workflow of block creation in PoW chains is explained below in Algorithm 1 where, Mempool is an assembly of transactions gathered by the miners in a descending order of gas fee assigned. From this pool of transactions, miners usually select the one with the highest gas fee and configure the block header with a parent hash, transaction list for the block, and nonce. The data in the block header is used to make the block hash. A new block is added only if the block hash is lesser than the target hash decided by the chain before hand 20 . Due to the computing-intensive process involved in block mining, PoW chains require a lot of time to complete one transaction, leading to transaction blockages as the number of nodes increase. This in turn leads to low throughput and high latency of these chains. There is a very high chance of several miners combining their respective computation powers together and making a centralised mining pool which makes the chain vulnerable. PoW chains also consume a lot of power to solve the mining puzzles, thus increasing the carbon footprint of the system.
The wasteful computing-intensive process is replaced by economic stakes in PoS blockchains. Block-proposal rights and voting weight in this protocol are directly proportional to stake value of the peer 21 . Any malicious activity results in slashing, thereby confiscating a significant portion or the entirety of the stake, which results in lower security costs. PoS is used in the Ethereum chain, where the minimum requirement to start mining a new block is 32 ETH. The block creation process in PoS chains are shown below in Fig. 4 .
As mentioned above, validators are those users who stake 32 ETH for block creation, and their IDs are stored in Beacon Chain’s validator registry. In this protocol, there is a slot during which one block can be proposed and it lasts for 12 seconds. At the beginning of each slot, PoS uses a random function to select a validator as the block proposer. Along with the proposer, another set of 128 validators are randomly selected to form an attestation committee that is responsible for validating the block proposed by the proposer in that assigned slot. These committee members are selected using a shuffling algorithm.
Then, the proposer collects a set of transactions from the Mempool and constructs a new block and signs it using a private key. This new block consists of metadata, transaction details and the state transitions. After signing the block by using a private key, this block is broad-casted to the entire network using a gossip protocol. Once the committee members receive the block, the validity of the block is checked and if valid, these members also sign using their private key and block hash and then broadcast their attestations into the network. These attestations serve as votes and the block is finalised only when at least two-thirds of the entire ETH staked by the validators votes in favor of creating the block in two consecutive epochs (One epoch is equal to 32 slots). Table 1 reveals that PoS addresses most of the limitations that PoW brings to the table while maintaining security through economic incentives rather than computational power. Though both PoW and PoS chains face centralisation risks in the form of miner pools and stake concentration respectively, PoS chains are better suited for power consumption-constrained microgrid environments through deterministic finality.
This mechanism was introduced in 2014 by Daniel Larimer and is used in popular blockchain platforms like EOS, Lisk and BitShares. This protocol is more scalable compared to its counterparts, especially in high-frequency and permissioned blockchains. The stakeholders in this protocol vote to elect a fixed number of delegates who are responsible for proposing and validating new blocks into the chain. The voting weight of stakeholders is proportional to their stake in the chain and these voters can vote for multiple delegates. 21 delegates with the most number of votes are elected as active witnesses for the current round of block proposal. Then, these witnesses are ordered into a 21-slot round by a random function, where each slot lasts for up to 0.5 s 22 .
During these assigned time slots, each witness must sign and publish a block and if they fail to comply, they will not be able to create a block in this round and also face penalties that lead to a loss of their reputation. A block is completely finalised and irreversible only when at least two-thirds of the witnesses have built their blocks on top of it directly, all within a second under normal conditions. This mechanism primarily works on the reputation of the witnesses, and if any malicious user is noted, his reputation tanks and he loses his stake. Algorithm 2 depicts the block creation process in a DPoS blockchain.
PoET was introduced first in the Hyperledger Sawtooth blockchain by Intel. This mechanism has a random leader election similar to PoW chains but uses trusted execution environments (TEE) like the software guard extensions (SGX) developed by Intel as leverage instead of computing power. Each validator is assigned a random wait time by this protocol and the validator whose time period expires first gets to create a new block in the chain 23 . The randomness is generated in the SGX enclave ensuring its security from malicious actors. The workflow of this protocol is depicted in Algorithm 3 This is one of the oldest consensus mechanisms proposed by Castro and Liskov in 1999 for optimising performance in asynchronous systems. This mechanism works on a deterministic consensus mechanism rather than a probabilistic approach.
It uses three rounds of message exchanges between nodes and remains functional as long as lesser than one-third of the nodes are faulty 24 , 25 . Workflow for block creation in PBFT chains is shown in Algorithm 4. Introduced by Diego Ongaro and John Ousterhout in 2014, this protocol was designed for implementation in distributed systems. There are three phases in the workflow of this protocol : Leader election : a random node becomes a candidate for a leader election at the start of a new term and becomes a leader if he gets the majority of votes. He remains the leader for the entirety of the term Log replication : the transaction requests are accepted by the leader and then appended to the local log of the leader. Along with this, the leader also broadcasts this entry to all the followers, and the new log entry is committed if the majority of followers have received the entry. The committed entries are then added to the state machine of the followers.
Consistency: if any follower lags behind, the leader can update the logs incrementally to help the follower catch up. Figure 5 represents the workflow in Raft consensus algorithm. As soon as the client makes a request for a new block, the leader of the current term appends the proposed block into their local log of the blockchain and then propagates that appended log to the follower nodes and then waits for the majority of followers to append the new block onto their respective local logs of the chain. If majority of the followers append the block, then the block is considered valid and is appended onto the state machine of the entire blockchain. This message is then carried to the client by the leader. If majority attestation fails, then the leader retries the propagation as long as he is elected. If the leader crashes or loses his leadership before the log is committed onto the chain, then any log entry that is not replicated by the majority of followers is discarded and then a new leader is elected.
All the protocols explained above in “ Consensus mechanisms ” are tested for several metrics like throughput, latency, scalability, energy efficiency, security, and fault tolerance 26 , 27 . The performance metrics and the formulation behind them are explained further in this section. Throughout quantifies the productivity of a blockchain under steady state. For example, throughput can be thought as the capacity of a toll on a highway—higher the number of lanes (bigger blocksize), more the number of cars passing through (transactions). A blockchain with a low throught is similar to having a single toll booth on a highway and gets blocked if there is a lot of traffic (transaction backlog). For example, a Bitcoin blockchain processes roughly 7 transactions per second and the remaining transactions require a waiting period os almost an hour to get processed with high confidence confirmation. It is defined as the number of transactions processed by the blockchain in a given observation time window, as shown in Eq. ( 1 ) 5. Performance Evaluation & Extended Technical Observations Where \(N_{committed}\) is the number of transactions committed into the blockchain during the time interval \(\Delta t\) . Most blockchains, batch up a set of transactions into a single block, and therefore the maximum throughput that can be achieved by a blockchain is defined in Eq. ( 2 ), assuming that every block is fully packed with transactions, all the transactions in the block are homogeneous and that there is no block reorganisation, orphaning or failure.
TPS of a particular blockchain is affected by the time taken for blocks and votes to reach all peers and validators, bandwidth of the gossip protocol, mempool saturation, delays in reaching a consensus and the time taken to reach finality 28 . In P2P energy trading systems, energy offers, bids, and settlements are coded as transactions and require near real-time processing without any delay because any delay would clog the entire network.
The total time observed by the end user between submitting a transaction and receiving confirmation about its irreversible commitment into the chain is called latency. It is basically the wait time for a transaction akin to waiting for the confirmation receipt from an online shopping transaction. Latency consists of three sub-components, such as : Propagation delay ( \(L_{prop}\) ) : this is the time taken for a transaction to reach all the peers in the network. This time is fully dependent on the efficiency of the gossip protocol and increases with an increase in the number of nodes in the network.
Consensus delay ( \(L_{cons}\) ): this is the time between receiving a transaction and reaching a consensus on its next state. In different blockchains, it means different things. Like in PoW, it is the time to mine a block, whereas in PoS, it is the time required for a transaction to be selected and confirmed via voting. Confirmation delay ( \(L_{conf}\) ): the time taken for a transaction to finally process the transaction after the consensus is achieved.
Several factors influencing the latency of a block include network size, complexity of the protocol, block creation intervals, faulty nodes or forked chains, and leader re-elections in some protocols. In an energy market context, latency determines the speed of bid matching and any delays in this case would lead to a mismatch of prices and load imbalance. For example, consider a household placing a bid to buy extra power at a certain price. If the blockchain takes too long to confirm the trade, by the time the trade is finalised, the available power or the prices might have changed within that time. This can cause mis-priced trades or load imbalances due to shortages of power in some cases. A low latency blockchain can match bids and offers in real-time, so the transactions are confirmed without any noticeable delay.
The capacity of a consensus mechanism to maintain its performance and accuracy despite system expansion is known as scalability. It is evaluated by observing performance metrics like TPS, latency, fault tolerance and energy consumption as the scale of the system increases 29 , 30 . A system can be scaled in multiple ways as shown in Table 2 . Any scalable protocol must have the per-node resource cost increasing linearly with the scale of the chain. To quantify the scalability of a system, its elasticity is calculated. Elasticity E is defined as the ratio between relative change in TPS and relative change in the number of validators as shown in Eq. ( 4 ).
where, \(\Delta TPS\) is the change observed in TPS and \(\Delta n\) is the change in validator count. \(E \approx 1\) : near-linear scalability—throughput increases proportionally with node count \(E > 1\) : superlinear scalability—rare and typically due to parallelisation or sharding Scalability of a blockchain protocol is extremely important because P2P trading networks have a huge amount of peers and node count keeps increasing as more people want to participate in the trade. Having good scalability ensures proper functionality of the entire system as the energy ecosystem becomes more distributed and data extensive. Consider a microgrid consisting of 100 homes that generate 10 transactions per second. If the network is expanded to 1000 houses (10x the number of nodes), a truly scalable blockchain should ideally be able to handle 100 TPS (10x the original TPS) with only a proportional increase in the reource per node.
The amount of electricity consumed per transaction is called energy efficiency of a protocol. It is defines as shown below in Eq. ( 5 ) where, \(P_{total}\) is the total power consumed by all the consensus nodes, \(\Delta t\) is the time in which the transactions were committed and \(N_{committed}\) is the number of transactions committed into the chain during \(\Delta t\) . Energy efficiency of a protocol is especially important when it comes to microgrids because higher power consumption leads to reduced battery life, increased carbon foot print, and increased dependence on the grid thereby counter-impacting the motives of a microgrid. For example, in a microgrid executing 1000 transactions per day, if a blockchain consumes 1kWh power per transaction, then for an entire day, the consumption would be 1000 kWh in just overhead costs and is extremely high (enough to power dozens of homes ).
Finality of a transaction is reached when it is committed to the block and that decision cannot be reversed. There are two kinds of finality : Probabilistic finality : in protocols that work on a longest chain basis, each additional block added on top of a chain reduces the chance of being overtaken by a competing fork (another alternating chain) vying to enter the network. The probability of reorganisation of the protocol after blocks are added is defined by : Where k is the number of blocks added to the chain by an honest network, \(\beta\) is the block production power of the attacker, i is the number of blocks mined by the adversary that is usually in the range of 0 to k , and \(\left( {\begin{array}{c}k\\ i\end{array}}\right)\) is a binomial coefficient that represents the number of ways to choose i blocks out of k . The above formula in Eq. 6 estimates the probability that an attacker can create a chain longer than the one made by a honest network and invalidate the previously confirmed transaction. If k is high, then the probability of an attacker catching up to the honest chain is very less. However, if the attacker’s power ( \(\beta\) ) is high, then the probability of the attacker winning and forking the chain is very high.
Deterministic finality: used in Byzantine fault tolerance (BFT)-based protocols, in this method, finality is guaranteed when at least \(2f+1\) validators sign off on the proposed block, where f is the maximum number of faulty validators that can be tolerated by the system. f is calculated as shown in Eq. ( 7 ). where n is the total number of validators in the chain. For example, in a chain with 100 validators, the system can tolerate up to 33 faulty validators and for a block to be finalised, at least 67 validators need to sign off.
In a P2P trading scenario, finality ensures the execution of permanent trades, and prevents roll-back of trades to eliminate double-spending and fraud. Fault tolerance of a protocol depicts how many fault nodes can be tolerated by the network without endangering its accuracy. Any BFT style protocol stems from the fischer-lynch-patterson (FLP) theorem for distributed systems that influences the design of deterministic finality based protocols. FLP theorem states that “In an asynchronous distributed system, no deterministic consensus protocol can guarantee both safety and liveness if even one node may fail”. It basically means that it is impossible to achieve safety, liveness and fault tolerance simultaneously in an asynchronous system. Therefore, all the BFT based protocols assume a partial synchrony where, system is asynchronous, but after some time, can behave synchronously, delivering reliable messages on time. Under this partial synchrony, BFT protocols are bounded by the below mentioned assumption in Eq. ( 8 ) where, n is the total number of validators in a network and f is the maximum number of faulty nodes that can be tolerated by a system. This metric is an important parameter with regards to P2P energy trading because smart meter outages and internet failures are a common risk in microgrids, along with market manipulations and hence a highly fault tolerant system is required in a P2P energy trading scenario.
The time required to achieve consensus on the next state of a blockchain network is known as consensus time and is represented by \(T_{cons}\) . Equation ( 9 ) quantifies the consensus time for all blockchain networks as mentioned below : Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Proof%20of%20stake • https://en.wikipedia.org/wiki/Digital%20currency • https://ethereum.org/developers/docs/consensus-mechanisms/ • https://theblockverse.co/consensus-mechanisms-guide/ • https://nownodes.io/blog/proof-of-work-vs-proof-of-stake-a-developer-focused-guide/ • https://www.nature.com/articles/s41598-025-27431-w
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Consensus Mechanism Simulation Proof Of Work Vs Proof Of Stake.
[*] Metasploit Scan Running on Target Subnet for Consensus Mechanism Simulation Proof Of Work Vs Proof Of Stake... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |