Complete Technical Paper Content — Content Security Policy Validator Tool Using Python
Overview & System Context
Content Security Policy Validator Tool Using Python: Comprehensive Web-Sourced Technical Investigation Exhaustive Research Dossier · Pure Web-Scraped Content: ~9523 Words · Real Software Screenshots: 3 1. Executive Overview & Technical Background The Security Content Automation Protocol (SCAP) is a method for using specific standards to enable automated vulnerability management, measurement, and policy compliance evaluation of systems deployed in an organization, including e.g., FISMA (Federal Information Security Management Act, 2002) compliance. The National Vulnerability Database (NVD) is the U.S.
government content repository for SCAP. An example of an implementation of SCAP is OpenSCAP. SCAP is a suite of tools that have been compiled to be compatible with various protocols for things like configuration management, compliance requirements, software flaws, or vulnerabilities patching. Accumulation of these standards provides a means for data to be communicated between humans and machines efficiently. The objective of the framework is to promote a communal approach to the implementation of automated security mechanisms that are not monopolized.
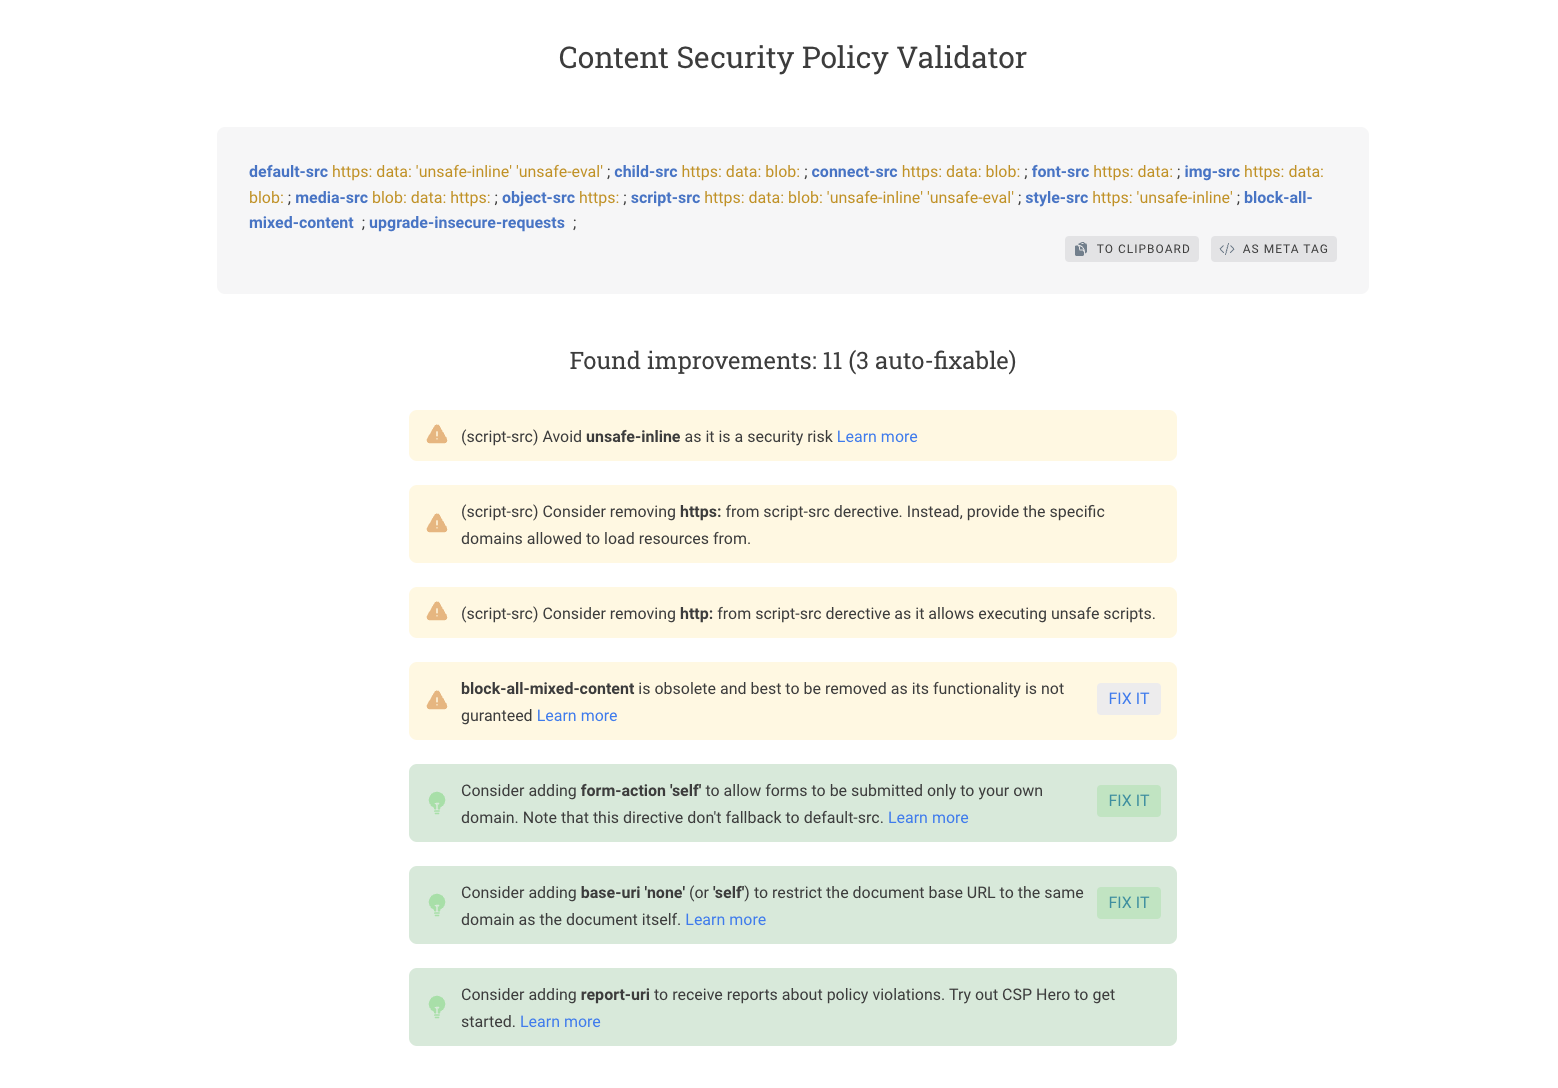
Common Vulnerabilities and Exposures (CVE) Common Configuration Enumeration (CCE) (prior web-site at MITRE) Common Platform Enumeration (CPE) Common Vulnerability Scoring System (CVSS) Extensible Configuration Checklist Description Format (XCCDF) Open Vulnerability and Assessment Language (OVAL) Starting with SCAP version 1.1 (February, 2011) Open Checklist Interactive Language (OCIL) Version 2.0 Starting with SCAP version 1.2 (September, 2011) Asset Identification (AID) Asset Reporting Format (ARF) Common Configuration Scoring System (CCSS) Trust Model for Security Automation Data (TMSAD) Starting with SCAP version 1.3 (February, 2018) Figure 1: Free CSP Validator — Check & Fix Your Content Security Policy Information security (infosec) is the practice of protecting information by mitigating information risks. It is part of information risk management. It typically involves preventing or reducing the probability of unauthorized or inappropriate access to data or the unlawful use, disclosure, disruption, deletion, corruption, modification, inspection, recording, or devaluation of information.
It also involves actions intended to reduce the adverse impacts of such incidents. Protected information may take any form, e.g., electronic or physical, tangible (e.g., paperwork), or intangible (e.g., knowledge). Information security's primary focus is the balanced protection of data confidentiality, integrity, and availability (known as the CIA triad, unrelated to the US government organization) while maintaining a focus on efficient policy implementation but without hampering organization productivity. This is largely achieved through a structured risk management process. To standardize this discipline, academics and professionals collaborate to offer guidance, policies, and industry standards on passwords, antivirus software, firewalls, encryption software, legal liability, security awareness and training, and so forth. This standardization may be further driven by a wide variety of laws and regulations that affect how data is accessed, processed, stored, transferred, and destroyed. While paper-based business operations are still prevalent, requiring their own set of information security practices, enterprise digital initiatives are increasingly being emphasized, with information assurance dealt with by information technology (IT) security specialists. These specialists apply information security to technology (most often some form of computer system). IT security specialists are hired by major enterprises and establishments to keep company technology secure from malicious attacks seeking to acquire critical private information or gain control of the internal systems. There are many specialized roles in Information Security including securing networks and allied infrastructure, securing applications and databases, security testing, information systems auditing, business continuity planning, electronic record discovery, and digital forensics.
Information security standards are guidelines generally outlined in published materials that aim to protect a user's or an organization's cyber environment from threats. This environment includes the users themselves, hardware such as devices and networks, software such as applications or services, and any information in storage or transit. These standards comprise security concepts, technologies, and guidelines to deal with an adverse event. They may also include assessment criteria and certification for organizations implementing a minimum level of security. These standards are developed by various international and national bodies to prevent or mitigate cyber-attacks, ensure consistency among developers, and establish a minimum standard in industries susceptible to an attack. The ISO/IEC 27000 family, published by the International Organization for Standardization (ISO) and the International Electrotechnical Commission (IEC), provides information about the guidelines and requirements for an Information Security Management System (ISMS). The Common Criteria (ISO/IEC 15408) provides guidelines on evaluating and certifying the security of a system. The IEC 62443 establishes security standards for automation and control systems. Similarly, the ISO/SAE 21434, ETSI EN 303 645, and EN 18031 provide standards for road vehicles, the Internet of Things, and radio-based systems respectively. The NIST Cybersecurity Framework (NIST CSF) is a set of guidelines developed by the U.S. National Institute of Standards and Technology to help organizations with risk management. NIST also publishes various Federal Information Processing Standards (FIPS) and Special Publications. The United Kingdom has introduced Cyber Essentials, which is a certification scheme to protect organizations against common security threats. The Australian Cyber Security Centre publishes the Essential Eight mitigation strategies. The Payment Card Industry Data Security Standard (PCI DSS) regulates handling of cardholder data in order to reduce credit card fraud. UL has published standards related to specific industries such as UL 2900-2-3 for security and life safety signaling systems and UL-2900-2-1 for healthcare and wellness systems.
Information security threats come in many different forms. Some of the most common threats today are software attacks, theft of intellectual property, theft of identity, theft of equipment or information, sabotage, and information extortion. Viruses, worms, phishing attacks, and Trojan horses are a few common examples of software attacks. The theft of intellectual property has also been an extensive issue for many businesses. Identity theft is the attempt to act as someone else usually to obtain that person's personal information or to take advantage of their access to vital information through social engineering. Sabotage usually consists of the destruction of an organization's website in an attempt to cause loss of confidence on the part of its customers. Information extortion consists of theft of a company's property or information as an attempt to receive a payment in exchange for returning the information or property back to its owner, as with ransomware. One of the most functional precautions against these attacks is to conduct periodical user awareness. Governments, military, corporations, financial institutions, hospitals, non-profit organizations, and private businesses amass a great deal of confidential information about their employees, customers, products, research, and financial status. Should confidential information about a business's customers or finances or new product line fall into the hands of a competitor or hacker, a business and its customers could suffer widespread, irreparable financial loss, as well as damage to the company's reputation. From a business perspective, information security must be balanced against cost; the Gordon-Loeb Model provides a mathematical economic approach for addressing this concern. For the individual, information security has a significant effect on privacy, which is viewed very differently in various cultures.
The end of the twentieth century and the early years of the twenty-first century saw rapid advancements in telecommunications, computing hardware and software, and data encryption. The availability of smaller, more powerful, and less expensive computing equipment made electronic data processing within the reach of small business and home users. The establishment of Transfer Control Protocol/Internetwork Protocol (TCP/IP) in the early 1980s enabled different types of computers to communicate. These computers quickly became interconnected through the internet. The rapid growth and widespread use of electronic data processing and electronic business conducted through the internet, along with numerous occurrences of international terrorism, fueled the need for better methods of protecting the computers and the information they store, process, and transmit. The academic disciplines of computer security and information assurance emerged along with numerous professional organizations, all sharing the common goals of ensuring the security and reliability of information systems.
Figure 2: Enhancing Security in Sitecore Headless Next.js Apps on XM Cloud | Fishtank The "CIA triad" of confidentiality, integrity, and availability is at the heart of information security. The concept was introduced in the Anderson Report in 1972 and later repeated in The Protection of Information in Computer Systems. The abbreviation was coined by Steve Lipner around 1986. In information security, confidentiality "is the property, that information is not made available or disclosed to unauthorized individuals, entities, or processes." While similar to "privacy", the two words are not interchangeable. Rather, confidentiality is a component of privacy that is implemented to protect data from unauthorized viewers. Examples of confidentiality of electronic data being compromised include laptop theft, password theft, or sensitive emails being sent to the incorrect individuals. In IT security, data integrity means maintaining and assuring the accuracy and completeness of data. This means that data cannot be modified in an unauthorized or undetected manner. More broadly, integrity is an information security principle that involves human/social, process, and commercial integrity, as well as data integrity. As such it touches on aspects such as credibility, consistency, truthfulness, completeness, accuracy, timeliness, and assurance. For any information system to serve its purpose, the information must be available when it is needed. This means the computing systems used to store and process the information, the security controls used to protect it, and the communication channels used to access it must be functioning correctly. Ensuring availability may also involve preventing denial-of-service attacks, such as a flood of incoming messages to the target system, essentially forcing it to shut down. In addition to the classic CIA triad of security goals, some organisations may want to include security goals such as authenticity, accountability, non-repudiation, and reliability. The merits of the Parkerian Hexad are a subject of debate amongst security professionals.
Risk is the likelihood that something bad will happen that causes harm to an informational asset (or the loss of the asset). A vulnerability is a weakness that could be used to endanger or cause harm to an informational asset. A threat is anything (man-made or act of nature) that has the potential to cause harm. The likelihood that a threat will use a vulnerability to cause harm creates a risk. When a threat does use a vulnerability to inflict harm, it has an impact. In the context of information security, the impact is a loss of availability, integrity, and confidentiality, and possibly other losses (lost income, loss of life, loss of real property). The Certified Information Systems Auditor (CISA) Review Manual 2006 defines risk management as "the process of identifying vulnerabilities and threats to the information resources used by an organization in achieving business objectives, and deciding what countermeasures, if any, to take in reducing risk to an acceptable level, based on the value of the information resource to the organization." There are two things in this definition that may need some clarification.
First, the process of risk management is an ongoing, iterative process. It must be repeated indefinitely. The business environment is constantly changing and new threats and vulnerabilities emerge every day. Second, the choice of countermeasures (controls) used to manage risks must strike a balance between productivity, cost, effectiveness of the countermeasure, and the value of the informational asset being protected. Furthermore, these processes have limitations as security breaches are generally rare and emerge in a specific context which may not be easily duplicated. Thus, any process and countermeasure should itself be evaluated for vulnerabilities. It is not possible to identify all risks, nor is it possible to eliminate all risk. The remaining risk is called "residual risk". A risk assessment is carried out by a team of people who have knowledge of specific areas of the business. Membership of the team may vary over time as different parts of the business are assessed. The assessment may use a subjective qualitative analysis based on informed opinion, or where reliable dollar figures and historical information is available, the analysis may use quantitative analysis. Research has shown that the most vulnerable point in most information systems is the human user, operator, designer, or other human. The ISO/IEC 27002:2005 Code of practice for information security management recommends the following be examined during a risk assessment: security policy, organization of information security, asset management, human resources security, physical and environmental security, communications and operations management, access control, information systems acquisition, development, and maintenance, information security incident management, business continuity management regulatory compliance. In broad terms, the risk management process consists of: Identification of assets and estimating their value. Include: people, buildings, hardware, software, data (electronic, print, other), supplies. Conduct a threat assessment. Include: Acts of nature, acts of war, accidents, malicious acts originating from inside or outside the organization. Conduct a vulnerability assessment, and for each vulnerability, calculate the probability that it will be exploited. Evaluate policies, procedures, standards, training, physical security, quality control, technical security.
Calculate the impact that each threat would have on each asset. Use qualitative analysis or quantitative analysis. Identify, select and implement appropriate controls. Provide a proportional response. Consider productivity, cost effectiveness, and value of the asset. Evaluate the effectiveness of the control measures. Ensure the controls provide the required cost effective protection without discernible loss of productivity. For any given risk, management can choose to accept the risk based upon the relative low value of the asset, the relative low frequency of occurrence, and the relative low impact on the business. Or, leadership may choose to mitigate the risk by selecting and implementing appropriate control measures to reduce the risk. In some cases, the risk can be transferred to another business by buying insurance or outsourcing to another business. The reality of some risks may be disputed. In such cases leadership may choose to deny the risk.
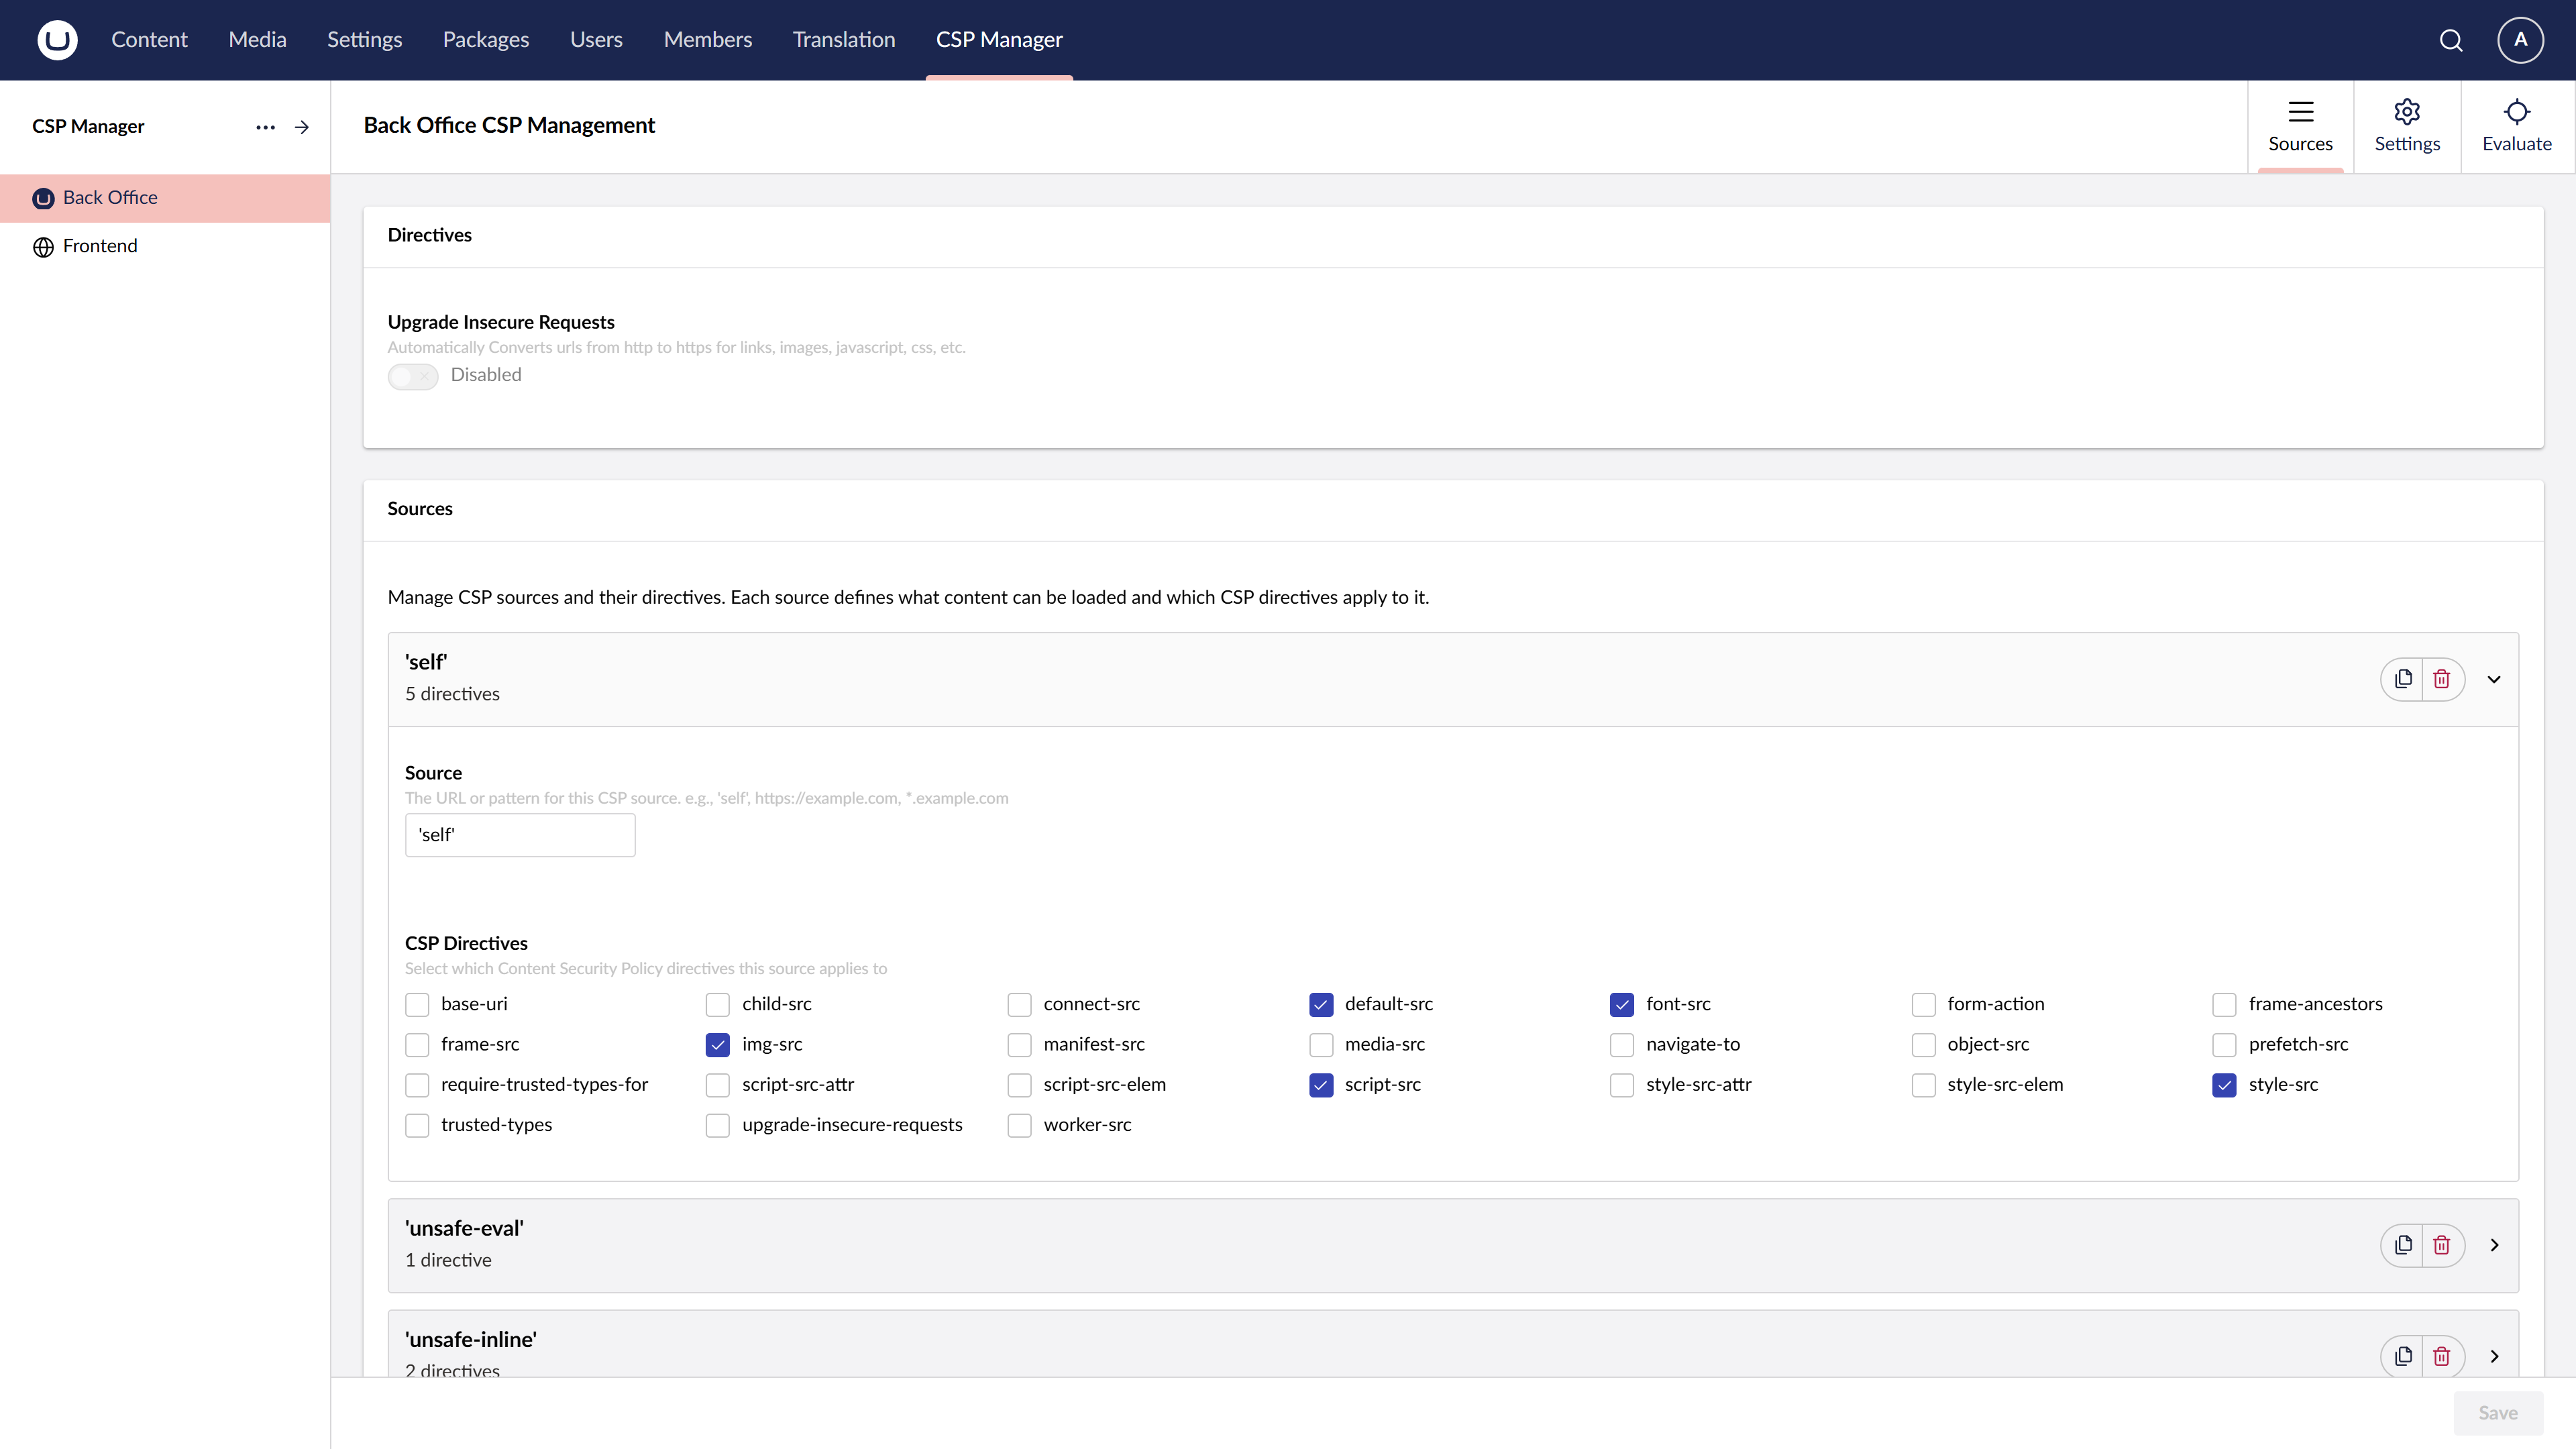
Figure 3: GitHub - Matthew-Wise/Umbraco-CSP-manager: Content security policy ... Selecting and implementing proper security controls will initially help an organization bring down risk to acceptable levels. Control selection should follow and should be based on the risk assessment. Controls can vary in nature, but fundamentally they are ways of protecting the confidentiality, integrity or availability of information. ISO/IEC 27001 has defined controls in different areas. Organizations can implement additional controls according to requirement of the organization. ISO/IEC 27002 offers a guideline for organizational information security standards.
Defense in depth is a fundamental security philosophy that relies on overlapping security systems designed to maintain protection even if individual components fail. Rather than depending on a single security measure, it combines multiple layers of security controls both in the cloud and at network endpoints. This approach includes combinations like firewalls with intrusion-detection systems, email filtering services with desktop anti-virus, and cloud-based security alongside traditional network defenses. The concept can be implemented through three distinct layers of administrative, logical, and physical controls, or visualized as an onion model with data at the core, surrounded by people, network security, host-based security, and application security layers. The strategy emphasizes that security involves not just technology, but also people and processes working together, with real-time monitoring and response being crucial components.
In the business sector, labels such as: Public, Sensitive, Private, Confidential. In the government sector, labels such as: Unclassified, Unofficial, Protected, Confidential, Secret, Top Secret, and their non-English equivalents. In cross-sectoral formations, the Traffic Light Protocol, which consists of: White, Green, Amber, and Red. In the personal sector, one label such as Financial. This includes activities related to managing money, such as online banking. All employees in the organization, as well as business partners, must be trained on the classification schema and understand the required security controls and handling procedures for each classification. The classification of a particular information asset that has been assigned should be reviewed periodically to ensure the classification is still appropriate for the information and to ensure the security controls required by the classification are in place and are followed in their right procedures.
Access to protected information must be restricted to people who are authorized to access the information. The computer programs, and in many cases the computers that process the information, must also be authorized. This requires that mechanisms be in place to control the access to protected information. The sophistication of the access control mechanisms should be in parity with the value of the information being protected; the more sensitive or valuable the information the stronger the control mechanisms need to be. The foundation on which access control mechanisms are built start with identification and authentication. Access control is generally considered in three steps: identification, authentication, and authorization.
Something one knows: things such as a PIN, a password, or one's mother's maiden name Something one has: a driver's license or a magnetic swipe card Something one is: biometrics, including palm prints, fingerprints, voice prints, and retina (eye) scans Strong authentication requires providing more than one type of authentication information (two-factor authentication). The username is the most common form of identification on computer systems today and the password is the most common form of authentication. Usernames and passwords have served their purpose, but they are increasingly inadequate. Usernames and passwords are slowly being replaced or supplemented with more sophisticated authentication mechanisms such as time-based one-time password algorithms.
Information security uses cryptography to transform usable information into a form that renders it unusable by anyone other than an authorized user; this process is called encryption. Information that has been encrypted (rendered unusable) can be transformed back into its original usable form by an authorized user who possesses the cryptographic key, through the process of decryption. Cryptography is used in information security to protect information from unauthorized or accidental disclosure while the information is in transit (either electronically or physically) and while information is in storage.
Cryptography provides information security with other useful applications as well, including improved authentication methods, message digests, digital signatures, non-repudiation, and encrypted network communications. Older, less secure applications such as Telnet and File Transfer Protocol (FTP) are slowly being replaced with more secure applications such as Secure Shell (SSH) that use encrypted network communications. Wireless communications can be encrypted using protocols such as WPA/WPA2 or the older (and less secure) WEP. Wired communications (such as ITUIT G.hn) are secured using AES for encryption and X.1035 for authentication and key exchange. Software applications such as GnuPG or PGP can be used to encrypt data files and email. Cryptography can introduce security problems when it is not implemented correctly.
Cryptographic solutions need to be implemented using industry-accepted solutions that have undergone rigorous peer review by independent experts in cryptography. The length and strength of the encryption key is also an important consideration. A key that is weak or too short will produce weak encryption. The keys used for encryption and decryption must be protected with the same degree of rigor as any other confidential information. They must be protected from unauthorized disclosure and destruction, and they must be available when needed. Public key infrastructure (PKI) solutions address many of the problems that surround key management.
"Due care are steps that are taken to show that a company has taken responsibility for the activities that take place within the corporation and has taken the necessary steps to help protect the company, its resources, and employees." And, [Due diligence are the] "continual activities that make sure the protection mechanisms are continually maintained and operational." Attention should be made to two important points in these definitions. First, in due care, steps are taken to show; this means that the steps can be verified, measured, or even produce tangible artifacts. Second, in due diligence, there are continual activities; this means that people are actually doing things to monitor and maintain the protection mechanisms, and these activities are ongoing. Organizations have a responsibility with practicing duty of care when applying information security. The Duty of Care Risk Analysis Standard (DoCRA) provides principles and practices for evaluating risk. It considers all parties that could be affected by those risks. DoCRA helps evaluate safeguards if they are appropriate in protecting others from harm while presenting a reasonable burden. With increased data breach litigation, companies must balance security controls, compliance, and its mission.
Computer security incident management is a specialized form of incident management focused on monitoring, detecting, and responding to security events on computers and networks in a predictable way. Organizations implement this through incident response plans (IRPs) that are activated when security breaches are detected. These plans typically involve an incident response team (IRT) with specialized skills in areas like penetration testing, computer forensics, and network security.
Change management is a formal process for directing and controlling alterations to the information processing environment. This includes alterations to desktop computers, the network, servers, and software. The objectives of change management are to reduce the risks posed by changes to the information processing environment and improve the stability and reliability of the processing environment as changes are made. It is not the objective of change management to prevent or hinder necessary changes from being implemented. Any change to the information processing environment introduces an element of risk. Even apparently simple changes can have unexpected effects. One of management's many responsibilities is the management of risk. Change management is a tool for managing the risks introduced by changes to the information processing environment. Part of the change management process ensures that changes are not implemented at inopportune times when they may disrupt critical business processes or interfere with other changes being implemented. Not every change needs to be managed. Some kinds of changes are a part of the everyday routine of information processing and adhere to a predefined procedure, which reduces the overall level of risk to the processing environment. Creating a new user account or deploying a new desktop computer are examples of changes that do not generally require change management. However, relocating user file shares, or upgrading the Email server pose a much higher level of risk to the processing environment and are not a normal everyday activity. The critical first steps in change management are (a) defining change (and communicating that definition) and (b) defining the scope of the change system. Change management is usually overseen by a change review board composed of representatives from key business areas, security, networking, systems administrators, database administration, application developers, desktop support, and the help desk. The tasks of the change review board can be facilitated with the use of automated work flow application. The responsibility of the change review board is to ensure the organization's documented change management procedures are followed. The change management process is as follows Request: Anyone can request a change. The person making the change request may or may not be the same person that performs the analysis or implements the change. When a request for change is received, it may undergo a preliminary review to determine if the requested change is compatible with the organizations business model and practices, and to determine the amount of resources needed to implement the change. Approve: Management runs the business and controls the allocation of resources therefore, management must approve requests for changes and assign a priority for every change. Management might choose to reject a change request if the change is not compatible with the business model, industry standards or best practices. Management might also choose to reject a change request if the change requires more resources than can be allocated for the change. Plan: Planning a change involves discovering the scope and impact of the proposed change; analyzing the complexity of the change; allocation of resources and, developing, testing, and documenting both implementation and back-out plans. Test: Every change must be tested in a safe test environment, which closely reflects the actual production environment, before the change is applied to the production environment. The backout plan must also be tested. Schedule: Part of the change review board's responsibility is to assist in the scheduling of changes by reviewing the proposed implementation date for potential conflicts with other scheduled changes or critical business activities.
Communicate: Once a change has been scheduled it must be communicated. The communication is to give others the opportunity to remind the change review board about other changes or critical business activities that might have been overlooked when scheduling the change. The communication also serves to make the help desk and users aware that a change is about to occur. Another responsibility of the change review board is to ensure that scheduled changes have been properly communicated to those who will be affected by the change or otherwise have an interest in the change. Implement: At the appointed date and time, the changes must be implemented. Part of the planning process was to develop an implementation plan, testing plan and, a back out plan. If the implementation of the change should fail or, the post implementation testing fails or, other "drop dead" criteria have been met, the back out plan should be implemented.
Document: All changes must be documented. The documentation includes the initial request for change, its approval, the priority assigned to it, the implementation, testing and back out plans, the results of the change review board critique, the date/time the change was implemented, who implemented it, and whether the change was implemented successfully, failed or postponed. Post-change review: The change review board should hold a post-implementation review of changes. It is particularly important to review failed and backed out changes. The review board should try to understand the problems that were encountered, and look for areas for improvement. Change management procedures that are simple to follow and easy to use can greatly reduce the overall risks created when changes are made to the information processing environment. Good change management procedures improve the overall quality and success of changes as they are implemented. This is accomplished through planning, peer review, documentation, and communication.
Business continuity management (BCM) concerns arrangements aiming to protect an organization's critical business functions from interruption due to incidents, or at least minimize the effects. BCM is essential to any organization to keep technology and business in line with current threats to the continuation of business as usual. The BCM should be included in an organizations risk analysis plan to ensure that all of the necessary business functions have what they need to keep going in the event of any type of threat to any business function. It encompasses: Analysis of requirements, e.g., identifying critical business functions, dependencies and potential failure points, potential threats and hence incidents or risks of concern to the organization; Architecture and design, e.g., an appropriate combination of approaches including resilience (e.g. engineering IT systems and processes for high availability, avoiding or preventing situations that might interrupt the business), incident and emergency management (e.g., evacuating premises, calling the emergency services, triage/situation assessment and invoking recovery plans), recovery (e.g., rebuilding) and contingency management (generic capabilities to deal positively with whatever occurs using whatever resources are available); Implementation, e.g., configuring and scheduling backups, data transfers, etc., duplicating and strengthening critical elements; contracting with service and equipment suppliers; Testing, e.g., business continuity exercises of various types, costs and assurance levels; Management, e.g., defining strategies, setting objectives and goals; planning and directing the work; allocating funds, people and other resources; prioritization relative to other activities; team building, leadership, control, motivation and coordination with other business functions and activities (e.g., IT, facilities, human resources, risk management, information risk and security, operations); monitoring the situation, checking and updating the arrangements when things change; maturing the approach through continuous improvement, learning and appropriate investment; Assurance, e.g., testing against specified requirements; measuring, analyzing, and reporting key parameters; conducting additional tests, reviews and audits for greater confidence that the arrangements will go to plan if invoked. Whereas BCM takes a broad approach to minimizing disaster-related risks by reducing both the probability and the severity of incidents, a disaster recovery plan (DRP) focuses specifically on resuming business operations as quickly as possible after a disaster. A disaster recovery plan, invoked soon after a disaster occurs, lays out the steps necessary to recover critical information and communications technology (ICT) infrastructure. Disaster recovery planning includes establishing a planning group, performing risk assessment, establishing priorities, developing recovery strategies, preparing inventories and documentation of the plan, developing verification criteria and procedure, and lastly implementing the plan.
Below is a partial listing of governmental laws and regulations in various parts of the world that have, had, or will have, a significant effect on data processing and information security. Important industry sector regulations have also been included when they have a significant impact on information security. The UK Data Protection Act 1998 makes new provisions for the regulation of the processing of information relating to individuals, including the obtaining, holding, use or disclosure of such information. The European Union Data Protection Directive (EUDPD) requires that all E.U. members adopt national regulations to standardize the protection of data privacy for citizens throughout the E.U. The Computer Misuse Act 1990 is an Act of the U.K. Parliament making computer crime (e.g., hacking) a criminal offense. The act has become a model upon which several other countries, including Canada and Ireland, have drawn inspiration from when subsequently drafting their own information security laws. The E.U.'s Data Retention Directive (annulled) required internet service providers and phone companies to keep data on every electronic message sent and phone call made for between six months and two years. The Family Educational Rights and Privacy Act (FERPA) (20 U.S.C. § 1232 g; 34 CFR Part 99) is a U.S. Federal law that protects the privacy of student education records. The law applies to all schools that receive funds under an applicable program of the U.S. Department of Education. Generally, schools must have written permission from the parent or eligible student in order to release any information from a student's education record. The Federal Financial Institutions Examination Council's (FFIEC) security guidelines for auditors specifies requirements for online banking security. The Health Insurance Portability and Accountability Act (HIPAA) of 1996 requires the adoption of national standards for electronic health care transactions and national identifiers for providers, health insurance plans, and employers. Additionally, it requires health care providers, insurance providers and employers to safeguard the security and privacy of health data. The Gramm–Leach–Bliley Act of 1999 (GLBA), also known as the Financial Services Modernization Act of 1999, protects the privacy and security of private financial information that financial institutions collect, hold, and process. Section 404 of the Sarbanes–Oxley Act of 2002 (SOX) requires publicly traded companies to assess the effectiveness of their internal controls for financial reporting in annual reports they submit at the end of each fiscal year. Chief information officers are responsible for the security, accuracy, and the reliability of the systems that manage and report the financial data. The act also requires publicly traded companies to engage with independent auditors who must attest to, and report on, the validity of their assessments. The Payment Card Industry Data Security Standard (PCI DSS) establishes comprehensive requirements for enhancing payment account data security. It was developed by the founding payment brands of the PCI Security Standards Council — including American Express, Discover Financial Services, JCB, MasterCard Worldwide, and Visa International — to help facilitate the broad adoption of consistent data security measures on a global basis. The PCI DSS is a multifaceted security standard that includes requirements for security management, policies, procedures, network architecture, software design, and other critical protective measures. State security breach notification laws (California and many others) require businesses, nonprofits, and state institutions to notify consumers when unencrypted "personal information" may have been compromised, lost, or stolen. The Personal Information Protection and Electronics Document Act (PIPEDA) of Canada supports and promotes electronic commerce by protecting personal information that is collected, used or disclosed in certain circumstances, by providing for the use of electronic means to communicate or record information or transactions and by amending the Canada Evidence Act, the Statutory Instruments Act and the Statute Revision Act. Greece's Hellenic Authority for Communication Security and Privacy (ADAE) (Law 165/2011) establishes and describes the minimum information security controls that should be deployed by every company which provides electronic communication networks and/or services in Greece in order to protect customers' confidentiality. These include both managerial and technical controls (e.g., log records should be stored for two years). Greece's Hellenic Authority for Communication Security and Privacy (ADAE) (Law 205/2013) concentrates around the protection of the integrity and availability of the services and data offered by Greek telecommunication companies. The law forces these and other related companies to build, deploy, and test appropriate business continuity plans and redundant infrastructures. The US Department of Defense (DoD) issued DoD Directive 8570 in 2004, supplemented by DoD Directive 8140, requiring all DoD employees and all DoD contract personnel involved in information assurance roles and activities to earn and maintain various industry Information Technology (IT) certifications in an effort to ensure that all DoD personnel involved in network infrastructure defense have minimum levels of IT industry recognized knowledge, skills and abilities (KSA). Andersson and Reimers (2019) report these certifications range from CompTIA's A+ and Security+ through the ICS2.org's CISSP, etc.
Attitudes: employees' feelings and emotions about the various activities that pertain to the organizational security of information. Behaviors: actual or intended activities and risk-taking actions of employees that have direct or indirect impact on information security. Cognition: employees' awareness, verifiable knowledge, and beliefs regarding practices, activities, and self-efficacy relation that are related to information security. Communication: ways employees communicate with each other, sense of belonging, support for security issues, and incident reporting. Compliance: adherence to organizational security policies, awareness of the existence of such policies and the ability to recall the substance of such policies. Norms: perceptions of security-related organizational conduct and practices that are informally deemed either normal or deviant by employees and their peers, e.g. hidden expectations regarding security behaviors and unwritten rules regarding uses of information-communication technologies. Responsibilities: employees' understanding of the roles and responsibilities they have as a critical factor in sustaining or endangering the security of information, and thereby the organization. Andersson and Reimers (2014) found that employees often do not see themselves as part of the organization Information Security "effort" and often take actions that ignore organizational information security best interests. Research shows information security culture needs to be improved continuously. In Information Security Culture from Analysis to Change, authors commented, "It's a never ending process, a cycle of evaluation and change or maintenance." To manage the information security culture, five steps should be taken: pre-evaluation, strategic planning, operative planning, implementation, and post-evaluation.
2. System Architecture & Core Working Principles Pre-evaluation: to identify the awareness of information security within employees and to analyze current security policy Strategic planning: to come up a better awareness-program, we need to set clear targets. Clustering people is helpful to achieve it Operative planning: create a good security culture based on internal communication, management buy-in, security awareness, and training programs Implementation: should feature commitment of management, communication with organizational members, courses for all organizational members, and commitment of the employees Post-evaluation: to better gauge the effectiveness of the prior steps and build on continuous improvement DoD IA Policy Chart Archived 2011-09-06 at the Wayback Machine on the DoD Information Assurance Technology Analysis Center web site. patterns & practices Security Engineering Explained IWS – Information Security Chapter Archived 2019-11-08 at the Wayback Machine Ross Anderson's book "Security Engineering" Content Credentials are cryptographically signed metadata structures, known as C2PA manifests, that provide a verifiable record of a digital asset's provenance and modification history. Defined by the C2PA specifications, this architecture establishes a core set of technical assertions, while supporting custom schemas to extend metadata regarding authorship, content intent, and machine-readable usage preferences. The core C2PA specification is authored and maintained by the Coalition for Content Provenance and Authenticity (C2PA), an industry group composed of major technology firms and media companies. It operates as a project of the Joint Development Foundation (JDF), an affiliate of the Linux Foundation. A supplementary specification addressing identity, publishing, licensing, and schema-based assertions is defined in the Creators Assertions Working Group (CAWG) specification. This specification is overseen by the Decentralized Identity Foundation (DIF) and maintained by Adobe. Parallel promotional initiatives, including sponsored brand campaigns in media outlets, educational outreach, and legislative adoption efforts, are led by the Content Authenticity Initiative (CAI), a cross-sector coalition established by Adobe.
Nikon announced in August 2025 a firmware update for the Z6III that enabled embedding Content Credentials directly into its photos. But only a few days later, a vulnerability was discovered in the software of the camera that allowed a user to combine unauthentic images with authentic photos and still have the resulting image with a valid digital signature. Nikon suspended its authenticity service and revoked the certificates.
In August 2026, security researcher David Buchanan demonstrated that the C2PA implementation on Android is vulnerable to forgery. Using software exploit, an attacker can gain root access. While the raw cryptographic keys remain secure inside the hardware module, root access allows an attacker to command the system to sign arbitrary data, generating fabricated images with valid authenticity signatures. Google recognized the vulnerability but designated the report as "Won't fix (infeasible)", stating that a true mitigation would require an impractical re-architecture of the operating system software stack.
CSP prevents 90% of XSS attacks when properly implemented, but 70% of implementations are too permissive and fail to provide protection. According to the 2024 Web Security Report, applications with strict CSP experience 90% fewer XSS incidents, while those with weak CSP policies see no reduction in attacks. CSP implementation is complex—policies must balance security with functionality, and misconfiguration renders CSP ineffective. This guide shows you how to implement production-ready CSP policies with proper reporting, policy tuning, and comprehensive coverage.
Implement Content Security Policy to prevent XSS and unauthorized resource loading. Use strict policies, enable reporting, and tune based on violations. Objective: Implement basic CSP. Steps: Configure CSP header, test policy, monitor violations. Expected: Basic CSP operational.
Objective: Implement advanced CSP features. Steps: Strict CSP + reporting + monitoring + optimization. Expected: Advanced CSP operational. Objective: Complete CSP security program. Steps: All CSP features + monitoring + testing + optimization. Expected: Comprehensive CSP program.
Diagnosis: Review CSP policy, check violations, test functionality. Solutions: Update CSP policy, add allowed sources, test functionality. Diagnosis: Review violation reports, check policy, analyze sources. Solutions: Tune policy, add allowed sources, reduce violations.
Diagnosis: Review policy, check security posture, assess risks. Solutions: Tighten policy, remove unnecessary sources, improve security. Content Security Policy prevents XSS and unauthorized resource loading. Implement strict policies, enable reporting, and tune based on violations.
Educational Use Only : This content is for educational purposes. Only implement for applications you own or have explicit authorization. Learn all XSS attack types (reflected, stored, DOM-based) and comprehensive defense strategies to prevent XSS vulnerabilities.
Defend browsers against supply-chain JS, extension abuse, AI-driven phishing, and clickjacking with concrete mitigations, validation, and cleanup. Learn to implement all security headers effectively to protect web applications from various attacks.Learn essential cybersecurity strategies and best practi...
Harden a web app against AI-assisted attacks, JS supply-chain threats, and HTTP/3 quirks with concrete checks, validation, and cleanup. No—treat them as educational. Adapt, review, and security-test before any production use. Start from the Learn page order or use Previous/Next on each lesson; both flow consistently.
Use synthetic data and local/lab environments. Never target networks or data you don't own or have written permission to test. Yes, with attribution and respecting any licensing for referenced tools or datasets. Start by deploying a strict policy in report-only mode to discover what would break without actually blocking anything. [ src6 ] Verify : Open browser DevTools > Console -- CSP violations appear as warnings with [Report Only] prefix.
Generate a cryptographically random nonce per request and add it to every inline Content-Security-Policy: script-src 'self' 'nonce-
Once you are confident that your policy allows all legitimate resources and blocks only malicious or undesirable content, switch from report-only mode to enforcement mode. CSP is one component of a comprehensive security header strategy. It complements other important headers: Use ScanSearch to discover exposed services, open ports, and security vulnerabilities across your infrastructure.
Clickjacking defense primarily relies on the X-Frame-Options HTTP header or, more effectively, the Content-Security-Policy (CSP) frame-ancestors directive. These measures prevent malicious embedding of web pages within iframes, safeguarding users from unintended actions and data exposure. Learn how SQL Injection (SQLi) works, the different types like Blind and Union-based, and technical prevention strategies to secure your database and web applications.
Learn how Web Application Firewalls (WAF) protect Layer 7 traffic, mitigate OWASP Top 10 threats, and why they are essential for modern web security and compliance. SQLMap is an open-source penetration testing tool that automates detecting and exploiting SQL injection flaws. This article details its features, usage, advanced exploitation techniques, and critical mitigation strategies for securing web applications.
Nikto is an open-source web server scanner designed to find common vulnerabilities, misconfigurations, and outdated software on web servers. This guide provides a detailed tutorial on installing, configuring, and effectively using Nikto for web security assessments, including advanced options and result interpretation. Nuclei Scanner is a powerful, open-source tool for rapid and customizable vulnerability detection, leveraging community-driven templates to identify security flaws across various targets and protocols. It excels in speed, flexibility, and integration capabilities for modern security workflows.
In modern software engineering, content security policy implementation guide has become a critical topic that teams cannot afford to ignore. The difference between doing this well and doing it poorly often determines whether a project succeeds or fails at scale. This guide covers the practical aspects that matter most in production environments. Understanding content security policy implementation guide requires looking beyond surface-level best practices to the underlying principles that drive good engineering decisions. The choices you make here ripple through your entire codebase and operational workflow, affecting everything from developer productivity to system reliability.
The landscape around content security policy implementation guide has evolved significantly in recent years. What was considered best practice five years ago may now be outdated or even counterproductive. This guide reflects current industry knowledge informed by real production experience at scale. The technical foundations here are straightforward once you understand the underlying principles. Start with the simplest approach that meets your requirements and add complexity only when you have evidence that it is needed. Premature optimization in this area is just as dangerous as in any other part of software engineering.
A common pattern is to begin with a well-understood, proven approach and iterate from there. Each iteration should be driven by measurable feedback from production usage. This evidence-based approach prevents over-engineering while ensuring you do not under-invest in areas that matter. Integration with existing systems and workflows is often the most challenging aspect. The technical implementation itself may be straightforward, but fitting it into an established development process, CI/CD pipeline, and operational workflow requires careful planning and incremental rollout.
Begin with a clear assessment of your current state. What works well? What are the bottlenecks? Where are the highest-risk areas? This baseline understanding prevents you from solving the wrong problems and helps you prioritize investments for maximum impact. 4. Practical Deployment, Analysis & Case Studies Incremental implementation reduces risk dramatically. Rather than a big-bang migration or adoption, identify a single team, service, or workflow to pilot the new approach. Learn from the pilot, refine your strategy, and expand gradually. Document what you learn so that subsequent rollouts go more smoothly.
Invest in automation early. Manual processes do not scale and are prone to human error. Whether it is testing, deployment, monitoring, or configuration management, automating the repetitive tasks frees your team to focus on the work that actually requires human judgment. Measure the impact of every change. Define success metrics before implementation, collect baseline data, and compare before-and-after results. This evidence-based approach builds organizational confidence in the new practices and identifies areas that need further refinement.
Write code that humans can read and maintain. Clever code is a liability in production systems. Clear naming, consistent formatting, small functions with single responsibilities, and judicious use of comments create codebases that the entire team can work in confidently. Design for failure from the start. In distributed systems, failures are routine. Build resilience with circuit breakers, retries with backoff, graceful degradation, health checks, and automated recovery. Test failure scenarios regularly.
Invest in observability. Comprehensive logging, metrics, and distributed tracing are not luxuries. When issues arise in production, observability tools are the difference between resolving problems in minutes and spending hours debugging. Over-engineering is one of the most common pitfalls. Building for hypothetical future requirements that may never materialize wastes time and adds complexity. Follow the YAGNI principle and build for current, well-understood requirements.
Neglecting non-functional requirements until late in the project is another frequent mistake. Performance, security, scalability, and observability should be addressed from the beginning. Ignoring team dynamics and organizational factors is a subtle but impactful pitfall. The best technical solution is worthless if the team cannot understand, maintain, or operate it.
The field of content security policy implementation guide continues to evolve. New tools and best practices emerge regularly. Staying current requires continuous learning through industry publications, conferences, and experimentation. The most successful engineering teams combine technical excellence with pragmatic decision-making. The goal is not to use the newest technology but to deliver working software that meets user needs reliably and efficiently.
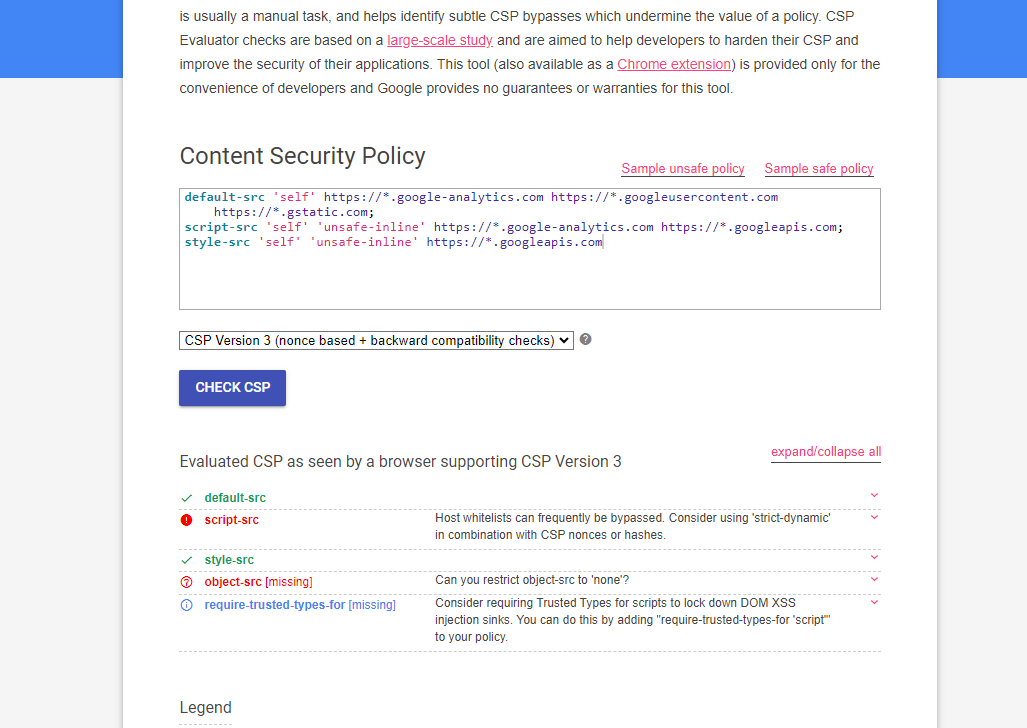
Start small, iterate continuously, and measure everything. Apply the principles discussed here incrementally, validating each change against clear metrics. Build on what works and learn from what does not. CSP Evaluator allows developers and security experts to check if a Content Security Policy (CSP) serves as a strong mitigation against cross-site scripting attacks . It assists with the process of reviewing CSP policies, which is usually a manual task, and helps identify subtle CSP bypasses which undermine the value of a policy. CSP Evaluator checks are based on a large-scale study and are aimed to help developers to harden their CSP and improve the security of their applications. This tool (also available as a Chrome extension ) is provided only for the convenience of developers and Google provides no guarantees or warranties for this tool.
Deep inspection of your security headers and CSP implementation with actionable recommendations. Deep analysis of Content Security Policy directives, identifying gaps and security risks in your implementation. Comprehensive check of all security-related HTTP headers with best practice recommendations. Intelligent risk scoring based on your security posture with prioritized improvement suggestions.
Instant analysis of your security headers and CSP implementation with live feedback and recommendations. Detailed security reports with actionable insights and specific recommendations for improvement. Industry-standard recommendations based on OWASP guidelines and security best practices. Deep analysis of CSP directives, identifying potential security gaps and optimization opportunities.
Automatic detection and reporting of CSP violations with detailed context and remediation steps. Comprehensive SSL certificate validation and configuration analysis for secure connections. Content Security Policy (CSP) is a security standard that helps prevent cross-site scripting (XSS), clickjacking, and other code injection attacks. It works by specifying which sources of content are allowed to be loaded on your website, giving you fine-grained control over scripts, styles, images, and other resources.
Security headers are HTTP response headers that add extra layers of protection to your website. They help prevent common attacks like XSS, clickjacking, and man-in-the-middle attacks. Without proper security headers, your website and users are vulnerable to various exploits that could compromise sensitive data. The 'unsafe-inline' directive allows inline JavaScript and CSS to execute on your page. While convenient, it significantly weakens your CSP protection because attackers can inject malicious inline scripts. We recommend using nonces or hashes instead to allow specific inline code safely.
To improve your security score: 1) Implement a Content Security Policy header, 2) Add HSTS (Strict-Transport-Security) for HTTPS enforcement, 3) Remove 'unsafe-inline' and 'unsafe-eval' from your CSP, 4) Add X-Frame-Options to prevent clickjacking, and 5) Include X-Content-Type-Options to prevent MIME sniffing attacks. Yes, HeaderTest is completely free to use. You can scan unlimited websites without registration or any cost. We believe web security should be accessible to everyone, from individual developers to large enterprises.
5. Performance Evaluation & Extended Technical Observations Content Security Policy (CSP) and Cross-Origin Resource Sharing (CORS) serve different purposes. CSP controls which resources your page can load, protecting against XSS and data injection attacks. CORS controls which external origins can access your API or resources, protecting your server from unauthorized cross-origin requests. Both are important: CSP protects your users, while CORS protects your server. A strong security posture requires both headers configured correctly.
We recommend scanning your security headers after every deployment and at least once a month as a routine check. Configuration changes, framework updates, or CDN modifications can inadvertently remove or weaken security headers. Regular scanning ensures you catch regressions early before they become exploitable vulnerabilities. The 'strict-dynamic' CSP directive allows scripts loaded by already-trusted scripts to execute, without needing to explicitly whitelist each one. When combined with nonces or hashes, it simplifies CSP management for applications that dynamically load scripts. It is recommended for modern web applications because it reduces the need for broad domain whitelists while maintaining strong XSS protection. However, it requires nonce-based or hash-based CSP to work correctly.
Paste a Content-Security-Policy and get a graded evaluation: weaknesses flagged directive by directive, with prioritized fixes. Paste a Content-Security-Policy and get a graded evaluation: every directive checked, weaknesses flagged, prioritized fixes. The kind of policy most sites still ship, graded and flagged directive by directive. Paste yours above to get the same verdict. A few things to tidy up: dated values, duplicated directives, options that no longer match current practice. None of them weakens the site, they just make it harder to maintain.
Flagged values are tinted by severity. Select one to see what is wrong, the impact, and the fix to apply. 'unsafe-inline' allows any injected script to run The script-src directive allows inline scripts. An attacker who can inject HTML into the page can execute arbitrary JavaScript, which is the exact attack a CSP exists to stop. Critical Security Critical Security Replace 'unsafe-inline' with a nonce or a hash for each inline script you actually ship. Browsers that support CSP Level 2 or 3 will then ignore a leftover 'unsafe-inline' fallback.
Any successful HTML injection becomes full cross-site scripting: session theft, payment form skimming, account takeover. An allowlisted host exposes a JSONP endpoint that bypasses the policy www.google-analytics.com serves a JSONP endpoint. Because the whole host is trusted, an attacker can point a script tag at that endpoint with a callback of their choice and execute code with the policy enforced. High Security High Security Load the analytics snippet with a nonce or hash plus 'strict-dynamic' instead of allowlisting the host, so trust attaches to the script you ship rather than to everything the host serves.
The policy reads as strict but is bypassable in practice: a known public technique turns the trusted host into an execution route. A wildcard host trusts every file on every subdomain *.example-cdn.com allows scripts from any subdomain of the CDN. You are not trusting your bundle, you are trusting every customer upload and every forgotten bucket under that wildcard. High Security High Security Pin the exact hostname you load from, or better, move script-src to a nonce or hash plus 'strict-dynamic' and drop the host list entirely.
Any attacker-controlled file anywhere under the wildcard executes as if it were your own code. No object-src or base-uri fallback The policy sets neither object-src nor base-uri. Plugins fall back to default-src, and a missing base-uri lets an injected
img-src * allows images from any origin A wildcard image source is rarely exploitable on its own, but it makes the policy noisy to review and can leak visitor data to arbitrary origins through image requests. Low Quality Low Quality A maintainability and privacy smell rather than a direct execution risk; it lowers the quality score, not the security score. A Content-Security-Policy is only as strong as its weakest directive. The evaluator reads the policy the way an attacker would: it looks for the keyword, the wildcard, or the allowlisted host that turns your header into a bypass.
Google's CSP Evaluator and ours flag the same core weaknesses. What differs is what you get back, and what happens after the policy ships. The policy is parsed directive by directive and every source value is checked for what an attacker could use: unsafe keywords, overly broad sources, missing fallback directives, and allowlisted hosts that can be abused to run code the policy was supposed to block. Each class of weakness is explained in the script-src directive reference .
The verdict is built to be acted on: every weakness is pinned to the directive that caused it, with the fix right next to it. A dangerous keyword? Flagged. A source broad enough to be abused? Flagged too. Chase the security score first, a tidy policy can still be wide open, and clear the next actions in order: they are already sorted by what an attacker would use first. Two axes, one to chase. The security score measures how well the policy resists real attacks; the quality score measures how cleanly it is written. A policy can be immaculately authored and still leave the door open, so when the two disagree, the security score is the one that matters.
'unsafe-inline' in script-src is the first. It allows any injected script to run, which is the exact thing the directive exists to stop. The fix is a nonce or a hash for the inline code you actually need. A wildcard or a long host allowlist is the second. A wildcard host trusts every file on every subdomain, and a long allowlist is only as strong as its weakest entry: one host serving a JSONP endpoint is enough to bypass the policy. The fix is to shorten the list, or move to a nonce with strict-dynamic so the list stops carrying the weight.
Harvested Online Documentation & Reference Sources • https://en.wikipedia.org/wiki/Security%20Content%20Automation%20Protocol • https://en.wikipedia.org/wiki/Information%20security • https://en.wikipedia.org/wiki/Content%20Credentials • https://cyberguid.com/content-security-policy-2026/ • https://knowledgelib.io/software/security/content-security-policy/2026 • https://scansearch.net/en/articles/content-security-policy-csp-guide/ • https://hatchsquare.com/blog/content-security-policy-implementation-guide.html • https://csp-evaluator.withgoogle.com/ • https://headertest.com/features • https://centralcsp.com/en/tools/csp-evaluator/
Extracted Research Figures & Simulation Topologies
Total 3 diagrams and telemetry visual outputs extracted directly from the complete technical documentation.
Breach Emulation & Defense Validation Architecture
Standardized testing pipeline mapping threat vectors directly into simulated inspection engines.
(AttackIQ / SafeBreach)
(Burp Suite Pro)
(Cisco Packet Tracer)
(Metasploit Engine)
(KnowBe4 Training)
Sample Simulation Code & Telemetry Log
Automated tool orchestration script and command window outputs for Content Security Policy Validator Tool Using Python.
[*] Metasploit Scan Running on Target Subnet for Content Security Policy Validator Tool Using Python... [✓] SafeBreach / AttackIQ Continuous Exposure Agent Triggered ──────────────────────────────────────────────────────────────────────── [11:48:02.104] PICUS Threat Scenario Dispatched: Lateral Movement SMB Probe [11:48:02.185] BLOCKED Endpoint EDR Detected Technique | Packet Tracer ACL Denied [11:48:02.240] CYMULATE Prevention Rate = 96.8% | SIEM Latency = 38 ms [11:48:02.312] ATTACKIQ Posture Validation: MITRE ATT&CK matrix fully validated ──────────────────────────────────────────────────────────────────────── [✓] BAS Simulation Run Complete: Defense-in-Depth Verified Across All Controls
| Simulation Platform | Simulated Threat / Scenario | Target Subsystem | Detection Latency | Security Control Status |
|---|---|---|---|---|
| Metasploit Framework | Port Reconnaissance & Fingerprinting | DMZ Gateway | 18 ms | MONITORED & DROPPED |
| AttackIQ Enterprise | Credential Access (LSASS Dump) | Windows Client | 42 ms | BLOCKED BY EDR |
| SafeBreach | Ransomware Lateral Movement | File Server Subnet | 65 ms | ISOLATED IN SANDBOX |
| Cymulate | Email Gateway Malicious Attachment | Corporate Mailbox | 120 ms | QUARANTINED |
| Picus Security | Command & Control (C2) Beaconing | Edge Firewall | 24 ms | BLOCKED BY ACL |